ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | Recorder-devices-setup.exe |
| Full analysis: | https://app.any.run/tasks/5142bc40-675d-4e8a-bf3e-9efe6cabe009 |
| Verdict: | Malicious activity |
| Analysis date: | April 20, 2022, 09:17:47 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/x-dosexec |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows |
| MD5: | E09736A4ED2CBB2F19AAB3F58D910DDA |
| SHA1: | 213C561FD813B301E92A391BF8DB49B14721B57F |
| SHA256: | CA84B2FF21BE23E1301E2B00C5464D558B797354AE39BEC611756B1E09E4A8F5 |
| SSDEEP: | 24576:t4nXubIQGyxbPV0db26W582L39rcB/sv1Et9uGpckT52zedlq89Ws5uIzk5aM/py:tqe3f6P2L39rA0SffPMWrQ0ZkK |
| .exe | | | Inno Setup installer (53.5) |
|---|---|---|
| .exe | | | InstallShield setup (21) |
| .exe | | | Win32 EXE PECompact compressed (generic) (20.2) |
| .exe | | | Win32 Executable (generic) (2.1) |
| .exe | | | Win16/32 Executable Delphi generic (1) |
| ProductVersion: | 0.12.10 |
|---|---|
| ProductName: | Recorder Devices for ShareX |
| OriginalFileName: | |
| LegalCopyright: | |
| FileVersion: | |
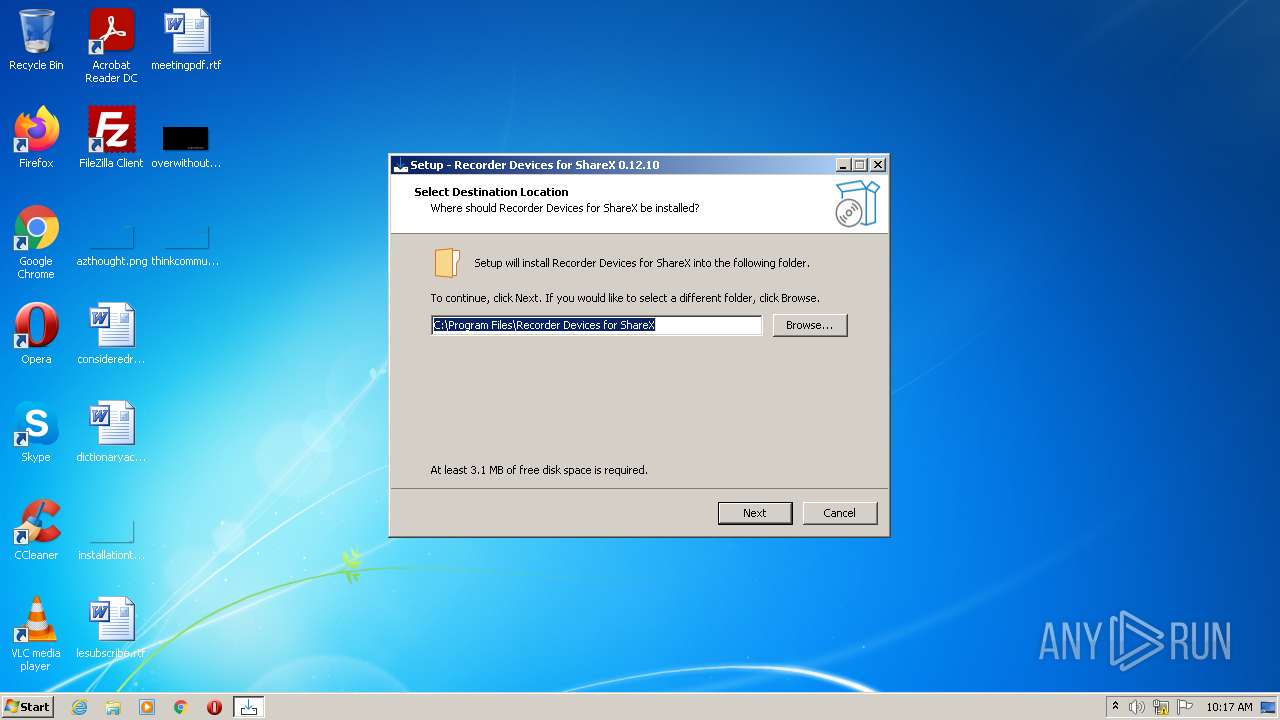
| FileDescription: | Recorder Devices for ShareX Setup |
| CompanyName: | |
| Comments: | This installation was built with Inno Setup. |
| CharacterSet: | Unicode |
| LanguageCode: | Neutral |
| FileSubtype: | - |
| ObjectFileType: | Executable application |
| FileOS: | Win32 |
| FileFlags: | (none) |
| FileFlagsMask: | 0x003f |
| ProductVersionNumber: | 0.0.0.0 |
| FileVersionNumber: | 0.0.0.0 |
| Subsystem: | Windows GUI |
| SubsystemVersion: | 6.1 |
| ImageVersion: | 6 |
| OSVersion: | 6.1 |
| EntryPoint: | 0xb5eec |
| UninitializedDataSize: | - |
| InitializedDataSize: | 89088 |
| CodeSize: | 741376 |
| LinkerVersion: | 2.25 |
| PEType: | PE32 |
| TimeStamp: | 2021:06:03 10:09:11+02:00 |
| MachineType: | Intel 386 or later, and compatibles |
| Architecture: | IMAGE_FILE_MACHINE_I386 |
|---|---|
| Subsystem: | IMAGE_SUBSYSTEM_WINDOWS_GUI |
| Compilation Date: | 03-Jun-2021 08:09:11 |
| Detected languages: |
|
| Comments: | This installation was built with Inno Setup. |
| CompanyName: | - |
| FileDescription: | Recorder Devices for ShareX Setup |
| FileVersion: | - |
| LegalCopyright: | - |
| OriginalFileName: | - |
| ProductName: | Recorder Devices for ShareX |
| ProductVersion: | 0.12.10 |
| Magic number: | MZ |
|---|---|
| Bytes on last page of file: | 0x0050 |
| Pages in file: | 0x0002 |
| Relocations: | 0x0000 |
| Size of header: | 0x0004 |
| Min extra paragraphs: | 0x000F |
| Max extra paragraphs: | 0xFFFF |
| Initial SS value: | 0x0000 |
| Initial SP value: | 0x00B8 |
| Checksum: | 0x0000 |
| Initial IP value: | 0x0000 |
| Initial CS value: | 0x0000 |
| Overlay number: | 0x001A |
| OEM identifier: | 0x0000 |
| OEM information: | 0x0000 |
| Address of NE header: | 0x00000100 |
| Signature: | PE |
|---|---|
| Machine: | IMAGE_FILE_MACHINE_I386 |
| Number of sections: | 10 |
| Time date stamp: | 03-Jun-2021 08:09:11 |
| Pointer to Symbol Table: | 0x00000000 |
| Number of symbols: | 0 |
| Size of Optional Header: | 0x00E0 |
| Characteristics: |
|
Name | Virtual Address | Virtual Size | Raw Size | Charateristics | Entropy |
|---|---|---|---|---|---|
.text | 0x00001000 | 0x000B361C | 0x000B3800 | IMAGE_SCN_CNT_CODE, IMAGE_SCN_MEM_EXECUTE, IMAGE_SCN_MEM_READ | 6.35606 |
.itext | 0x000B5000 | 0x00001688 | 0x00001800 | IMAGE_SCN_CNT_CODE, IMAGE_SCN_MEM_EXECUTE, IMAGE_SCN_MEM_READ | 5.97275 |
.data | 0x000B7000 | 0x000037A4 | 0x00003800 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 5.0444 |
.bss | 0x000BB000 | 0x00006DE8 | 0x00000000 | IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 0 |
.idata | 0x000C2000 | 0x00000F36 | 0x00001000 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 4.8987 |
.didata | 0x000C3000 | 0x000001A4 | 0x00000200 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 2.75636 |
.edata | 0x000C4000 | 0x0000009A | 0x00000200 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ | 1.87222 |
.tls | 0x000C5000 | 0x00000018 | 0x00000000 | IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 0 |
.rdata | 0x000C6000 | 0x0000005D | 0x00000200 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ | 1.38389 |
.rsrc | 0x000C7000 | 0x00010E00 | 0x00010E00 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ | 3.71088 |
Title | Entropy | Size | Codepage | Language | Type |
|---|---|---|---|---|---|
1 | 5.18295 | 1830 | UNKNOWN | English - United States | RT_MANIFEST |
2 | 1.98658 | 1640 | UNKNOWN | English - United States | RT_ICON |
3 | 2.01586 | 744 | UNKNOWN | English - United States | RT_ICON |
4 | 2.1704 | 296 | UNKNOWN | English - United States | RT_ICON |
5 | 1.912 | 5672 | UNKNOWN | English - United States | RT_ICON |
6 | 1.8663 | 3752 | UNKNOWN | English - United States | RT_ICON |
7 | 1.49649 | 2216 | UNKNOWN | English - United States | RT_ICON |
8 | 0.972379 | 1384 | UNKNOWN | English - United States | RT_ICON |
9 | 7.68913 | 4837 | UNKNOWN | English - United States | RT_ICON |
10 | 2.03031 | 16936 | UNKNOWN | English - United States | RT_ICON |
advapi32.dll |
comctl32.dll |
kernel32.dll |
kernel32.dll (delay-loaded) |
netapi32.dll |
oleaut32.dll |
user32.dll |
version.dll |
Title | Ordinal | Address |
|---|---|---|
dbkFCallWrapperAddr | 1 | 0x000BE63C |
__dbk_fcall_wrapper | 2 | 0x0000D0A0 |
TMethodImplementationIntercept | 3 | 0x00054060 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1520 | "C:\Users\admin\AppData\Local\Temp\Recorder-devices-setup.exe" /SPAWNWND=$20130 /NOTIFYWND=$20138 | C:\Users\admin\AppData\Local\Temp\Recorder-devices-setup.exe | Recorder-devices-setup.tmp | ||||||||||||
User: admin Company: Integrity Level: HIGH Description: Recorder Devices for ShareX Setup Exit code: 0 Version: Modules
| |||||||||||||||
| 2544 | "C:\Users\admin\AppData\Local\Temp\Recorder-devices-setup.exe" | C:\Users\admin\AppData\Local\Temp\Recorder-devices-setup.exe | Explorer.EXE | ||||||||||||
User: admin Company: Integrity Level: MEDIUM Description: Recorder Devices for ShareX Setup Exit code: 0 Version: Modules
| |||||||||||||||
| 2572 | "C:\Users\admin\AppData\Local\Temp\is-LNL27.tmp\Recorder-devices-setup.tmp" /SL5="$20138,924133,831488,C:\Users\admin\AppData\Local\Temp\Recorder-devices-setup.exe" | C:\Users\admin\AppData\Local\Temp\is-LNL27.tmp\Recorder-devices-setup.tmp | — | Recorder-devices-setup.exe | |||||||||||
User: admin Company: Integrity Level: MEDIUM Description: Setup/Uninstall Exit code: 0 Version: 51.1052.0.0 Modules
| |||||||||||||||
| 3708 | "C:\Users\admin\AppData\Local\Temp\is-0NF4N.tmp\Recorder-devices-setup.tmp" /SL5="$2013A,924133,831488,C:\Users\admin\AppData\Local\Temp\Recorder-devices-setup.exe" /SPAWNWND=$20130 /NOTIFYWND=$20138 | C:\Users\admin\AppData\Local\Temp\is-0NF4N.tmp\Recorder-devices-setup.tmp | — | Recorder-devices-setup.exe | |||||||||||
User: admin Company: Integrity Level: HIGH Description: Setup/Uninstall Exit code: 0 Version: 51.1052.0.0 Modules
| |||||||||||||||
| (PID) Process: | (3708) Recorder-devices-setup.tmp | Key: | HKEY_CURRENT_USER\Software\Microsoft\RestartManager\Session0000 |
| Operation: | write | Name: | Owner |
Value: 7C0E0000BC6ECC839754D801 | |||
| (PID) Process: | (3708) Recorder-devices-setup.tmp | Key: | HKEY_CURRENT_USER\Software\Microsoft\RestartManager\Session0000 |
| Operation: | write | Name: | SessionHash |
Value: 96DA54DA8F8C3BE5317FBC9ADCD2863A86C4F54330878C1339D7E42083525D43 | |||
| (PID) Process: | (3708) Recorder-devices-setup.tmp | Key: | HKEY_CURRENT_USER\Software\Microsoft\RestartManager\Session0000 |
| Operation: | write | Name: | Sequence |
Value: 1 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2544 | Recorder-devices-setup.exe | C:\Users\admin\AppData\Local\Temp\is-LNL27.tmp\Recorder-devices-setup.tmp | executable | |
MD5:975FC54803CACE54FD3190149DC446DE | SHA256:00CD32780D79F1CDFCBC4271AB6586CBB2792502AA195232F46662D5EC330124 | |||
| 1520 | Recorder-devices-setup.exe | C:\Users\admin\AppData\Local\Temp\is-0NF4N.tmp\Recorder-devices-setup.tmp | executable | |
MD5:975FC54803CACE54FD3190149DC446DE | SHA256:00CD32780D79F1CDFCBC4271AB6586CBB2792502AA195232F46662D5EC330124 | |||