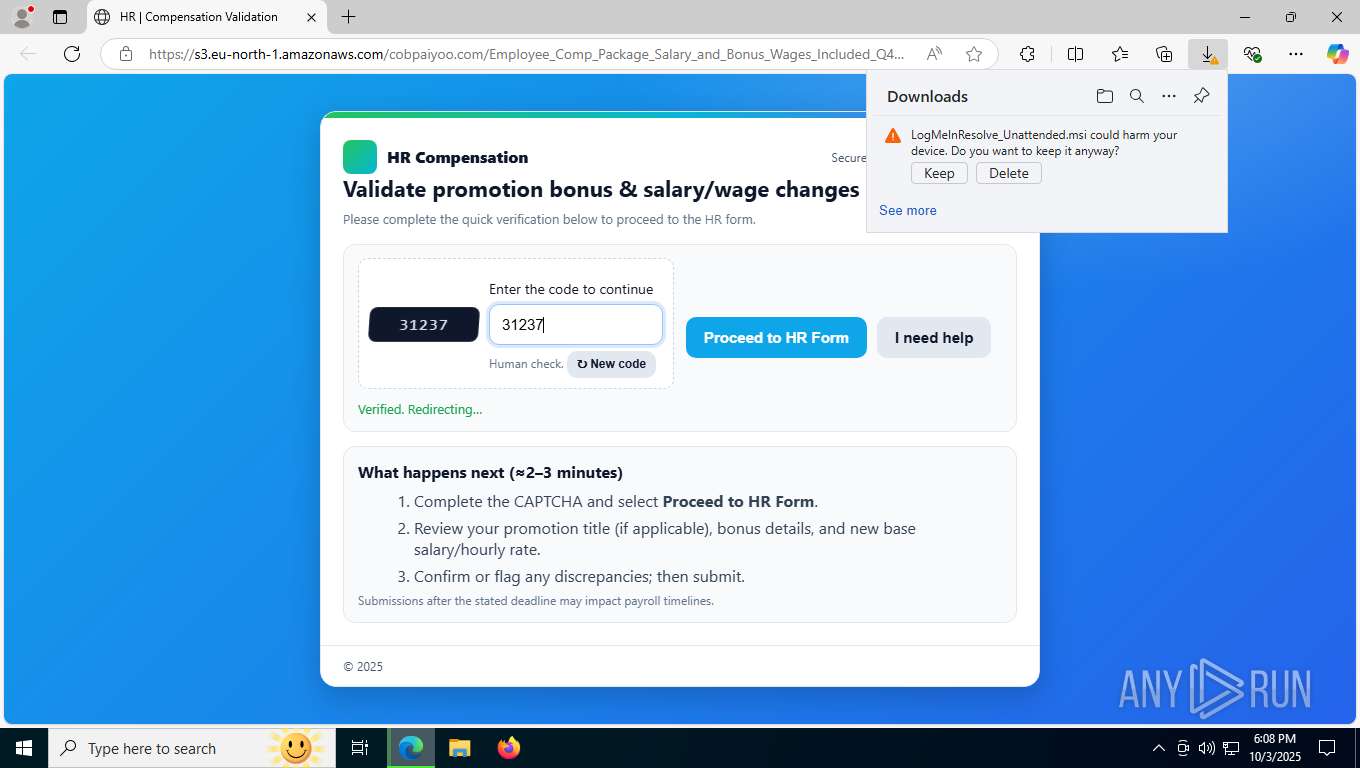
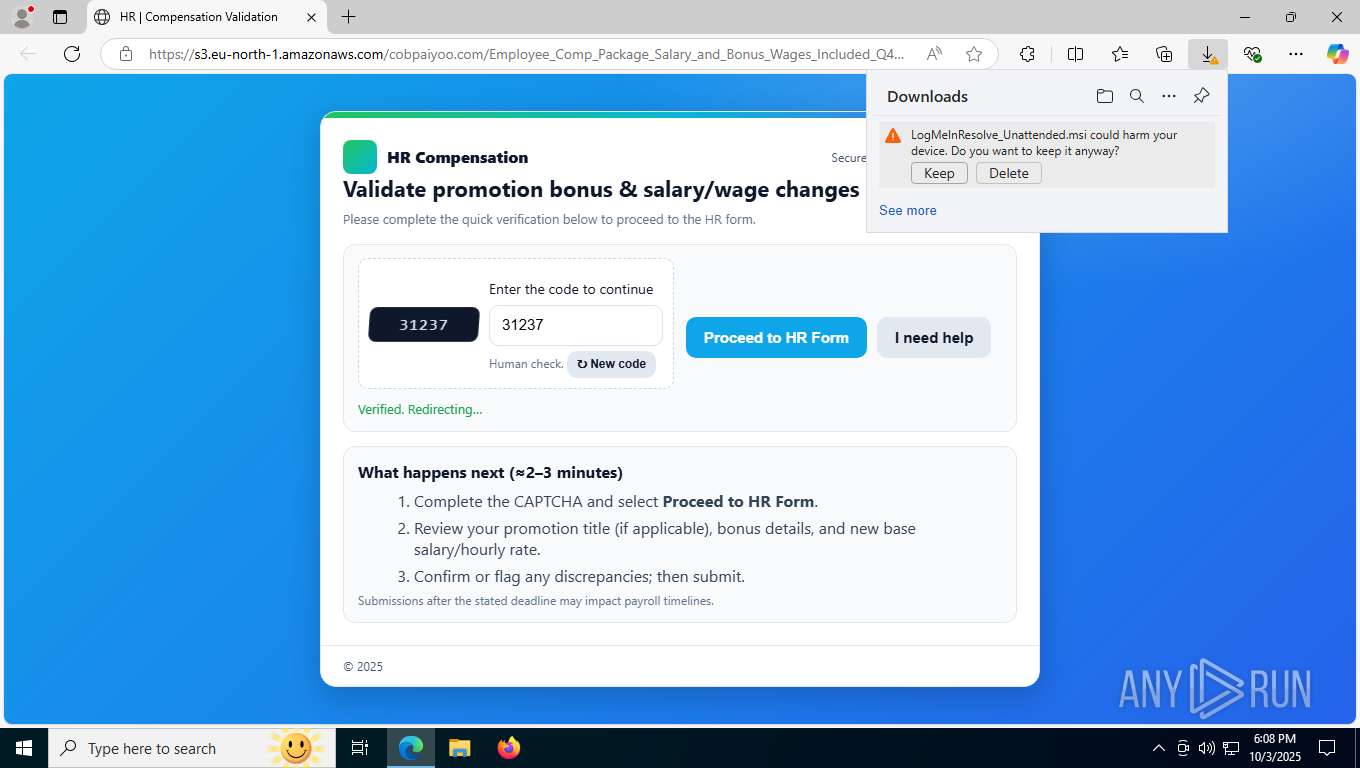
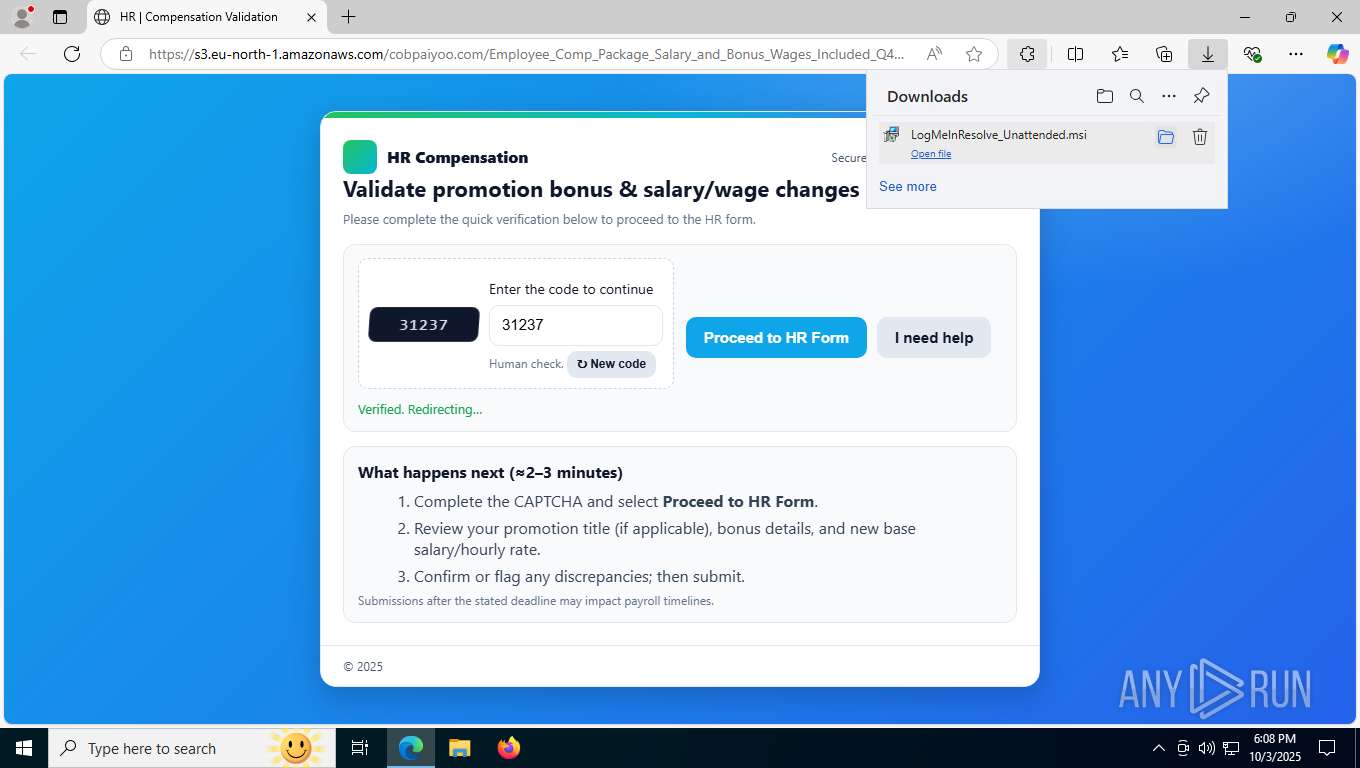
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
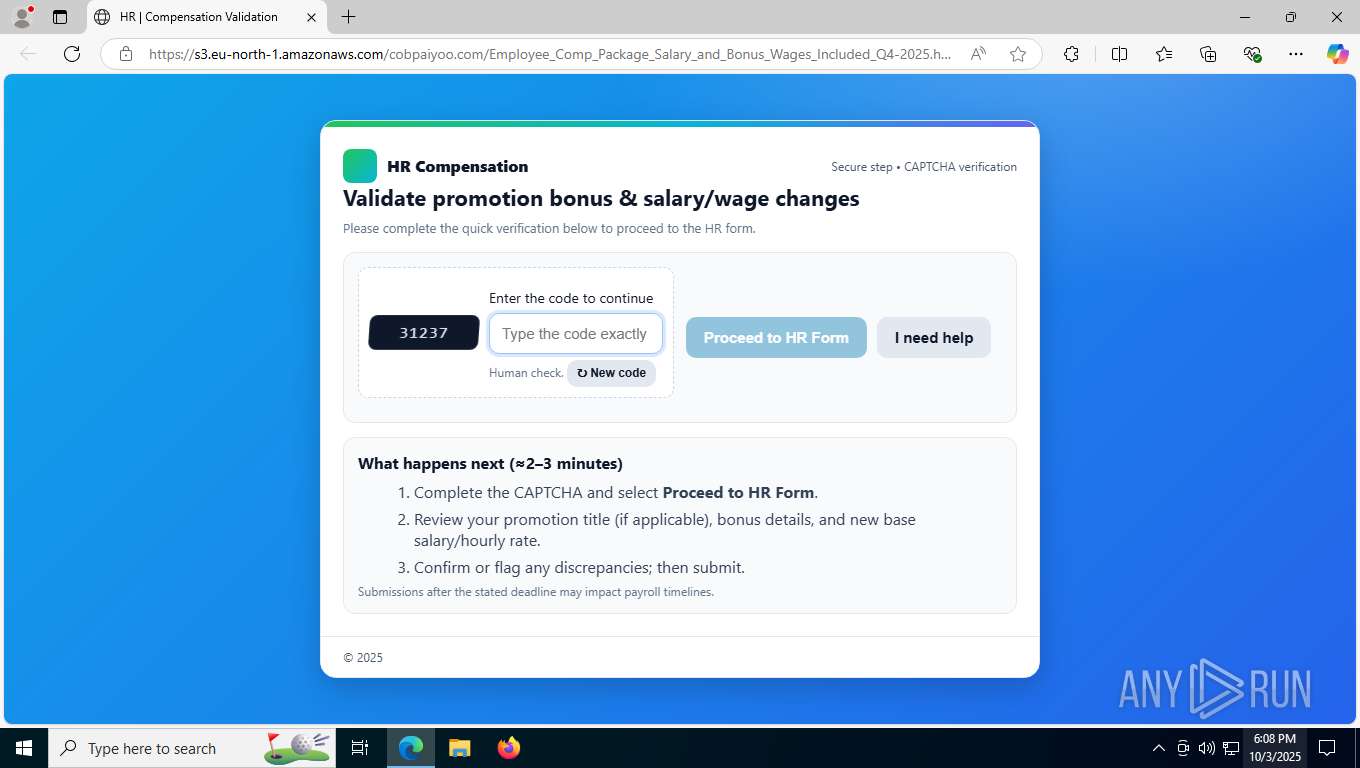
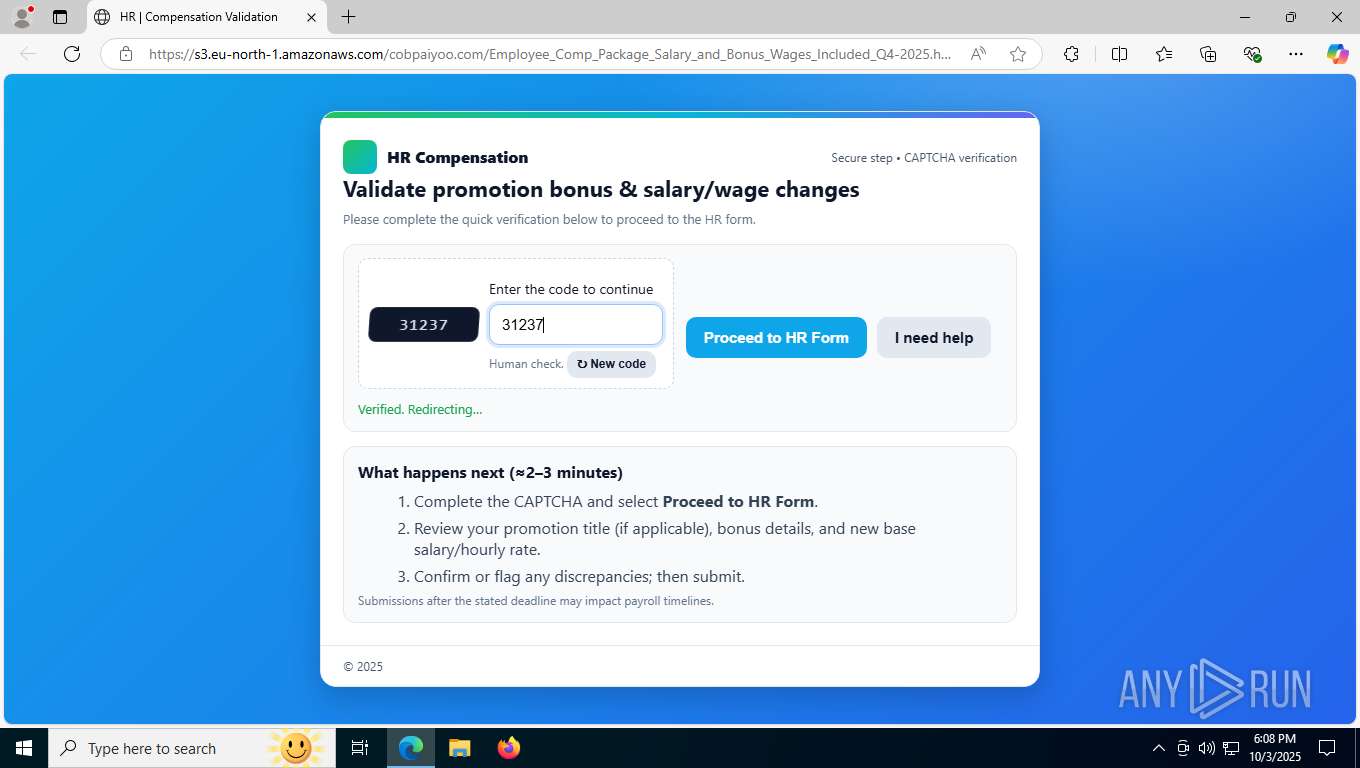
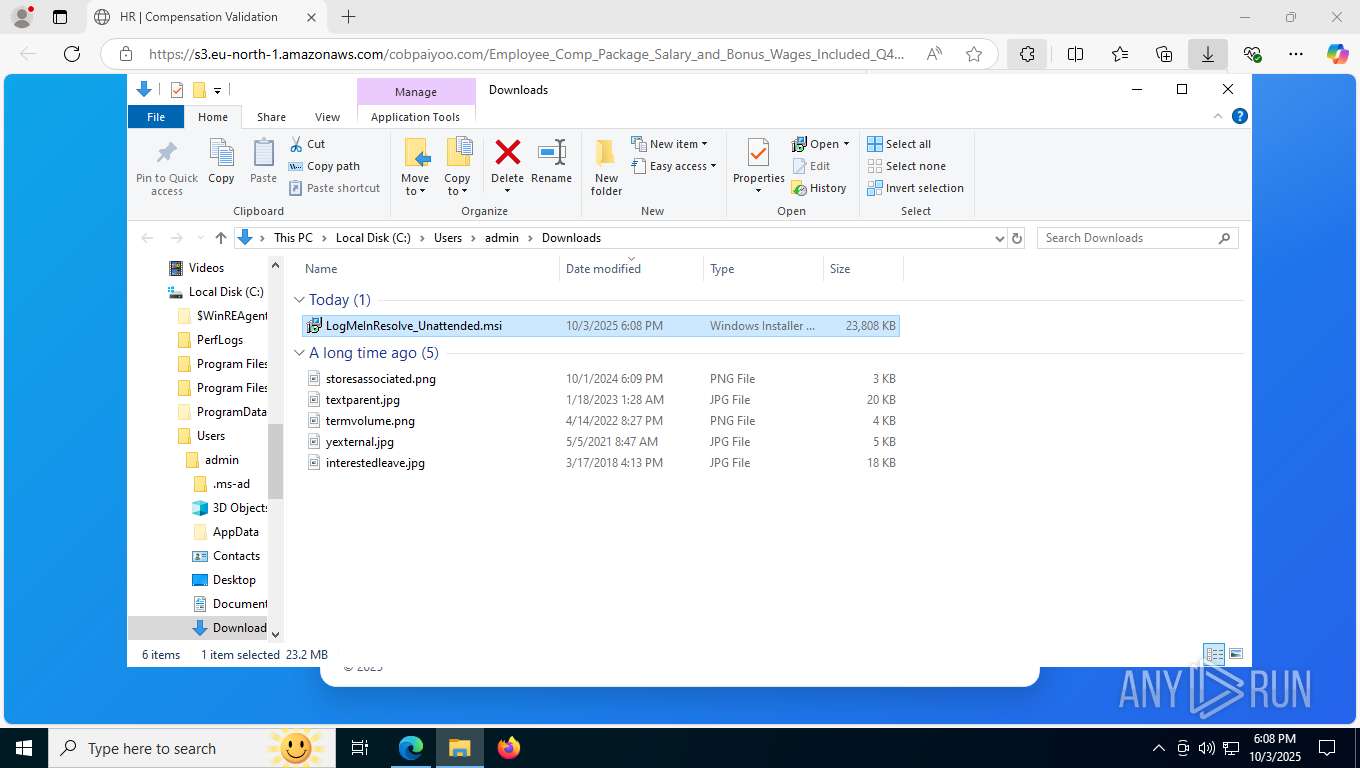
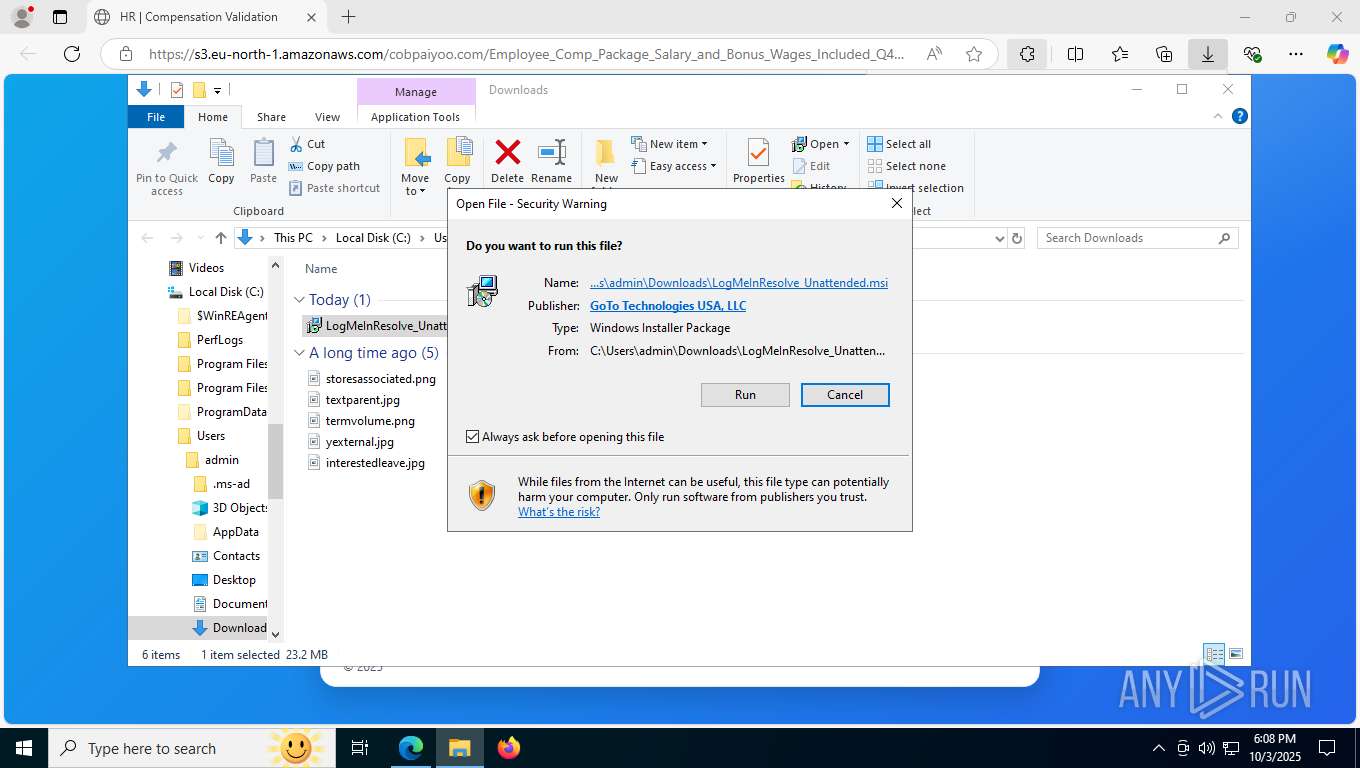
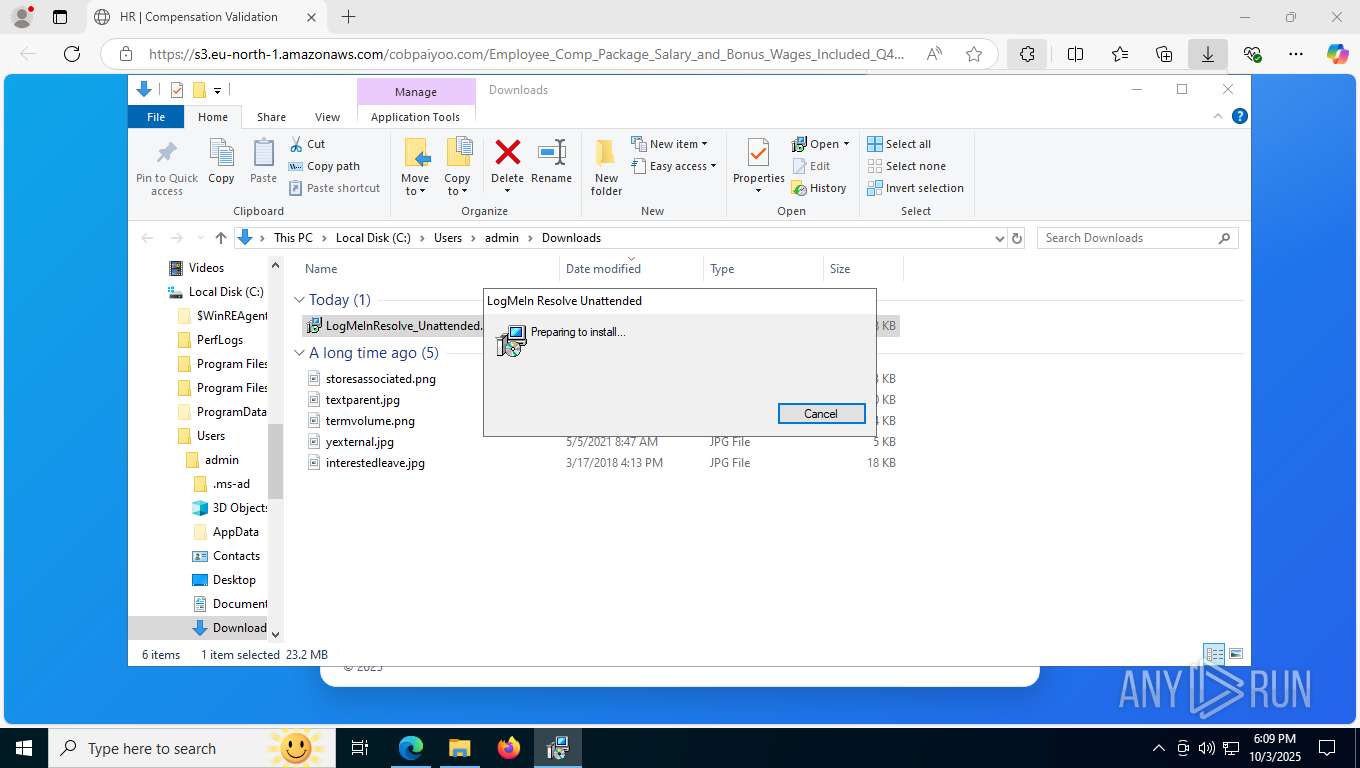
| URL: | https://s3.eu-north-1.amazonaws.com/cobpaiyoo.com/Employee_Comp_Package_Salary_and_Bonus_Wages_Included_Q4-2025.html |
| Full analysis: | https://app.any.run/tasks/c407f8a8-999a-40c6-a5a3-32aa92822673 |
| Verdict: | Malicious activity |
| Analysis date: | October 03, 2025, 18:07:55 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MD5: | 99B9F4A9B4A7BD27A0D757F306473AA0 |
| SHA1: | D41ED2166150382436F10F4057F09DD553F9E1C7 |
| SHA256: | C3F41E050D405216AD145B948A534C517E0614C3B42104CED6A4B25A1ADECC14 |
| SSDEEP: | 3:N8qI2Q7WtGKHARyK3pKt1BCegHMKsshVti0:2z2QtcARyDt10tHM0VE0 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 8 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=quarantine.mojom.Quarantine --lang=en-US --service-sandbox-type=none --disable-quic --string-annotations --always-read-main-dll --field-trial-handle=4396,i,8185389340003056799,4831351900110130767,262144 --variations-seed-version --mojo-platform-channel-handle=6504 /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Edge Exit code: 0 Version: 133.0.3065.92 Modules
| |||||||||||||||
| 1136 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=network.mojom.NetworkService --lang=en-US --service-sandbox-type=none --disable-quic --string-annotations --always-read-main-dll --field-trial-handle=2112,i,8185389340003056799,4831351900110130767,262144 --variations-seed-version --mojo-platform-channel-handle=1144 /prefetch:3 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | msedge.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Edge Version: 133.0.3065.92 Modules
| |||||||||||||||
| 1340 | "C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\GoToResolveProcessChecker.exe" -Service -WorkFolder "C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065" -ApplicationType "4" | C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\GoToResolveProcessChecker.exe | services.exe | ||||||||||||
User: SYSTEM Company: GoTo, Inc. Integrity Level: SYSTEM Description: LogMeIn Resolve Version: 1.27.1.2836 Modules
| |||||||||||||||
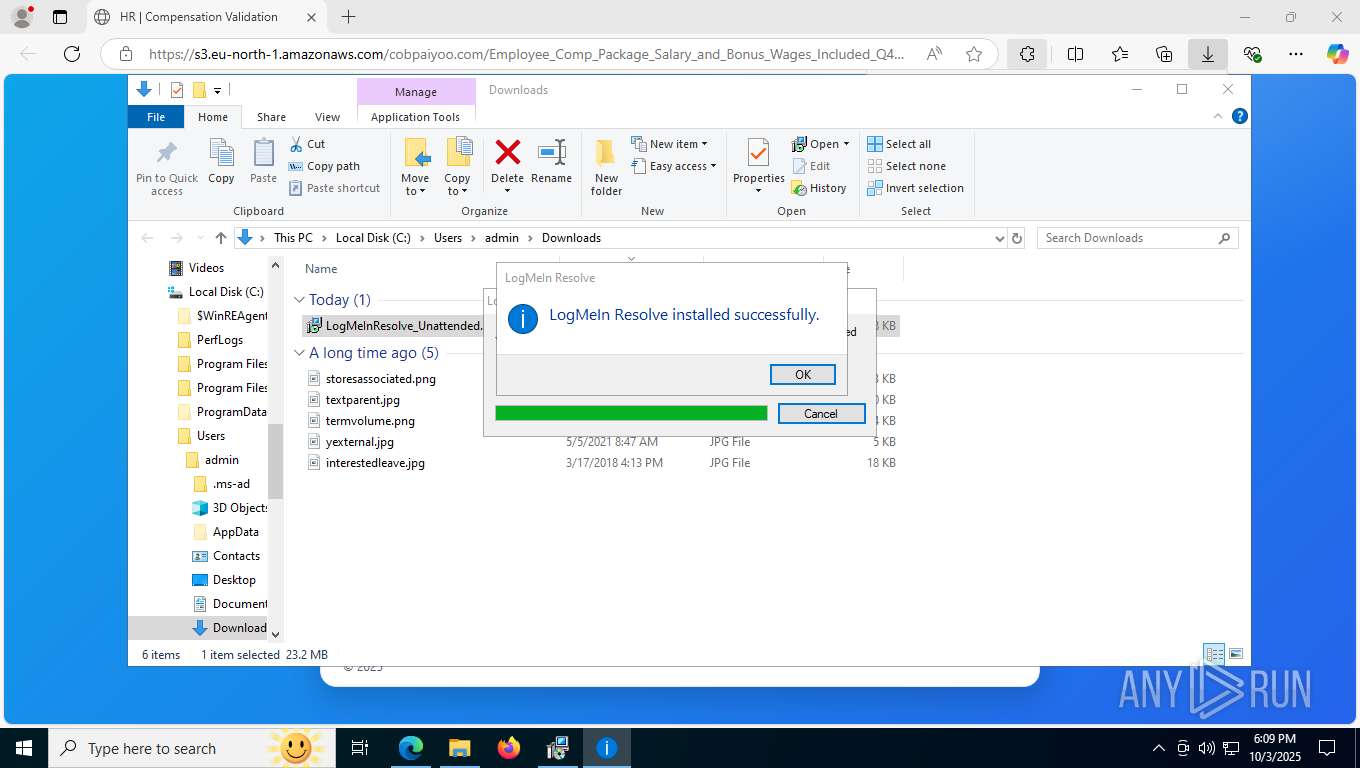
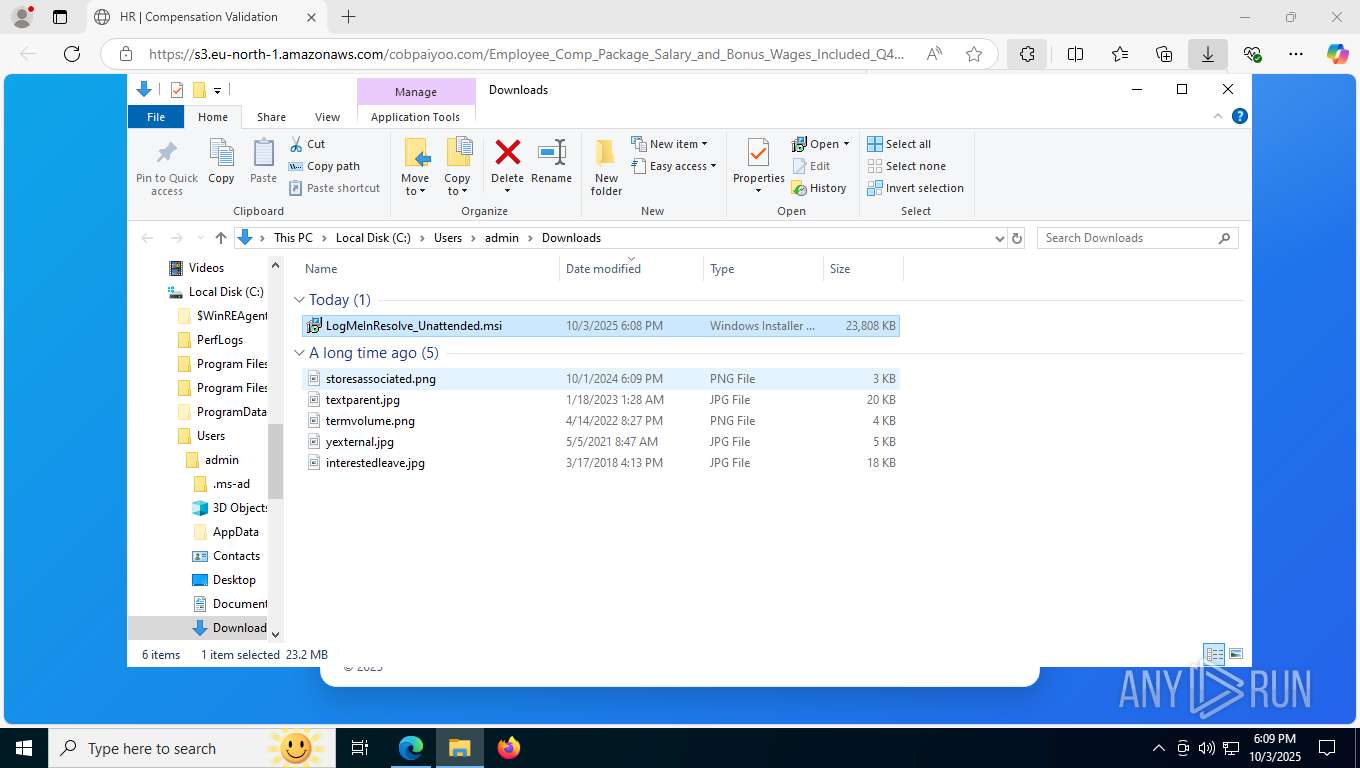
| 2144 | "C:\Program Files (x86)\GoTo Resolve Unattended\unattended-updater.exe" -regsvc "-MsiInstallerPath" "C:\Users\admin\Downloads\LogMeInResolve_Unattended.msi" "-MsiInstanceGuid" "{E24F358C-152A-41E5-BD34-D9FDB7E29FF0}" "-MsiUiLevel" "5" | C:\Program Files (x86)\GoTo Resolve Unattended\unattended-updater.exe | msiexec.exe | ||||||||||||
User: admin Company: GoTo, Inc. Integrity Level: MEDIUM Description: LogMeIn Resolve Exit code: 0 Version: 1.27.1.2836 Modules
| |||||||||||||||
| 2184 | GoToResolveLoggerProcess.exe -ParentProcessId 3984 -CompanyId 6411612292273186065 -InstallationId jFZLcTTDNG -WorkFolder "C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065" -Environment Production -ApplicationType 4 -HostId 17002f6769a4dfedec7290f3e97ff877 -LogLevel 2 -SessionType Unattended | C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\GoToResolveLoggerProcess.exe | GoToResolveUnattended.exe | ||||||||||||
User: SYSTEM Company: GoTo, Inc. Integrity Level: SYSTEM Description: LogMeIn Resolve Version: 1.27.1.2836 Modules
| |||||||||||||||
| 2188 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=chrome.mojom.UtilWin --lang=en-US --service-sandbox-type=none --disable-quic --message-loop-type-ui --string-annotations --always-read-main-dll --field-trial-handle=7016,i,8185389340003056799,4831351900110130767,262144 --variations-seed-version --mojo-platform-channel-handle=7108 /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Edge Exit code: 0 Version: 133.0.3065.92 Modules
| |||||||||||||||
| 2284 | cmd.exe /S /C ""C:\Program Files (x86)\GoTo Resolve Unattended\unattended-updater.exe.cmd" "C:\Program Files (x86)\GoTo Resolve Unattended\unattended-updater.exe"" | C:\Windows\SysWOW64\cmd.exe | unattended-updater.exe | ||||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Windows Command Processor Exit code: 1 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2488 | "C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\GoToResolveUnattended.exe" -regsvc -regsvc "-MsiInstallerPath" "C:\Users\admin\Downloads\LogMeInResolve_Unattended.msi" "-MsiInstanceGuid" "{E24F358C-152A-41E5-BD34-D9FDB7E29FF0}" "-MsiUiLevel" "5" | C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\GoToResolveUnattended.exe | unattended-updater.exe | ||||||||||||
User: SYSTEM Company: GoTo, Inc. Integrity Level: SYSTEM Description: LogMeIn Resolve Exit code: 0 Version: 1.27.1.2836 Modules
| |||||||||||||||
| 2532 | "C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\GoToResolveCrashHandler.exe" "--database=C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\appdata\ProcessCheckerCrashReportDB" "--metrics-dir=C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\appdata\ProcessCheckerCrashReportDB" --url=https://dumpster.console.gotoresolve.com/api/dump --annotation=format=minidump --annotation=hostname=DESKTOP-JGLLJLD --annotation=installationid=jFZLcTTDNG --annotation=version=1.27.1.2836 --initial-client-data=0x7d4,0x7e0,0x7e4,0x5d0,0x7e8,0x70b06fac,0x70b06fbc,0x70b06fcc | C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\GoToResolveCrashHandler.exe | — | GoToResolveProcessChecker.exe | |||||||||||
User: SYSTEM Integrity Level: SYSTEM Modules
| |||||||||||||||
| 2980 | "C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\GoToResolveCrashHandler.exe" "--attachment=attachment_GoToResolveUnattended.log=C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\appdata\GoToResolveUnattended.log" "--attachment=attachment_unattended.json=C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\unattended.json" "--database=C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\appdata\UnattendedCrashReportDB" "--metrics-dir=C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\appdata\UnattendedCrashReportDB" --url=https://dumpster.console.gotoresolve.com/api/dump --annotation=format=minidump --annotation=hostname=DESKTOP-JGLLJLD --annotation=installationid=jFZLcTTDNG --annotation=version=1.27.1.2836 --initial-client-data=0x794,0x798,0x79c,0x548,0x7a0,0x70b06fac,0x70b06fbc,0x70b06fcc | C:\Program Files (x86)\GoTo Resolve Unattended\6411612292273186065\GoToResolveCrashHandler.exe | — | GoToResolveUnattended.exe | |||||||||||
User: SYSTEM Integrity Level: SYSTEM Modules
| |||||||||||||||
| (PID) Process: | (5156) explorer.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\SessionInfo\1\ApplicationViewManagement\W32:000000000004024C |
| Operation: | write | Name: | VirtualDesktop |
Value: 100000003030445694ACE2E2F1AF094C9D246B54025DD75A | |||
| (PID) Process: | (8084) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | failed_count |
Value: 0 | |||
| (PID) Process: | (8084) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | state |
Value: 2 | |||
| (PID) Process: | (8084) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\ThirdParty |
| Operation: | write | Name: | StatusCodes |
Value: | |||
| (PID) Process: | (8084) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\ThirdParty |
| Operation: | write | Name: | StatusCodes |
Value: 01000000 | |||
| (PID) Process: | (8084) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | state |
Value: 1 | |||
| (PID) Process: | (8084) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\EdgeUpdate\ClientState\{56EB18F8-B008-4CBD-B6D2-8C97FE7E9062} |
| Operation: | write | Name: | dr |
Value: 1 | |||
| (PID) Process: | (8084) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\StabilityMetrics |
| Operation: | write | Name: | user_experience_metrics.stability.exited_cleanly |
Value: 0 | |||
| (PID) Process: | (8084) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge |
| Operation: | write | Name: | UsageStatsInSample |
Value: 1 | |||
| (PID) Process: | (8084) msedge.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\EdgeUpdate\ClientStateMedium\{56EB18F8-B008-4CBD-B6D2-8C97FE7E9062} |
| Operation: | write | Name: | usagestats |
Value: 0 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 8084 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\ClientCertificates\LOG.old~RF171155.TMP | — | |
MD5:— | SHA256:— | |||
| 8084 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\ClientCertificates\LOG.old | — | |
MD5:— | SHA256:— | |||
| 8084 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\discounts_db\LOG.old~RF171165.TMP | — | |
MD5:— | SHA256:— | |||
| 8084 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\LOG.old~RF171165.TMP | — | |
MD5:— | SHA256:— | |||
| 8084 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\discounts_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 8084 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\LOG.old | — | |
MD5:— | SHA256:— | |||
| 8084 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\PersistentOriginTrials\LOG.old~RF171165.TMP | — | |
MD5:— | SHA256:— | |||
| 8084 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\PersistentOriginTrials\LOG.old | — | |
MD5:— | SHA256:— | |||
| 8084 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\parcel_tracking_db\LOG.old~RF171155.TMP | — | |
MD5:— | SHA256:— | |||
| 8084 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\parcel_tracking_db\LOG.old | — | |
MD5:— | SHA256:— | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
1136 | msedge.exe | GET | 200 | 150.171.27.11:80 | http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:AiIinfeaZ-fx7doQiOf4iPLa7xDVhkkhU8Xd0WbLhkE&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855 | US | text | 100 b | whitelisted |
2876 | svchost.exe | GET | 200 | 2.23.77.188:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | DE | binary | 471 b | whitelisted |
2876 | svchost.exe | GET | 200 | 2.23.77.188:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | DE | binary | 471 b | whitelisted |
9076 | backgroundTaskHost.exe | GET | 200 | 2.23.77.188:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | DE | binary | 313 b | whitelisted |
9100 | backgroundTaskHost.exe | GET | 200 | 2.23.77.188:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | DE | binary | 471 b | whitelisted |
9180 | backgroundTaskHost.exe | GET | 200 | 2.23.77.188:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | DE | binary | 471 b | whitelisted |
8896 | BackgroundTransferHost.exe | GET | 200 | 2.23.77.188:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | DE | binary | 313 b | whitelisted |
5156 | explorer.exe | GET | 200 | 23.54.109.203:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBT3xL4LQLXDRDM9P665TW442vrsUQQUReuir%2FSSy4IxLVGLp6chnfNtyA8CEA6bGI750C3n79tQ4ghAGFo%3D | DE | binary | 471 b | whitelisted |
5156 | explorer.exe | GET | 200 | 23.54.109.203:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTfIs%2BLjDtGwQ09XEB1Yeq%2BtX%2BBgQQU7NfjgtJxXWRM3y5nP%2Be6mK4cD08CEAitQLJg0pxMn17Nqb2Trtk%3D | DE | binary | 727 b | whitelisted |
5156 | explorer.exe | GET | 200 | 23.54.109.203:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSRXerF0eFeSWRripTgTkcJWMm7iQQUaDfg67Y7%2BF8Rhvv%2BYXsIiGX0TkICEA4Mh2e7LU%2FvwtYX3xHOG4k%3D | DE | binary | 727 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4416 | RUXIMICS.exe | 20.73.194.208:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
6016 | MoUsoCoreWorker.exe | 20.73.194.208:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
1136 | msedge.exe | 150.171.27.11:80 | edge.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
1136 | msedge.exe | 150.171.22.17:443 | config.edge.skype.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
1136 | msedge.exe | 3.5.216.66:443 | s3.eu-north-1.amazonaws.com | AMAZON-02 | SE | shared |
1136 | msedge.exe | 150.171.28.11:443 | edge.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
1136 | msedge.exe | 23.192.36.141:443 | copilot.microsoft.com | AKAMAI-AS | US | whitelisted |
1136 | msedge.exe | 23.192.36.137:443 | www.bing.com | AKAMAI-AS | US | whitelisted |
1136 | msedge.exe | 150.171.27.11:443 | edge.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
edge.microsoft.com |
| whitelisted |
config.edge.skype.com |
| whitelisted |
s3.eu-north-1.amazonaws.com |
| shared |
copilot.microsoft.com |
| whitelisted |
www.bing.com |
| whitelisted |
xpaywalletcdn.azureedge.net |
| whitelisted |
update.googleapis.com |
| whitelisted |
clients2.googleusercontent.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
— | — | Potentially Bad Traffic | ET INFO Possible Chrome Plugin install |
— | — | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |
2428 | svchost.exe | Misc activity | ET INFO Observed DNS Query to RMM Domain (gotoresolve .com) |
2184 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
2184 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
2184 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
2184 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
2184 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
2184 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
2428 | svchost.exe | Misc activity | ET INFO Observed DNS Query to RMM Domain (gotoresolve .com) |
Process | Message |
|---|---|
GoToResolveUnattended.exe | DllMain: DLL_PROCESS_ATTACH: lpReserved=0
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_ATTACH
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_ATTACH
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_ATTACH
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_ATTACH
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_ATTACH
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_DETACH
|
GoToResolveProcessChecker.exe | DllMain: DLL_PROCESS_ATTACH: lpReserved=0
|
GoToResolveProcessChecker.exe | DllMain: DLL_PROCESS_ATTACH: lpReserved=0
|
GoToResolveProcessChecker.exe | DllMain: DLL_THREAD_ATTACH
|