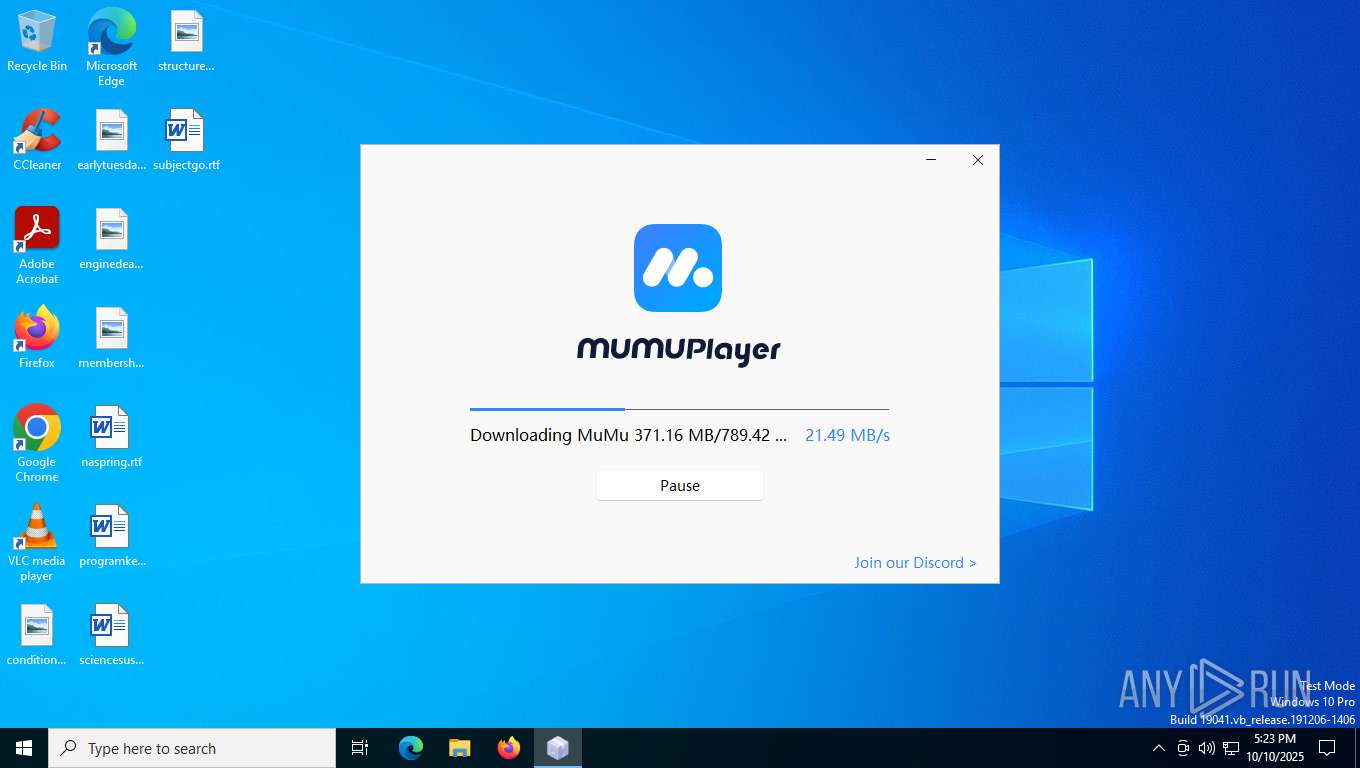
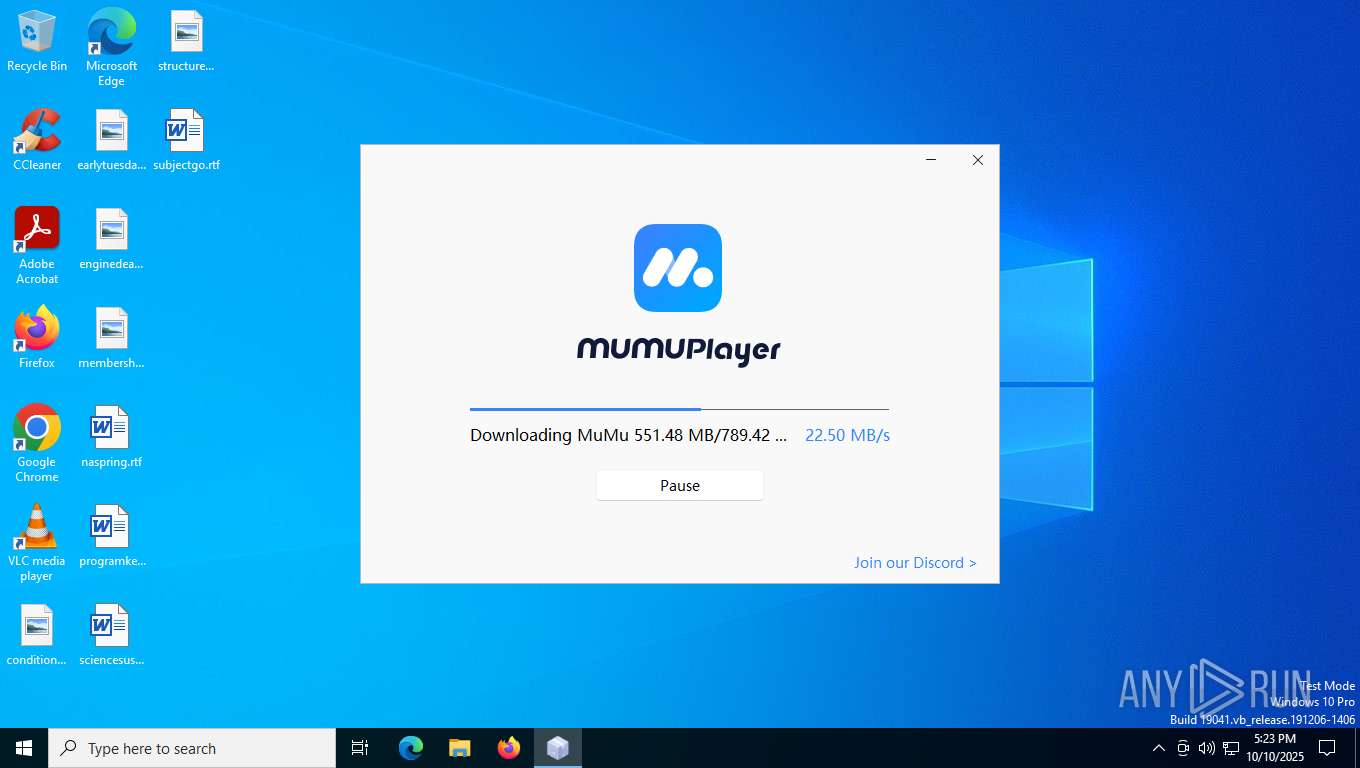
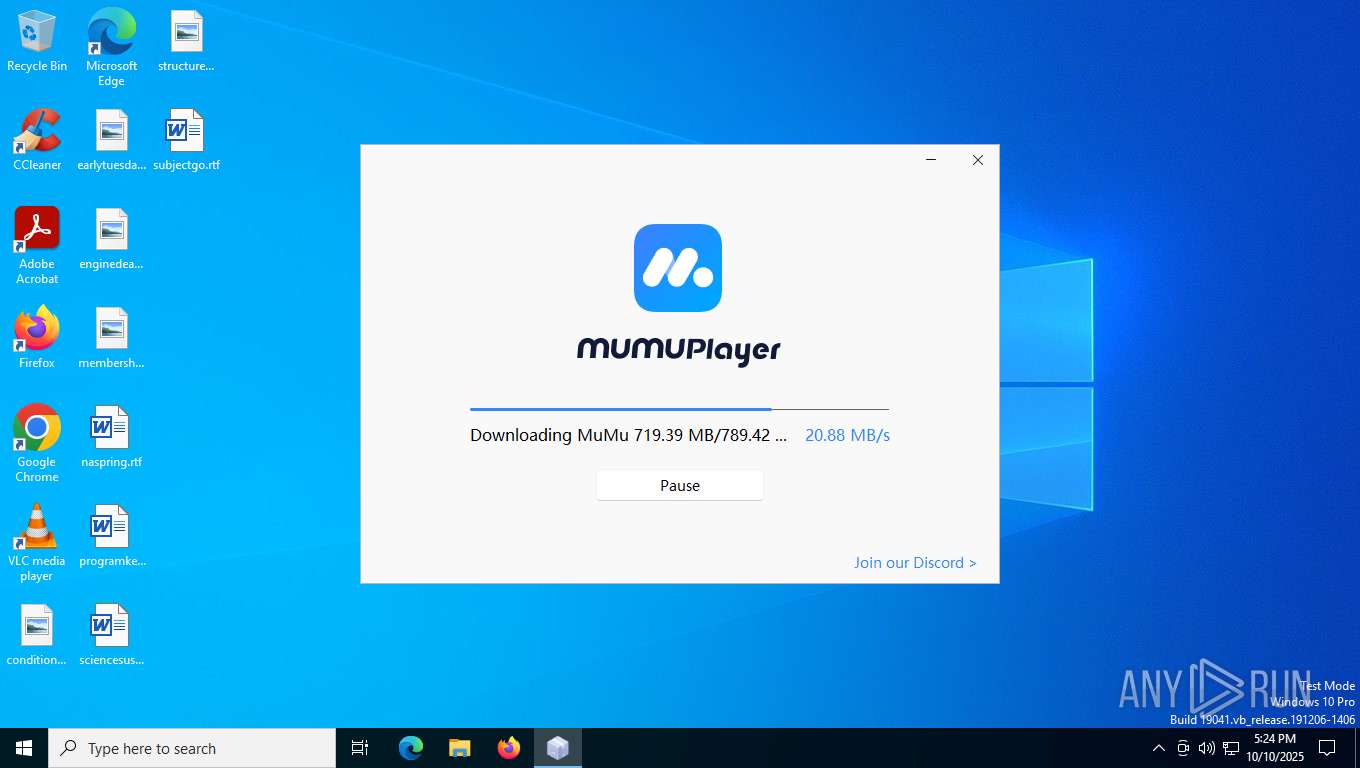
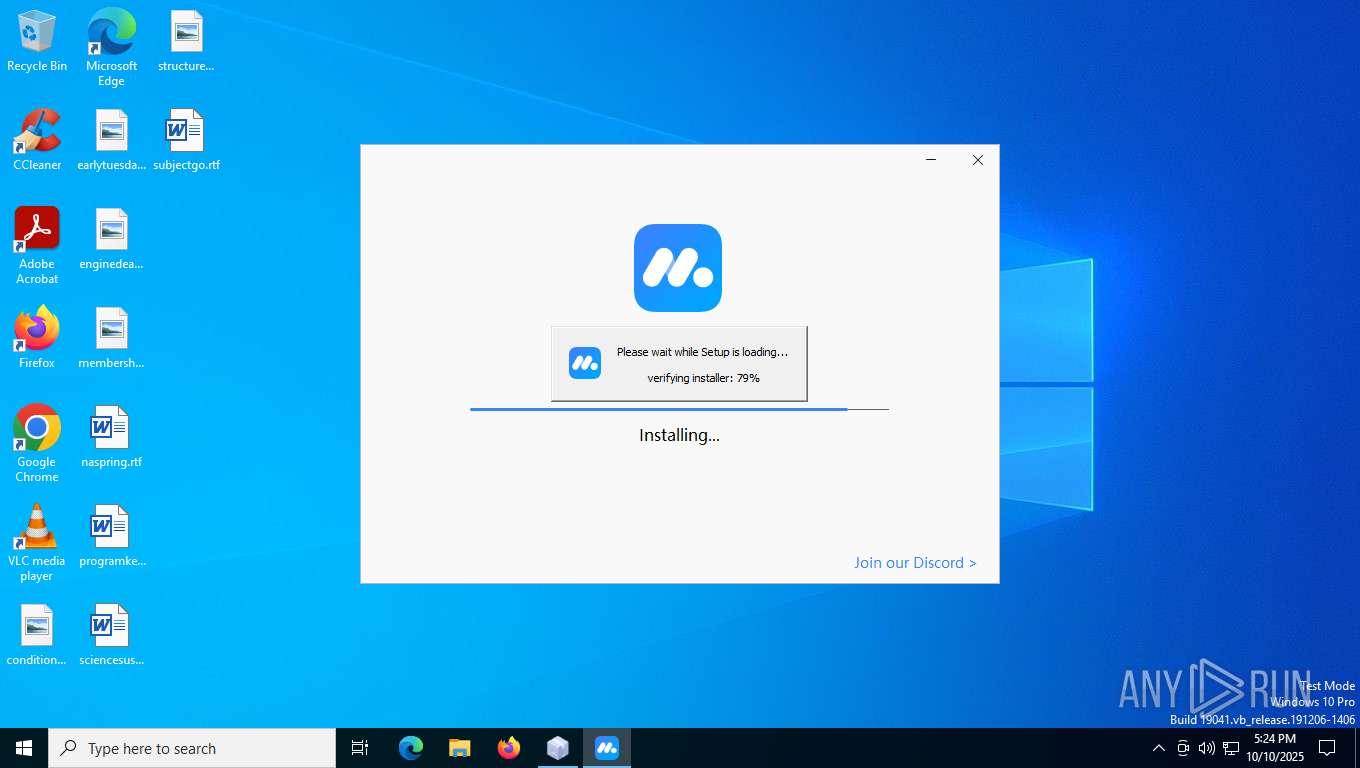
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
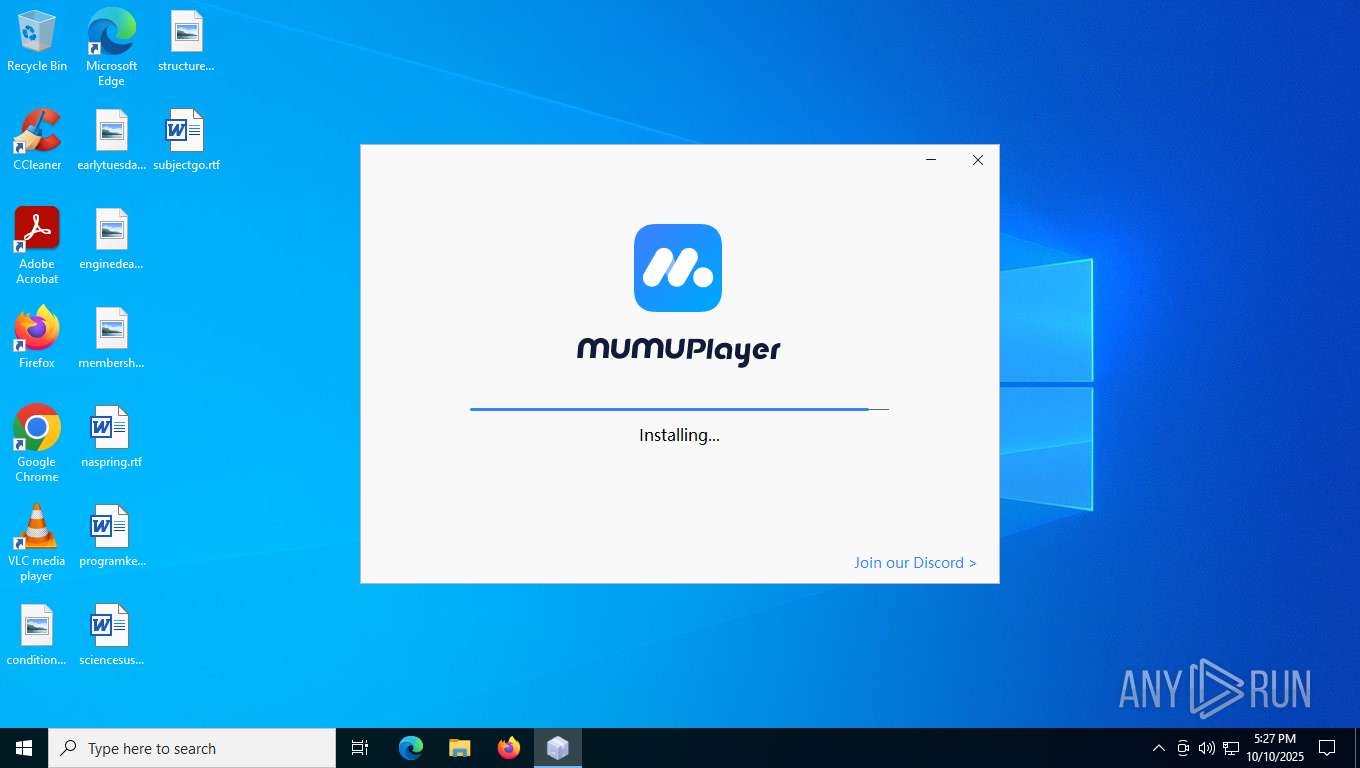
| File name: | MuMu_5.0.4_qH5tMMC.exe |
| Full analysis: | https://app.any.run/tasks/e37eedab-5c38-49bd-97fa-167c5c380db6 |
| Verdict: | Malicious activity |
| Analysis date: | October 10, 2025, 17:23:04 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, 4 sections |
| MD5: | 8CFB4AD5982EC59B03F9890995FDC07F |
| SHA1: | 6F2F02B099947D391353DC732C268D2CCB8BED5D |
| SHA256: | C19227AA1051686596164EEFC103CEF60E6F8F904929B096DE4F1FA825BD4119 |
| SSDEEP: | 98304:CrUBkVCAd+I7SCLAx24A/nKbXoyF+MPD12Bh/frTw7vaVUMHq79e0Sfe2ceem0XW:UMof/53PLUFQ |
| .exe | | | Win32 Executable MS Visual C++ (generic) (42.2) |
|---|---|---|
| .exe | | | Win64 Executable (generic) (37.3) |
| .dll | | | Win32 Dynamic Link Library (generic) (8.8) |
| .exe | | | Win32 Executable (generic) (6) |
| .exe | | | Generic Win/DOS Executable (2.7) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2022:06:15 13:00:00+00:00 |
| ImageFileCharacteristics: | No relocs, Executable, No line numbers, No symbols, Large address aware, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 6 |
| CodeSize: | 28672 |
| InitializedDataSize: | 197632 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x7c84 |
| OSVersion: | 4 |
| ImageVersion: | - |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 22.0.0.0 |
| ProductVersionNumber: | 22.0.0.0 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Windows NT 32-bit |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | English (U.S.) |
| CharacterSet: | Unicode |
| CompanyName: | NetEase, Inc. |
| FileDescription: | MuMuPlayer |
| FileVersion: | 2022 |
| InternalName: | 7zS2.sfx |
| LegalCopyright: | Copyright (C) 2022 |
| OriginalFileName: | NemuDownloader.exe |
| ProductName: | MuMuPlayer |
| ProductVersion: | 1.0.0.0 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 572 | "C:\Program Files\MuMuVMMVbox\LoadedDrivers\SUPUninstall.exe" | C:\Program Files\MuMuVMMVbox\LoadedDrivers\SUPUninstall.exe | — | MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | |||||||||||
User: admin Integrity Level: HIGH Exit code: 0 Modules
| |||||||||||||||
| 1136 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | HyperVChecker.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1408 | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\nemu-downloader.exe | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\nemu-downloader.exe | MuMu_5.0.4_qH5tMMC.exe | ||||||||||||
User: admin Company: NetEase, Inc. Integrity Level: HIGH Description: MuMu Player Installer Version: 1.3.0.1 Modules
| |||||||||||||||
| 1472 | /s "C:\Program Files\MuMuVMMVbox\Hypervisor\MuMuVMMProxyStub.dll" | C:\Windows\System32\regsvr32.exe | — | regsvr32.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Microsoft(C) Register Server Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1516 | "C:\WINDOWS\system32\sc.exe" query MuMuVMMDrv | C:\Windows\SysWOW64\sc.exe | — | MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Service Control Manager Configuration Tool Exit code: 1060 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1536 | "C:\WINDOWS\system32\sc.exe" query MuMuVMMDrv | C:\Windows\SysWOW64\sc.exe | — | MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Service Control Manager Configuration Tool Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2092 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | netsh.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2288 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | HyperVChecker.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2428 | C:\WINDOWS\system32\svchost.exe -k NetworkService -p -s Dnscache | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2480 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | SUPUninstall.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (1408) nemu-downloader.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\NemuServer |
| Operation: | write | Name: | uuid |
Value: 28ba278f-d3c5-4bcc-82cb-c2ac39d6cb15 | |||
| (PID) Process: | (1408) nemu-downloader.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\NemuServer |
| Operation: | write | Name: | channel |
Value: gw-win-download | |||
| (PID) Process: | (1408) nemu-downloader.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\NemuServer |
| Operation: | write | Name: | package |
Value: mumu | |||
| (PID) Process: | (8844) MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | Key: | HKEY_CLASSES_ROOT\CLSID\{00020424-0000-0000-C000-000000000046}\InprocServer32 |
| Operation: | write | Name: | InprocServer32 |
Value: C:\WINDOWS\system32\oleaut32.dll | |||
| (PID) Process: | (8844) MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | Key: | HKEY_CLASSES_ROOT\CLSID\{00020424-0000-0000-C000-000000000046}\InprocServer32 |
| Operation: | write | Name: | ThreadingModel |
Value: Both | |||
| (PID) Process: | (8844) MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | Key: | HKEY_CLASSES_ROOT\CLSID\{00020420-0000-0000-C000-000000000046}\InprocServer32 |
| Operation: | write | Name: | InprocServer32 |
Value: C:\WINDOWS\system32\oleaut32.dll | |||
| (PID) Process: | (8844) MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | Key: | HKEY_CLASSES_ROOT\CLSID\{00020420-0000-0000-C000-000000000046}\InprocServer32 |
| Operation: | write | Name: | ThreadingModel |
Value: Both | |||
| (PID) Process: | (8844) MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\SOFTWARE\Classes\CLSID\{00020424-0000-0000-C000-000000000046}\InprocServer32 |
| Operation: | write | Name: | InprocServer32 |
Value: C:\WINDOWS\system32\oleaut32.dll | |||
| (PID) Process: | (8844) MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\SOFTWARE\Classes\CLSID\{00020424-0000-0000-C000-000000000046}\InprocServer32 |
| Operation: | write | Name: | ThreadingModel |
Value: Both | |||
| (PID) Process: | (8844) MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{00020424-0000-0000-C000-000000000046}\InprocServer32 |
| Operation: | write | Name: | InprocServer32 |
Value: C:\WINDOWS\system32\oleaut32.dll | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 8180 | MuMu_5.0.4_qH5tMMC.exe | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\winring0.cat | binary | |
MD5:5691A9B76C5B0BD1DD83687F5F0E87A1 | SHA256:784E031565C67F1D29640C62F0CC205D5B56C1F78BE894252CCE06474B64A618 | |||
| 8180 | MuMu_5.0.4_qH5tMMC.exe | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\WinRing0.inf | binary | |
MD5:F069F20871CB316BFB73C276393D1648 | SHA256:07942017E8CAAA1065867AECC561577199E53142545CB6FB41239AE4C607D46B | |||
| 8180 | MuMu_5.0.4_qH5tMMC.exe | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\WinRing0x64.inf | binary | |
MD5:0F6D3047D1B670058D71C411707EF16E | SHA256:3FDED2F4457B0BEB415B841B40F6EDE5ED527DD537E53E2F70F2FB4A6E24EBFD | |||
| 8180 | MuMu_5.0.4_qH5tMMC.exe | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\MuMuDownloader.exe | executable | |
MD5:2F3D77B4F587F956E9987598B0A218EB | SHA256:2F980C56D81F42BA47DC871A04406976DC490DED522131CE9A2E35C40CA8616E | |||
| 8180 | MuMu_5.0.4_qH5tMMC.exe | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\winring0x64.cat | binary | |
MD5:E7CEE7F541C057F490D486927D659122 | SHA256:317D01D9956F052D929FDBAC258F1A2DC5163D3432FC488023A1F4D332AE3D45 | |||
| 8180 | MuMu_5.0.4_qH5tMMC.exe | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\config.ini | text | |
MD5:41AECA28306726D96716495730534729 | SHA256:9348FFEB2EE9DC21E5A763D0DB404D45C3F5F57B1F1B51DA7F2BBE552D5EBF2F | |||
| 8180 | MuMu_5.0.4_qH5tMMC.exe | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\msvcrt.dll | executable | |
MD5:0DAA0D9DC786F95C8DC2CCC0221B2863 | SHA256:279A03ACC810C1FE613BE283EB24762F0451DA9A6142ED3DC996A1D10FE2F692 | |||
| 8180 | MuMu_5.0.4_qH5tMMC.exe | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\nemu-downloader.exe | executable | |
MD5:AC3E5A845A25B3B89205A221320E15BE | SHA256:45E1DE48B8EF753E896E2B5E1AAA7E8A9CF35CA16E6E375A35C9A70E3ED70821 | |||
| 3600 | MuMuDownloader.exe | C:\Users\admin\AppData\Local\Temp\MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | — | |
MD5:— | SHA256:— | |||
| 8180 | MuMu_5.0.4_qH5tMMC.exe | C:\Users\admin\AppData\Local\Temp\7z6CE29FF4\WinRing0x64.sys | executable | |
MD5:1C57D067B9FC5E9EF9AEB14223481243 | SHA256:D5BCA2CA464A6CC91344BD85E812A7BAC6E7C67038C4929A29E0BC60C7EABE4D | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
1408 | nemu-downloader.exe | GET | 200 | 76.223.88.1:80 | http://76.223.88.1/v2/?domain=a11.gdl.easebar.com | US | binary | 80 b | unknown |
3600 | MuMuDownloader.exe | GET | — | 2.16.10.181:80 | http://2.16.10.181:80/MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | AT | — | — | whitelisted |
3600 | MuMuDownloader.exe | GET | — | 2.16.10.181:80 | http://2.16.10.181:80/MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | AT | — | — | whitelisted |
3600 | MuMuDownloader.exe | GET | — | 2.16.10.181:80 | http://2.16.10.181:80/MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | AT | — | — | whitelisted |
5940 | svchost.exe | GET | 200 | 23.63.118.230:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | DE | binary | 471 b | whitelisted |
5368 | backgroundTaskHost.exe | GET | 200 | 23.63.118.230:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | DE | binary | 471 b | whitelisted |
572 | backgroundTaskHost.exe | GET | 200 | 23.63.118.230:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | DE | binary | 471 b | whitelisted |
3600 | MuMuDownloader.exe | GET | — | 2.16.10.181:80 | http://2.16.10.181:80/MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | AT | — | — | whitelisted |
592 | backgroundTaskHost.exe | GET | 200 | 23.63.118.230:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | DE | binary | 313 b | whitelisted |
3600 | MuMuDownloader.exe | GET | — | 2.16.10.181:80 | http://2.16.10.181:80/MuMu-setup-V5.7.1.1860-overseas-0928154451.exe | AT | — | — | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
6016 | MoUsoCoreWorker.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
8008 | RUXIMICS.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
1408 | nemu-downloader.exe | 34.36.47.246:443 | api.mumuglobal.com | GOOGLE-CLOUD-PLATFORM | US | unknown |
1408 | nemu-downloader.exe | 104.86.151.7:443 | dns.update.easebar.com | AKAMAI-AS | DE | unknown |
1408 | nemu-downloader.exe | 76.223.88.1:80 | — | AMAZON-02 | US | unknown |
3600 | MuMuDownloader.exe | 2.16.10.181:80 | — | Akamai International B.V. | AT | whitelisted |
5224 | SearchApp.exe | 2.16.204.148:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
5224 | SearchApp.exe | 2.16.204.145:443 | th.bing.com | Akamai International B.V. | DE | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
api.mumuglobal.com |
| unknown |
dns.update.easebar.com |
| unknown |
www.bing.com |
| whitelisted |
th.bing.com |
| whitelisted |
a11.gdl.easebar.com |
| malicious |
login.live.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
3600 | MuMuDownloader.exe | A Network Trojan was detected | ET USER_AGENTS Aria2 User-Agent |
3600 | MuMuDownloader.exe | Potential Corporate Privacy Violation | ET INFO PE EXE or DLL Windows file download HTTP |
3600 | MuMuDownloader.exe | A Network Trojan was detected | ET USER_AGENTS Aria2 User-Agent |
3600 | MuMuDownloader.exe | A Network Trojan was detected | ET USER_AGENTS Aria2 User-Agent |
3600 | MuMuDownloader.exe | A Network Trojan was detected | ET USER_AGENTS Aria2 User-Agent |
3600 | MuMuDownloader.exe | A Network Trojan was detected | ET USER_AGENTS Aria2 User-Agent |
3600 | MuMuDownloader.exe | A Network Trojan was detected | ET USER_AGENTS Aria2 User-Agent |
3600 | MuMuDownloader.exe | A Network Trojan was detected | ET USER_AGENTS Aria2 User-Agent |
3600 | MuMuDownloader.exe | A Network Trojan was detected | ET USER_AGENTS Aria2 User-Agent |
3600 | MuMuDownloader.exe | A Network Trojan was detected | ET USER_AGENTS Aria2 User-Agent |