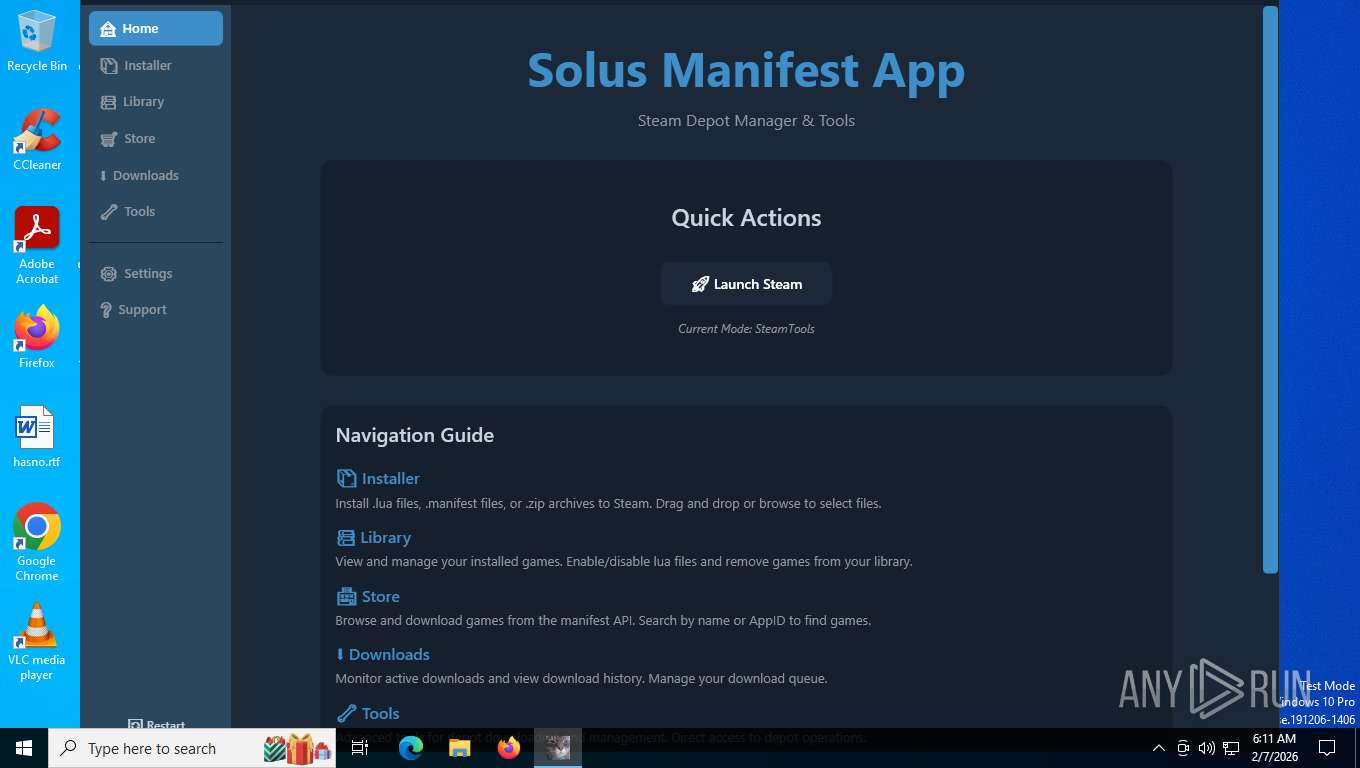
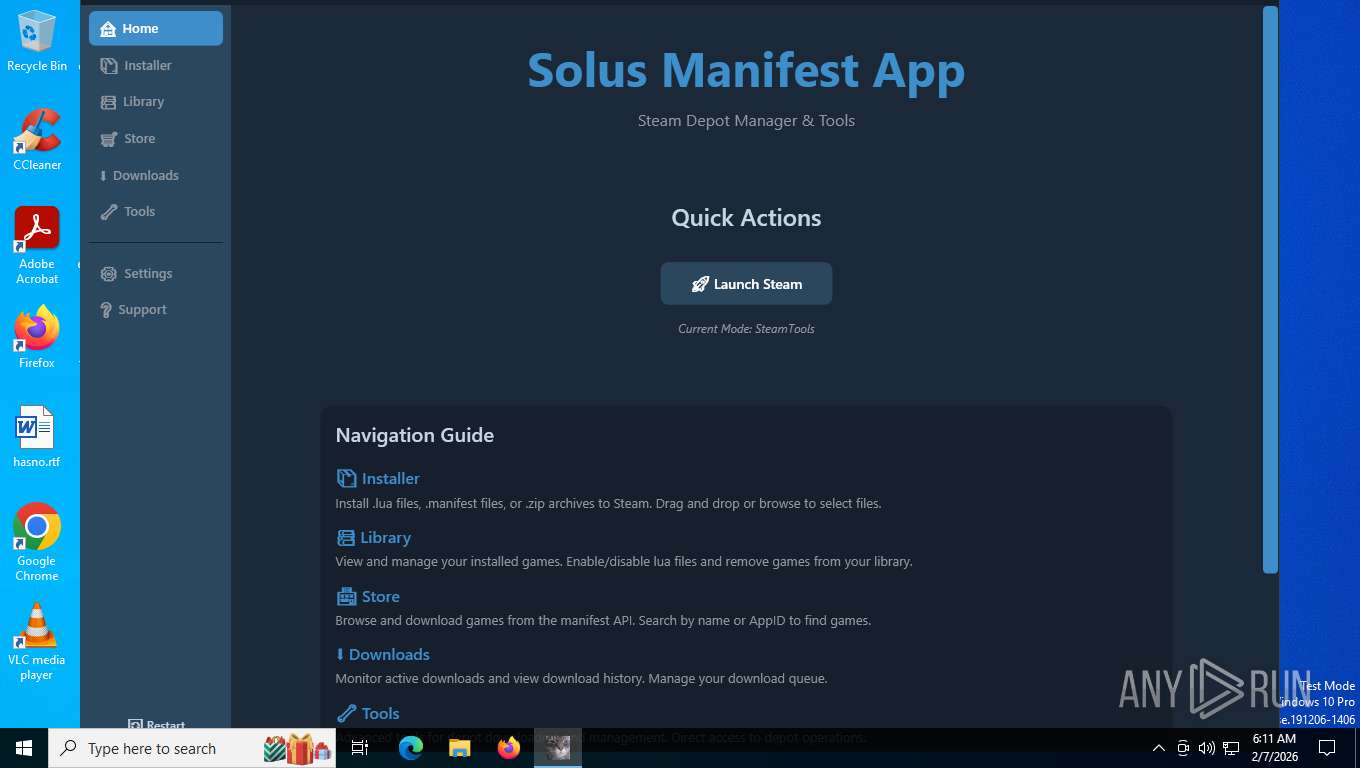
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | SolusManifestApp.exe |
| Full analysis: | https://app.any.run/tasks/db31a6d3-266f-4805-9e14-59b22f9b3f48 |
| Verdict: | Malicious activity |
| Analysis date: | February 07, 2026, 11:10:47 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32+ executable (GUI) x86-64, for MS Windows, 10 sections |
| MD5: | B9EFE50C550F4196AD83BBB93A8562E8 |
| SHA1: | 9F0306F0CF7102D3F413B16D72C7C431ABF8B1E7 |
| SHA256: | BC542BF51EC327CC34C0ADC450DFA01203F37E6FC5C15703E26941E5F8B5CB78 |
| SSDEEP: | 786432:mgVdkK0l34rICQ3RM/vLwwq+Xx4gA3eefOTuH/DlTJB:moSK0lIsCQ3RMM4XGgA3zGSH/hTJB |
| .exe | | | Generic Win/DOS Executable (50) |
|---|---|---|
| .exe | | | DOS Executable Generic (49.9) |
| MachineType: | AMD AMD64 |
|---|---|
| TimeStamp: | 2025:12:06 22:33:16+00:00 |
| ImageFileCharacteristics: | Executable, Large address aware |
| PEType: | PE32+ |
| LinkerVersion: | 14.44 |
| CodeSize: | 6347776 |
| InitializedDataSize: | 3382272 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x5c2df0 |
| OSVersion: | 6 |
| ImageVersion: | - |
| SubsystemVersion: | 6 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 2026.1.31.2 |
| ProductVersionNumber: | 2026.1.31.2 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Win32 |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | Neutral |
| CharacterSet: | Unicode |
| Comments: | Solus Manifest App |
| CompanyName: | Solus |
| FileDescription: | SolusManifestApp |
| FileVersion: | 2026.1.31.2 |
| InternalName: | SolusManifestApp.dll |
| LegalCopyright: | |
| OriginalFileName: | SolusManifestApp.dll |
| ProductName: | SolusManifestApp |
| ProductVersion: | 2026.01.31.02+111392e22674a32198f09d6af5276f98057f5fc6 |
| AssemblyVersion: | 2026.1.31.2 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 3516 | "C:\Users\admin\Desktop\SolusManifestApp.exe" | C:\Users\admin\Desktop\SolusManifestApp.exe | explorer.exe | ||||||||||||
User: admin Company: Solus Integrity Level: MEDIUM Description: SolusManifestApp Version: 2026.1.31.2 Modules
| |||||||||||||||
| 6820 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (3516) SolusManifestApp.exe | Key: | HKEY_CLASSES_ROOT\solusapp |
| Operation: | write | Name: | URL Protocol |
Value: | |||
| (PID) Process: | (3516) SolusManifestApp.exe | Key: | HKEY_CLASSES_ROOT\AppUserModelId\C:/Users/admin/Desktop/SolusManifestApp.exe |
| Operation: | write | Name: | DisplayName |
Value: SolusManifestApp | |||
| (PID) Process: | (3516) SolusManifestApp.exe | Key: | HKEY_CLASSES_ROOT\AppUserModelId\C:/Users/admin/Desktop/SolusManifestApp.exe |
| Operation: | write | Name: | IconUri |
Value: C:\Users\admin\AppData\Local\ToastNotificationManagerCompat\Apps\A40E588E-FD2A-3D0A-4A02-F996D9E3DB9B\Icon.png | |||
| (PID) Process: | (3516) SolusManifestApp.exe | Key: | HKEY_CLASSES_ROOT\AppUserModelId\C:/Users/admin/Desktop/SolusManifestApp.exe |
| Operation: | write | Name: | IconBackgroundColor |
Value: FFDDDDDD | |||
| (PID) Process: | (3516) SolusManifestApp.exe | Key: | HKEY_CLASSES_ROOT\AppUserModelId\C:/Users/admin/Desktop/SolusManifestApp.exe |
| Operation: | write | Name: | Has7.0.1Fix |
Value: 1 | |||
| (PID) Process: | (3516) SolusManifestApp.exe | Key: | HKEY_CLASSES_ROOT\AppUserModelId\C:/Users/admin/Desktop/SolusManifestApp.exe |
| Operation: | write | Name: | CustomActivator |
Value: {a40e588e-fd2a-3d0a-4a02-f996d9e3db9b} | |||
| (PID) Process: | (3516) SolusManifestApp.exe | Key: | HKEY_CLASSES_ROOT\AppUserModelId\C:/Users/admin/Desktop/SolusManifestApp.exe |
| Operation: | write | Name: | HasSentNotification |
Value: 1 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3516 | SolusManifestApp.exe | C:\Users\admin\AppData\Local\Temp\.net\SolusManifestApp\dbc\SolusManifestApp.dll | — | |
MD5:— | SHA256:— | |||
| 3516 | SolusManifestApp.exe | C:\Users\admin\AppData\Local\Temp\.net\SolusManifestApp\dbc\SolusManifestApp.runtimeconfig.json | text | |
MD5:9C13746E2BEDC00E104FC98B2176E3E4 | SHA256:0FE526073C0561C18870F66ABAF813FB9B2166A5DB7D626B626CBB880DD5B145 | |||
| 3516 | SolusManifestApp.exe | C:\Users\admin\AppData\Local\Temp\.net\SolusManifestApp\dbc\System.Buffers.dll | executable | |
MD5:41765B786FD39A9B7E962360C6DB83E2 | SHA256:BE0676A25A7D06671F9E875BB95FADFDC757BF1EF1371A804D869744F74EE2FA | |||
| 3516 | SolusManifestApp.exe | C:\Users\admin\AppData\Local\Temp\.net\SolusManifestApp\dbc\System.AppContext.dll | executable | |
MD5:8209B40BE8F535AAD8E2C363EA05531A | SHA256:3C57A7696EB1D3C0EF92C788DB9D319045997F3D4E4ACD4BF19AF6C01493F3C5 | |||
| 3516 | SolusManifestApp.exe | C:\Users\admin\AppData\Local\Temp\.net\SolusManifestApp\dbc\Microsoft.Win32.Primitives.dll | executable | |
MD5:6DE6A4CF7EDDEC4902C38D74654D758B | SHA256:D2ECE2888E84009FA0D802B471A8A79A922CB76069A6DC083251AA258A9C3CE9 | |||
| 3516 | SolusManifestApp.exe | C:\Users\admin\AppData\Local\Temp\.net\SolusManifestApp\dbc\System.Collections.Concurrent.dll | executable | |
MD5:5D0A6DBB2EA6FF8702D9588F583A580B | SHA256:4E00A1B4696FEFC0384D1060B4330EE1321F221B9FA76D84958F954DA677D873 | |||
| 3516 | SolusManifestApp.exe | C:\Users\admin\AppData\Local\Temp\.net\SolusManifestApp\dbc\System.Collections.Immutable.dll | executable | |
MD5:4836F0E4466A5E17B7527A23088F933D | SHA256:61030351D8BC49E2345597F4A115A8B783B3FA7F3CF5949B16AC1708DEBF04C3 | |||
| 3516 | SolusManifestApp.exe | C:\Users\admin\AppData\Local\Temp\.net\SolusManifestApp\dbc\Microsoft.Win32.Registry.dll | executable | |
MD5:B22AABFB0DB3119A5E4E39E7C807EB82 | SHA256:906B6D70E1630E7EB1D565F35EAB0A72A3851A5F8A4710FD8C4D5B24E788E361 | |||
| 3516 | SolusManifestApp.exe | C:\Users\admin\AppData\Local\Temp\.net\SolusManifestApp\dbc\System.ComponentModel.Annotations.dll | executable | |
MD5:4A12F13A87CFC9D551EDDA8CA5086ECA | SHA256:956ECED688DE9D333CF8A32F73F98E406A99DDBAA964022E09014E53FA3E1866 | |||
| 3516 | SolusManifestApp.exe | C:\Users\admin\AppData\Local\Temp\.net\SolusManifestApp\dbc\System.Collections.Specialized.dll | executable | |
MD5:32BE37FBF350F12DD5E1E3EBD95362B8 | SHA256:1FDDF55A3F33A29C7AB165F961403669990043897D9F7933228F70B313500D1F | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
3516 | SolusManifestApp.exe | GET | — | 188.114.96.3:443 | https://applist.morrenus.xyz/ | US | — | — | unknown |
5780 | svchost.exe | GET | 200 | 2.19.126.146:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 825 b | whitelisted |
— | — | GET | 200 | 2.19.126.146:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 825 b | whitelisted |
6768 | MoUsoCoreWorker.exe | GET | 200 | 2.19.126.146:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 825 b | whitelisted |
— | — | GET | 200 | 140.82.121.5:443 | https://api.github.com/repos/MorrenusGames/Solus-Manifest-App/releases/latest | US | text | 4.37 Kb | unknown |
— | — | GET | 200 | 188.114.97.3:443 | https://applist.morrenus.xyz/ | US | text | 19.9 Mb | unknown |
— | — | POST | 500 | 48.192.1.64:443 | https://activation-v2.sls.microsoft.com/SLActivateProduct/SLActivateProduct.asmx?configextension=Retail | US | — | — | unknown |
3292 | svchost.exe | GET | 200 | 23.59.18.102:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Update%20Signing%20CA%202.3.crl | US | binary | 400 b | whitelisted |
3516 | SolusManifestApp.exe | GET | 200 | 140.82.121.6:443 | https://api.github.com/repos/MorrenusGames/Solus-Manifest-App/releases/latest | US | text | 4.37 Kb | unknown |
3292 | svchost.exe | GET | 200 | 23.59.18.102:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Update%20Signing%20CA%202.2.crl | US | binary | 401 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 20.73.194.208:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
4 | System | 192.168.100.255:137 | — | Not routed | — | whitelisted |
4 | System | 192.168.100.255:138 | — | Not routed | — | whitelisted |
5780 | svchost.exe | 2.19.126.146:80 | crl.microsoft.com | AKAMAI-ASN1 | NL | whitelisted |
— | — | 2.19.126.146:80 | crl.microsoft.com | AKAMAI-ASN1 | NL | whitelisted |
6768 | MoUsoCoreWorker.exe | 2.19.126.146:80 | crl.microsoft.com | AKAMAI-ASN1 | NL | whitelisted |
— | — | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
3516 | SolusManifestApp.exe | 140.82.121.6:443 | api.github.com | GITHUB | US | whitelisted |
3516 | SolusManifestApp.exe | 188.114.96.3:443 | applist.morrenus.xyz | CLOUDFLARENET | US | whitelisted |
3560 | slui.exe | 48.192.1.64:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
self.events.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
applist.morrenus.xyz |
| unknown |
api.github.com |
| whitelisted |
activation-v2.sls.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
— | — | Potentially Bad Traffic | ET HUNTING Request to .XYZ Domain with Minimal Headers |
3516 | SolusManifestApp.exe | Potentially Bad Traffic | ET HUNTING Request to .XYZ Domain with Minimal Headers |