ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
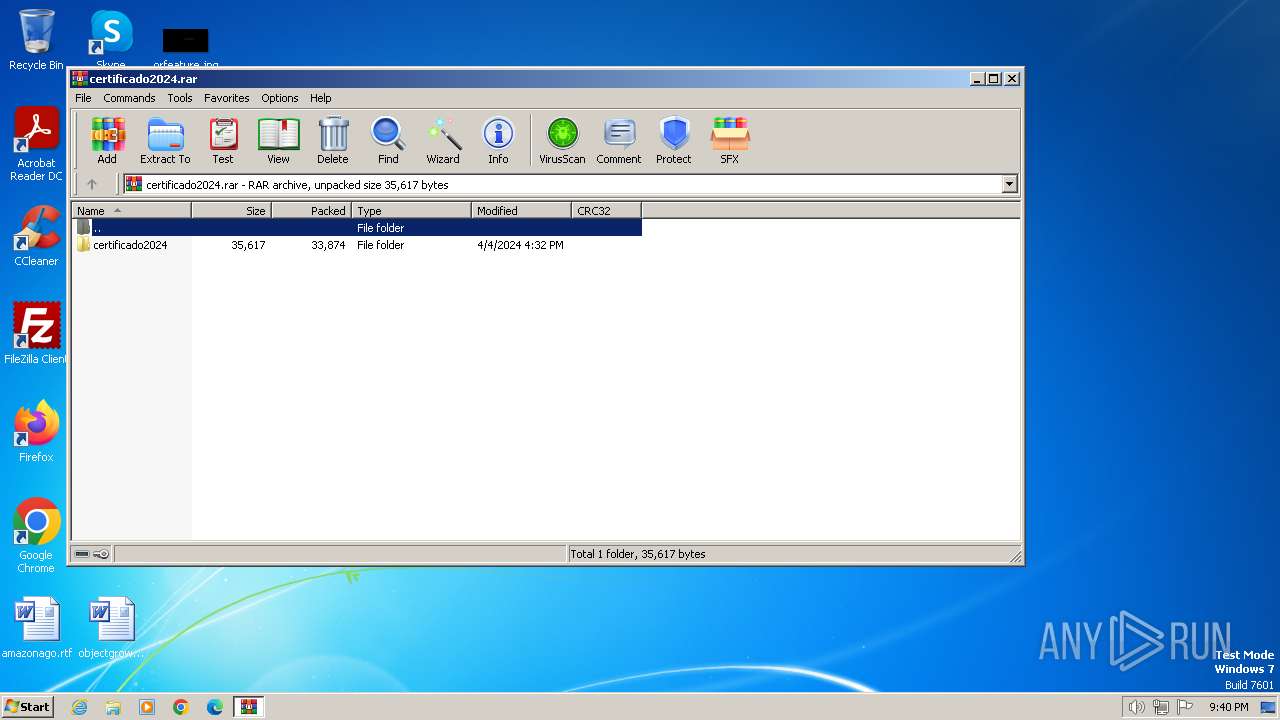
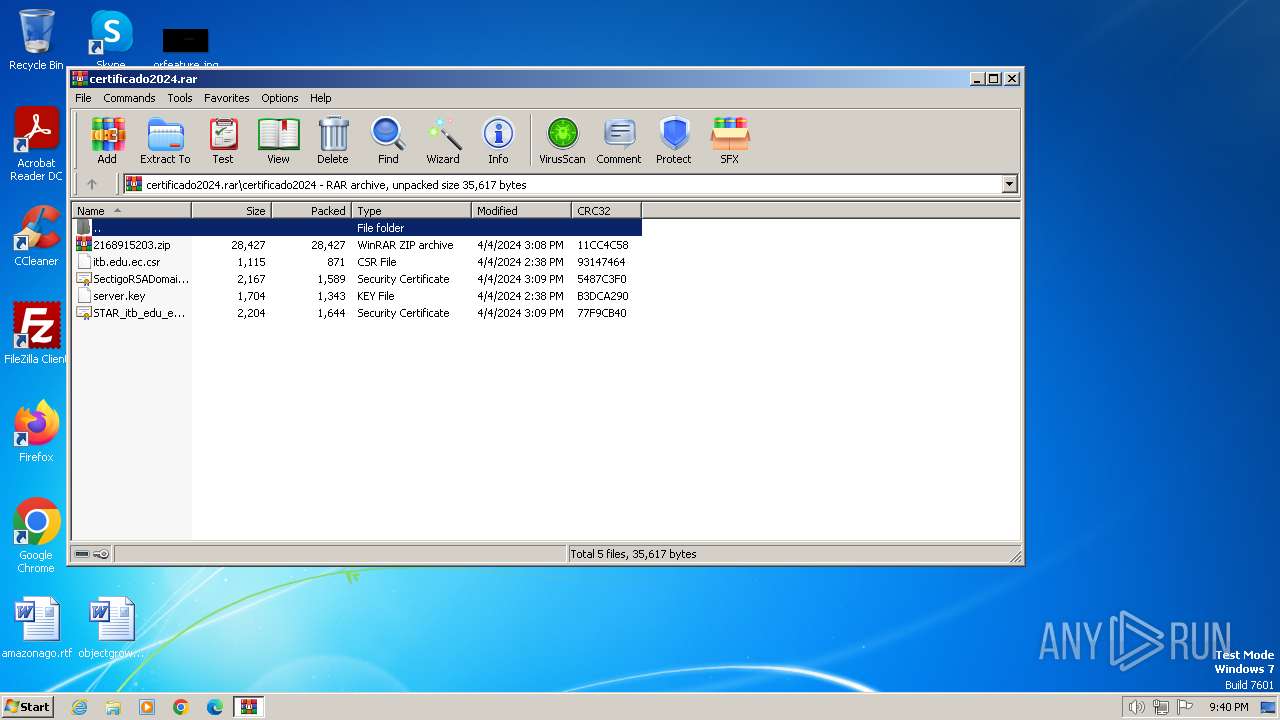
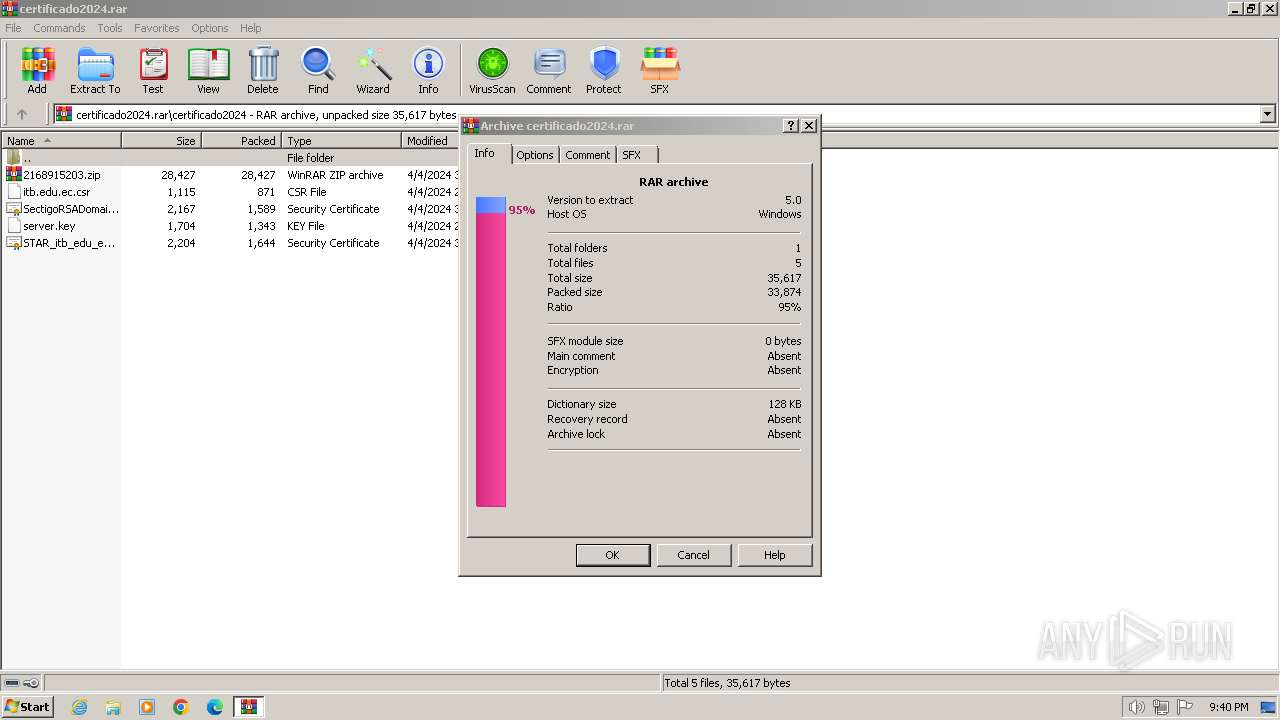
| File name: | certificado2024.rar |
| Full analysis: | https://app.any.run/tasks/598d137c-bd96-4f8a-a147-f0e446929ceb |
| Verdict: | Malicious activity |
| Analysis date: | April 16, 2024, 20:40:21 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Indicators: | |
| MIME: | application/x-rar |
| File info: | RAR archive data, v5 |
| MD5: | DD498F703860AA5430AD8CC769183C18 |
| SHA1: | 5D5284ECDCADEEF0084CB91CDE1D506DFAB960B1 |
| SHA256: | BB0576EE9672AAC31413A7C5912BC25E44AC10A0B8F1882F455C1DA83845D16F |
| SSDEEP: | 768:TOkLyZWtZcwMyOvxOv9gPGkXQGkXggmg3o7ohow8wXqpY:TOkOY0wmvcvjf3C0h5wY |
| .rar | | | RAR compressed archive (v5.0) (61.5) |
|---|---|---|
| .rar | | | RAR compressed archive (gen) (38.4) |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
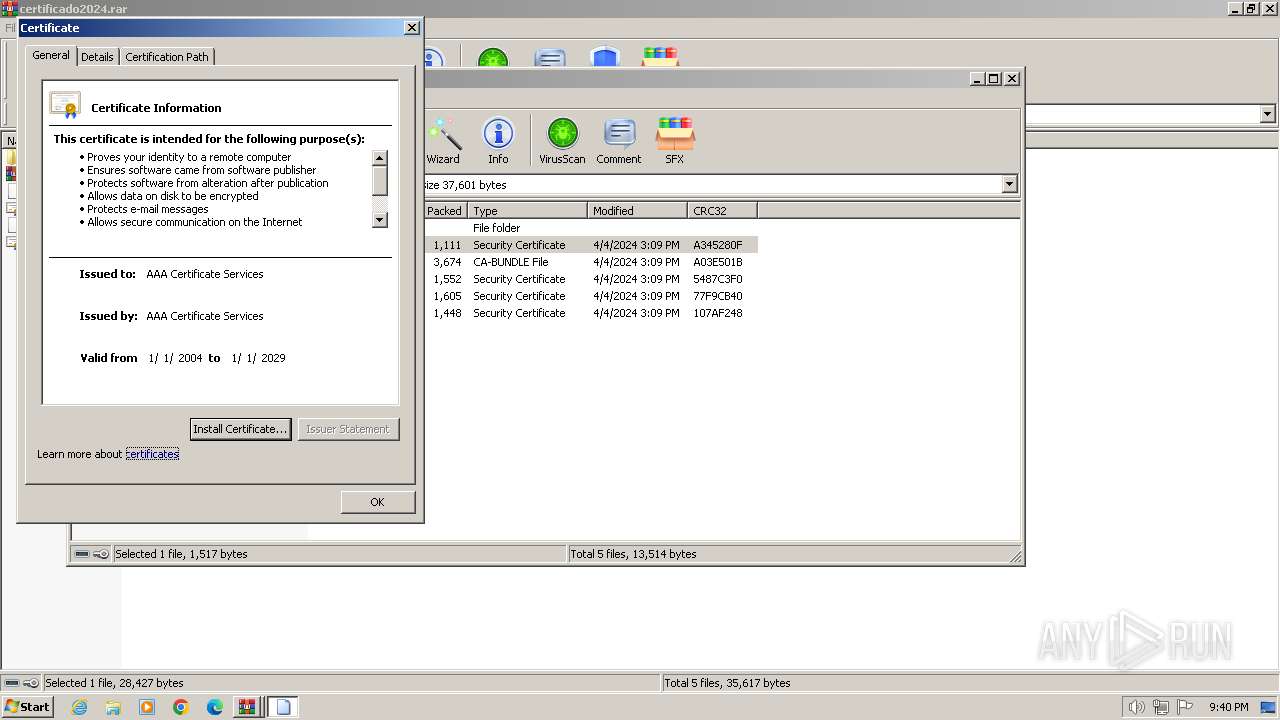
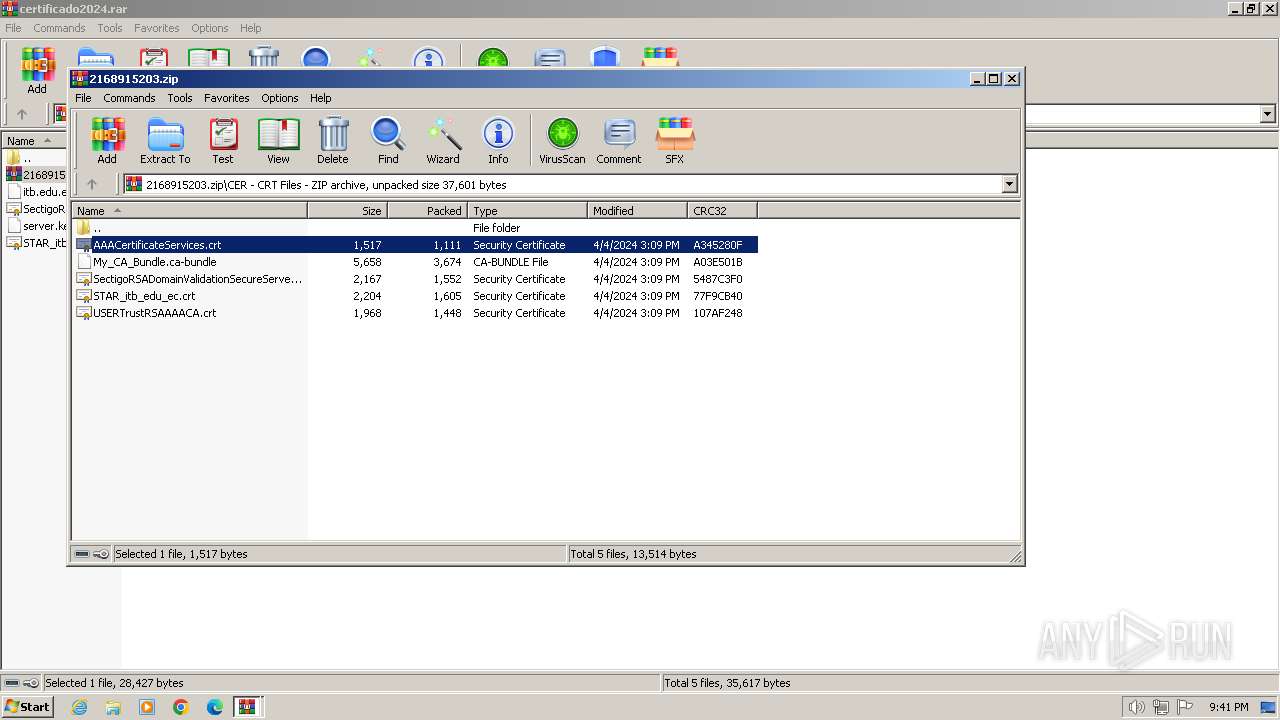
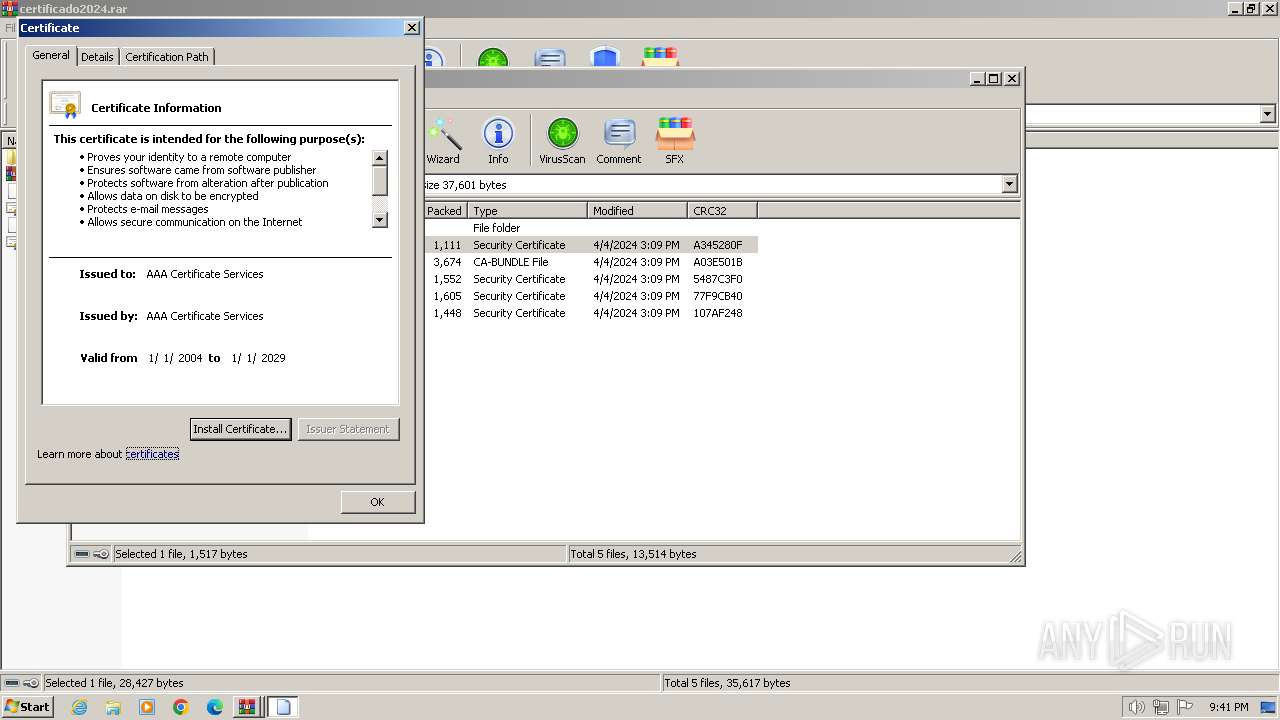
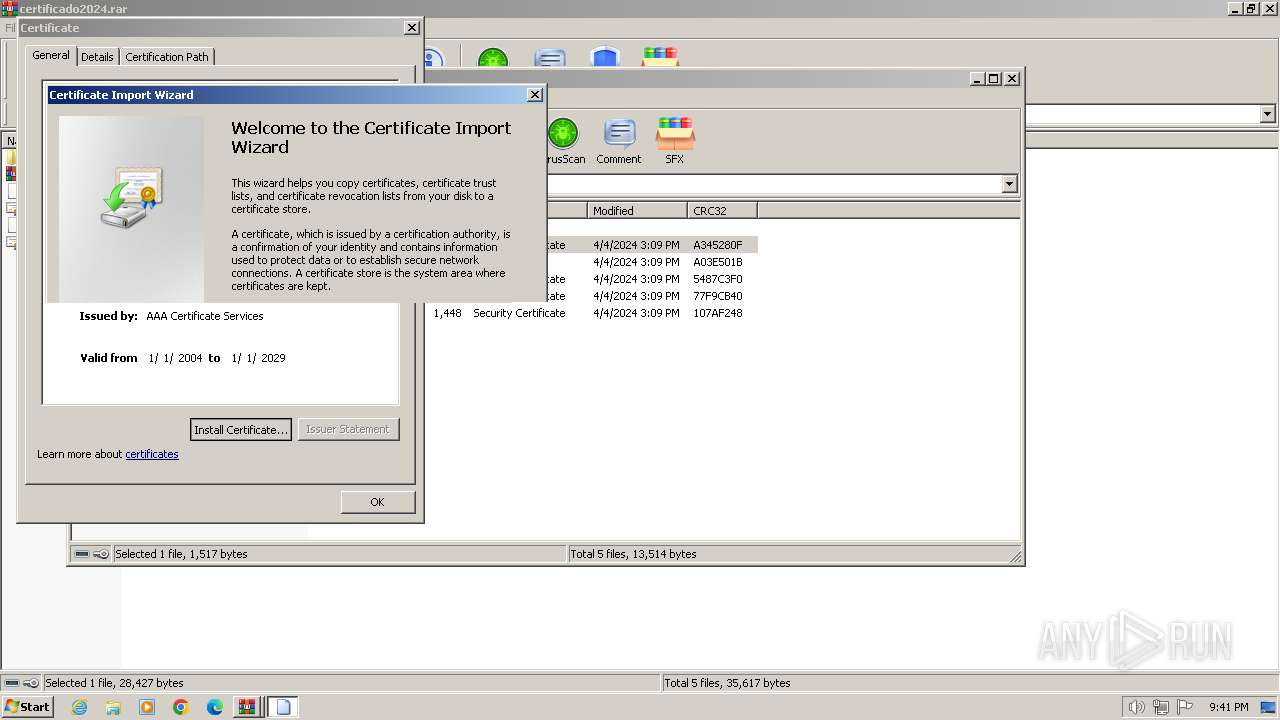
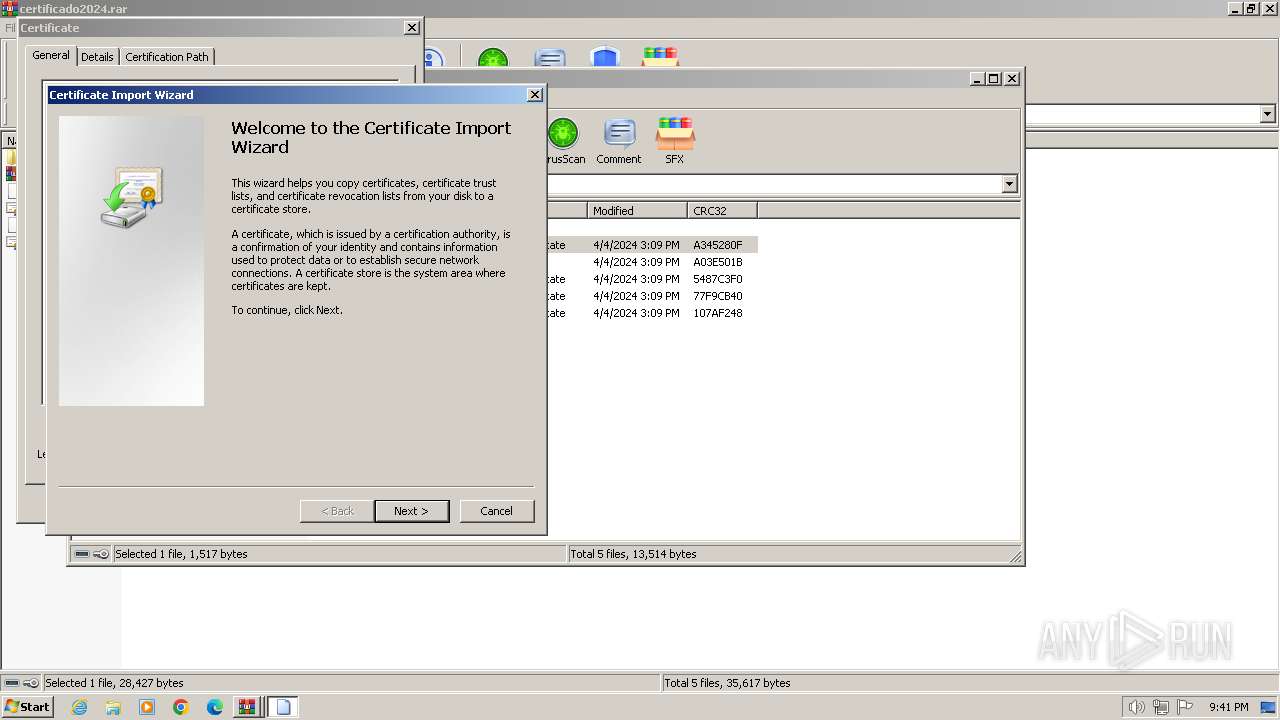
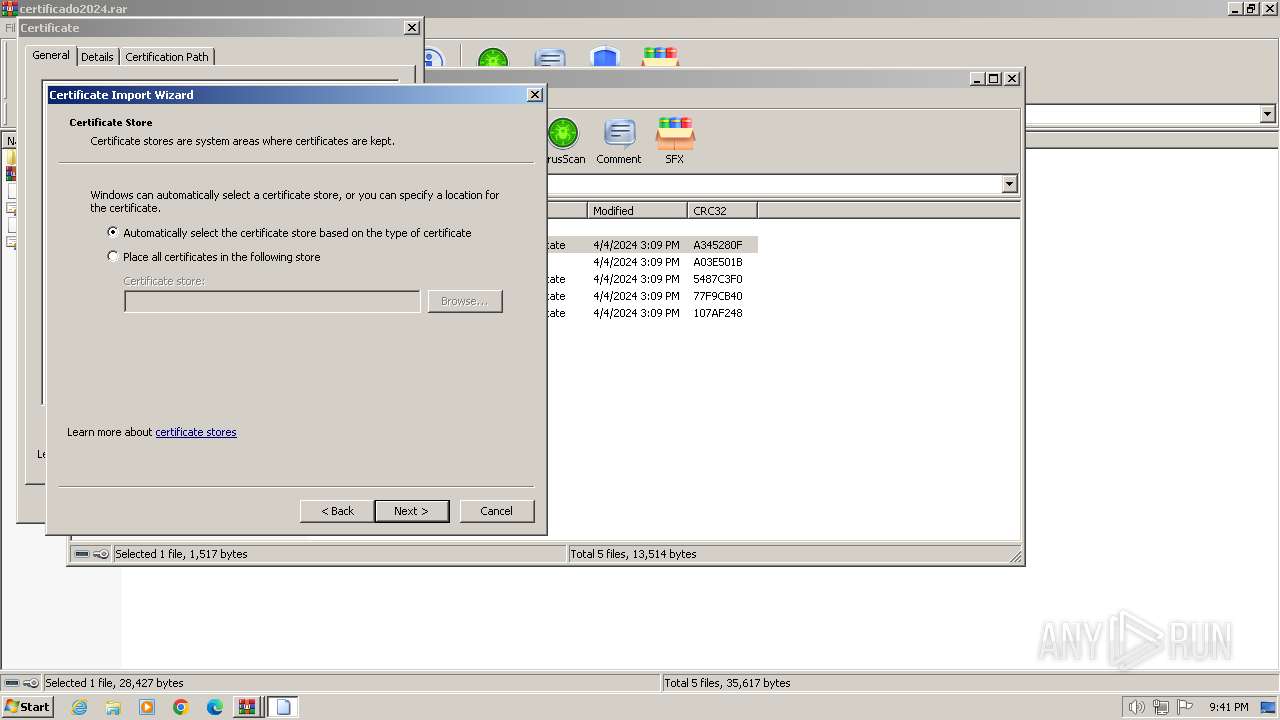
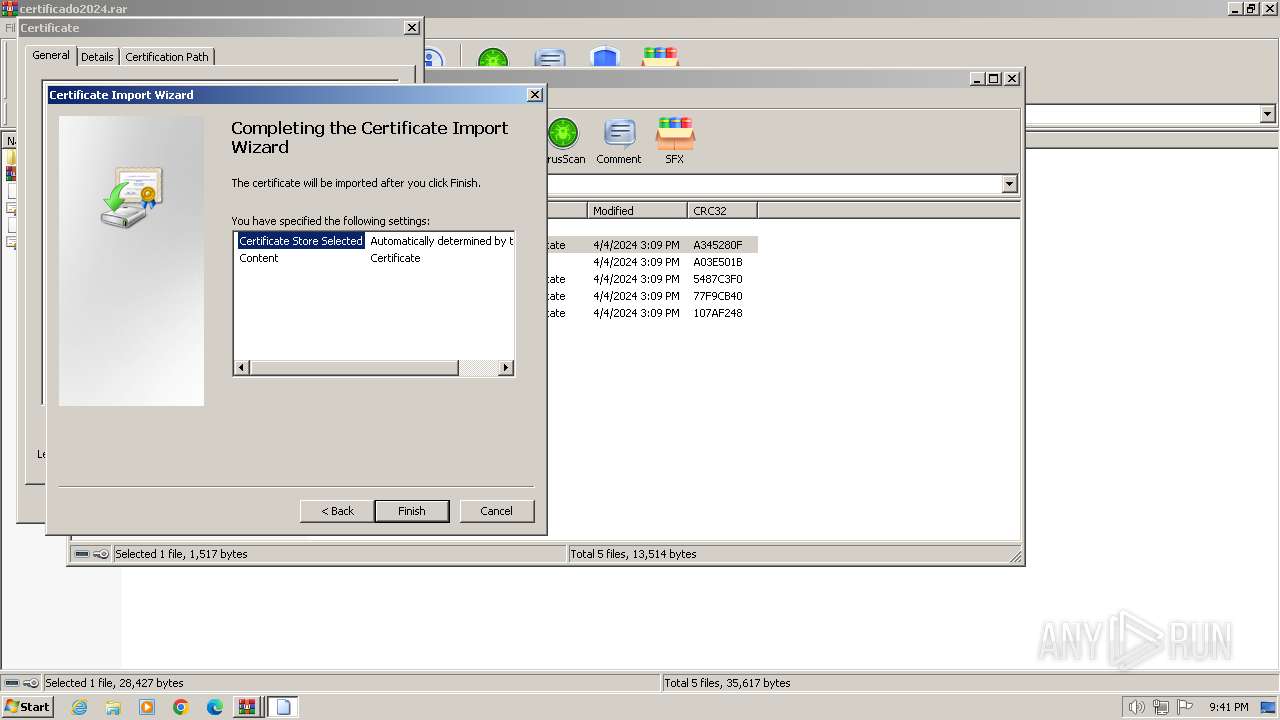
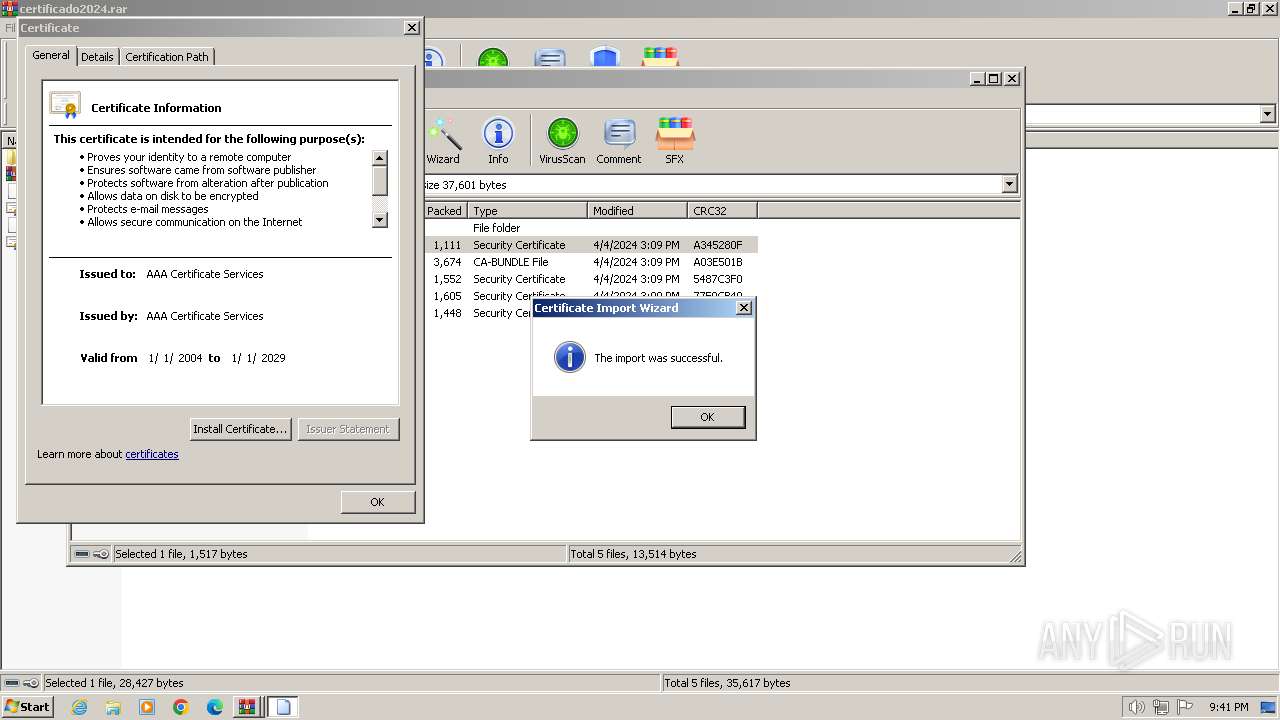
| 1820 | "C:\Windows\system32\rundll32.exe" cryptext.dll,CryptExtOpenCER C:\Users\admin\AppData\Local\Temp\Rar$DIa2344.37951\AAACertificateServices.crt | C:\Windows\System32\rundll32.exe | WinRAR.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
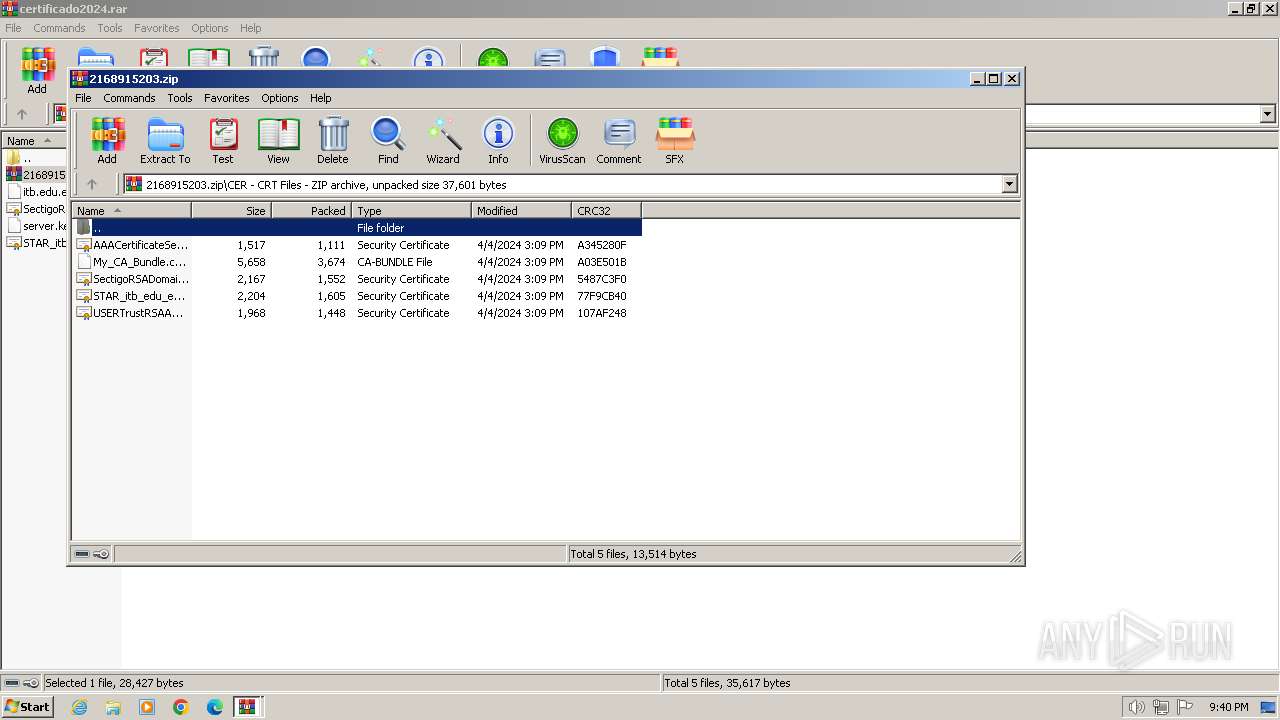
| 2308 | "C:\Program Files\WinRAR\WinRAR.exe" C:\Users\admin\AppData\Local\Temp\certificado2024.rar | C:\Program Files\WinRAR\WinRAR.exe | — | explorer.exe | |||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Version: 5.91.0 Modules
| |||||||||||||||
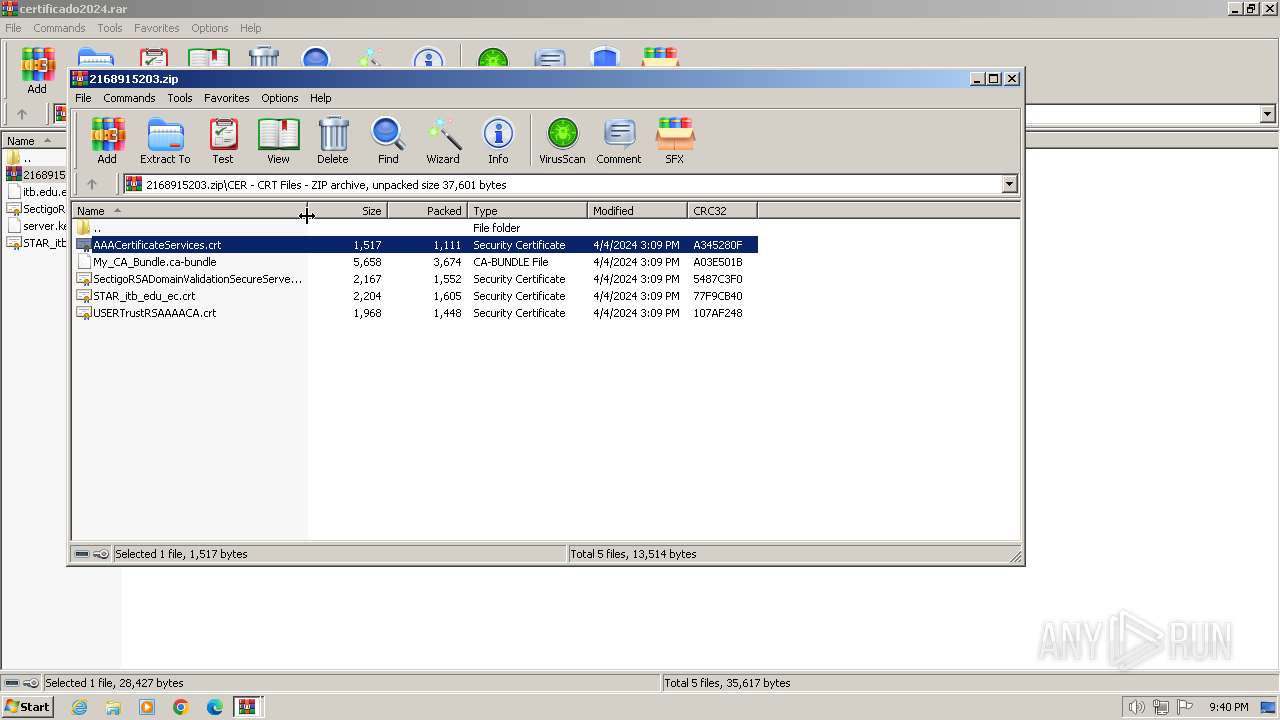
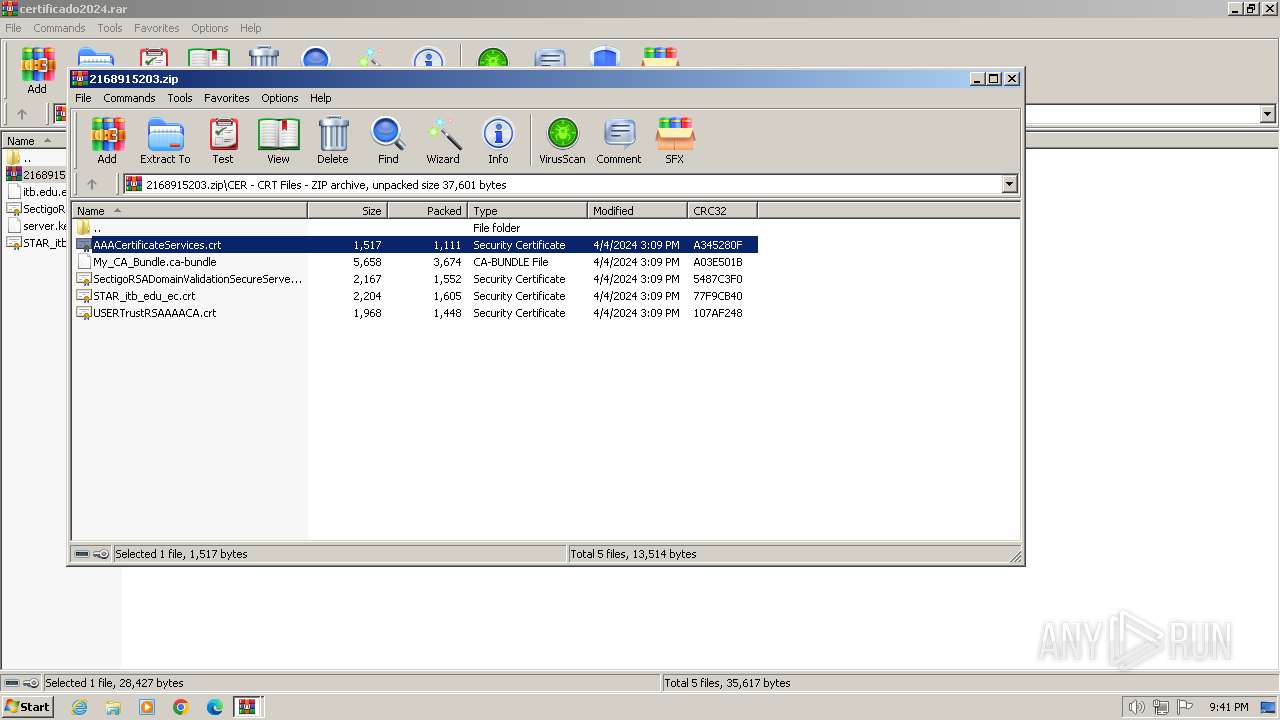
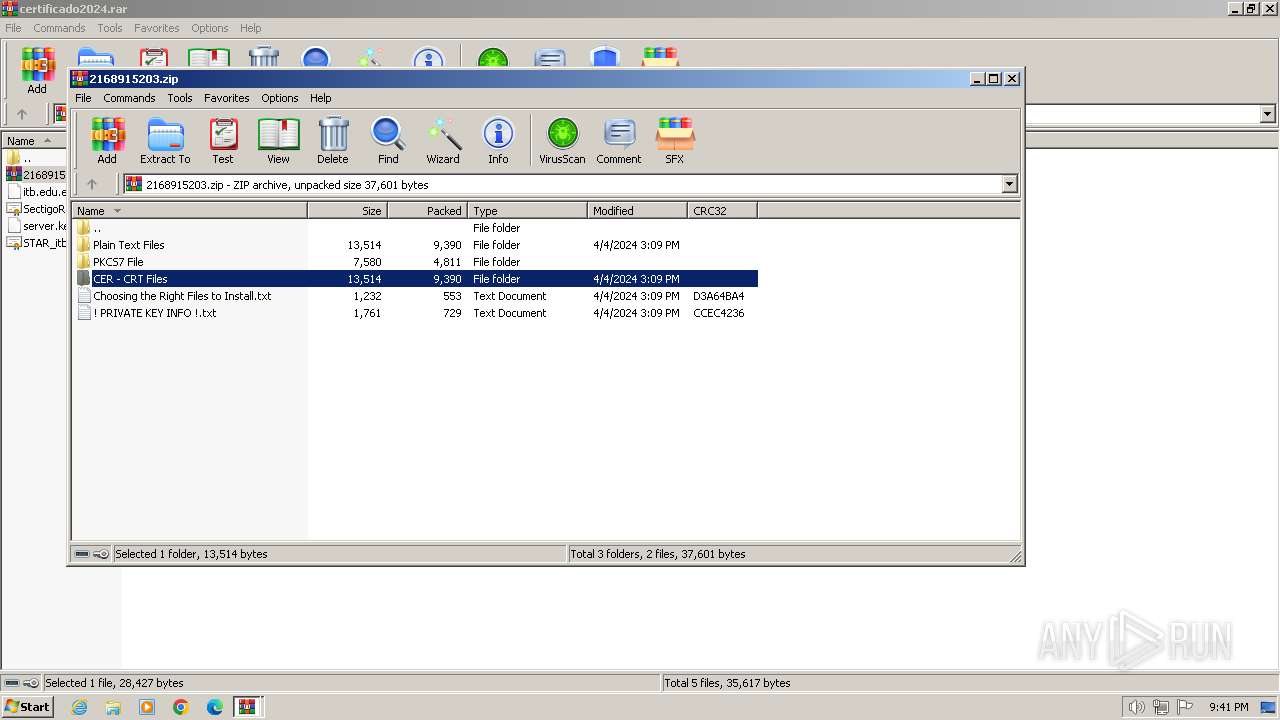
| 2344 | "C:\Program Files\WinRAR\WinRAR.exe" C:\Users\admin\AppData\Local\Temp\Rar$DIa2308.35638\2168915203.zip | C:\Program Files\WinRAR\WinRAR.exe | — | WinRAR.exe | |||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Version: 5.91.0 Modules
| |||||||||||||||
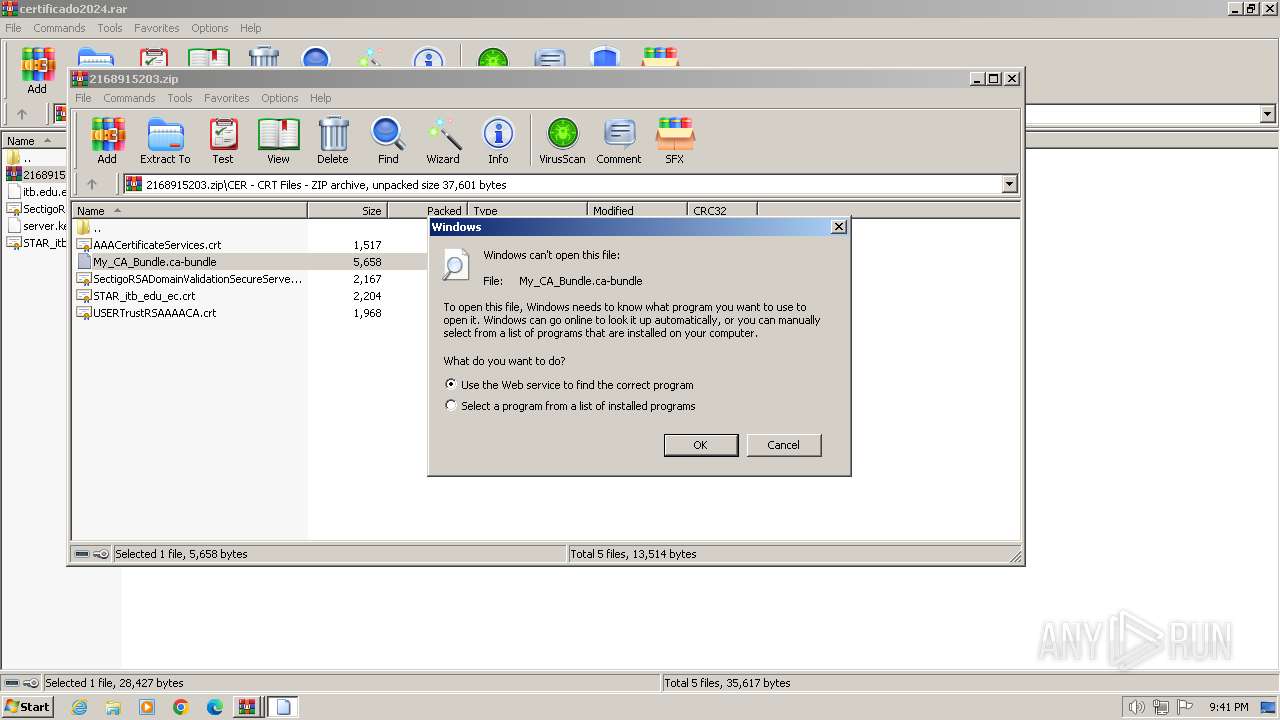
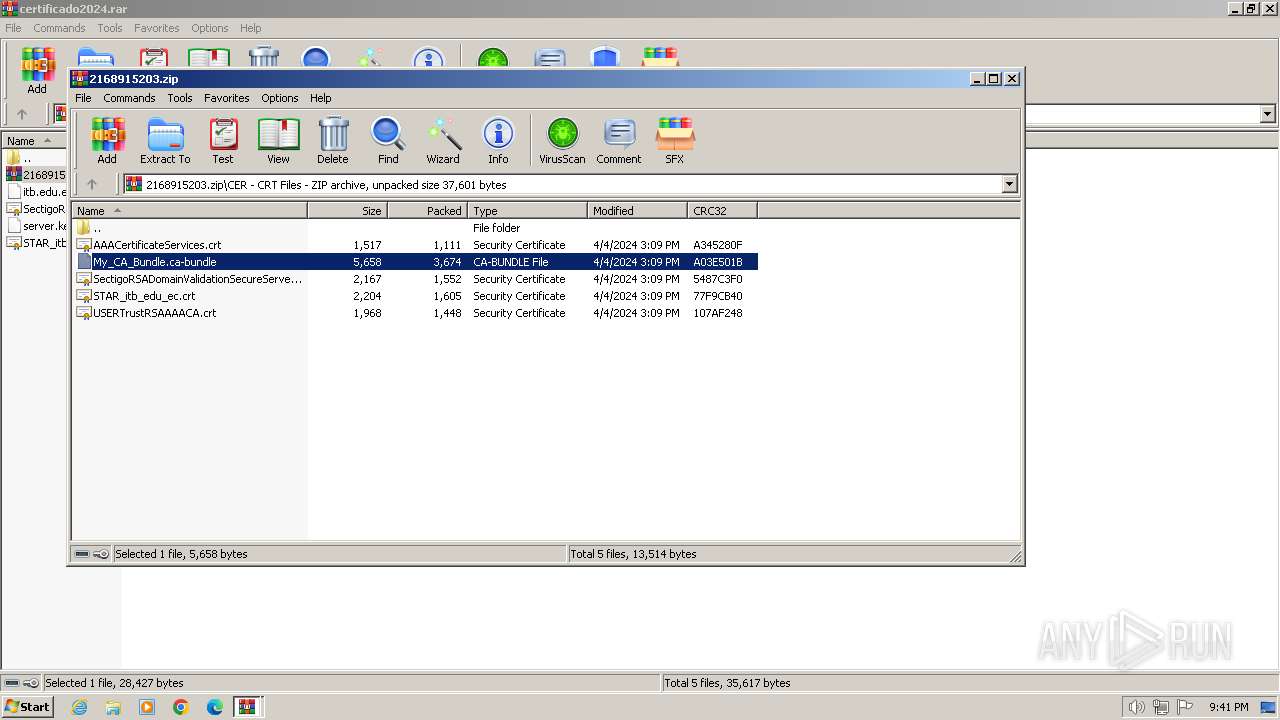
| 3192 | "C:\Windows\system32\rundll32.exe" C:\Windows\system32\shell32.dll,OpenAs_RunDLL C:\Users\admin\AppData\Local\Temp\Rar$DIa2344.37470\My_CA_Bundle.ca-bundle | C:\Windows\System32\rundll32.exe | — | WinRAR.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 3272 | "C:\Windows\system32\rundll32.exe" cryptext.dll,CryptExtOpenCER C:\Users\admin\AppData\Local\Temp\Rar$DIa2344.36882\AAACertificateServices.crt | C:\Windows\System32\rundll32.exe | — | WinRAR.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| (PID) Process: | (2308) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtBMP |
Value: | |||
| (PID) Process: | (2308) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtIcon |
Value: | |||
| (PID) Process: | (2308) WinRAR.exe | Key: | HKEY_CLASSES_ROOT\Local Settings\MuiCache\182\52C64B7E |
| Operation: | write | Name: | LanguageList |
Value: en-US | |||
| (PID) Process: | (2308) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 3 |
Value: C:\Users\admin\Desktop\phacker.zip | |||
| (PID) Process: | (2308) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 2 |
Value: C:\Users\admin\Desktop\Win7-KB3191566-x86.zip | |||
| (PID) Process: | (2308) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 1 |
Value: C:\Users\admin\Desktop\curl-8.5.0_1-win32-mingw.zip | |||
| (PID) Process: | (2308) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 0 |
Value: C:\Users\admin\AppData\Local\Temp\certificado2024.rar | |||
| (PID) Process: | (2308) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | name |
Value: 120 | |||
| (PID) Process: | (2308) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | size |
Value: 80 | |||
| (PID) Process: | (2308) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | type |
Value: 120 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2308 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DIa2308.35638\2168915203.zip | compressed | |
MD5:A22A580EEC5FDD8E3F2A066C1C5A1A5C | SHA256:A5DDABD1602AE1C66CE11AD078E734CC473DCB8E9F573037832D8536AE3DE90B | |||
| 2344 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DIa2344.37951\AAACertificateServices.crt | text | |
MD5:A22A580EEC5FDD8E3F2A066C1C5A1A5C | SHA256:A5DDABD1602AE1C66CE11AD078E734CC473DCB8E9F573037832D8536AE3DE90B | |||
| 2344 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DIa2344.36882\AAACertificateServices.crt | text | |
MD5:A22A580EEC5FDD8E3F2A066C1C5A1A5C | SHA256:A5DDABD1602AE1C66CE11AD078E734CC473DCB8E9F573037832D8536AE3DE90B | |||
| 2344 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DIa2344.37470\My_CA_Bundle.ca-bundle | text | |
MD5:6A07D397DD99A9CA1BF8E8AAEE60844B | SHA256:294F1760710CCA5E9122F7732503E2A1A7A5D0EBE3F16213D6E3AE9D5E16F14E | |||
| 1820 | rundll32.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\MetaData\57C8EDB95DF3F0AD4EE2DC2B8CFD4157 | binary | |
MD5:DC47D6E706B453DD4BC3477C38E887CE | SHA256:00325DB5A7C4549F934CC4E07A2E016DE8011D2963C51983EC3D8791E70447C6 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
1820 | rundll32.exe | GET | 304 | 2.23.81.40:80 | http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/disallowedcertstl.cab?8046d414a664c5c7 | DE | — | — | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
— | — | 224.0.0.252:5355 | — | — | — | unknown |
1080 | svchost.exe | 224.0.0.252:5355 | — | — | — | unknown |
1820 | rundll32.exe | 2.23.81.40:80 | ctldl.windowsupdate.com | Akamai International B.V. | DE | unknown |
Domain | IP | Reputation |
|---|---|---|
dns.msftncsi.com |
| shared |
ctldl.windowsupdate.com |
| whitelisted |