ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
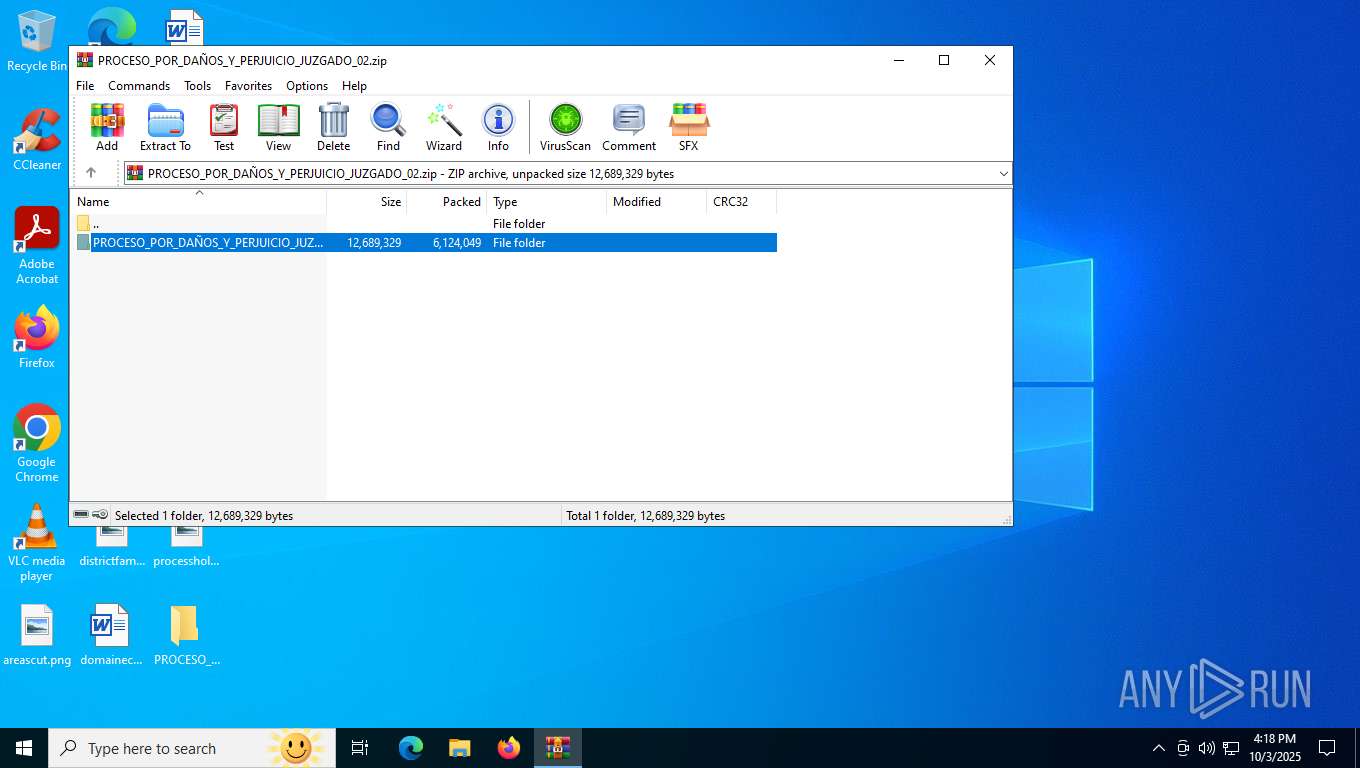
| File name: | PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02.zip |
| Full analysis: | https://app.any.run/tasks/976b9303-c744-4356-9388-675e259187e7 |
| Verdict: | Malicious activity |
| Analysis date: | October 03, 2025, 16:17:55 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/zip |
| File info: | Zip archive data, at least v2.0 to extract, compression method=deflate |
| MD5: | 359C2C2B1D4C3DCD7970EC24AAEAE670 |
| SHA1: | D46CC57B28EBF2893E729AA9AE471652404128EF |
| SHA256: | B8C6CE8F6C38D985A889B87B451BE9F84F69C11ABC8D6C931C39AB7A8A44A967 |
| SSDEEP: | 98304:HAp3qR4lv99JKuiteQbIRqUa0ODDP9JIjU2AEI3pZGJSnVO63kPv+uRsgydxNYba:mBAFWvTyYzTG |
| .zip | | | ZIP compressed archive (100) |
|---|
| ZipRequiredVersion: | 20 |
|---|---|
| ZipBitFlag: | - |
| ZipCompression: | Deflated |
| ZipModifyDate: | 2025:10:03 10:39:22 |
| ZipCRC: | 0x2c93ba91 |
| ZipCompressedSize: | 1479800 |
| ZipUncompressedSize: | 3307792 |
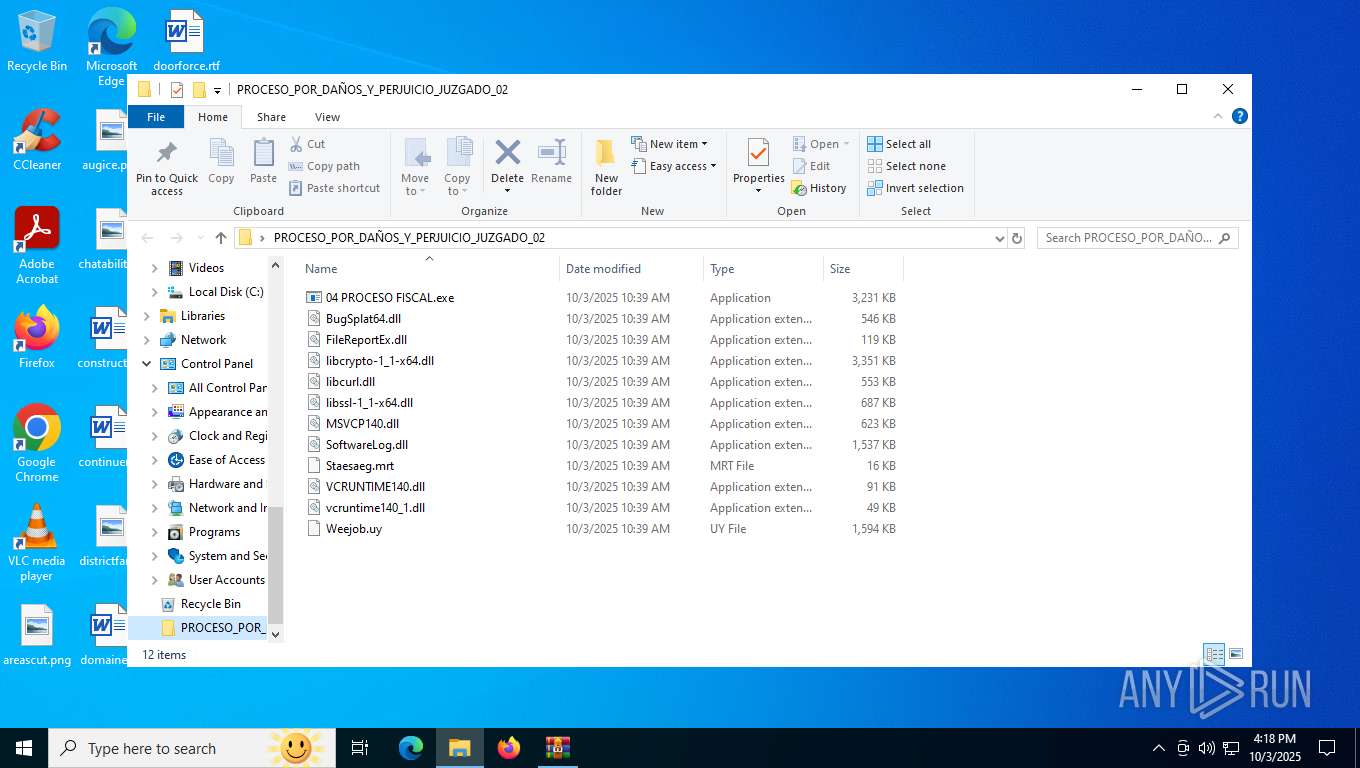
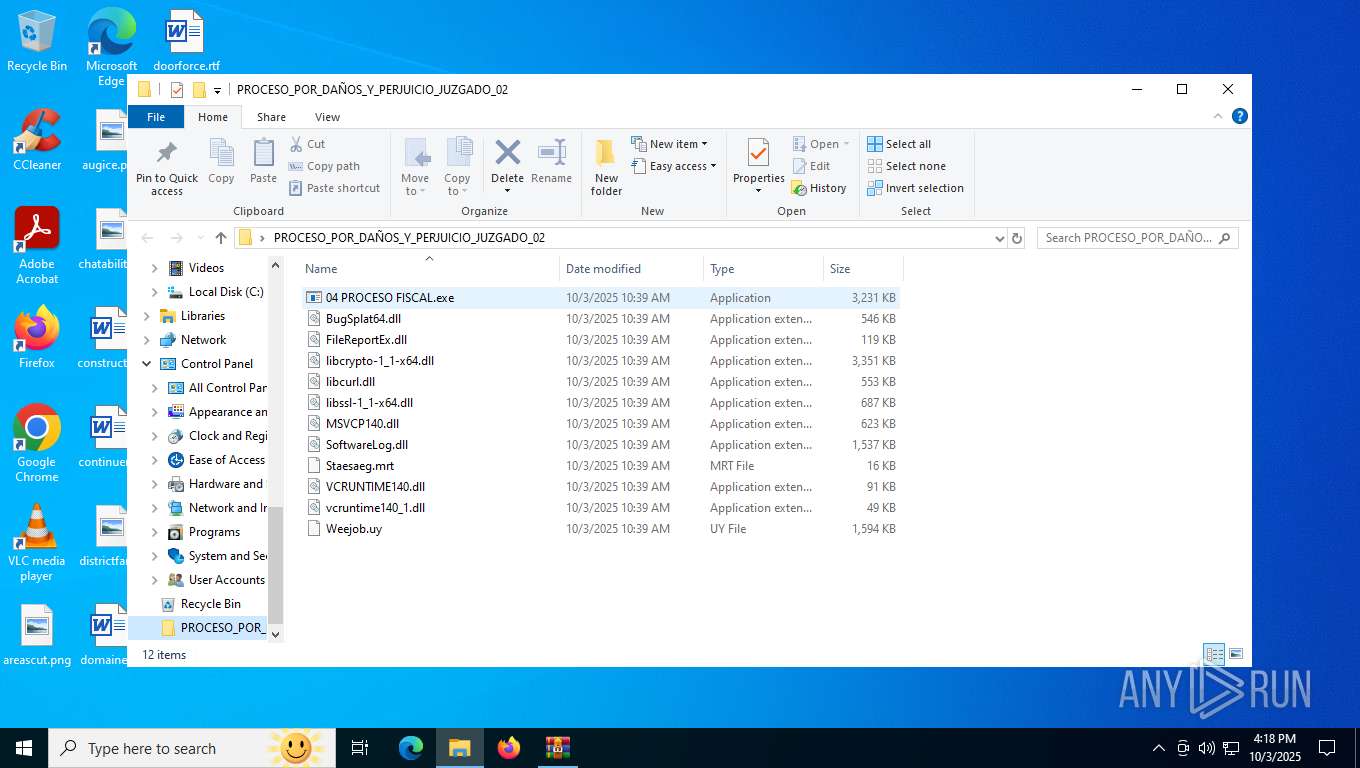
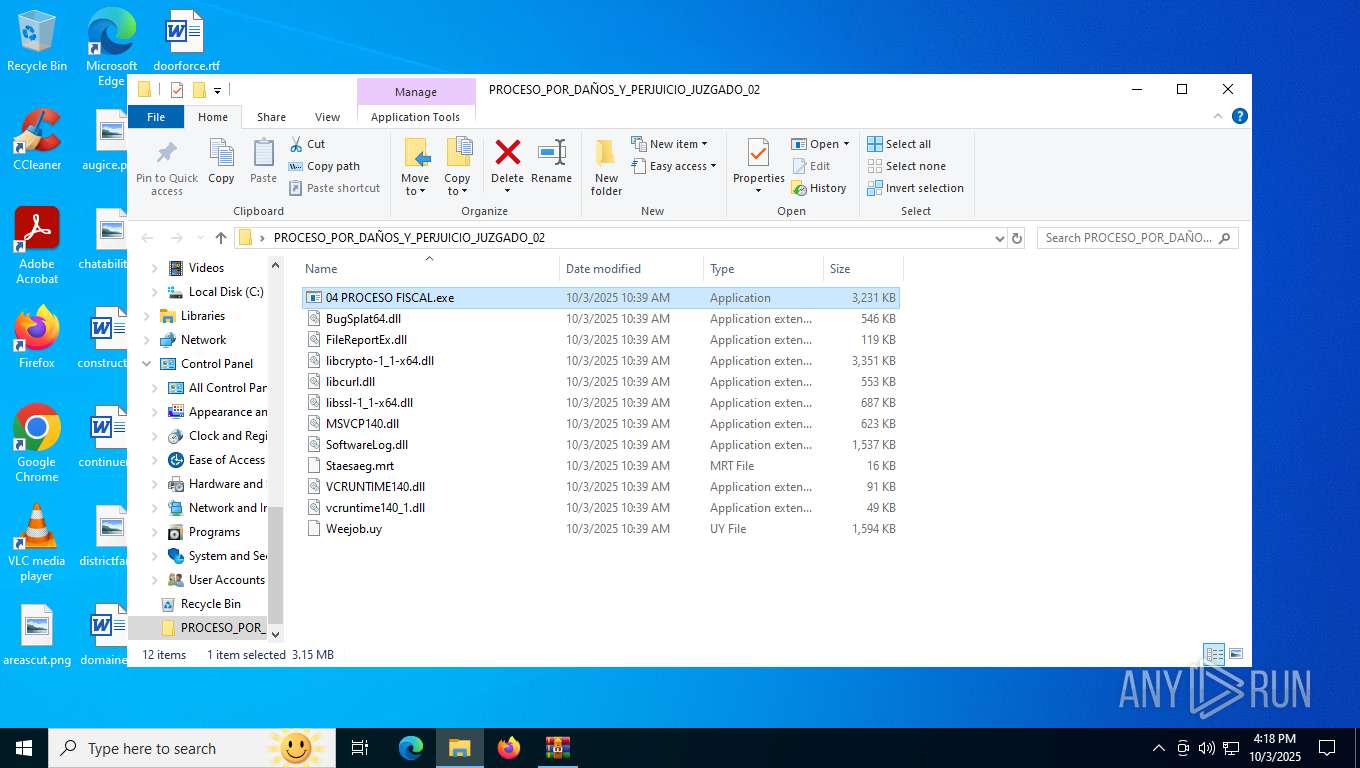
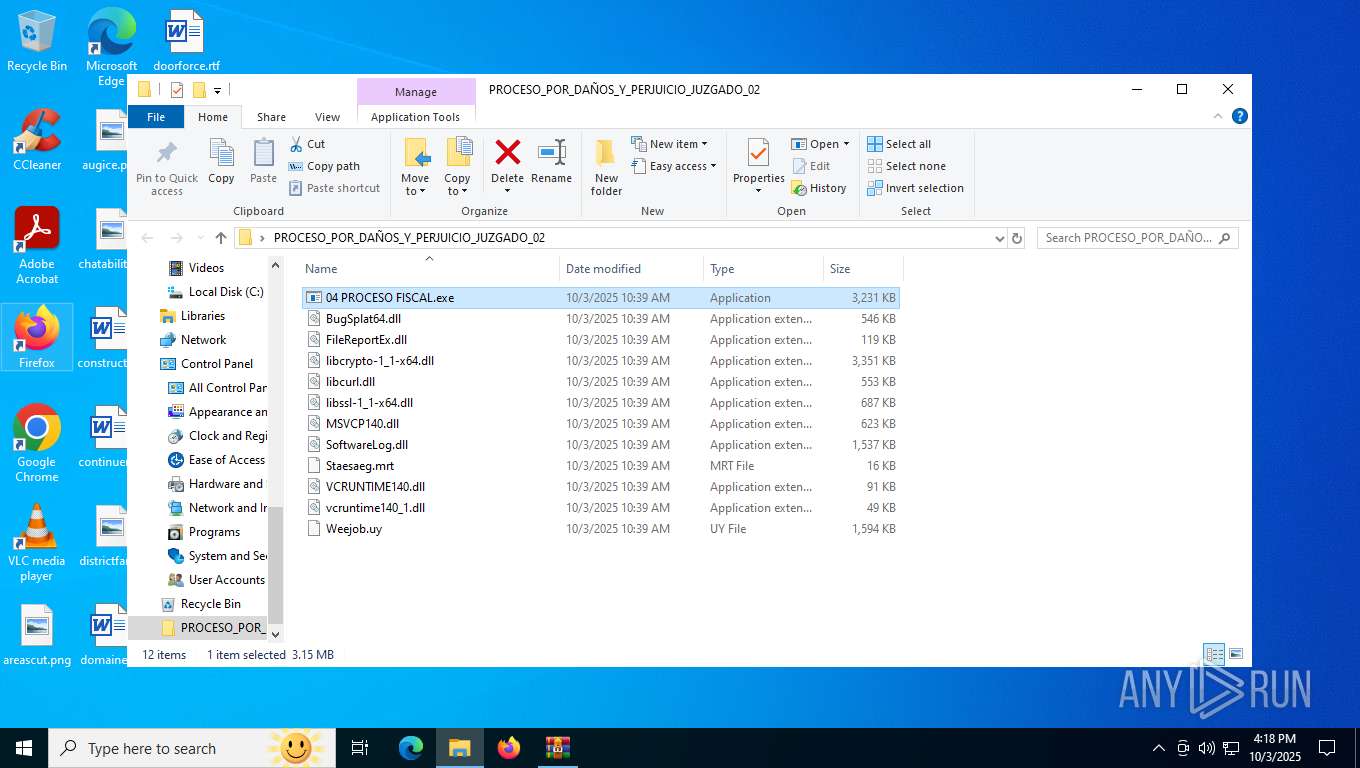
| ZipFileName: | PROCESO_POR_DA?OS_Y_PERJUICIO_JUZGADO_02/04 PROCESO FISCAL.exe |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1364 | "C:\Program Files\WinRAR\WinRAR.exe" C:\Users\admin\AppData\Local\Temp\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02.zip | C:\Program Files\WinRAR\WinRAR.exe | explorer.exe | ||||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Version: 5.91.0 Modules
| |||||||||||||||
| 2092 | C:\Users\admin\AppData\Roaming\ServerTls_v1\Chime.exe | C:\Users\admin\AppData\Roaming\ServerTls_v1\Chime.exe | — | 04 PROCESO FISCAL.exe | |||||||||||
User: admin Company: Amazon.com Services LLC Integrity Level: MEDIUM Description: Amazon Chime Version: 5.23.32022 | |||||||||||||||
| 2428 | C:\WINDOWS\system32\svchost.exe -k NetworkService -p -s Dnscache | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3240 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4416 | "C:\Users\admin\Desktop\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02\04 PROCESO FISCAL.exe" | C:\Users\admin\Desktop\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02\04 PROCESO FISCAL.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Description: UpdateService Version: 1.0.0.390 Modules
| |||||||||||||||
| 8060 | C:\Users\admin\AppData\Local\Temp\PortInterface32.exe | C:\Users\admin\AppData\Local\Temp\PortInterface32.exe | 04 PROCESO FISCAL.exe | ||||||||||||
User: admin Company: Ludwig.guru Integrity Level: MEDIUM Description: Ludwig Version: 3.1.8 Modules
| |||||||||||||||
| (PID) Process: | (1364) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtBMP |
Value: | |||
| (PID) Process: | (1364) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtIcon |
Value: | |||
| (PID) Process: | (1364) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 3 |
Value: C:\Users\admin\Desktop\preferences.zip | |||
| (PID) Process: | (1364) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 2 |
Value: C:\Users\admin\Desktop\chromium_ext.zip | |||
| (PID) Process: | (1364) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 1 |
Value: C:\Users\admin\Desktop\omni_23_10_2024_.zip | |||
| (PID) Process: | (1364) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 0 |
Value: C:\Users\admin\AppData\Local\Temp\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02.zip | |||
| (PID) Process: | (1364) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | name |
Value: 120 | |||
| (PID) Process: | (1364) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | size |
Value: 80 | |||
| (PID) Process: | (1364) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | type |
Value: 120 | |||
| (PID) Process: | (1364) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | mtime |
Value: 100 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 1364 | WinRAR.exe | C:\Users\admin\Desktop\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02\04 PROCESO FISCAL.exe | executable | |
MD5:D8D87C051555C6FF0337065FF828F7C6 | SHA256:ECBF9E6DE52105BE852593472611A21989EFFC7D4E73ACB4A0D0A01347A8D079 | |||
| 1364 | WinRAR.exe | C:\Users\admin\Desktop\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02\libcrypto-1_1-x64.dll | executable | |
MD5:98CC3EC8FDA3614538E4C69DB94F0957 | SHA256:8824021DAEDFF8F70E8DE972F47968AC4C8F96551A55FCEEBFA571BEAC5EDBEB | |||
| 1364 | WinRAR.exe | C:\Users\admin\Desktop\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02\Staesaeg.mrt | binary | |
MD5:26F41B82E5C9F72939DAA4C386B80D97 | SHA256:6FE4F26CCA1D7FA65CD3FE65D562498C3EE8BC0AB22BB1BE00BB1D7281FD468C | |||
| 1364 | WinRAR.exe | C:\Users\admin\Desktop\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02\libcurl.dll | executable | |
MD5:E42AAF7D8B0333CD81729F8A1766363C | SHA256:2AA945D79CDA4575F6219039331550E4F770E159539AF28239077DA35DDD1497 | |||
| 1364 | WinRAR.exe | C:\Users\admin\Desktop\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02\SoftwareLog.dll | executable | |
MD5:138AA79B69C1D73B654BD4EDFE7CE6BC | SHA256:26D73269784F077C32ABD67A8C7FB2CB521499450E1333D5BBD99CD9B6F38C70 | |||
| 1364 | WinRAR.exe | C:\Users\admin\Desktop\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02\VCRUNTIME140.dll | executable | |
MD5:D3ACD80CD5759CFD9AC4EB0F1900AD9A | SHA256:B490A65A7A23AB2387339F081B8F1D9665A13B03023DBB3BCAFE016324857ABE | |||
| 1364 | WinRAR.exe | C:\Users\admin\Desktop\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02\MSVCP140.dll | executable | |
MD5:79A9400C71C08209753268941915165C | SHA256:7E335A64C1A3F476E2B2D25FCD326E692907964D710D7938639BD7B4B9F9A91A | |||
| 1364 | WinRAR.exe | C:\Users\admin\Desktop\PROCESO_POR_DAÑOS_Y_PERJUICIO_JUZGADO_02\libssl-1_1-x64.dll | executable | |
MD5:87DF65426C8FF43297AD733C5A8038CD | SHA256:49C810B8ADE20F43142012F4CA26650A9A054CD74AA6BF12ABFE90C1736DE5C2 | |||
| 4416 | 04 PROCESO FISCAL.exe | C:\ProgramData\ServerTls_v1\SoftwareLog.dll | executable | |
MD5:138AA79B69C1D73B654BD4EDFE7CE6BC | SHA256:26D73269784F077C32ABD67A8C7FB2CB521499450E1333D5BBD99CD9B6F38C70 | |||
| 4416 | 04 PROCESO FISCAL.exe | C:\ProgramData\ServerTls_v1\libssl-1_1-x64.dll | executable | |
MD5:87DF65426C8FF43297AD733C5A8038CD | SHA256:49C810B8ADE20F43142012F4CA26650A9A054CD74AA6BF12ABFE90C1736DE5C2 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
2756 | backgroundTaskHost.exe | GET | 200 | 162.159.142.9:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | unknown | binary | 471 b | whitelisted |
7068 | svchost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
7808 | backgroundTaskHost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | US | binary | 313 b | whitelisted |
7068 | svchost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
7552 | backgroundTaskHost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | US | binary | 471 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
8100 | RUXIMICS.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
6016 | MoUsoCoreWorker.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5224 | SearchApp.exe | 92.123.104.6:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
7068 | svchost.exe | 20.190.160.67:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
7068 | svchost.exe | 172.66.2.5:80 | ocsp.digicert.com | — | US | whitelisted |
7808 | backgroundTaskHost.exe | 92.123.104.6:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
7808 | backgroundTaskHost.exe | 172.66.2.5:80 | ocsp.digicert.com | — | US | whitelisted |
3464 | svchost.exe | 172.211.123.249:443 | client.wns.windows.com | MICROSOFT-CORP-MSN-AS-BLOCK | FR | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
www.bing.com |
| whitelisted |
google.com |
| whitelisted |
login.live.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
arc.msn.com |
| whitelisted |
fd.api.iris.microsoft.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
— | — | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |
2428 | svchost.exe | Potentially Bad Traffic | ET DYN_DNS DYNAMIC_DNS Query to a *.mysynology .net Domain |
8060 | PortInterface32.exe | Domain Observed Used for C2 Detected | ET MALWARE Generic AsyncRAT/zgRAT Style SSL Cert |