ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
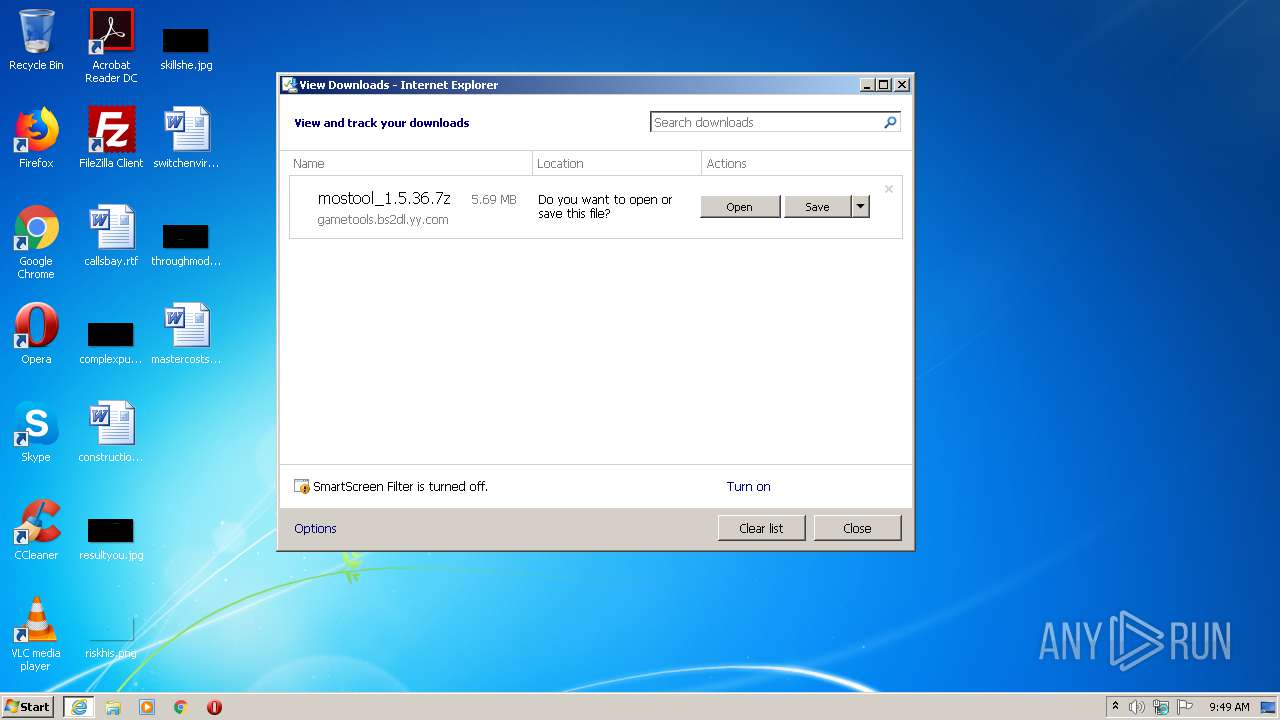
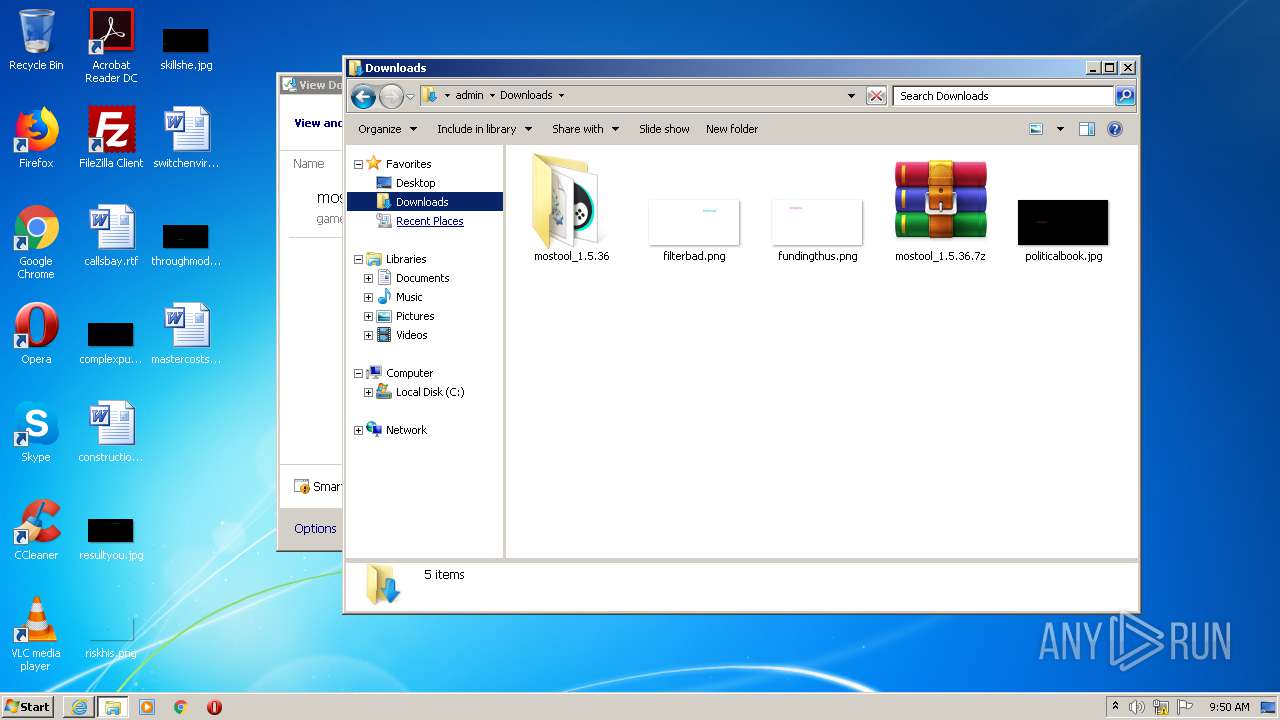
| URL: | http://gametools.bs2dl.yy.com/pc/mostool/mostool/mostool_1.5.36.7z |
| Full analysis: | https://app.any.run/tasks/28601ffd-38f2-46bb-aca1-53ea811d2acb |
| Verdict: | Malicious activity |
| Analysis date: | June 19, 2020, 08:49:04 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Indicators: | |
| MD5: | 0F7946D35CAB647686B2F3903265C05D |
| SHA1: | 1131FA9405626AC8C3F961F1ED10CBD27AE4794D |
| SHA256: | B59CD3415DD66256A33FDB72CC597330629DC530DDF66996F669EDE43E44AF8B |
| SSDEEP: | 3:N1KZEIp8BmwsKmRRJGNKJGNKJ/Chf:C6Ip8BSBRONNNa4f |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 656 | "C:\Windows\system32\SearchProtocolHost.exe" Global\UsGthrFltPipeMssGthrPipe2_ Global\UsGthrCtrlFltPipeMssGthrPipe2 1 -2147483646 "Software\Microsoft\Windows Search" "Mozilla/4.0 (compatible; MSIE 6.0; Windows NT; MS Search 4.0 Robot)" "C:\ProgramData\Microsoft\Search\Data\Temp\usgthrsvc" "DownLevelDaemon" | C:\Windows\System32\SearchProtocolHost.exe | — | SearchIndexer.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Microsoft Windows Search Protocol Host Exit code: 0 Version: 7.00.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
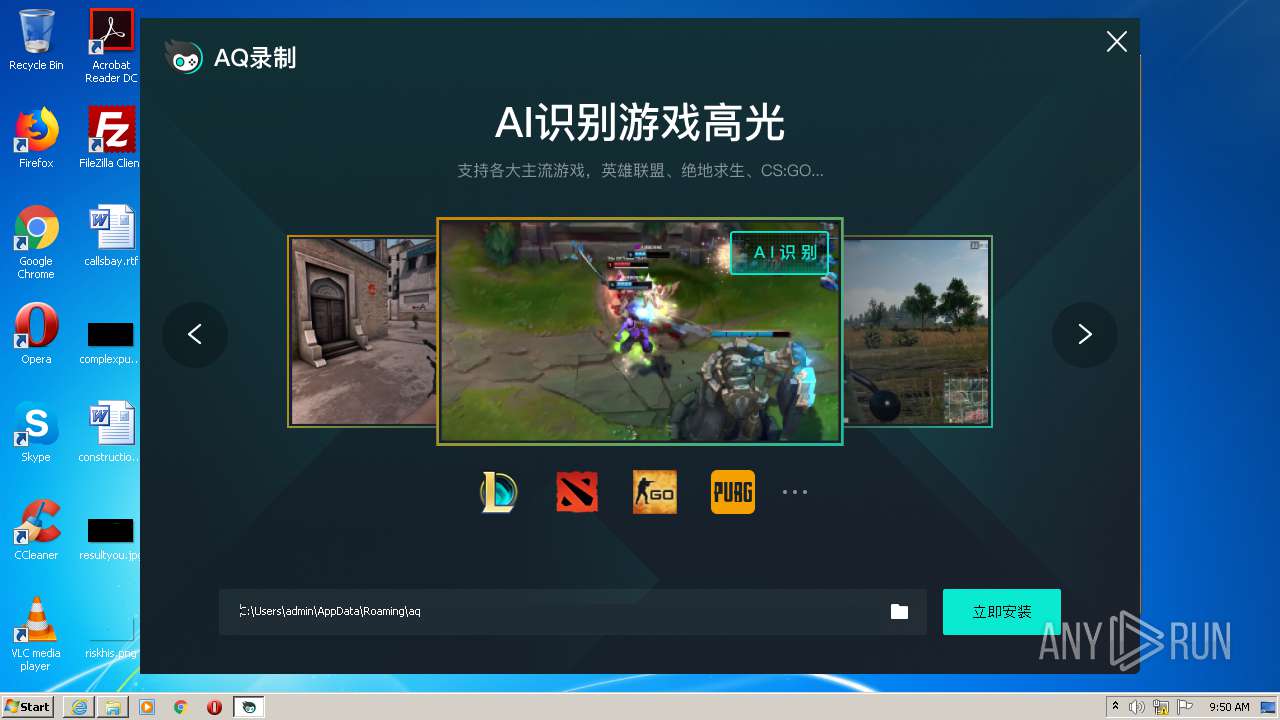
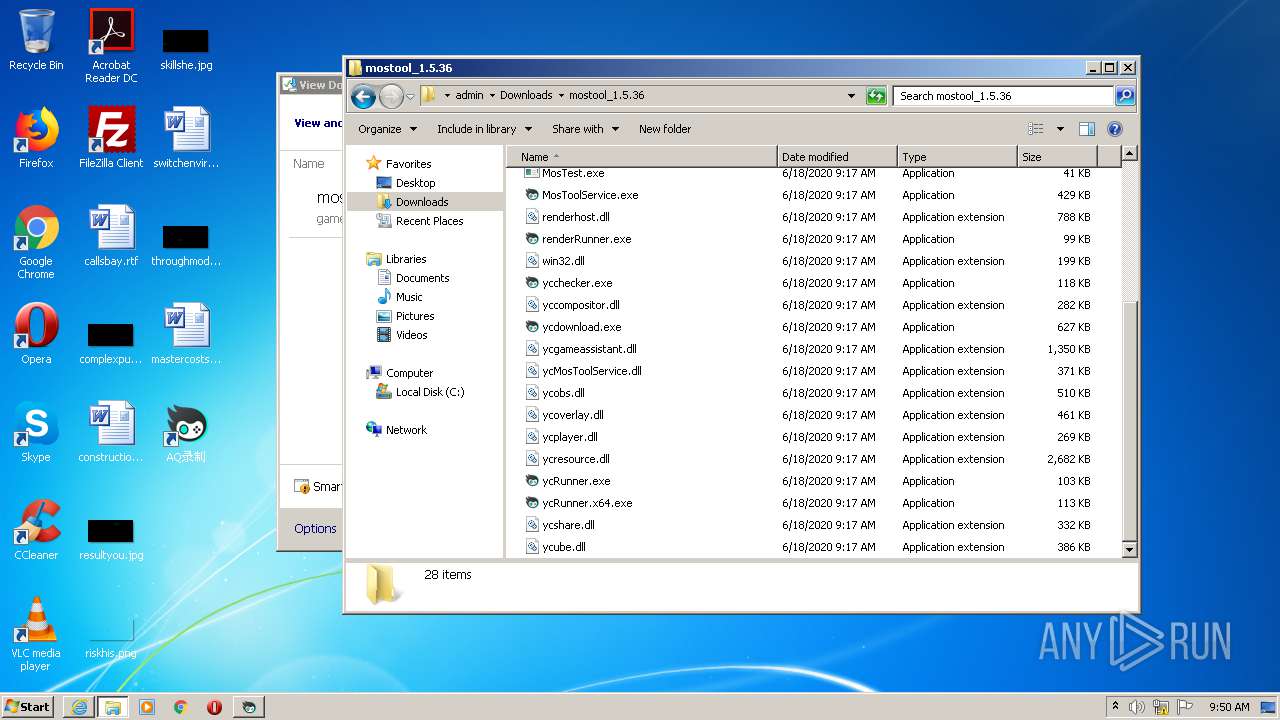
| 2108 | "C:\Users\admin\Downloads\mostool_1.5.36\AQ.exe" | C:\Users\admin\Downloads\mostool_1.5.36\AQ.exe | explorer.exe | ||||||||||||
User: admin Company: YY Inc. Integrity Level: MEDIUM Description: AQ Exit code: 0 Version: 1.5.36 Modules
| |||||||||||||||
| 2228 | C:\Users\admin\Downloads\mostool_1.5.36\AQ.exe | C:\Users\admin\Downloads\mostool_1.5.36\AQ.exe | mos171.tmp | ||||||||||||
User: admin Company: YY Inc. Integrity Level: MEDIUM Description: AQ Exit code: 0 Version: 1.5.36 Modules
| |||||||||||||||
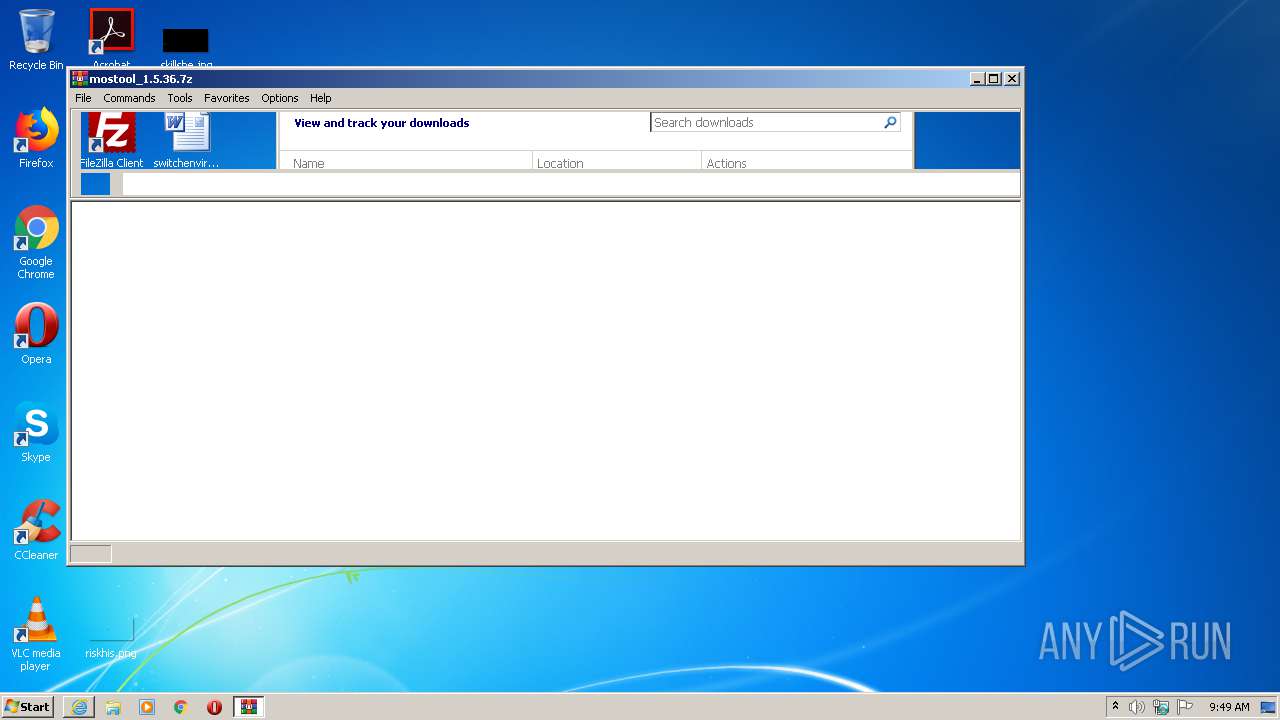
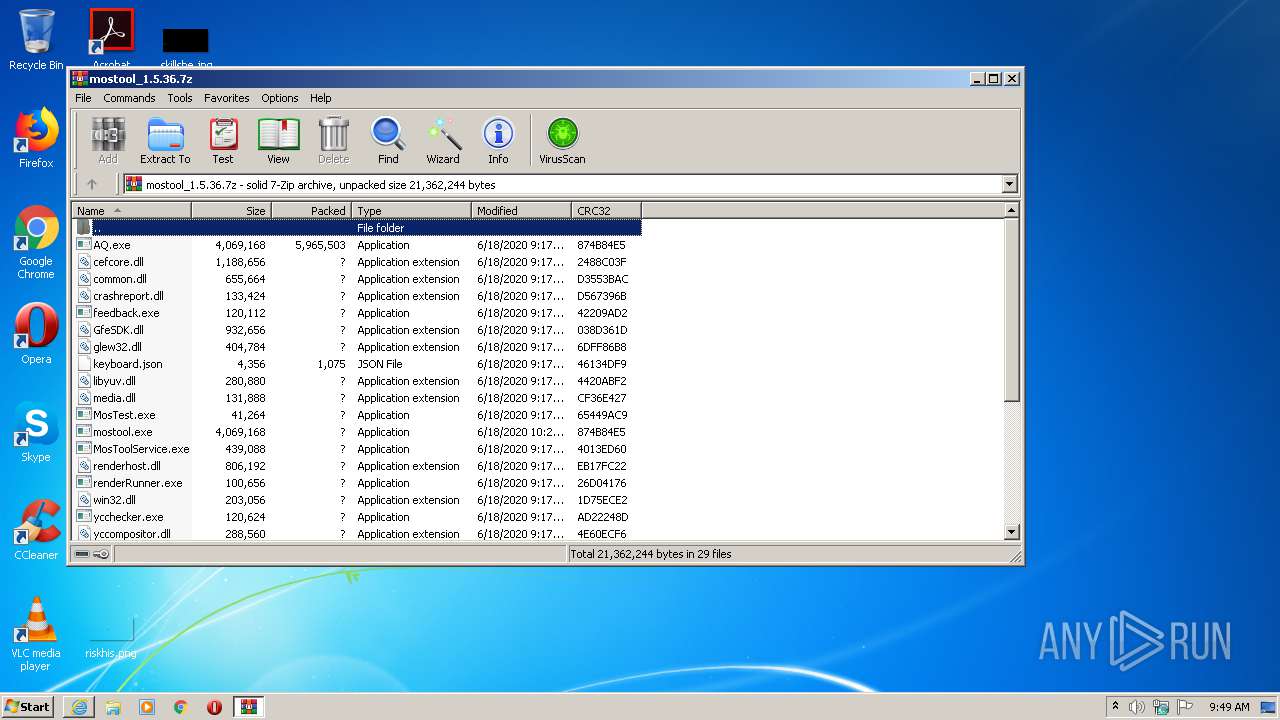
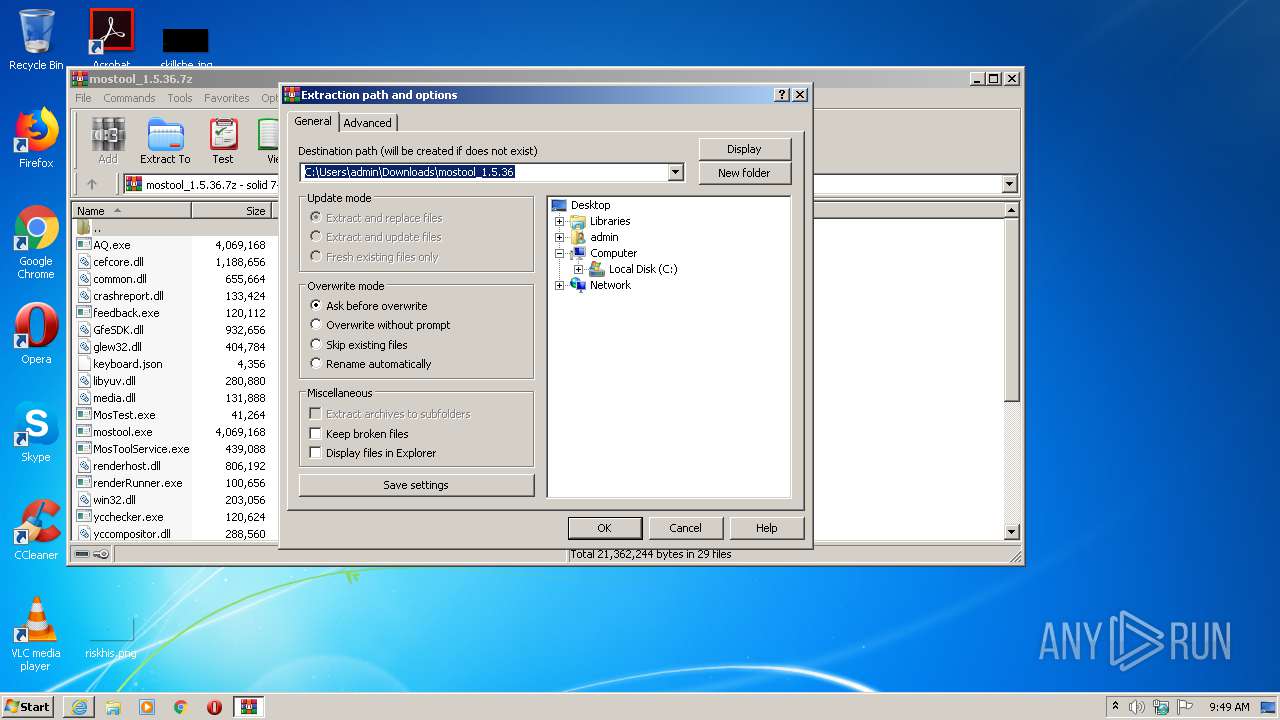
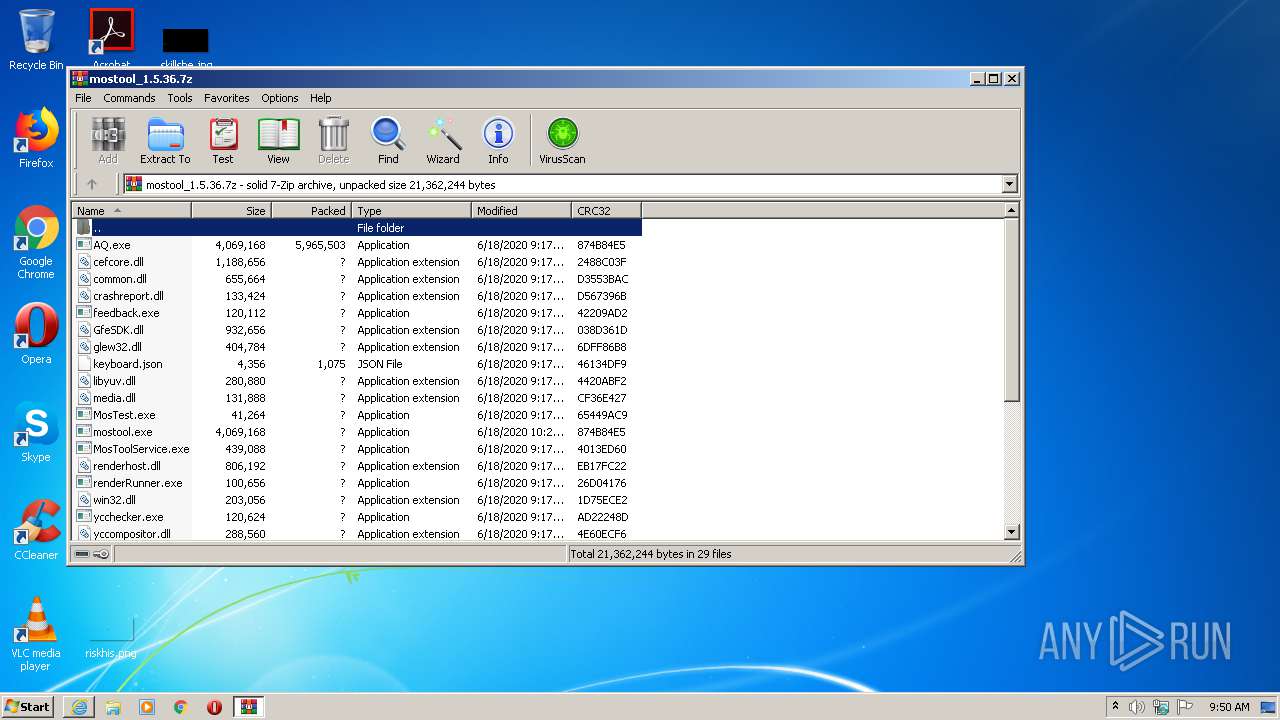
| 2388 | "C:\Program Files\WinRAR\WinRAR.exe" "C:\Users\admin\Downloads\mostool_1.5.36.7z" | C:\Program Files\WinRAR\WinRAR.exe | iexplore.exe | ||||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Exit code: 0 Version: 5.60.0 Modules
| |||||||||||||||
| 2468 | "C:\Program Files\Internet Explorer\iexplore.exe" SCODEF:2700 CREDAT:267521 /prefetch:2 | C:\Program Files\Internet Explorer\iexplore.exe | iexplore.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Internet Explorer Exit code: 0 Version: 11.00.9600.16428 (winblue_gdr.131013-1700) Modules
| |||||||||||||||
| 2512 | "C:\Windows\explorer.exe" | C:\Windows\explorer.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Explorer Exit code: 1 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
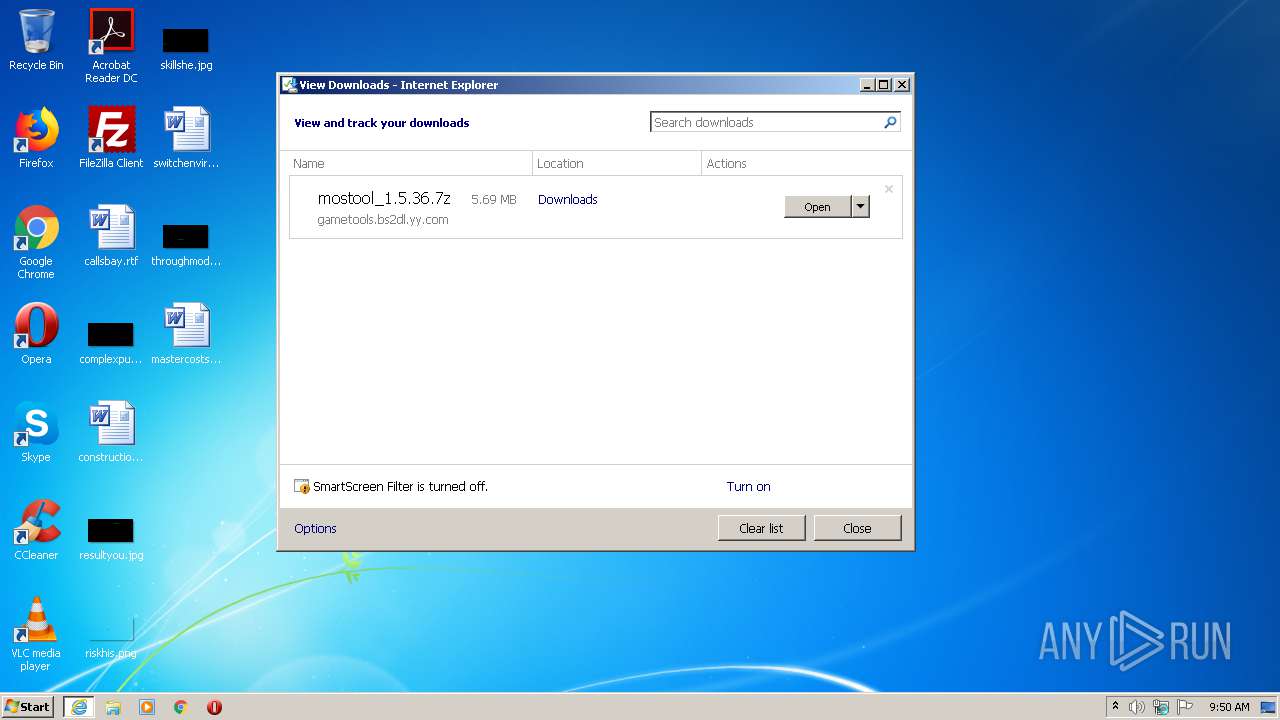
| 2700 | "C:\Program Files\Internet Explorer\iexplore.exe" "http://gametools.bs2dl.yy.com/pc/mostool/mostool/mostool_1.5.36.7z" | C:\Program Files\Internet Explorer\iexplore.exe | explorer.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Internet Explorer Exit code: 0 Version: 11.00.9600.16428 (winblue_gdr.131013-1700) Modules
| |||||||||||||||
| 2940 | "C:\Users\admin\Downloads\mostool_1.5.36\ycRunner.exe" | C:\Users\admin\Downloads\mostool_1.5.36\ycRunner.exe | — | explorer.exe | |||||||||||
User: admin Company: YY Inc. Integrity Level: MEDIUM Description: AQ Exit code: 0 Version: 1.5.36 Modules
| |||||||||||||||
| 3588 | "C:\Users\admin\AppData\Local\Temp\mos171.tmp" replace C:/Users/admin/Downloads/mostool_1.5.36/mostool.exe \"\" 5 1 -- C:/Users/admin/Downloads/mostool_1.5.36/AQ.exe | C:\Users\admin\AppData\Local\Temp\mos171.tmp | — | mostool.exe | |||||||||||
User: admin Company: YY Inc. Integrity Level: MEDIUM Description: AQ Exit code: 1 Version: 1.5.36 Modules
| |||||||||||||||
| 3948 | "C:\Users\admin\Downloads\mostool_1.5.36\mostool.exe" | C:\Users\admin\Downloads\mostool_1.5.36\mostool.exe | — | explorer.exe | |||||||||||
User: admin Company: YY Inc. Integrity Level: MEDIUM Description: AQ Exit code: 0 Version: 1.5.36 Modules
| |||||||||||||||
| (PID) Process: | (2700) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\UrlBlockManager |
| Operation: | write | Name: | NextCheckForUpdateLowDateTime |
Value: 2546818098 | |||
| (PID) Process: | (2700) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\UrlBlockManager |
| Operation: | write | Name: | NextCheckForUpdateHighDateTime |
Value: 30819862 | |||
| (PID) Process: | (2700) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Content |
| Operation: | write | Name: | CachePrefix |
Value: | |||
| (PID) Process: | (2700) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Cookies |
| Operation: | write | Name: | CachePrefix |
Value: Cookie: | |||
| (PID) Process: | (2700) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\History |
| Operation: | write | Name: | CachePrefix |
Value: Visited: | |||
| (PID) Process: | (2700) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Main |
| Operation: | write | Name: | CompatibilityFlags |
Value: 0 | |||
| (PID) Process: | (2700) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings |
| Operation: | write | Name: | ProxyEnable |
Value: 0 | |||
| (PID) Process: | (2700) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\Connections |
| Operation: | write | Name: | SavedLegacySettings |
Value: 46000000A1000000010000000000000000000000000000000000000000000000C0E333BBEAB1D301000000000000000000000000020000001700000000000000FE800000000000007D6CB050D9C573F70B000000000000006D00330032005C004D00530049004D004700330032002E0064006C000100000004AA400014AA4000040000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000002000000C0A8016400000000000000000000000000000000000000000800000000000000805D3F00983740000008000002000000000000600000002060040000B8A94000020000008802000060040000B8A9400004000000F8010000B284000088B64000B84B400043003A000000000000000000000000000000000000000000 | |||
| (PID) Process: | (2700) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | UNCAsIntranet |
Value: 0 | |||
| (PID) Process: | (2700) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | AutoDetect |
Value: 1 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2468 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Low\Content.IE5\MFAQUS6V\mostool_1.5.36[1].7z | — | |
MD5:— | SHA256:— | |||
| 2468 | iexplore.exe | C:\Users\admin\Downloads\mostool_1.5.36.7z.tj2b8bt.partial | — | |
MD5:— | SHA256:— | |||
| 2700 | iexplore.exe | C:\Users\admin\AppData\Local\Temp\~DF62B95C5778974D26.TMP | — | |
MD5:— | SHA256:— | |||
| 2700 | iexplore.exe | C:\Users\admin\Downloads\mostool_1.5.36.7z.tj2b8bt.partial:Zone.Identifier | — | |
MD5:— | SHA256:— | |||
| 2700 | iexplore.exe | C:\Users\admin\Downloads\mostool_1.5.36.7z | — | |
MD5:— | SHA256:— | |||
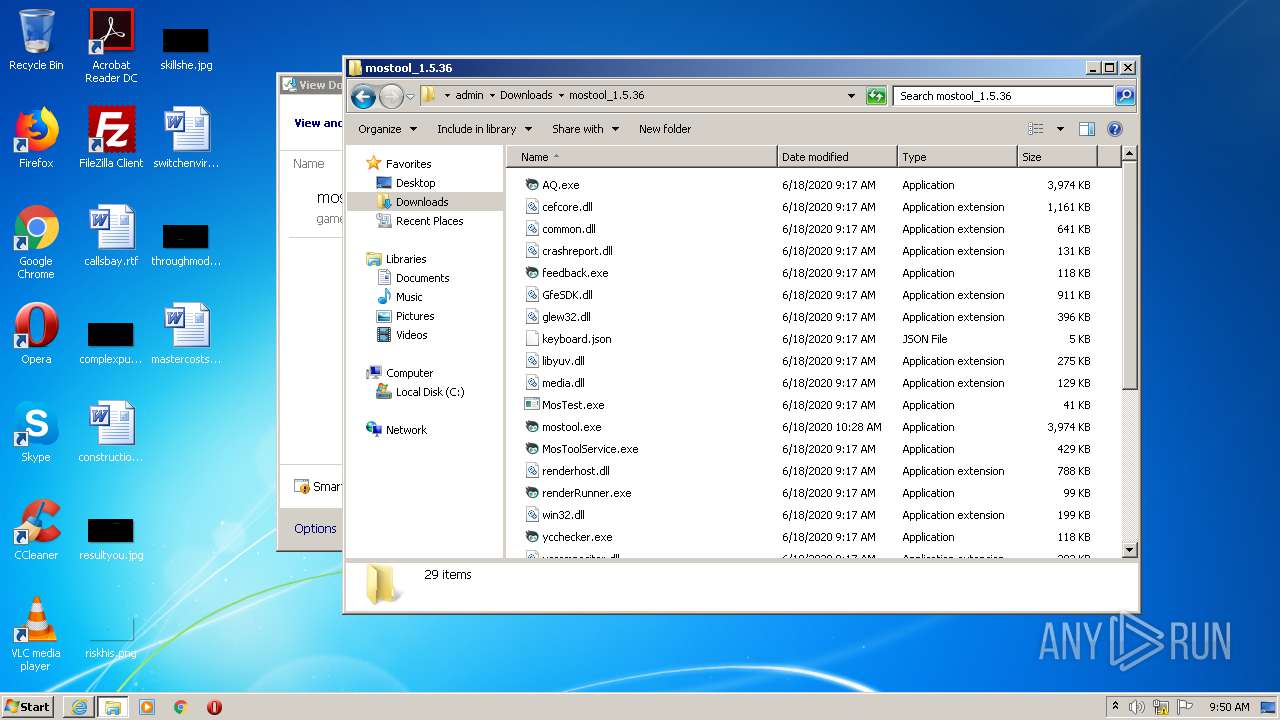
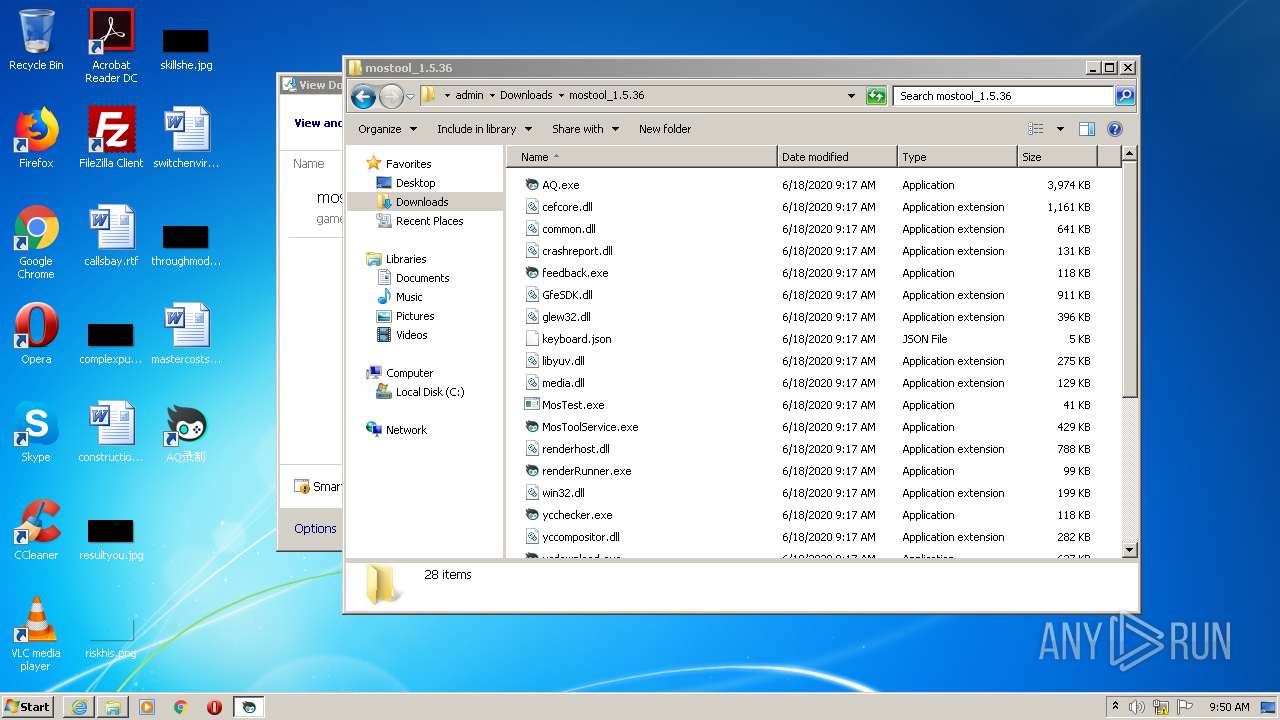
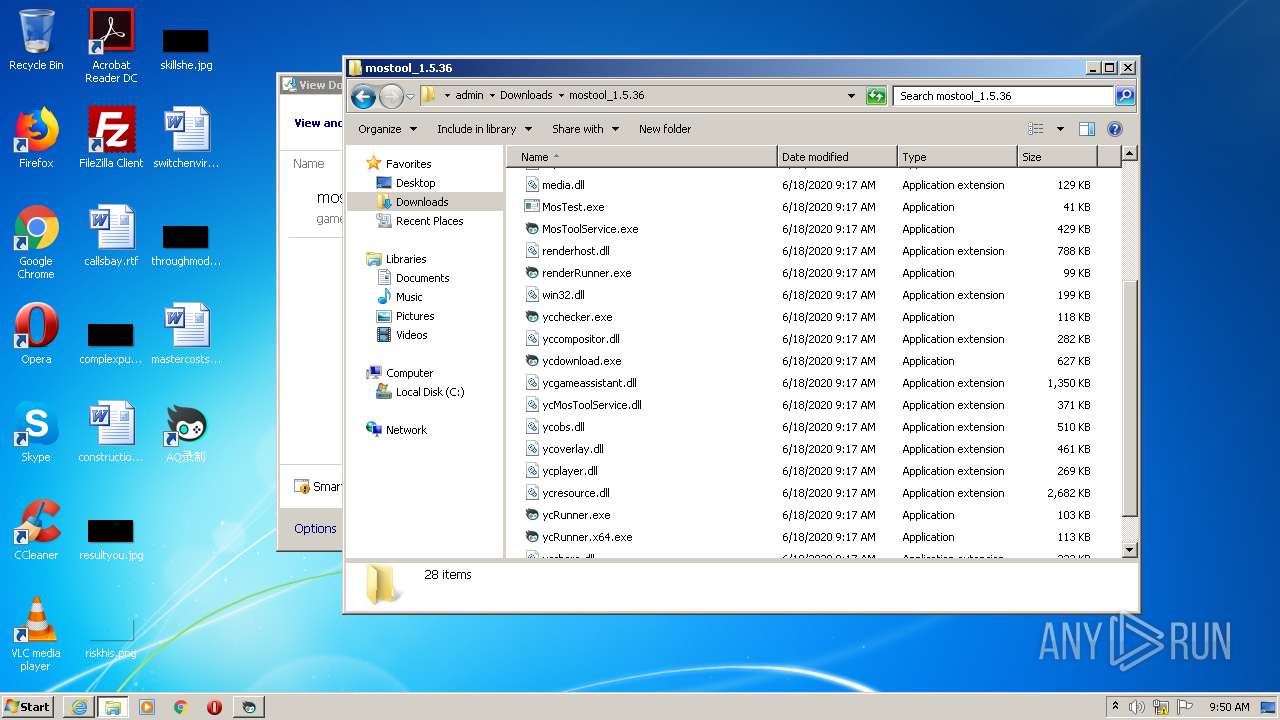
| 2388 | WinRAR.exe | C:\Users\admin\Downloads\mostool_1.5.36\feedback.exe | executable | |
MD5:7A404E523BE930D2273C0D7DB5D5E067 | SHA256:5AA3313042F9C4F6CC0BCB99B222C1E1CAF58DFAC153B43E4D8BF51A9BDAF752 | |||
| 2700 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Internet Explorer\Recovery\Active\{C385323F-B209-11EA-AA5F-5254004A04AF}.dat | binary | |
MD5:2DDC75CF6223EAA5001E21558798F091 | SHA256:5D6945B383D36F88C524D9B05C7AA76E023B4B54C13A1632AD1EAC2B21C55D64 | |||
| 2388 | WinRAR.exe | C:\Users\admin\Downloads\mostool_1.5.36\AQ.exe | executable | |
MD5:777FC4D53D460624FBF391A9229F4E43 | SHA256:204621D4F6C2F9D34EFB310CD530E4AAB31480F69844CA28A4AAAF08942028B4 | |||
| 2388 | WinRAR.exe | C:\Users\admin\Downloads\mostool_1.5.36\common.dll | executable | |
MD5:730305CA3EE9633AF2F68F74212A4C84 | SHA256:1B51545A64D88572934E98B0CAAB536E7D660758778A13FE22A95B85C67A29D7 | |||
| 2388 | WinRAR.exe | C:\Users\admin\Downloads\mostool_1.5.36\mostool.exe | executable | |
MD5:777FC4D53D460624FBF391A9229F4E43 | SHA256:204621D4F6C2F9D34EFB310CD530E4AAB31480F69844CA28A4AAAF08942028B4 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
2700 | iexplore.exe | GET | 200 | 93.184.220.29:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTBL0V27RVZ7LBduom%2FnYB45SPUEwQU5Z1ZMIJHWMys%2BghUNoZ7OrUETfACEA8sEMlbBsCTf7jUSfg%2BhWk%3D | US | der | 1.47 Kb | whitelisted |
2468 | iexplore.exe | GET | 200 | 101.227.95.3:80 | http://gametools.bs2dl.yy.com/pc/mostool/mostool/mostool_1.5.36.7z | CN | compressed | 5.69 Mb | whitelisted |
2700 | iexplore.exe | GET | 200 | 93.184.220.29:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTBL0V27RVZ7LBduom%2FnYB45SPUEwQU5Z1ZMIJHWMys%2BghUNoZ7OrUETfACEA8sEMlbBsCTf7jUSfg%2BhWk%3D | US | der | 1.47 Kb | whitelisted |
2700 | iexplore.exe | GET | 200 | 93.184.220.29:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTBL0V27RVZ7LBduom%2FnYB45SPUEwQU5Z1ZMIJHWMys%2BghUNoZ7OrUETfACEA8sEMlbBsCTf7jUSfg%2BhWk%3D | US | der | 1.47 Kb | whitelisted |
— | — | GET | 200 | 47.246.43.230:80 | http://ocsp.dcocsp.cn/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAoEcNCWvIoSyJCm34Ju7Es%3D | US | der | 471 b | whitelisted |
— | — | GET | 200 | 47.246.43.230:80 | http://ocsp.dcocsp.cn/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSmVYFXwi%2FRq9wx3PKhB8lC%2FFYUyAQUkZ9eMRWuEJ%2BtYMH3wcyqSDQvDCYCEAEUJeOCVfhUnovVyuc9OKQ%3D | US | der | 471 b | whitelisted |
— | — | GET | 200 | 47.246.43.230:80 | http://ocsp.dcocsp.cn/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSmVYFXwi%2FRq9wx3PKhB8lC%2FFYUyAQUkZ9eMRWuEJ%2BtYMH3wcyqSDQvDCYCEAvOHgOR4SLslqJ8x8g3bFs%3D | US | der | 471 b | whitelisted |
— | — | GET | 200 | 47.246.43.230:80 | http://ocsp.dcocsp.cn/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAh%2BGPuPqpJ%2B6HYKDYmC9RI%3D | US | der | 471 b | whitelisted |
— | — | GET | 200 | 47.246.43.230:80 | http://ocsp.dcocsp.cn/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTHv1Dj%2BciPJEWH5JNtwL5Y07mRqwQUxBF%2BiECGwkG%2FZfMa4bRTQKOr7H0CEATNC7u01owJC%2FH8YIL9x9w%3D | US | der | 471 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
2468 | iexplore.exe | 101.227.95.3:80 | gametools.bs2dl.yy.com | China Telecom (Group) | CN | unknown |
2700 | iexplore.exe | 152.199.19.161:443 | iecvlist.microsoft.com | MCI Communications Services, Inc. d/b/a Verizon Business | US | whitelisted |
2700 | iexplore.exe | 93.184.220.29:80 | ocsp.digicert.com | MCI Communications Services, Inc. d/b/a Verizon Business | US | whitelisted |
2700 | iexplore.exe | 204.79.197.200:443 | ieonline.microsoft.com | Microsoft Corporation | US | whitelisted |
2108 | AQ.exe | 47.254.170.219:443 | hlog.hiido.com | Alibaba (China) Technology Co., Ltd. | US | unknown |
— | — | 47.246.43.230:80 | ocsp.dcocsp.cn | — | US | malicious |
2228 | AQ.exe | 47.254.170.219:443 | hlog.hiido.com | Alibaba (China) Technology Co., Ltd. | US | unknown |
2228 | AQ.exe | 101.227.95.3:443 | gametools.bs2dl.yy.com | China Telecom (Group) | CN | unknown |
2228 | AQ.exe | 162.62.4.226:443 | iupdateplf.yy.com | — | US | unknown |
Domain | IP | Reputation |
|---|---|---|
gametools.bs2dl.yy.com |
| unknown |
iecvlist.microsoft.com |
| whitelisted |
r20swj13mr.microsoft.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
hlog.hiido.com |
| unknown |
ocsp.dcocsp.cn |
| whitelisted |
ieonline.microsoft.com |
| whitelisted |
iupdateplf.yy.com |
| unknown |