ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
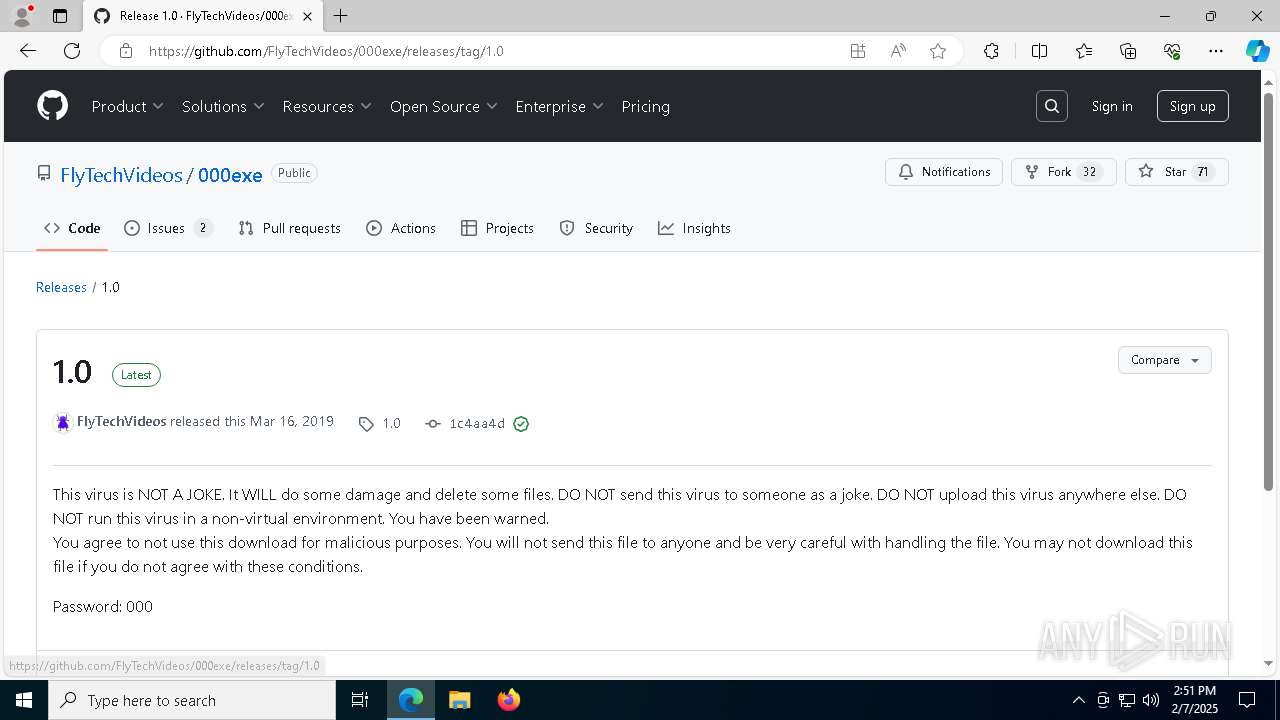
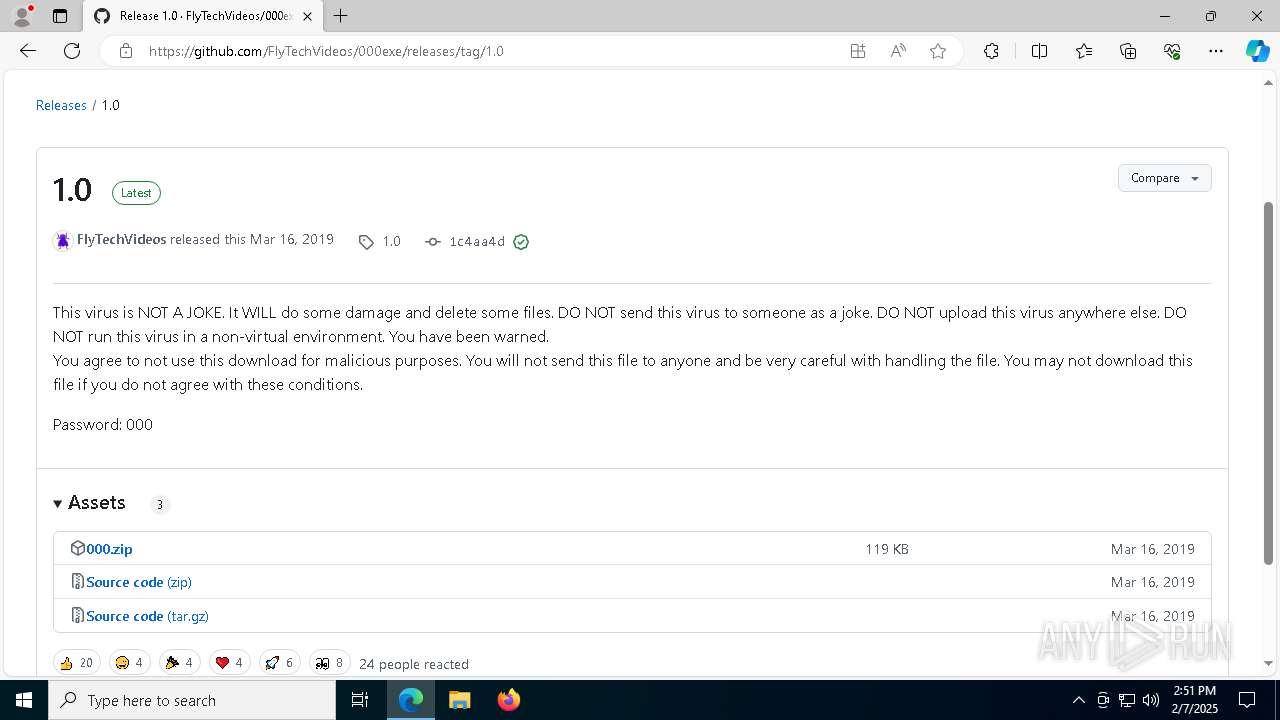
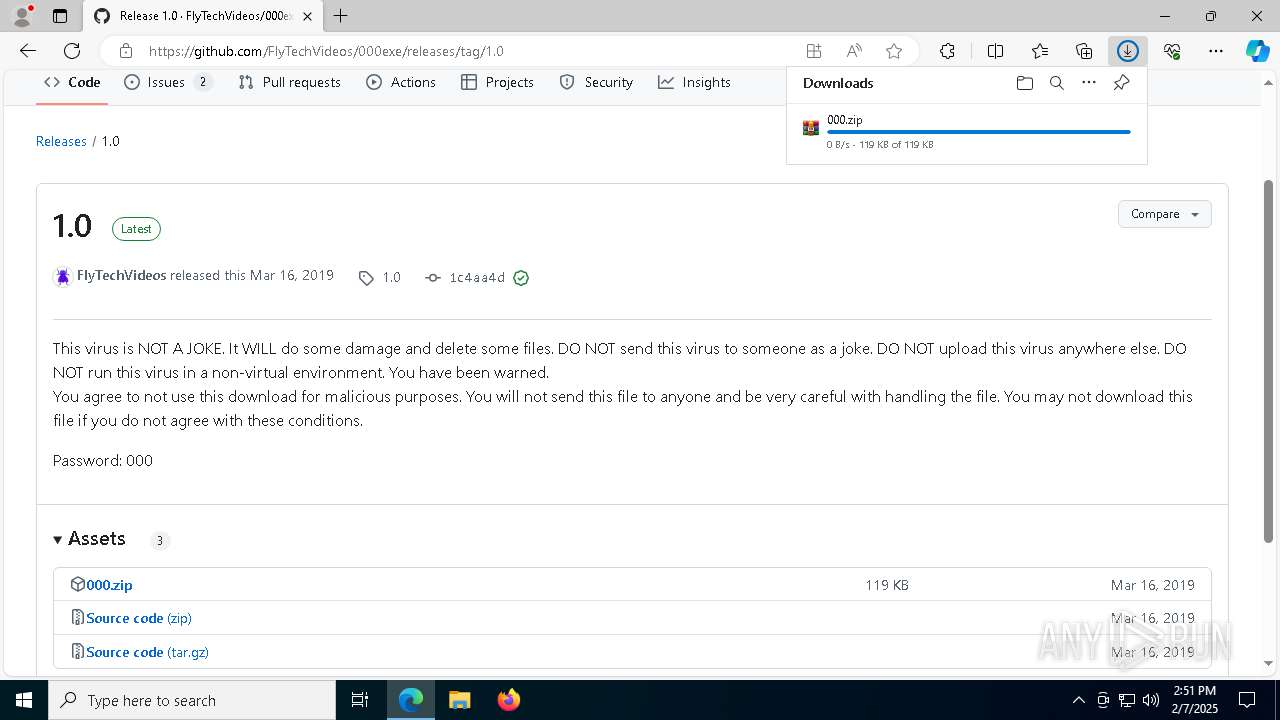
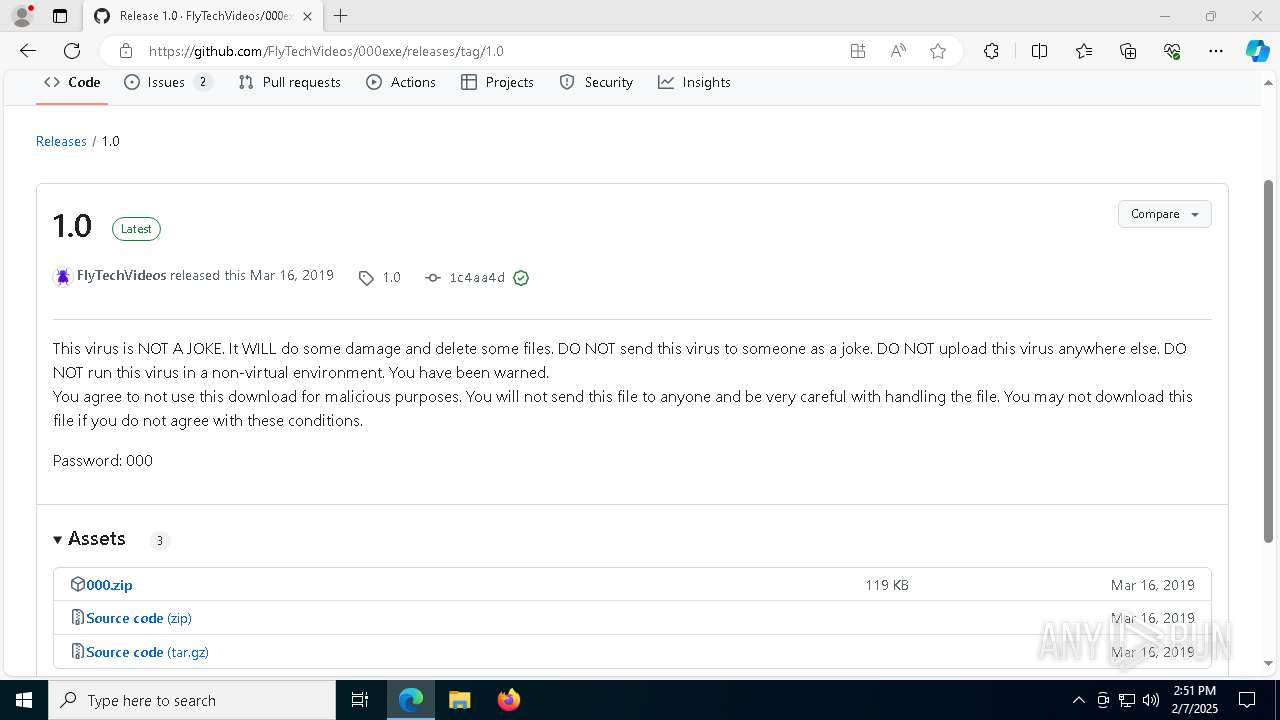
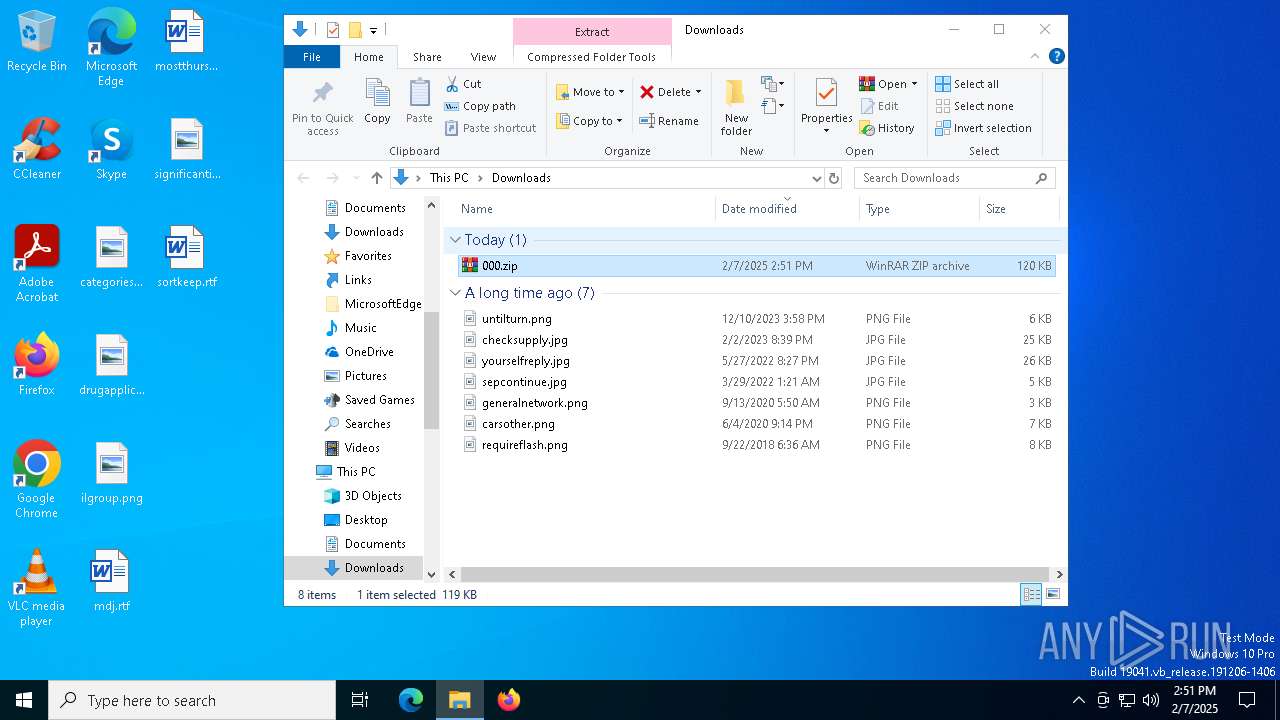
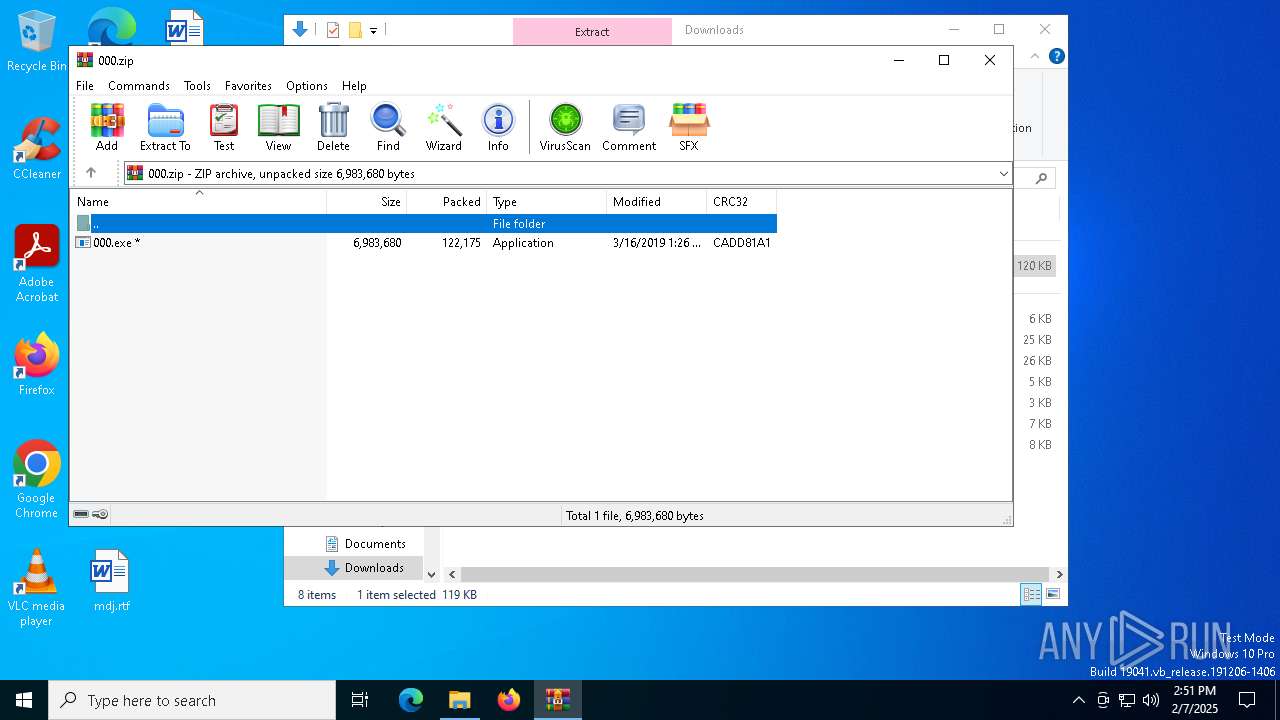
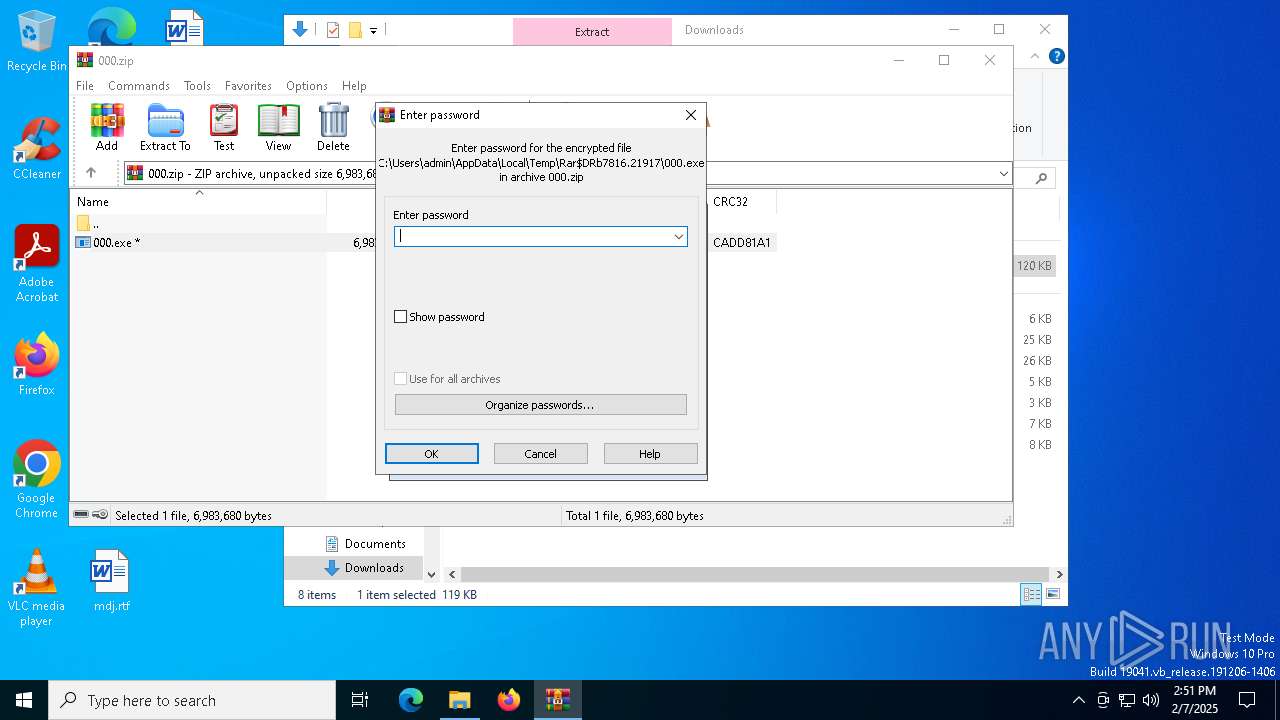
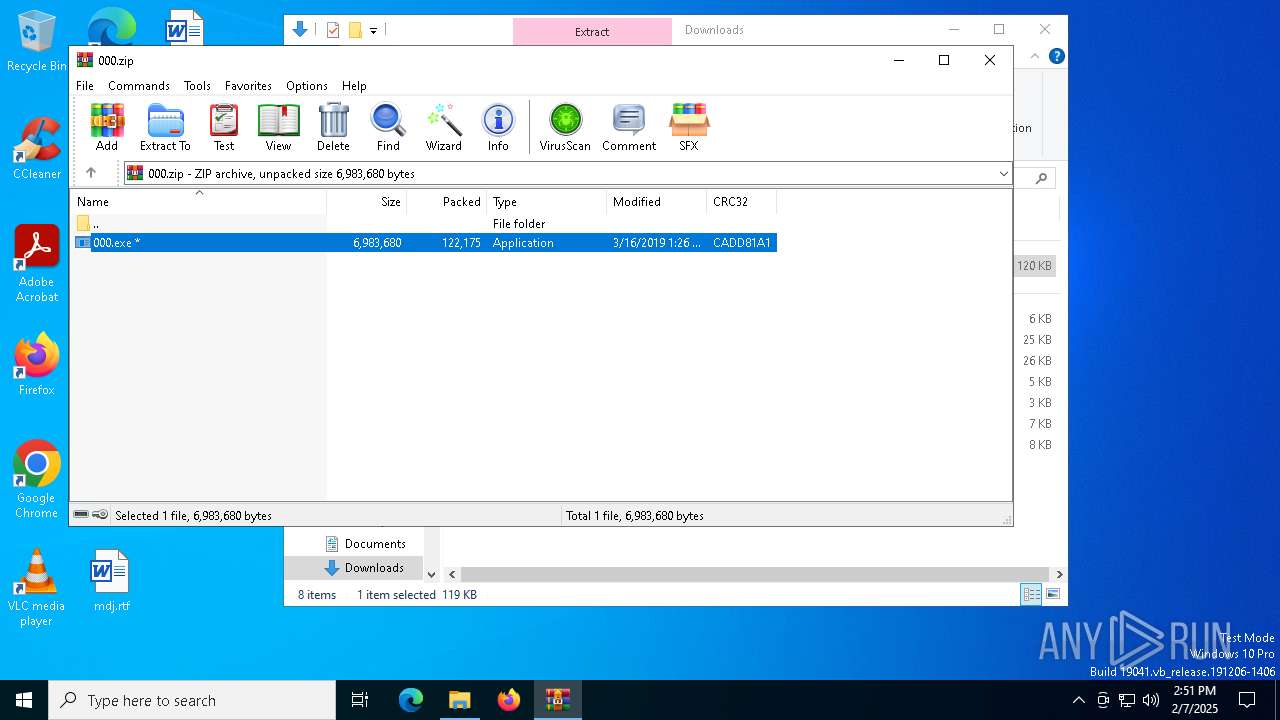
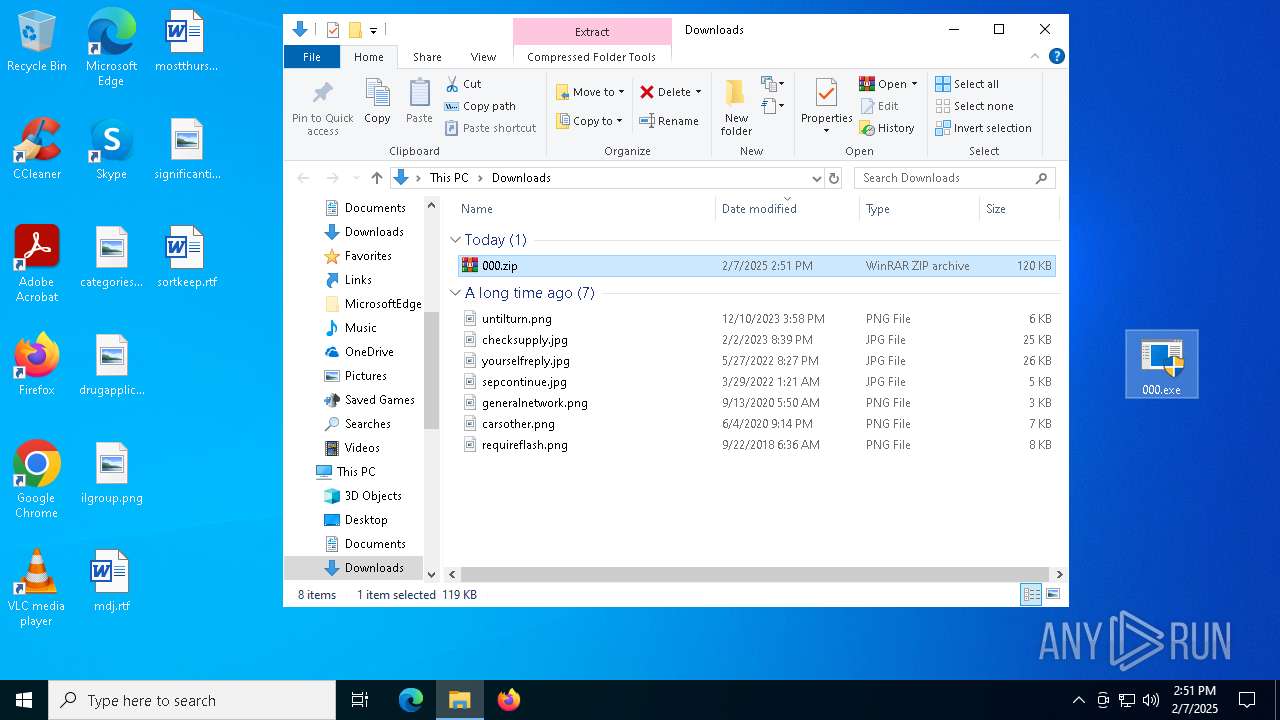
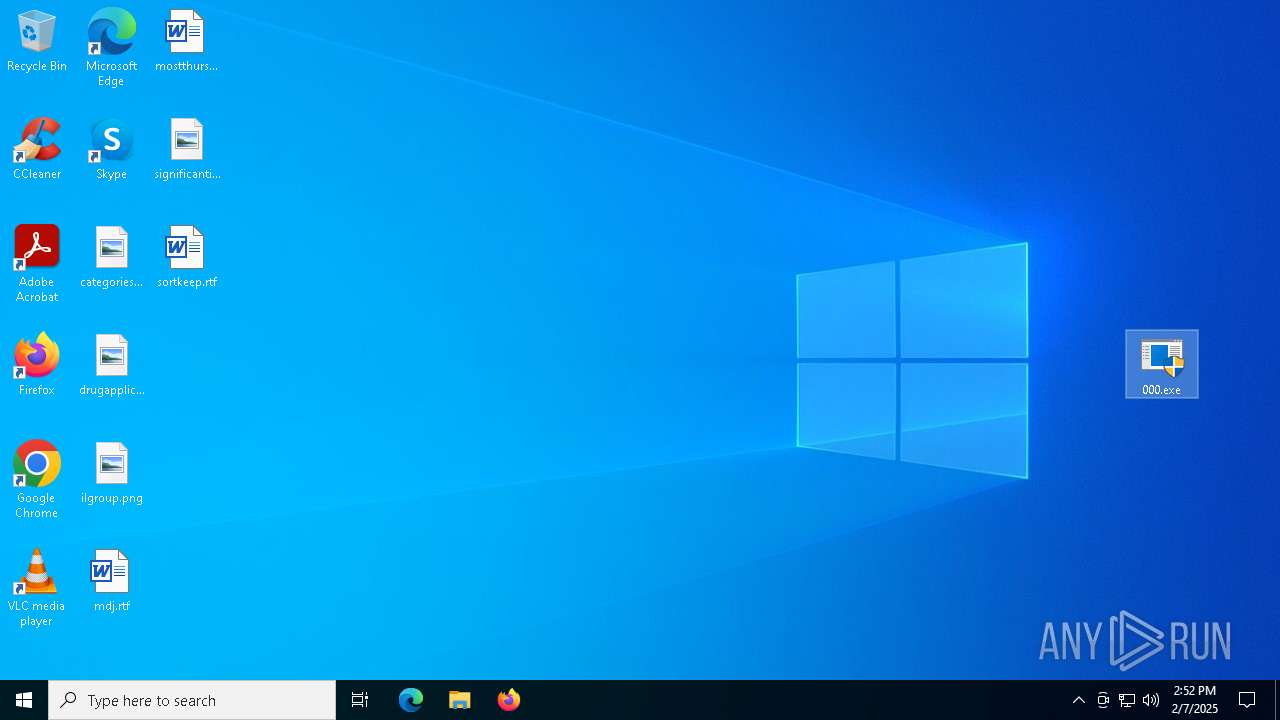
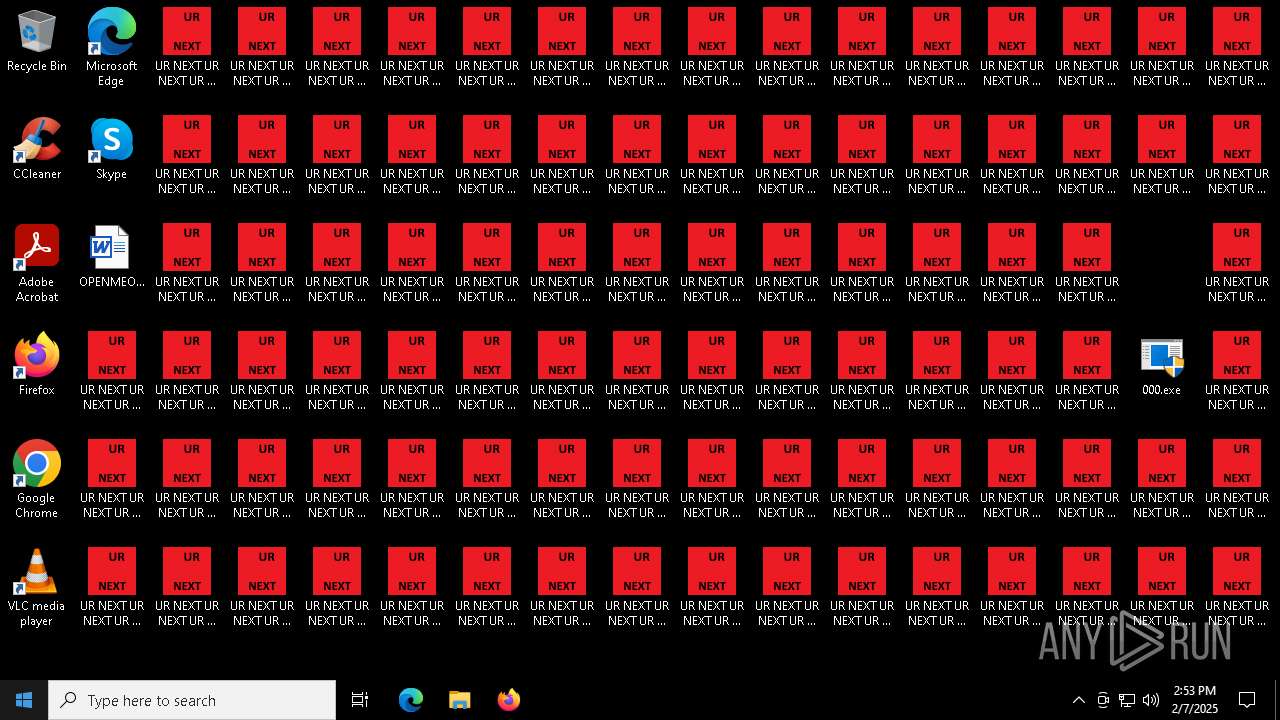
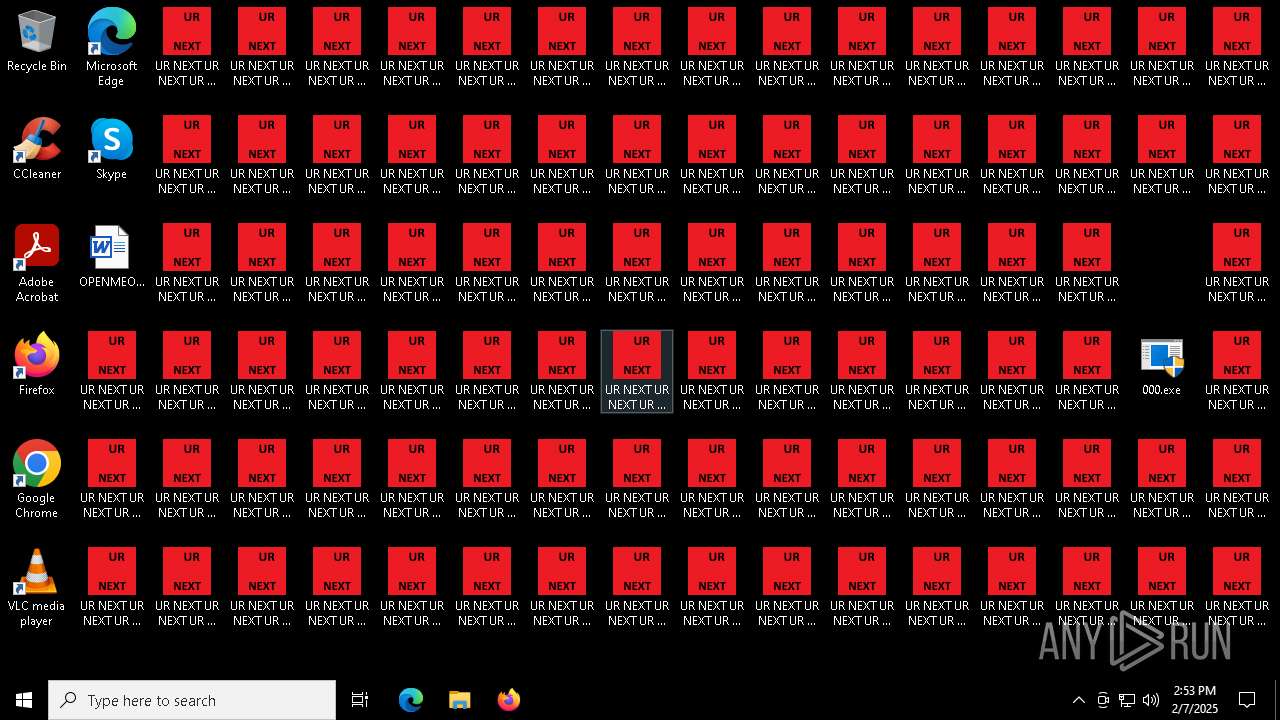
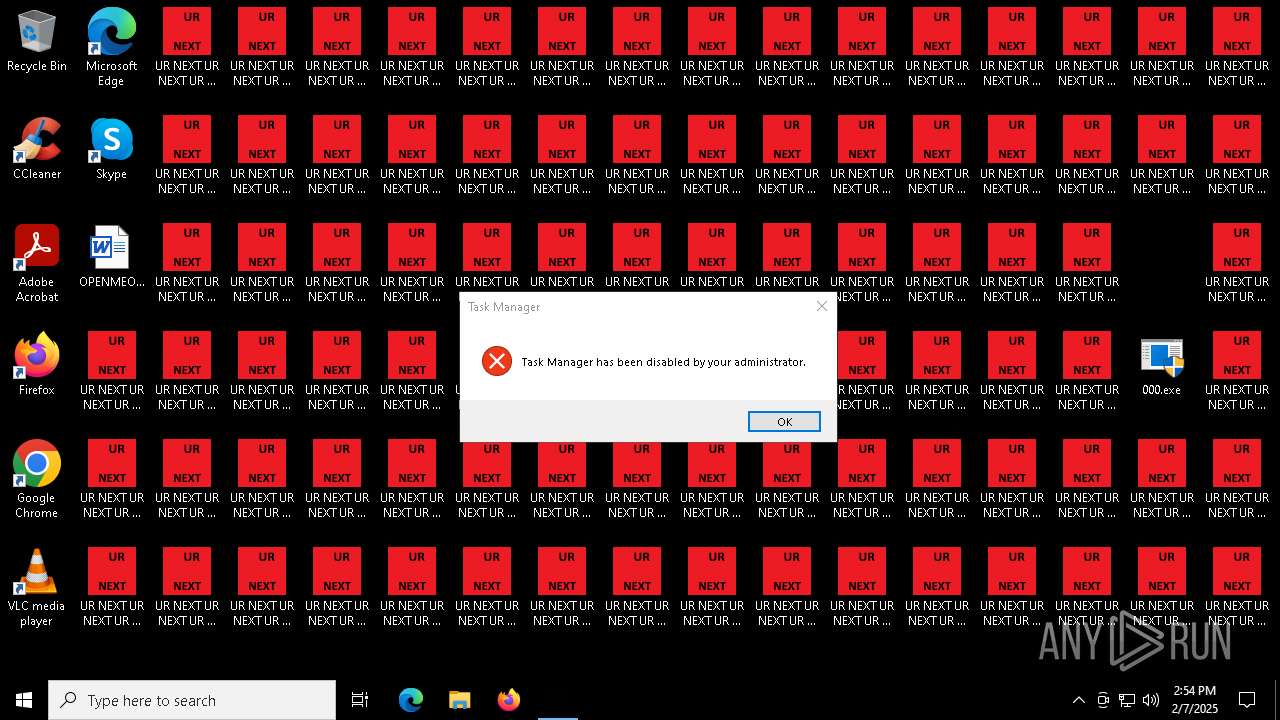
| URL: | https://github.com/FlyTechVideos/000exe |
| Full analysis: | https://app.any.run/tasks/afa6db19-a974-4909-b6b7-3b801b2e55a9 |
| Verdict: | Malicious activity |
| Analysis date: | February 07, 2025, 14:50:49 |
| OS: | Windows 10 Professional (build: 19045, 64 bit) |
| Tags: | |
| Indicators: | |
| MD5: | 95F16681F4E70E7ED7A92C5055D2691A |
| SHA1: | 3441A8DE7140716831828756E344E93DB1124D95 |
| SHA256: | B4922B329962DE74D7B1901115F60210B62F0EB88AA2B497C9C4D772D3774996 |
| SSDEEP: | 3:N8tEdFlagBAN6mAn:2uQSn |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
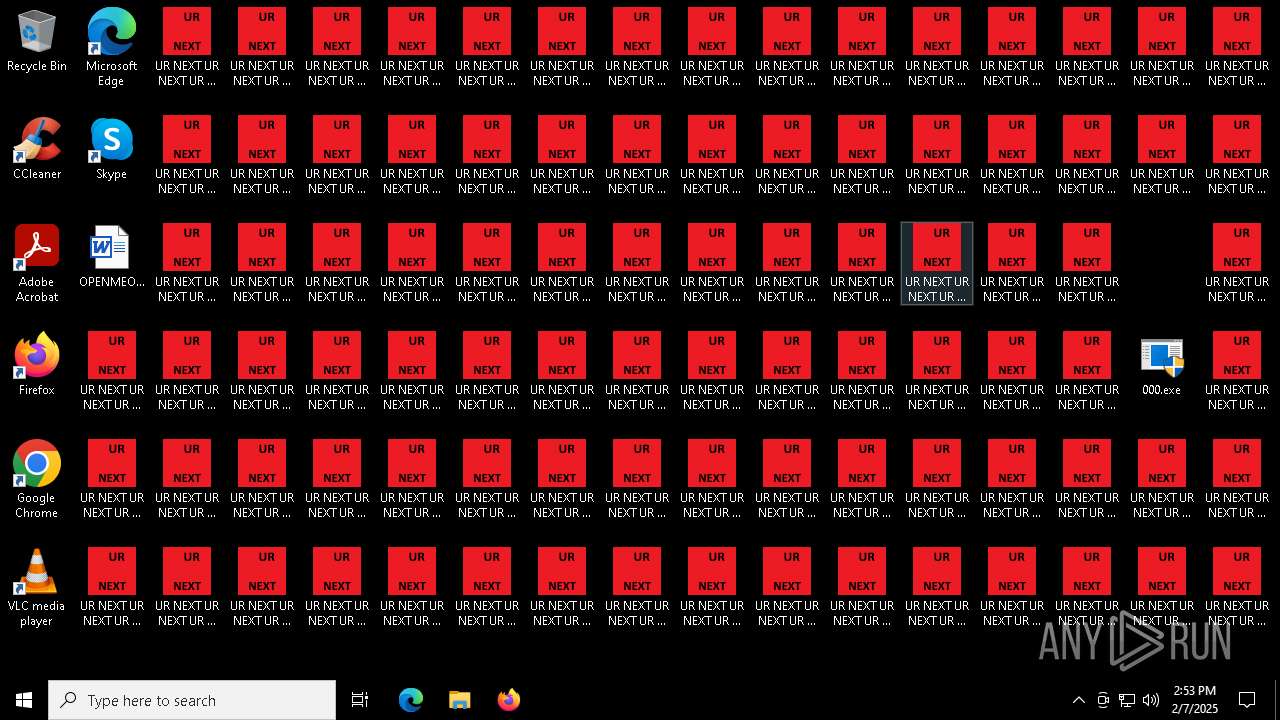
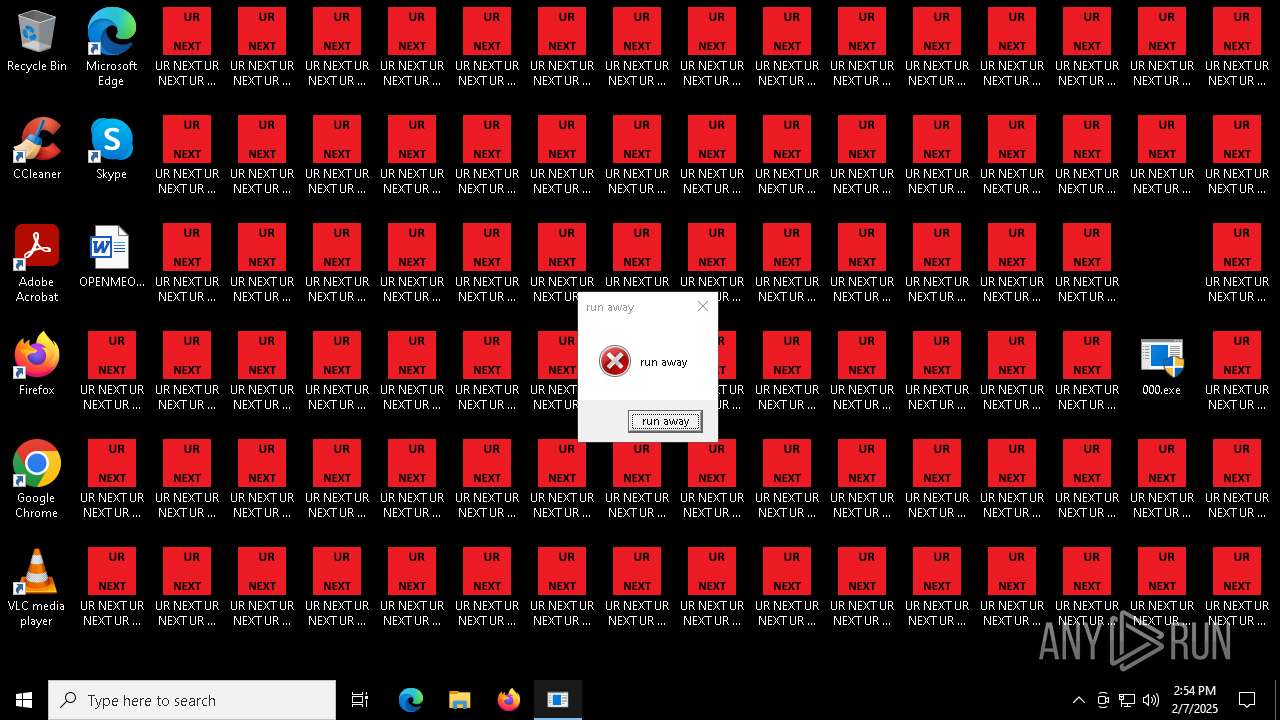
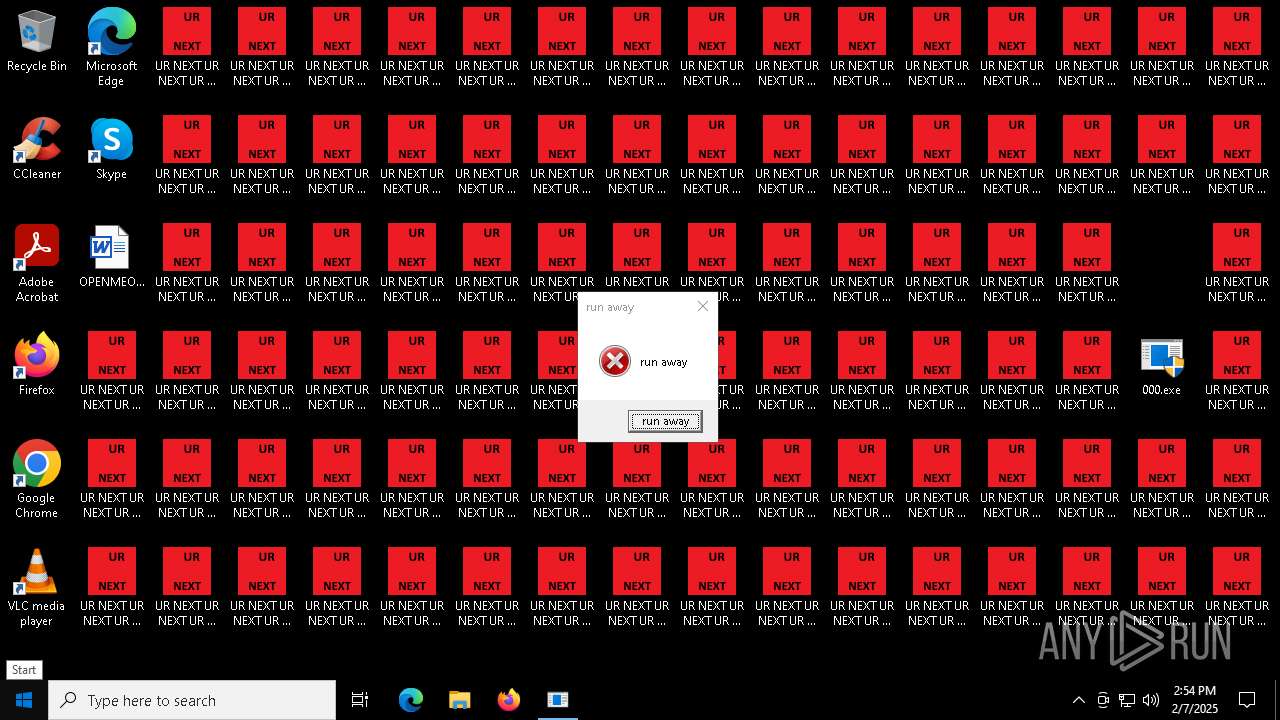
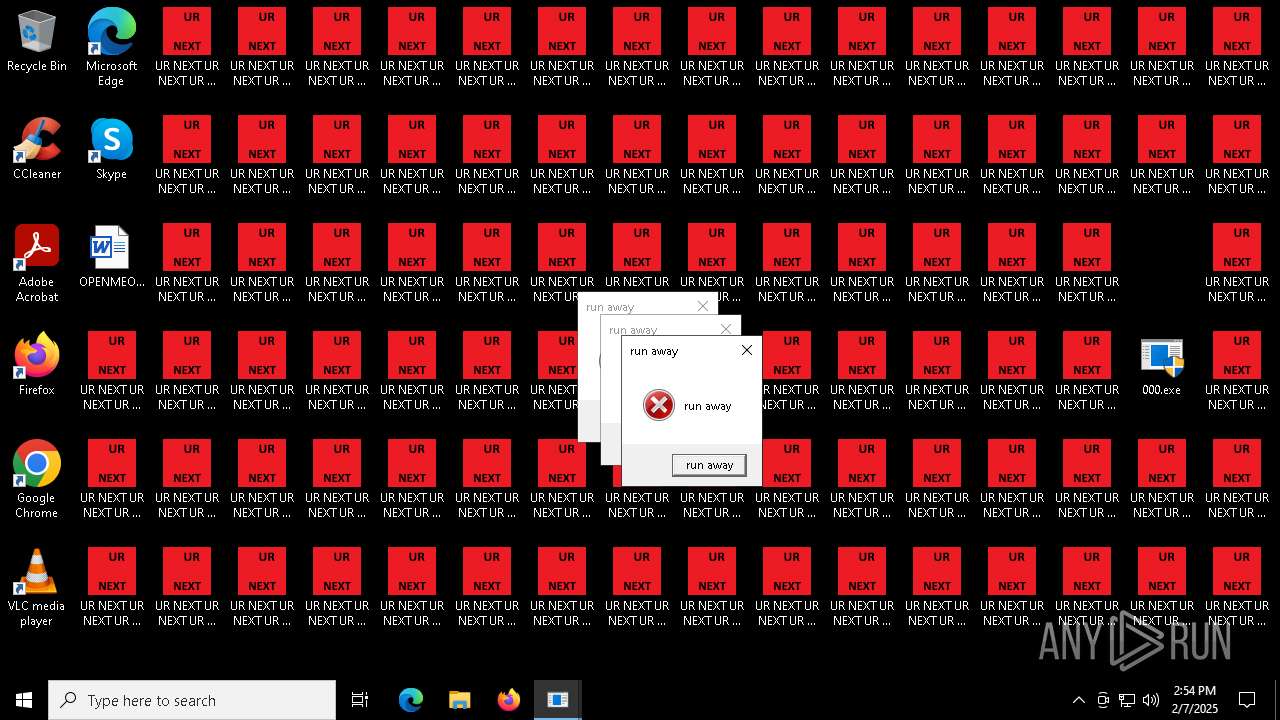
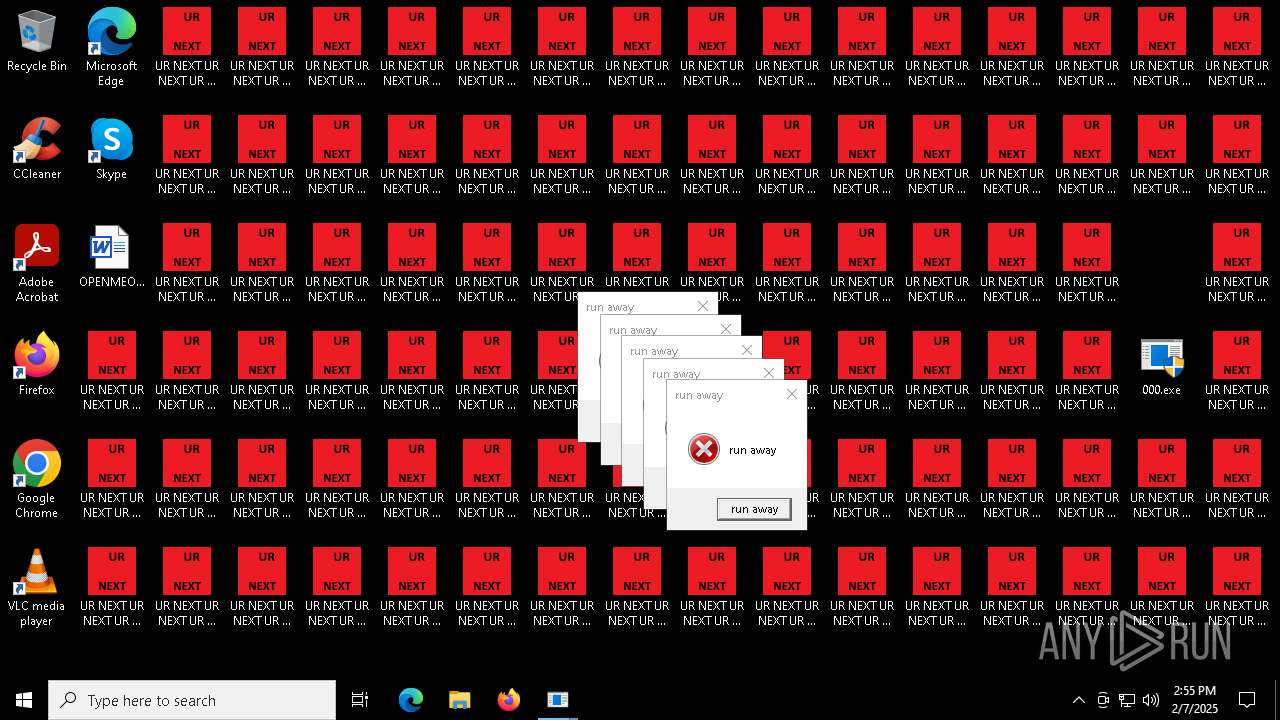
| 204 | runaway.exe | C:\Users\admin\AppData\Local\Temp\E4F1.tmp\runaway.exe | — | cmd.exe | |||||||||||
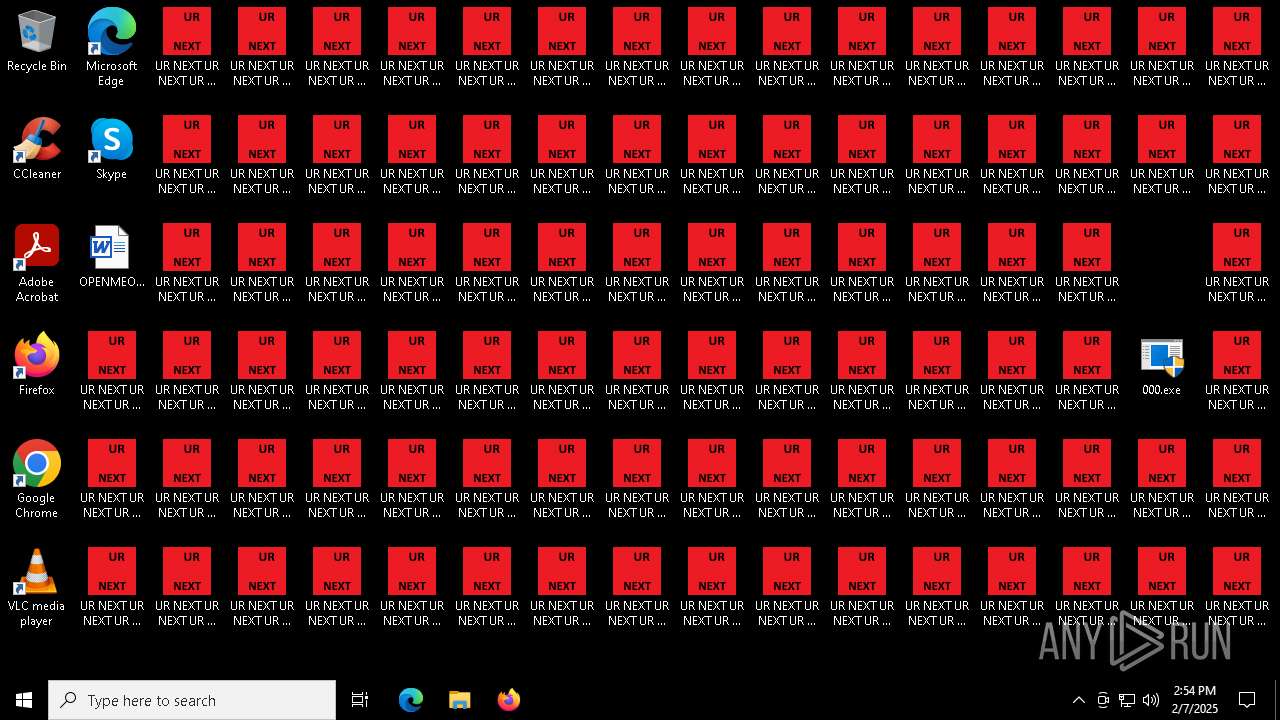
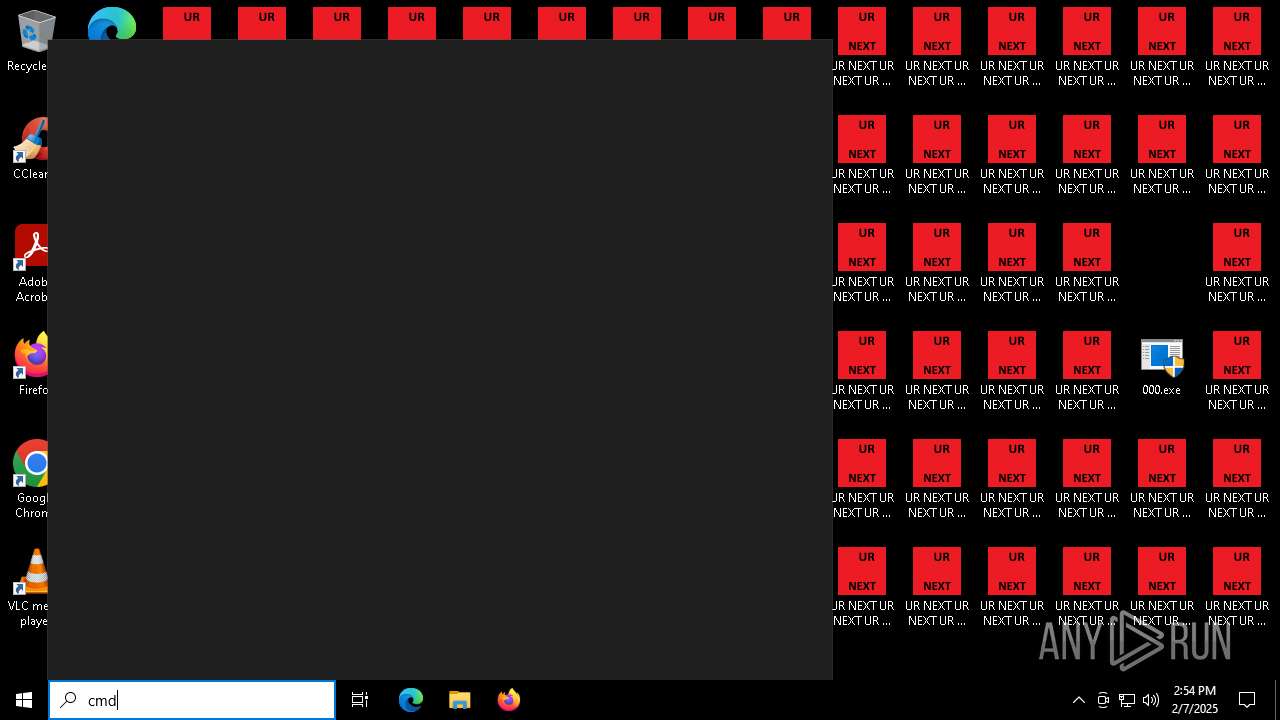
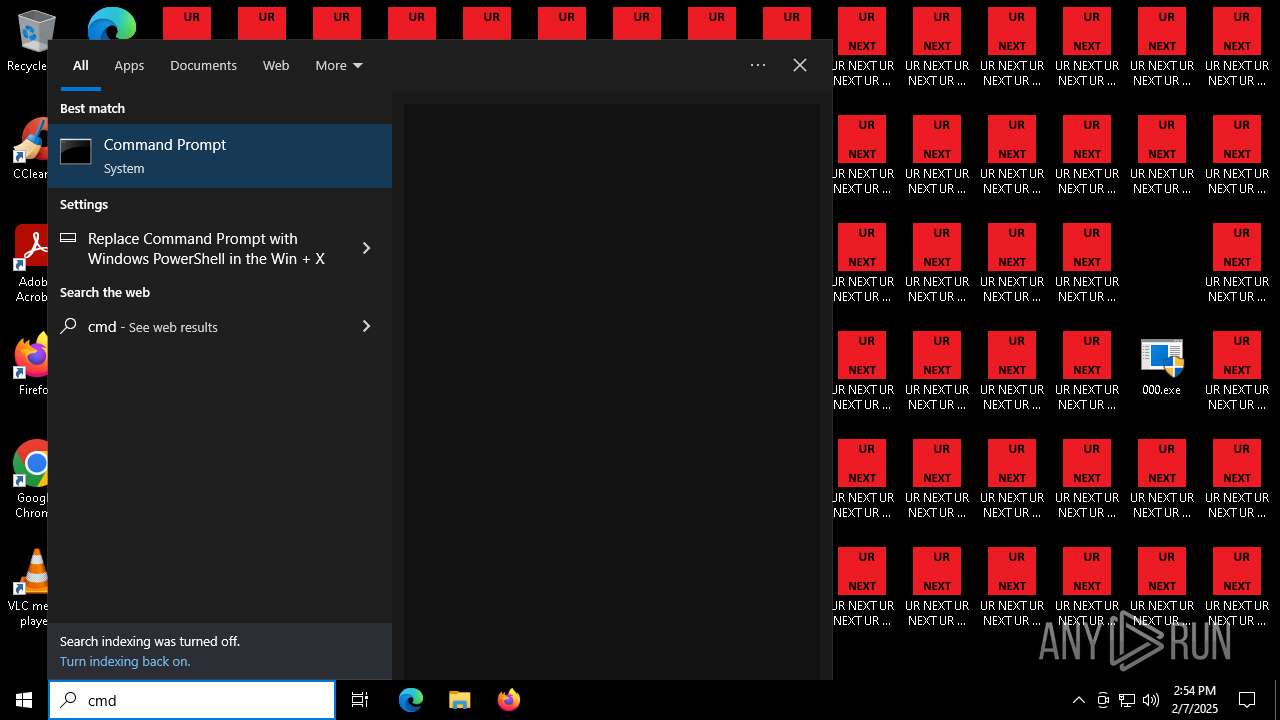
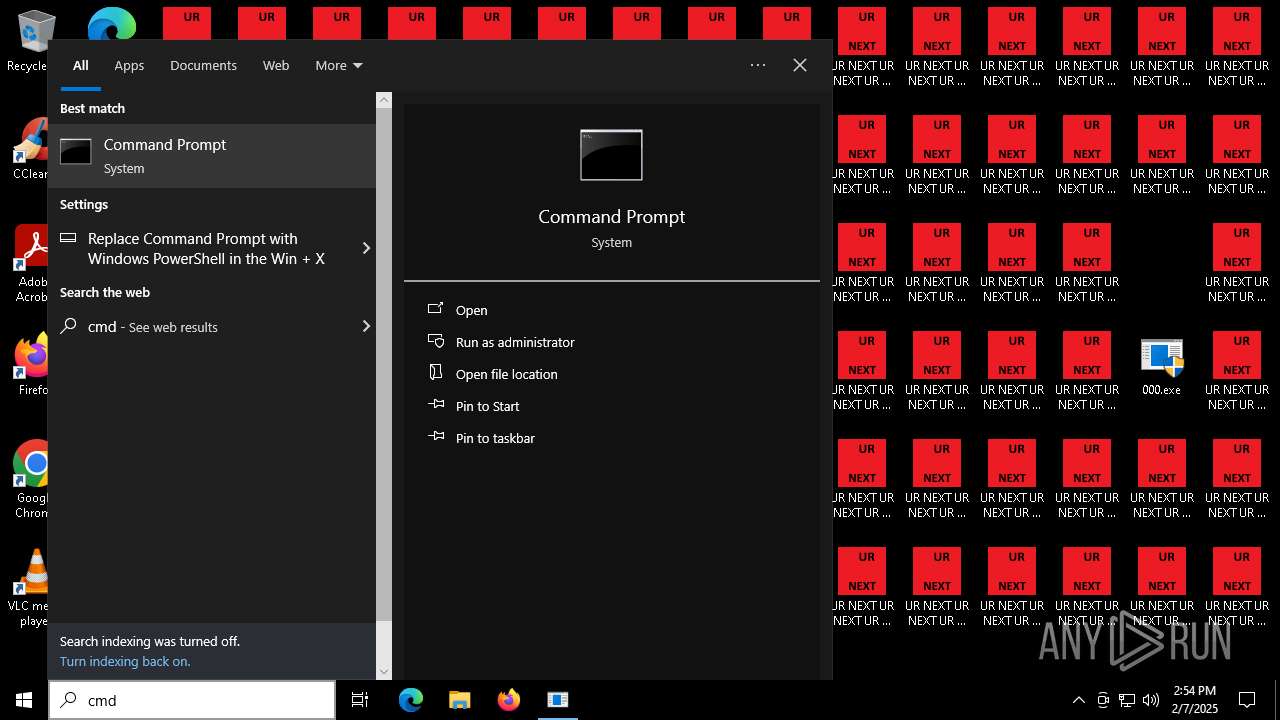
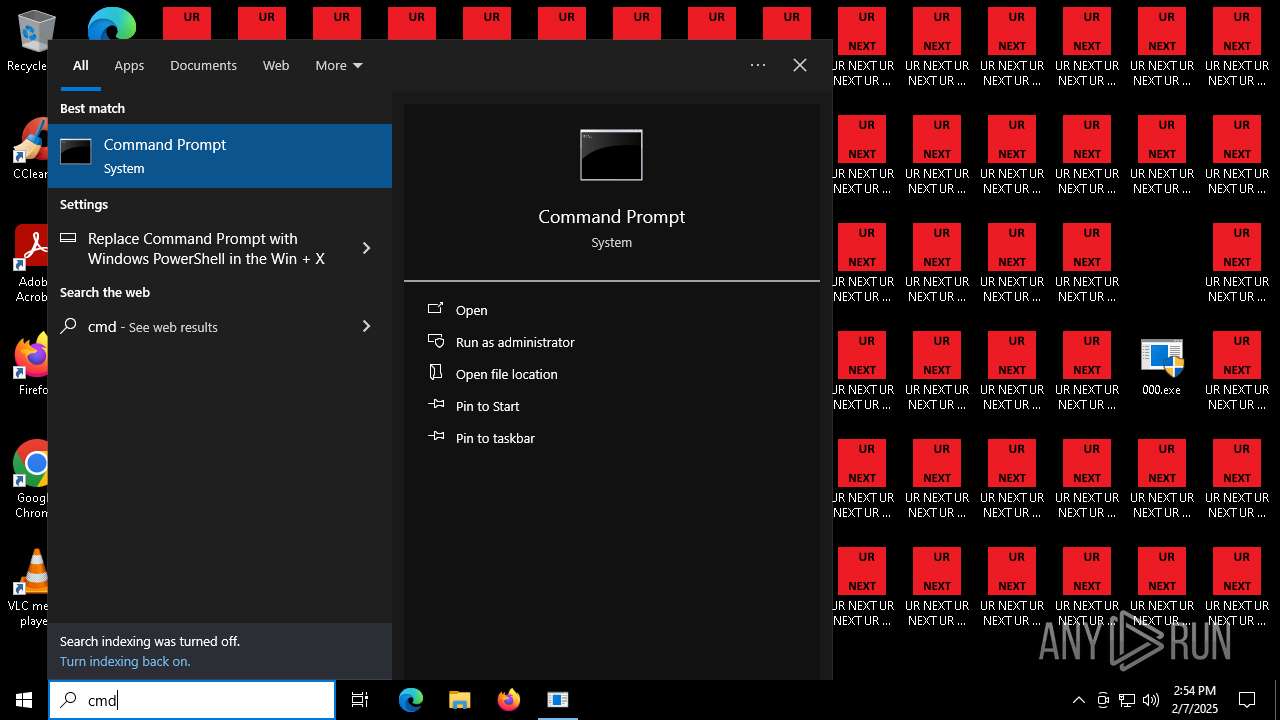
User: UR NEXT Integrity Level: MEDIUM Description: Version: 0.0.0.0 Modules
| |||||||||||||||
| 304 | ping 1.1.1.1 -n 1 -w 1000 | C:\Windows\System32\PING.EXE | — | cmd.exe | |||||||||||
User: UR NEXT Company: Microsoft Corporation Integrity Level: MEDIUM Description: TCP/IP Ping Command Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 496 | runaway.exe | C:\Users\admin\AppData\Local\Temp\E4F1.tmp\runaway.exe | — | cmd.exe | |||||||||||
User: UR NEXT Integrity Level: MEDIUM Description: Version: 0.0.0.0 Modules
| |||||||||||||||
| 536 | runaway.exe | C:\Users\admin\AppData\Local\Temp\E4F1.tmp\runaway.exe | — | cmd.exe | |||||||||||
User: UR NEXT Integrity Level: MEDIUM Description: Version: 0.0.0.0 Modules
| |||||||||||||||
| 664 | runaway.exe | C:\Users\admin\AppData\Local\Temp\E4F1.tmp\runaway.exe | — | cmd.exe | |||||||||||
User: UR NEXT Integrity Level: MEDIUM Description: Version: 0.0.0.0 Modules
| |||||||||||||||
| 668 | runaway.exe | C:\Users\admin\AppData\Local\Temp\E4F1.tmp\runaway.exe | — | cmd.exe | |||||||||||
User: UR NEXT Integrity Level: MEDIUM Description: Version: 0.0.0.0 Modules
| |||||||||||||||
| 716 | ping 1.1.1.1 -n 1 -w 1000 | C:\Windows\System32\PING.EXE | — | cmd.exe | |||||||||||
User: UR NEXT Company: Microsoft Corporation Integrity Level: MEDIUM Description: TCP/IP Ping Command Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 720 | ping 1.1.1.1 -n 1 -w 1000 | C:\Windows\System32\PING.EXE | — | cmd.exe | |||||||||||
User: UR NEXT Company: Microsoft Corporation Integrity Level: MEDIUM Description: TCP/IP Ping Command Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 720 | runaway.exe | C:\Users\admin\AppData\Local\Temp\E4F1.tmp\runaway.exe | — | cmd.exe | |||||||||||
User: UR NEXT Integrity Level: MEDIUM Description: Version: 0.0.0.0 Modules
| |||||||||||||||
| 772 | ping 1.1.1.1 -n 1 -w 1000 | C:\Windows\System32\PING.EXE | — | cmd.exe | |||||||||||
User: UR NEXT Company: Microsoft Corporation Integrity Level: MEDIUM Description: TCP/IP Ping Command Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (6172) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | failed_count |
Value: 0 | |||
| (PID) Process: | (6172) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | state |
Value: 2 | |||
| (PID) Process: | (6172) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | state |
Value: 1 | |||
| (PID) Process: | (6172) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\StabilityMetrics |
| Operation: | write | Name: | user_experience_metrics.stability.exited_cleanly |
Value: 0 | |||
| (PID) Process: | (6172) msedge.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\EdgeUpdate\ClientStateMedium\{56EB18F8-B008-4CBD-B6D2-8C97FE7E9062}\LastWasDefault |
| Operation: | write | Name: | S-1-5-21-1693682860-607145093-2874071422-1001 |
Value: 2381C3C4248C2F00 | |||
| (PID) Process: | (6172) msedge.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\EdgeUpdate\ClientStateMedium\{56EB18F8-B008-4CBD-B6D2-8C97FE7E9062}\LastWasDefault |
| Operation: | write | Name: | S-1-5-21-1693682860-607145093-2874071422-1001 |
Value: 3DA9D4C4248C2F00 | |||
| (PID) Process: | (6172) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowProperties\328526 |
| Operation: | write | Name: | WindowTabManagerFileMappingId |
Value: {F315F3D3-68A4-43B5-B13D-740CA23F2399} | |||
| (PID) Process: | (6172) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowProperties\328526 |
| Operation: | write | Name: | WindowTabManagerFileMappingId |
Value: {2F5EAFE5-E4BD-48AF-9513-8FB362A21891} | |||
| (PID) Process: | (6172) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowProperties\328526 |
| Operation: | write | Name: | WindowTabManagerFileMappingId |
Value: {8CFC2125-9962-4A68-9C49-FFD1DE58FF64} | |||
| (PID) Process: | (6172) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowProperties\328526 |
| Operation: | write | Name: | WindowTabManagerFileMappingId |
Value: {B50600B5-1A59-4A24-BE58-D035809A0AE3} | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 6172 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\parcel_tracking_db\LOG.old~RF13577a.TMP | — | |
MD5:— | SHA256:— | |||
| 6172 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\parcel_tracking_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 6172 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\PersistentOriginTrials\LOG.old~RF135789.TMP | — | |
MD5:— | SHA256:— | |||
| 6172 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\PersistentOriginTrials\LOG.old | — | |
MD5:— | SHA256:— | |||
| 6172 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\commerce_subscription_db\LOG.old~RF13577a.TMP | — | |
MD5:— | SHA256:— | |||
| 6172 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\commerce_subscription_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 6172 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\EdgePushStorageWithConnectTokenAndKey\LOG.old~RF135799.TMP | — | |
MD5:— | SHA256:— | |||
| 6172 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\EdgePushStorageWithConnectTokenAndKey\LOG.old | — | |
MD5:— | SHA256:— | |||
| 6172 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\discounts_db\LOG.old~RF135789.TMP | — | |
MD5:— | SHA256:— | |||
| 6172 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\discounts_db\LOG.old | — | |
MD5:— | SHA256:— | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
— | — | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | NL | binary | 973 b | whitelisted |
1412 | backgroundTaskHost.exe | GET | 200 | 2.17.190.73:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAUZZSZEml49Gjh0j13P68w%3D | DE | binary | 471 b | whitelisted |
6764 | svchost.exe | GET | 206 | 199.232.210.172:80 | http://msedge.b.tlu.dl.delivery.mp.microsoft.com/filestreamingservice/files/5cbc98ff-b69b-4fda-ad94-17ec2f9cf48b?P1=1739286757&P2=404&P3=2&P4=KL3QI3aOKx3o6ctoQIjyDj%2f%2fmS3zLodubImDYAmeFqJgv2kBB3%2bH4lXzV2GyXbgel%2bsGrcDBmOrjJjEGPdy%2fjg%3d%3d | US | binary | 1.41 Kb | whitelisted |
6764 | svchost.exe | HEAD | 200 | 199.232.210.172:80 | http://msedge.b.tlu.dl.delivery.mp.microsoft.com/filestreamingservice/files/5cbc98ff-b69b-4fda-ad94-17ec2f9cf48b?P1=1739286757&P2=404&P3=2&P4=KL3QI3aOKx3o6ctoQIjyDj%2f%2fmS3zLodubImDYAmeFqJgv2kBB3%2bH4lXzV2GyXbgel%2bsGrcDBmOrjJjEGPdy%2fjg%3d%3d | US | — | — | whitelisted |
— | — | GET | 200 | 23.48.23.193:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 1.01 Kb | whitelisted |
6764 | svchost.exe | GET | 206 | 199.232.210.172:80 | http://msedge.b.tlu.dl.delivery.mp.microsoft.com/filestreamingservice/files/5cbc98ff-b69b-4fda-ad94-17ec2f9cf48b?P1=1739286757&P2=404&P3=2&P4=KL3QI3aOKx3o6ctoQIjyDj%2f%2fmS3zLodubImDYAmeFqJgv2kBB3%2bH4lXzV2GyXbgel%2bsGrcDBmOrjJjEGPdy%2fjg%3d%3d | US | binary | 3.56 Kb | whitelisted |
7808 | SIHClient.exe | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Product%20Root%20Certificate%20Authority%202018.crl | NL | binary | 419 b | whitelisted |
4004 | svchost.exe | GET | 200 | 2.23.77.188:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | DE | binary | 471 b | whitelisted |
6764 | svchost.exe | GET | 200 | 199.232.210.172:80 | http://msedge.b.tlu.dl.delivery.mp.microsoft.com/filestreamingservice/files/e30939f9-8764-4977-9b5d-f865df373b71?P1=1739286758&P2=404&P3=2&P4=clUdEeAWWqkcj8IUoF1ZNbFLLMfa3epThl9tJSM3W5GSHVmfw1Jz3h9mQkcKwdzdEjQrtO8%2bkgerHPy888Y0SQ%3d%3d | US | binary | 16.8 Kb | whitelisted |
6764 | svchost.exe | GET | 206 | 199.232.210.172:80 | http://msedge.b.tlu.dl.delivery.mp.microsoft.com/filestreamingservice/files/5cbc98ff-b69b-4fda-ad94-17ec2f9cf48b?P1=1739286757&P2=404&P3=2&P4=KL3QI3aOKx3o6ctoQIjyDj%2f%2fmS3zLodubImDYAmeFqJgv2kBB3%2bH4lXzV2GyXbgel%2bsGrcDBmOrjJjEGPdy%2fjg%3d%3d | US | binary | 17.4 Kb | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 23.48.23.193:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
— | — | 95.101.149.131:80 | www.microsoft.com | Akamai International B.V. | NL | whitelisted |
640 | svchost.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4712 | MoUsoCoreWorker.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5064 | SearchApp.exe | 95.101.27.82:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
6172 | msedge.exe | 239.255.255.250:1900 | — | — | — | whitelisted |
6512 | msedge.exe | 13.107.42.16:443 | config.edge.skype.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
6512 | msedge.exe | 204.79.197.239:443 | edge.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
6512 | msedge.exe | 140.82.121.4:443 | github.com | GITHUB | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
www.bing.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
config.edge.skype.com |
| whitelisted |
edge.microsoft.com |
| whitelisted |
github.com |
| whitelisted |
business.bing.com |
| whitelisted |
edge-mobile-static.azureedge.net |
| whitelisted |
bzib.nelreports.net |
| whitelisted |