ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | 0061eecc_abc.exe |
| Full analysis: | https://app.any.run/tasks/7f900a1b-78f9-4d03-95af-e2277d1f7876 |
| Verdict: | Malicious activity |
| Analysis date: | October 03, 2025, 17:17:31 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, 6 sections |
| MD5: | 142C4426738BD84D17CB483B8605FE56 |
| SHA1: | 9CA15F170271A7CF3021ECF2AE354DB2E126132A |
| SHA256: | AB0F6022844C74C73CD8A8EB046FB95A1940E41DAB33F2F37ACCA15EEC176FE5 |
| SSDEEP: | 196608:D1LumI69j3X2RKIF2HnwHPtnnU3TUJE7Eza:1Tj4XF2HwVnaTUJ0Eza |
| .exe | | | Win32 Executable (generic) (52.9) |
|---|---|---|
| .exe | | | Generic Win/DOS Executable (23.5) |
| .exe | | | DOS Executable Generic (23.5) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2025:09:02 09:05:13+00:00 |
| ImageFileCharacteristics: | Executable, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 14.34 |
| CodeSize: | 1144320 |
| InitializedDataSize: | 23277568 |
| UninitializedDataSize: | - |
| EntryPoint: | 0xdca30 |
| OSVersion: | 6 |
| ImageVersion: | - |
| SubsystemVersion: | 6 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 1.27.1.2836 |
| ProductVersionNumber: | 1.27.1.2836 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Windows NT 32-bit |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | Unknown (0009) |
| CharacterSet: | Unicode |
| CompanyName: | GoTo, Inc. |
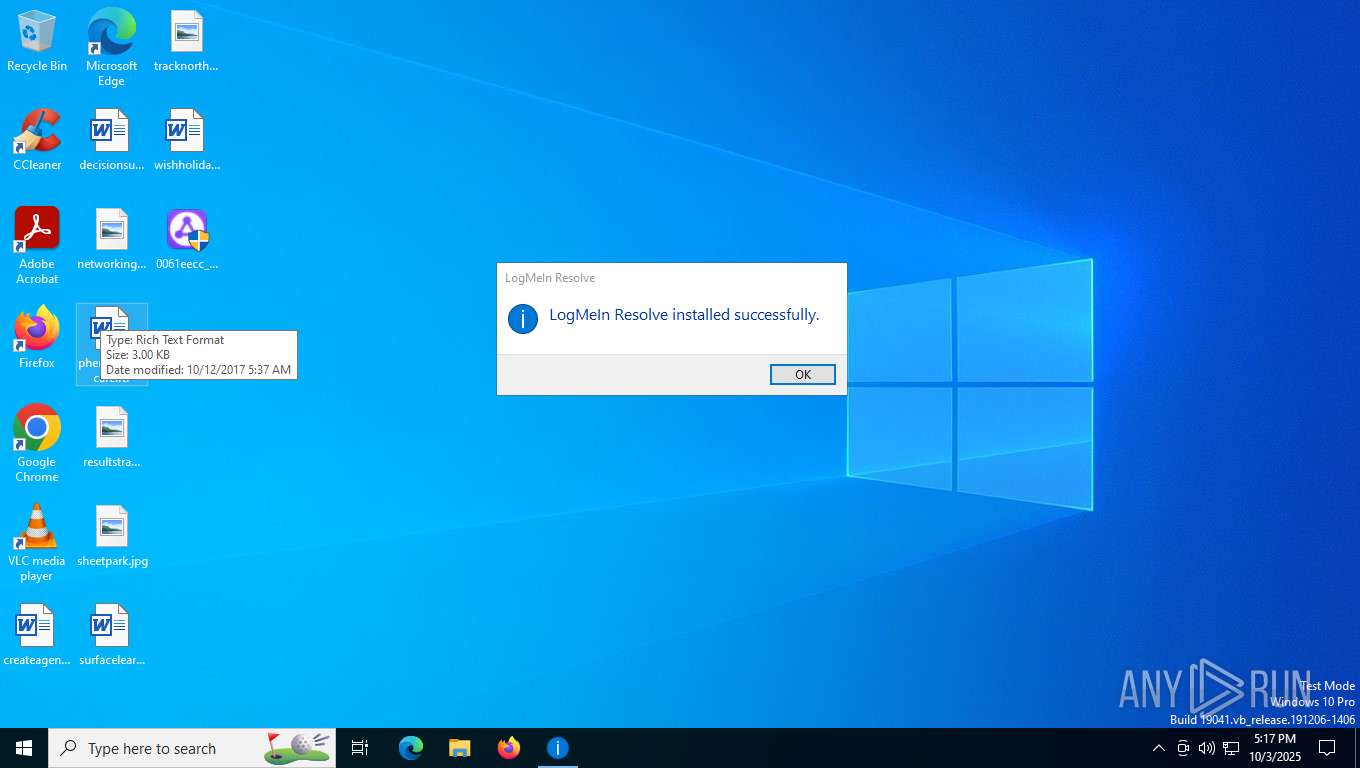
| FileDescription: | LogMeIn Resolve |
| FileVersion: | 1.27.1.2836 |
| InternalName: | GoToResolveUnattendedUpdater.exe |
| LegalCopyright: | Copyright © 2016-2025 GoTo, Inc. US patents pending. |
| OriginalFileName: | GoToResolveUnattendedUpdater.exe |
| ProductName: | GoTo Resolve |
| ProductVersion: | 1.27.1.2836 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 332 | cmd.exe /S /C ""C:\Users\admin\Desktop\0061eecc_abc.exe.cmd" "C:\Users\admin\Desktop\0061eecc_abc.exe"" | C:\Windows\SysWOW64\cmd.exe | — | 0061eecc_abc.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows Command Processor Exit code: 1 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1536 | "C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveExternalModuleHandler.exe" -InstallationId 8hnB1hW42B -CompanyId 2829436394331576853 -publickey ad6f62556f498789e1e5df37ee22b5995ee0a024029f5b59bc56eb9566f48138 -LogLevel 2 -Environment Production | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveExternalModuleHandler.exe | GoToResolveUnattended.exe | ||||||||||||
User: SYSTEM Company: GoTo, Inc. Integrity Level: SYSTEM Description: LogMeIn Resolve Version: 1.27.1.2836 Modules
| |||||||||||||||
| 2176 | GoToResolveTerminal.exe -CompanyId 2829436394331576853 -Environment Production -InstallationId 8hnB1hW42B -LogLevel 2 | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveTerminal.exe | GoToResolveUnattended.exe | ||||||||||||
User: SYSTEM Company: GoTo, Inc. Integrity Level: SYSTEM Description: LogMeIn Resolve Version: 1.27.1.2836 Modules
| |||||||||||||||
| 2332 | "C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveCrashHandler.exe" "--attachment=attachment_GoToResolveUnattended.log=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\appdata\GoToResolveUnattended.log" "--attachment=attachment_unattended.json=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\unattended.json" "--database=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\appdata\UnattendedCrashReportDB" "--metrics-dir=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\appdata\UnattendedCrashReportDB" --url=https://dumpster.console.gotoresolve.com/api/dump --annotation=format=minidump --annotation=hostname=DESKTOP-JGLLJLD --annotation=installationid=8hnB1hW42B --annotation=version=1.27.1.2836 --initial-client-data=0x7dc,0x7e0,0x7e4,0x584,0x7e8,0x70e26fac,0x70e26fbc,0x70e26fcc | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveCrashHandler.exe | — | GoToResolveUnattended.exe | |||||||||||
User: SYSTEM Integrity Level: SYSTEM Modules
| |||||||||||||||
| 2364 | "C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveCrashHandler.exe" "--database=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\appdata\ProcessCheckerCrashReportDB" "--metrics-dir=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\appdata\ProcessCheckerCrashReportDB" --url=https://dumpster.console.gotoresolve.com/api/dump --annotation=format=minidump --annotation=hostname=DESKTOP-JGLLJLD --annotation=installationid=8hnB1hW42B --annotation=version=1.27.1.2836 --initial-client-data=0x890,0x894,0x898,0x804,0x89c,0x70e26fac,0x70e26fbc,0x70e26fcc | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveCrashHandler.exe | — | GoToResolveProcessChecker.exe | |||||||||||
User: SYSTEM Integrity Level: SYSTEM Modules
| |||||||||||||||
| 2368 | "C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveCrashHandler.exe" "--database=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\appdata\ExternalModuleHandlerCrashReportDB" "--metrics-dir=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\appdata\ExternalModuleHandlerCrashReportDB" --url=https://dumpster.console.gotoresolve.com/api/dump --annotation=format=minidump --annotation=hostname=DESKTOP-JGLLJLD --annotation=installationid=8hnB1hW42B --annotation=version=1.27.1.2836 --initial-client-data=0x5f4,0x5e0,0x538,0x554,0x5d4,0x70e26fac,0x70e26fbc,0x70e26fcc | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveCrashHandler.exe | — | GoToResolveExternalModuleHandler.exe | |||||||||||
User: SYSTEM Integrity Level: SYSTEM Modules
| |||||||||||||||
| 2648 | "C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveCrashHandler.exe" "--attachment=attachment_GoToResolveLoggerProcess.log=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\appdata\GoToResolveLoggerProcess.log" "--attachment=attachment_logger.json=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\logger.json" "--database=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\appdata\LoggerProcessCrashReportDB" "--metrics-dir=C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\appdata\LoggerProcessCrashReportDB" --url=https://dumpster.console.gotoresolve.com/api/dump --annotation=format=minidump --annotation=hostname=DESKTOP-JGLLJLD --annotation=installationid=8hnB1hW42B --annotation=version=1.27.1.2836 --initial-client-data=0x6dc,0x6d4,0x6e8,0x6e0,0x70c,0x70e26fac,0x70e26fbc,0x70e26fcc | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveCrashHandler.exe | — | GoToResolveLoggerProcess.exe | |||||||||||
User: SYSTEM Integrity Level: SYSTEM Modules
| |||||||||||||||
| 2836 | GoToResolveRemoteControl.exe -CompanyId 2829436394331576853 -InstallationId 8hnB1hW42B -WorkFolder "C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853" -Environment Production -ApplicationType 4 -LogLevel 2 -Service 1 | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveRemoteControl.exe | GoToResolveUnattended.exe | ||||||||||||
User: SYSTEM Company: GoTo, Inc. Integrity Level: SYSTEM Description: LogMeIn Resolve Version: 1.27.1.2836 Modules
| |||||||||||||||
| 3040 | "C:\Users\admin\Desktop\0061eecc_abc.exe" | C:\Users\admin\Desktop\0061eecc_abc.exe | explorer.exe | ||||||||||||
User: admin Company: GoTo, Inc. Integrity Level: HIGH Description: LogMeIn Resolve Exit code: 0 Version: 1.27.1.2836 Modules
| |||||||||||||||
| 4108 | "C:\Users\admin\Desktop\0061eecc_abc.exe" | C:\Users\admin\Desktop\0061eecc_abc.exe | — | explorer.exe | |||||||||||
User: admin Company: GoTo, Inc. Integrity Level: MEDIUM Description: LogMeIn Resolve Exit code: 3221226540 Version: 1.27.1.2836 Modules
| |||||||||||||||
| (PID) Process: | (3040) 0061eecc_abc.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\GoTo Resolve Unattended 2829436394331576853 |
| Operation: | write | Name: | DisplayIcon |
Value: C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveUnattended.exe | |||
| (PID) Process: | (3040) 0061eecc_abc.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\GoTo Resolve Unattended 2829436394331576853 |
| Operation: | write | Name: | DisplayName |
Value: LogMeIn Resolve Unattended 2829436394331576853 | |||
| (PID) Process: | (3040) 0061eecc_abc.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\GoTo Resolve Unattended 2829436394331576853 |
| Operation: | write | Name: | DisplayVersion |
Value: 1.27.1.2836 | |||
| (PID) Process: | (3040) 0061eecc_abc.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\GoTo Resolve Unattended 2829436394331576853 |
| Operation: | write | Name: | InstallLocation |
Value: C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853 | |||
| (PID) Process: | (3040) 0061eecc_abc.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\GoTo Resolve Unattended 2829436394331576853 |
| Operation: | write | Name: | UninstallString |
Value: C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveUnattendedRemover.exe | |||
| (PID) Process: | (3040) 0061eecc_abc.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\GoTo Resolve Unattended\2829436394331576853 |
| Operation: | write | Name: | PublicKey |
Value: 01000000D08C9DDF0115D1118C7A00C04FC297EB01000000E800C405C6C8C543BF57BC0B73BBB6AC04000000020000000000106600000001000020000000AD88F8F8C1CCABE822E5ED6929637842B7A08084AE5F98926F77C14A3F85E3D8000000000E8000000002000020000000D0A540824027FB8F08BAA652A0F164690286FBC159A384A411FCC6E925710C9630000000CAF65FA1289AA84BA38DDE7561A08591D775761FB87B8A1265B5A0E55A8F7504910F22C57141C0A2F5F2F64B6515915E4000000078036163A0DB8C9EC6077E6105999F01A388F8096F8509F1705D952803577EEC9B7C4331D59F96088AC56EE6E3E3D6B3C90DBBDA24B05AB95101B494B88D0A4C | |||
| (PID) Process: | (5460) GoToResolveUnattended.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\GoTo Resolve Unattended\2829436394331576853 |
| Operation: | delete value | Name: | InstallationId |
Value: | |||
| (PID) Process: | (5460) GoToResolveUnattended.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\GoTo Resolve Unattended\2829436394331576853 |
| Operation: | write | Name: | HostId |
Value: 8a94e572ec8e00c85e215054b454f91b | |||
| (PID) Process: | (5460) GoToResolveUnattended.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\GoTo Resolve Unattended\2829436394331576853 |
| Operation: | delete value | Name: | regsvc |
Value: | |||
| (PID) Process: | (8144) GoToResolveProcessChecker.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\GoTo Resolve Unattended 2829436394331576853 |
| Operation: | write | Name: | DisplayName |
Value: LogMeIn Resolve Unattended 2829436394331576853 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3040 | 0061eecc_abc.exe | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveUnattendedRemover.exe | executable | |
MD5:11DFA6B306F1305A101E828077A315F4 | SHA256:7BD9410677CDC3CEA3EDC06A96CB1AEB7C7BF72BA222D070E8EBA86BDECC73A8 | |||
| 3040 | 0061eecc_abc.exe | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveProcessChecker.exe | executable | |
MD5:A4ACE4F2E6401EB63AF52A4F94696249 | SHA256:BB1DF8D1764BDB506A6A4F73AAA6F068228CC0357AAF0778F61C18D125DA930F | |||
| 3040 | 0061eecc_abc.exe | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\unattended.json | binary | |
MD5:D4AECB18082B32E5EA6AA56E7B003E38 | SHA256:259F48D4AC57D4025DB91F33498B59F9ABE48586B2307A128B7D2C18C610DAFD | |||
| 3040 | 0061eecc_abc.exe | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveRemoteControl.exe | executable | |
MD5:D48E2D379BF2200C8E52A9D5132C742A | SHA256:06779604172C844E860120E96B0DDD3B24136C87543EA99F6F4B5FF57599ED2D | |||
| 3040 | 0061eecc_abc.exe | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveUi.exe | executable | |
MD5:D1C108B023B231B779488F6CD610080B | SHA256:1BFA081822B5610A6E68C0FBBFDDA796020A843BC37C7620DA71795A04FABFA2 | |||
| 3040 | 0061eecc_abc.exe | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveUnattended.exe | executable | |
MD5:5F379149386225522203D074F951BA80 | SHA256:5B3EC6BF2FEDA602949814762751E155EB18B6F6EB92C8B015B3D1951619D5BD | |||
| 3040 | 0061eecc_abc.exe | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveLoggerProcess.exe | executable | |
MD5:271636F6BBC066B4373ACAB2A4C4AAA6 | SHA256:E9BE506B7E750150BBF9EA1E669F703458F62418AA1F0AFDB4F9F2E6A7152BB4 | |||
| 3040 | 0061eecc_abc.exe | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveUnattendedUi.exe | executable | |
MD5:DB0F7391C4D8F13F1E48C980F805D8E8 | SHA256:A948104AA578CAC631AF04053E900AF3238DF16F1FC89039D81B57888C67EDF9 | |||
| 3040 | 0061eecc_abc.exe | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\LibGoToResolve.dll | executable | |
MD5:BAC348BEF5E3CBE38FB5CAEF9F8AF5E8 | SHA256:EC73983805E0AF93291D585829242D0AE90E15CDD5177217D1E15DD853869574 | |||
| 3040 | 0061eecc_abc.exe | C:\Program Files (x86)\GoTo Resolve Unattended\2829436394331576853\GoToResolveNetworkChecker.exe | executable | |
MD5:E2B65DCBA9FA174D6AE90D5F00DD5991 | SHA256:FB6C33E722C55FC5AC286E35724051DD2FE1705D8552284214C865D80C4993D7 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
5460 | GoToResolveUnattended.exe | GET | 200 | 2.17.190.73:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSRXerF0eFeSWRripTgTkcJWMm7iQQUaDfg67Y7%2BF8Rhvv%2BYXsIiGX0TkICEA4Mh2e7LU%2FvwtYX3xHOG4k%3D | DE | binary | 727 b | whitelisted |
5460 | GoToResolveUnattended.exe | GET | 200 | 2.17.190.73:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBRbuhDibVrw1t5r3WYz1C9Jl6I%2FtwQU729TSunkBnx6yuKQVvYv1Ensy04CEAqA7xhLjfEFgtHEdqeVdGg%3D | DE | binary | 727 b | whitelisted |
8068 | GoToResolveProcessChecker.exe | GET | 200 | 2.17.190.73:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSRXerF0eFeSWRripTgTkcJWMm7iQQUaDfg67Y7%2BF8Rhvv%2BYXsIiGX0TkICEA4Mh2e7LU%2FvwtYX3xHOG4k%3D | DE | binary | 727 b | whitelisted |
— | — | POST | 202 | 18.185.192.238:443 | https://dumpster.console.gotoresolve.com/api/sendEventsV2 | DE | — | — | unknown |
8068 | GoToResolveProcessChecker.exe | GET | 200 | 2.17.190.73:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBRbuhDibVrw1t5r3WYz1C9Jl6I%2FtwQU729TSunkBnx6yuKQVvYv1Ensy04CEAqA7xhLjfEFgtHEdqeVdGg%3D | DE | binary | 727 b | whitelisted |
— | — | POST | 202 | 18.185.192.238:443 | https://dumpster.console.gotoresolve.com/api/sendEventsV2 | DE | — | — | unknown |
— | — | POST | 202 | 18.185.192.238:443 | https://dumpster.console.gotoresolve.com/api/sendEventsV2 | DE | — | — | unknown |
— | — | POST | 202 | 18.185.192.238:443 | https://dumpster.console.gotoresolve.com/api/sendEventsV2 | DE | — | — | unknown |
— | — | POST | 202 | 18.195.103.52:443 | https://dumpster.console.gotoresolve.com/api/sendEventsV2 | DE | — | — | unknown |
— | — | GET | 200 | 3.224.84.152:443 | https://devices.console.gotoresolve.com/properties | US | binary | 5.17 Kb | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
— | — | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
5460 | GoToResolveUnattended.exe | 2.17.190.73:80 | ocsp.digicert.com | AKAMAI-AS | DE | whitelisted |
8068 | GoToResolveProcessChecker.exe | 2.17.190.73:80 | ocsp.digicert.com | AKAMAI-AS | DE | whitelisted |
6128 | GoToResolveLoggerProcess.exe | 18.195.103.52:443 | dumpster.console.gotoresolve.com | AMAZON-02 | DE | unknown |
7552 | GoToResolveUnattended.exe | 44.213.43.156:443 | devices.console.gotoresolve.com | AMAZON-AES | US | unknown |
5792 | GoToResolveNetworkChecker.exe | 3.33.179.166:80 | ip.zscaler.com | AMAZON-02 | US | unknown |
5792 | GoToResolveNetworkChecker.exe | 18.195.103.52:443 | dumpster.console.gotoresolve.com | AMAZON-02 | DE | unknown |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
dumpster.console.gotoresolve.com |
| unknown |
devices.console.gotoresolve.com |
| unknown |
ip.zscaler.com |
| unknown |
zerotrust.services.gotoresolve.com |
| unknown |
devices-iot.console.gotoresolve.com |
| unknown |
sessions.console.gotoresolve.com |
| unknown |
www.bing.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2428 | svchost.exe | Misc activity | ET INFO Observed DNS Query to RMM Domain (gotoresolve .com) |
6128 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
6128 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
6128 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
— | — | Misc activity | INFO [ANY.RUN] USER_AGENTS Suspicious User-Agent (Mozilla/5.0) |
— | — | Misc activity | INFO [ANY.RUN] USER_AGENTS Suspicious User-Agent (Mozilla/5.0) |
6128 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
6128 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
6128 | GoToResolveLoggerProcess.exe | Misc activity | ET INFO Observed RMM Domain (gotoresolve .com in TLS SNI) |
— | — | Misc activity | INFO [ANY.RUN] USER_AGENTS Suspicious User-Agent (Mozilla/5.0) |
Process | Message |
|---|---|
GoToResolveUnattended.exe | DllMain: DLL_PROCESS_ATTACH: lpReserved=0
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_ATTACH
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_ATTACH
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_ATTACH
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_ATTACH
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_ATTACH
|
GoToResolveUnattended.exe | DllMain: DLL_THREAD_DETACH
|
GoToResolveProcessChecker.exe | DllMain: DLL_PROCESS_ATTACH: lpReserved=0
|
GoToResolveProcessChecker.exe | DllMain: DLL_PROCESS_ATTACH: lpReserved=0
|
GoToResolveProcessChecker.exe | DllMain: DLL_THREAD_ATTACH
|