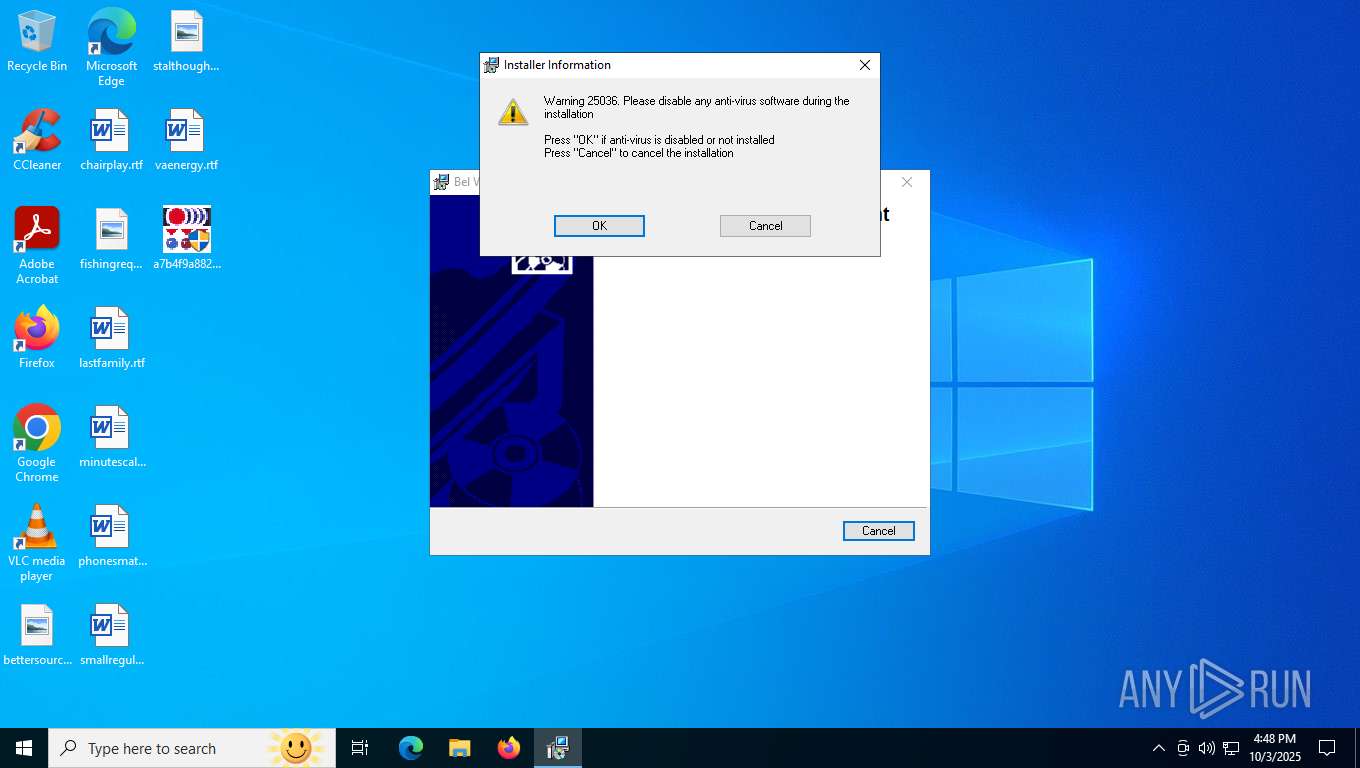
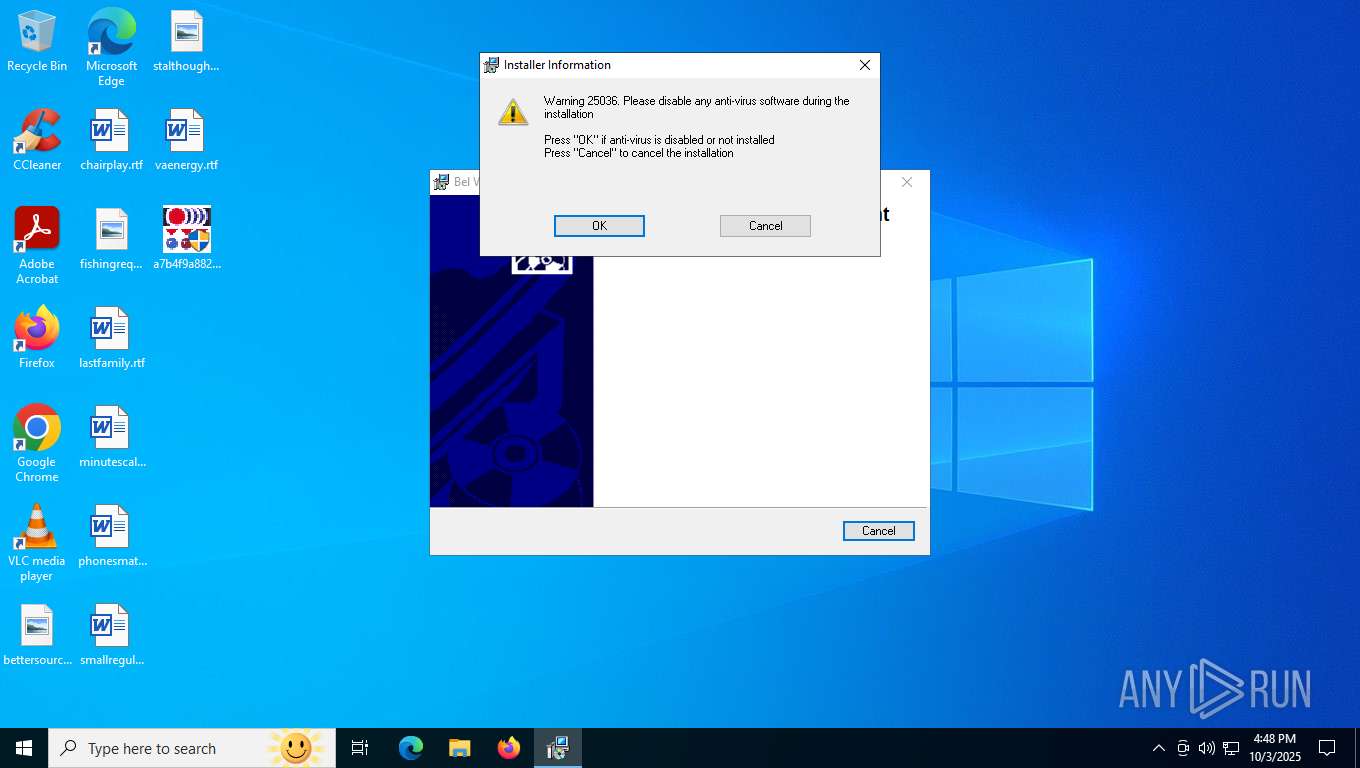
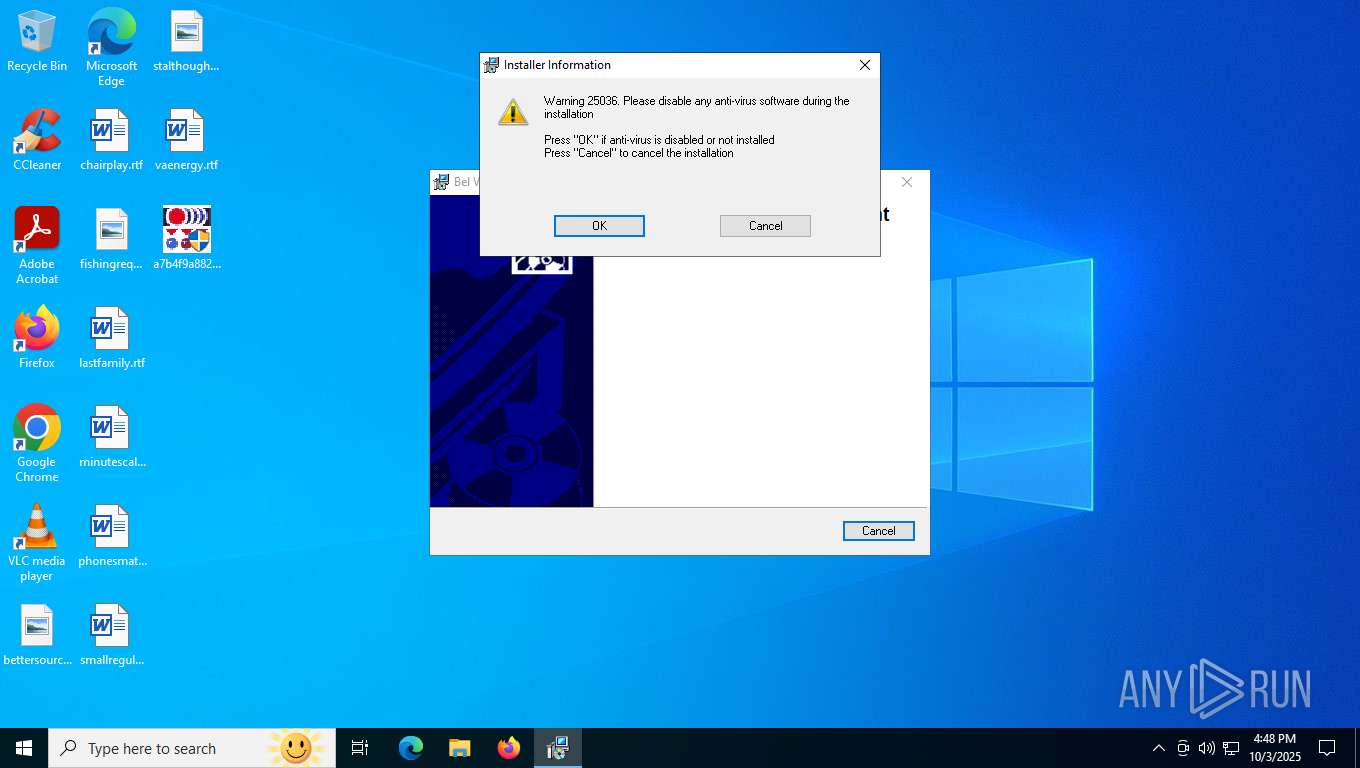
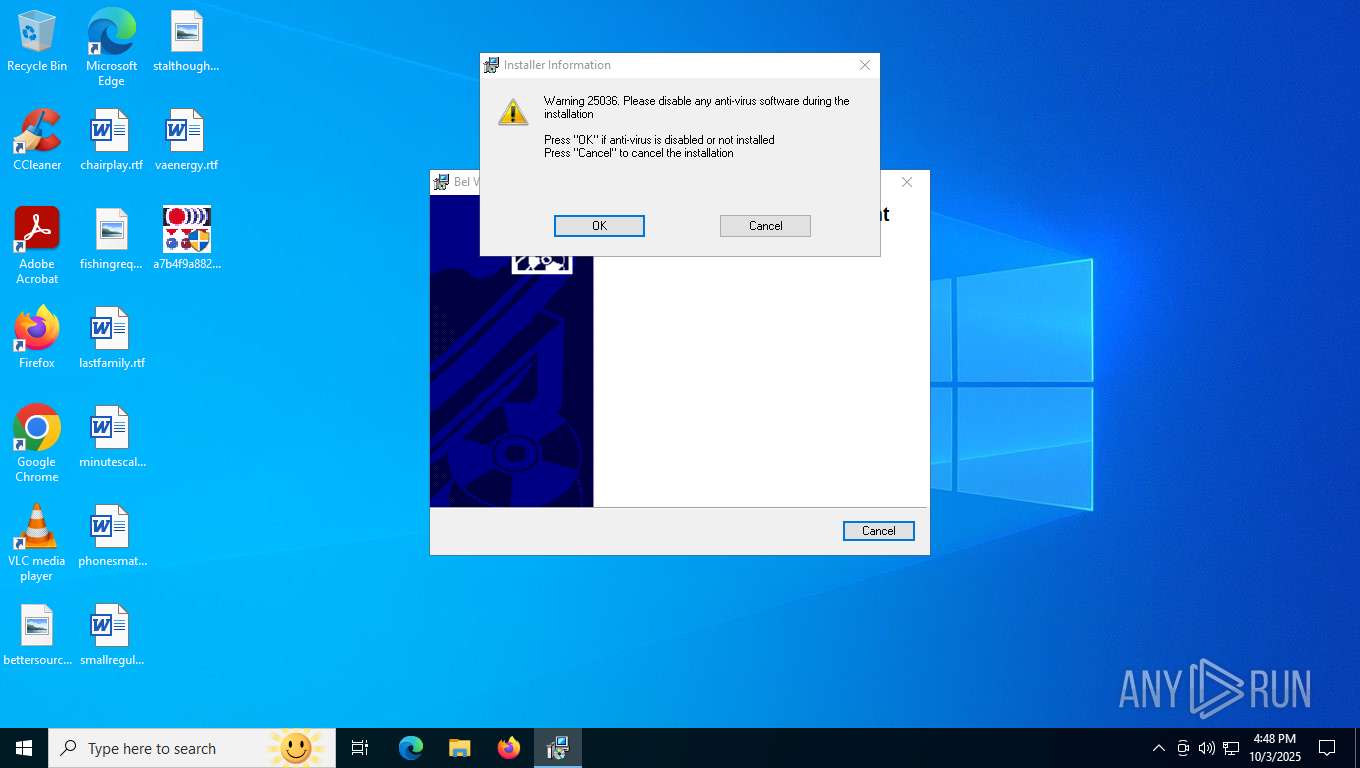
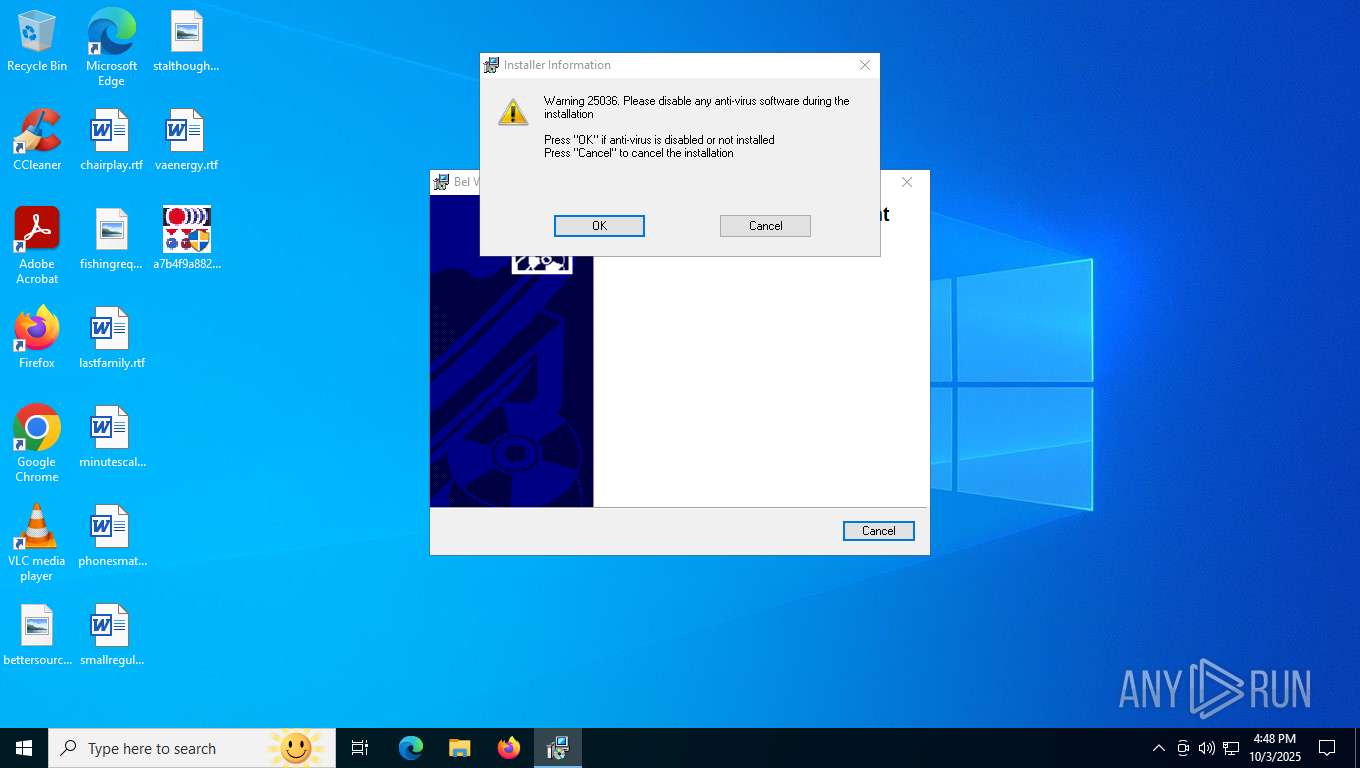
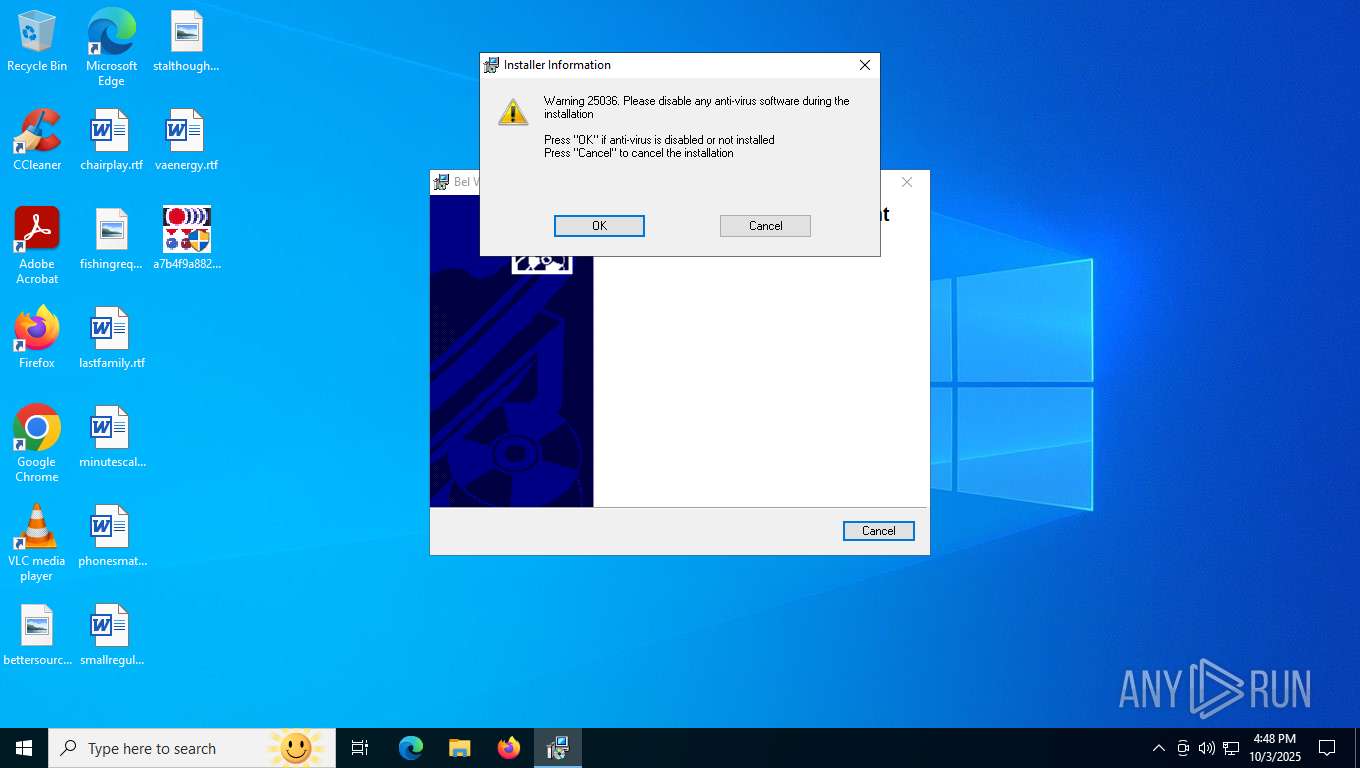
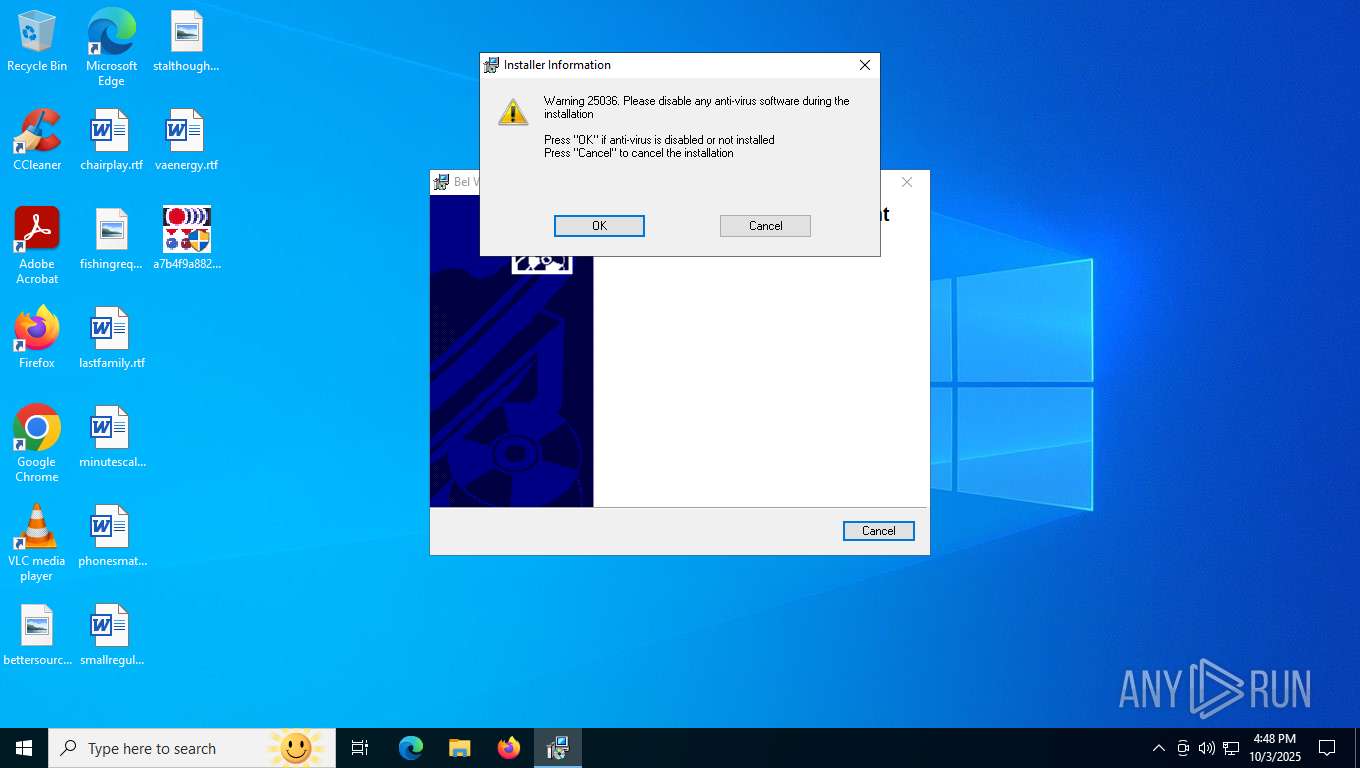
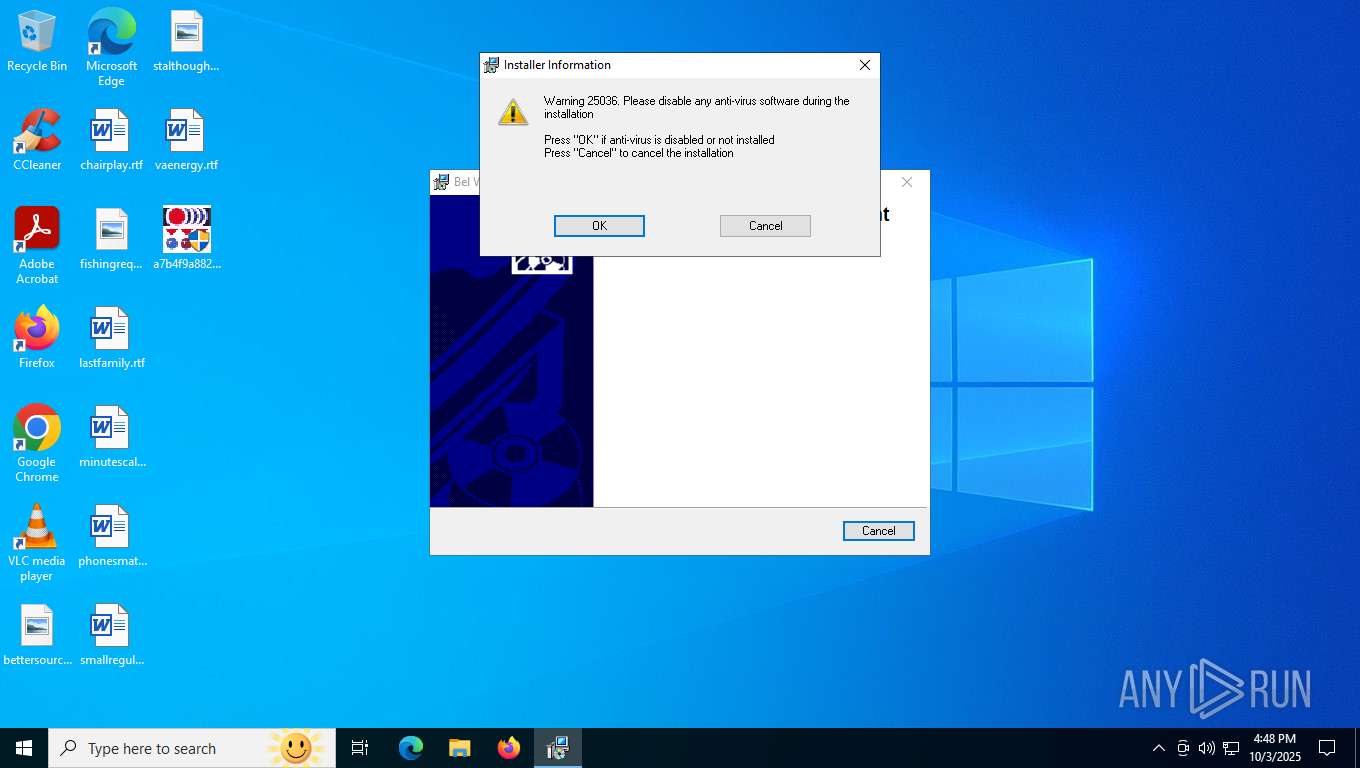
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe |
| Full analysis: | https://app.any.run/tasks/ebb7ba95-d727-4aad-b977-f7882ac2c2fc |
| Verdict: | Malicious activity |
| Analysis date: | October 03, 2025, 16:45:40 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, 4 sections |
| MD5: | 6AB3AE8F2FD0AD6D73C0932040937C76 |
| SHA1: | 71FB65E136FC89CDFDC2D5F1E7CBB588ACB05914 |
| SHA256: | A7B4F9A882D83B21FCB2F1D9AC479AF3395D2DAB0CBCC0324F1464BD3CB9C01B |
| SSDEEP: | 98304:P2NA49KlqBNh1UuElMiD6hdgdFhK7ai/tiWx4+dhI7AeJiU6xREDqZPYVtILEPfR:Zm+HcJ0EqvjgKatBqtV+QQJLPRCd7 |
| .exe | | | InstallShield setup (36.8) |
|---|---|---|
| .exe | | | Win32 Executable MS Visual C++ (generic) (26.6) |
| .exe | | | Win64 Executable (generic) (23.6) |
| .dll | | | Win32 Dynamic Link Library (generic) (5.6) |
| .exe | | | Win32 Executable (generic) (3.8) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2017:08:01 16:50:56+00:00 |
| ImageFileCharacteristics: | No relocs, Executable, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 9 |
| CodeSize: | 194560 |
| InitializedDataSize: | 79872 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x1bc19 |
| OSVersion: | 5 |
| ImageVersion: | - |
| SubsystemVersion: | 5 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 4.1.0.17758 |
| ProductVersionNumber: | 4.1.0.0 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Windows NT |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | English (U.S.) |
| CharacterSet: | Unicode |
| Comments: | CLIENT_STRB/WIN2K/Mon Jul 31 14:35:49 GMT 2017 |
| CompanyName: | S-Terra Bel |
| FileDescription: | - |
| FileVersion: | 4.1.17758 |
| InternalName: | setup |
| OriginalFileName: | setup.exe |
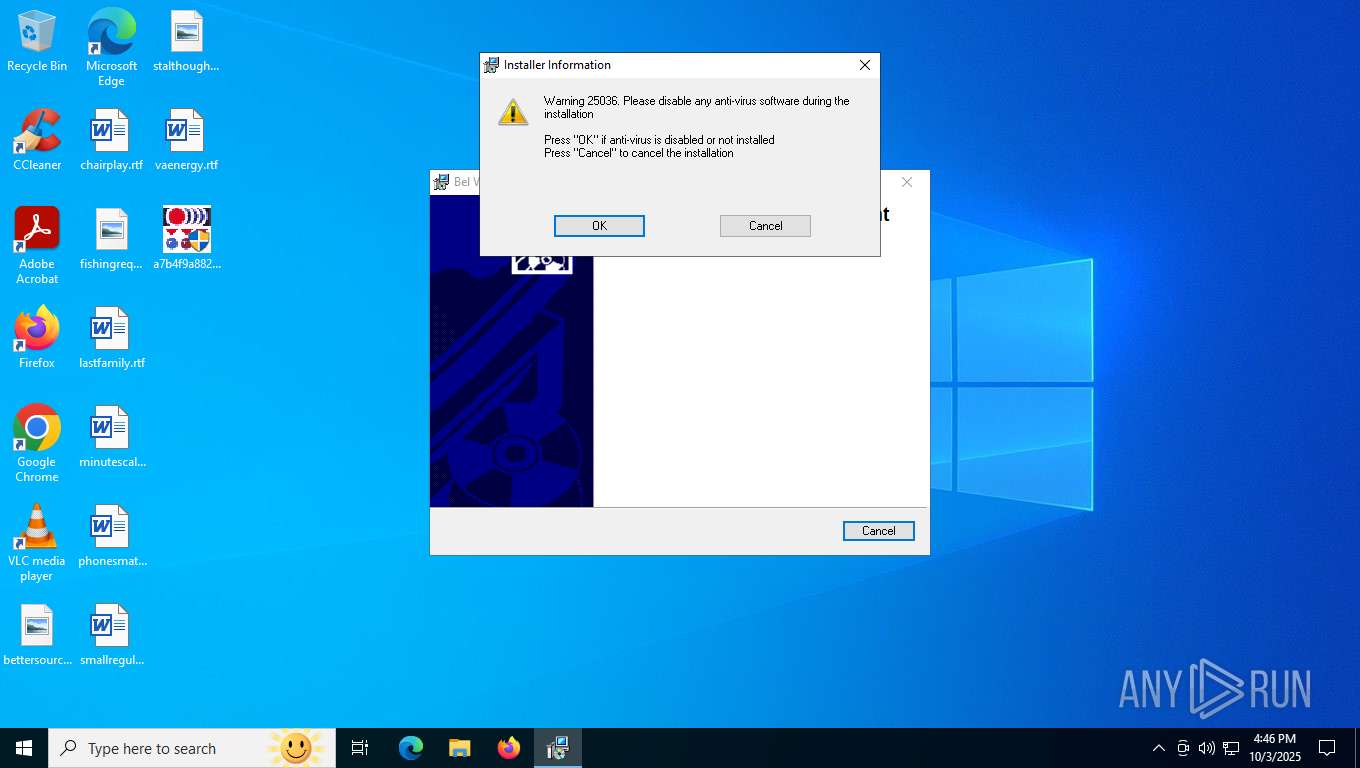
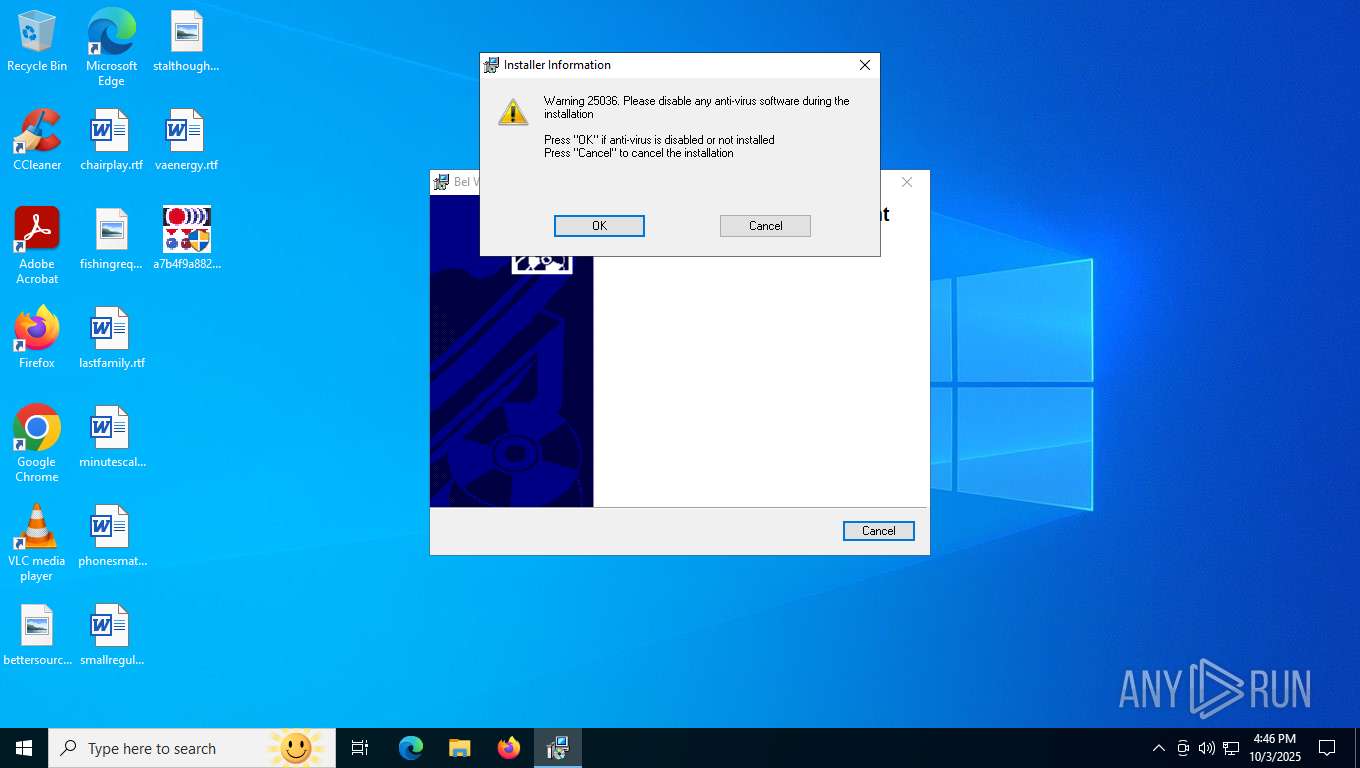
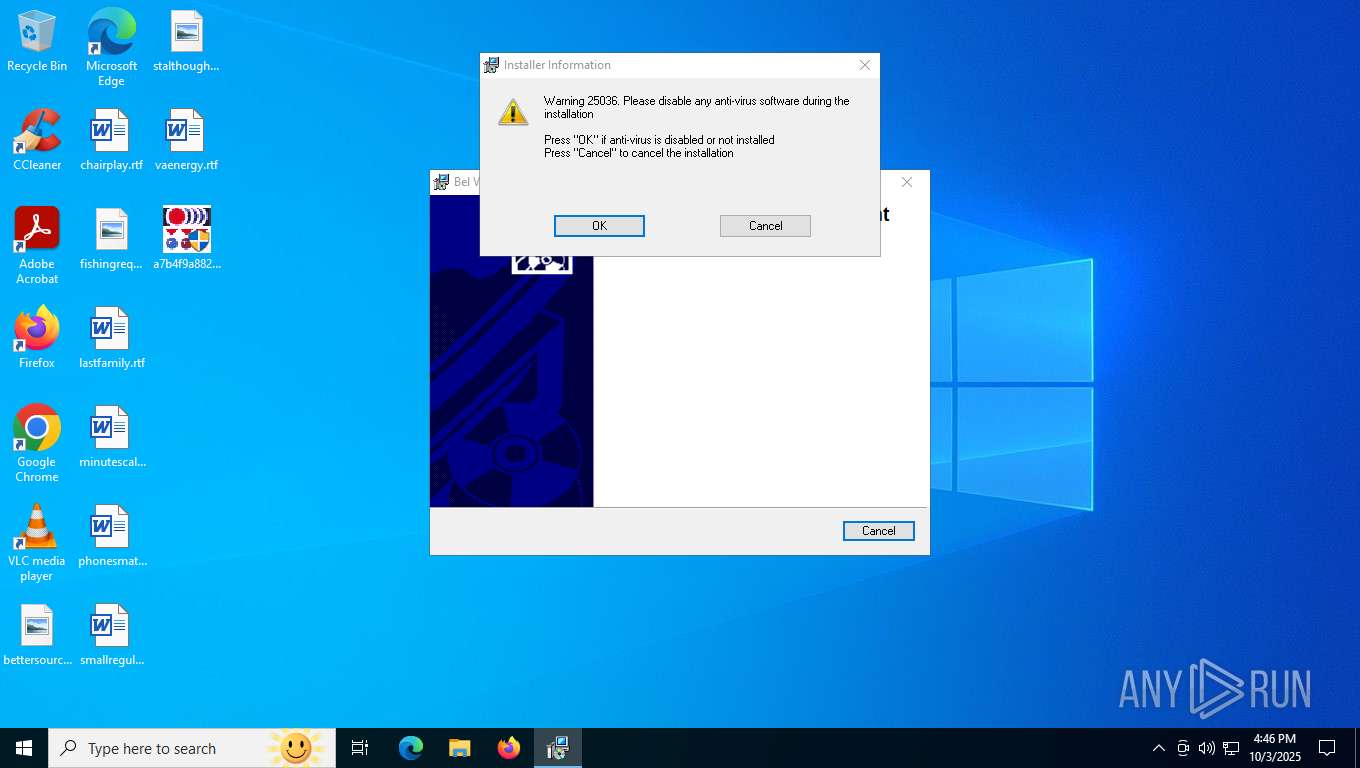
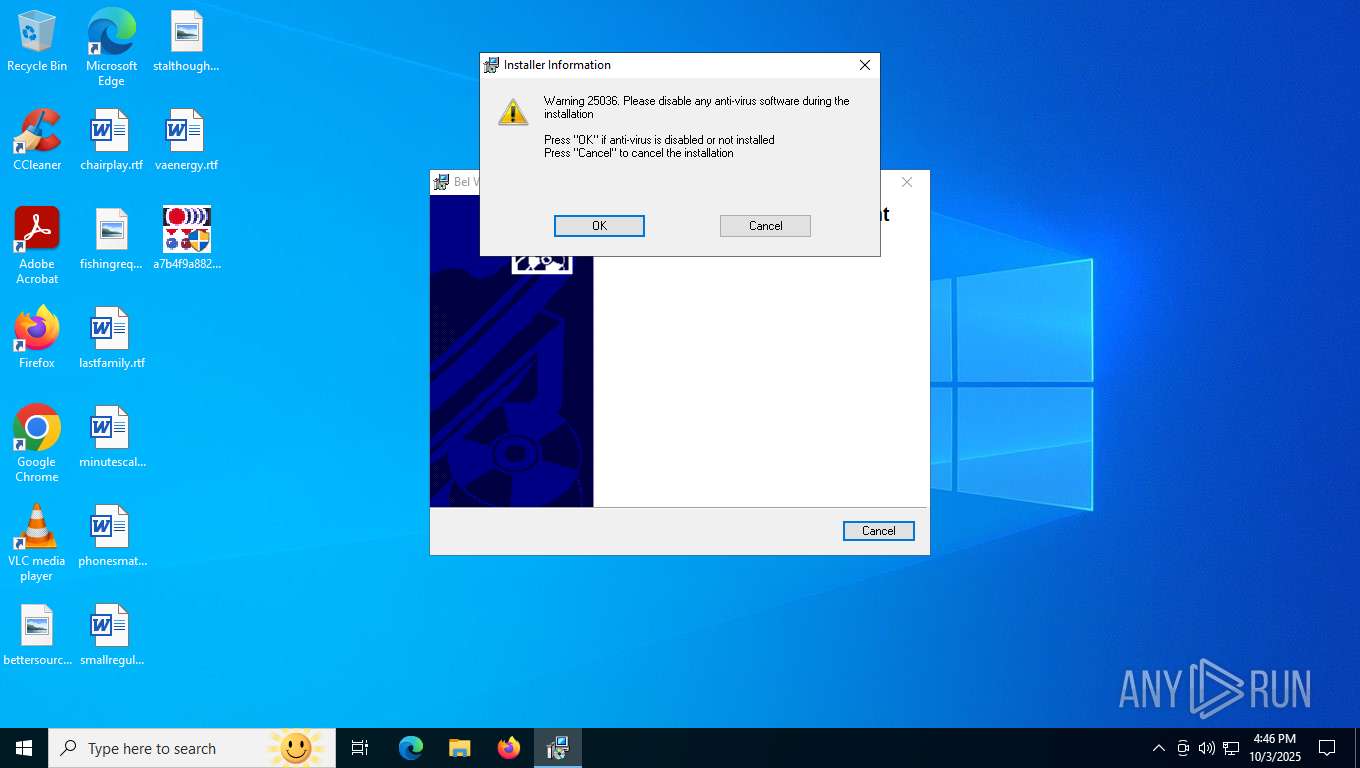
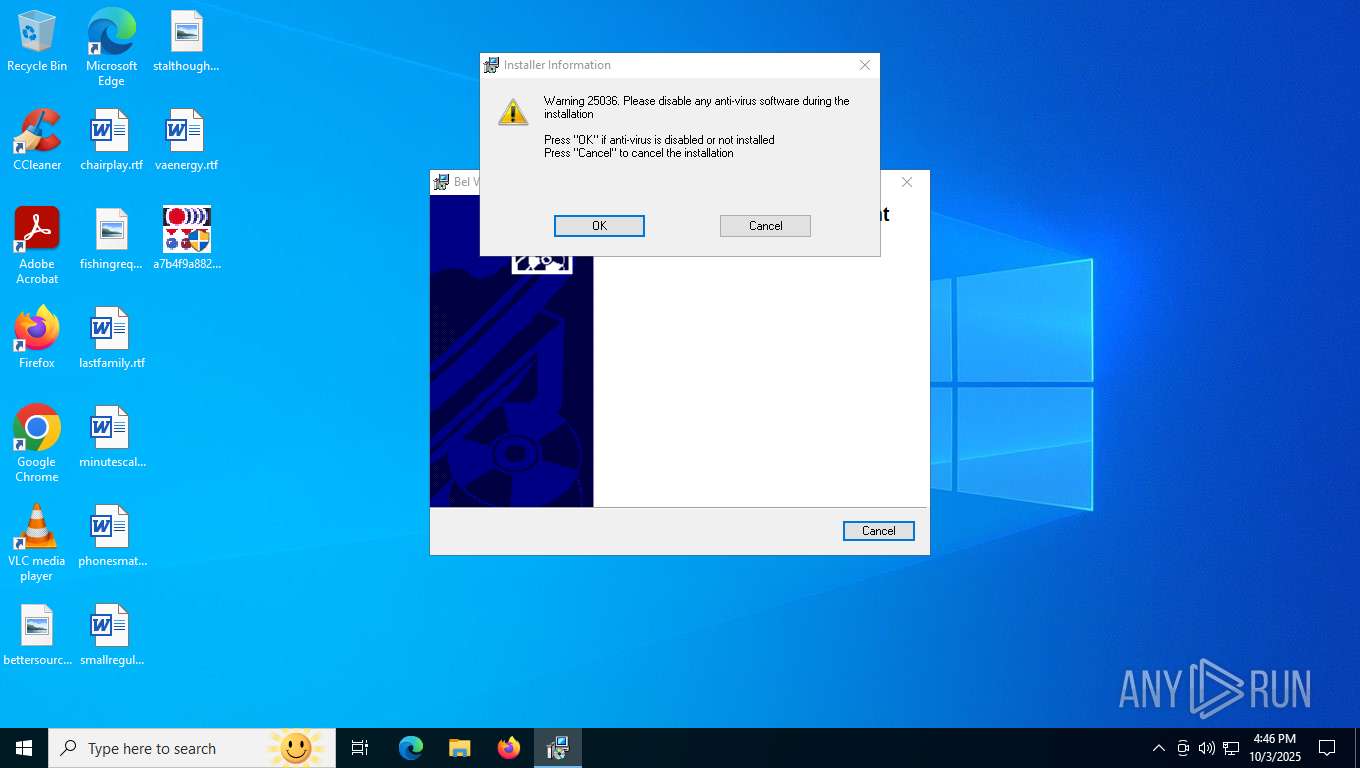
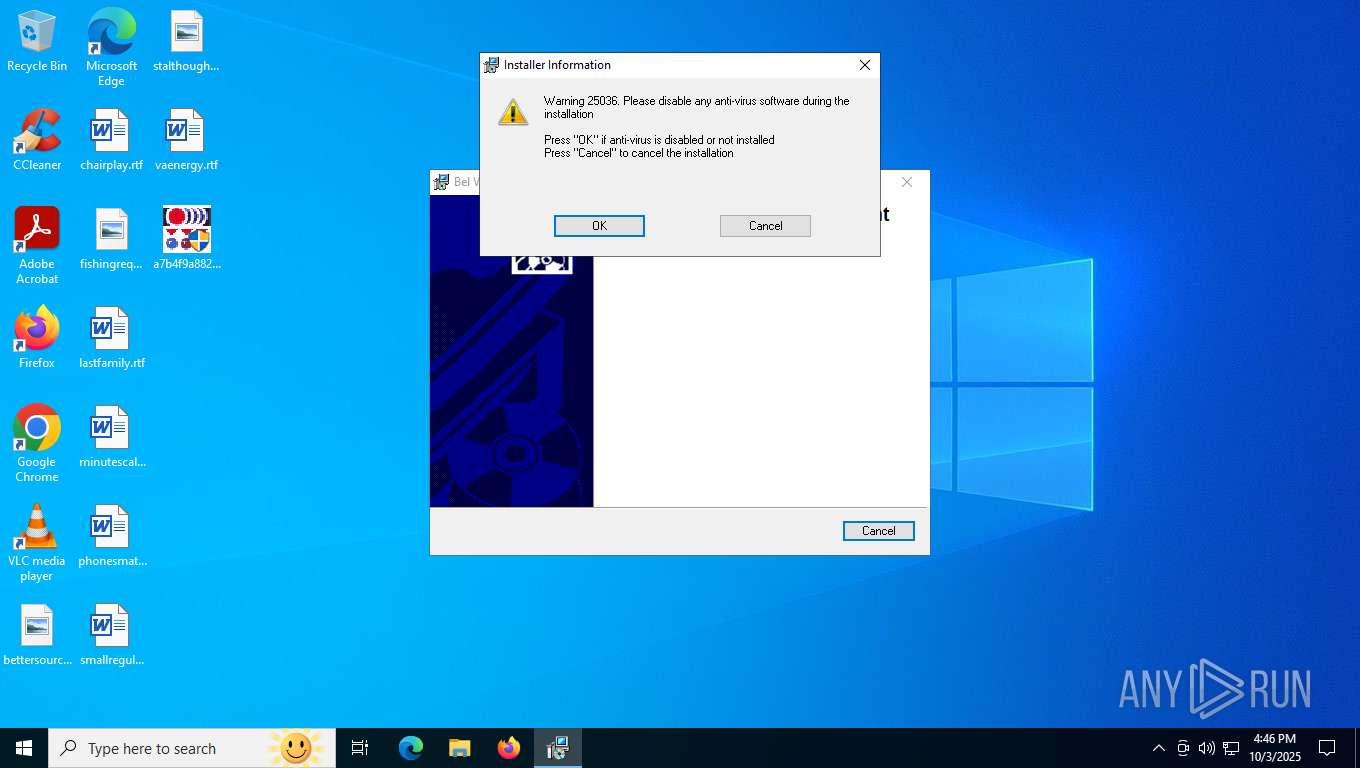
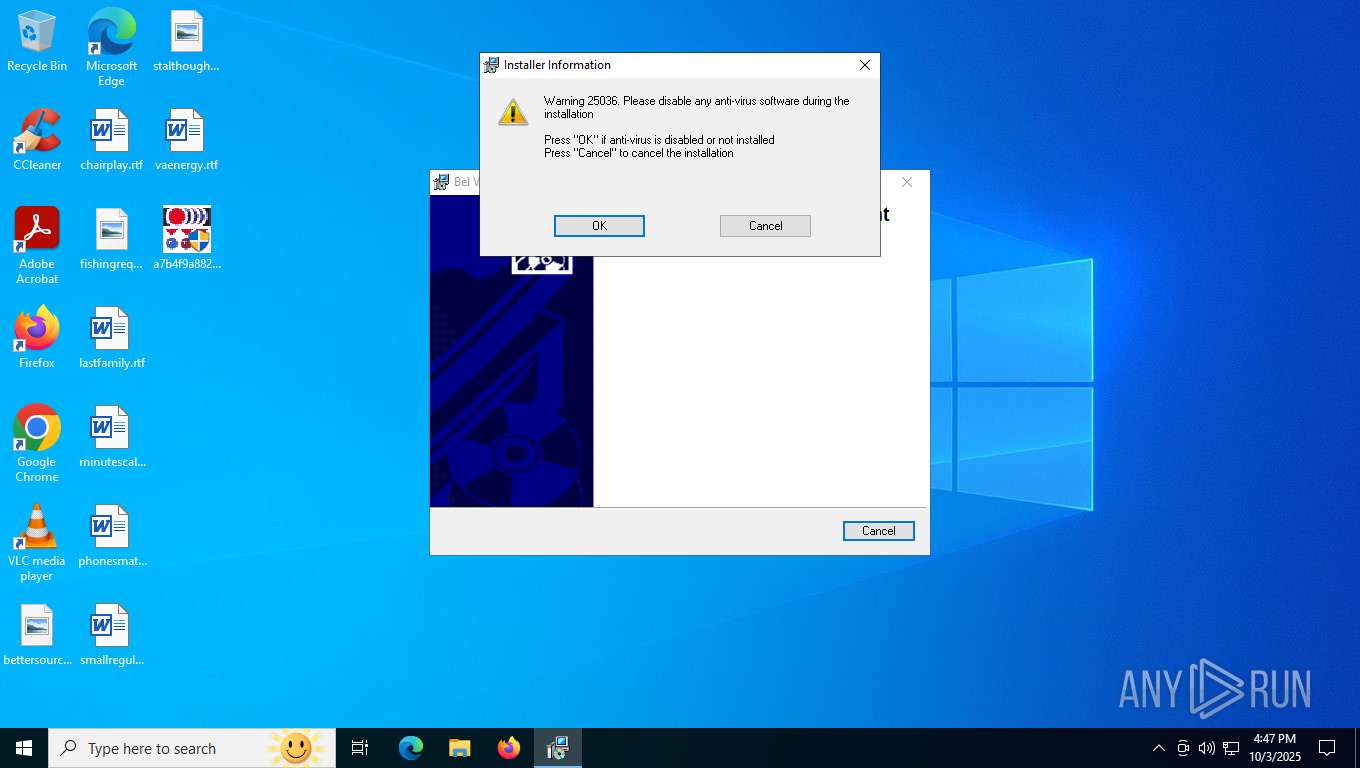
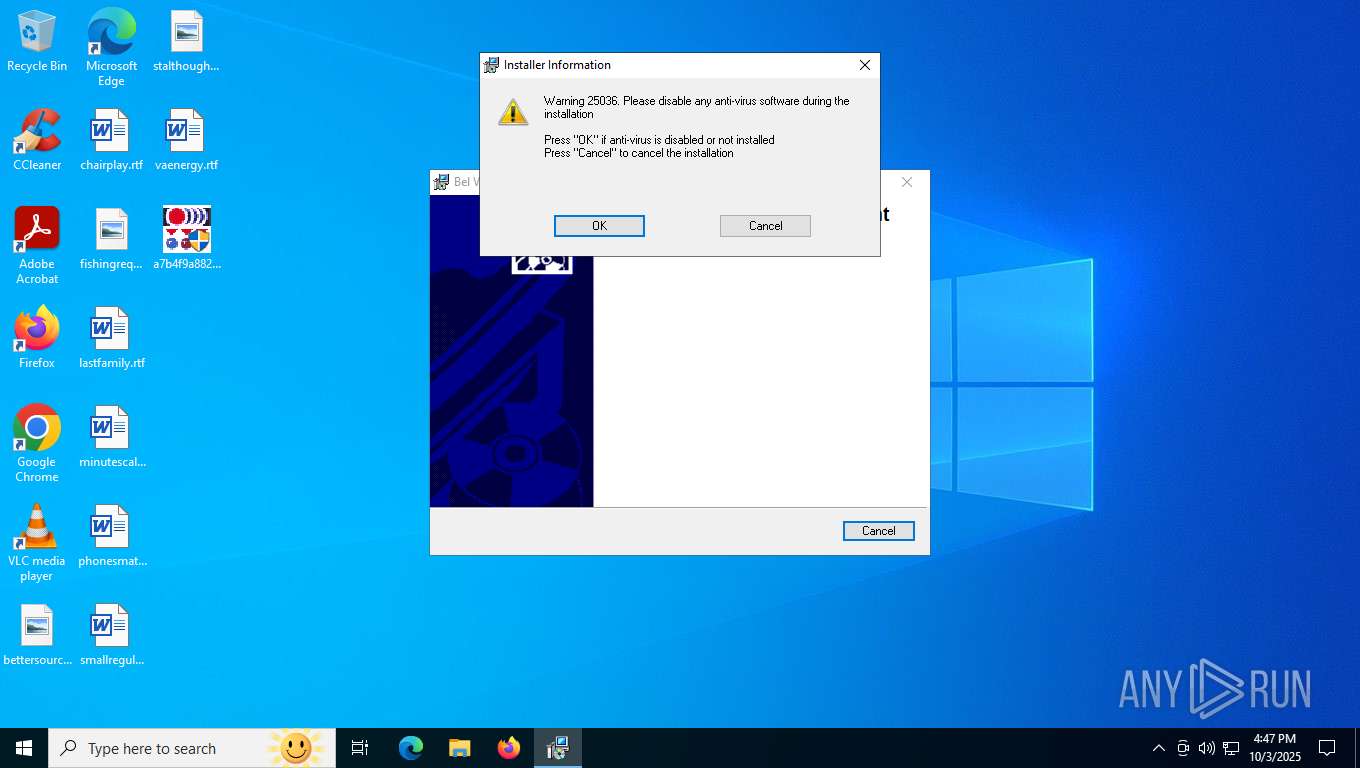
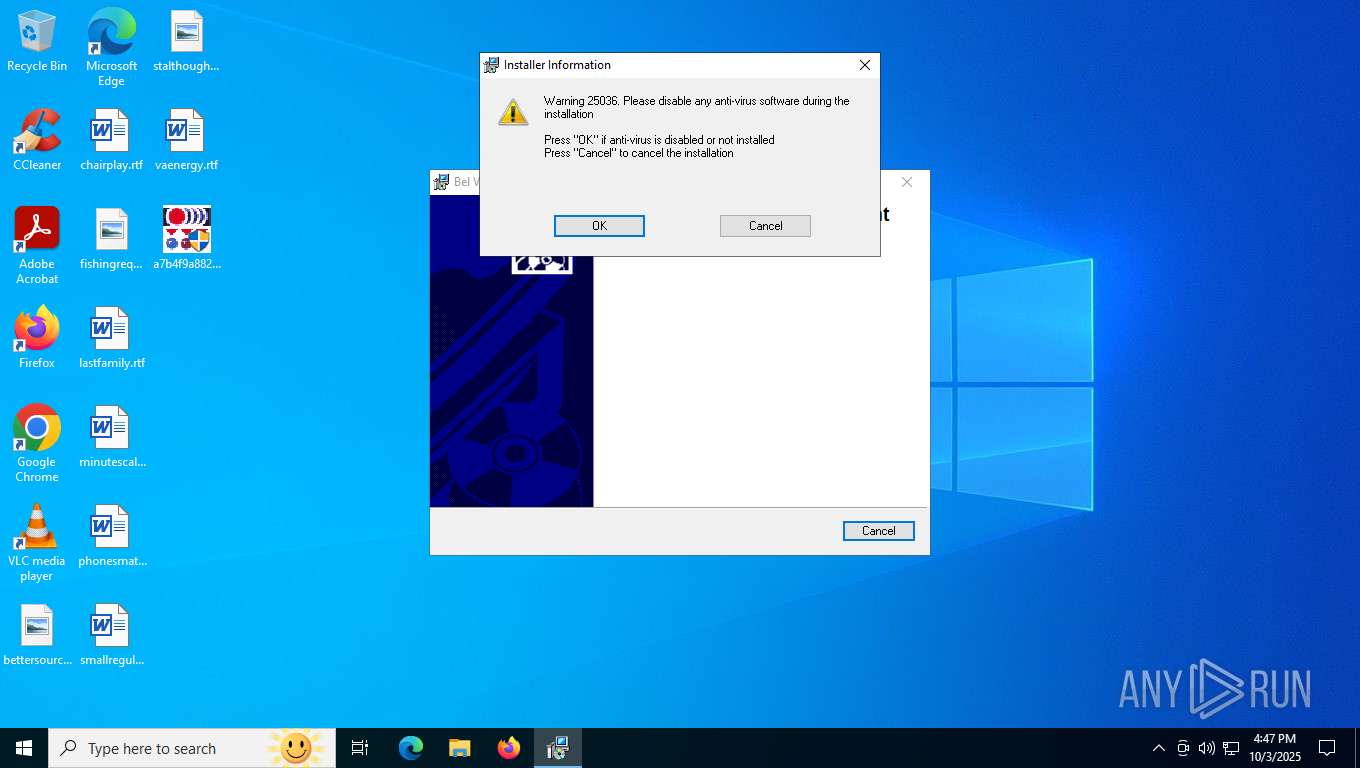
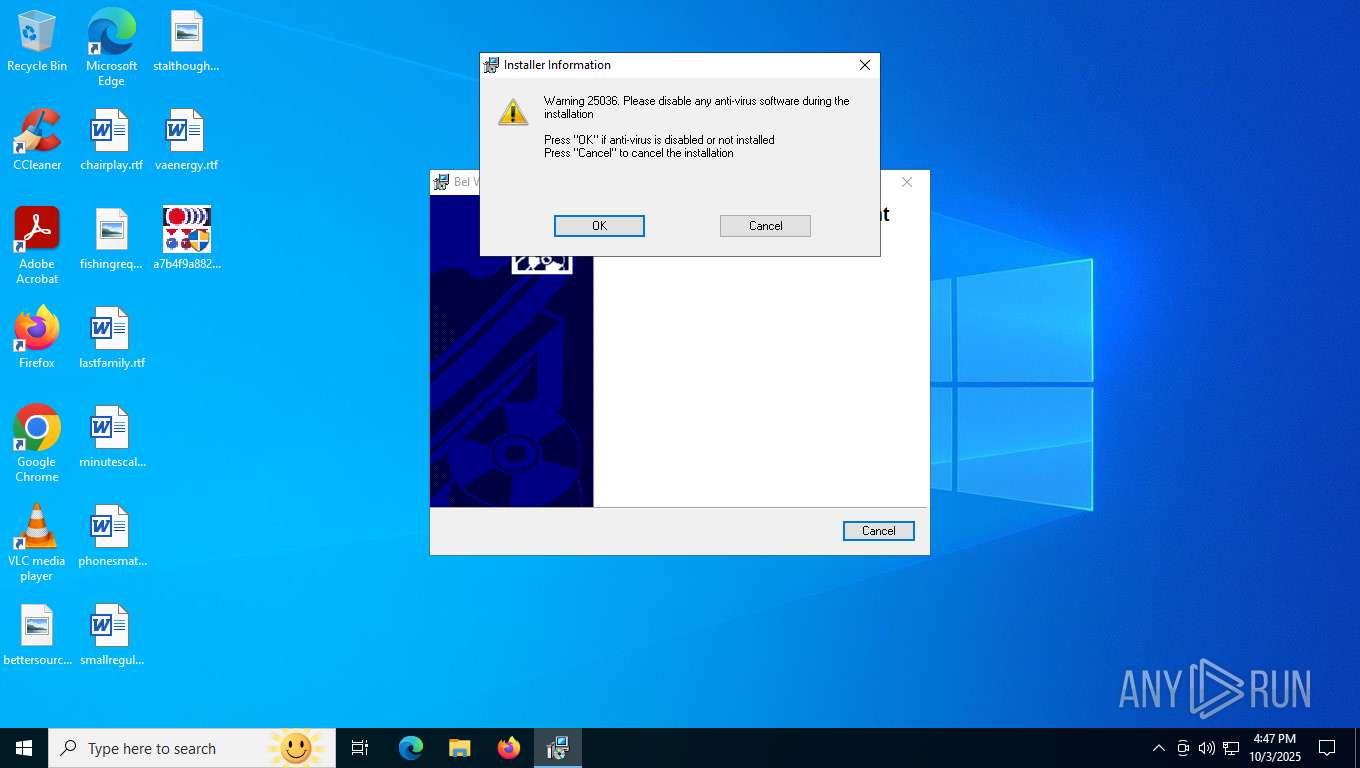
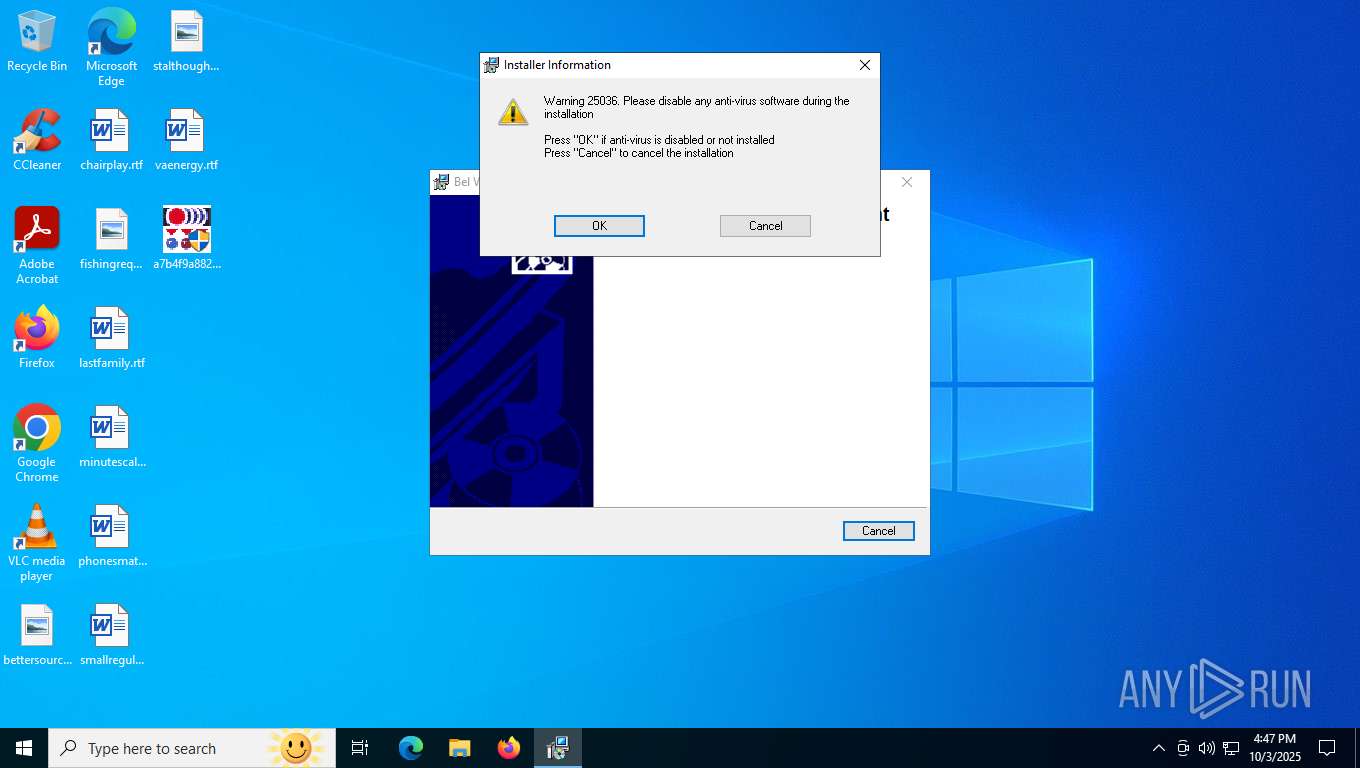
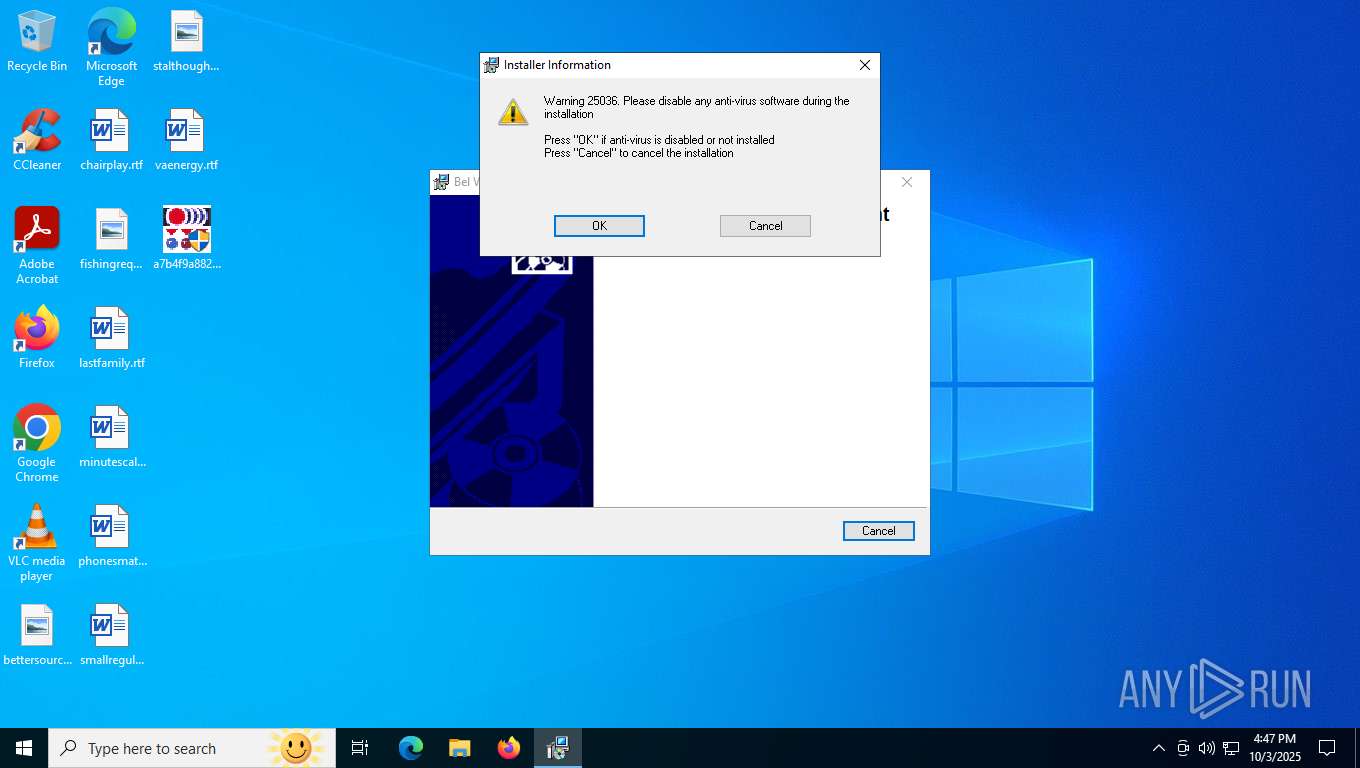
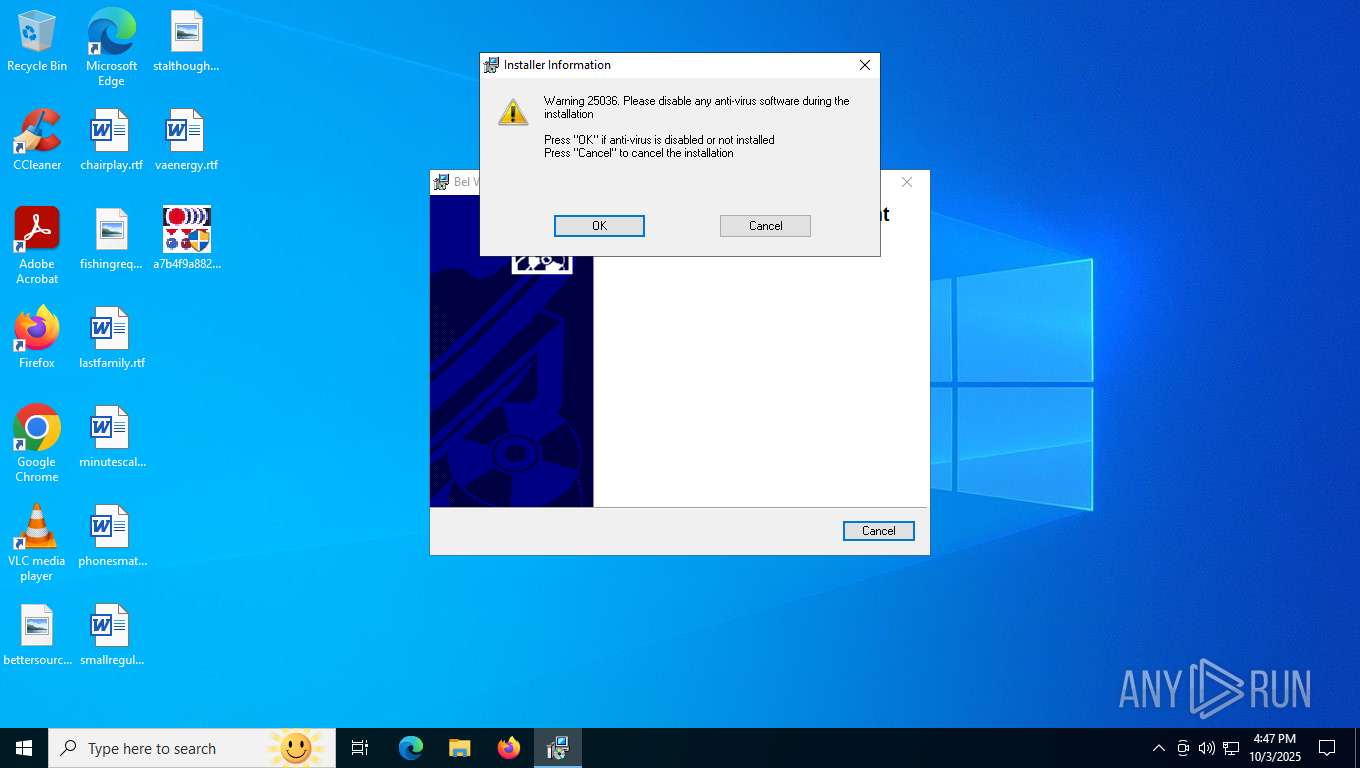
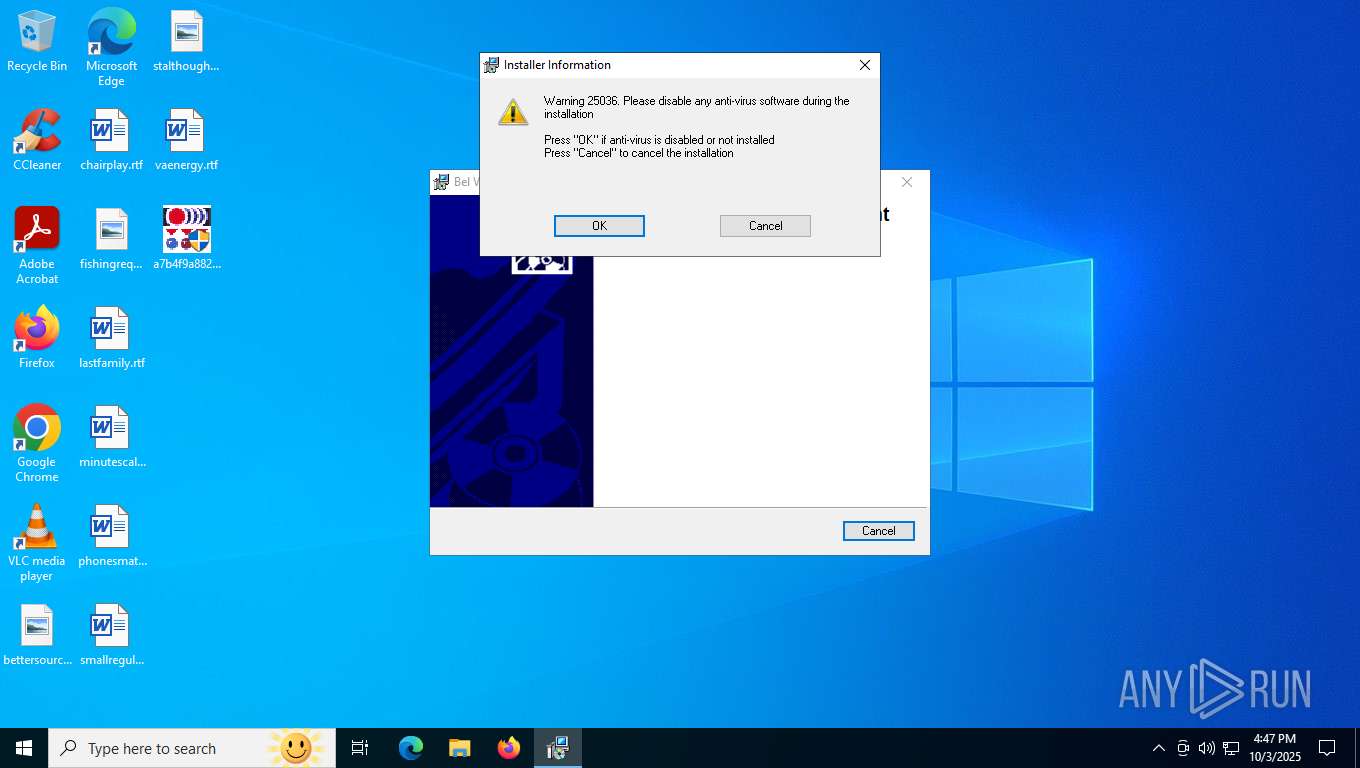
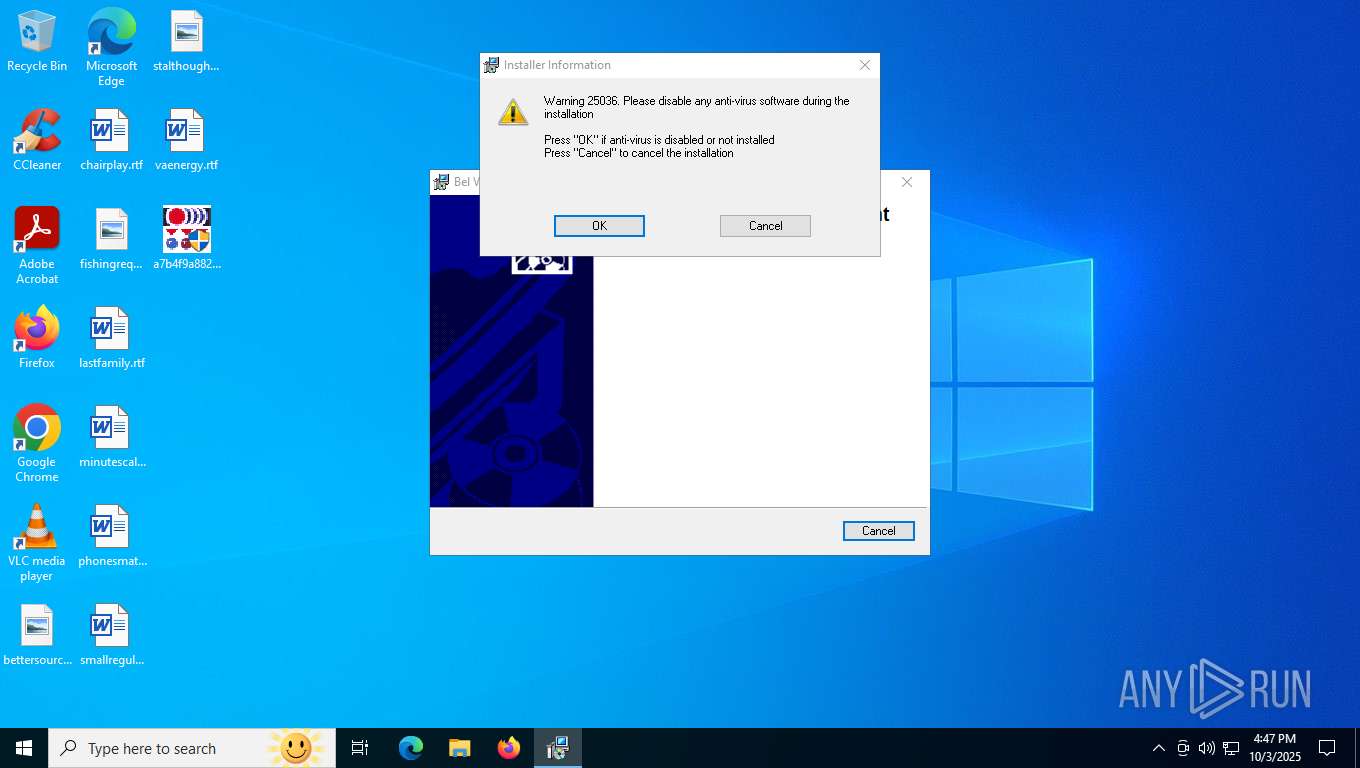
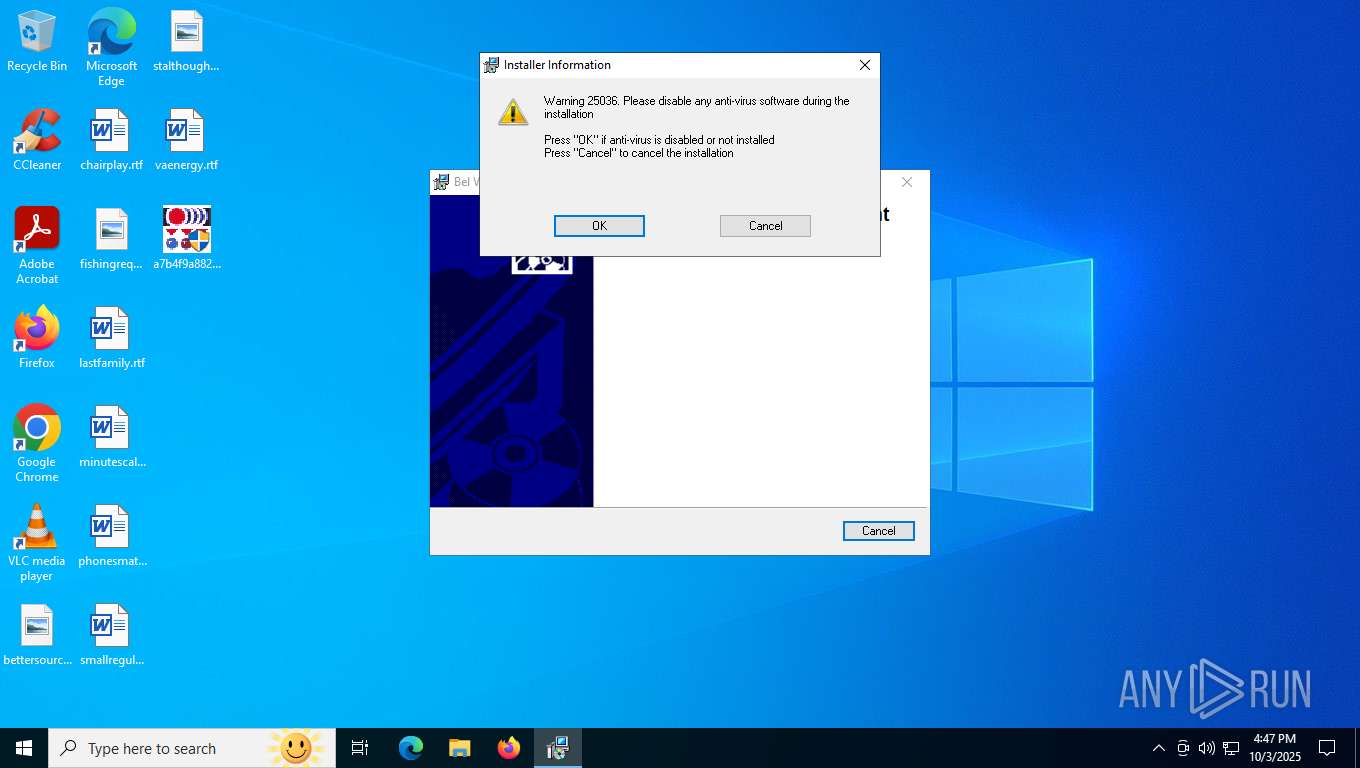
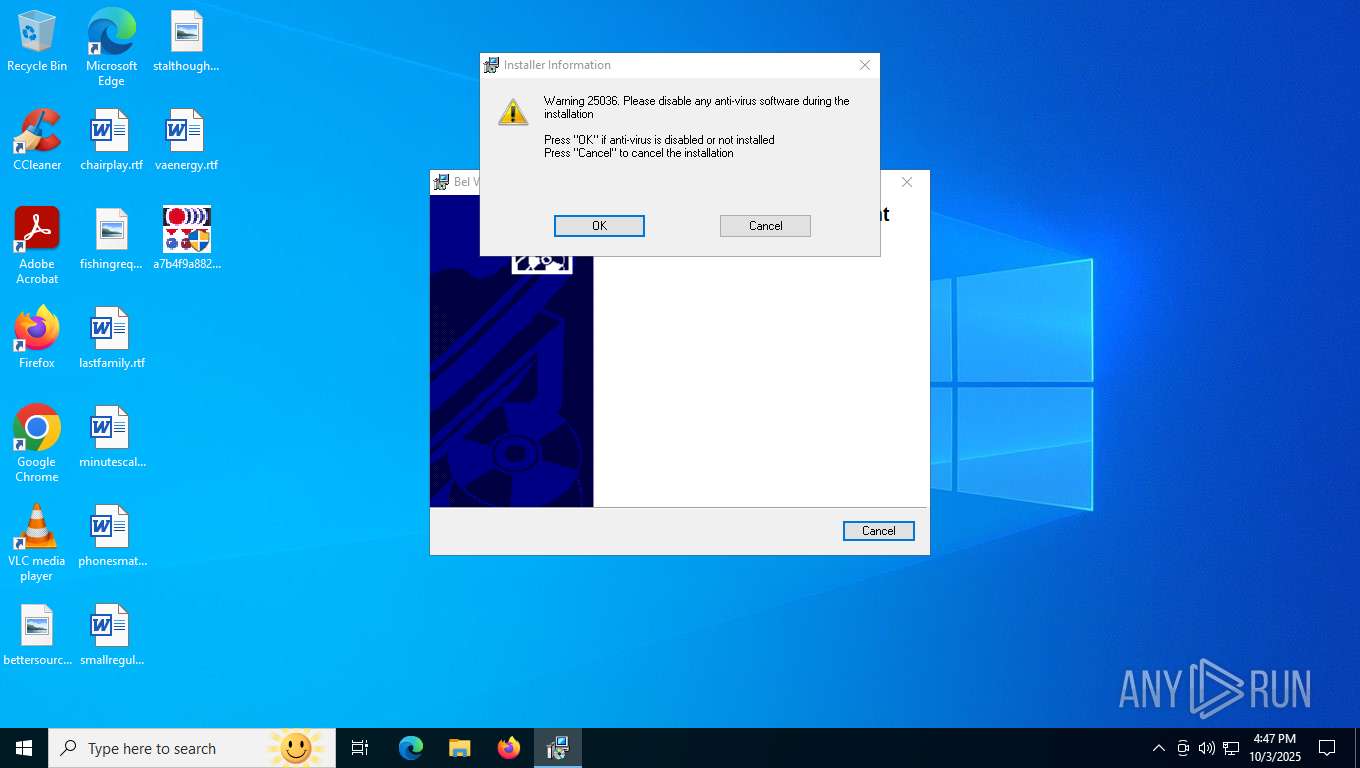
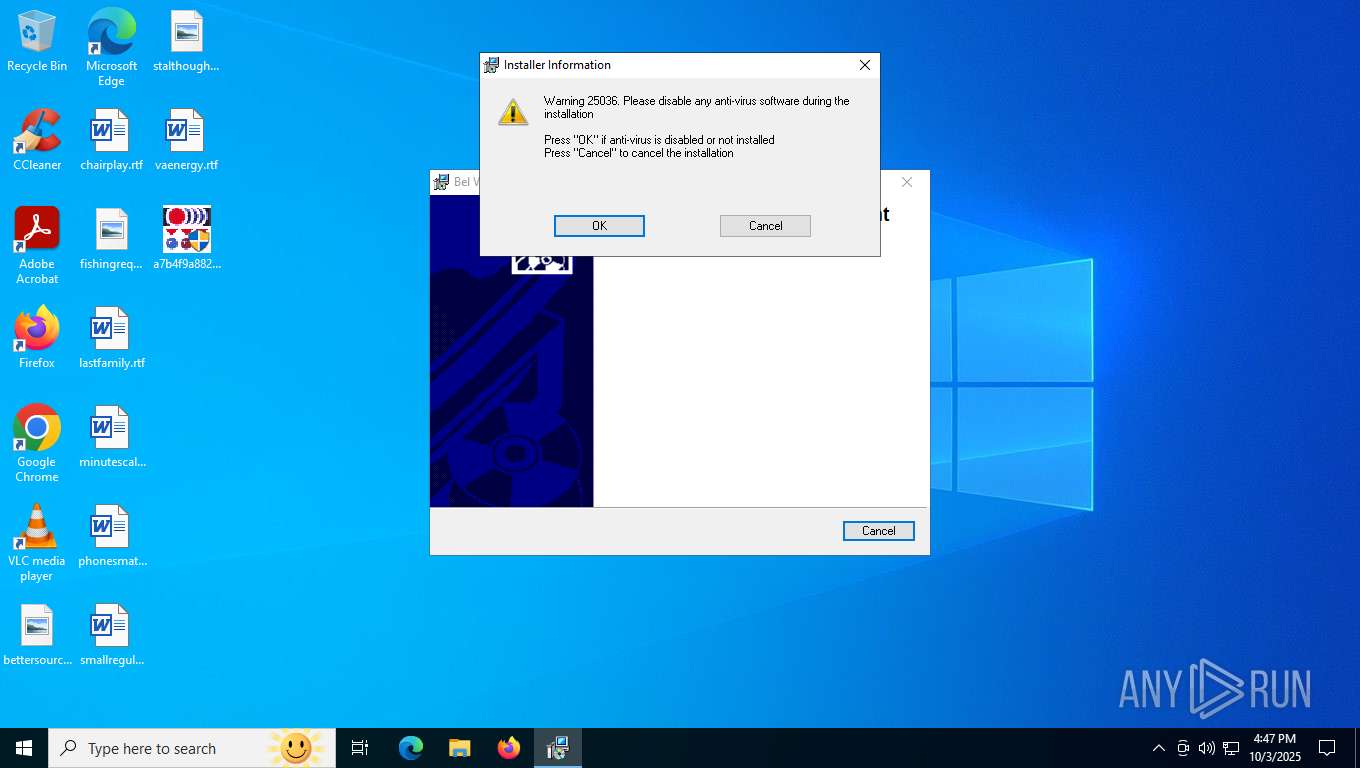
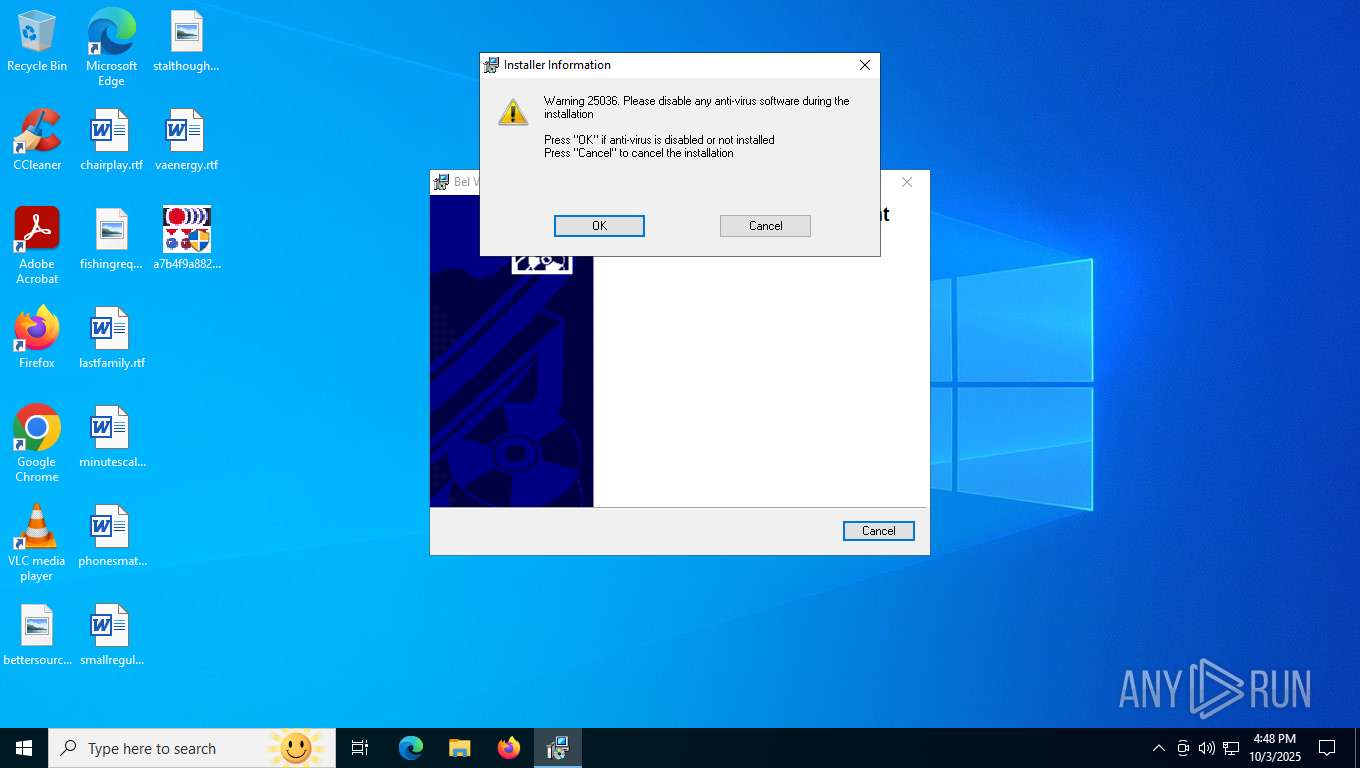
| ProductName: | Bel VPN Client |
| ProductVersion: | 4.1 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
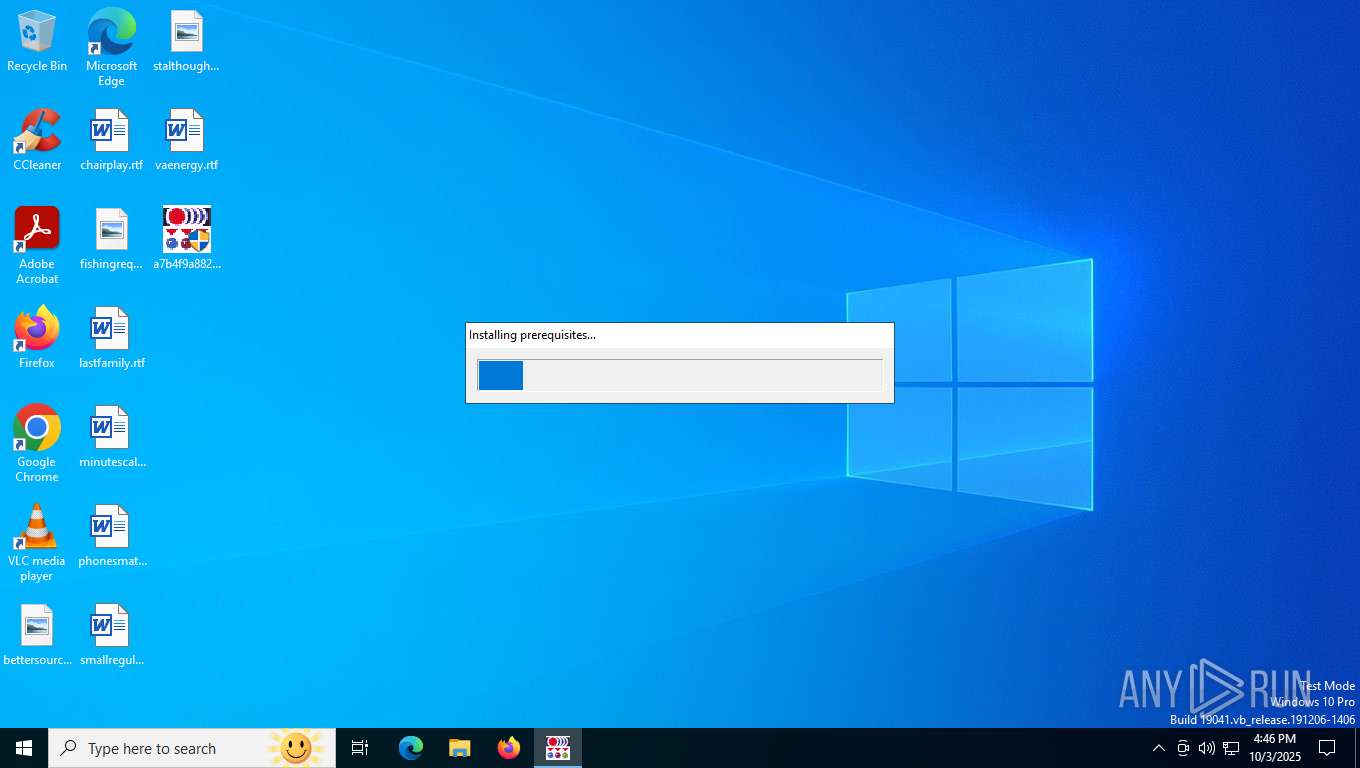
| 704 | "C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\vcredist_x64.exe" /q | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\vcredist_x64.exe | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Microsoft Visual C++ 2008 Redistributable Setup Exit code: 0 Version: 9.0.30729.01 Modules
| |||||||||||||||
| 708 | "C:\Users\admin\Desktop\a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe" | C:\Users\admin\Desktop\a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | explorer.exe | ||||||||||||
User: admin Company: S-Terra Bel Integrity Level: HIGH Version: 4.1.17758 Modules
| |||||||||||||||
| 1408 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1852 | "C:\Users\admin\Desktop\a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe" | C:\Users\admin\Desktop\a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | — | explorer.exe | |||||||||||
User: admin Company: S-Terra Bel Integrity Level: MEDIUM Exit code: 3221226540 Version: 4.1.17758 Modules
| |||||||||||||||
| 1852 | C:\WINDOWS\system32\msiexec.exe /V | C:\Windows\System32\msiexec.exe | services.exe | ||||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Windows® installer Version: 5.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3000 | c:\242a5f6ecae890d252efc3030f\.\install.exe /q | C:\242a5f6ecae890d252efc3030f\install.exe | — | vcredist_x64.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: External Installer Exit code: 0 Version: 9.0.30729.1 built by: SP Modules
| |||||||||||||||
| 4108 | C:\Windows\syswow64\MsiExec.exe -Embedding 67C7769F56C38161BD897A9A53CE20FE C | C:\Windows\SysWOW64\msiexec.exe | — | msiexec.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows® installer Version: 5.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4288 | C:\WINDOWS\winsxs\amd64_microsoft-windows-servicingstack_31bf3856ad364e35_10.0.19041.3989_none_7ddb45627cb30e03\TiWorker.exe -Embedding | C:\Windows\WinSxS\amd64_microsoft-windows-servicingstack_31bf3856ad364e35_10.0.19041.3989_none_7ddb45627cb30e03\TiWorker.exe | svchost.exe | ||||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Windows Modules Installer Worker Exit code: 0 Version: 10.0.19041.3989 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 7028 | "C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\vcredist_x86.exe" /q | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\vcredist_x86.exe | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Microsoft Visual C++ 2008 Redistributable Setup Exit code: 0 Version: 9.0.30729.01 Modules
| |||||||||||||||
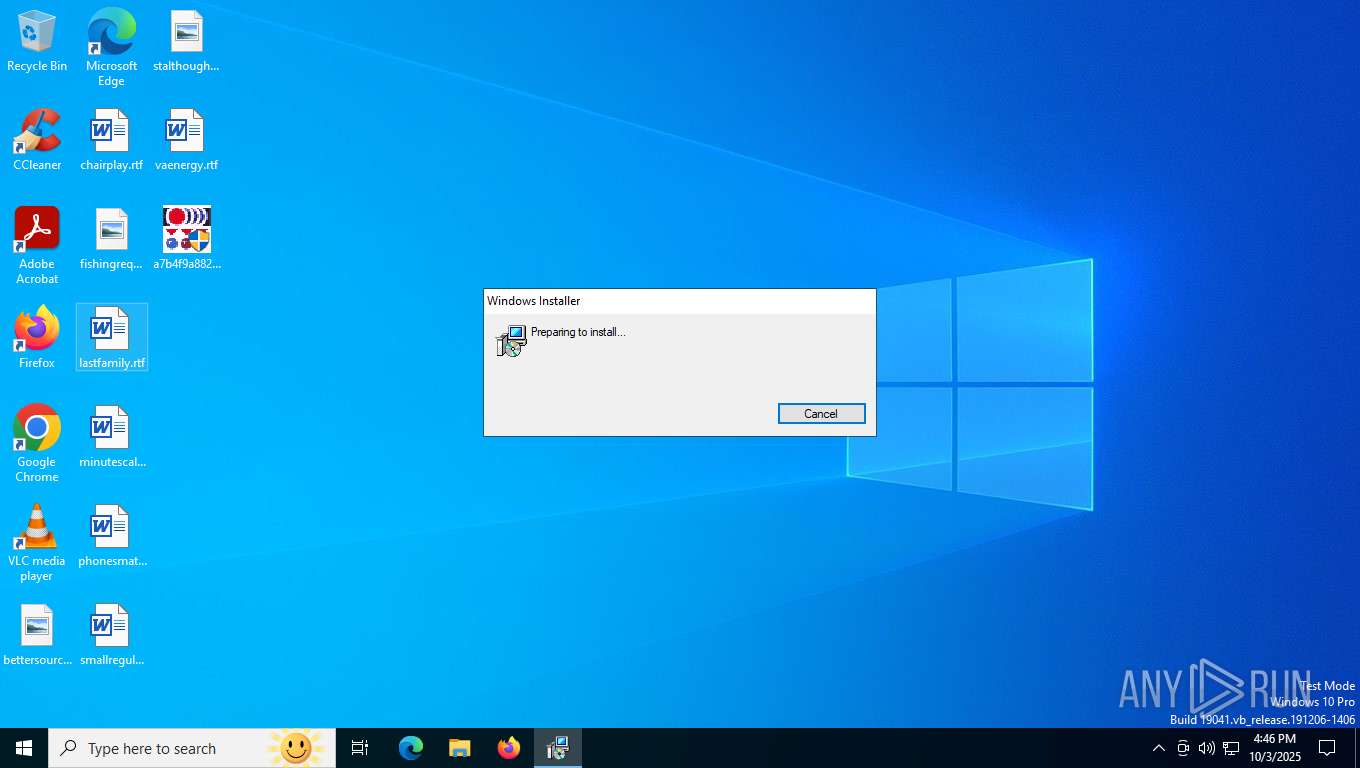
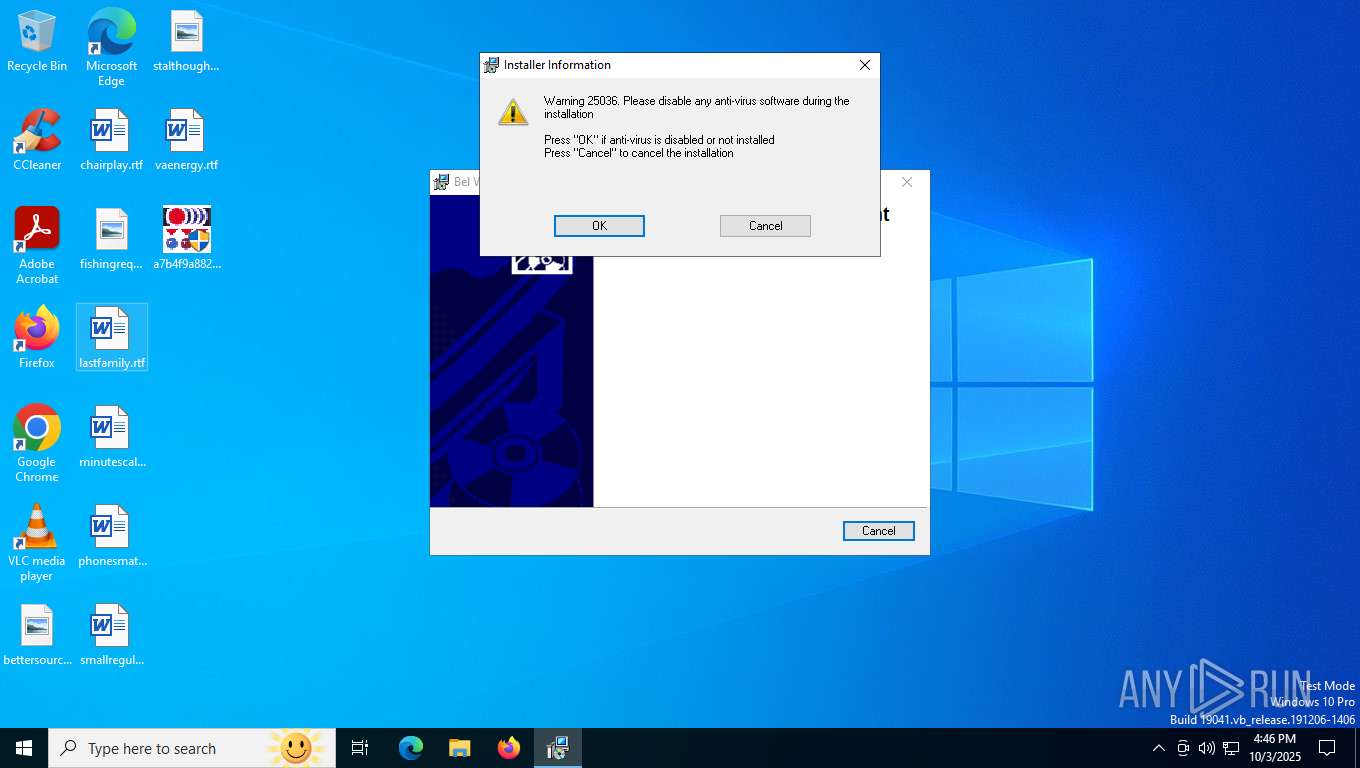
| 8000 | msiexec.exe AVPASS_DIALOG_MODE=DISABLE_EDIT_CONTAINER_NAME- LOCAL_MANAGEMENT=1 DISABLE_CALL_LOGIN=1 /i "C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\VPN_CLIENT_WIN_x64.msi" | C:\Windows\SysWOW64\msiexec.exe | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows® installer Version: 5.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (1852) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\Folders |
| Operation: | write | Name: | c:\Config.Msi\ |
Value: | |||
| (PID) Process: | (1852) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\Rollback\Scripts |
| Operation: | write | Name: | c:\Config.Msi\1765e0.rbs |
Value: 31208581 | |||
| (PID) Process: | (1852) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\Rollback\Scripts |
| Operation: | write | Name: | c:\Config.Msi\1765e0.rbsLow |
Value: 956783024 | |||
| (PID) Process: | (1852) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Components\AA5D9C68C00F12943B2F6CA09FE28244 |
| Operation: | write | Name: | F2EBB725DEF1B8D319BCD40B8F836EE9 |
Value: 02:\SOFTWARE\Microsoft\DevDiv\VC\Servicing\9.0\SP | |||
| (PID) Process: | (1852) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Components\7599622B447F37D4E970575BD92209E6 |
| Operation: | write | Name: | F2EBB725DEF1B8D319BCD40B8F836EE9 |
Value: 02:\SOFTWARE\Microsoft\DevDiv\VC\Servicing\9.0\RED\1049\Install | |||
| (PID) Process: | (1852) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Windows\CurrentVersion\SharedDlls |
| Operation: | write | Name: | c:\Program Files (x86)\Common Files\Microsoft Shared\VC\msdia90.dll |
Value: 1 | |||
| (PID) Process: | (1852) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Components\A771E8EB1E10BCE44AA8014E39DCC206 |
| Operation: | write | Name: | F2EBB725DEF1B8D319BCD40B8F836EE9 |
Value: c:\?Program Files (x86)\Common Files\Microsoft Shared\VC\msdia90.dll | |||
| (PID) Process: | (1852) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Components\D2B3EF2522FB0693FA4336E05E3EE623 |
| Operation: | write | Name: | F2EBB725DEF1B8D319BCD40B8F836EE9 |
Value: | |||
| (PID) Process: | (1852) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Components\5FAA65EA0C3FB4D388951A5EA0E372FB |
| Operation: | write | Name: | F2EBB725DEF1B8D319BCD40B8F836EE9 |
Value: >atl90.dll\Microsoft.VC90.ATL,version="9.0.30729.1",publicKeyToken="1fc8b3b9a1e18e3b",processorArchitecture="x86",type="win32" | |||
| (PID) Process: | (1852) msiexec.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Installer\UserData\S-1-5-18\Components\6E5749FF32D22E334AADA52C638EE202 |
| Operation: | write | Name: | F2EBB725DEF1B8D319BCD40B8F836EE9 |
Value: | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 708 | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\VPN_CLIENT_WIN_common.cab | — | |
MD5:— | SHA256:— | |||
| 708 | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\OCI\db\keys\00000002.dsc | text | |
MD5:12504B20079613C5D9E05747D442DD5E | SHA256:D3D24BD2E0EC10AB9125737E8AD4CCAEA9B1B78D2286F37A5FC1FB853EA07D77 | |||
| 708 | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\OCI\db\lsps\00000004.dsc | text | |
MD5:159103E8FC3727147B0675F16C842917 | SHA256:40CFB725F742ADB704E423EC6FC91D06AF778C2D675EEF2C597A4D03EE793960 | |||
| 708 | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\OCI\db\keys\00000001 | binary | |
MD5:03564CD707913C5ECC4A2807A70D05BA | SHA256:F23BAC00C02F6B57ABB2E63636D29386DD01DFDF2B93801781331A0A813D7208 | |||
| 708 | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\OCI\db\settings\log_set.dsc.hash | text | |
MD5:246DC68A3B06C7A4E9EA328854AD91E8 | SHA256:49C8ABCE1909DE7F5B66220C9F9DCD36B9EEE9994D09805AF0366755EE06A9E2 | |||
| 708 | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\OCI\db\settings\log_set.dsc | text | |
MD5:4D1A04F30FF5399BF53C2490EEF00CA1 | SHA256:AEBFC0D0940B57FD988D497DAAB35D140EB9F228FEFCE1DAB70FDE25ED9E5A34 | |||
| 708 | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\OCI\db\settings\users.dsc | text | |
MD5:3C4E41DA9035E076DC1D8FF1A8D93B5F | SHA256:218F3882CE27CF2BB35E8F6A6778C533BB894022F5F70C10050FE2EDF916EEA2 | |||
| 708 | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\OCI\db\lsps\00000003 | binary | |
MD5:477F4D788926B697F0476071BBC0436A | SHA256:64F5FE925B55896E1B7FBE44C7E4764BC8EF821FEC605E3ABDDC9103A240B91F | |||
| 708 | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\VPN_CLIENT_WIN_hashes_x64.cab | compressed | |
MD5:0F8570CE27CB5BCA53D6AE86D3E948AA | SHA256:EB68F3DAD3F6EB5B65FCEDE15ED813603C332F260500BAD1B268037322D2F1CA | |||
| 708 | a7b4f9a882d83b21fcb2f1d9ac479af3395d2dab0cbcc0324f1464bd3cb9c01b.exe | C:\Users\admin\AppData\Local\Temp\~TempSfxDir2\vcredist_x86.exe | executable | |
MD5:B93E5505F59CF6C5FD2FB1CA2A74A520 | SHA256:155863F6B293D1D50EDB814BB11A1A7A285F286CEDE36860DA4AFF9ED2BD8F49 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
— | — | GET | 200 | 95.101.136.201:443 | https://www.bing.com/DSB/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=US&setlang=en-us&clientDateTime=10%2F3%2F2025%2C%204%3A45%3A57%20PM | unknown | binary | 64.1 Kb | unknown |
— | — | POST | 200 | 40.126.32.138:443 | https://login.live.com/RST2.srf | US | xml | 11.0 Kb | unknown |
— | — | GET | 200 | 95.101.136.194:443 | https://www.bing.com/th?id=ODSWG.8229b0e5-fa8c-4e4a-af74-69717698b903&pid=dsb | unknown | image | 4.62 Kb | unknown |
— | — | GET | 200 | 20.31.169.57:443 | https://arc.msn.com/v3/Delivery/Placement?pubid=da63df93-3dbc-42ae-a505-b34988683ac7&pid=88000045&adm=2&w=1&h=1&wpx=1&hpx=1&fmt=json&cltp=app&dim=le&rafb=0&nct=1&pm=1&cfmt=text,image,poly&sft=jpeg,png,gif&topt=1&poptin=0&localid=w:AC7699B0-48EA-FD22-C8DC-06A02098A0F0&ctry=US&time=20251003T164558Z&lc=en-US&pl=en-US&idtp=mid&uid=9115d6d1-9f4e-4053-9297-2a8c833b3912&aid=00000000-0000-0000-0000-000000000000&ua=WindowsShellClient%2F9.0.40929.0%20%28Windows%29&asid=1f3fa818c77845f1bea10262a5199367&ctmode=MultiSession&arch=x64&betaedgever=0.0.0.0&canedgever=0.0.0.0&cdm=1&cdmver=10.0.19041.3636&currsel=137271744000000000&devedgever=0.0.0.0&devfam=Windows.Desktop&devform=Unknown&devosver=10.0.19045.4046&disphorzres=1360&dispsize=16.3&dispvertres=768&fosver=16299&isu=0&lo=4245645&metered=false&nettype=ethernet&npid=sc-88000045&oemName=DELL&oemid=DELL&ossku=Professional&prevosver=15063&smBiosDm=DELL&stabedgever=133.0.3065.92&tl=2&tsu=1636175&waasBldFlt=1&waasCfgExp=1&waasCfgSet=1&waasRetail=1&waasRing=&svoffered=2 | US | binary | 3.21 Kb | unknown |
— | — | POST | 200 | 40.126.32.72:443 | https://login.live.com/RST2.srf | US | xml | 11.3 Kb | unknown |
1852 | msiexec.exe | GET | 200 | 23.216.77.18:80 | http://crl.microsoft.com/pki/crl/products/CSPCA.crl | DE | binary | 506 b | whitelisted |
— | — | POST | 204 | 95.101.136.201:443 | https://www.bing.com/web/xlsc.aspx?t=5&dl=1&wsbc=1 | unknown | — | — | unknown |
— | — | GET | 200 | 74.178.240.61:443 | https://slscr.update.microsoft.com/sls/ping | US | — | — | unknown |
— | — | POST | 200 | 20.190.160.4:443 | https://login.live.com/RST2.srf | US | xml | 11.1 Kb | unknown |
— | — | GET | 200 | 74.178.240.61:443 | https://slscr.update.microsoft.com/SLS/%7B522D76A4-93E1-47F8-B8CE-07C937AD1A1E%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL | US | compressed | 27.7 Kb | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
6016 | MoUsoCoreWorker.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
5948 | svchost.exe | 51.124.78.146:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
5224 | SearchApp.exe | 2.16.241.222:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
4312 | svchost.exe | 40.126.31.0:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5360 | backgroundTaskHost.exe | 2.16.241.222:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
3464 | svchost.exe | 172.211.123.249:443 | client.wns.windows.com | MICROSOFT-CORP-MSN-AS-BLOCK | FR | whitelisted |
6340 | backgroundTaskHost.exe | 20.31.169.57:443 | arc.msn.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
www.bing.com |
| whitelisted |
login.live.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
arc.msn.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |