ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
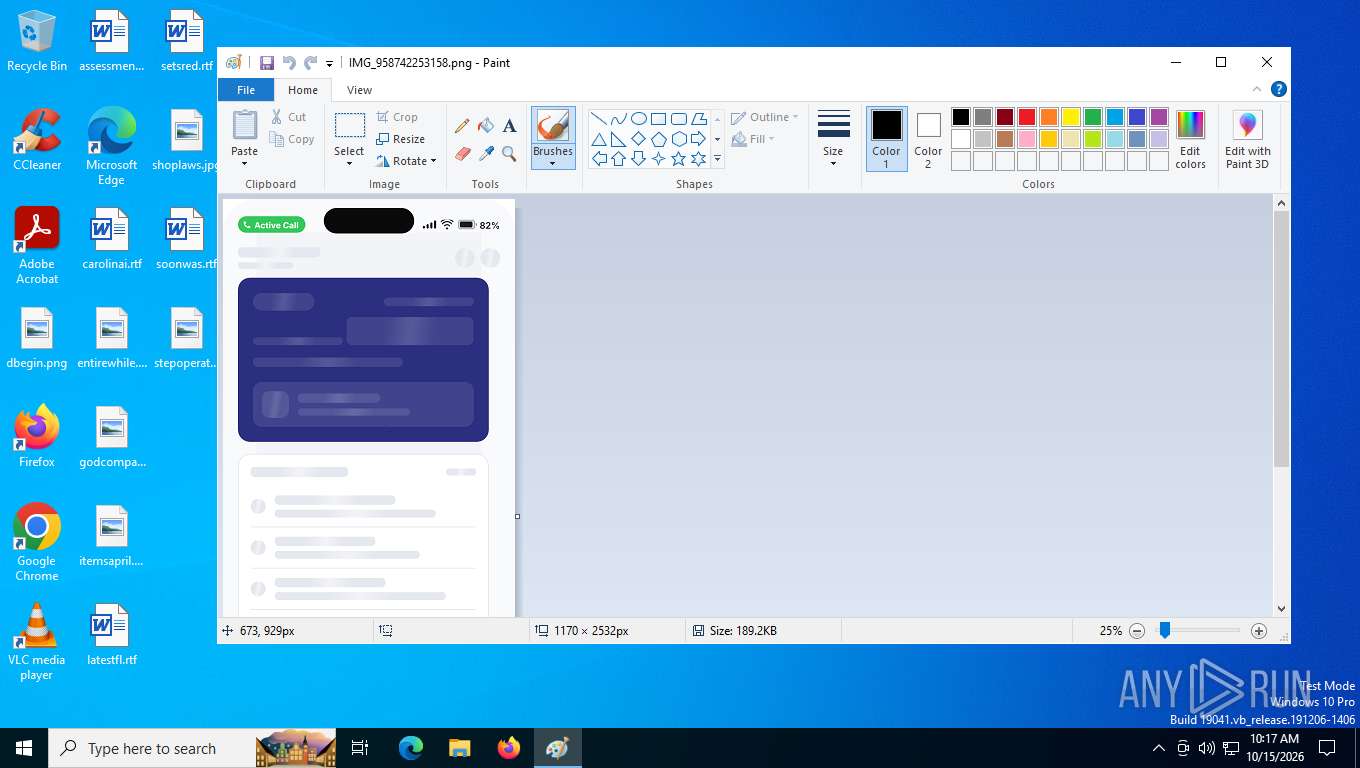
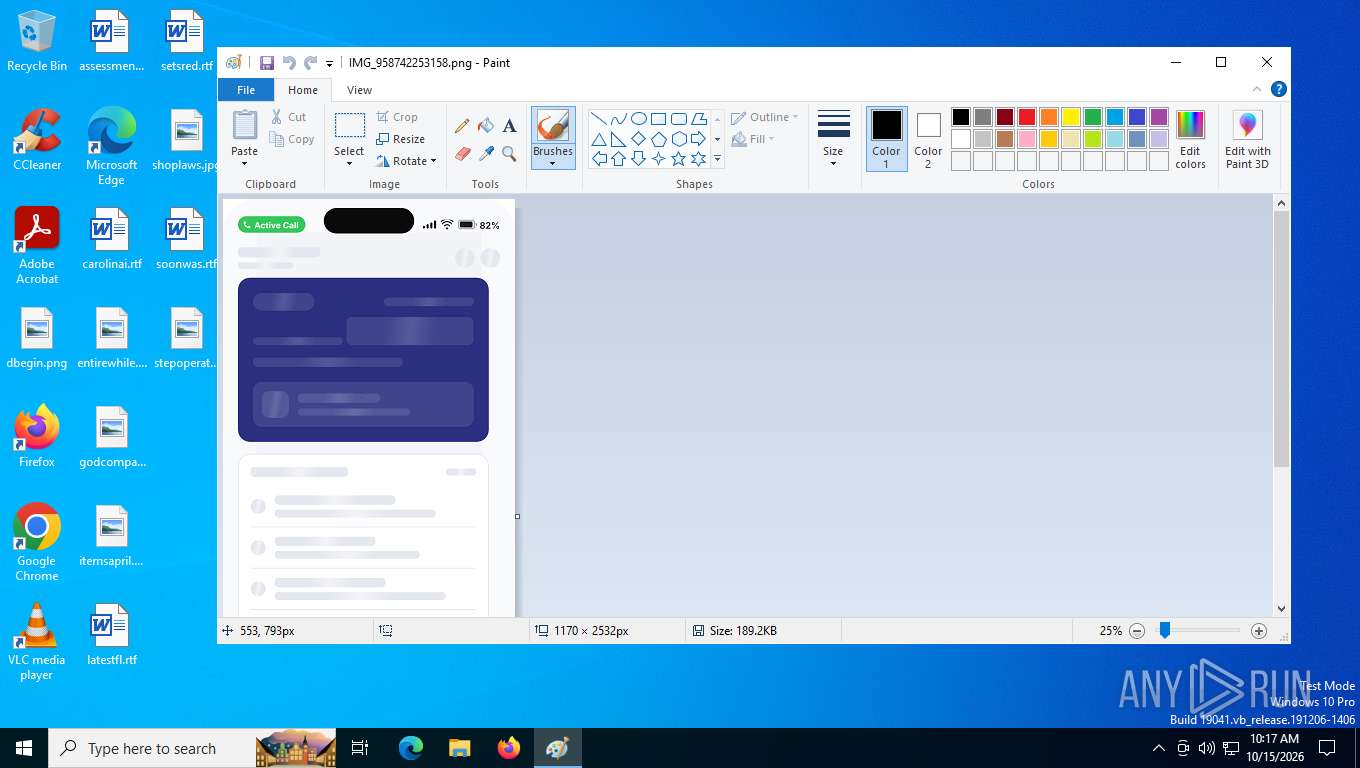
| File name: | IMG_958742253158.scr |
| Full analysis: | https://app.any.run/tasks/2af2b954-72a8-475d-b94c-a726d8ded008 |
| Verdict: | Malicious activity |
| Analysis date: | October 15, 2026, 14:12:33 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32+ executable (GUI) x86-64, for MS Windows, 7 sections |
| MD5: | 8772DCE19DE3EEC069559FE06557572D |
| SHA1: | 867F19FDD663CC4D589CA54B5CA1BCA56979B145 |
| SHA256: | 9B43BB4E22B438EF28EA41F29C755D71A825950C70A11FA9C569DD02BCA91129 |
| SSDEEP: | 12288:bjyjUBzZJX3n+cjCDio7dnSroBe4T7iG6ZZJPn6cj:beUxC7dSroE4XiGEZJf6cj |
| .exe | | | Generic Win/DOS Executable (50) |
|---|---|---|
| .exe | | | DOS Executable Generic (50) |
| MachineType: | AMD AMD64 |
|---|---|
| TimeStamp: | 2026:09:30 02:37:23+00:00 |
| ImageFileCharacteristics: | Executable, Large address aware |
| PEType: | PE32+ |
| LinkerVersion: | 14.44 |
| CodeSize: | 102400 |
| InitializedDataSize: | 329728 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x4f88 |
| OSVersion: | 6 |
| ImageVersion: | - |
| SubsystemVersion: | 6 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 1.0.0.0 |
| ProductVersionNumber: | 1.0.0.0 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Windows NT 32-bit |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | English (U.S.) |
| CharacterSet: | Unicode |
| CompanyName: | SOFTWARE DYNAMICS AS |
| FileDescription: | Advanced Photo Viewer |
| FileVersion: | 1.0.0.0 |
| InternalName: | MS |
| LegalCopyright: | Copyright (C) 2026 SOFTWARE DYNAMICS AS |
| ProductName: | Photo Viewer |
| ProductVersion: | 1.0.0.0 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 872 | C:\WINDOWS\explorer.exe /factory,{75dff2b7-6936-4c06-a8bb-676a7b00b24b} -Embedding | C:\Windows\explorer.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Explorer Exit code: 1 Version: 10.0.19041.3758 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1160 | C:\WINDOWS\System32\WaaSMedicAgent.exe a3636d97d4115e1ec2935548efc6dbcf O1I47K4Tr0KohLsOcu0U5Q.0.1.0.0.0 | C:\Windows\System32\WaaSMedicAgent.exe | — | svchost.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: WaasMedic Agent Exe Exit code: 0 Version: 10.0.19041.3758 (WinBuild.160101.0800) Modules
| |||||||||||||||
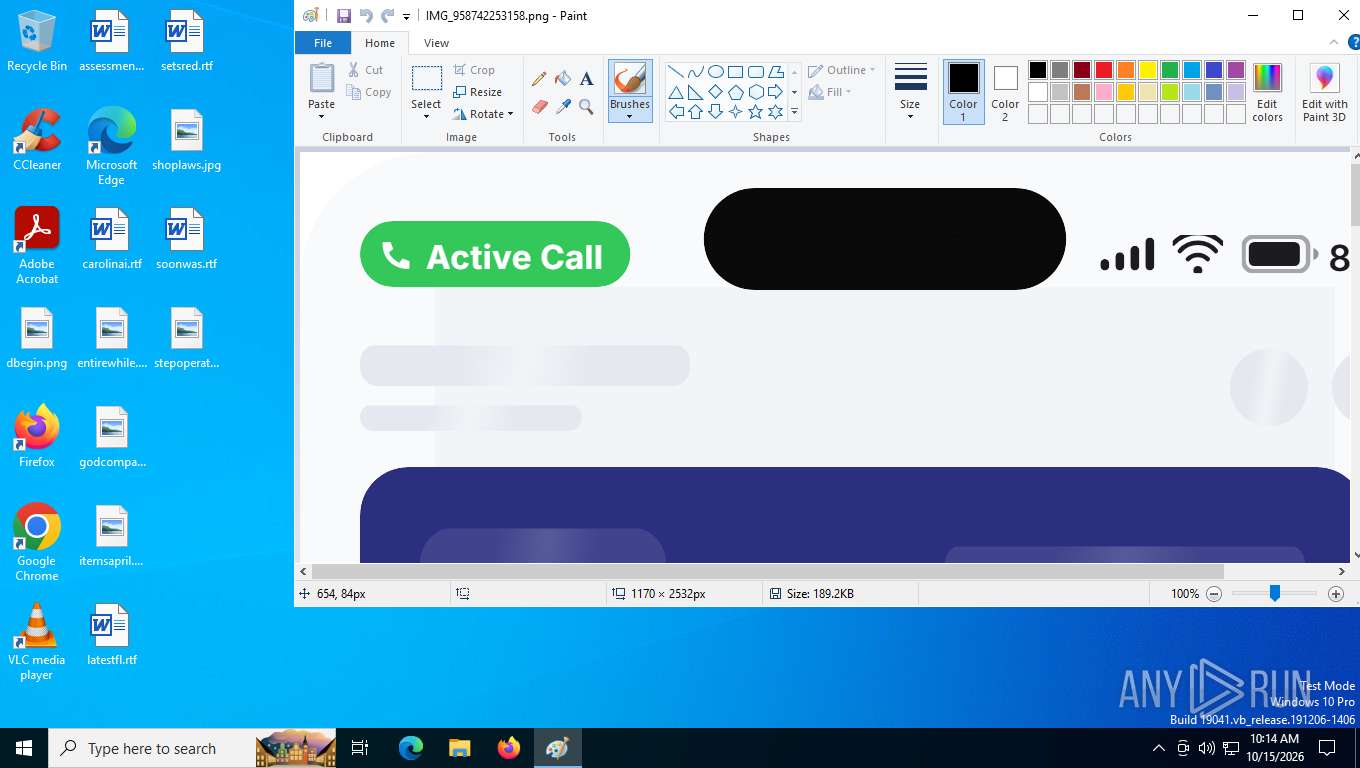
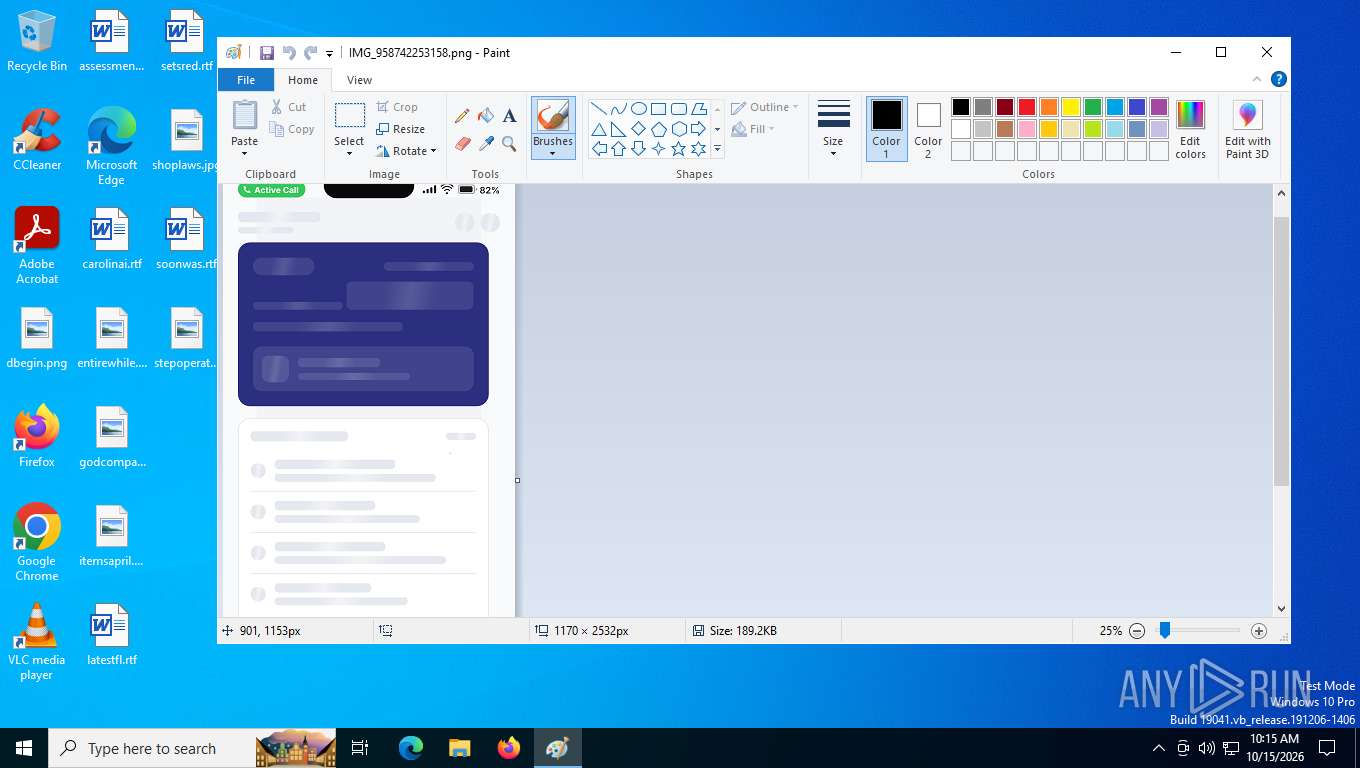
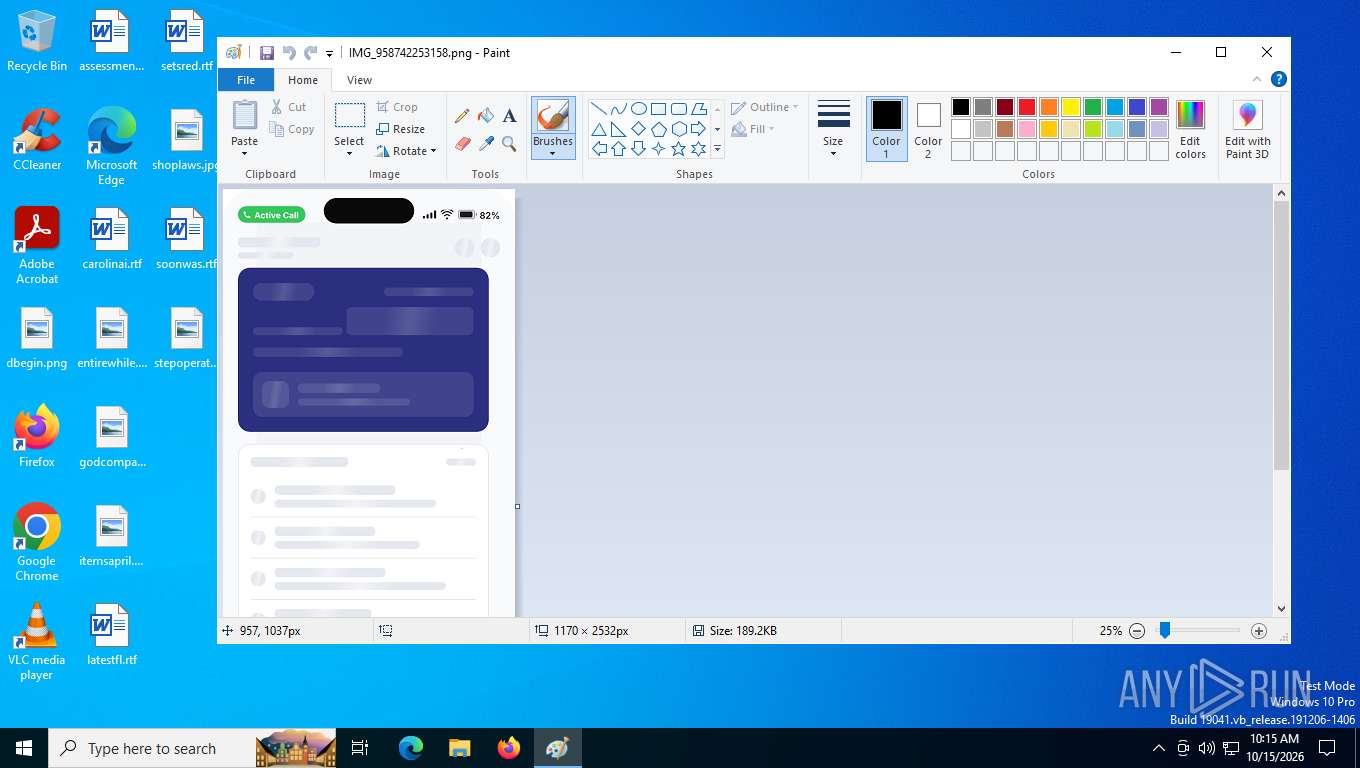
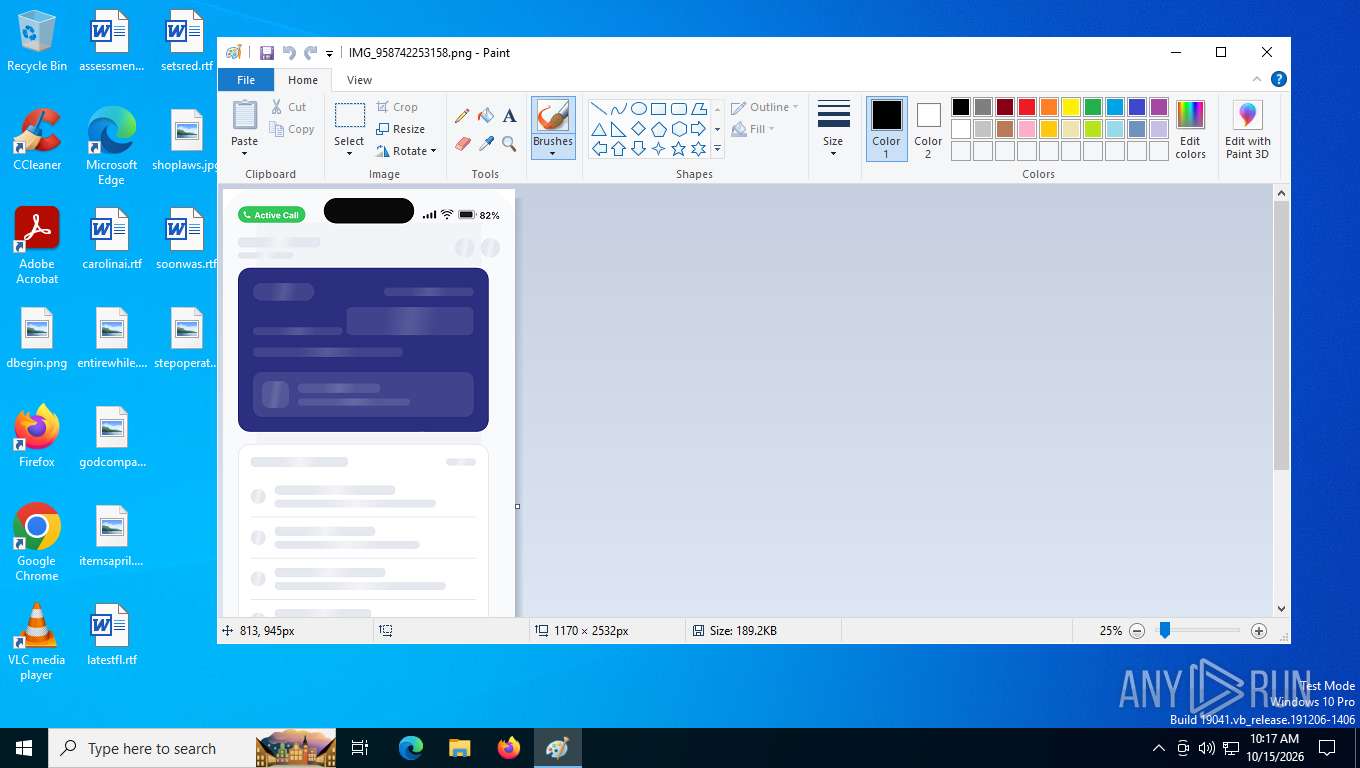
| 1656 | "C:\WINDOWS\system32\mspaint.exe" "C:\Users\admin\AppData\Local\IMG_958742253158.png" | C:\Windows\System32\mspaint.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Paint Exit code: 0 Version: 10.0.19041.3758 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3216 | "C:\Users\admin\AppData\Local\Temp\IMG_958742253158.scr.exe" | C:\Users\admin\AppData\Local\Temp\IMG_958742253158.scr.exe | explorer.exe | ||||||||||||
User: admin Company: SOFTWARE DYNAMICS AS Integrity Level: MEDIUM Description: Advanced Photo Viewer Exit code: 0 Version: 1.0.0.0 Modules
| |||||||||||||||
| 4152 | C:\WINDOWS\system32\cmd.exe /c "net config workstation" | C:\Windows\SysWOW64\cmd.exe | — | winsec.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 0 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5556 | C:\WINDOWS\system32\wbem\wmiprvse.exe -secured -Embedding | C:\Windows\System32\wbem\WmiPrvSE.exe | — | svchost.exe | |||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: WMI Provider Host Exit code: 0 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5672 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | WaaSMedicAgent.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5796 | net config workstation | C:\Windows\SysWOW64\net.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Net Command Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6008 | explorer.exe "C:\Users\admin\AppData\Local\IMG_958742253158.png" | C:\Windows\explorer.exe | — | IMG_958742253158.scr.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Explorer Exit code: 1 Version: 10.0.19041.3758 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6184 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3216 | IMG_958742253158.scr.exe | C:\Users\admin\AppData\Local\IMG_958742253158.png | media | |
MD5:42B692CDC9BB3C79A787A577CD1450E4 | SHA256:3E8E8BC8D856C73BCF6608490772C543D7C063CEC3D51A985ACF2BD425380975 | |||
| 3216 | IMG_958742253158.scr.exe | C:\Users\admin\AppData\Local\Wavesoft\6f2c634d-43a6-47e2-9998-daa308fca28d\python3.dll | executable | |
MD5:DD07013785E2BB606293FC3EC6467FCF | SHA256:34DA45B57BAEC57D1193901D24E9DC9DD23EECCD0776B016072B311DF1FF8379 | |||
| 3216 | IMG_958742253158.scr.exe | C:\Users\admin\AppData\Local\Wavesoft\6f2c634d-43a6-47e2-9998-daa308fca28d\python39.dll | executable | |
MD5:2A9C5DB70C6906571F2CA3A07521BAA2 | SHA256:C69CE89B0487D86A63B64951207781F8051282AFDE67B20D3B8374C1A067F611 | |||
| 3216 | IMG_958742253158.scr.exe | C:\Users\admin\AppData\Local\Wavesoft\6f2c634d-43a6-47e2-9998-daa308fca28d\DLLs\libssl-1_1.dll | executable | |
MD5:697766ABA55F44BBD896CBD091A72B55 | SHA256:44A228B3646EB3575ABD5CBCB079E018DE11CA6B838A29E4391893DE69E0CF4B | |||
| 3216 | IMG_958742253158.scr.exe | C:\Users\admin\AppData\Local\Wavesoft\6f2c634d-43a6-47e2-9998-daa308fca28d\DLLs\pyc.ico | media | |
MD5:B1C9980131A3F20E344AA3AA2C8DEA49 | SHA256:FDA28A734788A3F175CB6AED4DAEB5F05F0E49F6A272CCD2051BA337F7B3B42F | |||
| 3216 | IMG_958742253158.scr.exe | C:\Users\admin\AppData\Local\Wavesoft\6f2c634d-43a6-47e2-9998-daa308fca28d\DLLs\pyexpat.pyd | executable | |
MD5:3E43BCC2897F193512990E9E9024111B | SHA256:0D8AC2A2B81176A06B0FB8663702428D2CDD5BEDEAB68B04210BF5CB6B49A475 | |||
| 3216 | IMG_958742253158.scr.exe | C:\Users\admin\AppData\Local\Wavesoft\6f2c634d-43a6-47e2-9998-daa308fca28d\vcruntime140.dll | executable | |
MD5:55C8E69DAB59E56951D31350D7A94011 | SHA256:9D8D21022FF9D3F6B81A45209662A4F3481EDC2BEFAE0C73B83CF942EAB8BE25 | |||
| 3216 | IMG_958742253158.scr.exe | C:\Users\admin\AppData\Local\Wavesoft\6f2c634d-43a6-47e2-9998-daa308fca28d\winsec.exe | executable | |
MD5:1F6CE27A40898EF68562D9C5EAB4D2AB | SHA256:EA80F95FB9ACCD5059C0734B1F4BCC56AA07FD939376D4A13B733252AC26338E | |||
| 3216 | IMG_958742253158.scr.exe | C:\Users\admin\AppData\Local\Wavesoft\6f2c634d-43a6-47e2-9998-daa308fca28d\DLLs\py.ico | media | |
MD5:B35F68A3086562C4D5453FAAD5A3474E | SHA256:150C470F9943B806B44312EFDEC85755F22F8D7D52B31F93A9AF3C43E8627381 | |||
| 3216 | IMG_958742253158.scr.exe | C:\Users\admin\AppData\Local\Wavesoft\6f2c634d-43a6-47e2-9998-daa308fca28d\DLLs\python_tools.cat | other | |
MD5:31E8F0578AA477296E11A2E4C893C714 | SHA256:DCAB3ECF3F8BEF065AA505C2DB8EF9BB140B1CE4D256746E0E14C8A70FBC01AC | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
5180 | svchost.exe | GET | 304 | 48.209.6.48:443 | https://settings-win.data.microsoft.com/settings/v3.0/WSD/WaaSAssessment?os=Windows&osVer=10.0.19041.1.amd64fre.vb_release.191206-&ring=Retail&sku=48&deviceClass=Windows.Desktop&locale=en-US&deviceId=BAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&FlightRing=Retail&TelemetryLevel=1&HidOverGattReg=C%3A%5CWINDOWS%5CSystem32%5CDriverStore%5CFileRepository%5Chidbthle.inf_amd64_9610b4821fdf82a5%5CMicrosoft.Bluetooth.Profiles.HidOverGatt.dll&AppVer=10.0&ProcessorIdentifier=AMD64%20Family%2023%20Model%201%20Stepping%202&OEMModel=DELL&UpdateOfferedDays=4294967295&ProcessorManufacturer=AuthenticAMD&InstallDate=1661339444&OEMModelBaseBoard=&BranchReadinessLevel=CB&OEMSubModel=J5CR&IsCloudDomainJoined=0&DeferFeatureUpdatePeriodInDays=30&IsDeviceRetailDemo=0&FlightingBranchName=&OSUILocale=en-US&DeviceFamily=Windows.Desktop&WuClientVer=10.0.19041.3996&UninstallActive=1&IsFlightingEnabled=0&OSSkuId=48&ProcessorClockSpeed=3094&TotalPhysicalRAM=6144&SecureBootCapable=0&App=WaaSAssessment&ProcessorCores=6&CurrentBranch=vb_release&InstallLanguage=en-US&DeferQualityUpdatePeriodInDays=0&ServicingBranch=CB&OEMName_Uncleaned=DELL&TPMVersion=0&PrimaryDiskTotalCapacity=262144&InstallationType=Client&AttrDataVer=186&ProcessorModel=AMD%20Ryzen%205%203500%206-Core%20Processor&IsEdgeWithChromiumInstalled=1&OSVersion=10.0.19045.4046&IsMDMEnrolled=0&ActivationChannel=Retail&HonorWUfBDeferrals=0&FirmwareVersion=A.40&TrendInstalledKey=1&OSArchitecture=AMD64&DefaultUserRegion=244&UpdateManagementGroup=2 | US | — | — | whitelisted |
6644 | SIHClient.exe | GET | 304 | 74.178.240.61:443 | https://slscr.update.microsoft.com/SLS/%7B522D76A4-93E1-47F8-B8CE-07C937AD1A1E%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL | US | — | — | whitelisted |
6644 | SIHClient.exe | GET | 200 | 135.233.95.135:443 | https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping | US | — | — | whitelisted |
6644 | SIHClient.exe | GET | 200 | 74.178.240.61:443 | https://slscr.update.microsoft.com/sls/ping | US | — | — | whitelisted |
6644 | SIHClient.exe | GET | 304 | 74.178.240.61:443 | https://slscr.update.microsoft.com/SLS/%7BE7A50285-D08D-499D-9FF8-180FDC2332BC%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL | US | — | — | whitelisted |
7404 | svchost.exe | POST | 400 | 20.190.160.65:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text/data | 203 b | whitelisted |
7404 | svchost.exe | POST | 200 | 20.190.160.65:443 | https://login.live.com/RST2.srf | US | web | 11.1 Kb | whitelisted |
7404 | svchost.exe | POST | 200 | 20.190.160.65:443 | https://login.live.com/RST2.srf | US | web | 10.3 Kb | whitelisted |
7404 | svchost.exe | GET | 200 | 23.11.40.157:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAz1vQYrVgL0erhQLCPM8GY%3D | NL | other | 471 b | whitelisted |
7676 | svchost.exe | GET | 200 | 150.171.109.107:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | US | other | 870 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 23.44.215.153:443 | — | AKAMAI-ASN1 | NL | whitelisted |
— | — | 172.211.123.249:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
7404 | svchost.exe | 20.190.160.65:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
— | — | 48.209.138.168:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5616 | SearchApp.exe | 23.44.215.153:443 | — | AKAMAI-ASN1 | NL | whitelisted |
7404 | svchost.exe | 23.11.40.157:80 | ocsp.digicert.com | AKAMAI-AMS | NL | whitelisted |
7676 | svchost.exe | 150.171.109.107:80 | crl.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
— | — | 23.11.40.157:80 | ocsp.digicert.com | AKAMAI-AMS | NL | whitelisted |
7676 | svchost.exe | 2.23.10.85:80 | www.microsoft.com | AKAMAI-AS | US | whitelisted |
— | — | 204.79.197.203:80 | oneocsp.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
login.live.com |
| whitelisted |
settings-win.data.microsoft.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
oneocsp.microsoft.com |
| whitelisted |
th.bing.com |
| whitelisted |
msvci.com |
| unknown |
ecs.office.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2228 | svchost.exe | Misc activity | INFO [ANY.RUN] .cc TLD domain request |
7848 | winsec.exe | Misc activity | INFO [ANY.RUN] Python requests User-agent in HTTP request |
7848 | winsec.exe | Not Suspicious Traffic | INFO [ANY.RUN] Websocket Upgrade Request |