ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
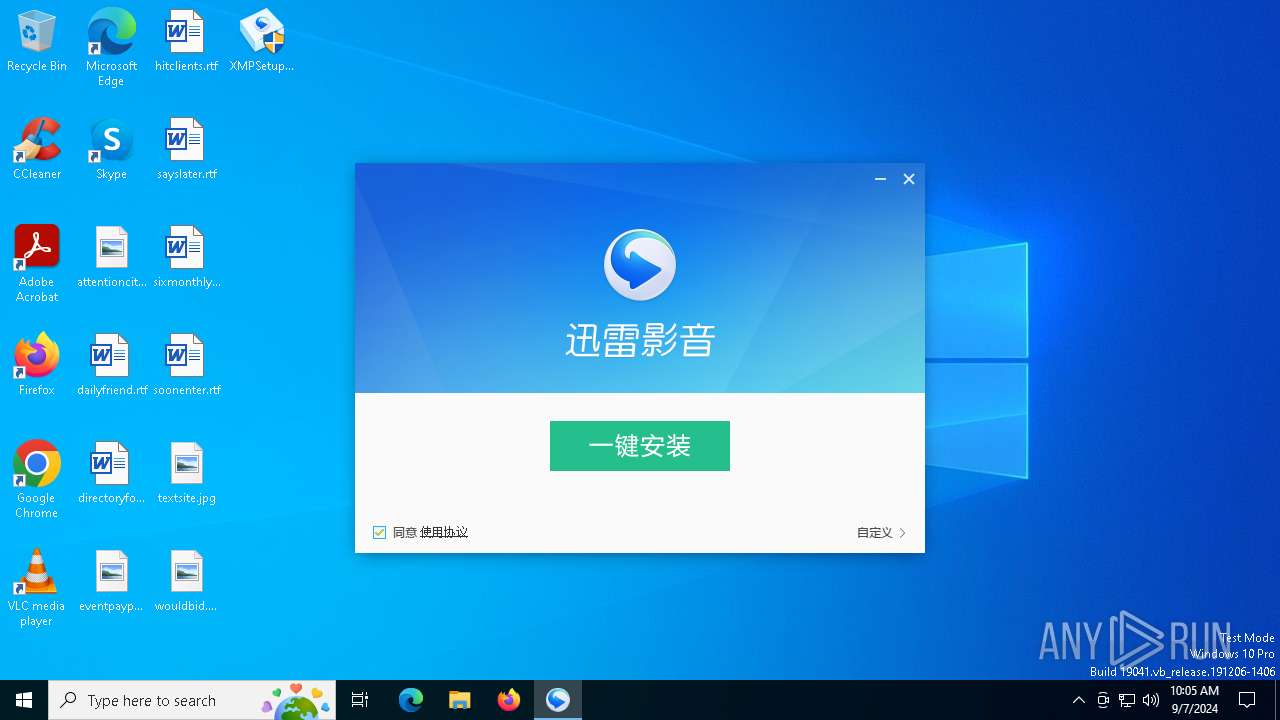
| File name: | XMPSetupKankan.exe |
| Full analysis: | https://app.any.run/tasks/6844e1e6-9f82-488b-af0b-ee42f304d4a5 |
| Verdict: | Malicious activity |
| Analysis date: | September 07, 2024, 10:05:27 |
| OS: | Windows 10 Professional (build: 19045, 64 bit) |
| Indicators: | |
| MIME: | application/x-dosexec |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows |
| MD5: | 1233C6ABAA32971CA49597373485F6F0 |
| SHA1: | 339B7E979BDB64AFF037BE8FB2982BB88E78371D |
| SHA256: | 94D6A3E72E8E3479FCF2B3D71ED0E2B91B483C60BE298144B41089A61F296055 |
| SSDEEP: | 196608:gmTaTPgmdViv/bUbwuuljNPmiX2ghz1PBU+vE9vcidTaBMV:gmebk/gbtmhmiX2gz589vcUa2 |
| .exe | | | InstallShield setup (54.3) |
|---|---|---|
| .exe | | | Win64 Executable (generic) (34.8) |
| .exe | | | Win32 Executable (generic) (5.6) |
| .exe | | | Generic Win/DOS Executable (2.5) |
| .exe | | | DOS Executable Generic (2.5) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2017:05:04 02:54:31+00:00 |
| ImageFileCharacteristics: | No relocs, Executable, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 9 |
| CodeSize: | 238080 |
| InitializedDataSize: | 29401600 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x232ae |
| OSVersion: | 5 |
| ImageVersion: | - |
| SubsystemVersion: | 5 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 5.2.18.5894 |
| ProductVersionNumber: | 5.2.18.5894 |
| FileFlagsMask: | 0x0017 |
| FileFlags: | (none) |
| FileOS: | Win32 |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | Chinese (Simplified) |
| CharacterSet: | Unicode |
| FileDescription: | 迅雷影音 安装程序 |
| FileVersion: | 5, 2, 18, 5894 |
| InternalName: | XMPSetup |
| LegalCopyright: | Copyright (c) 2003-2017 深圳市迅雷网络技术有限公司 |
| OriginalFileName: | XMPSetup.exe |
| ProductName: | 迅雷影音 安装程序 |
| ProductVersion: | 5, 2, 18, 5894 |
| CompanyName: | 深圳市迅雷网络技术有限公司 |
| LegalTrademarks: | Xunlei |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 4784 | "C:\Users\admin\Desktop\XMPSetupKankan.exe" | C:\Users\admin\Desktop\XMPSetupKankan.exe | — | explorer.exe | |||||||||||
User: admin Company: 深圳市迅雷网络技术有限公司 Integrity Level: MEDIUM Description: 迅雷影音 安装程序 Exit code: 3221226540 Version: 5, 2, 18, 5894 Modules
| |||||||||||||||
| 6984 | "C:\Users\admin\Desktop\XMPSetupKankan.exe" | C:\Users\admin\Desktop\XMPSetupKankan.exe | explorer.exe | ||||||||||||
User: admin Company: 深圳市迅雷网络技术有限公司 Integrity Level: HIGH Description: 迅雷影音 安装程序 Version: 5, 2, 18, 5894 Modules
| |||||||||||||||
| (PID) Process: | (6984) XMPSetupKankan.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows NT\CurrentVersion\AppCompatFlags\Compatibility Assistant\Persisted |
| Operation: | write | Name: | C:\Users\admin\Desktop\XMPSetupKankan.exe |
Value: 1 | |||
| (PID) Process: | (6984) XMPSetupKankan.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows NT\CurrentVersion\AppCompatFlags\Compatibility Assistant\Persisted |
| Operation: | write | Name: | SIGN.IE=01C48E90 XMPSetupKankan.exe |
Value: 1 | |||
| (PID) Process: | (6984) XMPSetupKankan.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows NT\CurrentVersion\AppCompatFlags\Compatibility Assistant\Persisted |
| Operation: | write | Name: | SIGN.MEDIA=10C1A20 XMPSetupKankan.exe |
Value: 1 | |||
| (PID) Process: | (6984) XMPSetupKankan.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Content |
| Operation: | write | Name: | CachePrefix |
Value: | |||
| (PID) Process: | (6984) XMPSetupKankan.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Cookies |
| Operation: | write | Name: | CachePrefix |
Value: Cookie: | |||
| (PID) Process: | (6984) XMPSetupKankan.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\History |
| Operation: | write | Name: | CachePrefix |
Value: Visited: | |||
| (PID) Process: | (6984) XMPSetupKankan.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Thunder Network\Xmp |
| Operation: | write | Name: | allowplaysubtype |
Value: | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 6984 | XMPSetupKankan.exe | C:\Users\admin\AppData\Local\Temp\XMPSetupKankan\5.2.18.5894\SetupUI.cab | — | |
MD5:— | SHA256:— | |||
| 6984 | XMPSetupKankan.exe | C:\ProgramData\Thunder Network\DownloadLib\pub_store.dat | text | |
MD5:F79C563BC47D7920DD680E84D5702346 | SHA256:5AFC59CCD82D6312D396E1923A910C645785C497E3CD0BD8CD545FE8FEC2E182 | |||
| 6984 | XMPSetupKankan.exe | C:\Users\admin\AppData\Local\Temp\XMPSetupKankan\5.2.18.5894\msvcp71.dll | executable | |
MD5:A94DC60A90EFD7A35C36D971E3EE7470 | SHA256:6C483CBE349863C7DCF6F8CB7334E7D28C299E7D5AA063297EA2F62352F6BDD9 | |||
| 6984 | XMPSetupKankan.exe | C:\Users\admin\AppData\Local\Temp\XMPSetupKankan\5.2.18.5894\atl90.dll | executable | |
MD5:338F1F7137860D3BF6094941AC2A9BA2 | SHA256:5122E4A2E48E34326B6267D48BD007DA76A15243B90550EA565F1654CCC64877 | |||
| 6984 | XMPSetupKankan.exe | C:\Users\admin\AppData\Local\Temp\XMPSetupKankan\5.2.18.5894\atl71.dll | executable | |
MD5:4EDD8D74EA48F58D3ECA7E9297F19221 | SHA256:D422497FEBAA2FBB83A8A2EC342E08884C5A77FBDDABDE7BEC4E21884F56D0CE | |||
| 6984 | XMPSetupKankan.exe | C:\Users\admin\AppData\Local\Temp\XMPSetupKankan\5.2.18.5894\msvcr71.dll | executable | |
MD5:CA2F560921B7B8BE1CF555A5A18D54C3 | SHA256:C4D4339DF314A27FF75A38967B7569D9962337B8D4CD4B0DB3ABA5FF72B2BFBB | |||
| 6984 | XMPSetupKankan.exe | C:\Users\admin\AppData\Local\Temp\XMPSetupKankan\5.2.18.5894\dl_peer_id.dll | executable | |
MD5:F102E167834E286EF584CE97D684189B | SHA256:045ED5F3E949BBDEC103DA8DB0EFBD45C218152BDD4AB34143B45E3B49B8E918 | |||
| 6984 | XMPSetupKankan.exe | C:\Users\admin\AppData\Local\Temp\XMPSetupKankan\5.2.18.5894\Microsoft.VC90.CRT.manifest | xml | |
MD5:4F9ED5EFA4F7B75BCFE0F36C36EE5CB6 | SHA256:FF718390133B400EE679177B2902BBB918DB148BBB4ABABA03D0A1DF325B3303 | |||
| 6984 | XMPSetupKankan.exe | C:\Users\admin\AppData\Local\Temp\XMPSetupKankan\5.2.18.5894\msvcp90.dll | executable | |
MD5:6DE5C66E434A9C1729575763D891C6C2 | SHA256:4F7ED27B532888CE72B96E52952073EAB2354160D1156924489054B7FA9B0B1A | |||
| 6984 | XMPSetupKankan.exe | C:\Users\admin\AppData\Local\Temp\XMPSetupKankan\5.2.18.5894\minizip.dll | executable | |
MD5:6C49EEA477828B88C4DF95BFD508B64C | SHA256:E5B5238CDC5C0F68F259C0C6793B0BCC3C38E1B6C4BD80186FE783C1A287C3FA | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
6012 | svchost.exe | GET | 200 | 184.30.21.171:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 973 b | whitelisted |
— | — | GET | 200 | 184.30.21.171:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 973 b | whitelisted |
2120 | MoUsoCoreWorker.exe | GET | 200 | 184.30.21.171:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 973 b | whitelisted |
6984 | XMPSetupKankan.exe | GET | — | 39.104.21.243:80 | http://conf.v.xunlei.com/setup/xmp5/startpageonline.lua | CN | — | — | unknown |
6984 | XMPSetupKankan.exe | GET | — | 39.104.21.243:80 | http://conf.v.xunlei.com/setup/xmp5/shortcutonline.lua | CN | — | — | unknown |
6984 | XMPSetupKankan.exe | GET | 200 | 39.104.21.243:80 | http://conf.v.xunlei.com/setup/xmp5/onlineindex.lua | CN | binary | 49.8 Kb | unknown |
6984 | XMPSetupKankan.exe | GET | 200 | 39.104.21.243:80 | http://conf.v.xunlei.com/setup/xmp5/onlineindex_config.lua | CN | text | 179 b | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
— | — | 51.124.78.146:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
6012 | svchost.exe | 184.30.21.171:80 | www.microsoft.com | AKAMAI-AS | DE | whitelisted |
— | — | 184.30.21.171:80 | www.microsoft.com | AKAMAI-AS | DE | whitelisted |
2120 | MoUsoCoreWorker.exe | 184.30.21.171:80 | www.microsoft.com | AKAMAI-AS | DE | whitelisted |
— | — | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
3888 | svchost.exe | 239.255.255.250:1900 | — | — | — | whitelisted |
6984 | XMPSetupKankan.exe | 39.104.21.243:80 | conf.v.xunlei.com | Hangzhou Alibaba Advertising Co.,Ltd. | CN | unknown |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
Domain | IP | Reputation |
|---|---|---|
google.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
settings-win.data.microsoft.com |
| whitelisted |
user.stat.v.xunlei.com |
| unknown |
setup.stat.v.xunlei.com |
| unknown |
conf.v.xunlei.com |
| unknown |
02.rcv.sandai.net |
| whitelisted |
zone.xmp.kankan.xunlei.com |
| unknown |