ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | register_wrapper.dll |
| Full analysis: | https://app.any.run/tasks/63661639-9b02-4122-aa16-4b1b1bd3997a |
| Verdict: | No threats detected |
| Analysis date: | December 02, 2020, 16:53:48 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Indicators: | |
| MIME: | application/x-dosexec |
| File info: | PE32 executable (DLL) (console) Intel 80386, for MS Windows, UPX compressed |
| MD5: | 8C8D3DF444B5AA49E9B5F74615411B13 |
| SHA1: | E9C813E5D28296543B4EE06C9DA9C229D88CBC29 |
| SHA256: | 8B61B7898E94C603F3A133DC211AFCCDC6CD052C037BC926F1AF1269A401ED62 |
| SSDEEP: | 384:ElxQ7DP2XvMvsKfY6YfseOfYbGmDmBORMWyOiDPHfbqMh5forK4zXc:K0OXvMkKXEse24Gmh6OibDhLwrHzX |
| .exe | | | UPX compressed Win32 Executable (64.2) |
|---|---|---|
| .dll | | | Win32 Dynamic Link Library (generic) (15.6) |
| .exe | | | Win32 Executable (generic) (10.6) |
| .exe | | | Generic Win/DOS Executable (4.7) |
| .exe | | | DOS Executable Generic (4.7) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2020:07:23 11:20:27+02:00 |
| PEType: | PE32 |
| LinkerVersion: | 10 |
| CodeSize: | 24576 |
| InitializedDataSize: | 4096 |
| UninitializedDataSize: | 57344 |
| EntryPoint: | 0x14150 |
| OSVersion: | 5.1 |
| ImageVersion: | - |
| SubsystemVersion: | 5.1 |
| Subsystem: | Windows command line |
| FileVersionNumber: | 1.0.1.8 |
| ProductVersionNumber: | 1.0.1.8 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Windows NT 32-bit |
| ObjectFileType: | Dynamic link library |
| FileSubtype: | - |
| LanguageCode: | Chinese (Simplified) |
| CharacterSet: | Unicode |
| FileDescription: | - |
| FileVersion: | 1.0.1.8 |
| InternalName: | register.dll |
| LegalCopyright: | Copyright (C) 2020 |
| OriginalFileName: | register.dll |
| ProductName: | Register |
| ProductVersion: | 1.0.1.8 |
| Architecture: | IMAGE_FILE_MACHINE_I386 |
|---|---|
| Subsystem: | IMAGE_SUBSYSTEM_WINDOWS_CUI |
| Compilation Date: | 23-Jul-2020 09:20:27 |
| Detected languages: |
|
| FileDescription: | - |
| FileVersion: | 1.0.1.8 |
| InternalName: | register.dll |
| LegalCopyright: | Copyright (C) 2020 |
| OriginalFilename: | register.dll |
| ProductName: | Register |
| ProductVersion: | 1.0.1.8 |
| Magic number: | MZ |
|---|---|
| Bytes on last page of file: | 0x0090 |
| Pages in file: | 0x0003 |
| Relocations: | 0x0000 |
| Size of header: | 0x0004 |
| Min extra paragraphs: | 0x0000 |
| Max extra paragraphs: | 0xFFFF |
| Initial SS value: | 0x0000 |
| Initial SP value: | 0x00B8 |
| Checksum: | 0x0000 |
| Initial IP value: | 0x0000 |
| Initial CS value: | 0x0000 |
| Overlay number: | 0x0000 |
| OEM identifier: | 0x0000 |
| OEM information: | 0x0000 |
| Address of NE header: | 0x00000100 |
| Signature: | PE |
|---|---|
| Machine: | IMAGE_FILE_MACHINE_I386 |
| Number of sections: | 3 |
| Time date stamp: | 23-Jul-2020 09:20:27 |
| Pointer to Symbol Table: | 0x00000000 |
| Number of symbols: | 0 |
| Size of Optional Header: | 0x00E0 |
| Characteristics: |
|
Name | Virtual Address | Virtual Size | Raw Size | Charateristics | Entropy |
|---|---|---|---|---|---|
UPX0 | 0x00001000 | 0x0000E000 | 0x00000000 | IMAGE_SCN_CNT_UNINITIALIZED_DATA, IMAGE_SCN_MEM_EXECUTE, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 0 |
UPX1 | 0x0000F000 | 0x00006000 | 0x00005400 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_EXECUTE, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 7.85349 |
.rsrc | 0x00015000 | 0x00001000 | 0x00000800 | IMAGE_SCN_CNT_INITIALIZED_DATA, IMAGE_SCN_MEM_READ, IMAGE_SCN_MEM_WRITE | 3.93433 |
Title | Entropy | Size | Codepage | Language | Type |
|---|---|---|---|---|---|
1 | 3.28848 | 616 | Latin 1 / Western European | Chinese - PRC | RT_VERSION |
2 | 4.79597 | 346 | Latin 1 / Western European | English - United States | RT_MANIFEST |
KERNEL32.DLL |
MSVCP100.dll |
MSVCR100.dll |
libcrypto-1_1.dll |
Title | Ordinal | Address |
|---|---|---|
getRegisterUserNameAndCode | 1 | 0x00002640 |
initialize | 2 | 0x00002500 |
registerUser | 3 | 0x000025B0 |
unregisterUser | 4 | 0x00001100 |
setCustomRegInfo | 5 | 0x00002980 |
getCustomRegInfo | 6 | 0x00002A10 |
delCustomRegInfo | 7 | 0x00002BA0 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
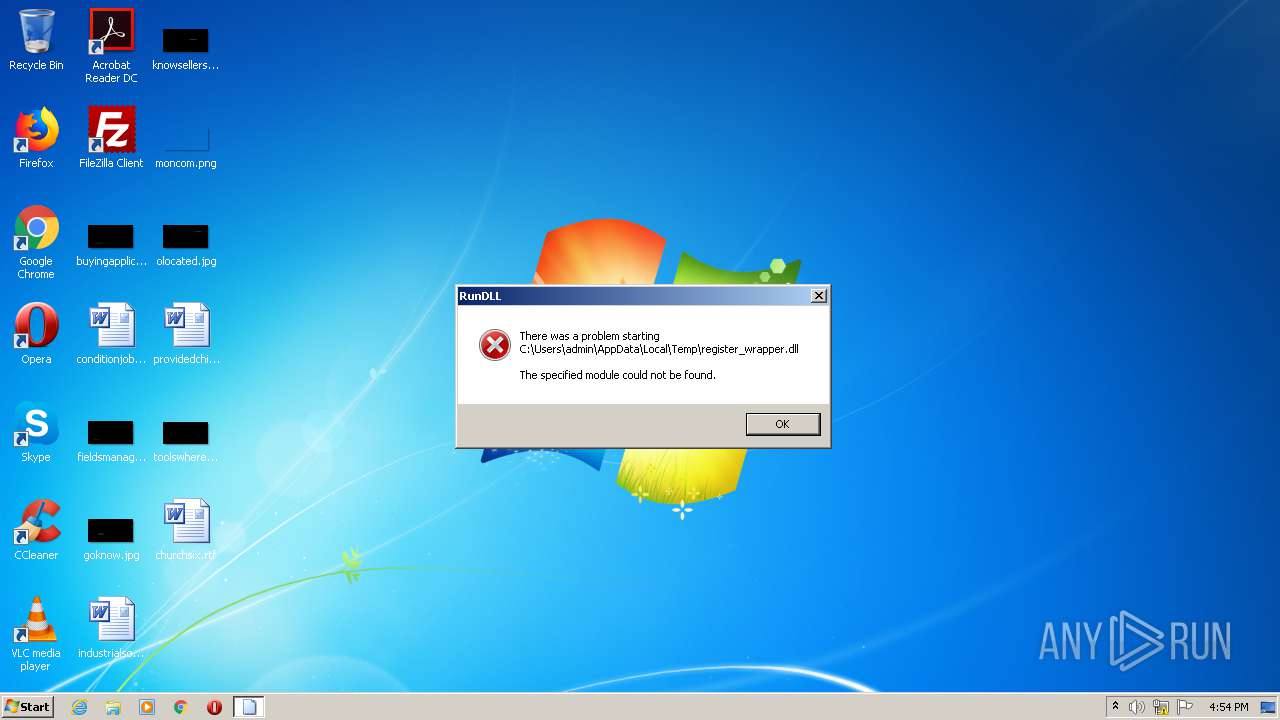
| 2192 | "C:\Windows\System32\rundll32.exe" "C:\Users\admin\AppData\Local\Temp\register_wrapper.dll", getRegisterUserNameAndCode | C:\Windows\System32\rundll32.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||