ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
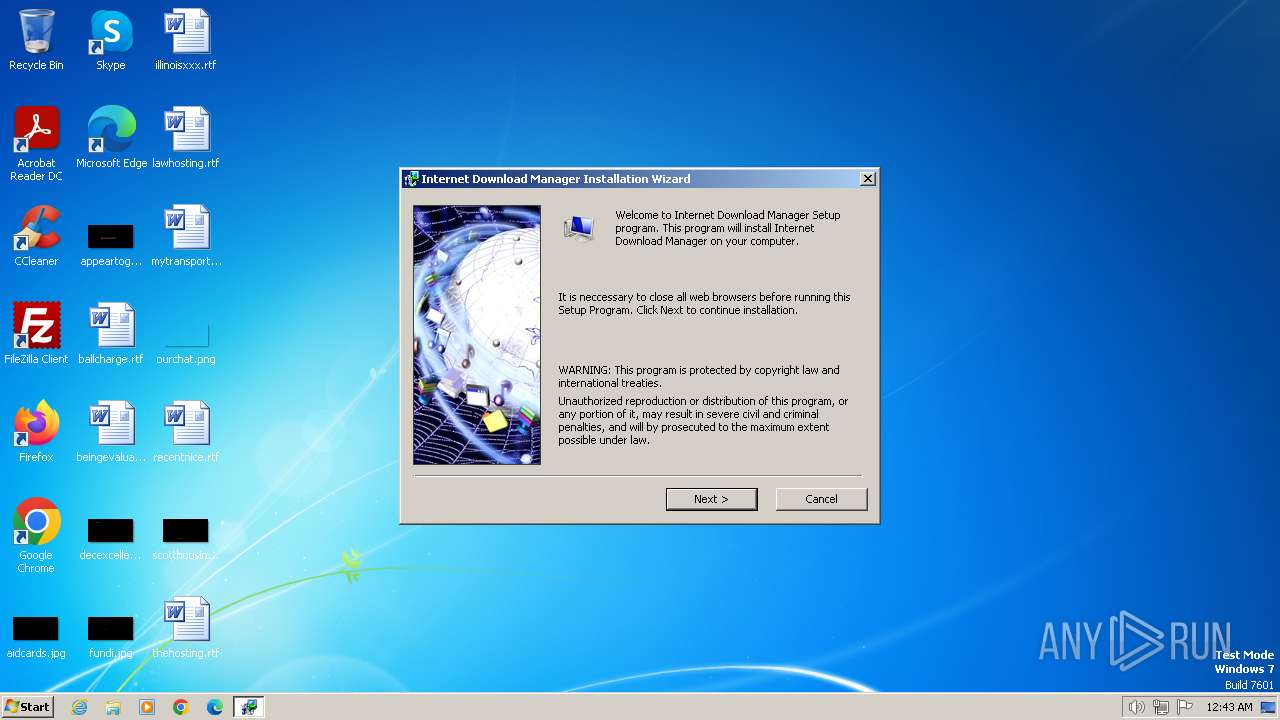
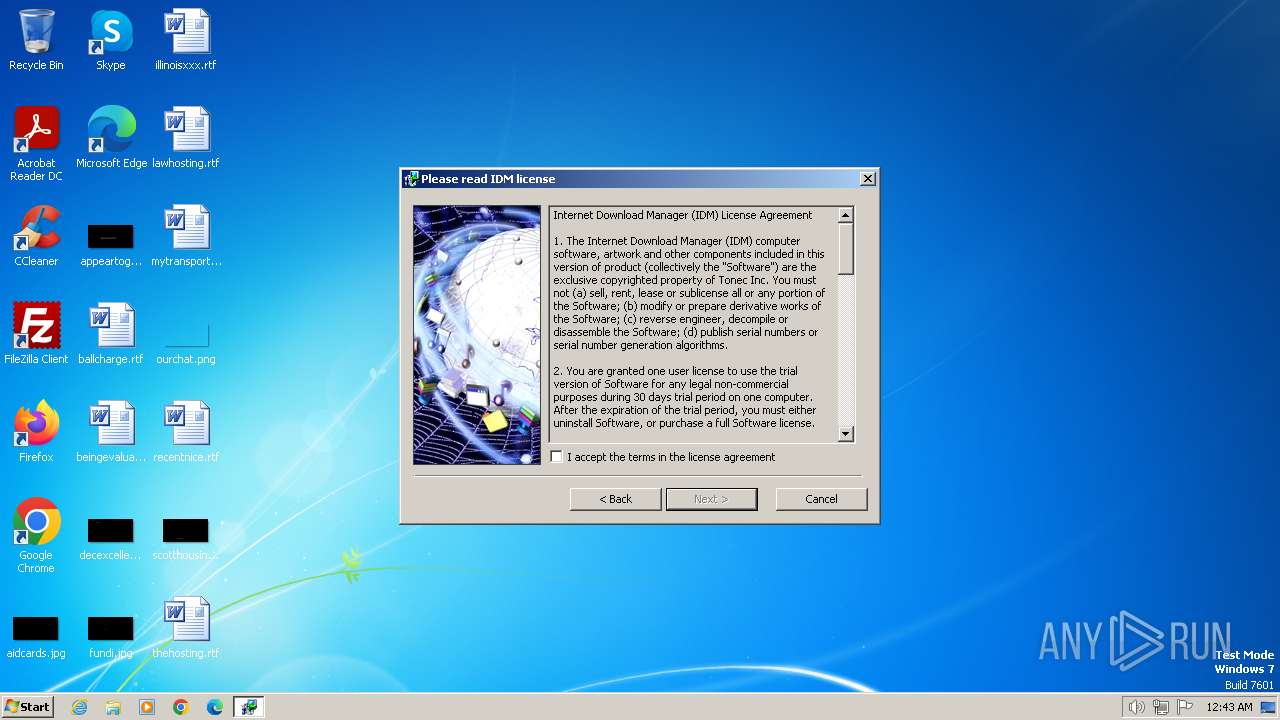
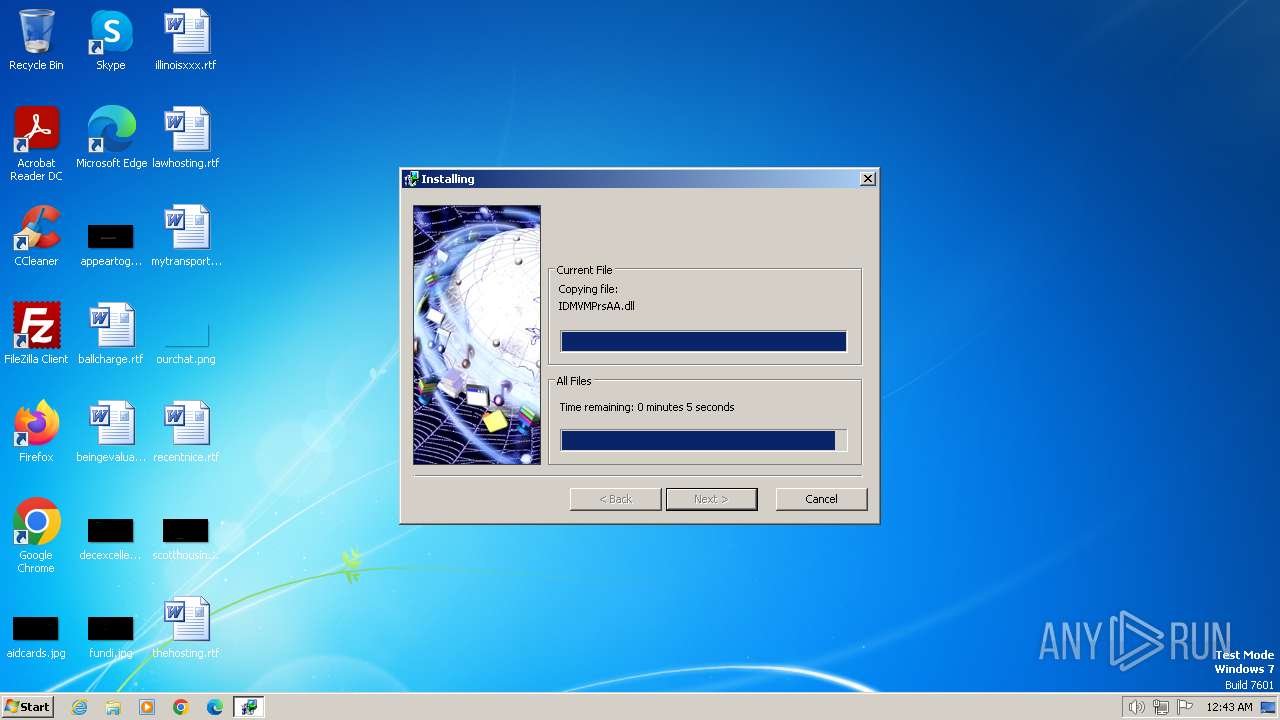
| File name: | idman642build7.exe |
| Full analysis: | https://app.any.run/tasks/5c5a9a99-c4a9-4e62-b9cb-05d9930d53a5 |
| Verdict: | Malicious activity |
| Analysis date: | April 01, 2024, 23:43:01 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Indicators: | |
| MIME: | application/x-dosexec |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows |
| MD5: | 443B94B1DE94E8C52F91DFD55EDE534A |
| SHA1: | 36ED74780E15766E1C7003F32D2893770CBECD3A |
| SHA256: | 89DE13BA26895A5C8C6D75CF2A2191A8F954D5FC581D4D55A288BF775FE4C56B |
| SSDEEP: | 98304:h2HQa73REIxBfQtROESn18u2KK8/LgxlQ+XXXqHov0cYrLekcBNlsSvr3WQsvZlc:QEr3D9/itwFjl7NCamBZgviW/H |
| .exe | | | Win32 Executable MS Visual C++ (generic) (35.8) |
|---|---|---|
| .exe | | | Win64 Executable (generic) (31.7) |
| .scr | | | Windows screen saver (15) |
| .dll | | | Win32 Dynamic Link Library (generic) (7.5) |
| .exe | | | Win32 Executable (generic) (5.1) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2024:03:24 08:31:19+00:00 |
| ImageFileCharacteristics: | No relocs, Executable, No line numbers, No symbols, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 6 |
| CodeSize: | 15872 |
| InitializedDataSize: | 26624 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x4336 |
| OSVersion: | 4 |
| ImageVersion: | - |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 6.42.7.1 |
| ProductVersionNumber: | 6.42.7.1 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Windows NT 32-bit |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | English (U.S.) |
| CharacterSet: | Unicode |
| Comments: | Please visit http://www.internetdownloadmanager.com |
| CompanyName: | Tonec Inc. |
| FileDescription: | Internet Download Manager installer |
| FileVersion: | 6, 42, 7, 1 |
| InternalName: | installer |
| LegalCopyright: | © 1999-2024. Tonec FZE. All rights reserved. |
| LegalTrademarks: | Internet Download Manager (IDM) |
| OriginalFileName: | installer.exe |
| PrivateBuild: | - |
| ProductName: | Internet Download Manager installer |
| ProductVersion: | 6, 42, 7, 1 |
| SpecialBuild: | - |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 748 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc --channel="2900.13.974414675\335128565" -childID 12 -isForBrowser -prefsHandle 4736 -prefMapHandle 4392 -prefsLen 29313 -prefMapSize 244195 -jsInitHandle 908 -jsInitLen 240908 -parentBuildID 20230710165010 -appDir "C:\Program Files\Mozilla Firefox\browser" - {1bbde85a-9f53-4275-9927-eb2850357cd5} 2900 "\\.\pipe\gecko-crash-server-pipe.2900" 4720 19866560 tab | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: LOW Description: Firefox Exit code: 0 Version: 115.0.2 Modules
| |||||||||||||||
| 880 | C:\Windows\system32\net1 start IDMWFP | C:\Windows\System32\net1.exe | — | net.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Net Command Exit code: 0 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
| 1424 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc --channel="2900.3.1775570728\348139556" -childID 2 -isForBrowser -prefsHandle 2828 -prefMapHandle 1924 -prefsLen 34225 -prefMapSize 244195 -jsInitHandle 908 -jsInitLen 240908 -parentBuildID 20230710165010 -appDir "C:\Program Files\Mozilla Firefox\browser" - {57c8fd61-472d-4c3d-bd62-92a100d686de} 2900 "\\.\pipe\gecko-crash-server-pipe.2900" 2848 1637e840 tab | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: LOW Description: Firefox Exit code: 0 Version: 115.0.2 Modules
| |||||||||||||||
| 1496 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc --channel="2900.8.1129330490\44655813" -childID 7 -isForBrowser -prefsHandle 2948 -prefMapHandle 3900 -prefsLen 29313 -prefMapSize 244195 -jsInitHandle 908 -jsInitLen 240908 -parentBuildID 20230710165010 -appDir "C:\Program Files\Mozilla Firefox\browser" - {e1475ba5-2d96-40cd-b852-ad40fc0fa3dc} 2900 "\\.\pipe\gecko-crash-server-pipe.2900" 2864 f285280 tab | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: LOW Description: Firefox Exit code: 0 Version: 115.0.2 Modules
| |||||||||||||||
| 1728 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc --channel="2900.1.122161524\1328386209" -parentBuildID 20230710165010 -prefsHandle 1408 -prefMapHandle 1404 -prefsLen 28600 -prefMapSize 244195 -appDir "C:\Program Files\Mozilla Firefox\browser" - {1607856e-cf0e-4904-b61a-24ad599e435f} 2900 "\\.\pipe\gecko-crash-server-pipe.2900" 1420 d721cf0 socket | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: LOW Description: Firefox Exit code: 0 Version: 115.0.2 Modules
| |||||||||||||||
| 1740 | "C:\Program Files\Internet Download Manager\idmBroker.exe" -RegServer | C:\Program Files\Internet Download Manager\idmBroker.exe | — | IDM1.tmp | |||||||||||
User: admin Company: Internet Download Manager, Tonec Inc. Integrity Level: HIGH Description: Broker for reading of IDM settings Exit code: 0 Version: 6, 35, 9, 1 Modules
| |||||||||||||||
| 1772 | "C:\Program Files\Internet Download Manager\MediumILStart.exe" | C:\Program Files\Internet Download Manager\MediumILStart.exe | — | IDMan.exe | |||||||||||
User: admin Company: Internet Download Manager, Tonec Inc. Integrity Level: MEDIUM Description: IDM module Exit code: 0 Version: 6, 42, 2, 1 Modules
| |||||||||||||||
| 1900 | "C:\Windows\System32\rundll32.exe" SETUPAPI.DLL,InstallHinfSection DefaultInstall 128 C:\Program Files\Internet Download Manager\idmwfp.inf | C:\Windows\System32\rundll32.exe | Uninstall.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2260 | "C:\Windows\System32\grpconv.exe" -o | C:\Windows\System32\grpconv.exe | — | runonce.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows Progman Group Converter Exit code: 1 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2372 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc --channel="2900.9.1389535242\337553307" -childID 8 -isForBrowser -prefsHandle 2164 -prefMapHandle 2152 -prefsLen 29313 -prefMapSize 244195 -jsInitHandle 908 -jsInitLen 240908 -parentBuildID 20230710165010 -appDir "C:\Program Files\Mozilla Firefox\browser" - {cd56fe98-6ac9-44f6-807f-23b9db1bd89c} 2900 "\\.\pipe\gecko-crash-server-pipe.2900" 2168 f2853f0 tab | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: LOW Description: Firefox Exit code: 0 Version: 115.0.2 Modules
| |||||||||||||||
| (PID) Process: | (3488) IDM1.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Internet Download Manager |
| Operation: | write | Name: | UninstallString |
Value: C:\Program Files\Internet Download Manager\Uninstall.exe | |||
| (PID) Process: | (3488) IDM1.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Internet Download Manager |
| Operation: | write | Name: | DisplayName |
Value: Internet Download Manager | |||
| (PID) Process: | (3488) IDM1.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Internet Download Manager |
| Operation: | write | Name: | DisplayVersion |
Value: 6.42.5 | |||
| (PID) Process: | (3488) IDM1.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Internet Download Manager |
| Operation: | write | Name: | DisplayIcon |
Value: C:\Program Files\Internet Download Manager\IDMan.exe | |||
| (PID) Process: | (3488) IDM1.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Internet Download Manager |
| Operation: | write | Name: | Publisher |
Value: Tonec Inc. | |||
| (PID) Process: | (3488) IDM1.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Internet Download Manager |
| Operation: | write | Name: | URLInfoAbout |
Value: http://www.internetdownloadmanager.com | |||
| (PID) Process: | (3488) IDM1.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Internet Download Manager |
| Operation: | write | Name: | HelpLink |
Value: http://www.internetdownloadmanager.com/contact_us.html | |||
| (PID) Process: | (3488) IDM1.tmp | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Session Manager |
| Operation: | write | Name: | PendingFileRenameOperations |
Value: \??\C:\Users\admin\AppData\Local\Temp\IDM_Setup_Temp\IDM1.tmp | |||
| (PID) Process: | (3488) IDM1.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{0055C089-8582-441B-A0BF-17B458C2A3A8} |
| Operation: | write | Name: | NoExplorer |
Value: 1 | |||
| (PID) Process: | (3488) IDM1.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Internet Explorer\Low Rights\ElevationPolicy\{E0DACC63-037F-46EE-AC02-E4C7B0FBFEB4} |
| Operation: | write | Name: | AppName |
Value: IDMan.exe | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3488 | IDM1.tmp | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Internet Download Manager\license.lnk | binary | |
MD5:D5B1B246AB055AF7B92D1476A879056A | SHA256:88C7530A0EA77F9C549DBEE6BF6908B7766431B86E153719F7AEF34609394034 | |||
| 3488 | IDM1.tmp | C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Internet Download Manager\Uninstall IDM.lnk | binary | |
MD5:11C9764D8073FE2D982B96943DC7FB56 | SHA256:4A4A1B983B43E5C1C8757DC3C6F3087043704B19E1E3DC75557E37FB81BDC742 | |||
| 3488 | IDM1.tmp | C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Internet Download Manager\IDM Help.lnk | binary | |
MD5:FFB03D83A9708AAA71FC2238BA8692FA | SHA256:B134DF5CD4C2DDC1D9EDEEEB7991B7DA3696088EE8A423DFCFE759D13D7D8432 | |||
| 3684 | IDMan.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\77EC63BDA74BD0D0E0426DC8F8008506 | compressed | |
MD5:29F65BA8E88C063813CC50A4EA544E93 | SHA256:1ED81FA8DFB6999A9FEDC6E779138FFD99568992E22D300ACD181A6D2C8DE184 | |||
| 3684 | IDMan.exe | C:\Users\admin\AppData\Roaming\IDM\urlexclist.dat | binary | |
MD5:AEE43AB150A20FCBACAE2088984F2B0E | SHA256:49CC9662B3C44F3EEFE6A6FA967CA34E0DA9606D451A6C408EE295CCEF01E852 | |||
| 3488 | IDM1.tmp | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Internet Download Manager\Grabber Help.lnk | binary | |
MD5:BD8024B9C0229B34AEB2D82C2A96EF2E | SHA256:CF48EC99697ED3281E12FE21667CCC83C022725CB657AFBC6C6087680E41F349 | |||
| 3488 | IDM1.tmp | C:\Program Files\Internet Download Manager\IDMSetup2.log | binary | |
MD5:27D144E10FBB7671462F49FB04414EAD | SHA256:81DBDBB8B56CC70F4FF0D1CE21DEB53891792281C4603EC322972834E69DC363 | |||
| 3488 | IDM1.tmp | C:\Users\admin\AppData\Local\Temp\IDM_Setup_Temp\IDMSetup2.log | binary | |
MD5:1C92BCB479B9EE7BBC5F5E6754B125B2 | SHA256:95EFFBCC2269DB3E96C984D8249D14DBCDD8D4CF6A43143CBA0D7D20F96DF991 | |||
| 3488 | IDM1.tmp | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Internet Download Manager\Uninstall IDM.lnk | binary | |
MD5:8A73BD6078EBC2364AE1AD391CC5D140 | SHA256:038DFE793CA625EE8CED334A9C2E9432CC9E1AFFEFE5EBD3D9F97C8AD40E8B1C | |||
| 3488 | IDM1.tmp | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Internet Download Manager\TUTORIALS.lnk | binary | |
MD5:5ED7F20691394D2E9F59F65998B684F3 | SHA256:F322DF898D9A6DD88EA215D151EF24427393170C58F649CBDE1F1C2888F349C3 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
3684 | IDMan.exe | GET | 200 | 199.232.210.172:80 | http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/authrootstl.cab?11df873858e6afdd | US | compressed | 68.3 Kb | unknown |
2900 | firefox.exe | GET | 200 | 34.107.221.82:80 | http://detectportal.firefox.com/canonical.html | US | text | 90 b | unknown |
2900 | firefox.exe | GET | 200 | 34.107.221.82:80 | http://detectportal.firefox.com/success.txt?ipv4 | US | text | 8 b | unknown |
2900 | firefox.exe | POST | 200 | 2.22.242.121:80 | http://r3.o.lencr.org/ | DE | binary | 503 b | unknown |
2900 | firefox.exe | POST | 200 | 2.22.242.121:80 | http://r3.o.lencr.org/ | DE | binary | 503 b | unknown |
2900 | firefox.exe | POST | 200 | 2.22.242.121:80 | http://r3.o.lencr.org/ | DE | binary | 503 b | unknown |
2900 | firefox.exe | POST | 200 | 2.22.242.121:80 | http://r3.o.lencr.org/ | DE | binary | 503 b | unknown |
2900 | firefox.exe | POST | 200 | 192.229.221.95:80 | http://ocsp.digicert.com/ | US | binary | 471 b | unknown |
2900 | firefox.exe | POST | 200 | 192.229.221.95:80 | http://ocsp.digicert.com/ | US | binary | 471 b | unknown |
2900 | firefox.exe | POST | 200 | 2.22.242.121:80 | http://r3.o.lencr.org/ | DE | binary | 503 b | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 224.0.0.252:5355 | — | — | — | unknown |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
1080 | svchost.exe | 224.0.0.252:5355 | — | — | — | unknown |
3684 | IDMan.exe | 199.232.210.172:80 | ctldl.windowsupdate.com | FASTLY | US | unknown |
2900 | firefox.exe | 169.61.27.133:443 | secure.internetdownloadmanager.com | SOFTLAYER | US | unknown |
2900 | firefox.exe | 34.107.221.82:80 | detectportal.firefox.com | GOOGLE | US | whitelisted |
2900 | firefox.exe | 34.117.237.239:443 | contile.services.mozilla.com | GOOGLE-CLOUD-PLATFORM | US | unknown |
2900 | firefox.exe | 34.117.188.166:443 | spocs.getpocket.com | GOOGLE-CLOUD-PLATFORM | US | unknown |
2900 | firefox.exe | 34.149.100.209:443 | firefox.settings.services.mozilla.com | GOOGLE | US | unknown |
Domain | IP | Reputation |
|---|---|---|
ctldl.windowsupdate.com |
| whitelisted |
test.internetdownloadmanager.com |
| whitelisted |
secure.internetdownloadmanager.com |
| whitelisted |
www.internetdownloadmanager.com |
| whitelisted |
mirror3.internetdownloadmanager.com |
| whitelisted |
mirror5.internetdownloadmanager.com |
| whitelisted |
registeridm.com |
| unknown |
detectportal.firefox.com |
| whitelisted |
contile.services.mozilla.com |
| whitelisted |
prod.detectportal.prod.cloudops.mozgcp.net |
| whitelisted |