ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
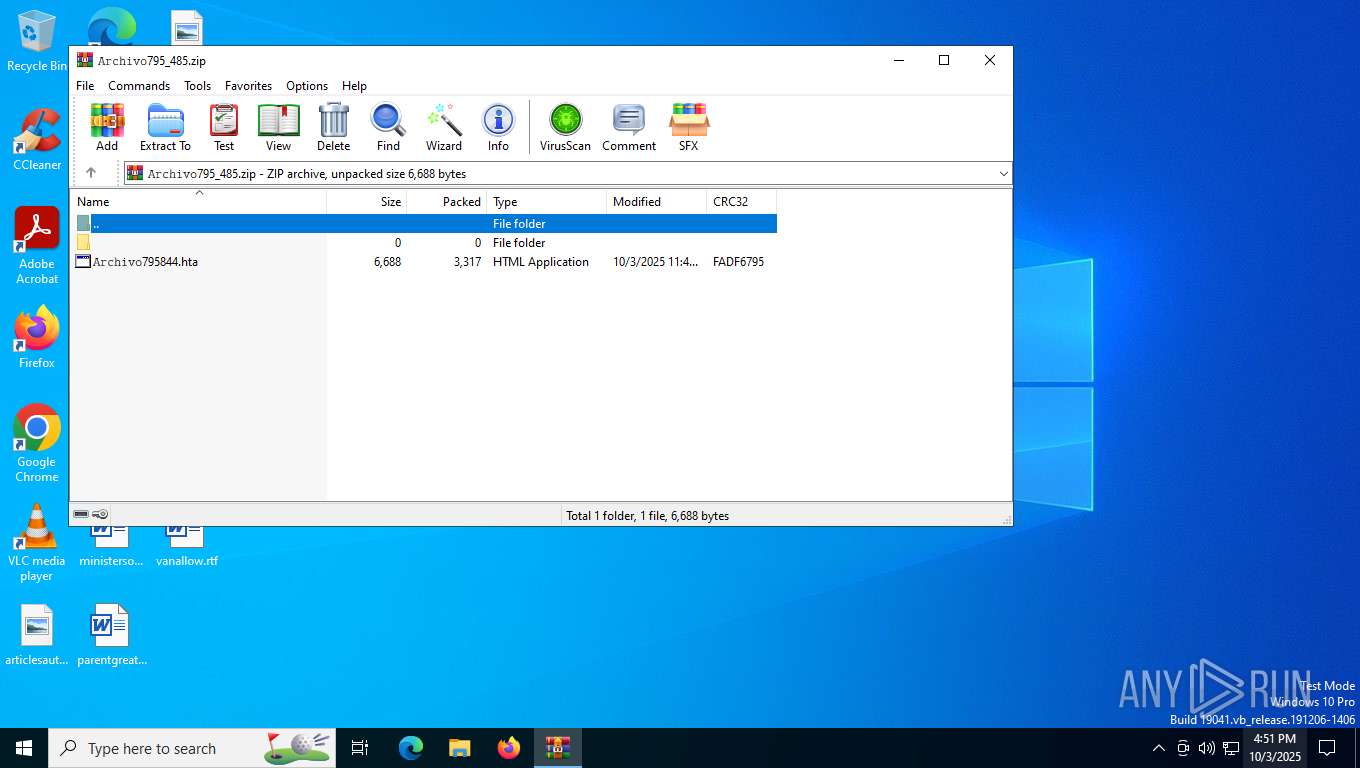
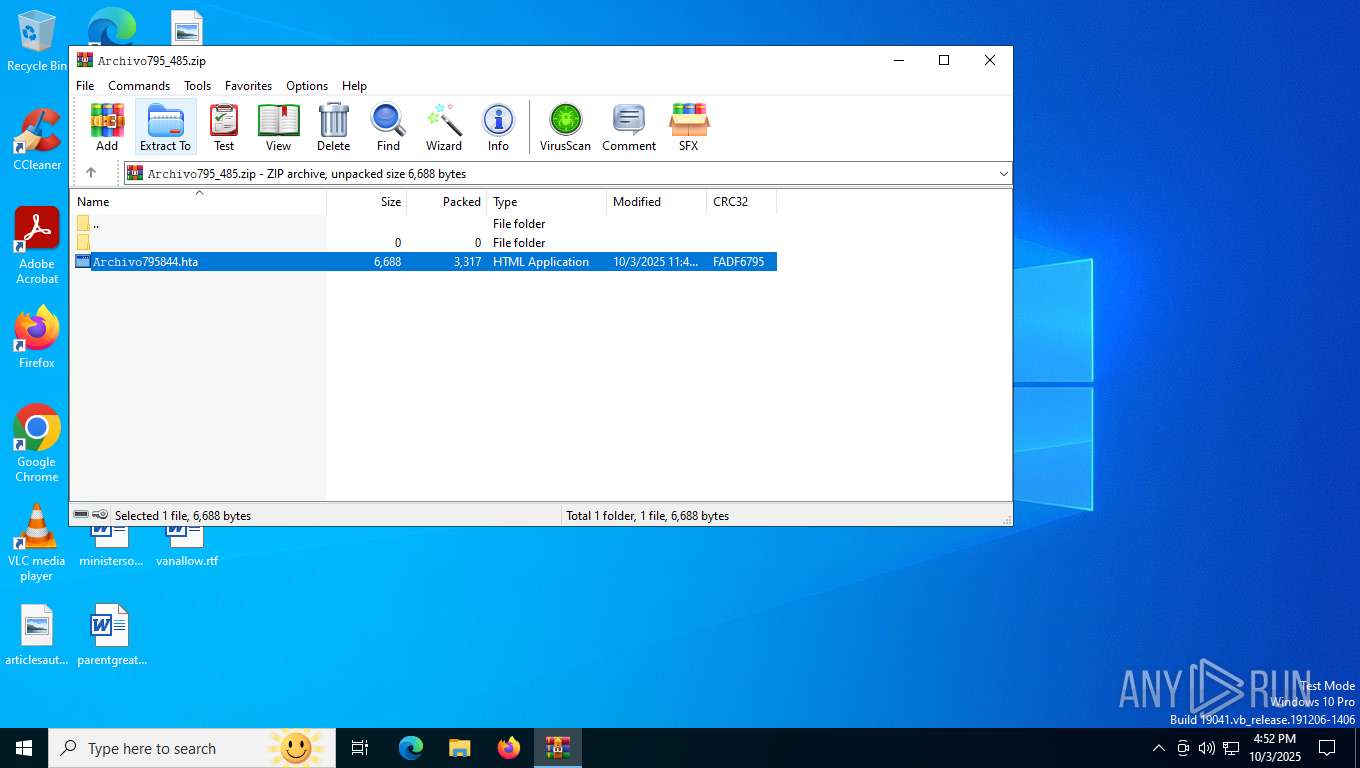
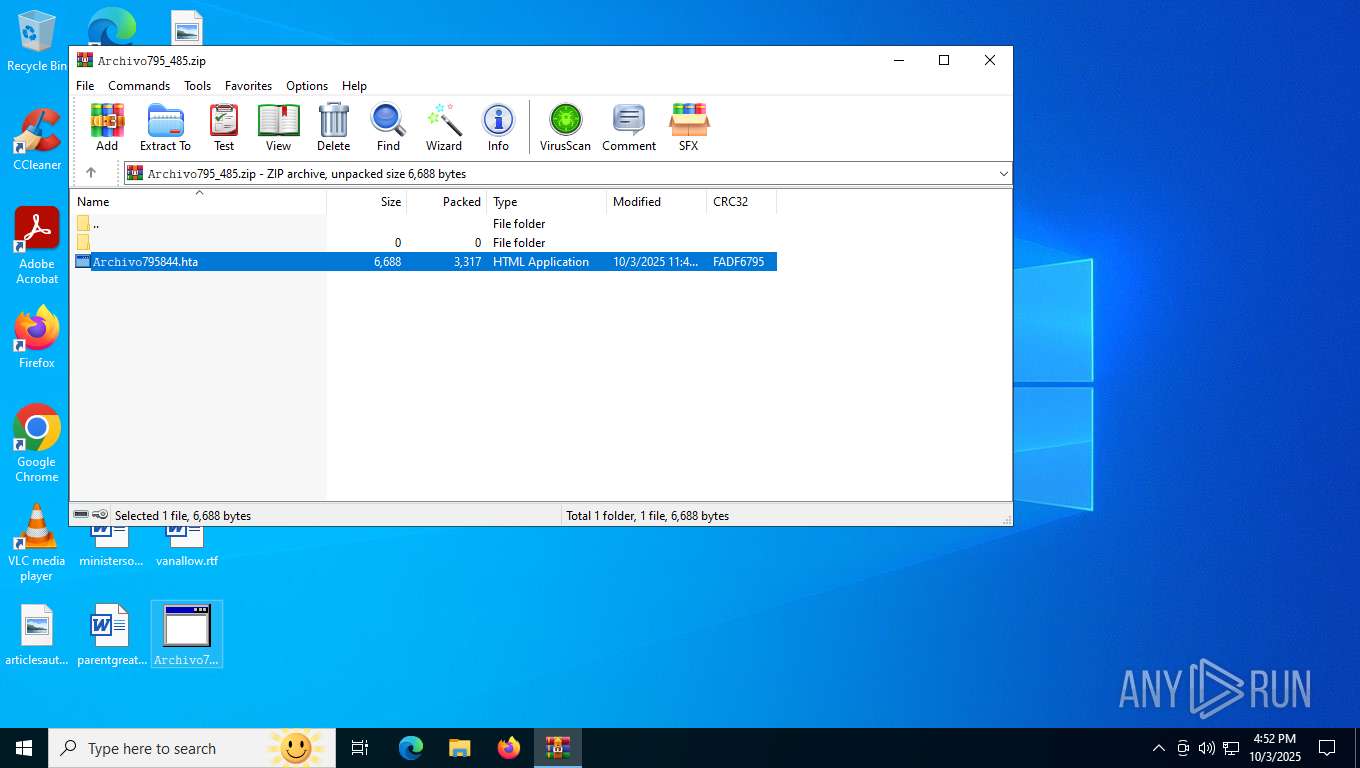
| File name: | 𝙰𝚛𝚌𝚑𝚒𝚟𝚘795_485.zip |
| Full analysis: | https://app.any.run/tasks/b18e9f4f-5301-468f-ac32-5360032b79d3 |
| Verdict: | Malicious activity |
| Analysis date: | October 03, 2025, 16:51:38 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/zip |
| File info: | Zip archive data, at least v2.0 to extract, compression method=store |
| MD5: | D43BFB4F8FA4EA921551A12BD4431C4A |
| SHA1: | DC7DD6A9D2192CEE0F4B913B61C82F1BCD22B145 |
| SHA256: | 89AA37A3D1090F64D30CD494C8FA3771E4E7AC6728C14D1698F38C36753B2A4F |
| SSDEEP: | 96:4UhV8oZ7l+JaecSt5n4waSGSMxzfGBTV8qhGY2+IC:FOh9t1XGSCIWBBC |
| .zip | | | ZIP compressed archive (100) |
|---|
| ZipRequiredVersion: | 20 |
|---|---|
| ZipBitFlag: | - |
| ZipCompression: | None |
| ZipModifyDate: | 2025:10:03 11:44:00 |
| ZipCRC: | 0x00000000 |
| ZipCompressedSize: | - |
| ZipUncompressedSize: | - |
| ZipFileName: | /\s/dAs557/ RY9CSI6VRWZZ |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
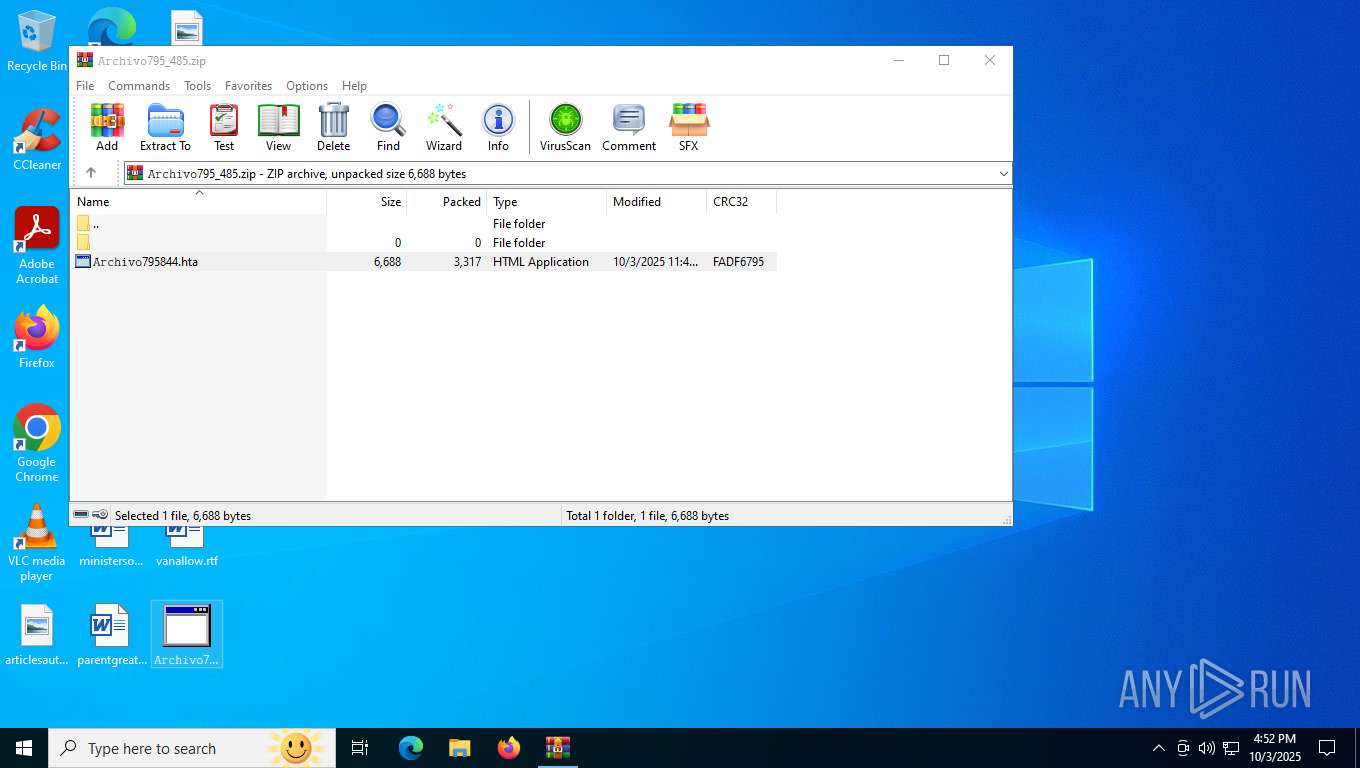
| 532 | "C:\Windows\SysWOW64\mshta.exe" "C:\Users\admin\Desktop\𝙰𝚛𝚌𝚑𝚒𝚟𝚘795844.hta" {1E460BD7-F1C3-4B2E-88BF-4E770A288AF5}{1E460BD7-F1C3-4B2E-88BF-4E770A288AF5} | C:\Windows\SysWOW64\mshta.exe | explorer.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft (R) HTML Application host Exit code: 0 Version: 11.00.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2116 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2428 | C:\WINDOWS\system32\svchost.exe -k NetworkService -p -s Dnscache | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
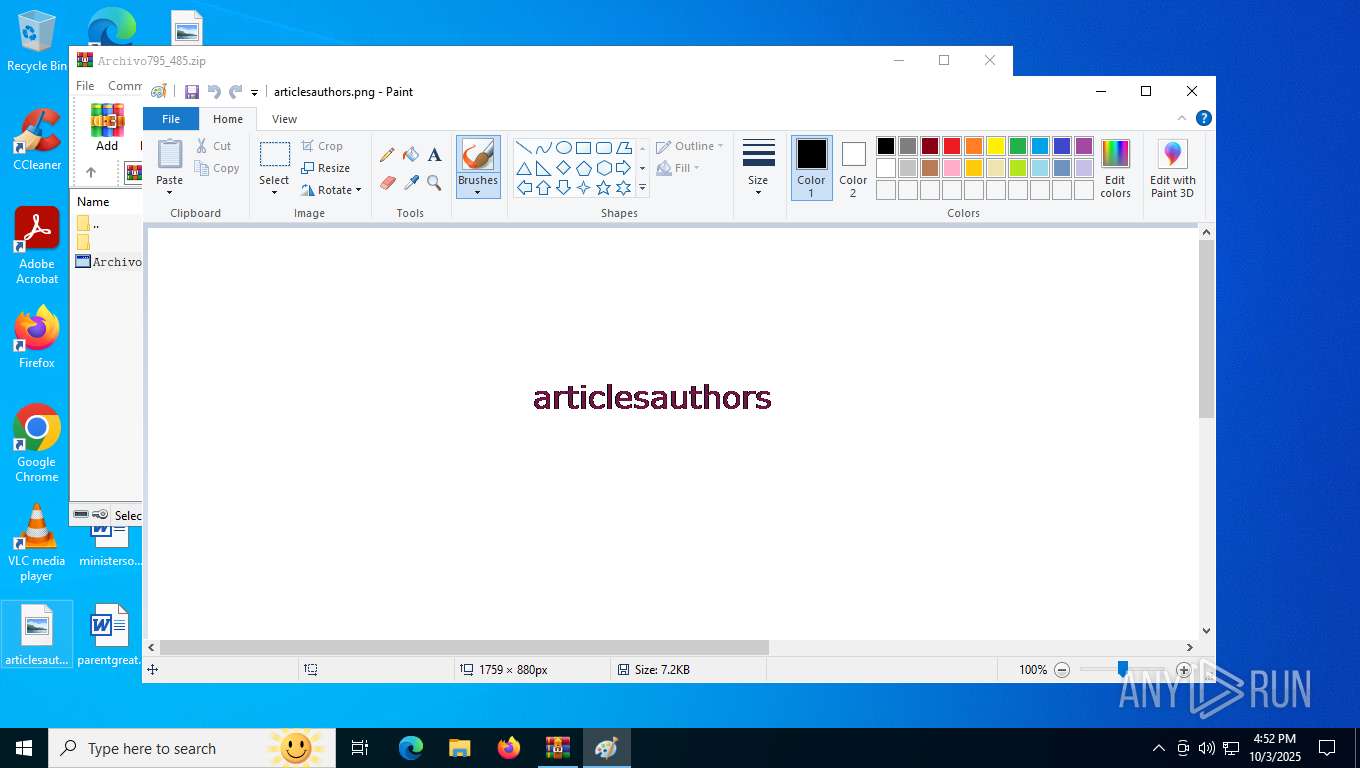
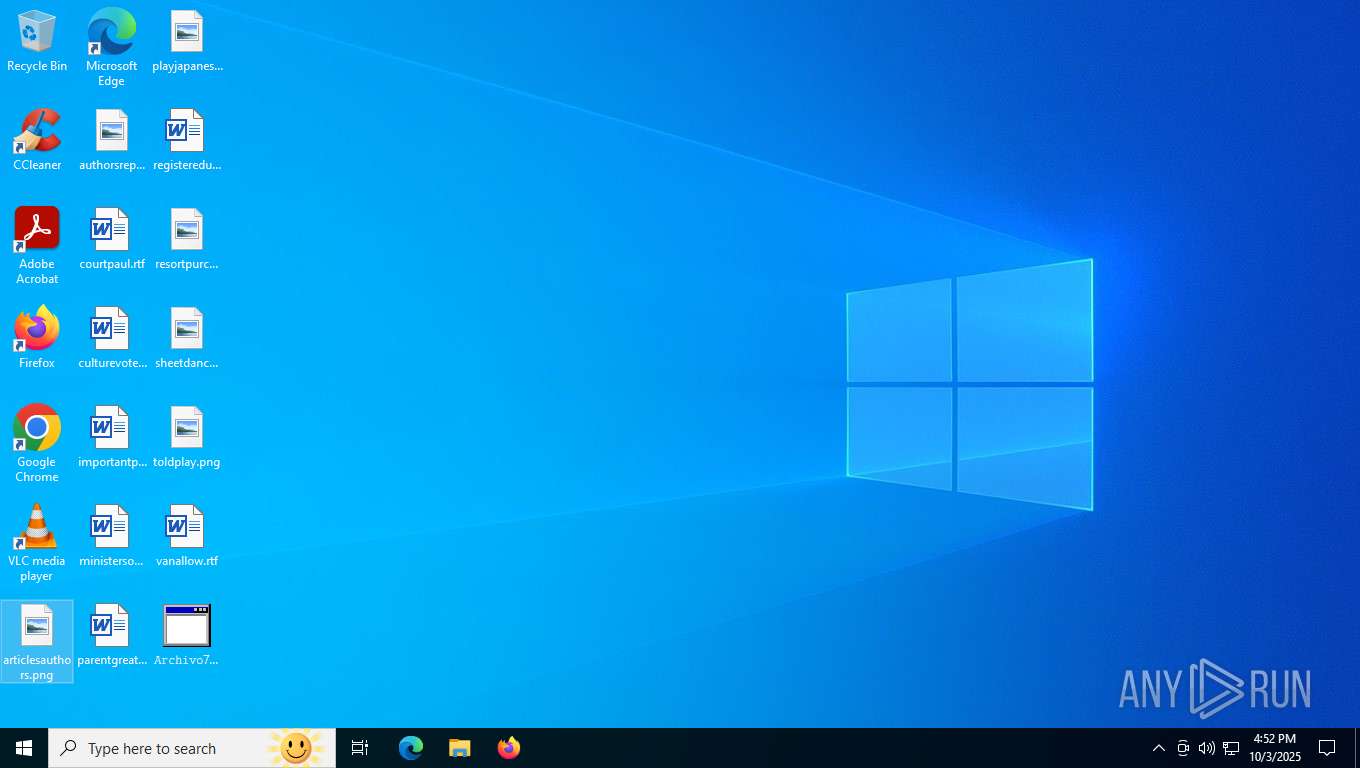
| 2864 | "C:\WINDOWS\system32\mspaint.exe" "C:\Users\admin\Desktop\articlesauthors.png" | C:\Windows\System32\mspaint.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Paint Exit code: 0 Version: 10.0.19041.3758 (WinBuild.160101.0800) Modules
| |||||||||||||||
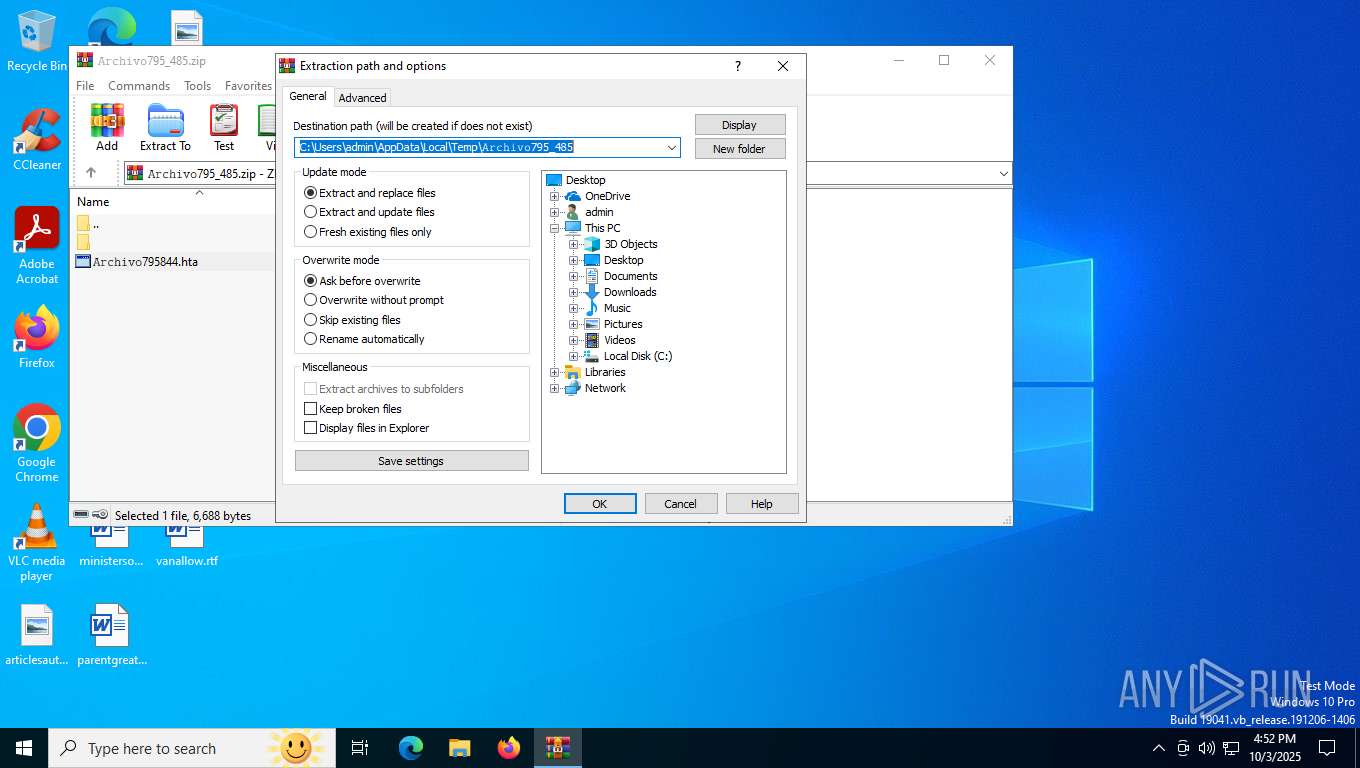
| 2896 | "C:\Windows\SysWOW64\mshta.exe" "C:\Users\admin\AppData\Local\Temp\Rar$DIa6512.44435\𝙰𝚛𝚌𝚑𝚒𝚟𝚘795844.hta" {1E460BD7-F1C3-4B2E-88BF-4E770A288AF5}{1E460BD7-F1C3-4B2E-88BF-4E770A288AF5} | C:\Windows\SysWOW64\mshta.exe | WinRAR.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft (R) HTML Application host Exit code: 0 Version: 11.00.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
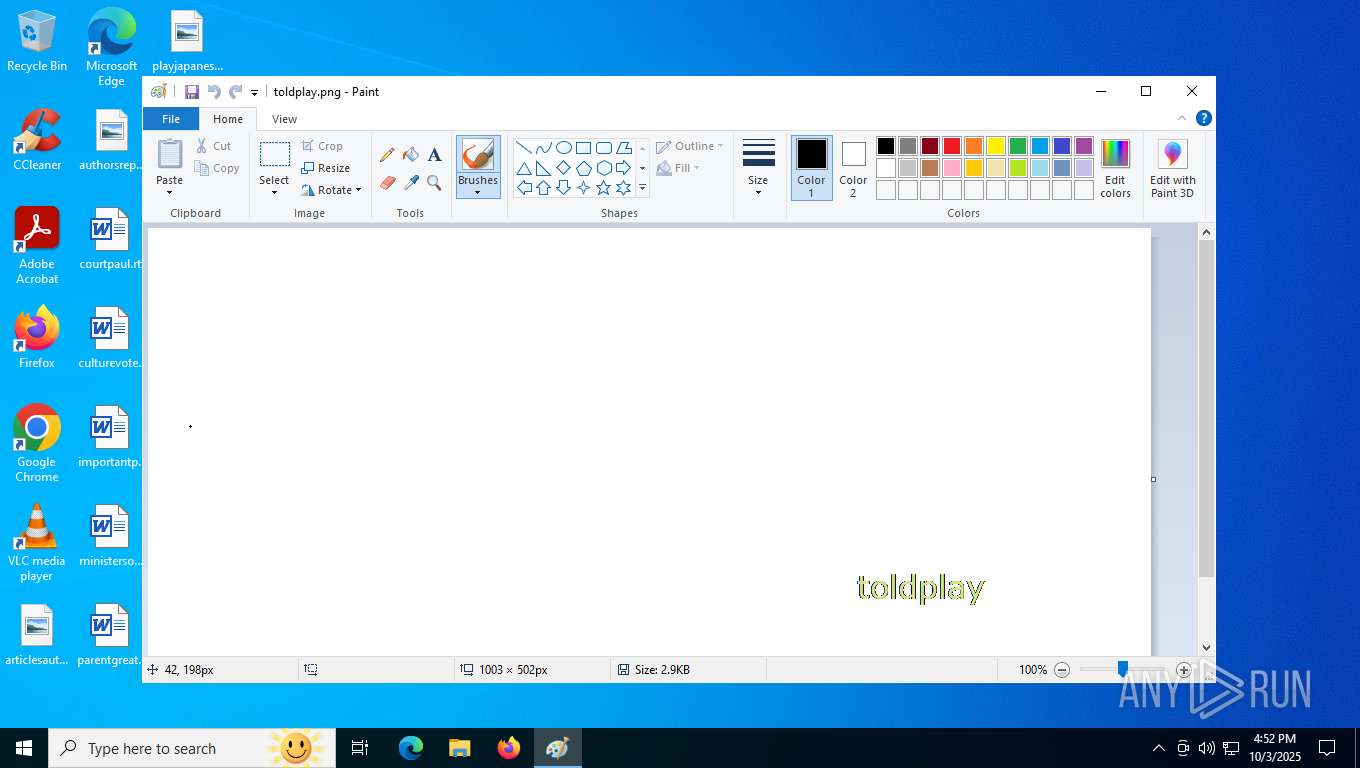
| 5584 | "C:\WINDOWS\system32\mspaint.exe" "C:\Users\admin\Desktop\toldplay.png" | C:\Windows\System32\mspaint.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Paint Exit code: 0 Version: 10.0.19041.3758 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6512 | "C:\Program Files\WinRAR\WinRAR.exe" C:\Users\admin\AppData\Local\Temp\𝙰𝚛𝚌𝚑𝚒𝚟𝚘795_485.zip | C:\Program Files\WinRAR\WinRAR.exe | — | explorer.exe | |||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Exit code: 0 Version: 5.91.0 Modules
| |||||||||||||||
| (PID) Process: | (6512) WinRAR.exe | Key: | HKEY_CLASSES_ROOT\Local Settings\MuiCache\3c\52C64B7E |
| Operation: | write | Name: | @C:\Windows\System32\mshta.exe,-6412 |
Value: HTML Application | |||
| (PID) Process: | (6512) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtBMP |
Value: | |||
| (PID) Process: | (6512) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtIcon |
Value: | |||
| (PID) Process: | (6512) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 3 |
Value: C:\Users\admin\Desktop\preferences.zip | |||
| (PID) Process: | (6512) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 2 |
Value: C:\Users\admin\Desktop\chromium_ext.zip | |||
| (PID) Process: | (6512) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 1 |
Value: C:\Users\admin\Desktop\omni_23_10_2024_.zip | |||
| (PID) Process: | (6512) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 0 |
Value: C:\Users\admin\AppData\Local\Temp\𝙰𝚛𝚌𝚑𝚒𝚟𝚘795_485.zip | |||
| (PID) Process: | (6512) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | name |
Value: 120 | |||
| (PID) Process: | (6512) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | size |
Value: 80 | |||
| (PID) Process: | (6512) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | type |
Value: 120 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2896 | mshta.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\83D863F495E7D991917B3ABB3E1EB382_552A1FD08486B486377D3C2208603584 | binary | |
MD5:D42FE64ACC33CF08CF1E8F276D2D3C9A | SHA256:83B5DA8BAD9FB442D70D1D9357430460F79B96192A14E90C3C3FADCE71FF7889 | |||
| 2896 | mshta.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\MetaData\75CA58072B9926F763A91F0CC2798706_645BC4A49DCDC40FE5917FA45C6D4517 | binary | |
MD5:150FDF9AF5D120559380AAC8B275EF23 | SHA256:88F0BE5DD898B3B41DB11A9AF439AC0F7D9553E17DB43FC4AA42CECA55AF8230 | |||
| 6512 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DIa6512.44435\𝙰𝚛𝚌𝚑𝚒𝚟𝚘795844.hta | html | |
MD5:3C255B5A16C58F2008DBAE192CF877A2 | SHA256:AD78E00EA786C4A12B99AC0D62E6070258C29A198445F5B3BBC941A2EA3E9602 | |||
| 2896 | mshta.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\75CA58072B9926F763A91F0CC2798706_645BC4A49DCDC40FE5917FA45C6D4517 | binary | |
MD5:6AB9279647E6795D3A6FDA750A0439A9 | SHA256:87F175790FFB7613BC7802FC4369F39FFECD5819A36E8082493041E3AD9E4B69 | |||
| 2896 | mshta.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\MetaData\103621DE9CD5414CC2538780B4B75751 | binary | |
MD5:7F924EAEA21BB91214FF7B4525F3BD29 | SHA256:E718475014C8F51A8F2746FBE90A7BFF516B65BEF36EE6340A5FC746BC5DFC32 | |||
| 2896 | mshta.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\MetaData\83D863F495E7D991917B3ABB3E1EB382_552A1FD08486B486377D3C2208603584 | binary | |
MD5:82412789B6FD333307F34D2B3BF270E0 | SHA256:0B10B13E5FA9C4B8F1BF9887D39D2516A7BE5A5C2A58FECCBB7D19EDC0141698 | |||
| 2896 | mshta.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\3F23679C268B8B3767EE301A5B644533 | binary | |
MD5:1B4FF19077F1152B74B6802AD8ABD5CE | SHA256:C8EB6B17E14E7E90C4FBCDDDD951D954233EA6F30CABF631ED224E7FA4716C35 | |||
| 2896 | mshta.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\MetaData\3F23679C268B8B3767EE301A5B644533 | binary | |
MD5:C9E18571FA6E13A9A31FEA6FBFAF94E9 | SHA256:9031961320A060C2FE5F5B6E87C51E6F0B70EA401DD3B365838589200CA12E06 | |||
| 2896 | mshta.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\INetCache\IE\E4DJRUXW\jOczvEXFD1[1].js | text | |
MD5:7299E2CAEBDBCB07315265974AB8145D | SHA256:FFD00623D3BD524CA289892AF18C42F6923D467FF8E836948C1A07361222681B | |||
| 2896 | mshta.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\INetCache\IE\E4DJRUXW\cid[1].htm | xml | |
MD5:FAD43F869F10D29E3010B9CC4146A94A | SHA256:B366B6FB6D575089CAFD41B066CF4C19EF8EC9F2675EBD30CBE75C6D6EB9F637 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
1828 | svchost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
2896 | mshta.exe | GET | 200 | 18.245.65.219:80 | http://ocsp.r2m03.amazontrust.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQqHI%2BsdmapawQncL1rpCEZZ8gTSAQUVdkYX9IczAHhWLS%2Bq9lVQgHXLgICEASSLs8bivtMtQSolDXxm6c%3D | US | binary | 471 b | whitelisted |
2896 | mshta.exe | GET | 200 | 18.245.38.235:80 | http://ocsp.rootca1.amazontrust.com/MFQwUjBQME4wTDAJBgUrDgMCGgUABBRPWaOUU8%2B5VZ5%2Fa9jFTaU9pkK3FAQUhBjMhTTsvAyUlC4IWZzHshBOCggCEwdzEkzUBtJnwJkc3SmanzgxeYU%3D | US | binary | 1.40 Kb | whitelisted |
2896 | mshta.exe | GET | 200 | 104.18.21.213:80 | http://r13.c.lencr.org/17.crl | unknown | binary | 83.3 Kb | whitelisted |
1828 | svchost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
1388 | backgroundTaskHost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | US | binary | 313 b | whitelisted |
6132 | backgroundTaskHost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | US | binary | 471 b | whitelisted |
5192 | backgroundTaskHost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | US | binary | 471 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
6016 | MoUsoCoreWorker.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
6332 | RUXIMICS.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5224 | SearchApp.exe | 92.123.104.32:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
2896 | mshta.exe | 68.178.207.114:443 | filesprocesomxs.cotilandiasolutions.com | GO-DADDY-COM-LLC | US | unknown |
2896 | mshta.exe | 99.84.152.39:443 | club-ui-static-files.cb.hotmart.com | AMAZON-02 | US | whitelisted |
2896 | mshta.exe | 18.245.38.235:80 | ocsp.rootca1.amazontrust.com | — | US | whitelisted |
2896 | mshta.exe | 18.245.65.219:80 | ocsp.r2m03.amazontrust.com | — | US | whitelisted |
2896 | mshta.exe | 104.18.21.213:80 | r13.c.lencr.org | CLOUDFLARENET | — | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
www.bing.com |
| whitelisted |
club-ui-static-files.cb.hotmart.com |
| unknown |
filesprocesomxs.cotilandiasolutions.com |
| unknown |
ocsp.rootca1.amazontrust.com |
| whitelisted |
ocsp.r2m03.amazontrust.com |
| whitelisted |
r13.c.lencr.org |
| unknown |
194.149.167.72.host.secureserver.net |
| malicious |
login.live.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
— | — | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |
— | — | A Network Trojan was detected | ET MALWARE Likely Malicious Windows SCT Download MSXMLHTTP AX M2 |
— | — | Misc activity | ET HUNTING [TW] Likely Javascript-Obfuscator Usage Observed M3 |
— | — | Misc activity | SUSPICIOUS [ANY.RUN] JavaScript Obfuscation (ParseInt) |
— | — | Misc activity | ET HUNTING [TW] Likely Javascript-Obfuscator Usage Observed M2 |
— | — | Misc activity | ET HUNTING [TW] Likely Javascript-Obfuscator Usage Observed M1 |
— | — | Misc activity | ET HUNTING [TW] Likely Javascript-Obfuscator Usage Observed M2 |
— | — | Misc activity | SUSPICIOUS [ANY.RUN] JavaScript Obfuscation (ParseInt) |
— | — | Misc activity | ET HUNTING [TW] Likely Javascript-Obfuscator Usage Observed M1 |
— | — | A Network Trojan was detected | ET MALWARE Likely Malicious Windows SCT Download MSXMLHTTP AX M2 |