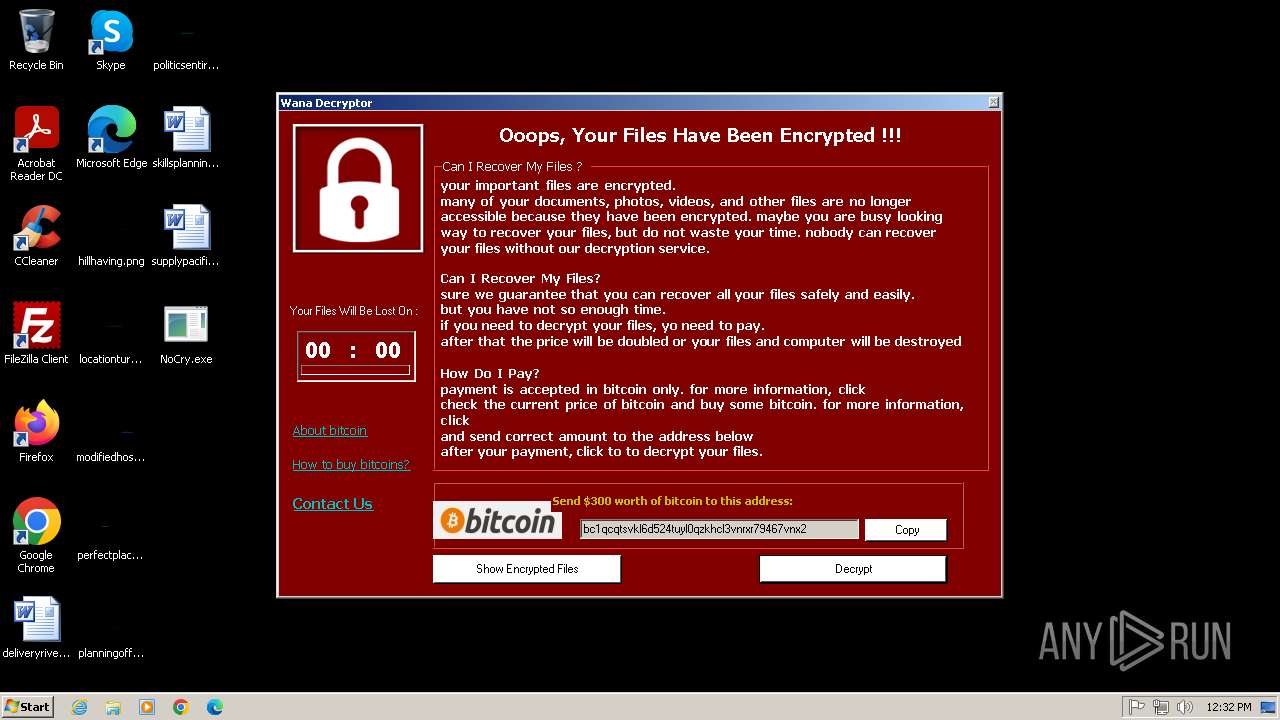
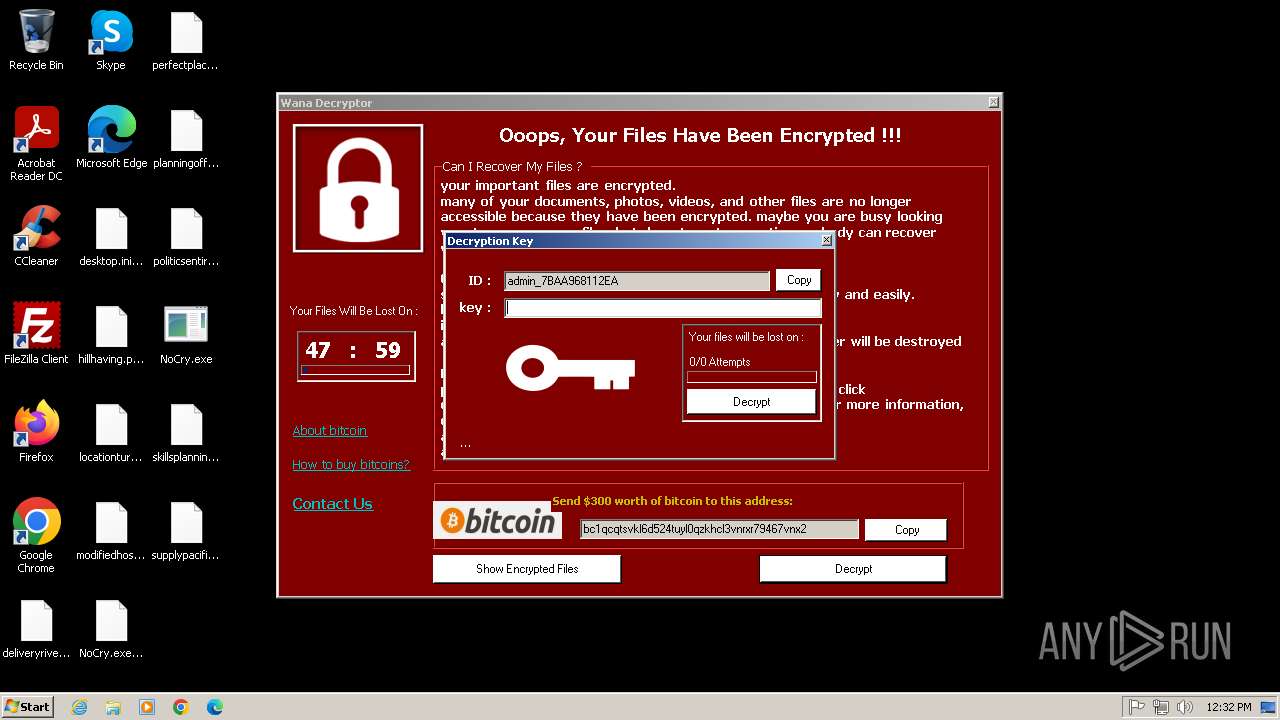
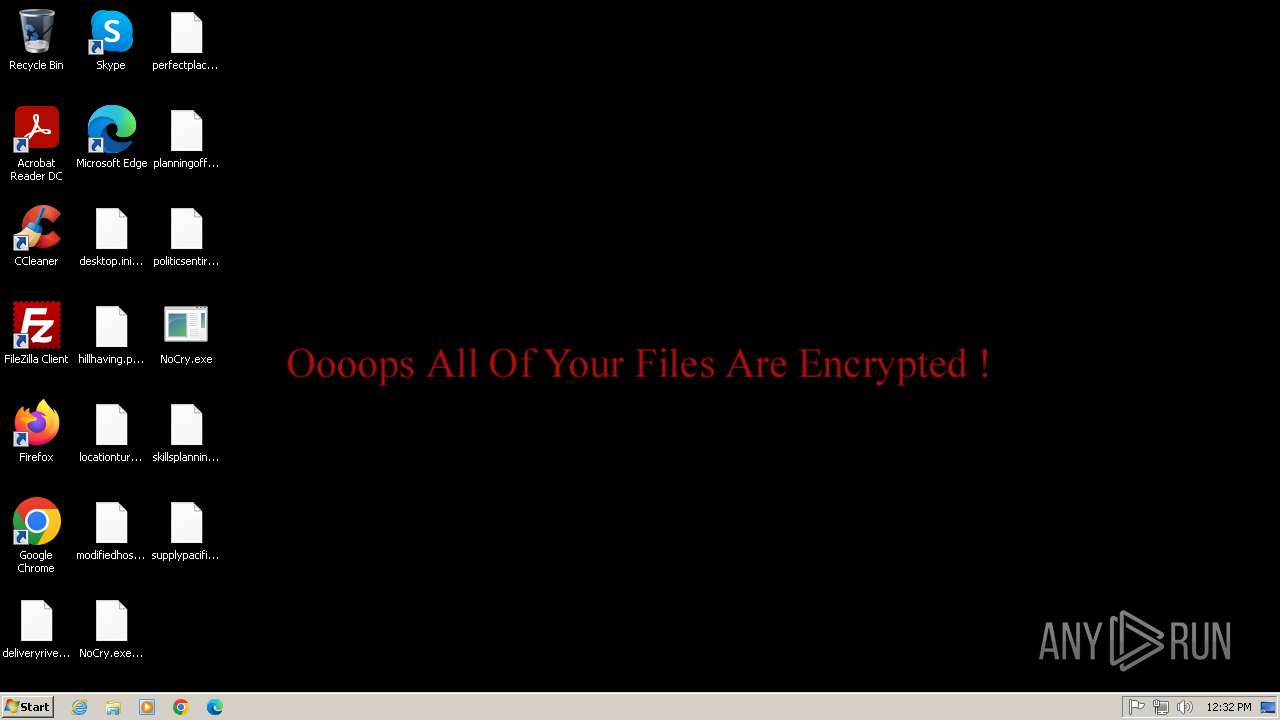
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | NoCry.exe |
| Full analysis: | https://app.any.run/tasks/954ce5f1-00c1-41e6-9c61-675915fb6c14 |
| Verdict: | Malicious activity |
| Threats: | Ransomware is a type of malicious software that locks users out of their system or data using different methods to force them to pay a ransom. Most often, such programs encrypt files on an infected machine and demand a fee to be paid in exchange for the decryption key. Additionally, such programs can be used to steal sensitive information from the compromised computer and even conduct DDoS attacks against affected organizations to pressure them into paying. |
| Analysis date: | April 13, 2025, 11:32:03 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386 Mono/.Net assembly, for MS Windows, 3 sections |
| MD5: | 3C97381E1FA936448E989BDBB32D197B |
| SHA1: | 7B20545D724B78CB7E781DF3CFB774E32CBDC1EF |
| SHA256: | 7F00765947ADED7174507E1146F8E28895402AB542D6B2B0F1969D5B7C8CE359 |
| SSDEEP: | 3072:b0UvvIpkAOWi43PVpk/OUyjn7Ed0SFtqZ918AGARsXQKa1VNnsrPC1:PvIHTi4/kejn76AZJGAI5 |
| .exe | | | Generic CIL Executable (.NET, Mono, etc.) (72.2) |
|---|---|---|
| .scr | | | Windows screen saver (12.9) |
| .dll | | | Win32 Dynamic Link Library (generic) (6.4) |
| .exe | | | Win32 Executable (generic) (4.4) |
| .exe | | | Generic Win/DOS Executable (1.9) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2025:04:07 00:18:09+00:00 |
| ImageFileCharacteristics: | Executable, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 8 |
| CodeSize: | 214528 |
| InitializedDataSize: | 1536 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x3648e |
| OSVersion: | 4 |
| ImageVersion: | - |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1080 | C:\Windows\system32\svchost.exe -k NetworkService | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2480 | "C:\Users\admin\Desktop\NoCry.exe" | C:\Users\admin\Desktop\NoCry.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 3076 | "C:\Windows\System32\WScript.exe" "C:\Users\admin\AppData\Local\Temp\del.vbs" | C:\Windows\System32\wscript.exe | — | NoCry.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft ® Windows Based Script Host Exit code: 0 Version: 5.8.7600.16385 Modules
| |||||||||||||||
| (PID) Process: | (1080) svchost.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\NetworkList\Nla\Cache\Intranet |
| Operation: | write | Name: | {4040CF00-1B3E-486A-B407-FA14C56B6FC0} |
Value: D4DA6D42058C | |||
| (PID) Process: | (2480) NoCry.exe | Key: | HKEY_CURRENT_USER\Software\VB and VBA Program Settings\F\0 |
| Operation: | write | Name: | Runcount.cry |
Value: 9IbTe6sZpfSAX6RXo8RRA0rxEIzu0yFIFS5AkdkeshQ= | |||
| (PID) Process: | (2480) NoCry.exe | Key: | HKEY_CURRENT_USER\Software\VB and VBA Program Settings\G\0 |
| Operation: | write | Name: | Runcount.cry |
Value: 6aMM+VBiOGERUT9MgC3ZIw== | |||
| (PID) Process: | (2480) NoCry.exe | Key: | HKEY_CURRENT_USER\Software\VB and VBA Program Settings\H\0 |
| Operation: | write | Name: | Runcount.cry |
Value: 48 | |||
| (PID) Process: | (2480) NoCry.exe | Key: | HKEY_CURRENT_USER\Software\VB and VBA Program Settings\M\0 |
| Operation: | write | Name: | Runcount.cry |
Value: 0 | |||
| (PID) Process: | (2480) NoCry.exe | Key: | HKEY_CURRENT_USER\Software\VB and VBA Program Settings\S\0 |
| Operation: | write | Name: | Runcount.cry |
Value: 59 | |||
| (PID) Process: | (2480) NoCry.exe | Key: | HKEY_CURRENT_USER\Software\VB and VBA Program Settings\P\0 |
| Operation: | write | Name: | Runcount.cry |
Value: 0 | |||
| (PID) Process: | (2480) NoCry.exe | Key: | HKEY_CURRENT_USER\Software\VB and VBA Program Settings\X\0 |
| Operation: | write | Name: | Runcount.cry |
Value: 48 | |||
| (PID) Process: | (2480) NoCry.exe | Key: | HKEY_CURRENT_USER\Software\VB and VBA Program Settings\P\0 |
| Operation: | write | Name: | Runcount.cry |
Value: 1 | |||
| (PID) Process: | (2480) NoCry.exe | Key: | HKEY_CURRENT_USER\Software\VB and VBA Program Settings\H\0 |
| Operation: | write | Name: | Runcount.cry |
Value: 47 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2480 | NoCry.exe | C:\Users\admin\Desktop\NoCry.exe.lmao | binary | |
MD5:3918C4ED2E9402C7DD0FDDAB62393247 | SHA256:1999379D9793B1E0B61A956B4714EAC0F395FE31CE1F40CDF46C9F6366DA39C9 | |||
| 2480 | NoCry.exe | C:\Users\admin\Desktop\politicsentire.png.lmao | binary | |
MD5:E1630BEAC9CB4C41C016120DB9089C7B | SHA256:824C060BC7BF1906F6E49F290C3F56F5CAF0A68082268CE5A805A7AE6108E461 | |||
| 2480 | NoCry.exe | C:\Users\admin\NTUSER.DAT{6cced2f1-6e01-11de-8bed-001e0bcd1824}.TM.blf.lmao | binary | |
MD5:3D36FF805D9F8CF02E58237CD3192018 | SHA256:48201C35A566882F1CF3F734F1939800F61D637B2926930DF22C9B811305C9C4 | |||
| 2480 | NoCry.exe | C:\Users\admin\ntuser.dat.LOG1.lmao | binary | |
MD5:3D36FF805D9F8CF02E58237CD3192018 | SHA256:48201C35A566882F1CF3F734F1939800F61D637B2926930DF22C9B811305C9C4 | |||
| 2480 | NoCry.exe | C:\Users\admin\NTUSER.DAT.lmao | binary | |
MD5:3D36FF805D9F8CF02E58237CD3192018 | SHA256:48201C35A566882F1CF3F734F1939800F61D637B2926930DF22C9B811305C9C4 | |||
| 2480 | NoCry.exe | C:\Users\admin\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\cgKDgnpFCNy1GXpD.exe | executable | |
MD5:3C97381E1FA936448E989BDBB32D197B | SHA256:7F00765947ADED7174507E1146F8E28895402AB542D6B2B0F1969D5B7C8CE359 | |||
| 2480 | NoCry.exe | C:\Users\admin\ntuser.dat.LOG2.lmao | binary | |
MD5:3D36FF805D9F8CF02E58237CD3192018 | SHA256:48201C35A566882F1CF3F734F1939800F61D637B2926930DF22C9B811305C9C4 | |||
| 2480 | NoCry.exe | C:\Users\admin\NTUSER.DAT{6cced2f1-6e01-11de-8bed-001e0bcd1824}.TMContainer00000000000000000002.regtrans-ms.lmao | binary | |
MD5:3D36FF805D9F8CF02E58237CD3192018 | SHA256:48201C35A566882F1CF3F734F1939800F61D637B2926930DF22C9B811305C9C4 | |||
| 2480 | NoCry.exe | C:\Users\admin\NTUSER.DAT{6cced2f1-6e01-11de-8bed-001e0bcd1824}.TMContainer00000000000000000001.regtrans-ms.lmao | binary | |
MD5:3D36FF805D9F8CF02E58237CD3192018 | SHA256:48201C35A566882F1CF3F734F1939800F61D637B2926930DF22C9B811305C9C4 | |||
| 2480 | NoCry.exe | C:\Users\admin\.oracle_jre_usage\90737d32e3abaa4.timestamp.lmao | binary | |
MD5:F1AEB5C1481FEAD93D8786BC83E253AA | SHA256:9C495A7D92813C95B458ECDA98AEF1E335F3B31C9CD054E811E28E417122F8B1 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
2480 | NoCry.exe | GET | 301 | 13.113.196.52:80 | http://site.com/log.php?admin_7BAA968112EA=im2AbOuaQYhKow4zRxzc | JP | — | — | malicious |
2480 | NoCry.exe | GET | 301 | 13.113.196.52:80 | http://site.com/log.php?admin_7BAA968112EA=im2AbOuaQYhKow4zRxzc | JP | — | — | malicious |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 224.0.0.252:5355 | — | — | — | whitelisted |
1080 | svchost.exe | 224.0.0.252:5355 | — | — | — | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
2480 | NoCry.exe | 13.113.196.52:80 | site.com | AMAZON-02 | JP | malicious |
2480 | NoCry.exe | 13.113.196.52:443 | site.com | AMAZON-02 | JP | malicious |
Domain | IP | Reputation |
|---|---|---|
google.com |
| whitelisted |
site.com |
| malicious |
PID | Process | Class | Message |
|---|---|---|---|
2480 | NoCry.exe | Malware Command and Control Activity Detected | RANSOMWARE [ANY.RUN] NoCry Ransomware CnC Communication |