ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| URL: | https://gamefervor.com:443/api/getisti/11480082?url=https://s3-us-west-1.amazonaws.com/ext-emulator/flow-helper/minigame/installer4.exe&appid=com.tencent.ig |
| Full analysis: | https://app.any.run/tasks/6a317278-91d3-48a4-a019-352d8540bb82 |
| Verdict: | Malicious activity |
| Threats: | A loader is malicious software that infiltrates devices to deliver malicious payloads. This malware is capable of infecting victims’ computers, analyzing their system information, and installing other types of threats, such as trojans or stealers. Criminals usually deliver loaders through phishing emails and links by relying on social engineering to trick users into downloading and running their executables. Loaders employ advanced evasion and persistence tactics to avoid detection. |
| Analysis date: | September 14, 2019, 11:18:58 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MD5: | C2F2C4F654E0D640F004F70C58D3B5B8 |
| SHA1: | 530812F7FCEBB563E18E35EEFE2D37268B65BF5F |
| SHA256: | 7EB913FC76B723206DF4354F9D57C001CD6945DBC172FF80996E5CE1B030BDB4 |
| SSDEEP: | 3:N8lQuKu9LDjaQXKVYpWIzPSEBQ7WtAT9txYJKSDsKxLDhSWRgOXRLREbyuRP:26uKpCKO13BQrptxYEmsugWRgOXRLiD9 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 364 | ATTRIB -r "\\?\C:\Users\admin\AppData\Local\Temp\{4A081~1\TEMPLA~1.MSI" | C:\Windows\system32\attrib.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Attribute Utility Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1032 | DrvInst.exe "1" "200" "STORAGE\VolumeSnapshot\HarddiskVolumeSnapshot22" "" "" "695c3f483" "00000000" "000005BC" "000003C8" | C:\Windows\system32\DrvInst.exe | — | svchost.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Driver Installation Module Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
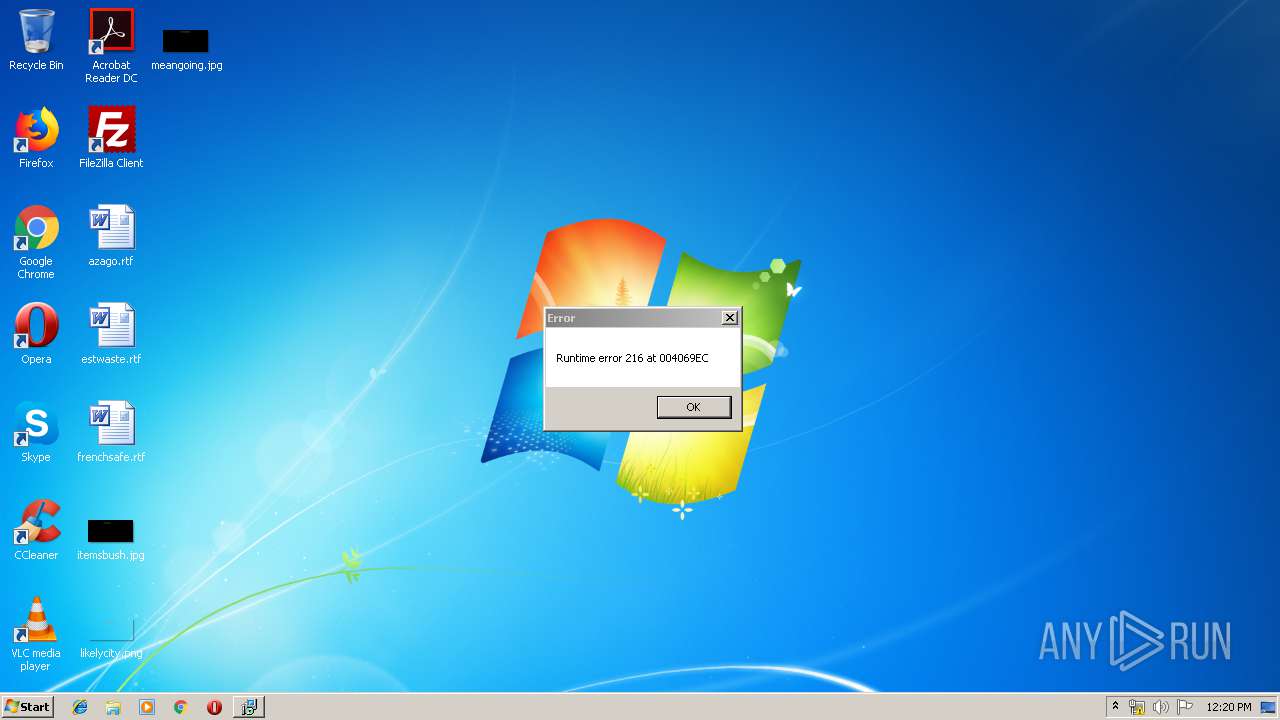
| 1336 | "C:\Users\admin\AppData\Roaming\Direct Game UNI Installer\dynamicgame__dy_1743176615.exe" | C:\Users\admin\AppData\Roaming\Direct Game UNI Installer\dynamicgame__dy_1743176615.exe | GameOffer.exe | ||||||||||||
User: admin Company: Integrity Level: MEDIUM Description: Lite Setup Exit code: 216 Version: Modules
| |||||||||||||||
| 1364 | ATTRIB -r "C:\Users\admin\AppData\Local\Temp\EXE3B6.tmp.bat" | C:\Windows\system32\attrib.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Attribute Utility Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1400 | C:\Windows\system32\cmd.exe /S /D /c" del "C:\Users\admin\AppData\Local\Temp\EXE4C1.tmp.bat" " | C:\Windows\system32\cmd.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 0 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
| 1512 | C:\Windows\system32\vssvc.exe | C:\Windows\system32\vssvc.exe | — | services.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Microsoft® Volume Shadow Copy Service Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1640 | -NoProfile -Noninteractive -ExecutionPolicy Bypass -File "C:\Users\admin\AppData\Local\Temp\pss410A.ps1" | C:\Windows\system32\WindowsPowerShell\v1.0\powershell.exe | — | MsiExec.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows PowerShell Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
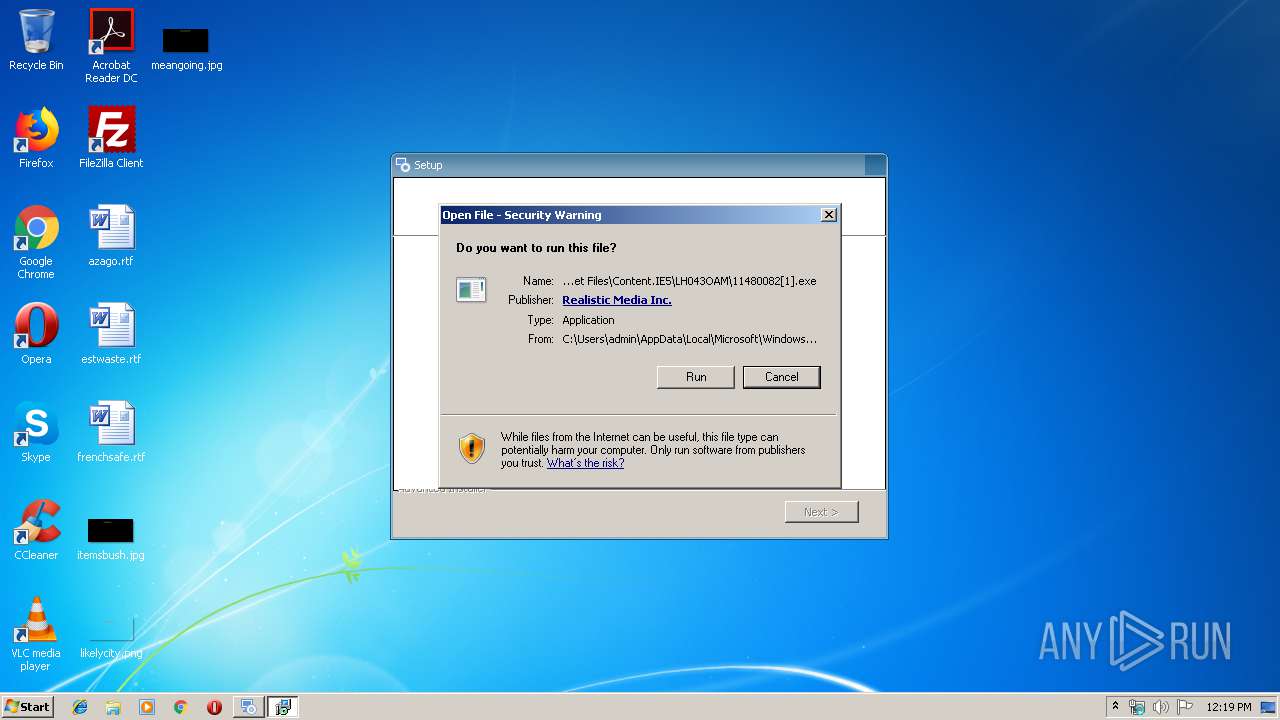
| 1796 | "C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\LH043OAM\11480082[1].exe" | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\LH043OAM\11480082[1].exe | iexplore.exe | ||||||||||||
User: admin Company: GamesLOL Integrity Level: MEDIUM Description: Direct Game UNI Installer Installer Exit code: 0 Version: 1.0.15 Modules
| |||||||||||||||
| 2124 | -NoProfile -Noninteractive -ExecutionPolicy Bypass -File "C:\Users\admin\AppData\Local\Temp\pss959.ps1" | C:\Windows\system32\WindowsPowerShell\v1.0\powershell.exe | MsiExec.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows PowerShell Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2248 | -NoProfile -Noninteractive -ExecutionPolicy Bypass -File "C:\Users\admin\AppData\Local\Temp\pssEAEE.ps1" | C:\Windows\system32\WindowsPowerShell\v1.0\powershell.exe | MsiExec.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows PowerShell Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| (PID) Process: | (3540) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Main |
| Operation: | write | Name: | CompatibilityFlags |
Value: 0 | |||
| (PID) Process: | (3540) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | UNCAsIntranet |
Value: 0 | |||
| (PID) Process: | (3540) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | AutoDetect |
Value: 1 | |||
| (PID) Process: | (3540) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\Zones |
| Operation: | write | Name: | SecuritySafe |
Value: 1 | |||
| (PID) Process: | (3540) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings |
| Operation: | write | Name: | ProxyEnable |
Value: 0 | |||
| (PID) Process: | (3540) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\Connections |
| Operation: | write | Name: | SavedLegacySettings |
Value: 4600000092000000010000000000000000000000000000000000000000000000C0E333BBEAB1D301000000000000000000000000020000001700000000000000FE800000000000007D6CB050D9C573F70B000000000000006D00330032005C004D00530049004D004700330032002E0064006C000100000004AA400014AA4000040000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000002000000C0A8016400000000000000000000000000000000000000000800000000000000805D3F00983740000008000002000000000000600000002060040000B8A94000020000008802000060040000B8A9400004000000F8010000B284000088B64000B84B400043003A000000000000000000000000000000000000000000 | |||
| (PID) Process: | (3540) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Recovery\Active |
| Operation: | write | Name: | {7ADB0815-D6E1-11E9-B86F-5254004A04AF} |
Value: 0 | |||
| (PID) Process: | (3540) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{2670000A-7350-4F3C-8081-5663EE0C6C49}\iexplore |
| Operation: | write | Name: | Type |
Value: 4 | |||
| (PID) Process: | (3540) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{2670000A-7350-4F3C-8081-5663EE0C6C49}\iexplore |
| Operation: | write | Name: | Count |
Value: 2 | |||
| (PID) Process: | (3540) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{2670000A-7350-4F3C-8081-5663EE0C6C49}\iexplore |
| Operation: | write | Name: | Time |
Value: E307090006000E000B0013000E008400 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3540 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\LH043OAM\favicon[1].ico | — | |
MD5:— | SHA256:— | |||
| 3540 | iexplore.exe | C:\Users\admin\AppData\LocalLow\Microsoft\Internet Explorer\Services\search_{0633EE93-D776-472f-A0FF-E1416B8B2E3A}.ico | — | |
MD5:— | SHA256:— | |||
| 4028 | iexplore.exe | C:\Users\admin\AppData\Local\Temp\Low\Cab9D00.tmp | — | |
MD5:— | SHA256:— | |||
| 4028 | iexplore.exe | C:\Users\admin\AppData\Local\Temp\Low\Tar9D01.tmp | — | |
MD5:— | SHA256:— | |||
| 4028 | iexplore.exe | C:\Users\admin\AppData\Local\Temp\Low\Cab9D12.tmp | — | |
MD5:— | SHA256:— | |||
| 4028 | iexplore.exe | C:\Users\admin\AppData\Local\Temp\Low\Tar9D13.tmp | — | |
MD5:— | SHA256:— | |||
| 4028 | iexplore.exe | C:\Users\admin\AppData\Local\Temp\Low\Cab9DB0.tmp | — | |
MD5:— | SHA256:— | |||
| 4028 | iexplore.exe | C:\Users\admin\AppData\Local\Temp\Low\Tar9DB1.tmp | — | |
MD5:— | SHA256:— | |||
| 3540 | iexplore.exe | C:\Users\admin\AppData\Local\Temp\~DF93B0694FEB23EFCE.TMP | — | |
MD5:— | SHA256:— | |||
| 4028 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Low\Content.IE5\O2D58JPZ\desktop.ini | ini | |
MD5:4A3DEB274BB5F0212C2419D3D8D08612 | SHA256:2842973D15A14323E08598BE1DFB87E54BF88A76BE8C7BC94C56B079446EDF38 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
1796 | 11480082[1].exe | GET | 200 | 13.225.78.105:80 | http://pads289.net/app/banner?it=3&fhnid= | US | html | 167 b | shared |
1796 | 11480082[1].exe | GET | 200 | 13.224.196.81:80 | http://sun346.net/app/banner?it=1&fhnid= | US | html | 167 b | whitelisted |
2596 | MsiExec.exe | GET | 200 | 172.217.18.4:80 | http://www.google.com/ | US | html | 12.2 Kb | malicious |
1796 | 11480082[1].exe | GET | 200 | 13.225.78.105:80 | http://pads289.net/Content/Site.css | US | text | 412 b | shared |
2124 | powershell.exe | POST | — | 52.33.155.26:80 | http://logs-01.loggly.com/inputs/1f667d94-35d0-4958-aa21-54e5d3fd784d/tag/browser-assistant/ | US | — | — | whitelisted |
1796 | 11480082[1].exe | GET | — | 13.224.196.81:80 | http://sun346.net/app/banner?it=3&fhnid= | US | — | — | whitelisted |
1796 | 11480082[1].exe | GET | 200 | 13.224.196.81:80 | http://sun346.net/Content/Site.css | US | text | 412 b | whitelisted |
2800 | powershell.exe | POST | — | 52.33.155.26:80 | http://logs-01.loggly.com/inputs/1f667d94-35d0-4958-aa21-54e5d3fd784d/tag/browser-assistant/ | US | — | — | whitelisted |
1796 | 11480082[1].exe | GET | 200 | 13.224.196.81:80 | http://sun346.net/app/banner?it=2&fhnid= | US | html | 167 b | whitelisted |
4088 | BrowserAssistant.exe | POST | 200 | 52.33.155.26:80 | http://logs-01.loggly.com/inputs/1f667d94-35d0-4958-aa21-54e5d3fd784d/tag/browser-assistant/ | US | text | 19 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4028 | iexplore.exe | 13.225.78.87:443 | gamefervor.com | — | US | suspicious |
3540 | iexplore.exe | 204.79.197.200:80 | www.bing.com | Microsoft Corporation | US | whitelisted |
4028 | iexplore.exe | 95.101.72.131:80 | www.download.windowsupdate.com | Akamai International B.V. | — | whitelisted |
2596 | MsiExec.exe | 172.217.18.4:80 | www.google.com | Google Inc. | US | whitelisted |
4028 | iexplore.exe | 143.204.98.159:80 | x.ss2.us | — | US | suspicious |
1796 | 11480082[1].exe | 13.224.196.81:80 | sun346.net | — | US | suspicious |
1796 | 11480082[1].exe | 13.225.78.105:80 | pads289.net | — | US | malicious |
3596 | powershell.exe | 52.33.155.26:80 | logs-01.loggly.com | Amazon.com, Inc. | US | unknown |
2124 | powershell.exe | 52.33.155.26:80 | logs-01.loggly.com | Amazon.com, Inc. | US | unknown |
2800 | powershell.exe | 52.33.155.26:80 | logs-01.loggly.com | Amazon.com, Inc. | US | unknown |
Domain | IP | Reputation |
|---|---|---|
gamefervor.com |
| whitelisted |
www.bing.com |
| whitelisted |
x.ss2.us |
| whitelisted |
www.download.windowsupdate.com |
| whitelisted |
www.google.com |
| malicious |
pads289.net |
| shared |
sun346.net |
| whitelisted |
logs-01.loggly.com |
| whitelisted |
ravenfile.com |
| suspicious |
www.nevenetet-yasak.com |
| suspicious |
PID | Process | Class | Message |
|---|---|---|---|
3576 | GameOffer.exe | A Network Trojan was detected | ET USER_AGENTS Suspicious User-Agent (MSIE) |
3576 | GameOffer.exe | A Network Trojan was detected | ET USER_AGENTS Suspicious User-Agent (MSIE) |
3576 | GameOffer.exe | Potential Corporate Privacy Violation | ET POLICY PE EXE or DLL Windows file download HTTP |
3576 | GameOffer.exe | Misc activity | ET INFO EXE - Served Attached HTTP |