ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| URL: | https://gltnub.live/d/St%65el%53e%72%69e%73-%47G |
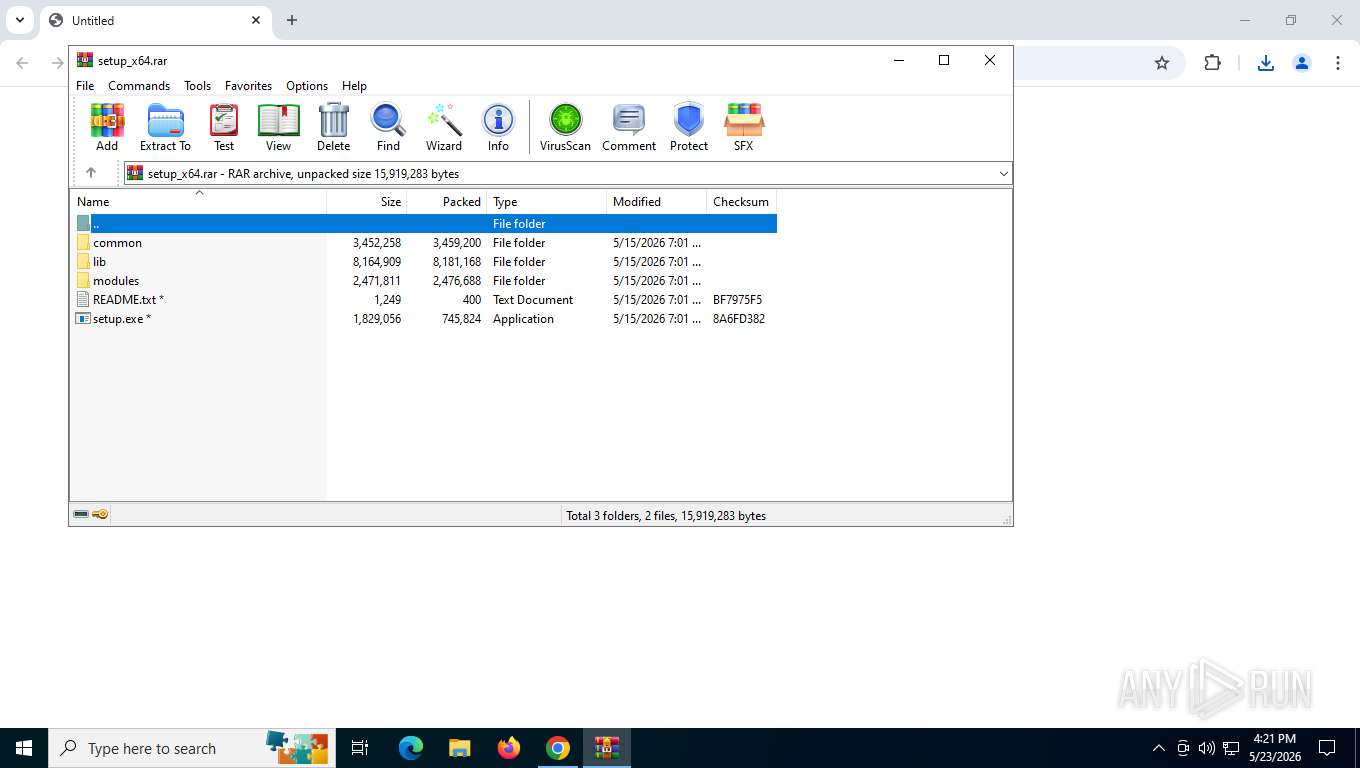
| Full analysis: | https://app.any.run/tasks/9f09445e-9422-4652-8807-d2e099446a25 |
| Verdict: | Malicious activity |
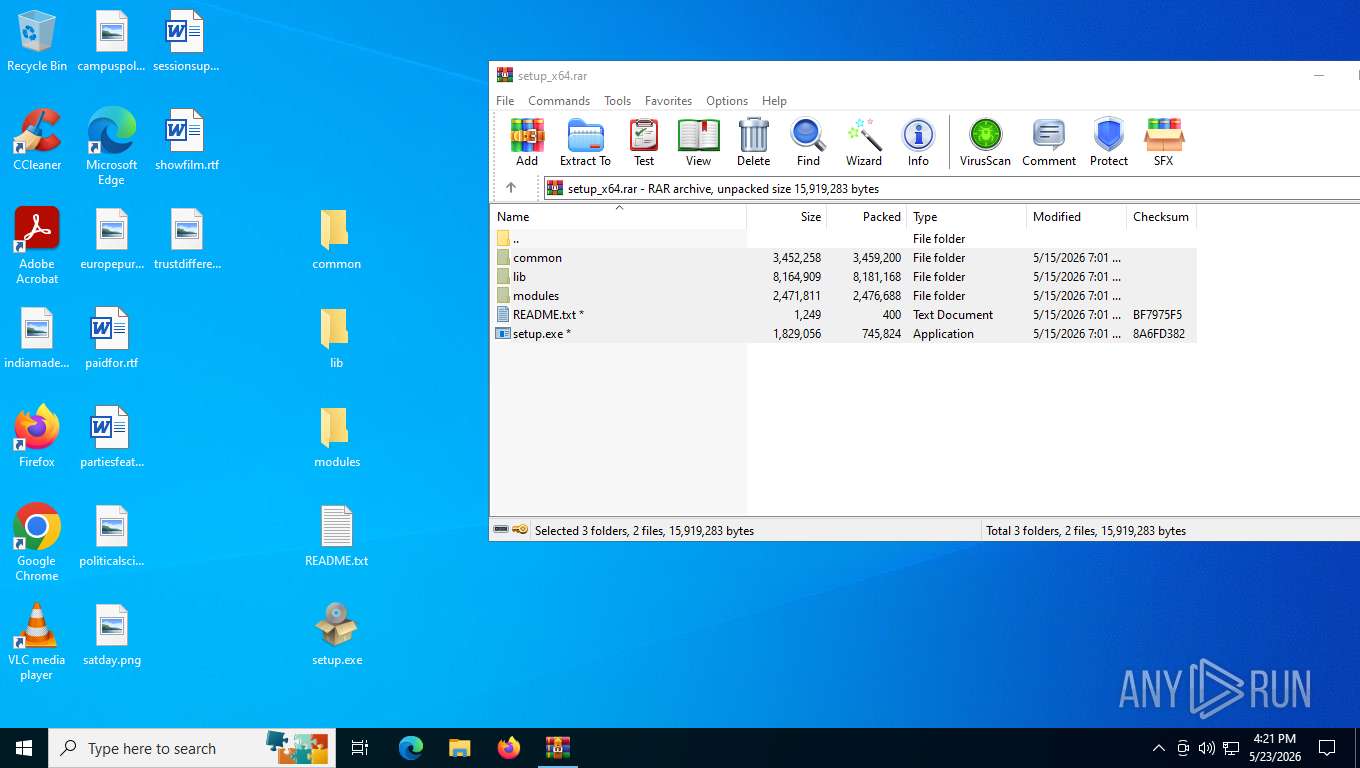
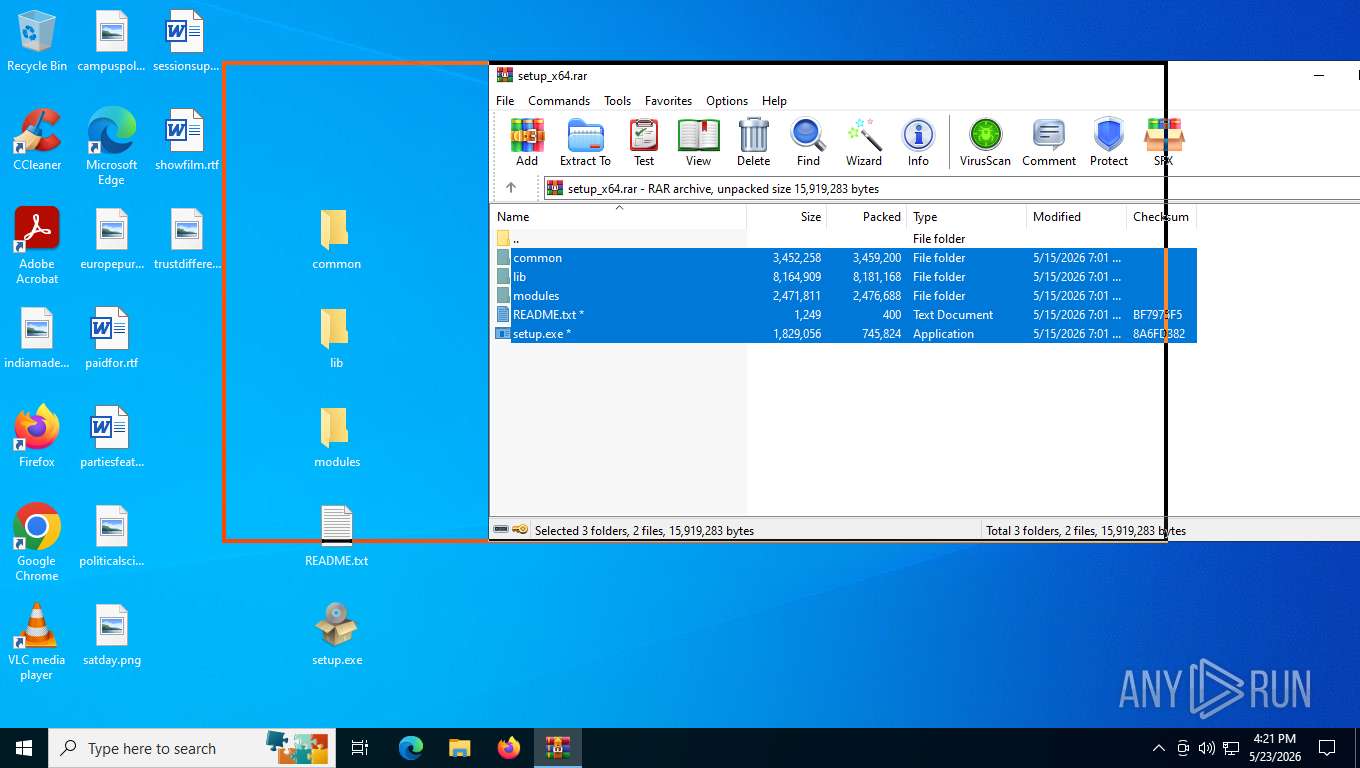
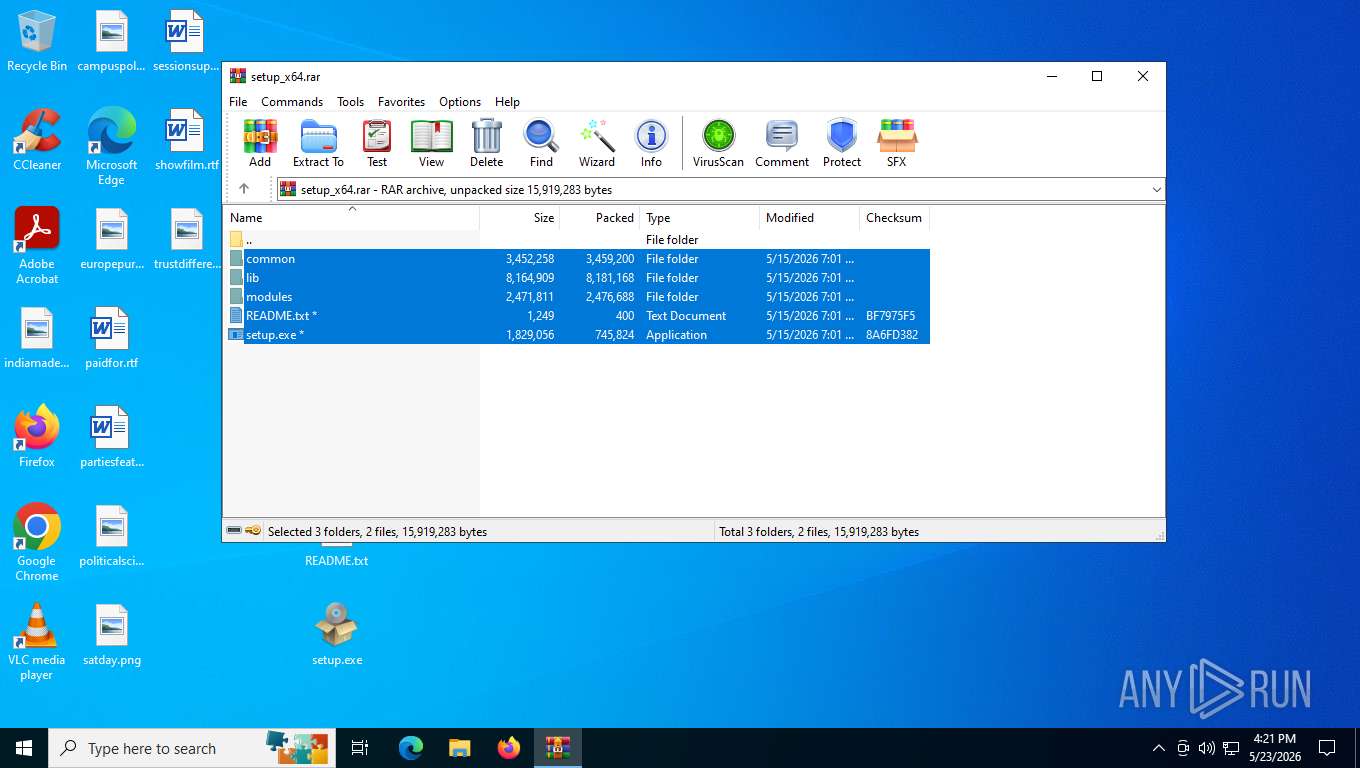
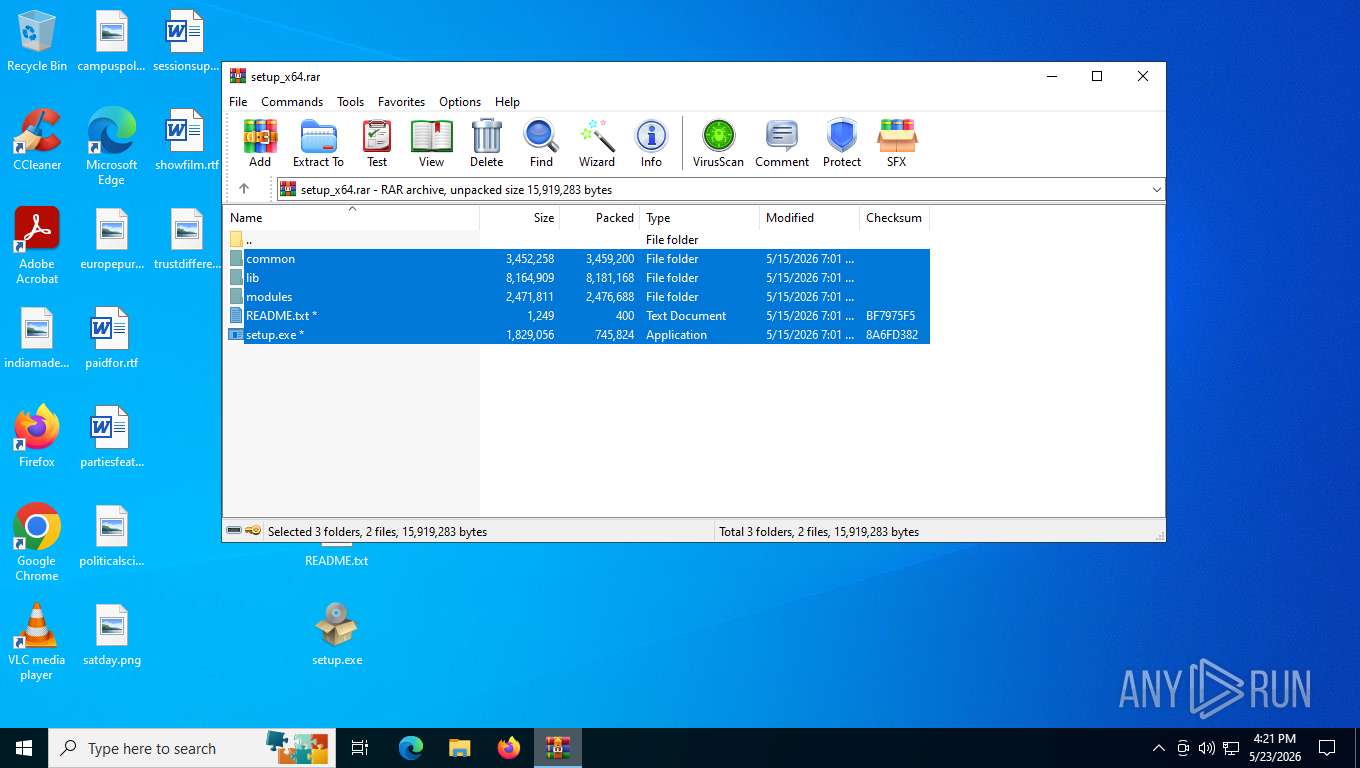
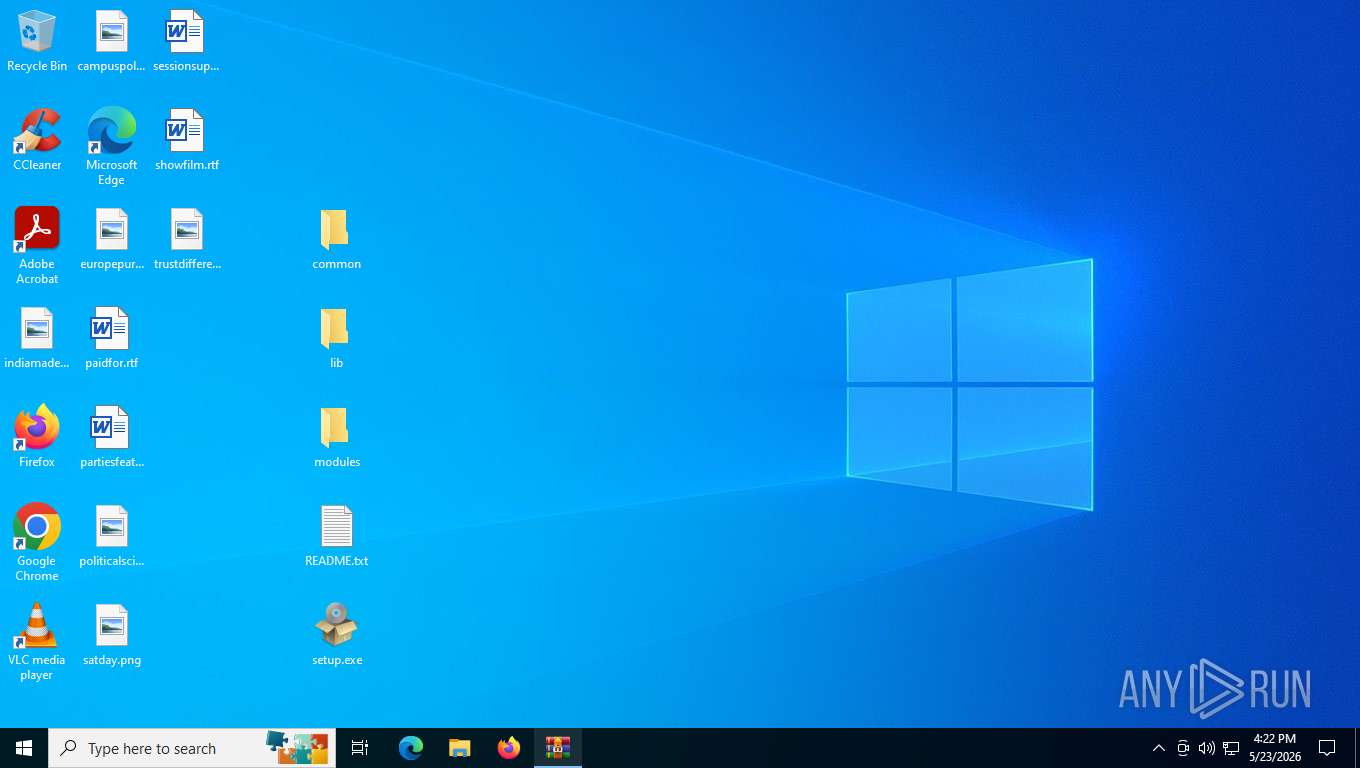
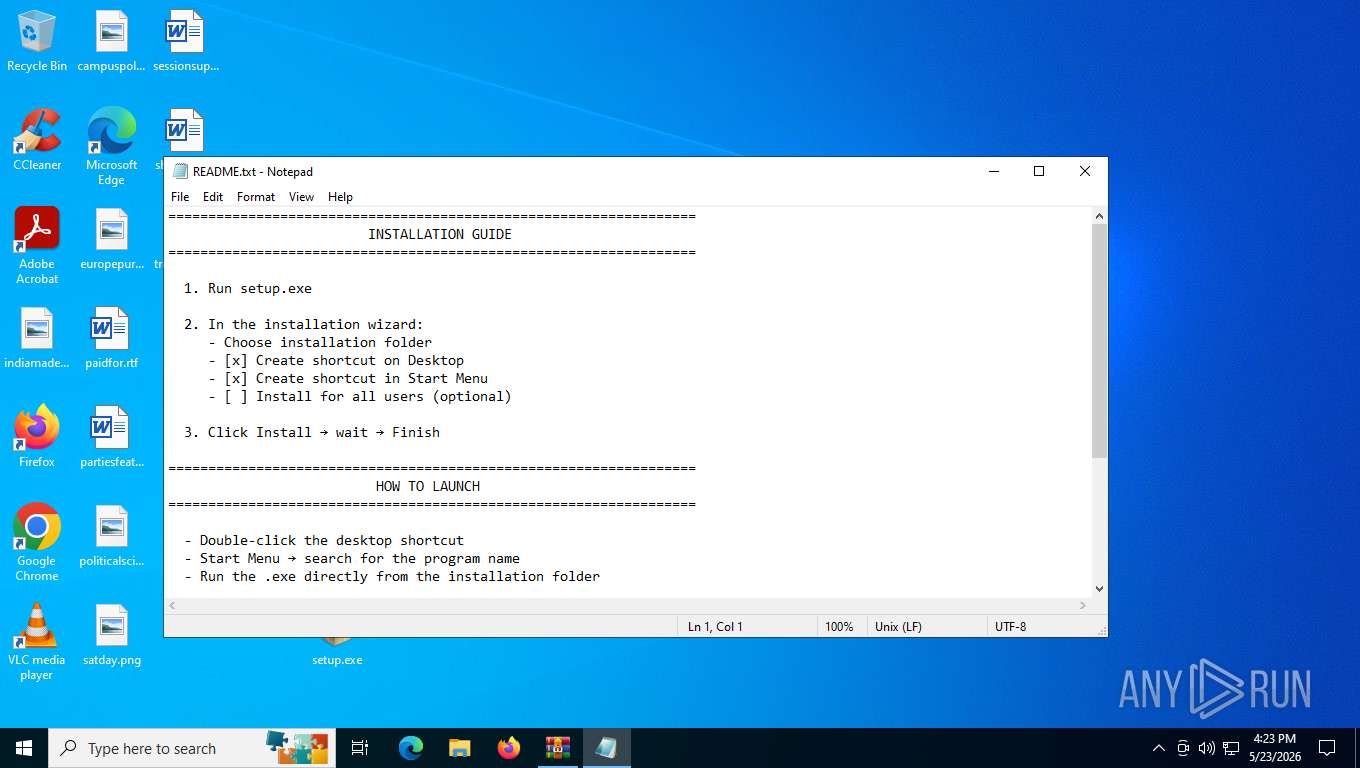
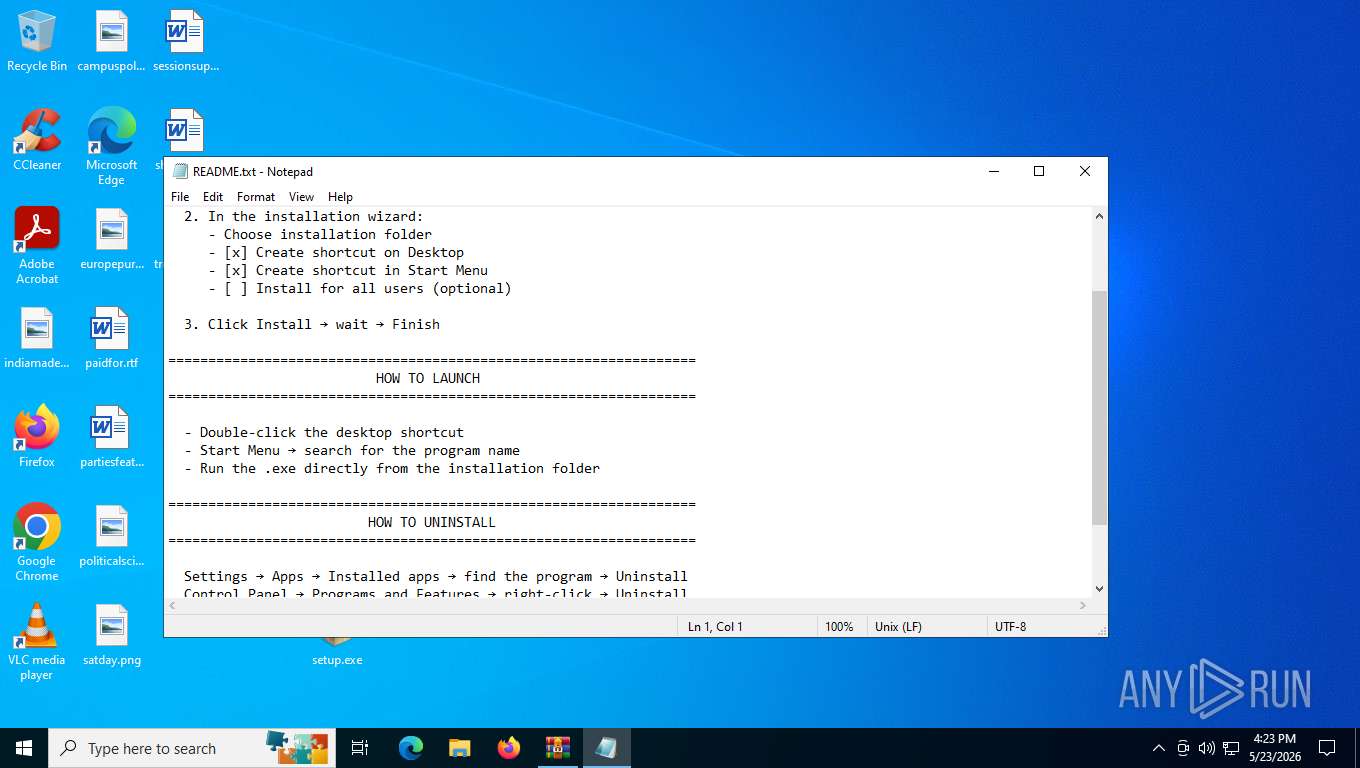
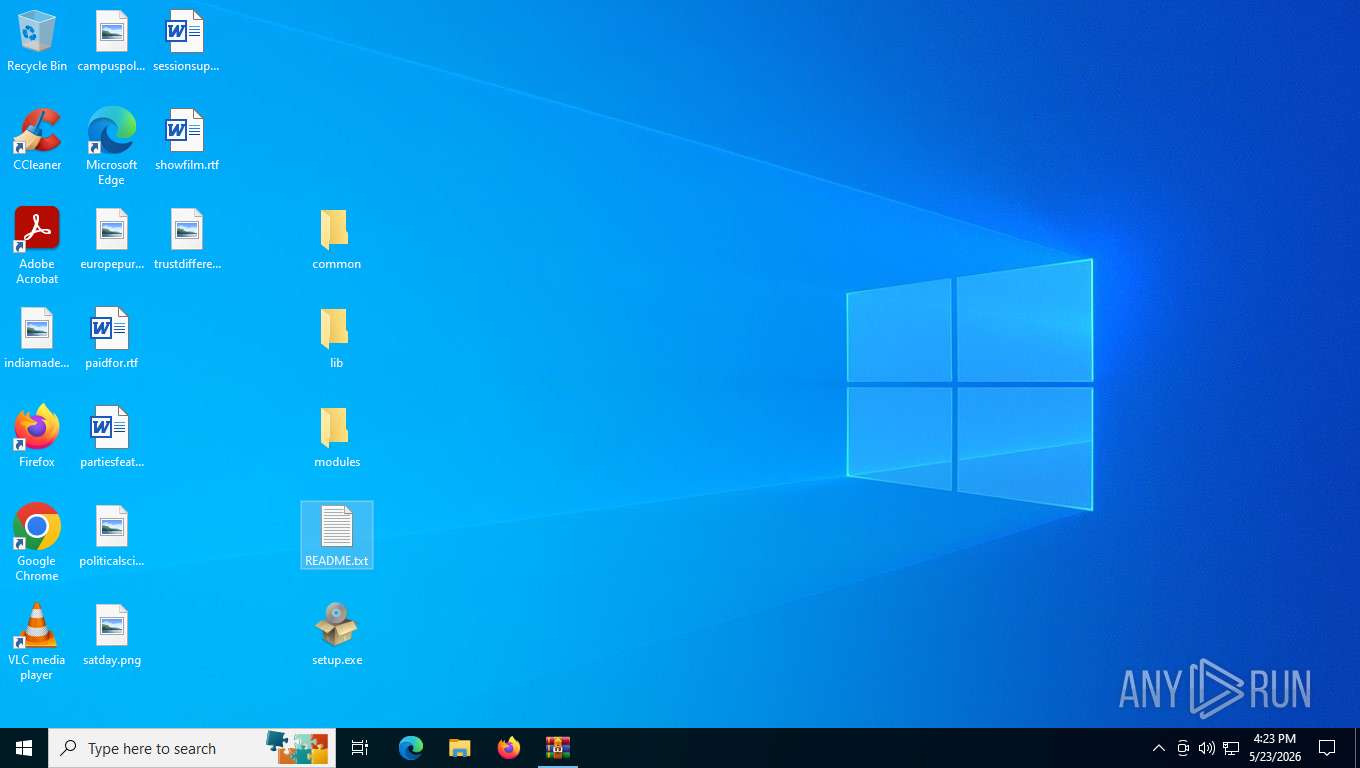
| Threats: | Remus Stealer is a sophisticated 64-bit information stealer operating under a Malware-as-a-Service (MaaS) model. Identified as a direct evolution of the infamous Lumma Stealer, Remus specializes in harvesting credentials, cookies, and cryptocurrency wallets while utilizing blockchain technology for command-and-control (C2) resilience. |
| Analysis date: | May 23, 2026, 20:20:51 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MD5: | DE3B354AC561920569F05AF7E61D5ABA |
| SHA1: | 4B94AEB2027B7622E46FE87D006845F3810694D1 |
| SHA256: | 7E68A3F1D82F67896D214CF64AC9571A8688BAE070A0BD76E5AD50965276B488 |
| SSDEEP: | 3:N8oiHumUILA34bn:2oDmUA |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 144 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=storage.mojom.StorageService --lang=en-US --service-sandbox-type=service --disable-quic --string-annotations --field-trial-handle=2444,i,2973739371747669039,9844410594859053848,262144 --variations-seed-version=20260523-030037.326000-production --mojo-platform-channel-handle=2460 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 552 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=renderer --string-annotations --enable-dinosaur-easter-egg-alt-images --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=3 --enable-main-frame-before-activation --renderer-client-id=5 --field-trial-handle=2644,i,8664953843404239709,15628853445802634750,262144 --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=3268 /prefetch:1 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 672 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=gpu-process --string-annotations --gpu-preferences=UAAAAAAAAADgAAAEAAAAAAAAAAAAAAAAAABgAAEAAAAAAAAAAAAAAAAAAAACAAAAAAAAAAAAAAAAAAAAAAAAABAAAAAAAAAAEAAAAAAAAAAIAAAAAAAAAAgAAAAAAAAA --field-trial-handle=2044,i,16308061181451850986,1769413731787346949,262144 --variations-seed-version=20260523-030037.326000-production --mojo-platform-channel-handle=2004 /prefetch:2 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 1108 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=edge_search_indexer.mojom.SearchIndexerInterfaceBroker --lang=en-US --service-sandbox-type=search_indexer --disable-quic --message-loop-type-ui --string-annotations --always-read-main-dll --field-trial-handle=4960,i,4798830907802030114,11807293852468088917,262144 --variations-seed-version --mojo-platform-channel-handle=5344 /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Version: 133.0.3065.92 Modules
| |||||||||||||||
| 1176 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=renderer --string-annotations --extension-process --enable-dinosaur-easter-egg-alt-images --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=3 --enable-main-frame-before-activation --renderer-client-id=7 --field-trial-handle=4268,i,16449764236725275607,5822374713417906428,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=4292 /prefetch:2 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 1268 | "C:\Program Files\Google\Chrome\Application\chrome.exe" | C:\Program Files\Google\Chrome\Application\chrome.exe | — | setup.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 1352 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=network.mojom.NetworkService --lang=en-US --service-sandbox-type=none --disable-quic --string-annotations --field-trial-handle=2196,i,2973739371747669039,9844410594859053848,262144 --variations-seed-version=20260523-030037.326000-production --mojo-platform-channel-handle=2188 /prefetch:3 | C:\Program Files\Google\Chrome\Application\chrome.exe | chrome.exe | ||||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 1904 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=renderer --string-annotations --instant-process --pdf-upsell-enabled --video-capture-use-gpu-memory-buffer --lang=en-US --js-flags=--ms-user-locale= --device-scale-factor=1 --num-raster-threads=3 --enable-main-frame-before-activation --renderer-client-id=5 --always-read-main-dll --field-trial-handle=3620,i,4798830907802030114,11807293852468088917,262144 --variations-seed-version --mojo-platform-channel-handle=3824 /prefetch:1 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Version: 133.0.3065.92 Modules
| |||||||||||||||
| 2000 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=quarantine.mojom.Quarantine --lang=en-US --service-sandbox-type=none --disable-quic --string-annotations --field-trial-handle=6672,i,16449764236725275607,5822374713417906428,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=6720 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 2132 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --lang=en-US --service-sandbox-type=service --disable-quic --string-annotations --always-read-main-dll --field-trial-handle=5280,i,4798830907802030114,11807293852468088917,262144 --variations-seed-version --mojo-platform-channel-handle=5660 /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Exit code: 0 Version: 133.0.3065.92 Modules
| |||||||||||||||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 4316 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Segmentation Platform\SegmentInfoDB\LOG.old~RFdfe36.TMP | — | |
MD5:— | SHA256:— | |||
| 4316 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\commerce_subscription_db\LOG.old~RFdfe36.TMP | — | |
MD5:— | SHA256:— | |||
| 4316 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Segmentation Platform\SegmentInfoDB\LOG.old | — | |
MD5:— | SHA256:— | |||
| 4316 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\commerce_subscription_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 4316 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\parcel_tracking_db\LOG.old~RFdfe46.TMP | — | |
MD5:— | SHA256:— | |||
| 4316 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Segmentation Platform\SignalDB\LOG.old~RFdfe46.TMP | — | |
MD5:— | SHA256:— | |||
| 4316 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Segmentation Platform\SignalDB\LOG.old | — | |
MD5:— | SHA256:— | |||
| 4316 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\parcel_tracking_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 4316 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\PersistentOriginTrials\LOG.old~RFdfe46.TMP | — | |
MD5:— | SHA256:— | |||
| 4316 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\PersistentOriginTrials\LOG.old | — | |
MD5:— | SHA256:— | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
4104 | chrome.exe | GET | 302 | 188.114.97.3:443 | https://gltnub.live/d/St%65el%53e%72%69e%73-%47G | US | — | — | unknown |
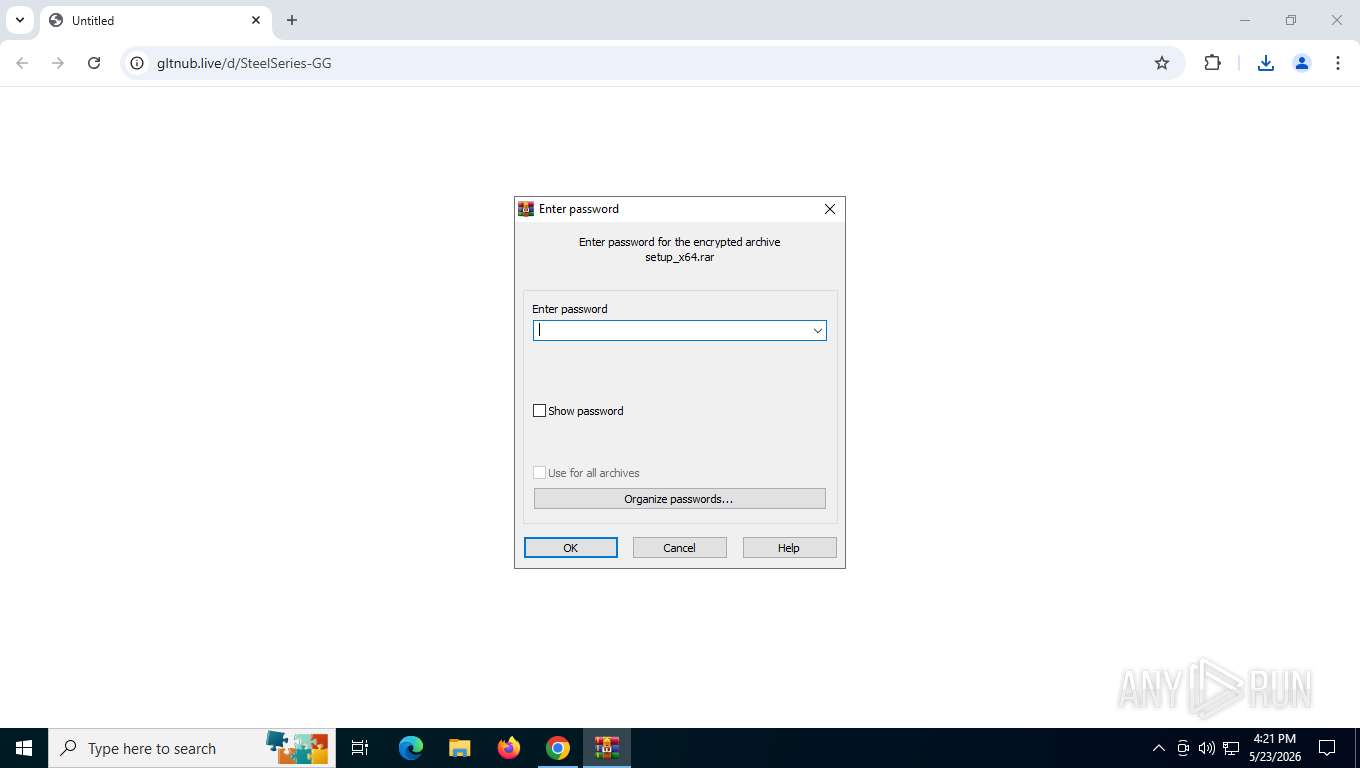
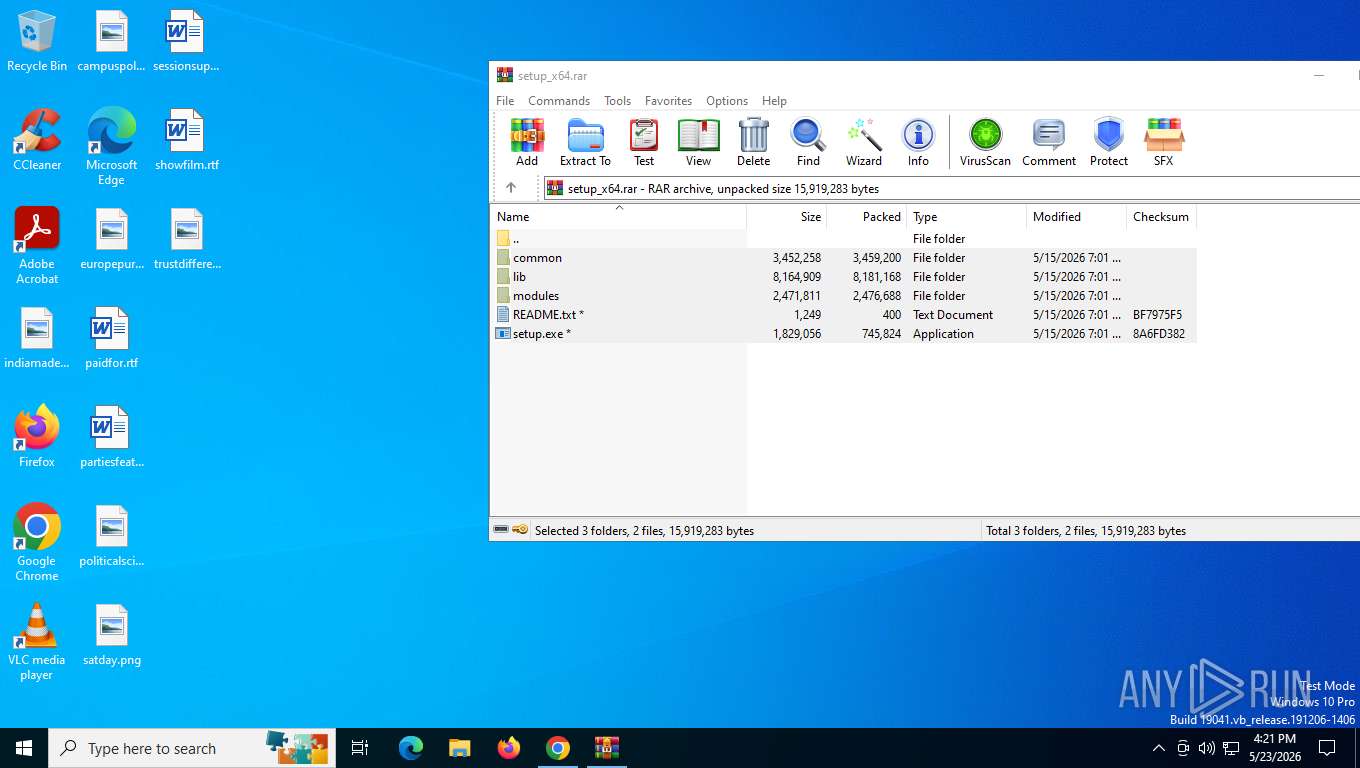
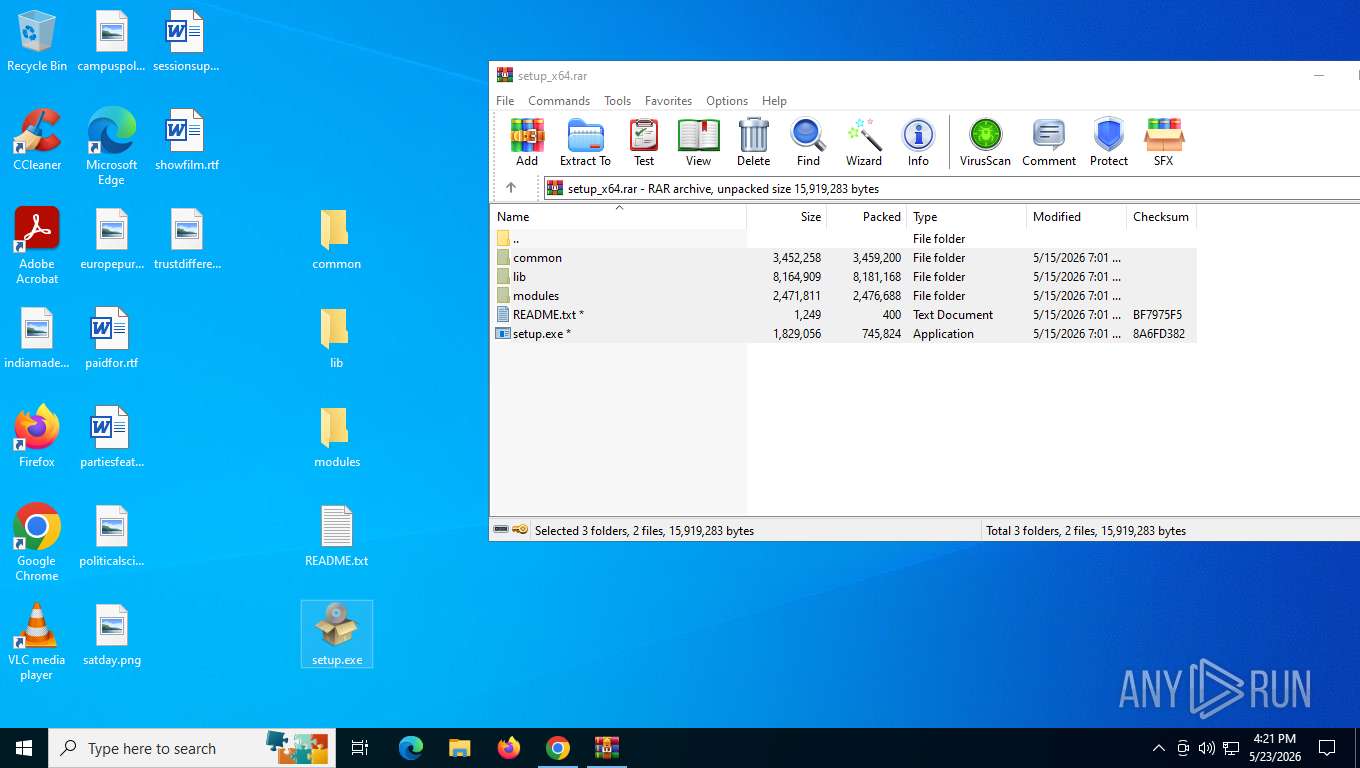
4104 | chrome.exe | GET | 302 | 140.82.121.4:443 | https://github.com/SecretChemist/duovdton/releases/download/dooown/setup_x64.rar | US | — | — | whitelisted |
— | — | GET | 200 | 204.79.197.203:80 | http://oneocsp.microsoft.com/ocsp/MFQwUjBQME4wTDAJBgUrDgMCGgUABBQ3L3%2F%2Fa6ADK8NraY2GXzVaYrHG4AQUb6t%2B2v%2BXQ3LsO2d33oJhNYhHQoUCEzMAAAAFUWohyJgUzPcAAAAAAAU%3D | US | binary | 960 b | whitelisted |
— | — | GET | 200 | 23.11.40.157:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAjTxtAB8my1oj8MfWpz%2F7Y%3D | NL | binary | 314 b | whitelisted |
4104 | chrome.exe | GET | 200 | 142.251.13.138:80 | http://clients2.google.com/time/1/current?cup2key=8:yf9Ri2dW_SisKJ0znnS98oBBhzxcBiC55duIMoOdiMk&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855 | US | text | 103 b | whitelisted |
4104 | chrome.exe | GET | 200 | 216.239.36.223:443 | https://safebrowsingohttpgateway.googleapis.com/v1/ohttp/hpkekeyconfig?key=AIzaSyA2KlwBX3mkFo30om9LUFYQhpqLoa_BNhE | US | binary | 41 b | whitelisted |
4104 | chrome.exe | GET | 200 | 142.250.154.100:443 | https://clientservices.googleapis.com/chrome-variations/seed?osname=win&channel=stable&milestone=133 | US | compressed | 94.0 Kb | whitelisted |
4104 | chrome.exe | POST | 200 | 142.251.127.84:443 | https://accounts.google.com/ListAccounts?gpsia=1&source=ChromiumBrowser&json=standard | US | text | 17 b | whitelisted |
4104 | chrome.exe | GET | 200 | 185.199.109.133:443 | https://release-assets.githubusercontent.com/github-production-release-asset/1195771016/30457f94-ff2c-4388-8162-e80cc355d142?sp=r&sv=2018-11-09&sr=b&spr=https&se=2026-05-23T20%3A59%3A39Z&rscd=attachment%3B+filename%3Dsetup_x64.rar&rsct=application%2Foctet-stream&skoid=96c2d410-5711-43a1-aedd-ab1947aa7ab0&sktid=398a6654-997b-47e9-b12b-9515b896b4de&skt=2026-05-23T19%3A59%3A35Z&ske=2026-05-23T20%3A59%3A39Z&sks=b&skv=2018-11-09&sig=rBM82Rnx3OA4jMJtFHwMmZECbyige6FEmdXRkVSwGuQ%3D&jwt=eyJ0eXAiOiJKV1QiLCJhbGciOiJIUzI1NiJ9.eyJpc3MiOiJnaXRodWIuY29tIiwiYXVkIjoicmVsZWFzZS1hc3NldHMuZ2l0aHVidXNlcmNvbnRlbnQuY29tIiwia2V5Ijoia2V5MSIsImV4cCI6MTc3OTU2OTQ1OCwibmJmIjoxNzc5NTY3NjU4LCJwYXRoIjoicmVsZWFzZWFzc2V0cHJvZHVjdGlvbi5ibG9iLmNvcmUud2luZG93cy5uZXQifQ.c7i28AvVg5OiI6su3UlJeEwwF5w0HP-sPVY1HMXaryI&response-content-disposition=attachment%3B%20filename%3Dsetup_x64.rar&response-content-type=application%2Foctet-stream | US | compressed | 5.00 Mb | whitelisted |
4104 | chrome.exe | POST | 200 | 192.178.183.138:443 | https://update.googleapis.com/service/update2/json?cup2key=14:kfnntWFIvIpShth9t2GOdkIFW5o7LaBhssr4GbBFGqA&cup2hreq=5fc43c63d4b5fc3aa942f89ba2604e2d248b4b9cae583d6c063d3966dd87437b | US | text | 289 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
5276 | MoUsoCoreWorker.exe | 48.209.138.189:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
4 | System | 192.168.100.255:137 | — | Not routed | — | whitelisted |
5392 | svchost.exe | 48.209.138.189:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
— | — | 128.24.231.64:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5532 | SearchApp.exe | 92.123.104.19:443 | www.bing.com | AKAMAI-ASN1 | NL | whitelisted |
— | — | 23.11.40.157:80 | ocsp.digicert.com | AKAMAI-AMS | NL | whitelisted |
— | — | 204.79.197.203:80 | oneocsp.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
4 | System | 192.168.100.255:138 | — | Not routed | — | whitelisted |
4104 | chrome.exe | 216.239.36.223:443 | safebrowsingohttpgateway.googleapis.com | GOOGLE | US | whitelisted |
4104 | chrome.exe | 142.251.13.138:80 | clients2.google.com | GOOGLE | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
activation-v2.sls.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
www.bing.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
oneocsp.microsoft.com |
| whitelisted |
clients2.google.com |
| whitelisted |
safebrowsingohttpgateway.googleapis.com |
| whitelisted |
gltnub.live |
| unknown |
clientservices.googleapis.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
4104 | chrome.exe | Not Suspicious Traffic | INFO [ANY.RUN] Attempting to access release user assets on GitHub |
5392 | svchost.exe | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |
6076 | setup.exe | A Network Trojan was detected | STEALER [ANY.RUN] Remus Stealer related HTTP POST request (access_token=&debug=) |
6076 | setup.exe | A Network Trojan was detected | STEALER [ANY.RUN] Remus Stealer related HTTP POST request (name= access_token) |
6076 | setup.exe | A Network Trojan was detected | STEALER [ANY.RUN] Remus Stealer related HTTP response |