ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
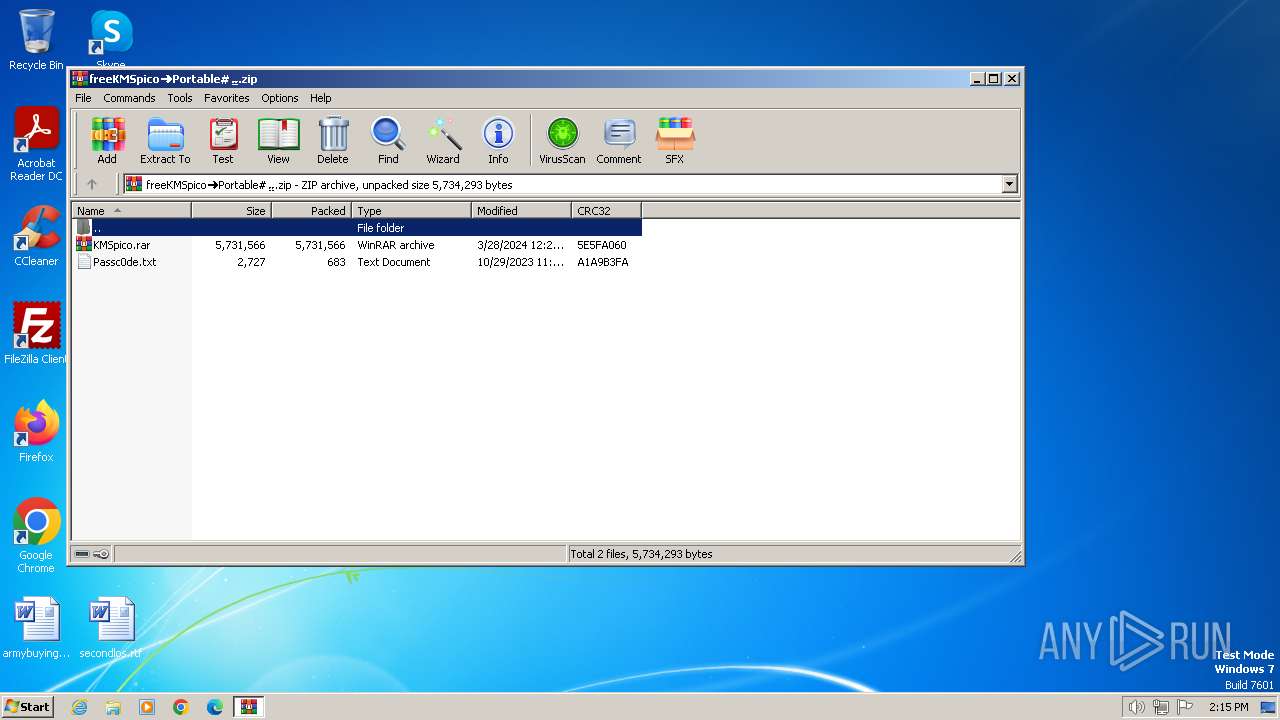
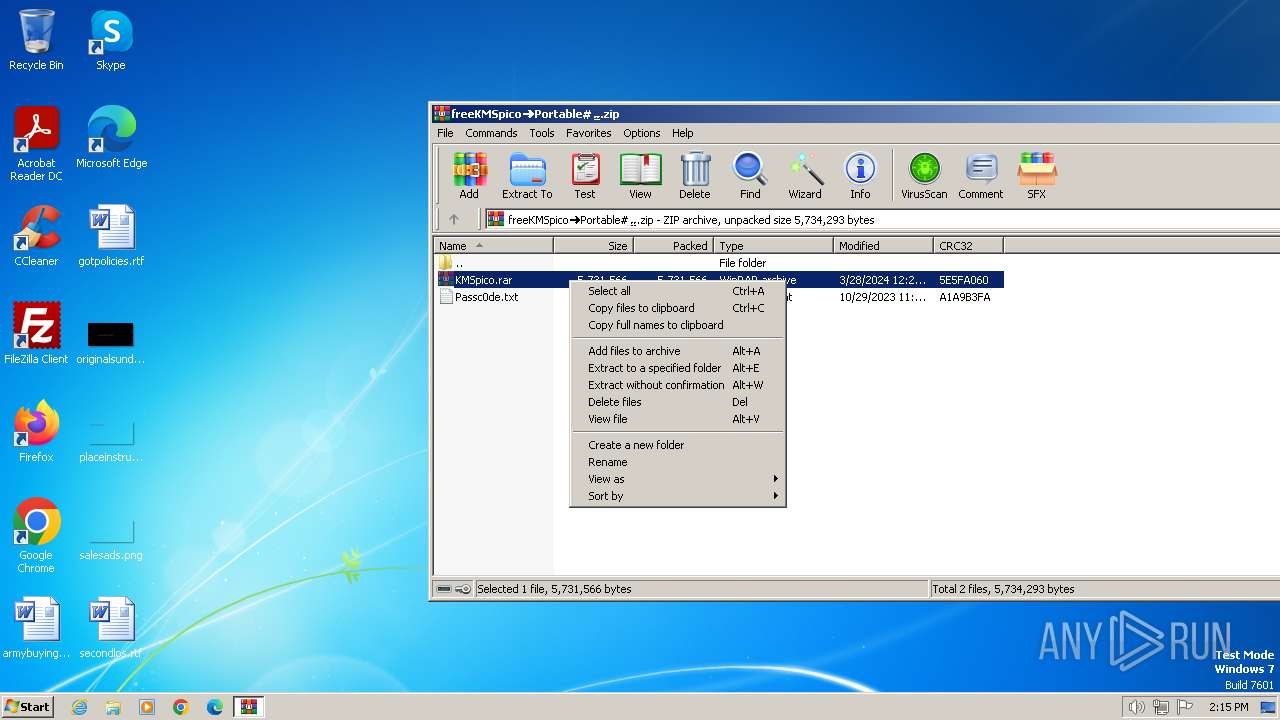
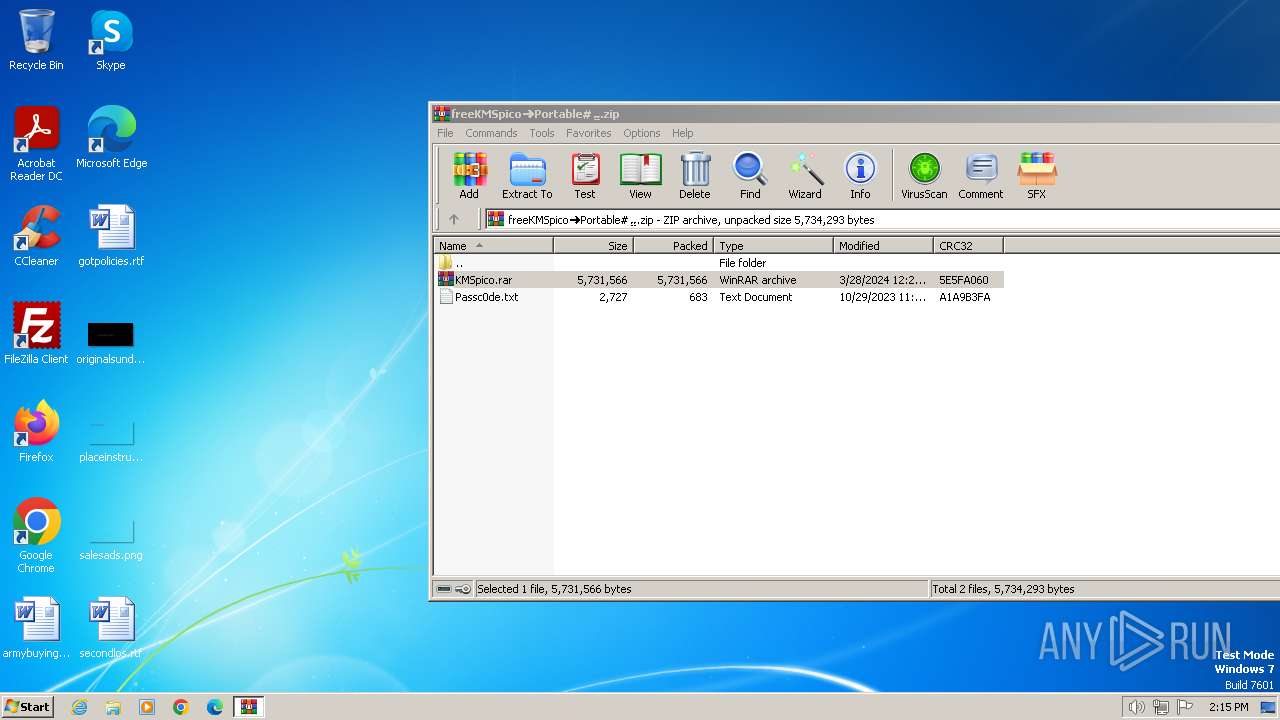
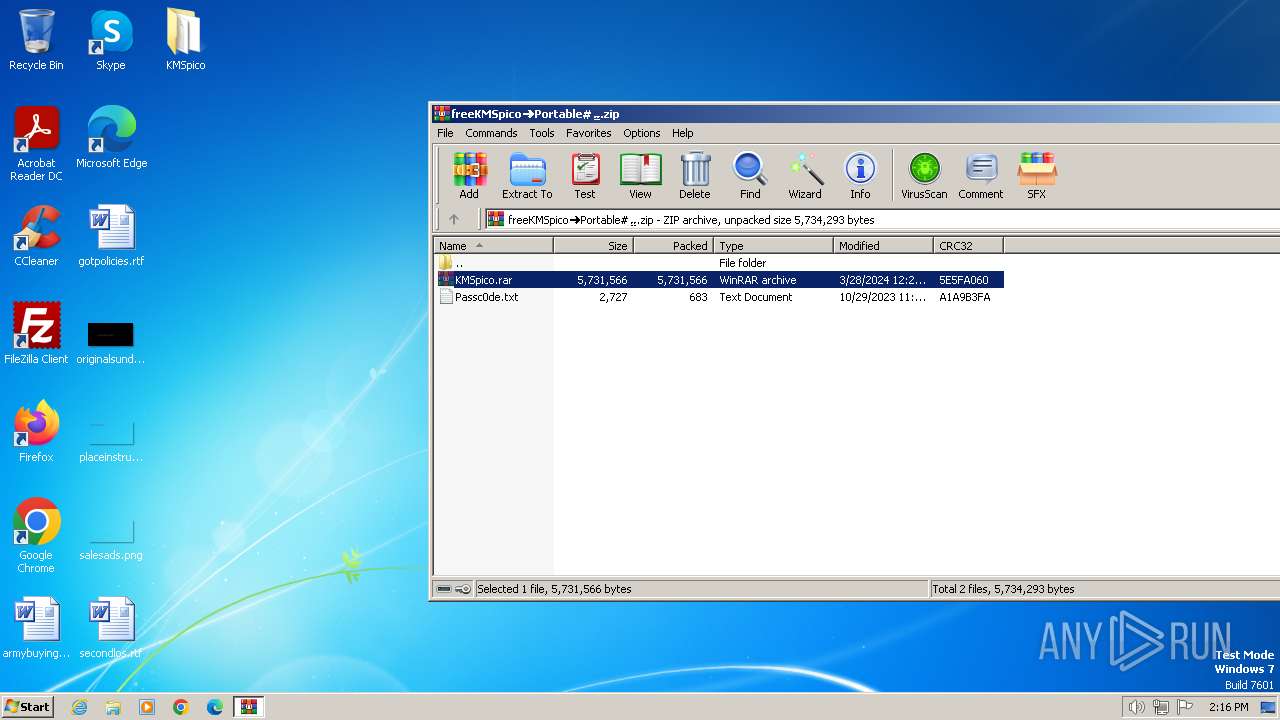
| File name: | frееКMSpico➜Portable#⣤.zip |
| Full analysis: | https://app.any.run/tasks/3808c69f-bc44-4a26-a6e1-a337929fea37 |
| Verdict: | Malicious activity |
| Analysis date: | March 28, 2024, 14:15:31 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Indicators: | |
| MIME: | application/zip |
| File info: | Zip archive data, at least v1.0 to extract, compression method=store |
| MD5: | DF1AB606A179EFE52F18FAFDBF14D787 |
| SHA1: | E2F44366906572D0C3DDC2BE56226EEA0A8E0750 |
| SHA256: | 7E4979445F16BD11D0C07B12375BD0A6958441F1772E3516BB0E3622F429842C |
| SSDEEP: | 98304:sjajAtU0/9RVoyllmRLZbgeKcJivMjVj2rBXpQspZoJqjWx4ISDM7EOFSEib+4cC:5kyYXhOwEYEon |
| .zip | | | ZIP compressed archive (100) |
|---|
| ZipRequiredVersion: | 10 |
|---|---|
| ZipBitFlag: | - |
| ZipCompression: | None |
| ZipModifyDate: | 2024:03:28 15:25:34 |
| ZipCRC: | 0x5e5fa060 |
| ZipCompressedSize: | 5731566 |
| ZipUncompressedSize: | 5731566 |
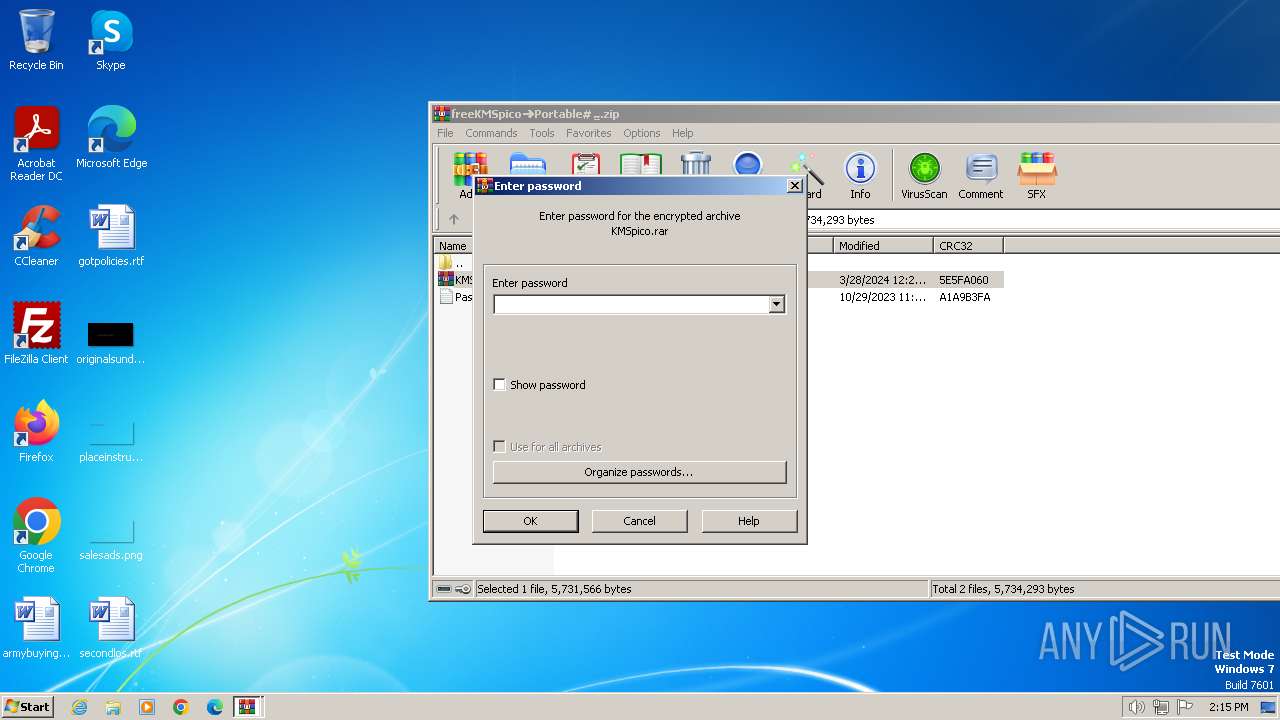
| ZipFileName: | KMSpico.rar |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1236 | "C:\Windows\system32\cmd.exe" /c schtasks /create /tn \Service\Data /tr """"C:\Users\admin\AppData\Roaming\ServiceData\Davonevur.exe""" """C:\Users\admin\AppData\Roaming\ServiceData\Davonevur.jpg"""" /st 00:01 /du 9800:59 /sc once /ri 1 /f | C:\Windows\System32\cmd.exe | — | activate.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 0 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
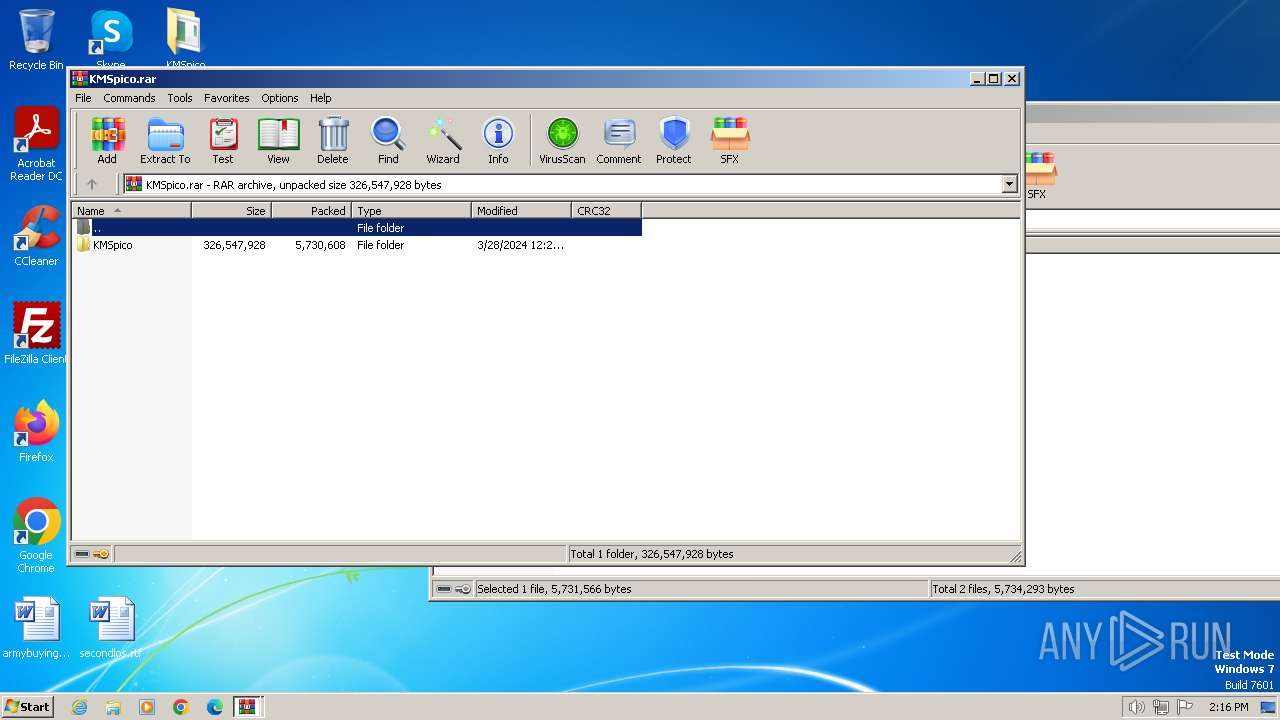
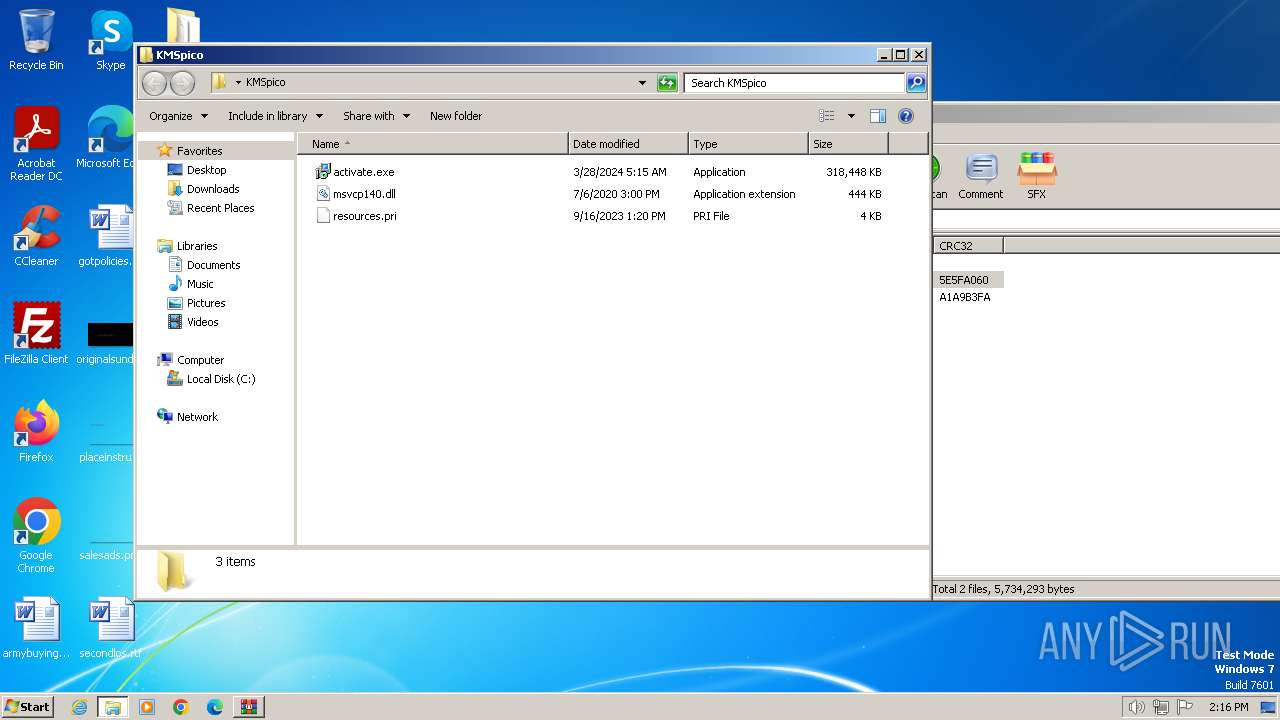
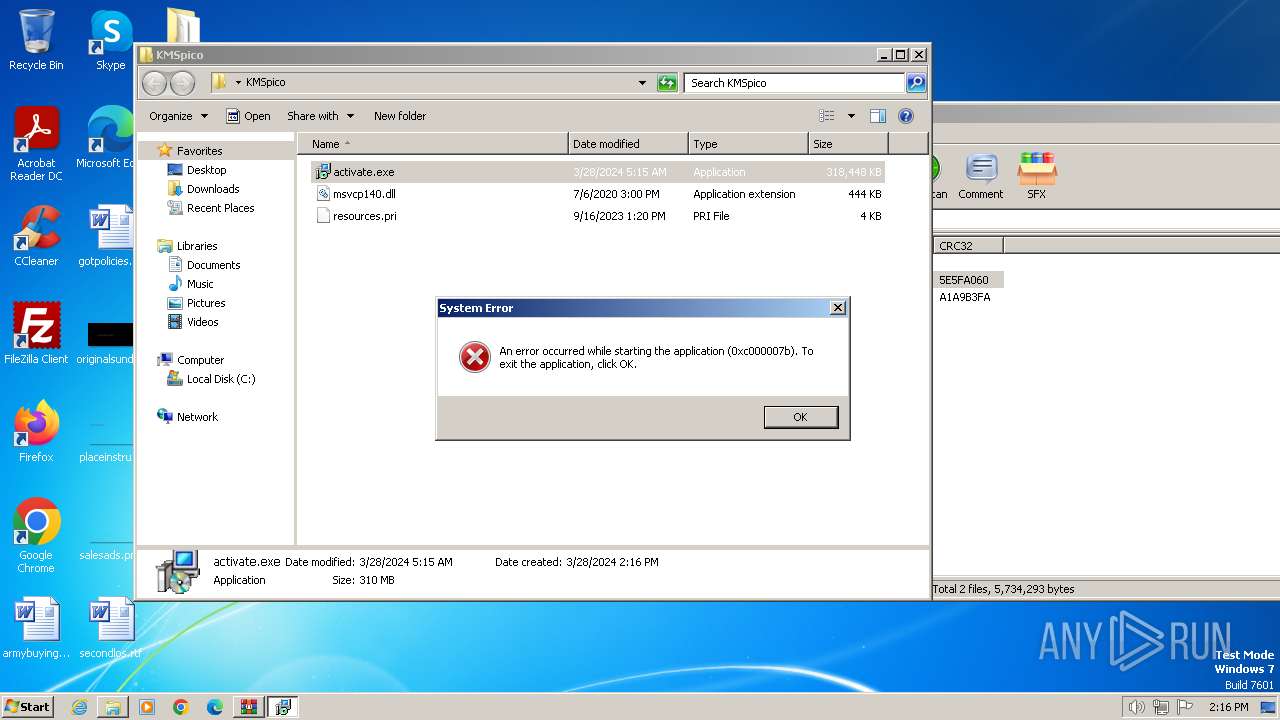
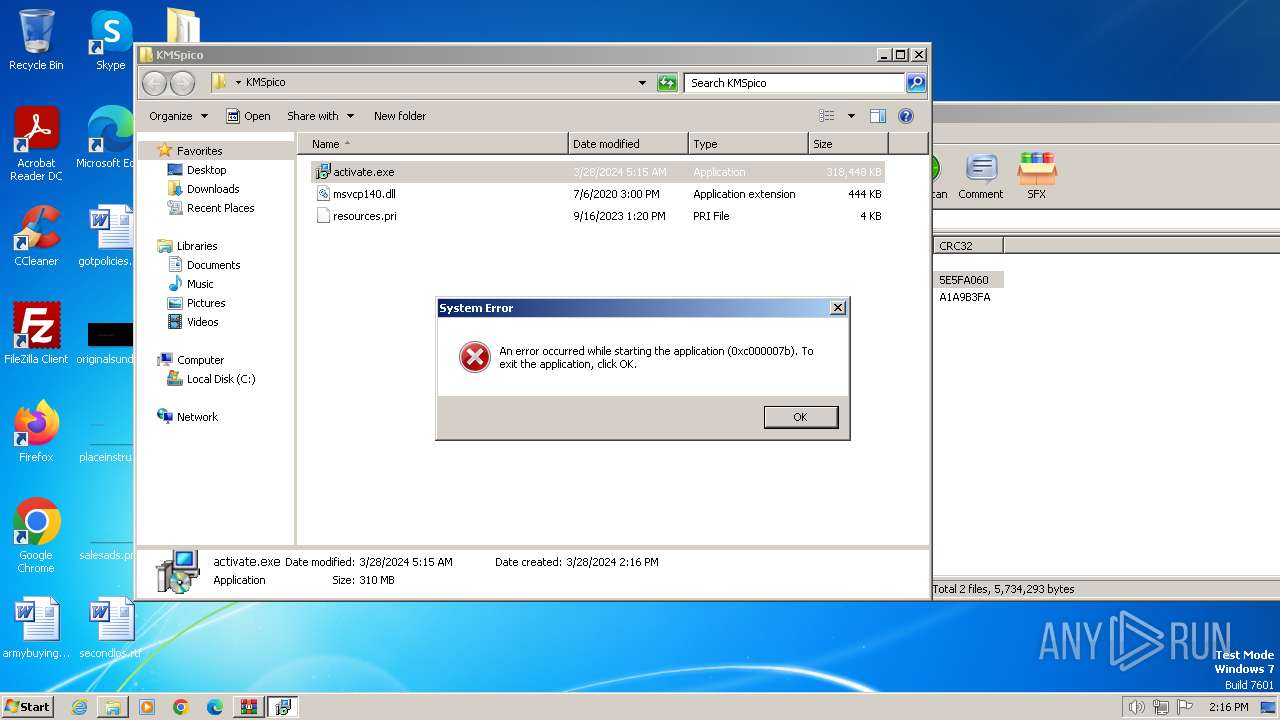
| 1340 | "C:\Users\admin\Desktop\KMSpico\activate.exe" | C:\Users\admin\Desktop\KMSpico\activate.exe | — | explorer.exe | |||||||||||
User: admin Integrity Level: MEDIUM Modules
| |||||||||||||||
| 1824 | "C:\Program Files\Windows Media Player\wmpnscfg.exe" | C:\Program Files\Windows Media Player\wmpnscfg.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Media Player Network Sharing Service Configuration Application Exit code: 0 Version: 12.0.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2060 | schtasks /create /tn \Service\Data /tr """"C:\Users\admin\AppData\Roaming\ServiceData\Davonevur.exe""" """C:\Users\admin\AppData\Roaming\ServiceData\Davonevur.jpg"""" /st 00:01 /du 9800:59 /sc once /ri 1 /f | C:\Windows\System32\schtasks.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Manages scheduled tasks Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
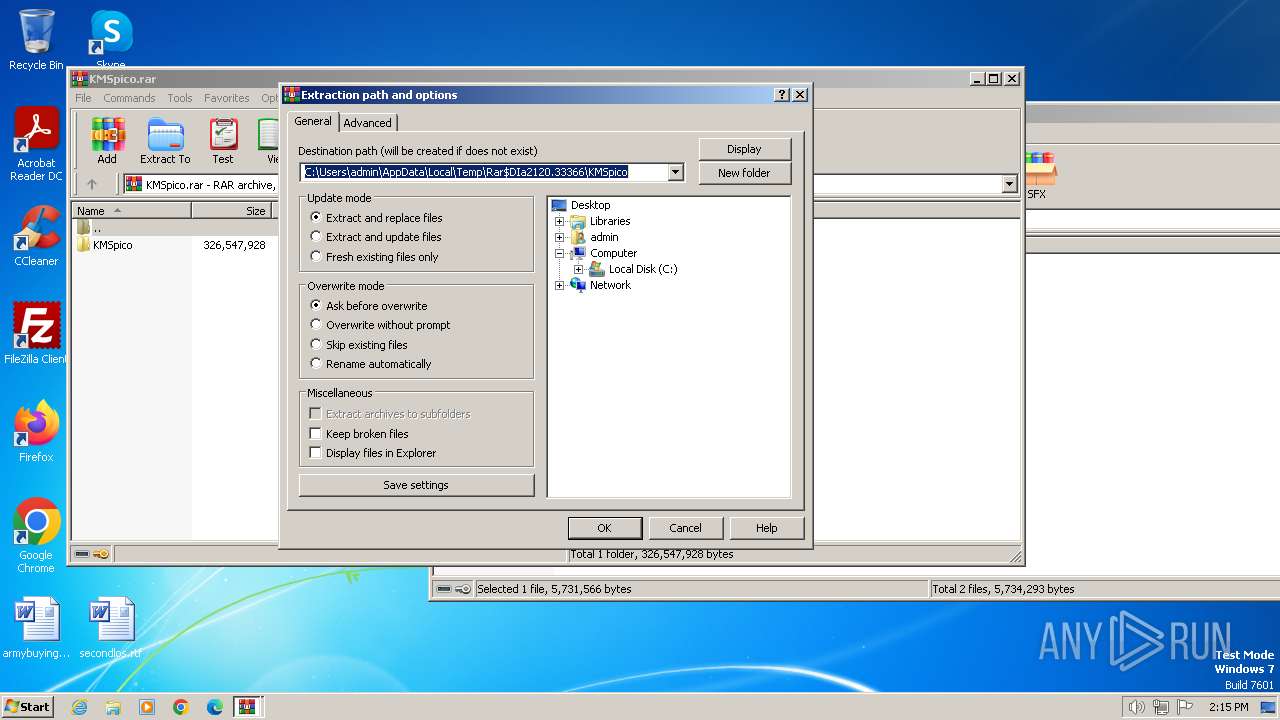
| 2120 | "C:\Program Files\WinRAR\WinRAR.exe" "C:\Users\admin\AppData\Local\Temp\frееКMSpico➜Portable#⣤.zip" | C:\Program Files\WinRAR\WinRAR.exe | — | explorer.exe | |||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Version: 5.91.0 Modules
| |||||||||||||||
| 2148 | "C:\Users\admin\Desktop\KMSpico\activate.exe" | C:\Users\admin\Desktop\KMSpico\activate.exe | — | explorer.exe | |||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
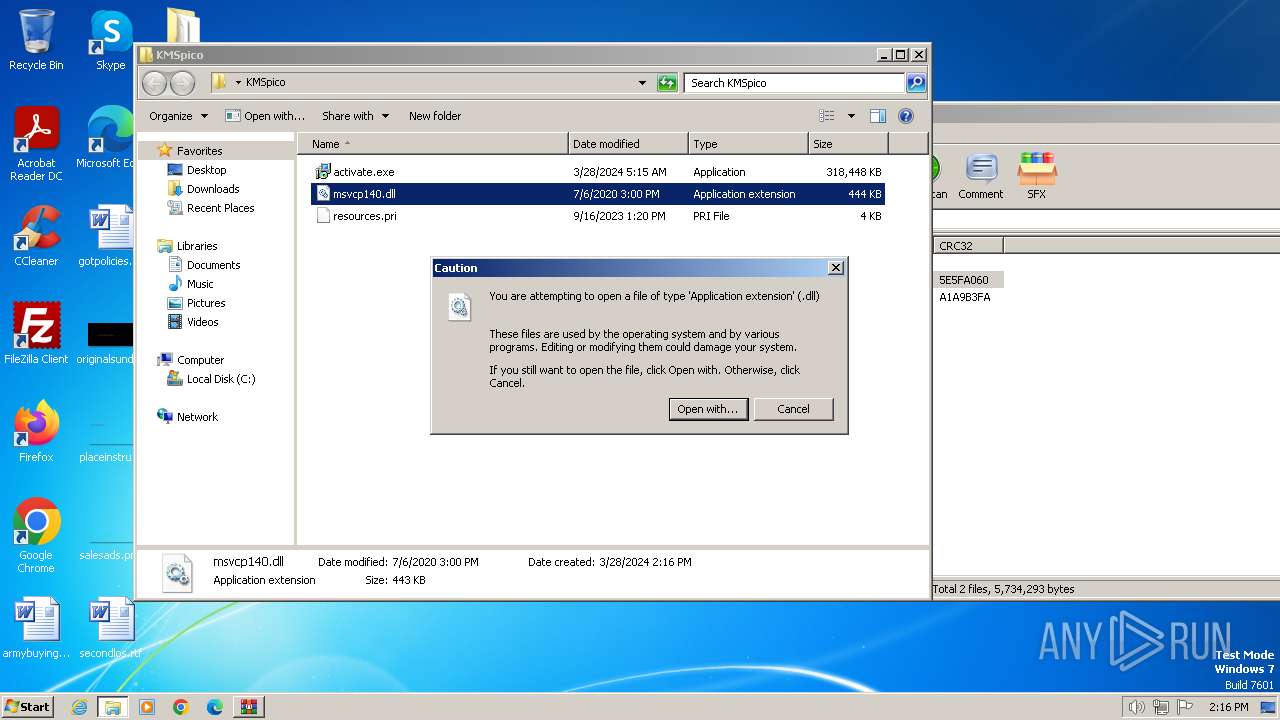
| 2152 | "C:\Windows\system32\rundll32.exe" C:\Windows\system32\shell32.dll,OpenAs_RunDLL C:\Users\admin\Desktop\KMSpico\msvcp140.dll | C:\Windows\System32\rundll32.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2432 | expand.exe "C:\Users\admin\AppData\Roaming\ServiceData\c2Gt4H.tmp" -F:* "C:\Users\admin\AppData\Roaming\ServiceData" | C:\Windows\System32\expand.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: LZ Expansion Utility Exit code: 0 Version: 6.1.7601.24535 (win7sp1_ldr_escrow.191105-1059) Modules
| |||||||||||||||
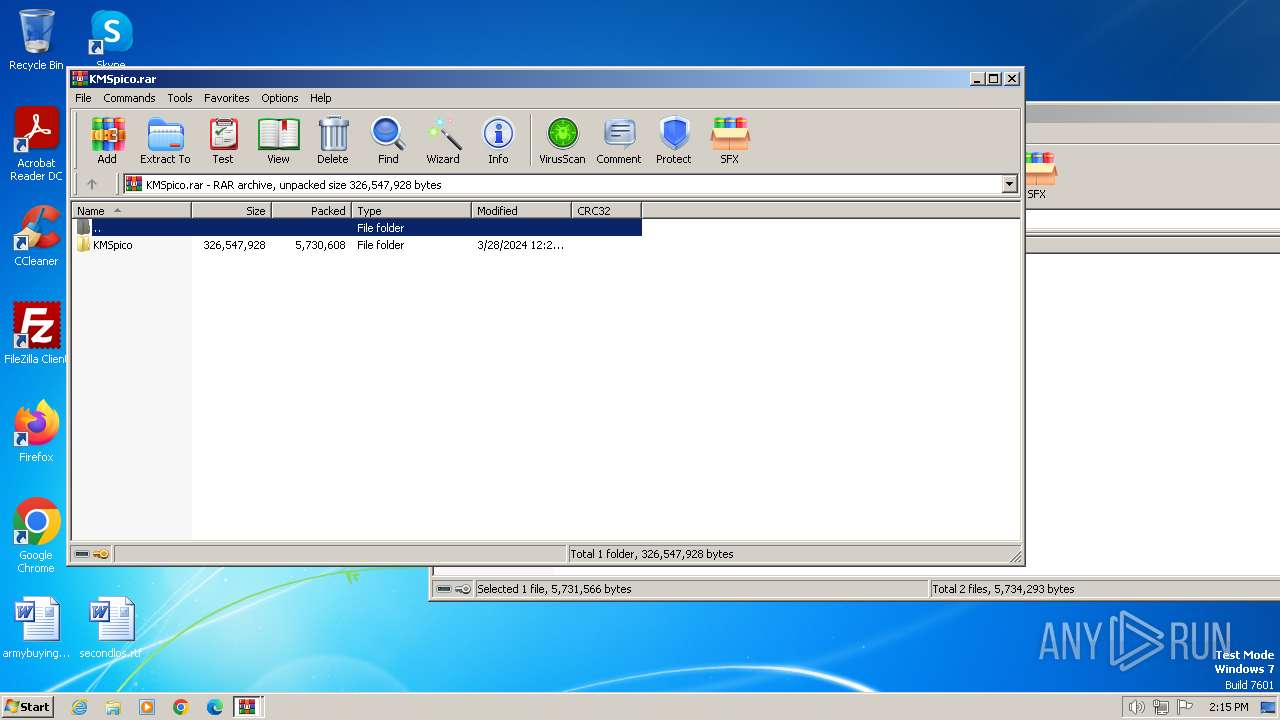
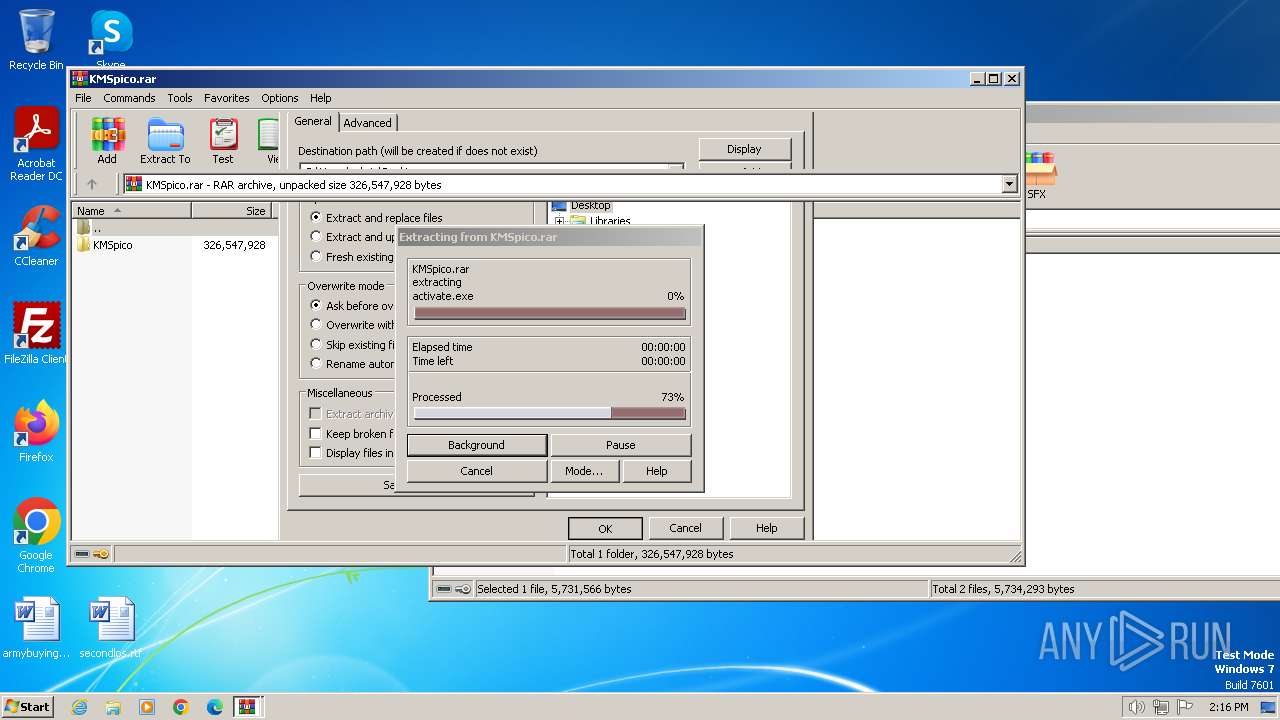
| 2648 | "C:\Program Files\WinRAR\WinRAR.exe" C:\Users\admin\AppData\Local\Temp\Rar$DIa2120.33366\KMSpico.rar | C:\Program Files\WinRAR\WinRAR.exe | — | WinRAR.exe | |||||||||||
User: admin Company: Alexander Roshal Integrity Level: MEDIUM Description: WinRAR archiver Exit code: 0 Version: 5.91.0 Modules
| |||||||||||||||
| 3180 | "C:\Users\admin\Desktop\KMSpico\activate.exe" | C:\Users\admin\Desktop\KMSpico\activate.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| (PID) Process: | (2120) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtBMP |
Value: | |||
| (PID) Process: | (2120) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtIcon |
Value: | |||
| (PID) Process: | (2120) WinRAR.exe | Key: | HKEY_CLASSES_ROOT\Local Settings\MuiCache\182\52C64B7E |
| Operation: | write | Name: | LanguageList |
Value: en-US | |||
| (PID) Process: | (2120) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 3 |
Value: C:\Users\admin\Desktop\phacker.zip | |||
| (PID) Process: | (2120) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 2 |
Value: C:\Users\admin\Desktop\Win7-KB3191566-x86.zip | |||
| (PID) Process: | (2120) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 1 |
Value: C:\Users\admin\Desktop\curl-8.5.0_1-win32-mingw.zip | |||
| (PID) Process: | (2120) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\ArcHistory |
| Operation: | write | Name: | 0 |
Value: C:\Users\admin\AppData\Local\Temp\frееКMSpico➜Portable#⣤.zip | |||
| (PID) Process: | (2120) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | name |
Value: 120 | |||
| (PID) Process: | (2120) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | size |
Value: 80 | |||
| (PID) Process: | (2120) WinRAR.exe | Key: | HKEY_CURRENT_USER\Software\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | type |
Value: 120 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2120 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DIa2120.33366\KMSpico.rar | — | |
MD5:— | SHA256:— | |||
| 2648 | WinRAR.exe | C:\Users\admin\Desktop\KMSpico\msvcp140.dll | executable | |
MD5:ECEFF9C92E14B580EA84365F3D60F7DE | SHA256:265591A709A5DB413D73C95B538DA321EDEACB40059BDCEB142F997A3D458B49 | |||
| 2648 | WinRAR.exe | C:\Users\admin\Desktop\KMSpico\resources.pri | binary | |
MD5:71AE70C6622CF8D689F029BE89FE887B | SHA256:99E80BF52DDA6DD81688E1578FF2ECC42EFA162C6CA9EDDD7F21FFCD6688D379 | |||
| 3180 | activate.exe | C:\Users\admin\AppData\Roaming\ServiceData\c2Gt4H.tmp | compressed | |
MD5:9533BA8D9930F60F0B6257BDB79B2384 | SHA256:6A30579A54855FF5899CD73278D61E6B3D69ABADC7FFEDC6C0E0C3AA03594131 | |||
| 2432 | expand.exe | C:\Users\admin\AppData\Roaming\ServiceData\Davonevur.jpg | — | |
MD5:B36280AB2514B1772D2058FE14633850 | SHA256:A3B628BE13EF3A1F09AB8E4AF4F59203E7E721283BD9414F2A35C03ABD0ECF46 | |||
| 2432 | expand.exe | C:\Users\admin\AppData\Roaming\ServiceData\Davonevur.exe | executable | |
MD5:0ADB9B817F1DF7807576C2D7068DD931 | SHA256:98E4F904F7DE1644E519D09371B8AFCBBF40FF3BD56D76CE4DF48479A4AB884B | |||
| 2432 | expand.exe | C:\Windows\Logs\DPX\setupact.log | text | |
MD5:CAE4934F83F89DED488F9D78E641583E | SHA256:FBCC018056B0152D307F6418C960D67874D35C7C4D76BB733C785512DB8D7D05 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
3180 | activate.exe | POST | 200 | 45.91.8.229:80 | http://bmseven7ht.top/upload.php | RU | text | 2 b | unknown |
3180 | activate.exe | POST | 200 | 45.91.8.229:80 | http://bmseven7ht.top/upload.php | RU | text | 2 b | unknown |
3180 | activate.exe | POST | 200 | 45.91.8.229:80 | http://bmseven7ht.top/upload.php | RU | text | 2 b | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 224.0.0.252:5355 | — | — | — | unknown |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
1080 | svchost.exe | 224.0.0.252:5355 | — | — | — | unknown |
3180 | activate.exe | 45.91.8.229:80 | bmseven7ht.top | Sprinthost.ru LLC | RU | unknown |
Domain | IP | Reputation |
|---|---|---|
bmseven7ht.top |
| unknown |
PID | Process | Class | Message |
|---|---|---|---|
1080 | svchost.exe | Potentially Bad Traffic | ET DNS Query to a *.top domain - Likely Hostile |
— | — | Potentially Bad Traffic | ET INFO HTTP Request to a *.top domain |