ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
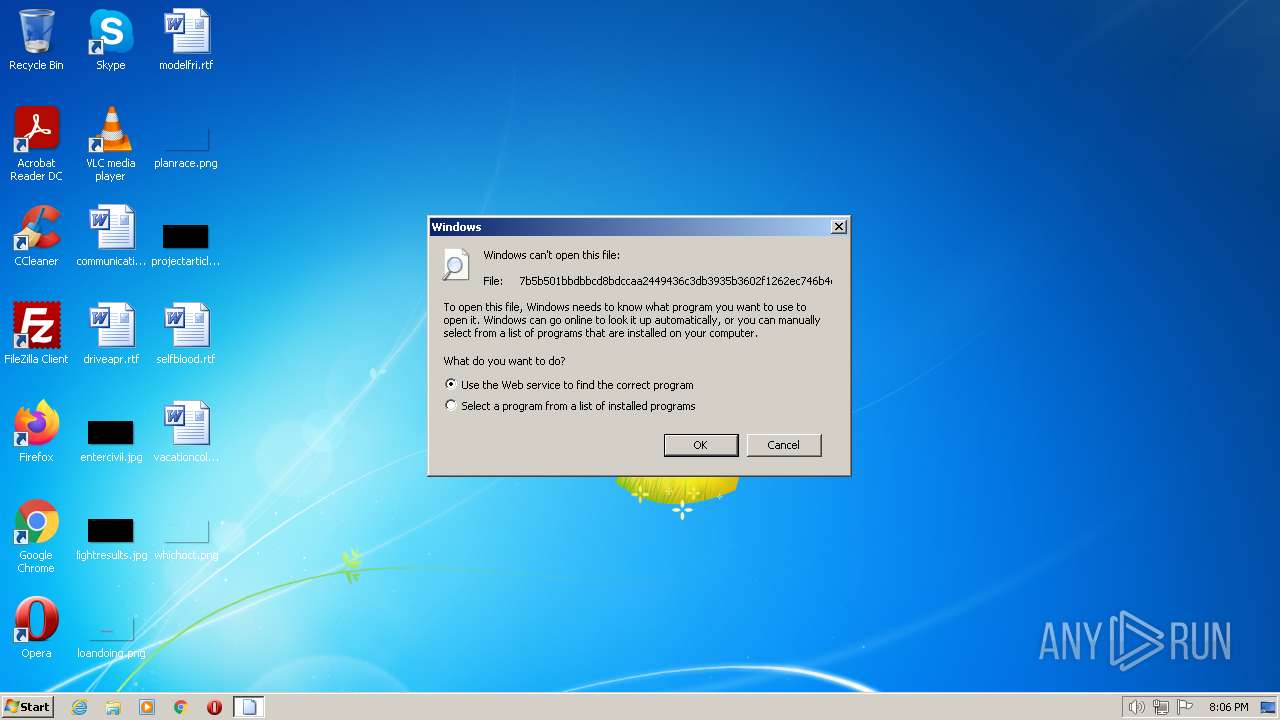
| File name: | 7b5b501bbdbbcd8bdccaa2449436c3db3935b3602f1262ec746b4daff2108fcb.unknown.html |
| Full analysis: | https://app.any.run/tasks/d108de93-3a5f-424b-b6ca-109b8f4cff04 |
| Verdict: | No threats detected |
| Analysis date: | February 20, 2023, 20:05:59 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| MIME: | application/octet-stream |
| File info: | data |
| MD5: | 93A8E36CD5A3F6C452D8BA3D401706BC |
| SHA1: | E0AFAC59459A4AF75957A240FE348CE9159F0C63 |
| SHA256: | 7B5B501BBDBBCD8BDCCAA2449436C3DB3935B3602F1262EC746B4DAFF2108FCB |
| SSDEEP: | 3072:72BT8YCHHmxyRs2HJhaTqvPT7PJgGj+YigDZy4RUWfqv4:i18XnmxVIaTI7PJHj+SaW1 |
| .a3x | | | AutoIt v3 compiled script (100) |
|---|
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 836 | "C:\Windows\system32\rundll32.exe" C:\Windows\system32\shell32.dll,OpenAs_RunDLL "C:\Users\admin\AppData\Local\Temp\7b5b501bbdbbcd8bdccaa2449436c3db3935b3602f1262ec746b4daff2108fcb.unknown.html.a3x" | C:\Windows\system32\rundll32.exe | — | Explorer.EXE | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||