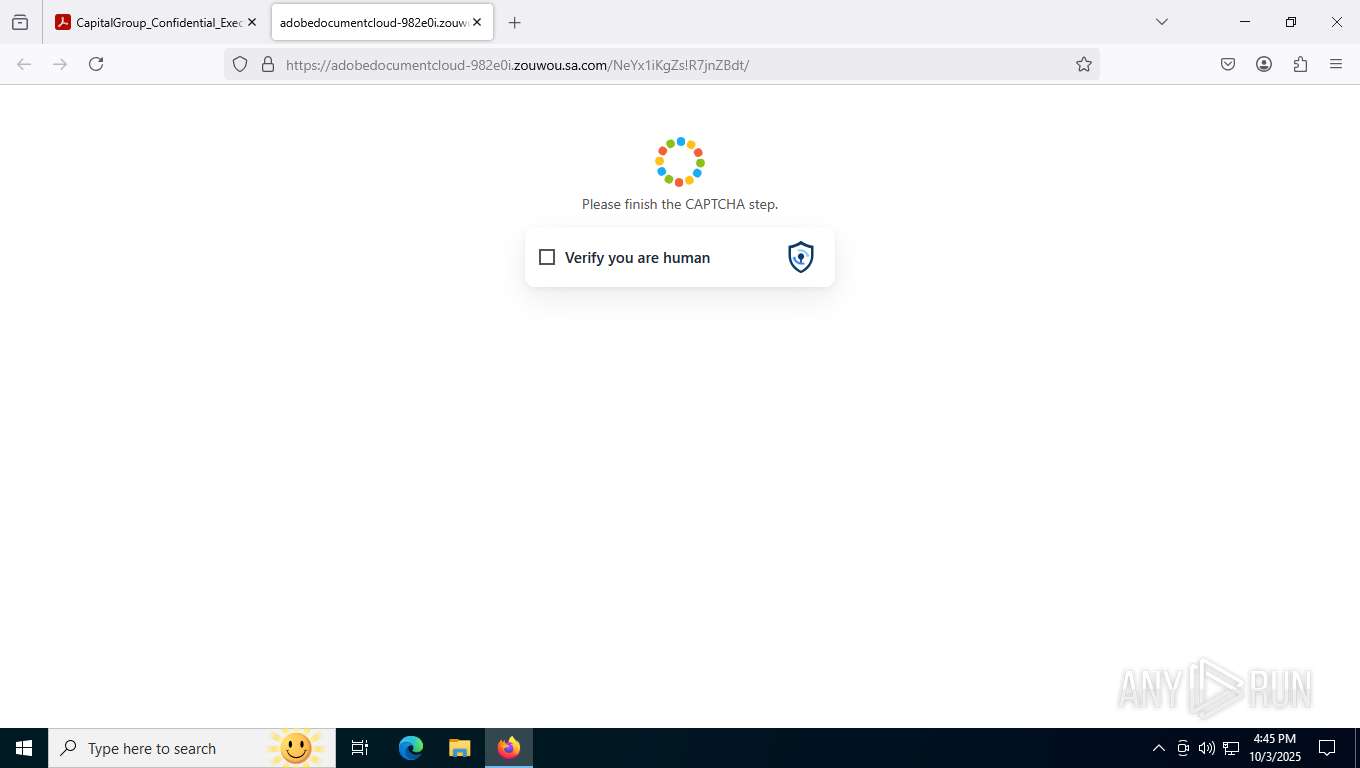
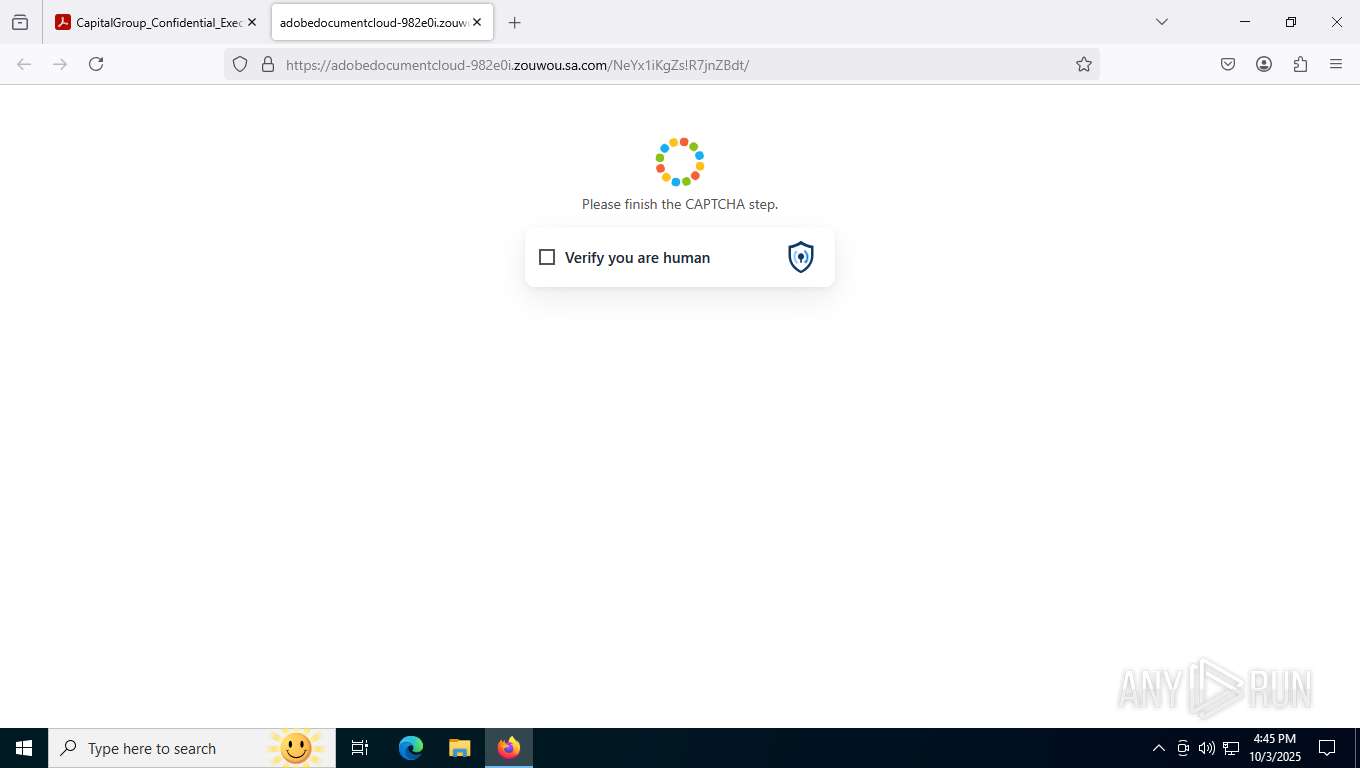
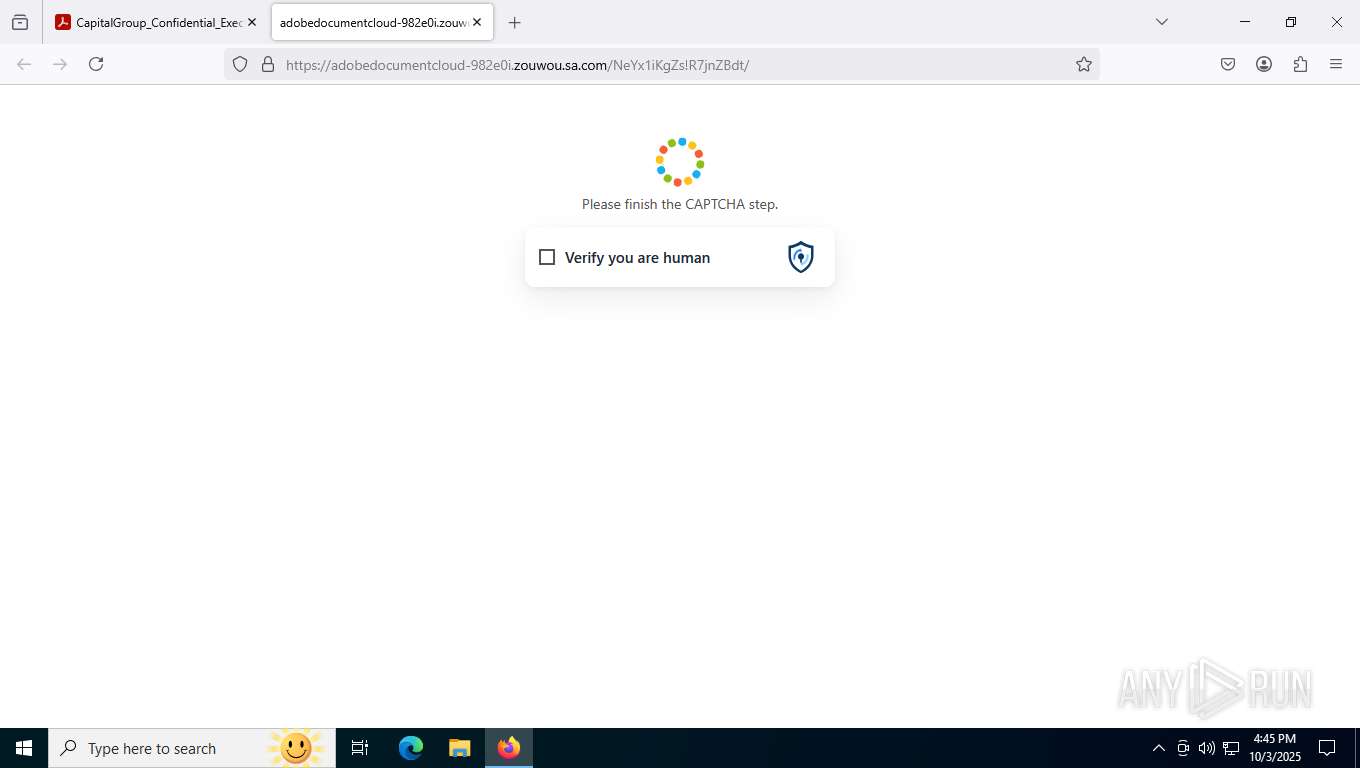
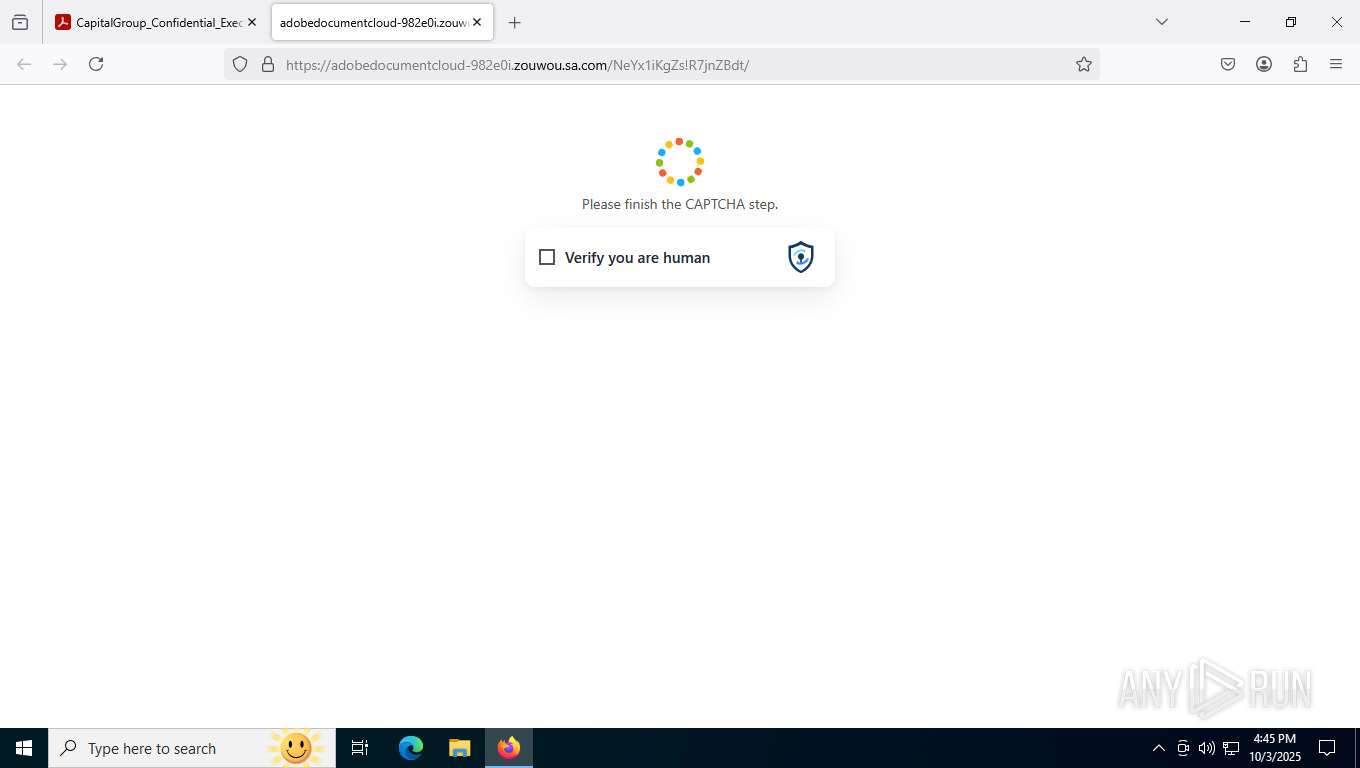
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
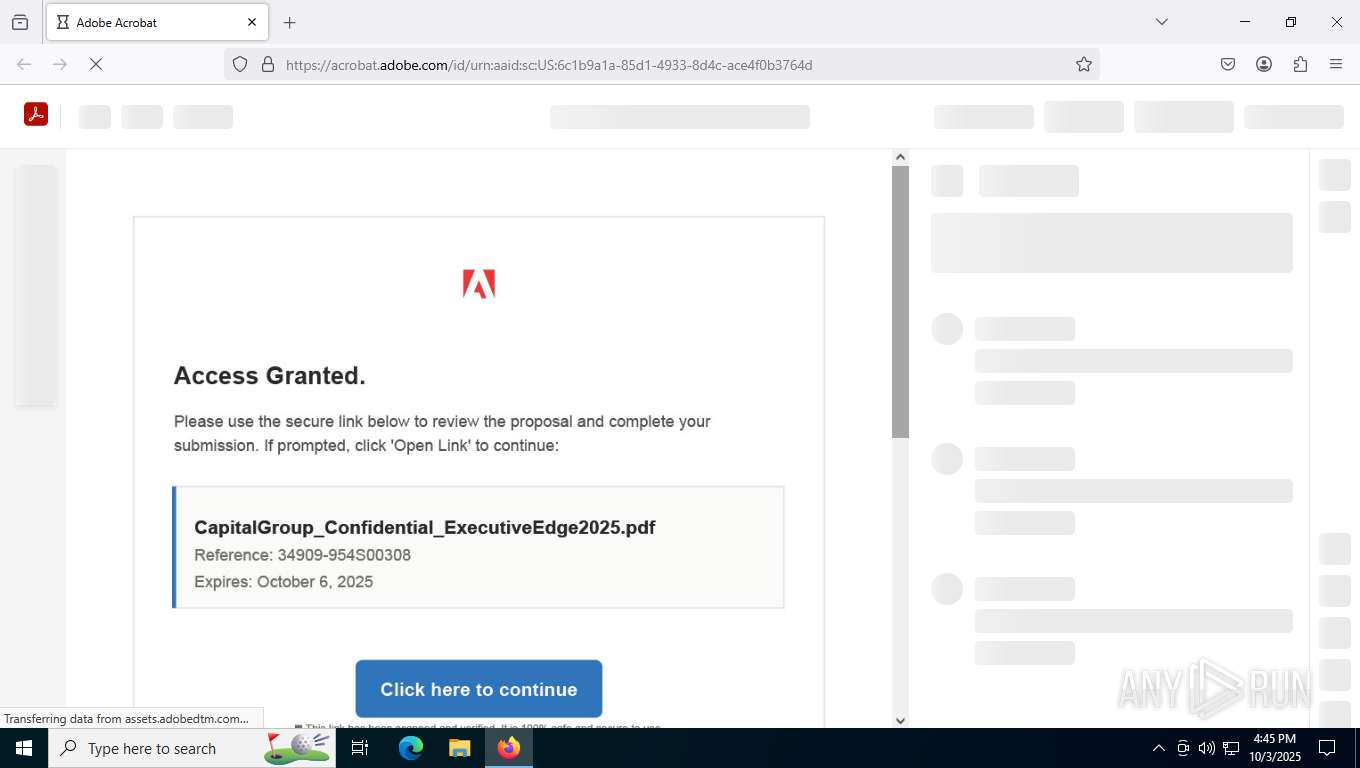
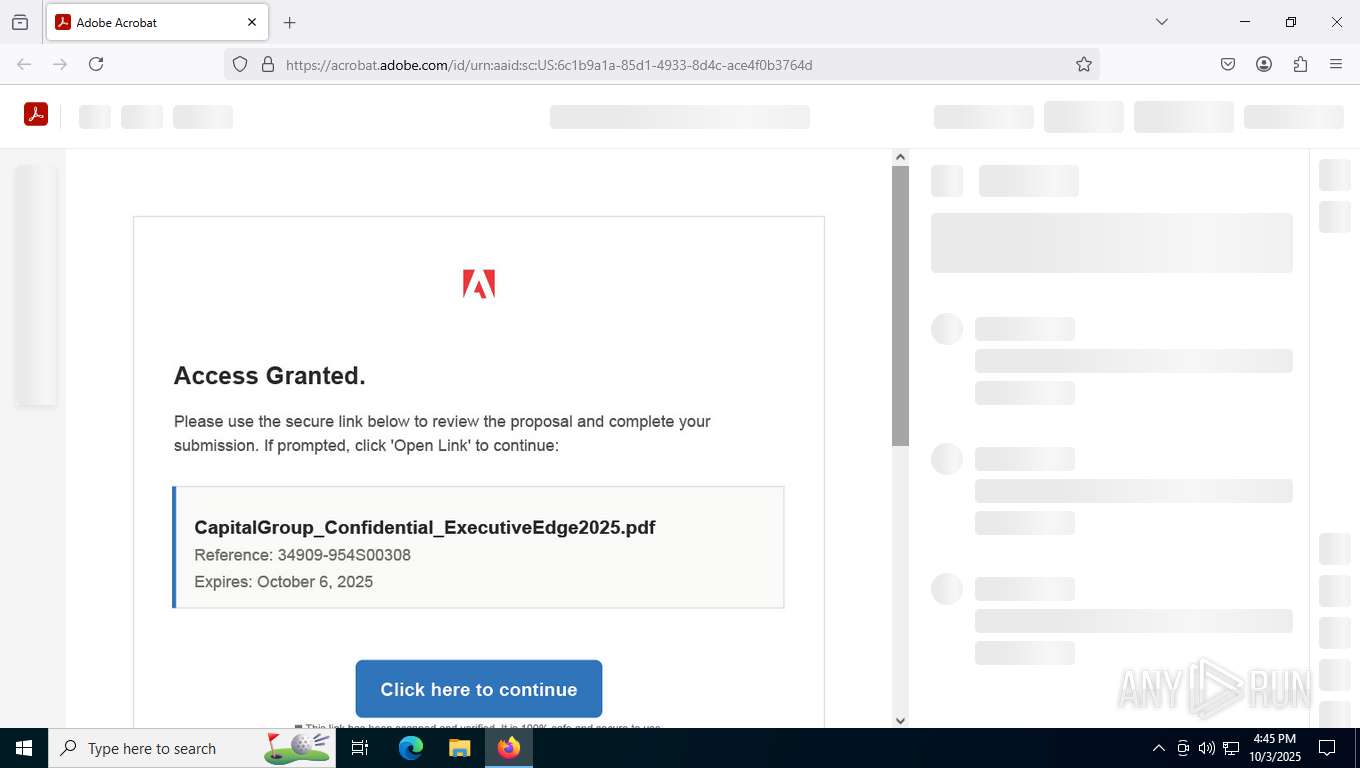
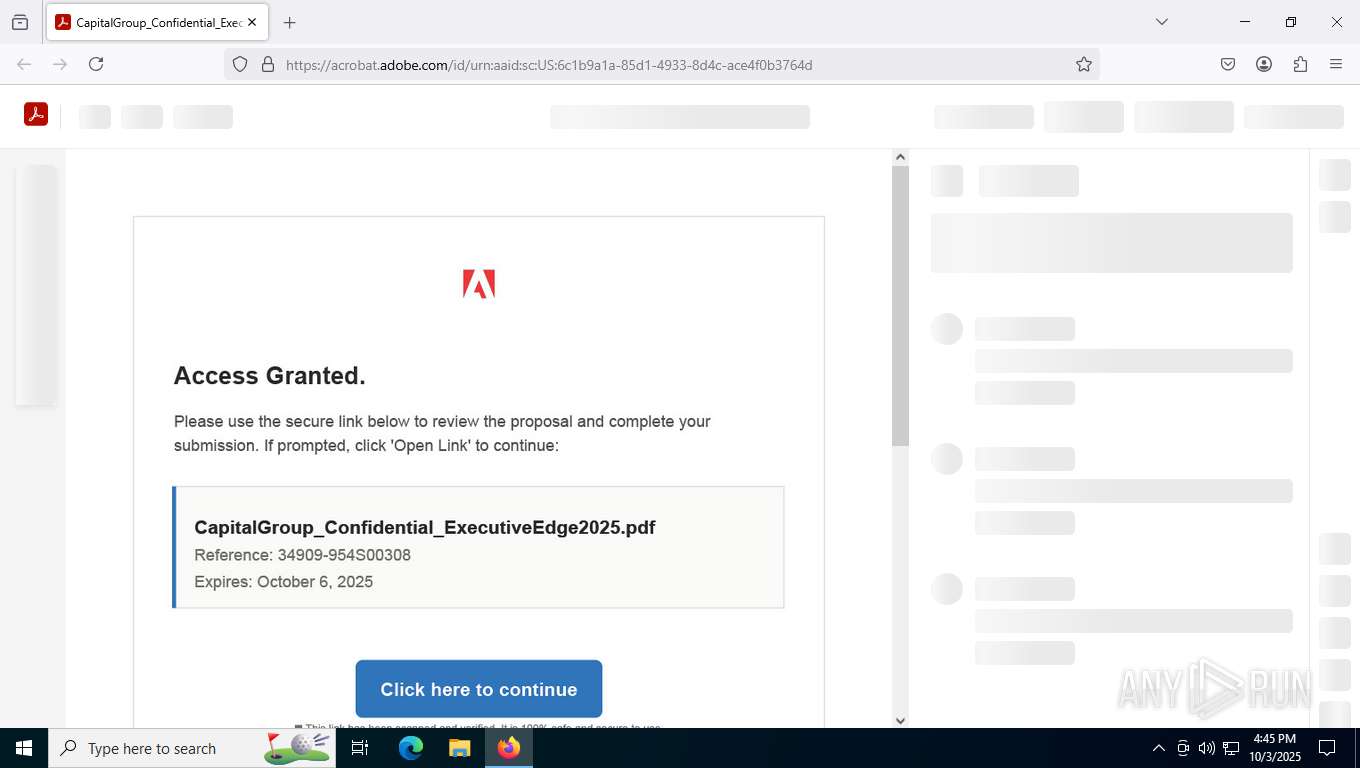
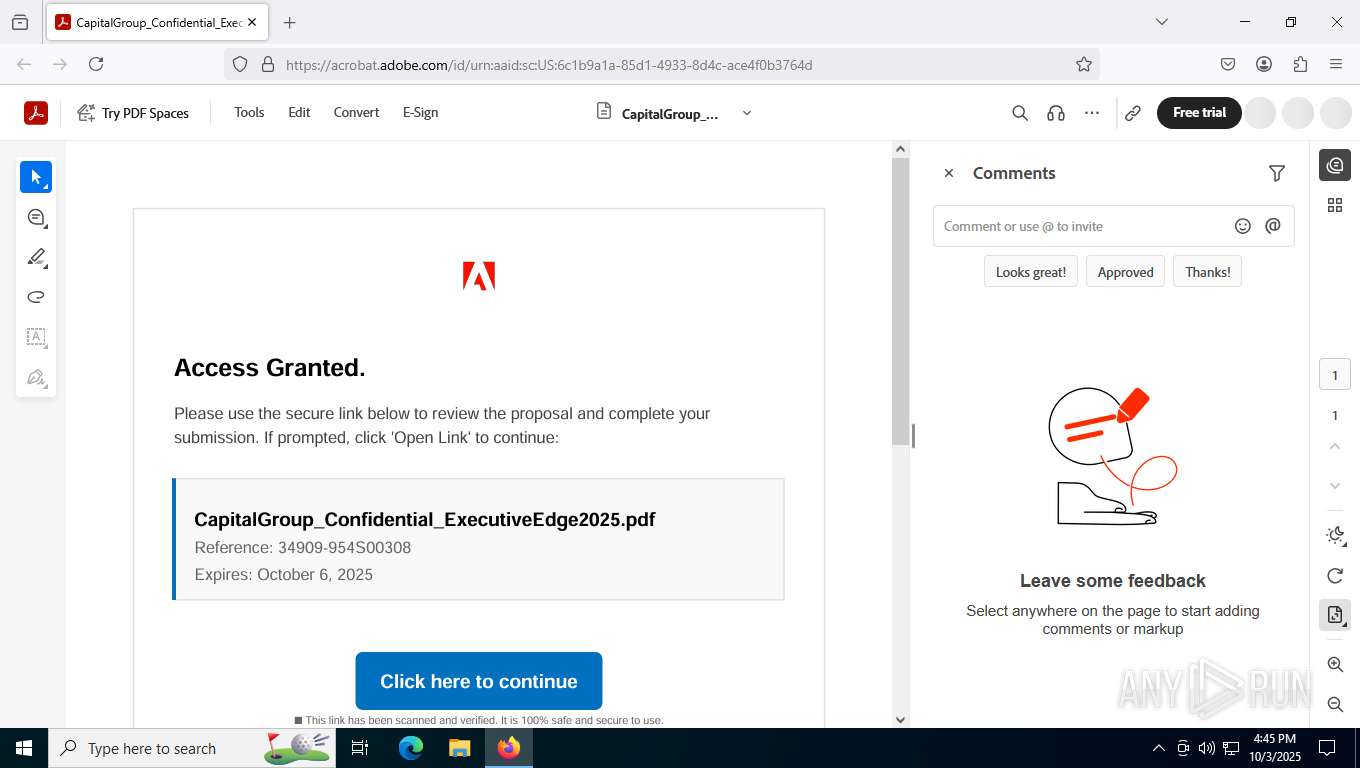
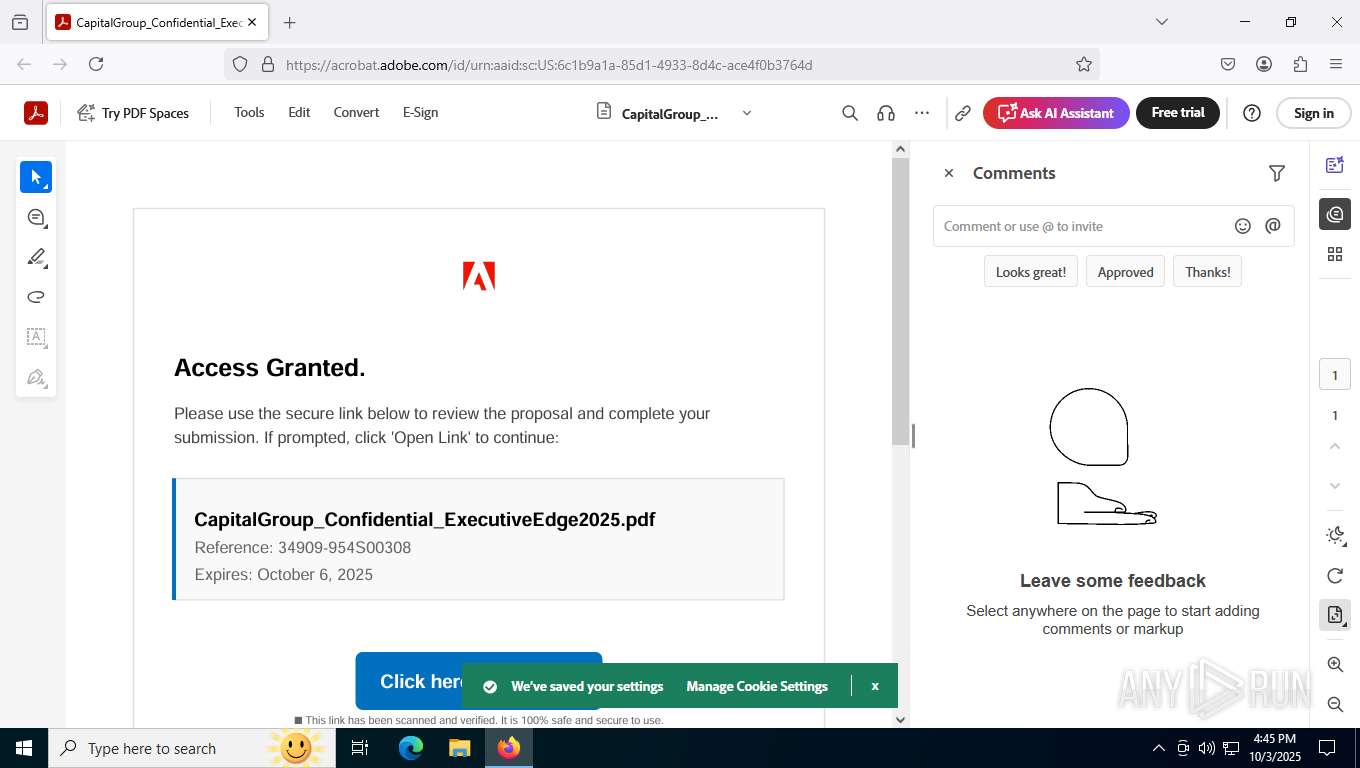
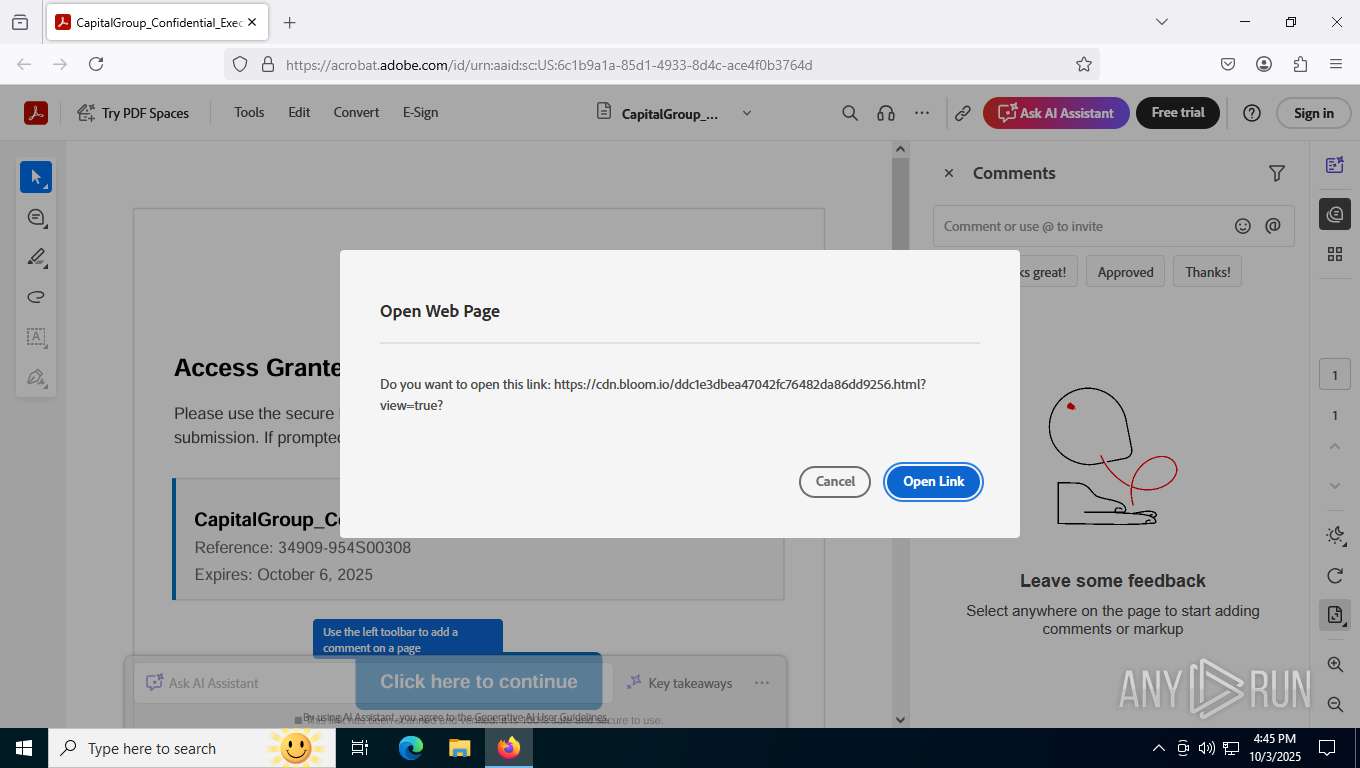
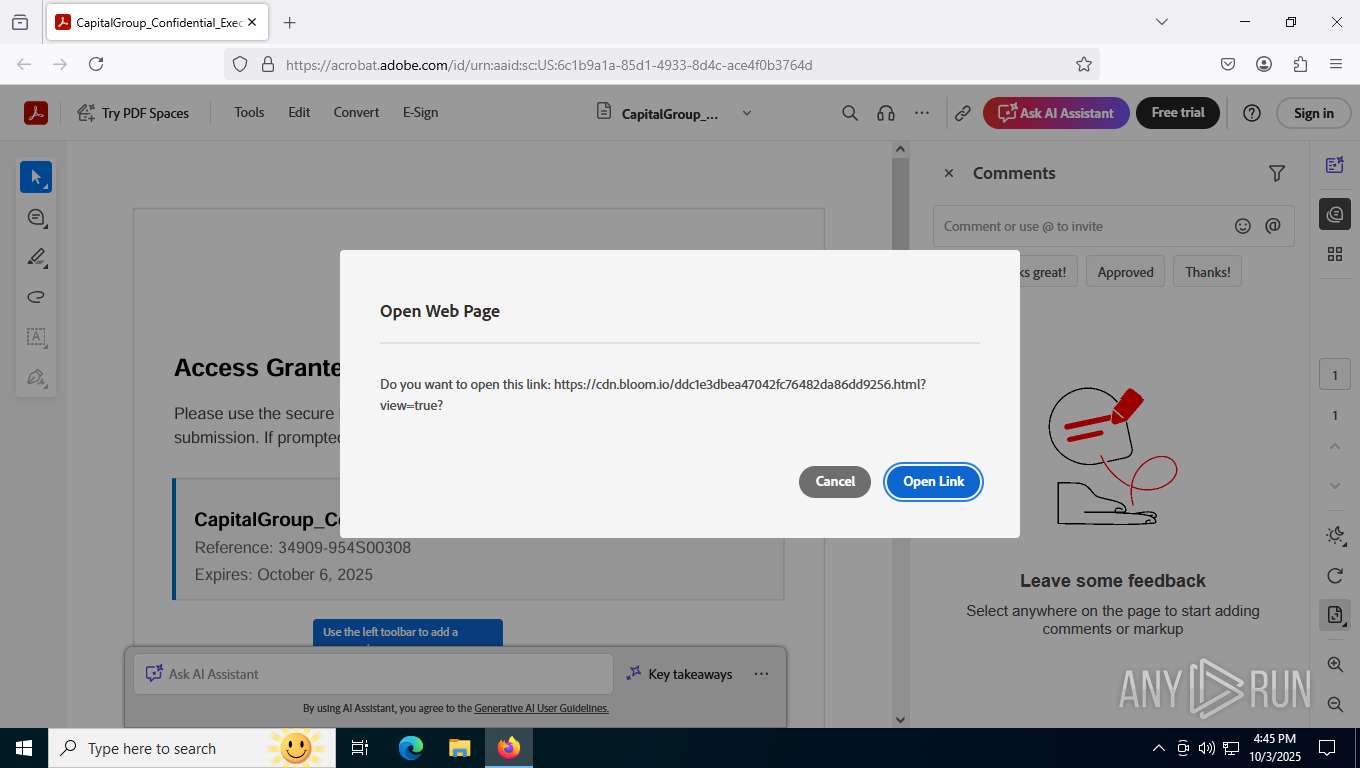
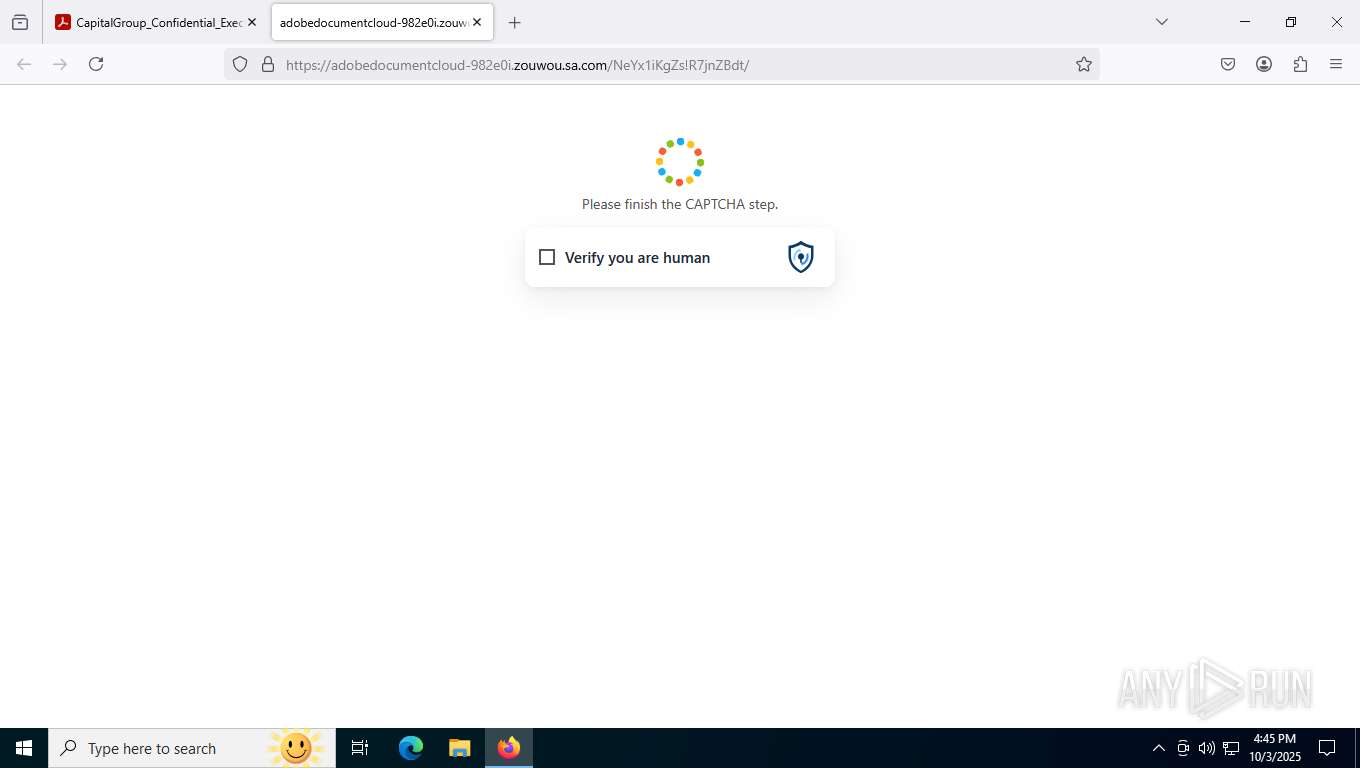
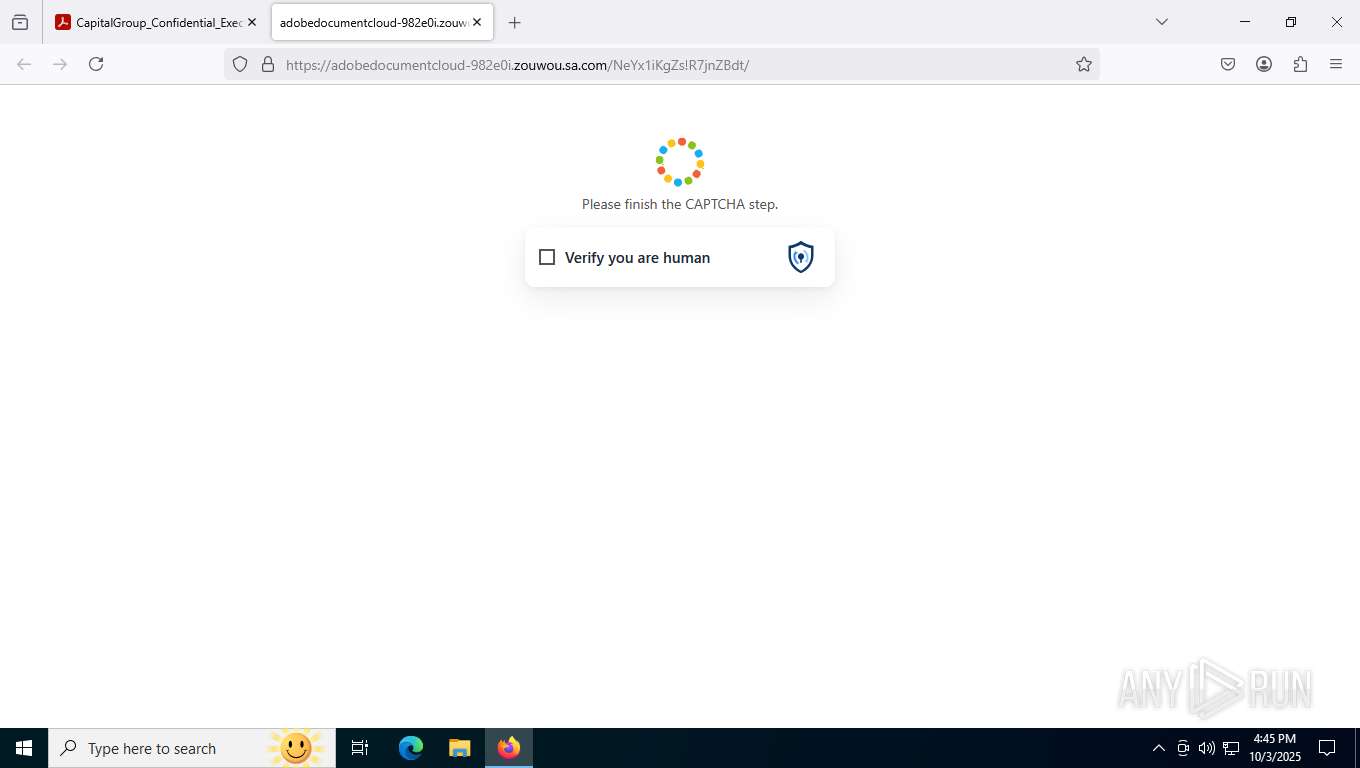
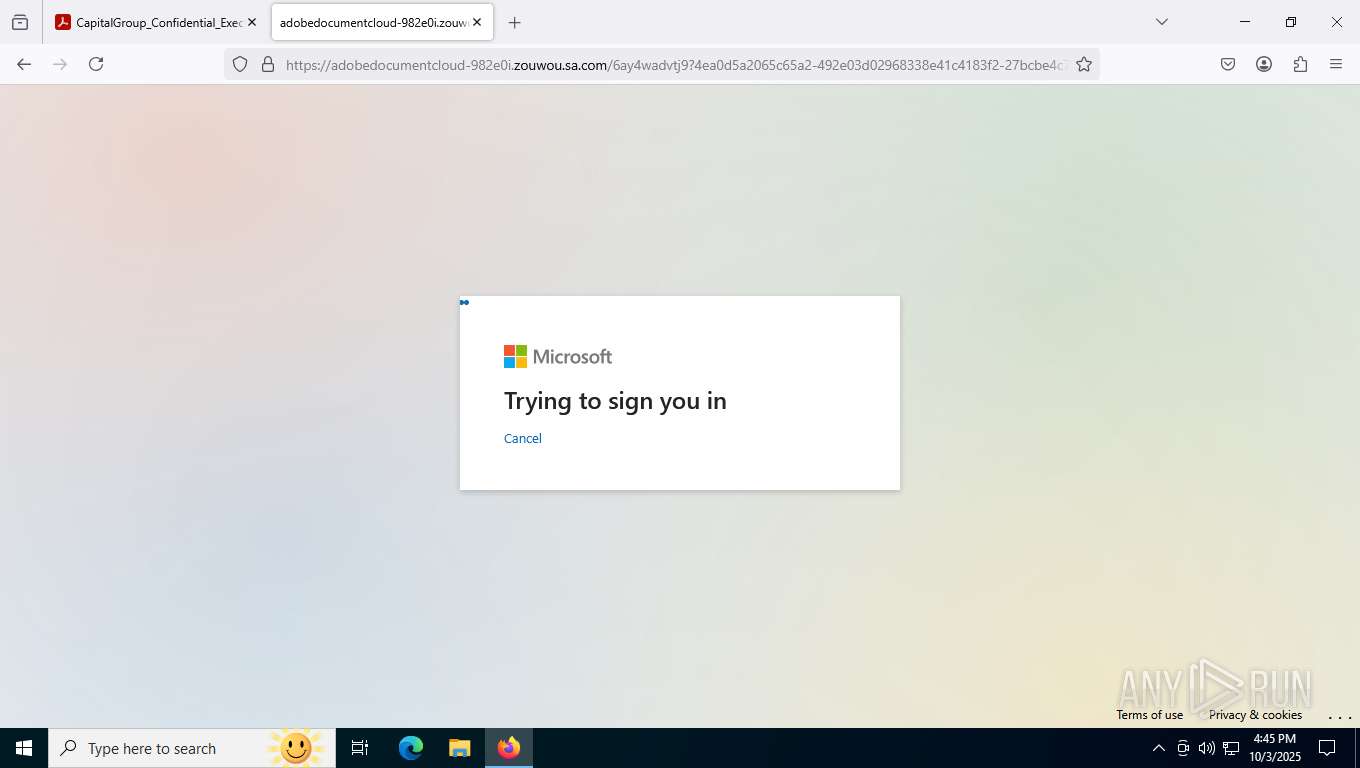
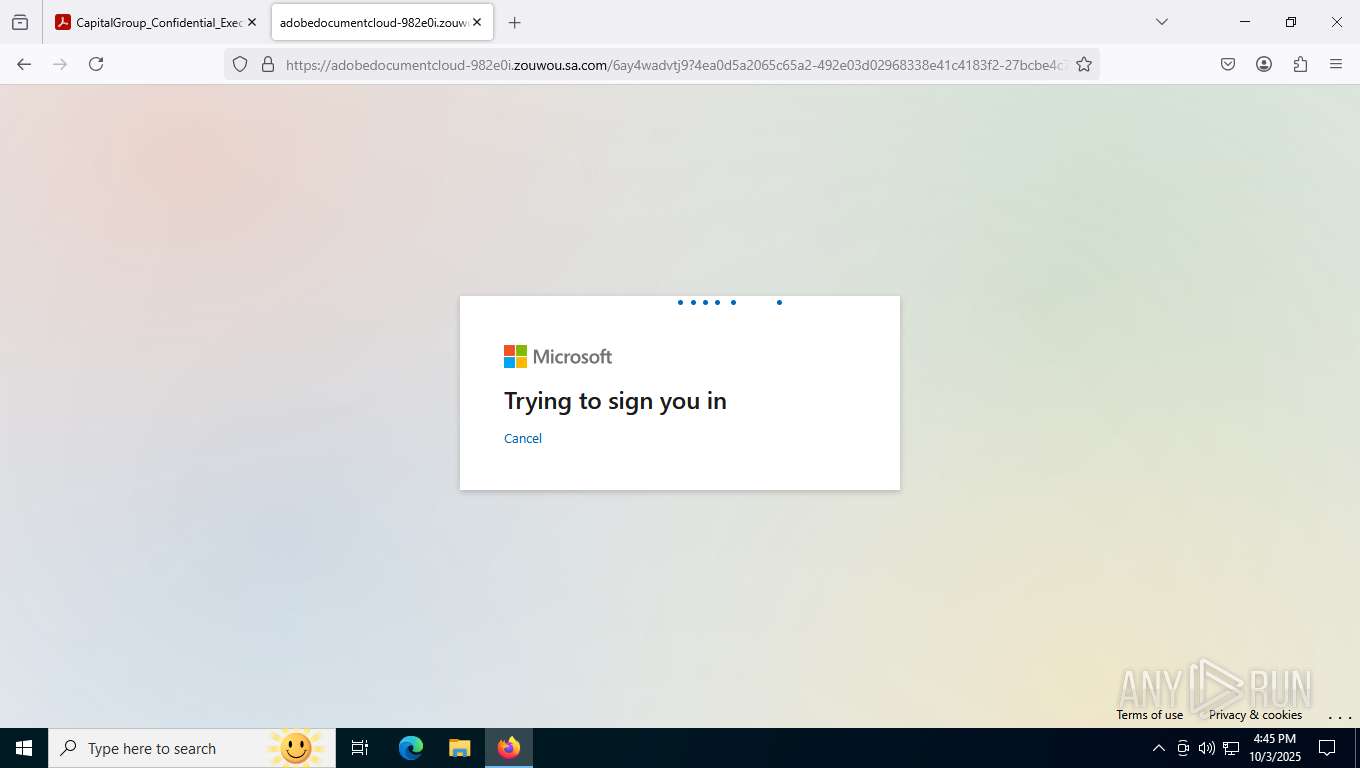
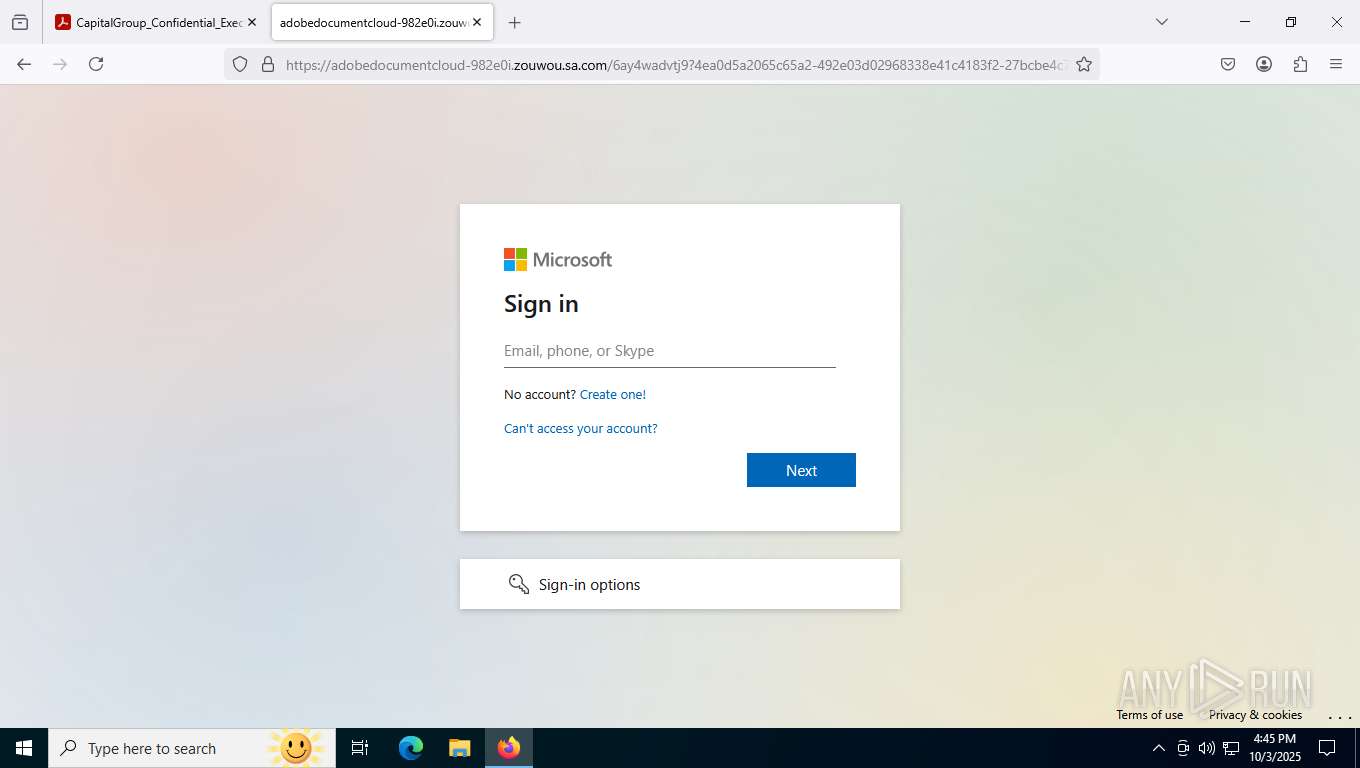
| URL: | https://postoffice.adobe.com/po-server/link/redirect?target=eyJhbGciOiJIUzUxMiJ9.eyJ0ZW1wbGF0ZSI6ImNjX2NvbGxhYl9hcnRpZmFjdF9pbnZpdGVfbm90aWZpY2F0aW9uIiwiZW1haWxBZGRyZXNzIjoibWF0dGhldy5raW1iZXJAbmF2aXRhaXJlLmNvbSIsInJlcXVlc3RJZCI6ImY0NTMxY2UwLTEyYTktNGNmMC04MTA0LWZjN2EyMDIyOThhMSIsImxpbmsiOiJodHRwczovL2Fjcm9iYXQuYWRvYmUuY29tL2lkL3VybjphYWlkOnNjOlVTOjZjMWI5YTFhLTg1ZDEtNDkzMy04ZDRjLWFjZTRmMGIzNzY0ZCIsImxhYmVsIjoiNSIsImxvY2FsZSI6ImVuX1VTIn0.btdE_zK2jl8uJPNibls1kk_CFnTKF2cP3UlxXQKTnYIEEM9INjPS9YXm-9qDeN_jQ3irio21Dwtcmu-5eJY-lA |
| Full analysis: | https://app.any.run/tasks/b8a6c74b-1923-4232-9c18-08072ca95bc4 |
| Verdict: | Malicious activity |
| Analysis date: | October 03, 2025, 16:45:14 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MD5: | 905D0349B9C8CB3591992BDAEB0ECB9D |
| SHA1: | 676FE5E6BAAC253CE0D49C324B316779AD632694 |
| SHA256: | 7A301C54CA23599E1E9AFA3D94B017CAC01CE77BE1F23C7BDB1D2C7CD992A437 |
| SSDEEP: | 12:2Tnxh4P5ApNz+VAY/QnMX5424uS3IZyOXhVZqP+QDo/T2Nr0d:2r25Ap0AtMXshEvYor2Nw |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 704 | "C:\Program Files\Mozilla Firefox\firefox.exe" "https://postoffice.adobe.com/po-server/link/redirect?target=eyJhbGciOiJIUzUxMiJ9.eyJ0ZW1wbGF0ZSI6ImNjX2NvbGxhYl9hcnRpZmFjdF9pbnZpdGVfbm90aWZpY2F0aW9uIiwiZW1haWxBZGRyZXNzIjoibWF0dGhldy5raW1iZXJAbmF2aXRhaXJlLmNvbSIsInJlcXVlc3RJZCI6ImY0NTMxY2UwLTEyYTktNGNmMC04MTA0LWZjN2EyMDIyOThhMSIsImxpbmsiOiJodHRwczovL2Fjcm9iYXQuYWRvYmUuY29tL2lkL3VybjphYWlkOnNjOlVTOjZjMWI5YTFhLTg1ZDEtNDkzMy04ZDRjLWFjZTRmMGIzNzY0ZCIsImxhYmVsIjoiNSIsImxvY2FsZSI6ImVuX1VTIn0.btdE_zK2jl8uJPNibls1kk_CFnTKF2cP3UlxXQKTnYIEEM9INjPS9YXm-9qDeN_jQ3irio21Dwtcmu-5eJY-lA" | C:\Program Files\Mozilla Firefox\firefox.exe | — | explorer.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: MEDIUM Description: Firefox Exit code: 0 Version: 136.0 Modules
| |||||||||||||||
| 708 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc -isForBrowser -prefsHandle 3280 -prefsLen 31065 -prefMapHandle 3284 -prefMapSize 273045 -jsInitHandle 3288 -jsInitLen 247456 -parentBuildID 20250227124745 -ipcHandle 3296 -initialChannelId {00c1d53d-3b3b-43ad-8456-d72cdee90981} -parentPid 5404 -crashReporter "\\.\pipe\gecko-crash-server-pipe.5404" -win32kLockedDown -appDir "C:\Program Files\Mozilla Firefox\browser" - 3 tab | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: MEDIUM Description: Firefox Version: 136.0 Modules
| |||||||||||||||
| 2392 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc -parentBuildID 20250227124745 -prefsHandle 1940 -prefsLen 36580 -prefMapHandle 1944 -prefMapSize 273045 -ipcHandle 1888 -initialChannelId {fbae2c13-a33f-453b-a7d0-a668b27fda9d} -parentPid 5404 -crashReporter "\\.\pipe\gecko-crash-server-pipe.5404" -appDir "C:\Program Files\Mozilla Firefox\browser" - 1 gpu | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: MEDIUM Description: Firefox Version: 136.0 Modules
| |||||||||||||||
| 2428 | C:\WINDOWS\system32\svchost.exe -k NetworkService -p -s Dnscache | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4952 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc -parentBuildID 20250227124745 -prefsHandle 3400 -prefsLen 37056 -prefMapHandle 3404 -prefMapSize 273045 -ipcHandle 3412 -initialChannelId {eaf5fb4c-e714-4250-80d5-33500713a0b5} -parentPid 5404 -crashReporter "\\.\pipe\gecko-crash-server-pipe.5404" -appDir "C:\Program Files\Mozilla Firefox\browser" - 4 rdd | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: MEDIUM Description: Firefox Version: 136.0 Modules
| |||||||||||||||
| 5404 | "C:\Program Files\Mozilla Firefox\firefox.exe" https://postoffice.adobe.com/po-server/link/redirect?target=eyJhbGciOiJIUzUxMiJ9.eyJ0ZW1wbGF0ZSI6ImNjX2NvbGxhYl9hcnRpZmFjdF9pbnZpdGVfbm90aWZpY2F0aW9uIiwiZW1haWxBZGRyZXNzIjoibWF0dGhldy5raW1iZXJAbmF2aXRhaXJlLmNvbSIsInJlcXVlc3RJZCI6ImY0NTMxY2UwLTEyYTktNGNmMC04MTA0LWZjN2EyMDIyOThhMSIsImxpbmsiOiJodHRwczovL2Fjcm9iYXQuYWRvYmUuY29tL2lkL3VybjphYWlkOnNjOlVTOjZjMWI5YTFhLTg1ZDEtNDkzMy04ZDRjLWFjZTRmMGIzNzY0ZCIsImxhYmVsIjoiNSIsImxvY2FsZSI6ImVuX1VTIn0.btdE_zK2jl8uJPNibls1kk_CFnTKF2cP3UlxXQKTnYIEEM9INjPS9YXm-9qDeN_jQ3irio21Dwtcmu-5eJY-lA | C:\Program Files\Mozilla Firefox\firefox.exe | firefox.exe | ||||||||||||
User: admin Company: Mozilla Corporation Integrity Level: MEDIUM Description: Firefox Version: 136.0 Modules
| |||||||||||||||
| 7952 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc -parentBuildID 20250227124745 -prefsHandle 2148 -prefsLen 36580 -prefMapHandle 2152 -prefMapSize 273045 -ipcHandle 2160 -initialChannelId {42cdbec9-2049-4f72-9669-894fc32a60e1} -parentPid 5404 -crashReporter "\\.\pipe\gecko-crash-server-pipe.5404" -win32kLockedDown -appDir "C:\Program Files\Mozilla Firefox\browser" - 2 socket | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: MEDIUM Description: Firefox Version: 136.0 Modules
| |||||||||||||||
| 8260 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc -isForBrowser -prefsHandle 3948 -prefsLen 44960 -prefMapHandle 3952 -prefMapSize 273045 -jsInitHandle 3956 -jsInitLen 247456 -parentBuildID 20250227124745 -ipcHandle 3964 -initialChannelId {6a789ac8-a222-4dcb-b2e4-ce0719f745ae} -parentPid 5404 -crashReporter "\\.\pipe\gecko-crash-server-pipe.5404" -win32kLockedDown -appDir "C:\Program Files\Mozilla Firefox\browser" - 5 tab | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: MEDIUM Description: Firefox Version: 136.0 Modules
| |||||||||||||||
| 8460 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc -parentBuildID 20250227124745 -sandboxingKind 0 -prefsHandle 4608 -prefsLen 45116 -prefMapHandle 4612 -prefMapSize 273045 -ipcHandle 4552 -initialChannelId {e3a21ef8-1153-4b46-af66-0d7fc8d23433} -parentPid 5404 -crashReporter "\\.\pipe\gecko-crash-server-pipe.5404" -win32kLockedDown -appDir "C:\Program Files\Mozilla Firefox\browser" - 6 utility | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: MEDIUM Description: Firefox Version: 136.0 Modules
| |||||||||||||||
| 8512 | "C:\Program Files\Mozilla Firefox\firefox.exe" -contentproc -isForBrowser -prefsHandle 4724 -prefsLen 45168 -prefMapHandle 4748 -prefMapSize 273045 -jsInitHandle 4752 -jsInitLen 247456 -parentBuildID 20250227124745 -ipcHandle 4756 -initialChannelId {7efb943b-9d31-4448-8637-caa3b46311cd} -parentPid 5404 -crashReporter "\\.\pipe\gecko-crash-server-pipe.5404" -win32kLockedDown -appDir "C:\Program Files\Mozilla Firefox\browser" - 7 tab | C:\Program Files\Mozilla Firefox\firefox.exe | — | firefox.exe | |||||||||||
User: admin Company: Mozilla Corporation Integrity Level: MEDIUM Description: Firefox Version: 136.0 Modules
| |||||||||||||||
| (PID) Process: | (704) firefox.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Mozilla\Firefox\Launcher |
| Operation: | write | Name: | C:\Program Files\Mozilla Firefox\firefox.exe|Launcher |
Value: 4663734201000000 | |||
| (PID) Process: | (5404) firefox.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Mozilla\Firefox\DllPrefetchExperiment |
| Operation: | write | Name: | C:\Program Files\Mozilla Firefox\firefox.exe |
Value: 0 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 5404 | firefox.exe | C:\Users\admin\AppData\Local\Mozilla\Firefox\Profiles\9kie7cg6.default-release\startupCache\scriptCache-current.bin | — | |
MD5:— | SHA256:— | |||
| 5404 | firefox.exe | C:\Users\admin\AppData\Roaming\Mozilla\Firefox\Profiles\9kie7cg6.default-release\storage\permanent\chrome\idb\1451318868ntouromlalnodry--epcr.sqlite-shm | binary | |
MD5:B7C14EC6110FA820CA6B65F5AEC85911 | SHA256:FD4C9FDA9CD3F9AE7C962B0DDF37232294D55580E1AA165AA06129B8549389EB | |||
| 5404 | firefox.exe | C:\Users\admin\AppData\Roaming\Mozilla\Firefox\Profiles\9kie7cg6.default-release\sessionCheckpoints.json | binary | |
MD5:EA8B62857DFDBD3D0BE7D7E4A954EC9A | SHA256:792955295AE9C382986222C6731C5870BD0E921E7F7E34CC4615F5CD67F225DA | |||
| 5404 | firefox.exe | C:\Users\admin\AppData\Local\Mozilla\Firefox\Profiles\9kie7cg6.default-release\startupCache\urlCache-current.bin | binary | |
MD5:B30329D7D2CF4258C22F500CBEA218FF | SHA256:C5E20431B116E1DABD383C6855A36E6DAF13E1CC125B83D59EF68B4BCEFB02E6 | |||
| 5404 | firefox.exe | C:\Users\admin\AppData\Roaming\Mozilla\Firefox\Profiles\9kie7cg6.default-release\cookies.sqlite-shm | binary | |
MD5:B7C14EC6110FA820CA6B65F5AEC85911 | SHA256:FD4C9FDA9CD3F9AE7C962B0DDF37232294D55580E1AA165AA06129B8549389EB | |||
| 5404 | firefox.exe | C:\Users\admin\AppData\Roaming\Mozilla\Firefox\Profiles\9kie7cg6.default-release\storage\permanent\chrome\idb\3870112724rsegmnoittet-es.sqlite-shm | binary | |
MD5:B7C14EC6110FA820CA6B65F5AEC85911 | SHA256:FD4C9FDA9CD3F9AE7C962B0DDF37232294D55580E1AA165AA06129B8549389EB | |||
| 5404 | firefox.exe | C:\Users\admin\AppData\Roaming\Mozilla\Firefox\Profiles\9kie7cg6.default-release\sessionCheckpoints.json.tmp | binary | |
MD5:EA8B62857DFDBD3D0BE7D7E4A954EC9A | SHA256:792955295AE9C382986222C6731C5870BD0E921E7F7E34CC4615F5CD67F225DA | |||
| 5404 | firefox.exe | C:\Users\admin\AppData\Roaming\Mozilla\Firefox\Profiles\9kie7cg6.default-release\prefs.js | text | |
MD5:8A3983F46534AE8E756E99635A279537 | SHA256:9ED0F72CB08EFA7F7A82635A9B2842113C82522C5150320D17C18C365069CAA2 | |||
| 5404 | firefox.exe | C:\Users\admin\AppData\Roaming\Mozilla\Firefox\Profiles\9kie7cg6.default-release\prefs-1.js | text | |
MD5:8A3983F46534AE8E756E99635A279537 | SHA256:9ED0F72CB08EFA7F7A82635A9B2842113C82522C5150320D17C18C365069CAA2 | |||
| 5404 | firefox.exe | C:\Users\admin\AppData\Roaming\Mozilla\Firefox\Profiles\9kie7cg6.default-release\SiteSecurityServiceState.bin | binary | |
MD5:0AABD9E5E3E5521E0A1ED35F1D62DB75 | SHA256:260A86BA84F58B68CA4113660DC26BE98851EF7222D1B05C635599447ADA2447 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
5404 | firefox.exe | GET | 200 | 34.107.221.82:80 | http://detectportal.firefox.com/success.txt?ipv4 | US | text | 8 b | whitelisted |
5404 | firefox.exe | POST | 200 | 142.250.185.163:80 | http://o.pki.goog/s/wr3/vbw | US | binary | 472 b | whitelisted |
5404 | firefox.exe | POST | 200 | 142.250.185.163:80 | http://o.pki.goog/we2 | US | binary | 279 b | whitelisted |
5404 | firefox.exe | POST | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/ | US | binary | 471 b | whitelisted |
5404 | firefox.exe | GET | 200 | 34.107.221.82:80 | http://detectportal.firefox.com/success.txt?ipv4 | US | text | 8 b | whitelisted |
5404 | firefox.exe | POST | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/ | US | binary | 471 b | whitelisted |
5404 | firefox.exe | POST | 200 | 142.250.185.163:80 | http://o.pki.goog/s/wr3/W6c | US | binary | 471 b | whitelisted |
5404 | firefox.exe | POST | 200 | 142.250.185.163:80 | http://o.pki.goog/s/wr3/W6c | US | binary | 471 b | whitelisted |
5404 | firefox.exe | POST | 200 | 142.250.185.163:80 | http://o.pki.goog/s/wr3/W6c | US | binary | 471 b | whitelisted |
5404 | firefox.exe | POST | 200 | 184.30.131.245:80 | http://ocsp.digicert.com/ | US | binary | 471 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
6864 | RUXIMICS.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
6016 | MoUsoCoreWorker.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5224 | SearchApp.exe | 23.36.162.84:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
5404 | firefox.exe | 34.160.144.191:443 | content-signature-2.cdn.mozilla.net | GOOGLE | US | whitelisted |
5404 | firefox.exe | 52.35.47.171:443 | postoffice.adobe.com | AMAZON-02 | US | whitelisted |
5404 | firefox.exe | 34.107.221.82:80 | detectportal.firefox.com | GOOGLE | US | whitelisted |
5404 | firefox.exe | 34.36.137.203:443 | contile.services.mozilla.com | GOOGLE-CLOUD-PLATFORM | US | whitelisted |
5404 | firefox.exe | 151.101.129.91:443 | firefox.settings.services.mozilla.com | FASTLY | US | whitelisted |
5404 | firefox.exe | 142.250.185.163:80 | o.pki.goog | GOOGLE | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
www.bing.com |
| whitelisted |
google.com |
| whitelisted |
content-signature-2.cdn.mozilla.net |
| whitelisted |
content-signature-chains.prod.autograph.services.mozaws.net |
| whitelisted |
postoffice.adobe.com |
| whitelisted |
detectportal.firefox.com |
| whitelisted |
prod.detectportal.prod.cloudops.mozgcp.net |
| whitelisted |
contile.services.mozilla.com |
| whitelisted |
spocs.getpocket.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2428 | svchost.exe | Misc activity | ET INFO Observed DNS Query to Online PDF Viewer Domain (postoffice .adobe .com) |
2428 | svchost.exe | Misc activity | ET INFO Observed DNS Query to Online PDF Viewer Domain (postoffice .adobe .com) |
2428 | svchost.exe | Misc activity | ET INFO Observed DNS Query to Online PDF Viewer Domain (postoffice .adobe .com) |
5404 | firefox.exe | Misc activity | ET INFO Observed Online PDF Viewer Domain (postoffice .adobe .com in TLS SNI) |
5404 | firefox.exe | Misc activity | ET INFO Observed Online PDF Viewer Domain (postoffice .adobe .com in TLS SNI) |
— | — | Not Suspicious Traffic | INFO [ANY.RUN] Request to load WebAssembly module |
— | — | Not Suspicious Traffic | INFO [ANY.RUN] Request to load WebAssembly module |
2428 | svchost.exe | Not Suspicious Traffic | INFO [ANY.RUN] An application monitoring request to newrelic .com |
2428 | svchost.exe | Not Suspicious Traffic | INFO [ANY.RUN] An application monitoring request to newrelic .com |
2428 | svchost.exe | Not Suspicious Traffic | INFO [ANY.RUN] An application monitoring request to newrelic .com |