ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
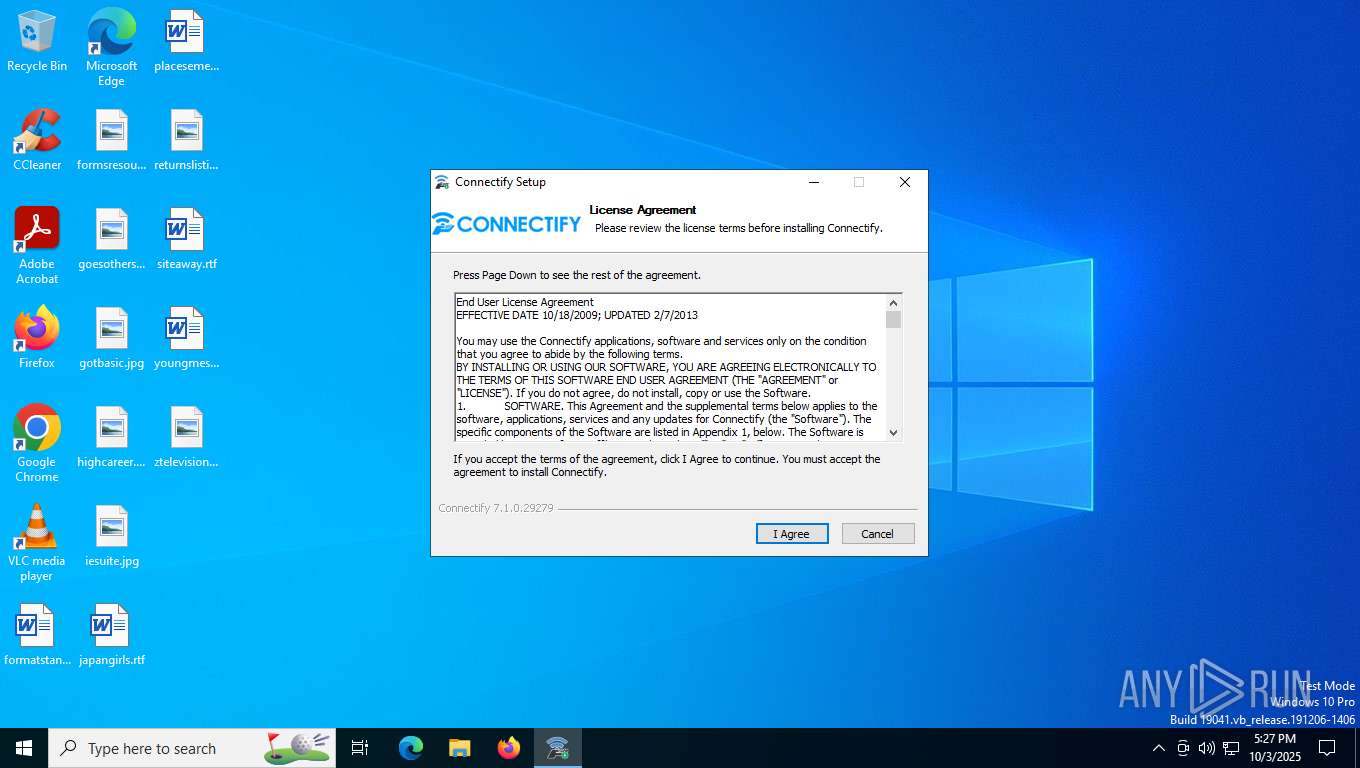
| File name: | ConnectifyInstaller.exe |
| Full analysis: | https://app.any.run/tasks/88bbc7d1-e9f4-4e78-9703-465a34310b02 |
| Verdict: | Malicious activity |
| Analysis date: | October 03, 2025, 17:27:34 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, Nullsoft Installer self-extracting archive, 5 sections |
| MD5: | E67EAD35EFAD0418B476AA8A0B2BB99B |
| SHA1: | A532EF8ADA4DA7CE99B1EB180FE2A8E8C187020F |
| SHA256: | 71B6E6B27F6B1742ACF06C70EBDC524F0DD6DC790898B5A6E44160BB2862065D |
| SSDEEP: | 98304:Hbfyhtf13BeWid1GexelE1nA1PGD447BjfrSOHMCc2dak71nqFCSxvpcoSp6NNKV:dSBXswRQT4DFHu |
| .exe | | | NSIS - Nullsoft Scriptable Install System (91.9) |
|---|---|---|
| .exe | | | Win32 Executable MS Visual C++ (generic) (3.3) |
| .exe | | | Win64 Executable (generic) (3) |
| .dll | | | Win32 Dynamic Link Library (generic) (0.7) |
| .exe | | | Win32 Executable (generic) (0.4) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2009:12:05 22:53:18+00:00 |
| ImageFileCharacteristics: | No relocs, Executable, No line numbers, No symbols, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 6 |
| CodeSize: | 25088 |
| InitializedDataSize: | 124928 |
| UninitializedDataSize: | 1024 |
| EntryPoint: | 0x36a0 |
| OSVersion: | 4 |
| ImageVersion: | 6 |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 708 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | Analytics.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 796 | "C:\Users\admin\AppData\Local\Temp\Connectify\3\ConnectifySupportCenter.exe" connectifysupport://swcheck Connectify | C:\Users\admin\AppData\Local\Temp\Connectify\3\ConnectifySupportCenter.exe | — | ConnectifyInstaller.exe | |||||||||||
User: admin Company: Connectify Integrity Level: HIGH Description: Connectify Hotspot Support Center Exit code: 0 Version: 1.0.0.0 Modules
| |||||||||||||||
| 1836 | "C:\Users\admin\AppData\Local\Temp\Connectify\3\Analytics.exe" navigation Installer Init 7.1.0.29279 None | C:\Users\admin\AppData\Local\Temp\Connectify\3\Analytics.exe | Analytics.exe | ||||||||||||
User: admin Company: Microsoft Integrity Level: HIGH Description: Analytics Exit code: 0 Version: 1.0.0.0 Modules
| |||||||||||||||
| 2092 | "C:\Users\admin\AppData\Local\Temp\ConnectifyInstaller.exe" /UAC:50310 /NCRC | C:\Users\admin\AppData\Local\Temp\ConnectifyInstaller.exe | ConnectifyInstaller.exe | ||||||||||||
User: admin Integrity Level: HIGH Modules
| |||||||||||||||
| 2368 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | GlobalAtomTable.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3116 | "BackgroundTransferHost.exe" -ServerName:BackgroundTransferHost.1 | C:\Windows\System32\BackgroundTransferHost.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Download/Upload Host Exit code: 1 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4696 | "C:\Users\admin\AppData\Local\Temp\Connectify\3\Analytics.exe" daemon navigation Installer Init 7.1.0.29279 None | C:\Users\admin\AppData\Local\Temp\Connectify\3\Analytics.exe | — | ConnectifyInstaller.exe | |||||||||||
User: admin Company: Microsoft Integrity Level: HIGH Description: Analytics Exit code: 0 Version: 1.0.0.0 Modules
| |||||||||||||||
| 5424 | "C:\Users\admin\AppData\Local\Temp\ConnectifyInstaller.exe" | C:\Users\admin\AppData\Local\Temp\ConnectifyInstaller.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Modules
| |||||||||||||||
| 5792 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | Analytics.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6292 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | Analytics.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (7556) Analytics.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Connectify |
| Operation: | write | Name: | InstallDate |
Value: 10/3/2025 | |||
| (PID) Process: | (7556) Analytics.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Connectify |
| Operation: | write | Name: | Source |
Value: dispatch_ | |||
| (PID) Process: | (1836) Analytics.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\Analytics_RASAPI32 |
| Operation: | write | Name: | EnableFileTracing |
Value: 0 | |||
| (PID) Process: | (1836) Analytics.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\Analytics_RASAPI32 |
| Operation: | write | Name: | EnableAutoFileTracing |
Value: 0 | |||
| (PID) Process: | (1836) Analytics.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\Analytics_RASAPI32 |
| Operation: | write | Name: | EnableConsoleTracing |
Value: 0 | |||
| (PID) Process: | (1836) Analytics.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\Analytics_RASAPI32 |
| Operation: | write | Name: | FileTracingMask |
Value: | |||
| (PID) Process: | (1836) Analytics.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\Analytics_RASAPI32 |
| Operation: | write | Name: | ConsoleTracingMask |
Value: | |||
| (PID) Process: | (1836) Analytics.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\Analytics_RASAPI32 |
| Operation: | write | Name: | MaxFileSize |
Value: 1048576 | |||
| (PID) Process: | (1836) Analytics.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\Analytics_RASAPI32 |
| Operation: | write | Name: | FileDirectory |
Value: %windir%\tracing | |||
| (PID) Process: | (1836) Analytics.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\Tracing\Analytics_RASMANCS |
| Operation: | write | Name: | EnableFileTracing |
Value: 0 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2092 | ConnectifyInstaller.exe | C:\Users\admin\AppData\Local\Temp\nst18D9.tmp\System.dll | executable | |
MD5:C17103AE9072A06DA581DEC998343FC1 | SHA256:DC58D8AD81CACB0C1ED72E33BFF8F23EA40B5252B5BB55D393A0903E6819AE2F | |||
| 2092 | ConnectifyInstaller.exe | C:\Users\admin\AppData\Local\Temp\nst18D9.tmp\modern-header.bmp | image | |
MD5:06D1C9640315DBE3AD514CB3A8E11A7F | SHA256:C4EC072EBA73B1D914E914CBEA632B1608689C5610C31D94DD0A391F7F1A0DBE | |||
| 5424 | ConnectifyInstaller.exe | C:\Users\admin\AppData\Local\Temp\nsb1399.tmp\System.dll | executable | |
MD5:C17103AE9072A06DA581DEC998343FC1 | SHA256:DC58D8AD81CACB0C1ED72E33BFF8F23EA40B5252B5BB55D393A0903E6819AE2F | |||
| 2092 | ConnectifyInstaller.exe | C:\Users\admin\AppData\Local\Temp\nst18D9.tmp\UAC.dll | executable | |
MD5:7F56C0D6A8733DEC142814ED5A58B0EE | SHA256:86445396775370AFF5834F10BDA25E505B6F89EFC69A04FE1CE46F5D128BE73F | |||
| 5424 | ConnectifyInstaller.exe | C:\Users\admin\AppData\Local\Temp\nsb1399.tmp\modern-wizard.bmp | image | |
MD5:AE43624C14859150EDFB54B4024AFF46 | SHA256:D5B56046F10941E6659277D46FFD4A0D327DB24BE3174D6A8E7AE0660DA874E9 | |||
| 2092 | ConnectifyInstaller.exe | C:\Users\admin\AppData\Local\Temp\nst18D9.tmp\modern-wizard.bmp | image | |
MD5:AE43624C14859150EDFB54B4024AFF46 | SHA256:D5B56046F10941E6659277D46FFD4A0D327DB24BE3174D6A8E7AE0660DA874E9 | |||
| 2092 | ConnectifyInstaller.exe | C:\Users\admin\AppData\Local\Temp\Connectify\3\Analytics.exe | executable | |
MD5:05712885EF39A6D6DAAD0EB884763946 | SHA256:D88789C5D5C5855CEC6EEFE3BFDB948F1C6E1033C02C3F947B71DDF93FB181AC | |||
| 2092 | ConnectifyInstaller.exe | C:\Users\admin\AppData\Local\Temp\nst18D9.tmp\md5dll.dll | executable | |
MD5:7059F133EA2316B9E7E39094A52A8C34 | SHA256:32C3D36F38E7E8A8BAFD4A53663203EF24A10431BDA16AF9E353C7D5D108610F | |||
| 2092 | ConnectifyInstaller.exe | C:\Users\admin\AppData\Local\Temp\Connectify\3\Connectify.exe | executable | |
MD5:52AF43B5AC5AED5DE13E60E72B9CBAF1 | SHA256:8465840E31D9F906BFA2FBF596F8FBB9BBD7A01FCF777829FCFC8744BEACB825 | |||
| 2092 | ConnectifyInstaller.exe | C:\Users\admin\AppData\Local\Temp\Connectify\3\Connectify.exe.config | xml | |
MD5:2E8901597468F263A183DCA9C59F1330 | SHA256:9A38F15BF07CD33E7FBFBF93000982575FC6A37DCBE0E98BC90EB488F49E41AD | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
4936 | svchost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
4936 | svchost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
6208 | backgroundTaskHost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | US | binary | 313 b | whitelisted |
4176 | backgroundTaskHost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | US | binary | 471 b | whitelisted |
8416 | BackgroundTransferHost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | US | binary | 313 b | whitelisted |
5792 | backgroundTaskHost.exe | GET | 200 | 172.66.2.5:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | US | binary | 471 b | whitelisted |
1836 | Analytics.exe | GET | 200 | 142.250.185.78:80 | http://www.google-analytics.com/__utm.gif?utmwv=4.4sa&utmn=571013505&utmhn=connectify.connectify.me&utmp=Installer%2fInit%2f7.1.0.29279%2fNone&utmac=UA-742036-6&utmcc=__utma%3D999.1814719801.999.999.999111111111111.1%3B%2B__utmz%3D999.999.999.999.utmcsr%3Ddispatch_%7Cutmccn%3D(referral)%7Cutmcmd%3Dreferral%7Cutmcct%3DInstaller%2fInit%2f7.1.0.29279%2fNone%3B&utmul=en&utmdebug=ON | US | image | 35 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
6016 | MoUsoCoreWorker.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
7072 | RUXIMICS.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5224 | SearchApp.exe | 95.101.142.200:443 | www.bing.com | Akamai International B.V. | SE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
1836 | Analytics.exe | 142.250.185.78:80 | www.google-analytics.com | GOOGLE | US | whitelisted |
4936 | svchost.exe | 20.190.160.2:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
4936 | svchost.exe | 172.66.2.5:80 | ocsp.digicert.com | — | US | whitelisted |
6208 | backgroundTaskHost.exe | 104.84.152.9:443 | www.bing.com | Akamai International B.V. | SE | whitelisted |
6208 | backgroundTaskHost.exe | 172.66.2.5:80 | ocsp.digicert.com | — | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
www.bing.com |
| whitelisted |
google.com |
| whitelisted |
www.google-analytics.com |
| whitelisted |
login.live.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
arc.msn.com |
| whitelisted |
fd.api.iris.microsoft.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
— | — | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |