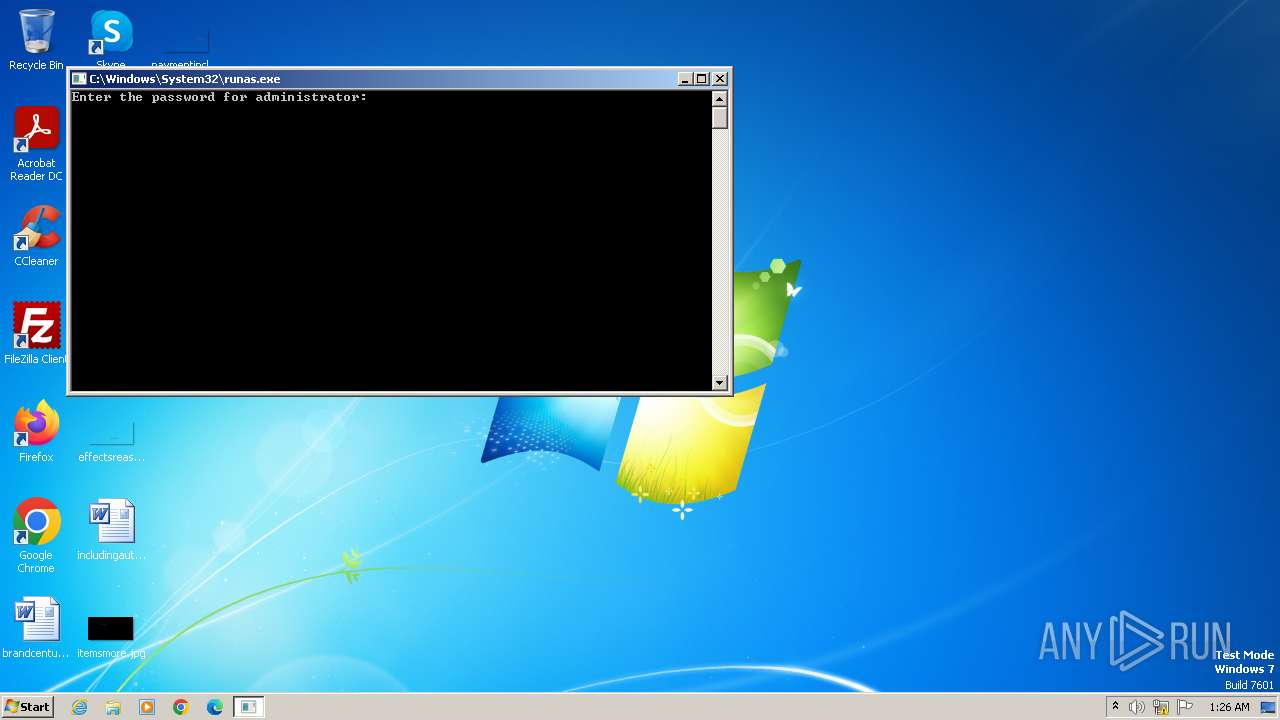
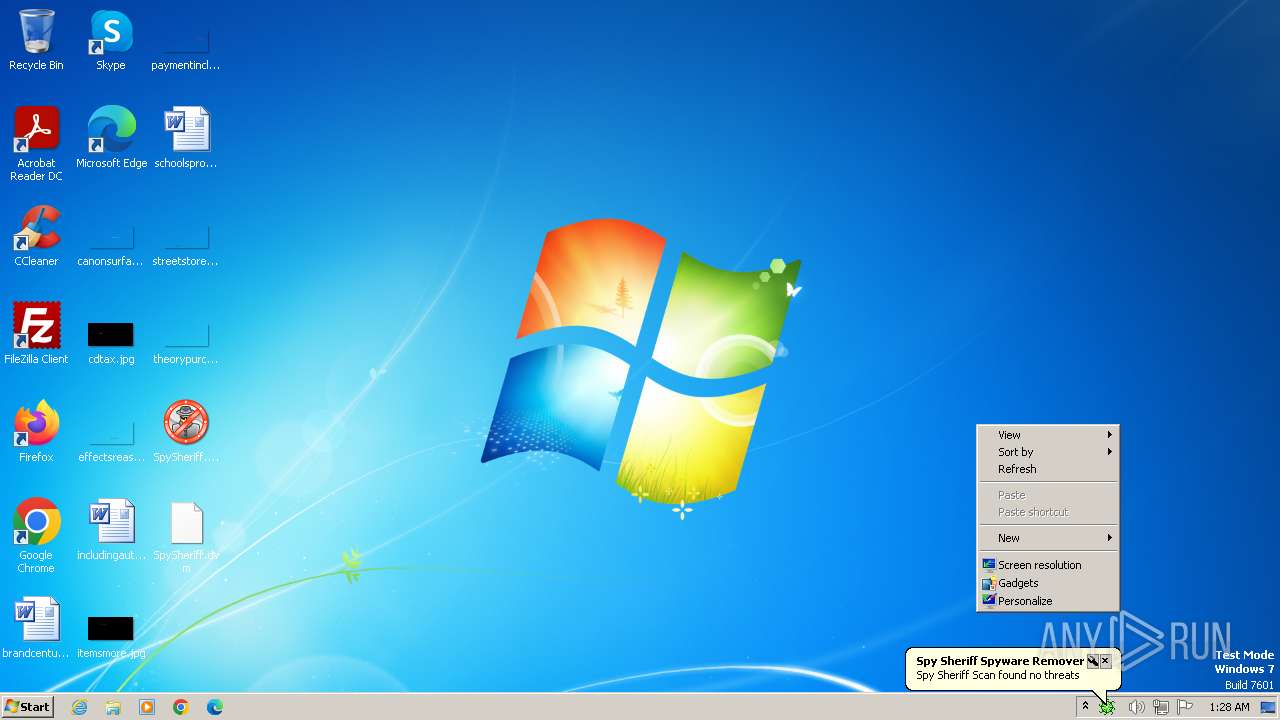
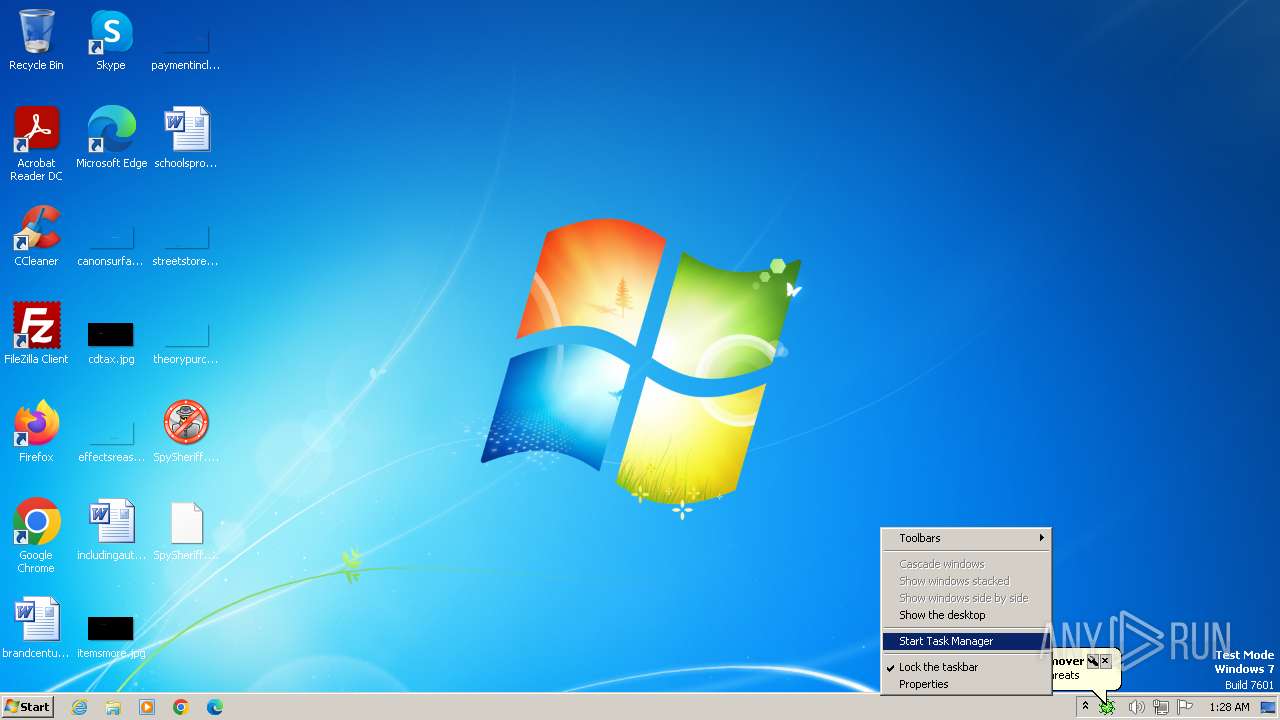
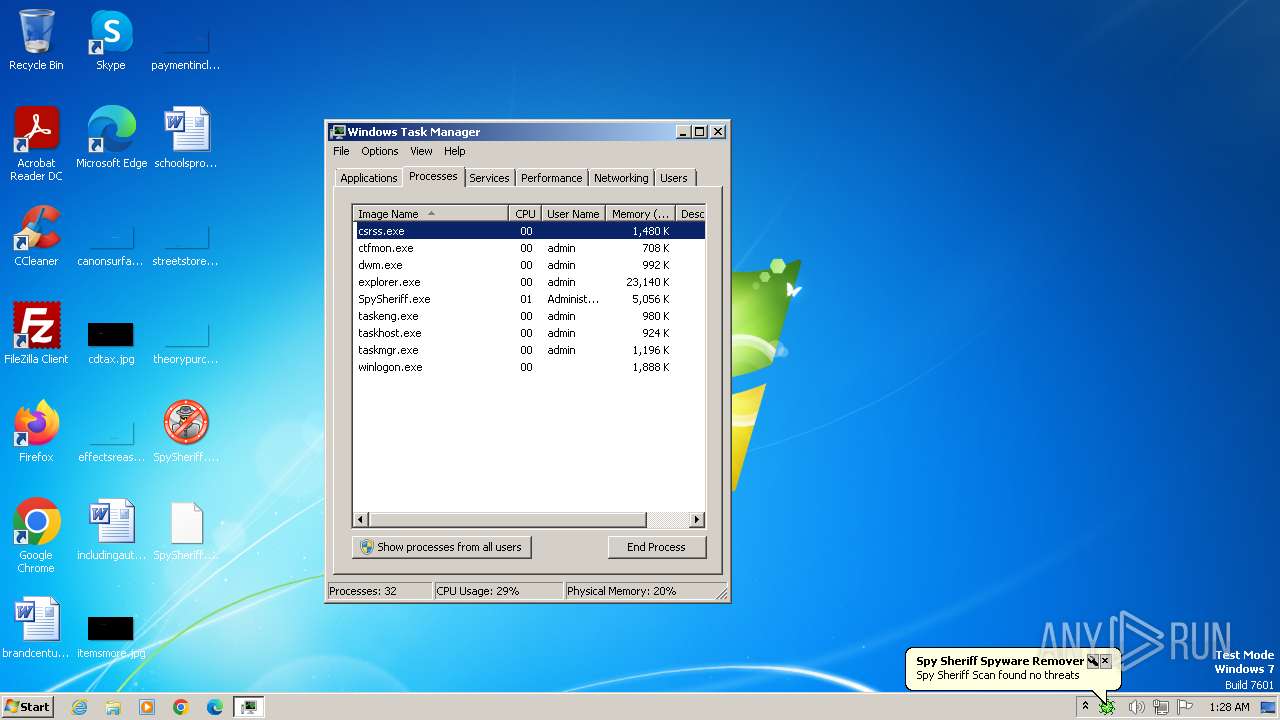
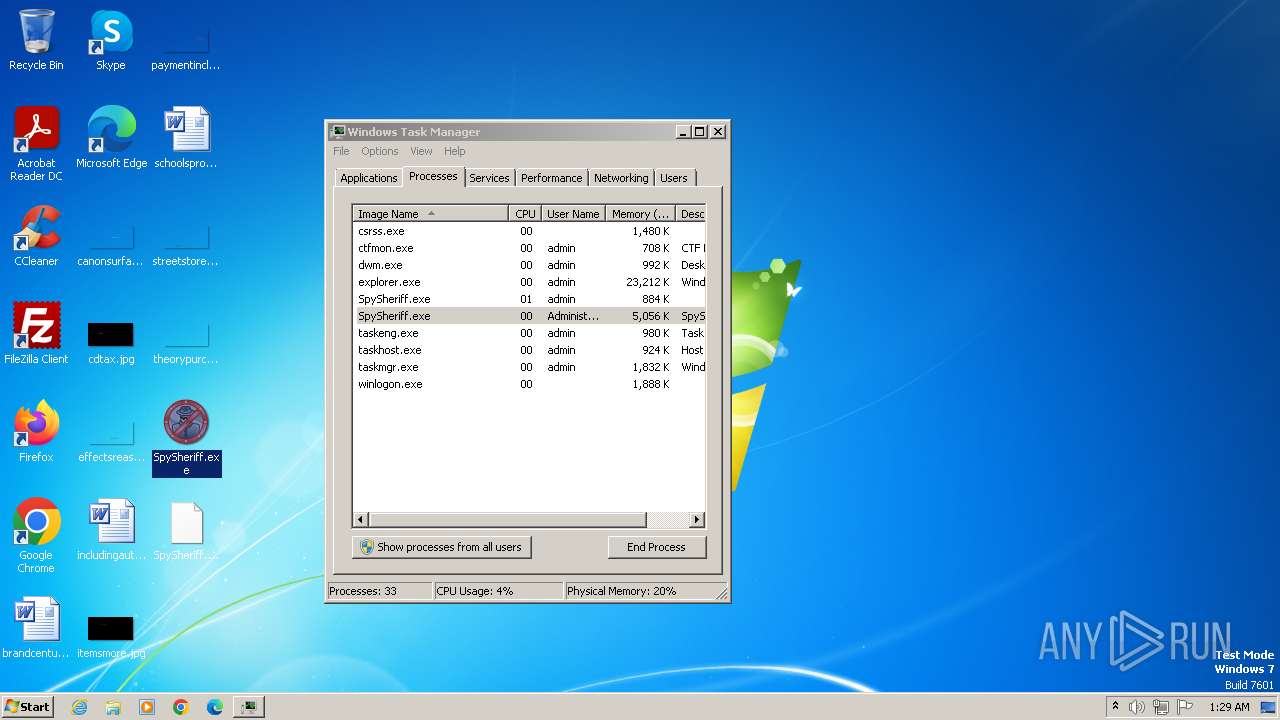
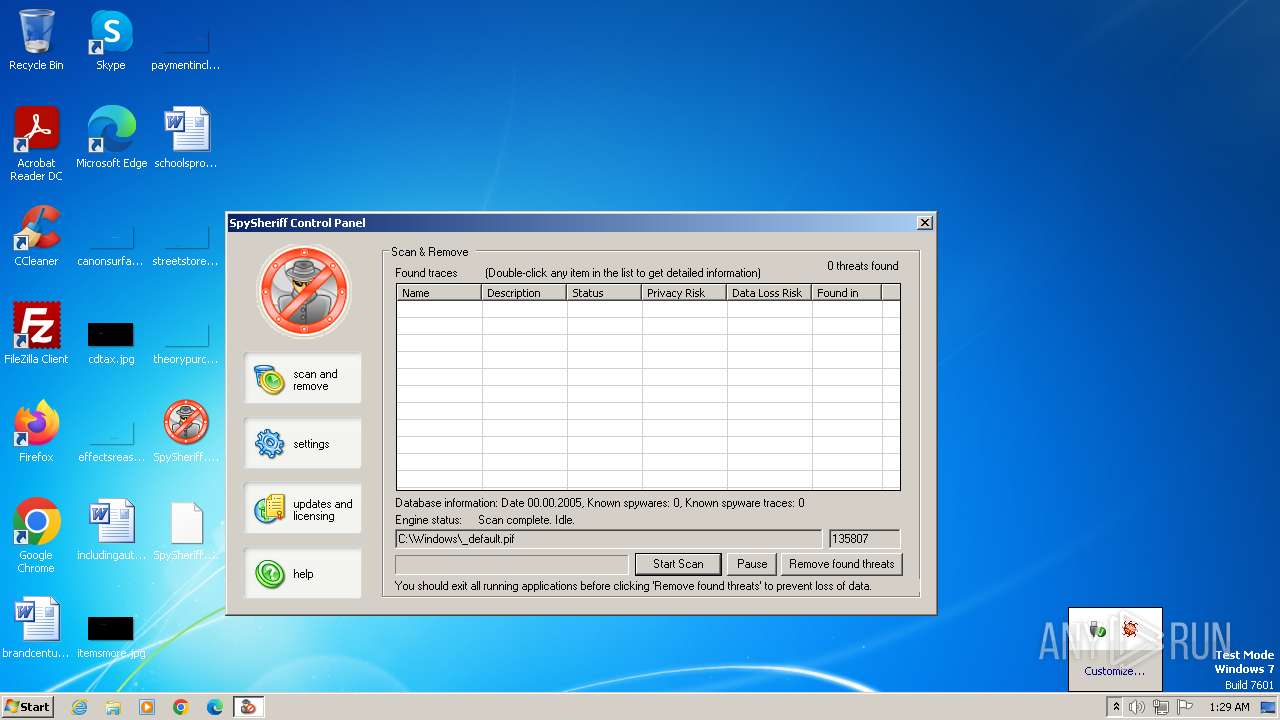
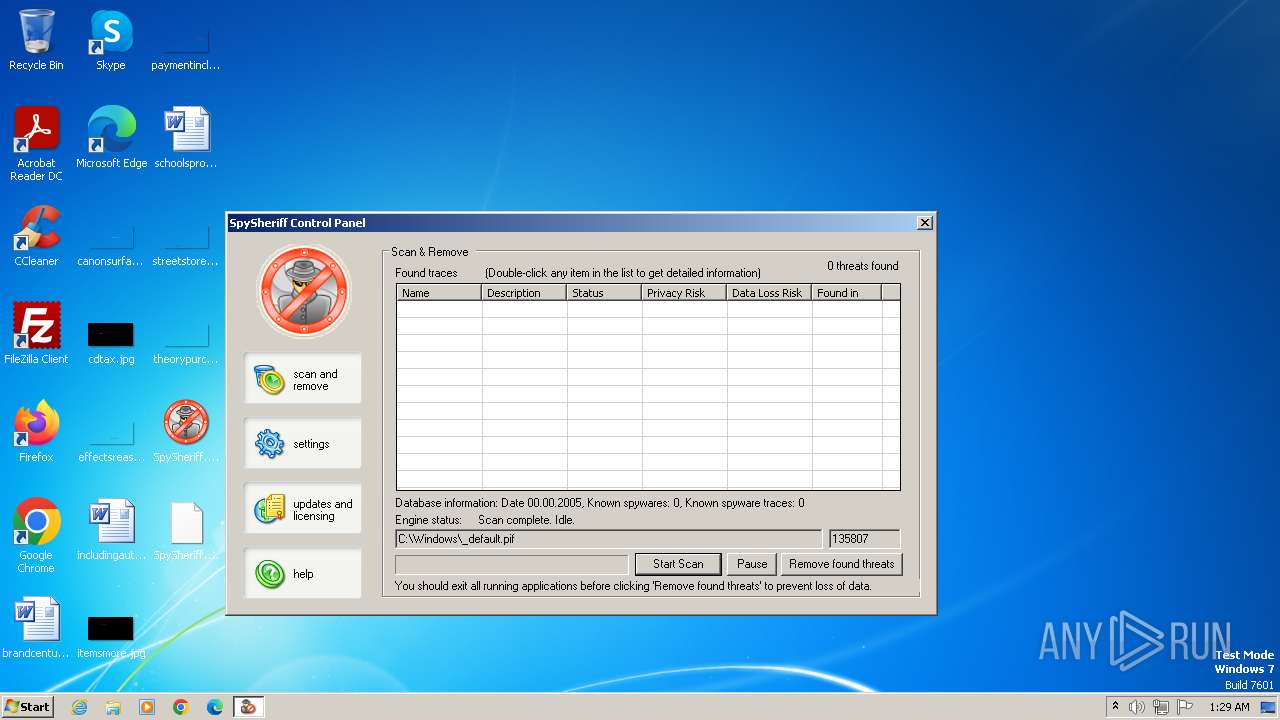
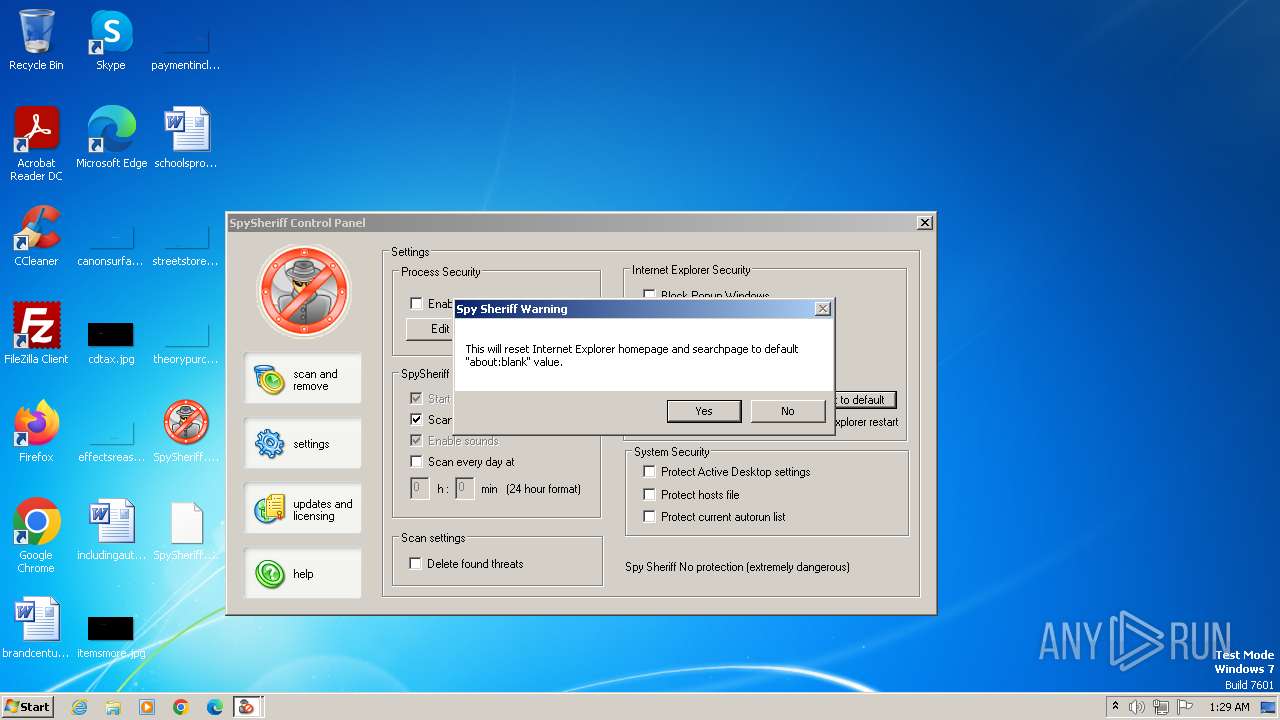
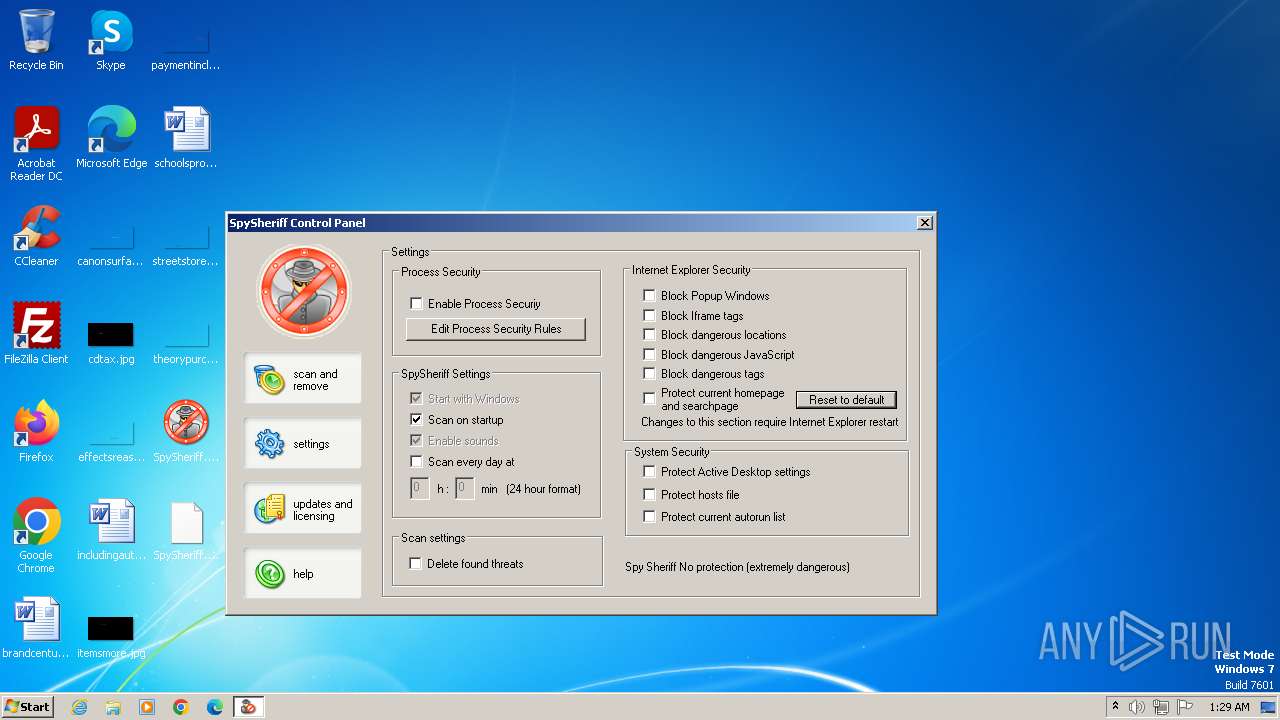
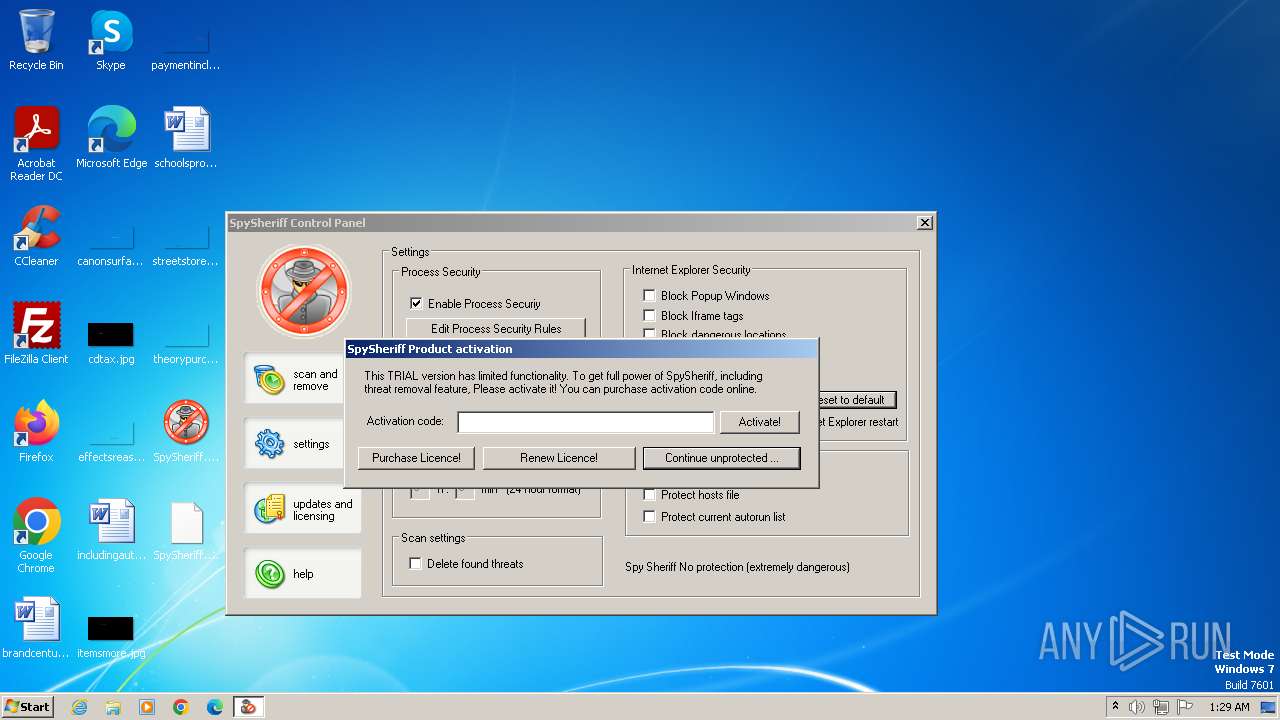
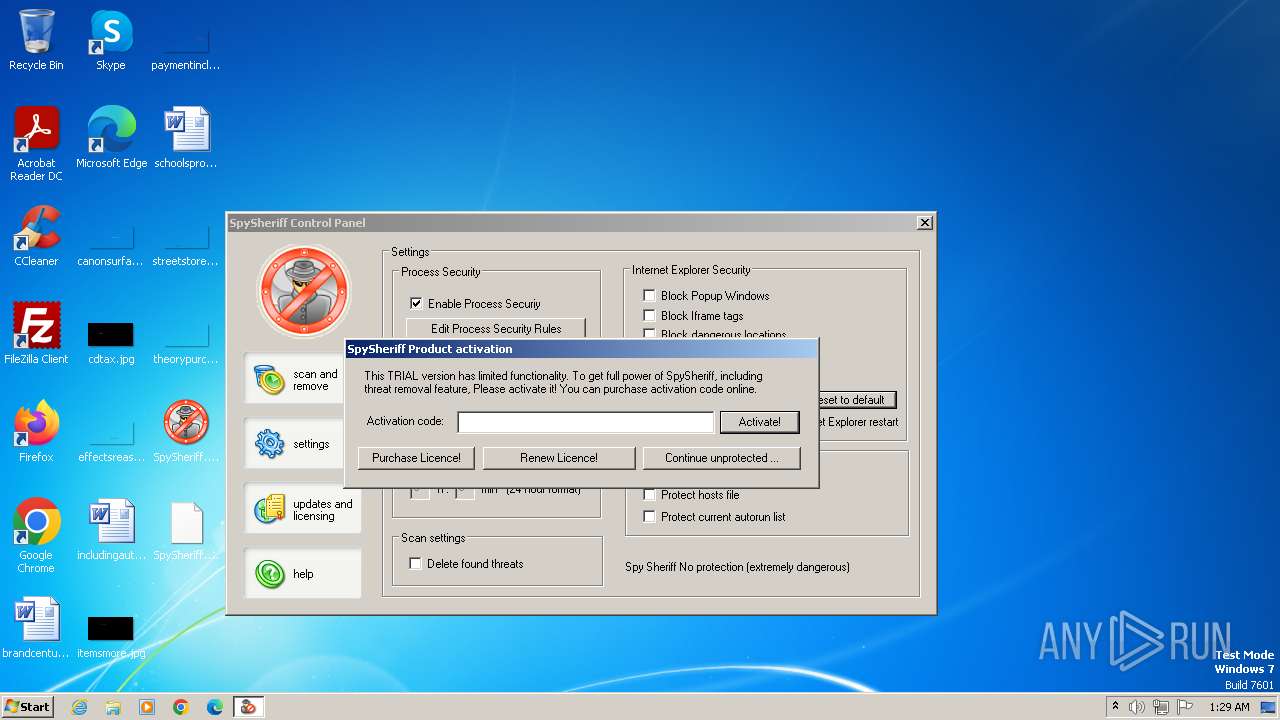
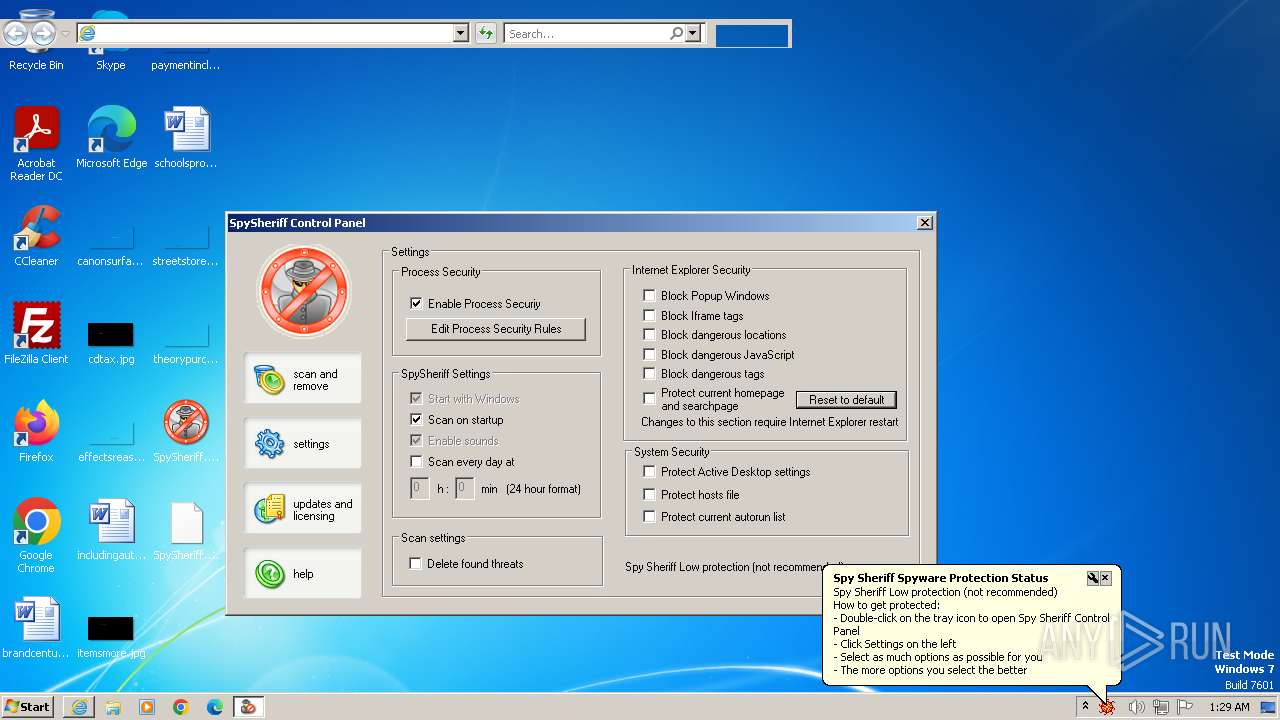
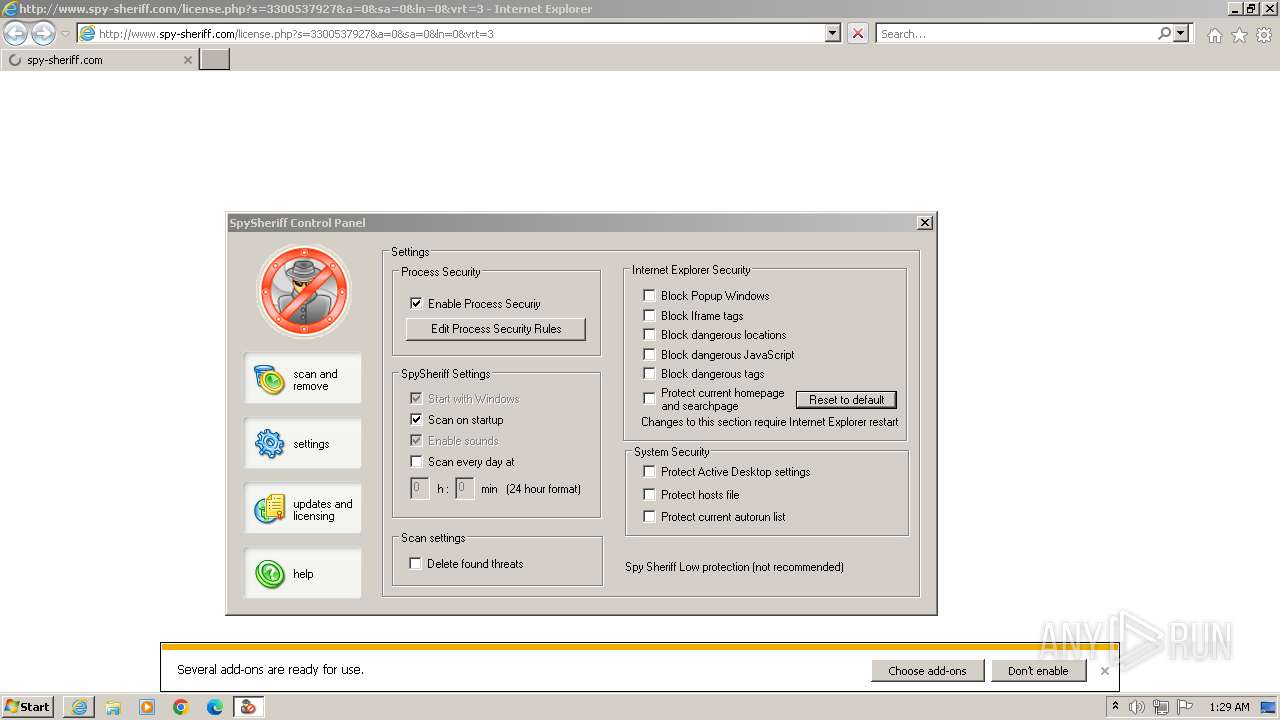
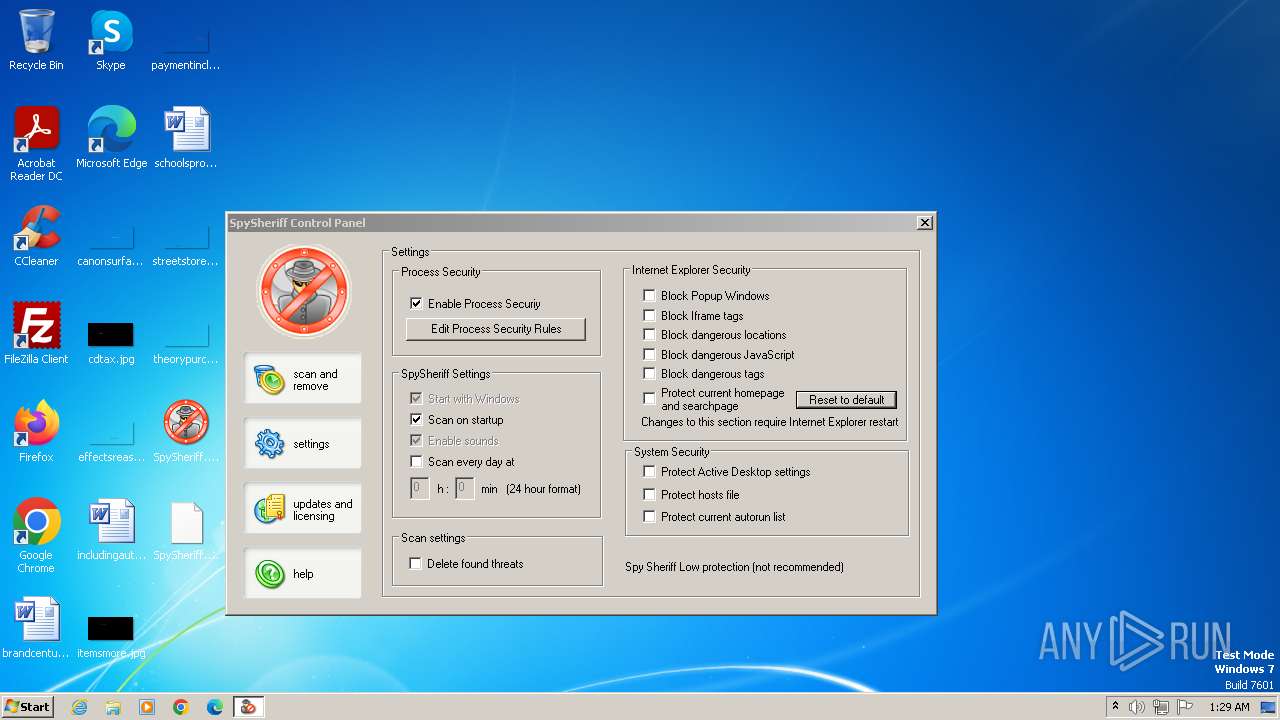
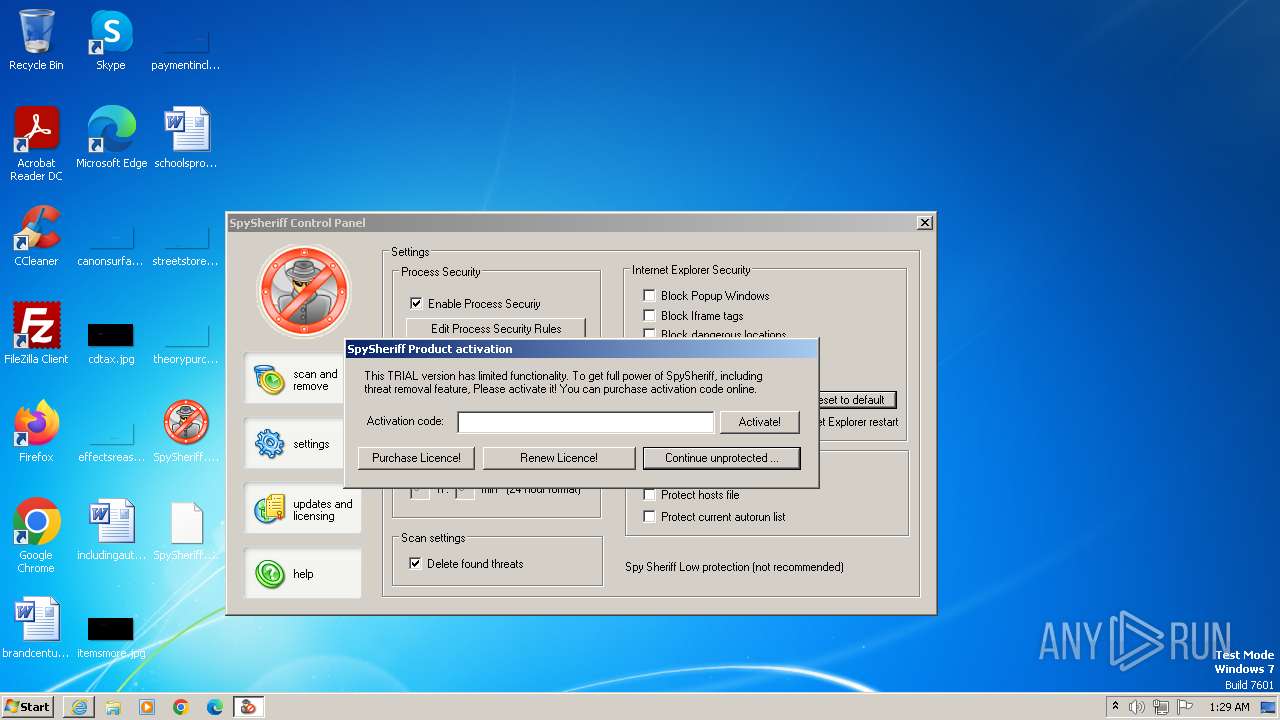
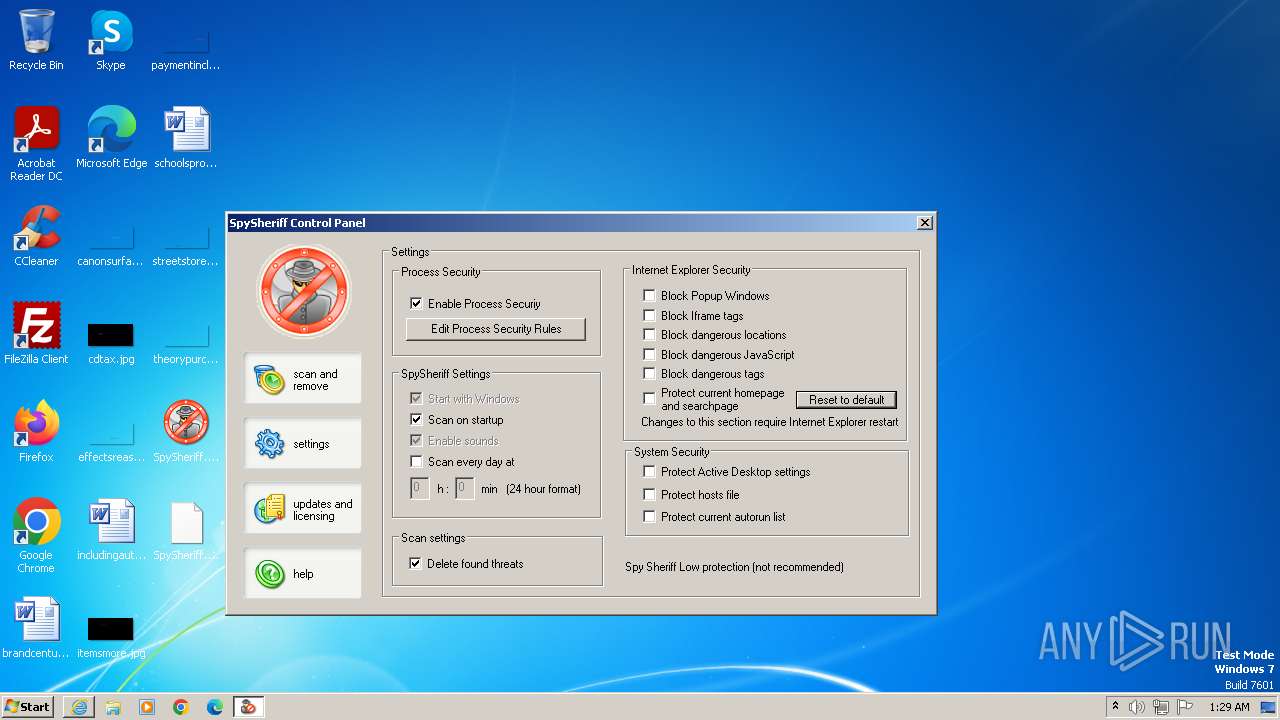
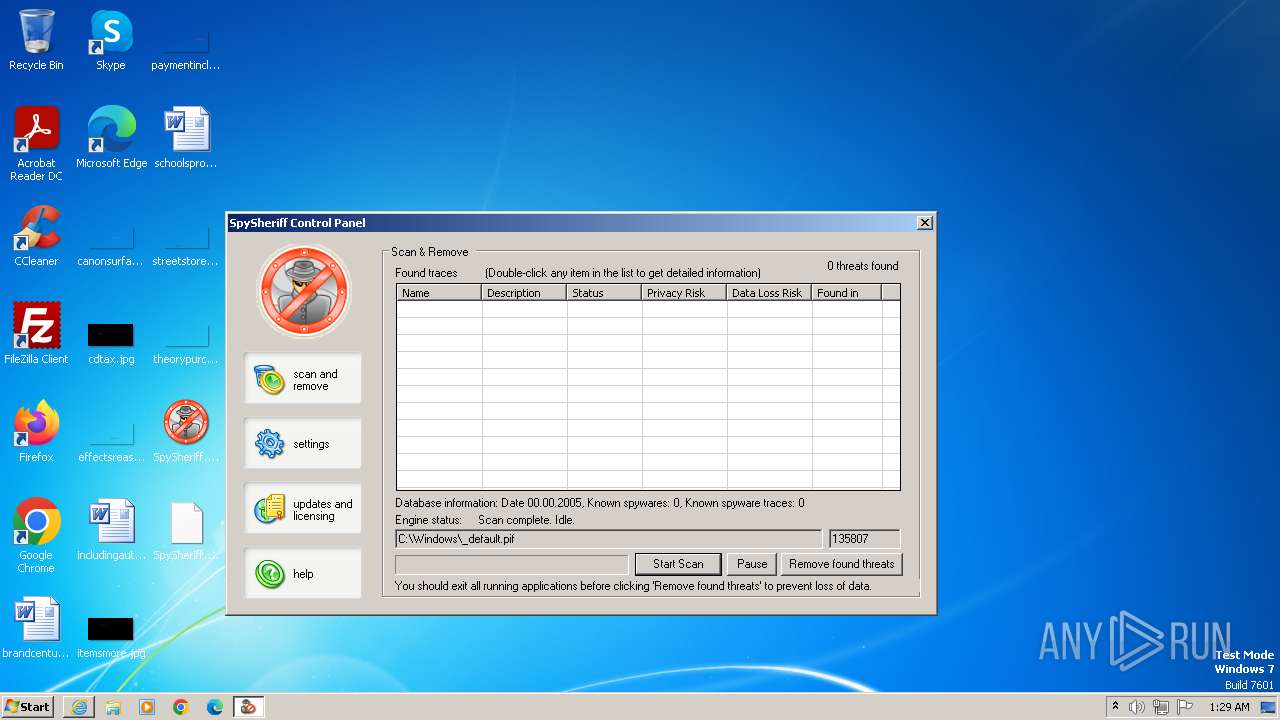
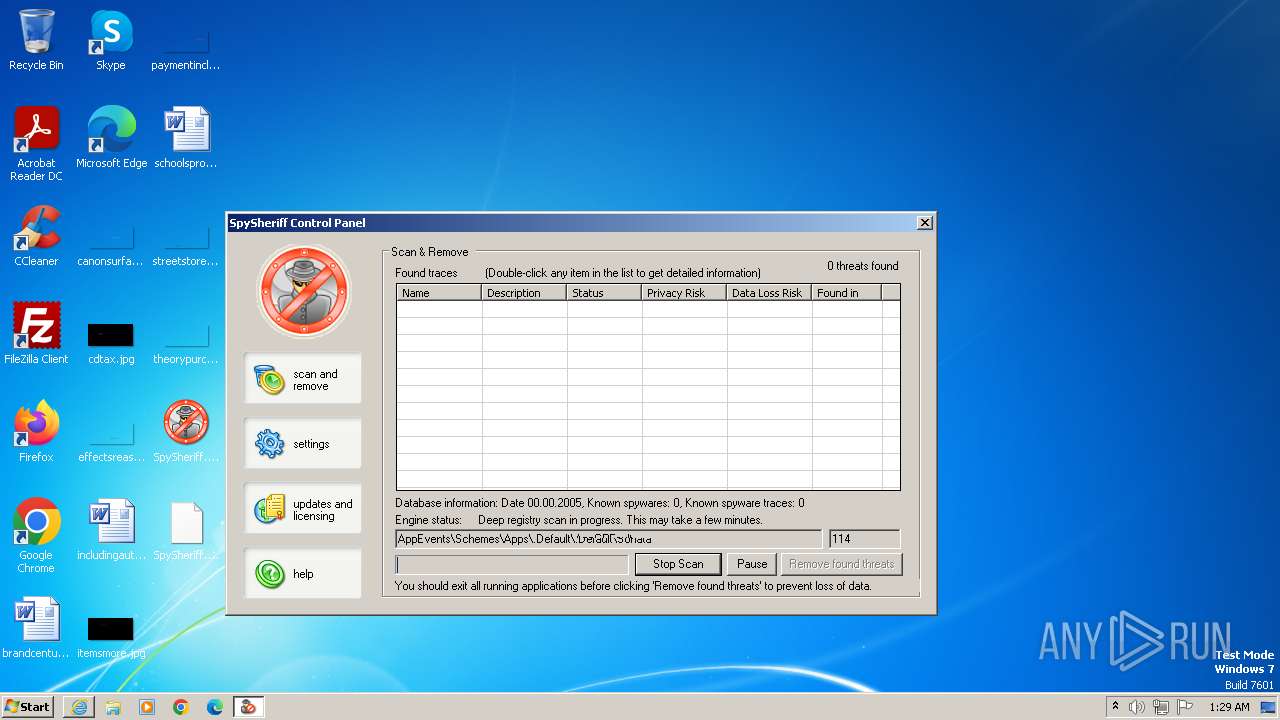
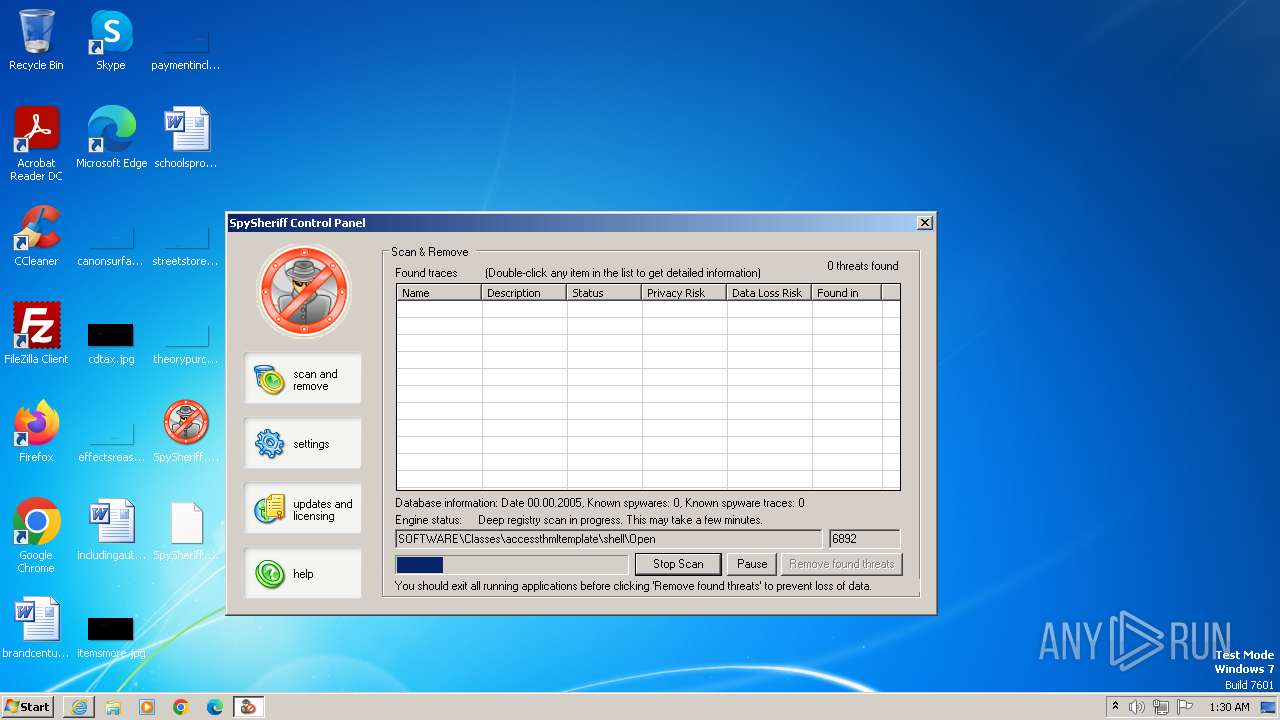
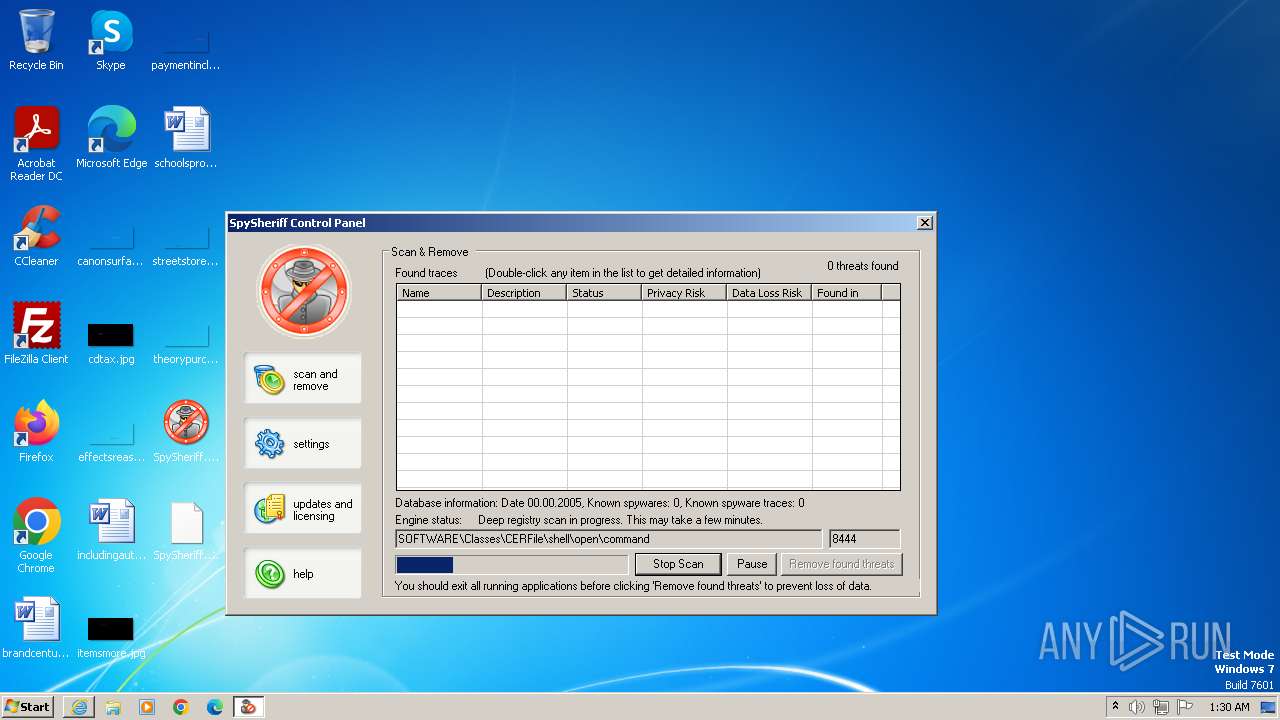
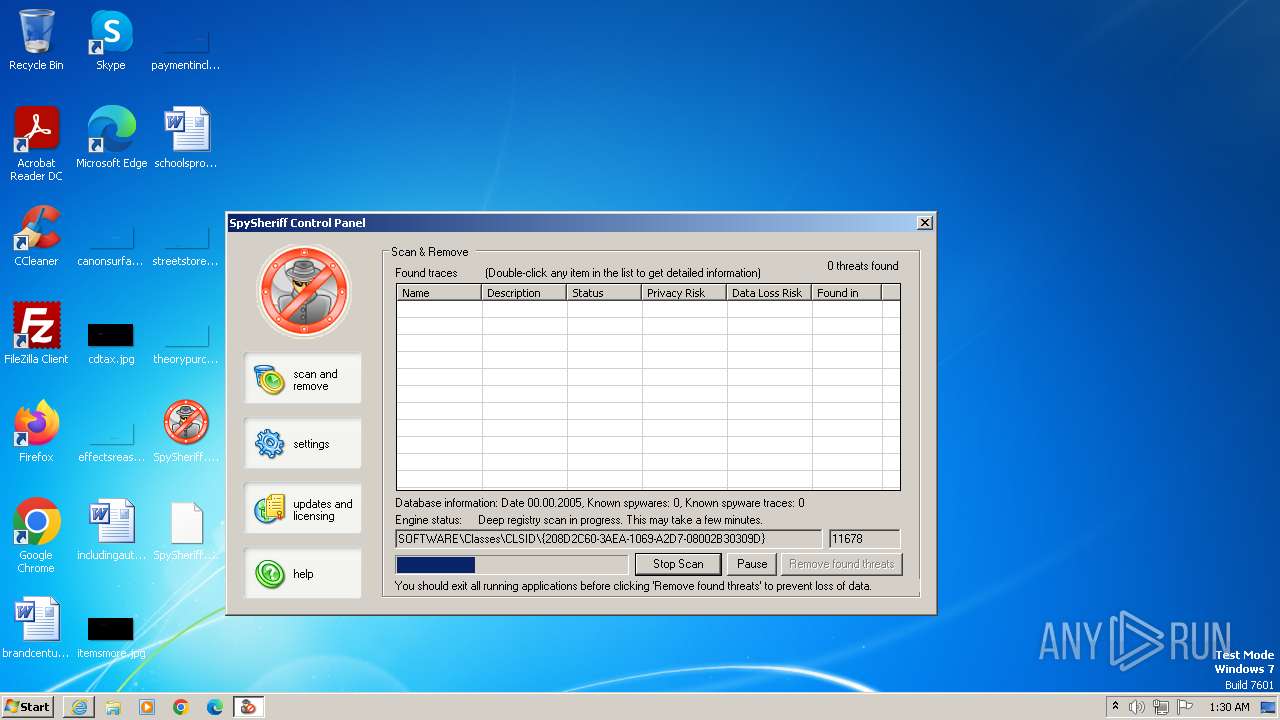
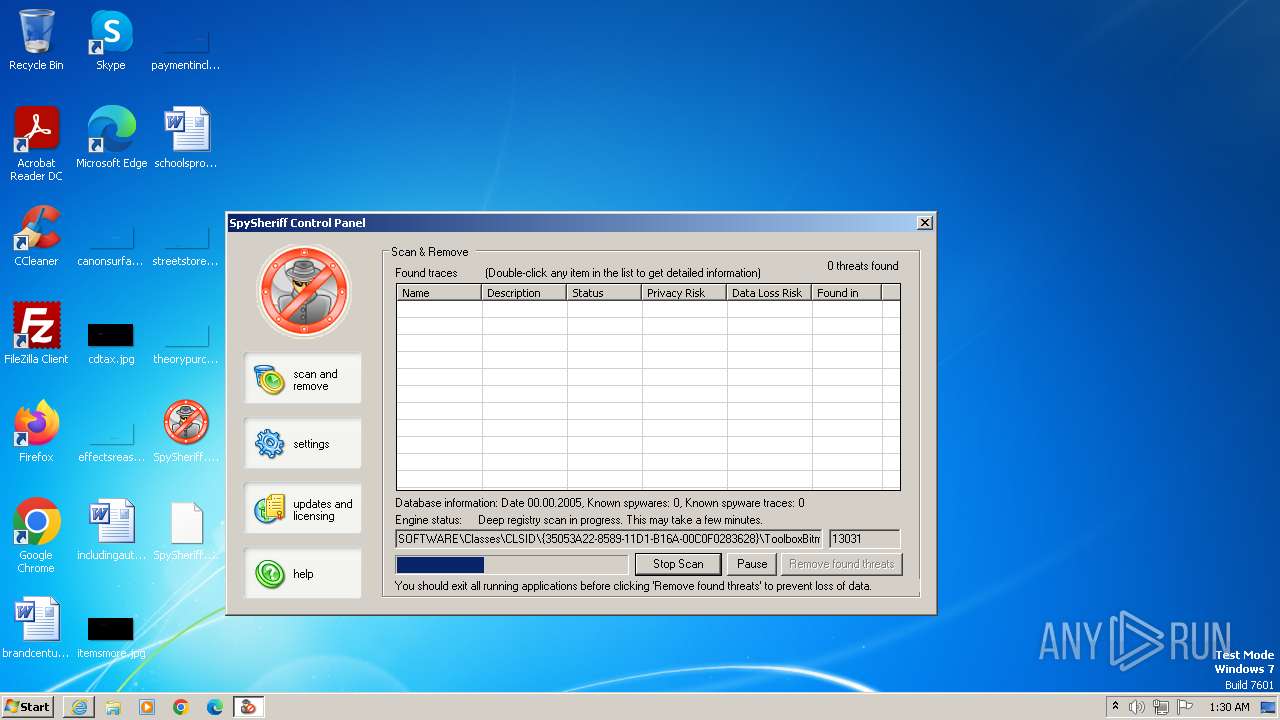
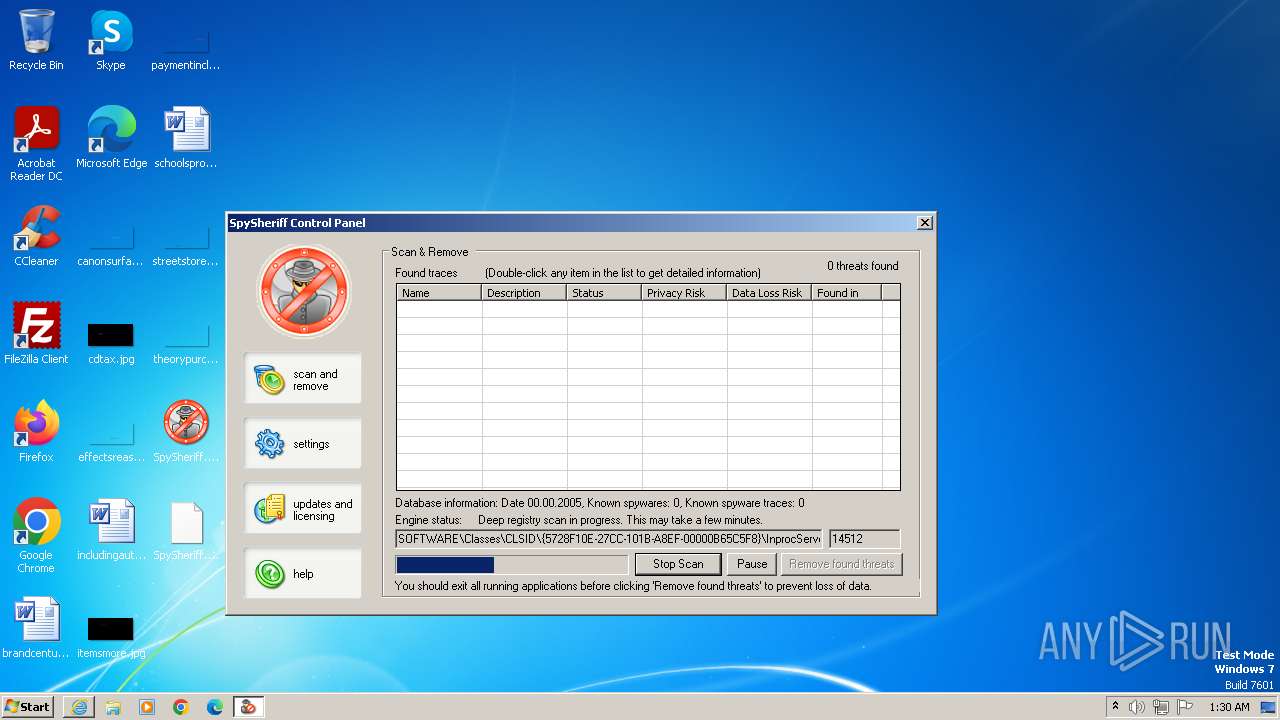
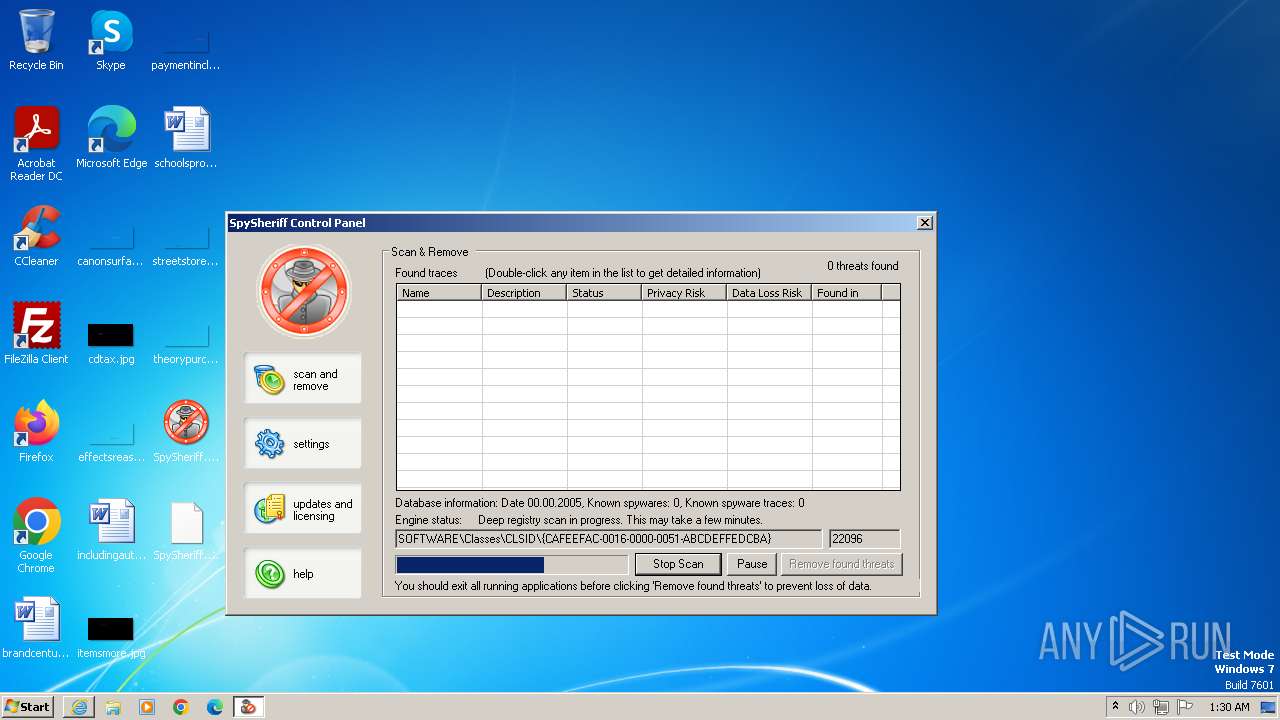
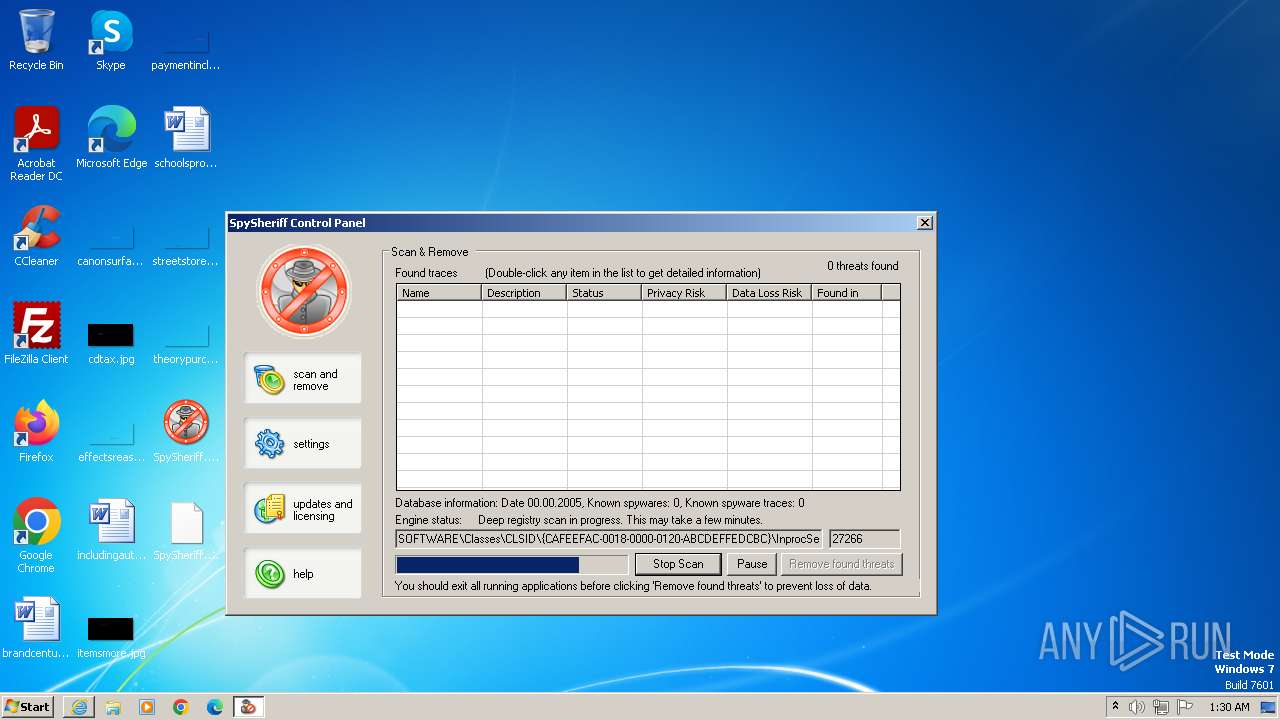
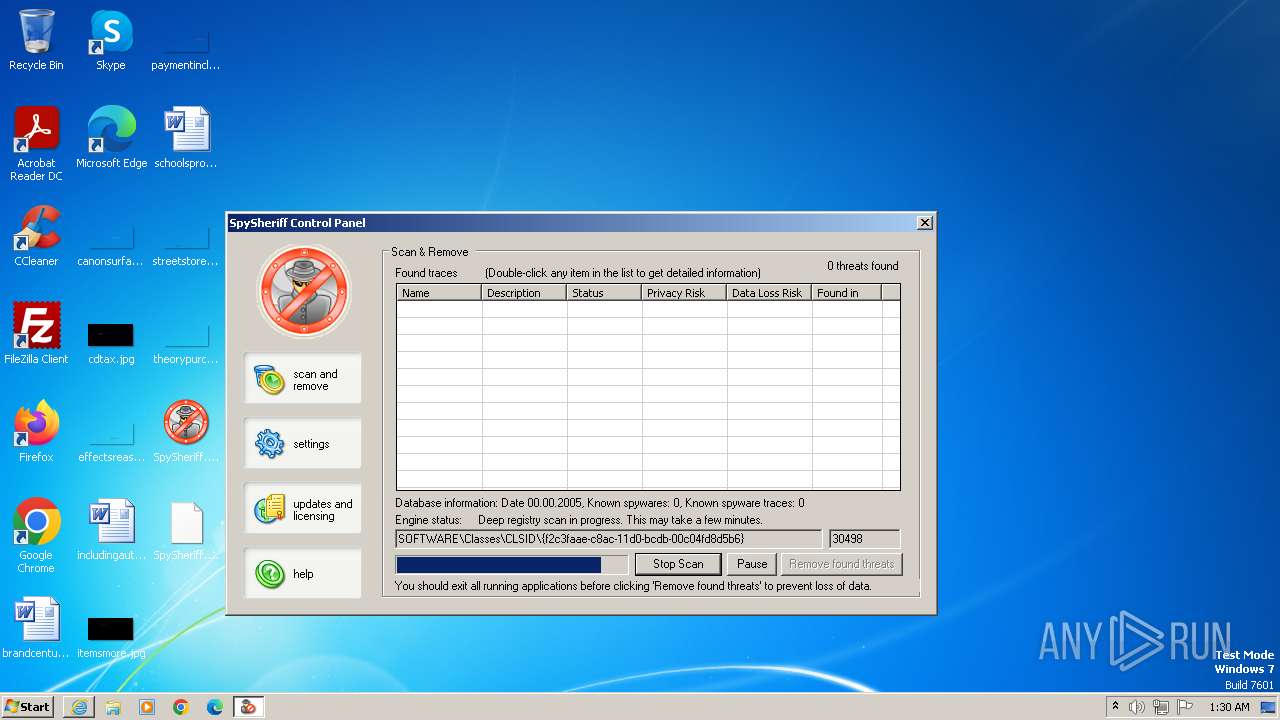
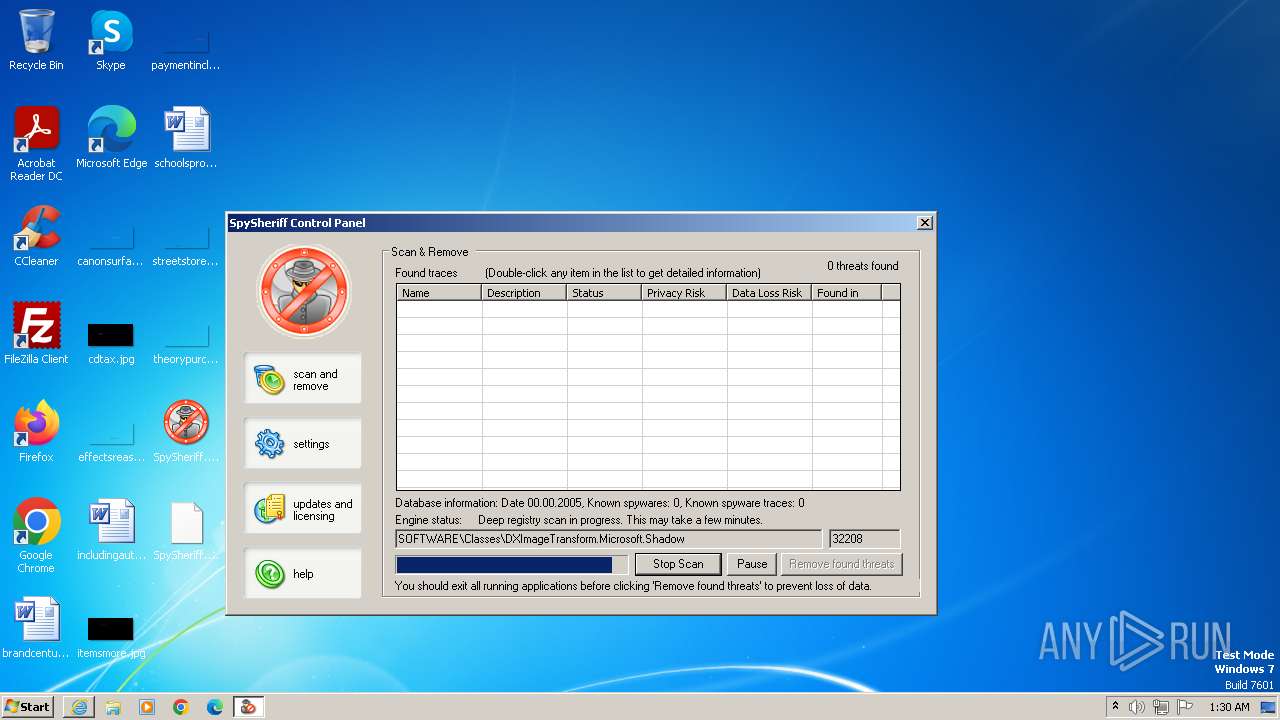
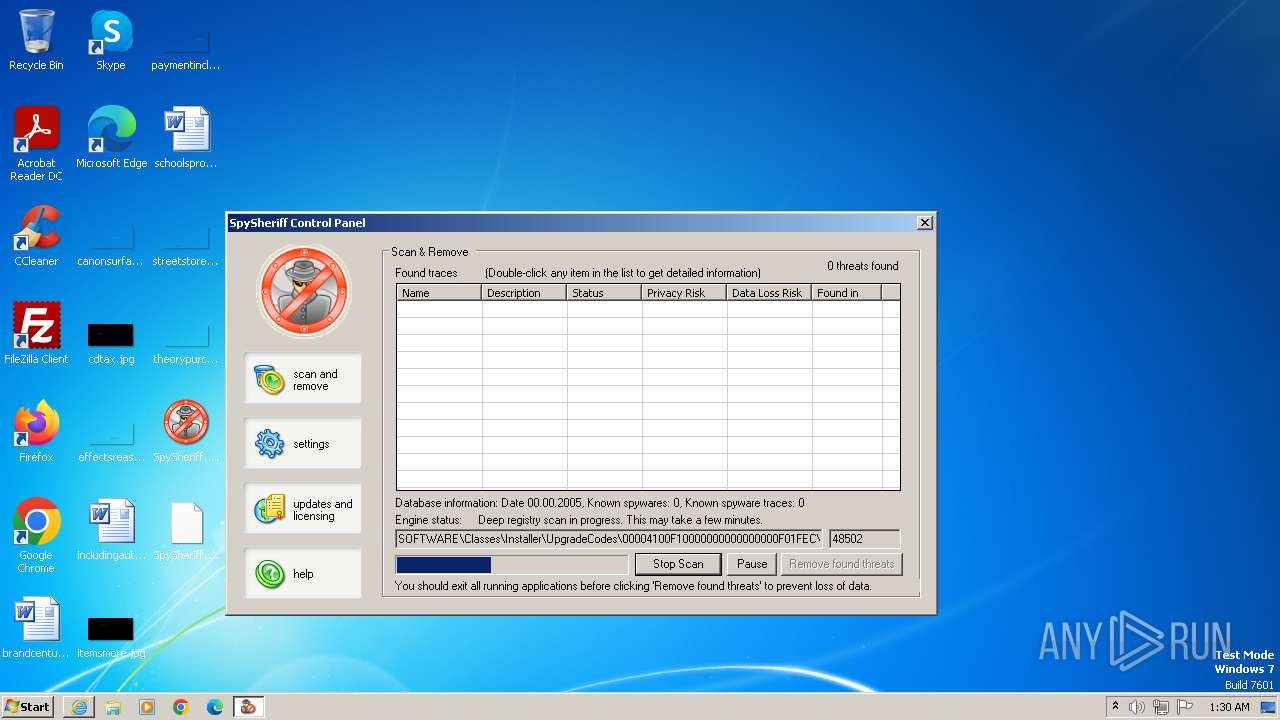
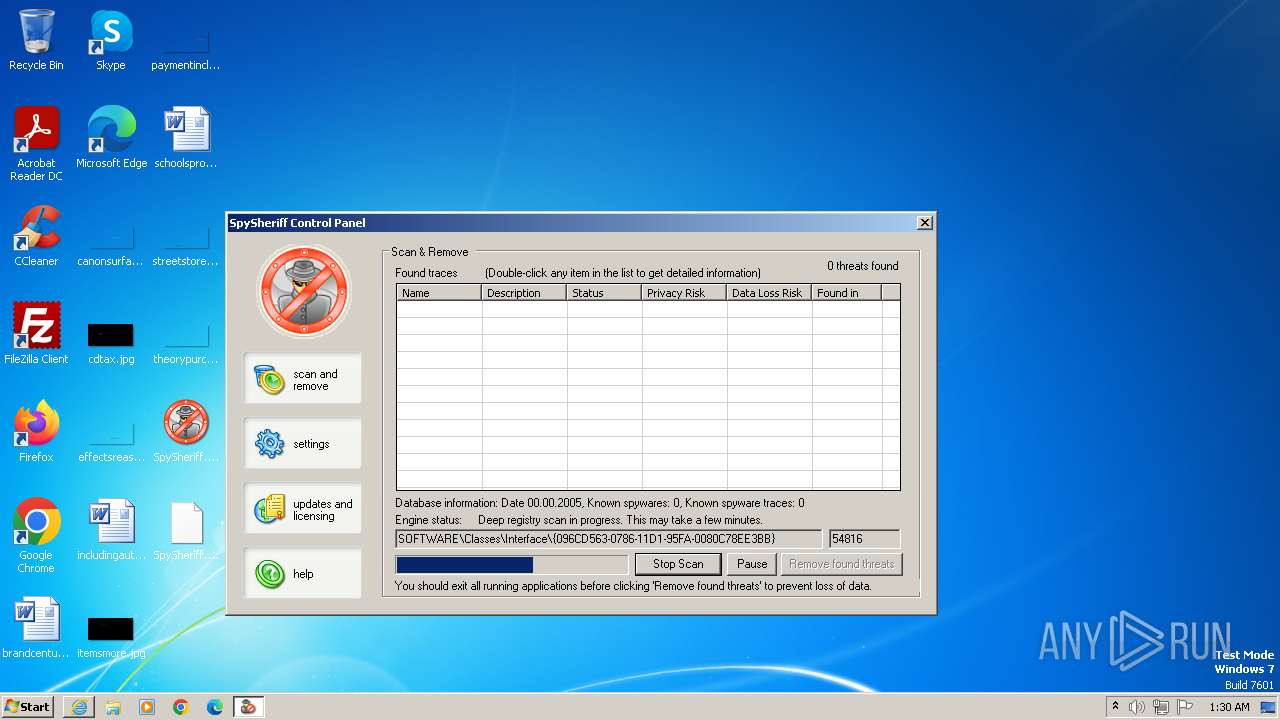
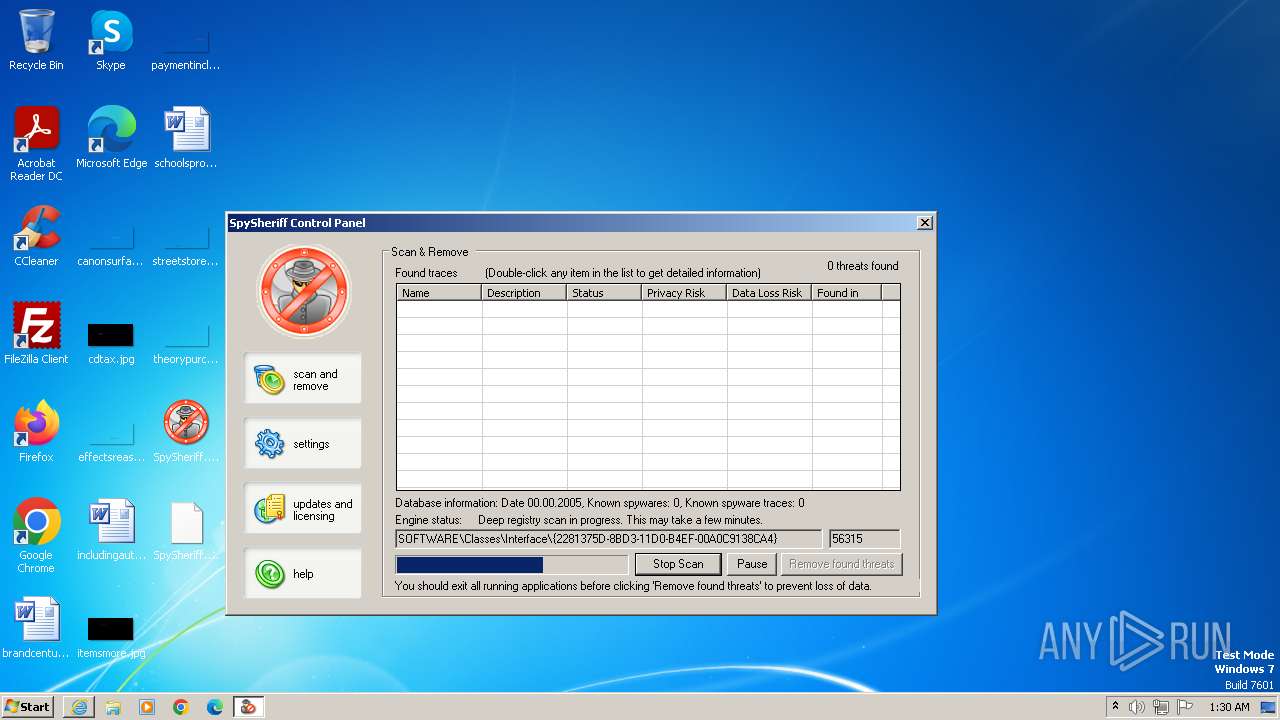
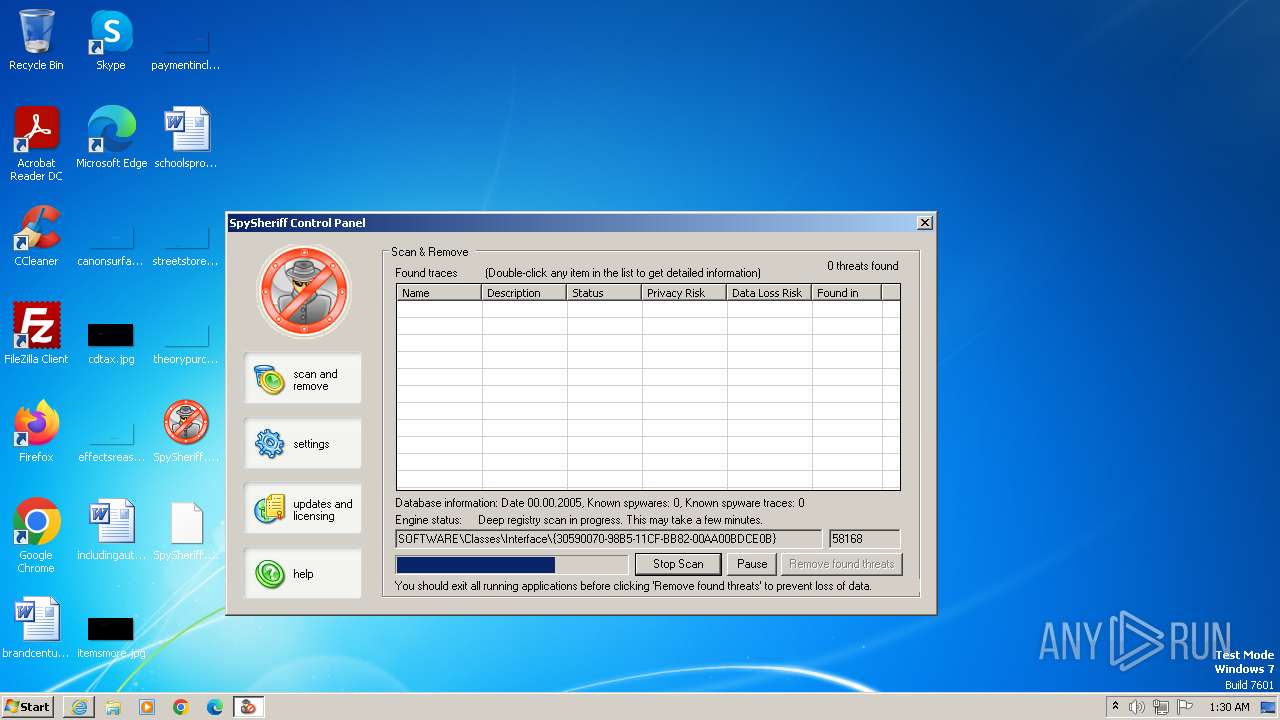
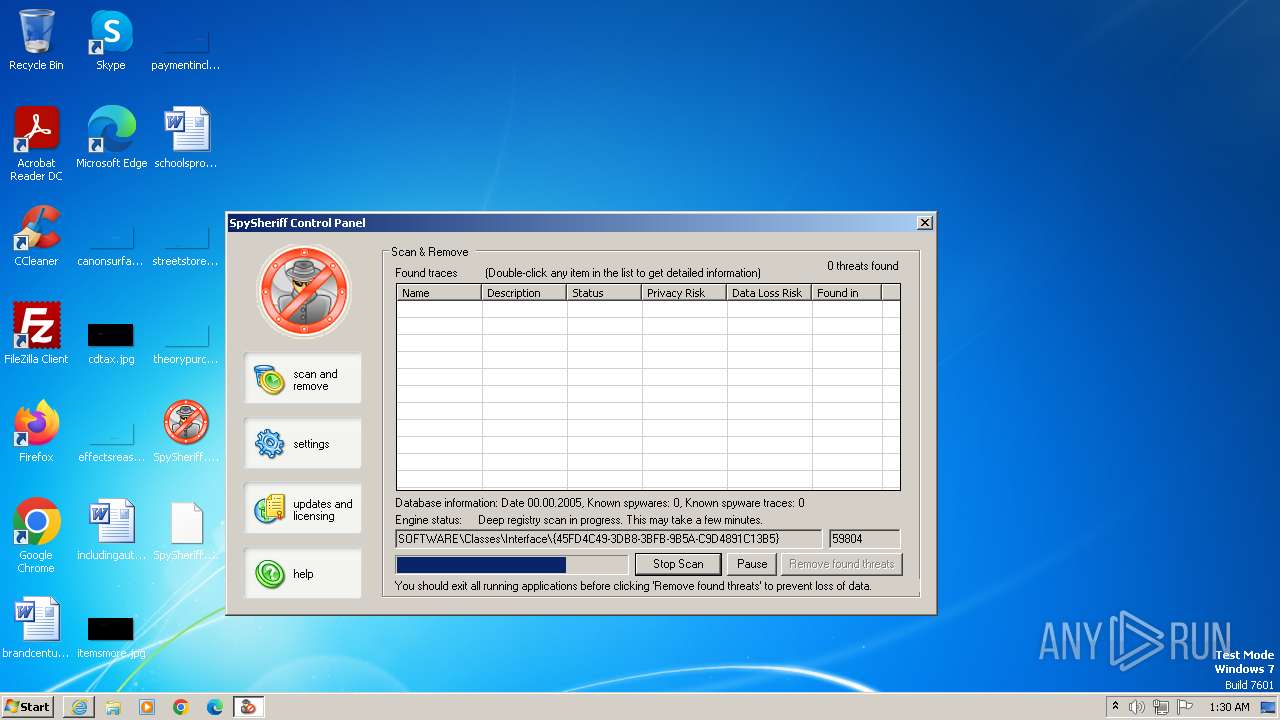
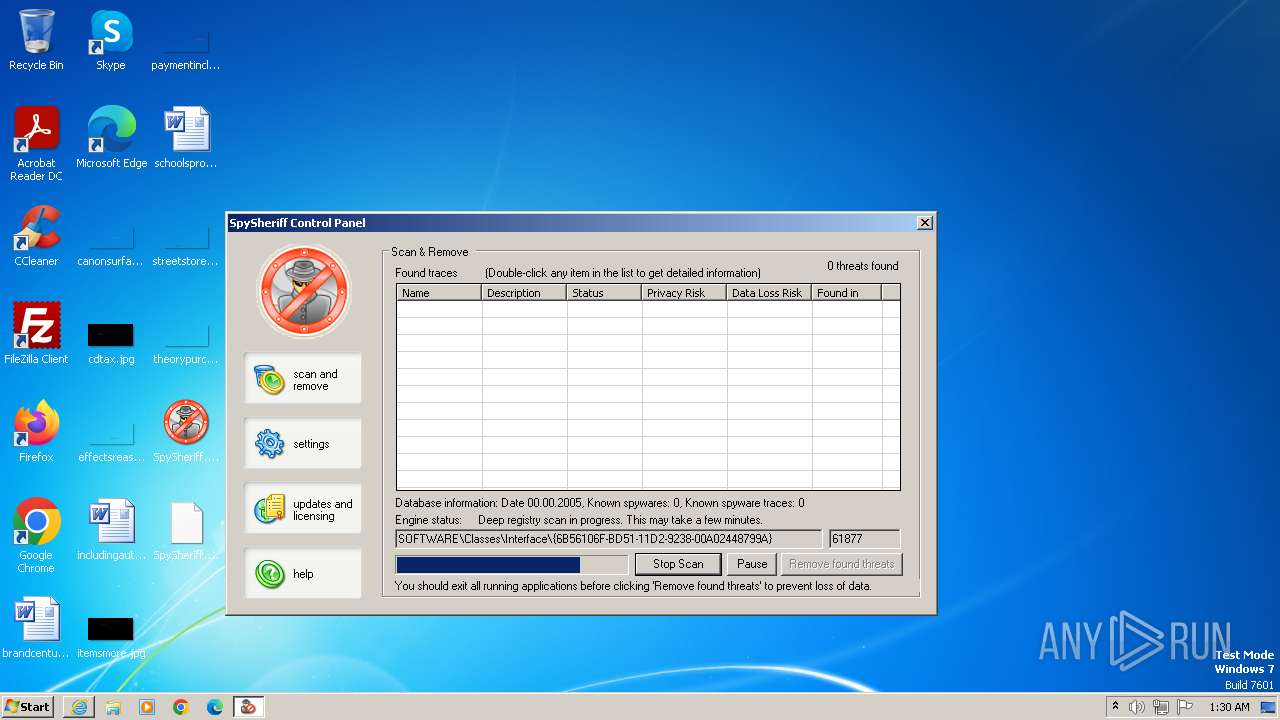
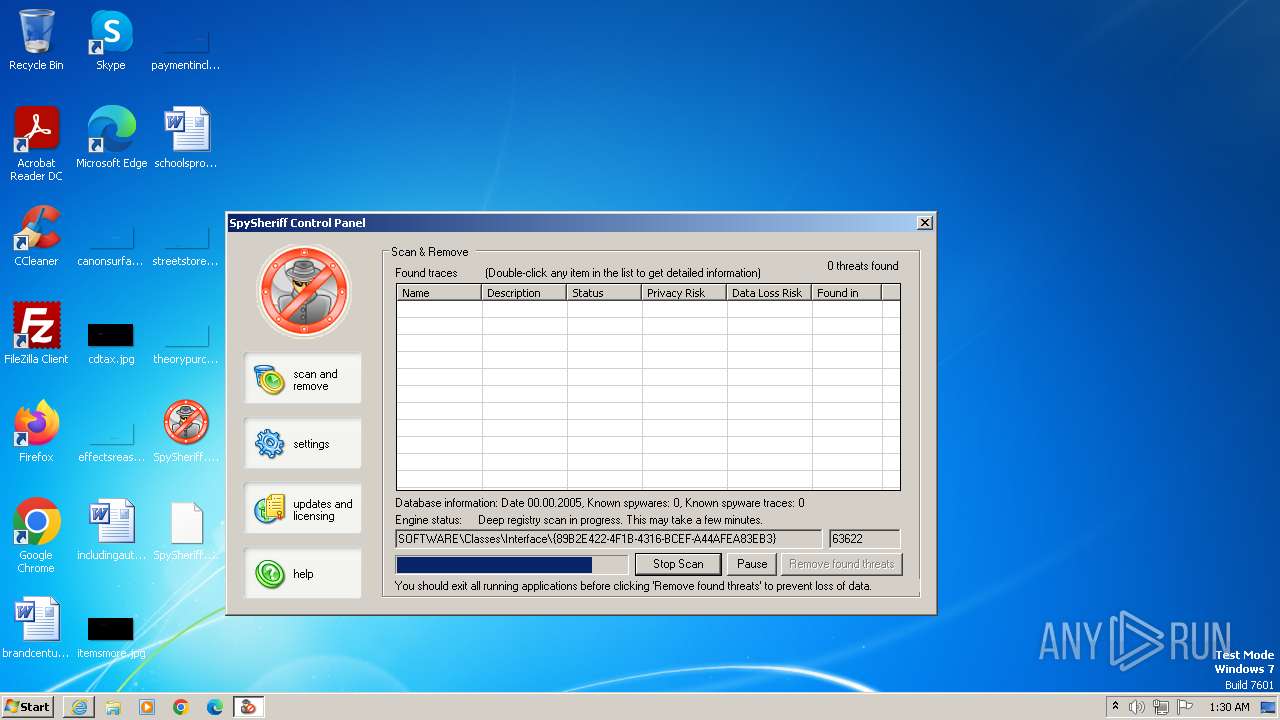
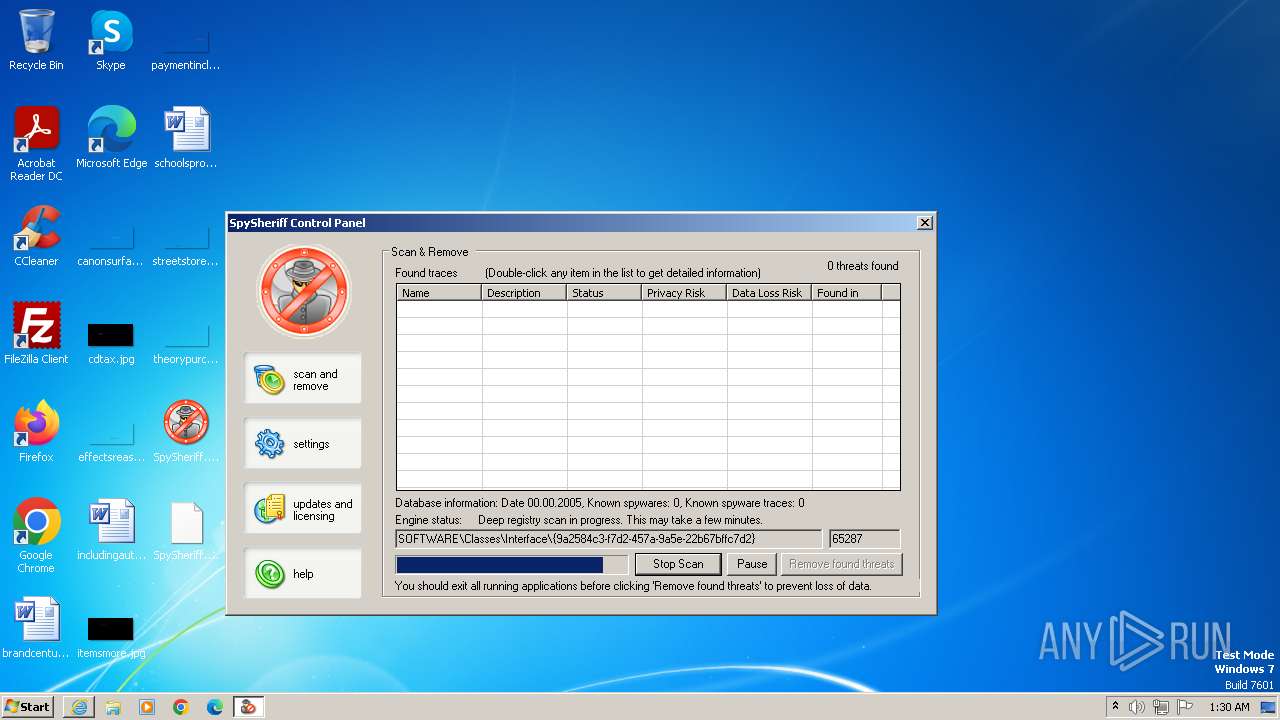
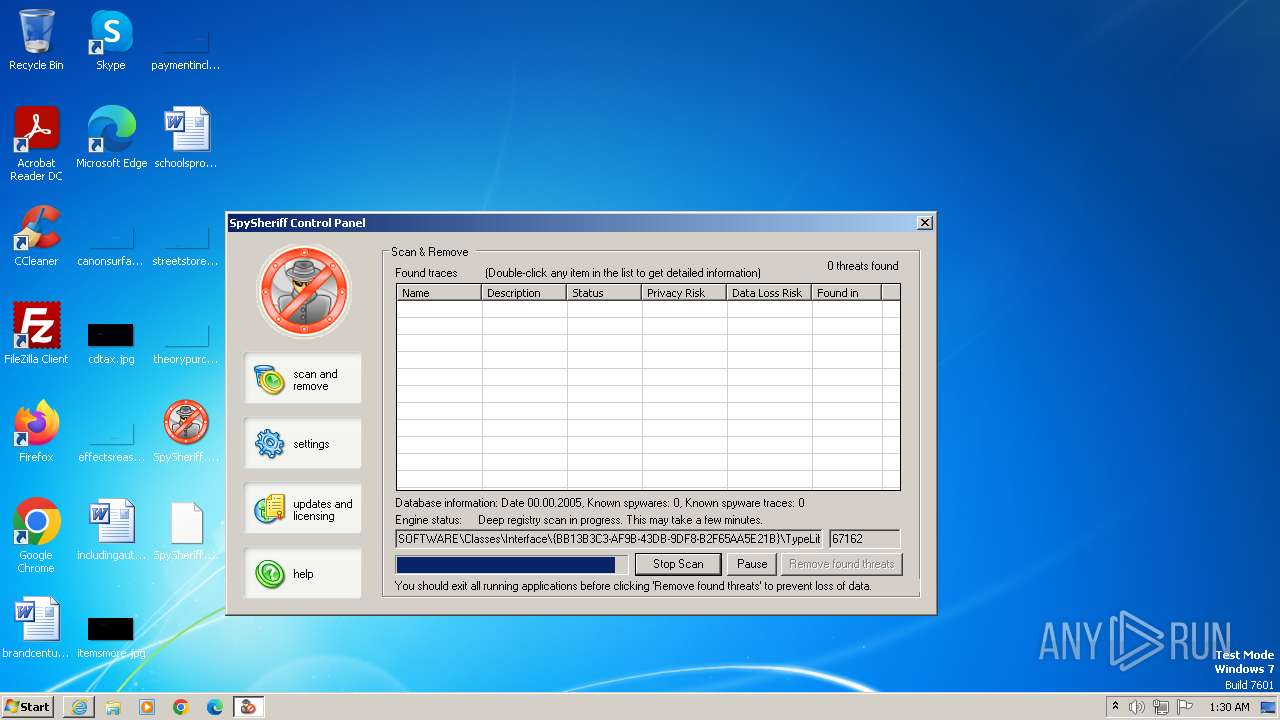
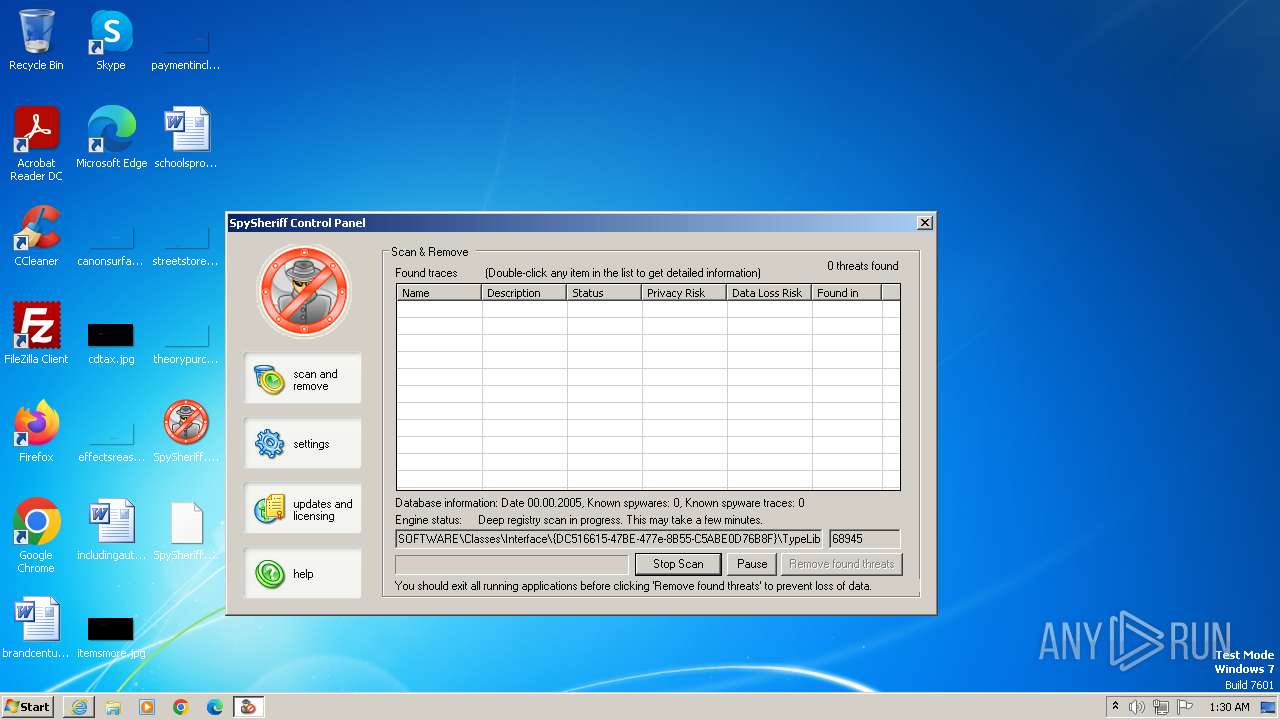
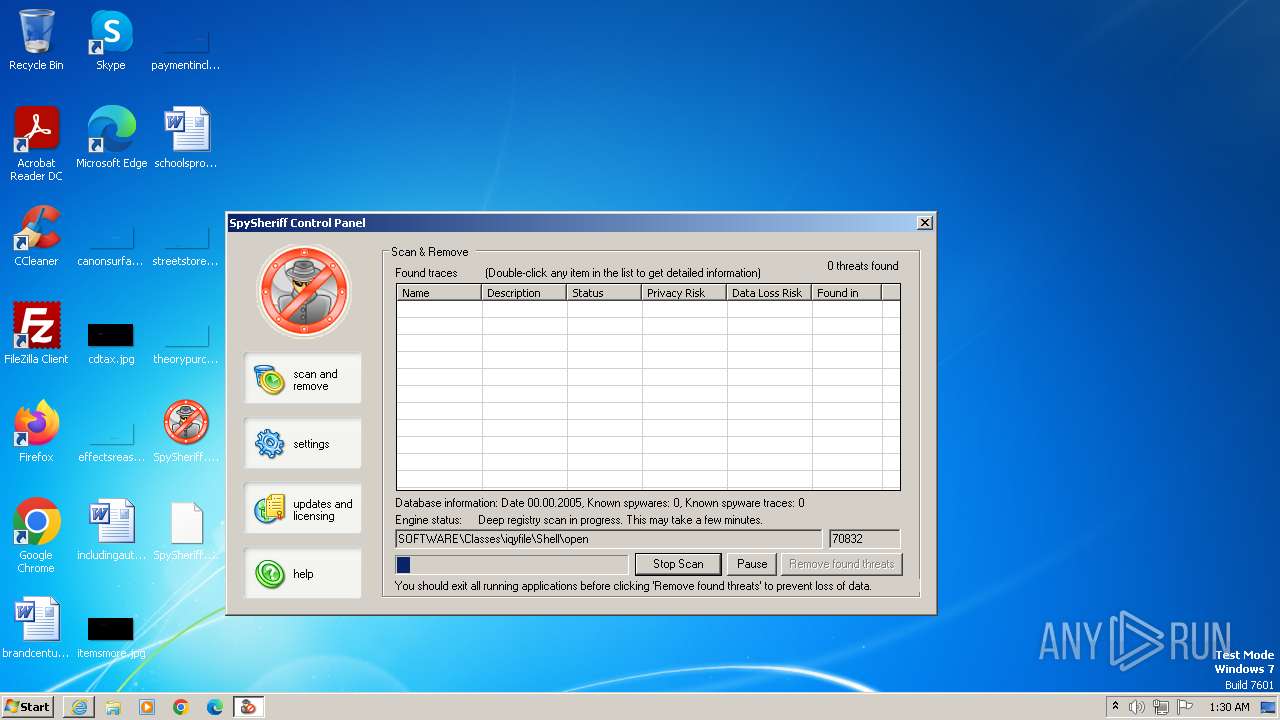
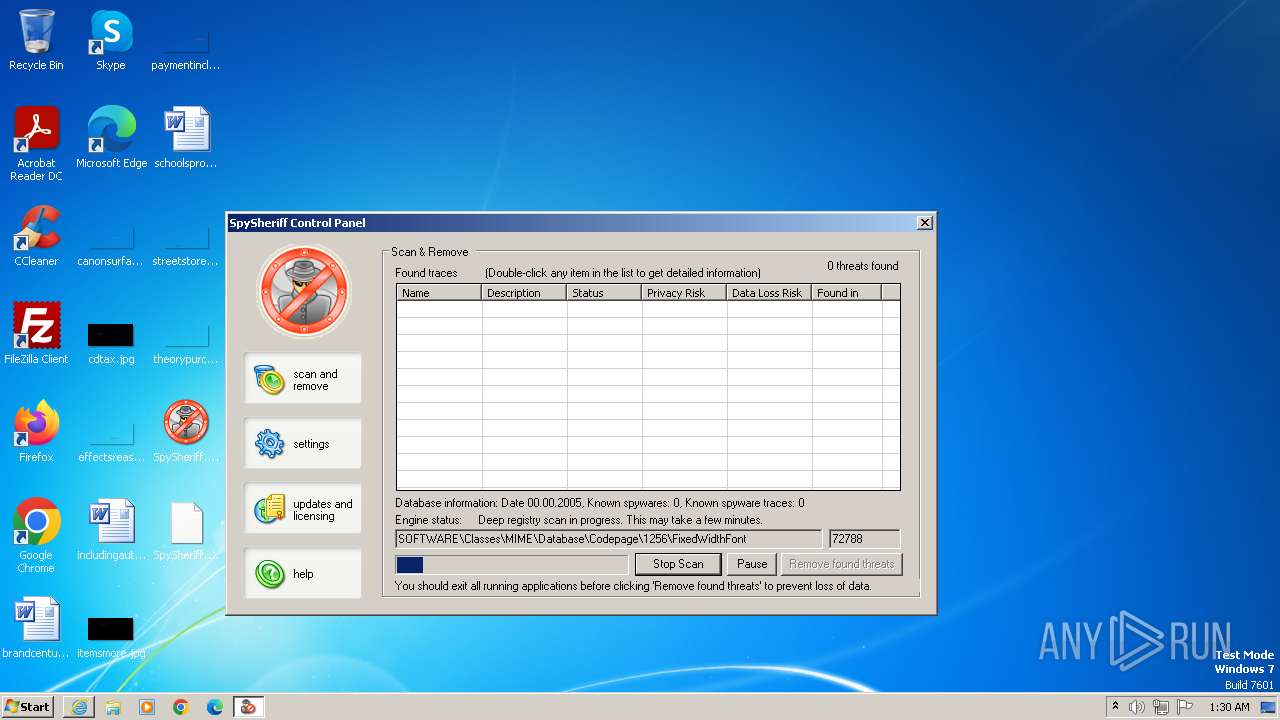
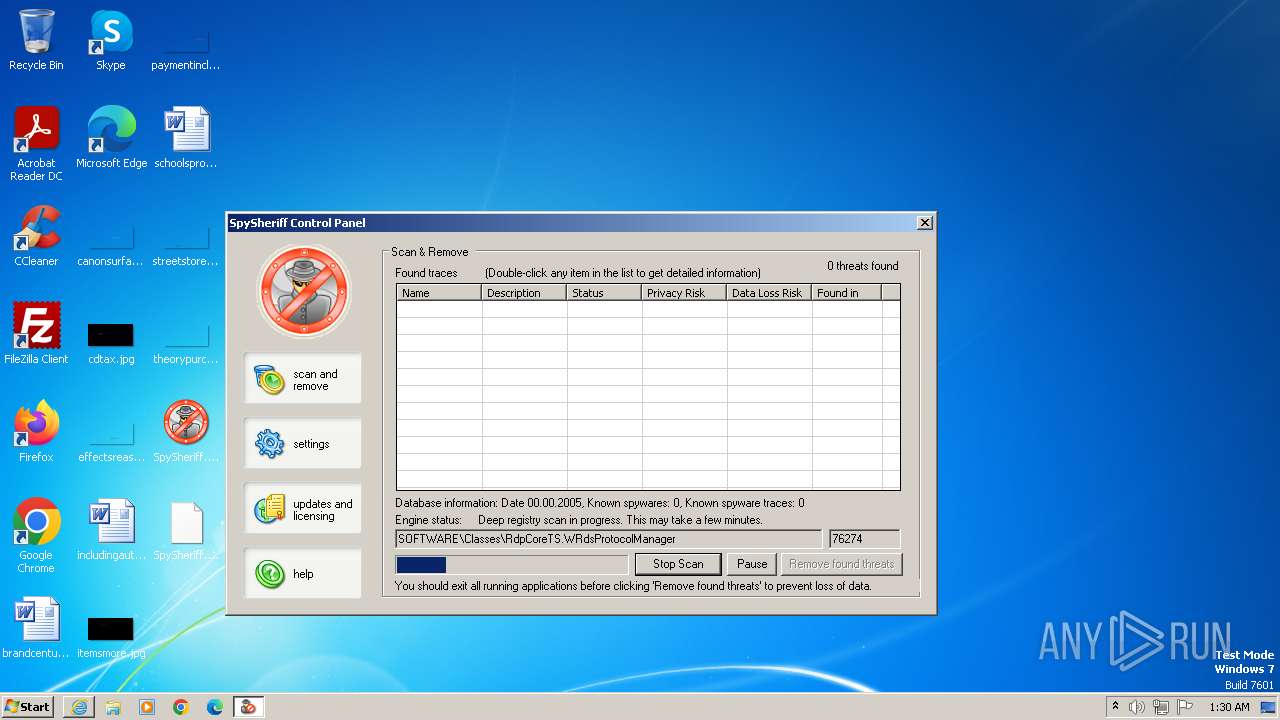
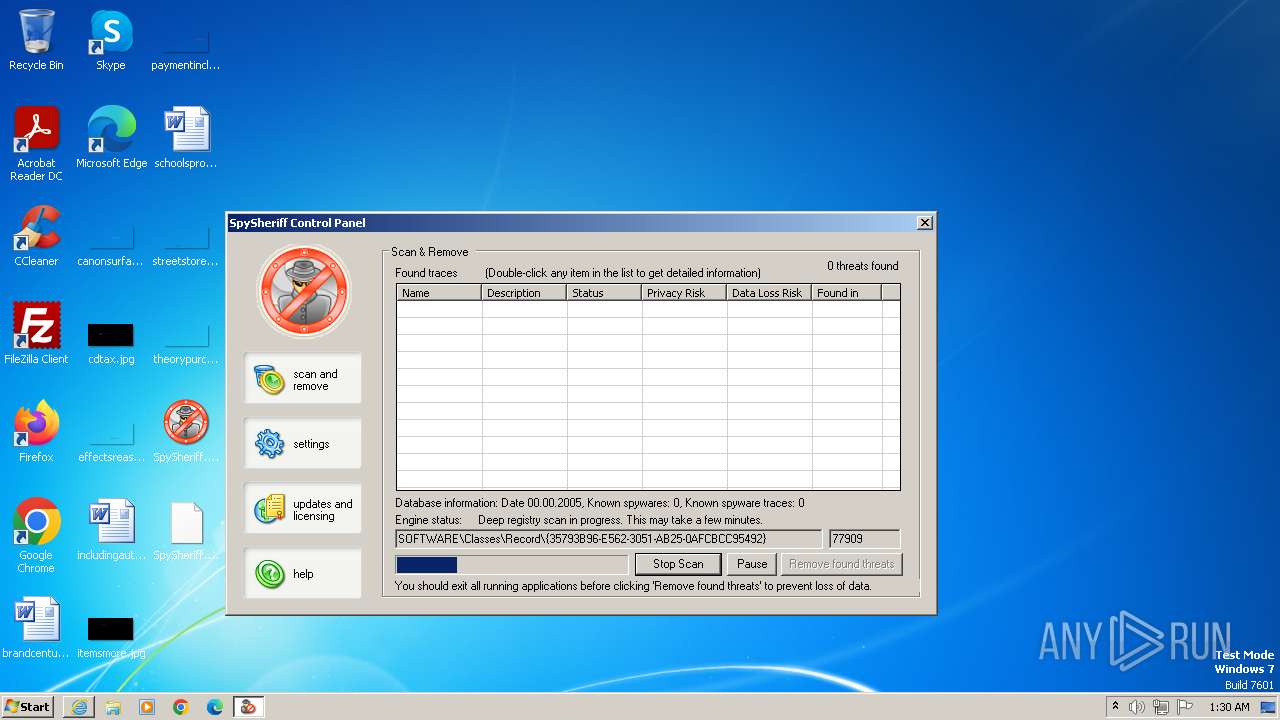
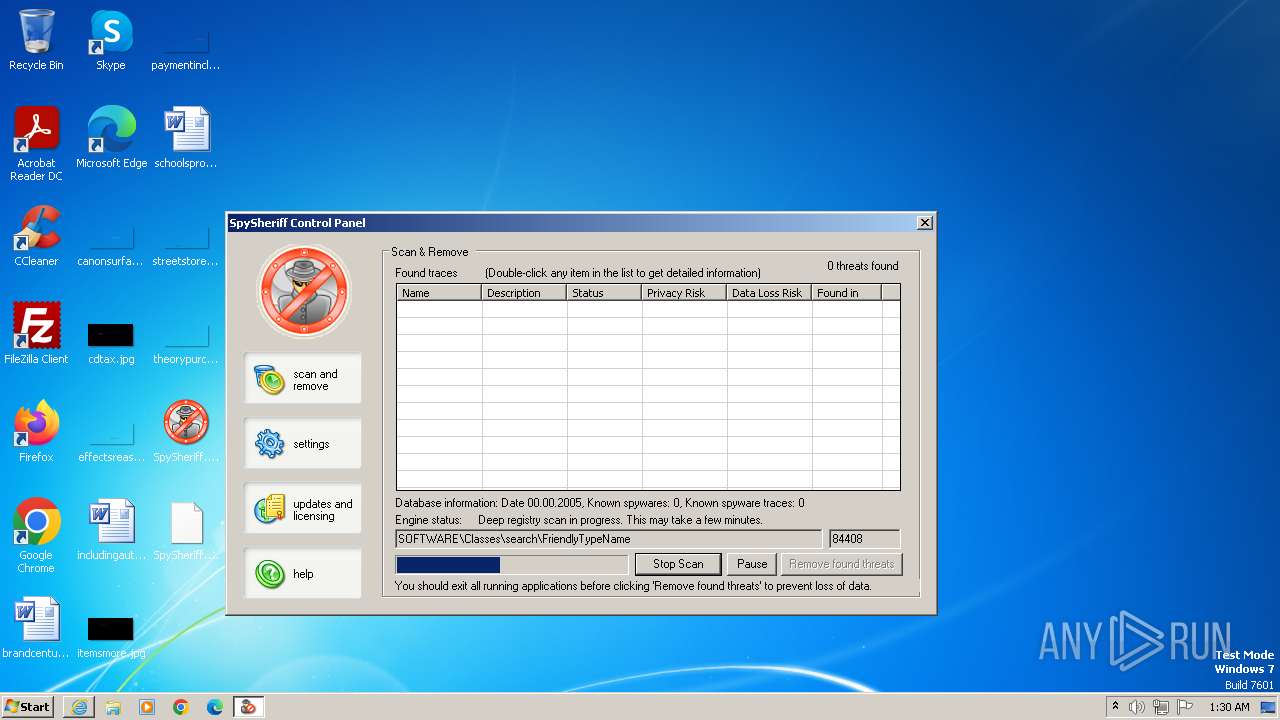
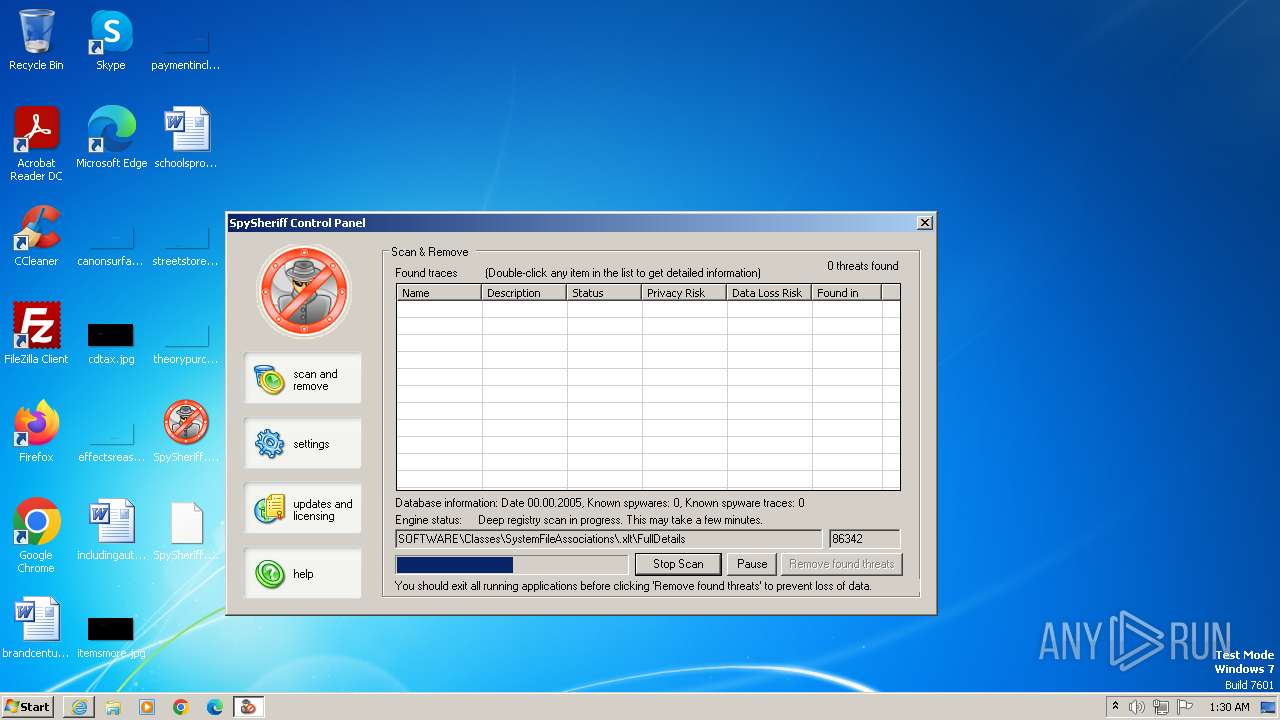
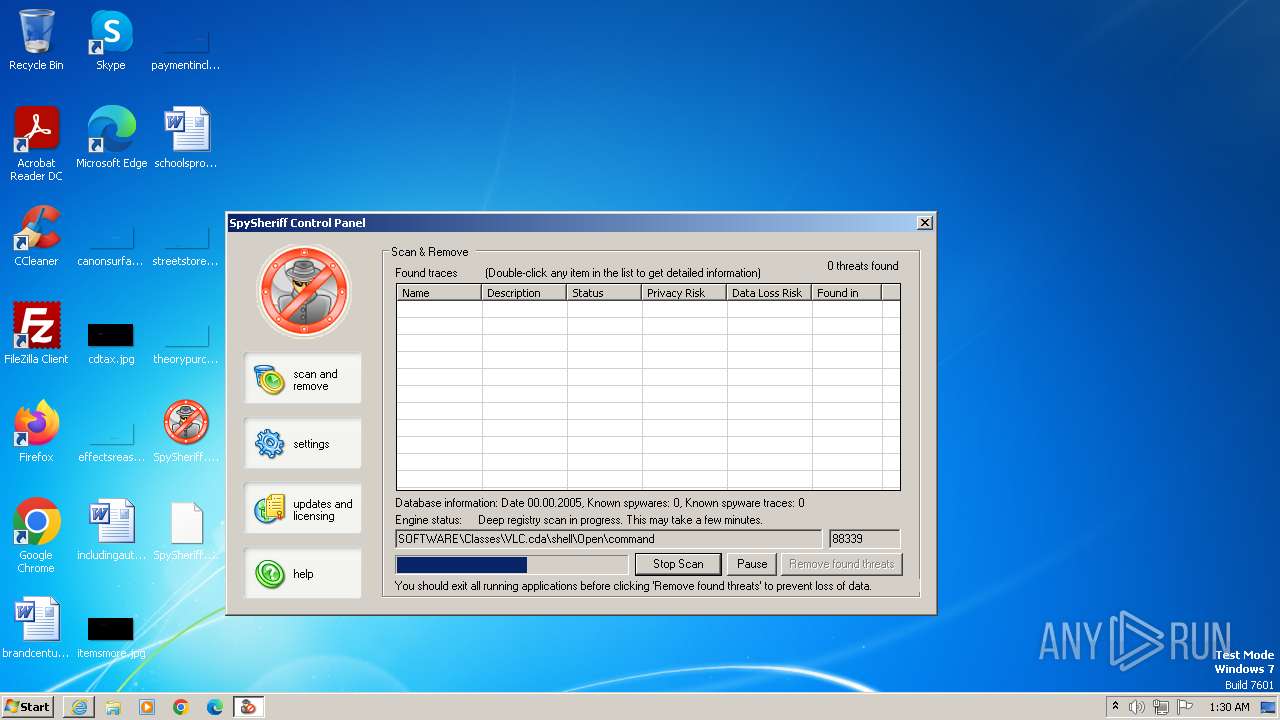
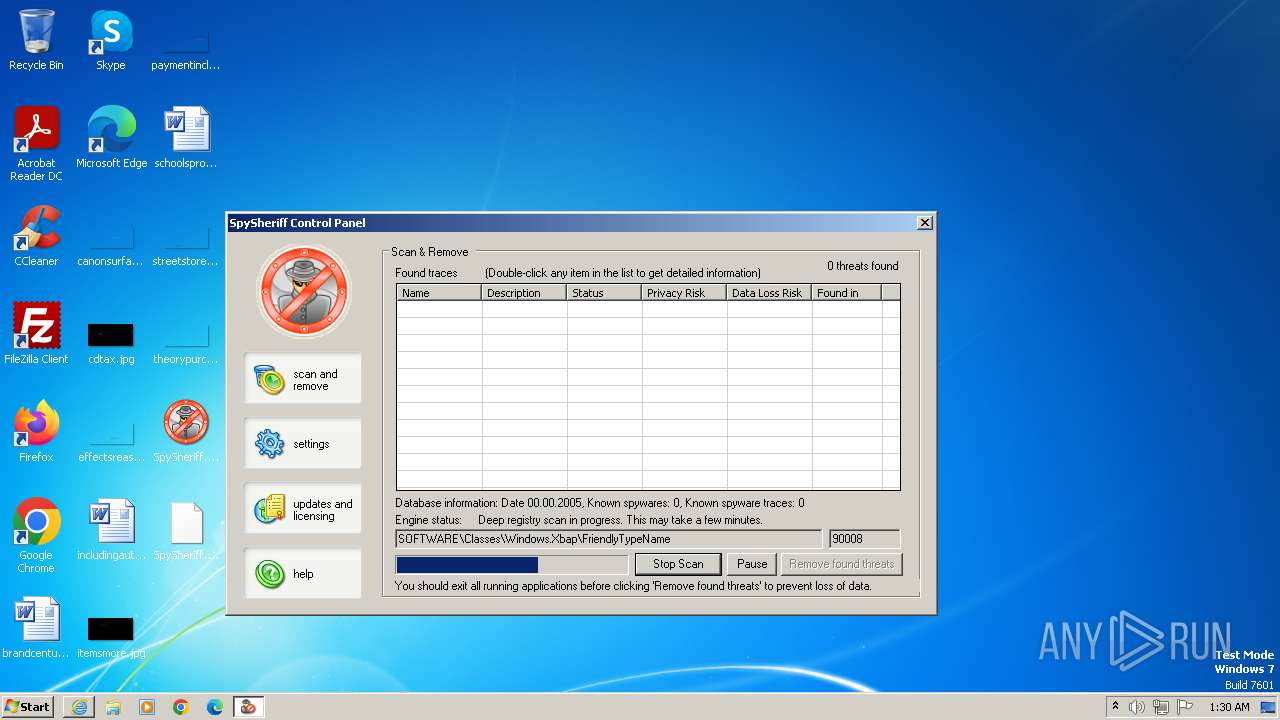
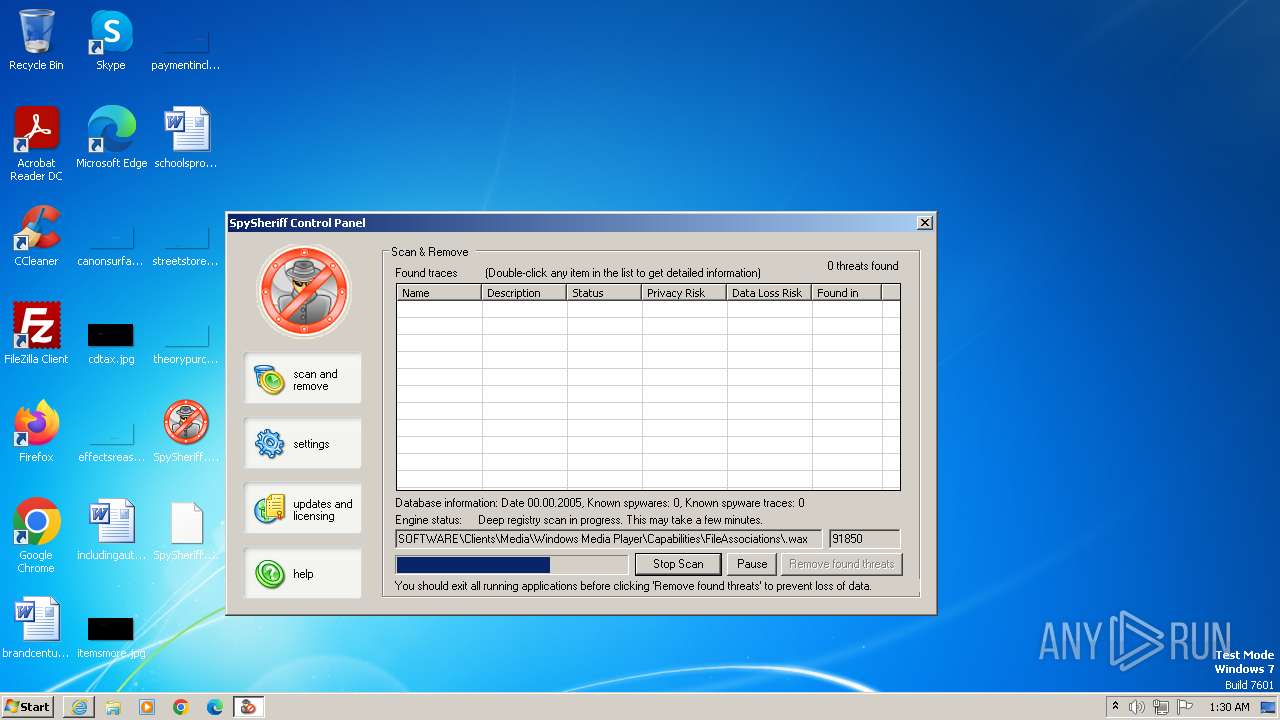
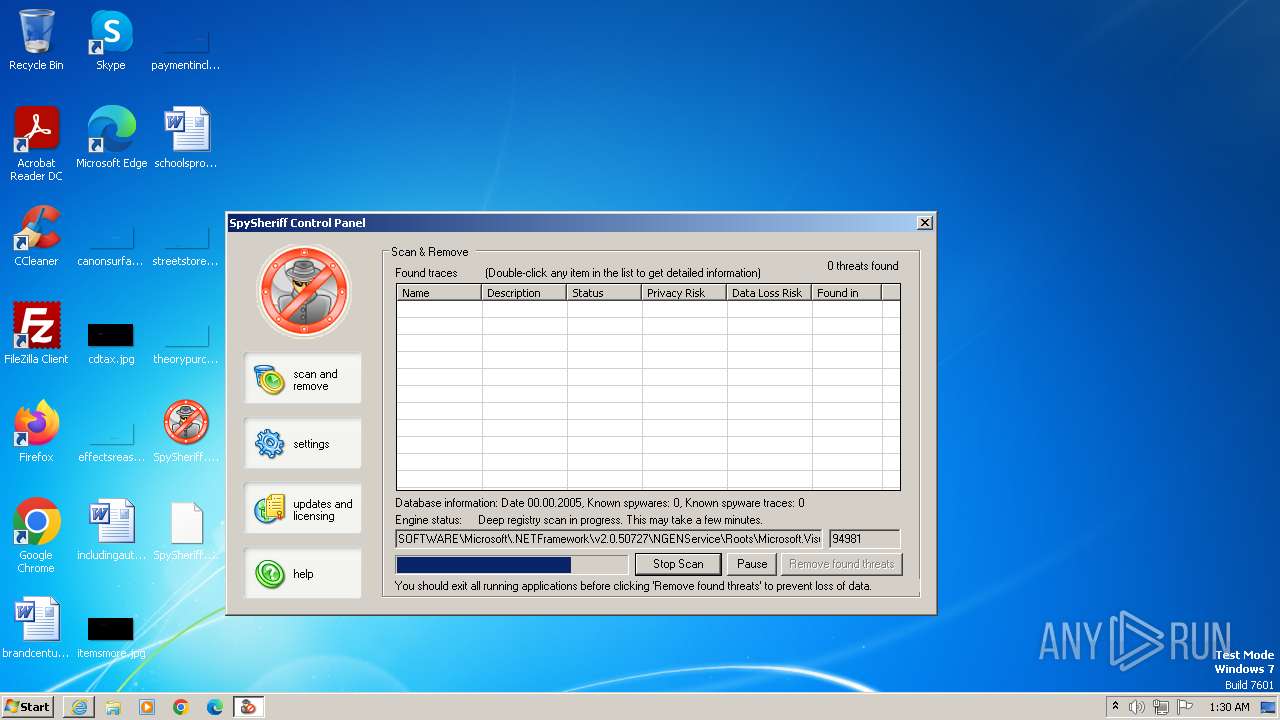
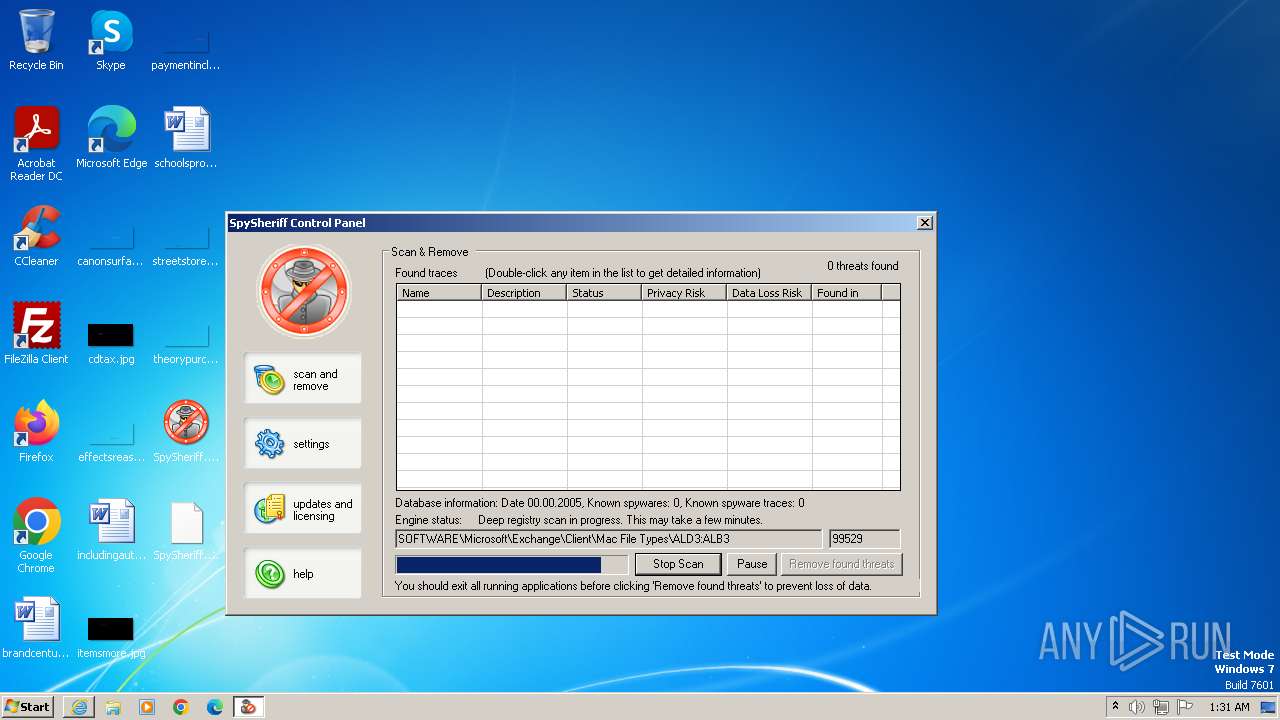
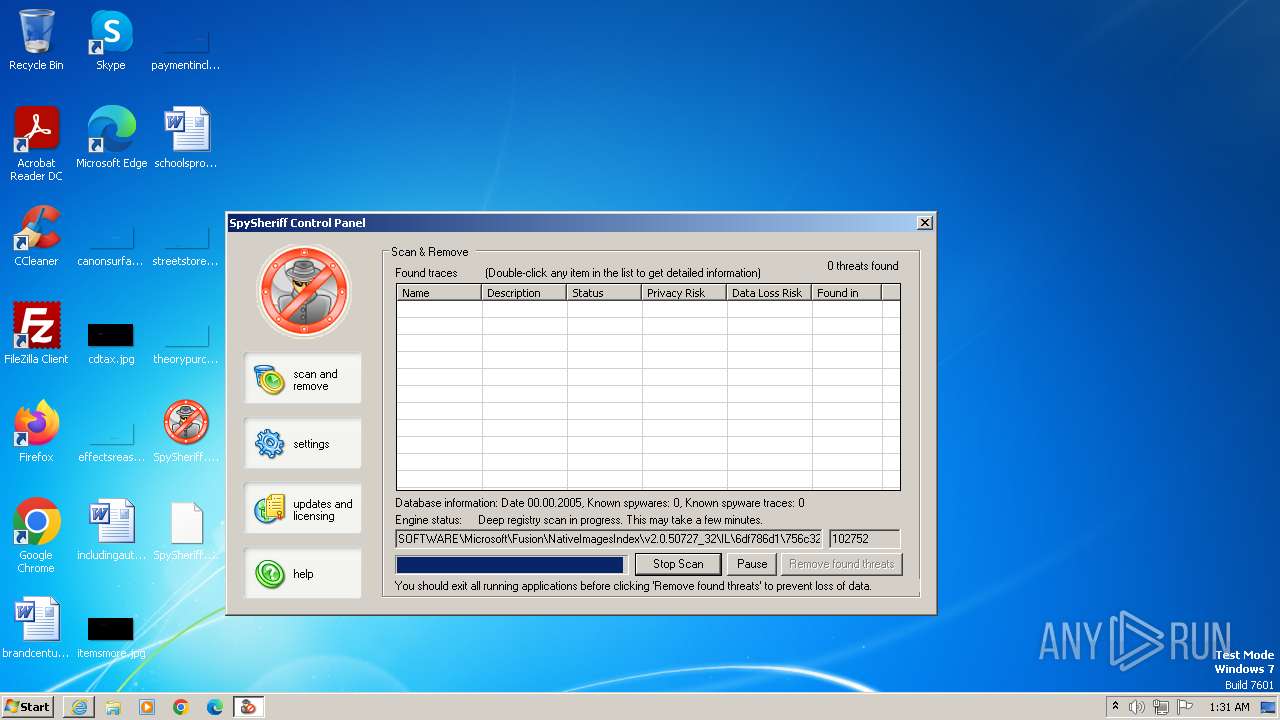
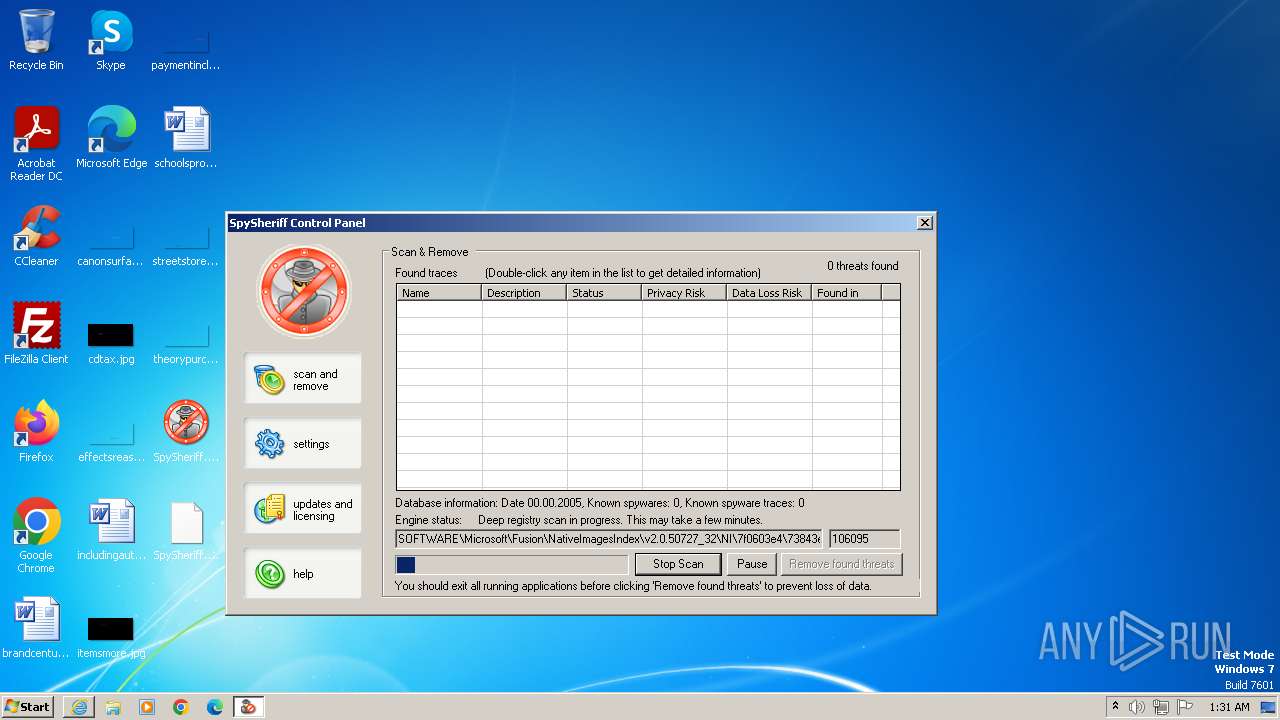
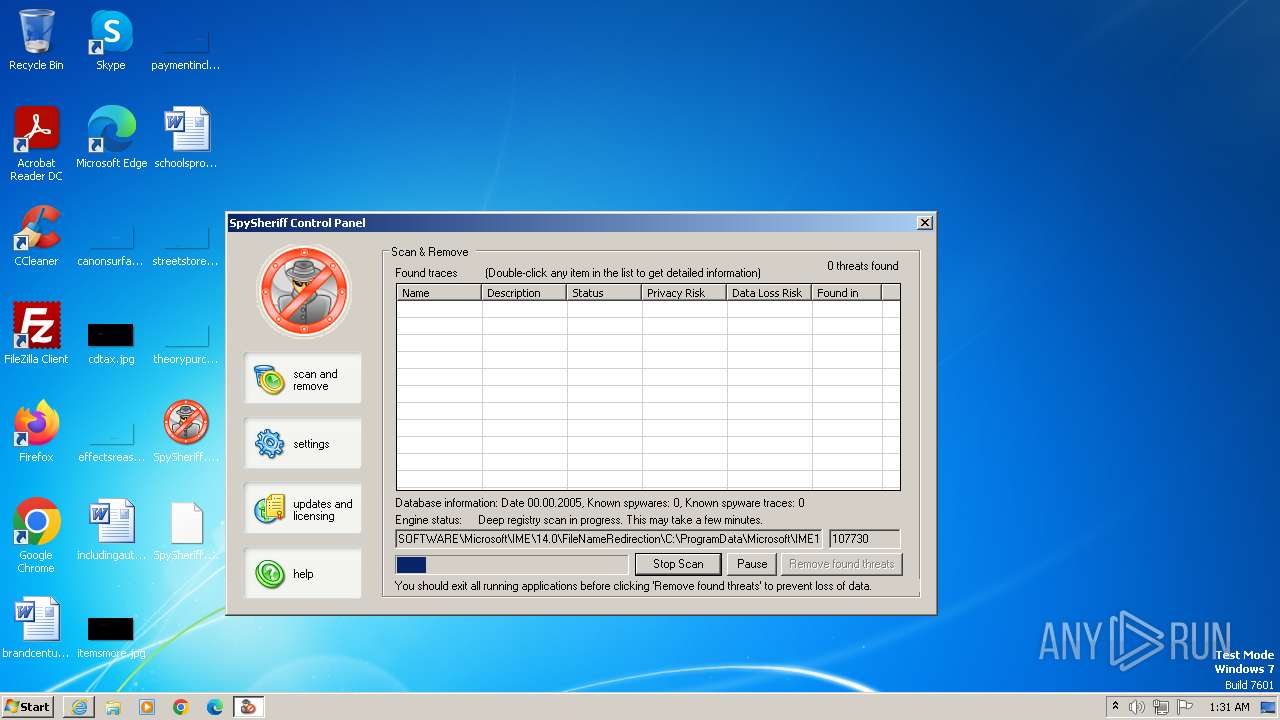
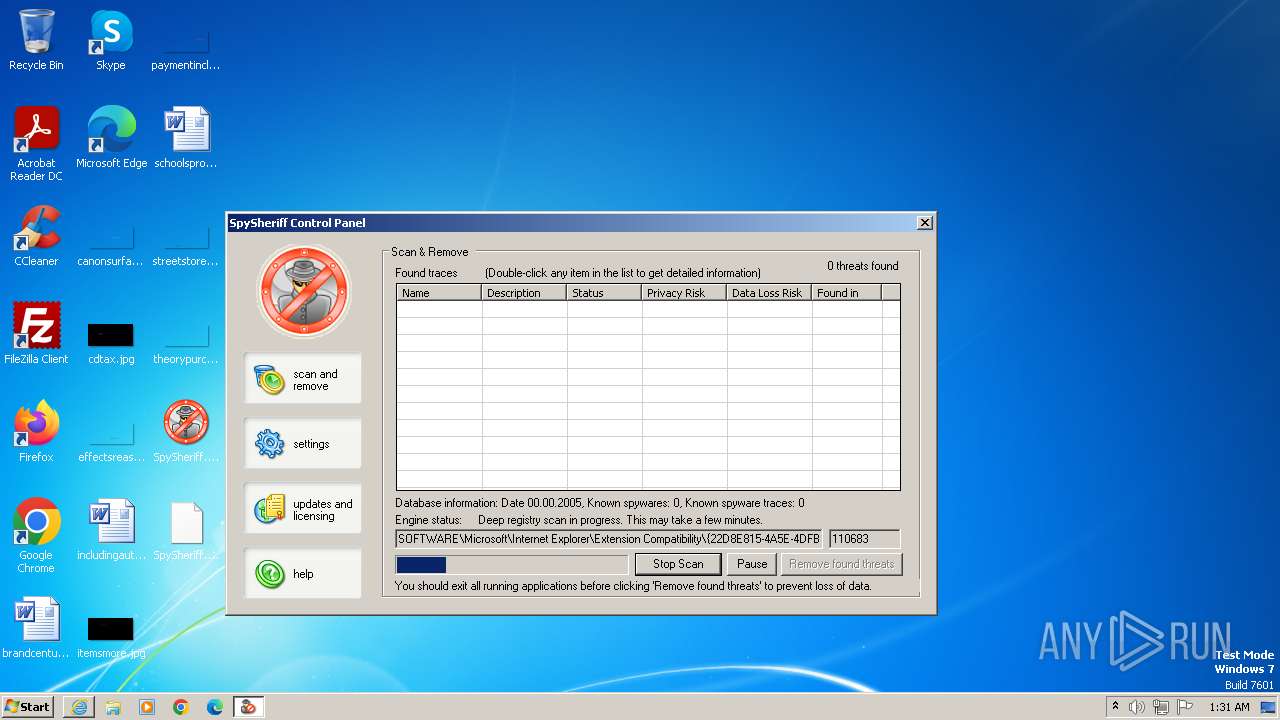
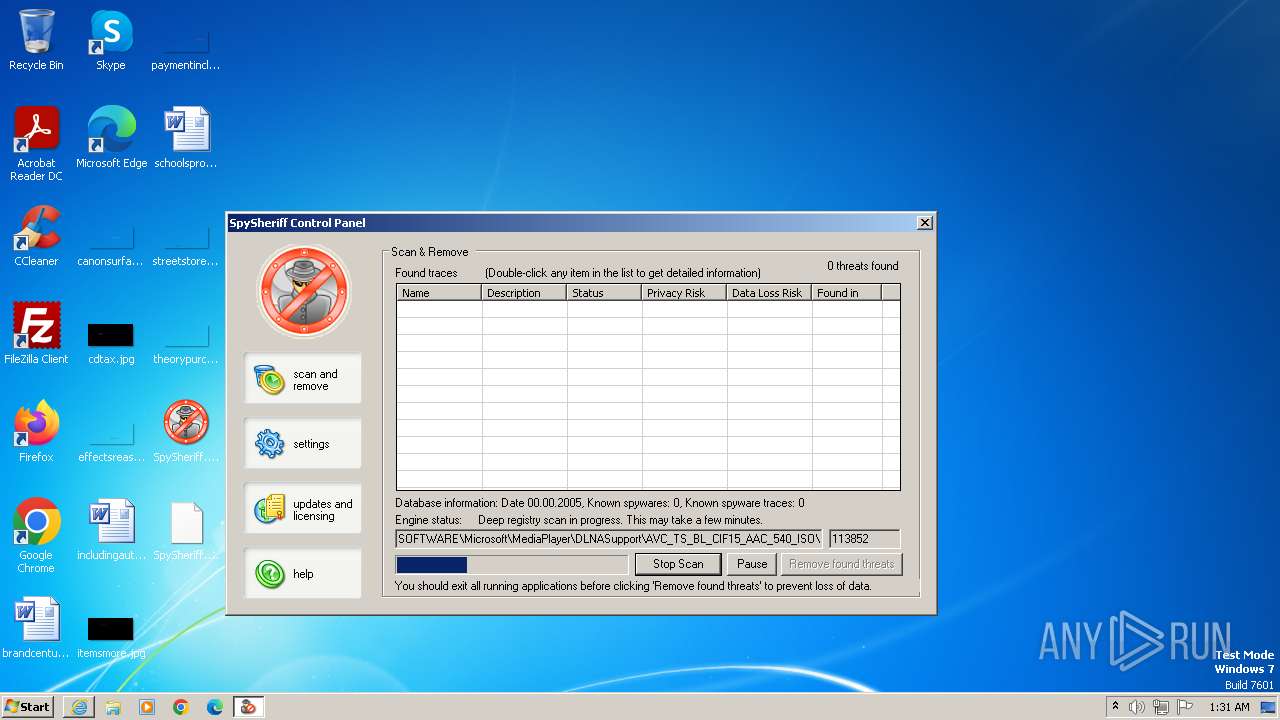
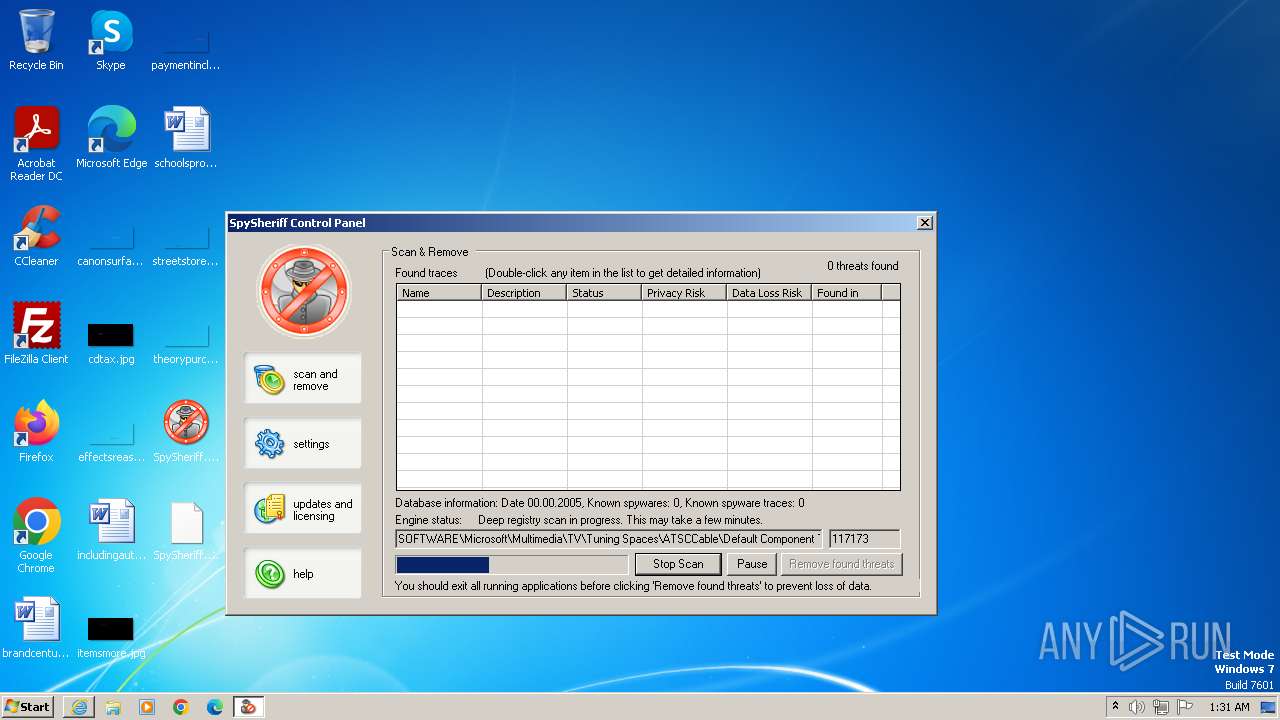
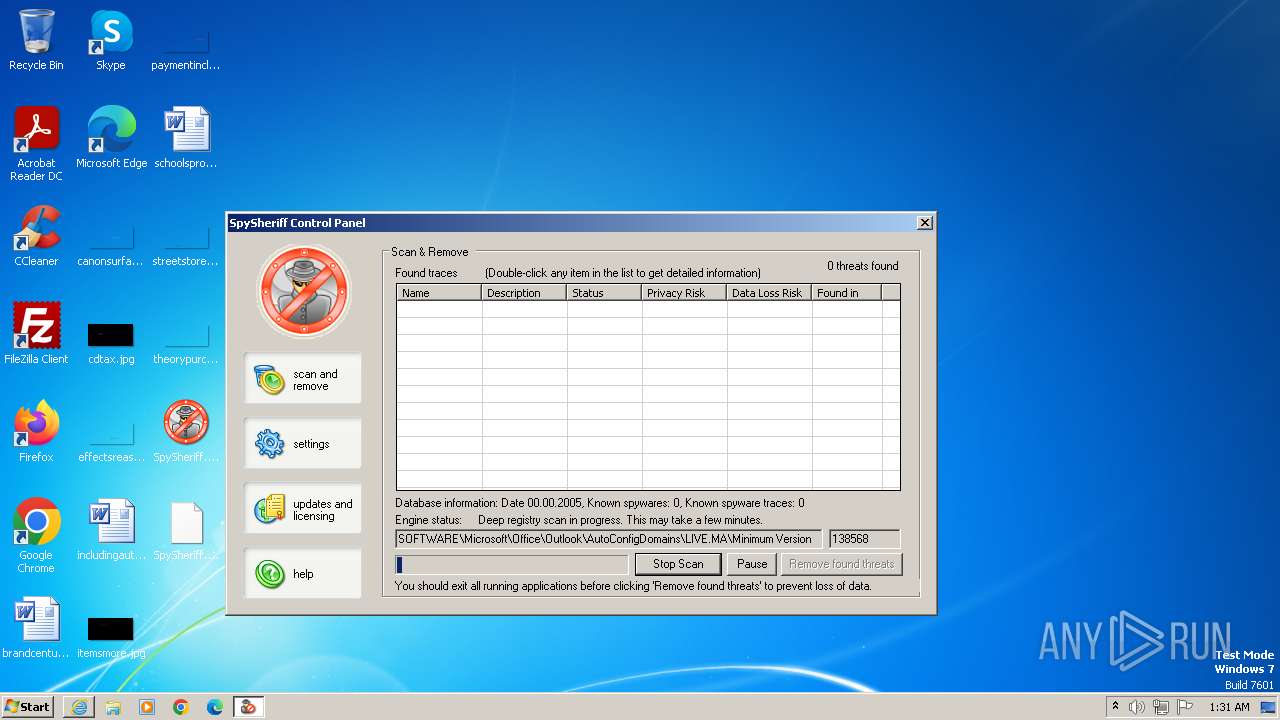
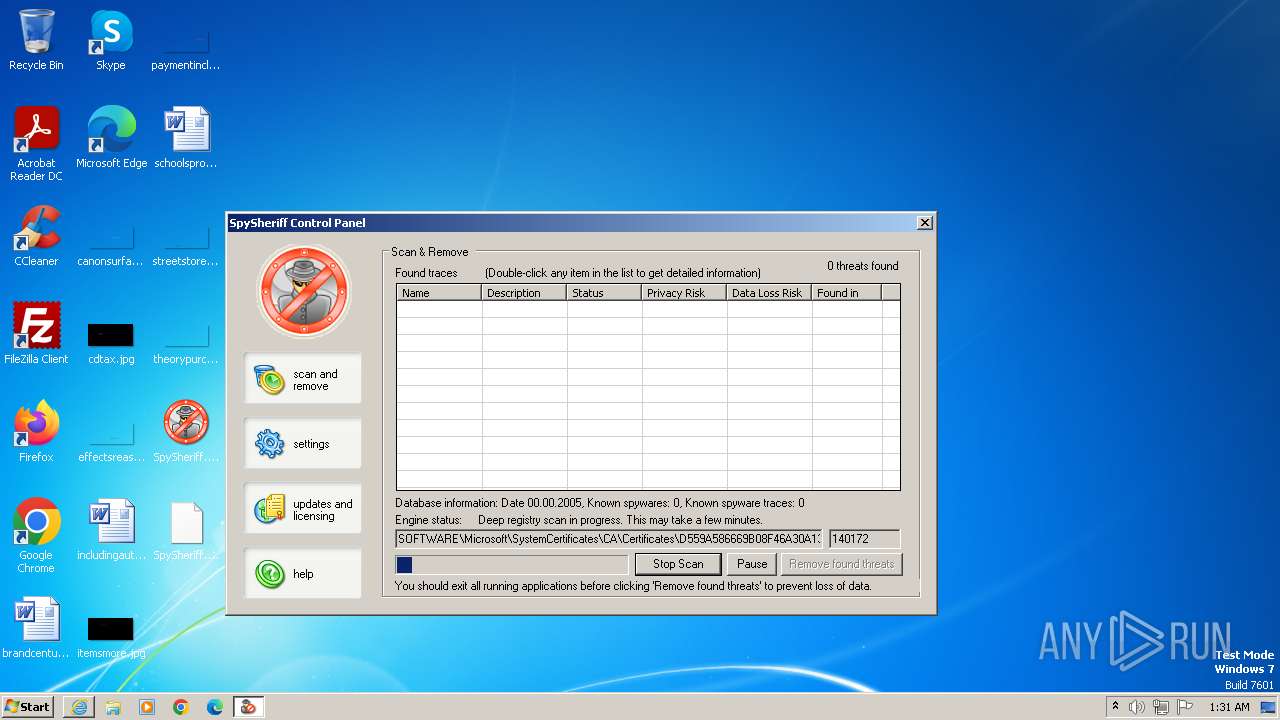
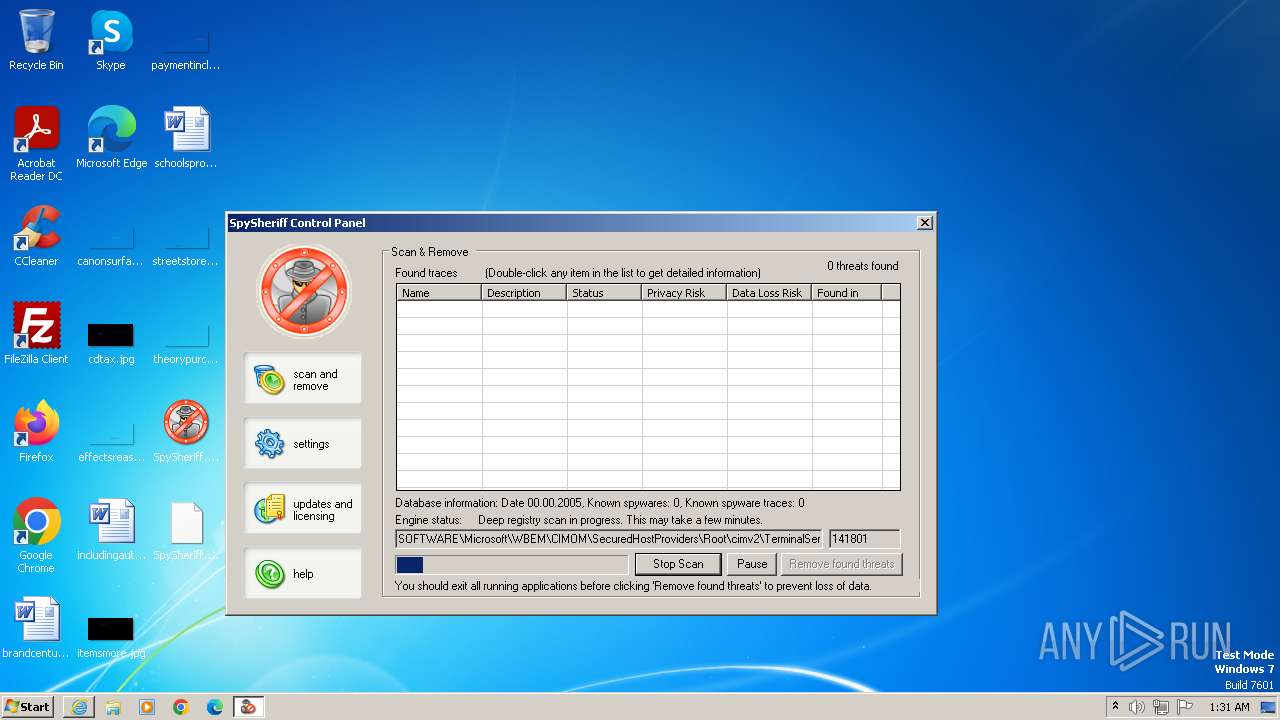
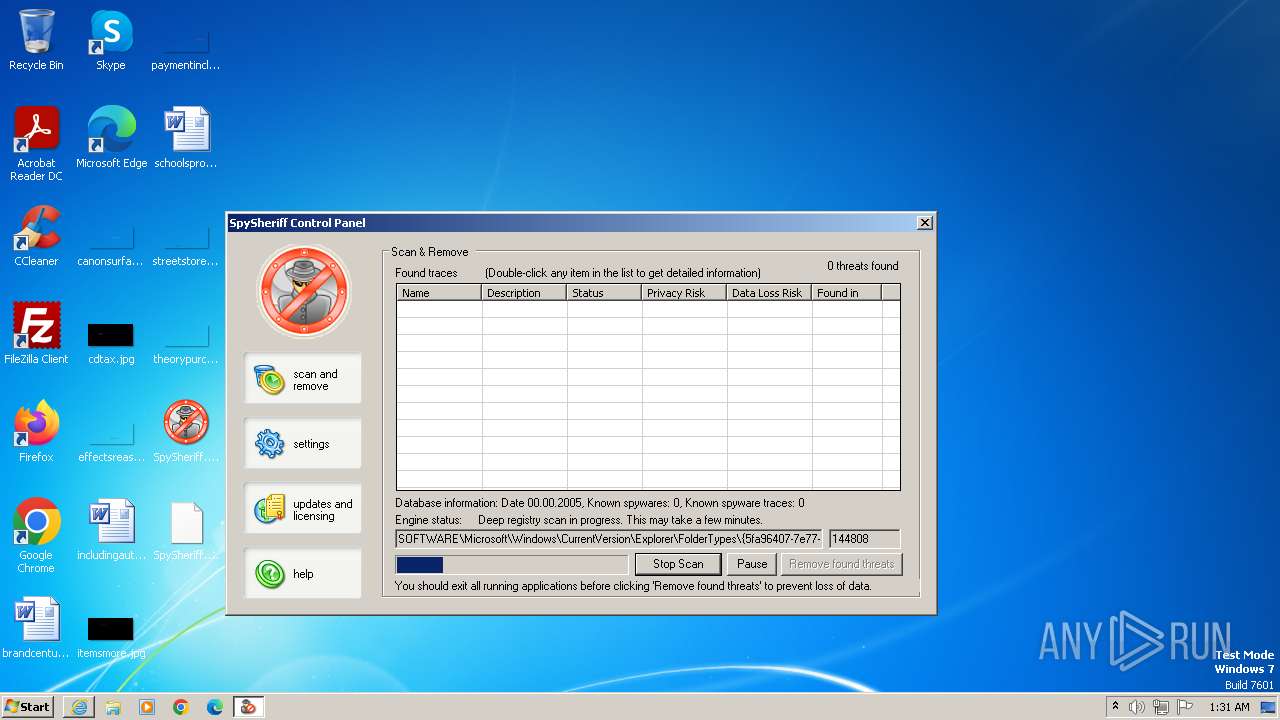
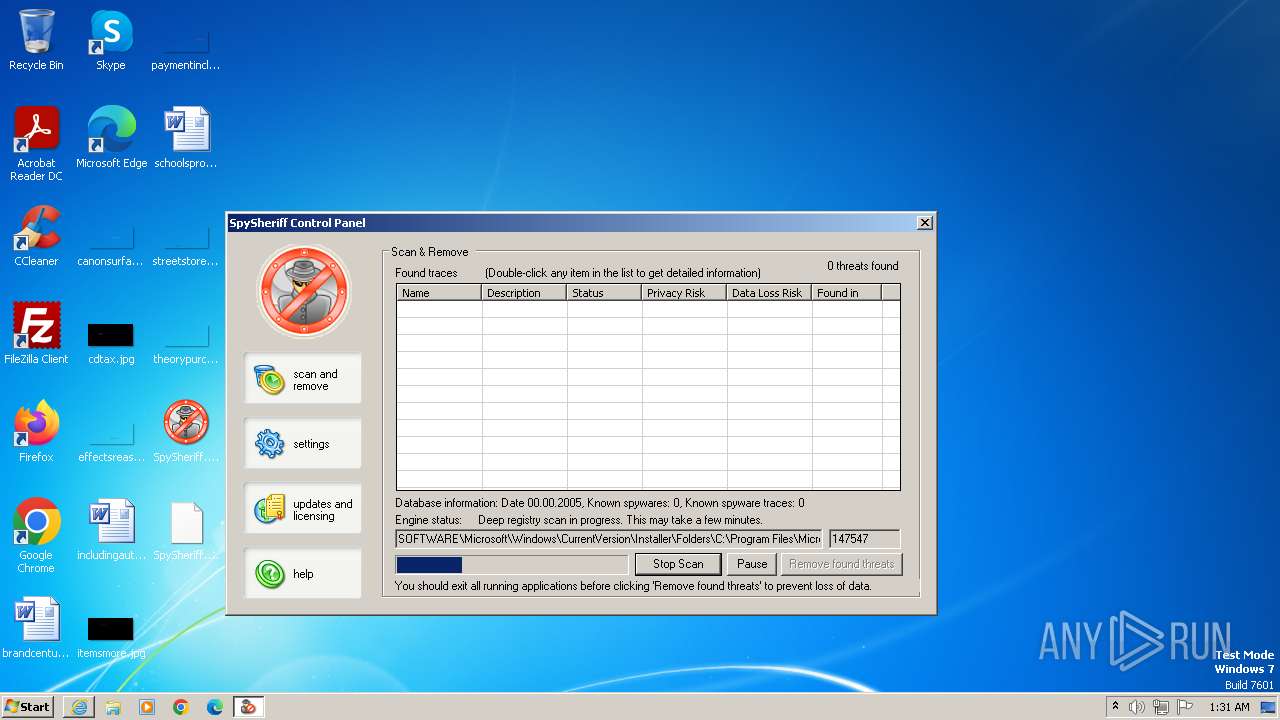
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
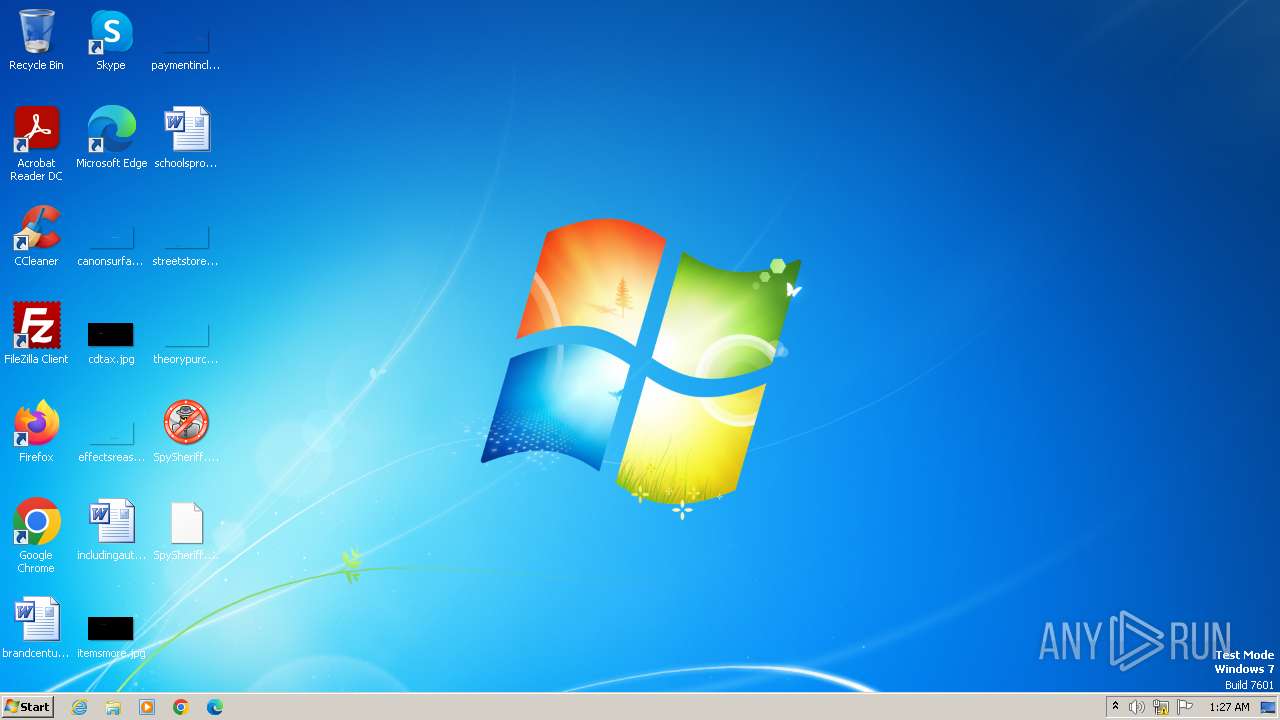
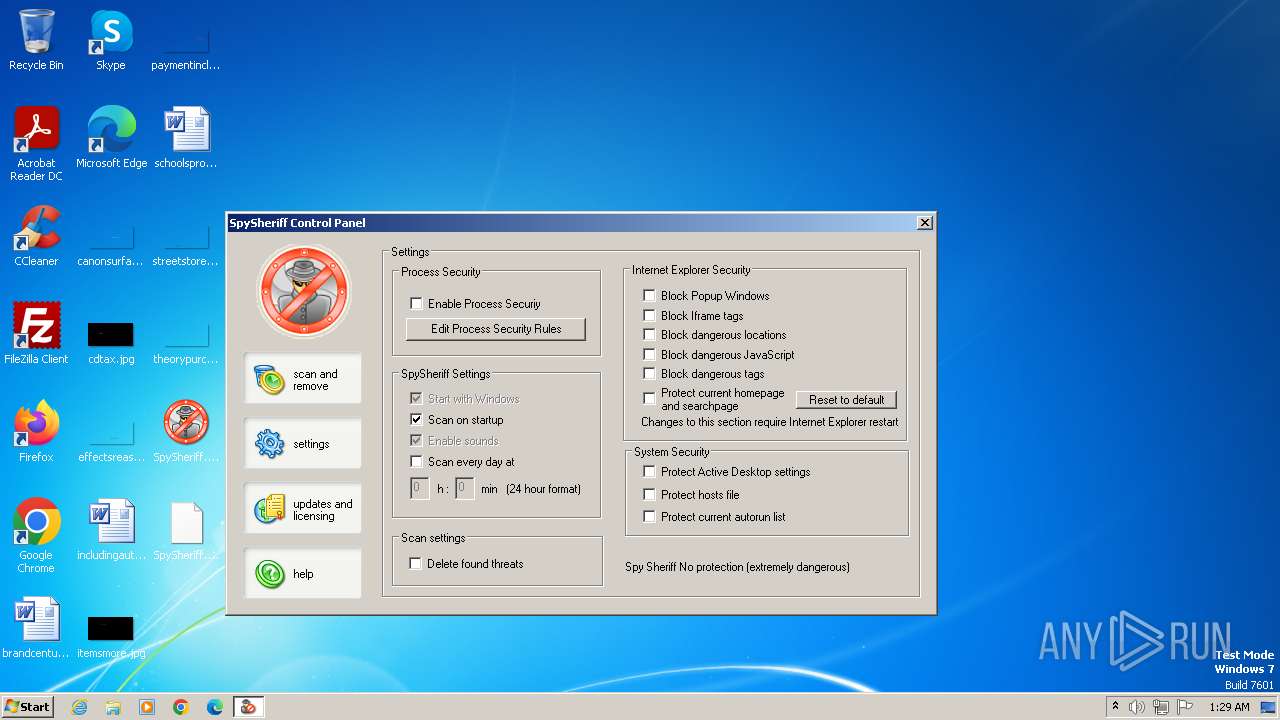
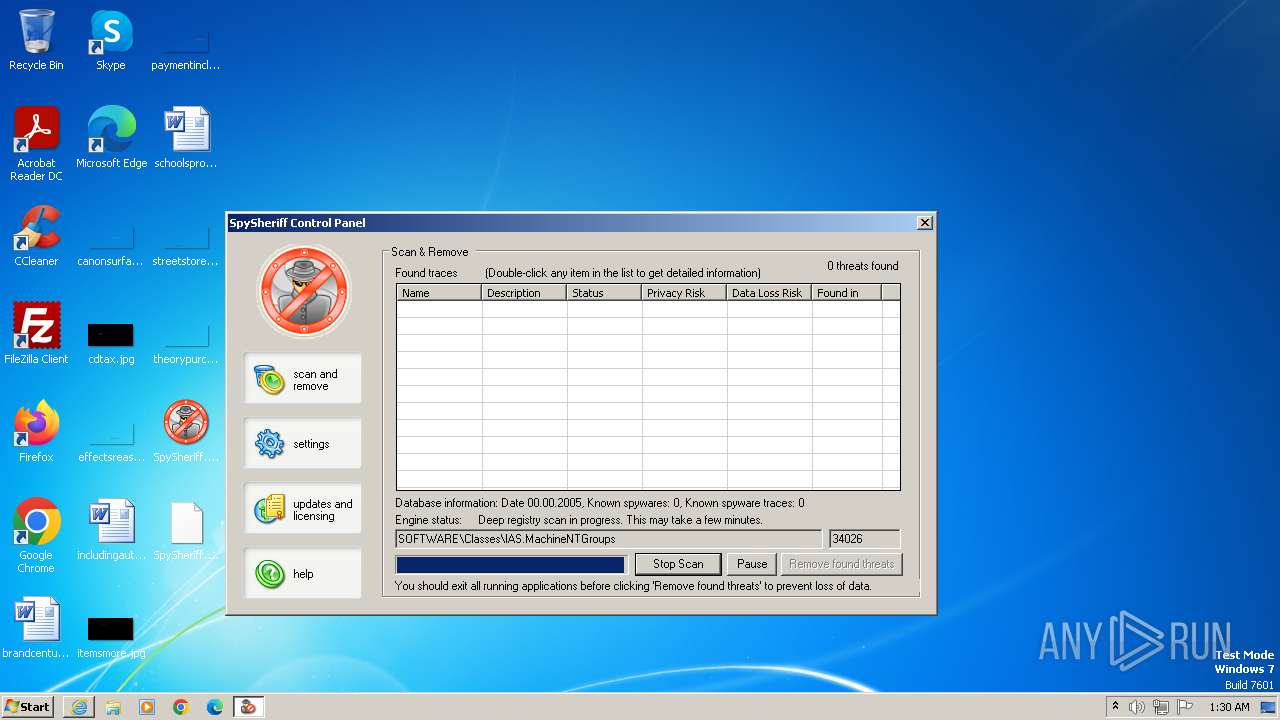
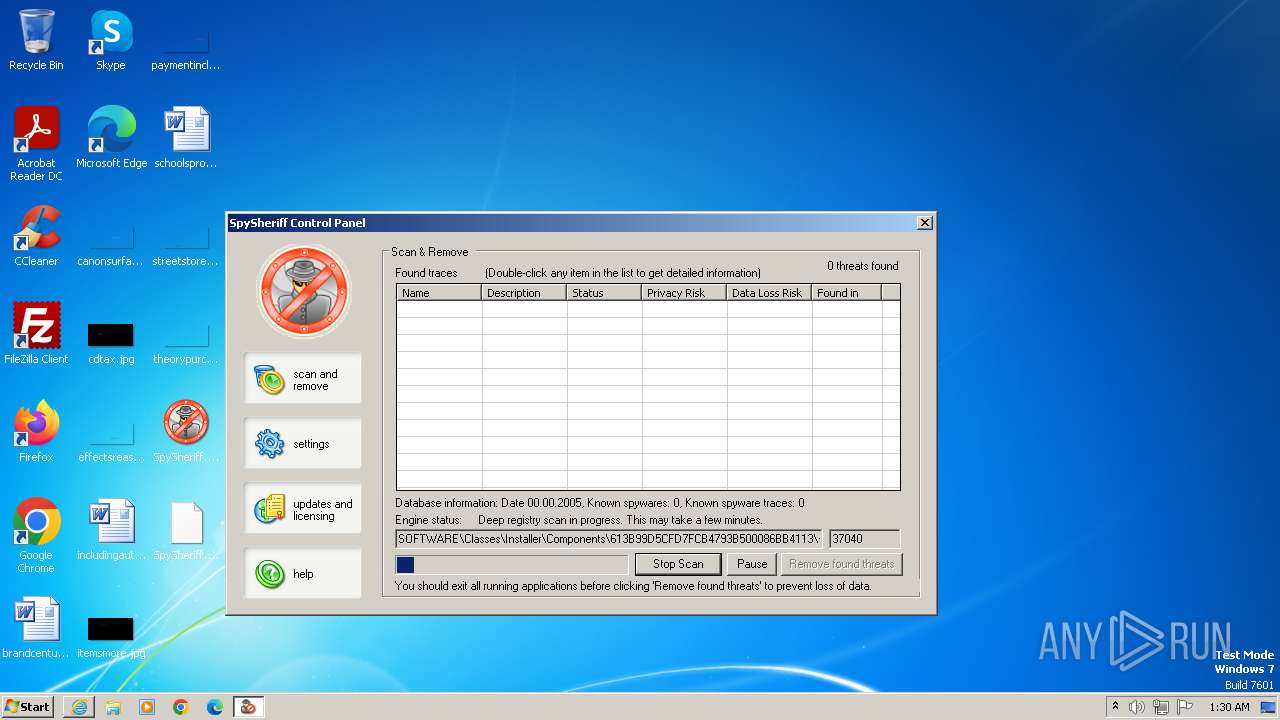
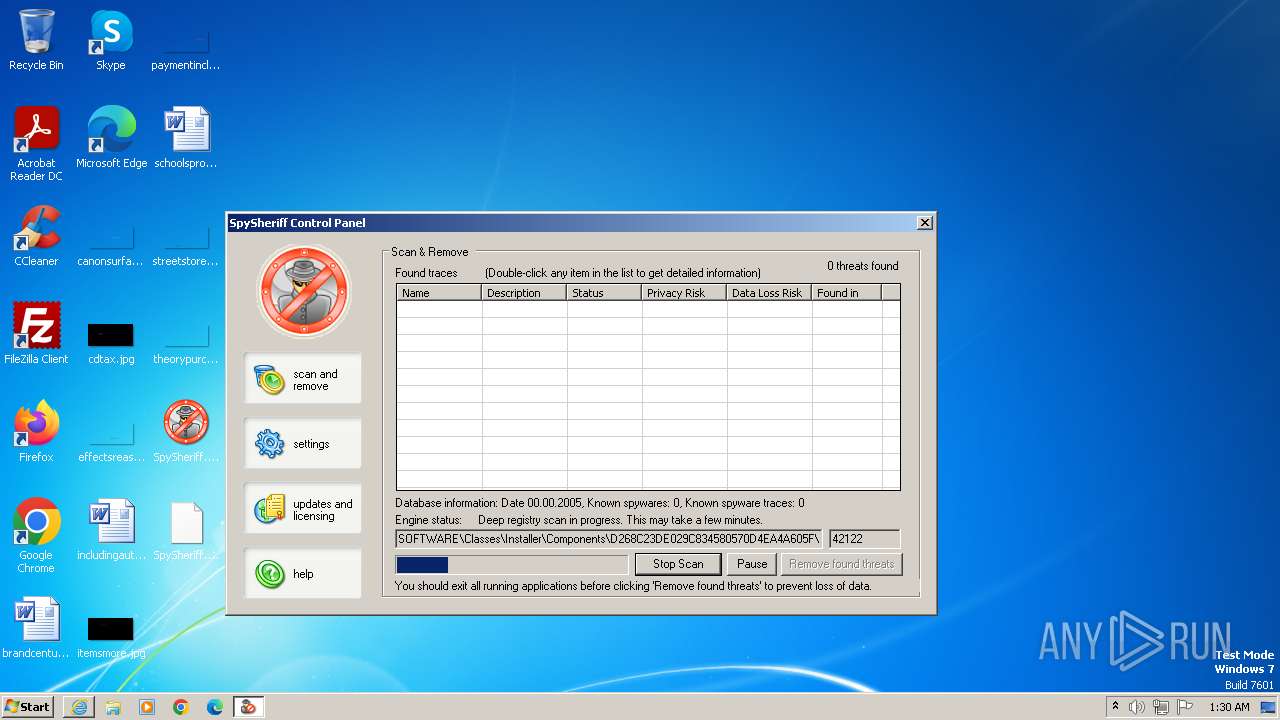
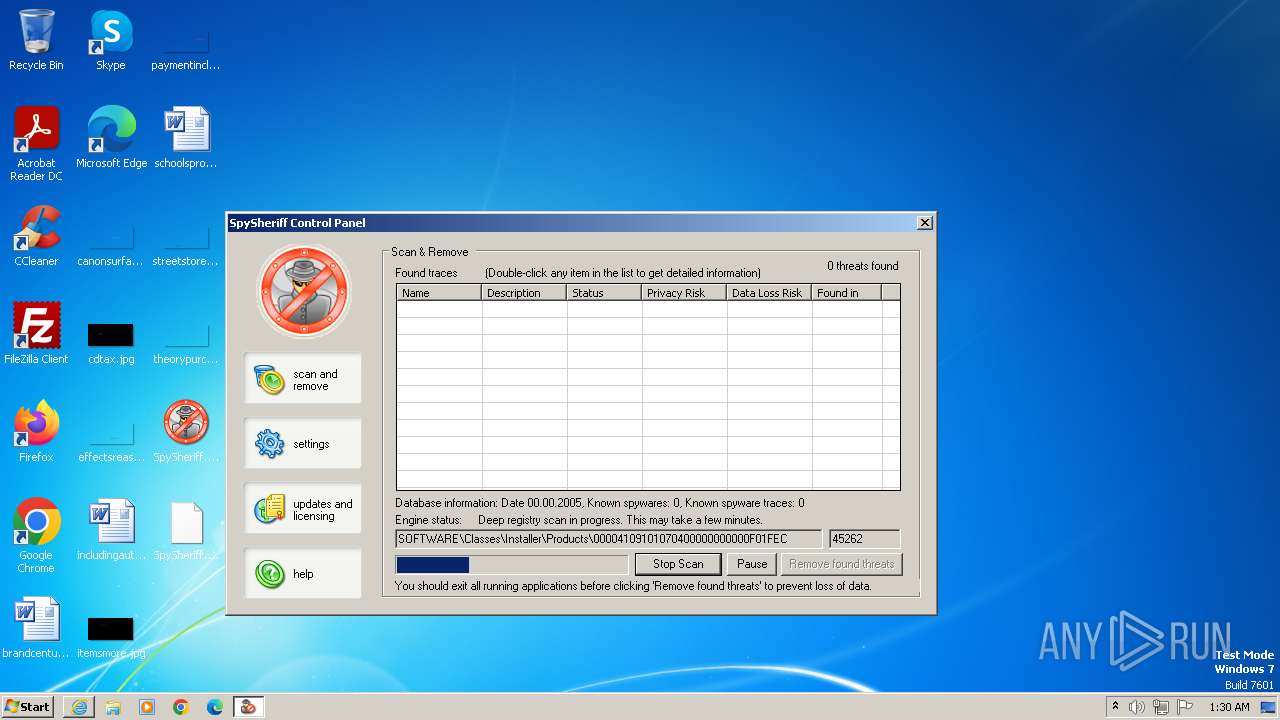
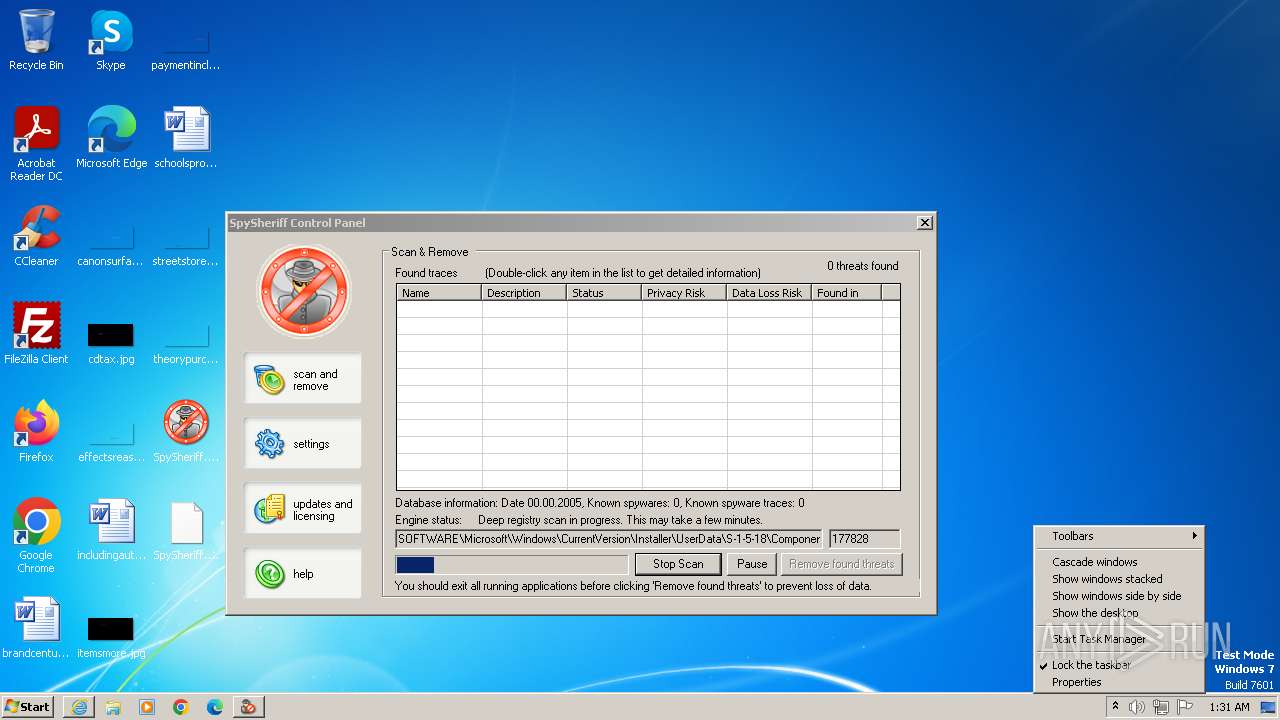
| File name: | SpySheriff.exe |
| Full analysis: | https://app.any.run/tasks/6e968d7a-2206-4ecd-b2d6-ea2bed9d545a |
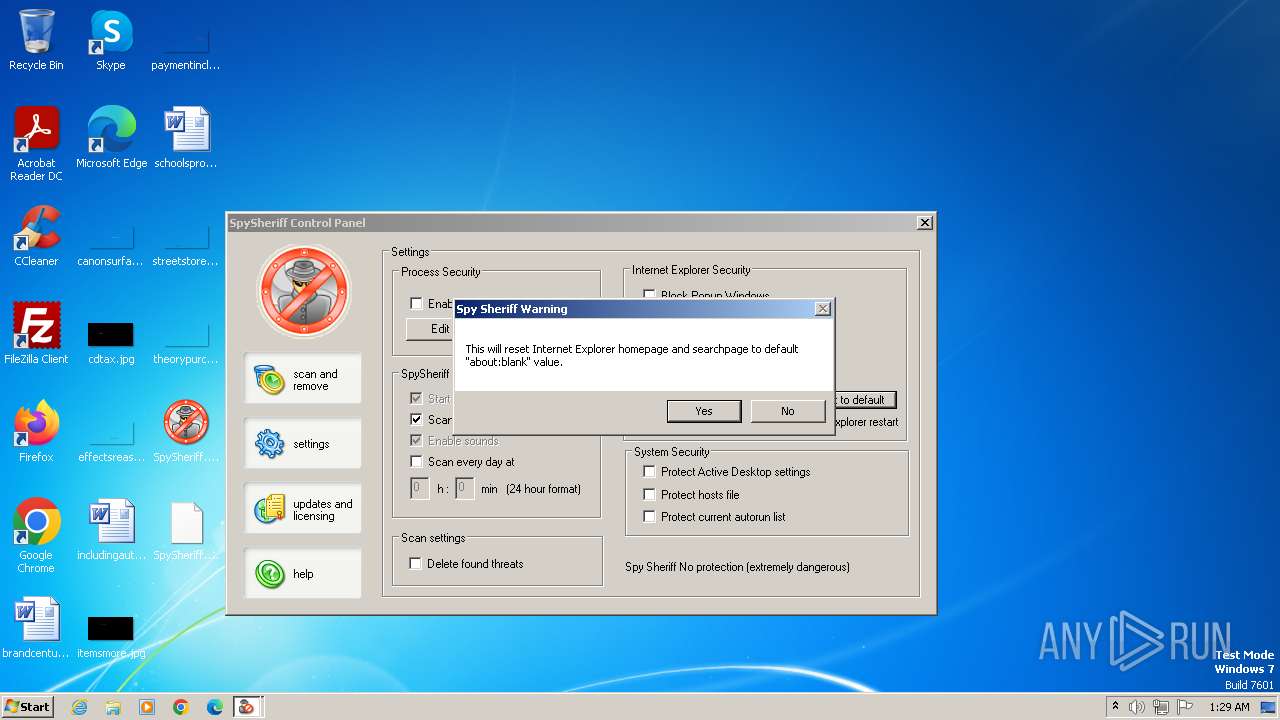
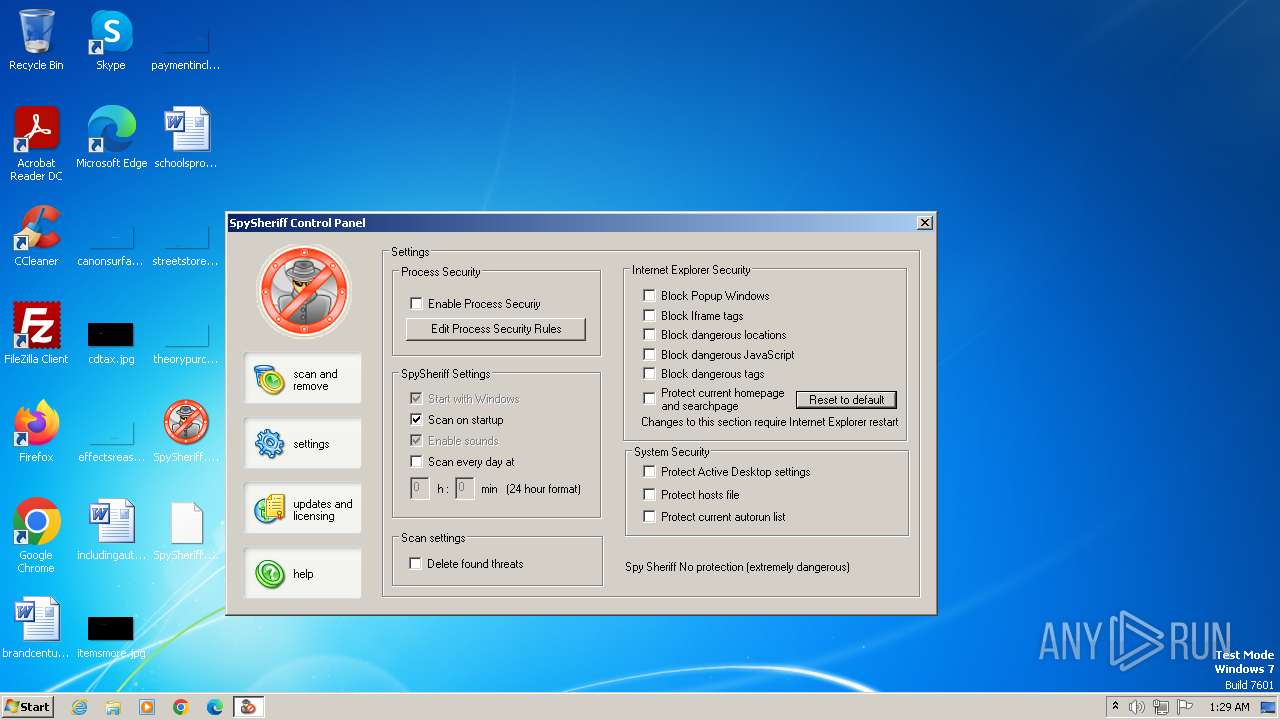
| Verdict: | Malicious activity |
| Threats: | Stealers are a group of malicious software that are intended for gaining unauthorized access to users’ information and transferring it to the attacker. The stealer malware category includes various types of programs that focus on their particular kind of data, including files, passwords, and cryptocurrency. Stealers are capable of spying on their targets by recording their keystrokes and taking screenshots. This type of malware is primarily distributed as part of phishing campaigns. |
| Analysis date: | December 21, 2024, 01:26:53 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, 5 sections |
| MD5: | C899F93E8B753FEDD068EF3FE2EDB0FD |
| SHA1: | 144B1F18D0E307D14937C21CA1D7CBFC91828A10 |
| SHA256: | 5C2A85FB56DE2E0A1A1D260EF2177E0209477586C8A6740494BBAF40A9785F47 |
| SSDEEP: | 12288:eBMDMf+ztV53y2k9I68iXDycz+rYIYsVRSHsDrL:eS4S53h68eIZjDP |
| .exe | | | Win32 Executable (generic) (52.9) |
|---|---|---|
| .exe | | | Generic Win/DOS Executable (23.5) |
| .exe | | | DOS Executable Generic (23.5) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2006:02:24 11:33:55+00:00 |
| ImageFileCharacteristics: | No relocs, Executable, No line numbers, No symbols, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 6 |
| CodeSize: | 698368 |
| InitializedDataSize: | 420290560 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x1000 |
| OSVersion: | 4 |
| ImageVersion: | - |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 316 | "C:\Program Files\Microsoft\Edge\Application\109.0.1518.115\BHO\ie_to_edge_stub.exe" --from-ie-to-edge=3 --ie-frame-hwnd=80200 | C:\Program Files\Microsoft\Edge\Application\109.0.1518.115\BHO\ie_to_edge_stub.exe | — | iexplore.exe | |||||||||||
User: Administrator Company: Microsoft Corporation Integrity Level: HIGH Description: IEToEdge BHO Exit code: 0 Version: 109.0.1518.115 Modules
| |||||||||||||||
| 568 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=gpu-process --gpu-preferences=UAAAAAAAAADgAAAYAAAAAAAAAAAAAAAAAABgAAAAAAAwAAAAAAAAAAAAAAAQAAAAAAAAAAAAAAAAAAAAAAAAAEgAAAAAAAAASAAAAAAAAAAYAAAAAgAAABAAAAAAAAAAGAAAAAAAAAAQAAAAAAAAAAAAAAAOAAAAEAAAAAAAAAABAAAADgAAAAgAAAAAAAAACAAAAAAAAAA= --mojo-platform-channel-handle=1100 --field-trial-handle=1144,i,16584017506648793557,11451991716507382693,131072 --disable-features=OptimizationGuideModelDownloading,OptimizationHints,OptimizationHintsFetching,OptimizationTargetPrediction /prefetch:2 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 109.0.5414.120 Modules
| |||||||||||||||
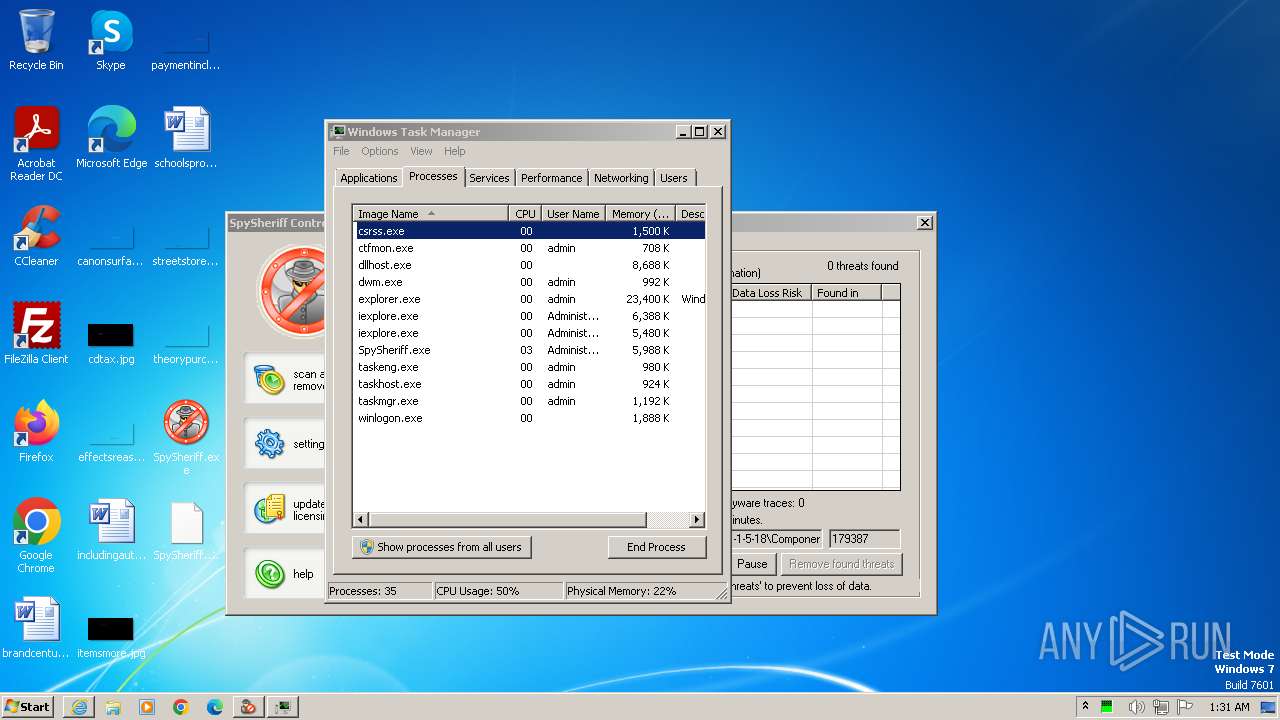
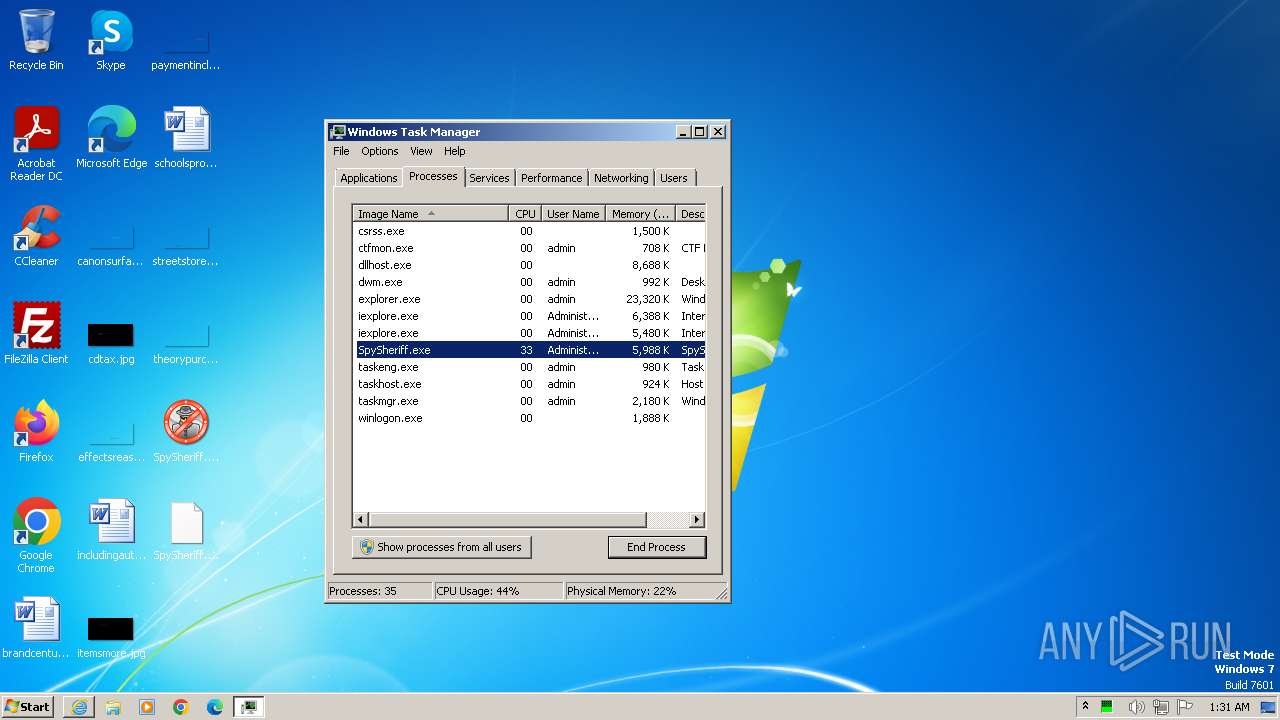
| 856 | "C:\Windows\system32\taskmgr.exe" /4 | C:\Windows\System32\taskmgr.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Task Manager Exit code: 1 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 912 | "C:\Program Files\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=network.mojom.NetworkService --lang=en-US --service-sandbox-type=none --mojo-platform-channel-handle=1368 --field-trial-handle=1296,i,16690615459709443678,1333317188642233079,131072 /prefetch:3 | C:\Program Files\Microsoft\Edge\Application\msedge.exe | msedge.exe | ||||||||||||
User: Administrator Company: Microsoft Corporation Integrity Level: HIGH Description: Microsoft Edge Exit code: 0 Version: 109.0.1518.115 Modules
| |||||||||||||||
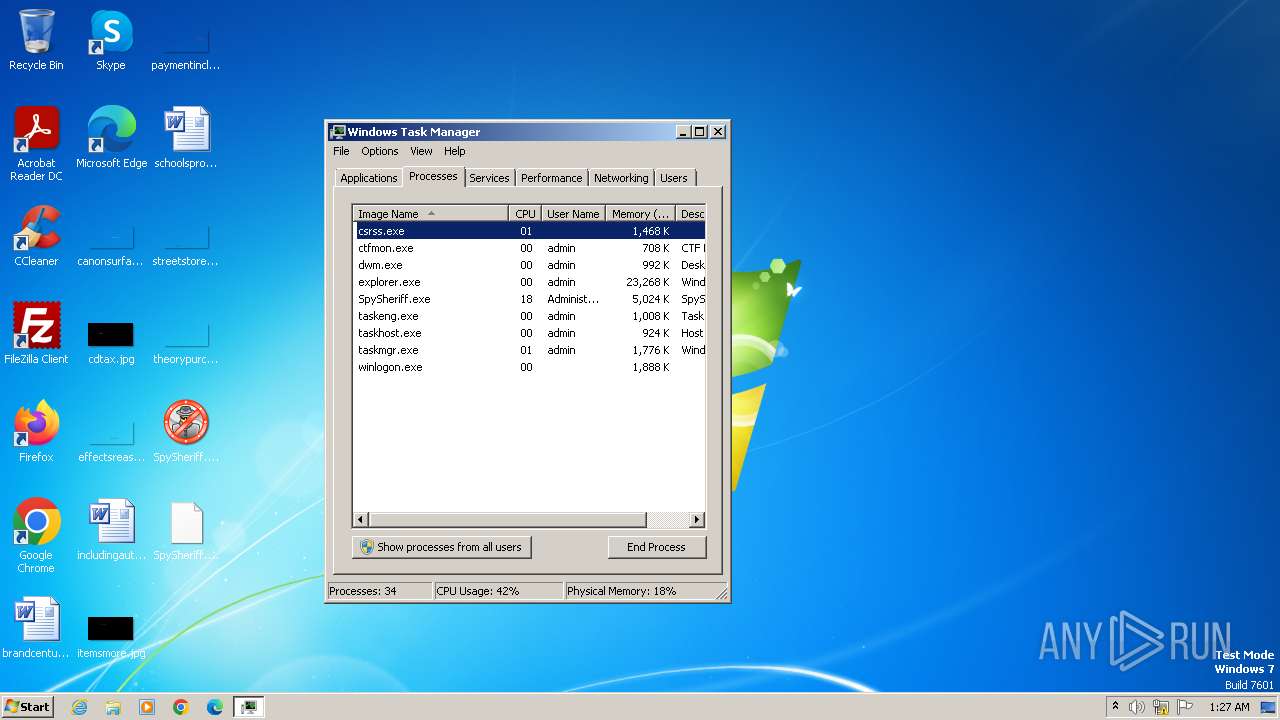
| 1096 | "C:\Users\admin\Desktop\SpySheriff.exe" | C:\Users\admin\Desktop\SpySheriff.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 1664 | "C:\Users\admin\Desktop\SpySheriff.exe" | C:\Users\admin\Desktop\SpySheriff.exe | — | explorer.exe | |||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 1740 | C:\Users\admin\Desktop\SpySheriff.exe | C:\Users\admin\Desktop\SpySheriff.exe | runas.exe | ||||||||||||
User: Administrator Integrity Level: HIGH Exit code: 1 Modules
| |||||||||||||||
| 1824 | "C:\Windows\System32\runas.exe" /user:administrator C:\Users\admin\Desktop\SpySheriff.exe | C:\Windows\System32\runas.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Run As Utility Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1836 | "C:\Program Files\Microsoft\Edge\Application\msedge.exe" --type=crashpad-handler "--user-data-dir=C:\Users\Administrator\AppData\Local\Microsoft\Edge\User Data" /prefetch:7 --monitor-self-annotation=ptype=crashpad-handler "--database=C:\Users\Administrator\AppData\Local\Microsoft\Edge\User Data\Crashpad" "--metrics-dir=C:\Users\Administrator\AppData\Local\Microsoft\Edge\User Data" --annotation=IsOfficialBuild=1 --annotation=channel= --annotation=chromium-version=109.0.5414.149 "--annotation=exe=C:\Program Files\Microsoft\Edge\Application\msedge.exe" --annotation=plat=Win32 "--annotation=prod=Microsoft Edge" --annotation=ver=109.0.1518.115 --initial-client-data=0xcc,0xd0,0xd4,0xa0,0xdc,0x6976f598,0x6976f5a8,0x6976f5b4 | C:\Program Files\Microsoft\Edge\Application\msedge.exe | msedge.exe | ||||||||||||
User: Administrator Company: Microsoft Corporation Integrity Level: HIGH Description: Microsoft Edge Exit code: 0 Version: 109.0.1518.115 Modules
| |||||||||||||||
| 1880 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=storage.mojom.StorageService --lang=en-US --service-sandbox-type=service --disable-quic --mojo-platform-channel-handle=1624 --field-trial-handle=1144,i,16584017506648793557,11451991716507382693,131072 --disable-features=OptimizationGuideModelDownloading,OptimizationHints,OptimizationHintsFetching,OptimizationTargetPrediction /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 109.0.5414.120 Modules
| |||||||||||||||
| (PID) Process: | (1740) SpySheriff.exe | Key: | HKEY_CURRENT_USER\Software\SpySheriff |
| Operation: | write | Name: | ScanOnStartup |
Value: 1 | |||
| (PID) Process: | (1740) SpySheriff.exe | Key: | HKEY_CURRENT_USER\Software\SpySheriff |
| Operation: | write | Name: | PlaySounds |
Value: 1 | |||
| (PID) Process: | (1740) SpySheriff.exe | Key: | HKEY_CURRENT_USER\Software\SpySheriff |
| Operation: | write | Name: | ScheduledScan |
Value: 0 | |||
| (PID) Process: | (1740) SpySheriff.exe | Key: | HKEY_CURRENT_USER\Software\SpySheriff |
| Operation: | write | Name: | ScheduledScanHour |
Value: 0 | |||
| (PID) Process: | (1740) SpySheriff.exe | Key: | HKEY_CURRENT_USER\Software\SpySheriff |
| Operation: | write | Name: | ScheduledScanMin |
Value: 0 | |||
| (PID) Process: | (1740) SpySheriff.exe | Key: | HKEY_CURRENT_USER\Software\SpySheriff |
| Operation: | write | Name: | SecurityLevel |
Value: 2 | |||
| (PID) Process: | (1740) SpySheriff.exe | Key: | HKEY_CURRENT_USER\Software\SpySheriff |
| Operation: | write | Name: | Uninstall |
Value: C:\Users\admin\Desktop | |||
| (PID) Process: | (1740) SpySheriff.exe | Key: | HKEY_CURRENT_USER\Software\SpySheriff\IE Security |
| Operation: | write | Name: | BlockIframeTags |
Value: 0 | |||
| (PID) Process: | (1740) SpySheriff.exe | Key: | HKEY_CURRENT_USER\Software\SpySheriff\IE Security |
| Operation: | write | Name: | BlockJavascripts |
Value: 0 | |||
| (PID) Process: | (1740) SpySheriff.exe | Key: | HKEY_CURRENT_USER\Software\SpySheriff\IE Security |
| Operation: | write | Name: | BlockLocations |
Value: 0 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3228 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\commerce_subscription_db\LOG.old~RF11efac.TMP | — | |
MD5:— | SHA256:— | |||
| 3228 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\commerce_subscription_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 3228 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Session Storage\LOG.old | text | |
MD5:C6F15CDB9302BD52235CBDDBA2789C07 | SHA256:99936CD5D4D75C455329F217F8B276A697BDCCC05664615E20BAB45D4638D8AF | |||
| 1740 | SpySheriff.exe | C:\Users\Administrator\Desktop\SpySheriff.lnk | binary | |
MD5:0CF9DB81C11AC1DA30A6339DB16BA526 | SHA256:D6F429D37A27B65FF168618D1EB966DC323FE1D77F75A30AAEC0789B0067AD68 | |||
| 1740 | SpySheriff.exe | C:\SpySheriff.lnk | binary | |
MD5:0CF9DB81C11AC1DA30A6339DB16BA526 | SHA256:D6F429D37A27B65FF168618D1EB966DC323FE1D77F75A30AAEC0789B0067AD68 | |||
| 3228 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Crashpad\settings.dat | binary | |
MD5:9C016064A1F864C8140915D77CF3389A | SHA256:0E7265D4A8C16223538EDD8CD620B8820611C74538E420A88E333BE7F62AC787 | |||
| 3228 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Last Version | text | |
MD5:9F941EA08DBDCA2EB3CFA1DBBBA6F5DC | SHA256:127F71DF0D2AD895D4F293E62284D85971AE047CA15F90B87BF6335898B0B655 | |||
| 3228 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Site Characteristics Database\LOG.old~RF11ef9d.TMP | text | |
MD5:825B582C78EC88D54C215EFDF1EAD639 | SHA256:367995D01A8F13E5C30C79499F86B034775BFD009D83DC97635DE438D47DFA37 | |||
| 3228 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Site Characteristics Database\LOG.old | text | |
MD5:1C6BD9993E8ECB91342E78927D81DCA3 | SHA256:76BE6BB39D2B3287BCBBCF6465599F0CF66FE5B9F4F55D10ED38B0BCF1A4BEC3 | |||
| 3228 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\Sync Data\LevelDB\LOG.old | text | |
MD5:46DCF7DB72970F06A3B4803F7064C6E6 | SHA256:179243BCC118729AE487E1CADCF2C0976413903B97CF5B5DA985D0D60B60716A | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
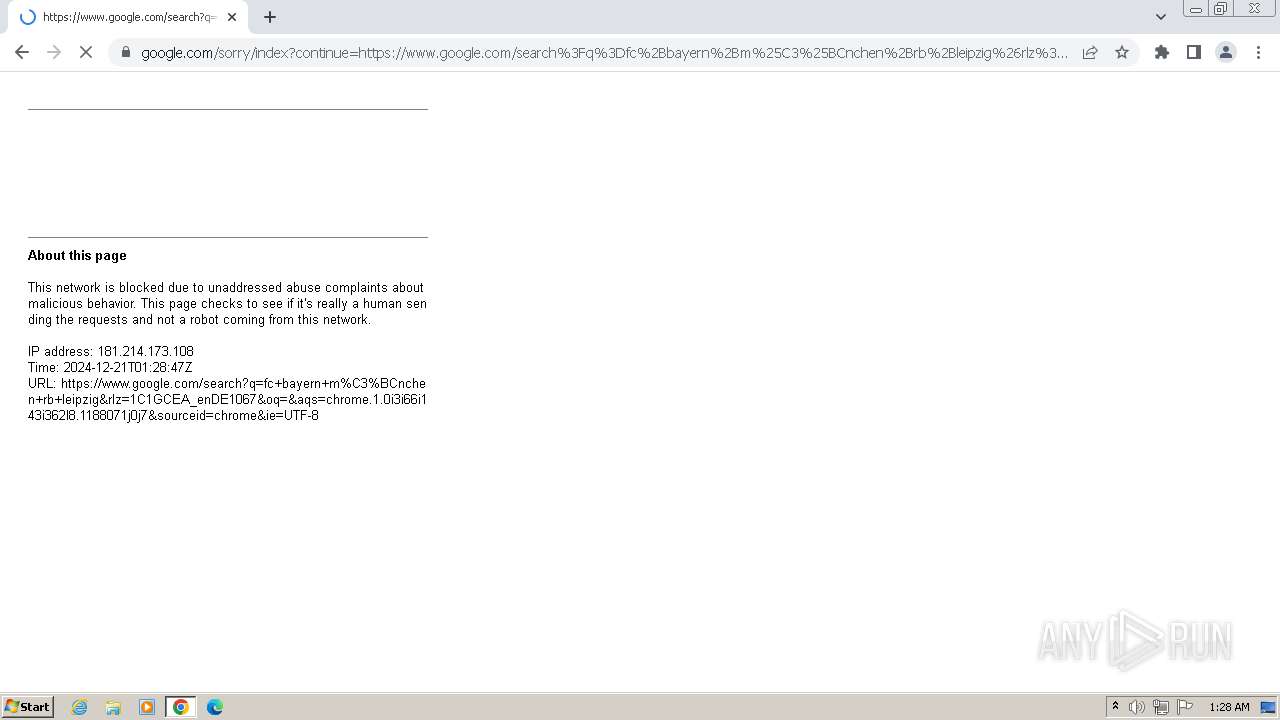
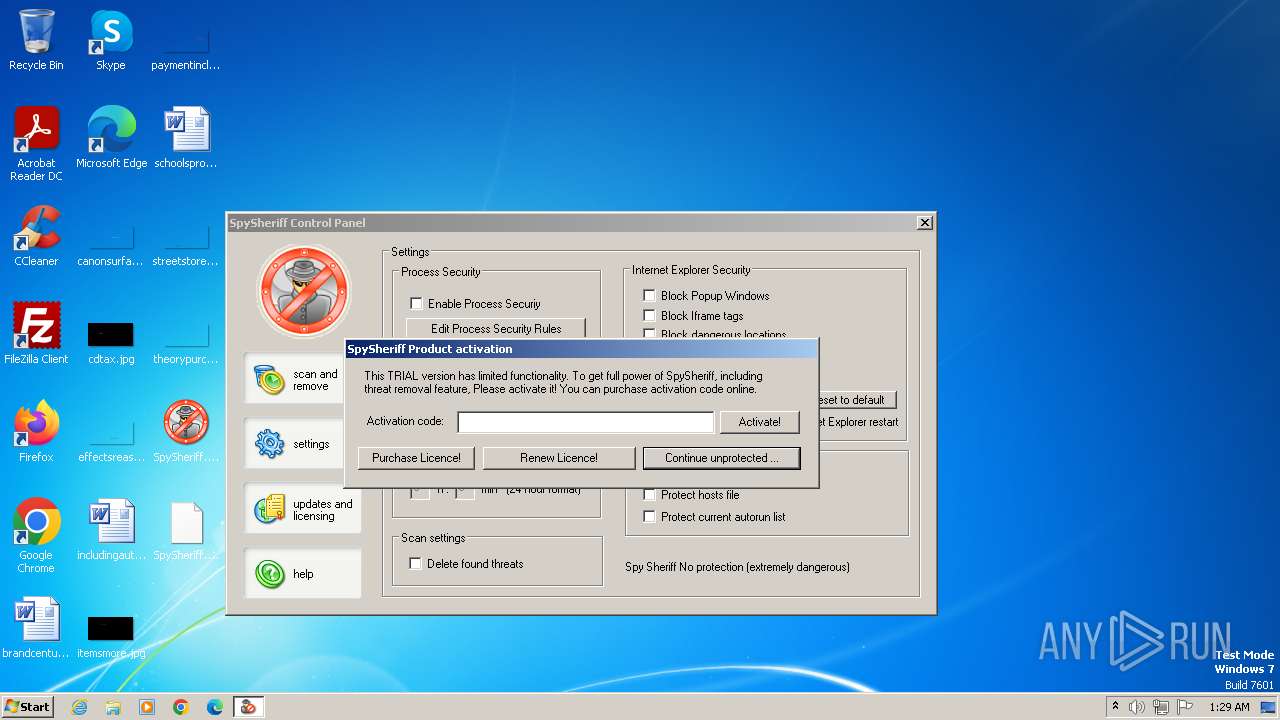
2632 | iexplore.exe | GET | 500 | 15.197.240.20:80 | http://www.spy-sheriff.com/license.php?s=3300537927&a=0&sa=0&ln=0&vrt=3 | US | html | 97 b | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 224.0.0.252:5355 | — | — | — | whitelisted |
1108 | svchost.exe | 224.0.0.252:5355 | — | — | — | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
2156 | chrome.exe | 108.177.127.84:443 | accounts.google.com | GOOGLE | US | whitelisted |
3228 | chrome.exe | 239.255.255.250:1900 | — | — | — | whitelisted |
2156 | chrome.exe | 142.250.186.131:443 | clientservices.googleapis.com | GOOGLE | US | whitelisted |
2156 | chrome.exe | 172.217.18.4:443 | www.google.com | GOOGLE | US | whitelisted |
2156 | chrome.exe | 142.250.185.67:443 | update.googleapis.com | GOOGLE | US | whitelisted |
2156 | chrome.exe | 142.250.181.227:443 | www.gstatic.com | GOOGLE | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
google.com |
| whitelisted |
clientservices.googleapis.com |
| whitelisted |
accounts.google.com |
| whitelisted |
www.google.com |
| whitelisted |
update.googleapis.com |
| whitelisted |
www.gstatic.com |
| whitelisted |
fonts.gstatic.com |
| whitelisted |
content-autofill.googleapis.com |
| whitelisted |
www.spy-sheriff.com |
| unknown |
go.microsoft.com |
| whitelisted |
Process | Message |
|---|---|
msedge.exe | [1221/012946.641:ERROR:process_info.cc(617)] range at 0x0, size 0x18 fully unreadable
|
msedge.exe | [1221/012946.657:ERROR:process_info.cc(617)] range at 0x0, size 0x18 fully unreadable
|
msedge.exe | [1221/012948.891:ERROR:filesystem_win.cc(130)] GetFileAttributes C:\Users\Administrator\AppData\Local\Microsoft\Edge\User Data\Crashpad\attachments\63507ade-059c-4cc8-94da-aba44fed84ae: The system cannot find the file specified. (0x2)
|
msedge.exe | [1221/012948.891:ERROR:filesystem_win.cc(130)] GetFileAttributes C:\Users\Administrator\AppData\Local\Microsoft\Edge\User Data\Crashpad\attachments\63507ade-059c-4cc8-94da-aba44fed84ae: The system cannot find the file specified. (0x2)
|
msedge.exe | [1221/012948.923:ERROR:filesystem_win.cc(130)] GetFileAttributes C:\Users\Administrator\AppData\Local\Microsoft\Edge\User Data\Crashpad\attachments\63507ade-059c-4cc8-94da-aba44fed84ae: The system cannot find the file specified. (0x2)
|
msedge.exe | [1221/012948.923:ERROR:filesystem_win.cc(130)] GetFileAttributes C:\Users\Administrator\AppData\Local\Microsoft\Edge\User Data\Crashpad\attachments\63507ade-059c-4cc8-94da-aba44fed84ae: The system cannot find the file specified. (0x2)
|
msedge.exe | [1221/012949.926:ERROR:process_info.cc(617)] range at 0x0, size 0x18 fully unreadable
|
msedge.exe | [1221/012949.942:ERROR:process_info.cc(617)] range at 0x0, size 0x18 fully unreadable
|
msedge.exe | [1221/012951.130:ERROR:filesystem_win.cc(130)] GetFileAttributes C:\Users\Administrator\AppData\Local\Microsoft\Edge\User Data\Crashpad\attachments\63507ade-059c-4cc8-94da-aba44fed84ae: The system cannot find the file specified. (0x2)
|
msedge.exe | [1221/012951.130:ERROR:filesystem_win.cc(130)] GetFileAttributes C:\Users\Administrator\AppData\Local\Microsoft\Edge\User Data\Crashpad\attachments\32cf6318-f881-401e-ae18-c5e3037ae749: The system cannot find the file specified. (0x2)
|