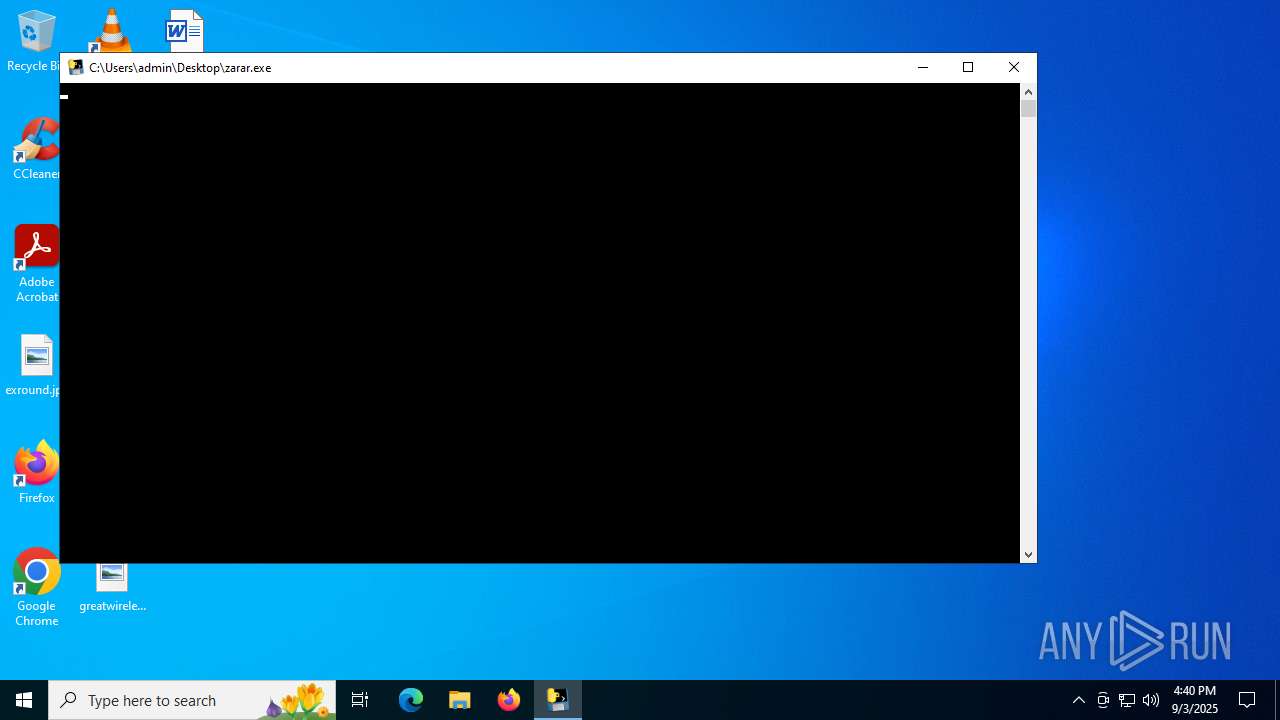
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | zarar.exe |
| Full analysis: | https://app.any.run/tasks/8eccae52-8985-41fa-a3ab-0a72f6a77514 |
| Verdict: | Malicious activity |
| Threats: | Stealers are a group of malicious software that are intended for gaining unauthorized access to users’ information and transferring it to the attacker. The stealer malware category includes various types of programs that focus on their particular kind of data, including files, passwords, and cryptocurrency. Stealers are capable of spying on their targets by recording their keystrokes and taking screenshots. This type of malware is primarily distributed as part of phishing campaigns. |
| Analysis date: | September 03, 2025, 16:39:58 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32+ executable (console) x86-64, for MS Windows, 7 sections |
| MD5: | 744FE0EC235C0A61E4E0BD7A8EF847E2 |
| SHA1: | A399E8CC740B85AAEDF31F7504B794C28E0E4D65 |
| SHA256: | 5B4679B596A3B604EE296FA6B2F9896689C3D330F3FF81E7FE6926BDFD1DFF71 |
| SSDEEP: | 196608:qhBiCWMG+A7q/T+pmkwQb3LTyYPu7Nddg7JVSRDKAmnu:2vWJzq/qkkz7TywcNddSJ0rmnu |
| .exe | | | InstallShield setup (57.6) |
|---|---|---|
| .exe | | | Win64 Executable (generic) (36.9) |
| .exe | | | Generic Win/DOS Executable (2.6) |
| .exe | | | DOS Executable Generic (2.6) |
| MachineType: | AMD AMD64 |
|---|---|
| TimeStamp: | 2025:09:03 16:11:30+00:00 |
| ImageFileCharacteristics: | Executable, Large address aware |
| PEType: | PE32+ |
| LinkerVersion: | 14.43 |
| CodeSize: | 179712 |
| InitializedDataSize: | 155136 |
| UninitializedDataSize: | - |
| EntryPoint: | 0xc650 |
| OSVersion: | 6 |
| ImageVersion: | - |
| SubsystemVersion: | 6 |
| Subsystem: | Windows command line |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 620 | "C:\Users\admin\Desktop\zarar.exe" | C:\Users\admin\Desktop\zarar.exe | zarar.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
ims-api(PID) Process(620) zarar.exe Telegram-Tokens (1)7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI Telegram-Info-Links 7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI Get info about bothttps://api.telegram.org/bot7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI/getMe Get incoming updateshttps://api.telegram.org/bot7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI/getUpdates Get webhookhttps://api.telegram.org/bot7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI/getWebhookInfo Delete webhookhttps://api.telegram.org/bot7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI/deleteWebhook Drop incoming updateshttps://api.telegram.org/bot7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI/deleteWebhook?drop_pending_updates=true (PID) Process(620) zarar.exe Telegram-Tokens (1)7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI Telegram-Info-Links 7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI Get info about bothttps://api.telegram.org/bot7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI/getMe Get incoming updateshttps://api.telegram.org/bot7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI/getUpdates Get webhookhttps://api.telegram.org/bot7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI/getWebhookInfo Delete webhookhttps://api.telegram.org/bot7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI/deleteWebhook Drop incoming updateshttps://api.telegram.org/bot7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI/deleteWebhook?drop_pending_updates=true Telegram-Requests Token7846233211:AAFzKPEOS43qwV6cKb0sFuWX88c5AFeB0VI End-PointsendMessage Args | |||||||||||||||
| 888 | "C:\Users\admin\Desktop\zarar.exe" | C:\Users\admin\Desktop\zarar.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 1096 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2200 | C:\WINDOWS\system32\svchost.exe -k NetworkService -p -s Dnscache | C:\Windows\System32\svchost.exe | services.exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Host Process for Windows Services Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2464 | schtasks /create /tn "WindowsUpdateService6111" /tr "python \"C:\Users\admin\AppData\Local\Temp\_MEI8882\zarar.py\"" /sc onlogon /f | C:\Windows\System32\schtasks.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Task Scheduler Configuration Tool Exit code: 1 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3736 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | zarar.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6808 | C:\WINDOWS\system32\cmd.exe /c "schtasks /create /tn "WindowsUpdateService6111" /tr "python \"C:\Users\admin\AppData\Local\Temp\_MEI8882\zarar.py\"" /sc onlogon /f" | C:\Windows\System32\cmd.exe | zarar.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 1 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| (PID) Process: | (620) zarar.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run |
| Operation: | write | Name: | WindowsUpdateService4596 |
Value: python "C:\Users\admin\AppData\Local\Temp\_MEI8882\zarar.py" | |||
| (PID) Process: | (620) zarar.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\RunOnce |
| Operation: | write | Name: | WindowsUpdateService5001 |
Value: python "C:\Users\admin\AppData\Local\Temp\_MEI8882\zarar.py" | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 888 | zarar.exe | C:\Users\admin\AppData\Local\Temp\_MEI8882\Pythonwin\win32ui.pyd | executable | |
MD5:621449EFF843B6128E15BA20B40E2688 | SHA256:AA9F43412393CD50340570ABF6AE6FD5C3A2119555B5D6CAF43AC693CC2AA244 | |||
| 888 | zarar.exe | C:\Users\admin\AppData\Local\Temp\_MEI8882\_bz2.pyd | executable | |
MD5:30F396F8411274F15AC85B14B7B3CD3D | SHA256:CB15D6CC7268D3A0BD17D9D9CEC330A7C1768B1C911553045C73BC6920DE987F | |||
| 888 | zarar.exe | C:\Users\admin\AppData\Local\Temp\_MEI8882\_hashlib.pyd | executable | |
MD5:A25BC2B21B555293554D7F611EAA75EA | SHA256:43ACECDC00DD5F9A19B48FF251106C63C975C732B9A2A7B91714642F76BE074D | |||
| 888 | zarar.exe | C:\Users\admin\AppData\Local\Temp\_MEI8882\_overlapped.pyd | executable | |
MD5:737F46E8DAC553427A823C5F0556961C | SHA256:2187281A097025C03991CD8EB2C9CA416278B898BD640A8732421B91ADA607E8 | |||
| 888 | zarar.exe | C:\Users\admin\AppData\Local\Temp\_MEI8882\VCRUNTIME140.dll | executable | |
MD5:BE8DBE2DC77EBE7F88F910C61AEC691A | SHA256:4D292623516F65C80482081E62D5DADB759DC16E851DE5DB24C3CBB57B87DB83 | |||
| 888 | zarar.exe | C:\Users\admin\AppData\Local\Temp\_MEI8882\Pythonwin\mfc140u.dll | executable | |
MD5:84B82C149B450D3C8E0D06F09A416B5D | SHA256:1EC2A31A1302E720C799BAD2FD90CF3457C6B2A375C4B41FAEFEE1A91D92F3E0 | |||
| 888 | zarar.exe | C:\Users\admin\AppData\Local\Temp\_MEI8882\_asyncio.pyd | executable | |
MD5:90A38A8271379A371A2A4C580E9CD97D | SHA256:3B46FA8F966288EAD65465468C8E300B9179F5D7B39AA25D7231FF3702CA7887 | |||
| 888 | zarar.exe | C:\Users\admin\AppData\Local\Temp\_MEI8882\VCRUNTIME140_1.dll | executable | |
MD5:F8DFA78045620CF8A732E67D1B1EB53D | SHA256:A113F192195F245F17389E6ECBED8005990BCB2476DDAD33F7C4C6C86327AFE5 | |||
| 888 | zarar.exe | C:\Users\admin\AppData\Local\Temp\_MEI8882\_ctypes.pyd | executable | |
MD5:5377AB365C86BBCDD998580A79BE28B4 | SHA256:6C5F31BEF3FDBFF31BEAC0B1A477BE880DDA61346D859CF34CA93B9291594D93 | |||
| 888 | zarar.exe | C:\Users\admin\AppData\Local\Temp\_MEI8882\_cffi_backend.cp312-win_amd64.pyd | executable | |
MD5:FCB71CE882F99EC085D5875E1228BDC1 | SHA256:86F136553BA301C70E7BADA8416B77EB4A07F76CCB02F7D73C2999A38FA5FA5B | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
1268 | svchost.exe | GET | 200 | 2.16.164.131:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 825 b | whitelisted |
5944 | MoUsoCoreWorker.exe | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | NL | binary | 814 b | whitelisted |
5944 | MoUsoCoreWorker.exe | GET | 200 | 2.16.164.131:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 825 b | whitelisted |
5460 | RUXIMICS.exe | GET | 200 | 2.16.164.131:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 825 b | whitelisted |
1268 | svchost.exe | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | NL | binary | 814 b | whitelisted |
5460 | RUXIMICS.exe | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | NL | binary | 814 b | whitelisted |
— | — | POST | 200 | 20.190.160.65:443 | https://login.live.com/RST2.srf | US | xml | 1.24 Kb | unknown |
— | — | POST | 400 | 20.190.160.132:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | unknown |
— | — | POST | 400 | 20.190.160.65:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | unknown |
— | — | POST | 400 | 20.190.160.130:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
1268 | svchost.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
5944 | MoUsoCoreWorker.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5460 | RUXIMICS.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
1268 | svchost.exe | 2.16.164.131:80 | crl.microsoft.com | Akamai International B.V. | NL | whitelisted |
5944 | MoUsoCoreWorker.exe | 2.16.164.131:80 | crl.microsoft.com | Akamai International B.V. | NL | whitelisted |
5460 | RUXIMICS.exe | 2.16.164.131:80 | crl.microsoft.com | Akamai International B.V. | NL | whitelisted |
5944 | MoUsoCoreWorker.exe | 95.101.149.131:80 | www.microsoft.com | Akamai International B.V. | NL | whitelisted |
1268 | svchost.exe | 95.101.149.131:80 | www.microsoft.com | Akamai International B.V. | NL | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
login.live.com |
| whitelisted |
api.telegram.org |
| whitelisted |
api.gofile.io |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |
self.events.data.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2200 | svchost.exe | Misc activity | ET HUNTING Telegram API Domain in DNS Lookup |
620 | zarar.exe | Misc activity | ET HUNTING Observed Telegram API Domain (api .telegram .org in TLS SNI) |
2200 | svchost.exe | Potentially Bad Traffic | ET FILE_SHARING Online File Storage Domain in DNS Lookup (gofile .io) |
620 | zarar.exe | Misc activity | ET FILE_SHARING File Sharing Related Domain in TLS SNI (gofile .io) |
620 | zarar.exe | Misc activity | ET FILE_SHARING File Sharing Related Domain in TLS SNI (gofile .io) |
620 | zarar.exe | Misc activity | ET FILE_SHARING File Sharing Related Domain in TLS SNI (gofile .io) |
620 | zarar.exe | Misc activity | ET FILE_SHARING File Sharing Related Domain in TLS SNI (gofile .io) |
620 | zarar.exe | Misc activity | ET FILE_SHARING File Sharing Related Domain in TLS SNI (gofile .io) |
620 | zarar.exe | Misc activity | ET FILE_SHARING File Sharing Related Domain in TLS SNI (gofile .io) |
620 | zarar.exe | Misc activity | ET FILE_SHARING File Sharing Related Domain in TLS SNI (gofile .io) |