ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | T1.exe |
| Full analysis: | https://app.any.run/tasks/443f8ce6-2326-4860-8a2f-40e600903be7 |
| Verdict: | Malicious activity |
| Analysis date: | April 06, 2025, 16:44:20 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32+ executable (console) x86-64, for MS Windows, 7 sections |
| MD5: | 60A2EB80992E0B23DBFF507CBAEC4B3D |
| SHA1: | 115B5CBD0FC9804ABF6A8160CB684CAB5C8F9578 |
| SHA256: | 55C73E761C550A377E94BD155F0C1B13FBD71FF121EA917AA3481692865C5EC6 |
| SSDEEP: | 98304:8xb2htCFdaNoMZqeLnc1ZaDPHUFK/uXbQKn352U09wW6yb2fg/BgKxCJRFl4Jx6R:pgK8YPWBCTyYpNUfuGhMU9z |
| .exe | | | Win64 Executable (generic) (87.3) |
|---|---|---|
| .exe | | | Generic Win/DOS Executable (6.3) |
| .exe | | | DOS Executable Generic (6.3) |
| MachineType: | AMD AMD64 |
|---|---|
| TimeStamp: | 2025:04:06 16:42:32+00:00 |
| ImageFileCharacteristics: | Executable, Large address aware |
| PEType: | PE32+ |
| LinkerVersion: | 14.42 |
| CodeSize: | 178688 |
| InitializedDataSize: | 153600 |
| UninitializedDataSize: | - |
| EntryPoint: | 0xc380 |
| OSVersion: | 6 |
| ImageVersion: | - |
| SubsystemVersion: | 6 |
| Subsystem: | Windows command line |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
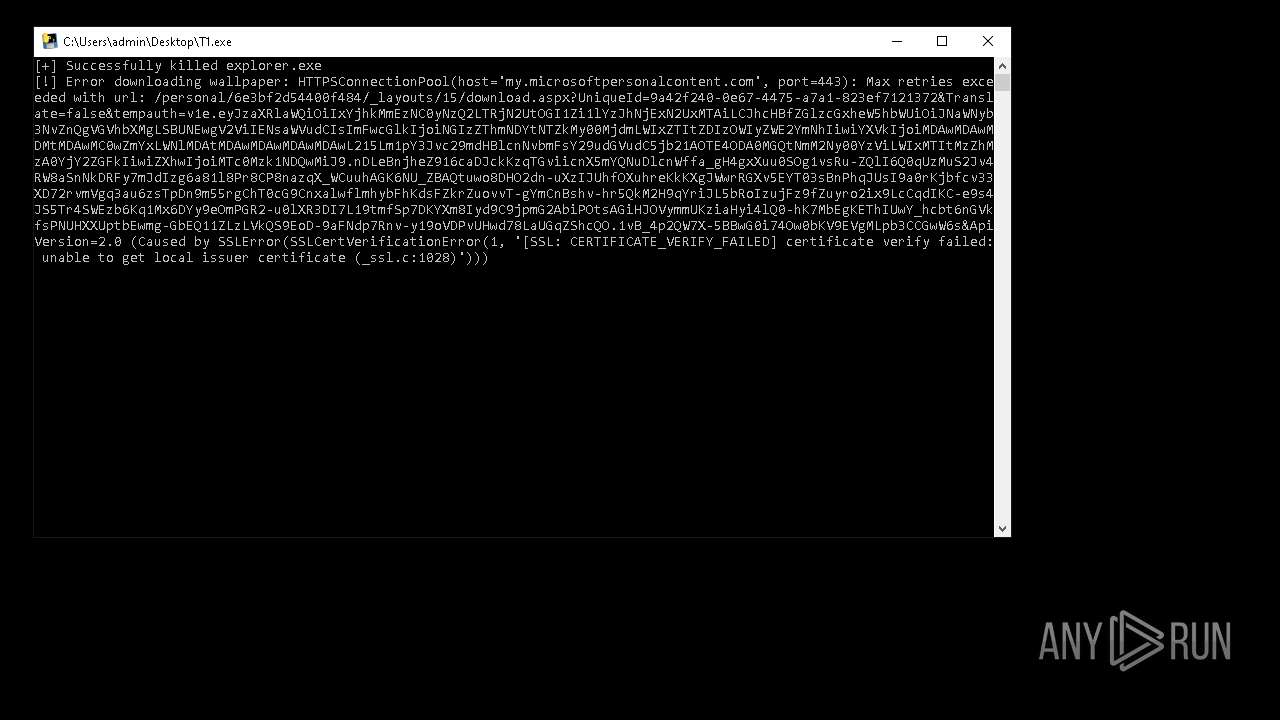
| 920 | taskkill /f /im explorer.exe | C:\Windows\System32\taskkill.exe | — | T1.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Terminates Processes Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
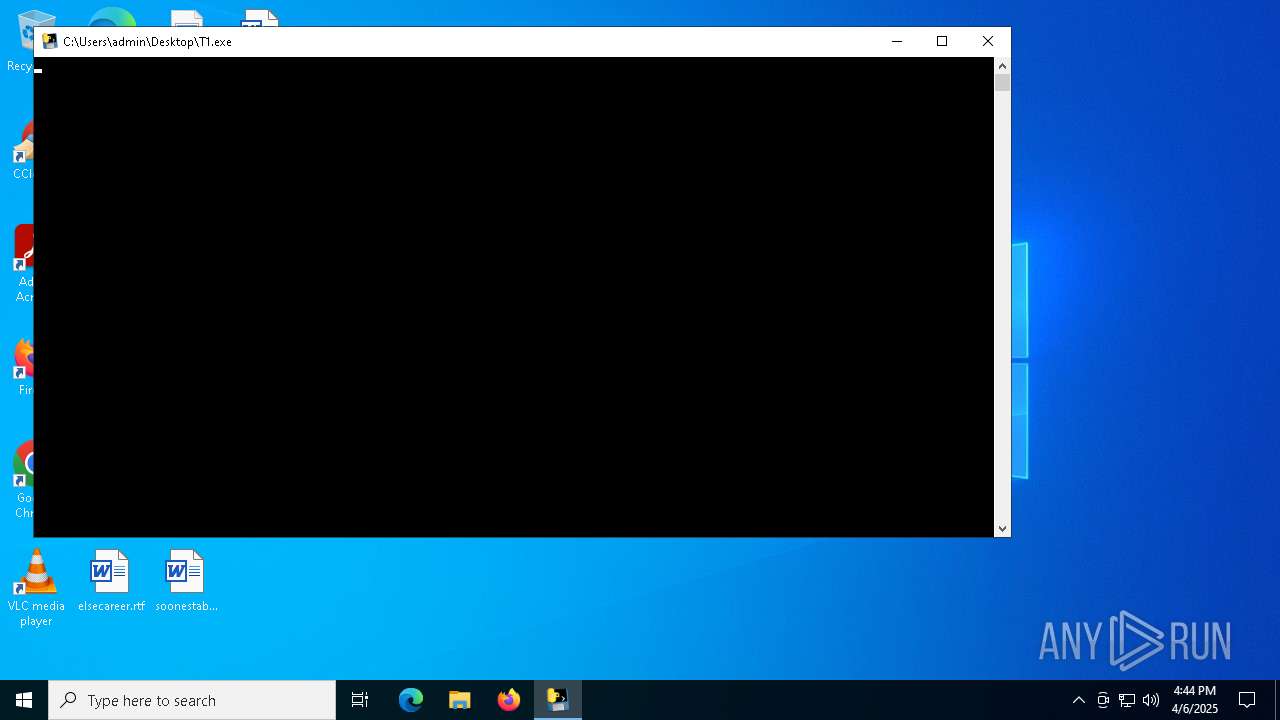
| 1324 | "C:\Users\admin\Desktop\T1.exe" | C:\Users\admin\Desktop\T1.exe | T1.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 3268 | C:\WINDOWS\system32\cmd.exe /c "netsh advfirewall firewall add rule name="AllowMyApp" dir=in action=allow program="C:\Program Files\YourApplication\YourApp.exe" enable=yes" | C:\Windows\System32\cmd.exe | — | T1.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 1 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 4976 | netsh advfirewall firewall add rule name="AllowMyApp" dir=in action=allow program="C:\Program Files\YourApplication\YourApp.exe" enable=yes | C:\Windows\System32\netsh.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Network Command Shell Exit code: 1 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5156 | vssadmin delete shadows /all /quiet | C:\Windows\System32\vssadmin.exe | — | T1.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Command Line Interface for Microsoft® Volume Shadow Copy Service Exit code: 2 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5728 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | T1.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6132 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | svchost.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6632 | "C:\WINDOWS\SystemApps\Microsoft.Windows.Search_cw5n1h2txyewy\SearchApp.exe" -ServerName:CortanaUI.AppX8z9r6jm96hw4bsbneegw0kyxx296wr9t.mca | C:\Windows\SystemApps\Microsoft.Windows.Search_cw5n1h2txyewy\SearchApp.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Search application Exit code: 2147945463 Version: 10.0.19041.3996 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6744 | "C:\Users\admin\Desktop\T1.exe" | C:\Users\admin\Desktop\T1.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 6744 | T1.exe | C:\Users\admin\AppData\Local\Temp\_MEI67442\_multiprocessing.pyd | executable | |
MD5:24AEE7D83525CB43AD02FD3116B28274 | SHA256:3262EC7496D397C0B6BFB2F745516E9E225BD9246F78518852C61D559AA89485 | |||
| 6744 | T1.exe | C:\Users\admin\AppData\Local\Temp\_MEI67442\_hashlib.pyd | executable | |
MD5:CF4120BAD9A7F77993DD7A95568D83D7 | SHA256:14765E83996FE6D50AEDC11BB41D7C427A3E846A6A6293A4A46F7EA7E3F14148 | |||
| 6744 | T1.exe | C:\Users\admin\AppData\Local\Temp\_MEI67442\_lzma.pyd | executable | |
MD5:3E73BC69EFB418E76D38BE5857A77027 | SHA256:6F48E7EBA363CB67F3465A6C91B5872454B44FC30B82710DFA4A4489270CE95C | |||
| 6744 | T1.exe | C:\Users\admin\AppData\Local\Temp\_MEI67442\_overlapped.pyd | executable | |
MD5:51E4C701E4EFA92A56ADAF5BDC9CF49B | SHA256:9EF177DB14CFA3AA66193078C431A96B6AE70858E9DD774B3D3E3CB6E39D10A3 | |||
| 6744 | T1.exe | C:\Users\admin\AppData\Local\Temp\_MEI67442\_queue.pyd | executable | |
MD5:59C05030E47BDE800AD937CCB98802D8 | SHA256:E4956834DF819C1758D17C1C42A152306F7C0EA7B457CA24CE2F6466A6CB1CAA | |||
| 6744 | T1.exe | C:\Users\admin\AppData\Local\Temp\_MEI67442\_socket.pyd | executable | |
MD5:69C4A9A654CF6D1684B73A431949B333 | SHA256:8DAEFAFF53E6956F5AEA5279A7C71F17D8C63E2B0D54031C3B9E82FCB0FB84DB | |||
| 6744 | T1.exe | C:\Users\admin\AppData\Local\Temp\_MEI67442\charset_normalizer\md.cp313-win_amd64.pyd | executable | |
MD5:480B5EB45AF69A315BD2C3B1B34459D1 | SHA256:1F8A5173D8BFE6C569E81C738B830800307ED4586D2AE9AC5CC13A468C6E1892 | |||
| 6744 | T1.exe | C:\Users\admin\AppData\Local\Temp\_MEI67442\charset_normalizer\md__mypyc.cp313-win_amd64.pyd | executable | |
MD5:501B867C424A8E3A41A9BE4AB22DBEED | SHA256:437CEB75E7BC7C72C9090558397EF3598B0BC7BC499434AF5827028083D300CA | |||
| 6744 | T1.exe | C:\Users\admin\AppData\Local\Temp\_MEI67442\certifi\cacert.pem | text | |
MD5:234D271ECB91165AAEC148AD6326DD39 | SHA256:C55B21F907F7F86D48ADD093552FB5651749FF5F860508CCBB423D6C1FBD80C7 | |||
| 6744 | T1.exe | C:\Users\admin\AppData\Local\Temp\_MEI67442\_ssl.pyd | executable | |
MD5:CE19076F6B62292ED66FD06E5BA67BBA | SHA256:21CA71B2C1766FC68734CB3D1E7C2C0439B86BCFB95E00B367C5FD48C59E617C | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
— | — | POST | 500 | 40.91.76.224:443 | https://activation-v2.sls.microsoft.com/SLActivateProduct/SLActivateProduct.asmx?configextension=Retail | US | xml | 512 b | whitelisted |
— | — | POST | 500 | 40.91.76.224:443 | https://activation-v2.sls.microsoft.com/SLActivateProduct/SLActivateProduct.asmx?configextension=Retail | US | xml | 512 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
— | — | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
1324 | T1.exe | 13.107.139.11:443 | my.microsoftpersonalcontent.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
1324 | T1.exe | 104.26.13.205:443 | api.ipify.org | CLOUDFLARENET | US | shared |
496 | slui.exe | 40.91.76.224:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
6132 | slui.exe | 40.91.76.224:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
my.microsoftpersonalcontent.com |
| whitelisted |
api.ipify.org |
| shared |
activation-v2.sls.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2196 | svchost.exe | Misc activity | ET INFO External IP Lookup Domain (ipify .org) in DNS Lookup |
1324 | T1.exe | Misc activity | ET INFO External IP Address Lookup Domain (ipify .org) in TLS SNI |