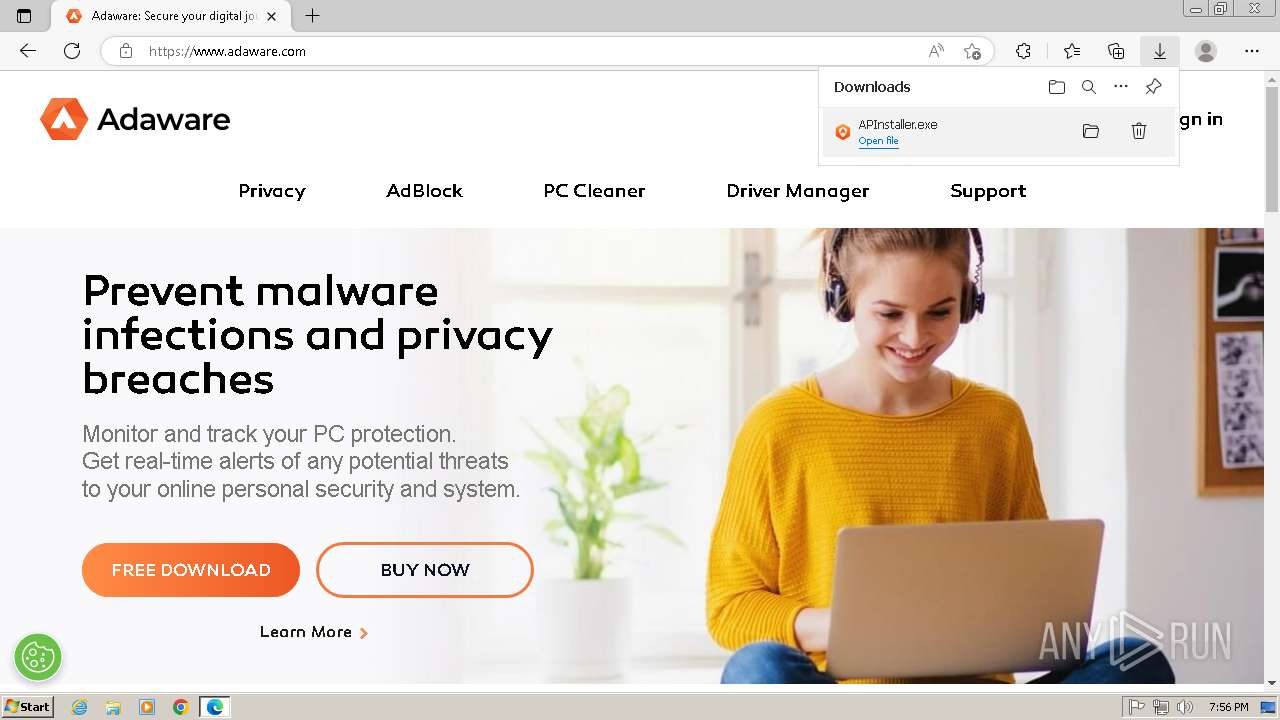
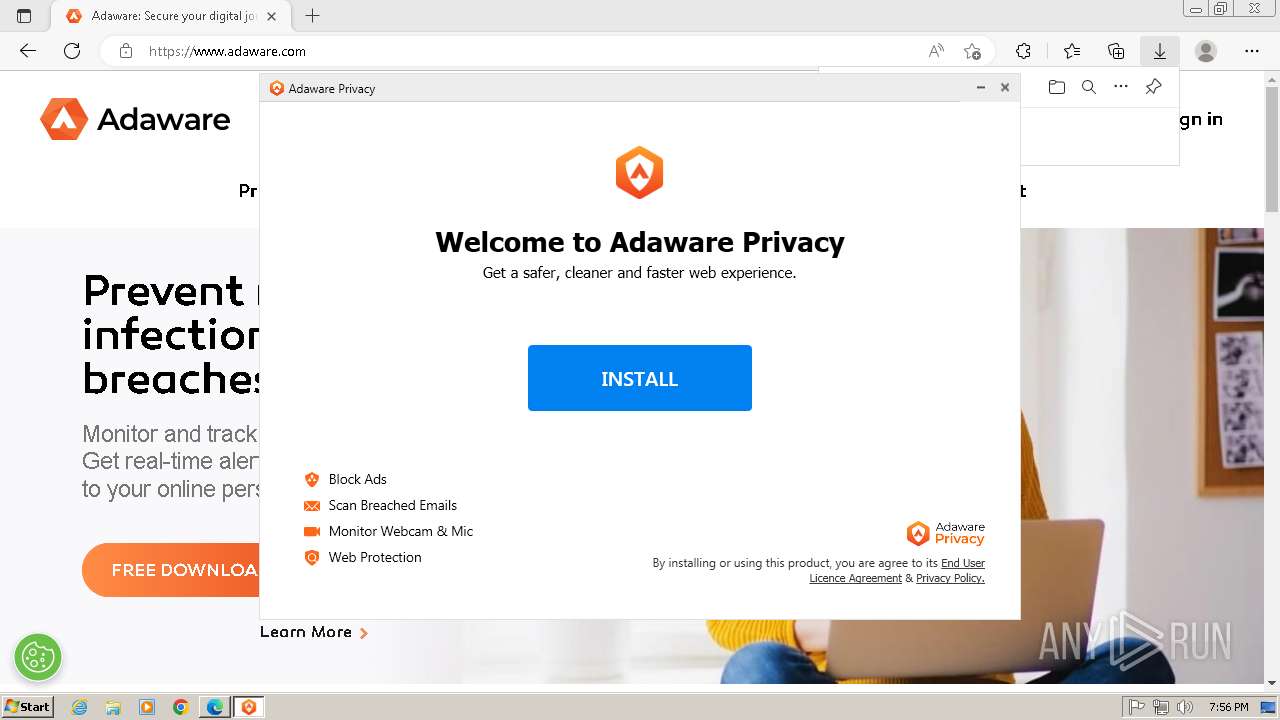
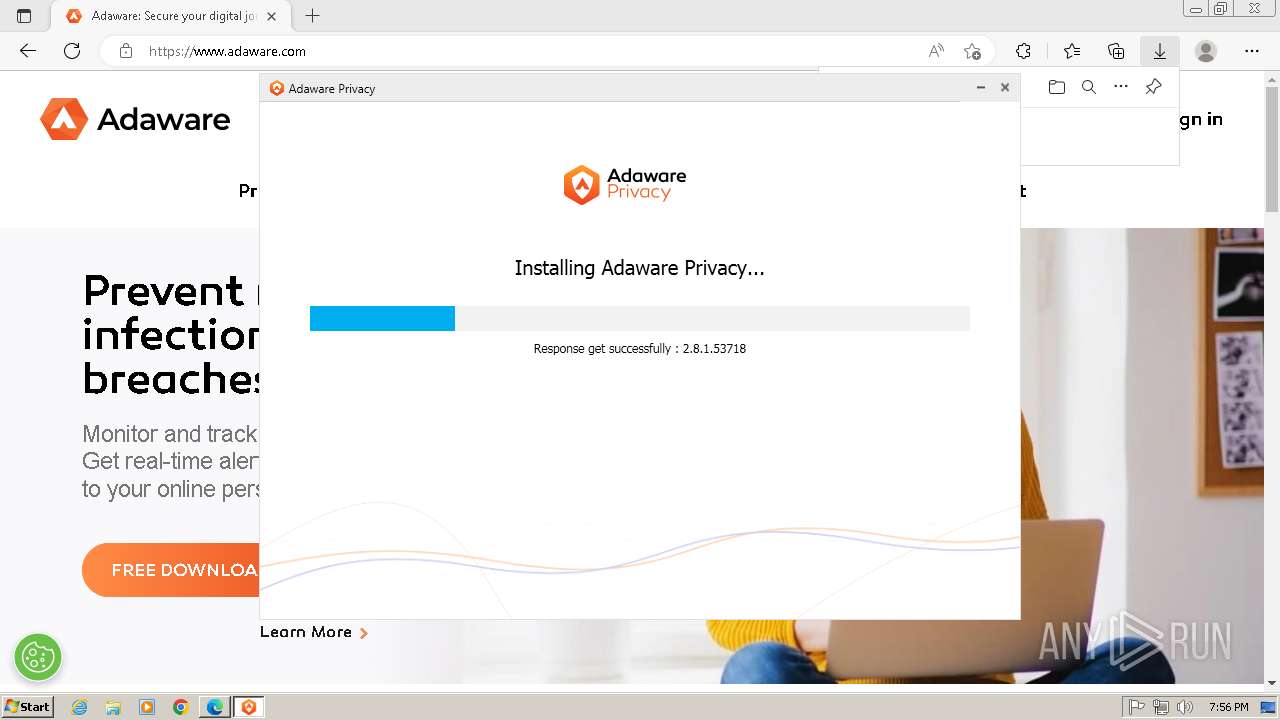
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| URL: | flow.lavasoft.com |
| Full analysis: | https://app.any.run/tasks/97a13955-f077-4fc0-aea0-c705985b7dcd |
| Verdict: | Malicious activity |
| Analysis date: | July 10, 2025, 18:55:54 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MD5: | A725EDA12815D5058BABE2D6F4124B0E |
| SHA1: | 286FF9663332760F0F8139DBEC5B01EE36CAC1DE |
| SHA256: | 4EBA8D9774E5A4C8489542FB2025C2F0F35C976C421E7B69D48054579939B4E6 |
| SSDEEP: | 3:gEEOK:gEu |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1124 | "C:\Program Files\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=quarantine.mojom.Quarantine --lang=en-US --service-sandbox-type=none --disable-quic --mojo-platform-channel-handle=4388 --field-trial-handle=1360,i,6215379166269565269,448774752709982587,131072 --enable-features=msMicrosoftRootStoreUsed /prefetch:8 | C:\Program Files\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Edge Exit code: 0 Version: 109.0.1518.115 Modules
| |||||||||||||||
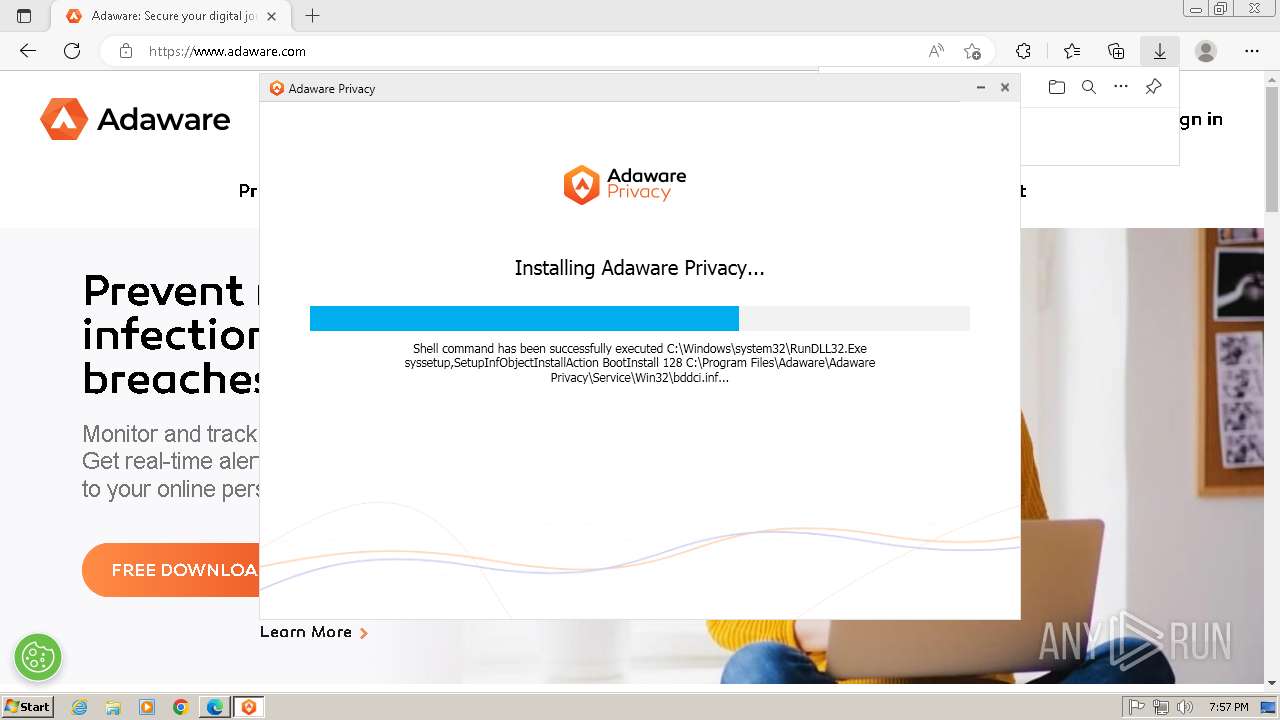
| 1156 | "sc.exe" description "DCIService" "Webprotection Bridge service" | C:\Windows\System32\sc.exe | — | APInstaller.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: A tool to aid in developing services for WindowsNT Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1168 | "C:\Windows\System32\grpconv.exe" -o | C:\Windows\System32\grpconv.exe | — | runonce.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows Progman Group Converter Exit code: 1 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1240 | "C:\Windows\system32\net.exe" start bddci | C:\Windows\System32\net.exe | — | APInstaller.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Net Command Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1404 | tasklist /FI "PID eq 3596" /fo csv | C:\Windows\System32\tasklist.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Lists the current running tasks Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1472 | "C:\Program Files\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=asset_store.mojom.AssetStoreService --lang=en-US --service-sandbox-type=asset_store_service --disable-quic --mojo-platform-channel-handle=2316 --field-trial-handle=1360,i,6215379166269565269,448774752709982587,131072 --enable-features=msMicrosoftRootStoreUsed /prefetch:8 | C:\Program Files\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Exit code: 0 Version: 109.0.1518.115 Modules
| |||||||||||||||
| 1488 | netsh http add urlacl url=http://+:8006/ user=Everyone | C:\Windows\System32\netsh.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Network Command Shell Exit code: 1 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1544 | C:\Windows\system32\cmd.exe /c ""C:\Users\admin\AppData\Local\Temp\ap_remove_resources.bat"" | C:\Windows\System32\cmd.exe | — | APInstaller.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows Command Processor Exit code: 1 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
| 1568 | "C:\Windows\System32\cmd.exe" /C netsh http add urlacl url=http://+:8006/ user=Everyone | C:\Windows\System32\cmd.exe | — | AP-Assistant-Service.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Windows Command Processor Exit code: 0 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
| 1664 | "C:\Program Files\Adaware\Adaware Privacy\Service\Win32\DCIService.exe" | C:\Program Files\Adaware\Adaware Privacy\Service\Win32\DCIService.exe | — | services.exe | |||||||||||
User: SYSTEM Company: Integrity Level: SYSTEM Description: DCIService.exe Version: 4.2.0.24 Modules
xor-url(PID) Process(1664) DCIService.exe Decrypted-URLs (1)http://geo.lavasoft.com/] | |||||||||||||||
| (PID) Process: | (2784) msedge.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | failed_count |
Value: 0 | |||
| (PID) Process: | (2784) msedge.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | state |
Value: 2 | |||
| (PID) Process: | (2784) msedge.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Edge\ThirdParty |
| Operation: | write | Name: | StatusCodes |
Value: | |||
| (PID) Process: | (2784) msedge.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Edge\ThirdParty |
| Operation: | write | Name: | StatusCodes |
Value: 01000000 | |||
| (PID) Process: | (2784) msedge.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | state |
Value: 1 | |||
| (PID) Process: | (2784) msedge.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\EdgeUpdate\ClientState\{56EB18F8-B008-4CBD-B6D2-8C97FE7E9062} |
| Operation: | write | Name: | dr |
Value: 1 | |||
| (PID) Process: | (2784) msedge.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Edge\StabilityMetrics |
| Operation: | write | Name: | user_experience_metrics.stability.exited_cleanly |
Value: 0 | |||
| (PID) Process: | (2784) msedge.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\EdgeUpdate\ClientStateMedium\{56EB18F8-B008-4CBD-B6D2-8C97FE7E9062}\LastWasDefault |
| Operation: | write | Name: | S-1-5-21-1302019708-1500728564-335382590-1000 |
Value: 5F8A0F072E982F00 | |||
| (PID) Process: | (2784) msedge.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\EdgeUpdate\ClientStateMedium\{56EB18F8-B008-4CBD-B6D2-8C97FE7E9062}\FirstNotDefault |
| Operation: | delete value | Name: | S-1-5-21-1302019708-1500728564-335382590-1000 |
Value: | |||
| (PID) Process: | (2784) msedge.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Edge |
| Operation: | write | Name: | UsageStatsInSample |
Value: 1 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2784 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\commerce_subscription_db\LOG.old~RF181076.TMP | — | |
MD5:— | SHA256:— | |||
| 2784 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\commerce_subscription_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 2784 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\EdgePushStorageWithConnectTokenAndKey\LOG.old~RF181085.TMP | — | |
MD5:— | SHA256:— | |||
| 2784 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\EdgePushStorageWithConnectTokenAndKey\LOG.old | — | |
MD5:— | SHA256:— | |||
| 2784 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\LOG.old~RF1810f3.TMP | — | |
MD5:— | SHA256:— | |||
| 2784 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\LOG.old | — | |
MD5:— | SHA256:— | |||
| 3232 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\CrashpadMetrics.pma~RF180ed0.TMP | binary | |
MD5:C612E96CBFAC63232FC2062E15600FB1 | SHA256:DB3C05D5EC0B6719A73E7F0BE84BCE9342772DA70567E7CE08CF6573480B38FF | |||
| 3232 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\CrashpadMetrics.pma | binary | |
MD5:C612E96CBFAC63232FC2062E15600FB1 | SHA256:DB3C05D5EC0B6719A73E7F0BE84BCE9342772DA70567E7CE08CF6573480B38FF | |||
| 2784 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Last Version | text | |
MD5:61FE7896F9494DCDF53480A325F4FB85 | SHA256:ACFD3CD36E0DFCF1DCB67C7F31F2A5B9BA0815528A0C604D4330DFAA9E683E51 | |||
| 2784 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\Sync Data\LevelDB\LOG.old~RF181066.TMP | text | |
MD5:DA58A5ED5A650FE47BBFB2CA6C156D15 | SHA256:A4C01ECF5D00CEE3AC9724408BD58DE8C54A620EF3BFEE44979E965F206598A4 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
2484 | msedge.exe | GET | 200 | 172.64.149.23:80 | http://crt.sectigo.com/SectigoPublicServerAuthenticationRootR46.p7c | US | binary | 4.46 Kb | whitelisted |
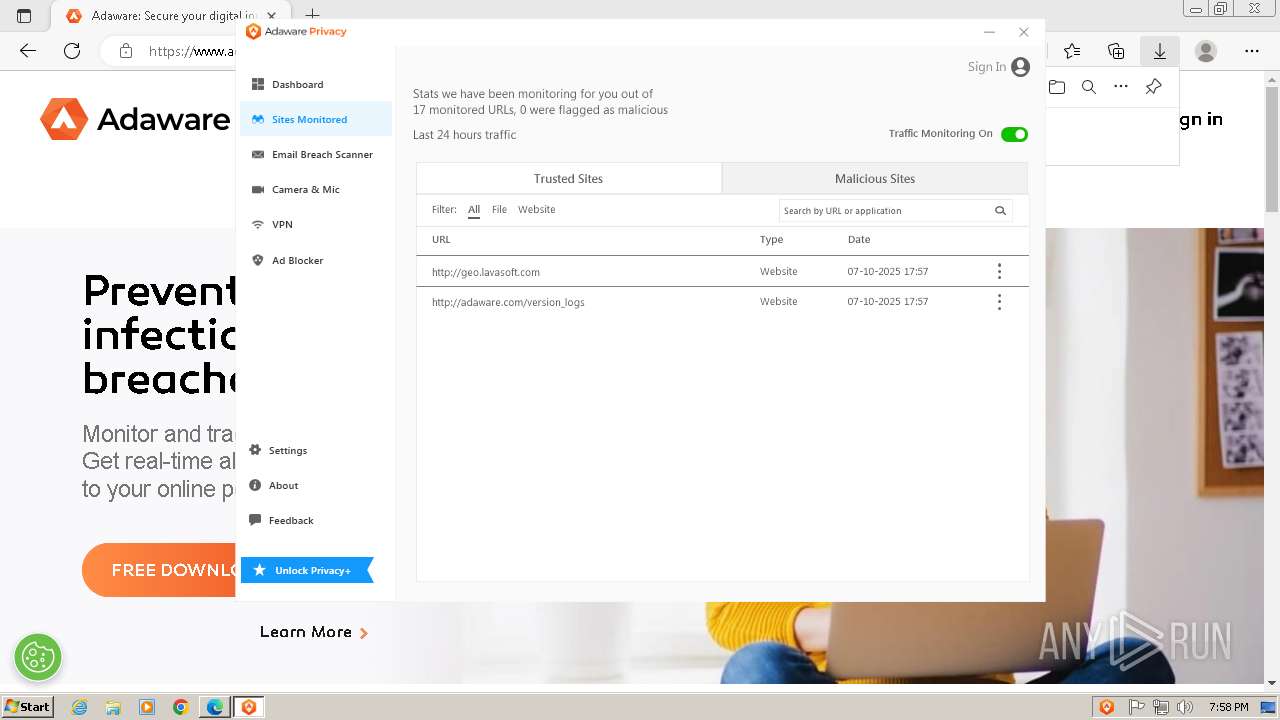
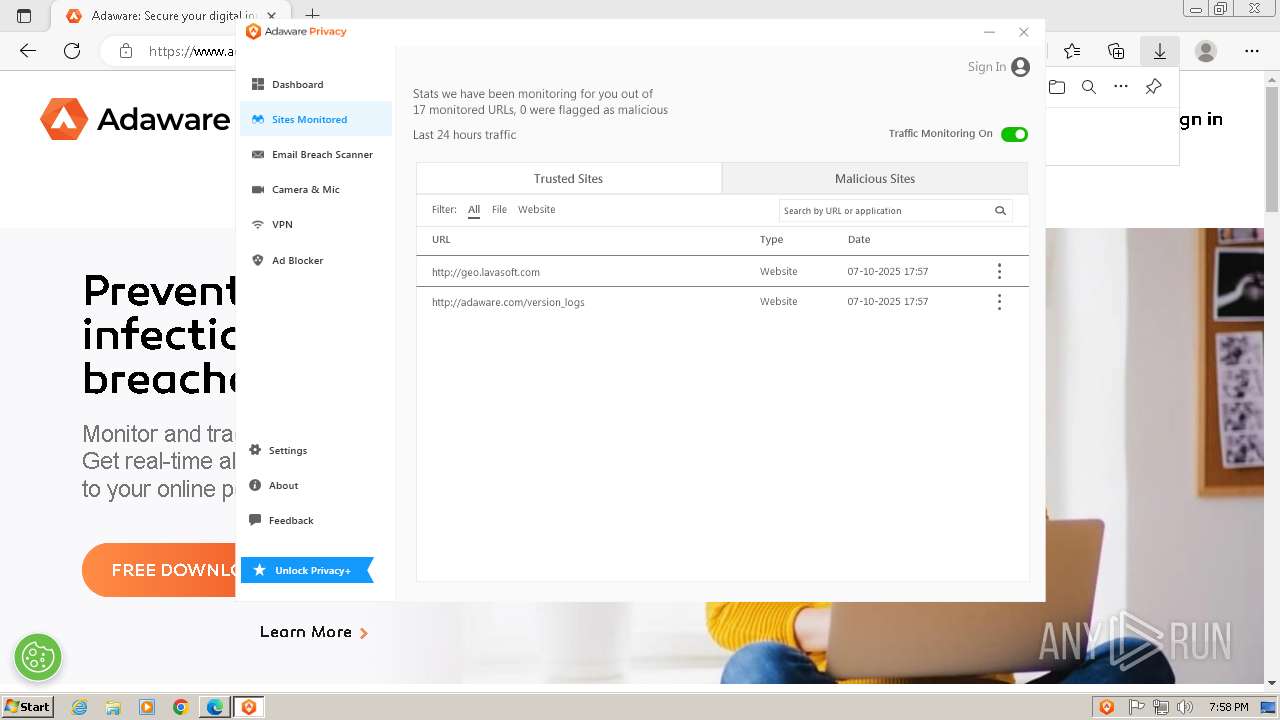
3596 | APInstaller.exe | GET | 200 | 104.16.149.130:80 | http://geo.lavasoft.com/ | unknown | binary | 70 b | whitelisted |
3596 | APInstaller.exe | GET | 200 | 104.16.149.130:80 | http://geo.lavasoft.com/ | unknown | binary | 70 b | whitelisted |
3332 | Adaware-Privacy.exe | GET | 200 | 104.16.149.130:80 | http://geo.lavasoft.com/ | unknown | binary | 70 b | whitelisted |
3332 | Adaware-Privacy.exe | GET | 302 | 104.16.213.94:80 | http://adaware.com/version_logs?json=true&version=2.8.1.53718 | unknown | — | — | whitelisted |
3596 | APInstaller.exe | GET | 200 | 104.16.149.130:80 | http://geo.lavasoft.com/ | unknown | binary | 70 b | whitelisted |
3332 | Adaware-Privacy.exe | GET | 200 | 104.16.149.130:80 | http://geo.lavasoft.com/ | unknown | binary | 70 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 224.0.0.252:5355 | — | — | — | whitelisted |
1080 | svchost.exe | 224.0.0.252:5355 | — | — | — | whitelisted |
2784 | msedge.exe | 239.255.255.250:1900 | — | — | — | whitelisted |
2484 | msedge.exe | 13.107.42.16:443 | config.edge.skype.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
2484 | msedge.exe | 150.171.28.11:443 | edge.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
2484 | msedge.exe | 104.16.149.130:443 | flow.lavasoft.com | CLOUDFLARENET | — | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
2484 | msedge.exe | 150.171.27.11:443 | edge.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
2784 | msedge.exe | 224.0.0.251:5353 | — | — | — | unknown |
Domain | IP | Reputation |
|---|---|---|
google.com |
| whitelisted |
config.edge.skype.com |
| whitelisted |
flow.lavasoft.com |
| whitelisted |
edge.microsoft.com |
| whitelisted |
www.bing.com |
| whitelisted |
lavasoft.com |
| whitelisted |
www.adaware.com |
| whitelisted |
avqtools.avanquest.com |
| whitelisted |
www.googletagmanager.com |
| whitelisted |
avqservice.avanquest.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2484 | msedge.exe | Not Suspicious Traffic | INFO [ANY.RUN] Google Tag Manager analytics (googletagmanager .com) |
2484 | msedge.exe | Not Suspicious Traffic | INFO [ANY.RUN] Google Tag Manager analytics (googletagmanager .com) |
— | — | Potential Corporate Privacy Violation | ET INFO PE EXE or DLL Windows file download HTTP |
— | — | Misc activity | ET INFO EXE - Served Attached HTTP |
Process | Message |
|---|---|
APInstaller.exe | Message: Installer starts
|
APInstaller.exe | Message: ResourceExtractor starts
|
APInstaller.exe | Message: ExtractFileFromAssemblyResources starts
|
APInstaller.exe | Message: ExtractFileFromAssemblyResources filePath=C:\Users\admin\AppData\Local\Temp\APResources\App.config
|
APInstaller.exe | Message: ExtractFileFromAssemblyResources end
|
APInstaller.exe | Message: Extracted App Config PathC:\Users\admin\AppData\Local\Temp\APResources\App.config
|
APInstaller.exe | Message: ResourceExtractor end
|
APInstaller.exe | Message: GetSelfVersion starts
|
APInstaller.exe | Message: InitializeDataCollector starts
|
APInstaller.exe | Message: filePath is C:\Users\admin\Downloads\APInstaller.exe
|