ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | SoundBoosterSetup.exe |
| Full analysis: | https://app.any.run/tasks/e1b85b0e-cbb2-4438-9ede-b944b2254618 |
| Verdict: | Malicious activity |
| Analysis date: | June 20, 2024, 14:10:32 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/x-dosexec |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows |
| MD5: | 99AA185A295411F72303FA9B7A497795 |
| SHA1: | 04CBAB9197165B1648EF6FCBF0D1B60D2E0F7A95 |
| SHA256: | 4C00A2F66BB1D2470B17EF277F5F12A90FF2FC86A258CB82BF294835B87D4E02 |
| SSDEEP: | 98304:hgVrBdoUFz1tgDp5uw27QaYrvBX4+YgnFOt+s0y1m9MRVPCC+RJUrLO5nGj1ysQd:G/rXKWDFWolprO |
| .exe | | | Win32 Executable Delphi generic (57.2) |
|---|---|---|
| .exe | | | Win32 Executable (generic) (18.2) |
| .exe | | | Win16/32 Executable Delphi generic (8.3) |
| .exe | | | Generic Win/DOS Executable (8) |
| .exe | | | DOS Executable Generic (8) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2016:04:06 14:39:04+00:00 |
| ImageFileCharacteristics: | No relocs, Executable, No line numbers, No symbols, Bytes reversed lo, 32-bit, Bytes reversed hi |
| PEType: | PE32 |
| LinkerVersion: | 2.25 |
| CodeSize: | 66560 |
| InitializedDataSize: | 344576 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x117dc |
| OSVersion: | 5 |
| ImageVersion: | 6 |
| SubsystemVersion: | 5 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 1.12.0.538 |
| ProductVersionNumber: | 1.12.0.538 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Win32 |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | Neutral |
| CharacterSet: | Unicode |
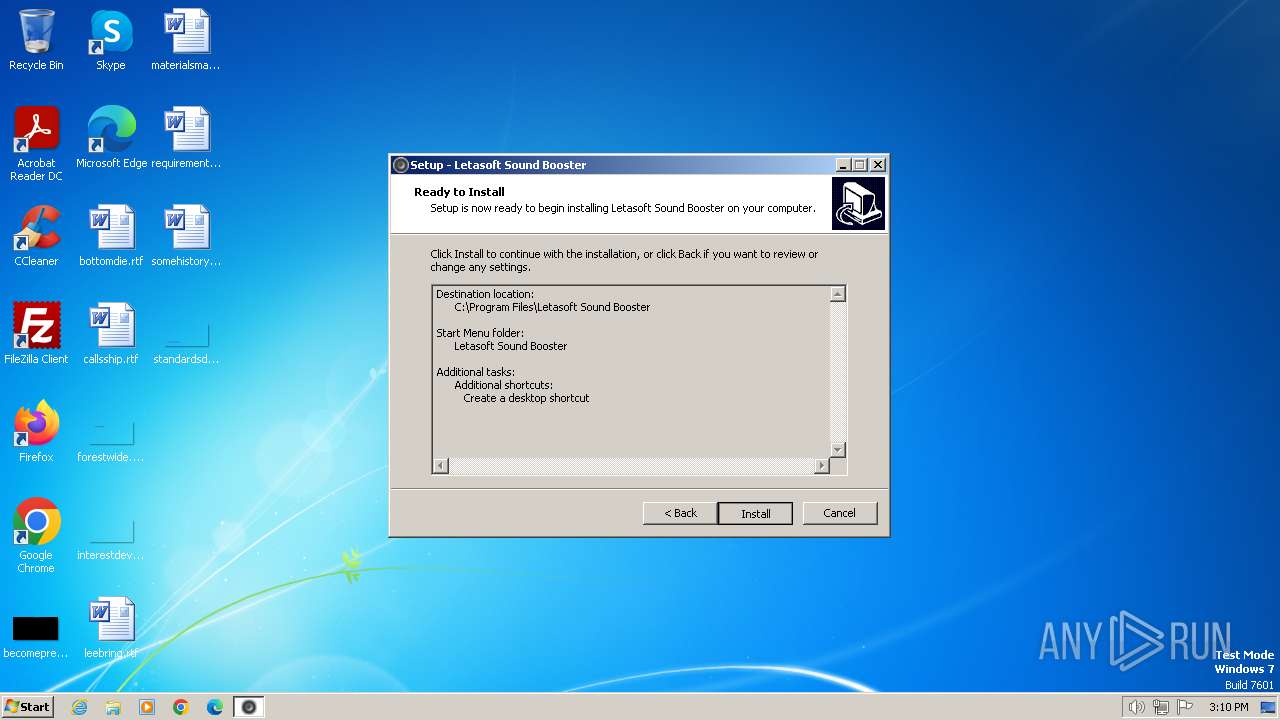
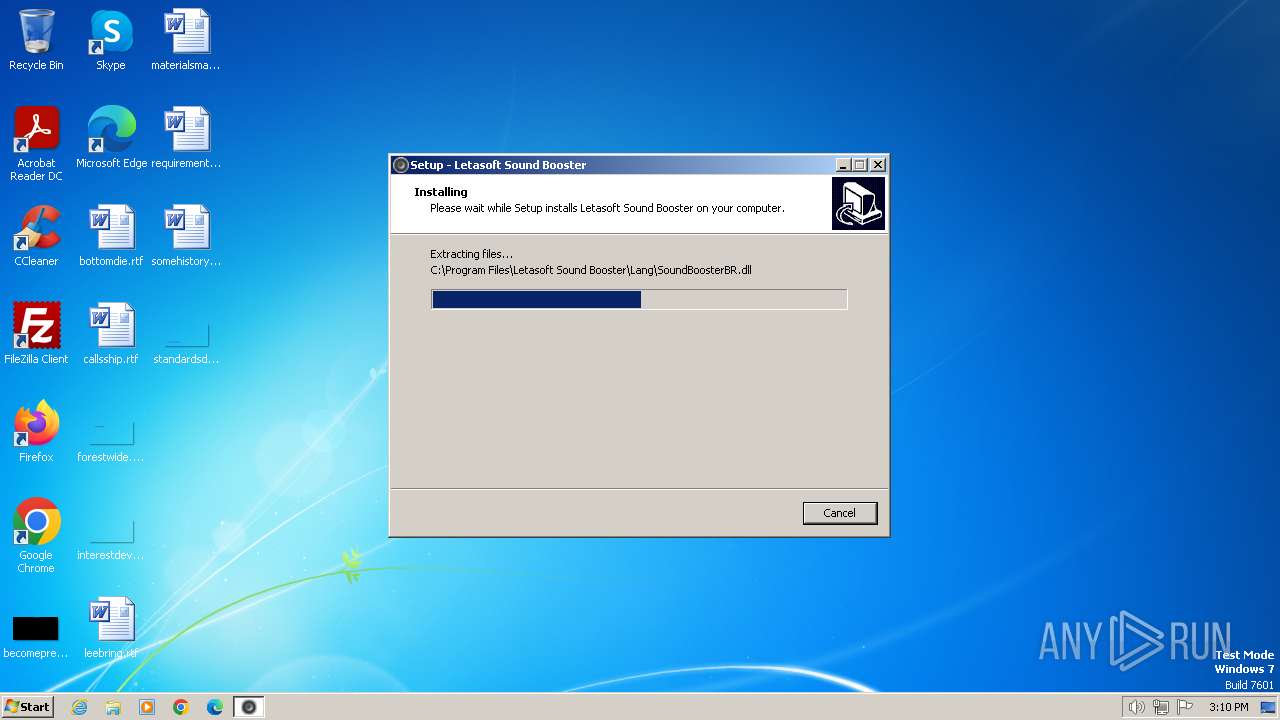
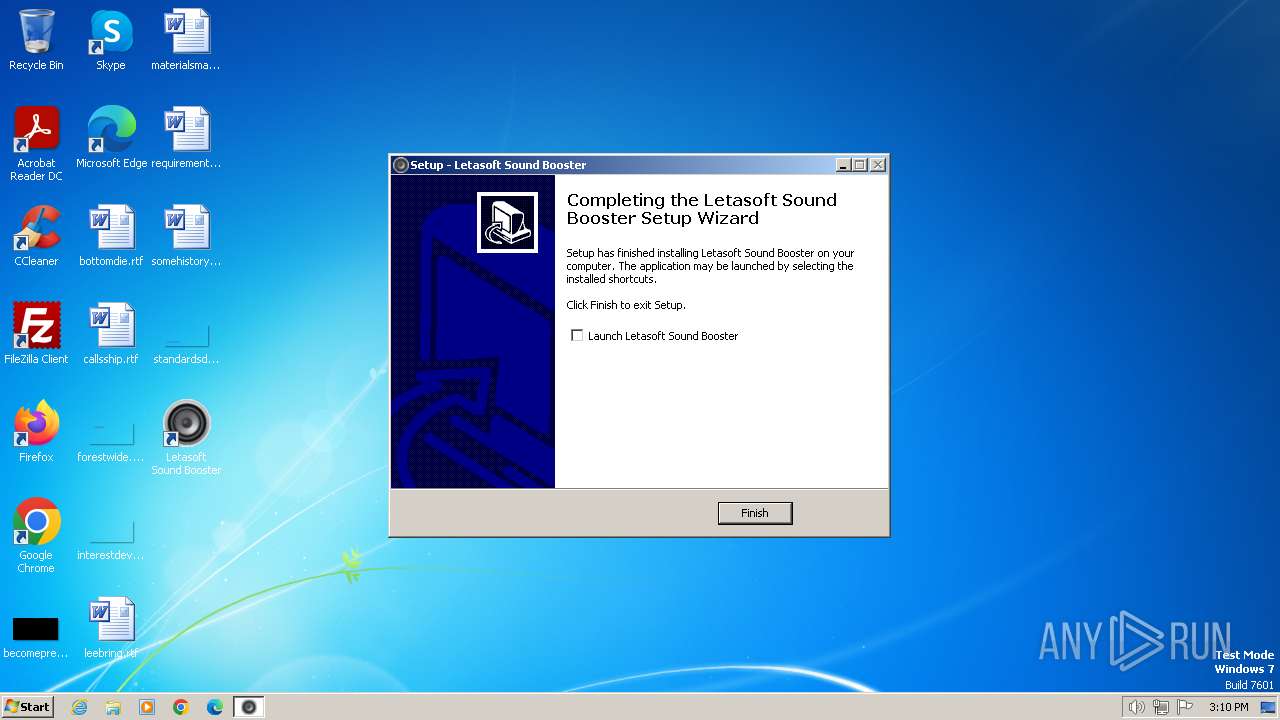
| Comments: | This installation was built with Inno Setup. |
| CompanyName: | Letasoft LLC |
| FileDescription: | Letasoft Sound Booster Setup |
| FileVersion: | 1.12.0.538 |
| LegalCopyright: | Copyright © Letasoft LLC |
| ProductName: | Letasoft Sound Booster |
| ProductVersion: | 1.12.0.538 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 996 | "C:\Windows\System32\regsvr32.exe" /s "C:\Program Files\Letasoft Sound Booster\Sbapo.dll" | C:\Windows\System32\regsvr32.exe | — | SoundBoosterTaskHost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Microsoft(C) Register Server Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1596 | "C:\Program Files\Letasoft Sound Booster\SoundBooster.exe" | C:\Program Files\Letasoft Sound Booster\SoundBooster.exe | — | explorer.exe | |||||||||||
User: admin Company: Letasoft Integrity Level: MEDIUM Description: Sound Booster Application Exit code: 3221226540 Version: 1.12.0.538 Modules
| |||||||||||||||
| 2348 | "C:\Program Files\Letasoft Sound Booster\SoundBoosterTaskHost.exe" -InstallAPO | C:\Program Files\Letasoft Sound Booster\SoundBoosterTaskHost.exe | — | SoundBoosterSetup.tmp | |||||||||||
User: admin Company: Letasoft Integrity Level: HIGH Description: Sound Booster Task Host Application Exit code: 0 Version: 1.12.0.538 Modules
| |||||||||||||||
| 2512 | "C:\Program Files\Letasoft Sound Booster\SoundBooster.exe" | C:\Program Files\Letasoft Sound Booster\SoundBooster.exe | explorer.exe | ||||||||||||
User: admin Company: Letasoft Integrity Level: HIGH Description: Sound Booster Application Version: 1.12.0.538 Modules
| |||||||||||||||
| 2748 | "C:\Users\admin\AppData\Local\Temp\SoundBoosterSetup.exe" /SPAWNWND=$F0168 /NOTIFYWND=$5010A | C:\Users\admin\AppData\Local\Temp\SoundBoosterSetup.exe | SoundBoosterSetup.tmp | ||||||||||||
User: admin Company: Letasoft LLC Integrity Level: HIGH Description: Letasoft Sound Booster Setup Exit code: 0 Version: 1.12.0.538 Modules
| |||||||||||||||
| 2936 | "C:\Users\admin\AppData\Local\Temp\is-UD52G.tmp\SoundBoosterSetup.tmp" /SL5="$7015A,6484768,412160,C:\Users\admin\AppData\Local\Temp\SoundBoosterSetup.exe" /SPAWNWND=$F0168 /NOTIFYWND=$5010A | C:\Users\admin\AppData\Local\Temp\is-UD52G.tmp\SoundBoosterSetup.tmp | SoundBoosterSetup.exe | ||||||||||||
User: admin Integrity Level: HIGH Description: Setup/Uninstall Exit code: 0 Version: 51.1052.0.0 Modules
| |||||||||||||||
| 3296 | "C:\Program Files\Windows Media Player\wmpnscfg.exe" | C:\Program Files\Windows Media Player\wmpnscfg.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Media Player Network Sharing Service Configuration Application Exit code: 0 Version: 12.0.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 3392 | "C:\Users\admin\AppData\Local\Temp\SoundBoosterSetup.exe" | C:\Users\admin\AppData\Local\Temp\SoundBoosterSetup.exe | explorer.exe | ||||||||||||
User: admin Company: Letasoft LLC Integrity Level: MEDIUM Description: Letasoft Sound Booster Setup Exit code: 0 Version: 1.12.0.538 Modules
| |||||||||||||||
| 3424 | "C:\Users\admin\AppData\Local\Temp\is-J16PH.tmp\SoundBoosterSetup.tmp" /SL5="$5010A,6484768,412160,C:\Users\admin\AppData\Local\Temp\SoundBoosterSetup.exe" | C:\Users\admin\AppData\Local\Temp\is-J16PH.tmp\SoundBoosterSetup.tmp | — | SoundBoosterSetup.exe | |||||||||||
User: admin Integrity Level: MEDIUM Description: Setup/Uninstall Exit code: 0 Version: 51.1052.0.0 Modules
| |||||||||||||||
| 3672 | "C:\Program Files\Letasoft Sound Booster\SoundBoosterService.exe" -install | C:\Program Files\Letasoft Sound Booster\SoundBoosterService.exe | — | SoundBoosterSetup.tmp | |||||||||||
User: admin Company: Letasoft Integrity Level: HIGH Description: Sound Booster Service Exit code: 0 Version: 1.12.0.538 Modules
| |||||||||||||||
| (PID) Process: | (2936) SoundBoosterSetup.tmp | Key: | HKEY_CURRENT_USER\Software\Letasoft\Sound Booster |
| Operation: | write | Name: | LangGUI |
Value: 1033 | |||
| (PID) Process: | (2936) SoundBoosterSetup.tmp | Key: | HKEY_CURRENT_USER\Software\Letasoft\Sound Booster\Options |
| Operation: | write | Name: | SoundLevel |
Value: 300 | |||
| (PID) Process: | (2936) SoundBoosterSetup.tmp | Key: | HKEY_CURRENT_USER\Software\Letasoft\Sound Booster\Options |
| Operation: | write | Name: | BoostIsEnabled |
Value: 1 | |||
| (PID) Process: | (2936) SoundBoosterSetup.tmp | Key: | HKEY_CURRENT_USER\Software\Letasoft\Sound Booster\Options |
| Operation: | write | Name: | BoostMethod |
Value: 1 | |||
| (PID) Process: | (2936) SoundBoosterSetup.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Letasoft\Sound Booster |
| Operation: | write | Name: | LangGUI |
Value: 1033 | |||
| (PID) Process: | (2936) SoundBoosterSetup.tmp | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\SecurityProviders\SCHANNEL\Protocols\TLS 1.2\Client |
| Operation: | write | Name: | DisabledByDefault |
Value: 0 | |||
| (PID) Process: | (2936) SoundBoosterSetup.tmp | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\SecurityProviders\SCHANNEL\Protocols\TLS 1.2\Client |
| Operation: | write | Name: | Enabled |
Value: 1 | |||
| (PID) Process: | (2936) SoundBoosterSetup.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{6C6CF38B-11DD-45C6-A15E-A3A0C4CE60F8}_is1 |
| Operation: | write | Name: | Inno Setup: Setup Version |
Value: 5.5.9 (u) | |||
| (PID) Process: | (2936) SoundBoosterSetup.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{6C6CF38B-11DD-45C6-A15E-A3A0C4CE60F8}_is1 |
| Operation: | write | Name: | Inno Setup: App Path |
Value: C:\Program Files\Letasoft Sound Booster | |||
| (PID) Process: | (2936) SoundBoosterSetup.tmp | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\{6C6CF38B-11DD-45C6-A15E-A3A0C4CE60F8}_is1 |
| Operation: | write | Name: | InstallLocation |
Value: C:\Program Files\Letasoft Sound Booster\ | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3392 | SoundBoosterSetup.exe | C:\Users\admin\AppData\Local\Temp\is-J16PH.tmp\SoundBoosterSetup.tmp | executable | |
MD5:A5E43FF07BF378503CF45D6EE7778021 | SHA256:48CC8C44E665CC3A24A1EF0807BCD87BDCC0AD9FF179C8D5C96924EBA48888F2 | |||
| 2748 | SoundBoosterSetup.exe | C:\Users\admin\AppData\Local\Temp\is-UD52G.tmp\SoundBoosterSetup.tmp | executable | |
MD5:A5E43FF07BF378503CF45D6EE7778021 | SHA256:48CC8C44E665CC3A24A1EF0807BCD87BDCC0AD9FF179C8D5C96924EBA48888F2 | |||
| 2936 | SoundBoosterSetup.tmp | C:\Program Files\Letasoft Sound Booster\is-MBEVN.tmp | executable | |
MD5:A5E43FF07BF378503CF45D6EE7778021 | SHA256:48CC8C44E665CC3A24A1EF0807BCD87BDCC0AD9FF179C8D5C96924EBA48888F2 | |||
| 2936 | SoundBoosterSetup.tmp | C:\Program Files\Letasoft Sound Booster\Lang\SoundBoosterBR.dll | executable | |
MD5:04836C4C3228B9E5FCD8A995D38030C5 | SHA256:FAAA95455F9C516CBDB02E233533A7D44E7F6FFB3F850A2ED0482E553FF18E71 | |||
| 2936 | SoundBoosterSetup.tmp | C:\Program Files\Letasoft Sound Booster\Lang\is-3VQ9B.tmp | xml | |
MD5:3F329982989AD24E151F51F513284C12 | SHA256:400B886854892F976A8E327D66F895DC71C3C9CCE42C0E576A69D0A7D129FA88 | |||
| 2936 | SoundBoosterSetup.tmp | C:\Program Files\Letasoft Sound Booster\is-GR7PI.tmp | executable | |
MD5:D9C75A5749132D77AE709C5EAE6FE9DD | SHA256:5A4A4AEBA559B86DB6D95EACC289AD27F84749E35CB51587D26355BF7732548A | |||
| 2936 | SoundBoosterSetup.tmp | C:\Program Files\Letasoft Sound Booster\unins000.exe | executable | |
MD5:A5E43FF07BF378503CF45D6EE7778021 | SHA256:48CC8C44E665CC3A24A1EF0807BCD87BDCC0AD9FF179C8D5C96924EBA48888F2 | |||
| 2936 | SoundBoosterSetup.tmp | C:\Program Files\Letasoft Sound Booster\SoundBooster.exe | executable | |
MD5:73284BAC5AE39DDC8A67EFFE040A3349 | SHA256:E0DD2F06DD96E8167168517CFB611456E3FBEA57A116916D4C4A1AA4D84D35CA | |||
| 2936 | SoundBoosterSetup.tmp | C:\Program Files\Letasoft Sound Booster\is-374BK.tmp | executable | |
MD5:FEDE08587BCE8D2931BAECC55BF2D0C1 | SHA256:9508EEBBDBAE1FC2EB6A4D3D3CF7E12B4EA2CC05DF7F7219B259D5AFC2A7C8CC | |||
| 2936 | SoundBoosterSetup.tmp | C:\Program Files\Letasoft Sound Booster\UltraActivate.dll | executable | |
MD5:FEDE08587BCE8D2931BAECC55BF2D0C1 | SHA256:9508EEBBDBAE1FC2EB6A4D3D3CF7E12B4EA2CC05DF7F7219B259D5AFC2A7C8CC | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
1372 | svchost.exe | GET | 304 | 2.16.100.168:80 | http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/disallowedcertstl.cab?33775f6043c93e33 | DE | — | — | unknown |
1372 | svchost.exe | GET | 200 | 2.16.164.120:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 1.01 Kb | unknown |
2512 | SoundBooster.exe | GET | 200 | 70.32.23.76:80 | http://files.letasoft.com/updates/soundbooster/appver | US | text | 46 b | unknown |
1372 | svchost.exe | GET | 200 | 88.221.169.152:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 973 b | unknown |
2512 | SoundBooster.exe | GET | 200 | 70.32.23.76:80 | http://files.letasoft.com/updates/soundbooster/changelog | US | text | 2.05 Kb | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 239.255.255.250:3702 | — | — | — | unknown |
1372 | svchost.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 224.0.0.252:5355 | — | — | — | unknown |
1060 | svchost.exe | 224.0.0.252:5355 | — | — | — | unknown |
1372 | svchost.exe | 2.16.100.168:80 | ctldl.windowsupdate.com | Akamai International B.V. | DE | whitelisted |
1372 | svchost.exe | 2.16.164.120:80 | crl.microsoft.com | Akamai International B.V. | NL | unknown |
1372 | svchost.exe | 88.221.169.152:80 | www.microsoft.com | AKAMAI-AS | DE | whitelisted |
2512 | SoundBooster.exe | 70.32.23.76:80 | files.letasoft.com | A2HOSTING | US | unknown |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
ctldl.windowsupdate.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
files.letasoft.com |
| unknown |