ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
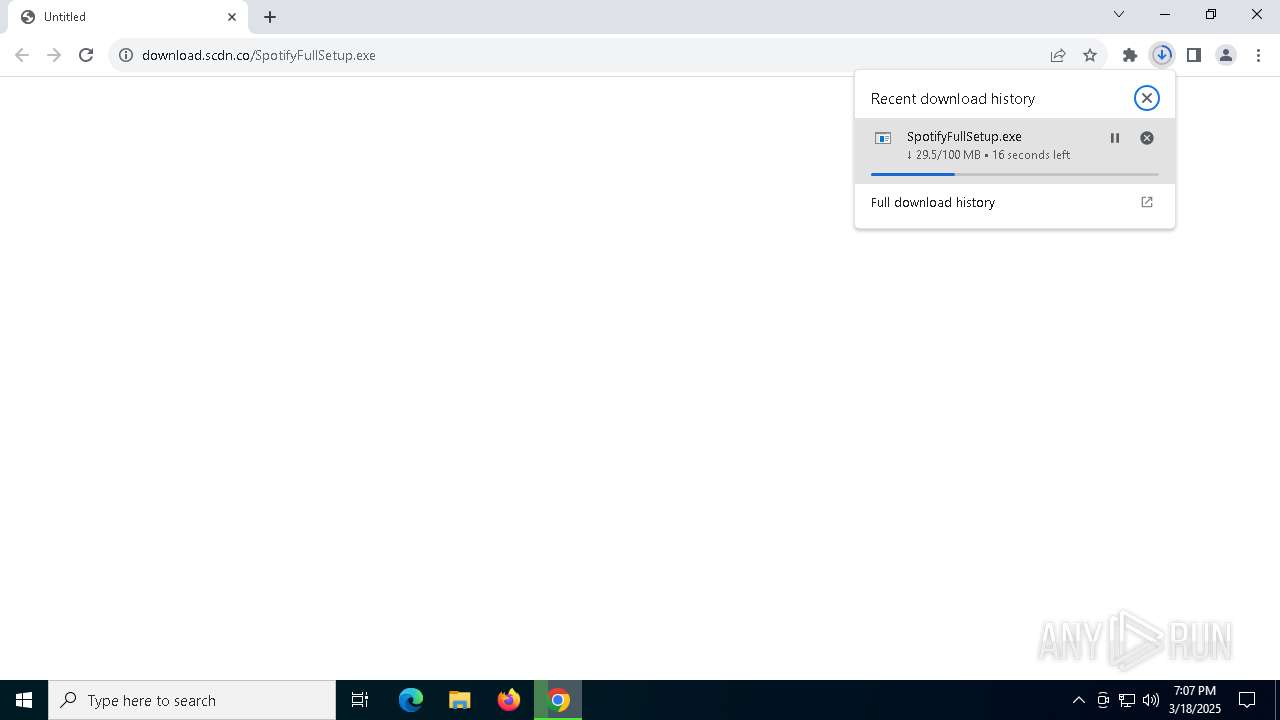
| URL: | https://download.scdn.co/SpotifyFullSetup.exe |
| Full analysis: | https://app.any.run/tasks/96aa34a2-ec55-4e2d-94c6-2e6544b0d18b |
| Verdict: | Malicious activity |
| Analysis date: | March 18, 2025, 19:06:43 |
| OS: | Windows 10 Professional (build: 19045, 64 bit) |
| Tags: | |
| Indicators: | |
| MD5: | B369DB42A10A9E1082726DE267AA473F |
| SHA1: | E88089F475D8476EC87F91D8B99BAD8F902D0268 |
| SHA256: | 4BE0F4F12DFF3608990C250905DC252091DEFF060AD21C7E5B47804E401D13B9 |
| SSDEEP: | 3:N8SEl7LgMHJJvA:2SK7LgkJxA |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 496 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=renderer --no-appcompat-clear --lang=en-US --js-flags=--ms-user-locale= --device-scale-factor=1 --num-raster-threads=2 --enable-main-frame-before-activation --renderer-client-id=6 --mojo-platform-channel-handle=3588 --field-trial-handle=2352,i,13270752764365674776,16201391523505643850,262144 --variations-seed-version /prefetch:1 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Version: 122.0.2365.59 Modules
| |||||||||||||||
| 632 | "C:\Users\admin\AppData\Roaming\Spotify\Spotify.exe" --type=renderer --string-annotations=is-enterprise-managed=no --user-data-dir="C:\Users\admin\AppData\Local\Spotify" --log-severity=disable --user-agent-product="Chrome/131.0.6778.109 Spotify/1.2.53.440" --autoplay-policy=no-user-gesture-required --disable-gpu-compositing --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=2 --enable-main-frame-before-activation --renderer-client-id=6 --field-trial-handle=4896,i,13947090721294360998,8293706266676754734,262144 --disable-features=BackForwardCache,PartitionAllocDanglingPtr,PartitionAllocUnretainedDanglingPtr --variations-seed-version --enable-logging=handle --log-file=4912 --mojo-platform-channel-handle=4908 /prefetch:1 | C:\Users\admin\AppData\Roaming\Spotify\Spotify.exe | — | Spotify.exe | |||||||||||
User: admin Company: Spotify Ltd Integrity Level: LOW Description: Spotify Version: 1.2.53.440 Modules
| |||||||||||||||
| 780 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=chrome.mojom.UtilReadIcon --lang=en-US --service-sandbox-type=icon_reader --disable-quic --no-appcompat-clear --mojo-platform-channel-handle=5152 --field-trial-handle=1920,i,12133758362450695426,17088862455498914844,262144 --disable-features=OptimizationGuideModelDownloading,OptimizationHints,OptimizationHintsFetching,OptimizationTargetPrediction --variations-seed-version /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 122.0.6261.70 Modules
| |||||||||||||||
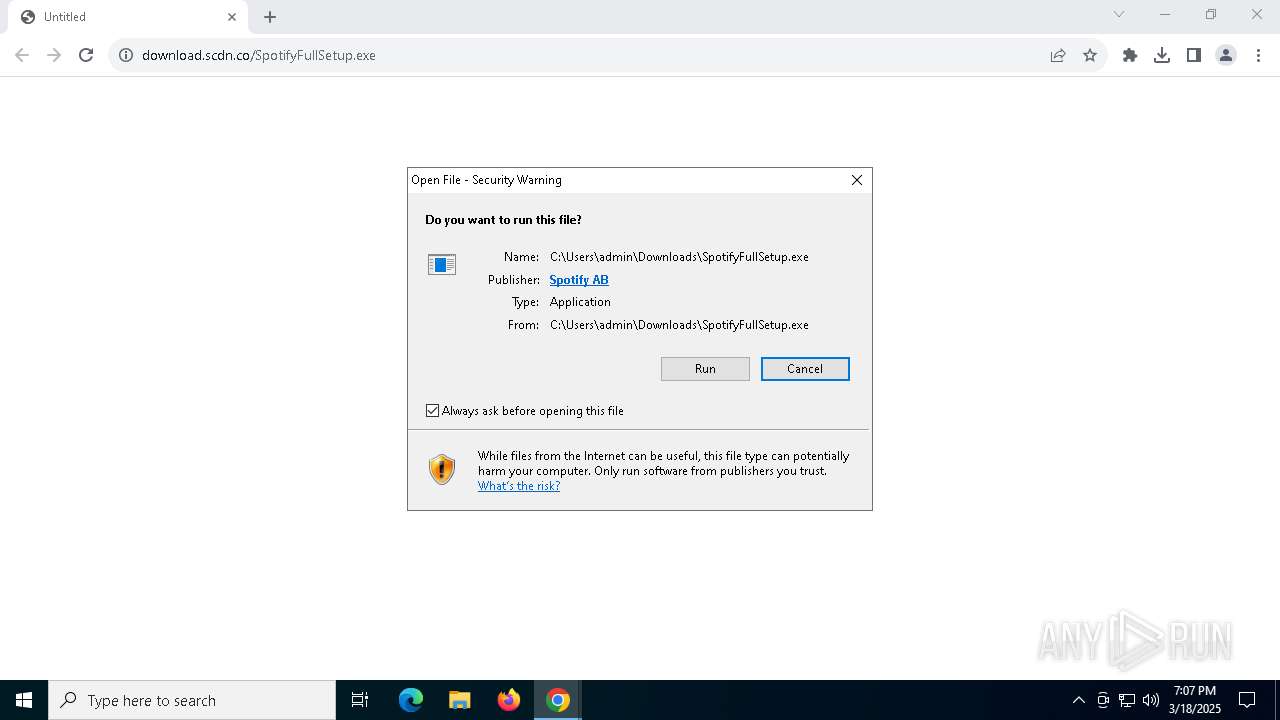
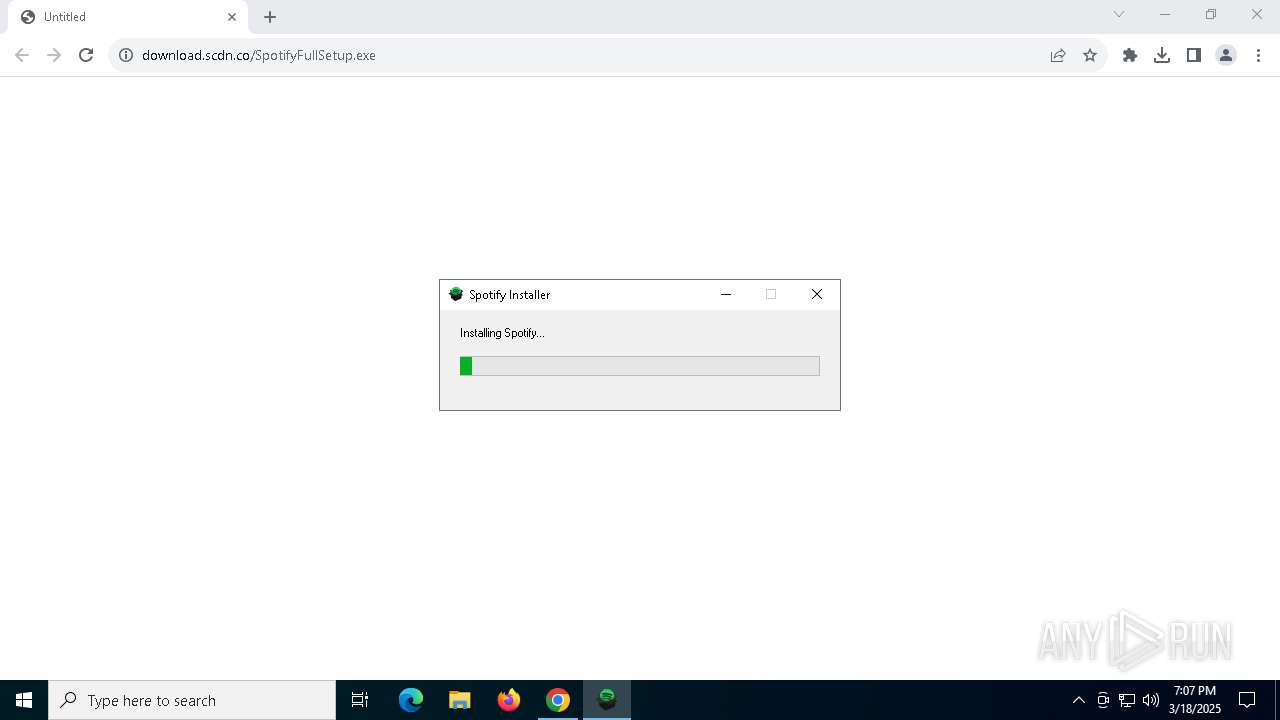
| 1040 | "C:\Users\admin\Downloads\SpotifyFullSetup.exe" | C:\Users\admin\Downloads\SpotifyFullSetup.exe | chrome.exe | ||||||||||||
User: admin Company: Spotify Ltd Integrity Level: MEDIUM Description: SpotifyInstaller Exit code: 0 Version: 0,0,0,0 Modules
| |||||||||||||||
| 1164 | C:\Users\admin\AppData\Roaming\Spotify\Spotify.exe --type=crashpad-handler /prefetch:4 --max-uploads=5 --max-db-size=20 --max-db-age=5 --monitor-self-annotation=ptype=crashpad-handler "--database=C:\Users\admin\AppData\Local\Spotify\User Data\Crashpad" --url=https://crashdump.spotify.com:443/ --annotation=platform=win32 --annotation=product=spotify --annotation=version=1.2.53.440 --initial-client-data=0x434,0x438,0x43c,0x430,0x440,0x751e2c90,0x751e2c9c,0x751e2ca8 | C:\Users\admin\AppData\Roaming\Spotify\Spotify.exe | — | Spotify.exe | |||||||||||
User: admin Company: Spotify Ltd Integrity Level: MEDIUM Description: Spotify Version: 1.2.53.440 Modules
| |||||||||||||||
| 1912 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=data_decoder.mojom.DataDecoderService --lang=en-US --service-sandbox-type=service --no-appcompat-clear --mojo-platform-channel-handle=5104 --field-trial-handle=2352,i,13270752764365674776,16201391523505643850,262144 --variations-seed-version /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Exit code: 0 Version: 122.0.2365.59 Modules
| |||||||||||||||
| 2284 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --disk-cache-dir=null --disk-cache-size=1 --media-cache-size=1 --disable-gpu-shader-disk-cache --disable-background-networking --disable-features=OptimizationGuideModelDownloading,OptimizationHintsFetching,OptimizationTargetPrediction,OptimizationHints "https://download.scdn.co/SpotifyFullSetup.exe" | C:\Program Files\Google\Chrome\Application\chrome.exe | explorer.exe | ||||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 122.0.6261.70 Modules
| |||||||||||||||
| 2340 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=edge_xpay_wallet.mojom.EdgeXPayWalletService --lang=en-US --service-sandbox-type=utility --no-appcompat-clear --mojo-platform-channel-handle=5380 --field-trial-handle=2352,i,13270752764365674776,16201391523505643850,262144 --variations-seed-version /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Version: 122.0.2365.59 Modules
| |||||||||||||||
| 2392 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=chrome.mojom.UtilReadIcon --lang=en-US --service-sandbox-type=icon_reader --disable-quic --no-appcompat-clear --mojo-platform-channel-handle=5172 --field-trial-handle=1920,i,12133758362450695426,17088862455498914844,262144 --disable-features=OptimizationGuideModelDownloading,OptimizationHints,OptimizationHintsFetching,OptimizationTargetPrediction --variations-seed-version /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 122.0.6261.70 Modules
| |||||||||||||||
| 5072 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=renderer --no-appcompat-clear --lang=en-US --js-flags=--ms-user-locale= --device-scale-factor=1 --num-raster-threads=2 --enable-main-frame-before-activation --renderer-client-id=5 --mojo-platform-channel-handle=3608 --field-trial-handle=2352,i,13270752764365674776,16201391523505643850,262144 --variations-seed-version /prefetch:1 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Version: 122.0.2365.59 Modules
| |||||||||||||||
| (PID) Process: | (5544) chrome.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Shell Extensions\Cached |
| Operation: | write | Name: | {2781761E-28E0-4109-99FE-B9D127C57AFE} {56FFCC30-D398-11D0-B2AE-00A0C908FA49} 0xFFFF |
Value: 0100000000000000294176F83898DB01 | |||
| (PID) Process: | (1040) SpotifyFullSetup.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run |
| Operation: | delete value | Name: | Spotify Web Helper |
Value: | |||
| (PID) Process: | (2284) chrome.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Google\Chrome\StabilityMetrics |
| Operation: | write | Name: | user_experience_metrics.stability.exited_cleanly |
Value: 1 | |||
| (PID) Process: | (2284) chrome.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run |
| Operation: | delete value | Name: | GoogleChromeAutoLaunch_A822CA3D40D4B8944864CFEA751D8D57 |
Value: | |||
| (PID) Process: | (1040) SpotifyFullSetup.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Spotify |
| Operation: | write | Name: | DisplayIcon |
Value: C:\Users\admin\AppData\Roaming\Spotify\Spotify.exe | |||
| (PID) Process: | (1040) SpotifyFullSetup.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Spotify |
| Operation: | write | Name: | DisplayName |
Value: Spotify | |||
| (PID) Process: | (1040) SpotifyFullSetup.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Spotify |
| Operation: | write | Name: | DisplayVersion |
Value: 1.2.53.440.g7b2f582a | |||
| (PID) Process: | (1040) SpotifyFullSetup.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Spotify |
| Operation: | write | Name: | Version |
Value: 1.2.53.440.g7b2f582a | |||
| (PID) Process: | (1040) SpotifyFullSetup.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Spotify |
| Operation: | write | Name: | InstallDate |
Value: 20250318 | |||
| (PID) Process: | (1040) SpotifyFullSetup.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\Spotify |
| Operation: | write | Name: | InstallLocation |
Value: C:\Users\admin\AppData\Roaming\Spotify | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2284 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\PersistentOriginTrials\LOG.old~RF10c6fb.TMP | — | |
MD5:— | SHA256:— | |||
| 2284 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\PersistentOriginTrials\LOG.old | — | |
MD5:— | SHA256:— | |||
| 2284 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\coupon_db\LOG.old~RF10c6fb.TMP | — | |
MD5:— | SHA256:— | |||
| 2284 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\chrome_cart_db\LOG.old~RF10c6fb.TMP | — | |
MD5:— | SHA256:— | |||
| 2284 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\discounts_db\LOG.old~RF10c6fb.TMP | — | |
MD5:— | SHA256:— | |||
| 2284 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\coupon_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 2284 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\discounts_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 2284 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\parcel_tracking_db\LOG.old~RF10c70b.TMP | — | |
MD5:— | SHA256:— | |||
| 2284 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\chrome_cart_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 2284 | chrome.exe | C:\Users\admin\AppData\Local\Google\Chrome\User Data\Default\parcel_tracking_db\LOG.old | — | |
MD5:— | SHA256:— | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
8956 | svchost.exe | GET | 206 | 34.104.35.123:80 | http://edgedl.me.gvt1.com/edgedl/release2/chrome_component/adnnf2xkczyschn5rjlarpymlqwq_2025.3.12.0/niikhdgajlphfehepabhhblakbdgeefj_2025.03.12.00_all_adq7z562swe73sgkbx65gzsho2ha.crx3 | US | binary | 2.24 Kb | whitelisted |
8956 | svchost.exe | GET | 206 | 34.104.35.123:80 | http://edgedl.me.gvt1.com/edgedl/release2/chrome_component/adnnf2xkczyschn5rjlarpymlqwq_2025.3.12.0/niikhdgajlphfehepabhhblakbdgeefj_2025.03.12.00_all_adq7z562swe73sgkbx65gzsho2ha.crx3 | US | compressed | 3.20 Kb | whitelisted |
8956 | svchost.exe | GET | 206 | 34.104.35.123:80 | http://edgedl.me.gvt1.com/edgedl/release2/chrome_component/pmztx7tk73bjttcb4b6ys6fixq_2025.1.3.1202/ggkkehgbnfjpeggfpleeakpidbkibbmn_2025.1.3.1202_all_afljkosaafpr5gqm7ftppqz7zq.crx3 | US | binary | 9.00 Kb | whitelisted |
8956 | svchost.exe | GET | 206 | 34.104.35.123:80 | http://edgedl.me.gvt1.com/edgedl/release2/chrome_component/pmztx7tk73bjttcb4b6ys6fixq_2025.1.3.1202/ggkkehgbnfjpeggfpleeakpidbkibbmn_2025.1.3.1202_all_afljkosaafpr5gqm7ftppqz7zq.crx3 | US | compressed | 724 b | whitelisted |
8956 | svchost.exe | HEAD | 200 | 34.104.35.123:80 | http://edgedl.me.gvt1.com/edgedl/release2/chrome_component/pmztx7tk73bjttcb4b6ys6fixq_2025.1.3.1202/ggkkehgbnfjpeggfpleeakpidbkibbmn_2025.1.3.1202_all_afljkosaafpr5gqm7ftppqz7zq.crx3 | US | compressed | 3.20 Kb | whitelisted |
— | — | GET | 200 | 184.24.77.13:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 825 b | whitelisted |
5496 | MoUsoCoreWorker.exe | GET | 200 | 184.24.77.13:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 825 b | whitelisted |
7240 | backgroundTaskHost.exe | GET | 200 | 2.17.190.73:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAUZZSZEml49Gjh0j13P68w%3D | DE | binary | 471 b | whitelisted |
— | — | GET | 200 | 2.17.190.73:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | DE | binary | 471 b | whitelisted |
8068 | SIHClient.exe | GET | 200 | 23.218.209.163:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Product%20Root%20Certificate%20Authority%202018.crl | DE | binary | 419 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
— | — | 184.24.77.13:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
5496 | MoUsoCoreWorker.exe | 184.24.77.13:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
2104 | svchost.exe | 4.231.128.59:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
— | — | 40.115.3.253:443 | client.wns.windows.com | MICROSOFT-CORP-MSN-AS-BLOCK | NL | whitelisted |
— | — | 239.255.255.250:1900 | — | — | — | whitelisted |
— | — | 199.232.214.248:443 | download.scdn.co | FASTLY | US | whitelisted |
— | — | 173.194.69.84:443 | accounts.google.com | GOOGLE | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
google.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
download.scdn.co |
| whitelisted |
accounts.google.com |
| whitelisted |
login.live.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
settings-win.data.microsoft.com |
| whitelisted |
www.google.com |
| whitelisted |
arc.msn.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
8132 | Spotify.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
8132 | Spotify.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
8132 | Spotify.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
8132 | Spotify.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
8132 | Spotify.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
8132 | Spotify.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
8132 | Spotify.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
8132 | Spotify.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
8132 | Spotify.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
8132 | Spotify.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |