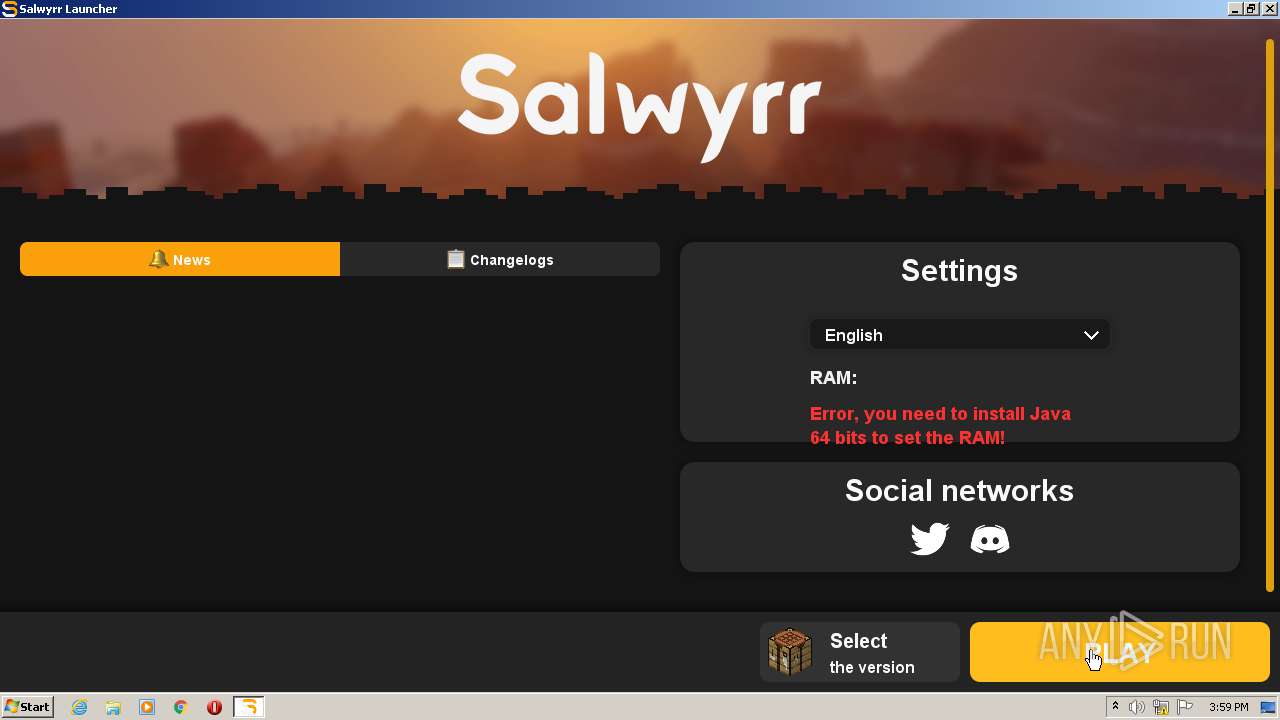
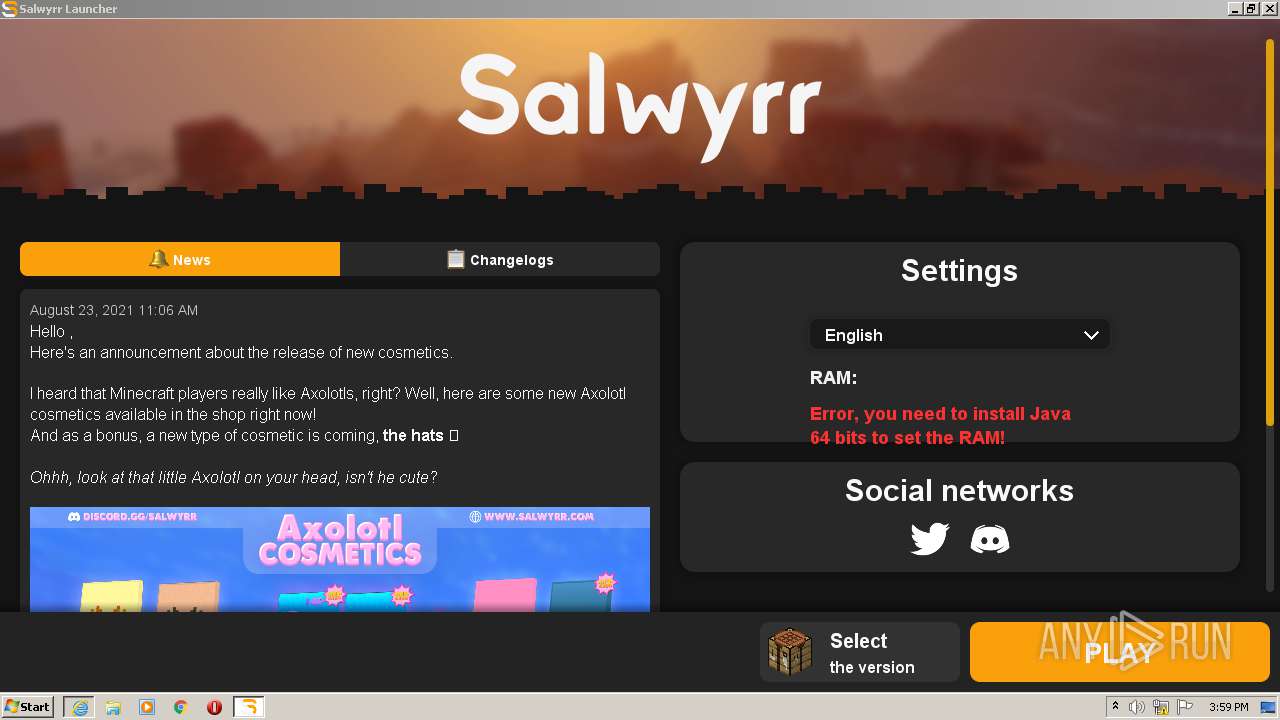
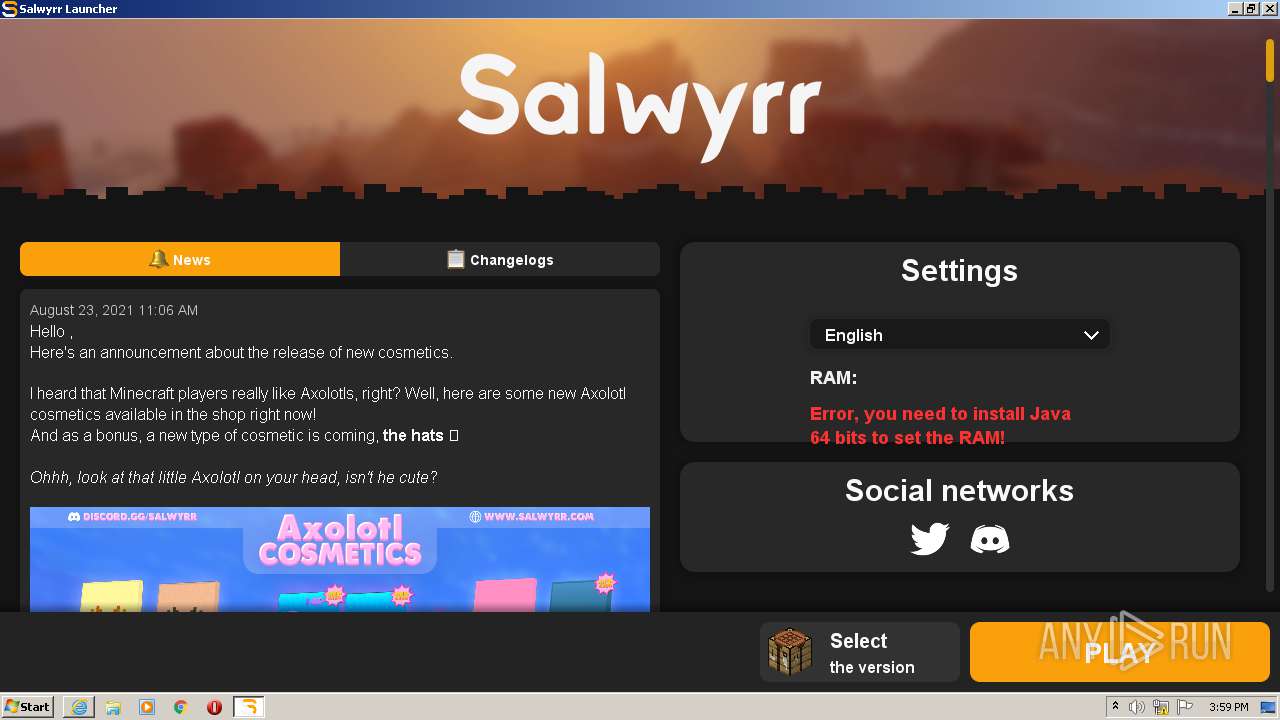
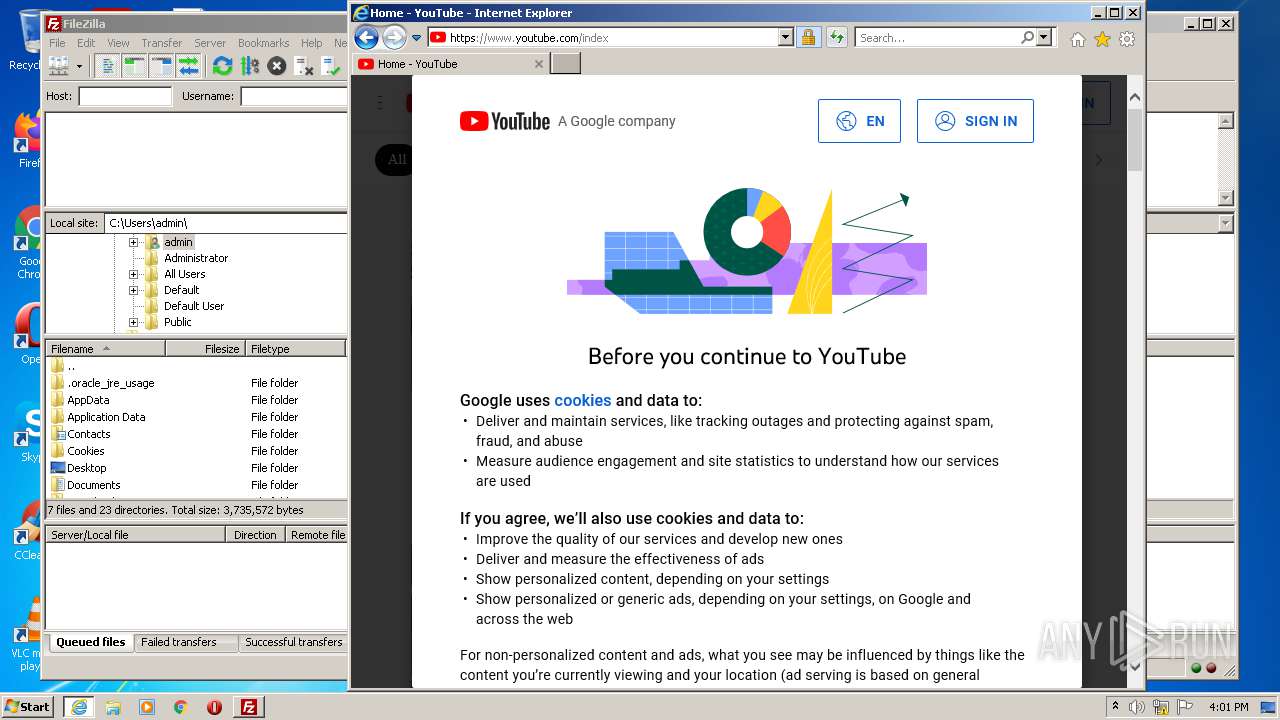
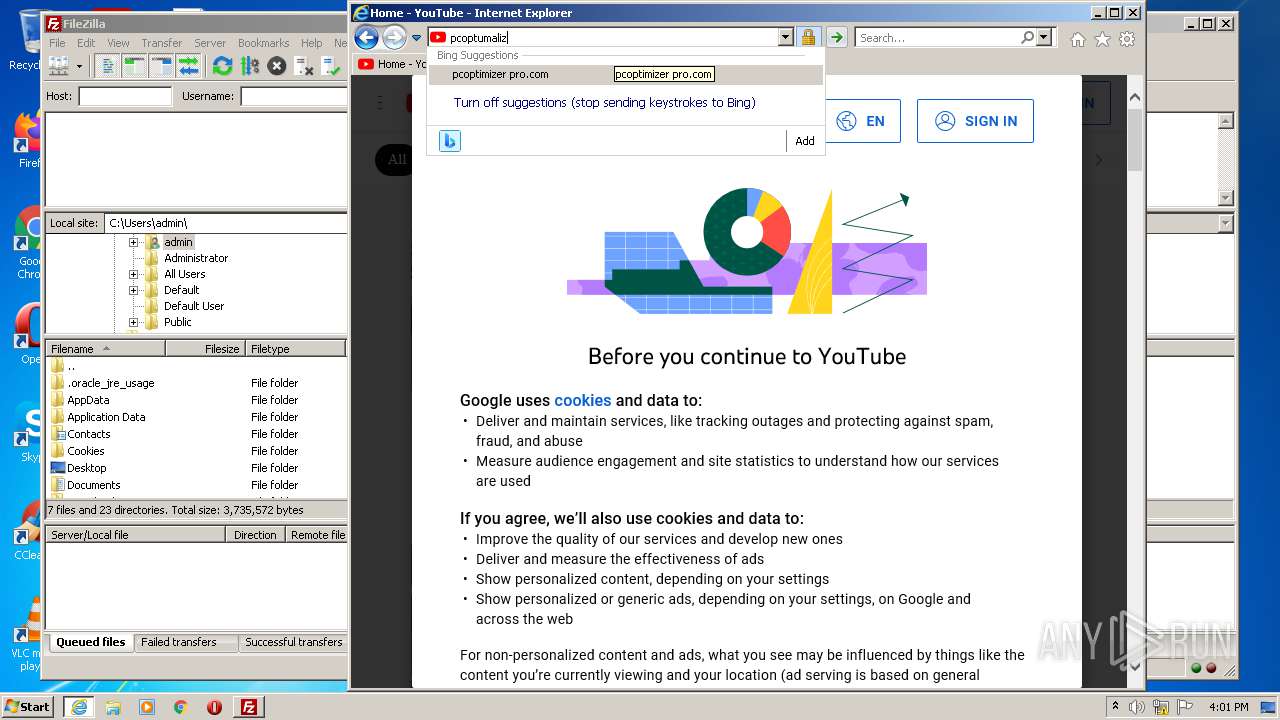
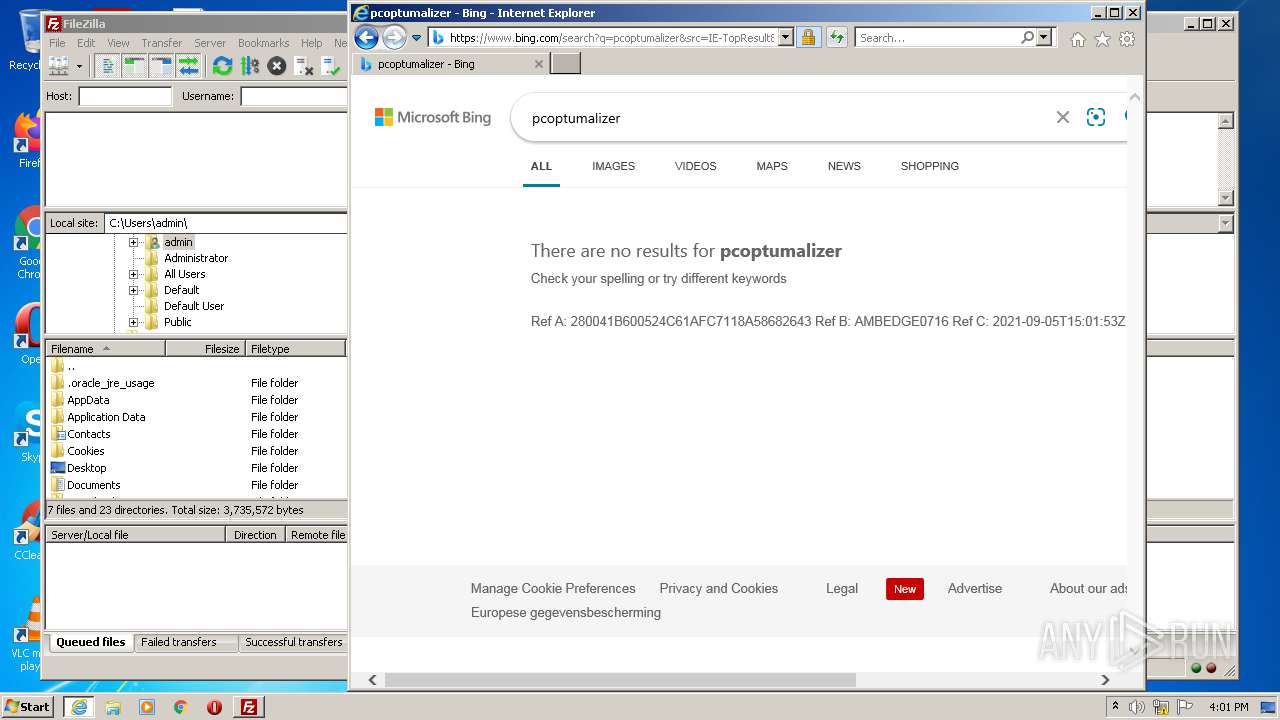
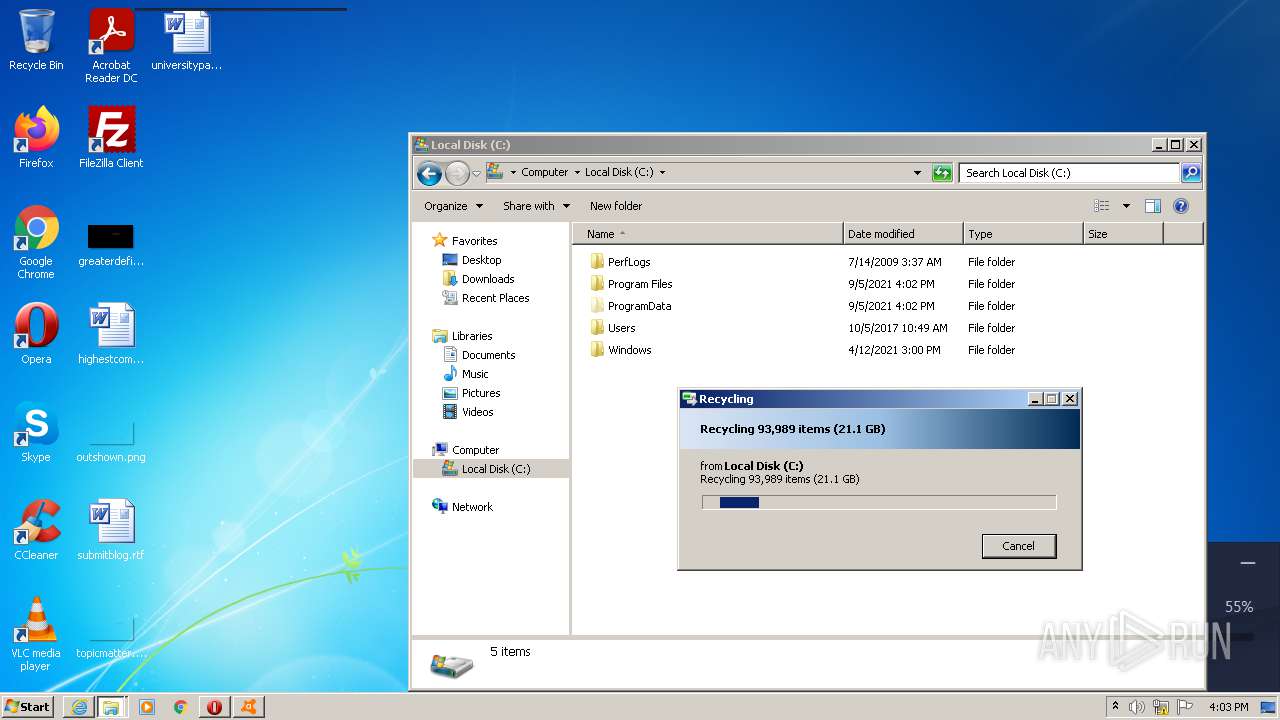
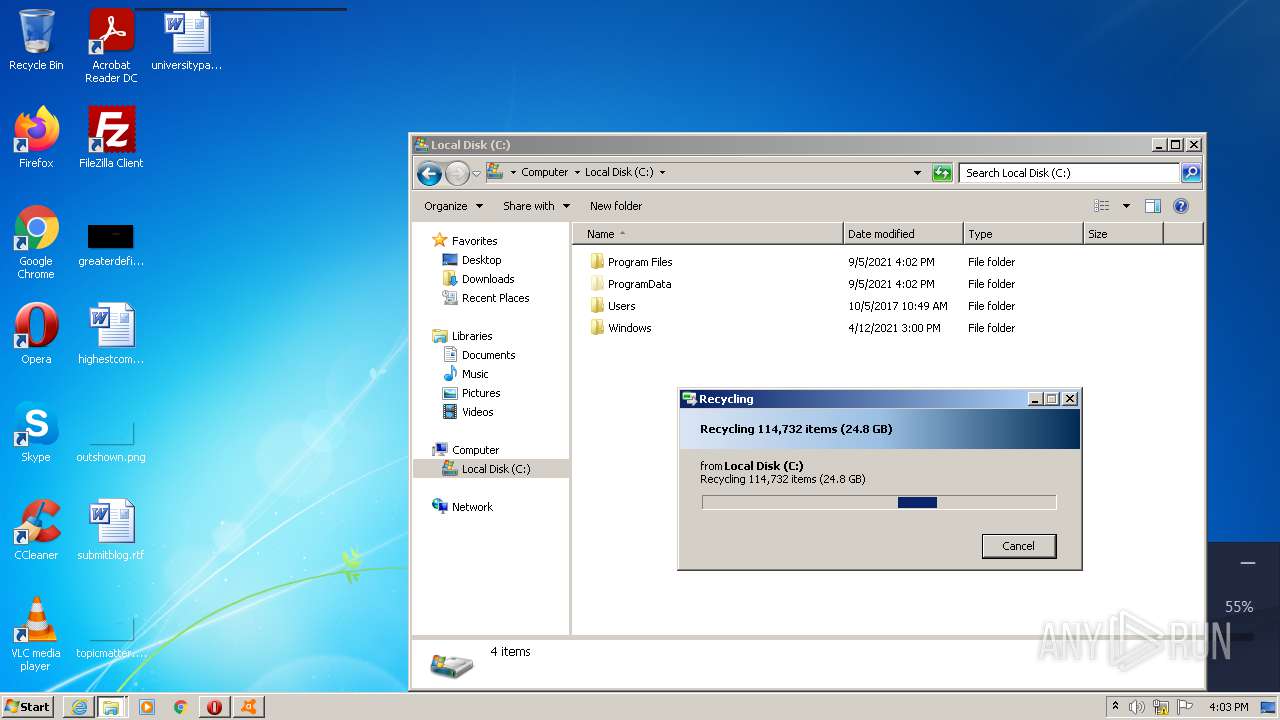
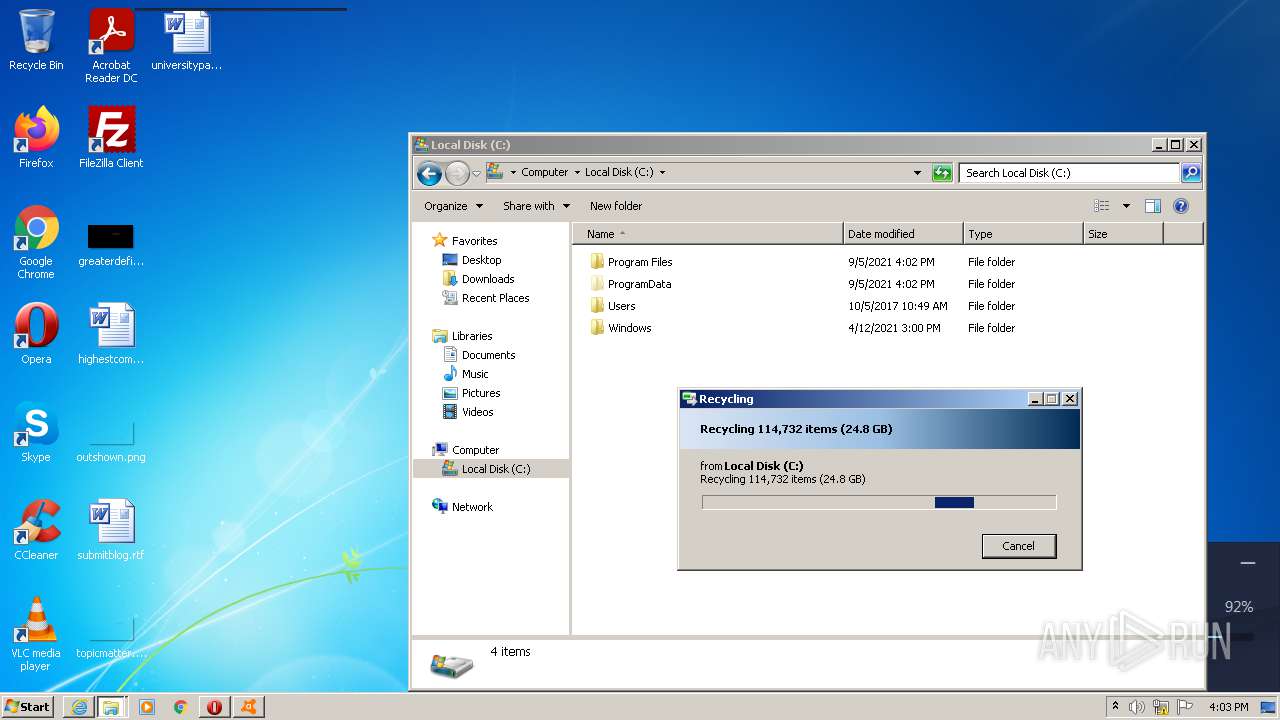
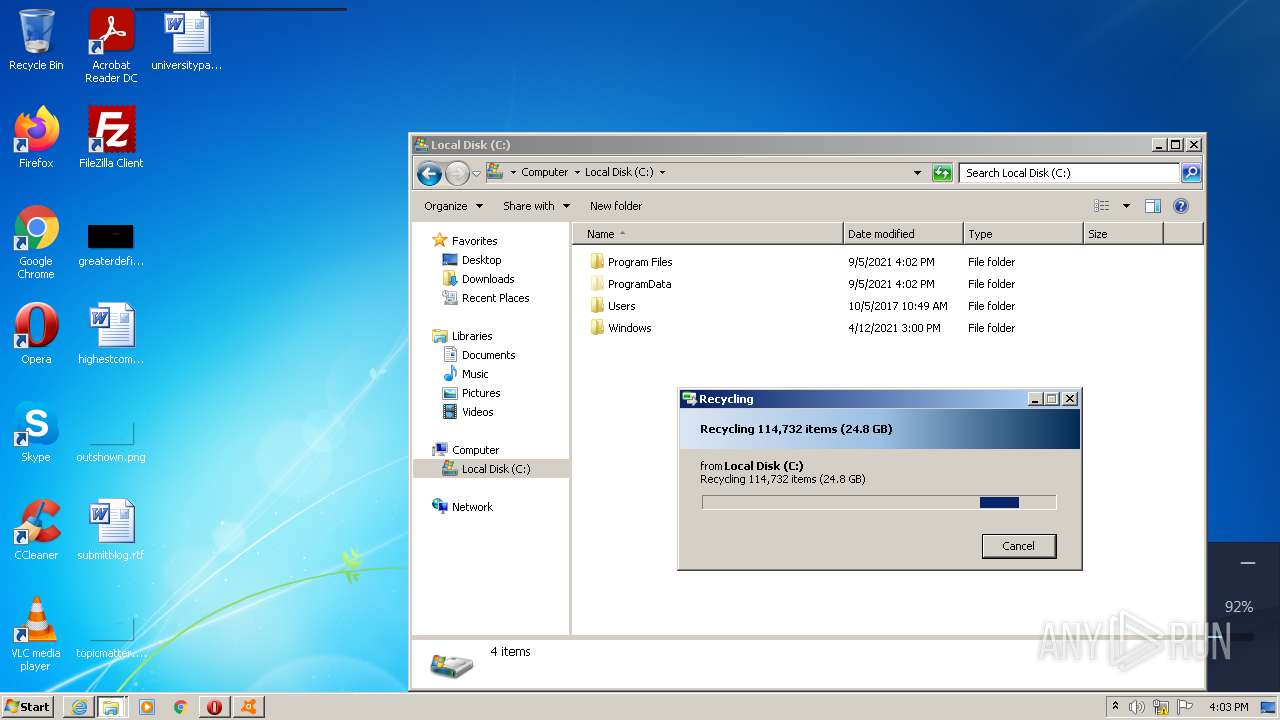
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
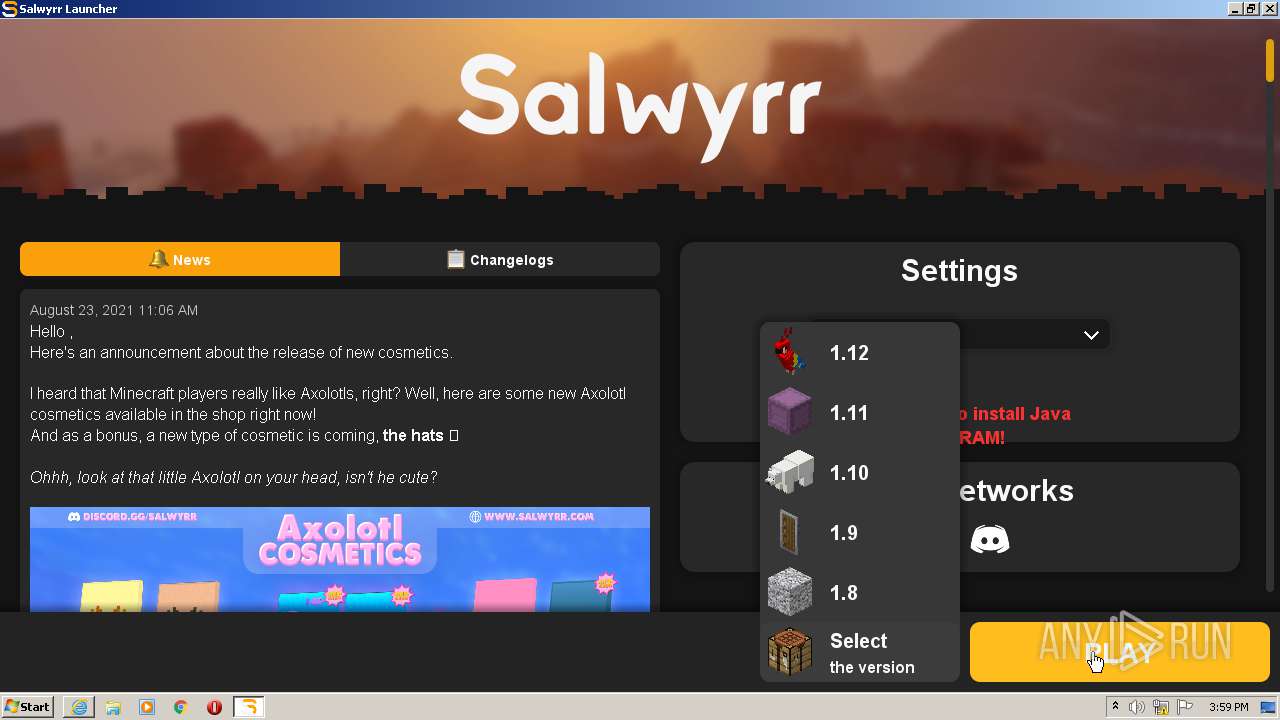
| File name: | Salwyrr Minecraft Launcher 4.jar |
| Full analysis: | https://app.any.run/tasks/42b9c4d0-9b6b-4130-843d-cb231c65dfa0 |
| Verdict: | Malicious activity |
| Analysis date: | September 05, 2021, 14:58:47 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Indicators: | |
| MIME: | application/zip |
| File info: | Zip archive data, at least v1.0 to extract |
| MD5: | 0D978F1DE0CF6D1E0D2793044EAE90FB |
| SHA1: | DA074EE152D44DB2E3E3A95B2CC05D8F11EA20B9 |
| SHA256: | 49E4F65C5378E2F46DE35F8DBE0AF0F20887FC24284480DC94818B4FCEB2A44D |
| SSDEEP: | 24576:jGyNIGcoO6Z54Ihj7HX/4sQgJAcb+mgWQZIKnuGHZm/aMUt:Cqx1t544j73/gcqmg1tuGHZm/aMUt |
| .jar | | | Java Archive (78.3) |
|---|---|---|
| .zip | | | ZIP compressed archive (21.6) |
| ZipFileName: | fr/ |
|---|---|
| ZipUncompressedSize: | - |
| ZipCompressedSize: | - |
| ZipCRC: | 0x00000000 |
| ZipModifyDate: | 2021:07:14 15:22:15 |
| ZipCompression: | None |
| ZipBitFlag: | 0x0800 |
| ZipRequiredVersion: | 10 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 120 | C:\Windows\system32\Macromed\Flash\FlashUtil32_32_0_0_453_ActiveX.exe -Embedding | C:\Windows\system32\Macromed\Flash\FlashUtil32_32_0_0_453_ActiveX.exe | — | svchost.exe | |||||||||||
User: admin Company: Adobe Integrity Level: MEDIUM Description: Adobe� Flash� Player Installer/Uninstaller 32.0 r0 Exit code: 0 Version: 32,0,0,453 Modules
| |||||||||||||||
| 852 | C:\Windows\system32\icacls.exe C:\ProgramData\Oracle\Java\.oracle_jre_usage /grant "everyone":(OI)(CI)M | C:\Windows\system32\icacls.exe | — | javaw.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 1324 | cmd.exe /c ""C:\Program Files\Java\jre1.8.0_271\bin\javaw" -Xmx512m -cp "C:\Users\admin\AppData\Roaming\.Salwyrr\launcher\launcher.jar" fr.salwyrr.launcher.frames.Main --salwyrr salwyrr " | C:\Windows\system32\cmd.exe | — | javaw.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 0 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
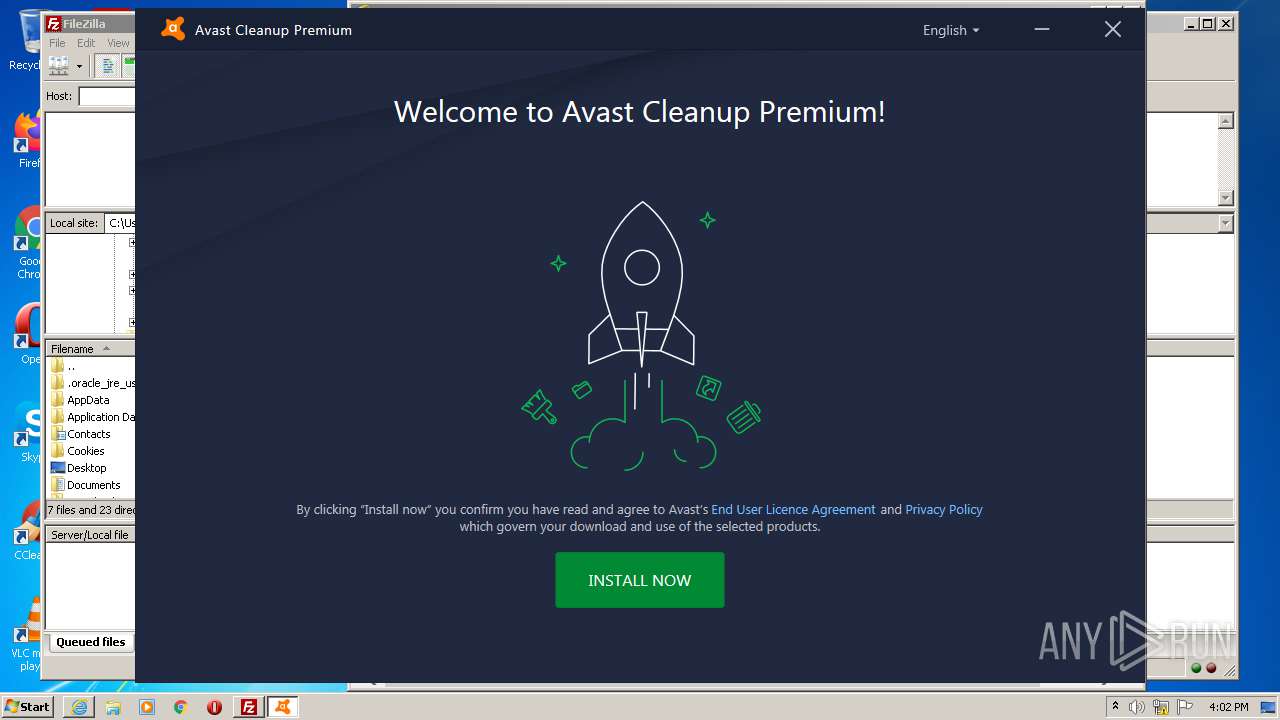
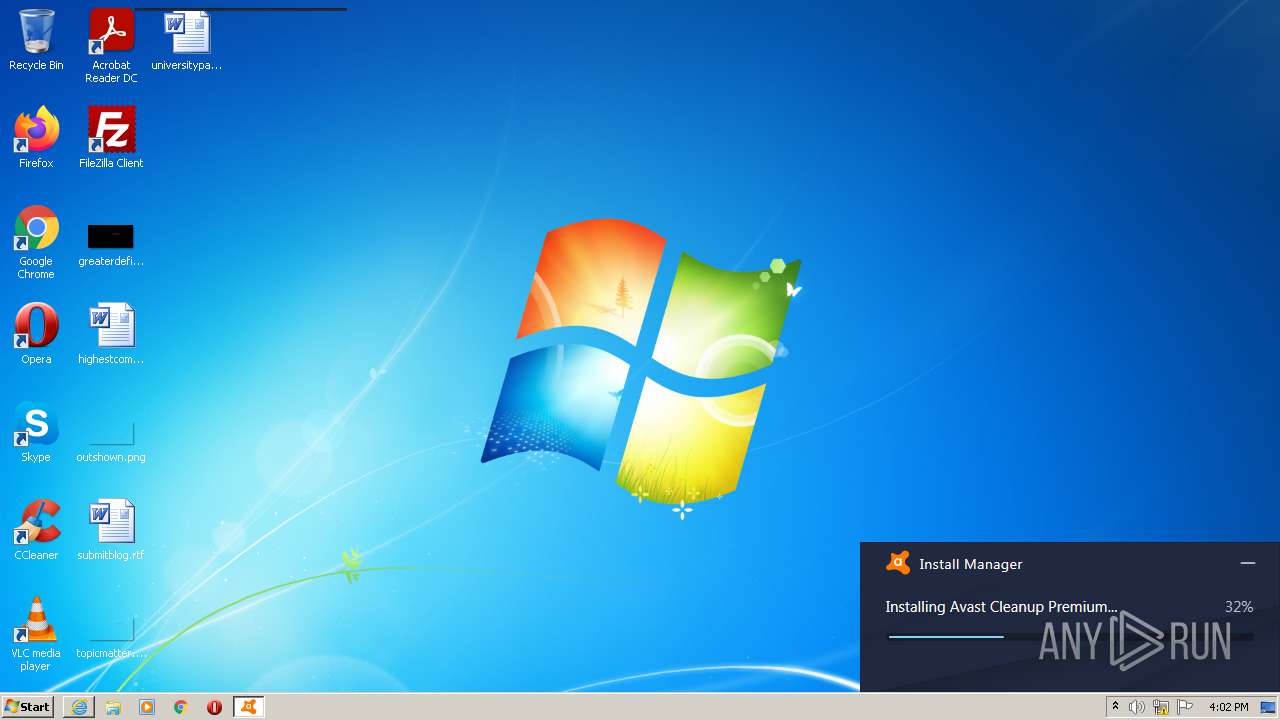
| 1468 | C:\Windows\Temp\asw-5bed29ab-fa26-4d3d-9e67-dad4ea8285e6\avast-tu\icarus.exe /sssid:2804 /er_master:master_ep_2b8d2dd1-d572-4aa9-80ce-38efbac058b9 /er_ui:ui_ep_3f5ae124-8627-47cd-819f-69aad68bf15a /er_slave:avast-tu_slave_ep_4cc191ff-d045-46ce-b73b-69c03a0853b3 /slave:avast-tu | C:\Windows\Temp\asw-5bed29ab-fa26-4d3d-9e67-dad4ea8285e6\avast-tu\icarus.exe | icarus.exe | ||||||||||||
User: admin Company: Avast Software Integrity Level: HIGH Description: Avast Installer Exit code: 0 Version: 21.3.3208.0 Modules
| |||||||||||||||
| 1532 | C:\Windows\system32\DllHost.exe /Processid:{3AD05575-8857-4850-9277-11B85BDB8E09} | C:\Windows\system32\DllHost.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: COM Surrogate Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
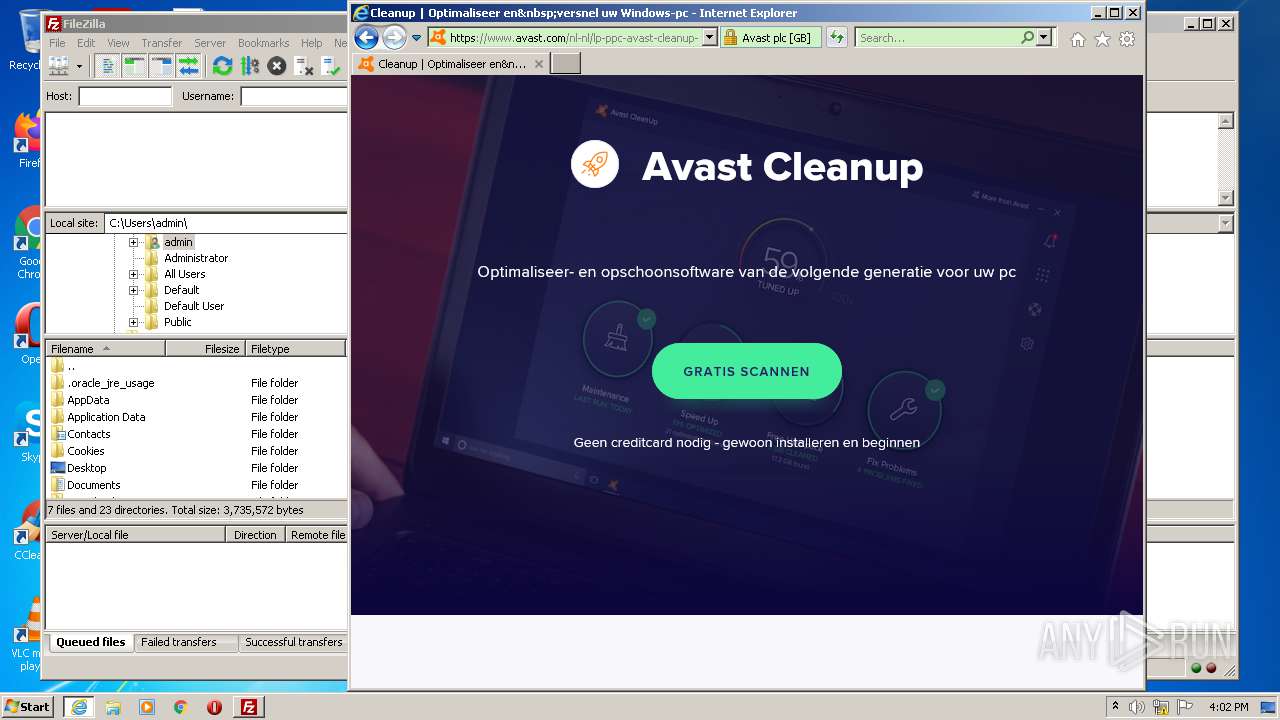
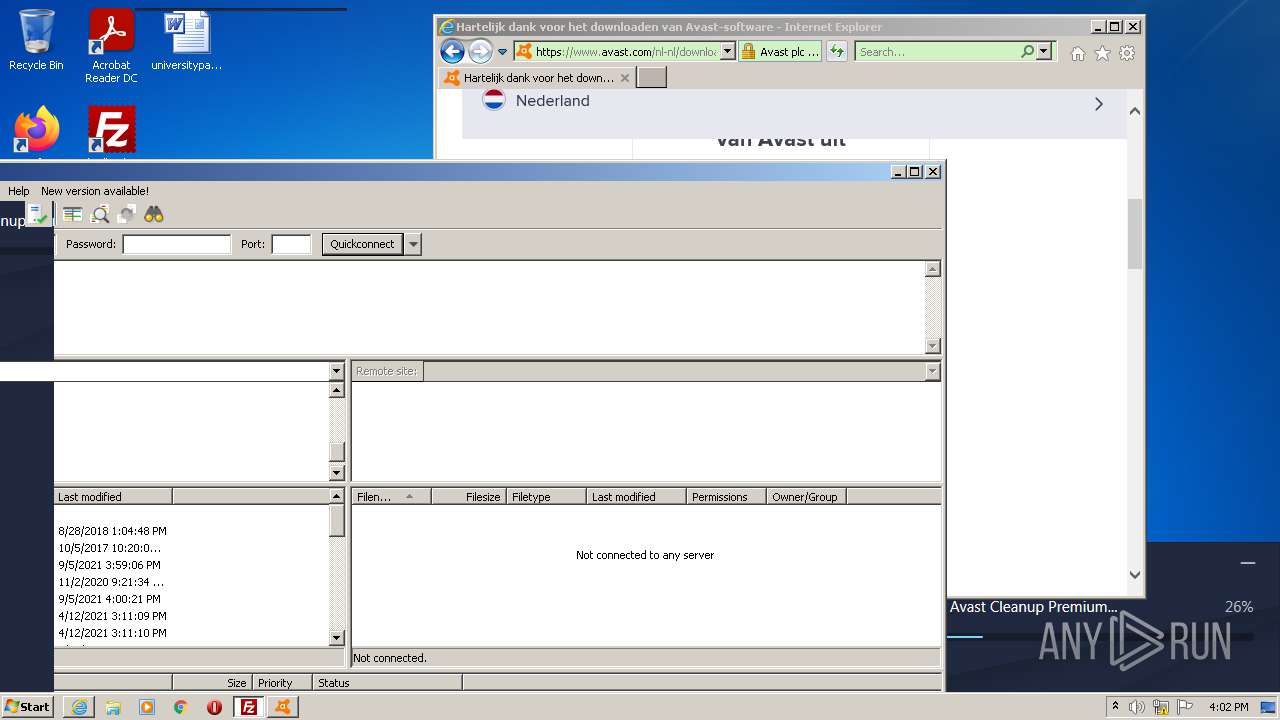
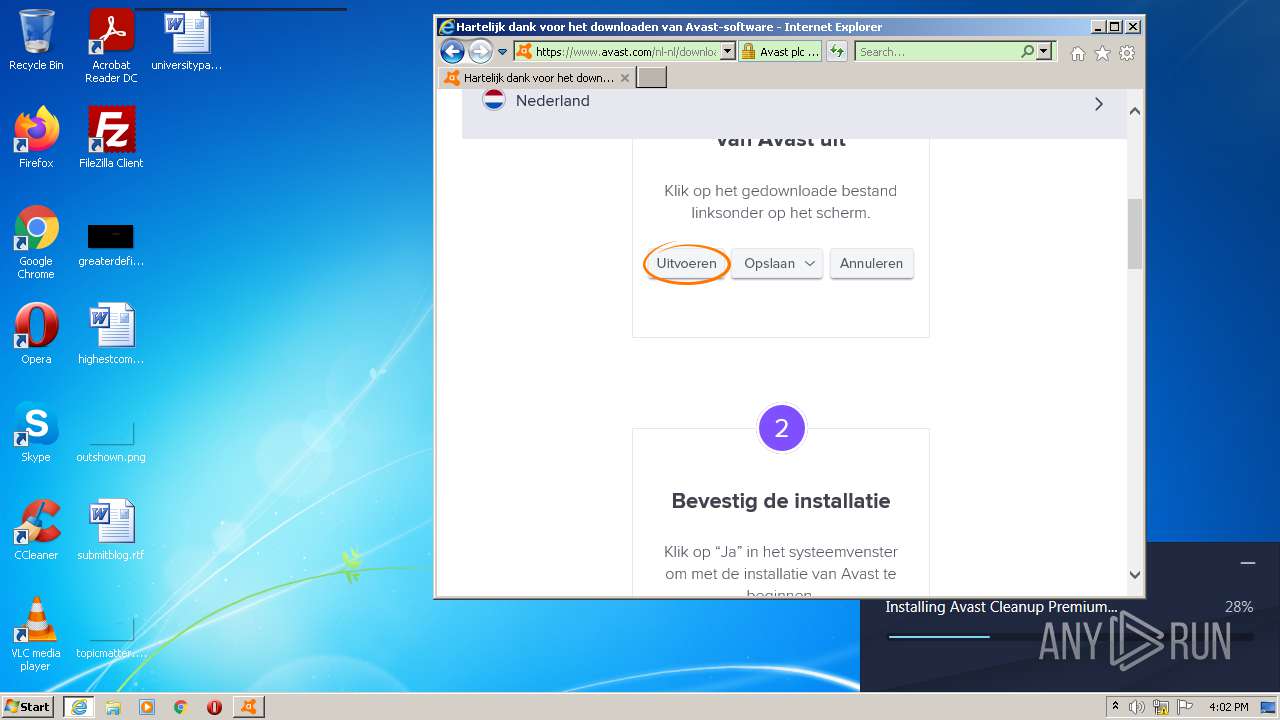
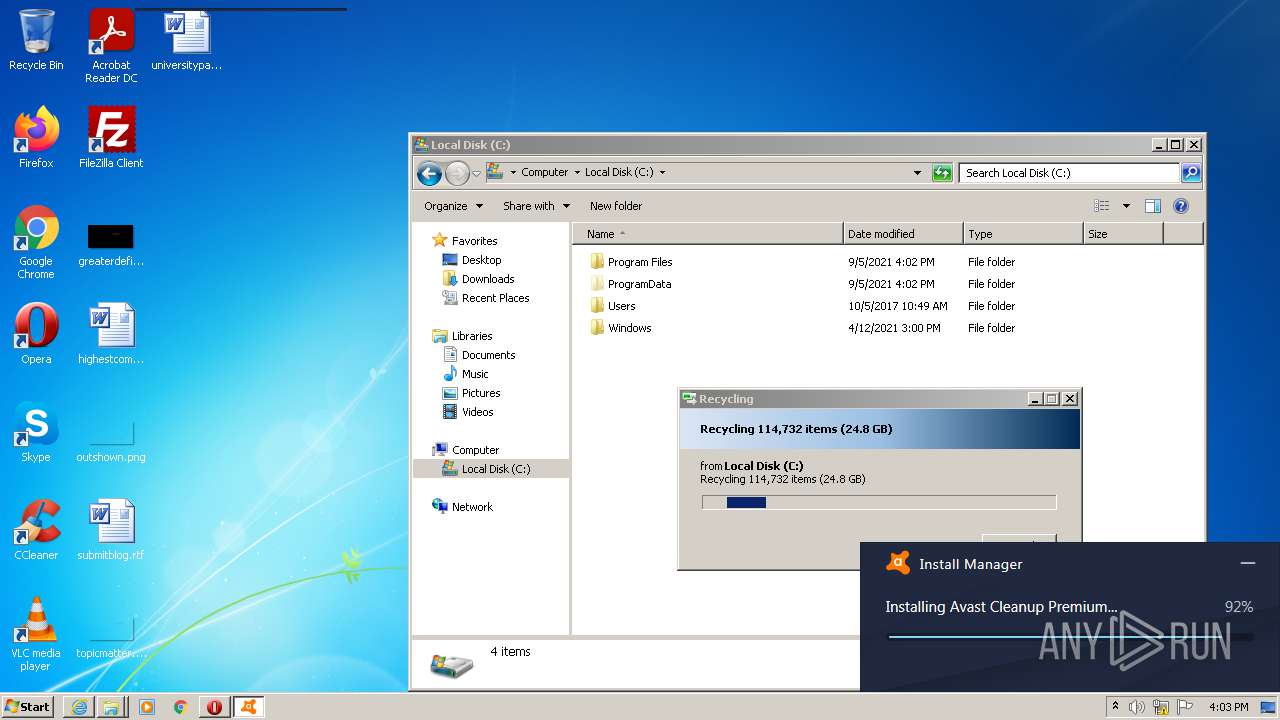
| 2096 | "C:\Users\admin\Downloads\avast_cleanup_online_setup.exe" | C:\Users\admin\Downloads\avast_cleanup_online_setup.exe | — | iexplore.exe | |||||||||||
User: admin Company: Avast Software Integrity Level: MEDIUM Description: Avast Self-Extract Package Exit code: 3221226540 Version: 21.3.3208.0 Modules
| |||||||||||||||
| 2804 | "C:\Users\admin\Downloads\avast_cleanup_online_setup.exe" | C:\Users\admin\Downloads\avast_cleanup_online_setup.exe | iexplore.exe | ||||||||||||
User: admin Company: Avast Software Integrity Level: HIGH Description: Avast Self-Extract Package Exit code: 0 Version: 21.3.3208.0 Modules
| |||||||||||||||
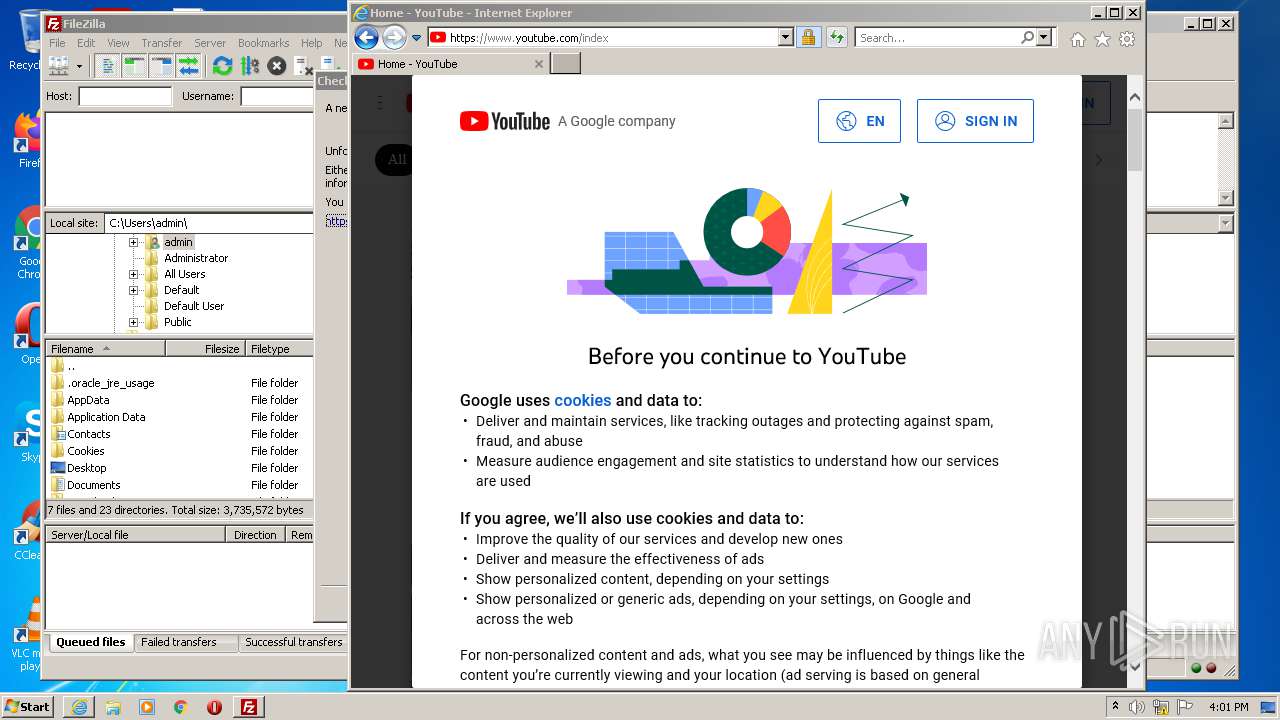
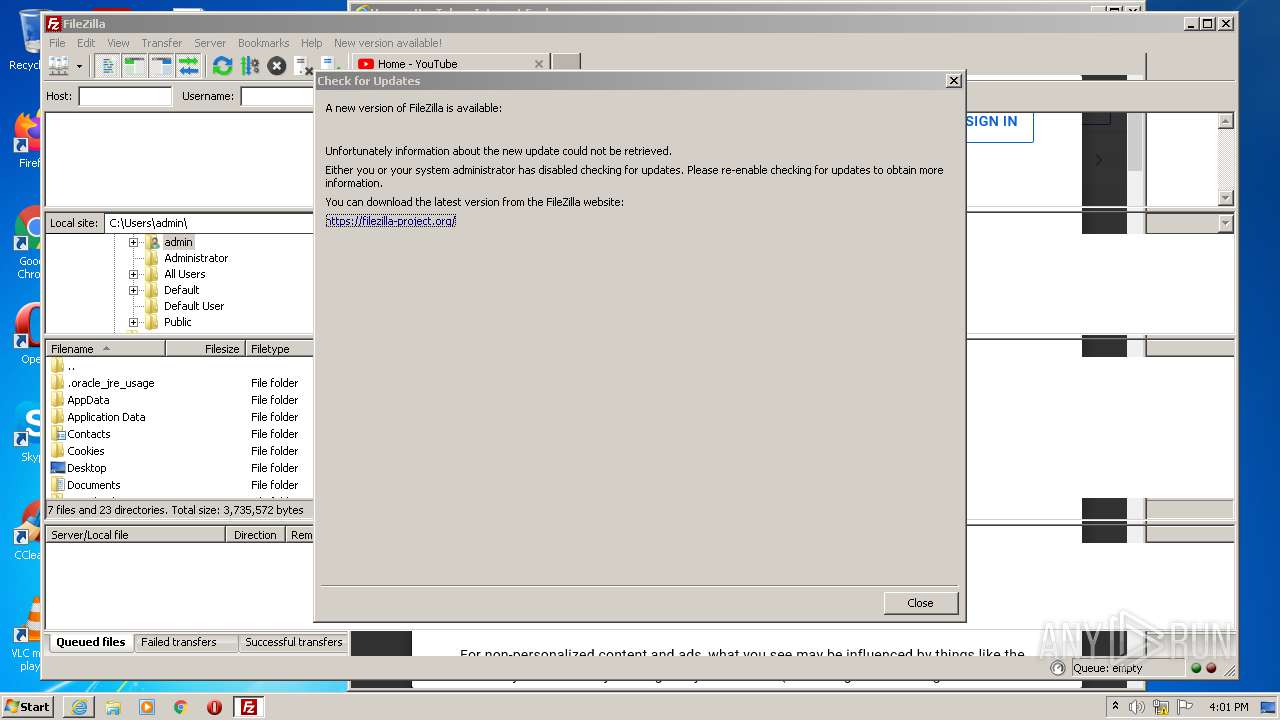
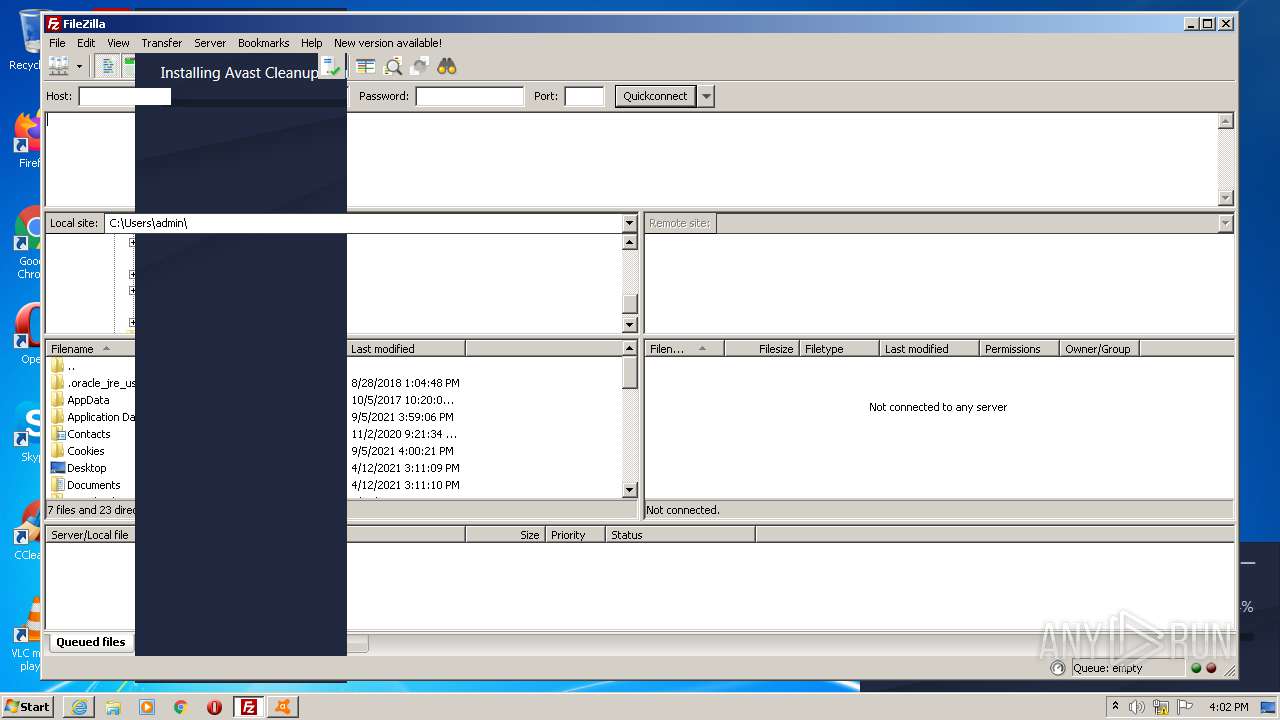
| 2808 | "C:\Program Files\FileZilla FTP Client\filezilla.exe" | C:\Program Files\FileZilla FTP Client\filezilla.exe | — | Explorer.EXE | |||||||||||
User: admin Company: FileZilla Project Integrity Level: MEDIUM Description: FileZilla FTP Client Exit code: 0 Version: 3, 51, 0, 0 Modules
| |||||||||||||||
| 2916 | "C:\Program Files\Java\jre1.8.0_271\bin\javaw.exe" -jar "C:\Users\admin\AppData\Local\Temp\Salwyrr Minecraft Launcher 4.jar" | C:\Program Files\Java\jre1.8.0_271\bin\javaw.exe | Explorer.EXE | ||||||||||||
User: admin Company: Oracle Corporation Integrity Level: MEDIUM Description: Java(TM) Platform SE binary Exit code: 0 Version: 8.0.2710.9 Modules
| |||||||||||||||
| 2964 | C:\Windows\Temp\asw-5bed29ab-fa26-4d3d-9e67-dad4ea8285e6\common\icarus_ui.exe /sssid:2804 /er_master:master_ep_2b8d2dd1-d572-4aa9-80ce-38efbac058b9 /er_ui:ui_ep_3f5ae124-8627-47cd-819f-69aad68bf15a | C:\Windows\Temp\asw-5bed29ab-fa26-4d3d-9e67-dad4ea8285e6\common\icarus_ui.exe | — | icarus.exe | |||||||||||
User: admin Company: Avast Software Integrity Level: HIGH Description: Avast UI Exit code: 0 Version: 21.3.3208.0 Modules
| |||||||||||||||
| (PID) Process: | (2916) javaw.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Direct3D\MostRecentApplication |
| Operation: | write | Name: | Name |
Value: javaw.exe | |||
| (PID) Process: | (3476) javaw.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Direct3D\MostRecentApplication |
| Operation: | write | Name: | Name |
Value: javaw.exe | |||
| (PID) Process: | (3184) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\TabbedBrowsing |
| Operation: | write | Name: | NTPDaysSinceLastAutoMigration |
Value: 1 | |||
| (PID) Process: | (3184) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\TabbedBrowsing |
| Operation: | write | Name: | NTPLastLaunchLowDateTime |
Value: | |||
| (PID) Process: | (3184) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\TabbedBrowsing |
| Operation: | write | Name: | NTPLastLaunchHighDateTime |
Value: 30909030 | |||
| (PID) Process: | (3184) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\UrlBlockManager |
| Operation: | write | Name: | NextCheckForUpdateLowDateTime |
Value: | |||
| (PID) Process: | (3184) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\UrlBlockManager |
| Operation: | write | Name: | NextCheckForUpdateHighDateTime |
Value: 30909030 | |||
| (PID) Process: | (3184) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Content |
| Operation: | write | Name: | CachePrefix |
Value: | |||
| (PID) Process: | (3184) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Cookies |
| Operation: | write | Name: | CachePrefix |
Value: Cookie: | |||
| (PID) Process: | (3184) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\History |
| Operation: | write | Name: | CachePrefix |
Value: Visited: | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2916 | javaw.exe | C:\ProgramData\Oracle\Java\.oracle_jre_usage\17dfc292991c8061.timestamp | text | |
MD5:7A04D94C12E40595411D509203FB7C77 | SHA256:29005A541E61D0E6D7EC762087330A73A1C9F7E044298E9762036FA82567F492 | |||
| 2916 | javaw.exe | C:\Users\admin\AppData\Local\Temp\imageio1735109242312573573.tmp | image | |
MD5:BCE8CD5A2036C38CE2410C75B0661192 | SHA256:4C0C14E9BDBEDFC3B502C47CA648449DCAD0416AD5ECCC7F86A073ABD2E0B47E | |||
| 2916 | javaw.exe | C:\Users\admin\AppData\Roaming\.Salwyrr\launcher\launcher.jar | compressed | |
MD5:71D4F071C3FE12CAA4C1EFD0A40058C2 | SHA256:BC719542CCBA100A6A87CF989BE2DD220E730680E0D163D34EB8E271CA3DD222 | |||
| 2916 | javaw.exe | C:\Users\admin\AppData\Local\Temp\imageio1701917825330558317.tmp | image | |
MD5:268C8630442CA5D8045693D60A2BEFDA | SHA256:42207FE6936597F4F52B4296072333D596467C2069FA2AFAC7A24B8CDE3BEB1B | |||
| 2916 | javaw.exe | C:\Users\admin\AppData\Local\Temp\imageio5471204592087958955.tmp | image | |
MD5:59831FDF4453BEA0A039B813E9D8236D | SHA256:106017ADE1A102169CC96DBEE614BC56DF5F60A2826653BCA223AB8423113CE0 | |||
| 2916 | javaw.exe | C:\Users\admin\AppData\Local\Temp\imageio2511137548101014869.tmp | image | |
MD5:0996AB5ACD55F63DA90DB7575CAE371A | SHA256:888669DE12F8A19B9F912A6A5B52802E858A24EFB29BE41382CF54BA4F912328 | |||
| 3476 | javaw.exe | C:\Users\admin\AppData\Local\Temp\imageio3886816782462729367.tmp | image | |
MD5:0340915C04AA1E91BFE012F0E067AFEF | SHA256:51A95FDB35E34C5A930743E7C5B1E4EF33800633B13E063C4324910BBF2F9D8F | |||
| 3476 | javaw.exe | C:\Users\admin\AppData\Local\Temp\imageio2361146691305457742.tmp | image | |
MD5:9709EF7633020620F70B466096E1C3D5 | SHA256:A1A631018828BFA33E0C475D49D0ED482799C3D1CFBBFFC8C439EF39149172A0 | |||
| 3476 | javaw.exe | C:\Users\admin\AppData\Local\Temp\imageio6422098479220194180.tmp | image | |
MD5:088562DC34A56FB7AADF6BB7AD63C016 | SHA256:DB6C6FF6BC4684006F2583D8F489E2FDD1F08813F3EC4D7DF30DB362598BE306 | |||
| 3476 | javaw.exe | C:\Users\admin\AppData\Local\Temp\imageio8317096187926550569.tmp | image | |
MD5:B4D8D88863849713FDB1687E36DBF404 | SHA256:014366D7C75963CEF3CF979094173354E3EC48E4D26868B87DCC1C1DE31C7EE8 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
3184 | iexplore.exe | GET | 200 | 69.16.175.42:80 | http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/disallowedcertstl.cab?bbe4ea4c6a23668c | US | compressed | 4.70 Kb | whitelisted |
3184 | iexplore.exe | GET | 200 | 93.184.220.29:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTBL0V27RVZ7LBduom%2FnYB45SPUEwQU5Z1ZMIJHWMys%2BghUNoZ7OrUETfACEA%2BnRyLFPYjID1ie%2Bx%2BdSjo%3D | US | der | 1.47 Kb | whitelisted |
3952 | iexplore.exe | GET | 200 | 142.250.74.195:80 | http://ocsp.pki.goog/gsr1/MFEwTzBNMEswSTAJBgUrDgMCGgUABBS3V7W2nAf4FiMTjpDJKg6%2BMgGqMQQUYHtmGkUNl8qJUC99BM00qP%2F8%2FUsCEHe9DWzbNvka6iEPxPBY0w0%3D | US | der | 1.41 Kb | whitelisted |
3952 | iexplore.exe | GET | 200 | 93.184.220.29:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | der | 471 b | whitelisted |
3952 | iexplore.exe | GET | 200 | 142.250.74.195:80 | http://ocsp.pki.goog/gtsr1/ME4wTDBKMEgwRjAJBgUrDgMCGgUABBQwkcLWD4LqGJ7bE7B1XZsEbmfwUAQU5K8rJnEaK0gnhS9SZizv8IkTcT4CDQIDvFNZazTHGPUBUGY%3D | US | der | 724 b | whitelisted |
3952 | iexplore.exe | GET | 200 | 142.250.74.195:80 | http://ocsp.pki.goog/gts1c3/MFIwUDBOMEwwSjAJBgUrDgMCGgUABBTHLnmK3f9hNLO67UdCuLvGwCQHYwQUinR%2Fr4XN7pXNPZzQ4kYU83E1HScCEQC3uGcTlGHzGAoAAAAA%2Bo1K | US | der | 472 b | whitelisted |
3952 | iexplore.exe | GET | 200 | 142.250.74.195:80 | http://ocsp.pki.goog/gts1c3/MFIwUDBOMEwwSjAJBgUrDgMCGgUABBTHLnmK3f9hNLO67UdCuLvGwCQHYwQUinR%2Fr4XN7pXNPZzQ4kYU83E1HScCEQC5z2OD8IgZMwoAAAAA%2BmIx | US | der | 472 b | whitelisted |
3952 | iexplore.exe | GET | 200 | 142.250.74.195:80 | http://ocsp.pki.goog/gts1c3/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTHLnmK3f9hNLO67UdCuLvGwCQHYwQUinR%2Fr4XN7pXNPZzQ4kYU83E1HScCEG7m8c0zRUimCgAAAAD6Yhk%3D | US | der | 471 b | whitelisted |
3952 | iexplore.exe | GET | 200 | 142.250.74.195:80 | http://ocsp.pki.goog/gts1c3/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTHLnmK3f9hNLO67UdCuLvGwCQHYwQUinR%2Fr4XN7pXNPZzQ4kYU83E1HScCEGOt6RAuLJ4ACgAAAAD6ZZ0%3D | US | der | 471 b | whitelisted |
3952 | iexplore.exe | GET | 200 | 142.250.74.195:80 | http://ocsp.pki.goog/gsr2/ME4wTDBKMEgwRjAJBgUrDgMCGgUABBTgXIsxbvr2lBkPpoIEVRE6gHlCnAQUm%2BIHV2ccHsBqBt5ZtJot39wZhi4CDQHjtJqhjYqpgSVpULg%3D | US | der | 468 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
2916 | javaw.exe | 62.210.119.175:443 | www.salwyrr.fr | Online S.a.s. | FR | unknown |
3476 | javaw.exe | 62.210.119.175:443 | www.salwyrr.fr | Online S.a.s. | FR | unknown |
3184 | iexplore.exe | 204.79.197.200:443 | www.bing.com | Microsoft Corporation | US | whitelisted |
3184 | iexplore.exe | 69.16.175.42:80 | ctldl.windowsupdate.com | Highwinds Network Group, Inc. | US | malicious |
3184 | iexplore.exe | 93.184.220.29:80 | ocsp.digicert.com | MCI Communications Services, Inc. d/b/a Verizon Business | US | whitelisted |
3952 | iexplore.exe | 13.107.5.80:443 | api.bing.com | Microsoft Corporation | US | whitelisted |
3952 | iexplore.exe | 204.79.197.200:443 | www.bing.com | Microsoft Corporation | US | whitelisted |
3952 | iexplore.exe | 20.190.160.73:443 | login.microsoftonline.com | Microsoft Corporation | US | suspicious |
3952 | iexplore.exe | 93.184.220.29:80 | ocsp.digicert.com | MCI Communications Services, Inc. d/b/a Verizon Business | US | whitelisted |
3952 | iexplore.exe | 20.190.160.129:443 | login.microsoftonline.com | Microsoft Corporation | US | suspicious |
Domain | IP | Reputation |
|---|---|---|
www.salwyrr.fr |
| unknown |
www.salwyrr.com |
| malicious |
api.bing.com |
| whitelisted |
www.bing.com |
| whitelisted |
ctldl.windowsupdate.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
www.youtube.com |
| whitelisted |
login.microsoftonline.com |
| whitelisted |
login.live.com |
| whitelisted |
www2.bing.com |
| whitelisted |