ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
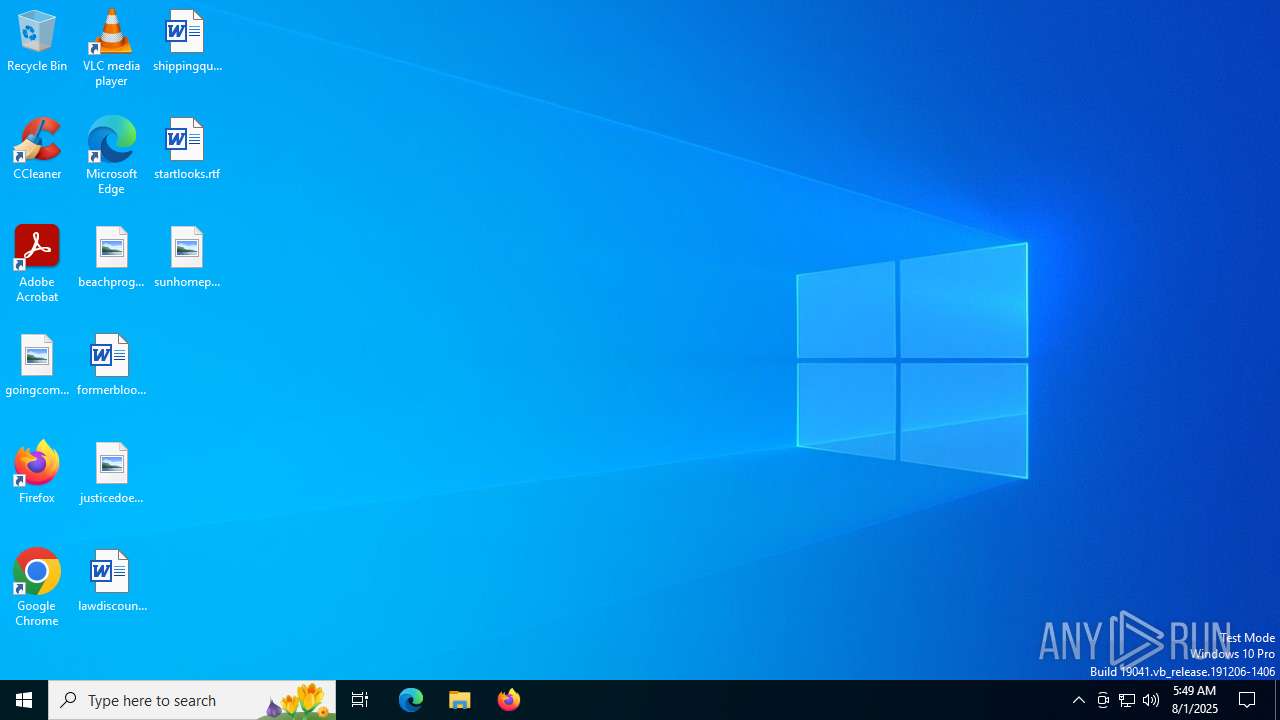
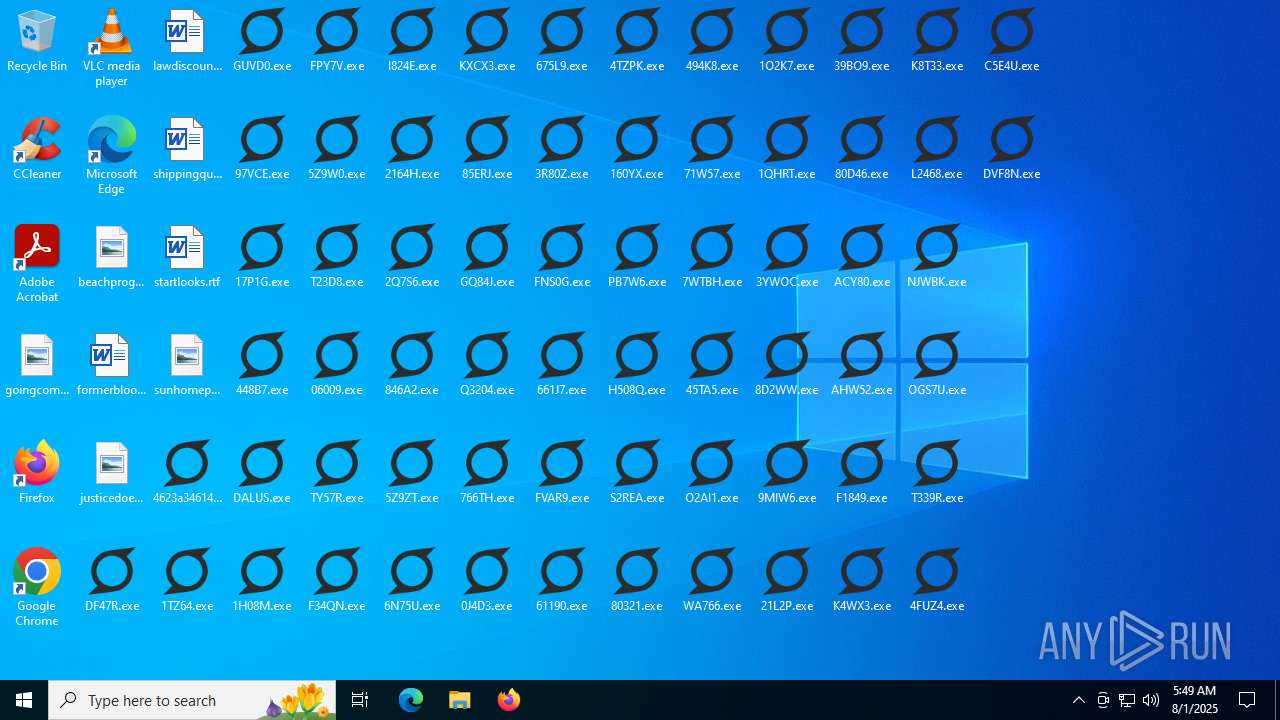
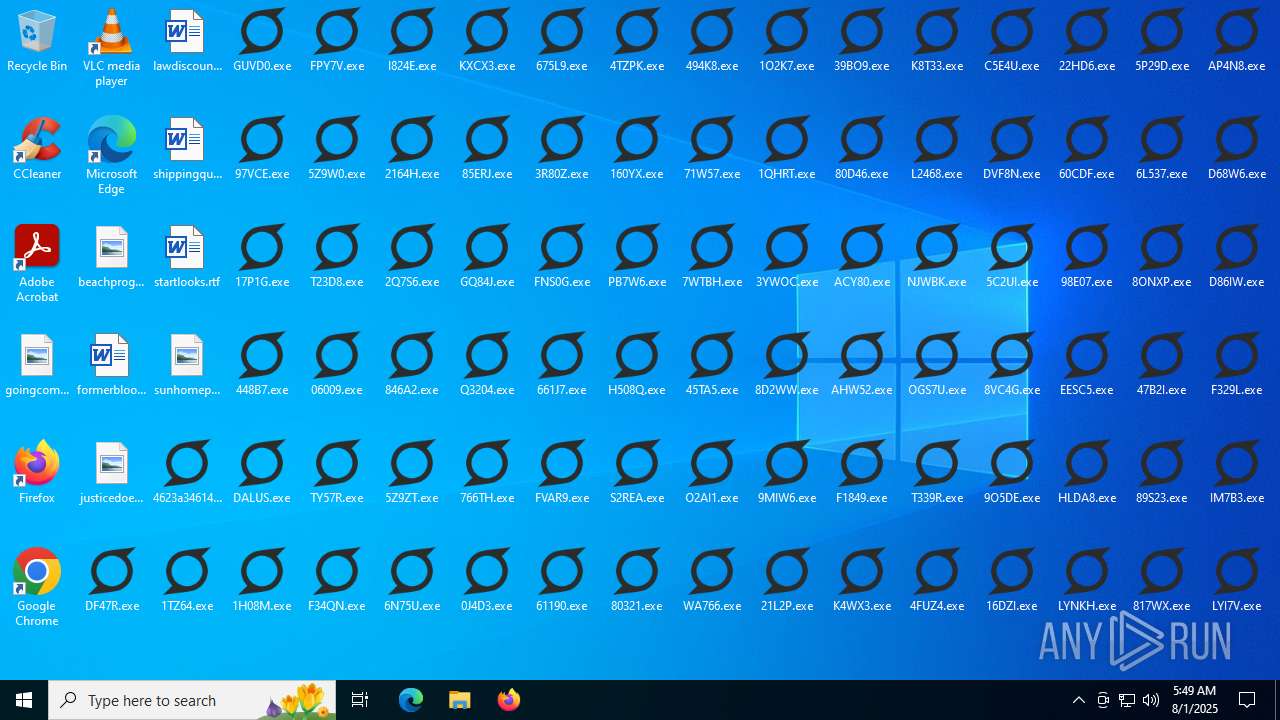
| File name: | 4623a346145abe2870061a1fc66b284a0afdebacffbfcf6fdc74154bce5ea431.exe |
| Full analysis: | https://app.any.run/tasks/6b011a66-6f96-445e-9e78-43d0e03fe592 |
| Verdict: | Malicious activity |
| Analysis date: | August 01, 2025, 05:49:18 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, 4 sections |
| MD5: | 2E9A4DF2F9482B424F7AE23C11EC156E |
| SHA1: | 7DF93AA804C283766FCC6579F9E338DBD5F2A28F |
| SHA256: | 4623A346145ABE2870061A1FC66B284A0AFDEBACFFBFCF6FDC74154BCE5EA431 |
| SSDEEP: | 49152:kfU00mvij07m88988NtxUaq41JEzw01S2Ss5+ZscFZ9bp8vey69EFZ9bp8vey69y:cU00mvjm2UO1S2Ss5uscFHpqFHpqFHpf |
| .exe | | | Win32 Executable MS Visual C++ (generic) (35.8) |
|---|---|---|
| .exe | | | Win64 Executable (generic) (31.7) |
| .scr | | | Windows screen saver (15) |
| .dll | | | Win32 Dynamic Link Library (generic) (7.5) |
| .exe | | | Win32 Executable (generic) (5.1) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 0000:00:00 00:00:00 |
| ImageFileCharacteristics: | No relocs, Executable, No line numbers, No symbols, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 6 |
| CodeSize: | 761856 |
| InitializedDataSize: | 479232 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x9add5 |
| OSVersion: | 4 |
| ImageVersion: | - |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 188 | "C:\Users\admin\Desktop\SP3P0.exe" | C:\Users\admin\Desktop\SP3P0.exe | — | A10QM.exe | |||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 236 | "C:\Users\admin\Desktop\3C46O.exe" | C:\Users\admin\Desktop\3C46O.exe | DY3Y2.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 236 | "C:\Users\admin\Desktop\17W68.exe" | C:\Users\admin\Desktop\17W68.exe | — | PY706.exe | |||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 304 | "C:\Users\admin\Desktop\2SHBJ.exe" | C:\Users\admin\Desktop\2SHBJ.exe | — | 89X7I.exe | |||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 | |||||||||||||||
| 320 | "C:\Users\admin\Desktop\CN7M6.exe" | C:\Users\admin\Desktop\CN7M6.exe | P6JF5.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 424 | "C:\Users\admin\Desktop\1ULPE.exe" | C:\Users\admin\Desktop\1ULPE.exe | 696G8.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 424 | "C:\Users\admin\Desktop\CW7S7.exe" | C:\Users\admin\Desktop\CW7S7.exe | P71B3.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 432 | "C:\Users\admin\Desktop\77DTV.exe" | C:\Users\admin\Desktop\77DTV.exe | — | L5AMU.exe | |||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 472 | "C:\Users\admin\Desktop\8AHU6.exe" | C:\Users\admin\Desktop\8AHU6.exe | X675L.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
| 480 | "C:\Users\admin\Desktop\6VC0B.exe" | C:\Users\admin\Desktop\6VC0B.exe | 96C38.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Exit code: 0 Modules
| |||||||||||||||
PID | Process | Filename | Type | |
|---|---|---|---|---|
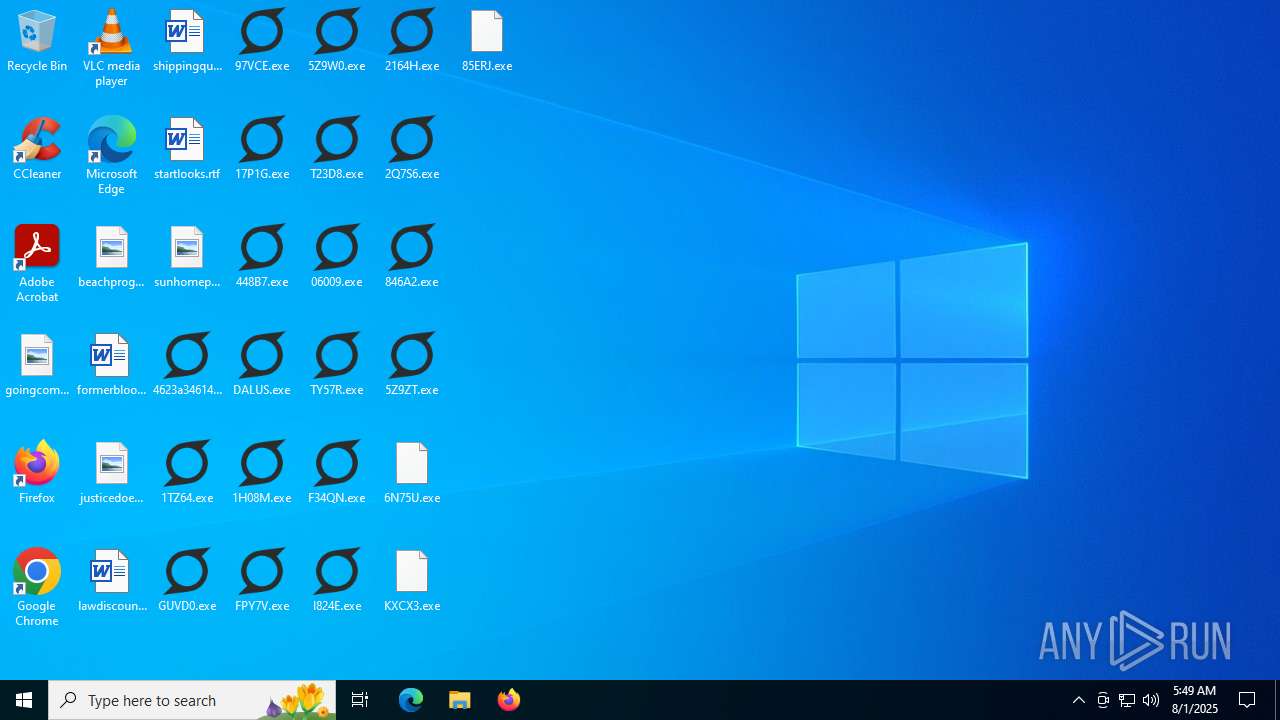
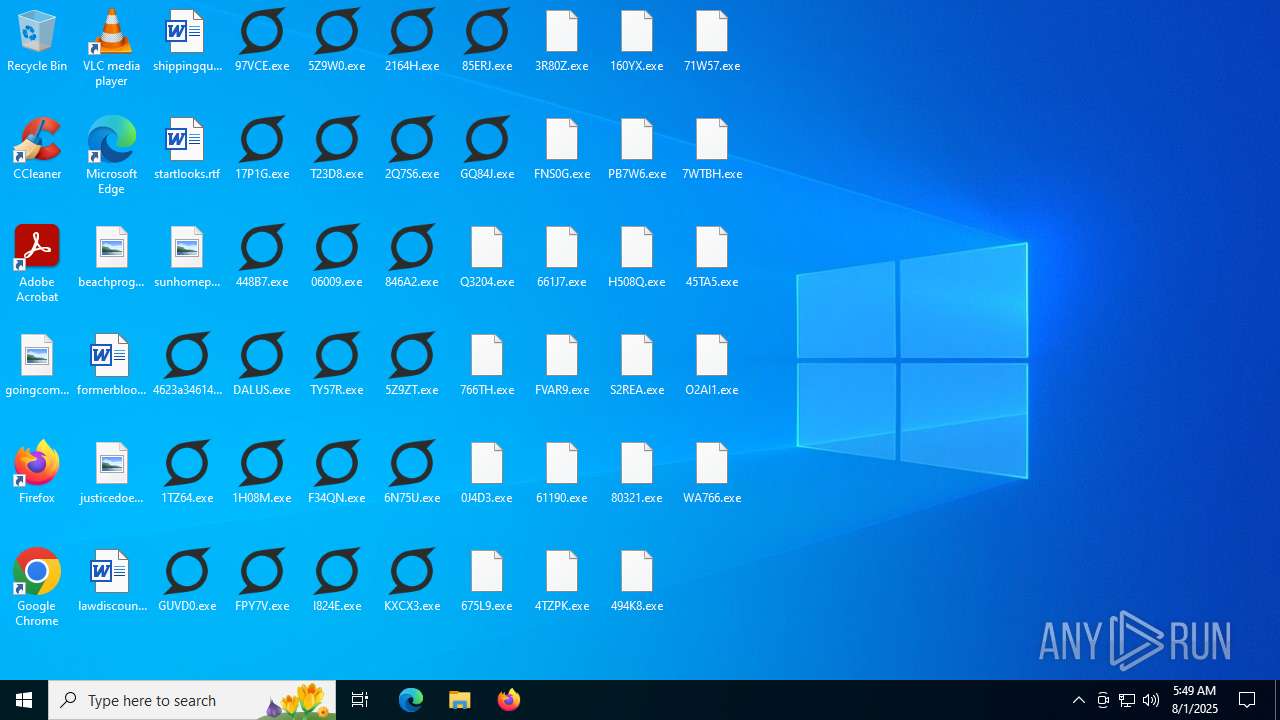
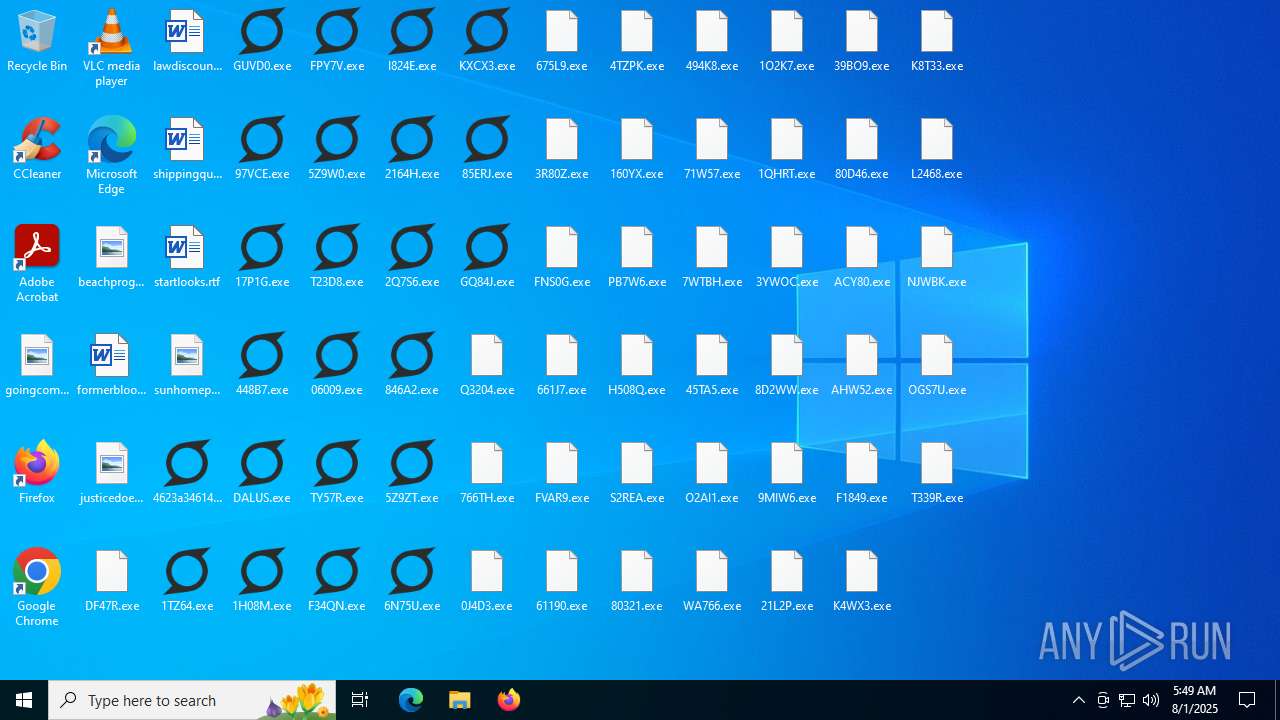
| 2976 | 4623a346145abe2870061a1fc66b284a0afdebacffbfcf6fdc74154bce5ea431.exe | C:\Users\admin\Desktop\1TZ64.exe | executable | |
MD5:A78C869A26E558D6AEA2D381E00286E3 | SHA256:19EDFF617901E04D20962E127EF615126016C07A39451E3A337858DA1975784A | |||
| 6840 | 1TZ64.exe | C:\Users\admin\Desktop\GUVD0.exe | executable | |
MD5:580A6B58B88867FCFBCBC2CA8085526D | SHA256:2A1C2F988DC1540615421B7302EAA416AB25359CA5E74C733AB852B13529DBB9 | |||
| 1944 | 448B7.exe | C:\Users\admin\Desktop\DALUS.exe | executable | |
MD5:2C10F1FE0E871DC8DA4D286378FC604C | SHA256:2C28A71583AAF25A0DFAAC2335F50C01405671EFA56648C362C7DF7D00C33A30 | |||
| 4768 | 5Z9W0.exe | C:\Users\admin\Desktop\T23D8.exe | executable | |
MD5:C57EFC805E85FB7D7ECCB439C4DCA99A | SHA256:7F89A04EA307F656ADB6298E06543131CB0414AD8DFDAA33F296D5B558339B80 | |||
| 2220 | T23D8.exe | C:\Users\admin\Desktop\06009.exe | executable | |
MD5:7AA6B80FD8DFF8D5509AD224714FAEC2 | SHA256:9C6F6130579FFA659AD61CFE4962F5664291FC25A3EEB8357DBD0EDFEFA0E36B | |||
| 6572 | 06009.exe | C:\Users\admin\Desktop\TY57R.exe | executable | |
MD5:1F3D1D0AE9426AEA77AB1A37A650373B | SHA256:F1F6CD62564965C9DB5E249BB4C5A678C39AA55883F325F15072587A77EFF12A | |||
| 1508 | FPY7V.exe | C:\Users\admin\Desktop\5Z9W0.exe | executable | |
MD5:8A902FC17701277C1730E1A43D8A889D | SHA256:A9B3E8C8243D703093FB9BF008AC0A9E7408D33BDA7F60A9914EA6B495A4EE13 | |||
| 6936 | KXCX3.exe | C:\Users\admin\Desktop\85ERJ.exe | executable | |
MD5:A60965474A9AA94A2C82614832A13CCE | SHA256:03FB01C36FA0D3426E3872AF79A158727B60DF6105BEFDC5702AF260BCB85E54 | |||
| 700 | 2164H.exe | C:\Users\admin\Desktop\2Q7S6.exe | executable | |
MD5:B8EC45C617FFF39635A7A4BF0209FBD3 | SHA256:1F0B9C439B6C7E98EB657523D86A4DD1541E8DEC1DCC55BAF8EBCC7F5C8419E7 | |||
| 2028 | 2Q7S6.exe | C:\Users\admin\Desktop\846A2.exe | executable | |
MD5:76EE959039D9237ACAE38E1C4FCC9DF7 | SHA256:7B6FB2183B02A208F2AE7BDFE02B7E741B2A0E85386A7870EAF223E595399C82 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
5944 | MoUsoCoreWorker.exe | GET | 200 | 23.57.4.240:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | FR | binary | 814 b | whitelisted |
— | — | POST | 400 | 40.126.32.133:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | whitelisted |
— | — | POST | 400 | 20.190.160.131:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | whitelisted |
— | — | POST | 200 | 40.126.32.72:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 16.7 Kb | whitelisted |
1268 | svchost.exe | GET | 200 | 23.57.4.240:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | FR | binary | 814 b | whitelisted |
2216 | RUXIMICS.exe | GET | 200 | 23.216.77.42:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 825 b | whitelisted |
— | — | GET | 200 | 52.149.20.212:443 | https://slscr.update.microsoft.com/SLS/%7B522D76A4-93E1-47F8-B8CE-07C937AD1A1E%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL | US | — | — | unknown |
— | — | POST | 200 | 40.126.32.134:443 | https://login.live.com/RST2.srf | US | xml | 11.1 Kb | whitelisted |
— | — | GET | 200 | 13.95.31.18:443 | https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping | NL | — | — | unknown |
— | — | POST | 200 | 40.126.32.140:443 | https://login.live.com/RST2.srf | US | xml | 1.24 Kb | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
5944 | MoUsoCoreWorker.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
1268 | svchost.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
2216 | RUXIMICS.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
5944 | MoUsoCoreWorker.exe | 23.216.77.42:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
1268 | svchost.exe | 23.216.77.42:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
2216 | RUXIMICS.exe | 23.216.77.42:80 | crl.microsoft.com | Akamai International B.V. | DE | whitelisted |
5944 | MoUsoCoreWorker.exe | 23.57.4.240:80 | www.microsoft.com | AKAMAI-AS | FR | whitelisted |
1268 | svchost.exe | 23.57.4.240:80 | www.microsoft.com | AKAMAI-AS | FR | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
login.live.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |
self.events.data.microsoft.com |
| whitelisted |
activation-v2.sls.microsoft.com |
| whitelisted |