ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
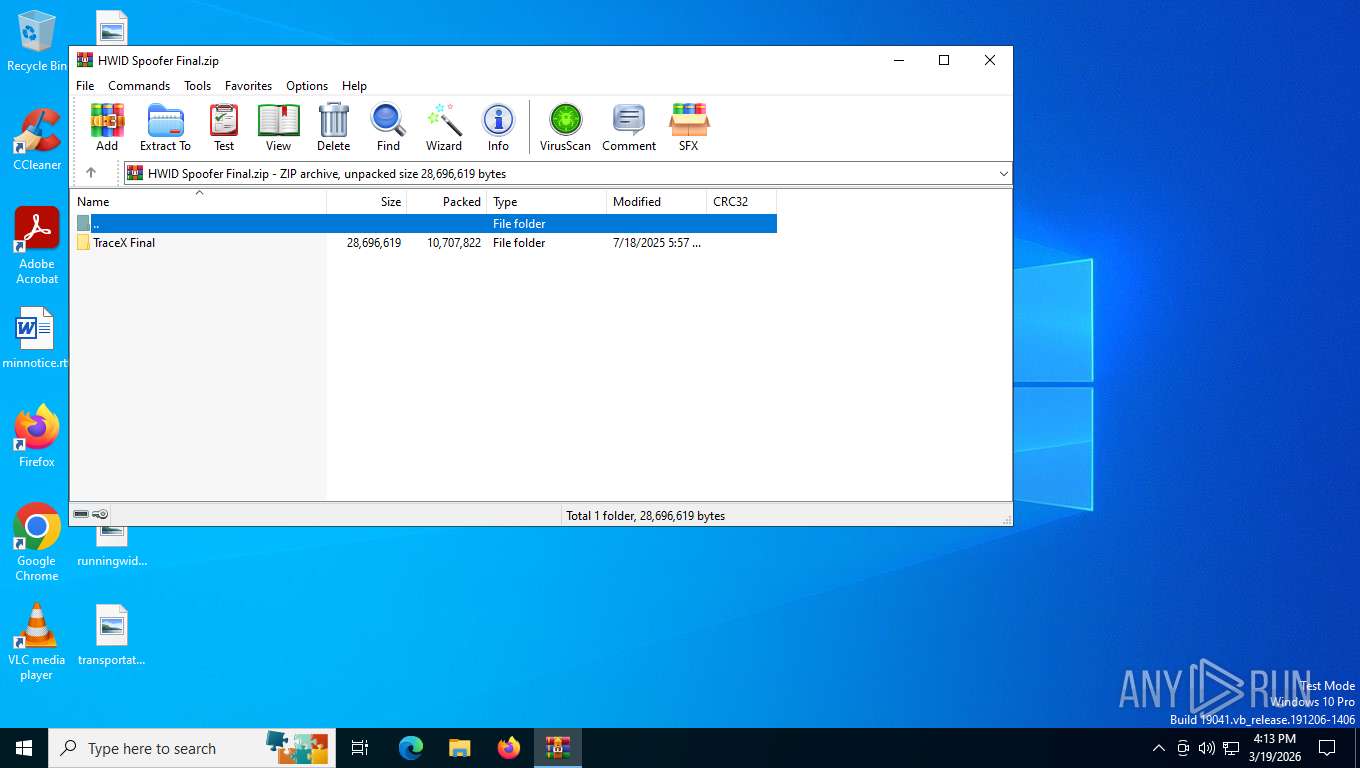
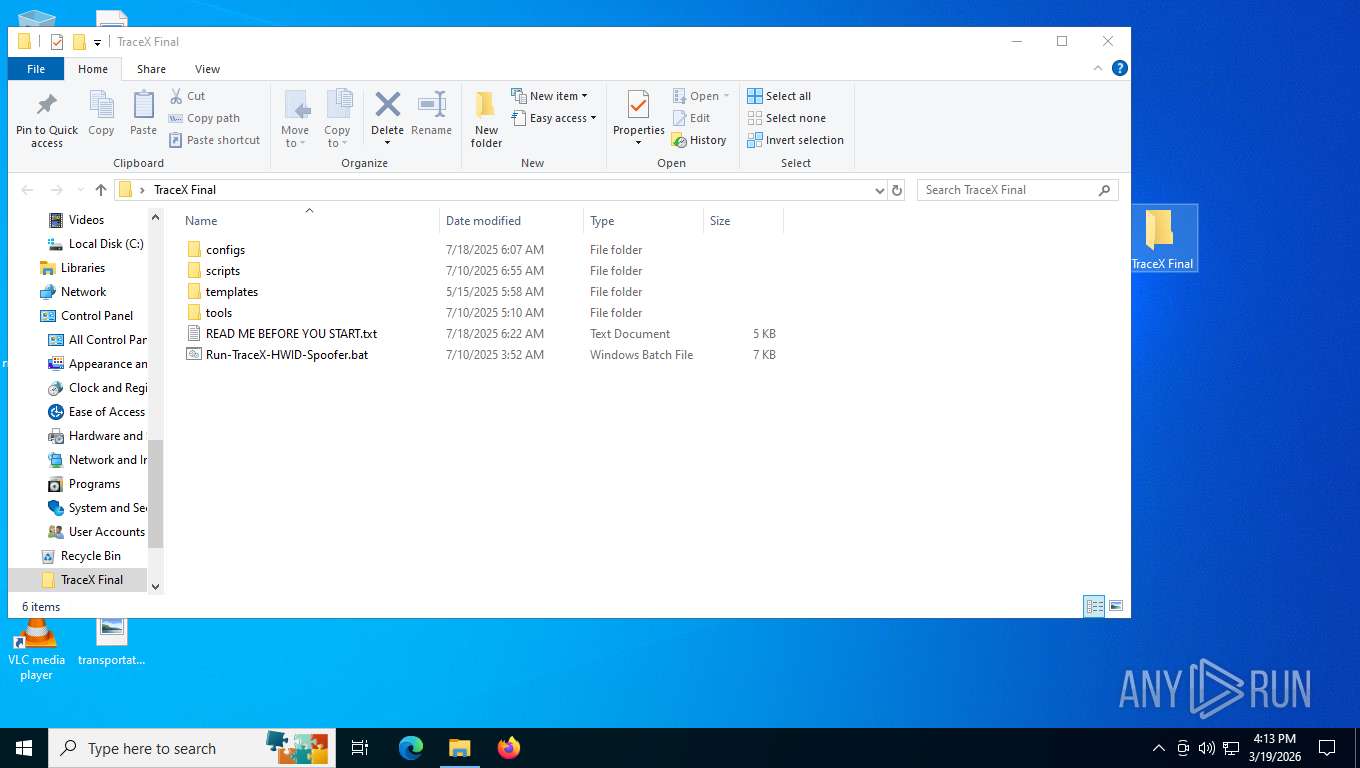
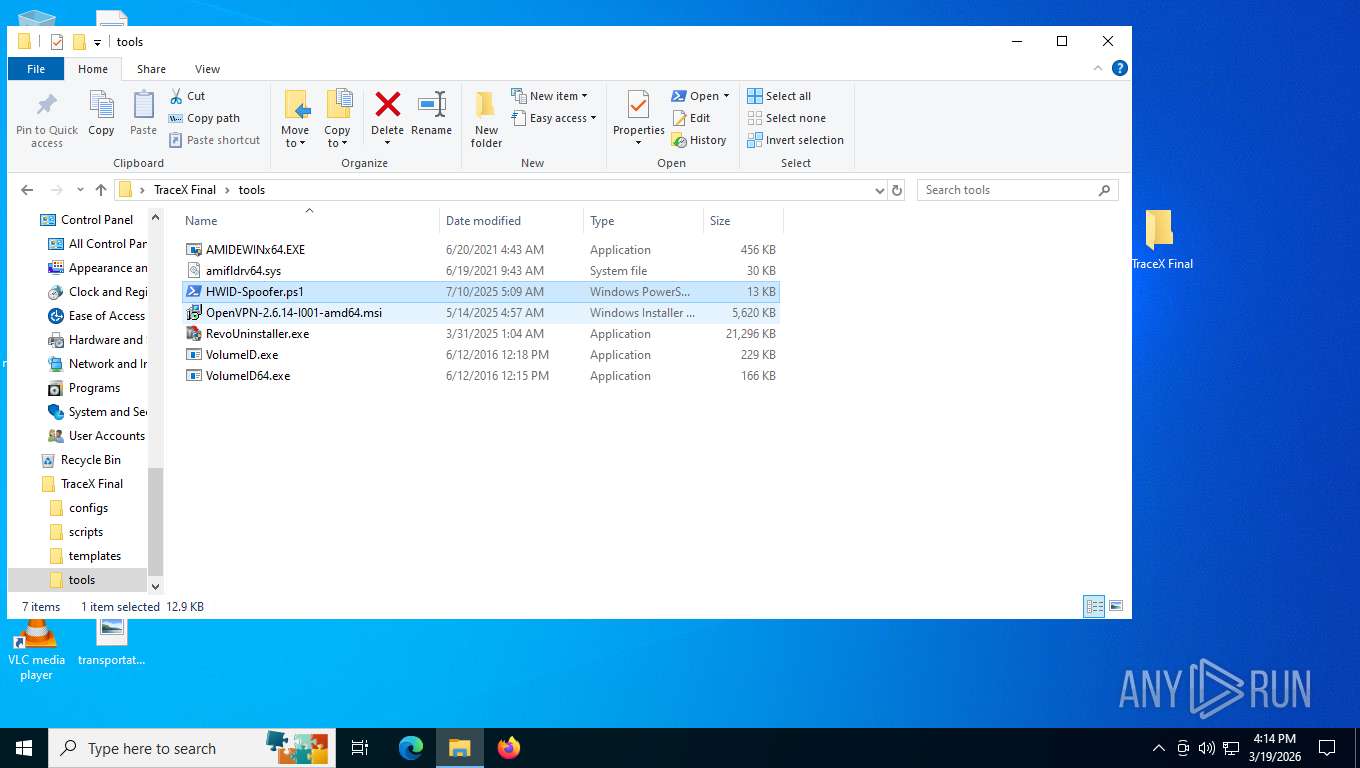
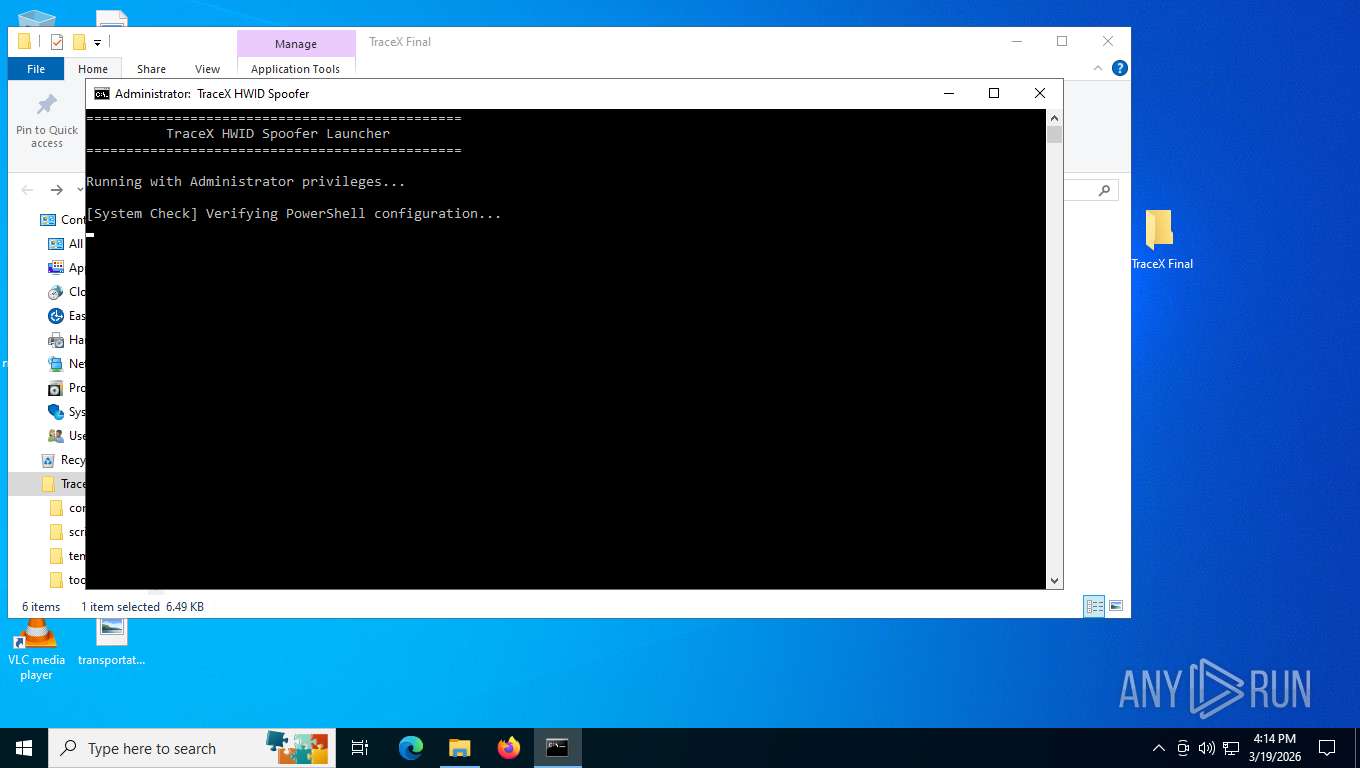
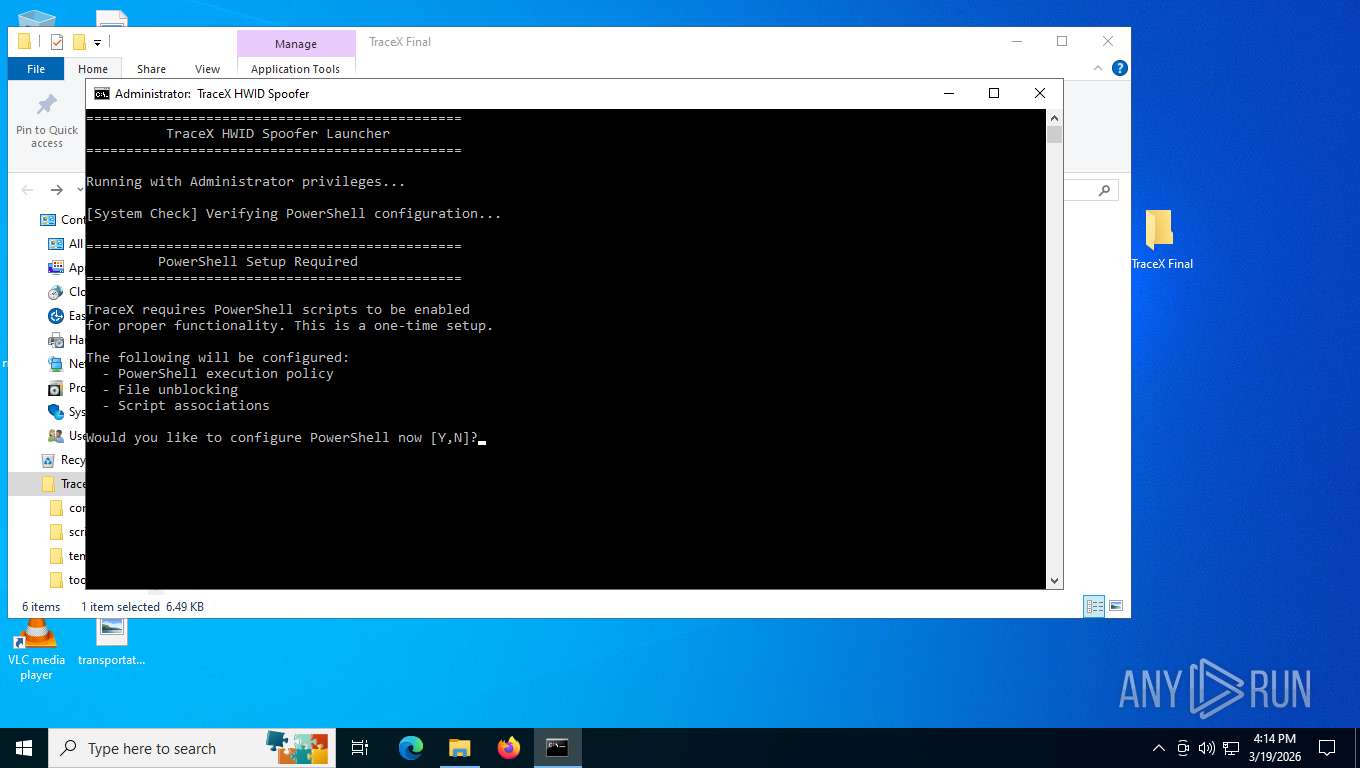
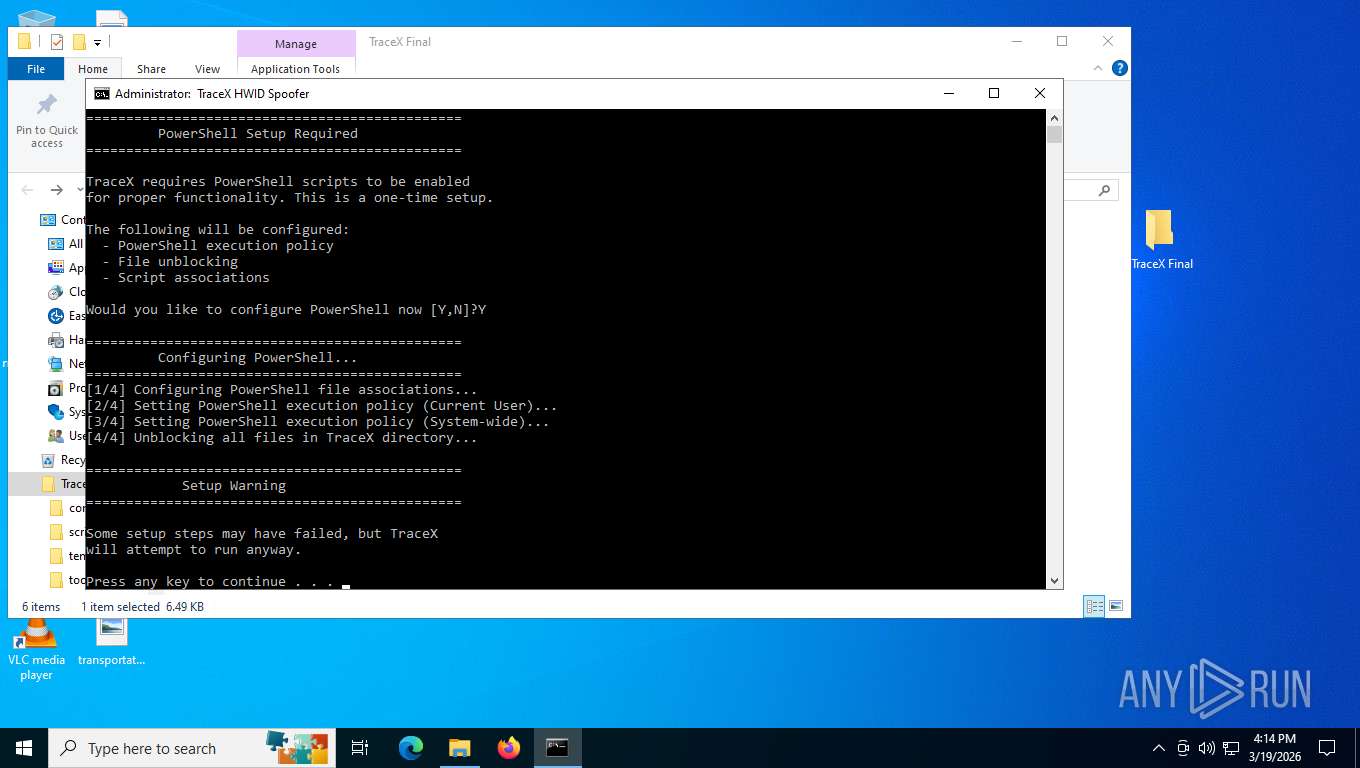
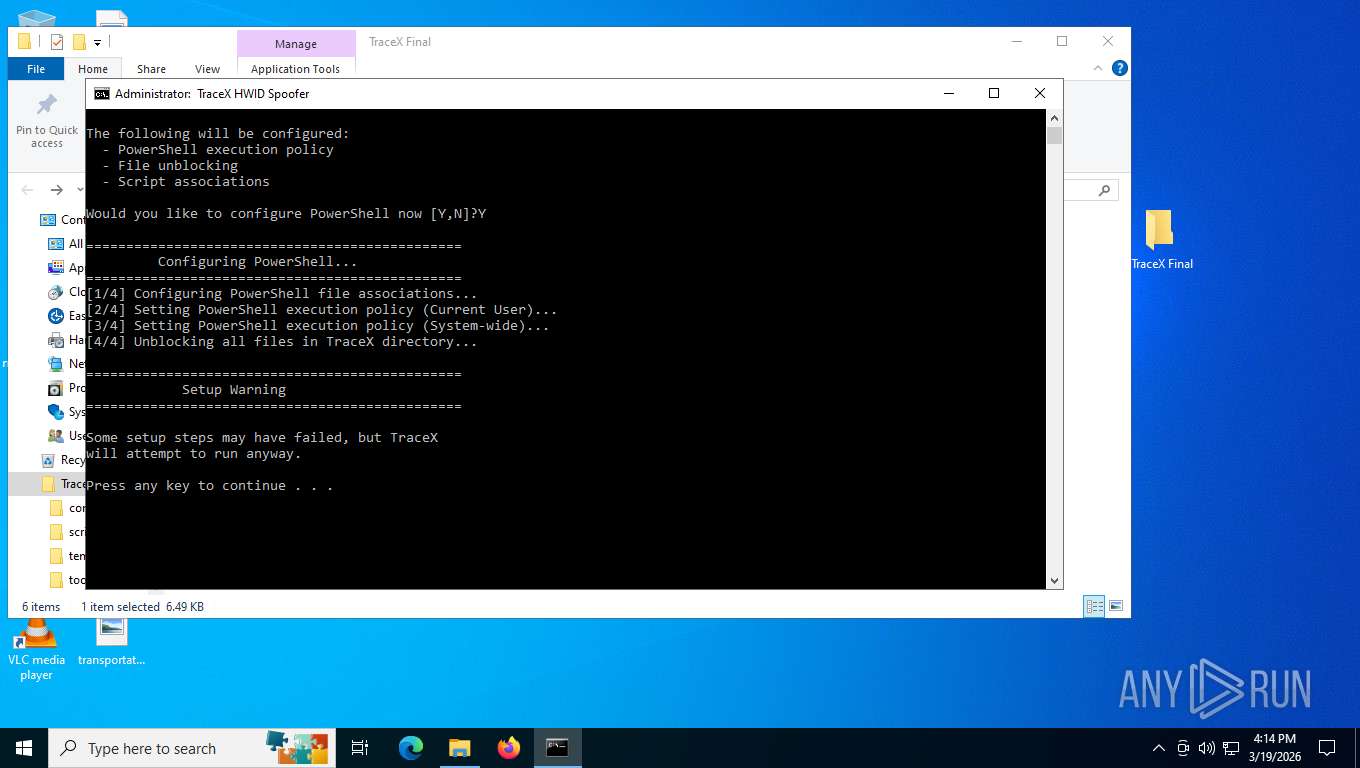
| File name: | HWID Spoofer Final.zip |
| Full analysis: | https://app.any.run/tasks/a1bc0105-b181-4bcc-a29f-f9b344c64350 |
| Verdict: | Malicious activity |
| Analysis date: | March 19, 2026, 20:13:08 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/zip |
| File info: | Zip archive data, at least v2.0 to extract, compression method=store |
| MD5: | C20D2C8EE0BBD890999AEA5DF5BE143C |
| SHA1: | 1CAB8A73E8ED5A97020433968C677DFF28E83BC1 |
| SHA256: | 3D5A0CDA5722CDEFDCEB86E511E191C1C9D147C9AADF964F792D63E5AACFBEB8 |
| SSDEEP: | 98304:zg1JBVy3Ug0KTMEL2YKfSd9GJ2f3+jyVlldbzV9ima6ehzDTs3251JrkSFLMEXca:aQ+qcG2h9dC+7ws |
| .zip | | | ZIP compressed archive (100) |
|---|
| ZipRequiredVersion: | 20 |
|---|---|
| ZipBitFlag: | - |
| ZipCompression: | None |
| ZipModifyDate: | 2025:07:18 12:57:12 |
| ZipCRC: | 0x00000000 |
| ZipCompressedSize: | - |
| ZipUncompressedSize: | - |
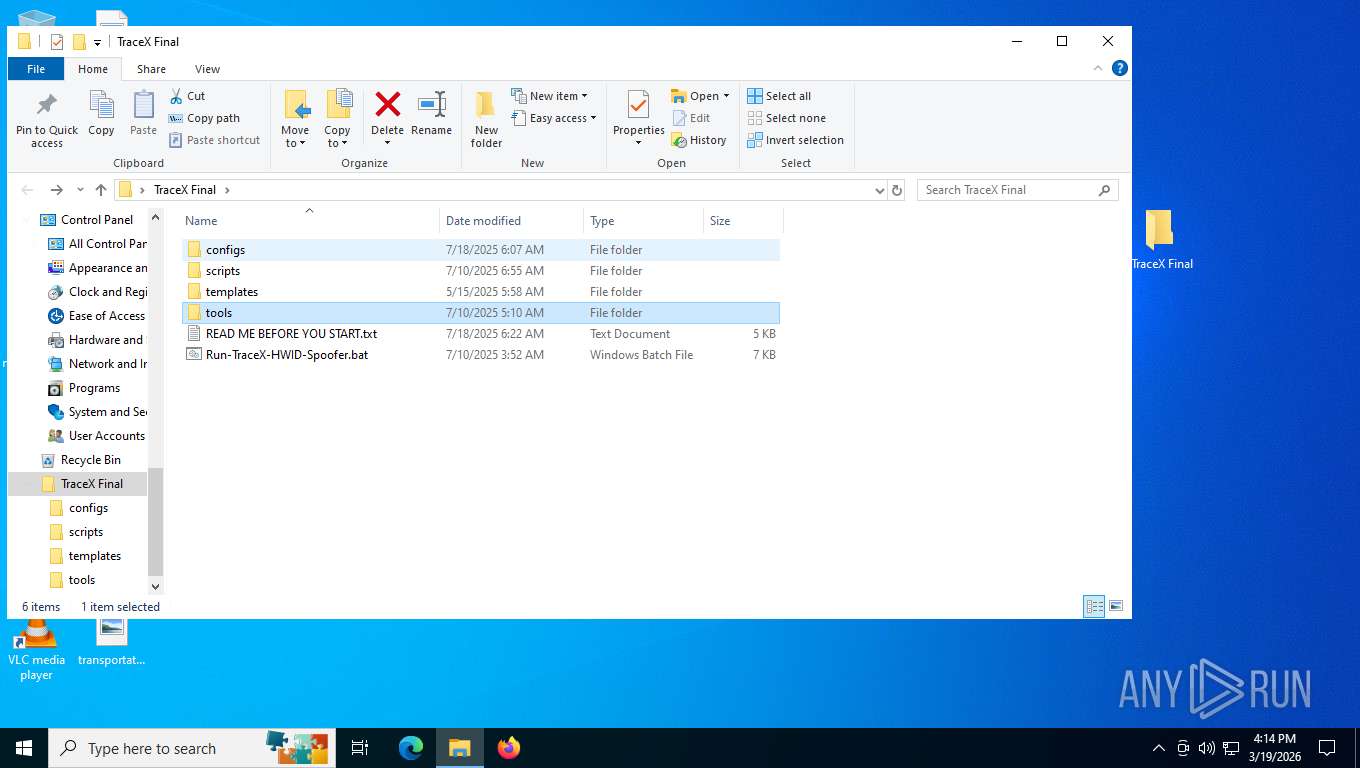
| ZipFileName: | TraceX Final/ |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1032 | "C:\WINDOWS\system32\ipconfig.exe" /renew | C:\Windows\System32\ipconfig.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: IP Configuration Utility Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
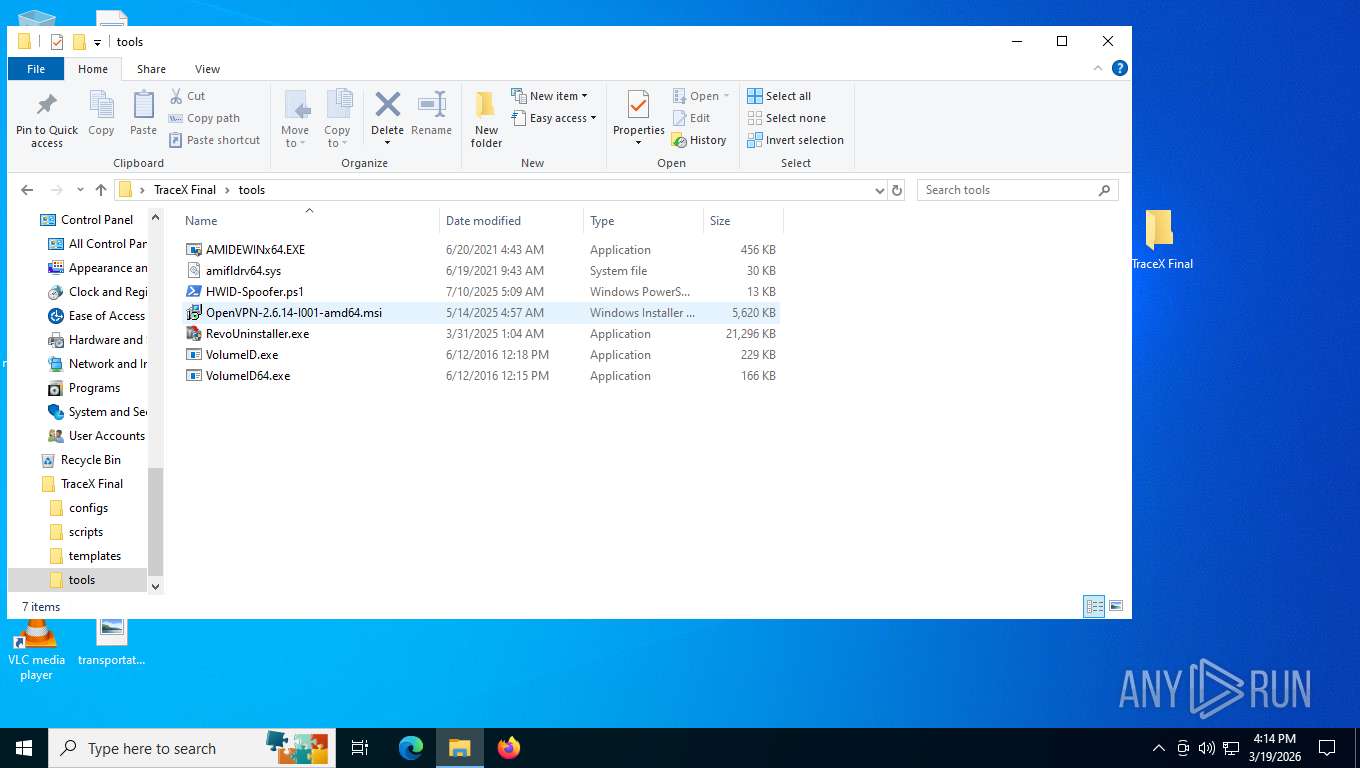
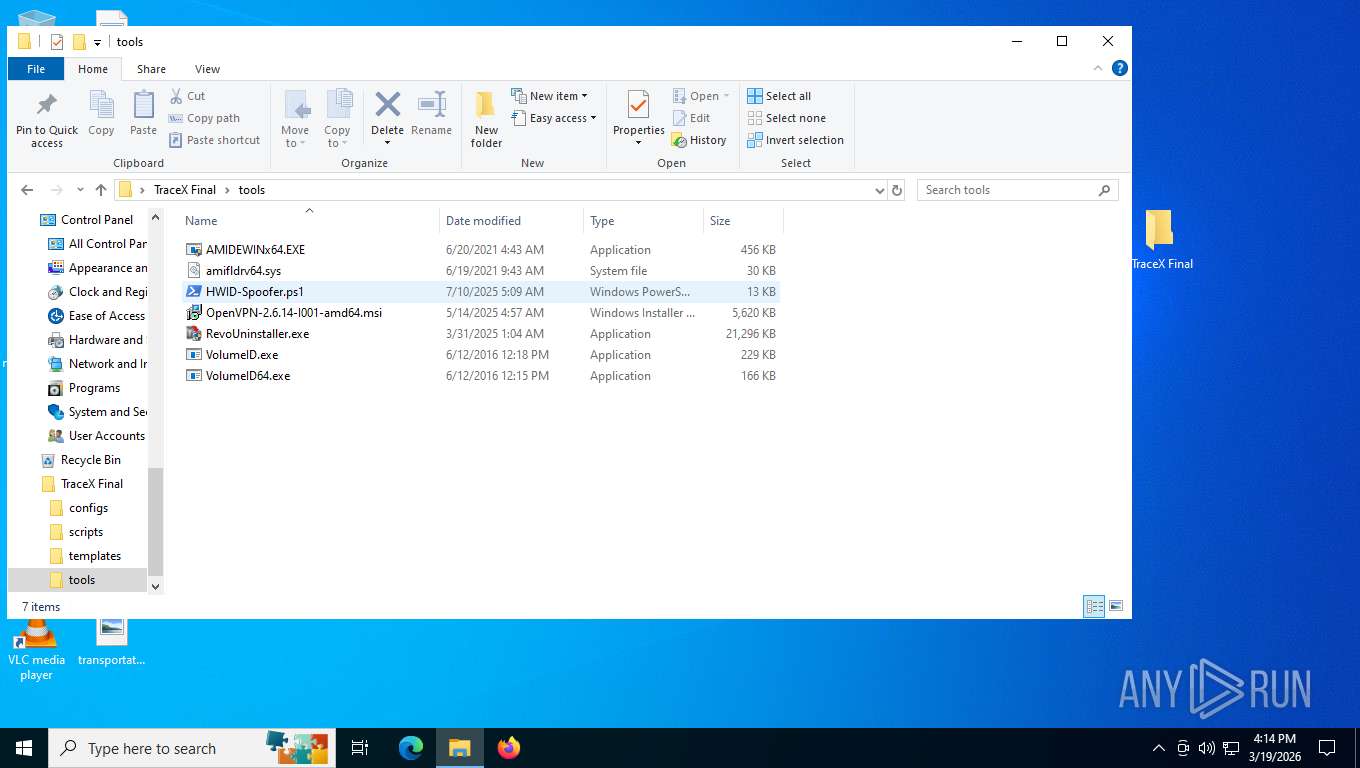
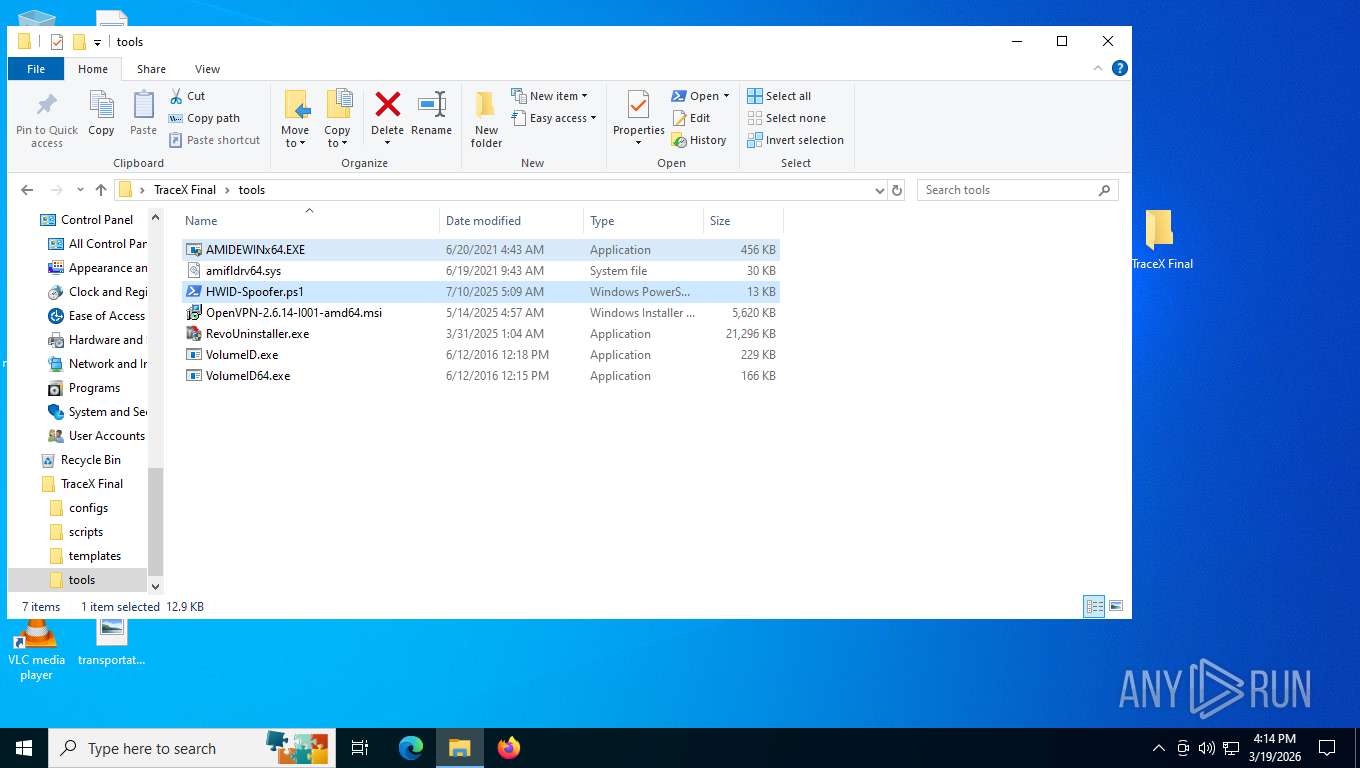
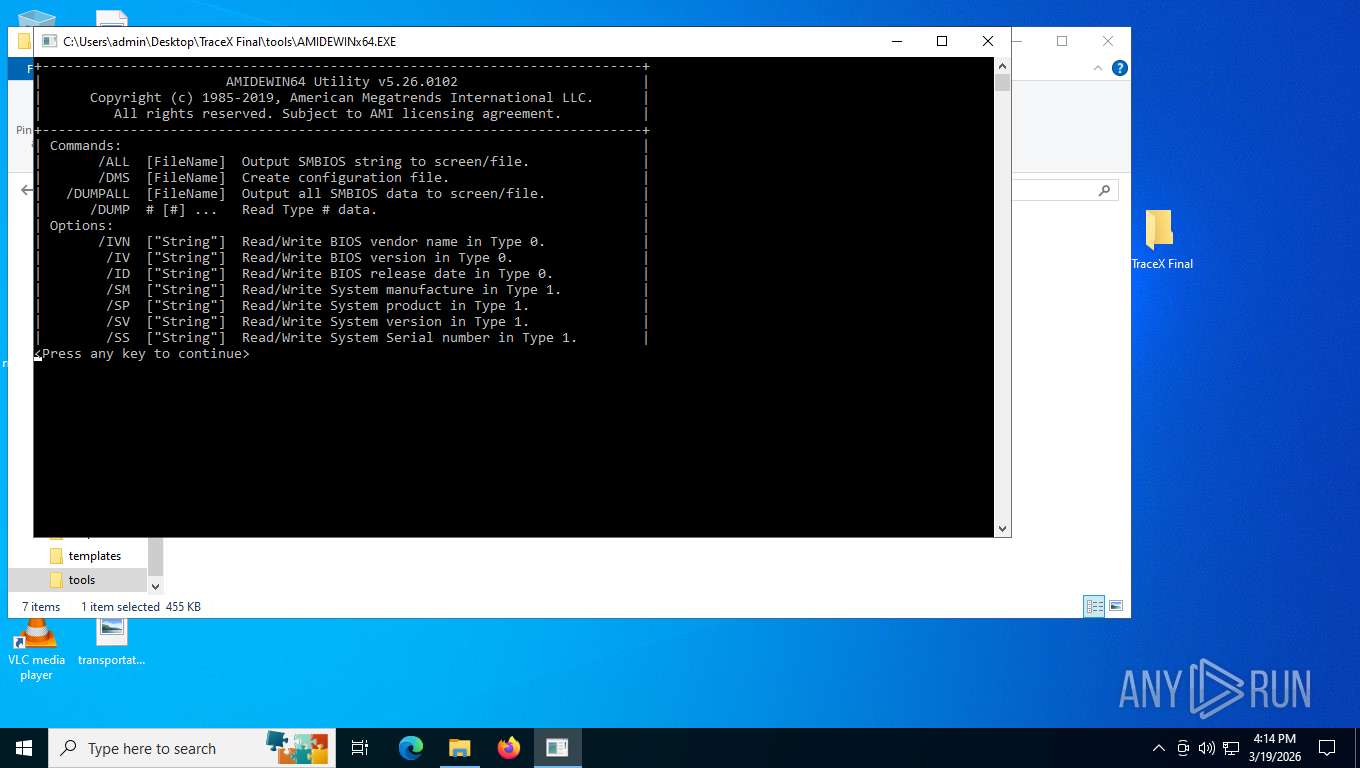
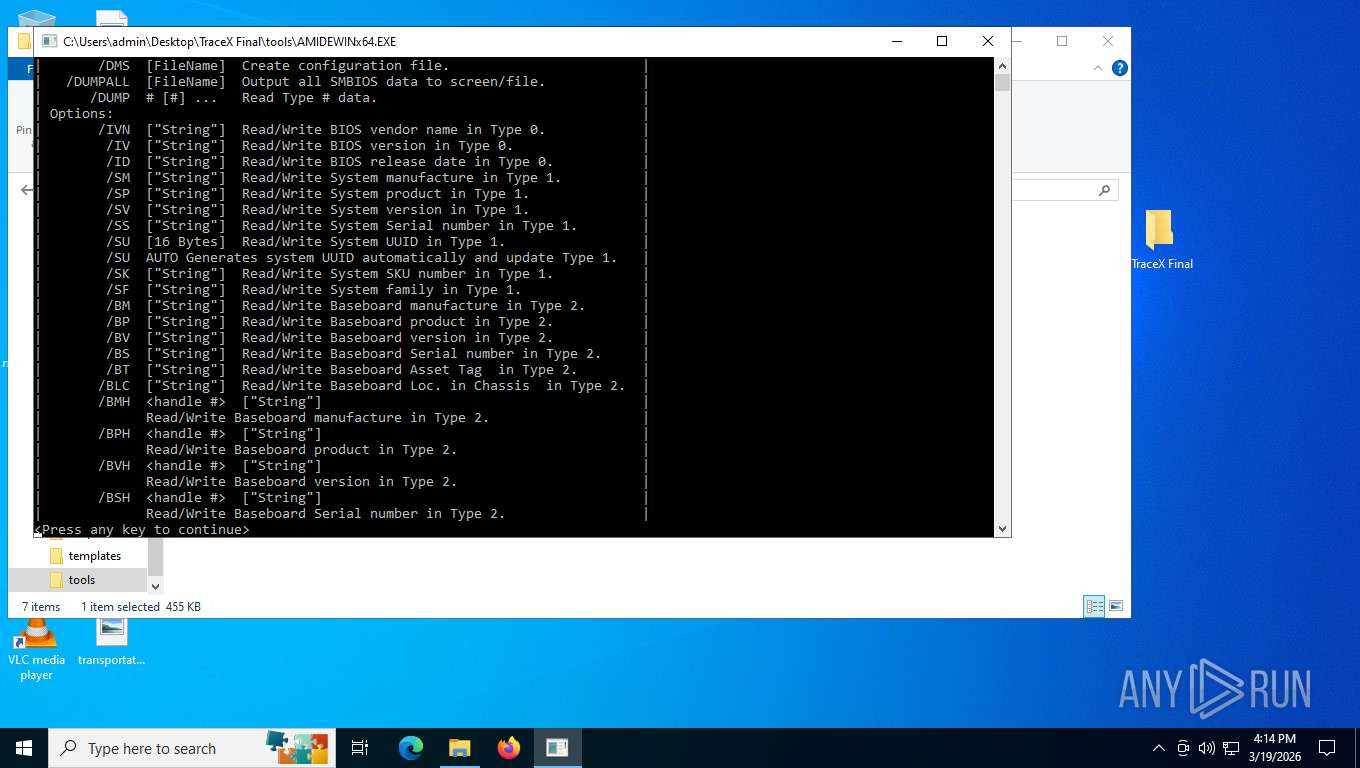
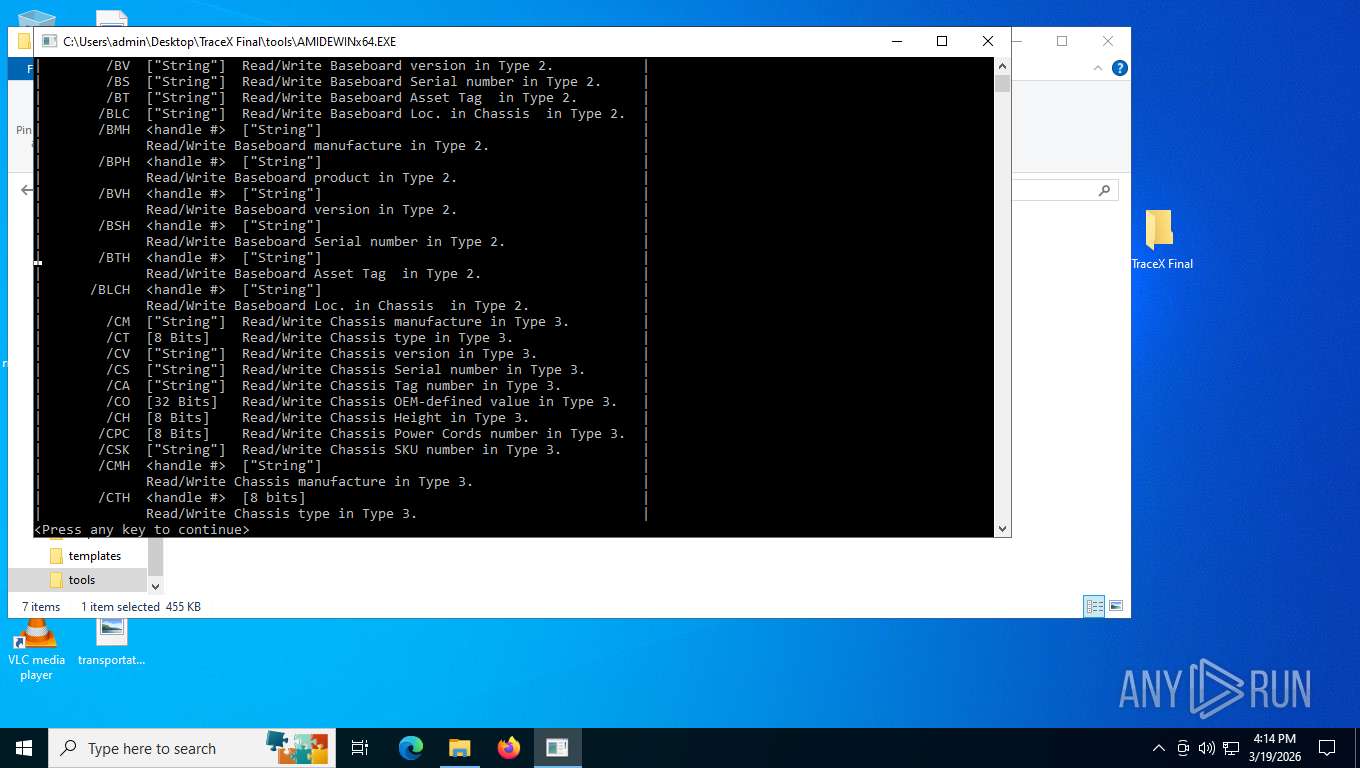
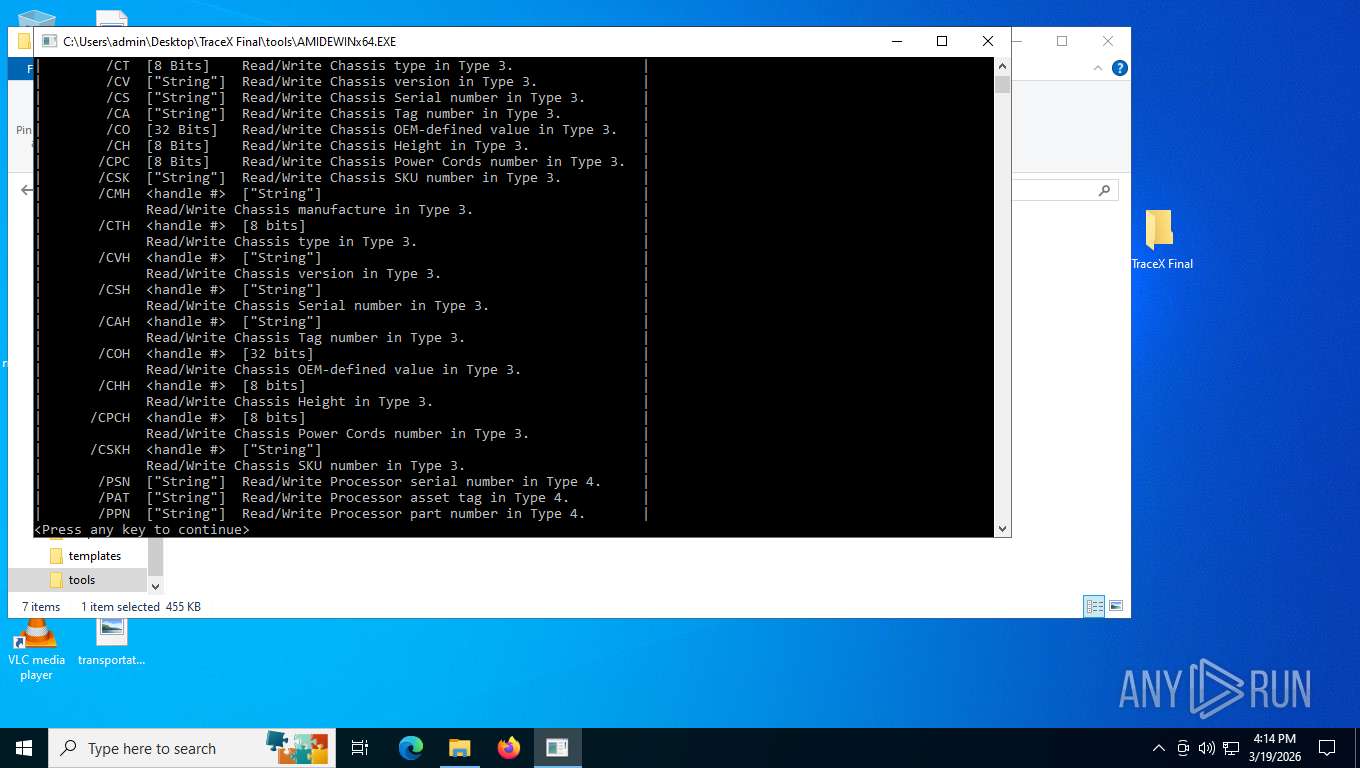
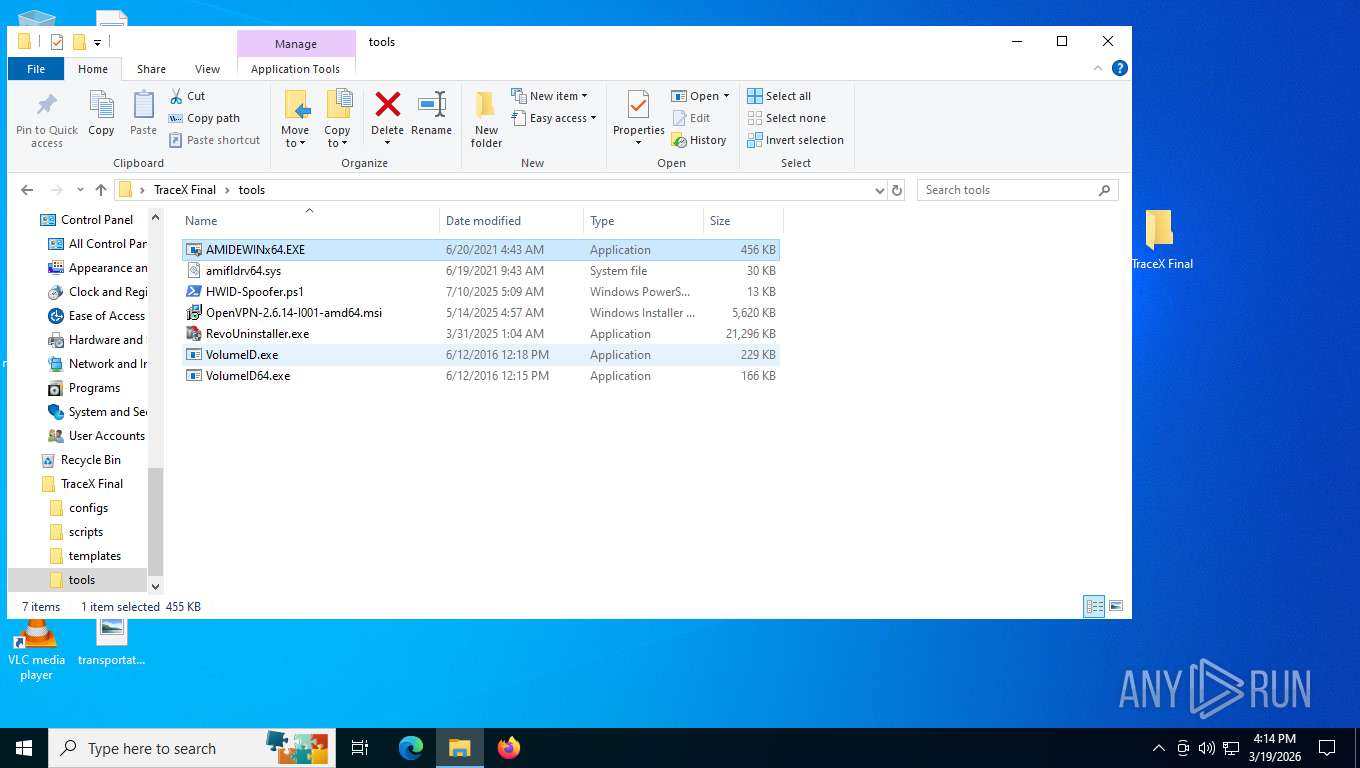
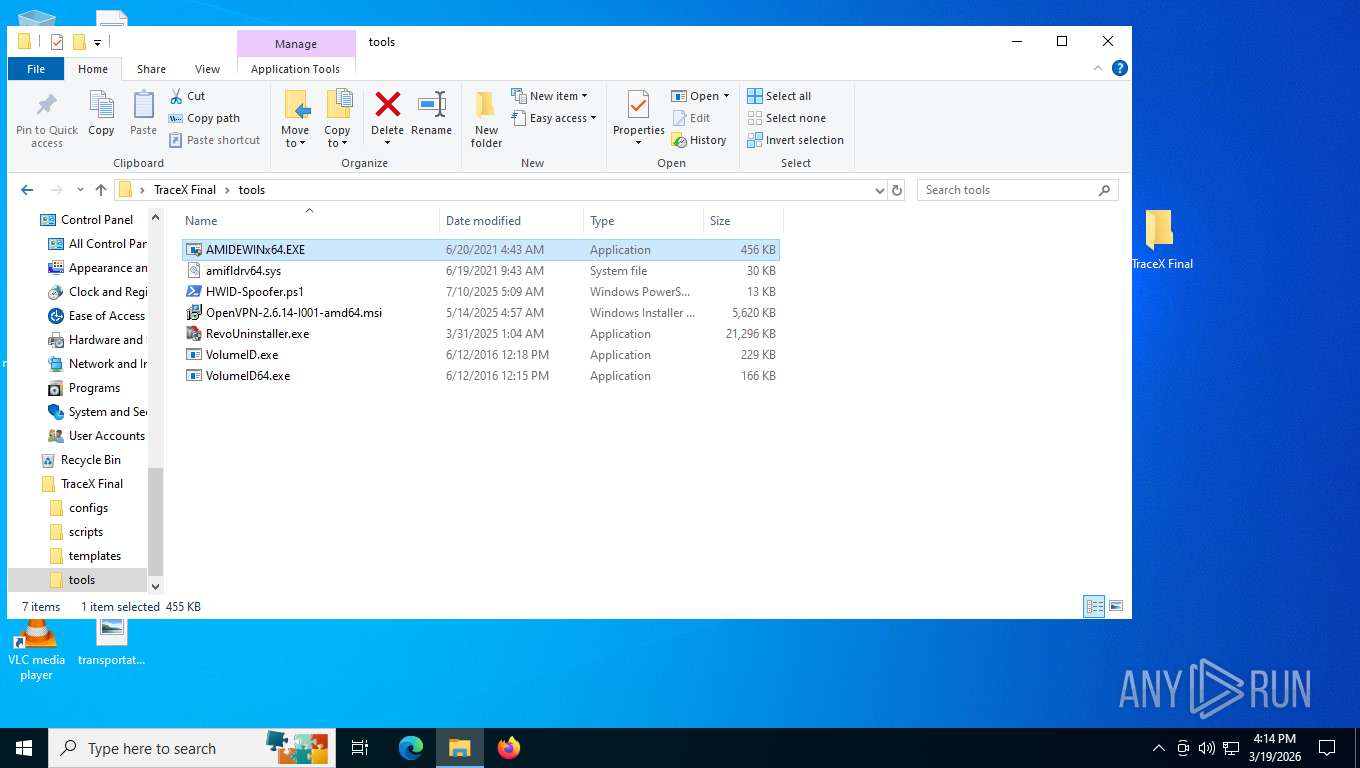
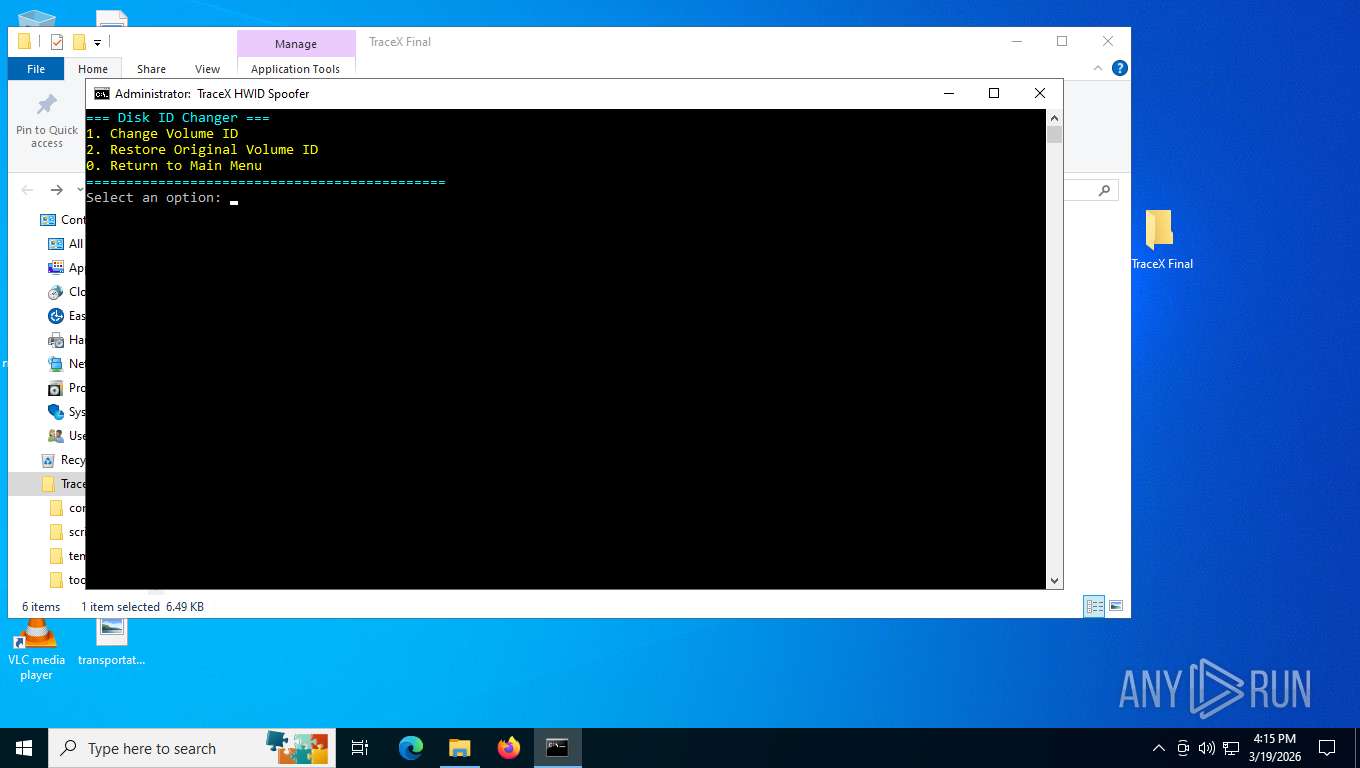
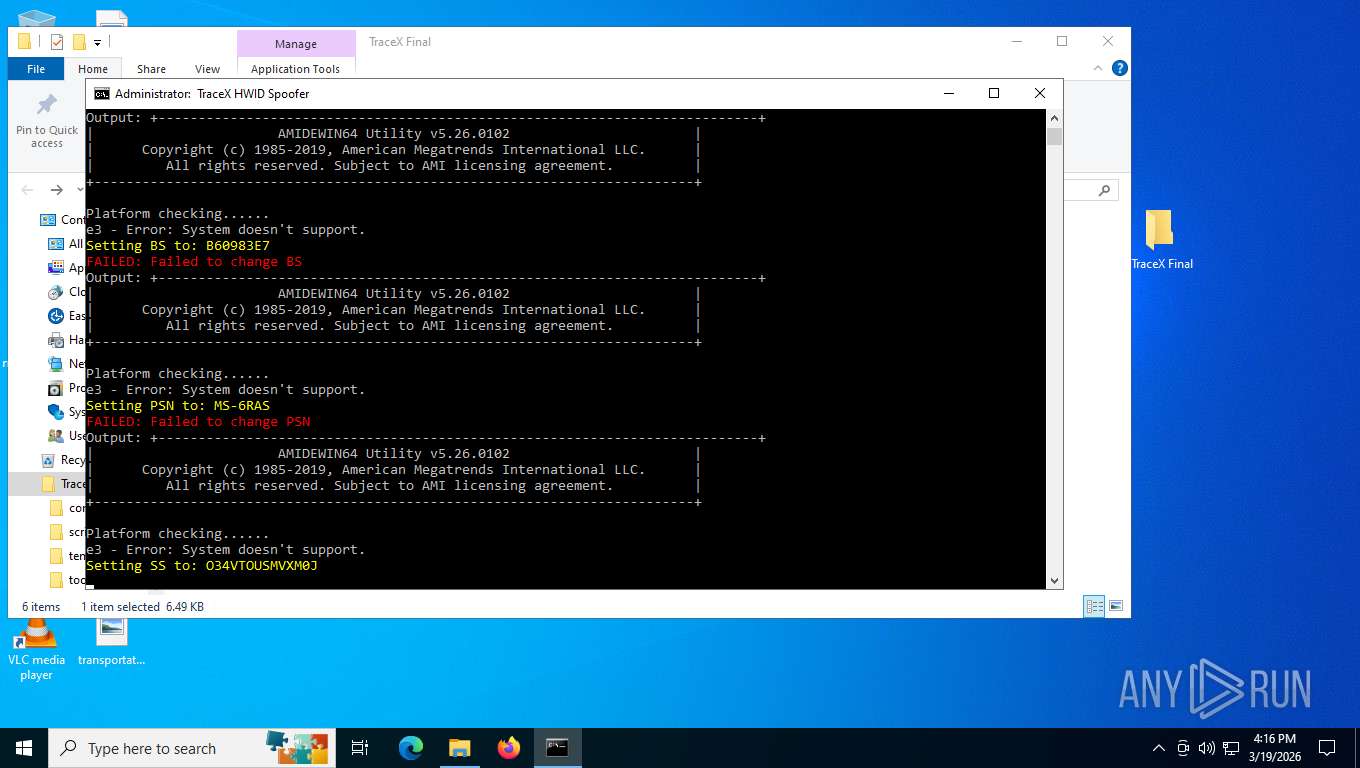
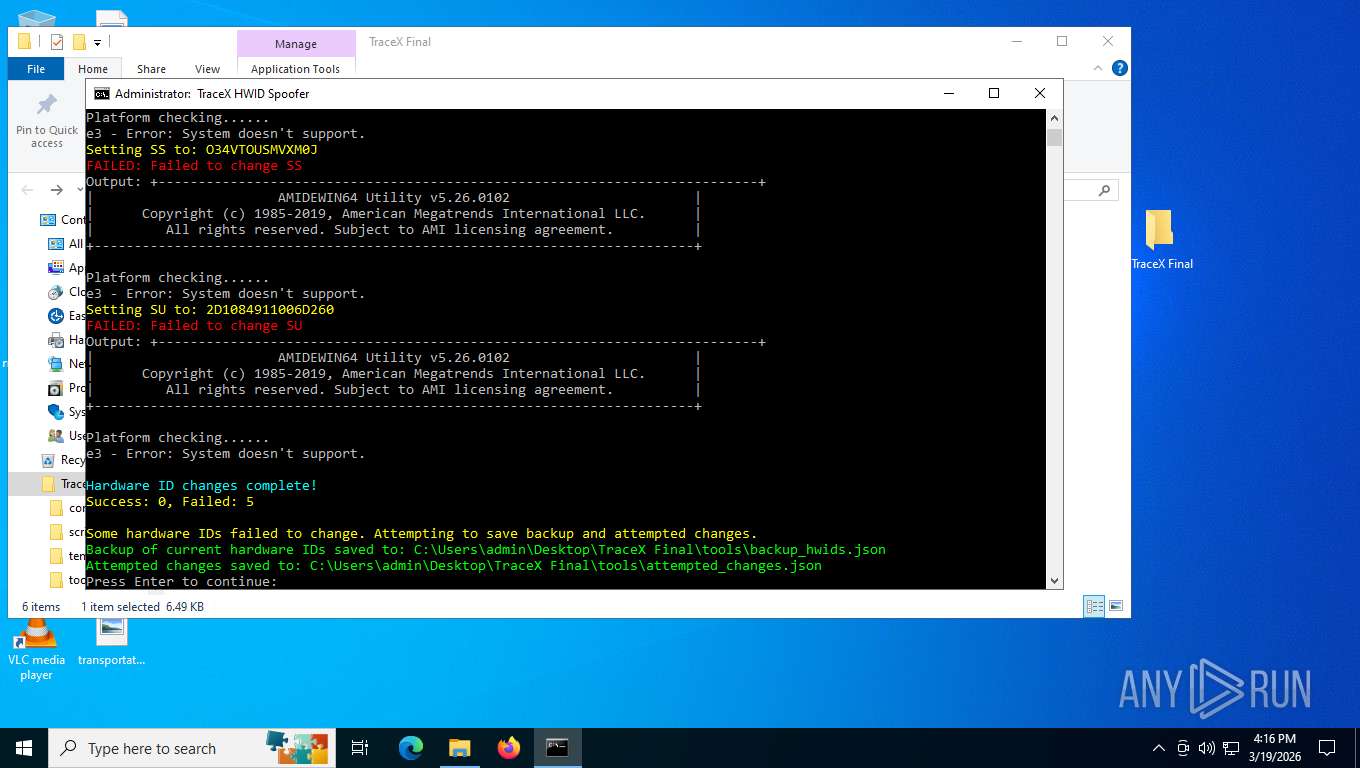
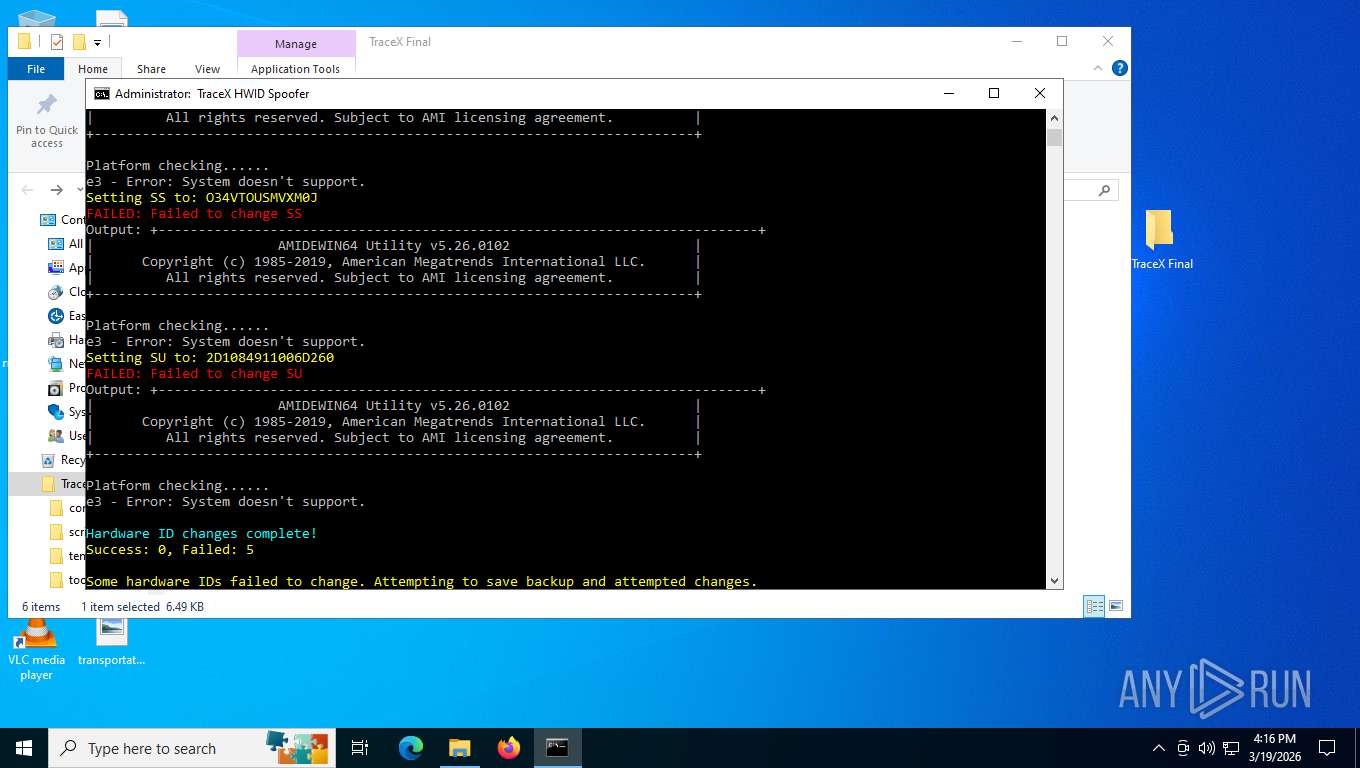
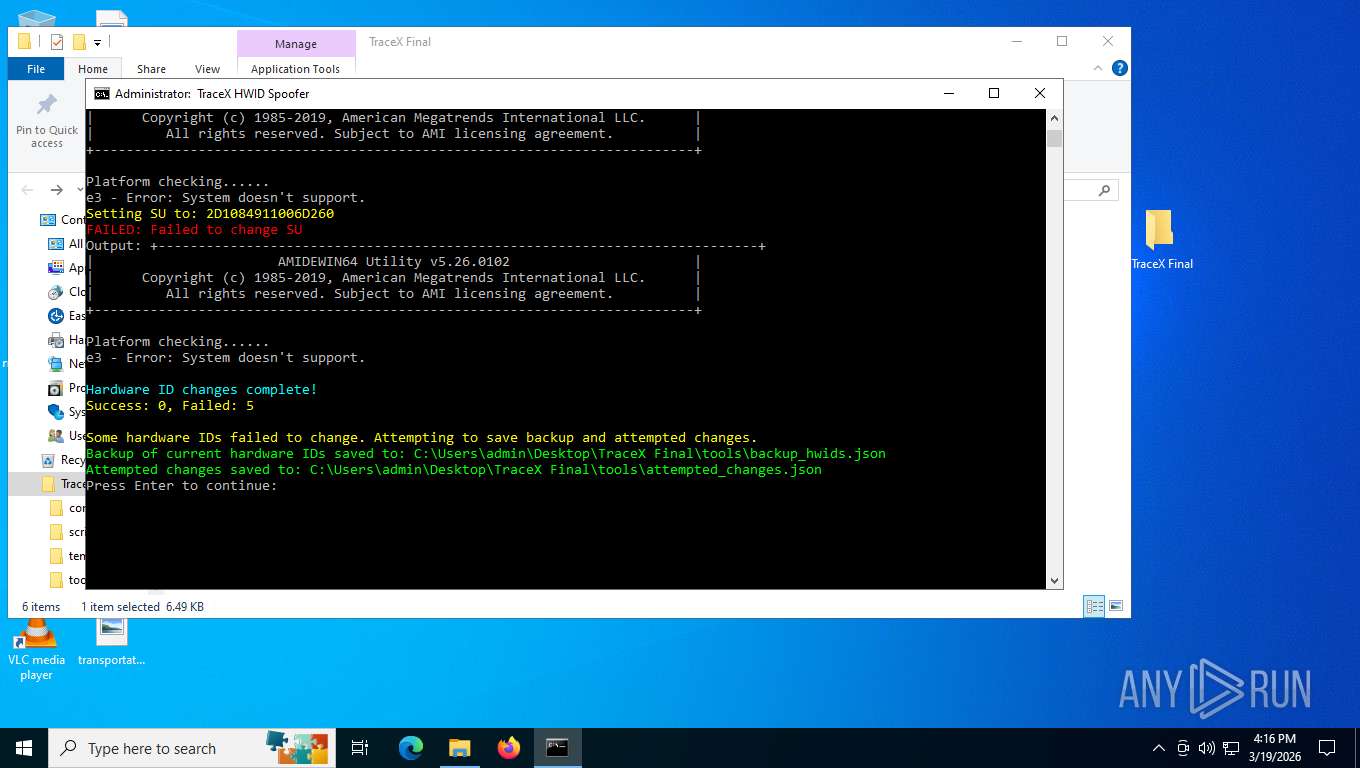
| 1268 | "C:\Users\admin\Desktop\TraceX Final\tools\AMIDEWINx64.EXE" /SS | C:\Users\admin\Desktop\TraceX Final\tools\AMIDEWINx64.EXE | — | powershell.exe | |||||||||||
User: admin Integrity Level: HIGH Exit code: 227 Modules
| |||||||||||||||
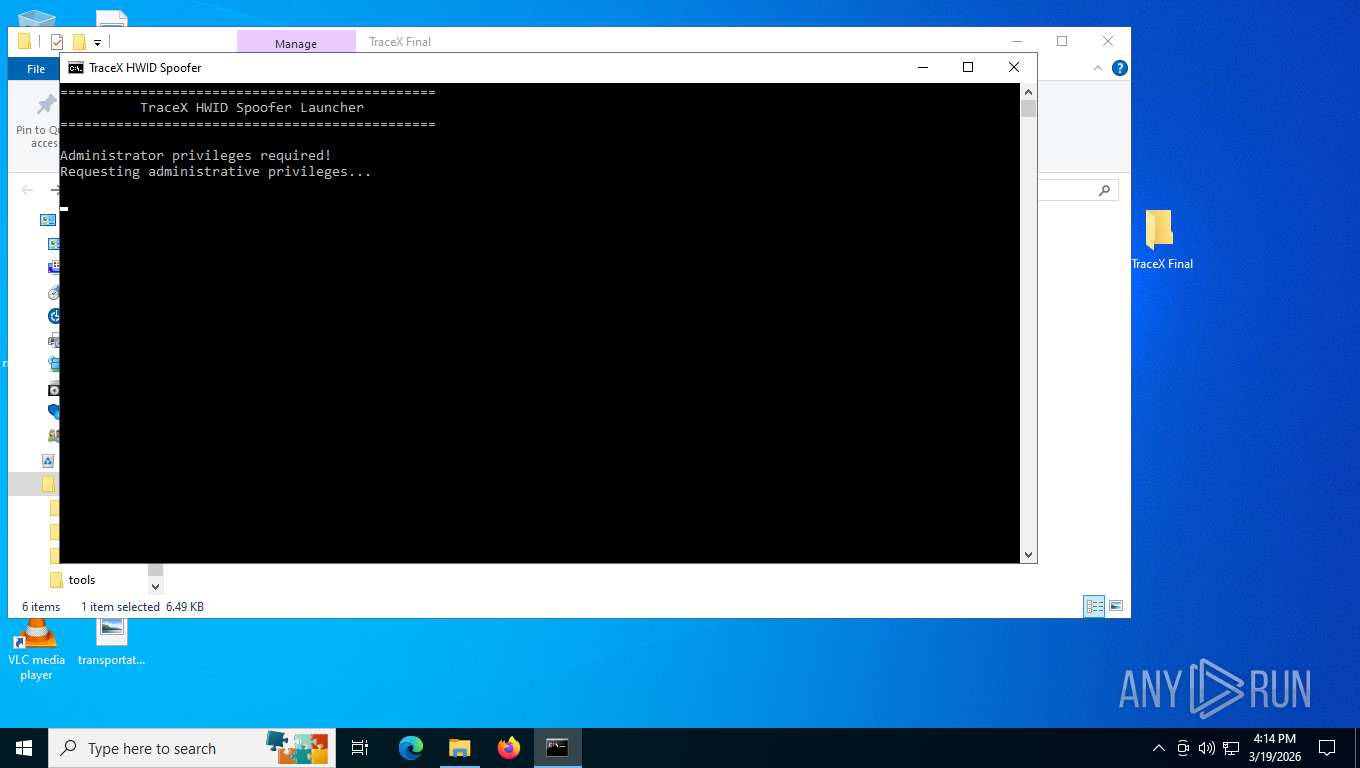
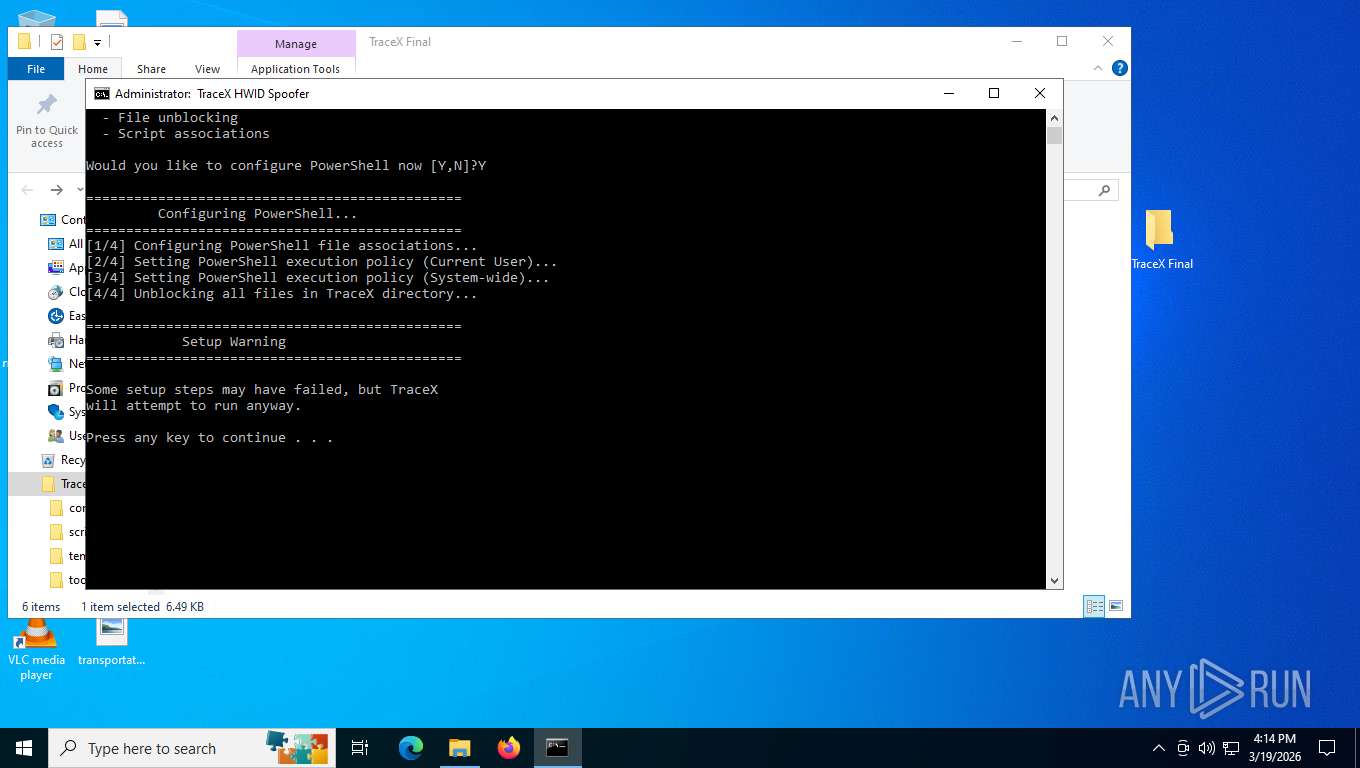
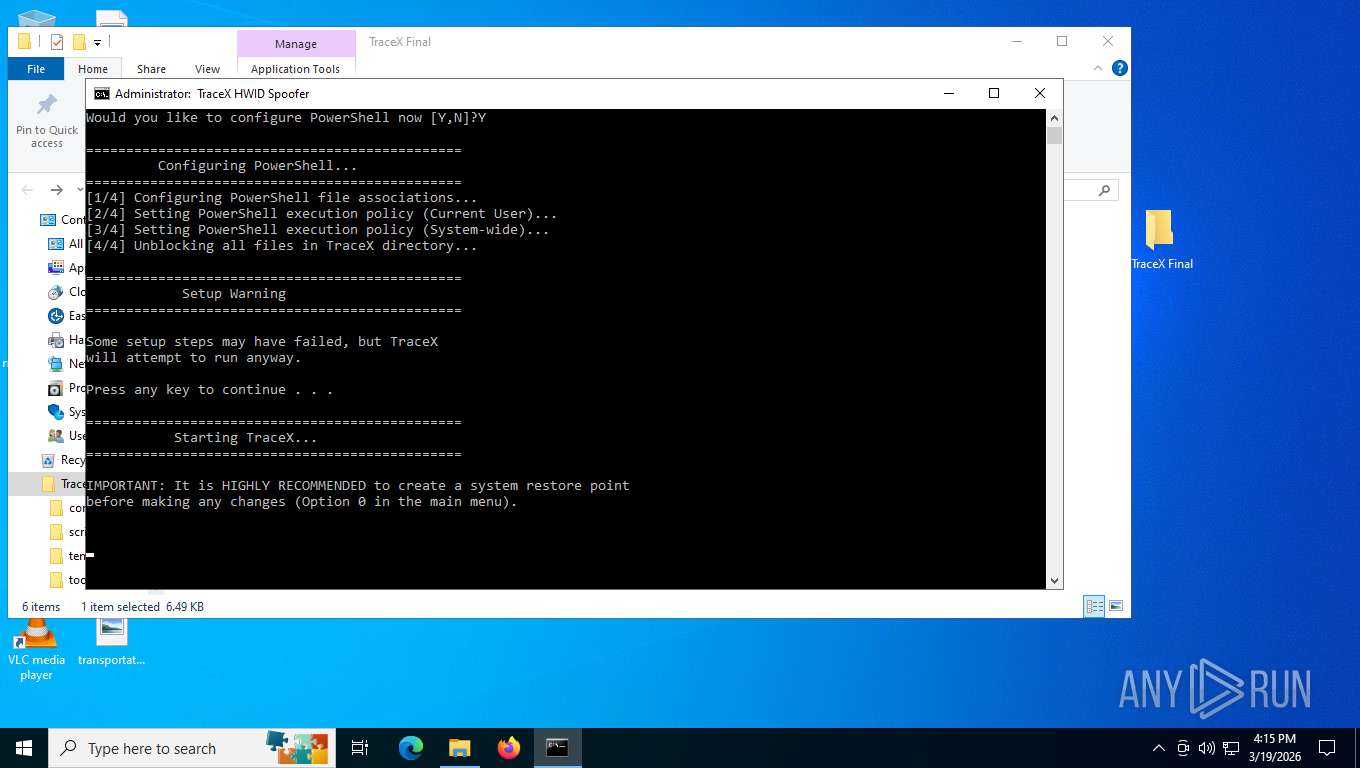
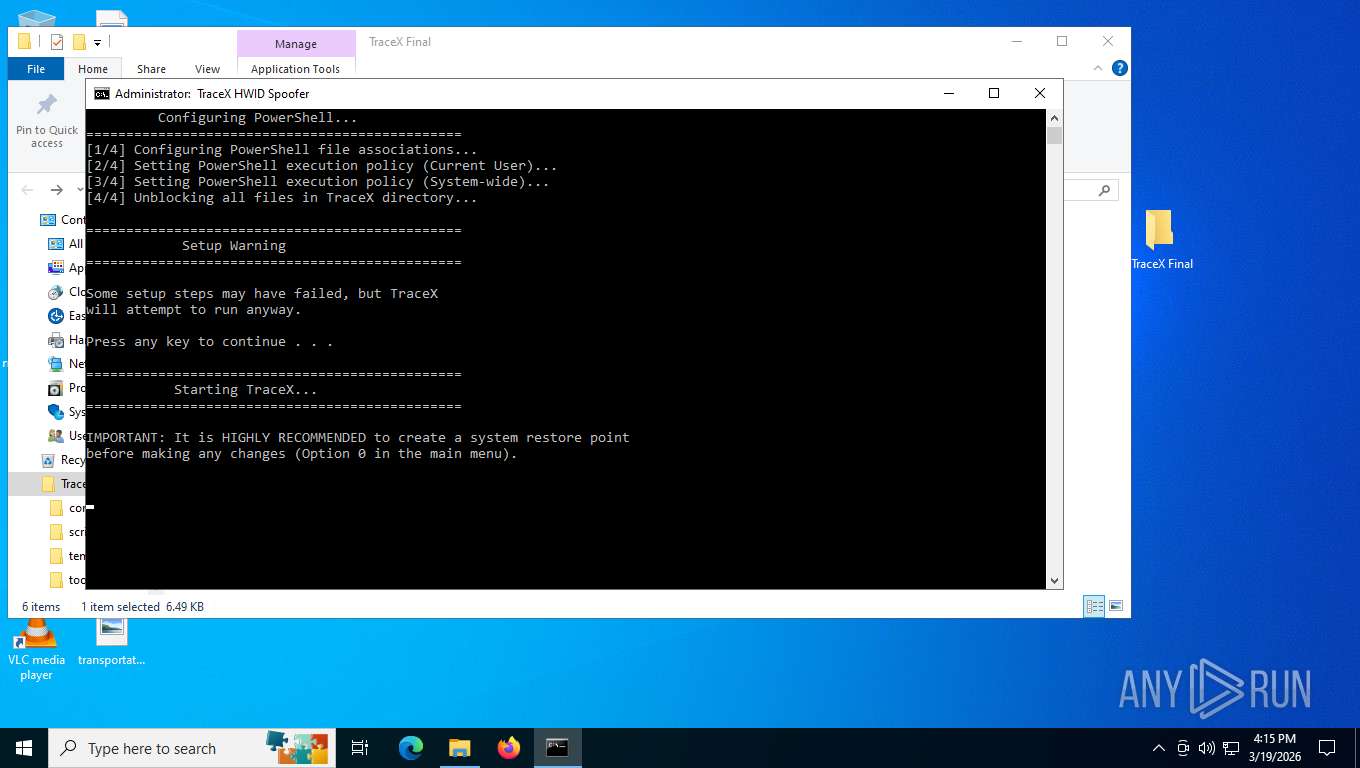
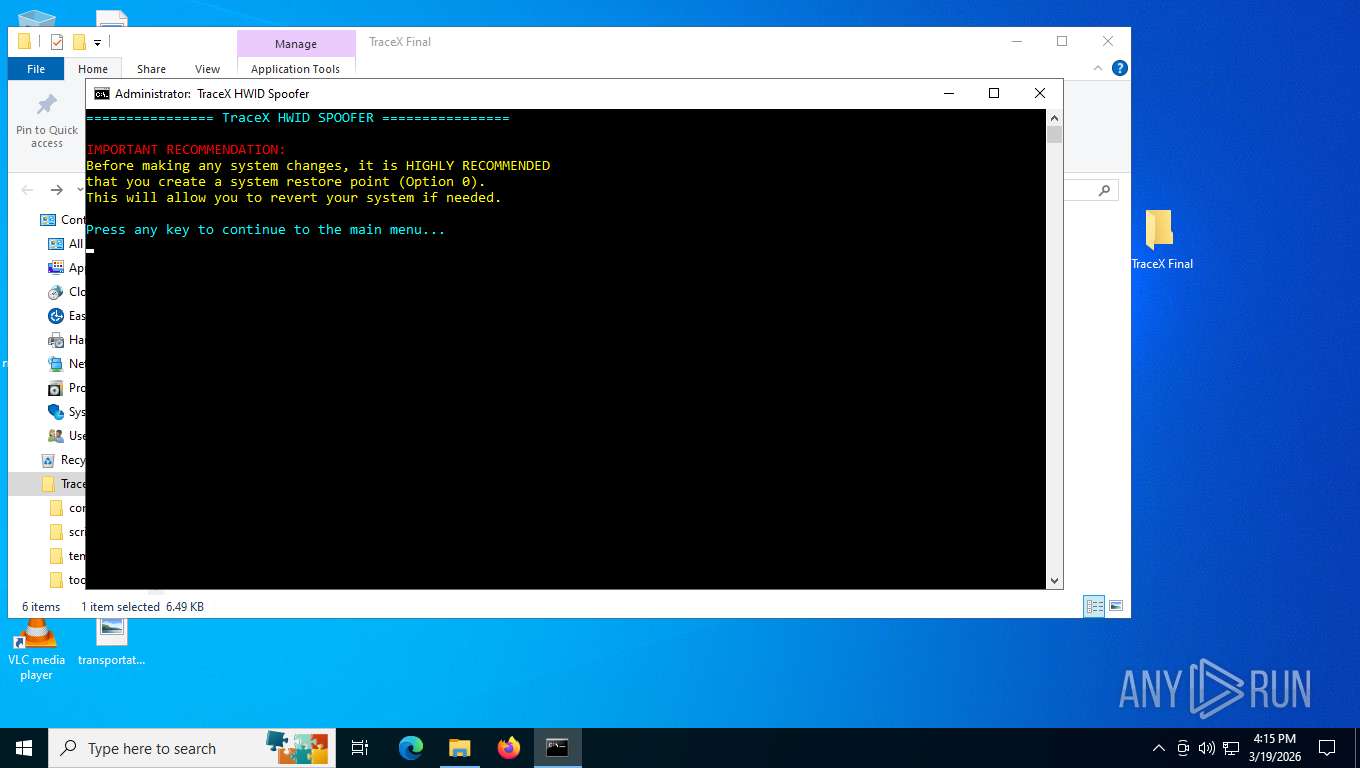
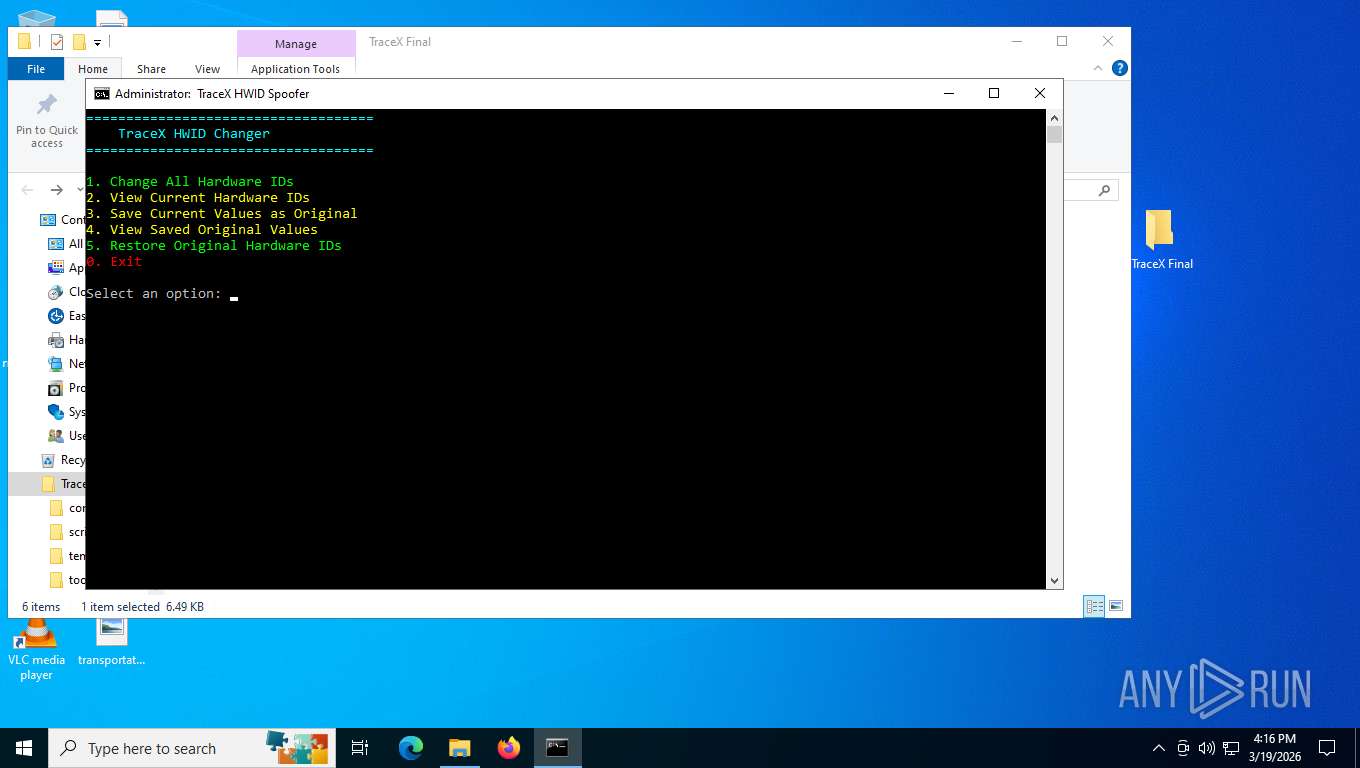
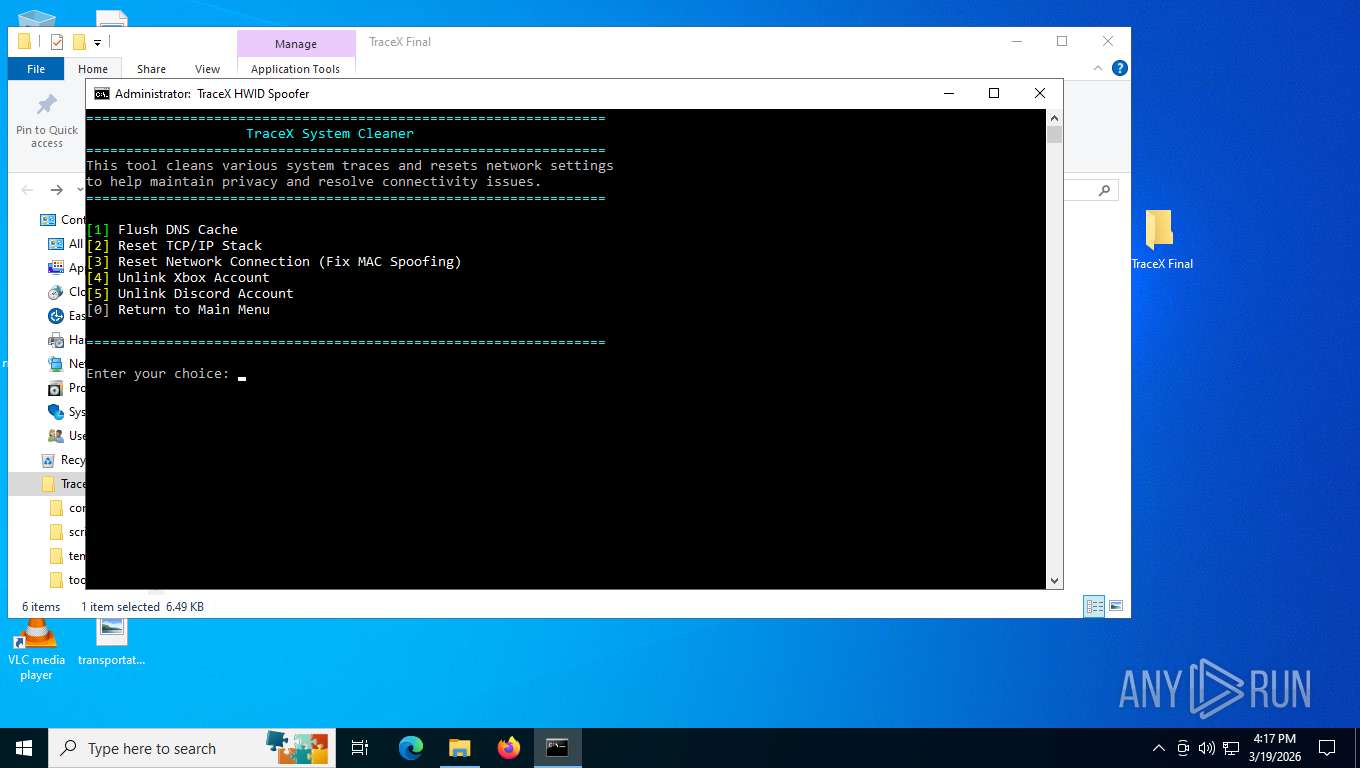
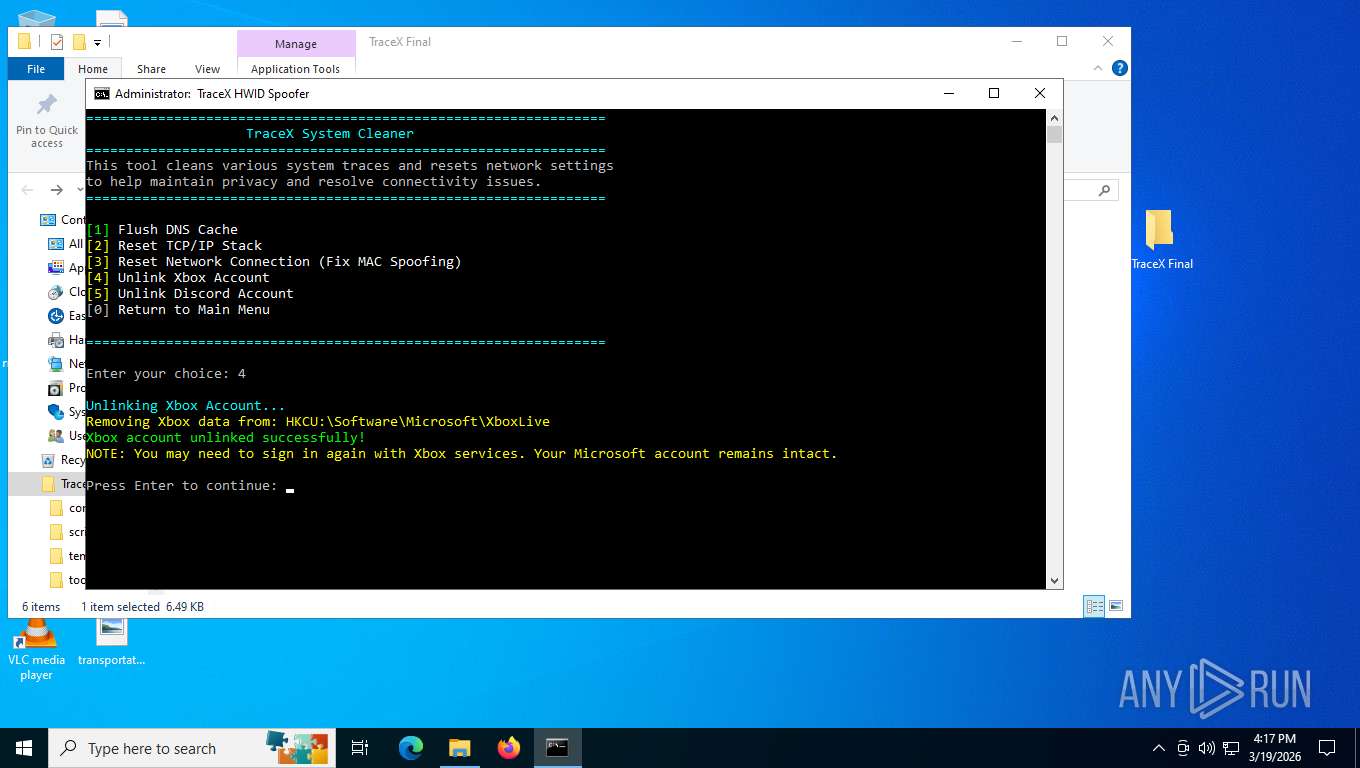
| 1296 | "C:\WINDOWS\System32\cmd.exe" /C "C:\Users\admin\Desktop\TRACEX~1\RUN-TR~1.BAT" | C:\Windows\System32\cmd.exe | wscript.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows Command Processor Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1352 | "C:\Users\admin\Desktop\TraceX Final\tools\AMIDEWINx64.EXE" /SU | C:\Users\admin\Desktop\TraceX Final\tools\AMIDEWINx64.EXE | — | powershell.exe | |||||||||||
User: admin Integrity Level: HIGH Exit code: 227 Modules
| |||||||||||||||
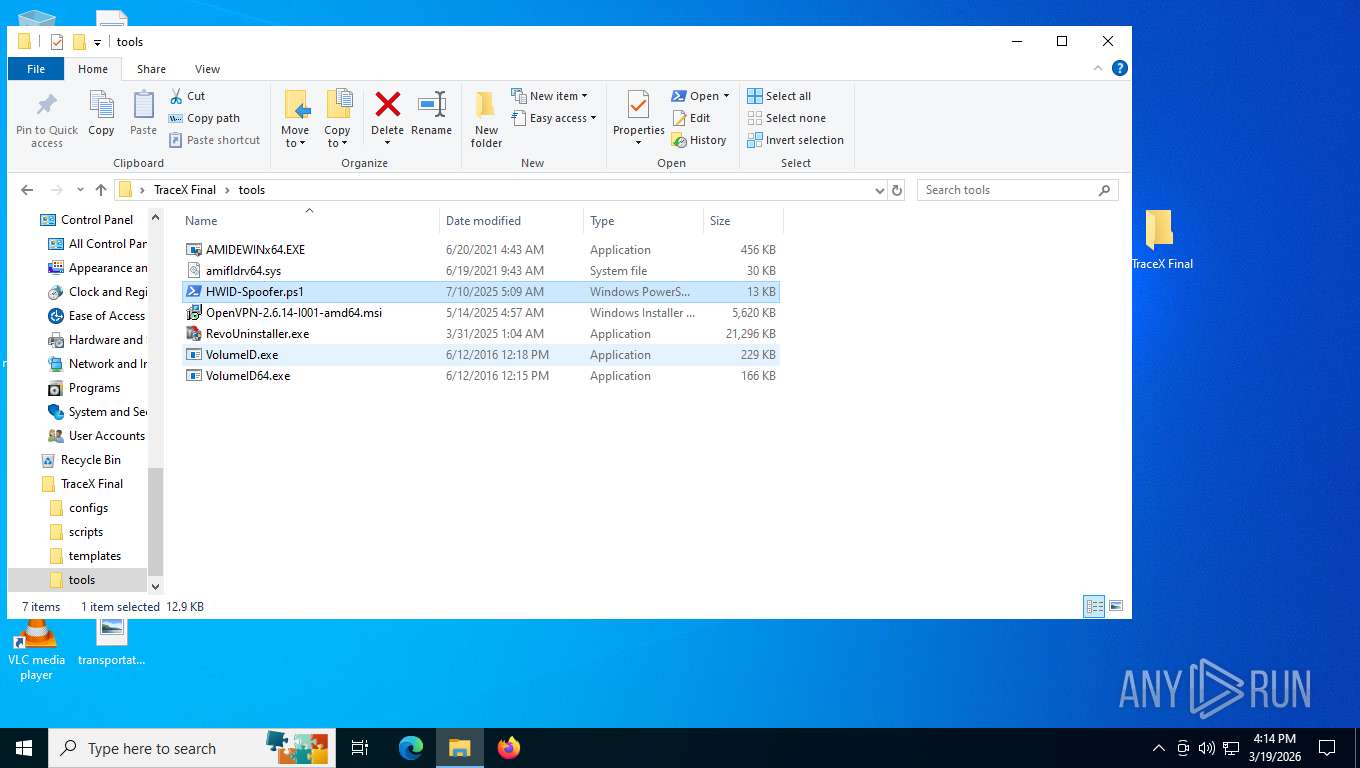
| 1772 | "C:\Users\admin\Desktop\TraceX Final\tools\VolumeID64.exe" -accepteula C: 08C0-1E65 | C:\Users\admin\Desktop\TraceX Final\tools\VolumeID64.exe | — | cmd.exe | |||||||||||
User: admin Company: Sysinternals - www.sysinternals.com Integrity Level: HIGH Description: Set disk volume id Exit code: 0 Version: 2.1 Modules
| |||||||||||||||
| 1776 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
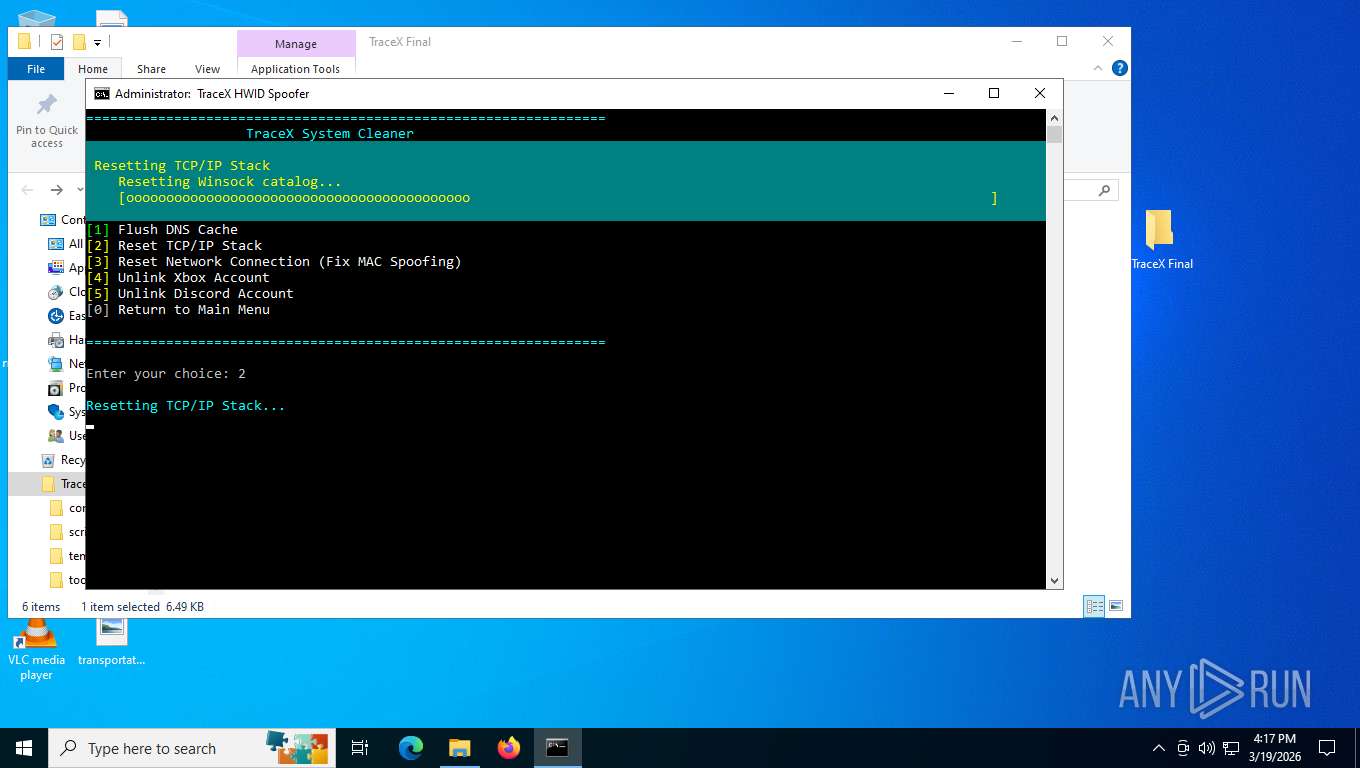
| 2092 | "C:\WINDOWS\system32\netsh.exe" winsock reset | C:\Windows\System32\netsh.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Network Command Shell Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2120 | "C:\Users\admin\Desktop\TraceX Final\tools\AMIDEWINx64.EXE" /CS | C:\Users\admin\Desktop\TraceX Final\tools\AMIDEWINx64.EXE | — | powershell.exe | |||||||||||
User: admin Integrity Level: HIGH Exit code: 227 Modules
| |||||||||||||||
| 2220 | "C:\WINDOWS\System32\WScript.exe" "C:\Users\admin\AppData\Local\Temp\getadmin.vbs" | C:\Windows\System32\wscript.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft ® Windows Based Script Host Exit code: 0 Version: 5.812.10240.16384 Modules
| |||||||||||||||
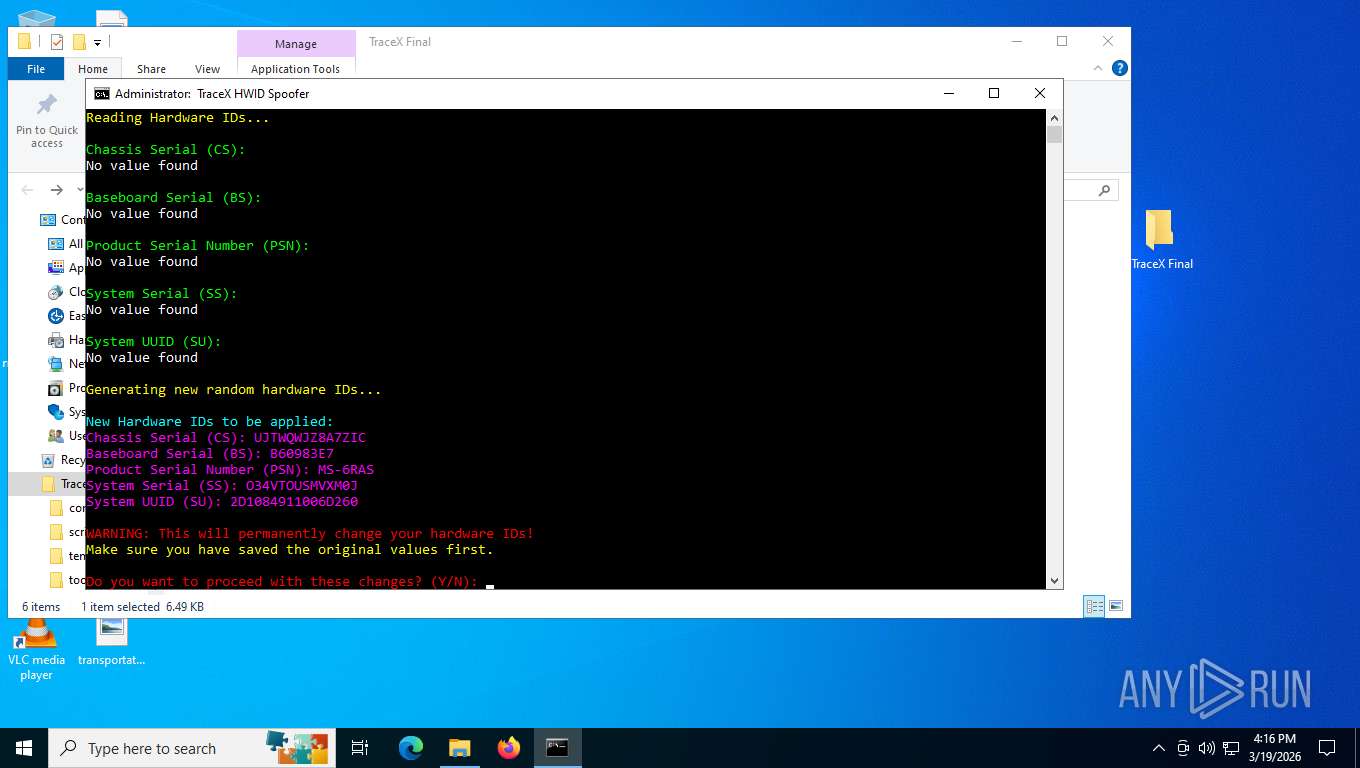
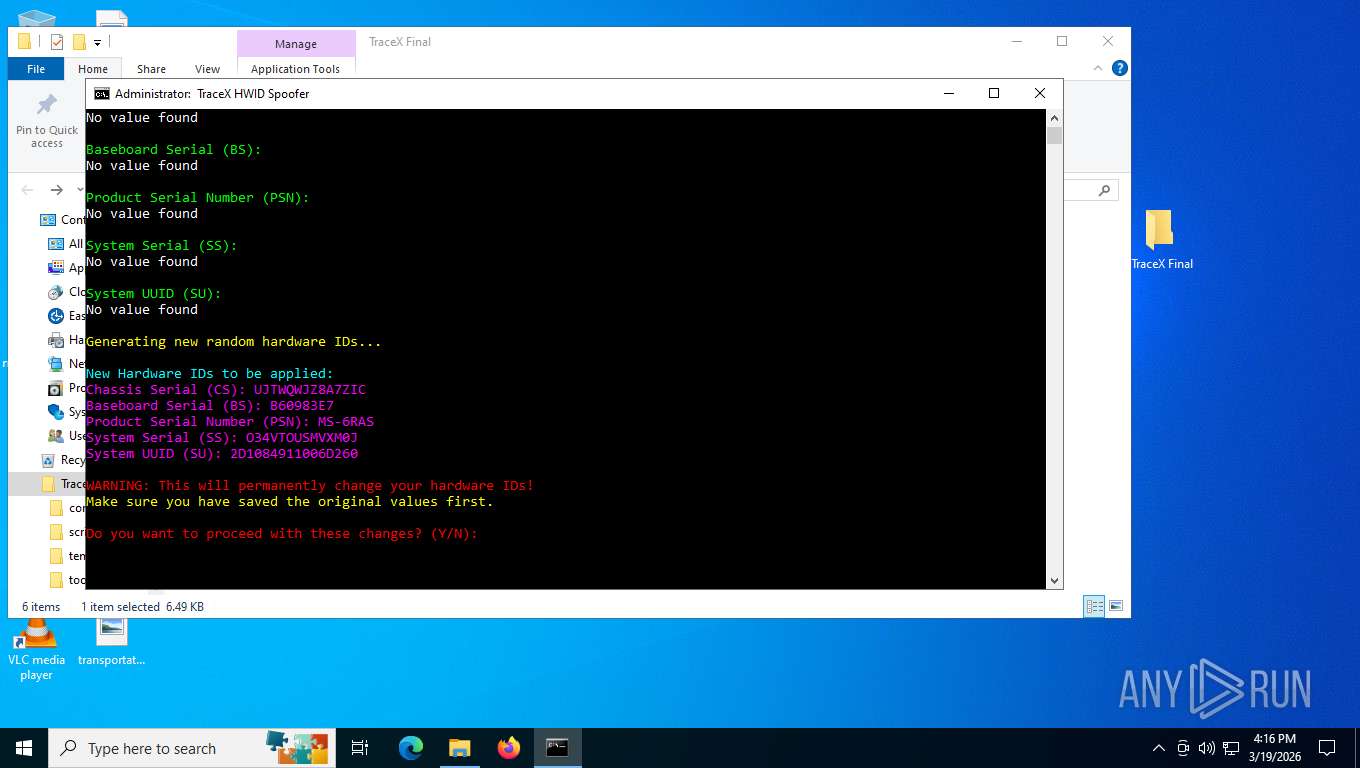
| 2332 | "C:\Users\admin\Desktop\TraceX Final\tools\AMIDEWINx64.EXE" /SU 2D1084911006D260 | C:\Users\admin\Desktop\TraceX Final\tools\AMIDEWINx64.EXE | — | powershell.exe | |||||||||||
User: admin Integrity Level: HIGH Exit code: 227 Modules
| |||||||||||||||
| (PID) Process: | (7776) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtBMP |
Value: | |||
| (PID) Process: | (7776) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\Interface\Themes |
| Operation: | write | Name: | ShellExtIcon |
Value: | |||
| (PID) Process: | (7776) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 3 |
Value: C:\Users\admin\Desktop\chromium_ext.zip | |||
| (PID) Process: | (7776) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 2 |
Value: C:\Users\admin\Desktop\omni_23_10_2024_.zip | |||
| (PID) Process: | (7776) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 1 |
Value: C:\Users\admin\Downloads\chromium_build 1.zip | |||
| (PID) Process: | (7776) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\ArcHistory |
| Operation: | write | Name: | 0 |
Value: C:\Users\admin\Downloads\HWID Spoofer Final.zip | |||
| (PID) Process: | (7776) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | name |
Value: 120 | |||
| (PID) Process: | (7776) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | size |
Value: 80 | |||
| (PID) Process: | (7776) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | type |
Value: 120 | |||
| (PID) Process: | (7776) WinRAR.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\WinRAR\FileList\FileColumnWidths |
| Operation: | write | Name: | mtime |
Value: 100 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 7776 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa7776.33767\TraceX Final\tools\OpenVPN-2.6.14-I001-amd64.msi | — | |
MD5:— | SHA256:— | |||
| 7776 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa7776.33767\TraceX Final\scripts\change_disk_ids.ps1 | text | |
MD5:2E9153EDC202D577555609C1D85C25B5 | SHA256:1F8D5F2B9F325C5FF76F2DEE89B58E87A14A8A63099FAADF67DC8C4E9C79B4F5 | |||
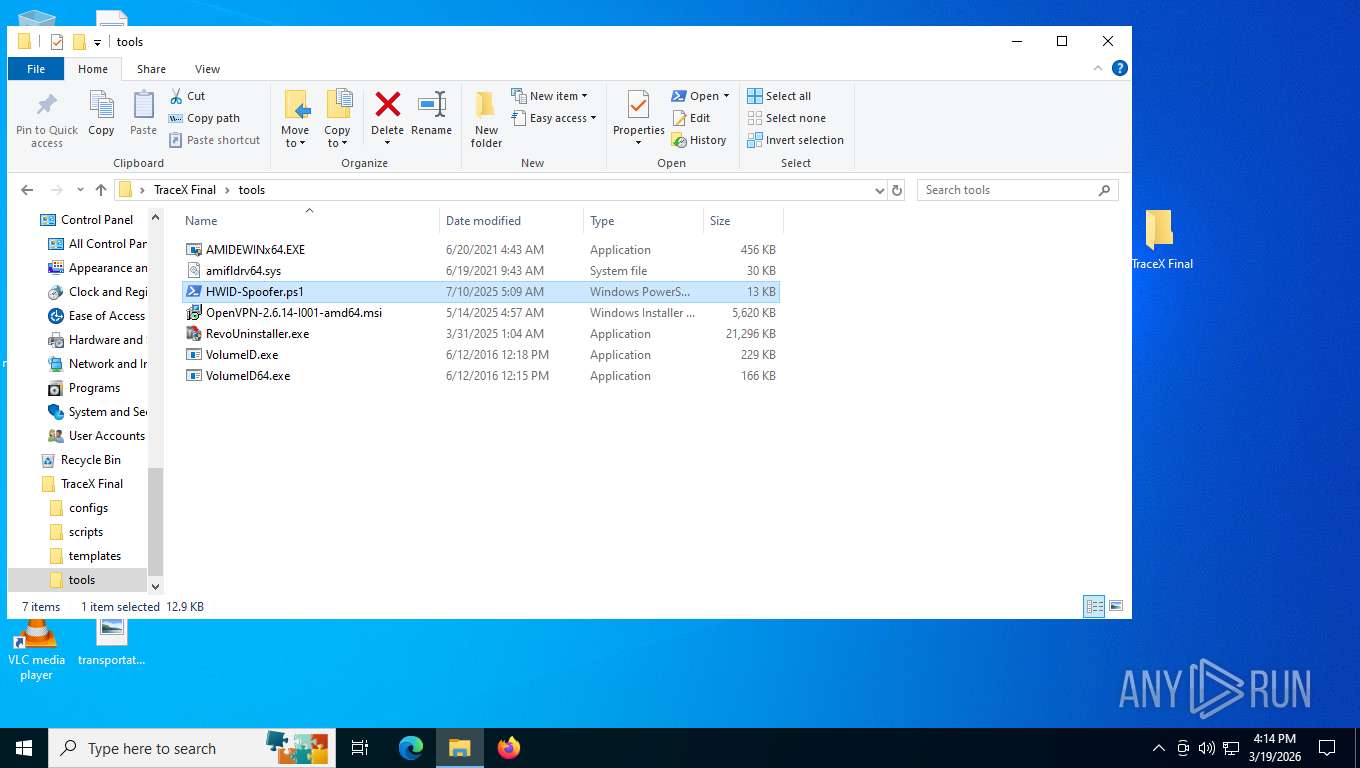
| 7776 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa7776.33767\TraceX Final\scripts\change_hardware_ids.ps1 | text | |
MD5:8933162333B954F8B77CDC3899B8B9E6 | SHA256:45ACB80D0E7018581549DD2151C9A5E7FB790010ADA6CC1BF68A1BDE2C6874E4 | |||
| 7776 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa7776.33767\TraceX Final\scripts\create_restore_point.ps1 | text | |
MD5:FF5F49AC8F6047E9D084035065841C06 | SHA256:6C03EAF50C6E371BD73C802DAC178F90071BA4061CF05106CFD94A6017B67B3A | |||
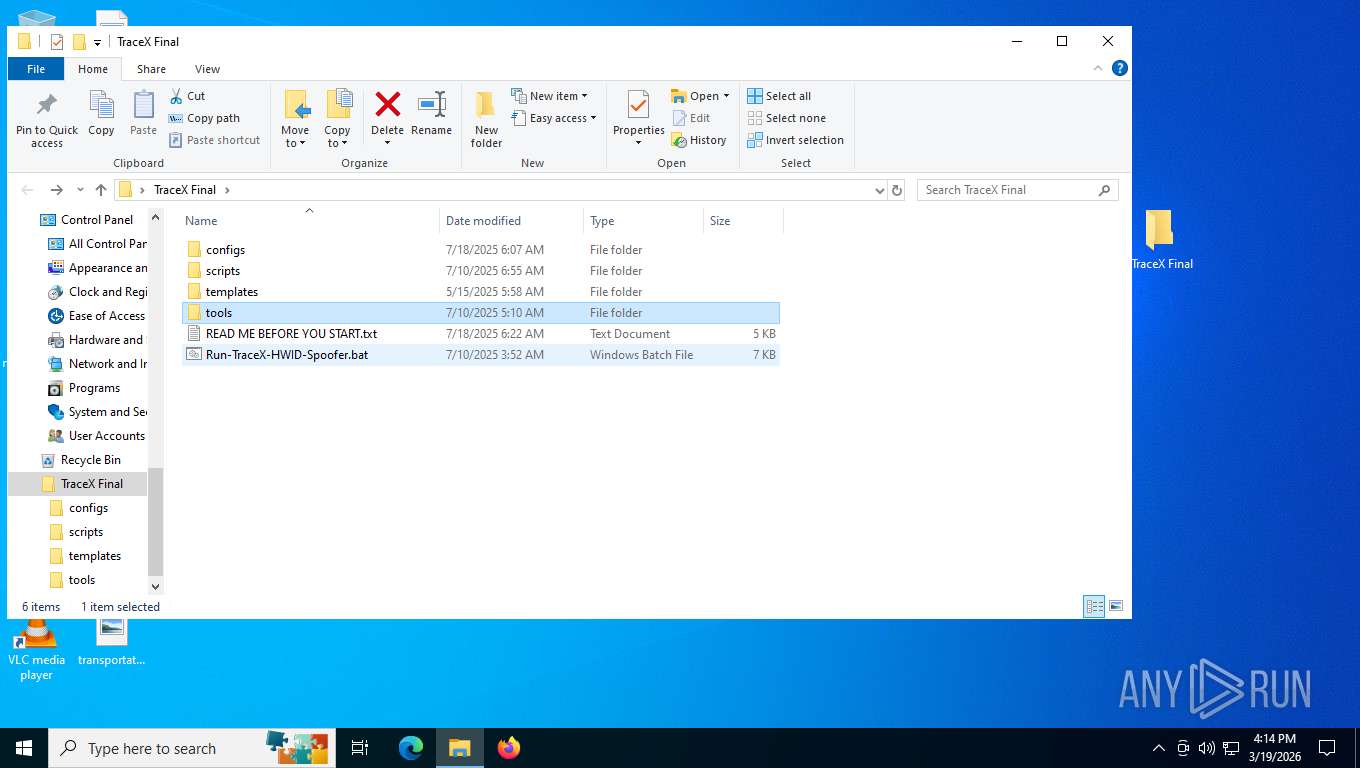
| 7776 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa7776.33767\TraceX Final\Run-TraceX-HWID-Spoofer.bat | text | |
MD5:4F98523504C362EF51A4C82768E8B51A | SHA256:37AF4C4519FE8FE3331D56E74FF2BE57C09A46041B32C5A3233ACC243B456945 | |||
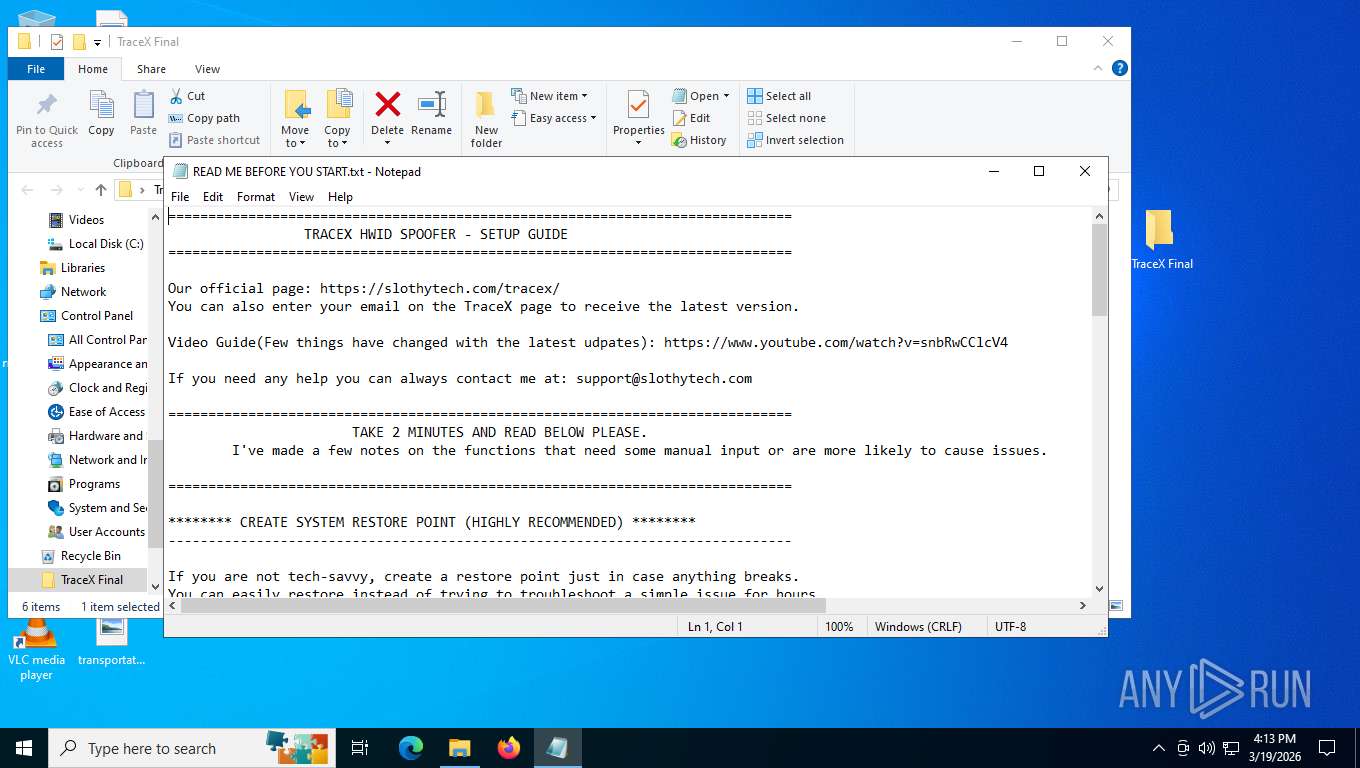
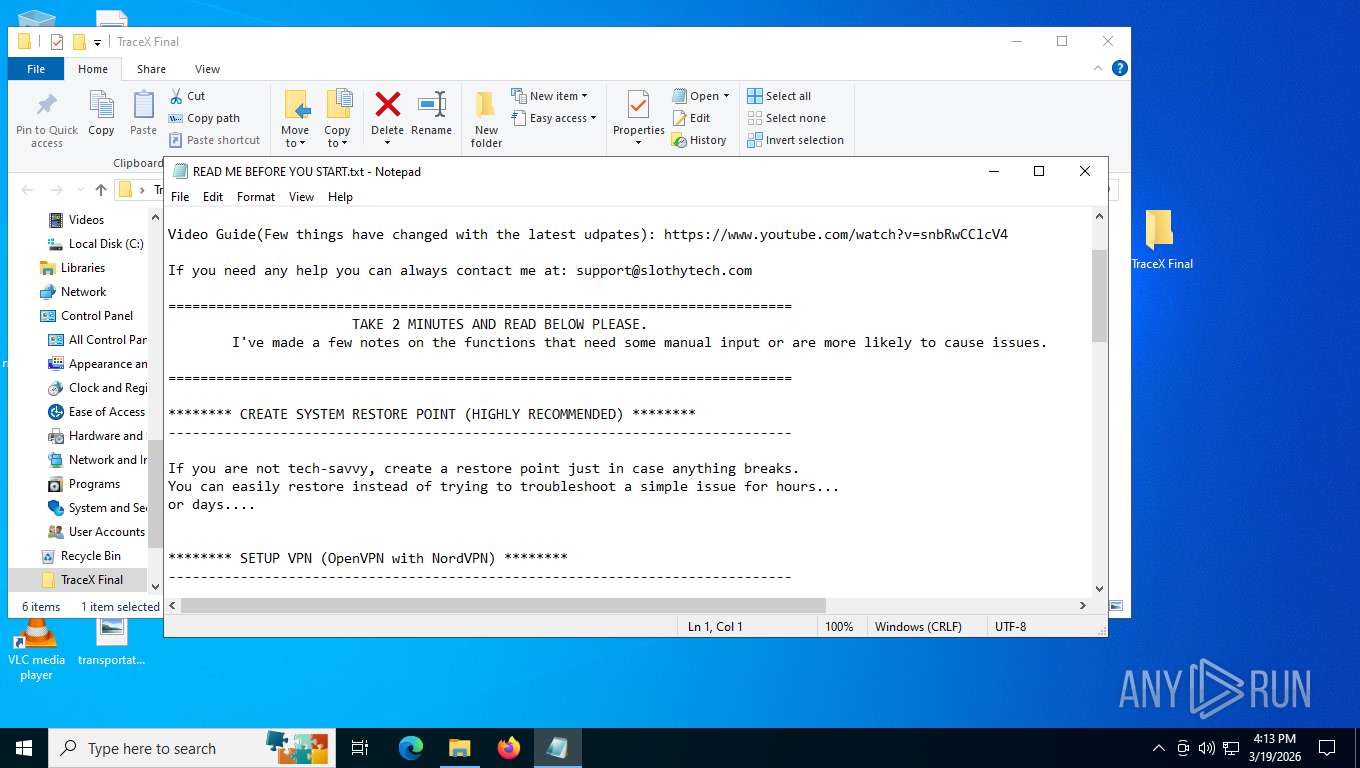
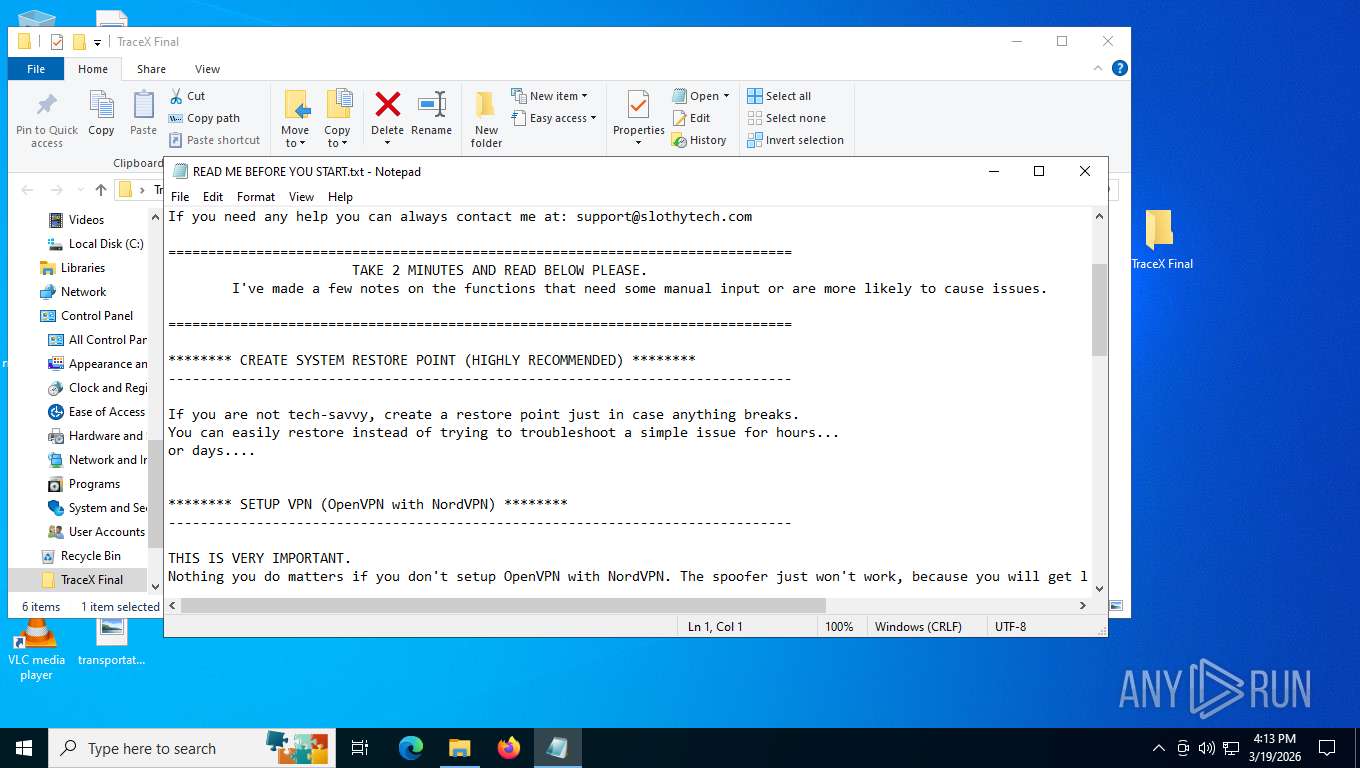
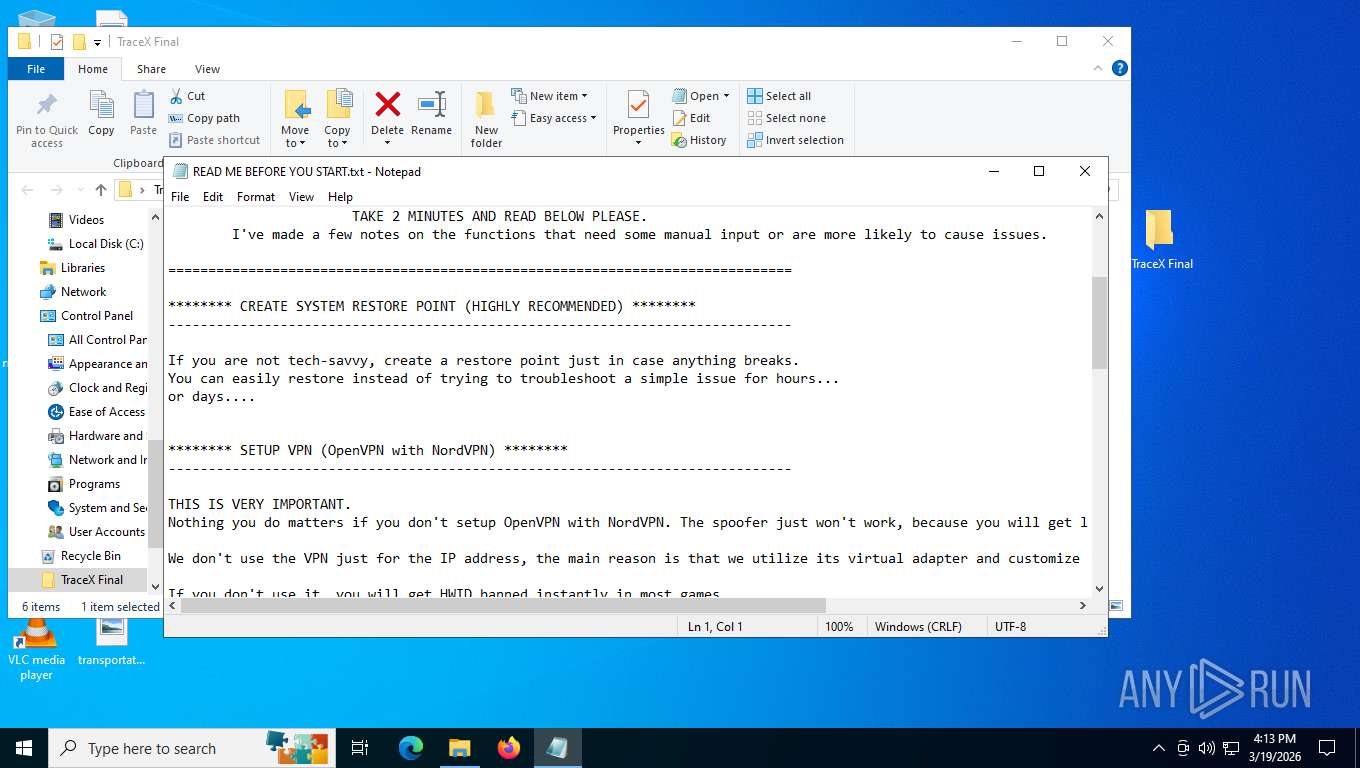
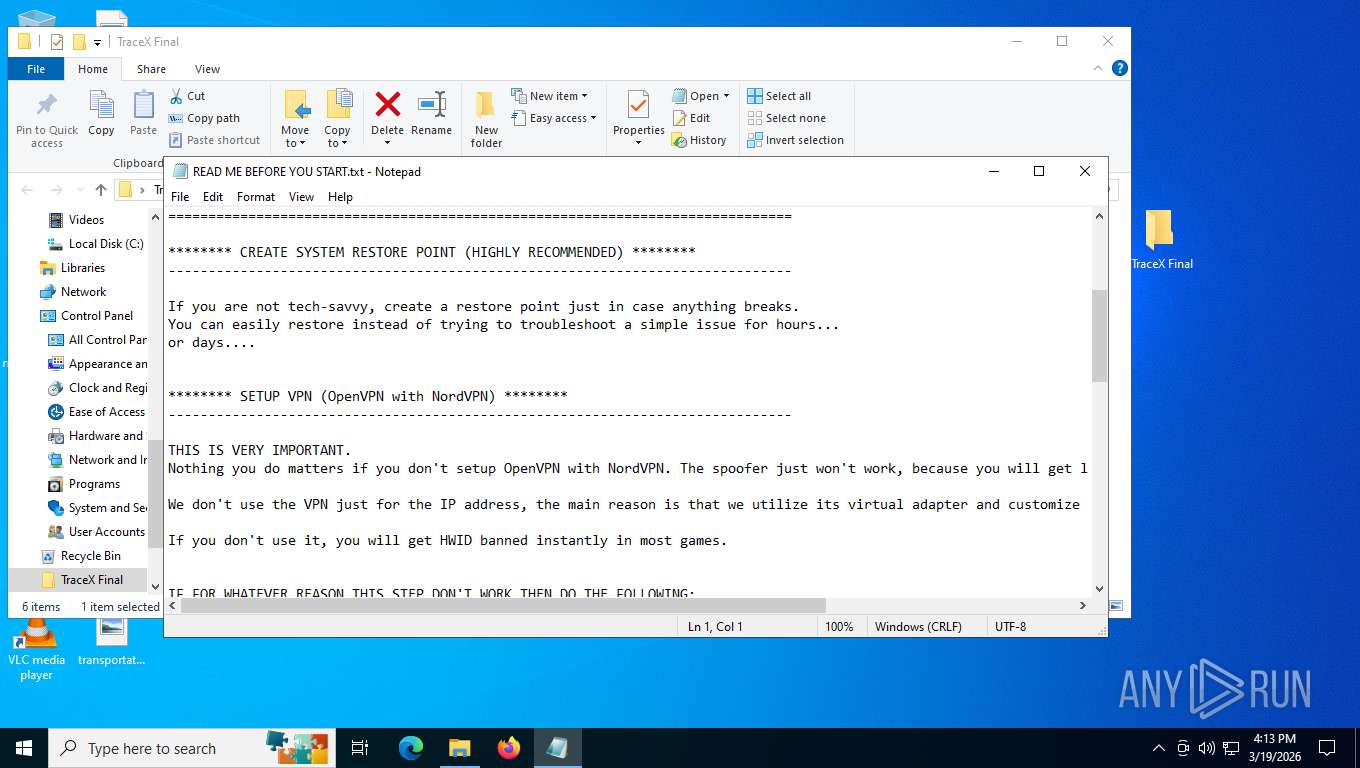
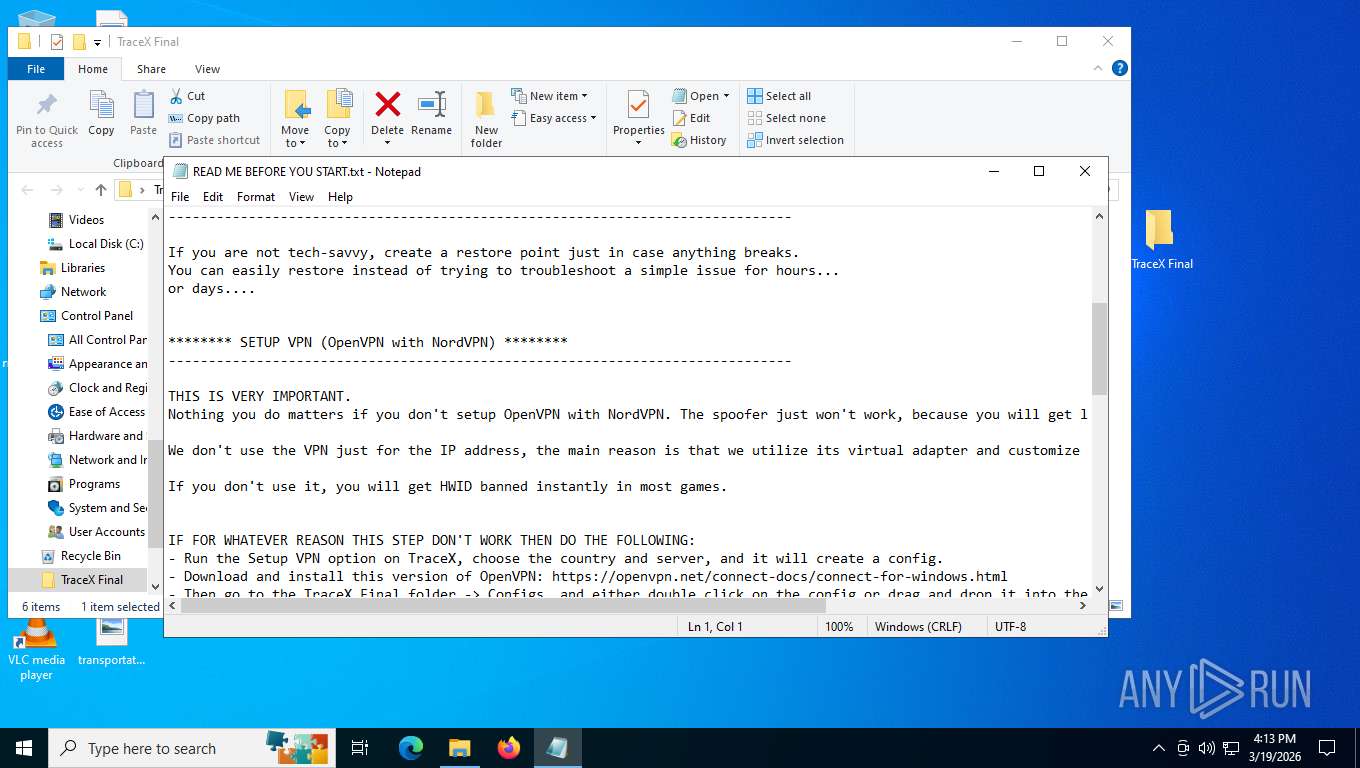
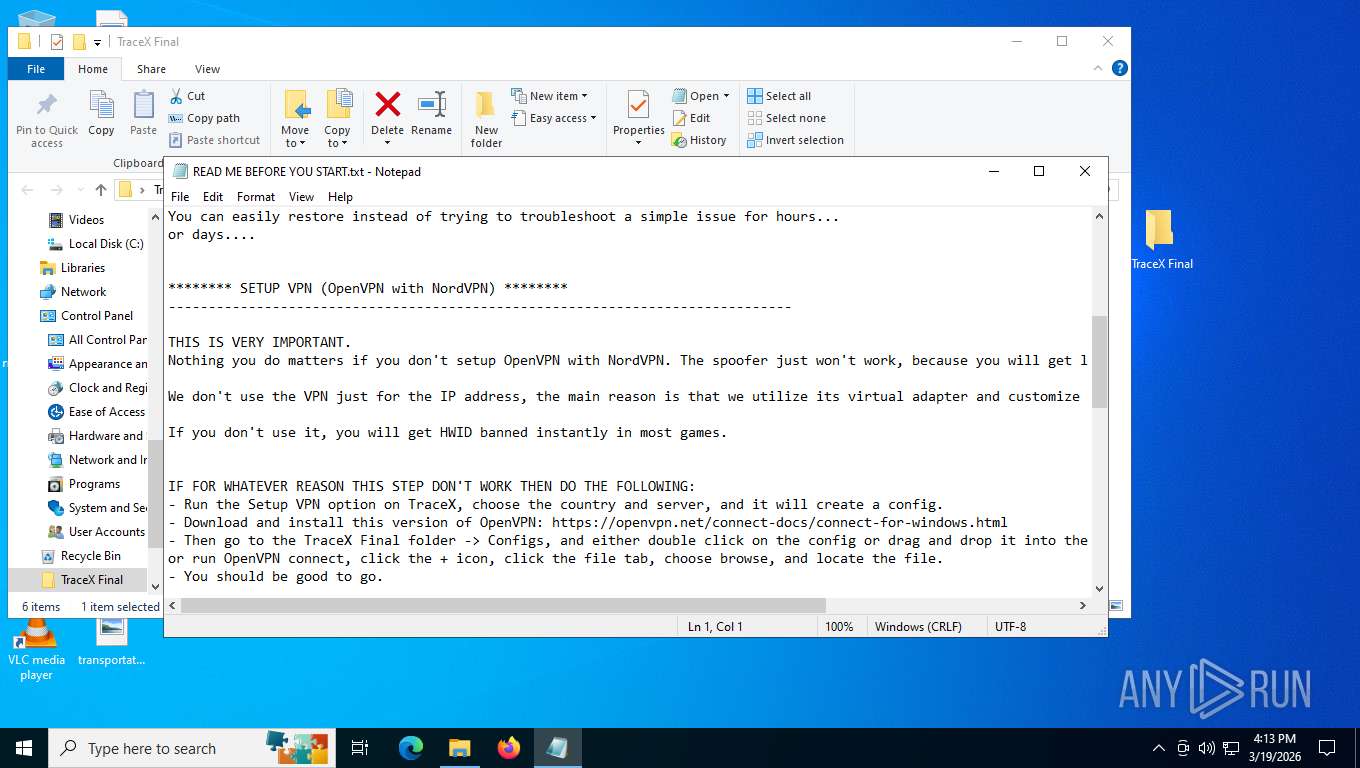
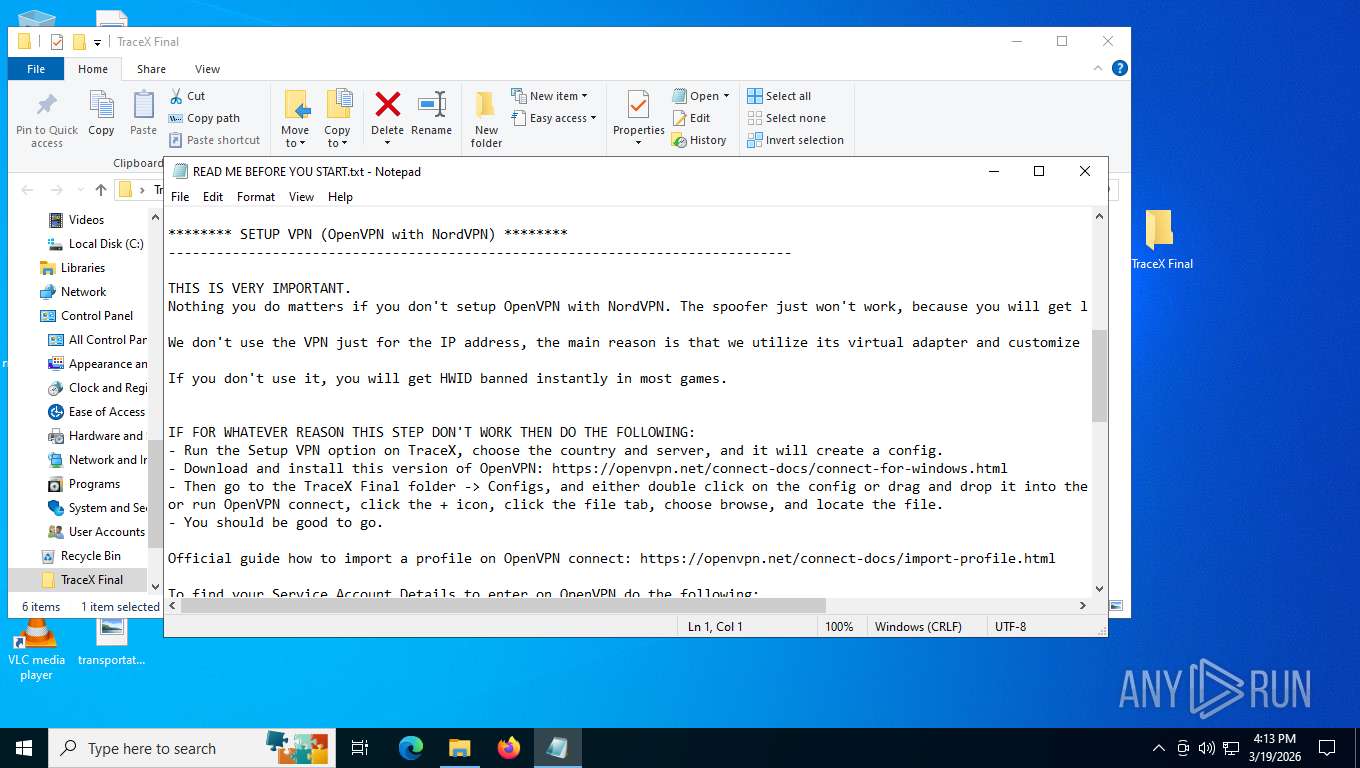
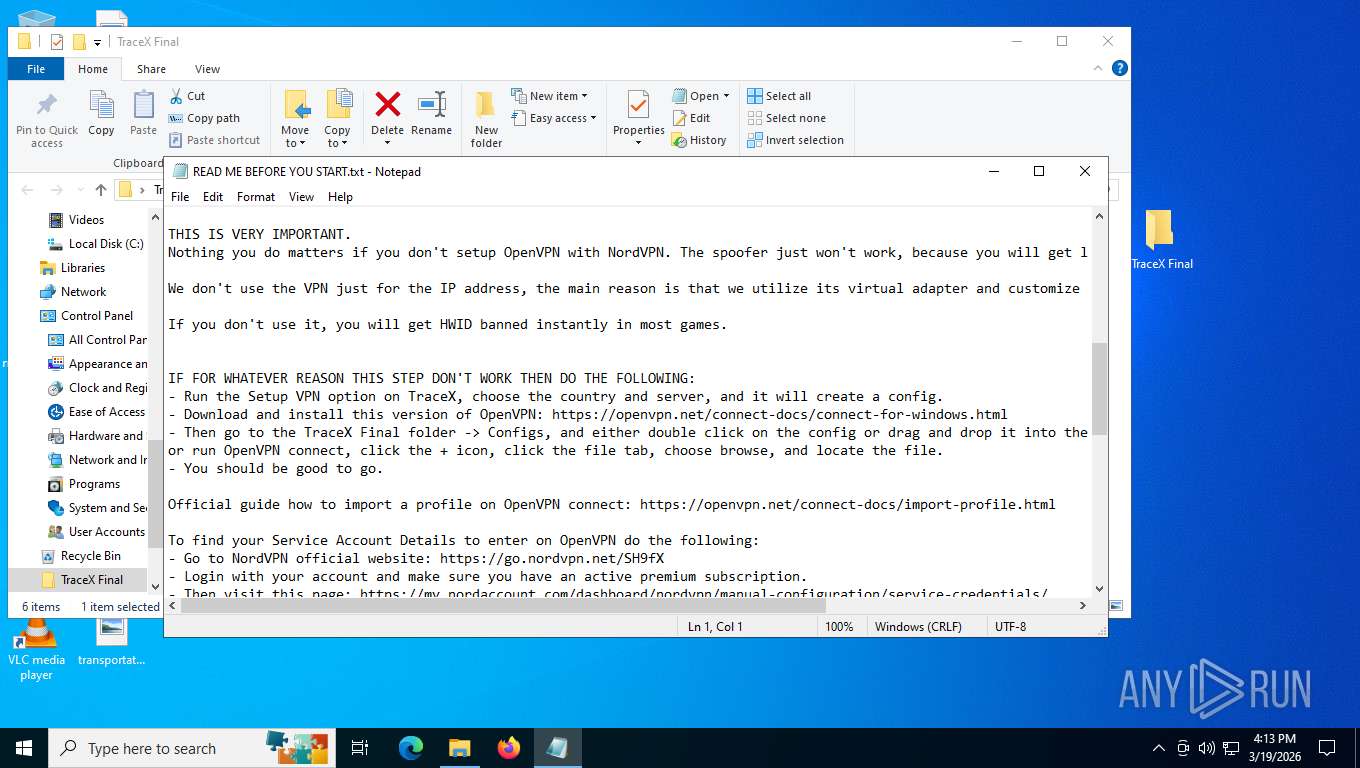
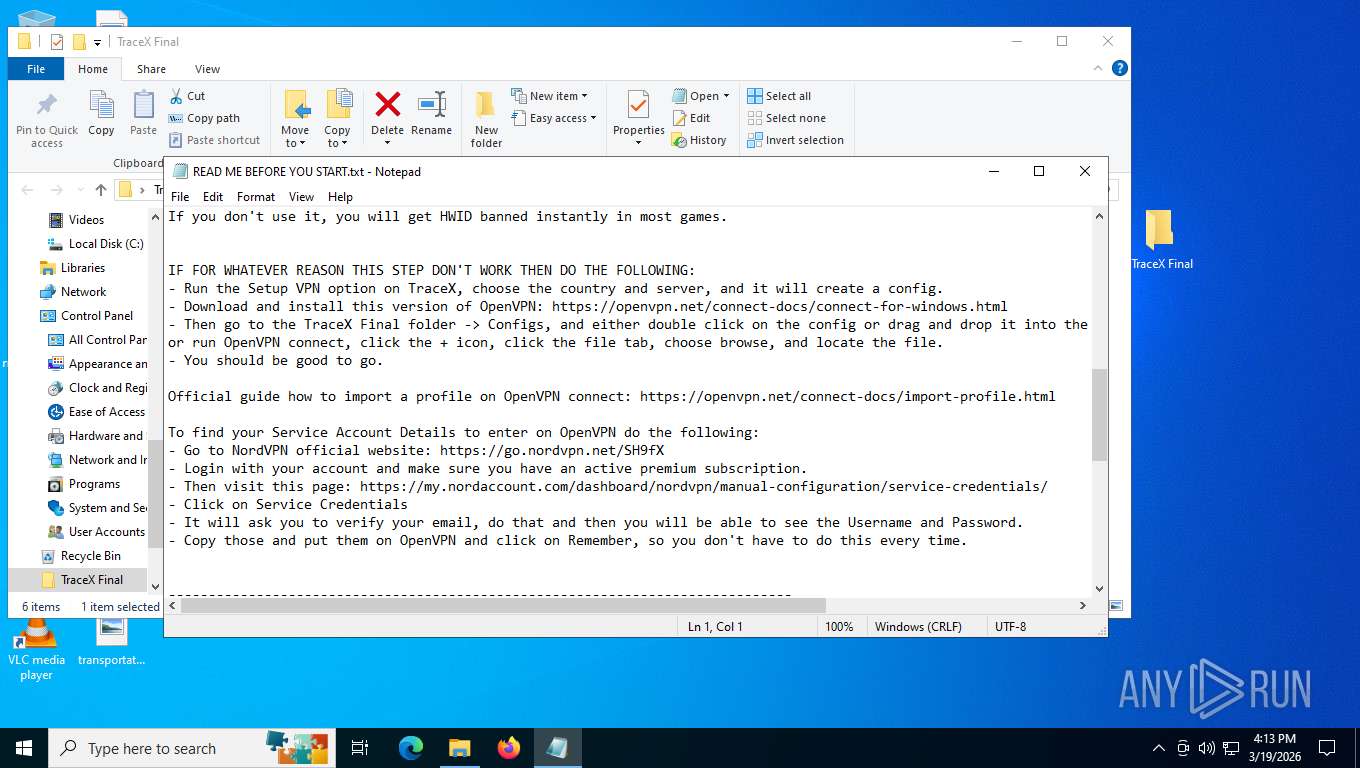
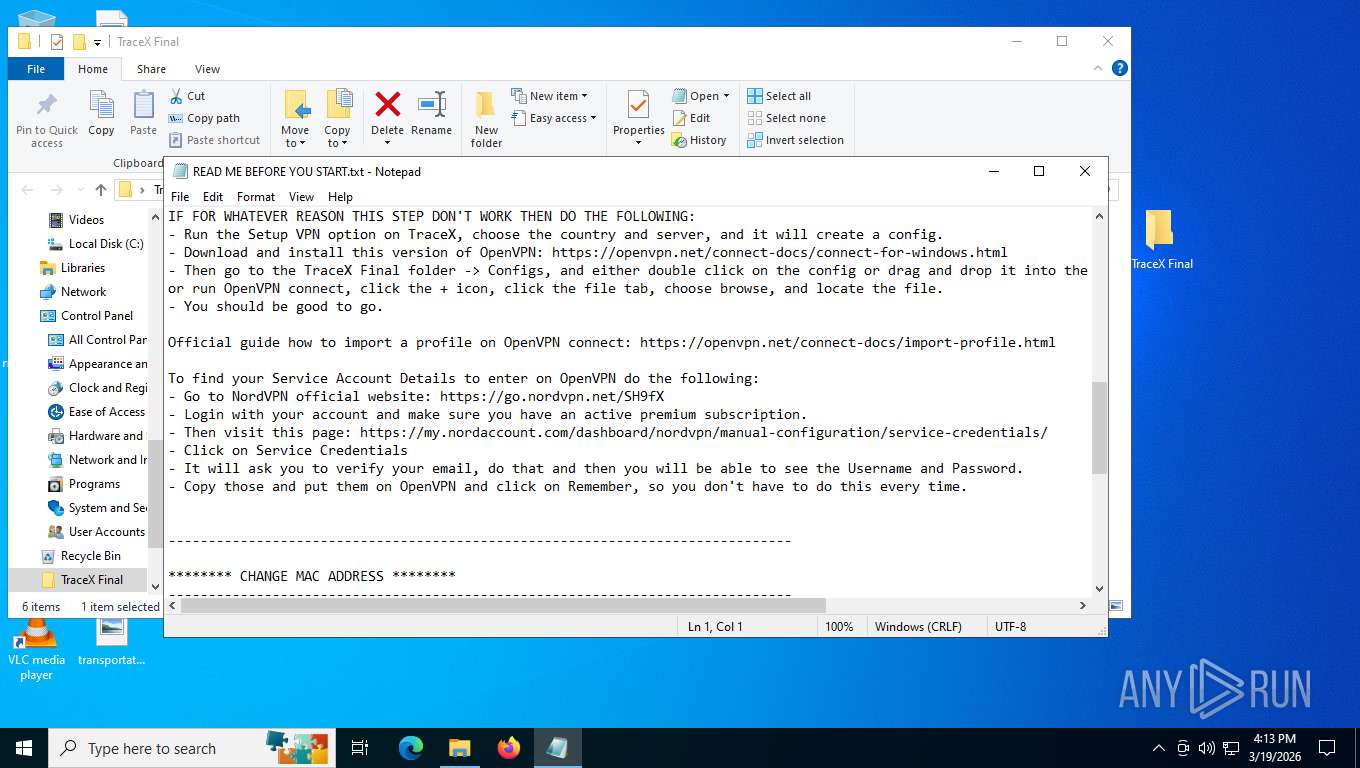
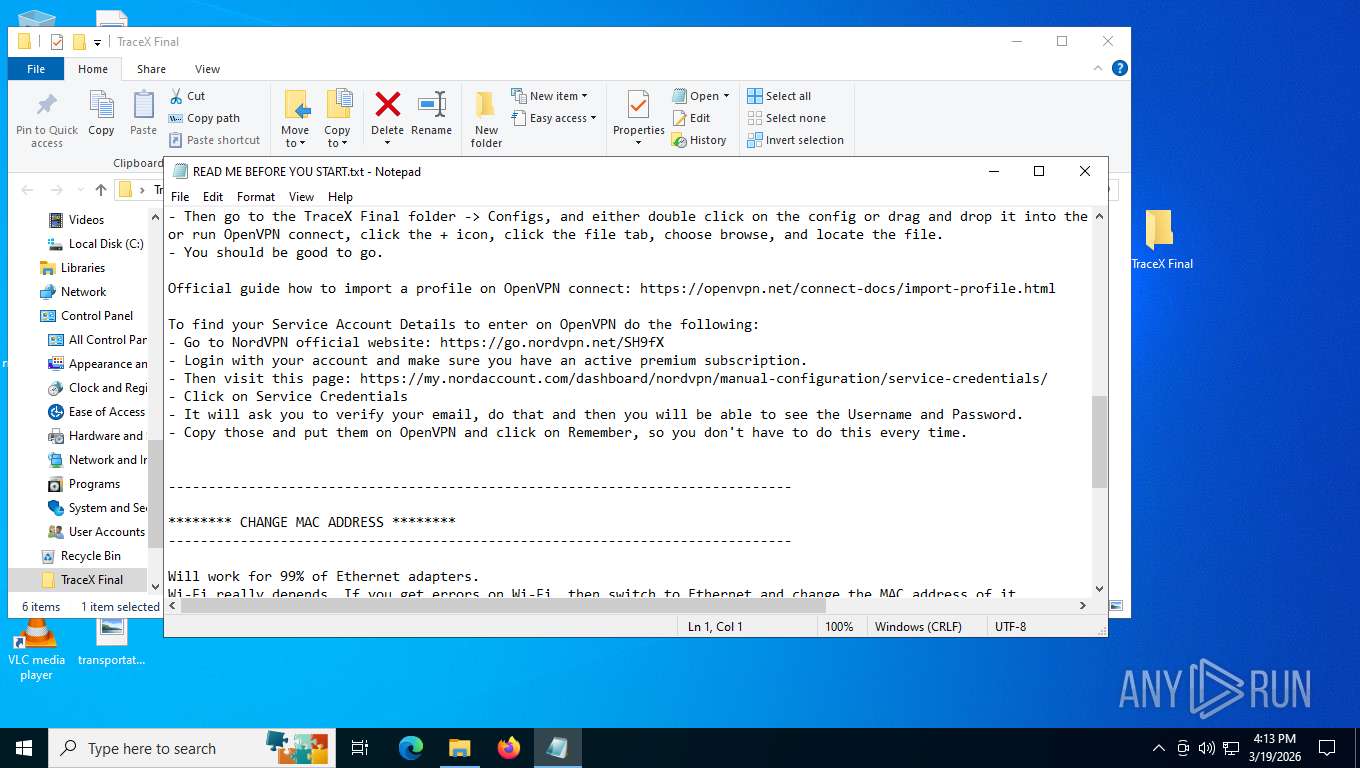
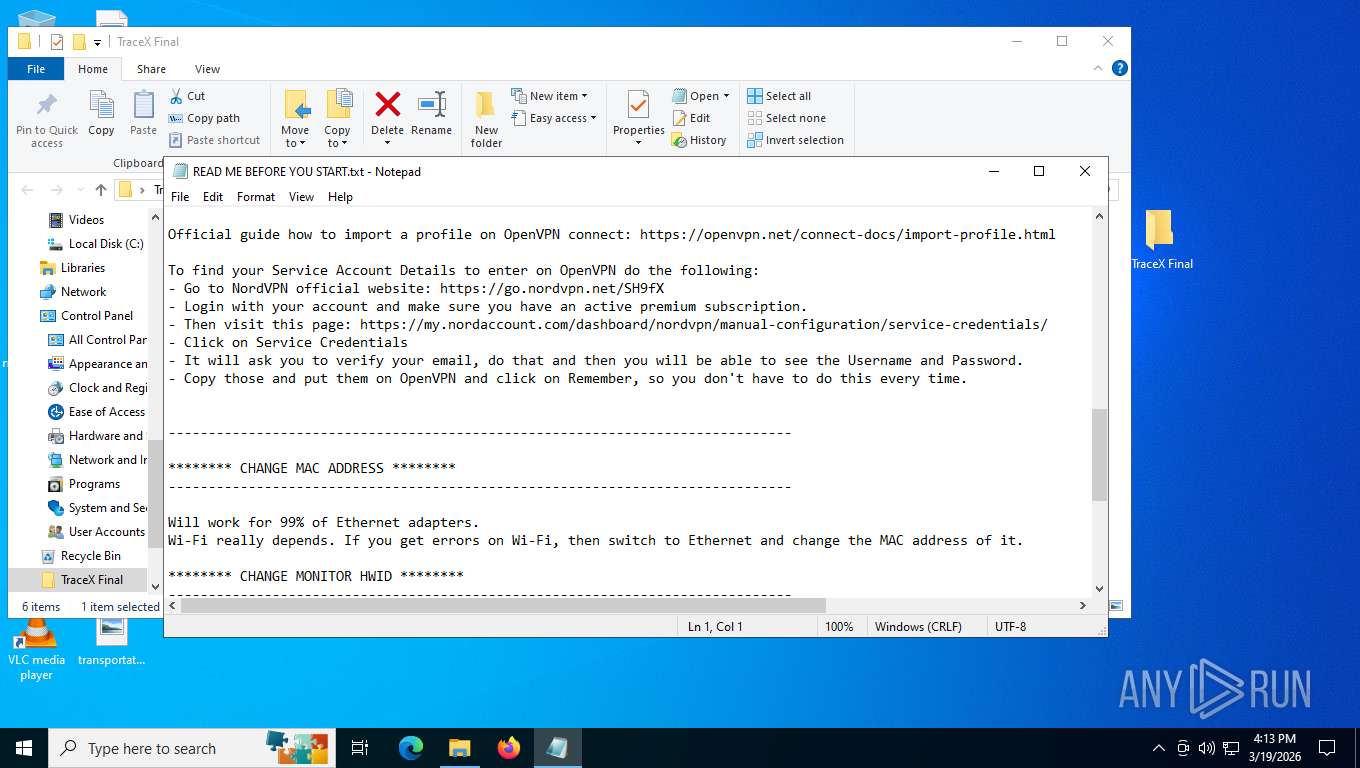
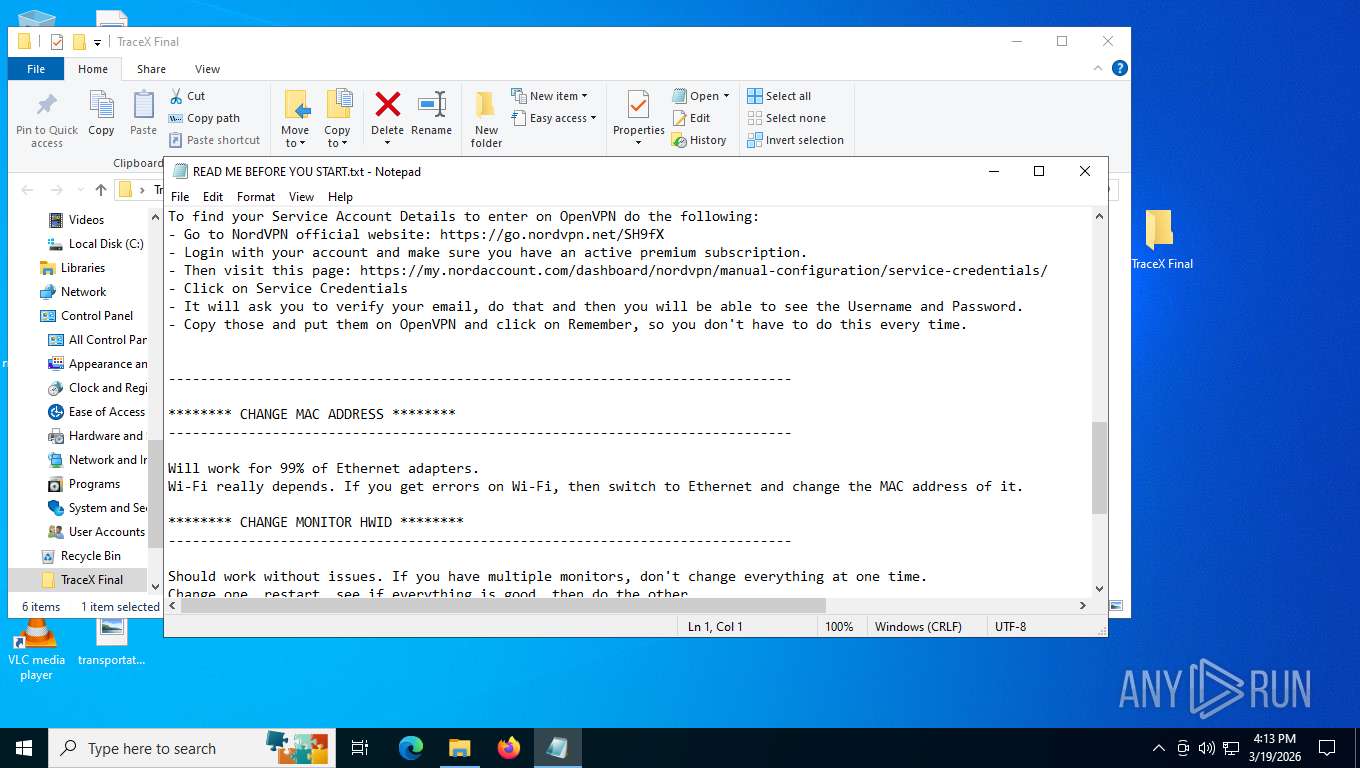
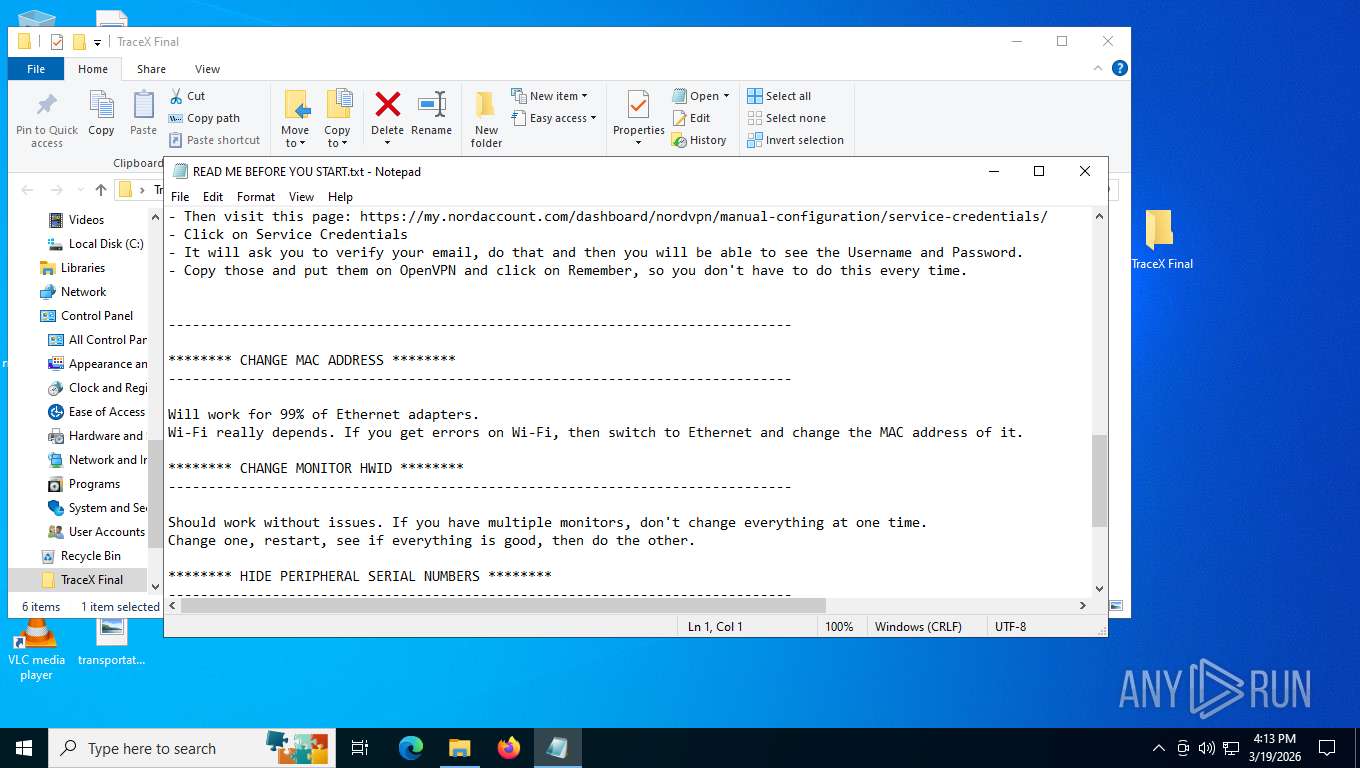
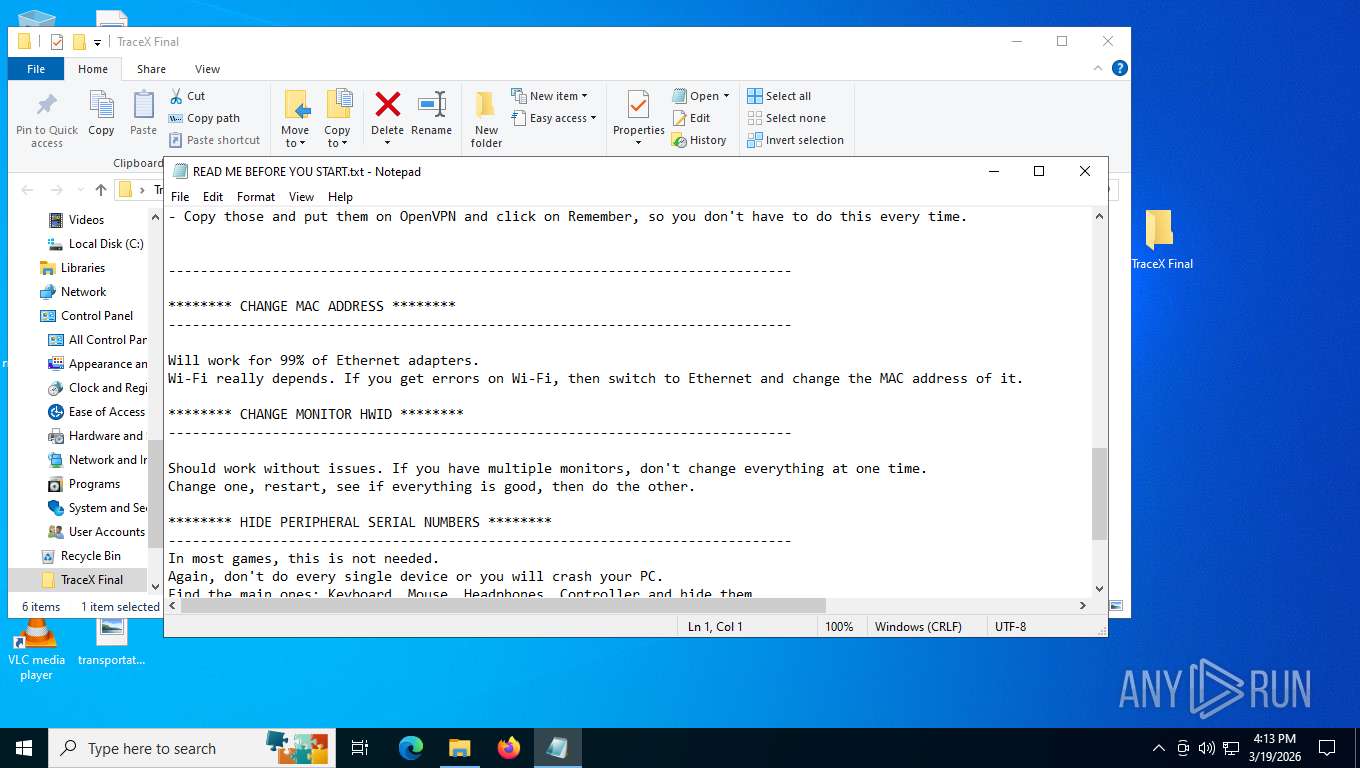
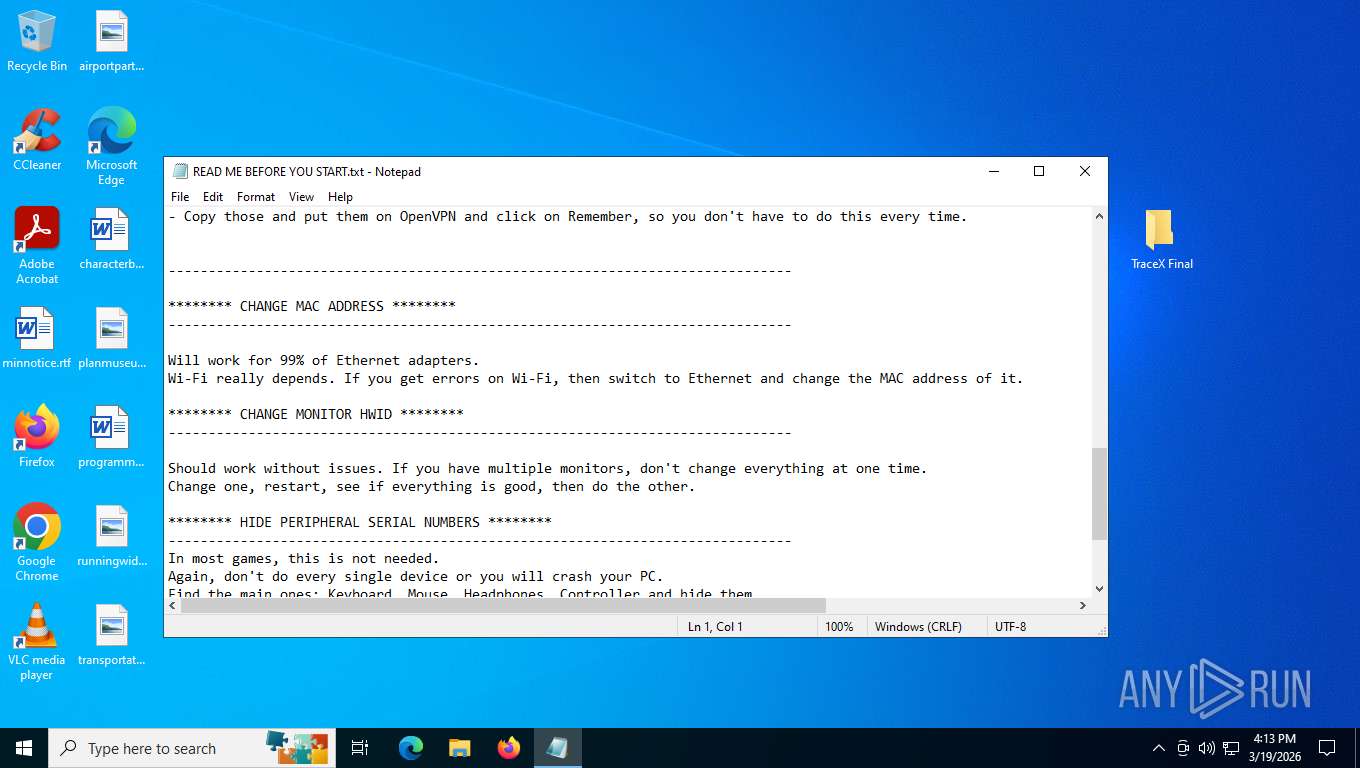
| 7776 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa7776.33767\TraceX Final\READ ME BEFORE YOU START.txt | text | |
MD5:BCB6E28D5890E32DC0FD8B647CD85F78 | SHA256:D8866F892B595753A400A63AD157715C3ABBFA11BD05A2DE09C1F2DA1FA3BA8A | |||
| 7776 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa7776.33767\TraceX Final\scripts\change_mac_address.ps1 | text | |
MD5:7C30E9DBC601CE74F051783907893CE7 | SHA256:ED8DECB95BCA85A67A7B561C13BD620AEA4435F6EB0F7281ECB9C978C659ADC4 | |||
| 7776 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa7776.33767\TraceX Final\scripts\TraceX-Helpers.ps1 | text | |
MD5:373620513B4D0F6F687841413CE2321D | SHA256:06CC3E5CD3FAFC24DA12DB08934CB700FCEB5EA61B448B94F0AAF2E656C0A125 | |||
| 7776 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa7776.33767\TraceX Final\scripts\setup_vpn.ps1 | text | |
MD5:56FA01E2DF8C9952A5C18531CB080D88 | SHA256:36F7CCA326F67CACF24D63FACAFA92E4300527946B590280DA30E99E65AB4752 | |||
| 7776 | WinRAR.exe | C:\Users\admin\AppData\Local\Temp\Rar$DRa7776.33767\TraceX Final\scripts\tracex_cleaner.ps1 | text | |
MD5:A82C7D9876943FB05EF4AFF598DB1534 | SHA256:4E1D8ACD1573D5AAF3F0A3BA2643FF4AE2C21198BC6A5088D6676A6C0646D4B4 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
5276 | MoUsoCoreWorker.exe | GET | 304 | 51.104.136.2:443 | https://settings-win.data.microsoft.com/settings/v3.0/OneSettings/Client?OSVersionFull=10.0.19045.4046.amd64fre.vb_release.191206-1406&LocalDeviceID=s%3ABAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&FlightRing=Retail&AttrDataVer=186&OSUILocale=en-US&OSSkuId=48&App=WOSC&AppVer=&IsFlightingEnabled=0&TelemetryLevel=1&DeviceFamily=Windows.Desktop | US | — | — | whitelisted |
5276 | MoUsoCoreWorker.exe | GET | 304 | 51.104.136.2:443 | https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?ProcessorClockSpeed=3094&FlightIds=&UpdateOfferedDays=4294967295&BranchReadinessLevel=CB&OEMManufacturerName=DELL&IsCloudDomainJoined=0&ProcessorIdentifier=AMD64%20Family%2023%20Model%201%20Stepping%202&sku=48&ActivationChannel=Retail&AttrDataVer=186&IsMDMEnrolled=0&ProcessorCores=6&ProcessorModel=AMD%20Ryzen%205%203500%206-Core%20Processor&TotalPhysicalRAM=6144&PrimaryDiskType=4294967295&FlightingBranchName=&ChassisTypeId=1&OEMModelNumber=DELL&SystemVolumeTotalCapacity=260281&sampleId=95271487&deviceClass=Windows.Desktop&App=muse&DisableDualScan=0&AppVer=10.0&OEMSubModel=J5CR&locale=en-US&IsAlwaysOnAlwaysConnectedCapable=0&ms=0&DefaultUserRegion=244&UpdateServiceUrl=http%3A%2F%2Fneverupdatewindows10.com&osVer=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceId=s%3ABAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&DeferQualityUpdatePeriodInDays=0&ring=Retail&DeferFeatureUpdatePeriodInDays=30 | US | — | — | whitelisted |
932 | SIHClient.exe | GET | 304 | 135.232.92.137:443 | https://slscr.update.microsoft.com/SLS/%7B522D76A4-93E1-47F8-B8CE-07C937AD1A1E%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL | US | — | — | whitelisted |
932 | SIHClient.exe | GET | 200 | 74.178.240.51:443 | https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping | US | — | — | whitelisted |
932 | SIHClient.exe | GET | 200 | 135.232.92.137:443 | https://slscr.update.microsoft.com/sls/ping | US | — | — | whitelisted |
932 | SIHClient.exe | GET | 304 | 135.232.92.137:443 | https://slscr.update.microsoft.com/SLS/%7BE7A50285-D08D-499D-9FF8-180FDC2332BC%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL | US | — | — | whitelisted |
5316 | svchost.exe | POST | 200 | 40.126.31.71:443 | https://login.live.com/RST2.srf | US | xml | 1.24 Kb | whitelisted |
3352 | svchost.exe | GET | 304 | 20.73.194.208:443 | https://settings-win.data.microsoft.com/settings/v3.0/WSD/UpdateHealthTools?os=Windows&osVer=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceClass=Windows.Desktop&locale=en-US&deviceId=s:BAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&sampleId=s:95271487&appVer=10.0.19041.3626&FlightRing=Retail&TelemetryLevel=1&HidOverGattReg=C%3A%5CWINDOWS%5CSystem32%5CDriverStore%5CFileRepository%5Chidbthle.inf_amd64_9610b4821fdf82a5%5CMicrosoft.Bluetooth.Profiles.HidOverGatt.dll&AppVer=&ProcessorIdentifier=AMD64%20Family%2023%20Model%201%20Stepping%202&OEMModel=DELL&UpdateOfferedDays=4294967295&ProcessorManufacturer=AuthenticAMD&InstallDate=1661339444&OEMModelBaseBoard=&BranchReadinessLevel=CB&OEMSubModel=J5CR&IsCloudDomainJoined=0&DeferFeatureUpdatePeriodInDays=30&IsDeviceRetailDemo=0&FlightingBranchName=&OSUILocale=en-US&DeviceFamily=Windows.Desktop&WuClientVer=10.0.19041.3996&UninstallActive=1&IsFlightingEnabled=0&OSSkuId=48&ProcessorClockSpeed=3094&TotalPhysicalRAM=6144&SecureBootCapable=0&App=SedimentPack&ProcessorCores=6&CurrentBranch=vb_release&InstallLanguage=en-US&DeferQualityUpdatePeriodInDays=0&OEMName_Uncleaned=DELL&TPMVersion=0&PrimaryDiskTotalCapacity=262144&InstallationType=Client&AttrDataVer=186&ProcessorModel=AMD%20Ryzen%205%203500%206-Core%20Processor&IsEdgeWithChromiumInstalled=1&OSVersion=10.0.19045.4046&IsMDMEnrolled=0&ActivationChannel=Retail&FirmwareVersion=A.40&TrendInstalledKey=1&OSArchitecture=AMD64&DefaultUserRegion=244&UpdateManagementGroup=2 | US | — | — | whitelisted |
5316 | svchost.exe | GET | 200 | 23.11.41.157:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAz1vQYrVgL0erhQLCPM8GY%3D | NL | binary | 471 b | whitelisted |
5316 | svchost.exe | POST | 400 | 40.126.31.71:443 | https://login.live.com/ppsecure/deviceaddcredential.srf | US | text | 203 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | Not routed | — | whitelisted |
3352 | svchost.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5276 | MoUsoCoreWorker.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
— | — | 128.24.231.64:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
4 | System | 192.168.100.255:138 | — | Not routed | — | whitelisted |
5316 | svchost.exe | 40.126.31.71:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5316 | svchost.exe | 23.11.41.157:80 | ocsp.digicert.com | AKAMAI-AMS | NL | whitelisted |
3428 | svchost.exe | 172.211.123.249:443 | client.wns.windows.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
3352 | svchost.exe | 184.24.77.16:80 | crl.microsoft.com | AKAMAI-ASN1 | NL | whitelisted |
3352 | svchost.exe | 23.52.181.212:80 | www.microsoft.com | AKAMAI-AS | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
activation-v2.sls.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
login.live.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |