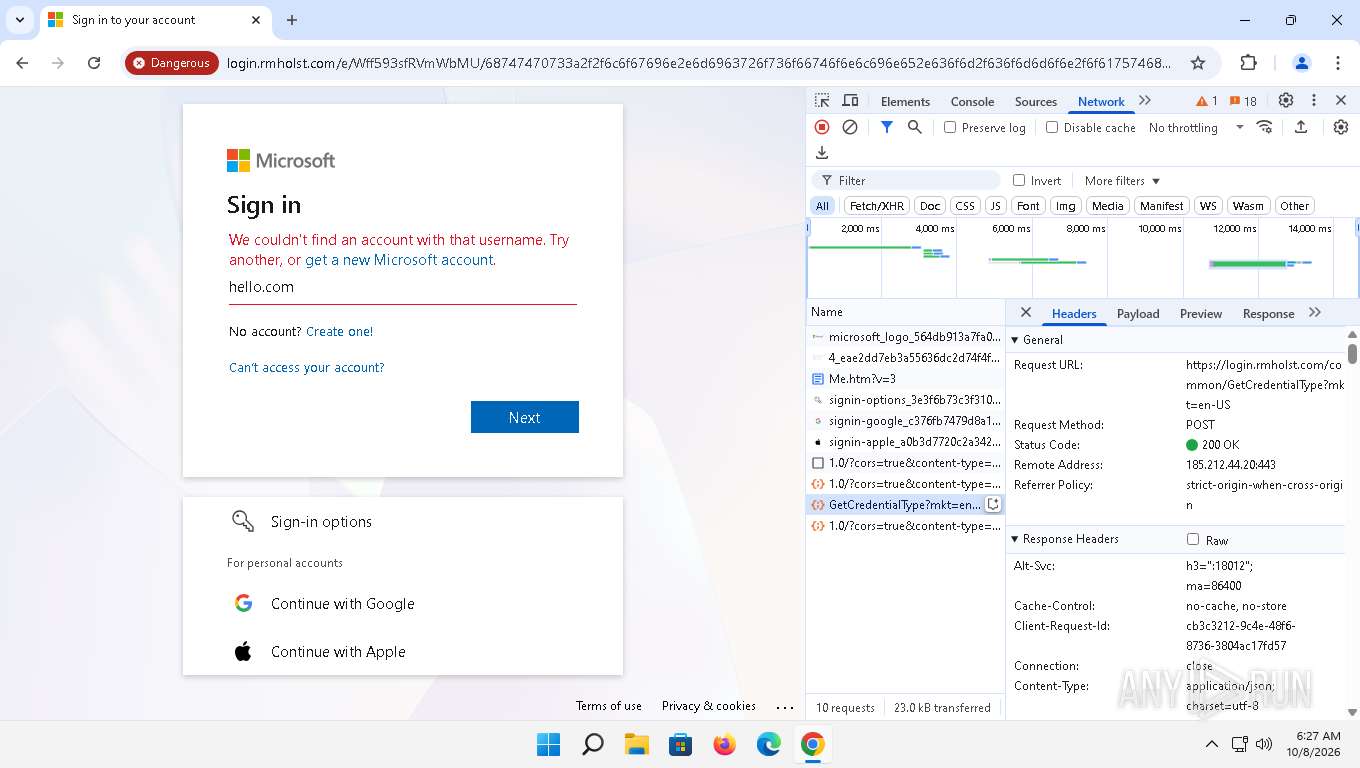
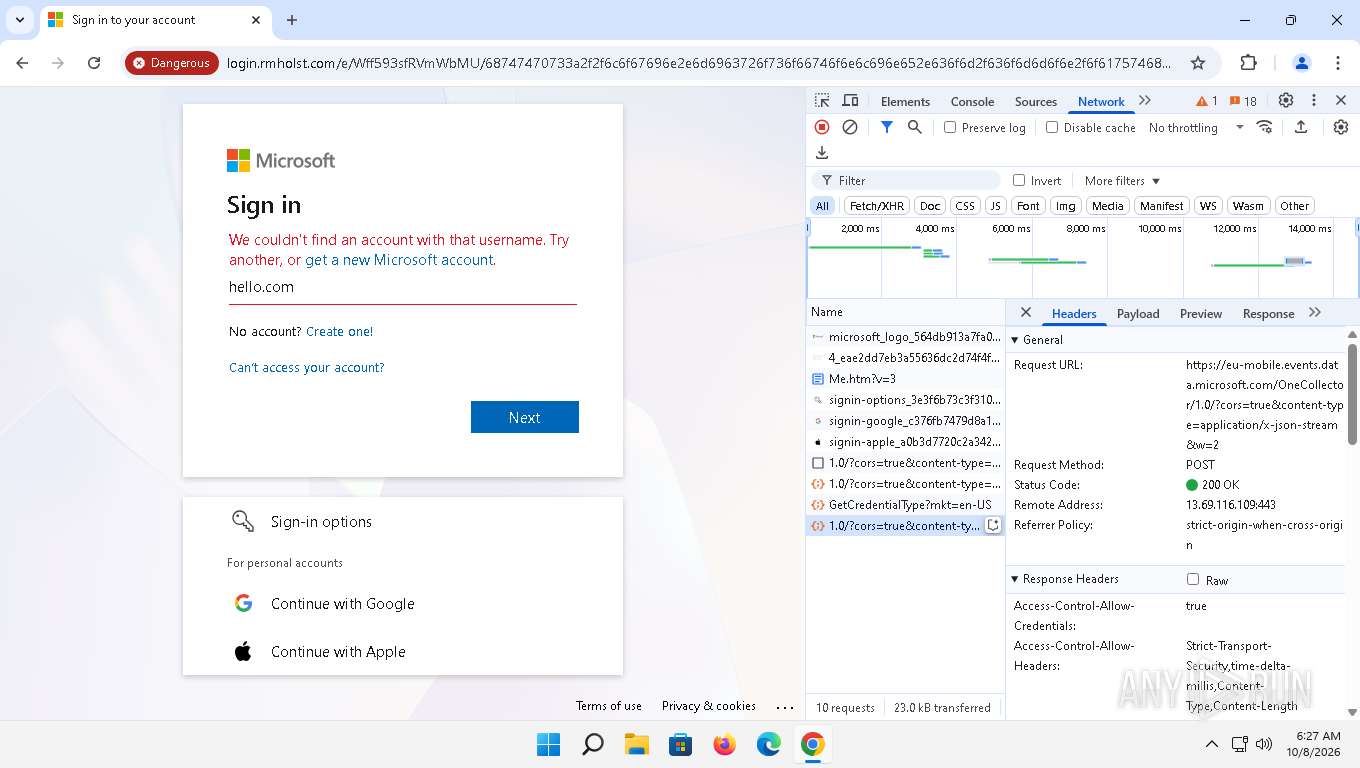
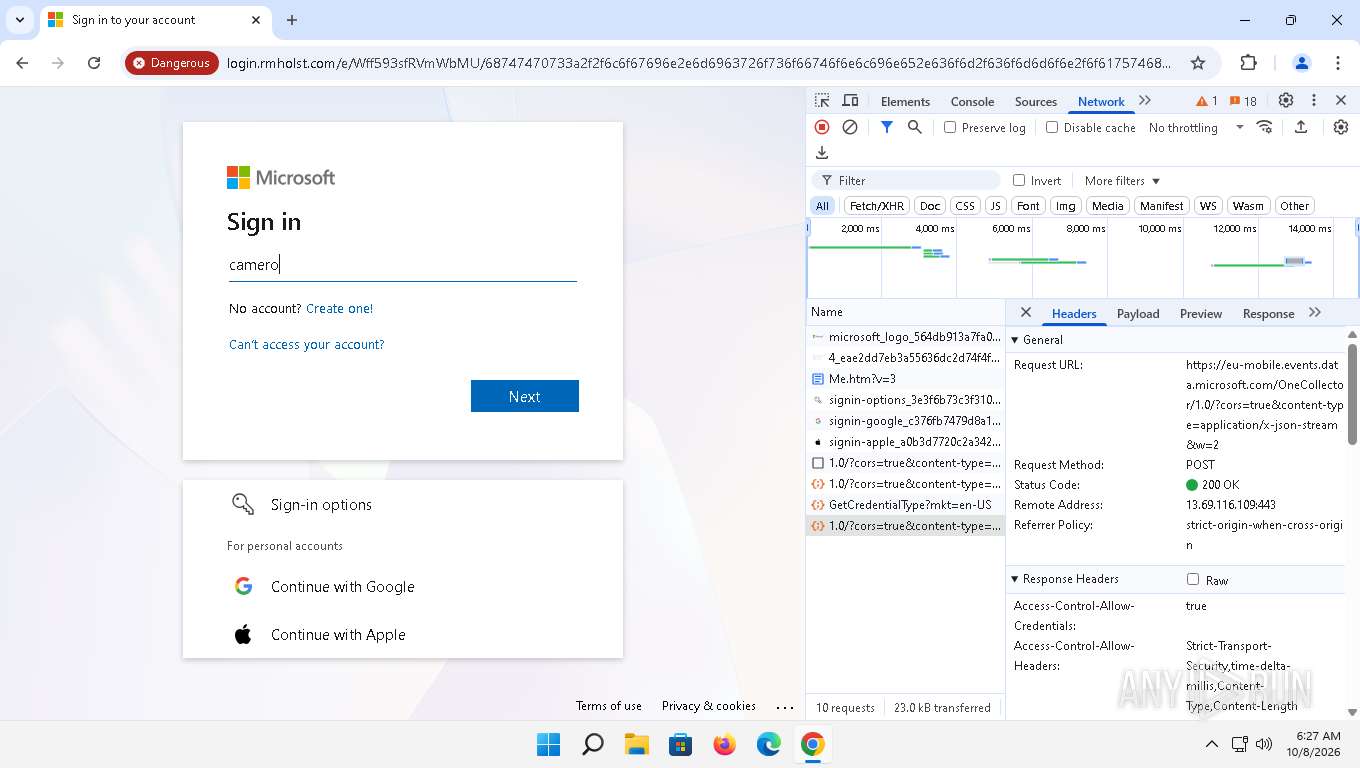
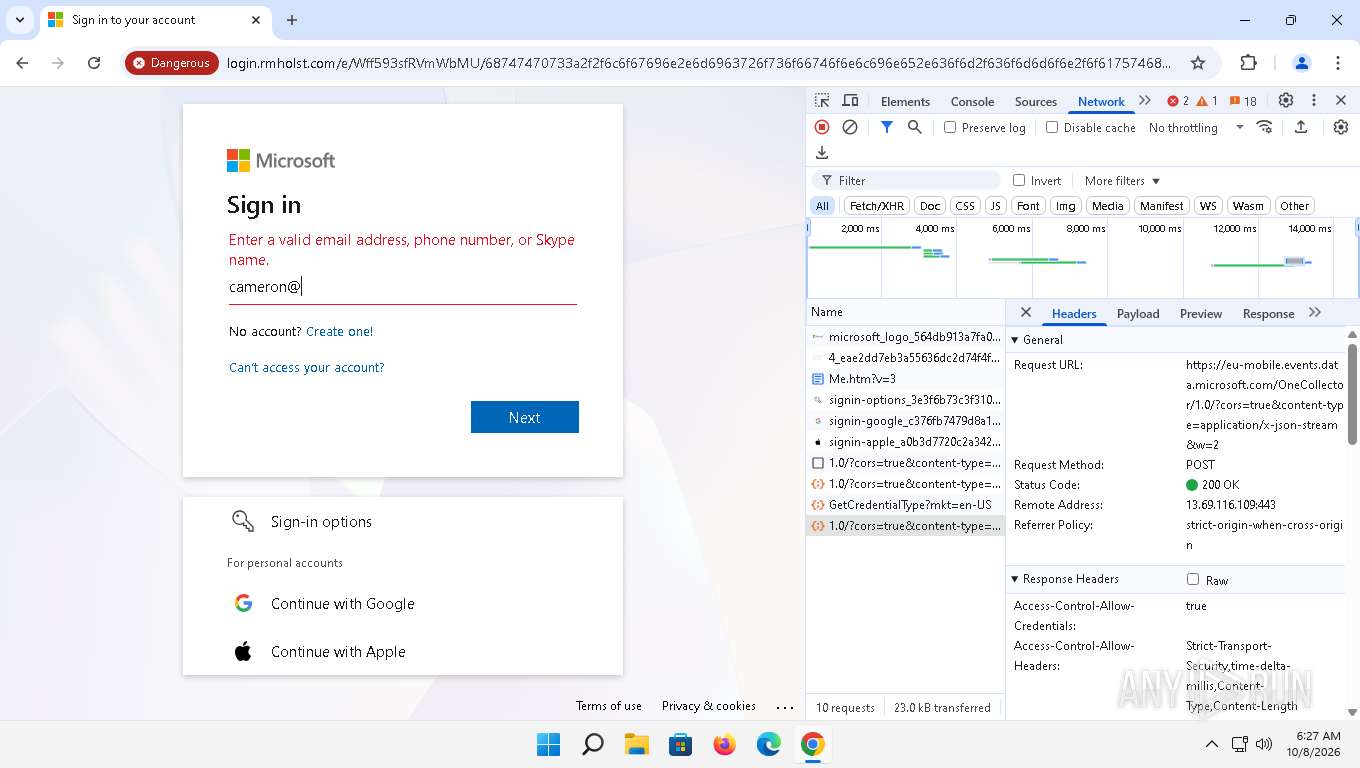
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
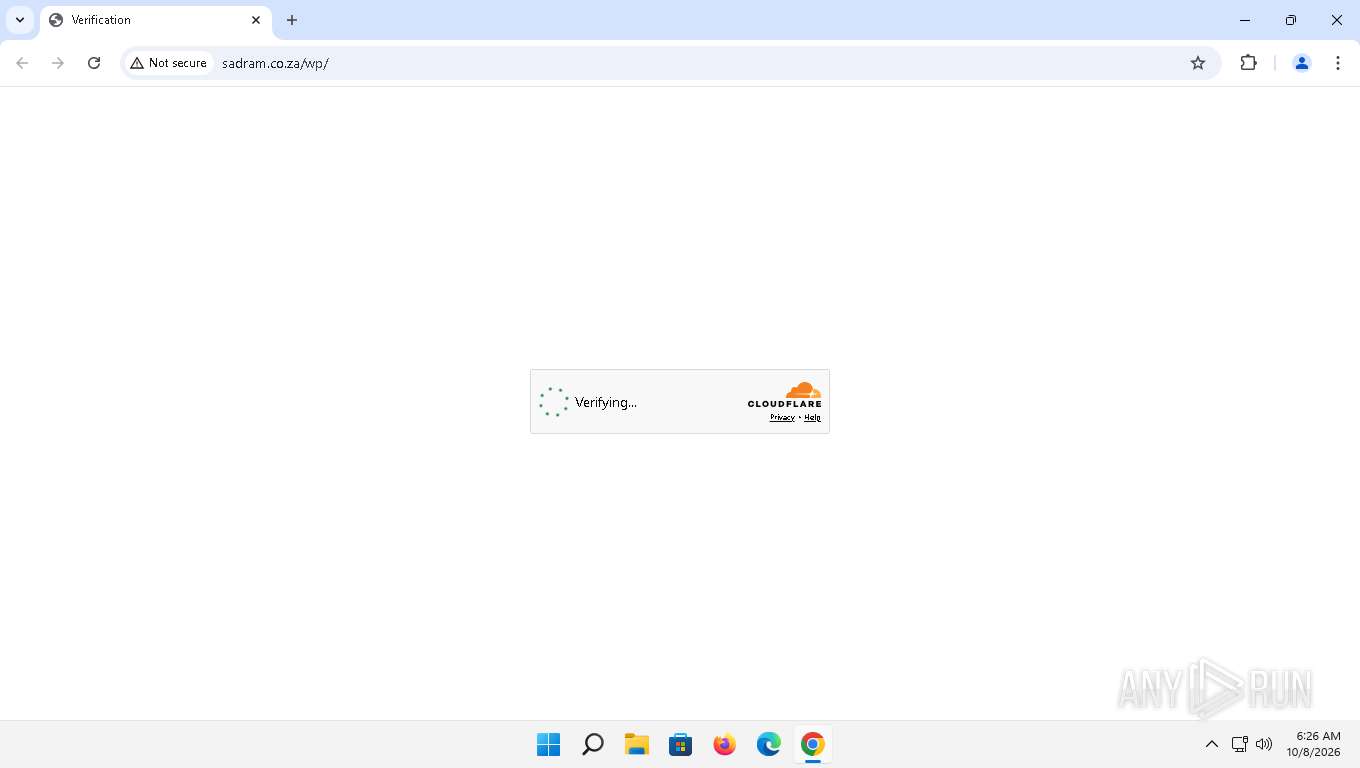
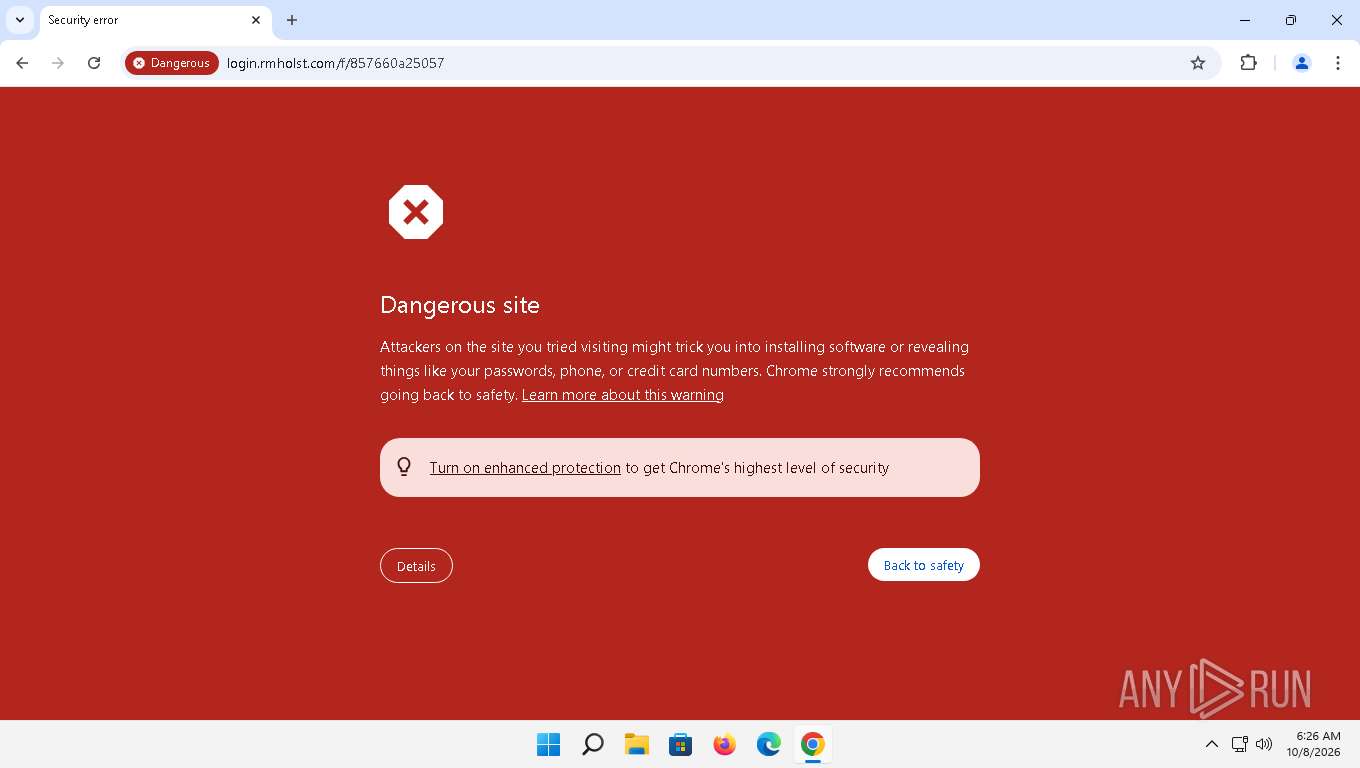
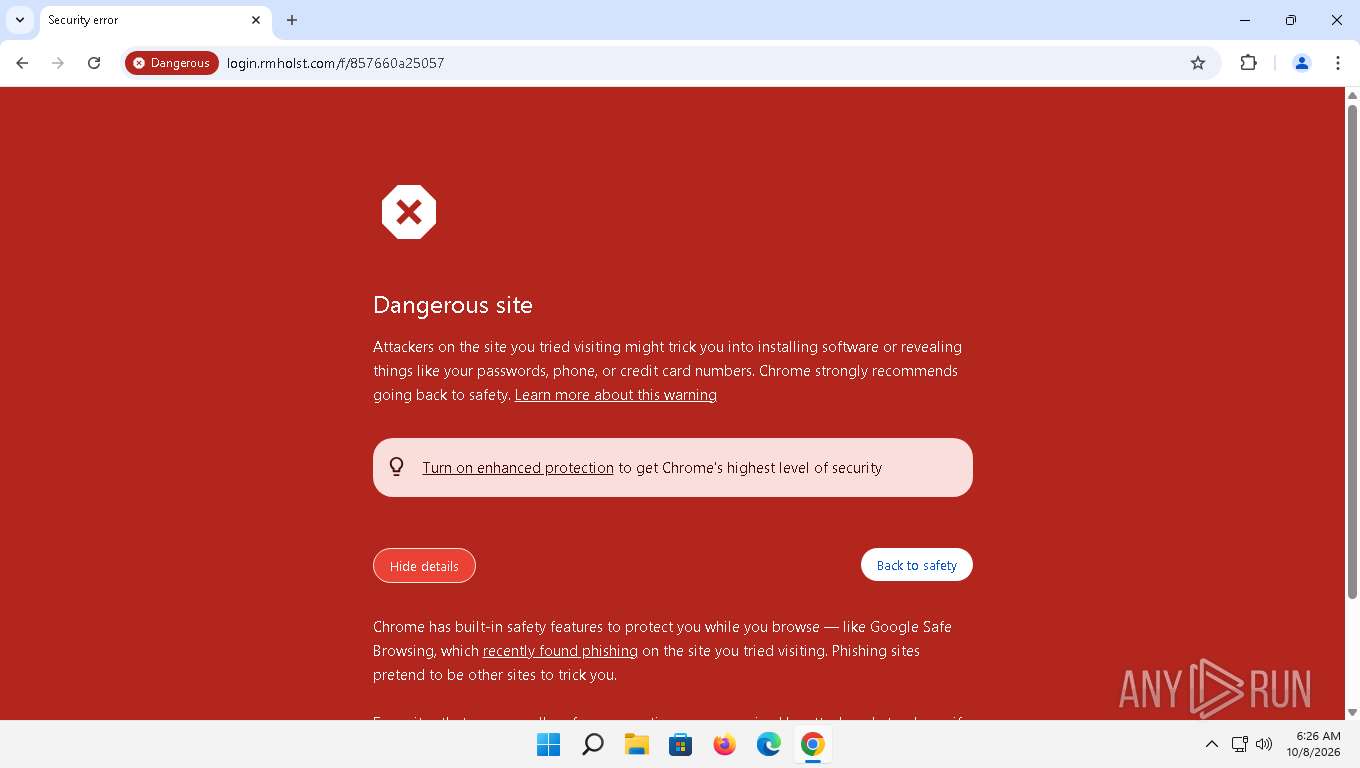
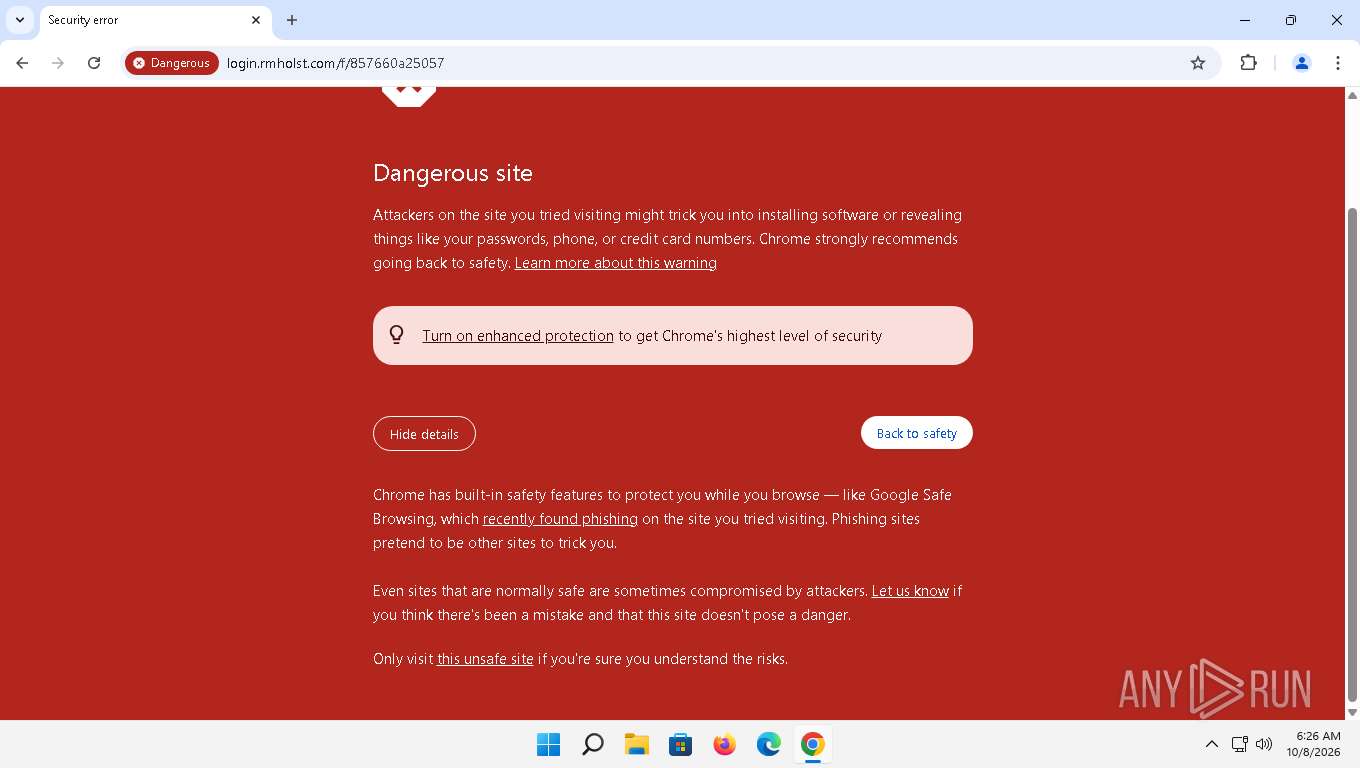
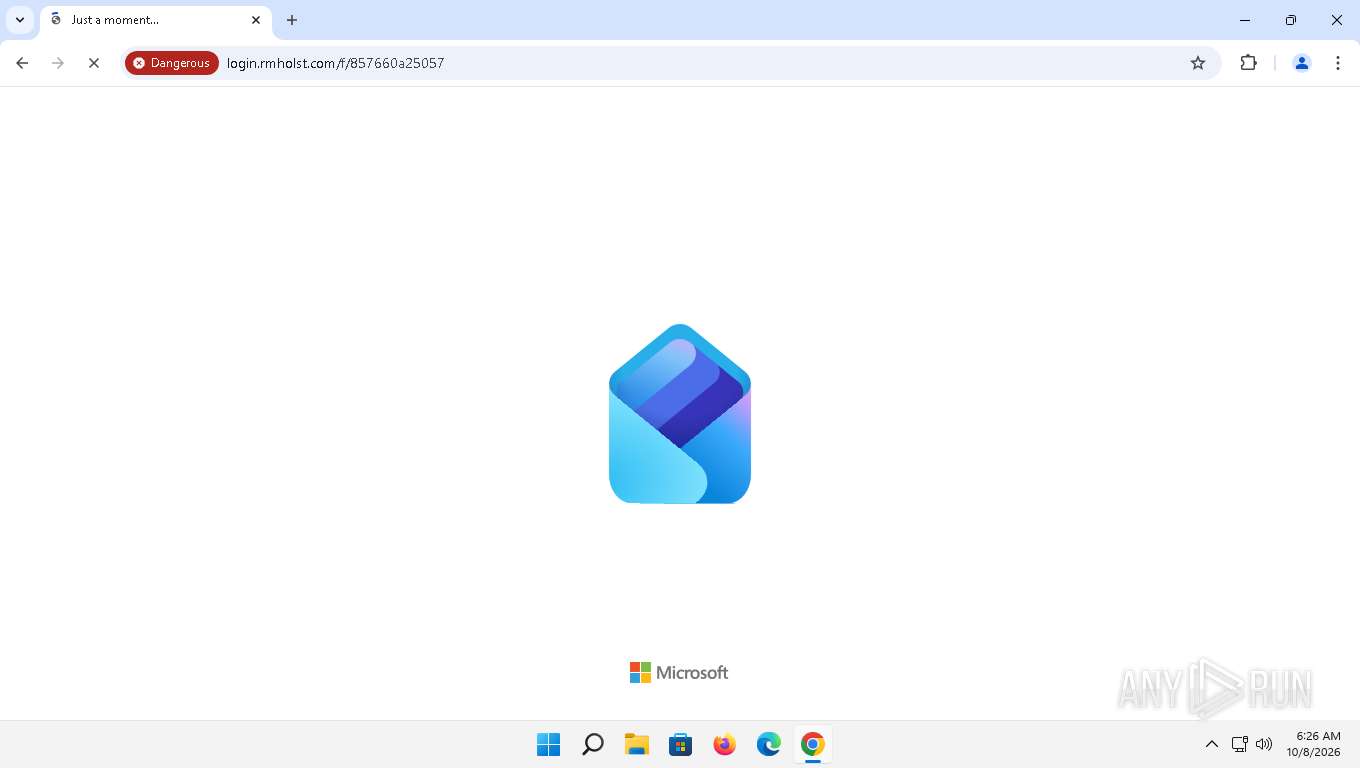
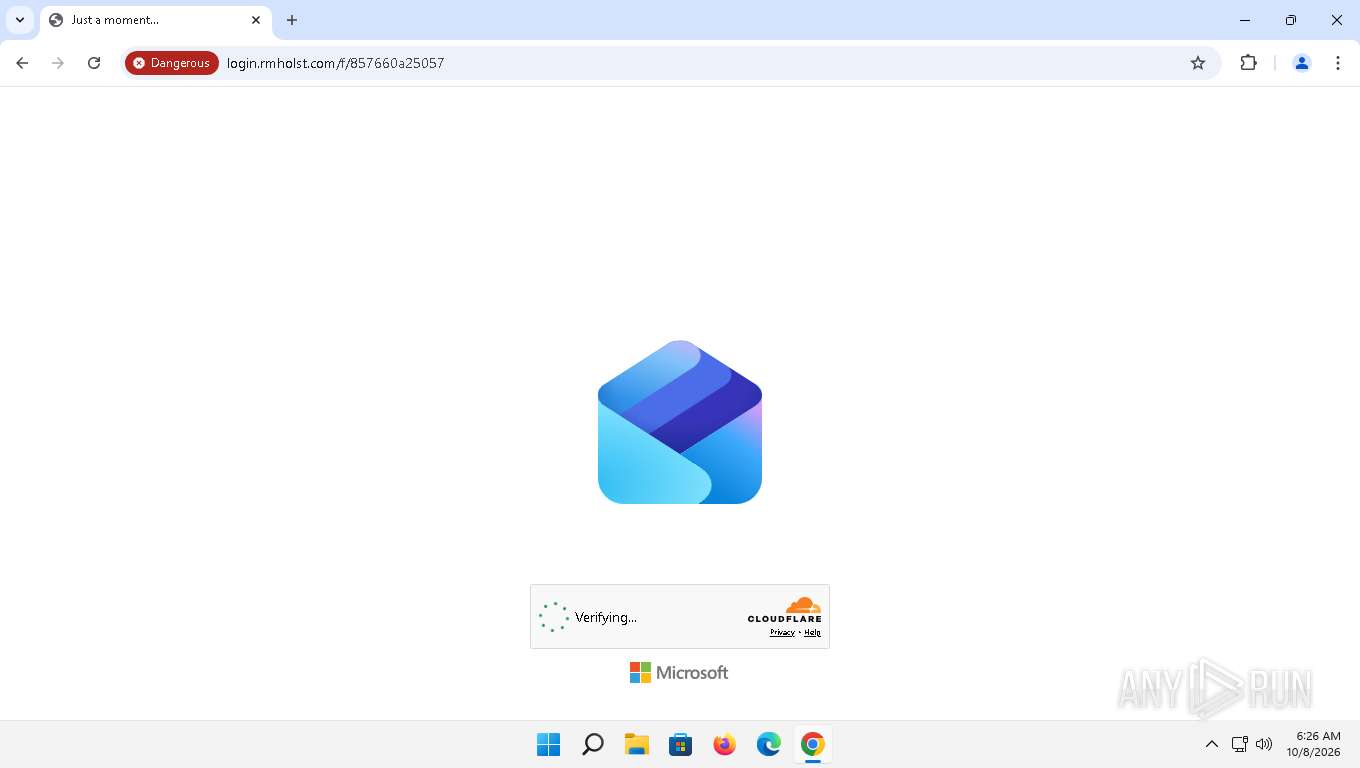
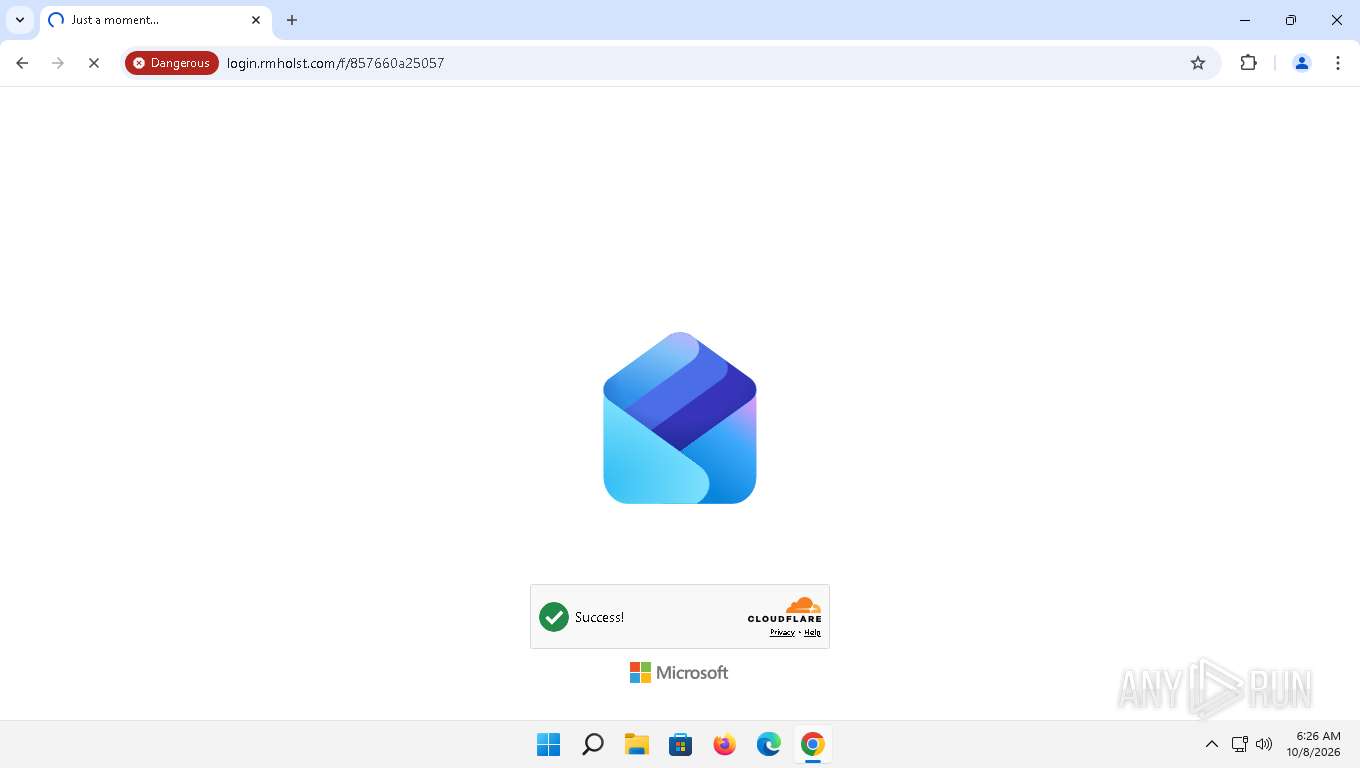
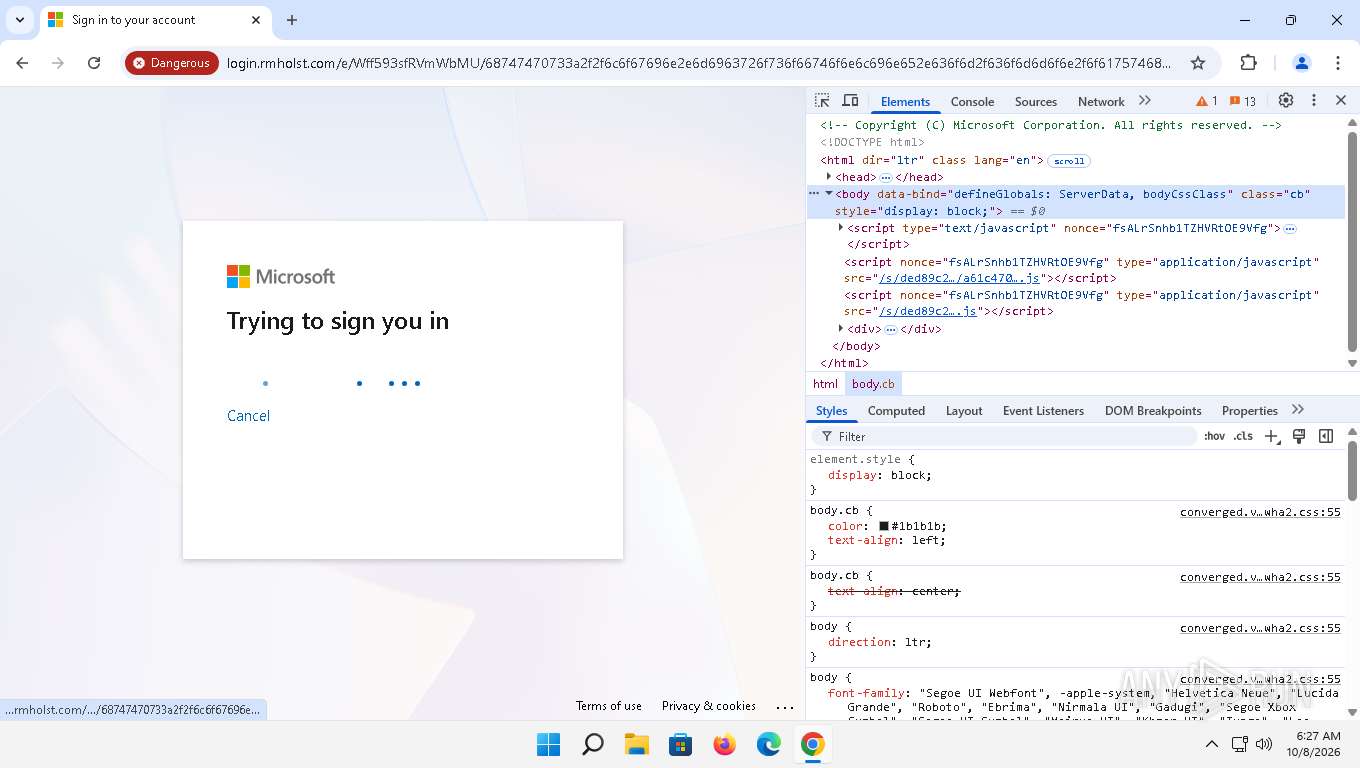
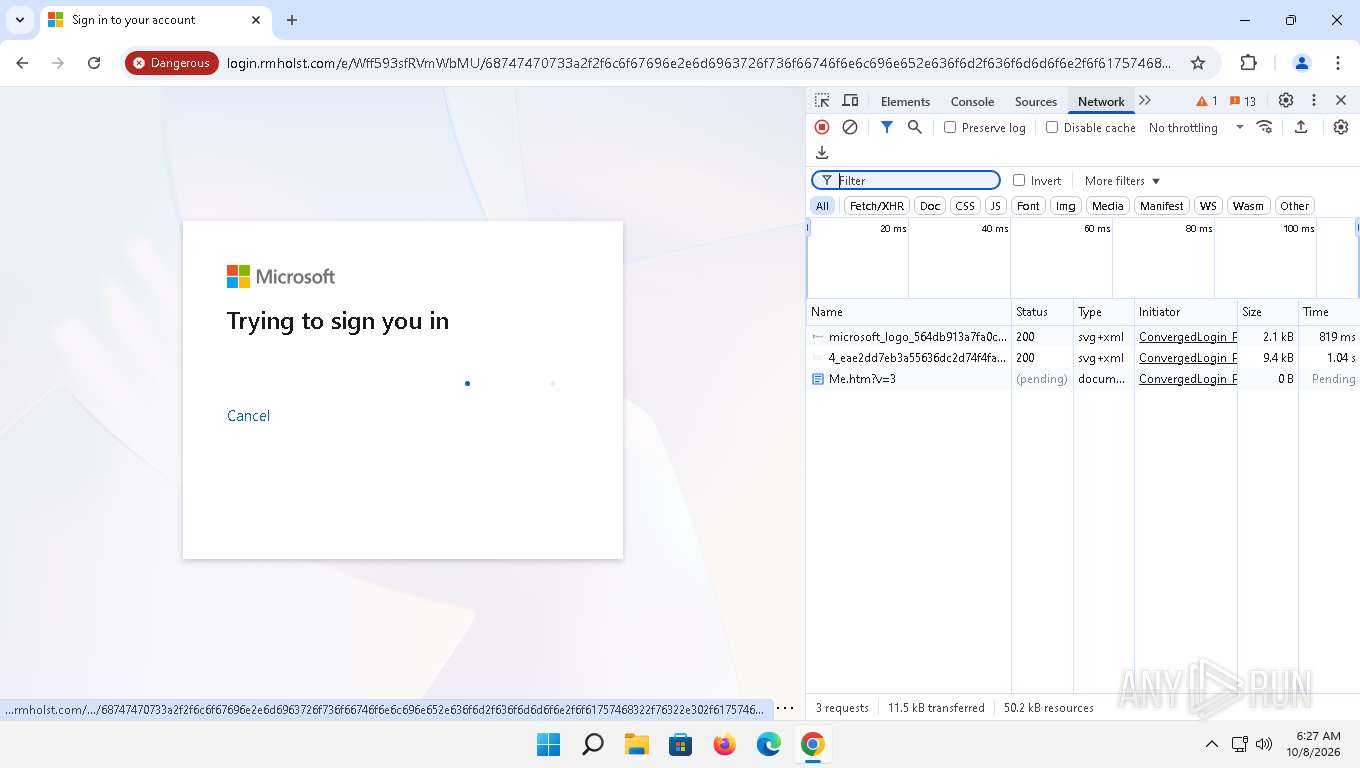
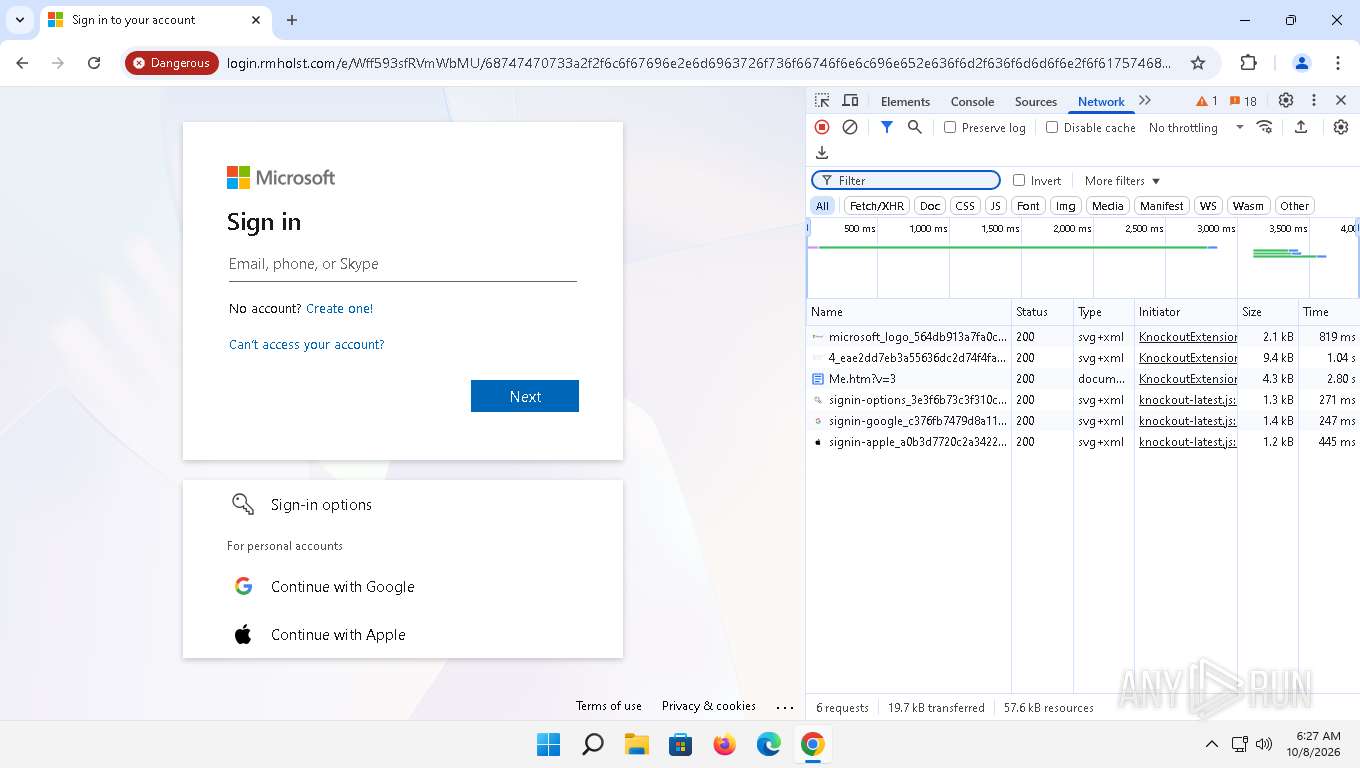
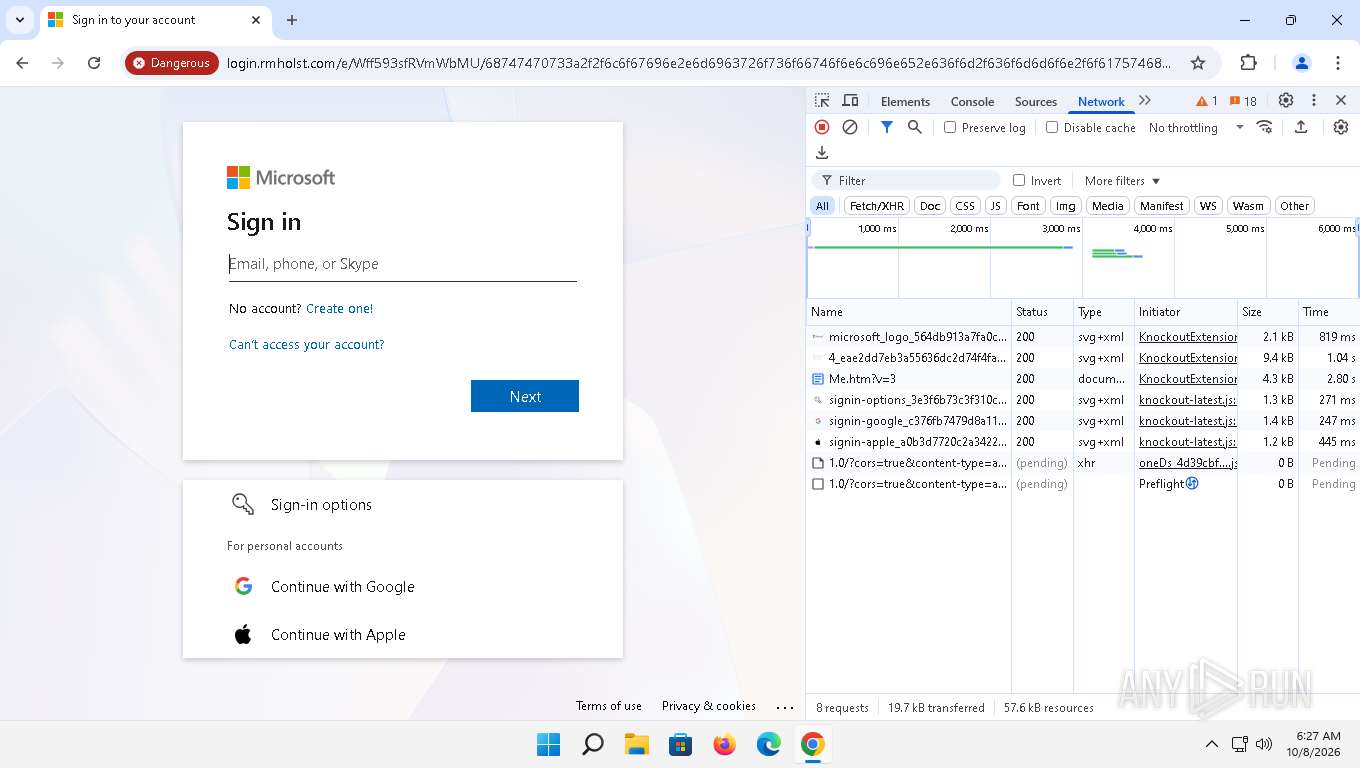
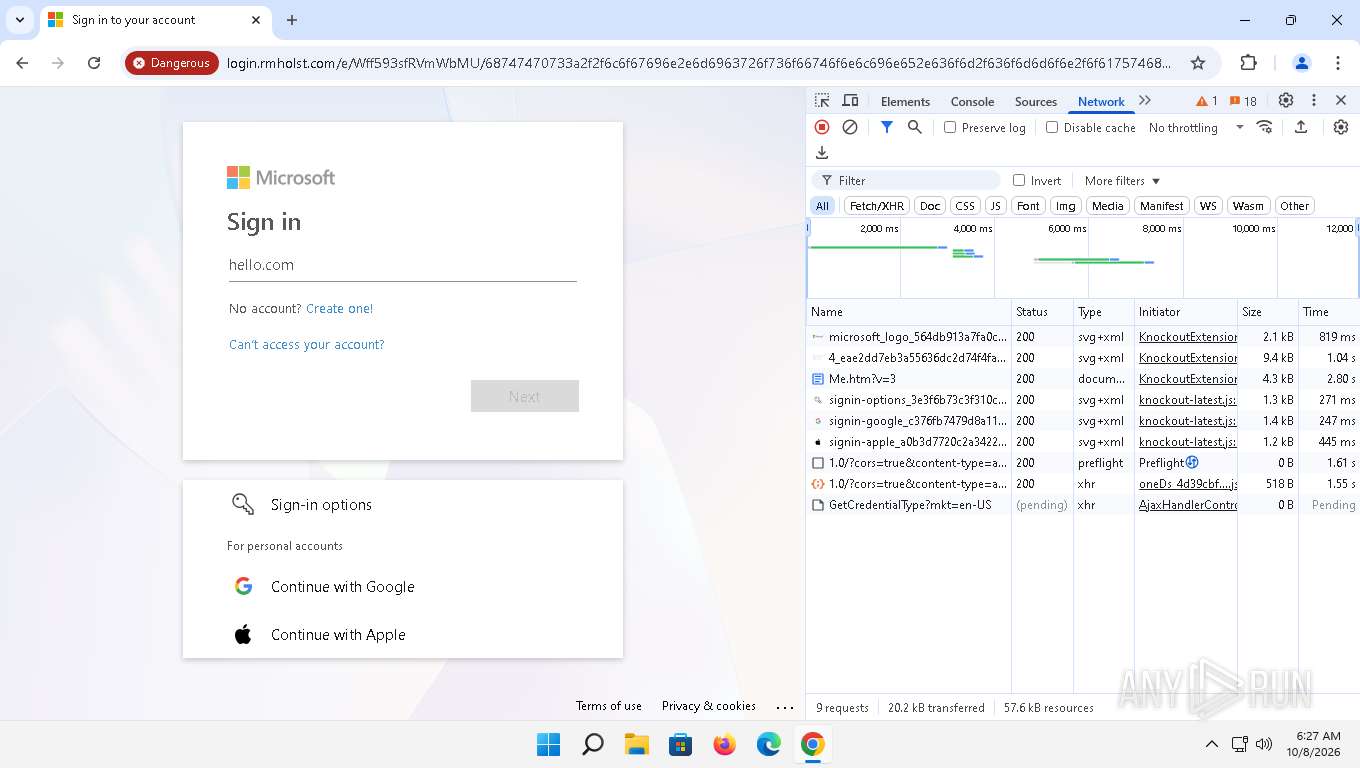
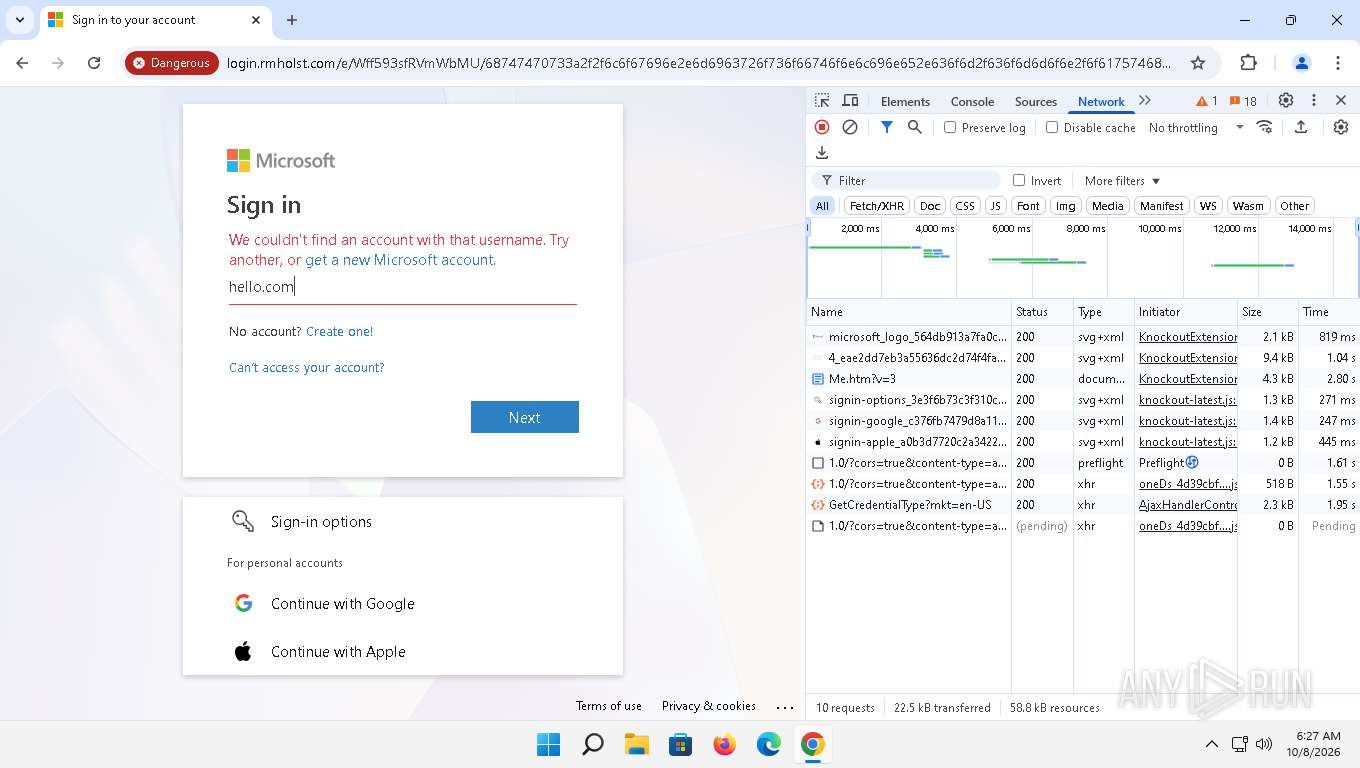
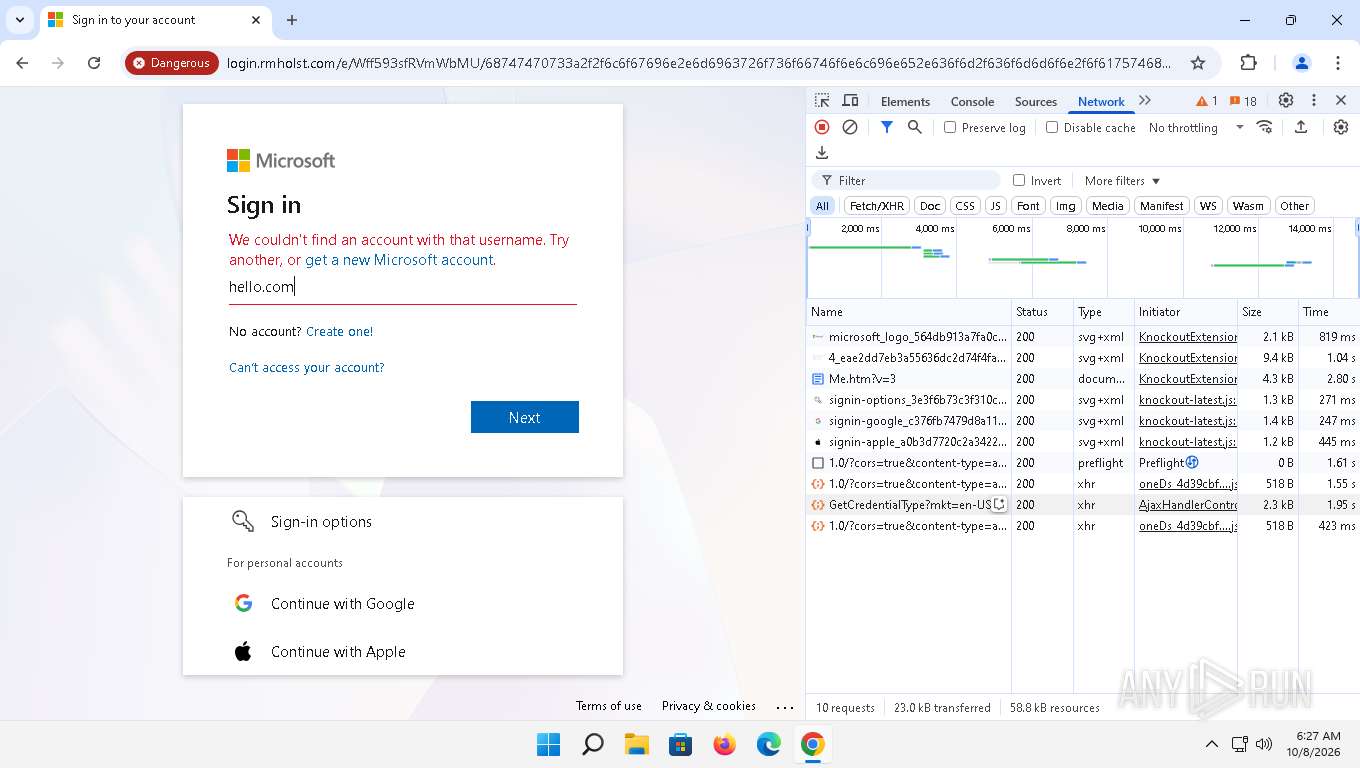
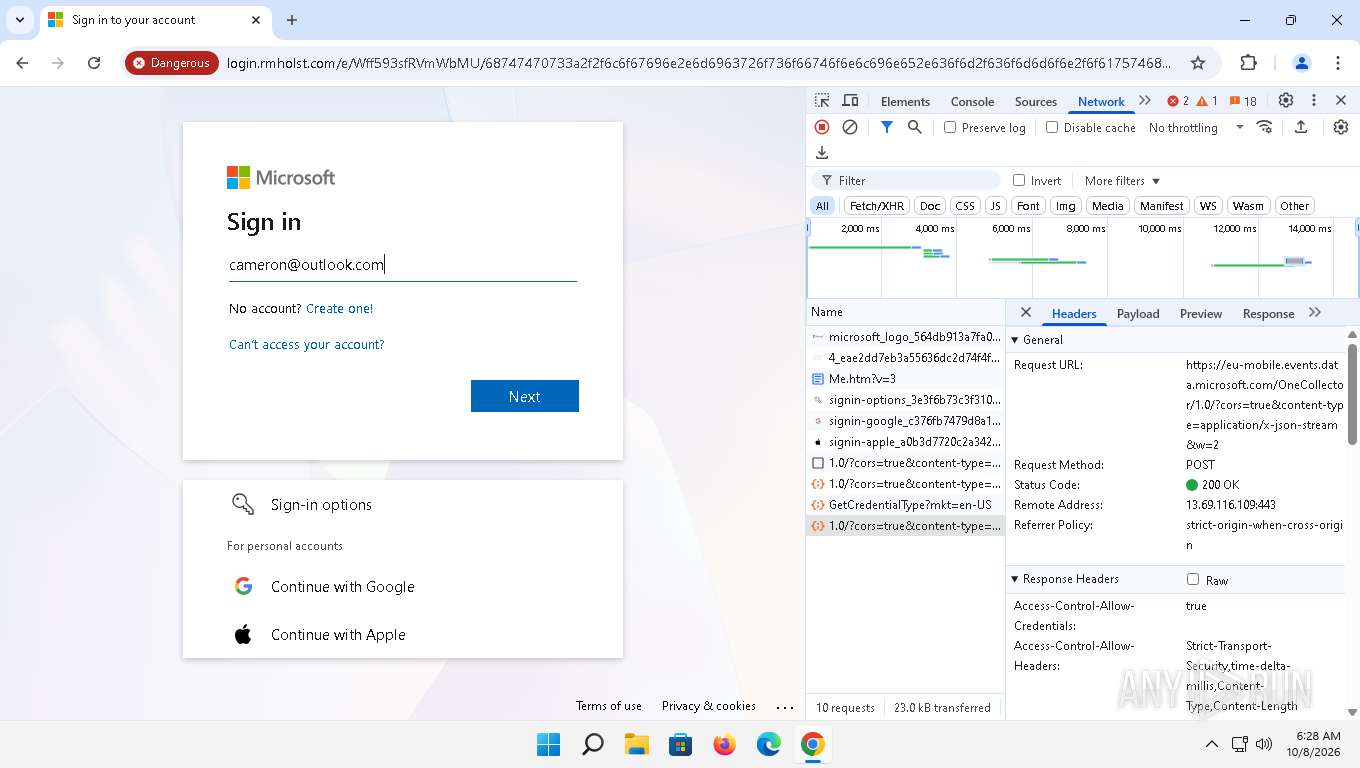
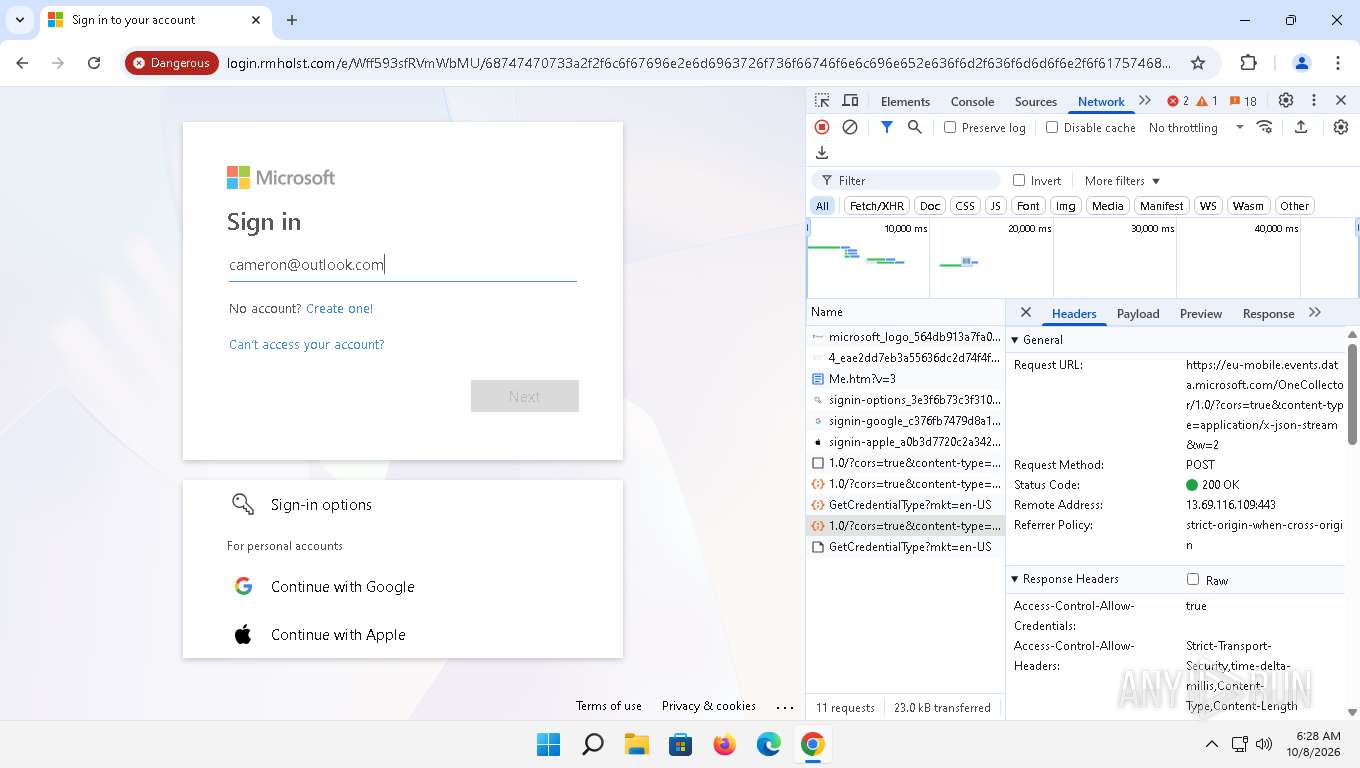
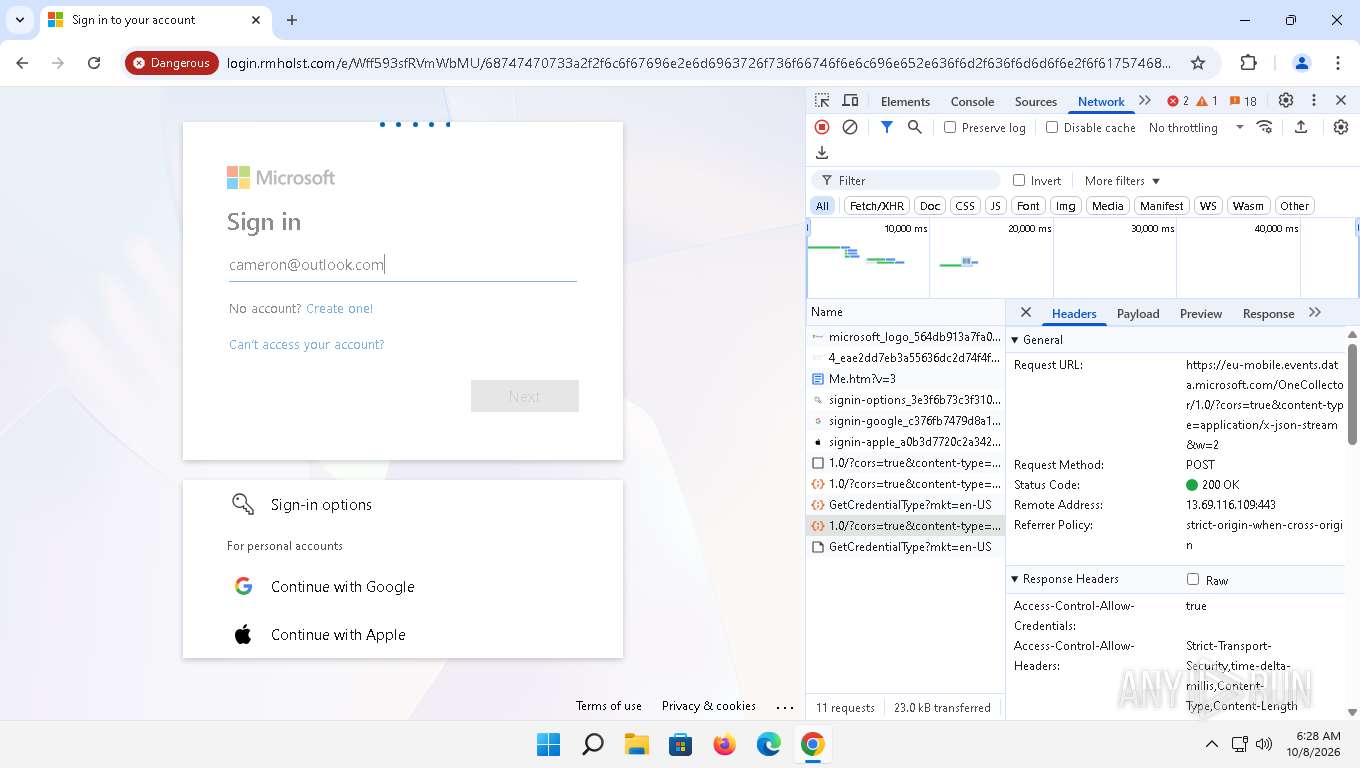
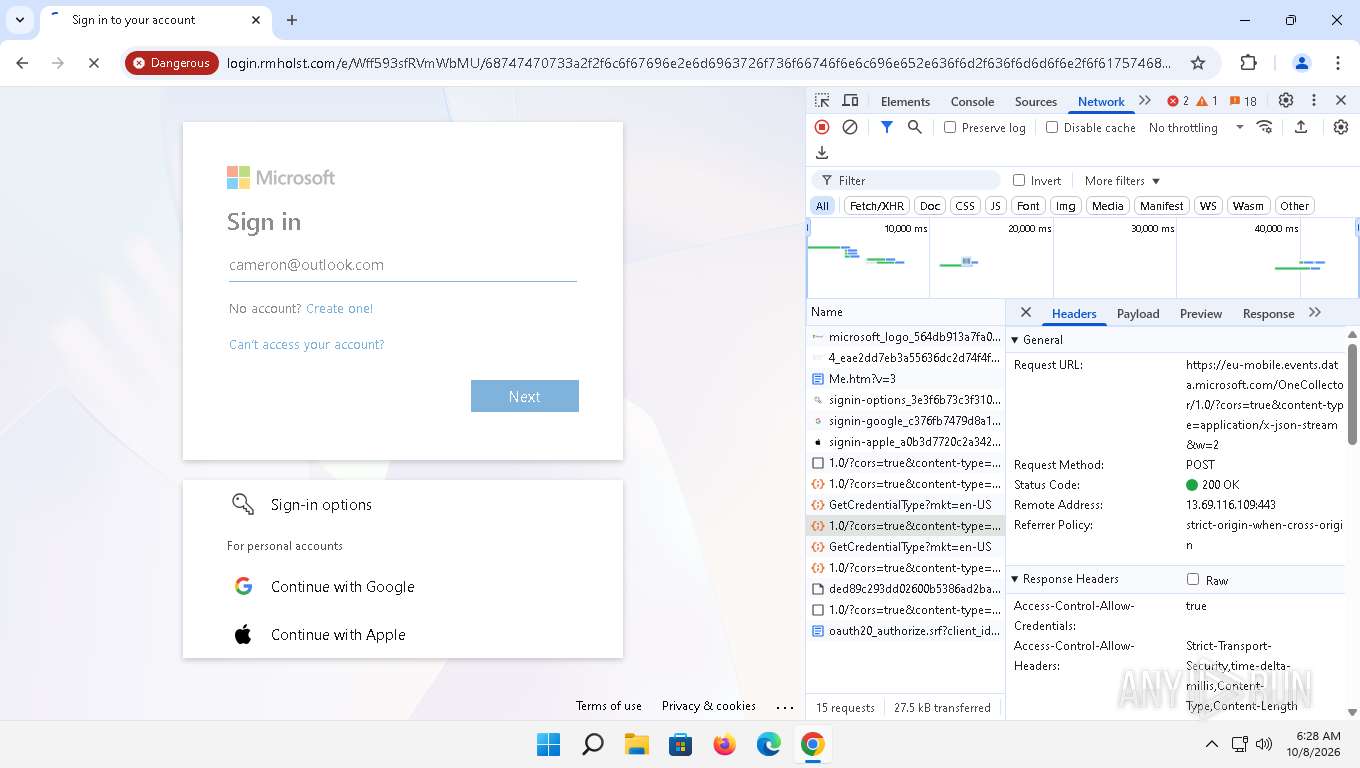
| URL: | sadram.co.za/wp |
| Full analysis: | https://app.any.run/tasks/0f810615-878b-477d-885d-81213e1360dc |
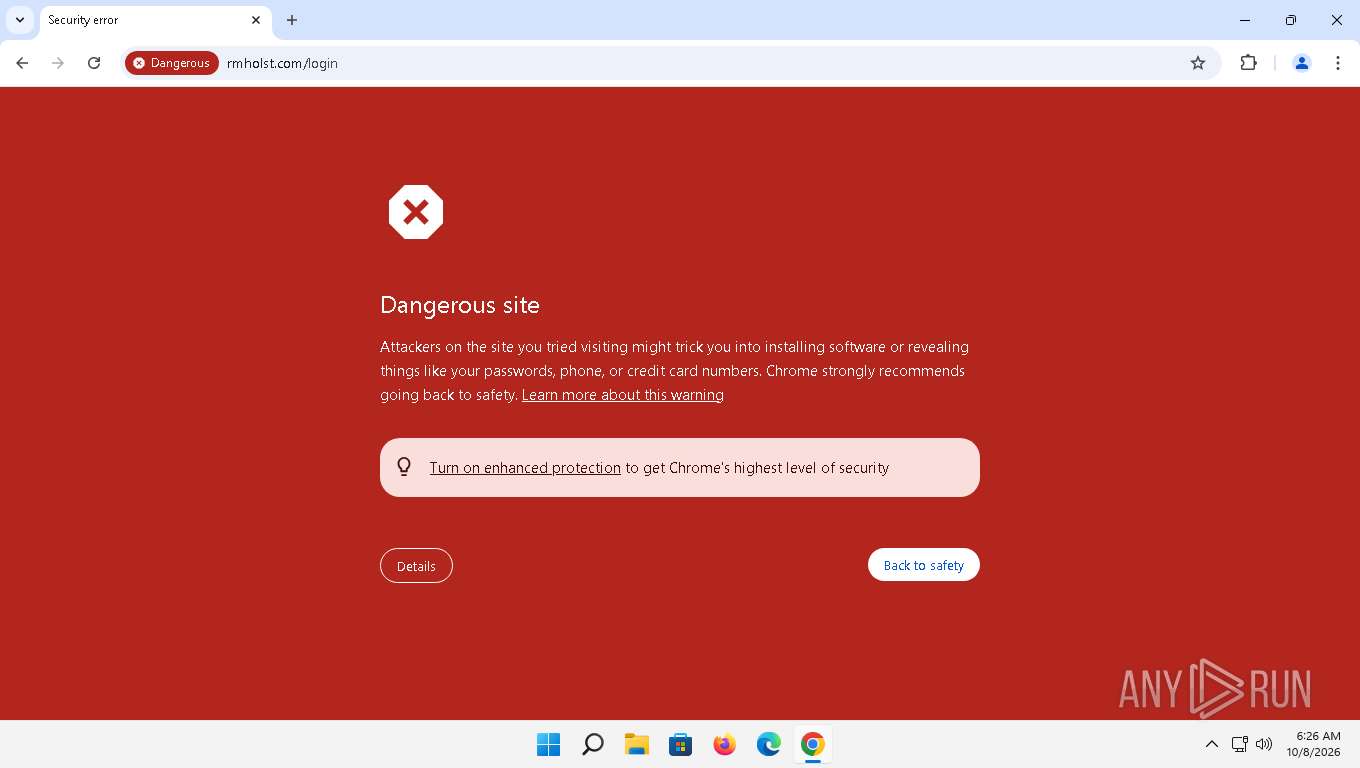
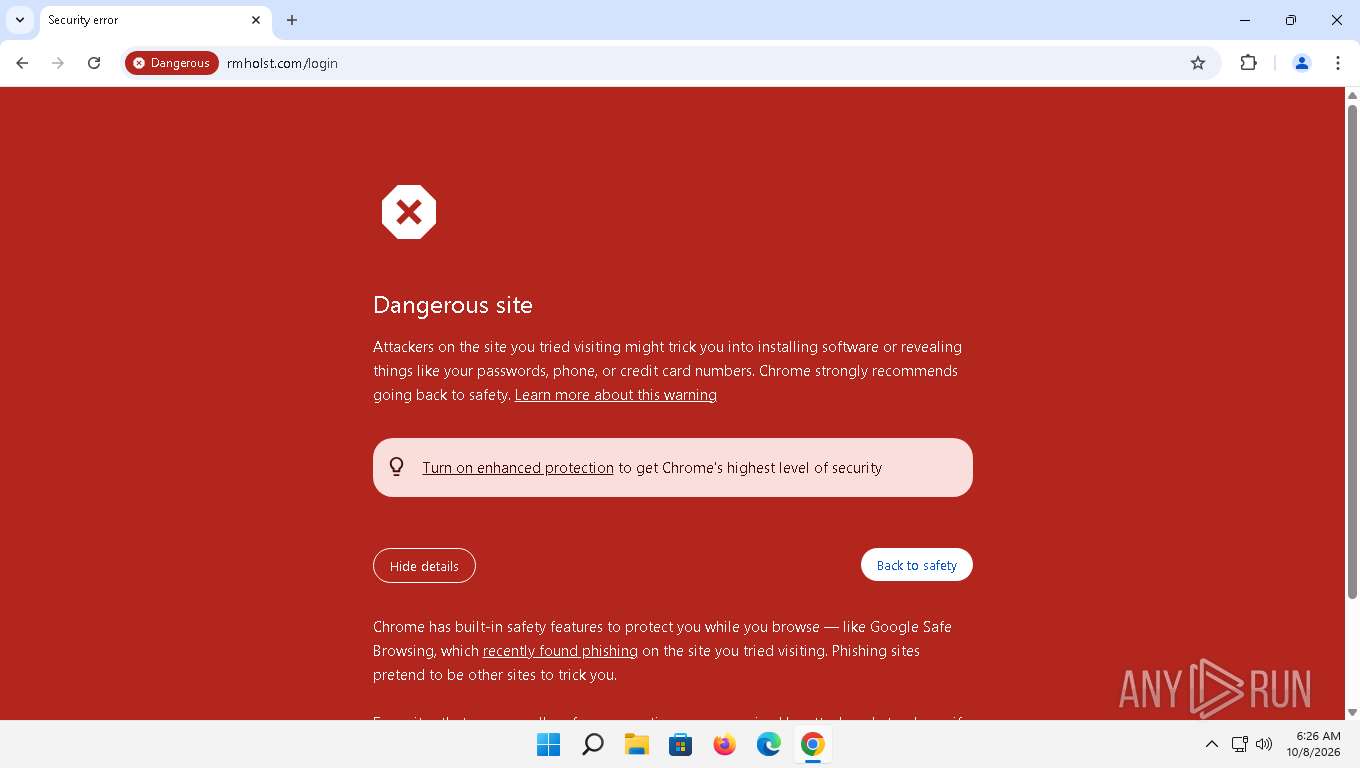
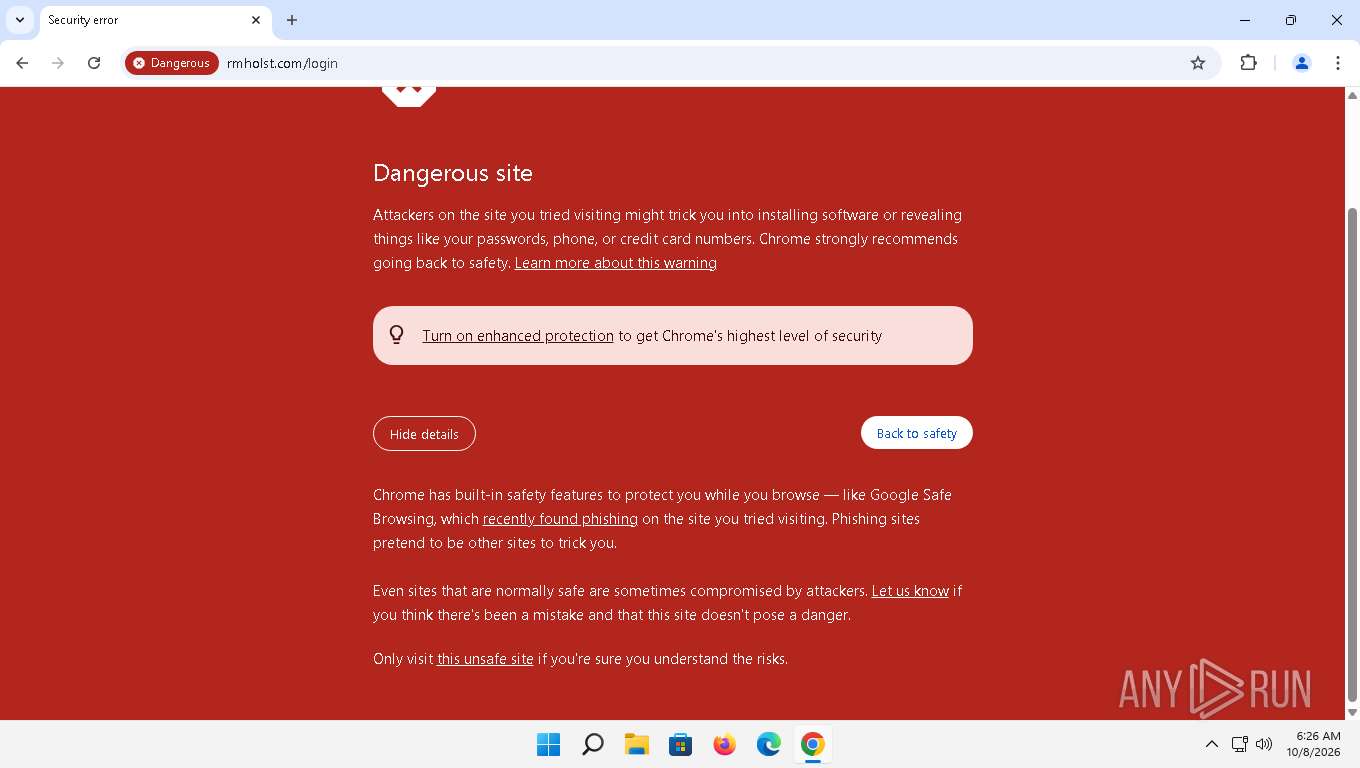
| Verdict: | Malicious activity |
| Analysis date: | October 08, 2026, 10:25:46 |
| OS: | Windows 11 Professional (build: 22000, 64 bit) |
| Tags: | |
| Indicators: | |
| MD5: | 1FC091BADEC52FD64CF7FDEF8B736C25 |
| SHA1: | BAB7FBA7BD887D9B72340B9497EC0ED62795AE38 |
| SHA256: | 31AD018488BF0DF24A4C1814CE70AA45C5F6459F15B6AEF74BCB0AA7FA3E7397 |
| SSDEEP: | 3:SKuV:IV |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 332 | "C:\Program Files (x86)\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=network.mojom.NetworkService --lang=en-US --service-sandbox-type=none --disable-quic --field-trial-handle=1832,i,12408440173651862772,12873408921005376988,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20250305-180124.387000 --mojo-platform-channel-handle=2208 /prefetch:11 | C:\Program Files (x86)\Google\Chrome\Application\chrome.exe | chrome.exe | ||||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 134.0.6998.36 Modules
| |||||||||||||||
| 476 | "C:\Program Files (x86)\Google\Chrome\Application\chrome.exe" --type=renderer --enable-dinosaur-easter-egg-alt-images --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=3 --enable-main-frame-before-activation --renderer-client-id=6 --field-trial-handle=1832,i,12408440173651862772,12873408921005376988,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20250305-180124.387000 --mojo-platform-channel-handle=3148 /prefetch:1 | C:\Program Files (x86)\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 134.0.6998.36 Modules
| |||||||||||||||
| 1816 | "C:\Program Files (x86)\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=quarantine.mojom.Quarantine --lang=en-US --service-sandbox-type=none --disable-quic --field-trial-handle=1832,i,12408440173651862772,12873408921005376988,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20250305-180124.387000 --mojo-platform-channel-handle=4896 /prefetch:14 | C:\Program Files (x86)\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 134.0.6998.36 Modules
| |||||||||||||||
| 2444 | "C:\Program Files (x86)\Google\Chrome\Application\chrome.exe" --type=renderer --enable-dinosaur-easter-egg-alt-images --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=3 --enable-main-frame-before-activation --renderer-client-id=5 --field-trial-handle=1832,i,12408440173651862772,12873408921005376988,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20250305-180124.387000 --mojo-platform-channel-handle=3160 /prefetch:1 | C:\Program Files (x86)\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 134.0.6998.36 Modules
| |||||||||||||||
| 2544 | "C:\Program Files (x86)\Google\Chrome\Application\chrome.exe" --type=renderer --enable-dinosaur-easter-egg-alt-images --disable-gpu-compositing --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=3 --enable-main-frame-before-activation --renderer-client-id=8 --field-trial-handle=1832,i,12408440173651862772,12873408921005376988,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20250305-180124.387000 --mojo-platform-channel-handle=4832 /prefetch:1 | C:\Program Files (x86)\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 134.0.6998.36 Modules
| |||||||||||||||
| 2920 | "C:\Program Files (x86)\Google\Chrome\Application\chrome.exe" --type=renderer --extension-process --enable-dinosaur-easter-egg-alt-images --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=3 --enable-main-frame-before-activation --renderer-client-id=7 --field-trial-handle=1832,i,12408440173651862772,12873408921005376988,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20250305-180124.387000 --mojo-platform-channel-handle=3848 /prefetch:9 | C:\Program Files (x86)\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 134.0.6998.36 Modules
| |||||||||||||||
| 4036 | "C:\Program Files (x86)\Google\Chrome\Application\chrome.exe" --type=gpu-process --gpu-preferences=UAAAAAAAAADgAAAEAAAAAAAAAAAAAAAAAABgAAEAAAAAAAAAAAAAAAAAAAACAAAAAAAAAAAAAAAAAAAAAAAAABAAAAAAAAAAEAAAAAAAAAAIAAAAAAAAAAgAAAAAAAAA --field-trial-handle=1832,i,12408440173651862772,12873408921005376988,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20250305-180124.387000 --mojo-platform-channel-handle=1820 /prefetch:2 | C:\Program Files (x86)\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 134.0.6998.36 Modules
| |||||||||||||||
| 4176 | C:\Windows\system32\wbem\wmiprvse.exe -secured -Embedding | C:\Windows\System32\wbem\WmiPrvSE.exe | — | svchost.exe | |||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: WMI Provider Host Exit code: 0 Version: 10.0.22000.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 5472 | "C:\Program Files (x86)\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=storage.mojom.StorageService --lang=en-US --service-sandbox-type=service --disable-quic --field-trial-handle=1832,i,12408440173651862772,12873408921005376988,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20250305-180124.387000 --mojo-platform-channel-handle=2280 /prefetch:13 | C:\Program Files (x86)\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 134.0.6998.36 Modules
| |||||||||||||||
| 5500 | "C:\Program Files (x86)\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --lang=en-US --service-sandbox-type=service --disable-quic --field-trial-handle=1832,i,12408440173651862772,12873408921005376988,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20250305-180124.387000 --mojo-platform-channel-handle=6616 /prefetch:14 | C:\Program Files (x86)\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 134.0.6998.36 Modules
| |||||||||||||||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 7092 | MoUsoCoreWorker.exe | C:\ProgramData\USOPrivate\UpdateStore\store.db-journal | other | |
MD5:936D843C2D081849271826DE7EE02CA3 | SHA256:4D24EB87713ACBF895595462D6C91985B1E04A3376FE7174BB6A36B793915525 | |||
| 7092 | MoUsoCoreWorker.exe | C:\Windows\SystemTemp\{7659485A-4A44-4F2F-8E45-81827F857901}\ssshim.dll | executable | |
MD5:3DE653713E705E001C3F0BE1EFC51ED3 | SHA256:C78EBEF77E03135B3CEA0705D4C259D782ED80746FAEA4E9F4A851E494FA94F9 | |||
| 8264 | MoNotificationUx.exe | C:\ProgramData\USOShared\Logs\User\MoNotificationUx.710b3e1a-275d-41be-90a0-c0562017a422.1.etl | windows system | |
MD5:5AE89FF2B981C7BDD2659E3D1AD97CC6 | SHA256:5906708438C1B36EFD8552F9D55E050C39CE40D5B79355E30527E28306BF3ABA | |||
| 8428 | MoNotificationUx.exe | C:\ProgramData\USOShared\Logs\User\MoNotificationUx.696a0d0b-2f14-41f6-8bc2-a5d18867353c.1.etl | windows system | |
MD5:62AAFDD29ACAE9DD33B1416E3DCF78E3 | SHA256:A390B3166AF56A6492CEA814E310AFFFA91004BD33EE0D8C098B6F2A9445B07D | |||
| 7092 | MoUsoCoreWorker.exe | C:\ProgramData\USOPrivate\UpdateStore\store.db | other | |
MD5:E0251CEA9DB7FECE2DC96CBEA2233010 | SHA256:17963539740A8BF03C49AAAEA2FA470316B374F325ADD3CB6745BC49157A281E | |||
| 7092 | MoUsoCoreWorker.exe | C:\ProgramData\USOShared\Logs\System\MoUsoCoreWorker.f2aac7ce-2fd4-4d73-b4b9-a509a3714eb7.1.etl | windows system | |
MD5:315706FA5CC4C1B74926DDED82EBA153 | SHA256:82988320C43821E68FA935E25A68AC31C0C224B2EF90B5EEEB757EA95DBD7506 | |||
| 7092 | MoUsoCoreWorker.exe | C:\ProgramData\USOShared\Logs\System\MoUsoCoreWorker.f2aac7ce-2fd4-4d73-b4b9-a509a3714eb7.2.etl | windows system | |
MD5:AE3616F11AC03CEA51410D3D2B0E446A | SHA256:3E53D18C63AD7FB900FAD27F38140DF2C59D0FDEC4ECAFBCAB1646CDBE7F7A75 | |||
| 7092 | MoUsoCoreWorker.exe | C:\ProgramData\USOShared\Logs\System\MoUxCoreWorker.f1548c3e-d167-4f65-a77a-b780da9e383c.1.etl | windows system | |
MD5:E4947EE73BF0AB2B131EF3E9A1B40987 | SHA256:E20EC31AEE5E79803B830367728424DCABE75BB5BE29D813ACBD5871989CC5B3 | |||
| 8340 | chrome.exe | C:\Users\admin\AppData\Local\Temp\chrome_Unpacker_BeginUnzipping7996_368003601\_metadata\verified_contents.json | text/data | |
MD5:6D1D175F88B64546105E3E7C31D1129A | SHA256:A0BC246E8E160A9BB32FA60F4E7A04D148A17125F426509466031E07731FDF81 | |||
| 7996 | chrome.exe | C:\Users\admin\AppData\Local\Temp\chrome_Unpacker_BeginUnzipping7996_368003601\manifest.fingerprint | text/data | |
MD5:684DA5CCA8ADC8CA59CBE5B082CFE0B5 | SHA256:F48C9D93CC216AF13BBFAD15DD5E6D1679CD35D318E664029DDF61EFC6E51A5D | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
7992 | svchost.exe | HEAD | 200 | 23.197.142.186:443 | https://fs.microsoft.com/fs/windows/config.json | US | — | — | whitelisted |
332 | chrome.exe | GET | — | 102.214.8.120:80 | http://sadram.co.za/wp | ZA | — | — | unknown |
332 | chrome.exe | GET | 302 | 104.18.94.41:443 | https://challenges.cloudflare.com/turnstile/v0/api.js | US | — | — | whitelisted |
3248 | svchost.exe | GET | 200 | 199.232.214.172:80 | http://ctldl.windowsupdate.com/msdownload/update/v3/static/trustedr/en/disallowedcertstl.cab?75ccd12021a62055 | US | archive | 78.8 Kb | whitelisted |
332 | chrome.exe | GET | 200 | 192.168.1.2:443 | https://clientservices.googleapis.com/chrome-variations/seed?osname=win&channel=stable&milestone=134 | unknown | archive | 104 Kb | whitelisted |
332 | chrome.exe | GET | 200 | 192.168.1.2:443 | https://safebrowsingohttpgateway.googleapis.com/v1/ohttp/hpkekeyconfig?key=AIzaSyA2KlwBX3mkFo30om9LUFYQhpqLoa_BNhE | unknown | — | — | — |
332 | chrome.exe | POST | 200 | 192.168.1.2:443 | https://accounts.google.com/ListAccounts?gpsia=1&source=ChromiumBrowser&json=standard | unknown | — | — | whitelisted |
332 | chrome.exe | GET | 302 | 104.18.94.41:443 | https://challenges.cloudflare.com/turnstile/v0/api.js | US | — | — | whitelisted |
332 | chrome.exe | GET | 302 | 192.168.1.2:443 | https://challenges.cloudflare.com/turnstile/v0/api.js | unknown | — | — | — |
— | — | HEAD | 200 | 192.168.1.2:443 | https://fs.microsoft.com/fs/windows/config.json | unknown | — | — | — |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
1380 | svchost.exe | 95.101.9.134:80 | — | AKAMAI-ASN1 | NL | whitelisted |
— | — | 48.209.138.168:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
— | — | 52.110.17.48:443 | officeclient.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
3248 | svchost.exe | 199.232.214.172:80 | ctldl.windowsupdate.com | FASTLY | US | whitelisted |
332 | chrome.exe | 142.251.20.138:80 | clients2.google.com | GOOGLE | US | whitelisted |
332 | chrome.exe | 192.178.183.100:443 | clientservices.googleapis.com | GOOGLE | US | whitelisted |
332 | chrome.exe | 172.217.117.4:443 | safebrowsingohttpgateway.googleapis.com | GOOGLE | US | whitelisted |
332 | chrome.exe | 142.251.127.84:443 | accounts.google.com | GOOGLE | US | whitelisted |
332 | chrome.exe | 102.214.8.120:80 | sadram.co.za | Absolute-Hosting-PTY-LTD-AS | ZA | unknown |
7992 | svchost.exe | 23.197.142.186:443 | fs.microsoft.com | AKAMAI-AS | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
officeclient.microsoft.com |
| whitelisted |
ctldl.windowsupdate.com |
| whitelisted |
google.com |
| whitelisted |
clients2.google.com |
| whitelisted |
clientservices.googleapis.com |
| whitelisted |
safebrowsingohttpgateway.googleapis.com |
| whitelisted |
sadram.co.za |
| unknown |
accounts.google.com |
| whitelisted |
fs.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
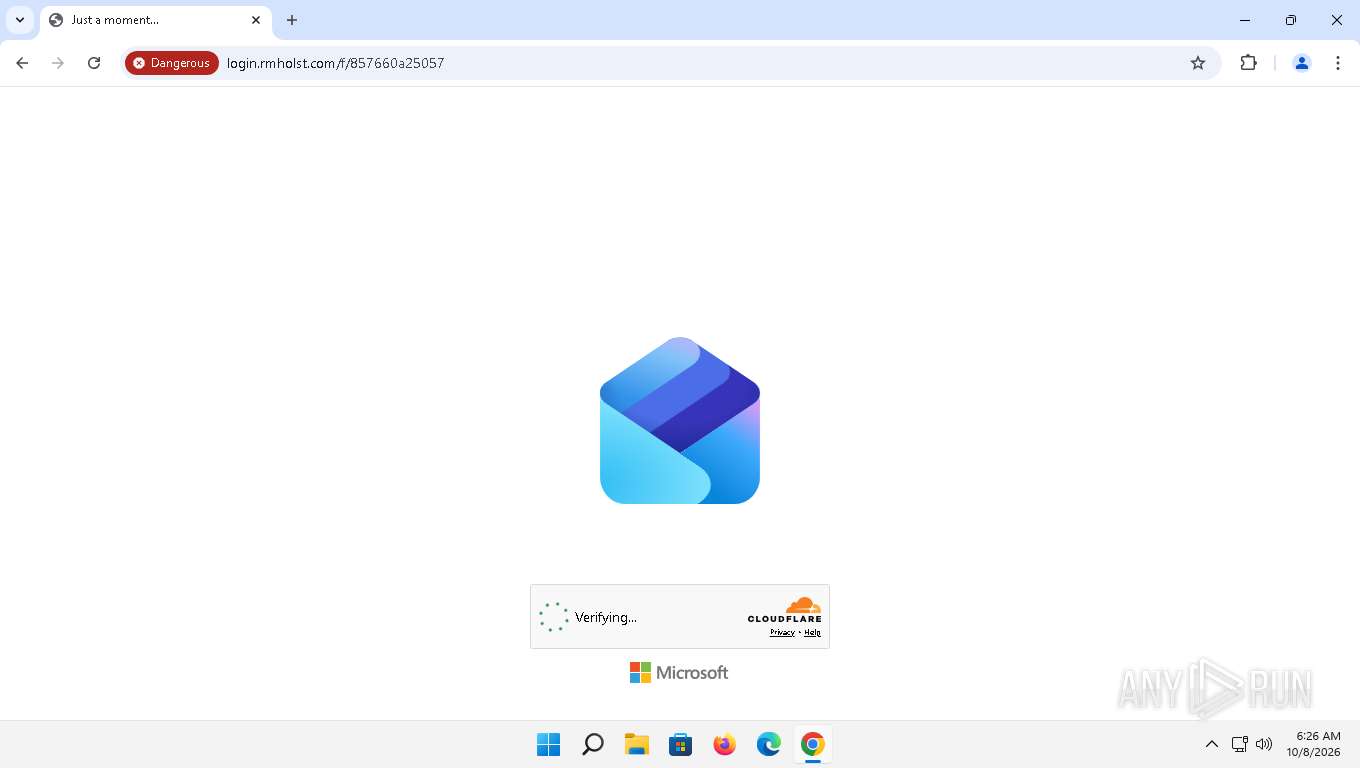
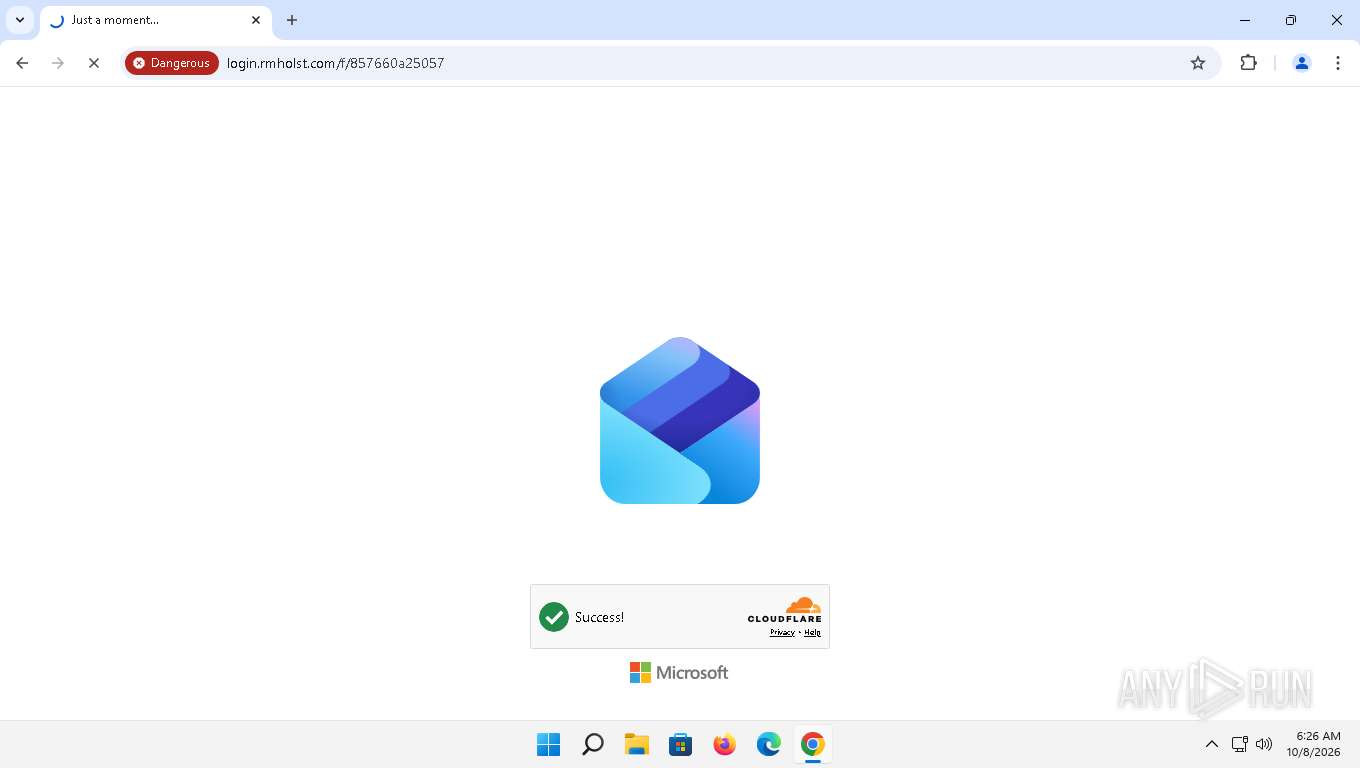
332 | chrome.exe | Not Suspicious Traffic | INFO [ANY.RUN] Cloudflare turnstile CAPTCHA challenge |
1380 | svchost.exe | Misc activity | ET INFO Microsoft Connection Test |
332 | chrome.exe | Misc activity | INFO [ANY.RUN] Google STUN server DNS query observed (stun .l .google .com) |
332 | chrome.exe | Not Suspicious Traffic | INFO [ANY.RUN] Cloudflare turnstile CAPTCHA challenge |
332 | chrome.exe | Misc activity | INFO [ANY.RUN] Google STUN server DNS query observed (stun .l .google .com) |
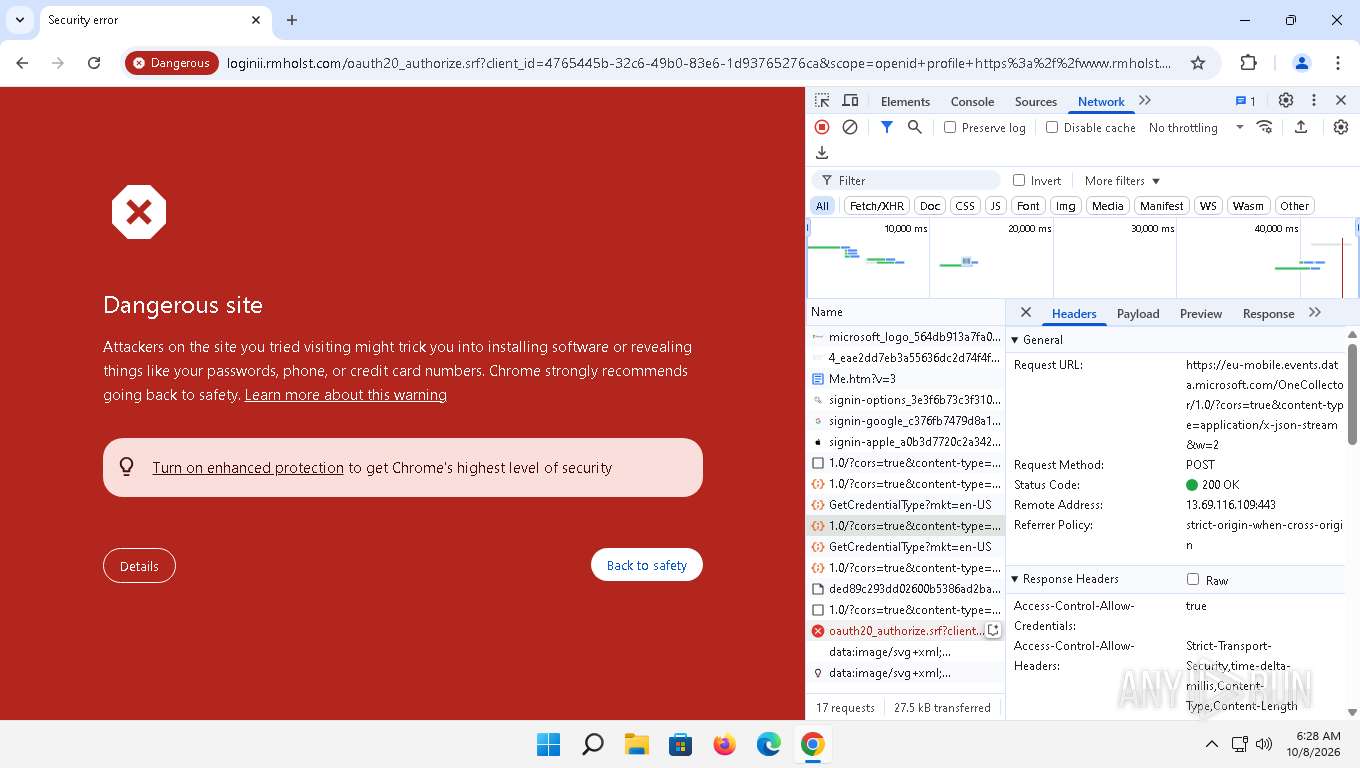
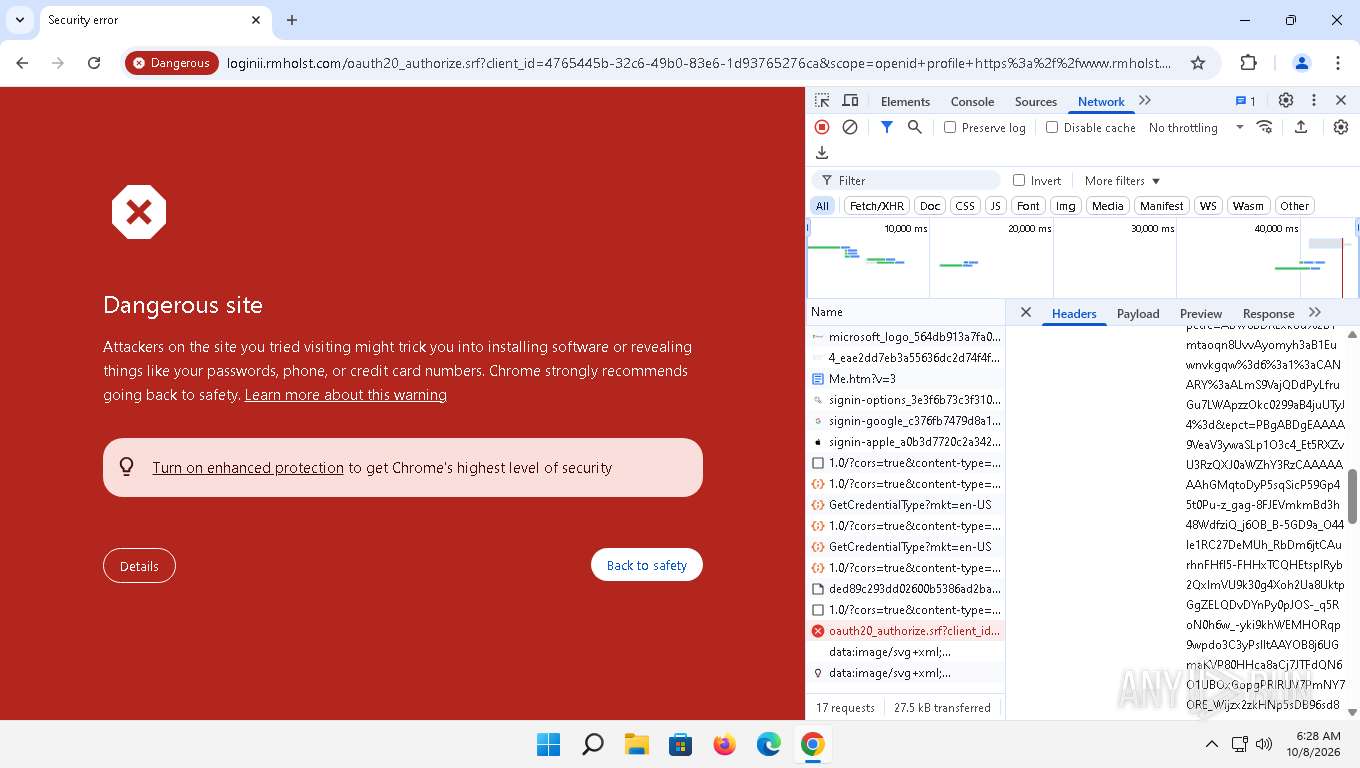
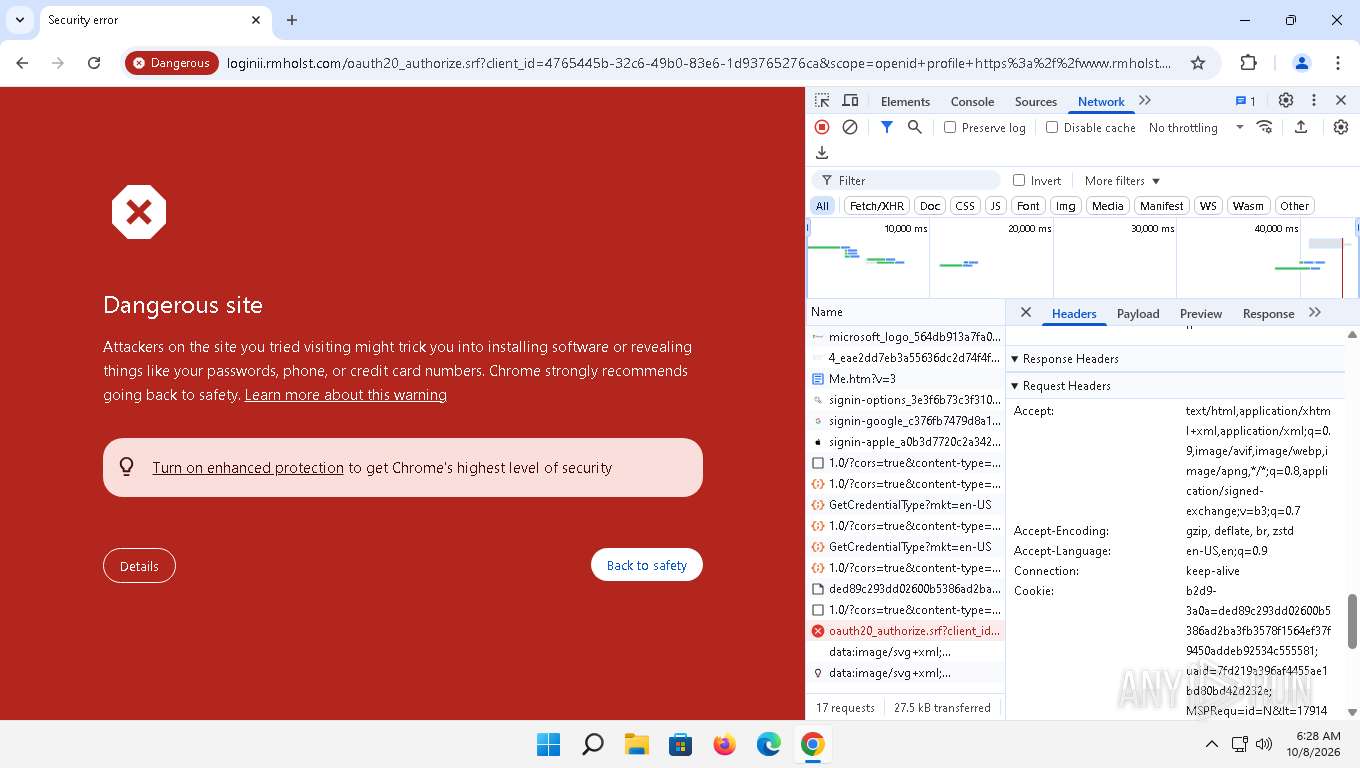
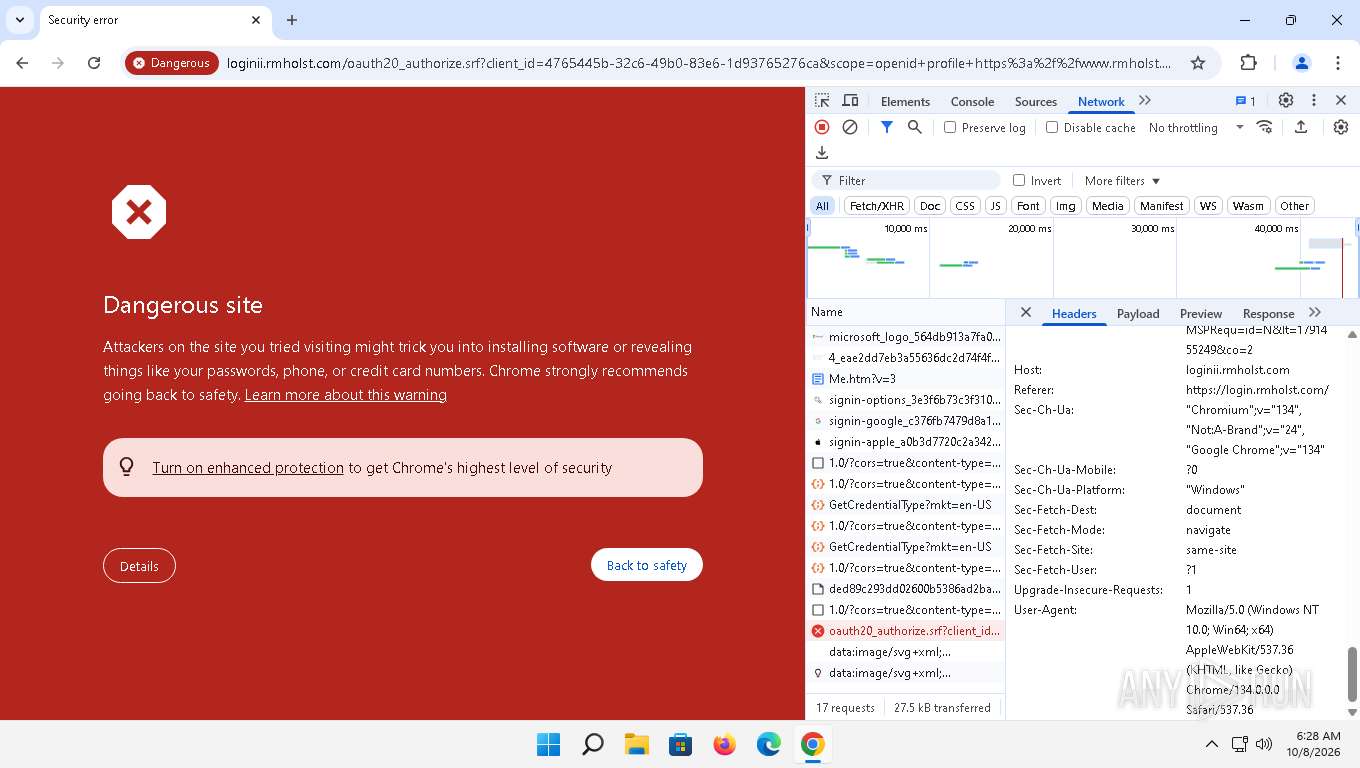
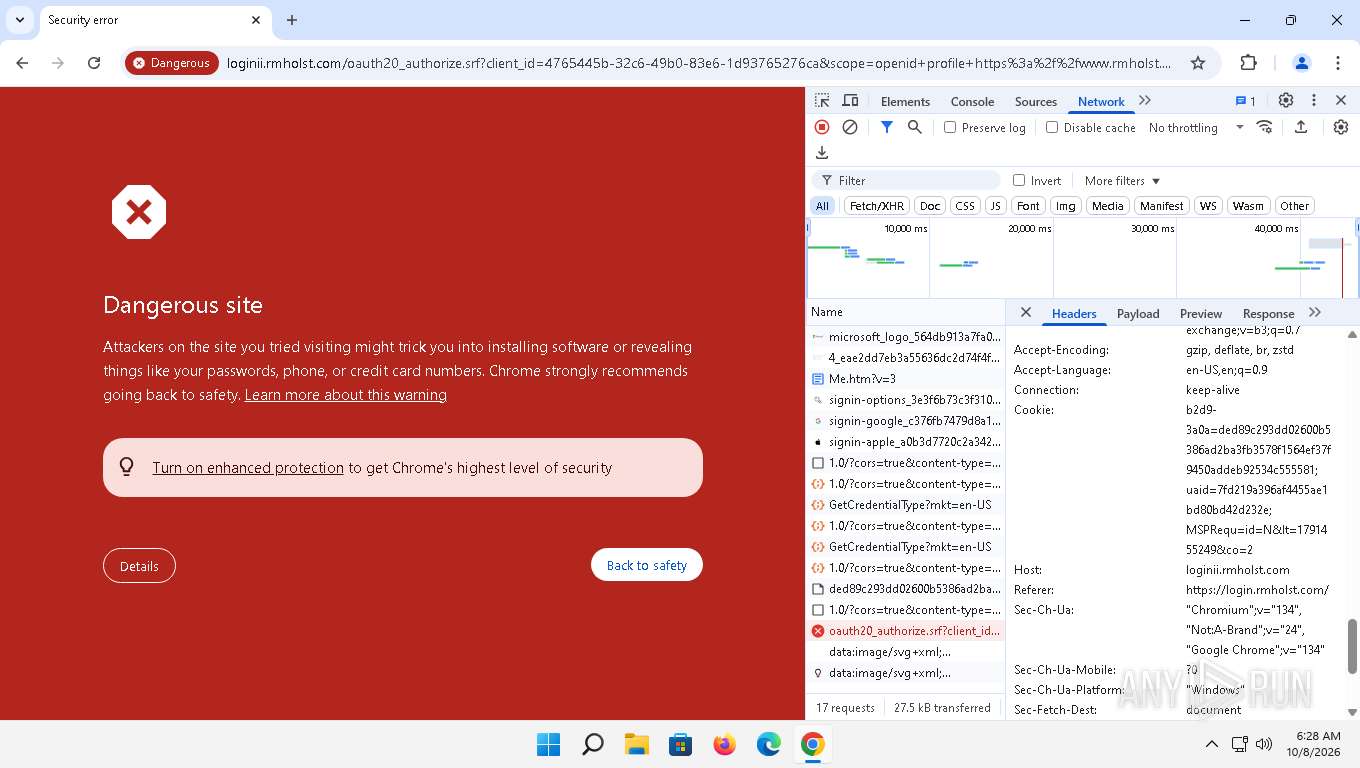
— | — | Possible Social Engineering Attempted | PHISHING [ANY.RUN] Evilginx-family phishkit cookie observed |
332 | chrome.exe | Possible Social Engineering Attempted | PHISHING [ANY.RUN] Evilginx-family phishkit cookie observed |
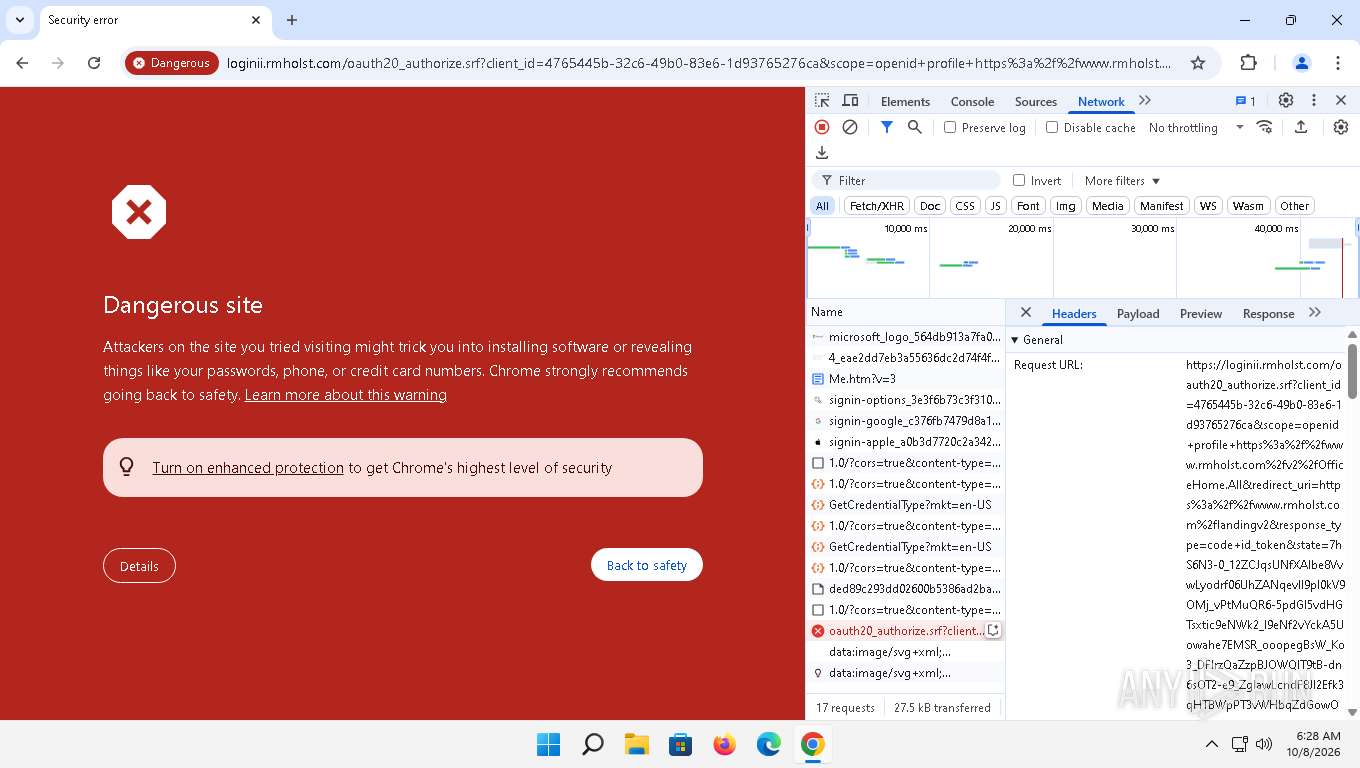
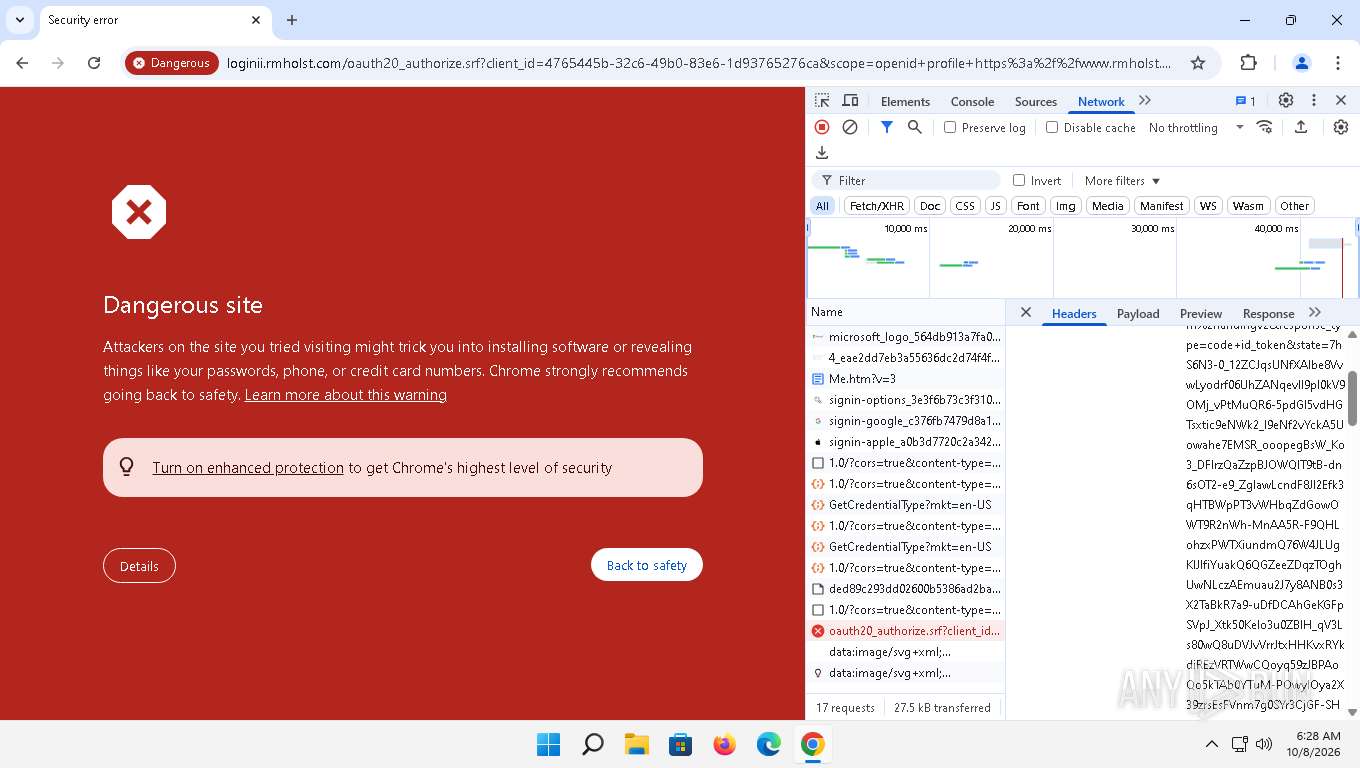
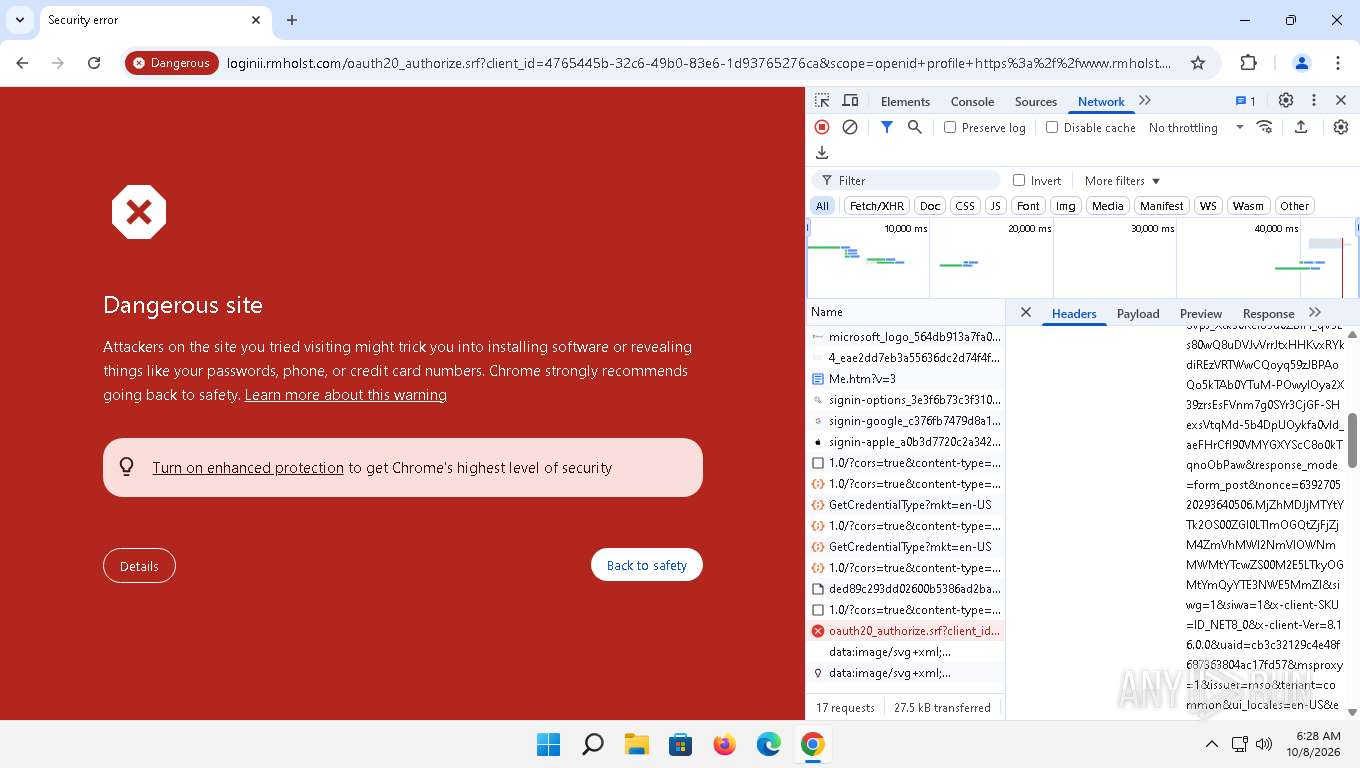
— | — | Possible Social Engineering Attempted | PHISHING [ANY.RUN] Microsoft Authorization URL Observed on Fake Domain (/common/oauth2/) |
332 | chrome.exe | Possible Social Engineering Attempted | PHISHING [ANY.RUN] Microsoft Authorization URL Observed on Fake Domain (/common/oauth2/) |
— | — | Possible Social Engineering Attempted | PHISHING [ANY.RUN] Microsoft Authorization URL Observed on Fake Domain (/common/oauth2/) |
Process | Message |
|---|---|
MoUsoCoreWorker.exe | Populating UpdatePolicy AllowList |
MoUsoCoreWorker.exe | All policies are allowed
|
MoUsoCoreWorker.exe | SKU MDM licensing allow list string from SLAPI:
|
MoUsoCoreWorker.exe | AboveLock|Accounts|ActiveXControls|ADMXIngest|AllowMessageSync|AppHVSI|ApplicationDefaults|AllowAllTrustedApps|AllowAppStoreAutoUpdate|AllowAutomaticAppArchiving|AllowDeveloperUnlock|AllowGameDVR|AllowSharedUserAppData|ApplicationRestrictions|Audit|ConfigureChatIcon|LaunchAppAfterLogOn|MSIAllowUserControlOverInstall|MSIAlwaysInstallWithElevatedPrivileges|RestrictAppDataToSystemVolume|RestrictAppToSystemVolume|AppRuntime|AttachmentManager|Authentication|Autoplay|BitLocker|BITS|Bluetooth|Browser|Camera|Cellular|Connectivity|ControlPolicyConflict|CredentialProviders|CredentialsDelegation|CredentialsUI|Cryptography|DataProtection|DataUsage|Defender|DeliveryOptimization|Desktop|ConfigureSystemGuardLaunch|EnableVirtualizationBasedSecurity|DeviceHealthMonitoring|DeviceInstallation|DeviceLock|Display|DmaGuard|ErrorReporting|Eap|Education|EnterpriseCloudPrint|EventLogService|AllowClipboardHistory|AllowCopyPaste|AllowCortana|AllowDeviceDiscovery|AllowManualMDMUnenrollment|AllowSaveAsOfOfficeFiles|AllowScreenCapture|AllowSharingOfOfficeFiles|AllowSIMErrorDialogPromptWhenNoSIM|AllowSyncMySettings|AllowTailoredExperiencesWithDiagnosticData|AllowTaskSwitcher|AllowThirdPartySuggestionsInWindowsSpotlight|AllowVoiceRecording|DoNotShowFeedbackNotifications|DoNotSyncBrowserSettings|AllowFindMyDevice|ExploitGuard|Feeds|FileExplorer|Games|Handwriting|HumanPresence|InternetExplorer|Kerberos|KioskBrowser|Knobs|LanmanWorkstation|Licensing|LocalPoliciesSecurityOptions|LocalUsersAndGroups|Lockdown|Maps|MemoryDump|MSSecurityGuide|MSSLegacy|Multitasking|NetworkIsolation|NetworkListManager|NewsAndInterests|Notifications|OneDrive|Power|Printers|Privacy|RemoteAssistance|RemoteDesktopServices|RemoteDesktop|RemoteManagement|RemoteProcedureCall|RemoteShell|RestrictedGroups|Search|Security|Settings|SmartScreen|Speech|Start|Storage|System|SystemServices|TaskManager|TaskScheduler|TenantRestrictions|TextInput|TimeLanguageSettings|Troubleshooting|Update|UserRights|VirtualizationBasedTechnology|WiFi|WindowsLogon|WirelessDisplay|Location|WindowsAutopilot|WindowsConnectionManager|WindowsDefenderSecurityCenter|WindowsInkWorkspace|WindowsPowerShell|WindowsSandbox|WiredNetwork|ADMX_ |
MoUsoCoreWorker.exe | |
MoUsoCoreWorker.exe | Populating EnterprisePolicy AllowList |
MoUsoCoreWorker.exe | SKU MDM licensing allow list string from SLAPI:
|
MoUsoCoreWorker.exe | All policies are allowed
|
MoUsoCoreWorker.exe | AboveLock|Accounts|ActiveXControls|ADMXIngest|AllowMessageSync|AppHVSI|ApplicationDefaults|AllowAllTrustedApps|AllowAppStoreAutoUpdate|AllowAutomaticAppArchiving|AllowDeveloperUnlock|AllowGameDVR|AllowSharedUserAppData|ApplicationRestrictions|Audit|ConfigureChatIcon|LaunchAppAfterLogOn|MSIAllowUserControlOverInstall|MSIAlwaysInstallWithElevatedPrivileges|RestrictAppDataToSystemVolume|RestrictAppToSystemVolume|AppRuntime|AttachmentManager|Authentication|Autoplay|BitLocker|BITS|Bluetooth|Browser|Camera|Cellular|Connectivity|ControlPolicyConflict|CredentialProviders|CredentialsDelegation|CredentialsUI|Cryptography|DataProtection|DataUsage|Defender|DeliveryOptimization|Desktop|ConfigureSystemGuardLaunch|EnableVirtualizationBasedSecurity|DeviceHealthMonitoring|DeviceInstallation|DeviceLock|Display|DmaGuard|ErrorReporting|Eap|Education|EnterpriseCloudPrint|EventLogService|AllowClipboardHistory|AllowCopyPaste|AllowCortana|AllowDeviceDiscovery|AllowManualMDMUnenrollment|AllowSaveAsOfOfficeFiles|AllowScreenCapture|AllowSharingOfOfficeFiles|AllowSIMErrorDialogPromptWhenNoSIM|AllowSyncMySettings|AllowTailoredExperiencesWithDiagnosticData|AllowTaskSwitcher|AllowThirdPartySuggestionsInWindowsSpotlight|AllowVoiceRecording|DoNotShowFeedbackNotifications|DoNotSyncBrowserSettings|AllowFindMyDevice|ExploitGuard|Feeds|FileExplorer|Games|Handwriting|HumanPresence|InternetExplorer|Kerberos|KioskBrowser|Knobs|LanmanWorkstation|Licensing|LocalPoliciesSecurityOptions|LocalUsersAndGroups|Lockdown|Maps|MemoryDump|MSSecurityGuide|MSSLegacy|Multitasking|NetworkIsolation|NetworkListManager|NewsAndInterests|Notifications|OneDrive|Power|Printers|Privacy|RemoteAssistance|RemoteDesktopServices|RemoteDesktop|RemoteManagement|RemoteProcedureCall|RemoteShell|RestrictedGroups|Search|Security|Settings|SmartScreen|Speech|Start|Storage|System|SystemServices|TaskManager|TaskScheduler|TenantRestrictions|TextInput|TimeLanguageSettings|Troubleshooting|Update|UserRights|VirtualizationBasedTechnology|WiFi|WindowsLogon|WirelessDisplay|Location|WindowsAutopilot|WindowsConnectionManager|WindowsDefenderSecurityCenter|WindowsInkWorkspace|WindowsPowerShell|WindowsSandbox|WiredNetwork|ADMX_ |
MoUsoCoreWorker.exe | |