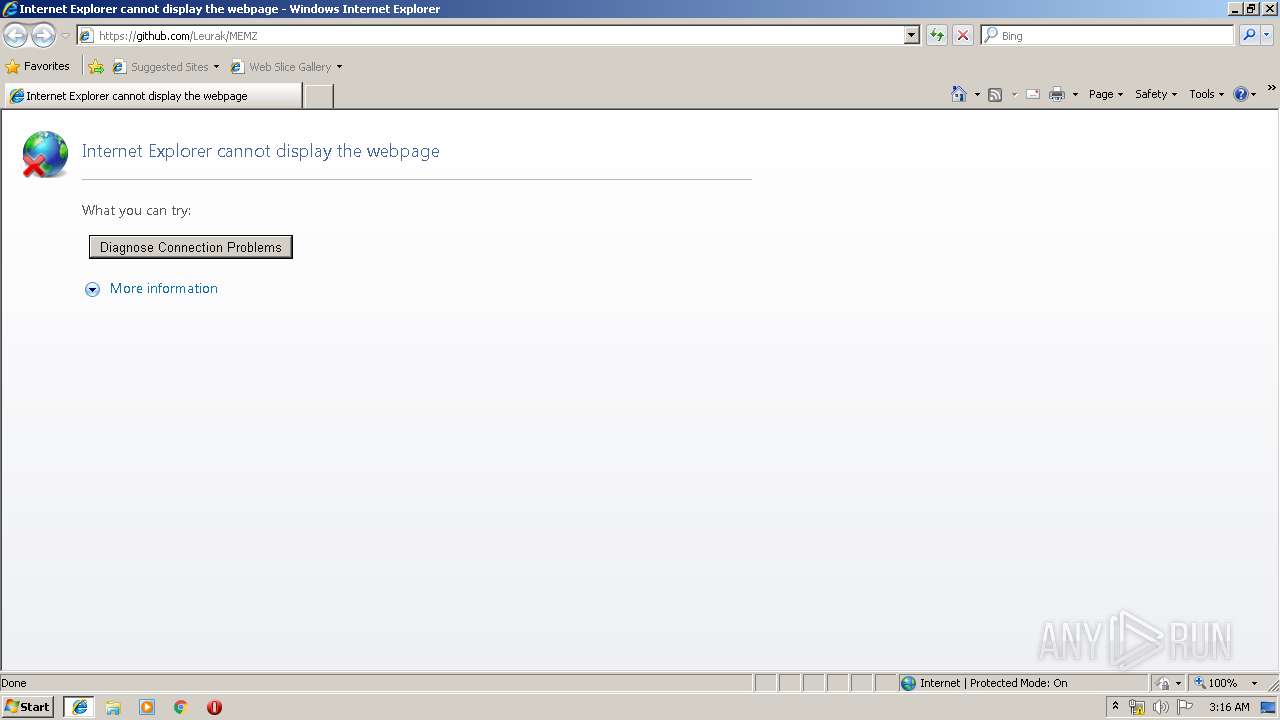
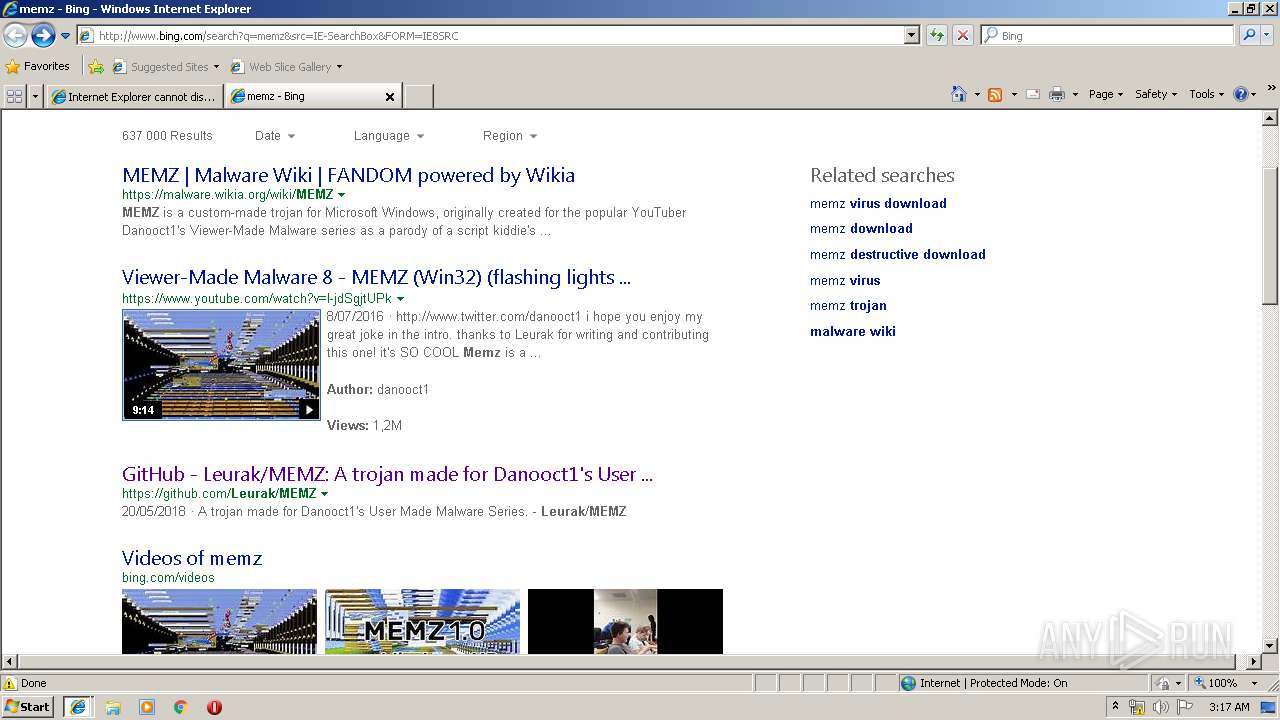
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| URL: | https://github.com/Leurak/MEMZ |
| Full analysis: | https://app.any.run/tasks/858ee9bd-b4a4-41b1-b220-27f47cc479e6 |
| Verdict: | No threats detected |
| Analysis date: | May 15, 2019, 02:16:22 |
| OS: | Windows 7 Professional Service Pack 1 (build: 7601, 32 bit) |
| Indicators: | |
| MD5: | BE3B5D2AFAFB3CCE220A311A503F941A |
| SHA1: | 61A1CD9245BF2BB7AEB471A4EB3EF8AB504BA74D |
| SHA256: | 2CF415A0839D3C606802B3BB295F9F6042304D2BD86D3DB59482C0A63556F8E2 |
| SSDEEP: | 3:N8tEd8logi:2uul9i |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 276 | "C:\Program Files\Internet Explorer\iexplore.exe" SCODEF:3324 CREDAT:71937 | C:\Program Files\Internet Explorer\iexplore.exe | iexplore.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Internet Explorer Exit code: 0 Version: 8.00.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 3152 | "C:\Program Files\Internet Explorer\iexplore.exe" SCODEF:3324 CREDAT:6403 | C:\Program Files\Internet Explorer\iexplore.exe | iexplore.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Internet Explorer Exit code: 0 Version: 8.00.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| 3324 | "C:\Program Files\Internet Explorer\iexplore.exe" -nohome | C:\Program Files\Internet Explorer\iexplore.exe | explorer.exe | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Internet Explorer Exit code: 0 Version: 8.00.7600.16385 (win7_rtm.090713-1255) Modules
| |||||||||||||||
| (PID) Process: | (3324) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Main |
| Operation: | write | Name: | CompatibilityFlags |
Value: 0 | |||
| (PID) Process: | (3324) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | UNCAsIntranet |
Value: 0 | |||
| (PID) Process: | (3324) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | AutoDetect |
Value: 1 | |||
| (PID) Process: | (3324) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\Zones |
| Operation: | write | Name: | SecuritySafe |
Value: 1 | |||
| (PID) Process: | (3324) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings |
| Operation: | write | Name: | ProxyEnable |
Value: 0 | |||
| (PID) Process: | (3324) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\Connections |
| Operation: | write | Name: | SavedLegacySettings |
Value: 4600000071000000010000000000000000000000000000000000000000000000C0E333BBEAB1D301000000000000000000000000020000001700000000000000FE800000000000007D6CB050D9C573F70B000000000000006D00330032005C004D00530049004D004700330032002E0064006C000100000004AA400014AA4000040000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000002000000C0A8016400000000000000000000000000000000000000000800000000000000805D3F00983740000008000002000000000000600000002060040000B8A94000020000008802000060040000B8A9400004000000F8010000B284000088B64000B84B400043003A000000000000000000000000000000000000000000 | |||
| (PID) Process: | (3324) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Recovery\Active |
| Operation: | write | Name: | {7DE26015-76B7-11E9-A09E-5254004A04AF} |
Value: 0 | |||
| (PID) Process: | (3324) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{2670000A-7350-4F3C-8081-5663EE0C6C49}\iexplore |
| Operation: | write | Name: | Type |
Value: 4 | |||
| (PID) Process: | (3324) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{2670000A-7350-4F3C-8081-5663EE0C6C49}\iexplore |
| Operation: | write | Name: | Count |
Value: 1 | |||
| (PID) Process: | (3324) iexplore.exe | Key: | HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Ext\Stats\{2670000A-7350-4F3C-8081-5663EE0C6C49}\iexplore |
| Operation: | write | Name: | Time |
Value: E307050003000F000200100031006300 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3324 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Content.IE5\H6QNMHE9\favicon[1].ico | — | |
MD5:— | SHA256:— | |||
| 3324 | iexplore.exe | C:\Users\admin\AppData\LocalLow\Microsoft\Internet Explorer\Services\search_{0633EE93-D776-472f-A0FF-E1416B8B2E3A}.ico | — | |
MD5:— | SHA256:— | |||
| 276 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Low\desktop.ini | ini | |
MD5:4A3DEB274BB5F0212C2419D3D8D08612 | SHA256:2842973D15A14323E08598BE1DFB87E54BF88A76BE8C7BC94C56B079446EDF38 | |||
| 3324 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Feeds Cache\desktop.ini | ini | |
MD5:4A3DEB274BB5F0212C2419D3D8D08612 | SHA256:2842973D15A14323E08598BE1DFB87E54BF88A76BE8C7BC94C56B079446EDF38 | |||
| 276 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Low\Content.IE5\desktop.ini | ini | |
MD5:4A3DEB274BB5F0212C2419D3D8D08612 | SHA256:2842973D15A14323E08598BE1DFB87E54BF88A76BE8C7BC94C56B079446EDF38 | |||
| 276 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Low\Content.IE5\2CIE88A7\desktop.ini | ini | |
MD5:4A3DEB274BB5F0212C2419D3D8D08612 | SHA256:2842973D15A14323E08598BE1DFB87E54BF88A76BE8C7BC94C56B079446EDF38 | |||
| 276 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Low\Content.IE5\WXCHHABC\desktop.ini | ini | |
MD5:4A3DEB274BB5F0212C2419D3D8D08612 | SHA256:2842973D15A14323E08598BE1DFB87E54BF88A76BE8C7BC94C56B079446EDF38 | |||
| 276 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Low\Content.IE5\LNXC975M\desktop.ini | ini | |
MD5:4A3DEB274BB5F0212C2419D3D8D08612 | SHA256:2842973D15A14323E08598BE1DFB87E54BF88A76BE8C7BC94C56B079446EDF38 | |||
| 276 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Low\Content.IE5\NUIISPTL\desktop.ini | ini | |
MD5:4A3DEB274BB5F0212C2419D3D8D08612 | SHA256:2842973D15A14323E08598BE1DFB87E54BF88A76BE8C7BC94C56B079446EDF38 | |||
| 276 | iexplore.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\Temporary Internet Files\Low\Content.IE5\index.dat | dat | |
MD5:8BFE5FC23208CD81779520912866FF04 | SHA256:6E11E01E523560A7E06AA5B987BD2044E04AB727BA0006170C96EFF125BD3571 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
3324 | iexplore.exe | GET | 200 | 204.79.197.200:80 | http://www.bing.com/favicon.ico | US | image | 237 b | whitelisted |
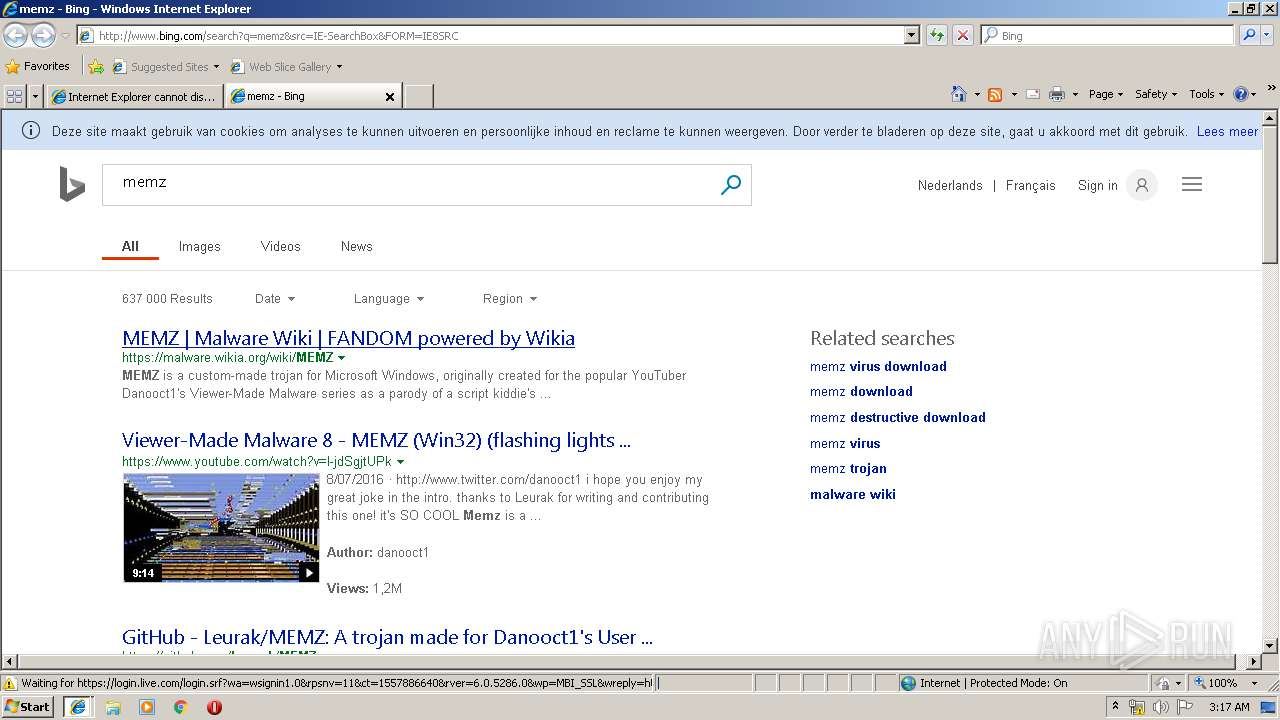
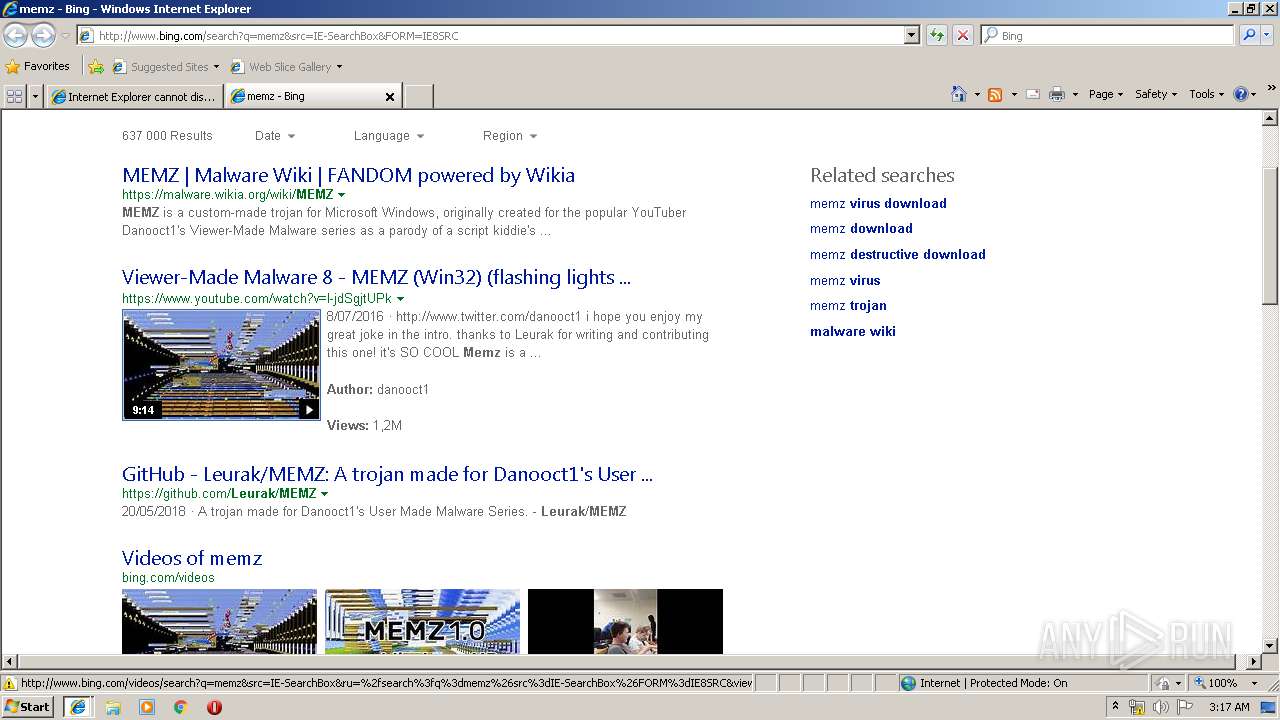
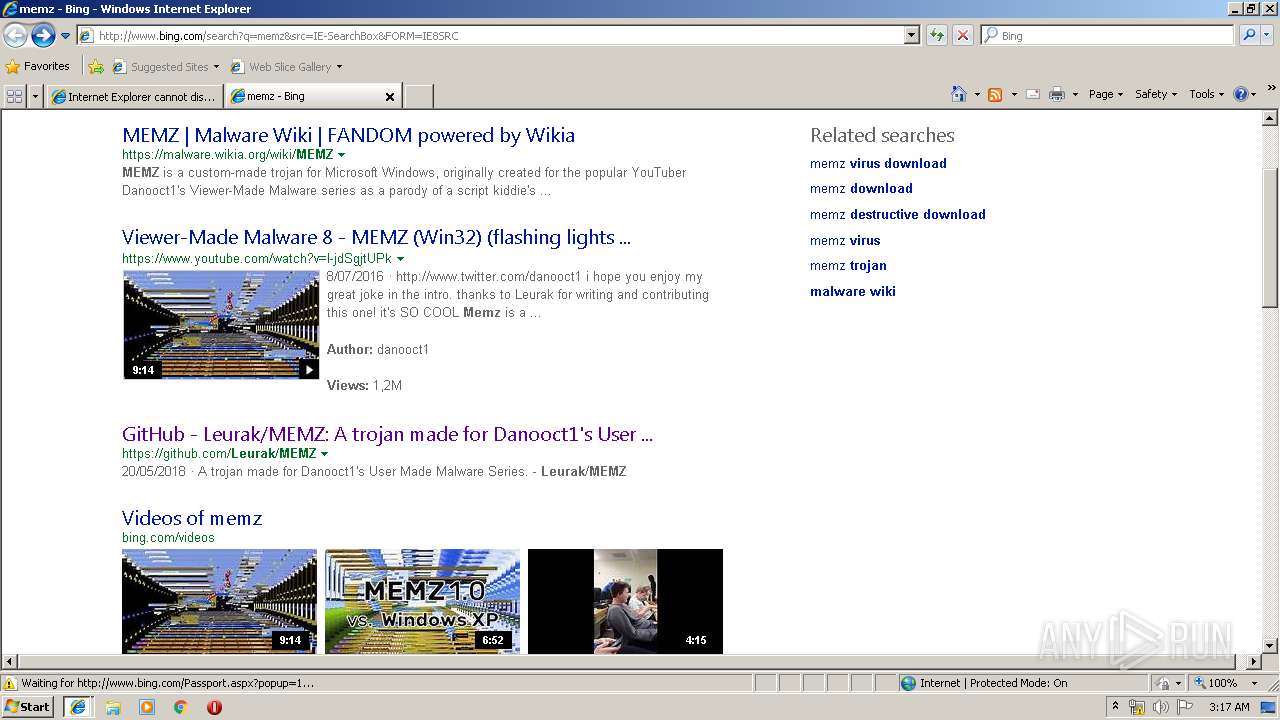
3152 | iexplore.exe | GET | 200 | 204.79.197.200:80 | http://www.bing.com/search?q=memz&src=IE-SearchBox&FORM=IE8SRC | US | html | 56.3 Kb | whitelisted |
3152 | iexplore.exe | GET | 200 | 204.79.197.200:80 | http://www.bing.com/sa/simg/SharedSpriteDesktopRewards_022118.png | US | image | 5.73 Kb | whitelisted |
3152 | iexplore.exe | GET | 200 | 204.79.197.200:80 | http://www.bing.com/fd/ls/l?IG=8FF997BE46A94B35872DE11E61A18781&CID=0389006103E0699D192F0D3C022A6851&Type=Event.CPT&DATA={"pp":{"S":"L","FC":78,"BC":203,"SE":-1,"TC":-1,"H":281,"BP":469,"CT":484,"IL":7},"ad":[-1,-1,1260,560,1260,498,0]}&P=SERP&DA=DUB02 | US | image | 5.73 Kb | whitelisted |
3152 | iexplore.exe | GET | 200 | 204.79.197.200:80 | http://www.bing.com/rb/5n/cj,nj/c44ec255/9a358300.js?bu=Eq0fzB_wHvUe4wSDH4Uf2B-HH44fmR_EH8Ifth-jHqwdrx2mHg | US | text | 4.95 Kb | whitelisted |
3152 | iexplore.exe | GET | 200 | 204.79.197.200:80 | http://www.bing.com/rs/6q/4N/cj,nj/347afee2/33036ea1.js | US | text | 1.77 Kb | whitelisted |
3152 | iexplore.exe | GET | 200 | 204.79.197.200:80 | http://www.bing.com/rb/6m/cj,nj/f28dadef/aea7e831.js?bu=AYUG | US | text | 174 b | whitelisted |
3152 | iexplore.exe | GET | 200 | 204.79.197.200:80 | http://www.bing.com/fd/ls/l?IG=8FF997BE46A94B35872DE11E61A18781&CID=0389006103E0699D192F0D3C022A6851&Type=Event.ClientInst&DATA=[{"T":"CI.GetError","FID":"CI","Name":"JSGetError","Text":"%27SVGElement%27%20is%20undefined","Meta":"http%3A//www.bing.com/search%3Fq%3Dmemz%26src%3DIE-SearchBox%26FORM%3DIE8SRC","Line":9258991,"Char":%20undefined}] | US | compressed | 773 b | whitelisted |
3152 | iexplore.exe | GET | 200 | 204.79.197.200:80 | http://www.bing.com/rb/16/cj,nj/1b7dfb88/cc8437ad.js?bu=DikuX29zd2tjZ68BswEuowEu | US | text | 7.54 Kb | whitelisted |
3152 | iexplore.exe | GET | 200 | 13.87.32.10:80 | http://21e7d85a789f82a48eec62f8c4029e79.clo.footprintdns.com/apc/trans.gif | GB | image | 43 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
3152 | iexplore.exe | 204.79.197.200:443 | www.bing.com | Microsoft Corporation | US | whitelisted |
3152 | iexplore.exe | 13.87.32.10:80 | 21e7d85a789f82a48eec62f8c4029e79.clo.footprintdns.com | Microsoft Corporation | GB | whitelisted |
3152 | iexplore.exe | 13.87.88.10:80 | 462e346f54ea63d7435f6ce0425fc487.clo.footprintdns.com | Microsoft Corporation | GB | whitelisted |
— | — | 13.107.42.10:80 | d379af6307f900718b675e5cedf290bb.clo.footprintdns.com | Microsoft Corporation | US | whitelisted |
3324 | iexplore.exe | 204.79.197.200:80 | www.bing.com | Microsoft Corporation | US | whitelisted |
3152 | iexplore.exe | 204.79.197.200:80 | www.bing.com | Microsoft Corporation | US | whitelisted |
— | — | 65.55.163.78:443 | login.live.com | Microsoft Corporation | US | whitelisted |
3152 | iexplore.exe | 204.79.197.222:80 | fp.msedge.net | Microsoft Corporation | US | whitelisted |
3152 | iexplore.exe | 140.82.118.4:443 | github.com | — | US | malicious |
3152 | iexplore.exe | 168.62.19.224:80 | 10b69ec6bb4b5d7d5c52d1825a85969e.clo.footprintdns.com | Microsoft Corporation | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
www.bing.com |
| whitelisted |
github.com |
| malicious |
login.live.com |
| whitelisted |
21e7d85a789f82a48eec62f8c4029e79.clo.footprintdns.com |
| unknown |
462e346f54ea63d7435f6ce0425fc487.clo.footprintdns.com |
| unknown |
d379af6307f900718b675e5cedf290bb.clo.footprintdns.com |
| unknown |
fp.msedge.net |
| whitelisted |
10b69ec6bb4b5d7d5c52d1825a85969e.clo.footprintdns.com |
| unknown |
a30f0c042b2f6341aca6bdea6d76f9e9.clo.footprintdns.com |
| unknown |
c8330a7c795b06bc9d18143d76f9cf3f.clo.footprintdns.com |
| unknown |