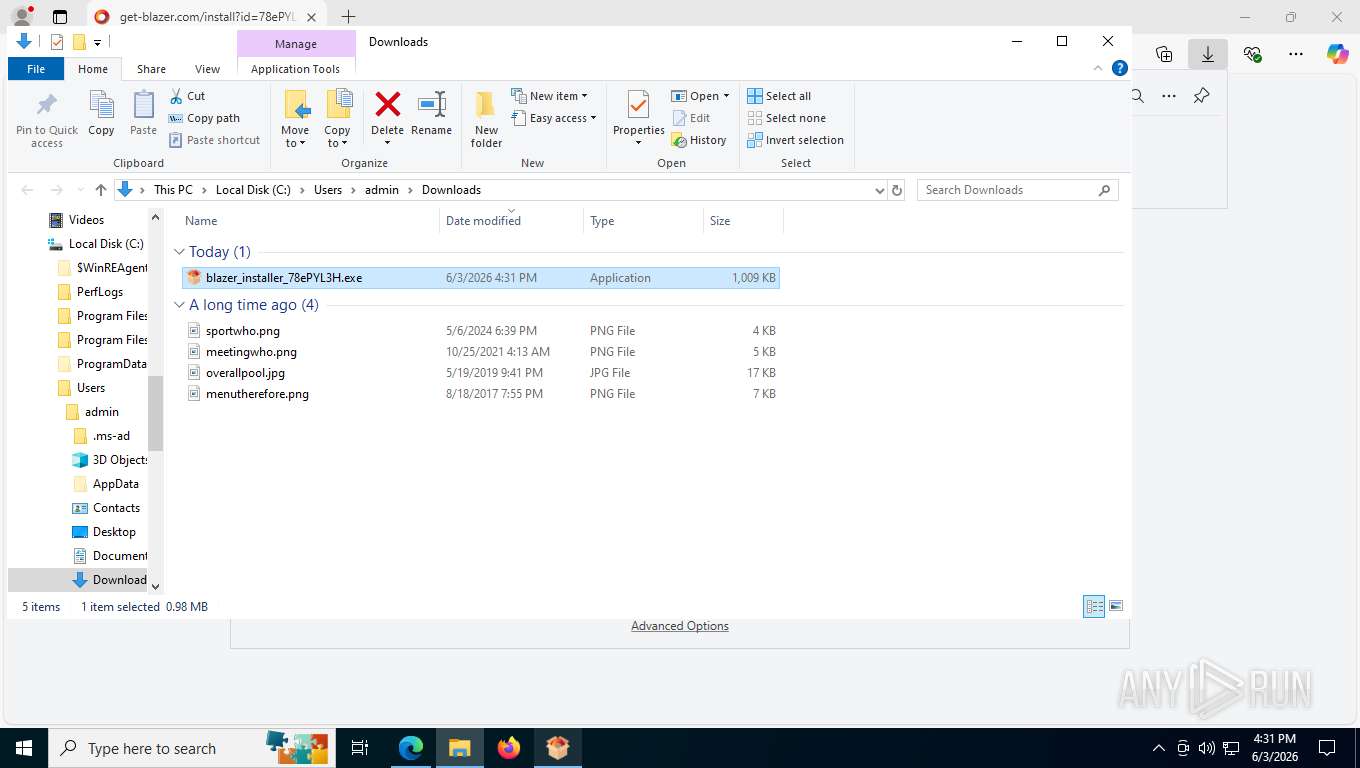
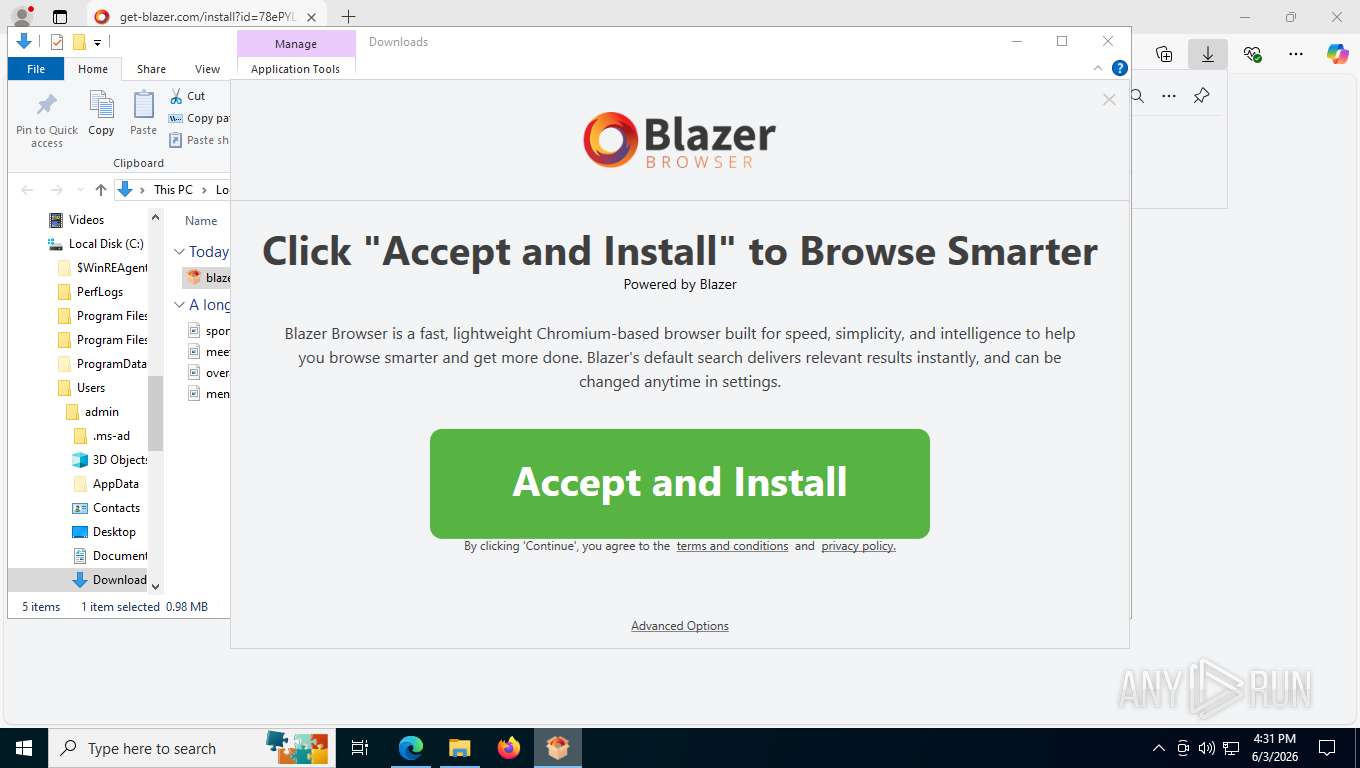
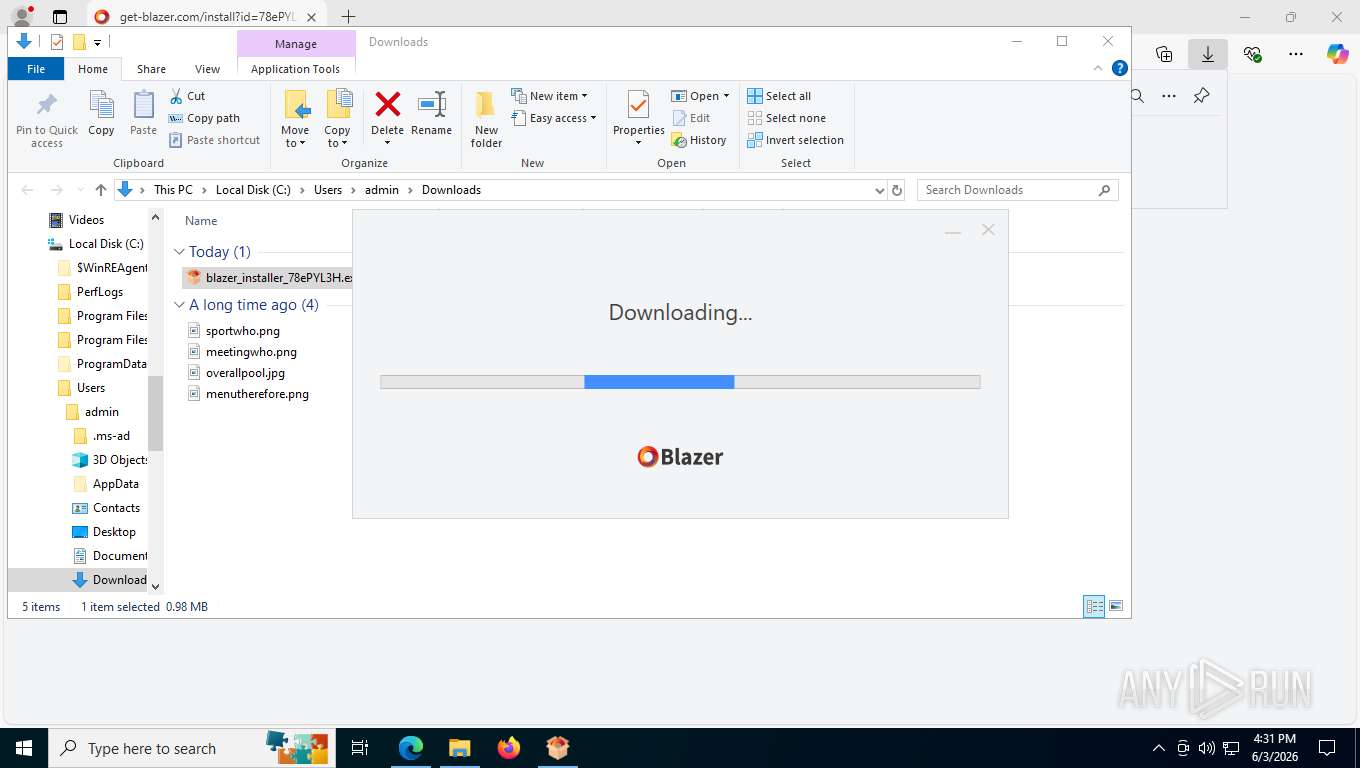
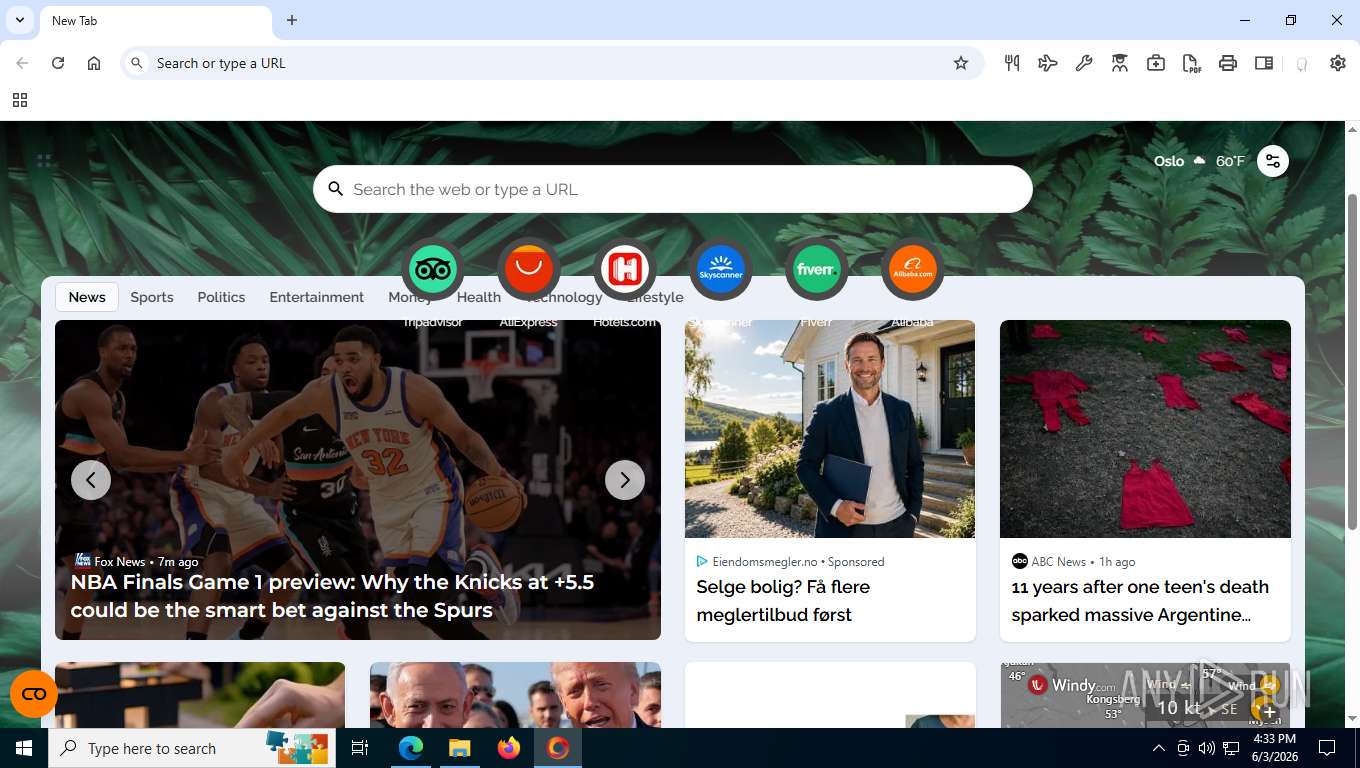
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
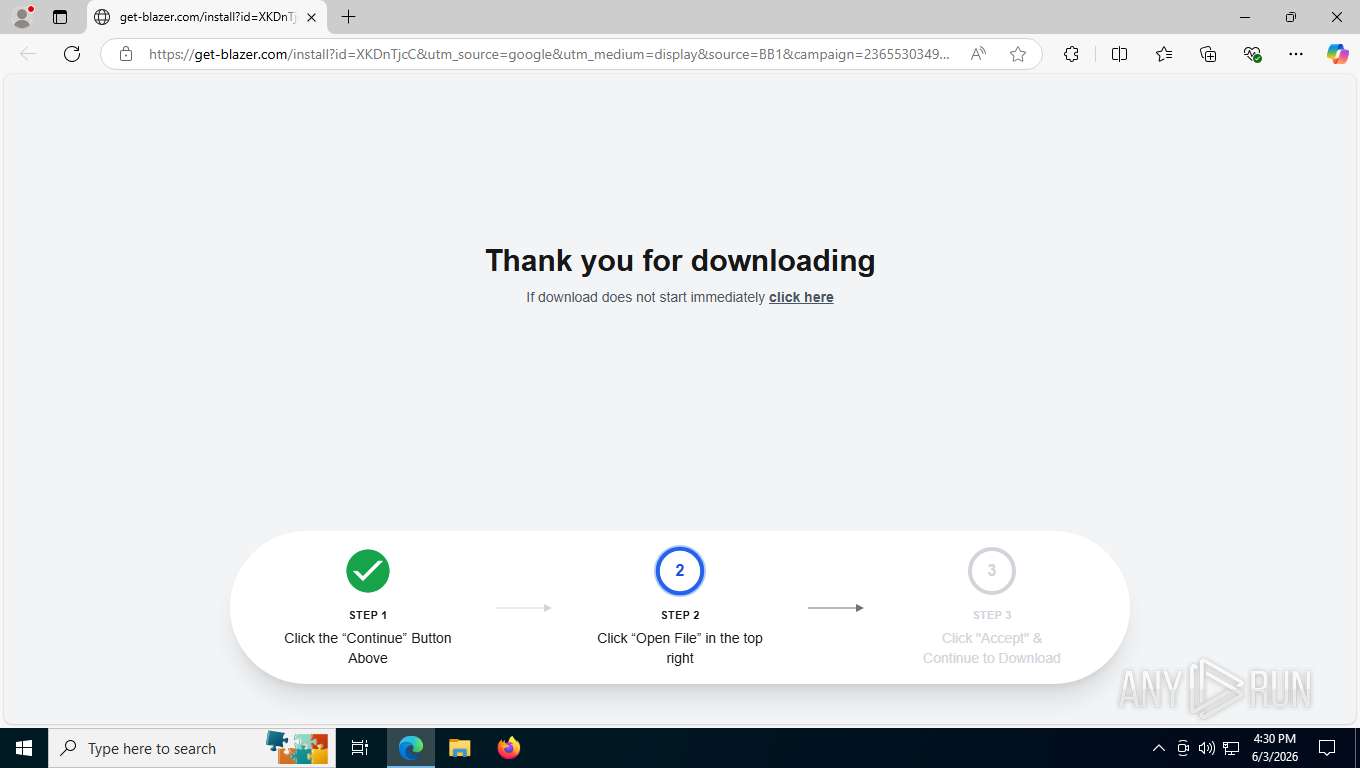
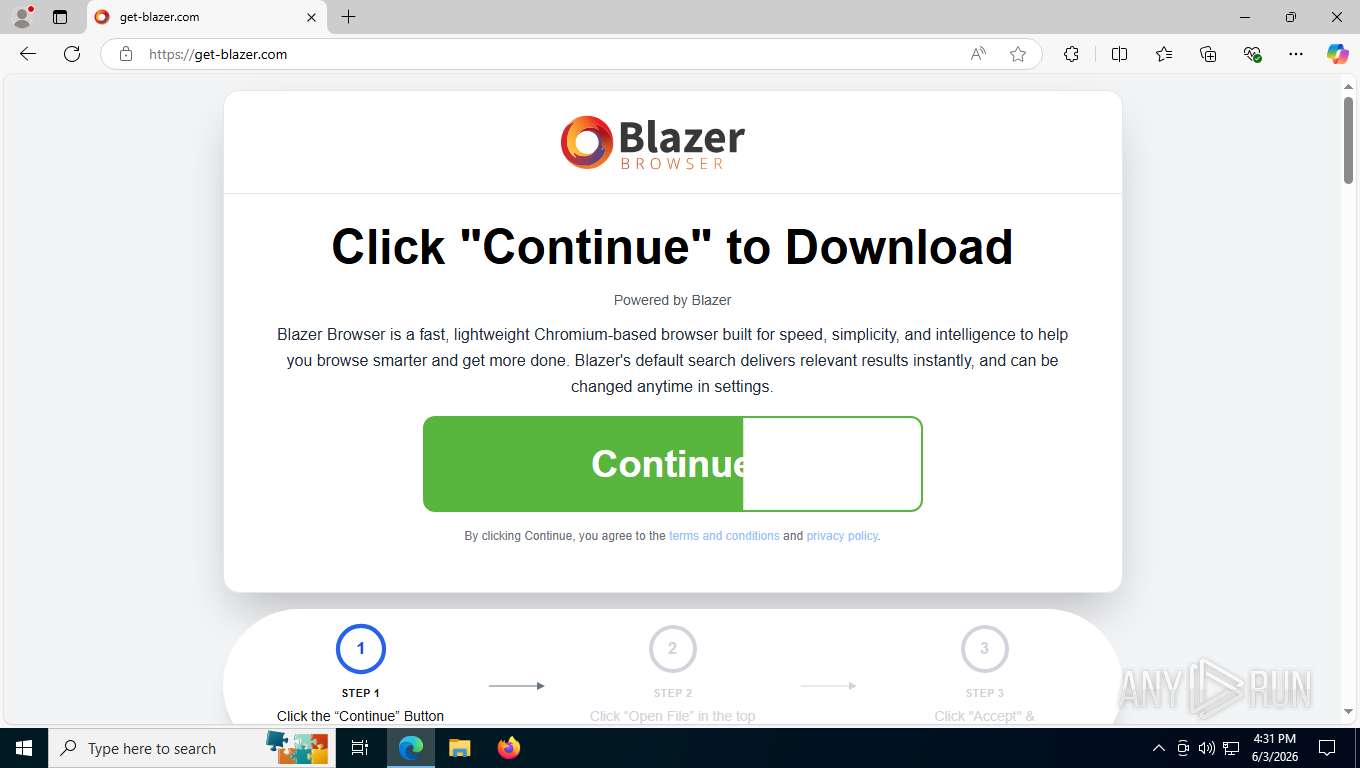
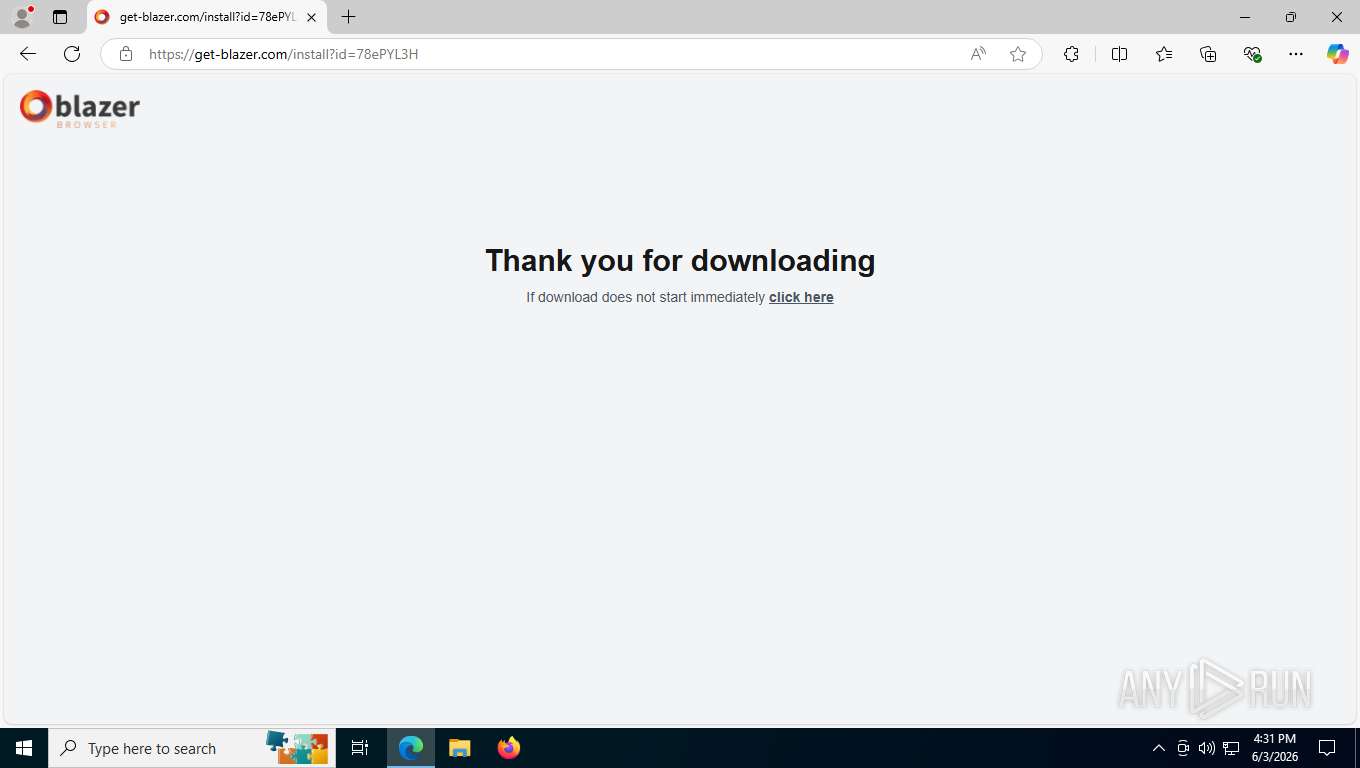
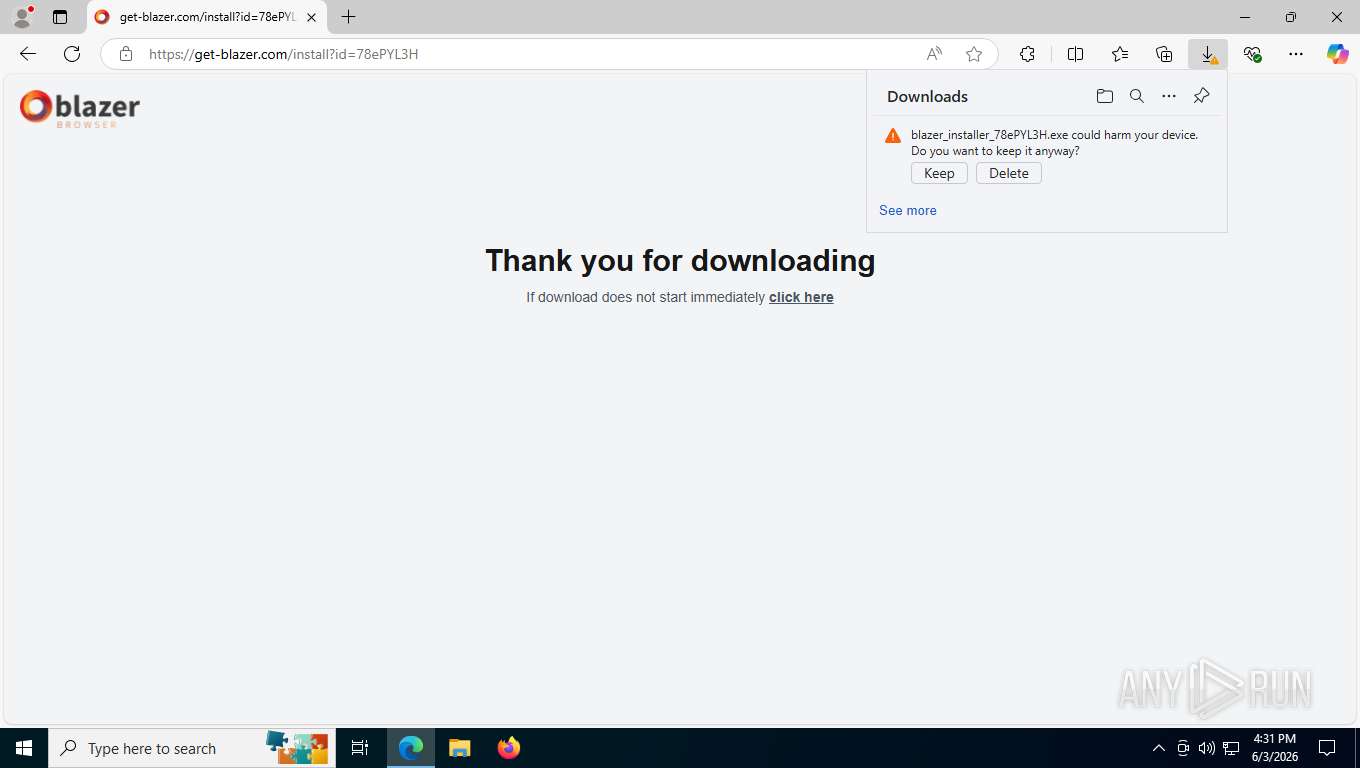
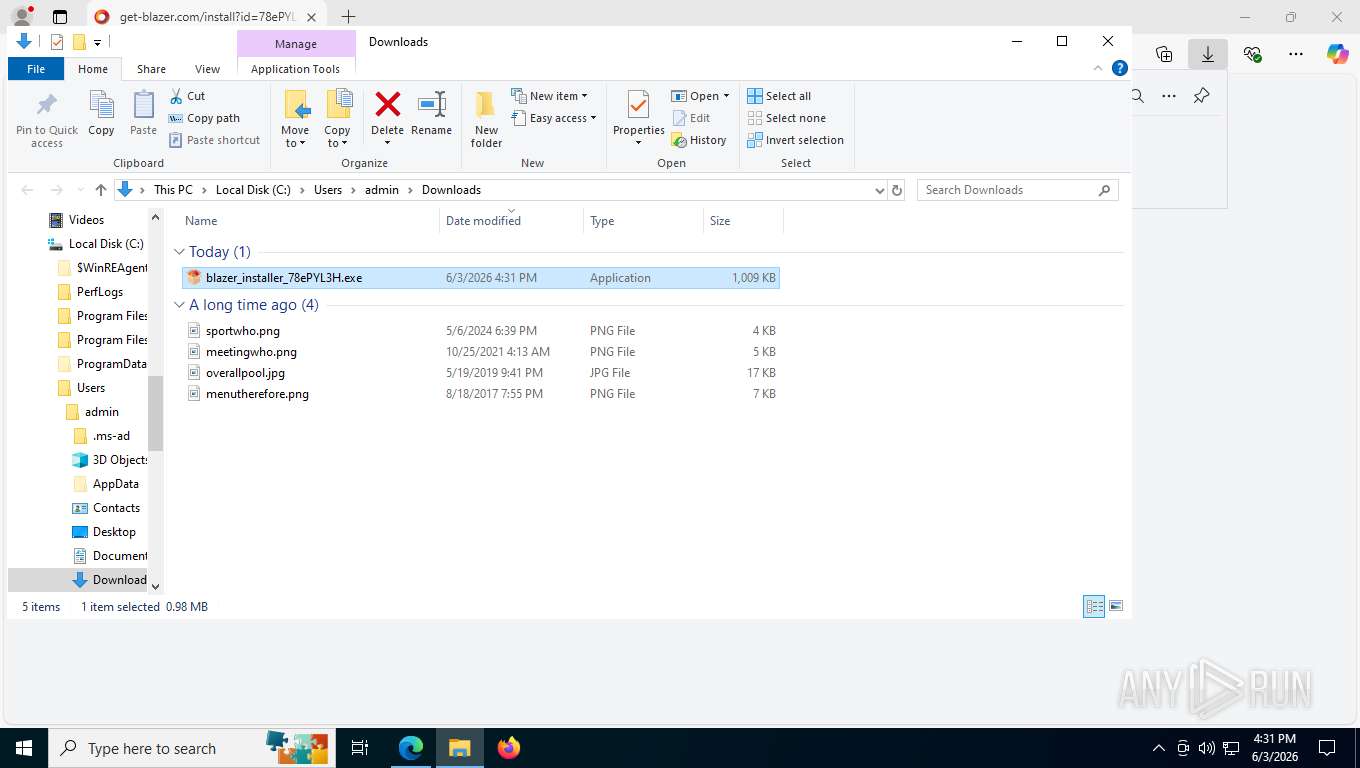
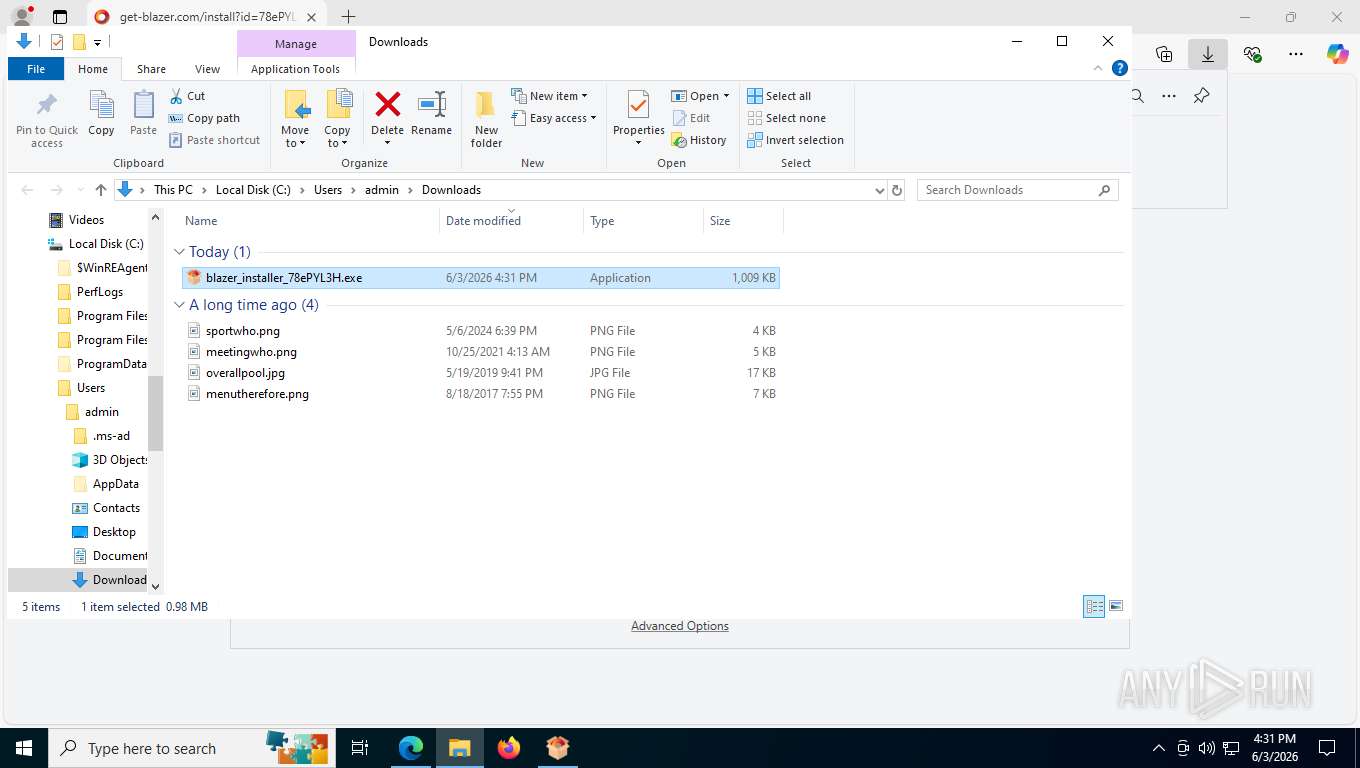
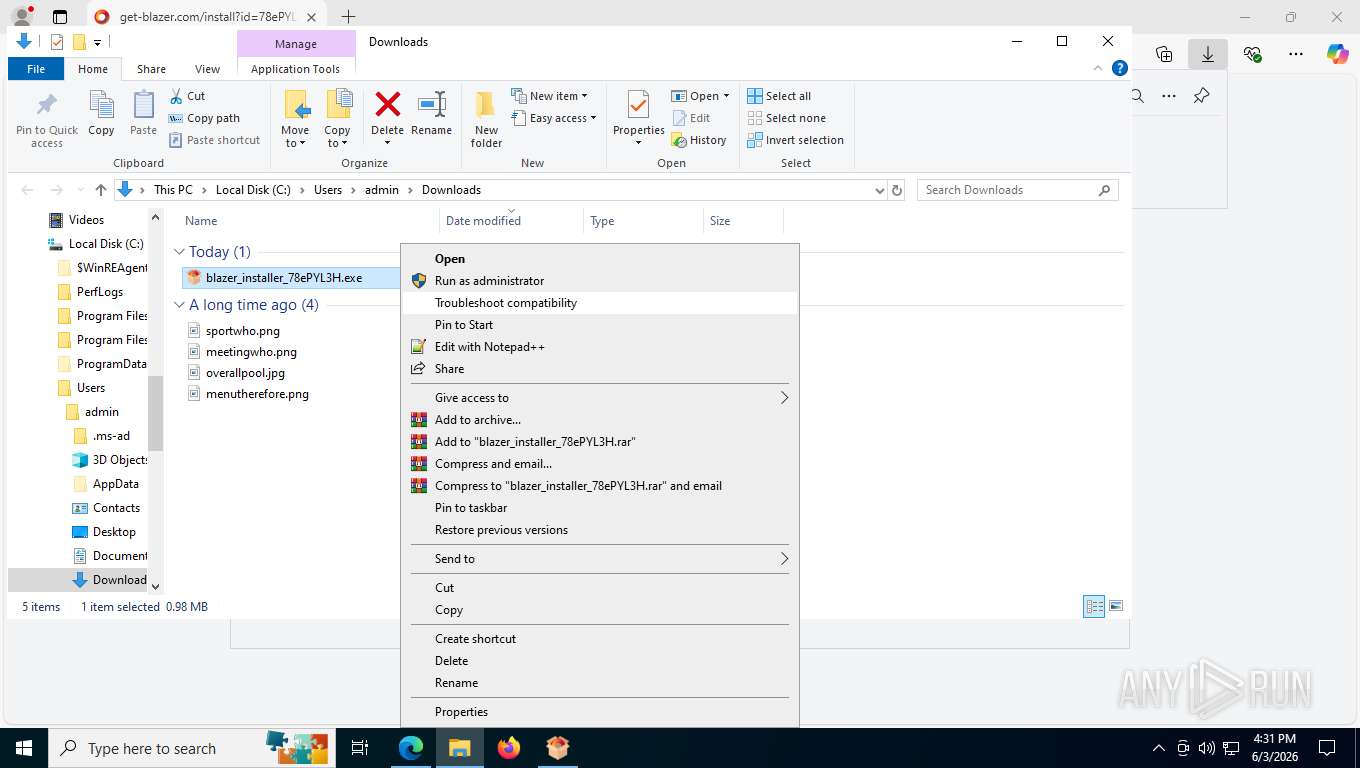
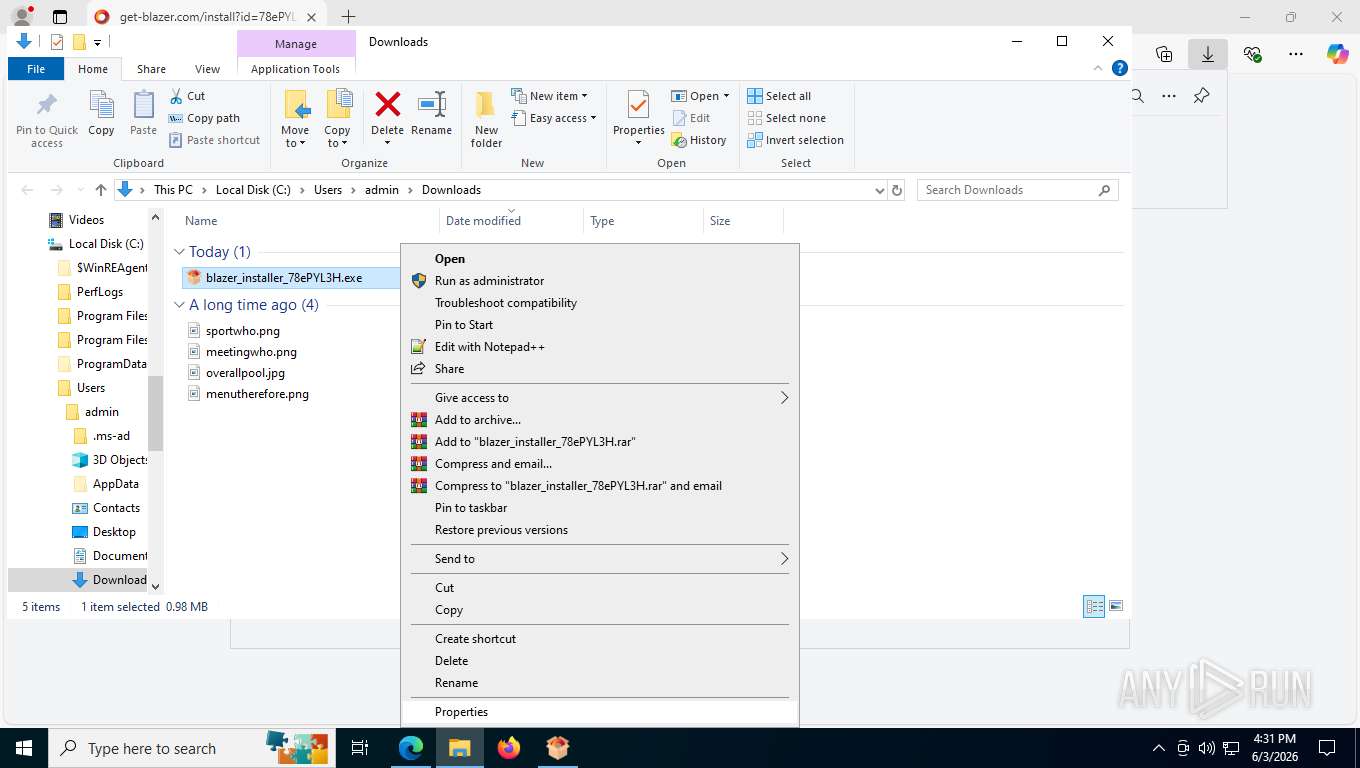
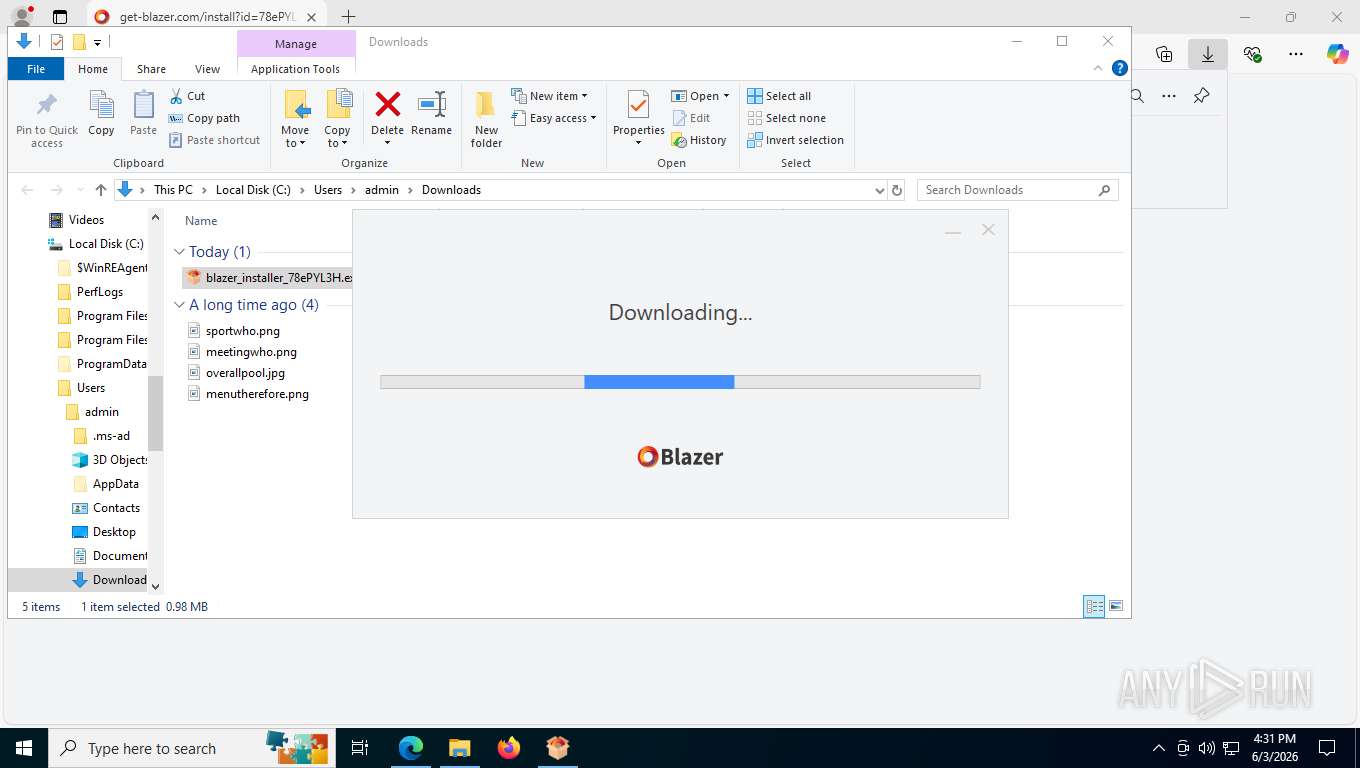
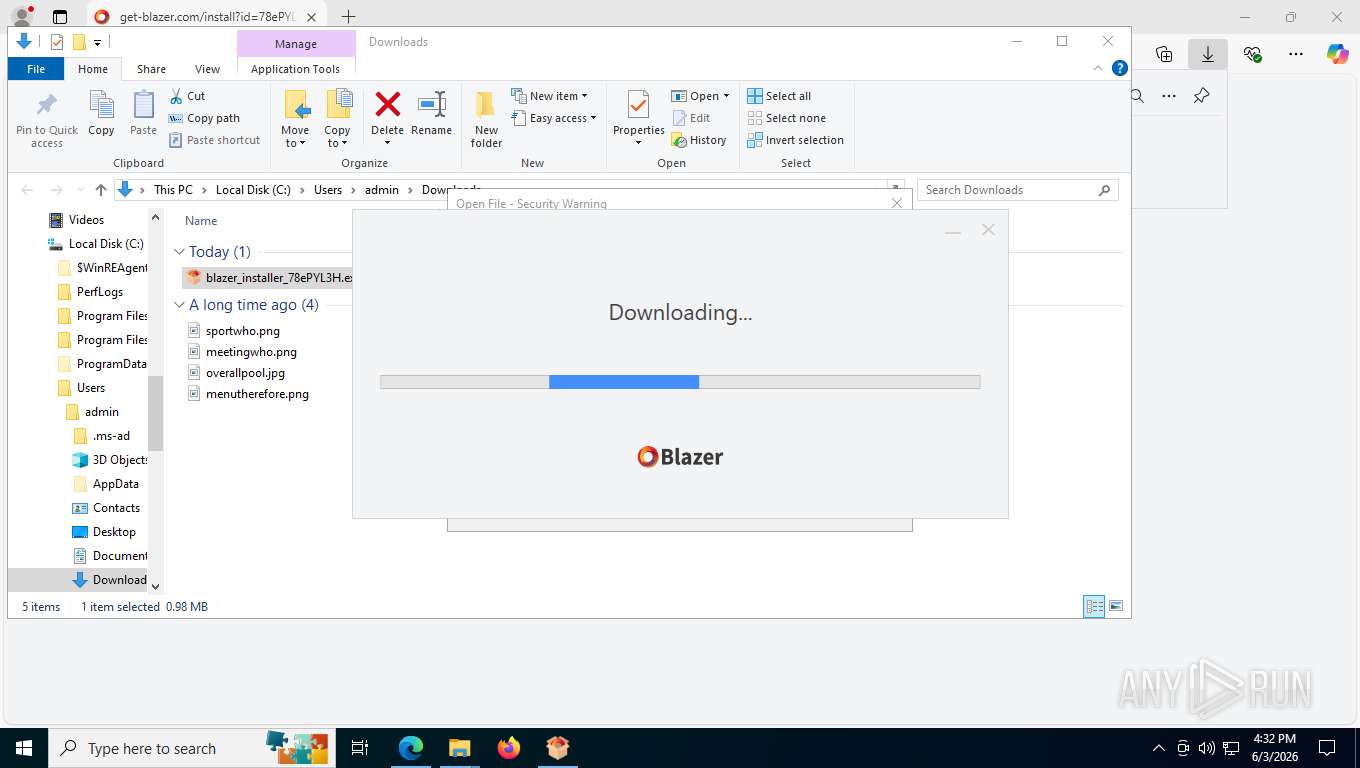
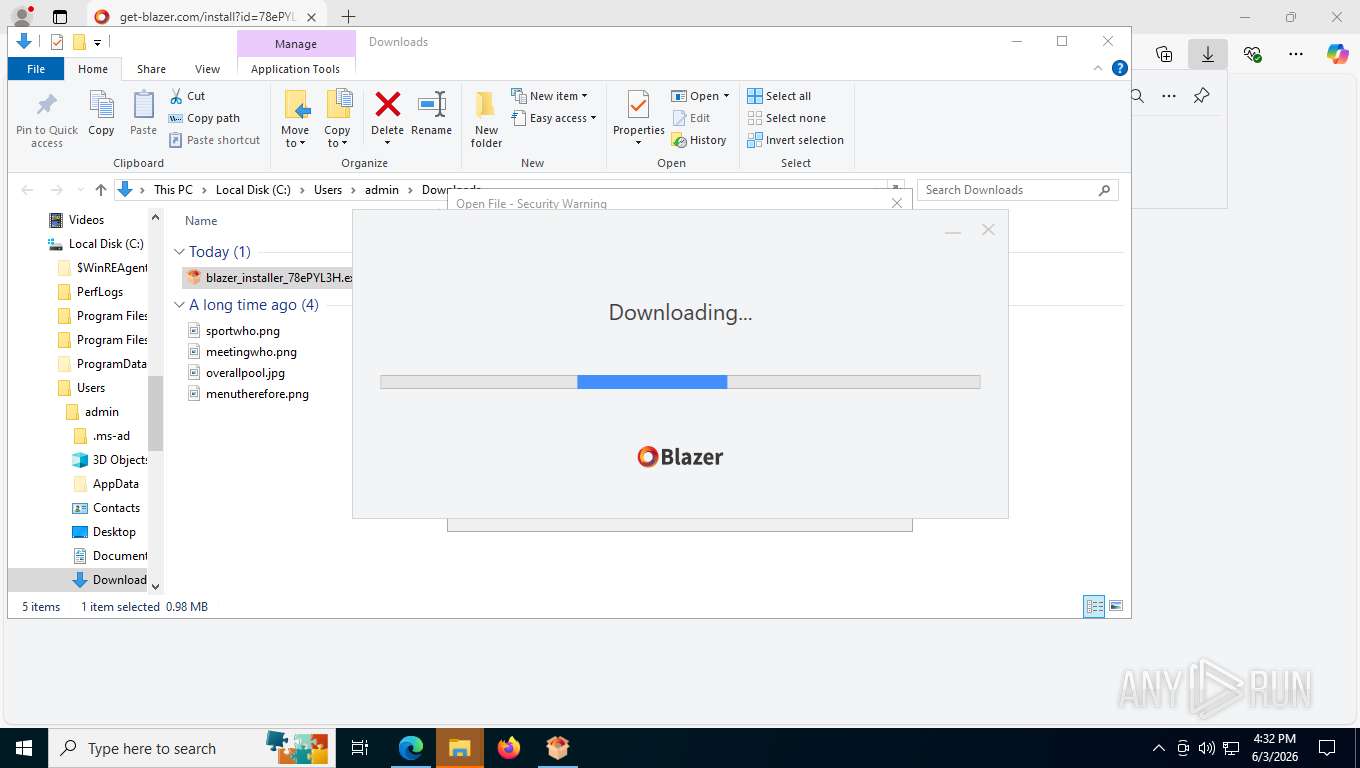
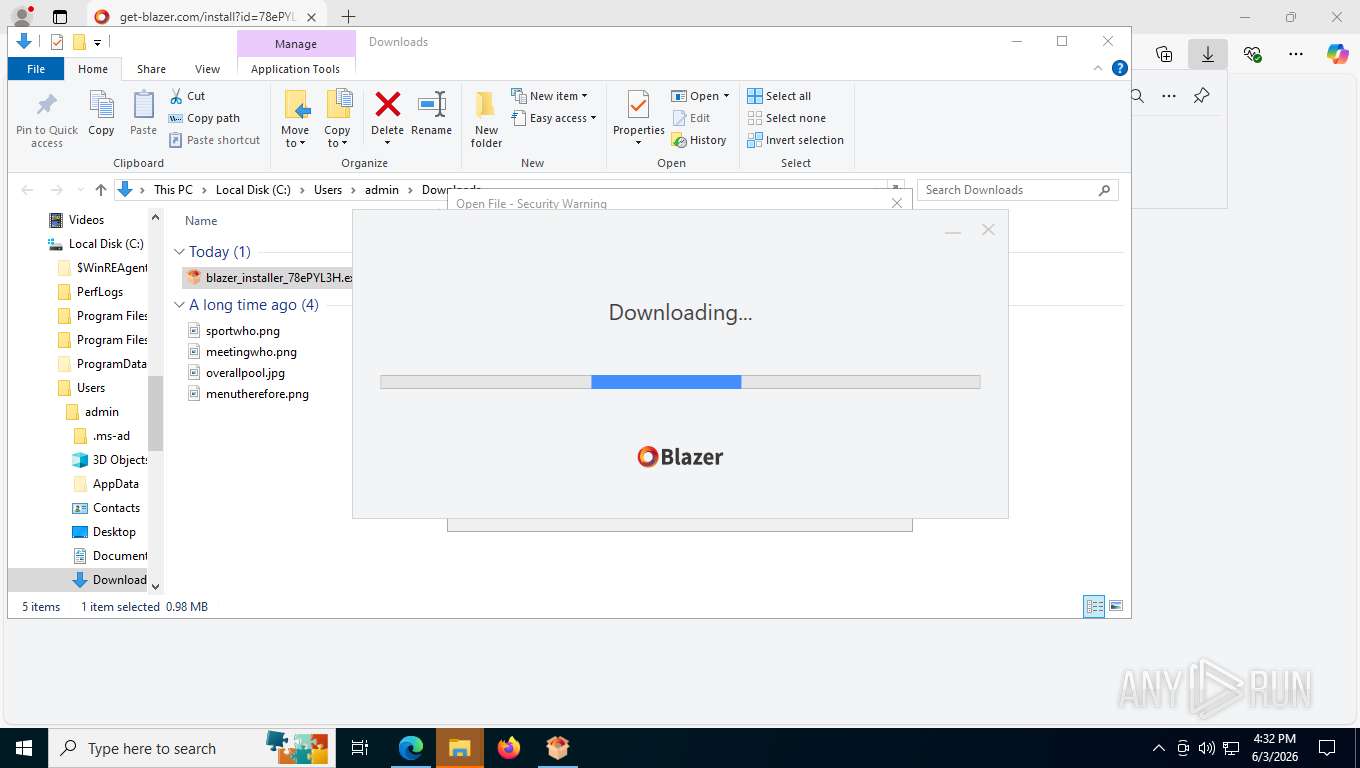
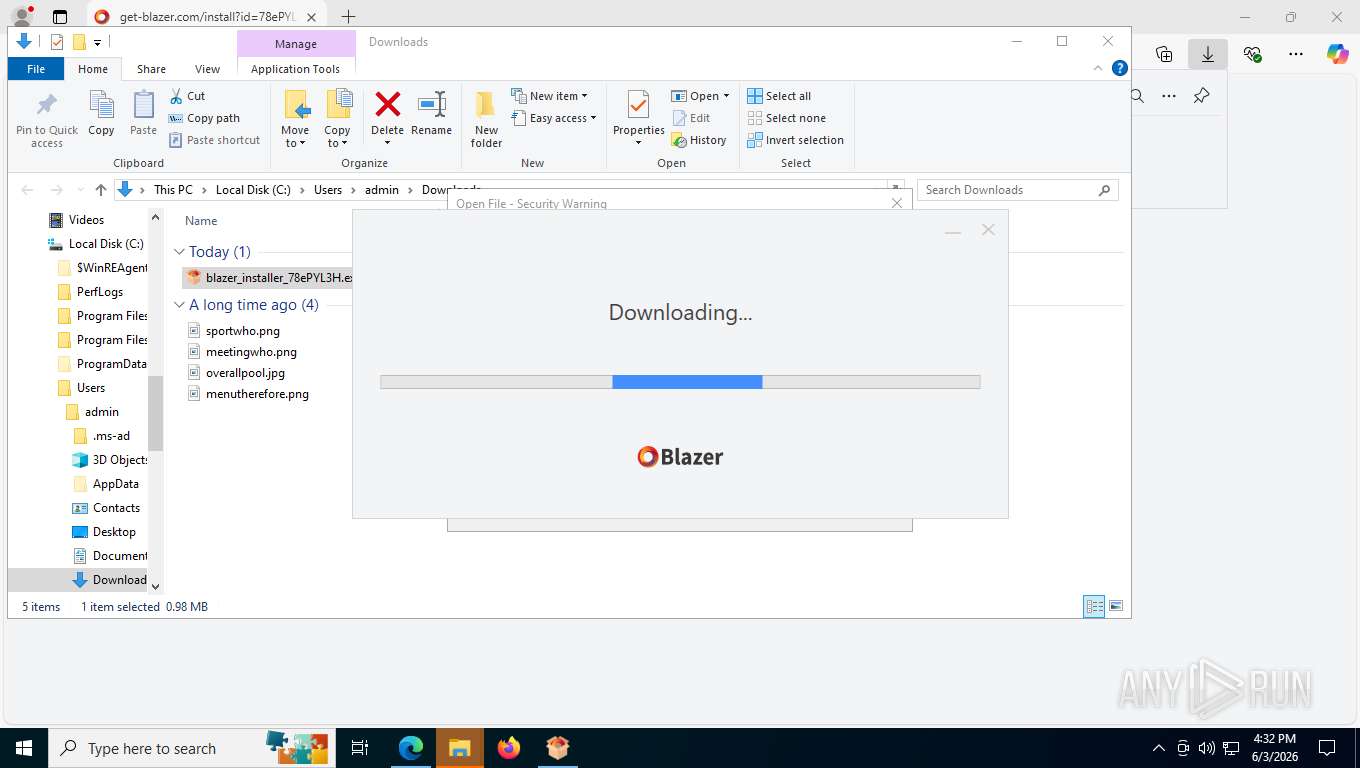
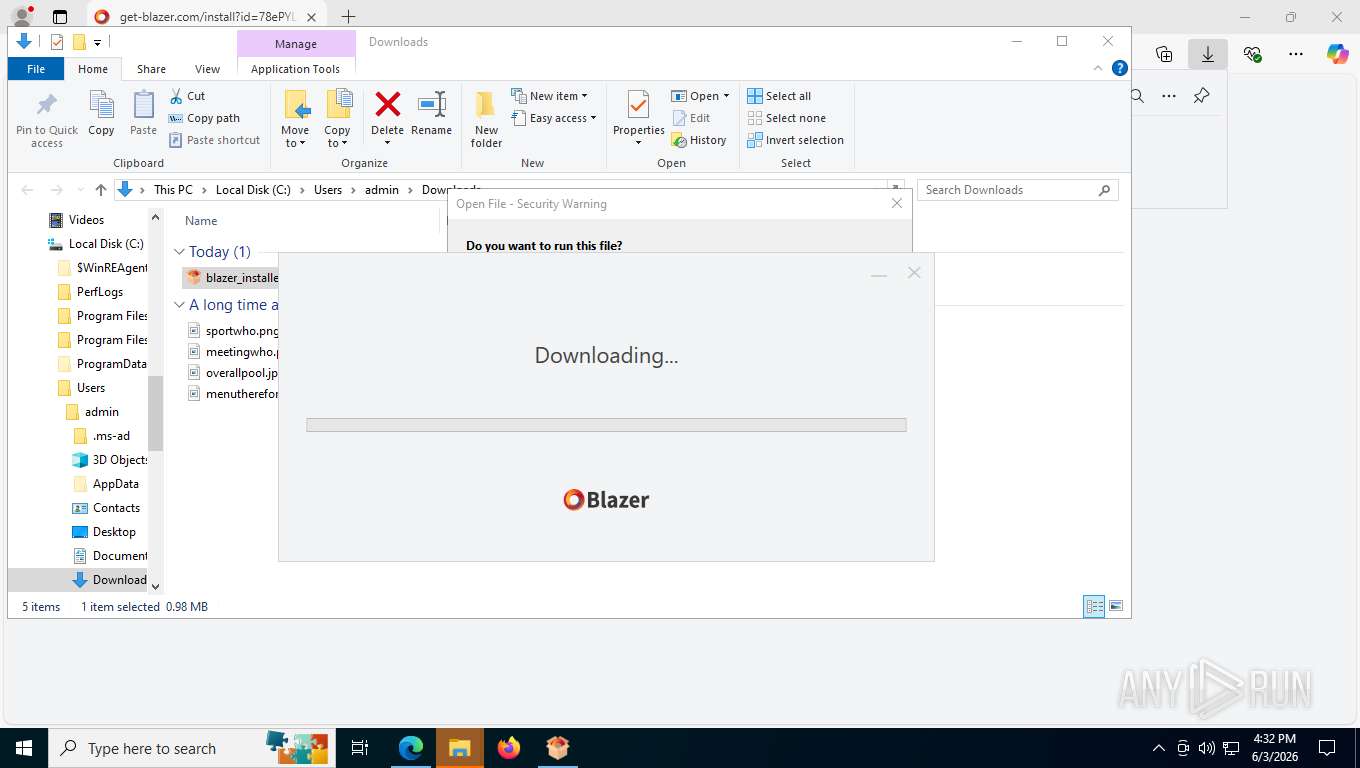
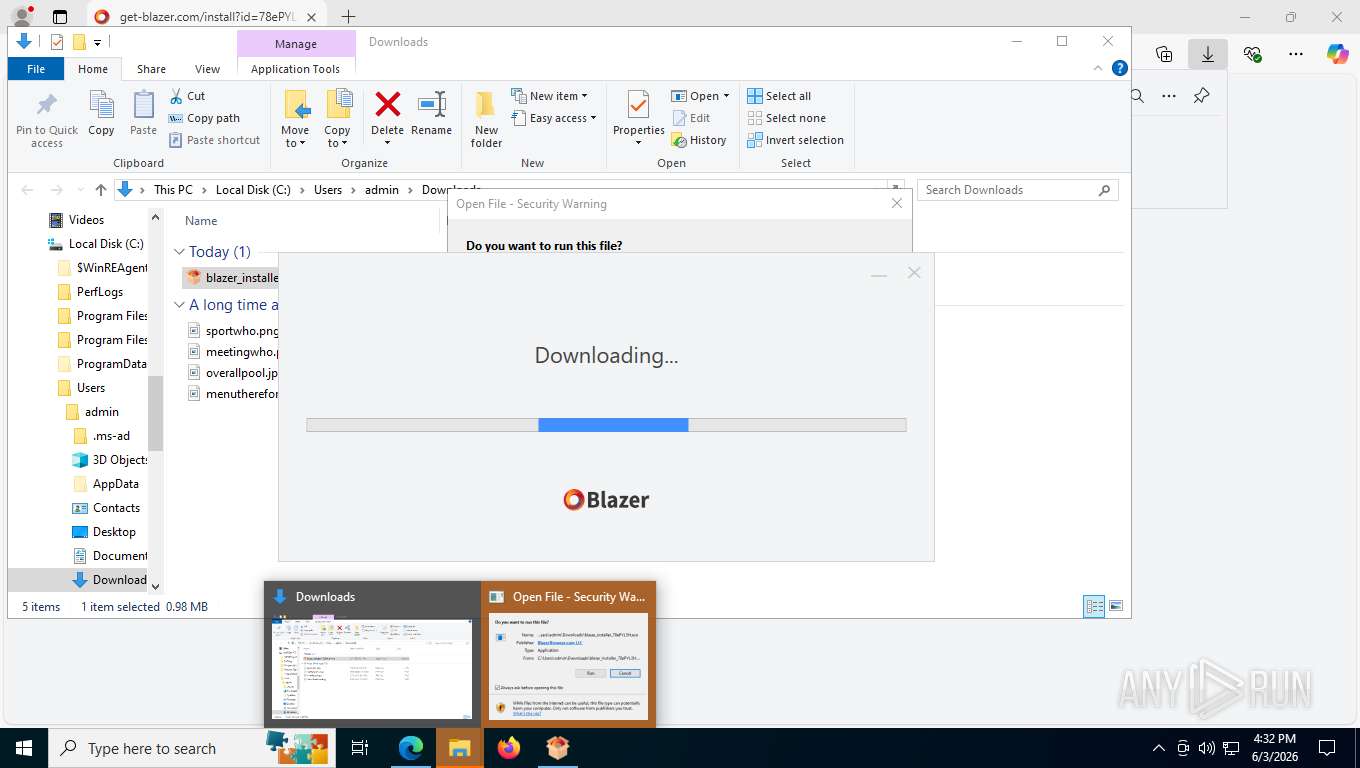
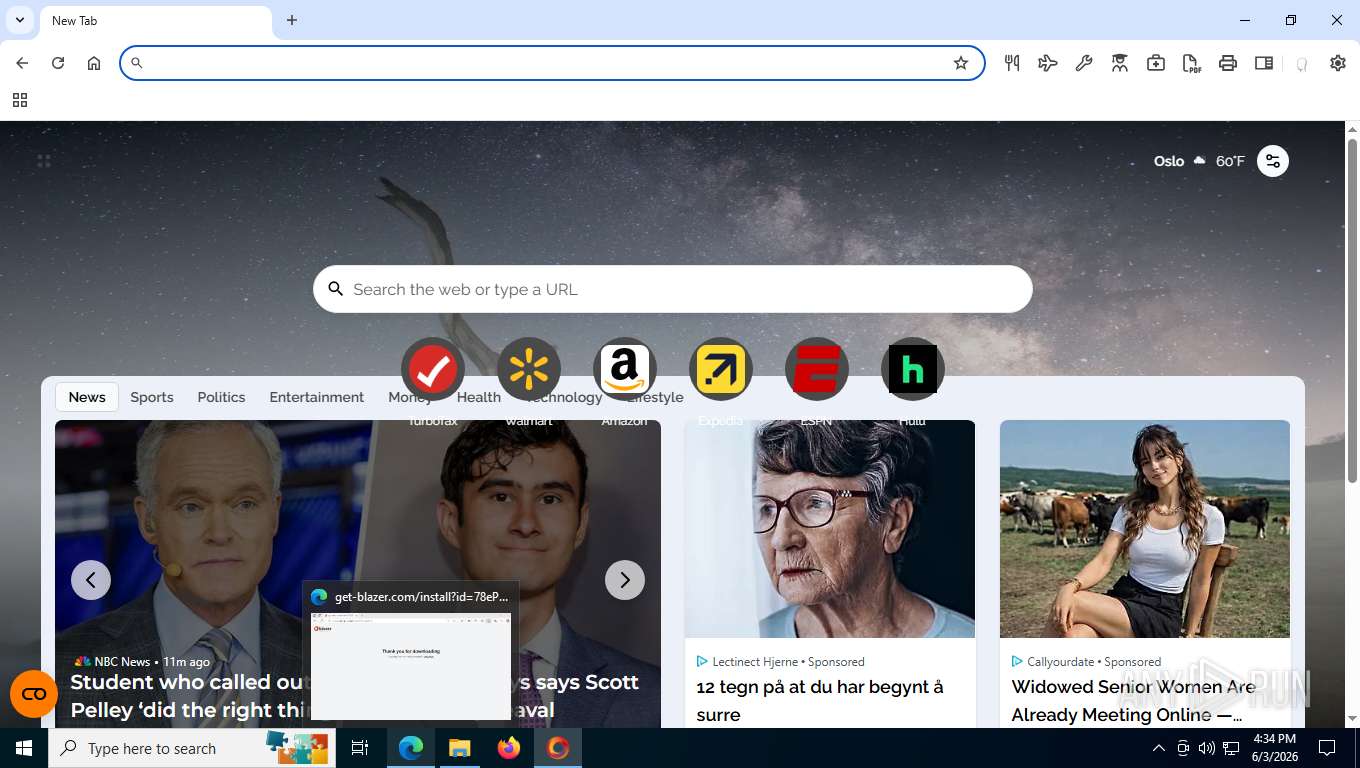
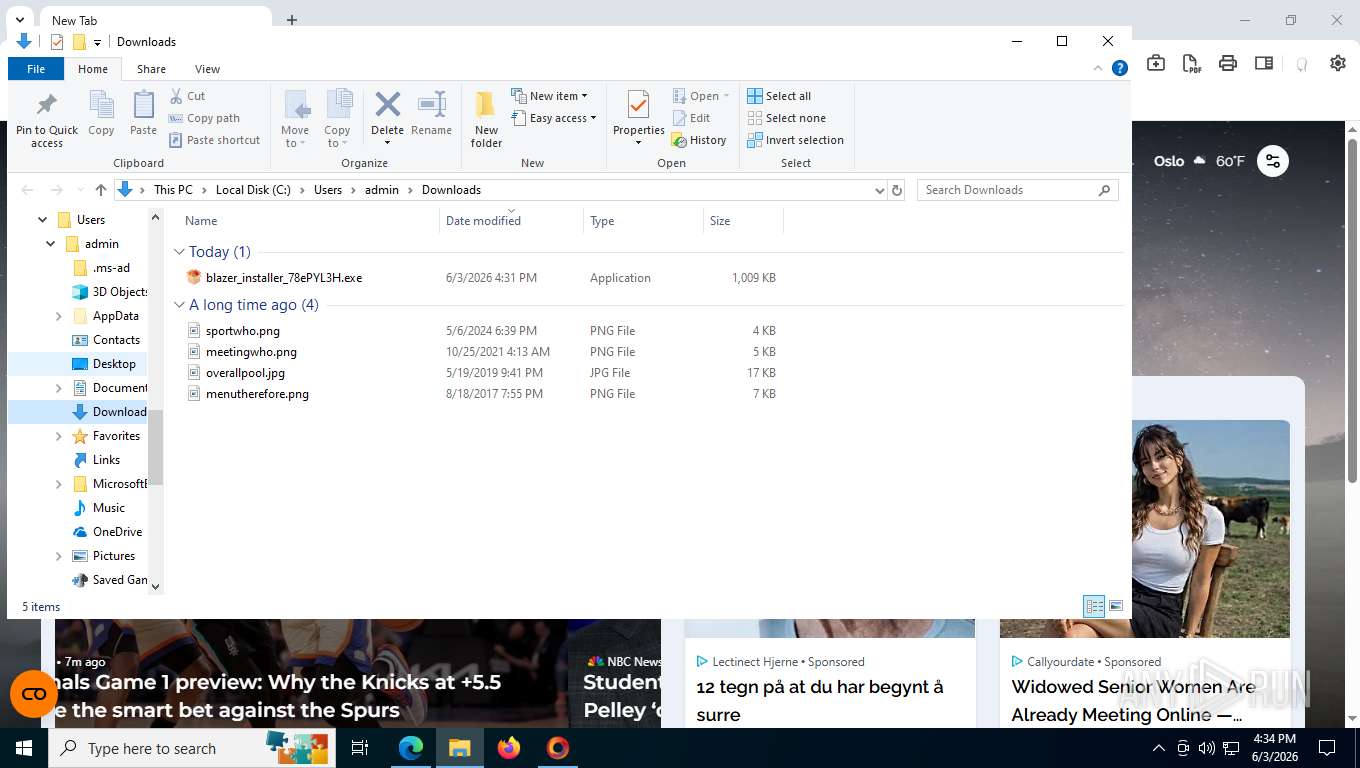
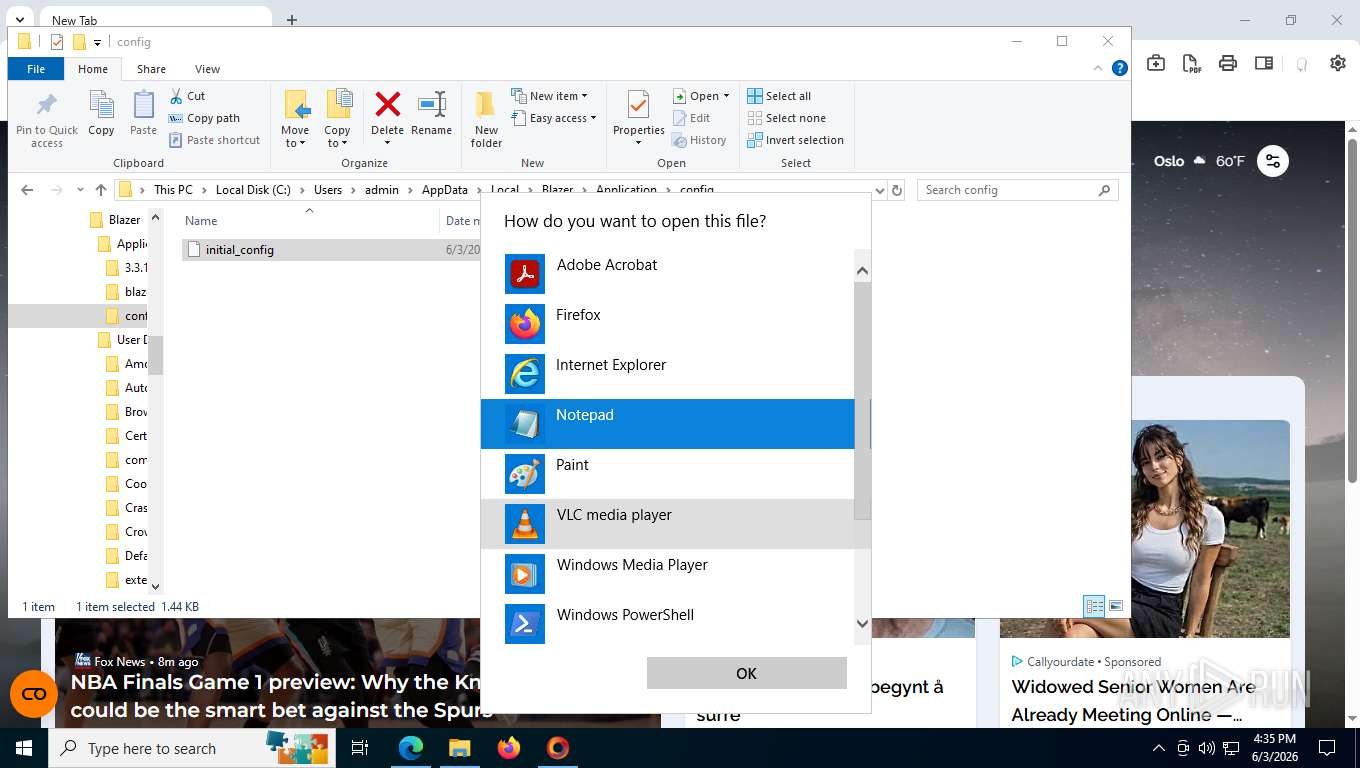
| URL: | https://get-blazer.com/install?id=XKDnTjcC&navigated_from_root=1&utm_source=google&utm_medium=display&source=BB1&campaign=23655303495&adgroup=195871852442&creative=800566387420&placement=www.calendar-12.com&term=&gclid=EAIaIQobChMI0_qpstPrlAMV_LQDAR2etTL3EAEYASAAEgKbDfD_BwE&gad_source=5&gad_campaignid=23655303495&gclid=EAIaIQobChMI0_qpstPrlAMV_LQDAR2etTL3EAEYASAAEgKbDfD_BwE |
| Full analysis: | https://app.any.run/tasks/67191634-20ef-49a1-ae63-bc194b618be1 |
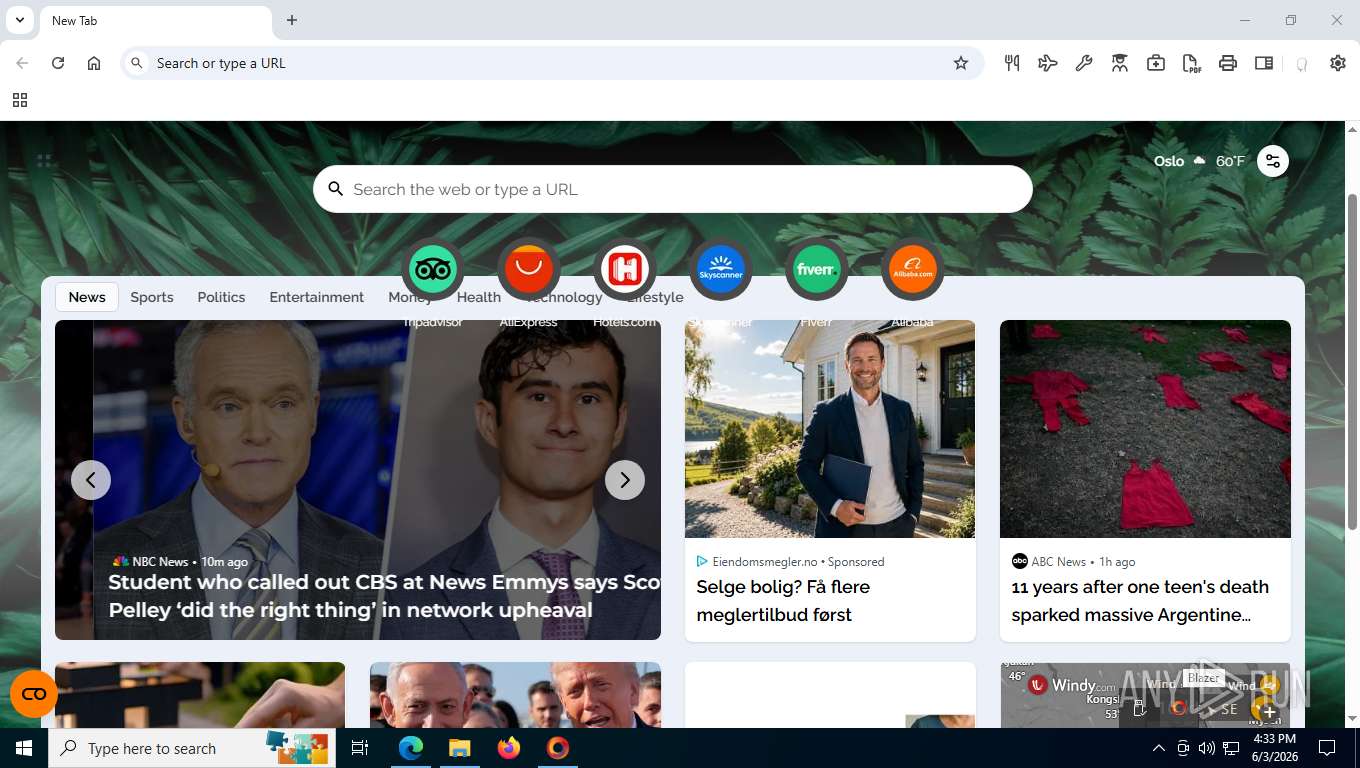
| Verdict: | Malicious activity |
| Threats: | A loader is malicious software that infiltrates devices to deliver malicious payloads. This malware is capable of infecting victims’ computers, analyzing their system information, and installing other types of threats, such as trojans or stealers. Criminals usually deliver loaders through phishing emails and links by relying on social engineering to trick users into downloading and running their executables. Loaders employ advanced evasion and persistence tactics to avoid detection. |
| Analysis date: | June 03, 2026, 20:30:47 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MD5: | 8B54239C596C38E2F67F3DDCD70F0720 |
| SHA1: | 94CBE5A603BE142A62C880E169AF0F3A0927B003 |
| SHA256: | 2744D66EAF61F28D1930AE45562F9F4CD1B33DB4083A1DCACA8A5D6703846282 |
| SSDEEP: | 6:26gU5RJWuhH3X5tCWQA5m5CdhSRJKTa3onpeYXA9wWdKTa3ons:26gkRThHn5t7QtehS6a3Q3ct8a3Qs |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1176 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --lang=en-US --service-sandbox-type=service --disable-quic --string-annotations --always-read-main-dll --field-trial-handle=6016,i,539695047706178200,11679952684815260304,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version --mojo-platform-channel-handle=4280 /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Exit code: 0 Version: 133.0.3065.92 Modules
| |||||||||||||||
| 1776 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=edge_search_indexer.mojom.SearchIndexerInterfaceBroker --lang=en-US --service-sandbox-type=search_indexer --disable-quic --message-loop-type-ui --string-annotations --always-read-main-dll --field-trial-handle=8252,i,539695047706178200,11679952684815260304,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version --mojo-platform-channel-handle=8260 /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Version: 133.0.3065.92 Modules
| |||||||||||||||
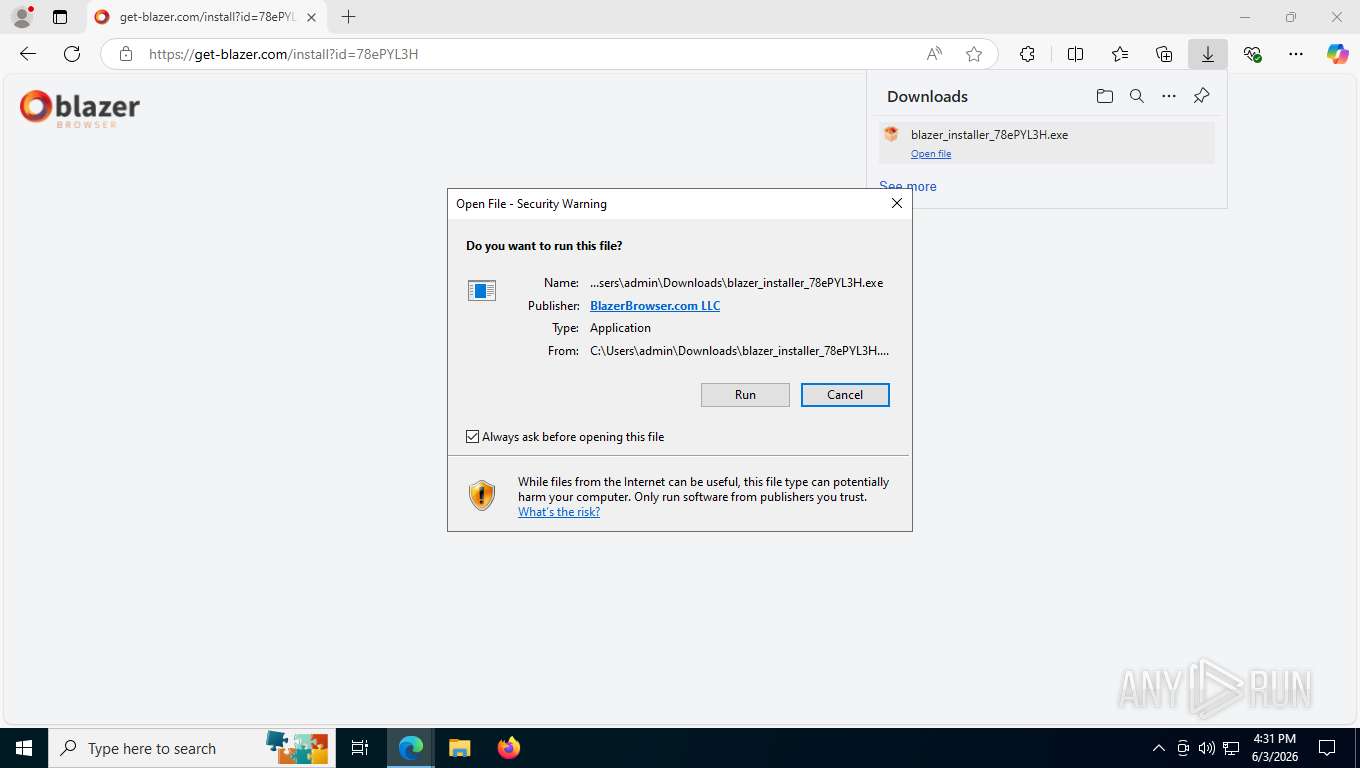
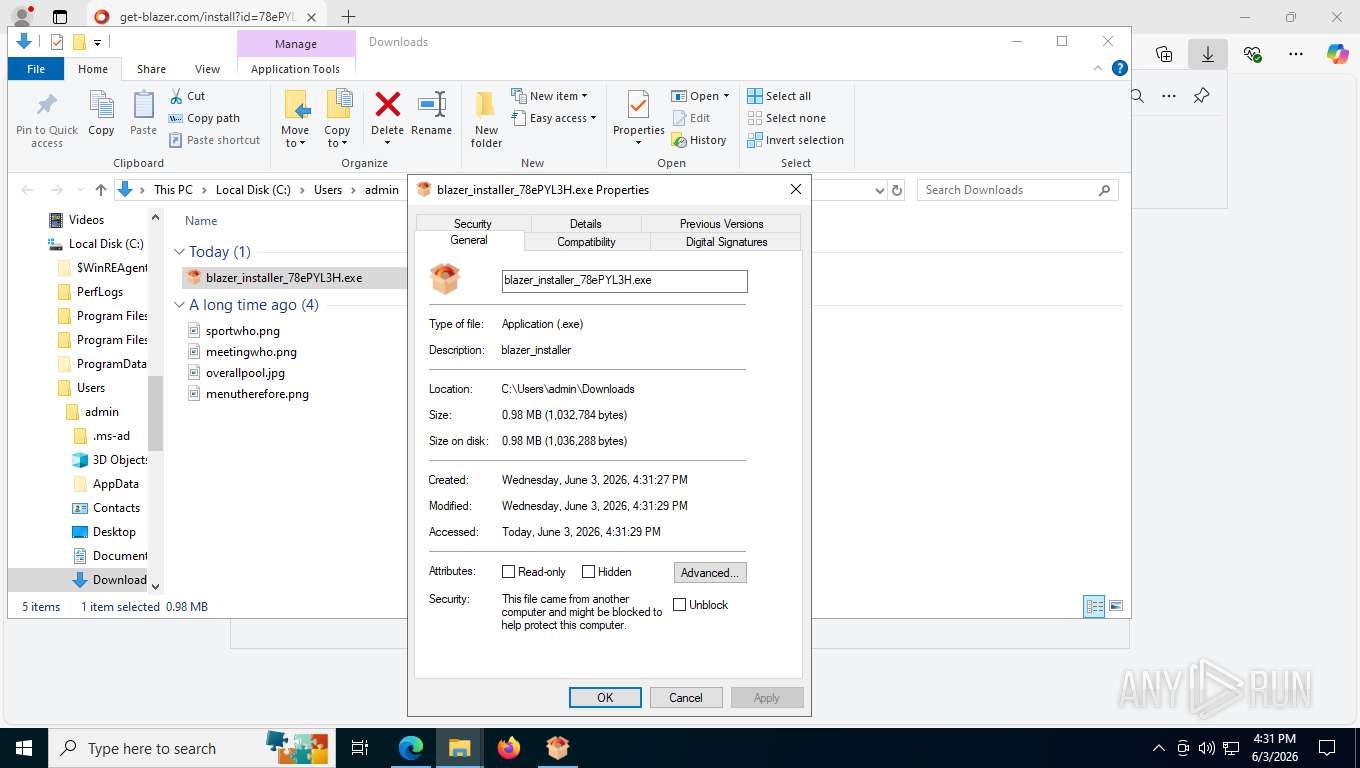
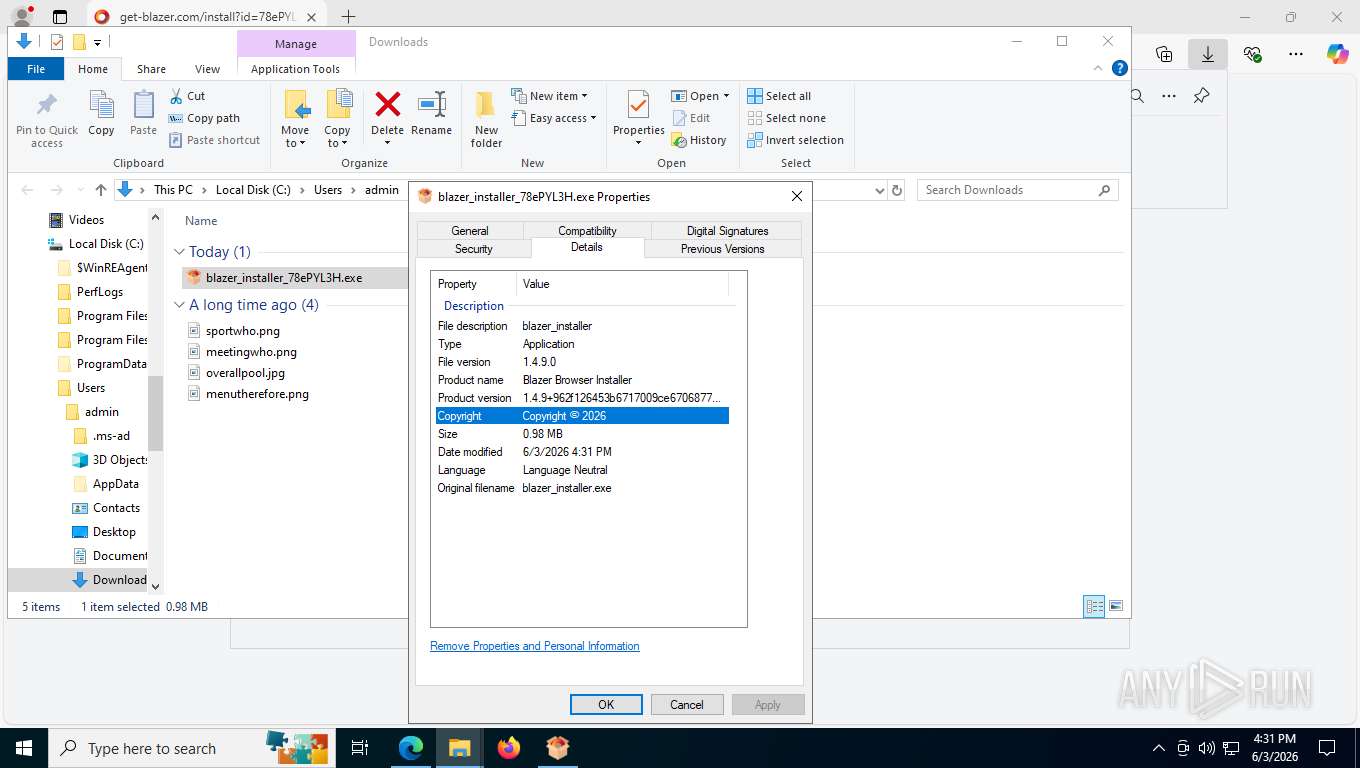
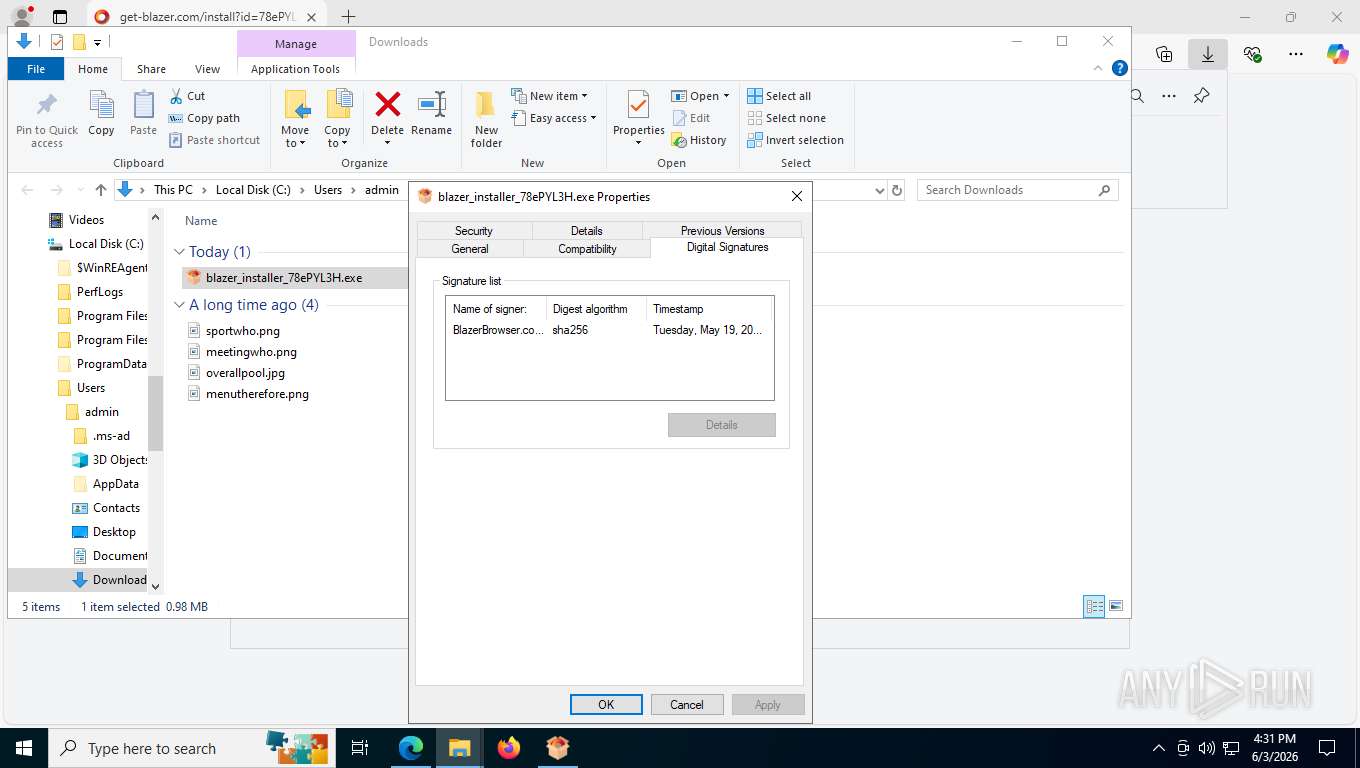
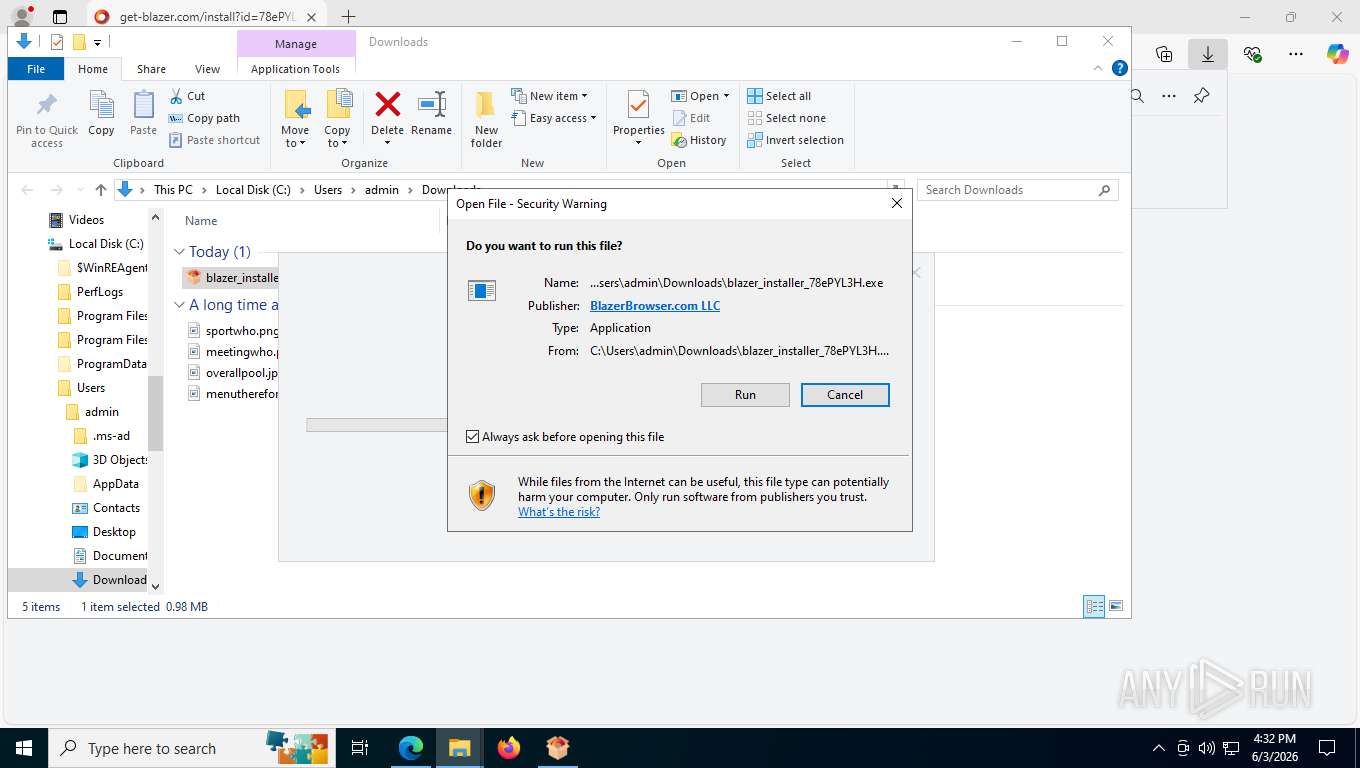
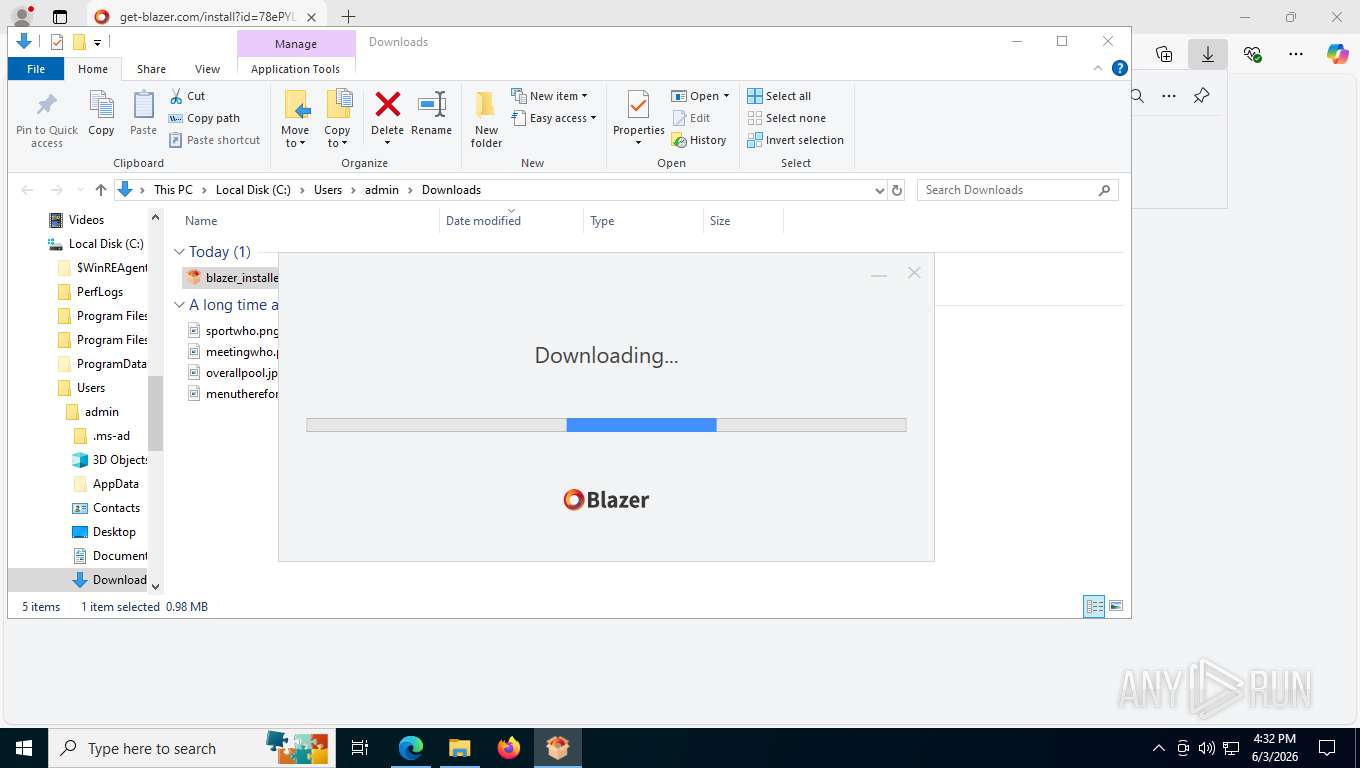
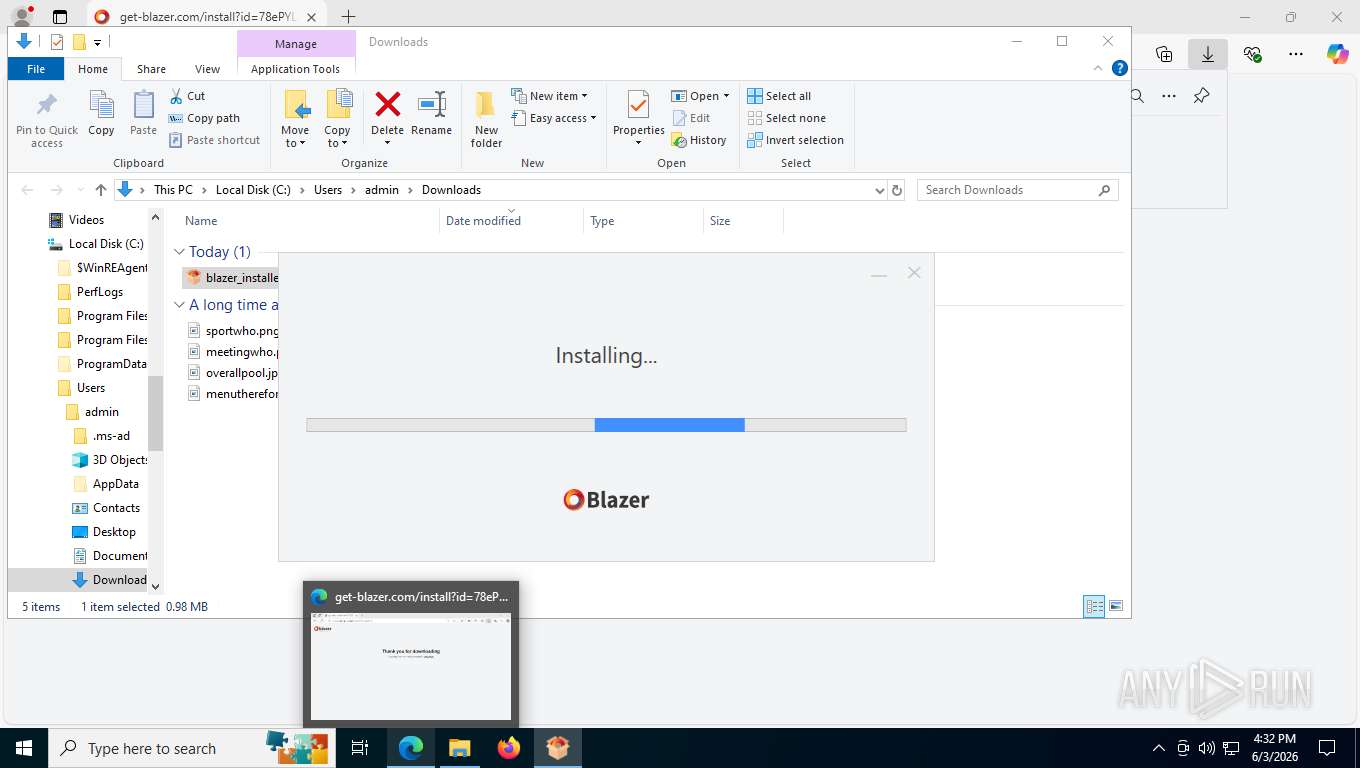
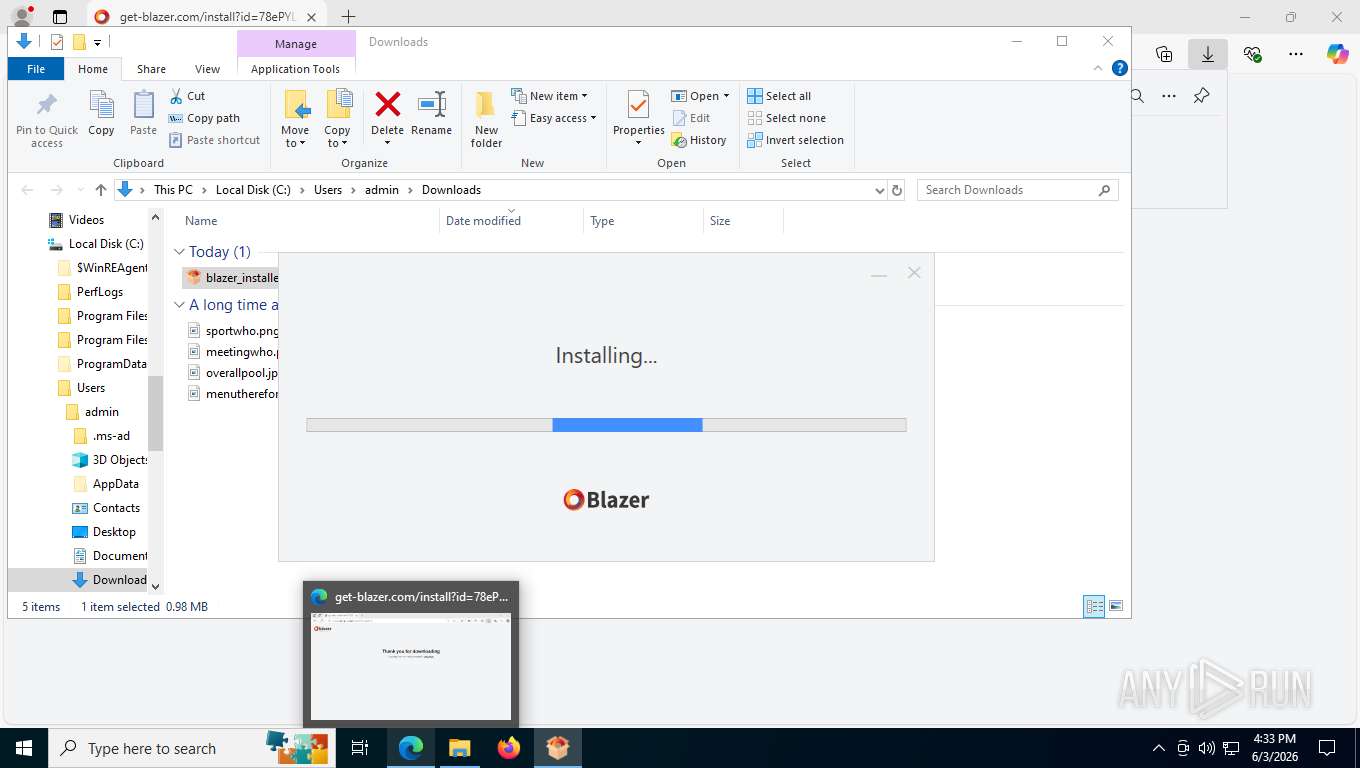
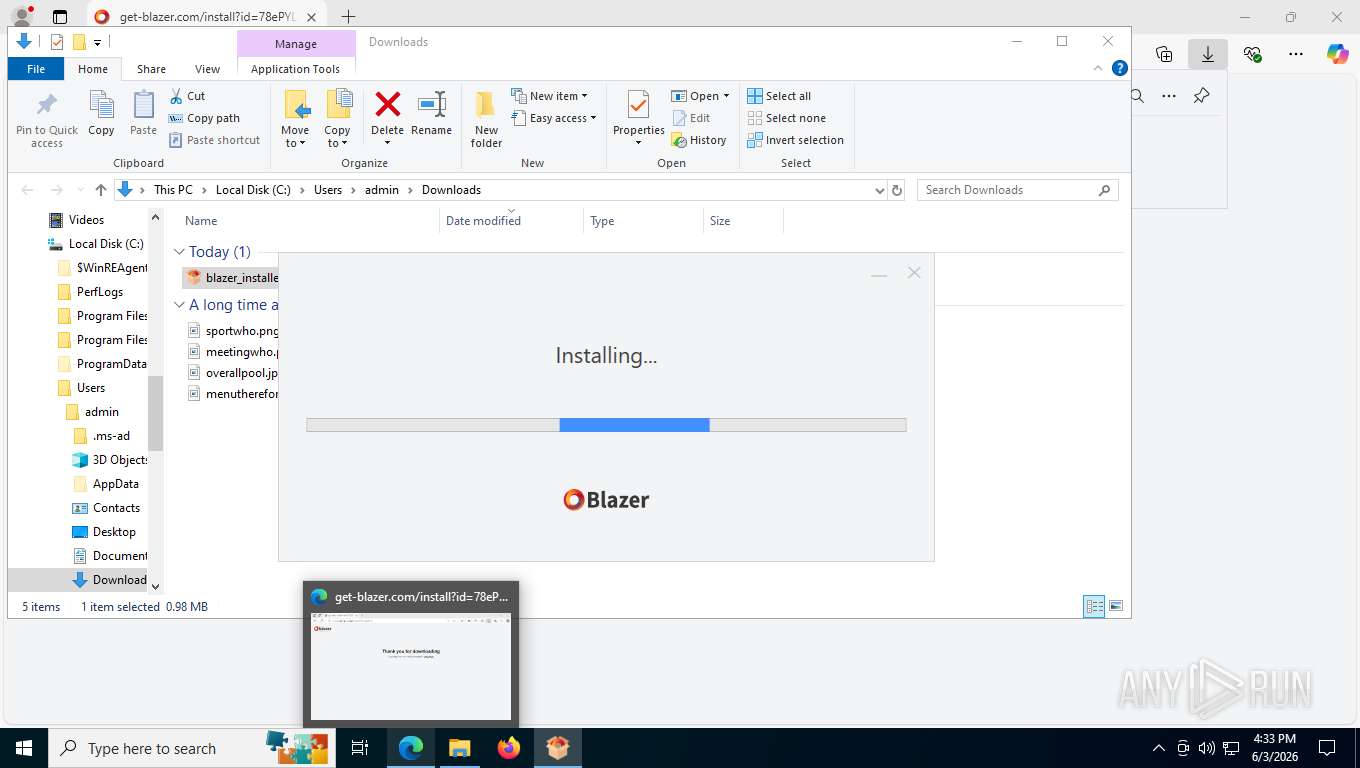
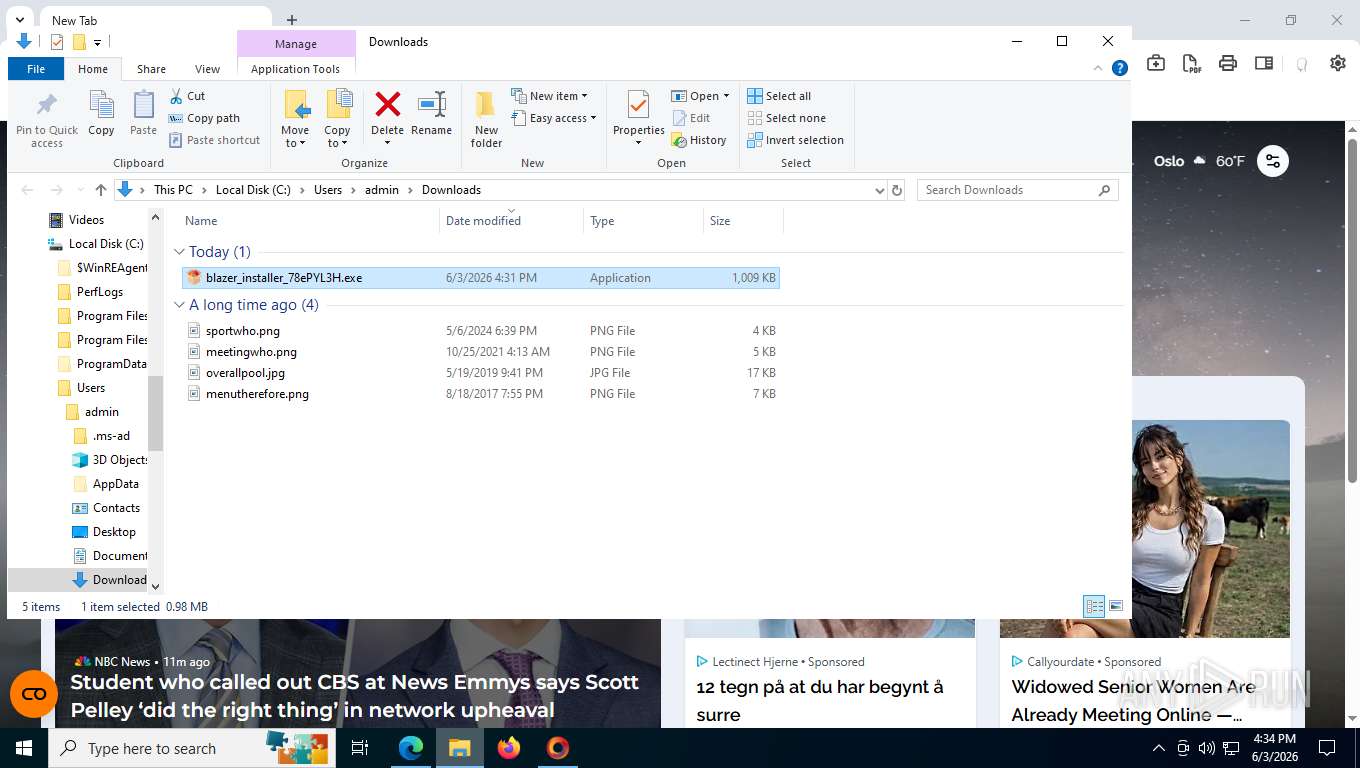
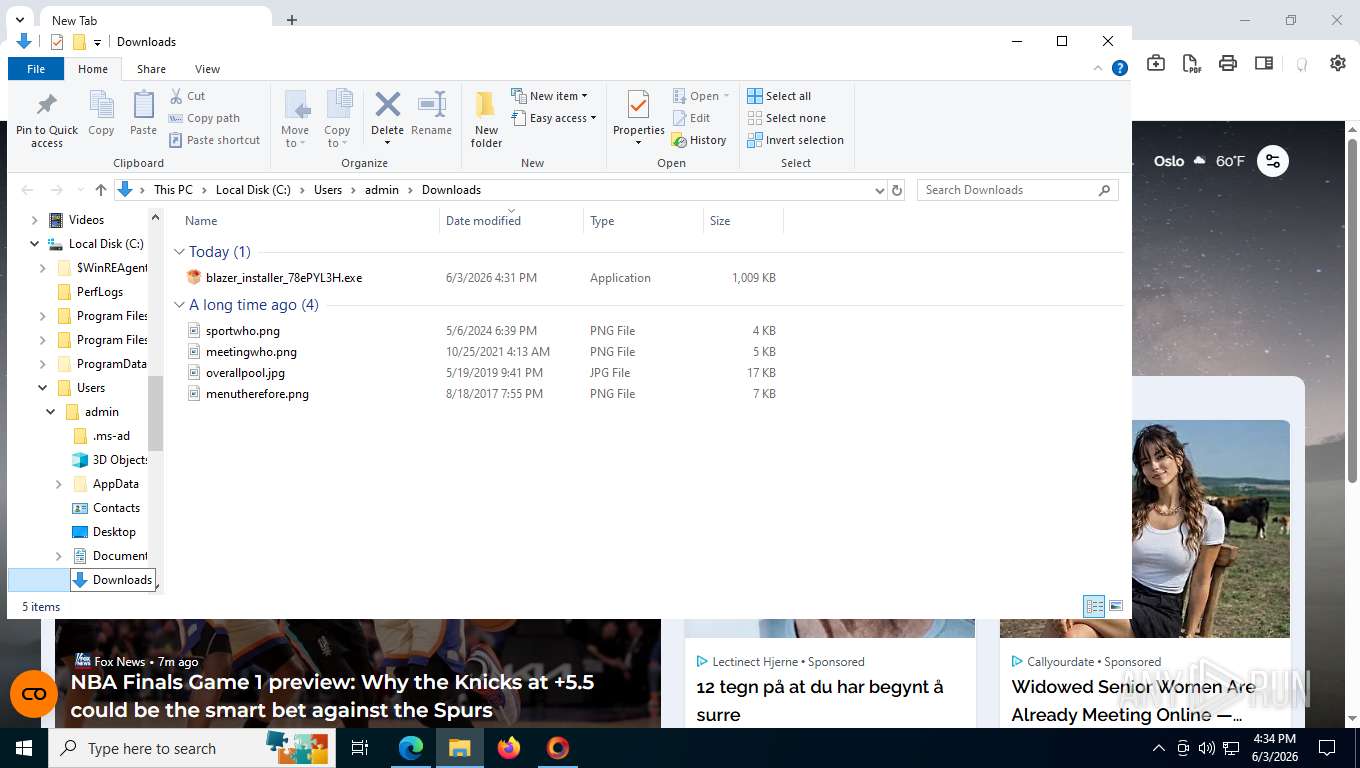
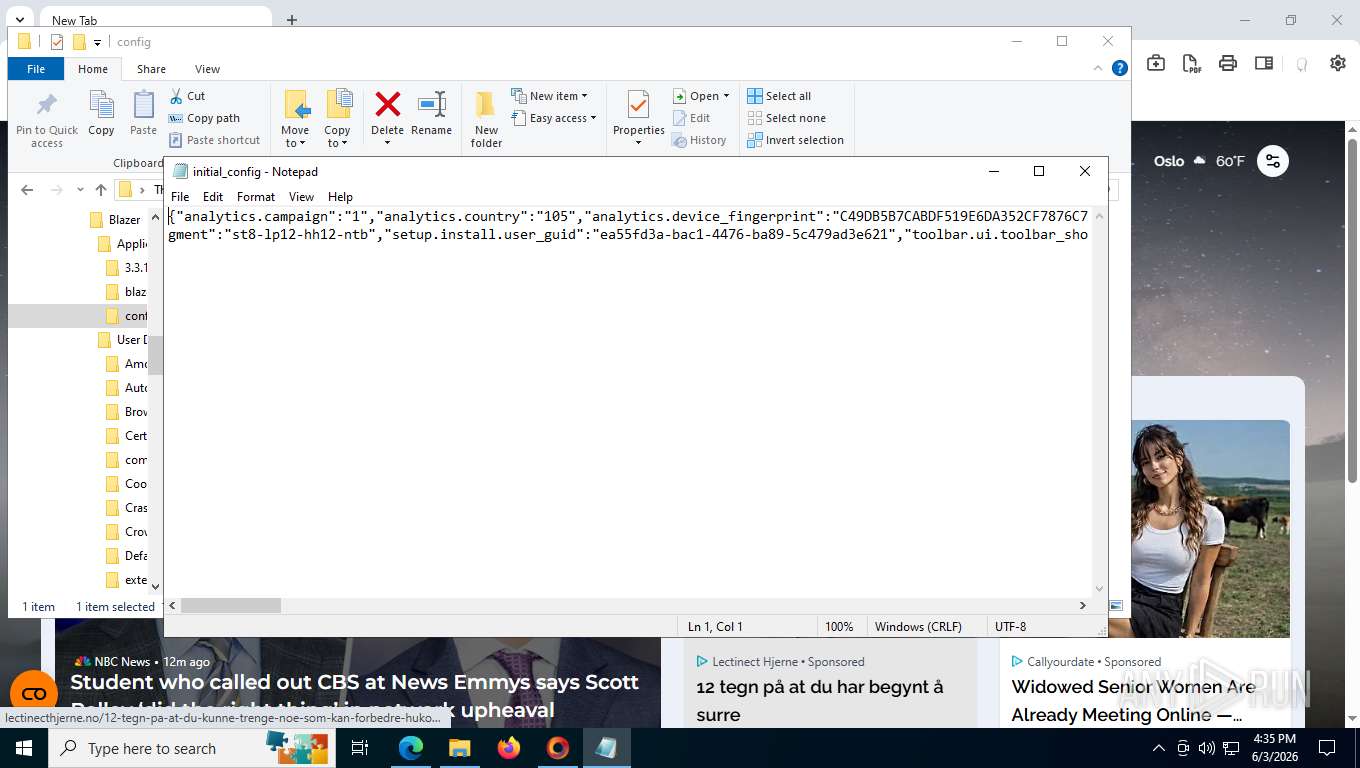
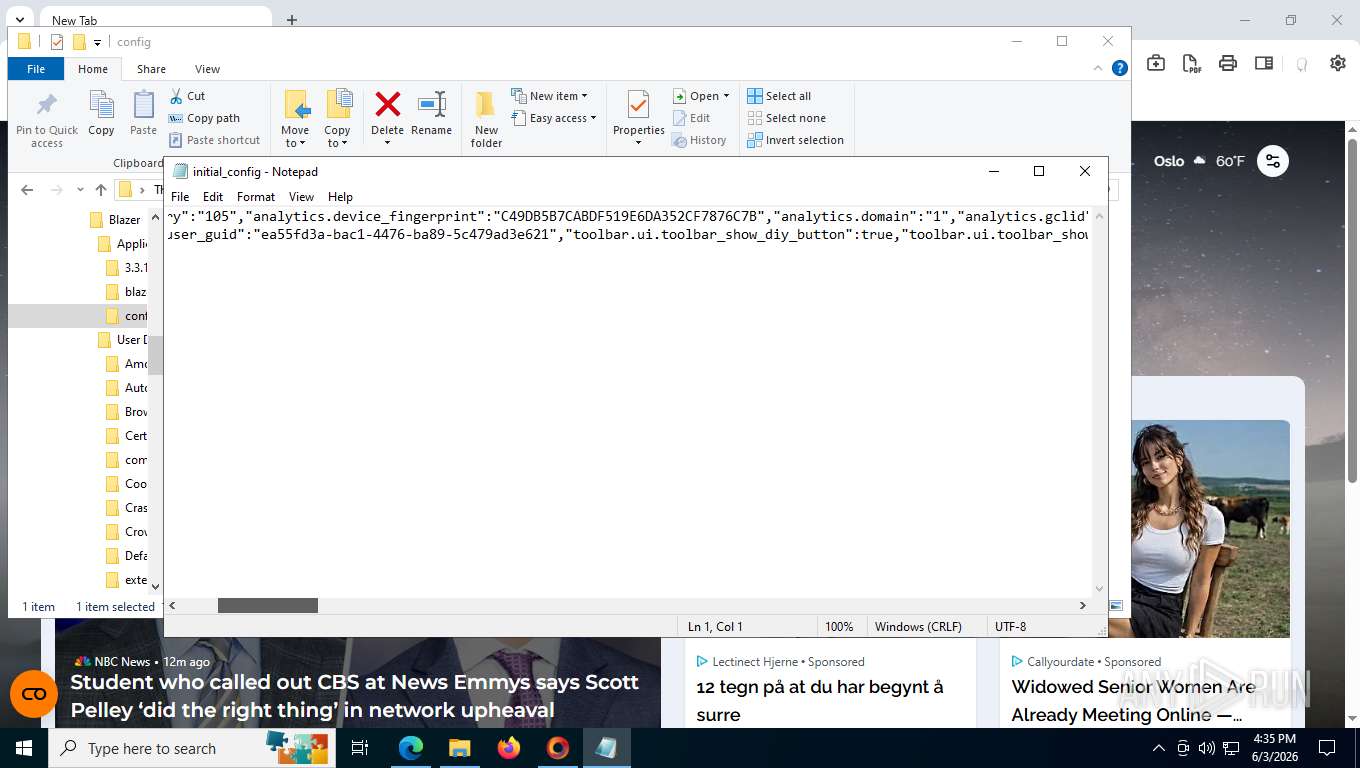
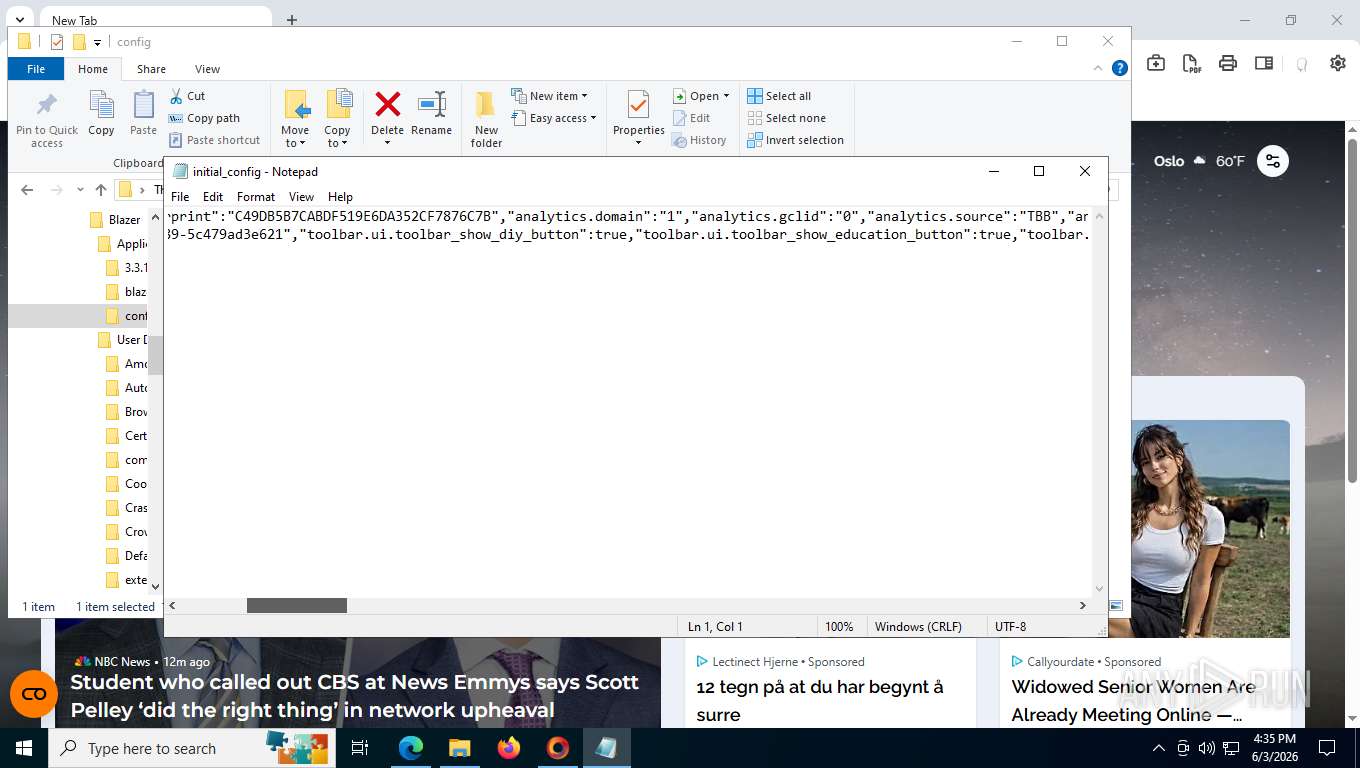
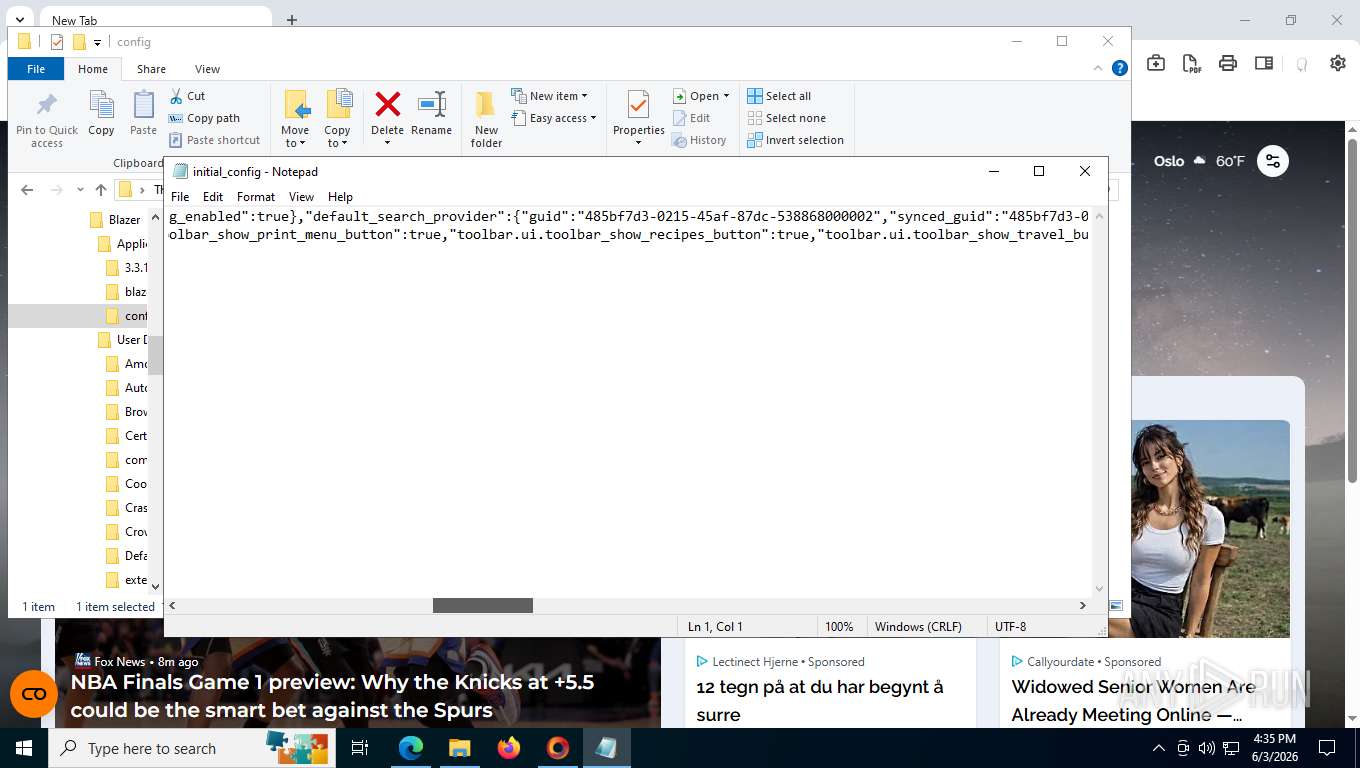
| 2220 | "C:\Users\admin\AppData\Local\Temp\ybihwujt.dgr\CR_5ACE9.tmp\setup.exe" --verbose-logging --create-shortcuts=0 --install-level=0 --v=1 --cache-key=78ePYL3H --device-fingerprint=C49DB5B7CABDF519E6DA352CF7876C7B --country-code=105 | C:\Users\admin\AppData\Local\Temp\ybihwujt.dgr\CR_5ACE9.tmp\setup.exe | — | setup.exe | |||||||||||
User: admin Company: The Blazer Authors Integrity Level: MEDIUM Description: Blazer Installer Exit code: 73 Version: 3.3.142.5 Modules
| |||||||||||||||
| 2396 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=audio.mojom.AudioService --lang=en-US --service-sandbox-type=audio --disable-quic --string-annotations --always-read-main-dll --field-trial-handle=5528,i,539695047706178200,11679952684815260304,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version --mojo-platform-channel-handle=5500 /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Version: 133.0.3065.92 Modules
| |||||||||||||||
| 2428 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=gpu-process --string-annotations --gpu-preferences=UAAAAAAAAADgAAAEAAAAAAAAAAAAAAAAAABgAAEAAAAAAAAAAAAAAAAAAAACAAAAAAAAAAAAAAAAAAAAAAAAABAAAAAAAAAAEAAAAAAAAAAIAAAAAAAAAAgAAAAAAAAA --always-read-main-dll --field-trial-handle=2344,i,539695047706178200,11679952684815260304,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version --mojo-platform-channel-handle=2284 /prefetch:2 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Version: 133.0.3065.92 Modules
| |||||||||||||||
| 2612 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=entity_extraction_service.mojom.Extractor --lang=en-US --service-sandbox-type=entity_extraction --disable-quic --onnx-enabled-for-ee --string-annotations --always-read-main-dll --field-trial-handle=5728,i,539695047706178200,11679952684815260304,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version --mojo-platform-channel-handle=5672 /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Exit code: 0 Version: 133.0.3065.92 Modules
| |||||||||||||||
| 2676 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=chrome.mojom.UtilWin --lang=en-US --service-sandbox-type=none --disable-quic --message-loop-type-ui --string-annotations --always-read-main-dll --field-trial-handle=6568,i,539695047706178200,11679952684815260304,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version --mojo-platform-channel-handle=6148 /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Microsoft Edge Exit code: 0 Version: 133.0.3065.92 Modules
| |||||||||||||||
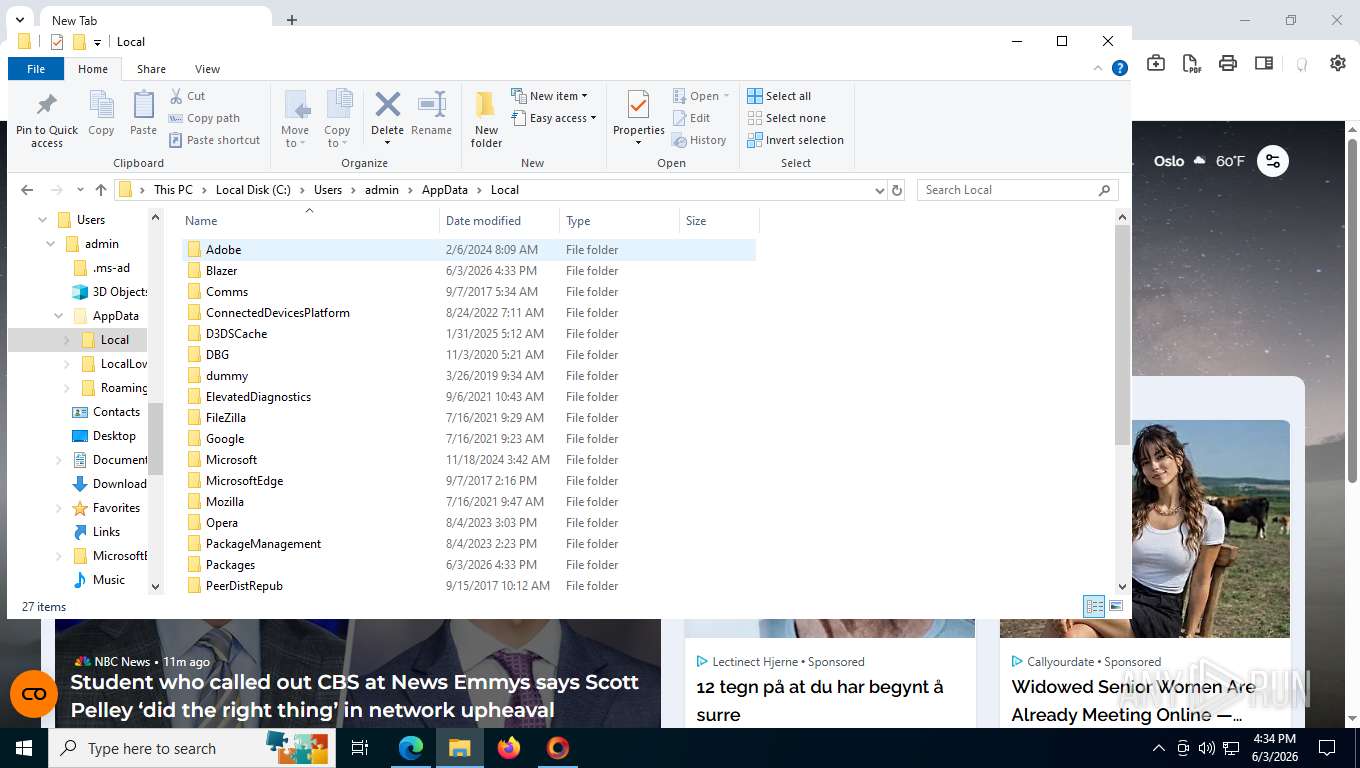
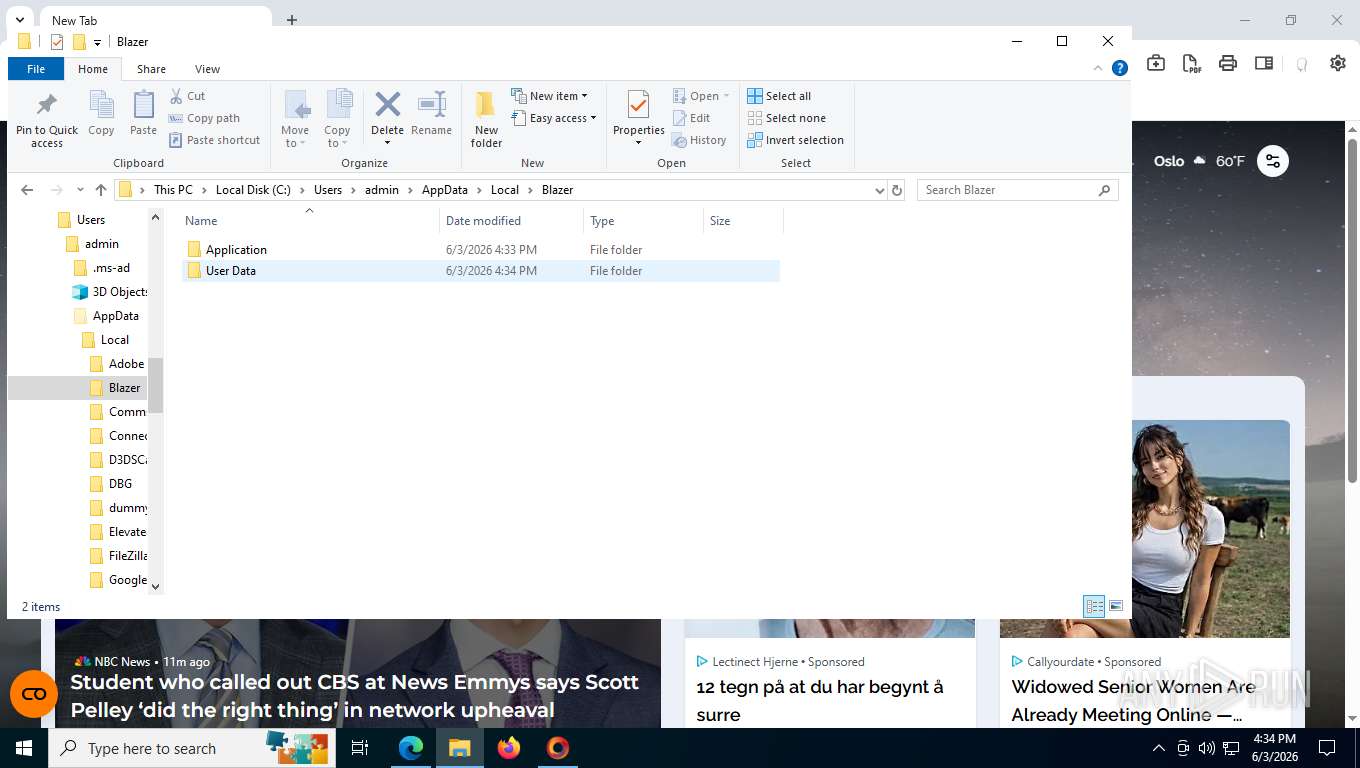
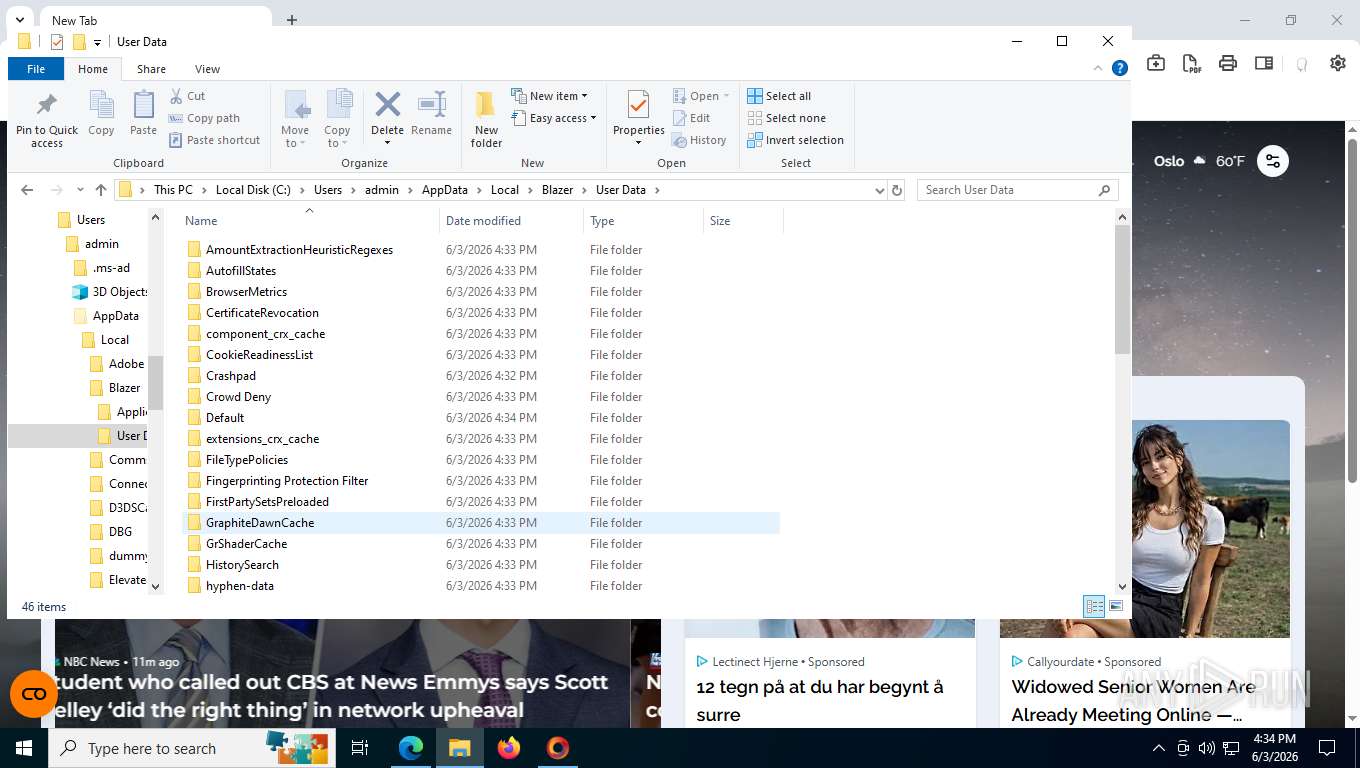
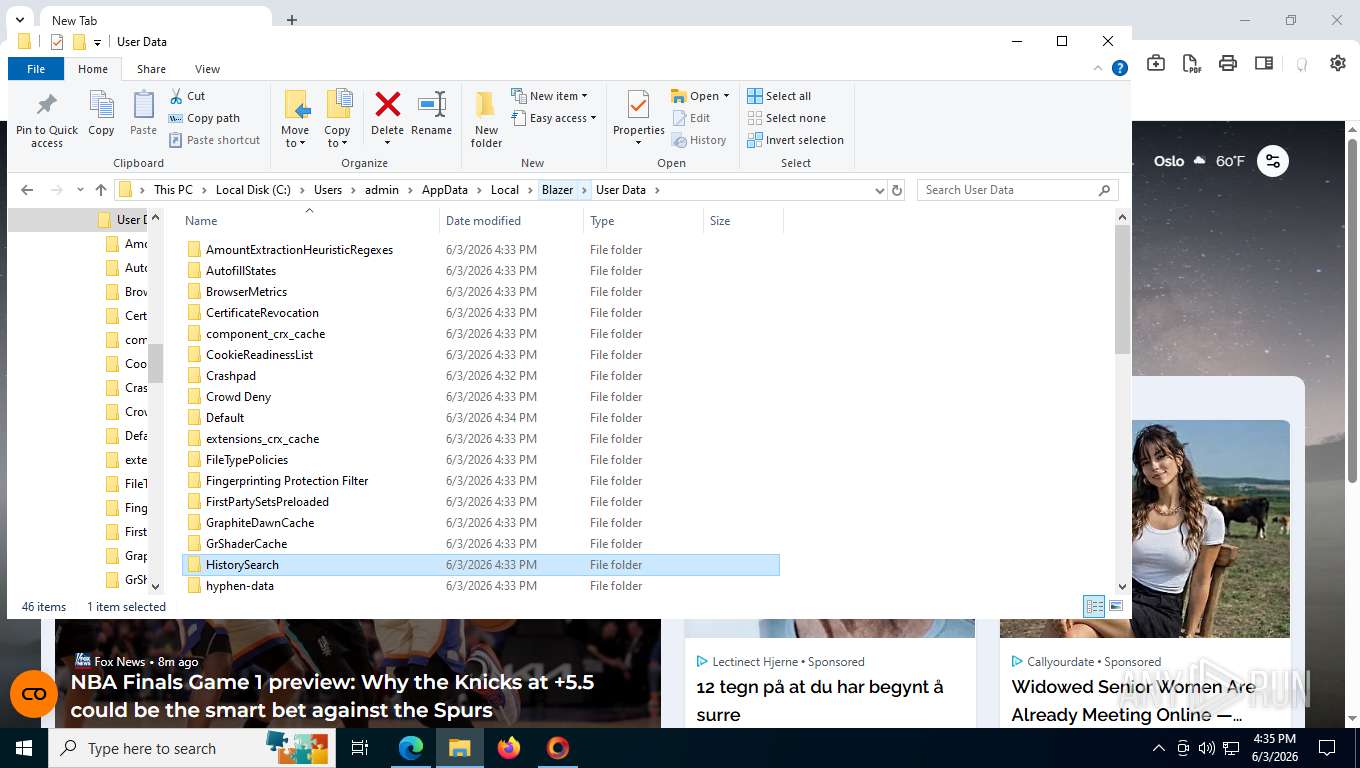
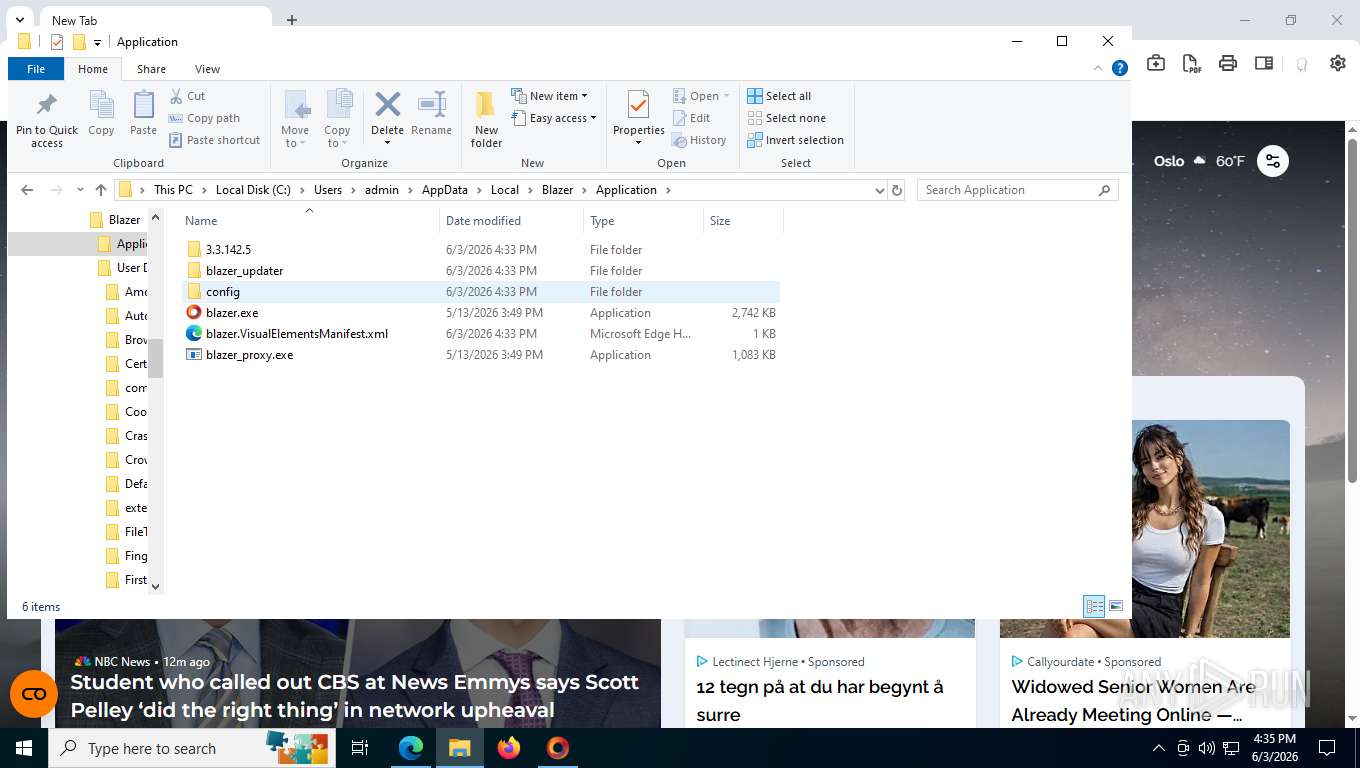
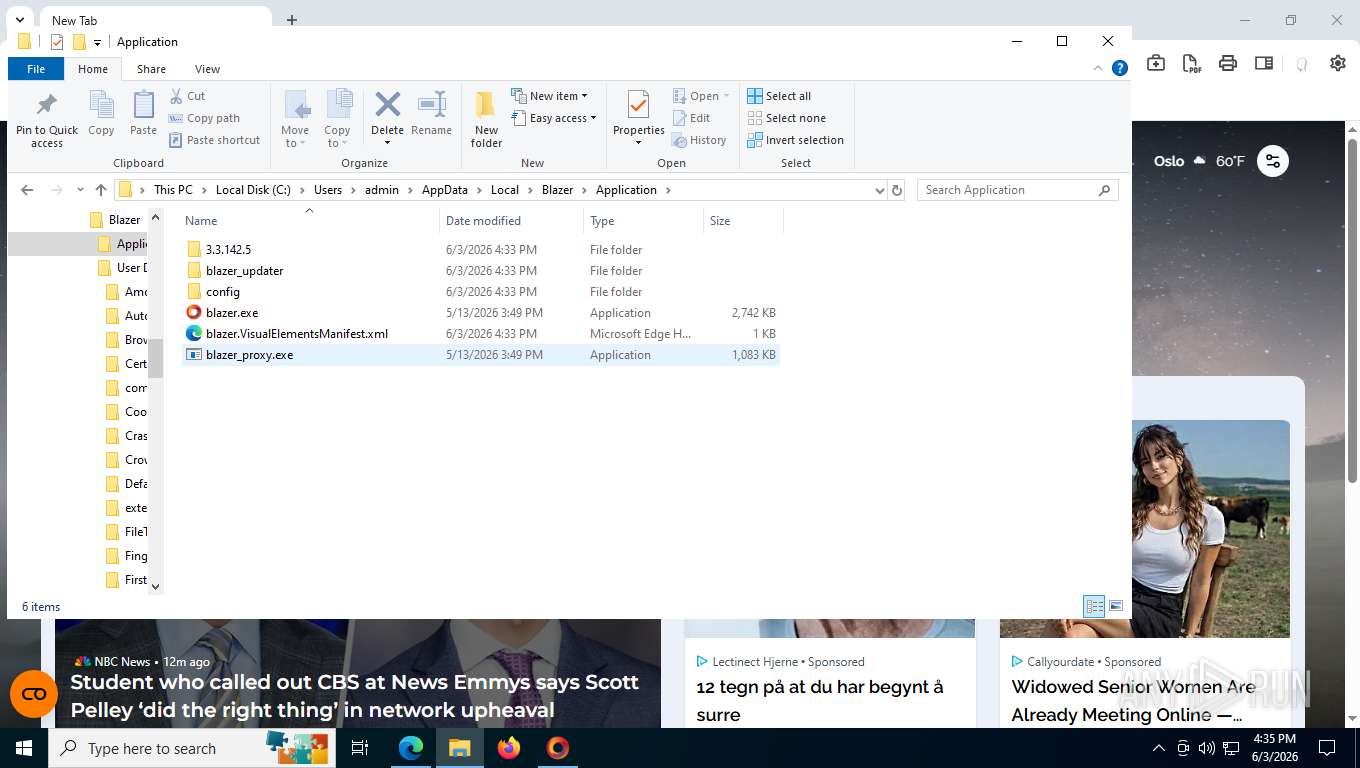
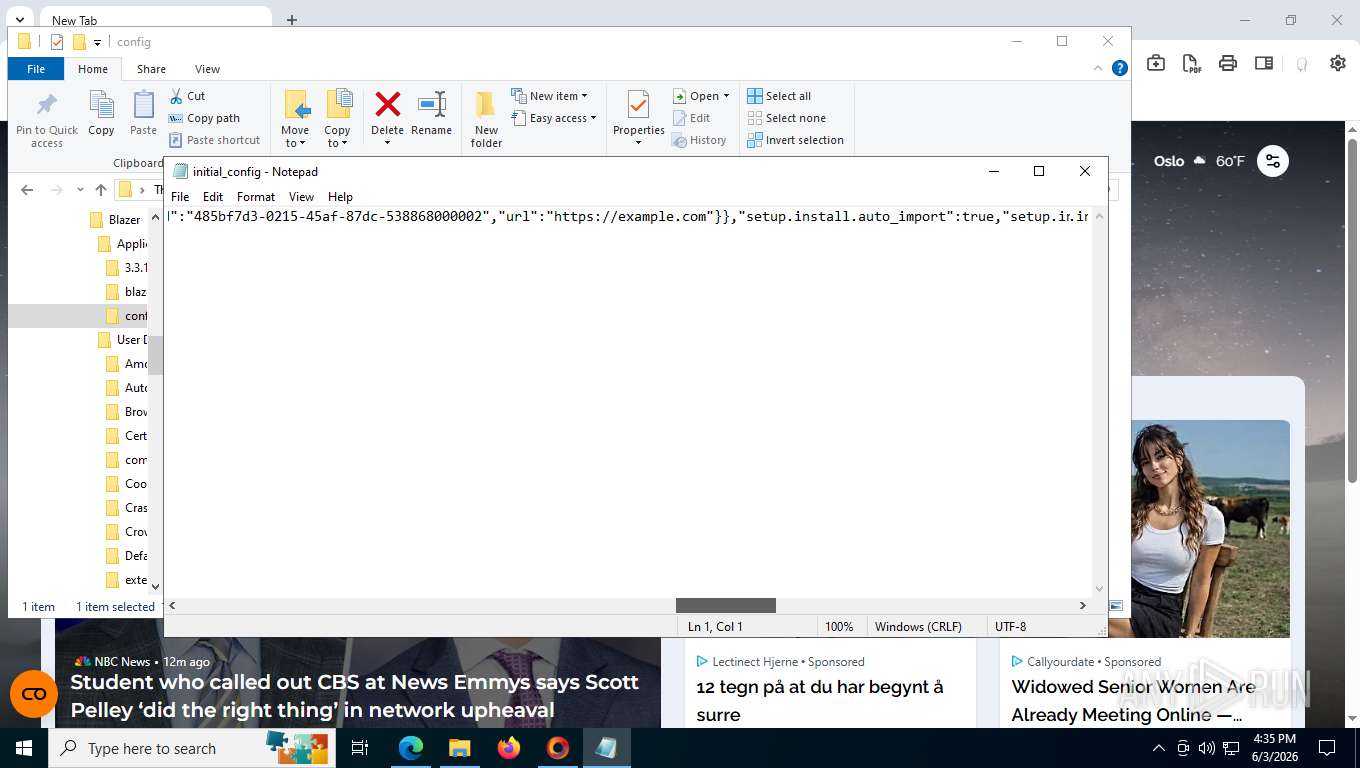
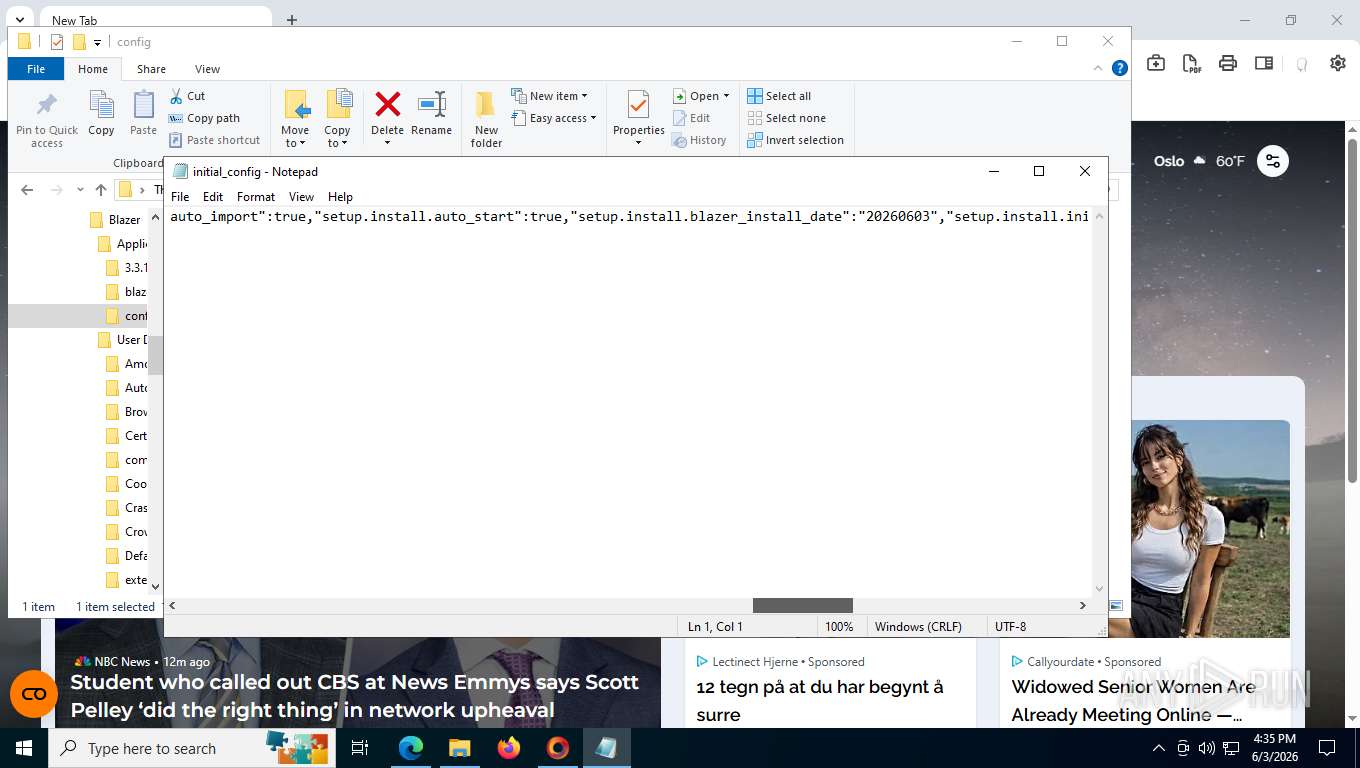
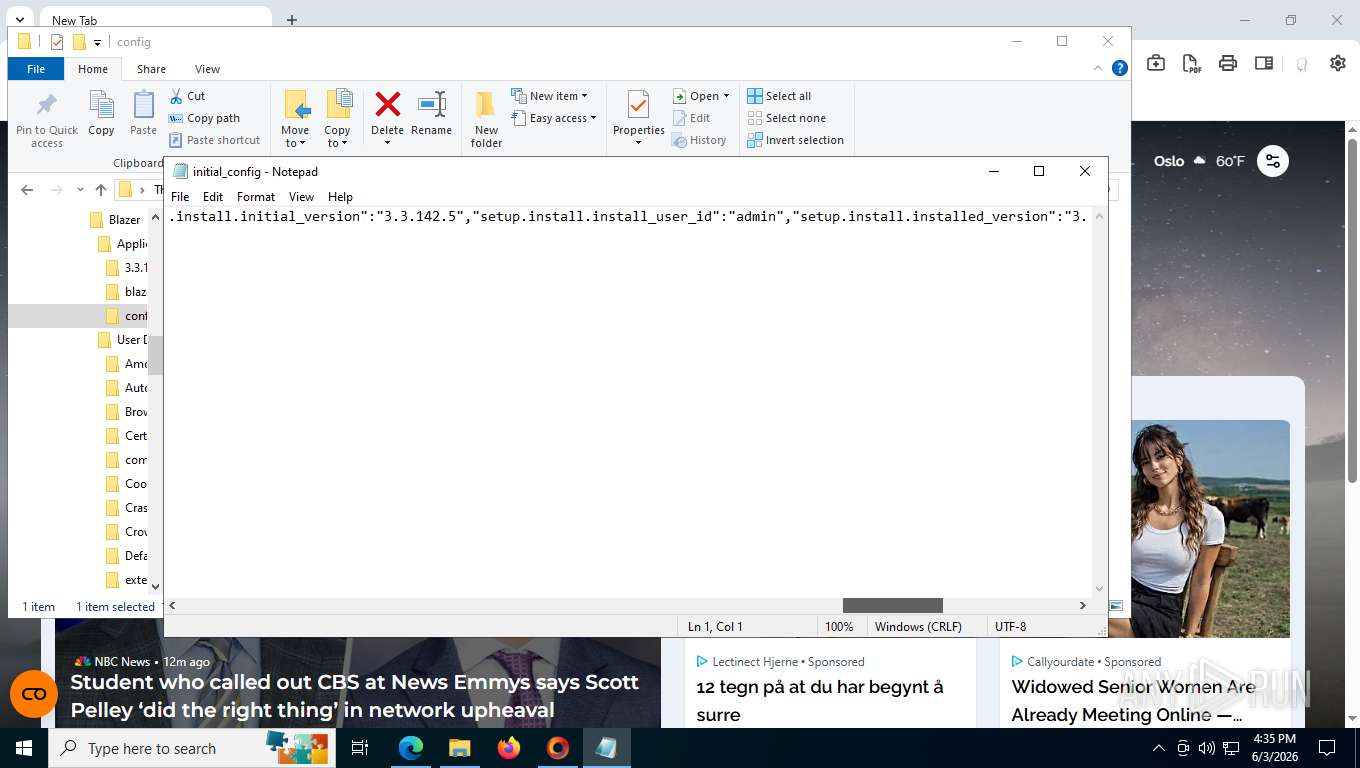
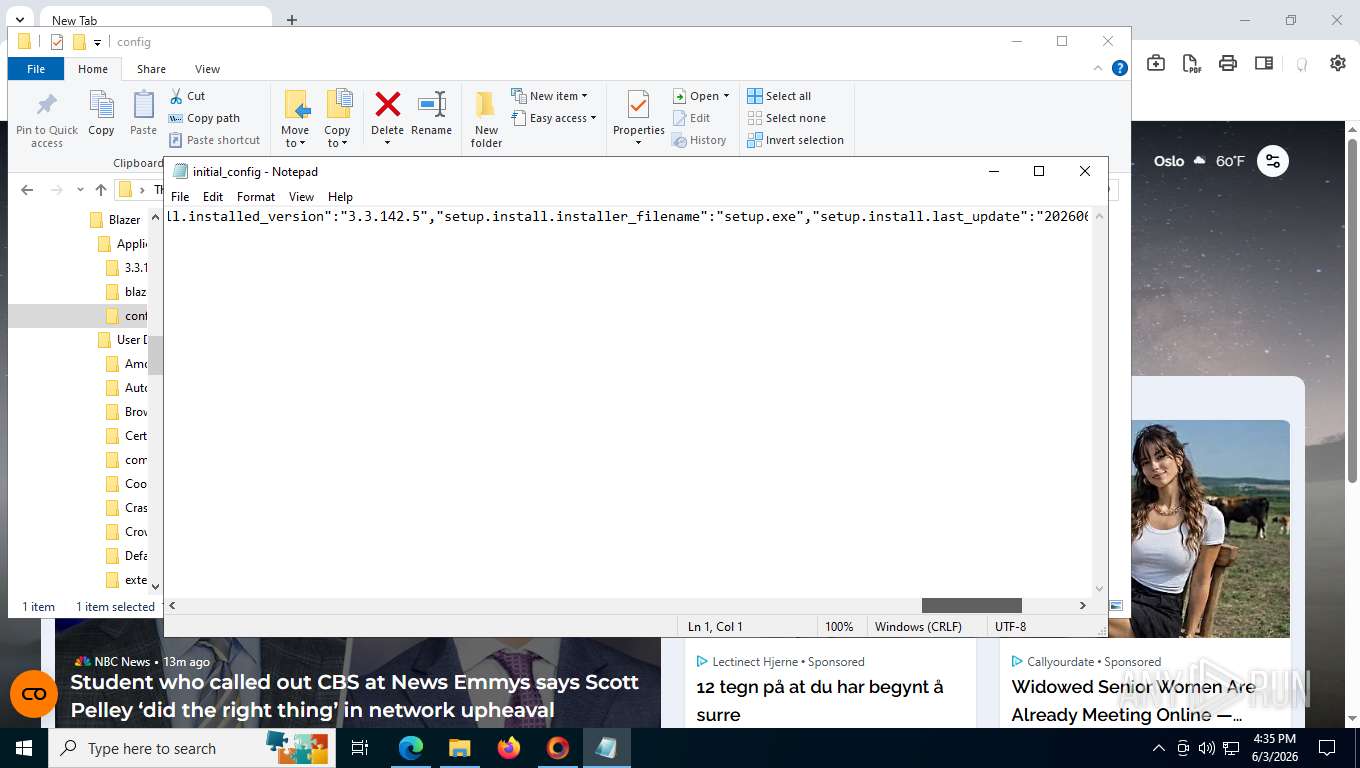
| 2724 | "C:\Users\admin\AppData\Local\Blazer\Application\blazer.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --lang=en-US --service-sandbox-type=service --force-high-res-timeticks=disabled --metrics-shmem-handle=5224,i,6088447127127715202,12892044016659073618,524288 --field-trial-handle=1912,i,6802338577896190940,9711079046119911716,262144 --variations-seed-version --trace-process-track-uuid=3190709000367499229 --mojo-platform-channel-handle=5212 /prefetch:8 | C:\Users\admin\AppData\Local\Blazer\Application\blazer.exe | — | blazer.exe | |||||||||||
User: admin Company: The Blazer Authors Integrity Level: LOW Description: Blazer Exit code: 0 Version: 3.3.142.5 Modules
| |||||||||||||||
| 2896 | C:\Users\admin\AppData\Local\Blazer\Application\blazer.exe --type=crashpad-handler "--user-data-dir=C:\Users\admin\AppData\Local\Blazer\User Data" /prefetch:4 --monitor-self-annotation=ptype=crashpad-handler "--database=C:\Users\admin\AppData\Local\Blazer\User Data\Crashpad" --annotation=plat=Win64 --annotation=prod=Blazer --annotation=ver=3.3.142.5 --initial-client-data=0x124,0x128,0x12c,0x100,0x130,0x7ffe271da1b8,0x7ffe271da1c4,0x7ffe271da1d0 | C:\Users\admin\AppData\Local\Blazer\Application\blazer.exe | — | blazer.exe | |||||||||||
User: admin Company: The Blazer Authors Integrity Level: MEDIUM Description: Blazer Version: 3.3.142.5 Modules
| |||||||||||||||
| 2912 | "C:\Users\admin\AppData\Local\Blazer\Application\blazer.exe" --type=gpu-process --disable-gpu-sandbox --use-gl=disabled --gpu-vendor-id=5140 --gpu-device-id=140 --gpu-sub-system-id=0 --gpu-revision=0 --gpu-driver-version=10.0.19041.3636 --force-high-res-timeticks=disabled --start-stack-profiler --gpu-preferences=SAAAAAAAAADoAQAEAAAAAAAAAAAAAMAAAAAAAAAAAAAAAAAAAAAAAEIAAAAAAAAAAAAAAAAAAAAQAAAAAAAAABAAAAAAAAAACAAAAAAAAAAIAAAAAAAAAA== --use-gl=disabled --metrics-shmem-handle=3780,i,15852180338188150359,14177700168427550414,262144 --field-trial-handle=1912,i,6802338577896190940,9711079046119911716,262144 --variations-seed-version --trace-process-track-uuid=3190709003178624776 --mojo-platform-channel-handle=6508 /prefetch:8 | C:\Users\admin\AppData\Local\Blazer\Application\blazer.exe | — | blazer.exe | |||||||||||
User: admin Company: The Blazer Authors Integrity Level: MEDIUM Description: Blazer Exit code: 0 Version: 3.3.142.5 Modules
| |||||||||||||||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 9136 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\ClientCertificates\LOG.old~RF1593ae.TMP | — | |
MD5:— | SHA256:— | |||
| 9136 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\ClientCertificates\LOG.old | — | |
MD5:— | SHA256:— | |||
| 9136 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\discounts_db\LOG.old~RF1593be.TMP | — | |
MD5:— | SHA256:— | |||
| 9136 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\discounts_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 9136 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\PersistentOriginTrials\LOG.old~RF1593be.TMP | — | |
MD5:— | SHA256:— | |||
| 9136 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\commerce_subscription_db\LOG.old~RF1593be.TMP | — | |
MD5:— | SHA256:— | |||
| 9136 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\PersistentOriginTrials\LOG.old | — | |
MD5:— | SHA256:— | |||
| 9136 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\commerce_subscription_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 9136 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\LOG.old~RF1593cd.TMP | — | |
MD5:— | SHA256:— | |||
| 9136 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\parcel_tracking_db\LOG.old~RF1593be.TMP | — | |
MD5:— | SHA256:— | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
6640 | msedge.exe | GET | 200 | 150.171.22.17:443 | https://config.edge.skype.com/config/v1/Edge/133.0.3065.92?clientId=4489578223053569932&agents=Edge%2CEdgeConfig%2CEdgeServices%2CEdgeFirstRun%2CEdgeFirstRunConfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=71&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0 | US | text | 8.00 Kb | whitelisted |
6640 | msedge.exe | GET | 200 | 150.171.27.11:443 | https://edge.microsoft.com/serviceexperimentation/v3/?osname=win&channel=stable&osver=10.0.19045&devicefamily=desktop&installdate=1661339457&clientversion=133.0.3065.92&experimentationmode=2&scpguard=0&scpfull=0&scpver=0 | US | text | 132 b | whitelisted |
6640 | msedge.exe | GET | 200 | 104.18.23.222:443 | https://copilot.microsoft.com/c/api/user/eligibility | US | text | 25 b | whitelisted |
6640 | msedge.exe | GET | 200 | 150.171.109.193:443 | https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appId=edge-extensions&country=US | US | binary | 82 b | whitelisted |
6640 | msedge.exe | GET | 200 | 150.171.109.100:443 | https://get-blazer.com/install?id=XKDnTjcC&navigated_from_root=1&utm_source=google&utm_medium=display&source=BB1&campaign=23655303495&adgroup=195871852442&creative=800566387420&placement=www.calendar-12.com&term=&gclid=EAIaIQobChMI0_qpstPrlAMV_LQDAR2etTL3EAEYASAAEgKbDfD_BwE&gad_source=5&gad_campaignid=23655303495&gclid=EAIaIQobChMI0_qpstPrlAMV_LQDAR2etTL3EAEYASAAEgKbDfD_BwE | US | html | 11.5 Kb | unknown |
6640 | msedge.exe | GET | 200 | 150.171.27.11:80 | http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:ZIRMKTh_S7iq-Ygyq_riZnF4CrxAT2nQ8VmO-4LqVAY&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855 | US | text | 101 b | whitelisted |
6640 | msedge.exe | GET | 200 | 150.171.109.100:443 | https://get-blazer.com/next-js-static-files/_next/static/chunks/0cnh.v6-y~glq.css | US | text | 23.9 Kb | unknown |
6640 | msedge.exe | GET | 200 | 150.171.109.100:443 | https://get-blazer.com/next-js-static-files/_next/static/chunks/0j18mdkvnuk-1.css | US | text | 1.36 Kb | unknown |
6640 | msedge.exe | GET | 200 | 150.171.109.100:443 | https://get-blazer.com/next-js-static-files/_next/static/chunks/0k0x_.kvacbkw.js | US | text | 29.0 Kb | unknown |
6640 | msedge.exe | GET | 200 | 150.171.109.100:443 | https://get-blazer.com/next-js-static-files/_next/static/chunks/0cje14_narrpx.js | US | text | 51.3 Kb | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | Not routed | — | whitelisted |
3068 | svchost.exe | 48.209.138.168:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5276 | MoUsoCoreWorker.exe | 48.209.138.168:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
— | — | 48.192.1.64:443 | activation-v2.sls.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5532 | SearchApp.exe | 2.16.204.156:443 | www.bing.com | AKAMAI-ASN1 | NL | whitelisted |
— | — | 23.11.40.157:80 | ocsp.digicert.com | AKAMAI-AMS | NL | whitelisted |
4 | System | 192.168.100.255:138 | — | Not routed | — | whitelisted |
6640 | msedge.exe | 150.171.22.17:443 | config.edge.skype.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
6640 | msedge.exe | 150.171.27.11:80 | edge.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
6640 | msedge.exe | 150.171.27.11:443 | edge.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
activation-v2.sls.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
www.bing.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
edge.microsoft.com |
| whitelisted |
config.edge.skype.com |
| whitelisted |
get-blazer.com |
| unknown |
api.edgeoffer.microsoft.com |
| whitelisted |
copilot.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
6640 | msedge.exe | Not Suspicious Traffic | INFO [ANY.RUN] Google Tag Manager analytics (googletagmanager .com) |
6640 | msedge.exe | Not Suspicious Traffic | INFO [ANY.RUN] Google Tag Manager analytics (googletagmanager .com) |
6640 | msedge.exe | Not Suspicious Traffic | INFO [ANY.RUN] Google Tag Manager analytics (googletagmanager .com) |
6640 | msedge.exe | Generic Protocol Command Decode | SURICATA HTTP Response excessive header repetition |
6640 | msedge.exe | Generic Protocol Command Decode | SURICATA HTTP Response excessive header repetition |
3068 | svchost.exe | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |
6640 | msedge.exe | Generic Protocol Command Decode | SURICATA HTTP Response excessive header repetition |
6640 | msedge.exe | Generic Protocol Command Decode | SURICATA HTTP Response excessive header repetition |
6640 | msedge.exe | Not Suspicious Traffic | INFO [ANY.RUN] Azure Blob Storage (.blob .core .windows .net) |
6640 | msedge.exe | Not Suspicious Traffic | INFO [ANY.RUN] Azure Blob Storage (.blob .core .windows .net) |