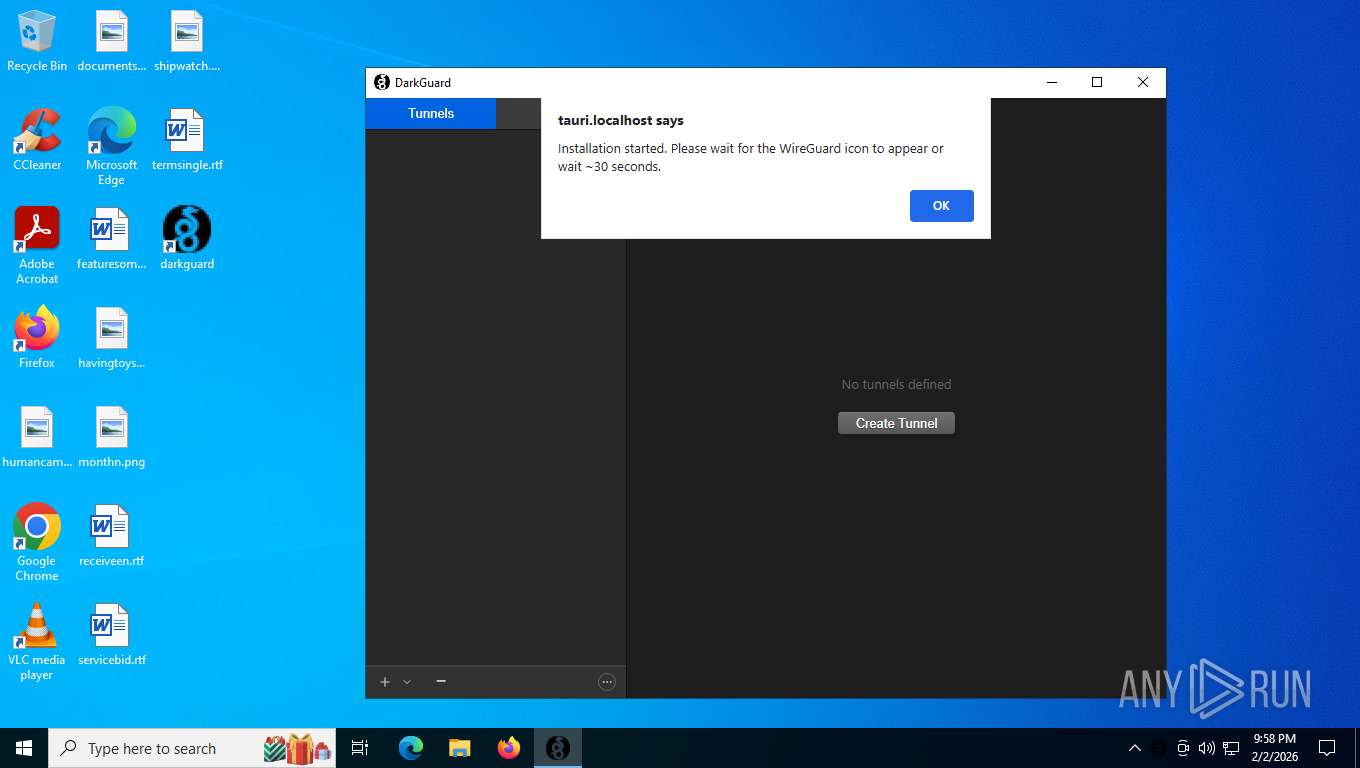
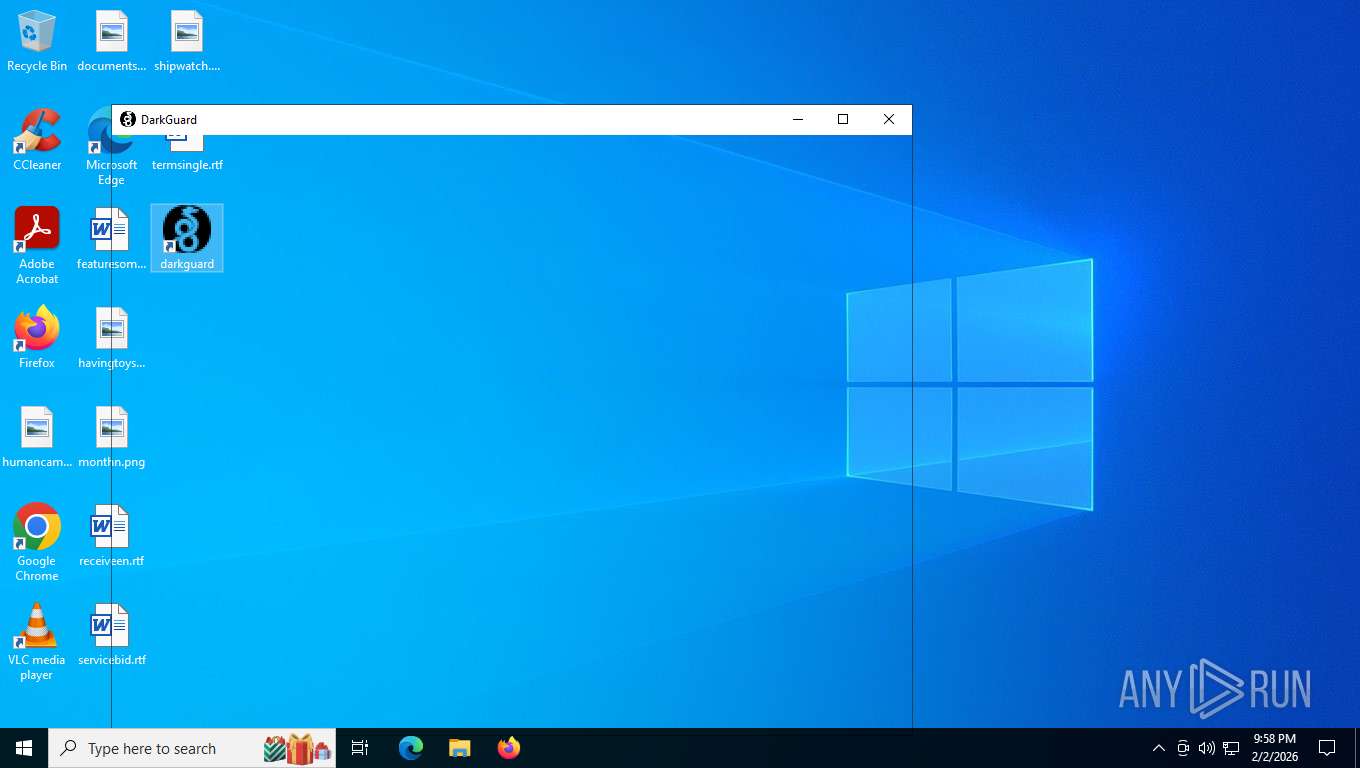
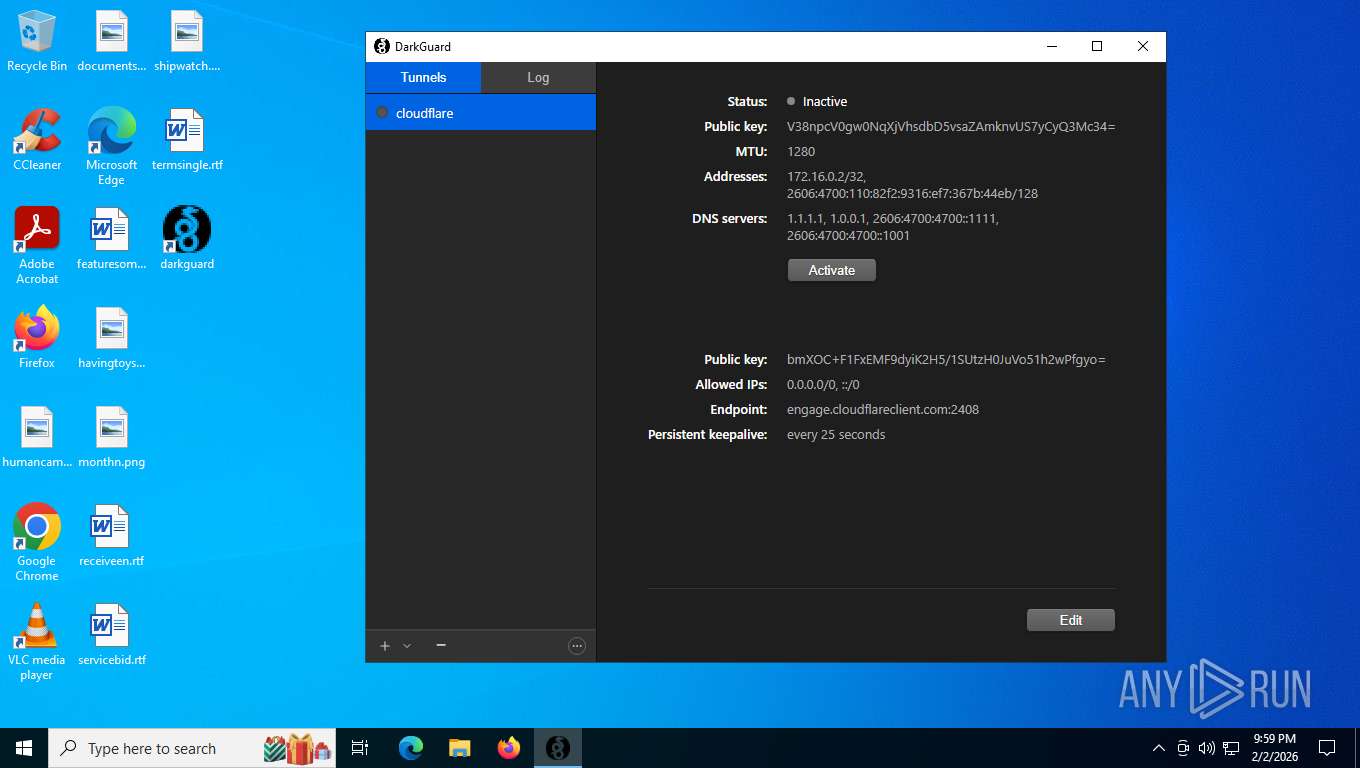
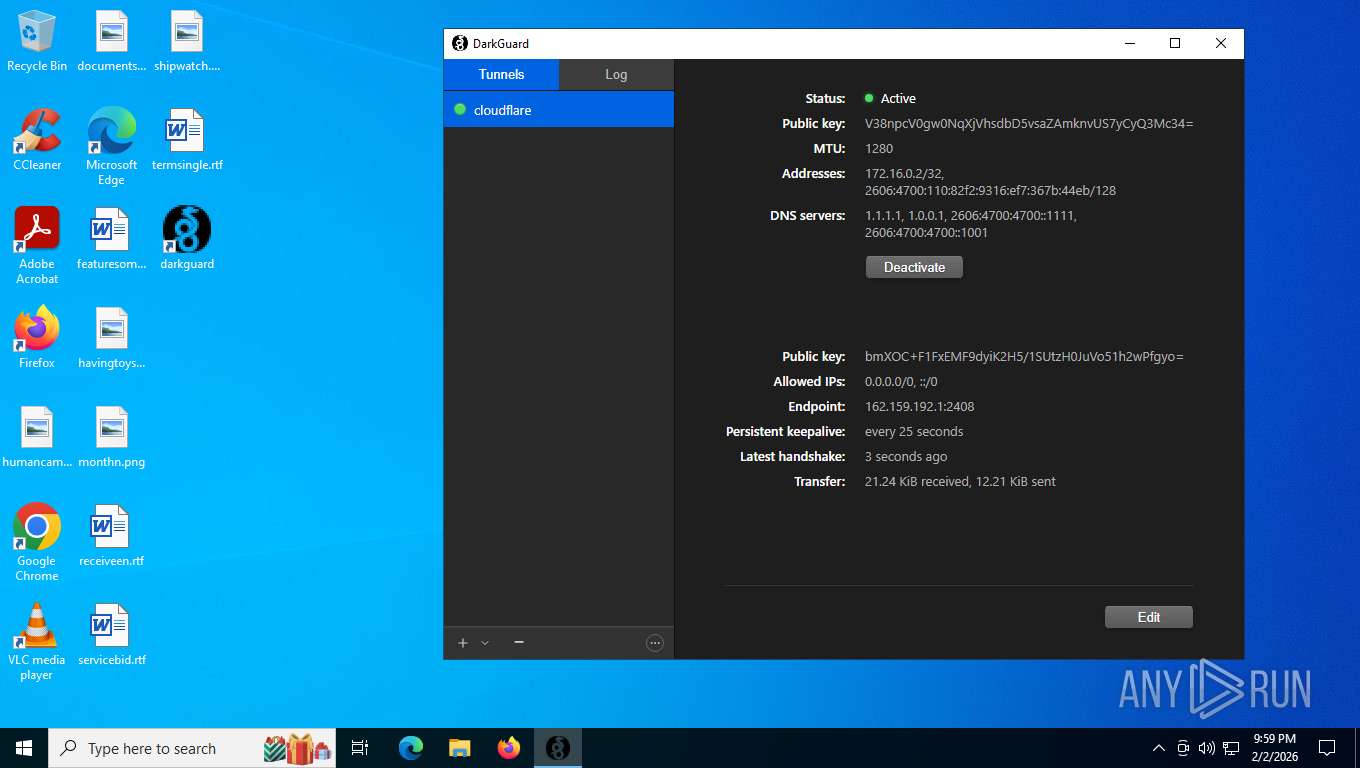
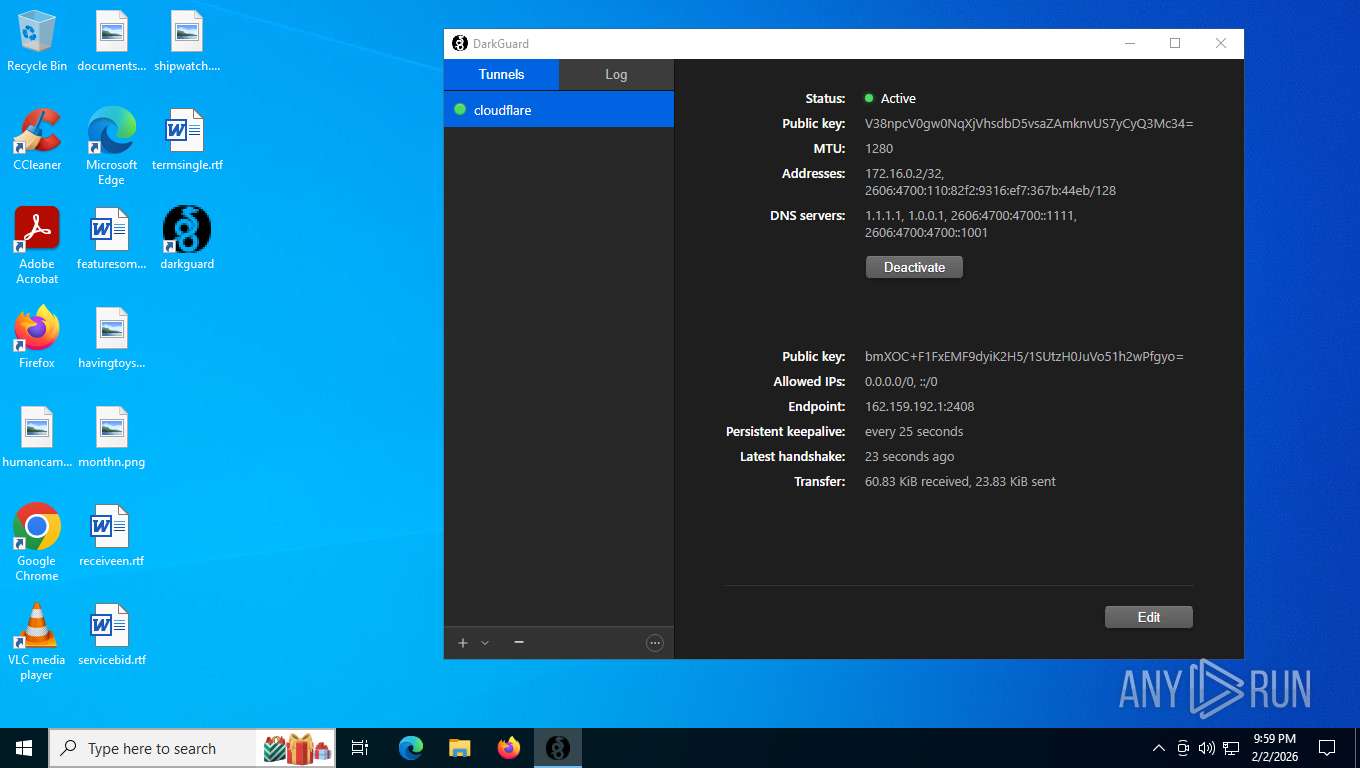
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
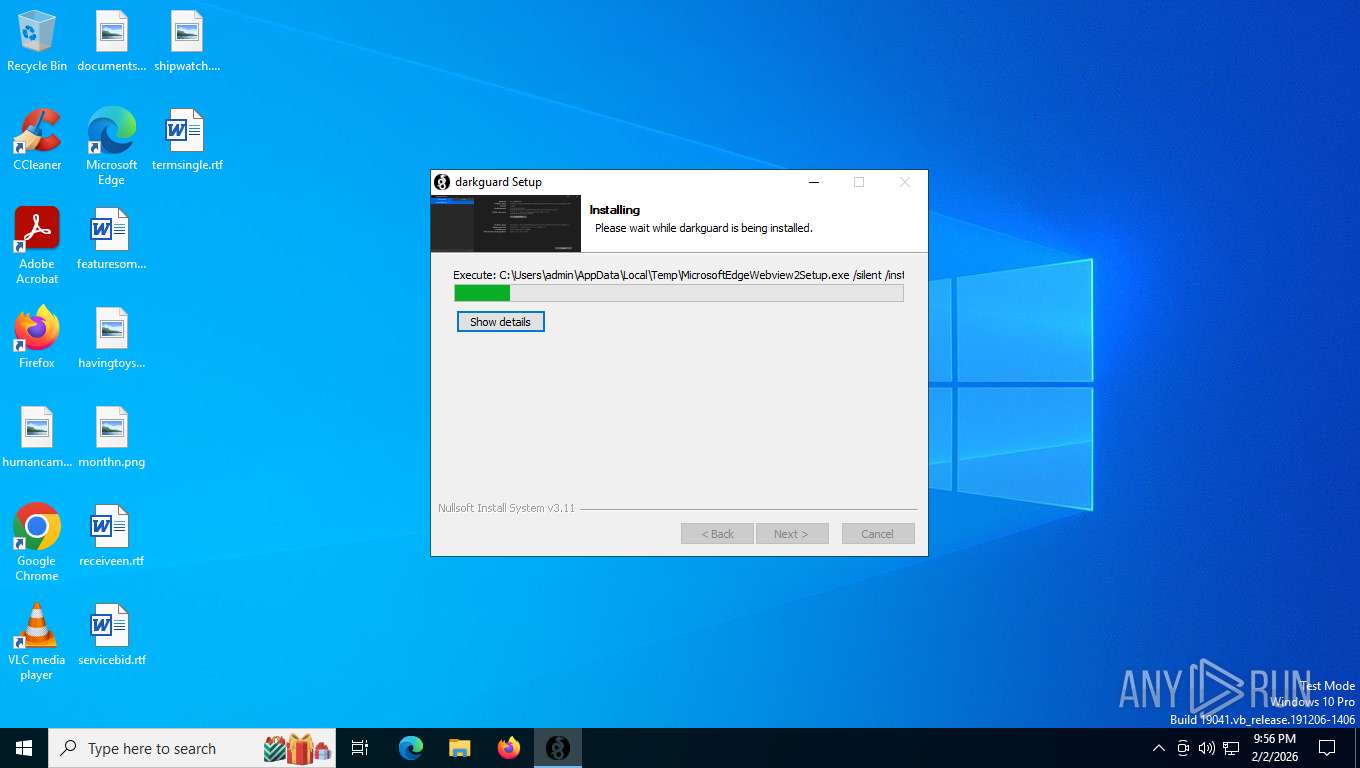
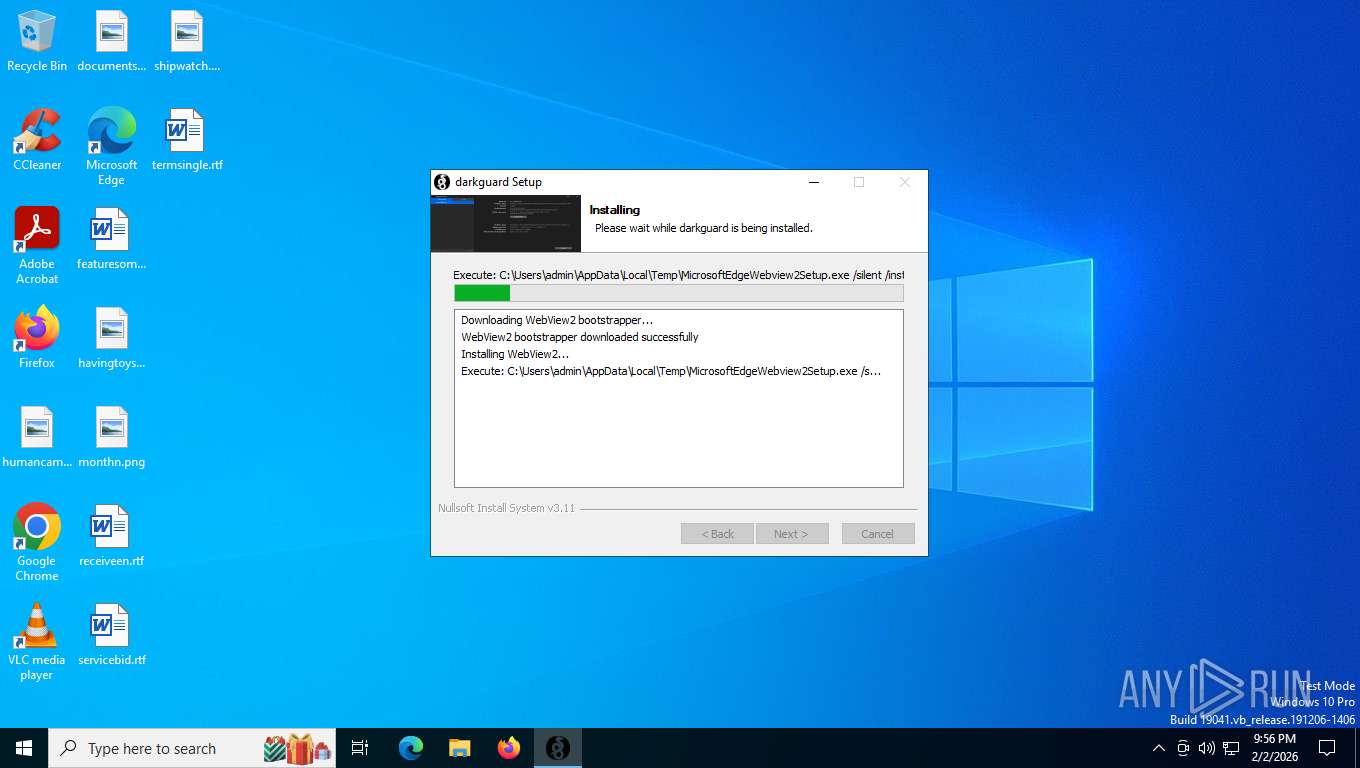
| File name: | darkguard_0.1.0_x64-setup.exe |
| Full analysis: | https://app.any.run/tasks/e21215e3-ed9c-48a9-9afe-785a95dde82e |
| Verdict: | Malicious activity |
| Threats: | A loader is malicious software that infiltrates devices to deliver malicious payloads. This malware is capable of infecting victims’ computers, analyzing their system information, and installing other types of threats, such as trojans or stealers. Criminals usually deliver loaders through phishing emails and links by relying on social engineering to trick users into downloading and running their executables. Loaders employ advanced evasion and persistence tactics to avoid detection. |
| Analysis date: | February 03, 2026, 02:56:28 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, Nullsoft Installer self-extracting archive, 5 sections |
| MD5: | 57963CD0C8613D7CEBB7216E5FC5CB2D |
| SHA1: | C8177AD2390A752F07202E1E74C29D15E664888B |
| SHA256: | 230B91DD4ECB22CA7333C3ED76032A392AC3EE1CE07813A12DD04665D58DB24D |
| SSDEEP: | 98304:x0z13sQ3jThjAGDbqYn8ho15qtKWSLBH8gq+gaPOKkDMwtAFZFSmCpP9bfTVHZO8:qxxy |
| .exe | | | Win32 Executable MS Visual C++ (generic) (67.4) |
|---|---|---|
| .dll | | | Win32 Dynamic Link Library (generic) (14.2) |
| .exe | | | Win32 Executable (generic) (9.7) |
| .exe | | | Generic Win/DOS Executable (4.3) |
| .exe | | | DOS Executable Generic (4.3) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2025:03:08 23:05:20+00:00 |
| ImageFileCharacteristics: | No relocs, Executable, No line numbers, No symbols, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 6 |
| CodeSize: | 26624 |
| InitializedDataSize: | 139776 |
| UninitializedDataSize: | 2048 |
| EntryPoint: | 0x369f |
| OSVersion: | 4 |
| ImageVersion: | 6 |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 0.1.0.0 |
| ProductVersionNumber: | 0.1.0.0 |
| FileFlagsMask: | 0x0000 |
| FileFlags: | (none) |
| FileOS: | Win32 |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | English (U.S.) |
| CharacterSet: | Unicode |
| FileDescription: | darkguard |
| FileVersion: | 0.1.0 |
| LegalCopyright: | - |
| ProductName: | darkguard |
| ProductVersion: | 0.1.0 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 148 | "sc" query WireGuardTunnel$cloudflare | C:\Windows\System32\sc.exe | — | DarkGuard.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Service Control Manager Configuration Tool Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 752 | "C:\Program Files\WireGuard\wireguard.exe" /tunnelservice C:\Users\admin\AppData\Local\Temp\cloudflare.conf | C:\Program Files\WireGuard\wireguard.exe | services.exe | ||||||||||||
User: SYSTEM Company: WireGuard LLC Integrity Level: SYSTEM Description: WireGuard: Fast, Modern, Secure VPN Tunnel Exit code: 0 Version: 0.5.3 Modules
| |||||||||||||||
| 876 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | powershell.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 888 | C:\WINDOWS\system32\SppExtComObj.exe -Embedding | C:\Windows\System32\SppExtComObj.Exe | — | svchost.exe | |||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: KMS Connection Broker Version: 10.0.19041.3996 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1044 | "C:\Program Files (x86)\Microsoft\EdgeUpdate\MicrosoftEdgeUpdate.exe" /regsvc | C:\Program Files (x86)\Microsoft\EdgeUpdate\MicrosoftEdgeUpdate.exe | — | MicrosoftEdgeUpdate.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Microsoft Edge Update Exit code: 0 Version: 1.3.217.3 Modules
| |||||||||||||||
| 1084 | "sc" query WireGuardTunnel$cloudflare | C:\Windows\System32\sc.exe | — | DarkGuard.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Service Control Manager Configuration Tool Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1092 | "powershell" -NoProfile -Command "Start-Process 'C:\Program Files\WireGuard\wireguard.exe' -ArgumentList '/uninstalltunnelservice', 'cloudflare' -Verb RunAs -WindowStyle Hidden -Wait" | C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe | — | DarkGuard.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows PowerShell Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1128 | DrvInst.exe "4" "9" "C:\WINDOWS\Temp\20fd762521a3b73c22f36d3fa26728d7cf2cb03caa0b4be4bab0b5a6fd696395\wireguard.inf" "9" "43f3a2977" "00000000000001CC" "Service-0x0-3e7$\Default" "00000000000001D4" "208" "C:\WINDOWS\Temp\20fd762521a3b73c22f36d3fa26728d7cf2cb03caa0b4be4bab0b5a6fd696395" | C:\Windows\System32\drvinst.exe | — | svchost.exe | |||||||||||
User: SYSTEM Company: Microsoft Corporation Integrity Level: SYSTEM Description: Driver Installation Module Exit code: 0 Version: 10.0.19041.3996 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1128 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | sc.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1340 | "C:\Program Files (x86)\Microsoft\EdgeWebView\Application\144.0.3719.93\msedgewebview2.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --lang=en-US --service-sandbox-type=service --noerrdialogs --user-data-dir="C:\Users\admin\AppData\Local\systems.banat.darkguard\EBWebView" --webview-exe-name=DarkGuard.exe --webview-exe-version=0.1.0 --embedded-browser-webview=1 --embedded-browser-webview-dpi-awareness=2 --skip-read-main-dll --metrics-shmem-handle=4120,i,11456158096244038381,11692542832399373015,524288 --field-trial-handle=1860,i,9190552724943748697,17610928704542699058,262144 --disable-features=msPdfOOUI,msSmartScreenProtection,msWebOOUI --variations-seed-version --trace-process-track-uuid=3190708995682289984 --mojo-platform-channel-handle=4108 /prefetch:8 | C:\Program Files (x86)\Microsoft\EdgeWebView\Application\144.0.3719.93\msedgewebview2.exe | — | msedgewebview2.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge WebView2 Exit code: 0 Version: 144.0.3719.93 Modules
| |||||||||||||||
| (PID) Process: | (1044) MicrosoftEdgeUpdate.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\AppID\{CECDDD22-2E72-4832-9606-A9B0E5E344B2} |
| Operation: | delete key | Name: | (default) |
Value: | |||
| (PID) Process: | (1044) MicrosoftEdgeUpdate.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\AppID\MicrosoftEdgeUpdate.exe |
| Operation: | delete key | Name: | (default) |
Value: | |||
| (PID) Process: | (1044) MicrosoftEdgeUpdate.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\AppID\MicrosoftEdgeUpdate.exe |
| Operation: | write | Name: | AppID |
Value: {CECDDD22-2E72-4832-9606-A9B0E5E344B2} | |||
| (PID) Process: | (1044) MicrosoftEdgeUpdate.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\AppID\{CECDDD22-2E72-4832-9606-A9B0E5E344B2} |
| Operation: | write | Name: | LocalService |
Value: edgeupdate | |||
| (PID) Process: | (1044) MicrosoftEdgeUpdate.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\AppID\{CECDDD22-2E72-4832-9606-A9B0E5E344B2} |
| Operation: | write | Name: | ServiceParameters |
Value: /comsvc | |||
| (PID) Process: | (1044) MicrosoftEdgeUpdate.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\EventLog\Application\edgeupdate |
| Operation: | write | Name: | EventMessageFile |
Value: C:\Program Files (x86)\Microsoft\EdgeUpdate\1.3.217.3\msedgeupdate.dll | |||
| (PID) Process: | (1044) MicrosoftEdgeUpdate.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\WOW6432Node\CLSID\{CECDDD22-2E72-4832-9606-A9B0E5E344B2}\ProgID |
| Operation: | delete key | Name: | (default) |
Value: | |||
| (PID) Process: | (1044) MicrosoftEdgeUpdate.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\WOW6432Node\CLSID\{CECDDD22-2E72-4832-9606-A9B0E5E344B2}\VersionIndependentProgID |
| Operation: | delete key | Name: | (default) |
Value: | |||
| (PID) Process: | (1044) MicrosoftEdgeUpdate.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\WOW6432Node\CLSID\{CECDDD22-2E72-4832-9606-A9B0E5E344B2} |
| Operation: | delete key | Name: | (default) |
Value: | |||
| (PID) Process: | (1044) MicrosoftEdgeUpdate.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Classes\WOW6432Node\CLSID\{CECDDD22-2E72-4832-9606-A9B0E5E344B2} |
| Operation: | write | Name: | AppID |
Value: {CECDDD22-2E72-4832-9606-A9B0E5E344B2} | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 7392 | darkguard_0.1.0_x64-setup.exe | C:\Users\admin\AppData\Local\Temp\nsw50B0.tmp\NSISdl.dll | executable | |
MD5:8EABBE36E8B52E69322780D0F541FD19 | SHA256:DDF40229DD9D6B268902D8DEA88C8A04AACF1AF218DD29F6DCD35BABC54AC08D | |||
| 7392 | darkguard_0.1.0_x64-setup.exe | C:\Users\admin\AppData\Local\Temp\nsw50B0.tmp\nsDialogs.dll | executable | |
MD5:8F0E7415F33843431DF308BB8E06AF81 | SHA256:BB49F15FA83452370047A7801E39FC7F64E70C7545B8999BB85AA4749EAA048B | |||
| 3516 | MicrosoftEdgeWebview2Setup.exe | C:\Program Files (x86)\Microsoft\Temp\EU5FF0.tmp\MicrosoftEdgeUpdateBroker.exe | executable | |
MD5:229AF2A53A7B3741BE616C1648637D47 | SHA256:BC8A862A95852B7D102C99910DABE38DD053E54D7ED8C40743AEB9B6A82AC4E5 | |||
| 7392 | darkguard_0.1.0_x64-setup.exe | C:\Users\admin\AppData\Local\Temp\nsw50B0.tmp\modern-header.bmp | image | |
MD5:368F434F2B74417F540EF920B66F4554 | SHA256:518EECCACEFC90B8839F50A36A89EE8B8600039C08CE1EC101D900E2A3EC2DC1 | |||
| 3516 | MicrosoftEdgeWebview2Setup.exe | C:\Program Files (x86)\Microsoft\Temp\EU5FF0.tmp\msedgeupdate.dll | executable | |
MD5:05A084F88F628C5EAD832619EB9E5E77 | SHA256:275F6BF9750EDED145E37B11DFA7C0580C88036E80C21395E8A4A77C66D51090 | |||
| 7392 | darkguard_0.1.0_x64-setup.exe | C:\Users\admin\AppData\Local\Temp\nsw50B0.tmp\modern-wizard.bmp | image | |
MD5:631227DF085BA169C1EC73327757EE1D | SHA256:E92EC1F4F133E41F1A2010788F05D567DE720A809D5091BBD762EB29FDE8F17C | |||
| 3516 | MicrosoftEdgeWebview2Setup.exe | C:\Program Files (x86)\Microsoft\Temp\EU5FF0.tmp\MicrosoftEdgeUpdateOnDemand.exe | executable | |
MD5:AFF93DDDA4796969CCC666B27FFEBC2E | SHA256:C0FA7B89F6A590D27AF4EE253920663CE9B10B0384DCE16AF666B0186B165F9C | |||
| 3516 | MicrosoftEdgeWebview2Setup.exe | C:\Program Files (x86)\Microsoft\Temp\EU5FF0.tmp\MicrosoftEdgeUpdateComRegisterShell64.exe | executable | |
MD5:36C60AC823BFF242FA1D4242D3FF6142 | SHA256:3CD8B4669F1E9EB22CBA842E79CE8A35F19E278D38E2D042D66752AD8EA75317 | |||
| 3516 | MicrosoftEdgeWebview2Setup.exe | C:\Program Files (x86)\Microsoft\Temp\EU5FF0.tmp\psmachine.dll | executable | |
MD5:843CAB3CD6A42071AA35D685F641D0AC | SHA256:6EF9B52D37339FAD9C7933C4D70D223EA54474AC9698A068EA5D139A7281CED6 | |||
| 7392 | darkguard_0.1.0_x64-setup.exe | C:\Users\admin\AppData\Local\Temp\nsw50B0.tmp\System.dll | executable | |
MD5:9B38A1B07A0EBC5C7E59E63346ECC2DB | SHA256:C881253DAFCF1322A771139B1A429EC1E78C507CA81A218A20DC1A4B25ABBFE7 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
6768 | MoUsoCoreWorker.exe | GET | 304 | 4.231.128.59:443 | https://settings-win.data.microsoft.com/settings/v3.0/OneSettings/Client?OSVersionFull=10.0.19045.4046.amd64fre.vb_release.191206-1406&LocalDeviceID=s%3ABAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&FlightRing=Retail&AttrDataVer=186&OSUILocale=en-US&OSSkuId=48&App=WOSC&AppVer=&IsFlightingEnabled=0&TelemetryLevel=1&DeviceFamily=Windows.Desktop | US | — | — | whitelisted |
7428 | svchost.exe | GET | 304 | 4.231.128.59:443 | https://settings-win.data.microsoft.com/settings/v3.0/WSD/UpdateHealthTools?os=Windows&osVer=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceClass=Windows.Desktop&locale=en-US&deviceId=s:BAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&sampleId=s:95271487&appVer=10.0.19041.3626&FlightRing=Retail&TelemetryLevel=1&HidOverGattReg=C%3A%5CWINDOWS%5CSystem32%5CDriverStore%5CFileRepository%5Chidbthle.inf_amd64_9610b4821fdf82a5%5CMicrosoft.Bluetooth.Profiles.HidOverGatt.dll&AppVer=&ProcessorIdentifier=AMD64%20Family%2023%20Model%201%20Stepping%202&OEMModel=DELL&UpdateOfferedDays=4294967295&ProcessorManufacturer=AuthenticAMD&InstallDate=1661339444&OEMModelBaseBoard=&BranchReadinessLevel=CB&OEMSubModel=J5CR&IsCloudDomainJoined=0&DeferFeatureUpdatePeriodInDays=30&IsDeviceRetailDemo=0&FlightingBranchName=&OSUILocale=en-US&DeviceFamily=Windows.Desktop&WuClientVer=10.0.19041.3996&UninstallActive=1&IsFlightingEnabled=0&OSSkuId=48&ProcessorClockSpeed=3094&TotalPhysicalRAM=6144&SecureBootCapable=0&App=SedimentPack&ProcessorCores=6&CurrentBranch=vb_release&InstallLanguage=en-US&DeferQualityUpdatePeriodInDays=0&OEMName_Uncleaned=DELL&TPMVersion=0&PrimaryDiskTotalCapacity=262144&InstallationType=Client&AttrDataVer=186&ProcessorModel=AMD%20Ryzen%205%203500%206-Core%20Processor&IsEdgeWithChromiumInstalled=1&OSVersion=10.0.19045.4046&IsMDMEnrolled=0&ActivationChannel=Retail&FirmwareVersion=A.40&TrendInstalledKey=1&OSArchitecture=AMD64&DefaultUserRegion=244&UpdateManagementGroup=2 | US | — | — | whitelisted |
4544 | SIHClient.exe | GET | 304 | 74.178.240.61:443 | https://slscr.update.microsoft.com/SLS/%7B522D76A4-93E1-47F8-B8CE-07C937AD1A1E%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL | US | — | — | whitelisted |
4544 | SIHClient.exe | GET | 200 | 40.69.42.241:443 | https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping | US | — | — | whitelisted |
4544 | SIHClient.exe | GET | 200 | 74.178.240.61:443 | https://slscr.update.microsoft.com/sls/ping | US | — | — | whitelisted |
4544 | SIHClient.exe | GET | 304 | 74.178.240.61:443 | https://slscr.update.microsoft.com/SLS/%7BE7A50285-D08D-499D-9FF8-180FDC2332BC%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL | US | — | — | whitelisted |
7392 | darkguard_0.1.0_x64-setup.exe | GET | 301 | 88.221.169.205:80 | http://go.microsoft.com/fwlink/p/?LinkId=2124703 | US | — | — | whitelisted |
356 | svchost.exe | GET | 200 | 2.17.190.73:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
7392 | darkguard_0.1.0_x64-setup.exe | GET | 200 | 199.232.210.172:80 | http://msedge.sf.dl.delivery.mp.microsoft.com/filestreamingservice/files/6610a652-5edd-4c88-99ad-6d23094fd465/MicrosoftEdgeWebview2Setup.exe | US | executable | 1.60 Mb | whitelisted |
7428 | svchost.exe | GET | 200 | 4.231.128.59:443 | https://settings-win.data.microsoft.com/settings/v3.0/WSD/WaaSAssessment?os=Windows&osVer=10.0.19041.1.amd64fre.vb_release.191206-&ring=Retail&sku=48&deviceClass=Windows.Desktop&locale=en-US&deviceId=BAD99146-31D3-4EC6-A1A4-BE76F32BA5D4&FlightRing=Retail&TelemetryLevel=1&HidOverGattReg=C%3A%5CWINDOWS%5CSystem32%5CDriverStore%5CFileRepository%5Chidbthle.inf_amd64_9610b4821fdf82a5%5CMicrosoft.Bluetooth.Profiles.HidOverGatt.dll&AppVer=10.0&ProcessorIdentifier=AMD64%20Family%2023%20Model%201%20Stepping%202&OEMModel=DELL&UpdateOfferedDays=4294967295&ProcessorManufacturer=AuthenticAMD&InstallDate=1661339444&OEMModelBaseBoard=&BranchReadinessLevel=CB&OEMSubModel=J5CR&IsCloudDomainJoined=0&DeferFeatureUpdatePeriodInDays=30&IsDeviceRetailDemo=0&FlightingBranchName=&OSUILocale=en-US&DeviceFamily=Windows.Desktop&WuClientVer=10.0.19041.3996&UninstallActive=1&IsFlightingEnabled=0&OSSkuId=48&ProcessorClockSpeed=3094&TotalPhysicalRAM=6144&SecureBootCapable=0&App=WaaSAssessment&ProcessorCores=6&CurrentBranch=vb_release&InstallLanguage=en-US&DeferQualityUpdatePeriodInDays=0&ServicingBranch=CB&OEMName_Uncleaned=DELL&TPMVersion=0&PrimaryDiskTotalCapacity=262144&InstallationType=Client&AttrDataVer=186&ProcessorModel=AMD%20Ryzen%205%203500%206-Core%20Processor&IsEdgeWithChromiumInstalled=1&OSVersion=10.0.19045.4046&IsMDMEnrolled=0&ActivationChannel=Retail&HonorWUfBDeferrals=0&FirmwareVersion=A.40&TrendInstalledKey=1&OSArchitecture=AMD64&DefaultUserRegion=244&UpdateManagementGroup=2 | US | text | 5.63 Kb | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
7428 | svchost.exe | 51.124.78.146:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
4 | System | 192.168.100.255:137 | — | Not routed | — | whitelisted |
876 | RUXIMICS.exe | 51.124.78.146:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
6768 | MoUsoCoreWorker.exe | 51.124.78.146:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
3412 | svchost.exe | 172.211.123.250:443 | client.wns.windows.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
4 | System | 192.168.100.255:138 | — | Not routed | — | whitelisted |
7392 | darkguard_0.1.0_x64-setup.exe | 88.221.169.205:80 | go.microsoft.com | AKAMAI-AS | US | whitelisted |
7392 | darkguard_0.1.0_x64-setup.exe | 199.232.210.172:80 | msedge.sf.dl.delivery.mp.microsoft.com | FASTLY | US | whitelisted |
7664 | MicrosoftEdgeUpdate.exe | 150.171.22.17:443 | config.edge.skype.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
8788 | MicrosoftEdgeUpdate.exe | 150.171.22.17:443 | config.edge.skype.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
self.events.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
go.microsoft.com |
| whitelisted |
msedge.sf.dl.delivery.mp.microsoft.com |
| whitelisted |
config.edge.skype.com |
| whitelisted |
msedge.api.cdp.microsoft.com |
| whitelisted |
login.live.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
settings-win.data.microsoft.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
7392 | darkguard_0.1.0_x64-setup.exe | Misc activity | ET INFO Packed Executable Download |
7428 | svchost.exe | Unknown Traffic | ET USER_AGENTS Microsoft Dr Watson User-Agent (MSDW) |
6756 | svchost.exe | Misc activity | ET INFO Packed Executable Download |
9072 | powershell.exe | Not Suspicious Traffic | ET INFO Windows Powershell User-Agent Usage |
Process | Message |
|---|---|
msedgewebview2.exe | RecursiveDirectoryCreate( C:\Users\admin\AppData\Local\systems.banat.darkguard directory exists )
|
msedgewebview2.exe | RecursiveDirectoryCreate( C:\Users\admin\AppData\Local\systems.banat.darkguard\EBWebView directory exists )
|
msedgewebview2.exe | [0202/215847.875:ERROR:third_party\crashpad\crashpad\util\win\exception_handler_server.cc:529] ConnectNamedPipe: The pipe is being closed. (0xE8)
|