ANY.RUN Interactive Sandbox
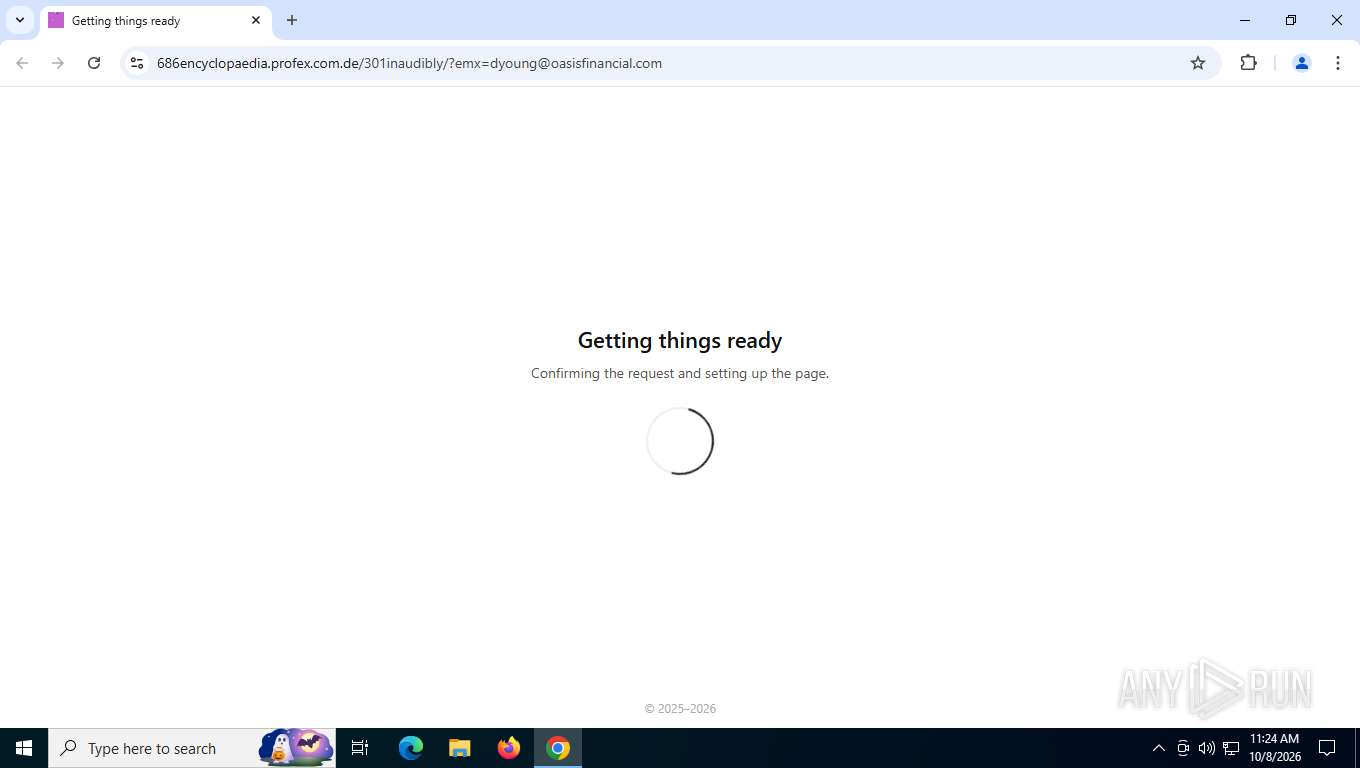
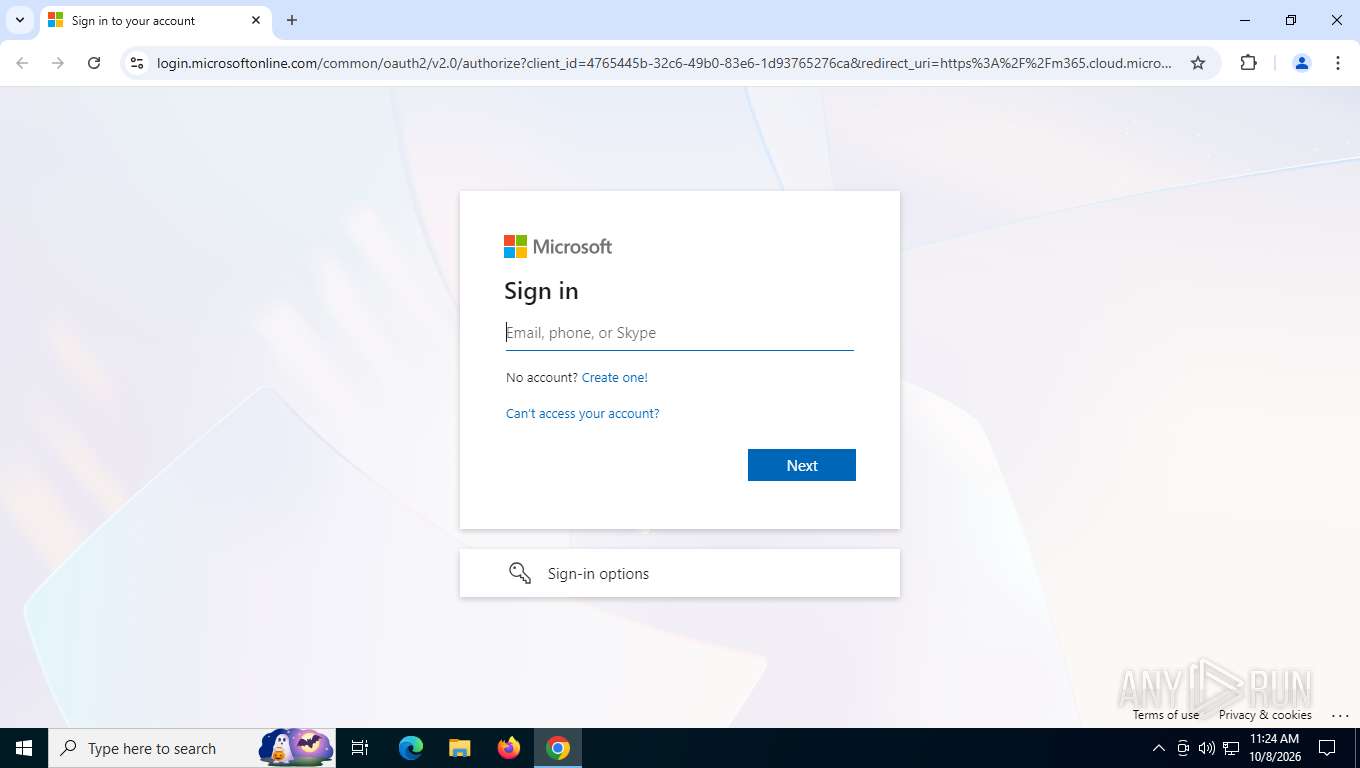
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
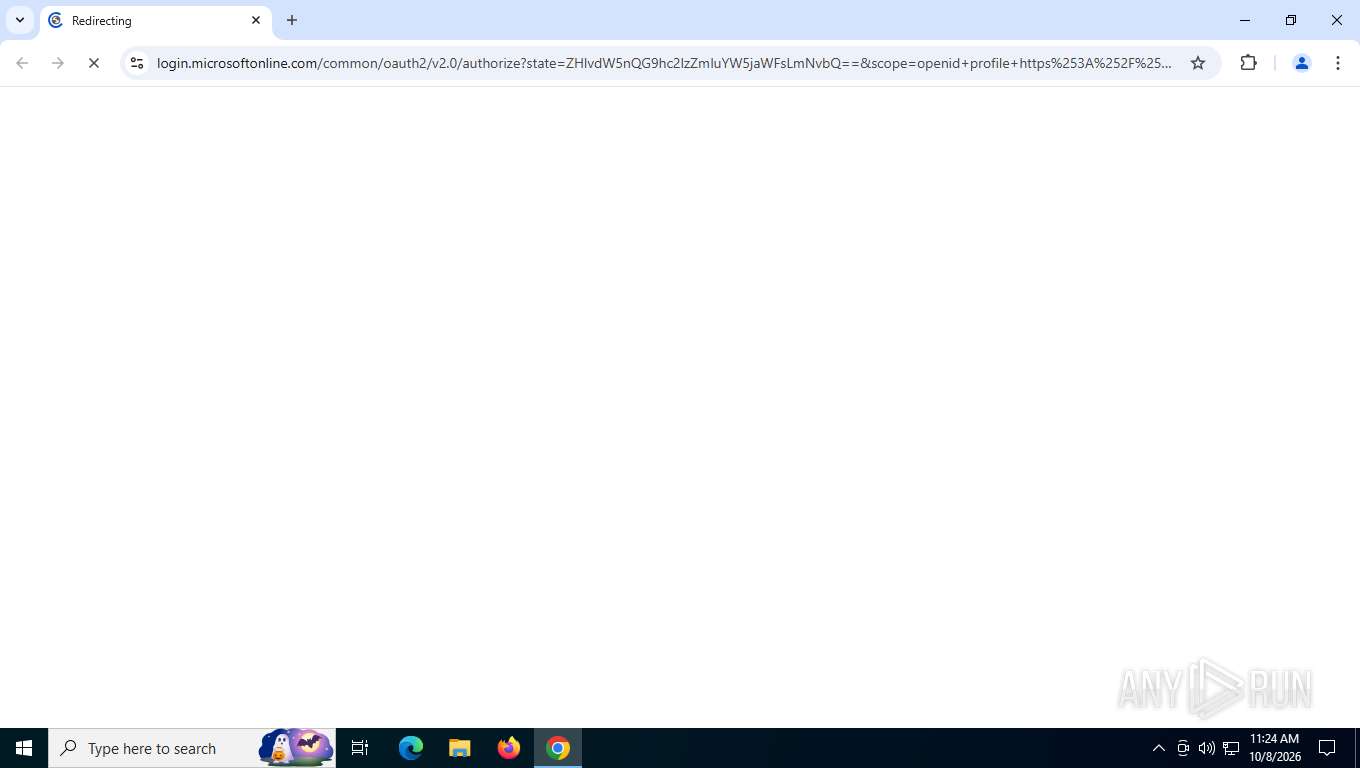
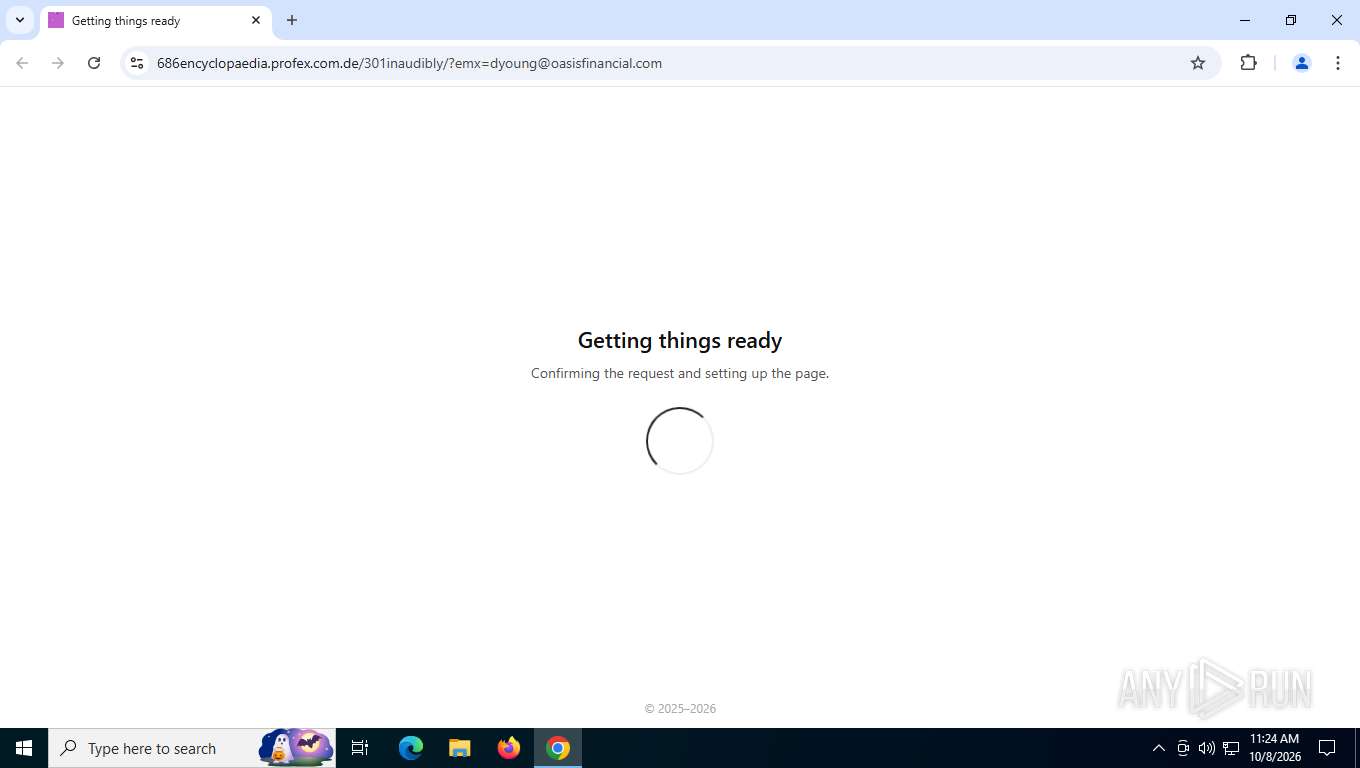
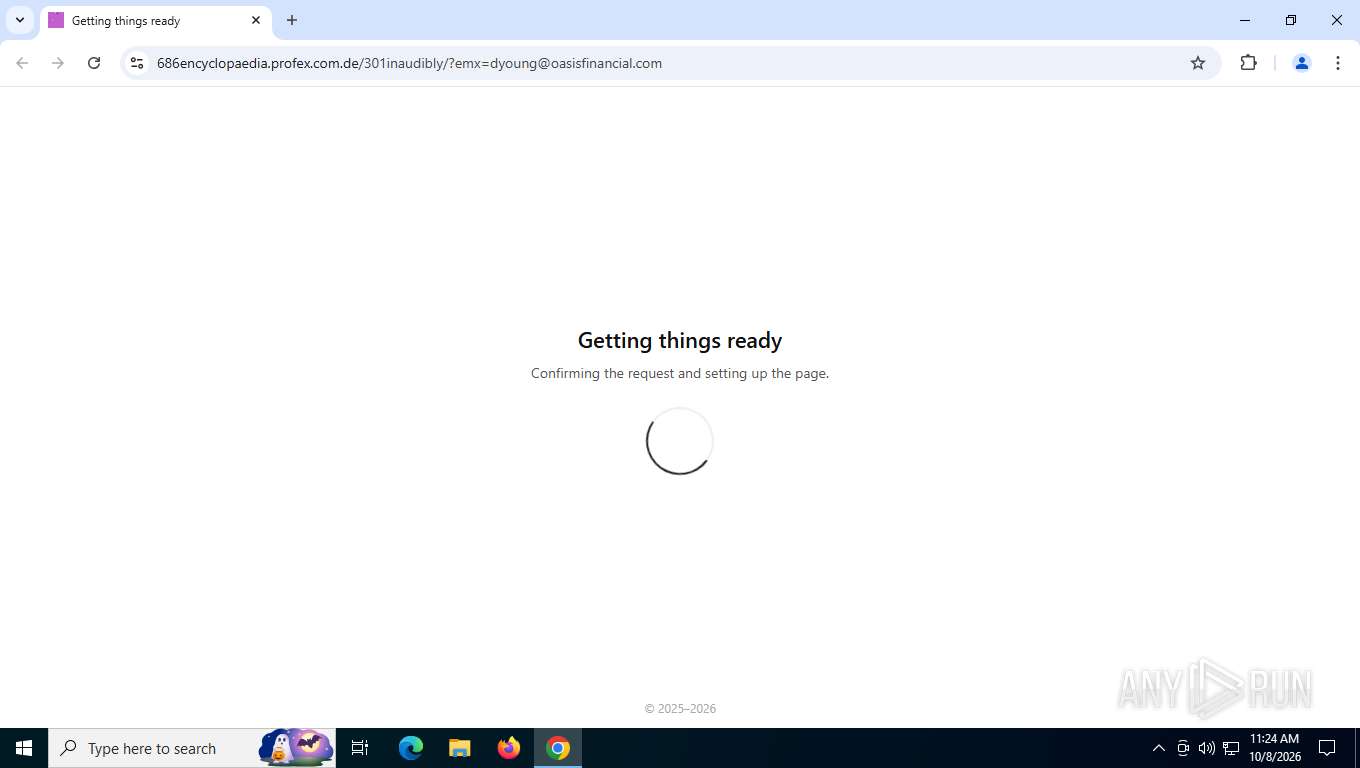
| URL: | https://login.microsoft.com//////////////////////////////common/oauth2/v2.0/authorize?state=ZHlvdW5nQG9hc2lzZmluYW5jaWFsLmNvbQ==&scope=openid+profile+https%253A%252F%252Fgraph.microsoft.com%252FUser.Read&prompt=none&client_id=0e6cf695-c438-42ec-9e89-593a791577c4&uri=https%253A%252F%252Fdeveloper.salesforce.com%252Fdashboard%252Fsession%252Fuser%252Fverify%252Fstep1&%255Ca3edq%250C+2e4c%250D%250A%2593bb66f835%2509%258C2979X%25BCint+Builder.Decode%250A%2509Context+%253A%253D+FlowEmail+%255B+OffsetStream+%253A=%2520Token%2509Data%2520%257C%2520Email%257Dfor%2520Stream%253A%253DPayloadBuilder+;+ValueContext+%257D+Trace%250A%2509Decode+.+SignalVector+%257B%2520Offset%257D%250Aa78c998ef06b569e%2597%25E9%252A%25CBa93627d06a07eba872664f4a92c74eae25f60308d1cad09a16e7beef0b79c03d8bd7528c4a7efc8bdb3fc053evar%252BVector-Secret%25250A%252509Decode%252B%25253B%252BBuffer%25250A%252509Encode%252B-%252BSession%25250A%252509Decode%252B%25255D%252BPayload%25250A%252509Offset%252B%25252B%252BBuilder%25250A%252509Builder%252B%252528%252BToken%25250A%252509Encode%252B.%252BKey%25250A%252509Context%252B%25257B%252BToken%25250A%25257D%25250Aelse%252BDecode%25252CBuilder%25250A%252509Stream%252B%25253A%25253D%252BHeader%25250A%252509Vector%252B%252526%252BVector%25250A%252509Payload%252B%25253D%252BBuilder%25250A%252509Value%252B%25257C%252BPayload%25250A%252509Secret%252B%25253D%252BBuffer%25250A%25257D%25250Aswitch%252BPayload%25252CSession%25250A%252509Payload%252B%252529%252BToken%25250A%252509Payload%252B%252526%252BBuilder%25250A%252509Data%252B%25257C%252BDecode%25250A%252509Secret%252B%25255B%252BStream%25250A%25257D%25250Astring%252BBody%252529Session%25250A%252509Session%252B%252528%252BTrace%25250A%252509Buffer%252B%25257B%252BSession%25250A%252509Vector%252B%25252A%252BVector%25250A%252509Context%252B%25253B%252BToken%25250A%252509Value%252B%25252A%252BData%25250A%252509Encode%252B%25253B%252BFlow%25250A%252509Trace%252B%252529%252BTrace%25250A%25257D%25250Aint%252BToken%25257CSignal%25250A%252509Header%252B%25255D%252BFlow%25250A%252509Body%252B.%252BKey%25250A%252509Vector%252B%252528%252BSignal%25250A%252509Session%252B%25252C%252BData%25250A%25257D%25250Ac2FuZGVlcEBmdmNvbS5hZQ== |
| Full analysis: | https://app.any.run/tasks/788884d6-0764-43c1-8b36-cbc0b0dfc874 |
| Verdict: | Malicious activity |
| Analysis date: | October 08, 2026, 15:24:38 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MD5: | A4C17D14F1D2F32B8C816D0C0C711B02 |
| SHA1: | 133AF4381D54DA0E45B0B22875E5DEEEF185C6D5 |
| SHA256: | 1816CD4C6E1C0EA82EA9BBF10D108919D675460EF2F826718F3C1BC0164C47E3 |
| SSDEEP: | 48:u+CJflmZGf9Q2QXUxsJpVC0GIWOEXgYqdpVQeUG1LmPyWNm1xQ3T/PYW+PZTj8wr:Rgfeg9uX0saUSw |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 1148 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --disable-features=HttpsUpgrades,HttpsFirstModeV2,HttpsOnlyMode,HttpsFirstBalancedMode --no-first-run --no-default-browser-check https://login.microsoft.com//////////////////////////////common/oauth2/v2.0/authorize?state=ZHlvdW5nQG9hc2lzZmluYW5jaWFsLmNvbQ==&scope=openid+profile+https%253A%252F%252Fgraph.microsoft.com%252FUser.Read&prompt=none&client_id=0e6cf695-c438-42ec-9e89-593a791577c4&uri=https%253A%252F%252Fdeveloper.salesforce.com%252Fdashboard%252Fsession%252Fuser%252Fverify%252Fstep1&%255Ca3edq%250C+2e4c%250D%250A%2593bb66f835%2509%258C2979X%25BCint+Builder.Decode%250A%2509Context+%253A%253D+FlowEmail+%255B+OffsetStream+%253A=%2520Token%2509Data%2520%257C%2520Email%257Dfor%2520Stream%253A%253DPayloadBuilder+;+ValueContext+%257D+Trace%250A%2509Decode+.+SignalVector+%257B%2520Offset%257D%250Aa78c998ef06b569e%2597%25E9%252A%25CBa93627d06a07eba872664f4a92c74eae25f60308d1cad09a16e7beef0b79c03d8bd7528c4a7efc8bdb3fc053evar%252BVector-Secret%25250A%252509Decode%252B%25253B%252BBuffer%25250A%252509Encode%252B-%252BSession%25250A%252509Decode%252B%25255D%252BPayload%25250A%252509Offset%252B%25252B%252BBuilder%25250A%252509Builder%252B%252528%252BToken%25250A%252509Encode%252B.%252BKey%25250A%252509Context%252B%25257B%252BToken%25250A%25257D%25250Aelse%252BDecode%25252CBuilder%25250A%252509Stream%252B%25253A%25253D%252BHeader%25250A%252509Vector%252B%252526%252BVector%25250A%252509Payload%252B%25253D%252BBuilder%25250A%252509Value%252B%25257C%252BPayload%25250A%252509Secret%252B%25253D%252BBuffer%25250A%25257D%25250Aswitch%252BPayload%25252CSession%25250A%252509Payload%252B%252529%252BToken%25250A%252509Payload%252B%252526%252BBuilder%25250A%252509Data%252B%25257C%252BDecode%25250A%252509Secret%252B%25255B%252BStream%25250A%25257D%25250Astring%252BBody%252529Session%25250A%252509Session%252B%252528%252BTrace%25250A%252509Buffer%252B%25257B%252BSession%25250A%252509Vector%252B%25252A%252BVector%25250A%252509Context%252B%25253B%252BToken%25250A%252509Value%252B%25252A%252BData%25250A%252509Encode%252B%25253B%252BFlow%25250A%252509Trace%252B%252529%252BTrace%25250A%25257D%25250Aint%252BToken%25257CSignal%25250A%252509Header%252B%25255D%252BFlow%25250A%252509Body%252B.%252BKey%25250A%252509Vector%252B%252528%252BSignal%25250A%252509Session%252B%25252C%252BData%25250A%25257D%25250Ac2FuZGVlcEBmdmNvbS5hZQ== | C:\Program Files\Google\Chrome\Application\chrome.exe | explorer.exe | ||||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 1544 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=quarantine.mojom.Quarantine --lang=en-US --service-sandbox-type=none --disable-quic --string-annotations --field-trial-handle=3192,i,196621018687189008,14504032707637925365,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=6356 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 2412 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=quarantine.mojom.Quarantine --lang=en-US --service-sandbox-type=none --disable-quic --string-annotations --field-trial-handle=5600,i,196621018687189008,14504032707637925365,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=6480 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 3304 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --lang=en-US --service-sandbox-type=service --disable-quic --string-annotations --field-trial-handle=6320,i,196621018687189008,14504032707637925365,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=6652 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 4208 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=renderer --string-annotations --enable-dinosaur-easter-egg-alt-images --disable-gpu-compositing --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=3 --enable-main-frame-before-activation --renderer-client-id=8 --field-trial-handle=4152,i,196621018687189008,14504032707637925365,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=4024 /prefetch:1 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 4876 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=renderer --string-annotations --enable-dinosaur-easter-egg-alt-images --disable-gpu-compositing --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=3 --enable-main-frame-before-activation --renderer-client-id=9 --field-trial-handle=3260,i,196621018687189008,14504032707637925365,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=3184 /prefetch:1 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 5136 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --lang=en-US --service-sandbox-type=service --disable-quic --string-annotations --field-trial-handle=6464,i,196621018687189008,14504032707637925365,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=6368 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 5308 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=unzip.mojom.Unzipper --lang=en-US --service-sandbox-type=service --disable-quic --string-annotations --field-trial-handle=6208,i,196621018687189008,14504032707637925365,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=6240 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 5864 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=quarantine.mojom.Quarantine --lang=en-US --service-sandbox-type=none --disable-quic --string-annotations --field-trial-handle=6716,i,196621018687189008,14504032707637925365,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=6560 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 6272 | "C:\Program Files\Google\Chrome\Application\chrome.exe" --type=utility --utility-sub-type=network.mojom.NetworkService --lang=en-US --service-sandbox-type=none --disable-quic --string-annotations --field-trial-handle=2256,i,196621018687189008,14504032707637925365,262144 --disable-features=HttpsFirstBalancedMode,HttpsFirstModeV2,HttpsOnlyMode,HttpsUpgrades --variations-seed-version=20251218-201203.402000 --mojo-platform-channel-handle=2224 /prefetch:3 | C:\Program Files\Google\Chrome\Application\chrome.exe | chrome.exe | ||||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
6272 | chrome.exe | GET | 404 | 20.190.160.128:443 | https://login.microsoftonline.com/favicon.ico | US | — | — | whitelisted |
6272 | chrome.exe | GET | 404 | 20.190.160.128:443 | https://login.microsoftonline.com/favicon.ico | US | — | — | whitelisted |
6272 | chrome.exe | GET | 404 | 20.190.160.128:443 | https://login.microsoftonline.com/favicon.ico | US | — | — | whitelisted |
6272 | chrome.exe | GET | 404 | 20.190.160.128:443 | https://login.microsoftonline.com/favicon.ico | US | — | — | whitelisted |
6272 | chrome.exe | POST | 200 | 142.251.127.84:443 | https://accounts.google.com/ListAccounts?gpsia=1&source=ChromiumBrowser&json=standard | US | text/data | 17 b | whitelisted |
5616 | SearchApp.exe | GET | 200 | 23.11.41.157:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAjTxtAB8my1oj8MfWpz%2F7Y%3D | NL | other | 313 b | whitelisted |
6272 | chrome.exe | GET | 200 | 142.251.20.101:80 | http://clients2.google.com/time/1/current?cup2key=8:khaDFDP2EgqPGs5yJfT5HgaUB7ujoGQjLp5umzxq5J0&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855 | US | text/data | 106 b | whitelisted |
6272 | chrome.exe | GET | 200 | 142.251.110.139:443 | https://clientservices.googleapis.com/chrome-variations/seed?osname=win&channel=stable&milestone=133 | US | archive | 109 Kb | whitelisted |
6272 | chrome.exe | GET | 200 | 172.217.116.4:443 | https://safebrowsingohttpgateway.googleapis.com/v1/ohttp/hpkekeyconfig?key=AIzaSyA2KlwBX3mkFo30om9LUFYQhpqLoa_BNhE | US | other | 41 b | whitelisted |
5616 | SearchApp.exe | GET | 200 | 2.16.204.139:443 | https://www.bing.com/th?id=ODSWG.dd482747-0b27-423b-a458-0ac58ffc4b0e&pid=dsb | NL | web | 26.1 Kb | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 172.211.123.249:443 | client.wns.windows.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
— | — | 2.16.204.139:443 | — | AKAMAI-ASN1 | NL | whitelisted |
7404 | svchost.exe | 20.190.159.129:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
— | — | 48.209.133.15:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
— | — | 23.11.41.157:80 | ocsp.digicert.com | AKAMAI-AMS | NL | whitelisted |
5616 | SearchApp.exe | 2.16.204.139:443 | — | AKAMAI-ASN1 | NL | whitelisted |
548 | svchost.exe | 150.171.109.100:80 | crl.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5616 | SearchApp.exe | 23.11.41.157:80 | ocsp.digicert.com | AKAMAI-AMS | NL | whitelisted |
5616 | SearchApp.exe | 204.79.197.203:80 | oneocsp.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
6272 | chrome.exe | 142.251.110.139:443 | clientservices.googleapis.com | GOOGLE | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
client.wns.windows.com |
| whitelisted |
login.live.com |
| whitelisted |
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
oneocsp.microsoft.com |
| whitelisted |
clients2.google.com |
| whitelisted |
safebrowsingohttpgateway.googleapis.com |
| whitelisted |
clientservices.googleapis.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
6272 | chrome.exe | Not Suspicious Traffic | INFO [ANY.RUN] Request to Azure content delivery network (aadcdn .msauth .net) |
2228 | svchost.exe | Misc activity | INFO [ANY.RUN] Google STUN server DNS query observed (stun .l .google .com) |
6272 | chrome.exe | Possible Social Engineering Attempted | PHISHING [ANY.RUN] Phishing TDS HTTP activity observed (analytics=) |
6272 | chrome.exe | Information Leak | SUSPICIOUS [ANY.RUN] FingerprintJS Collected Data observed in HTTP POST request |
6272 | chrome.exe | Misc activity | ET INFO Microsoft OAuth 2.0 Device Auth Activity M3 (GET) |