ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
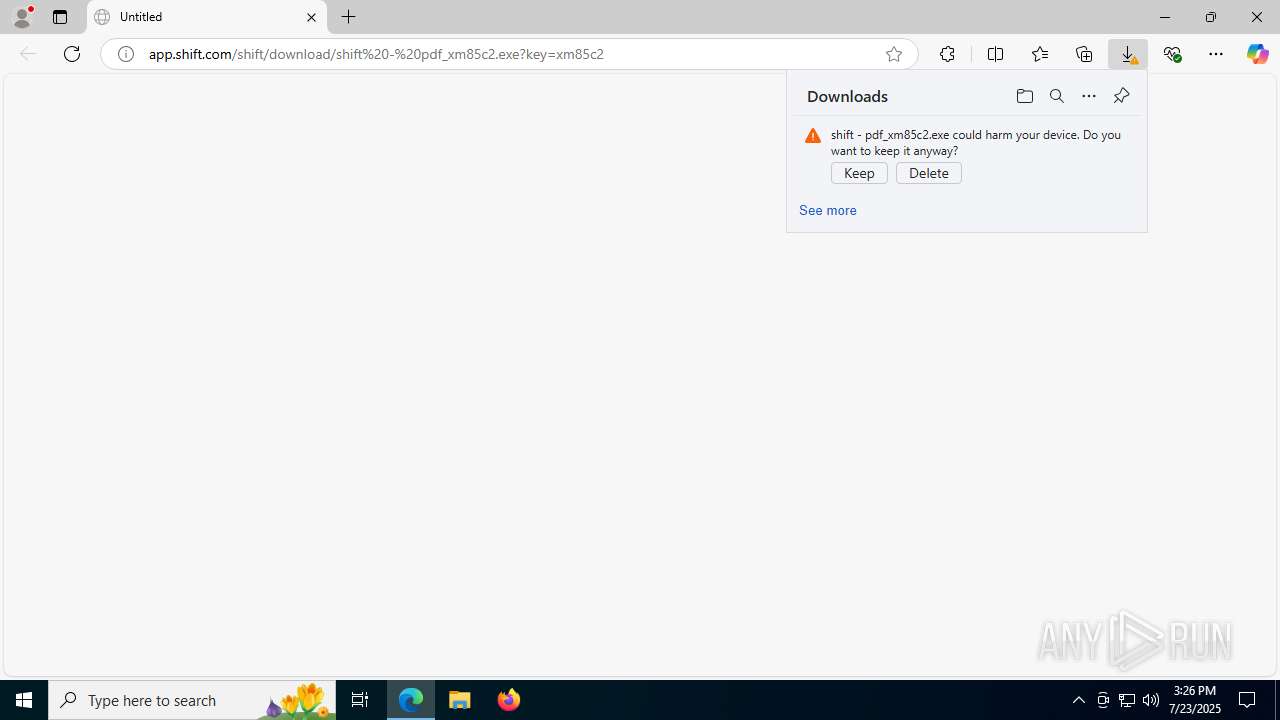
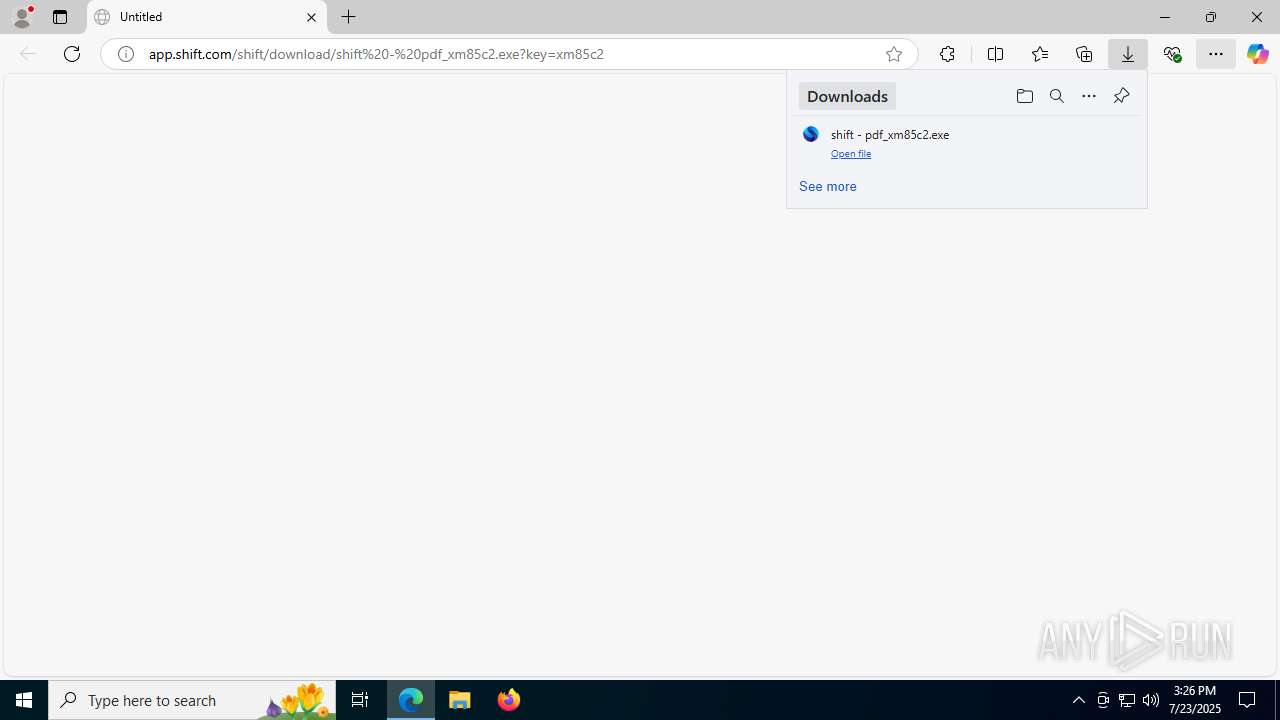
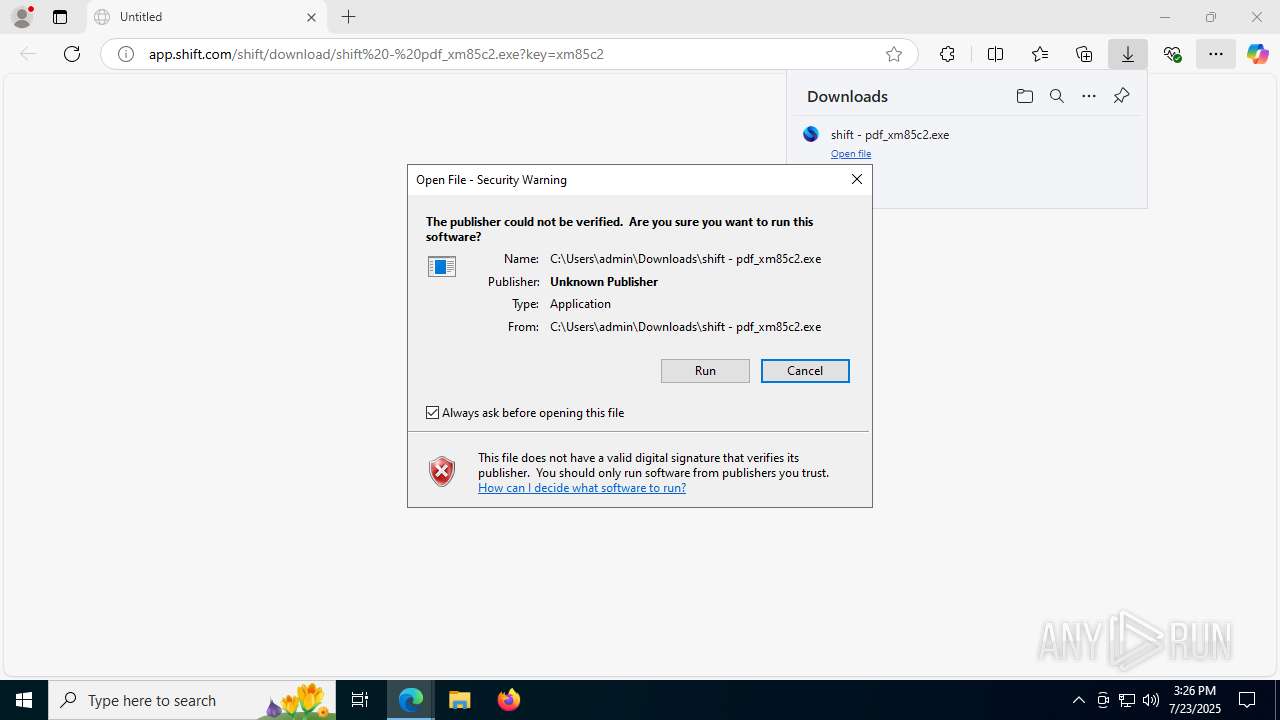
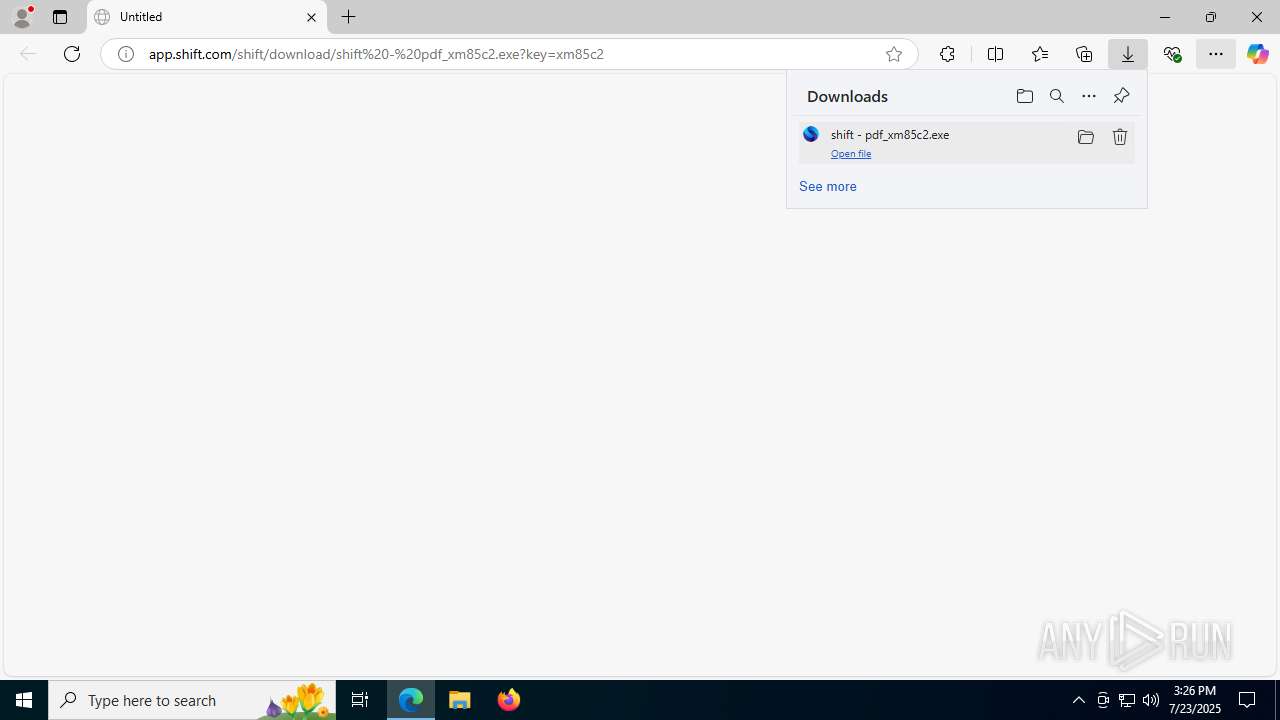
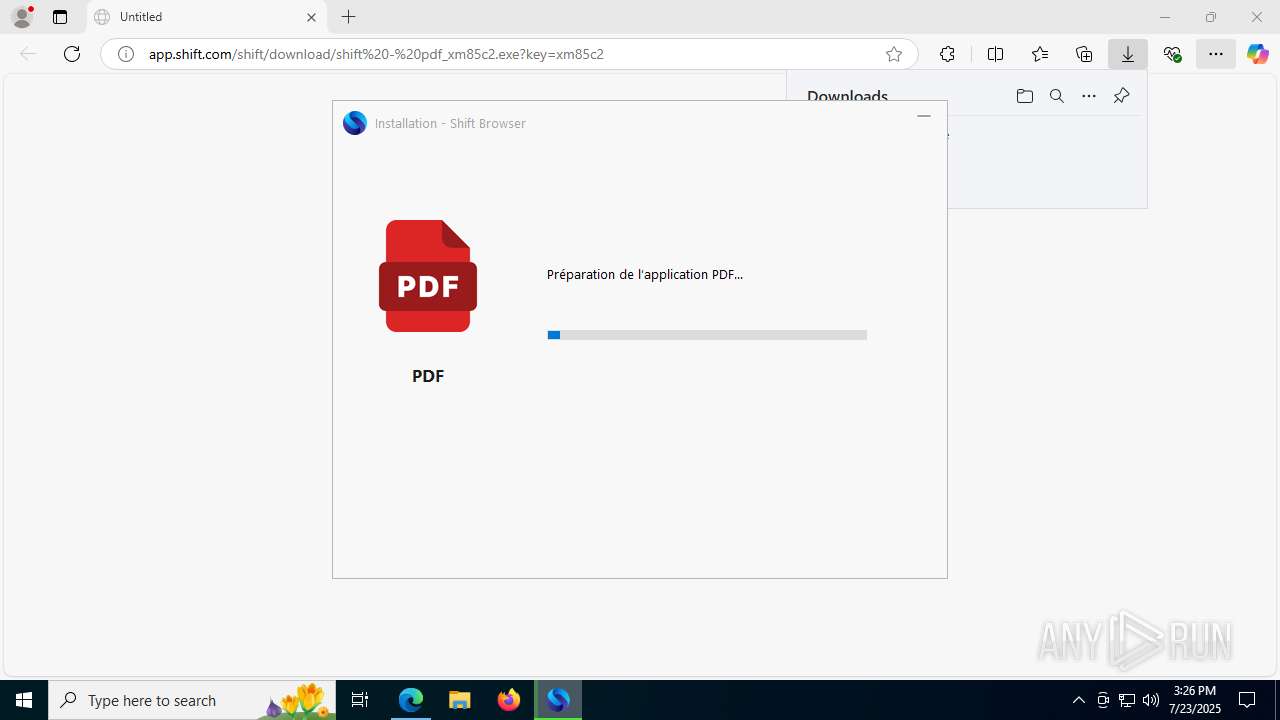
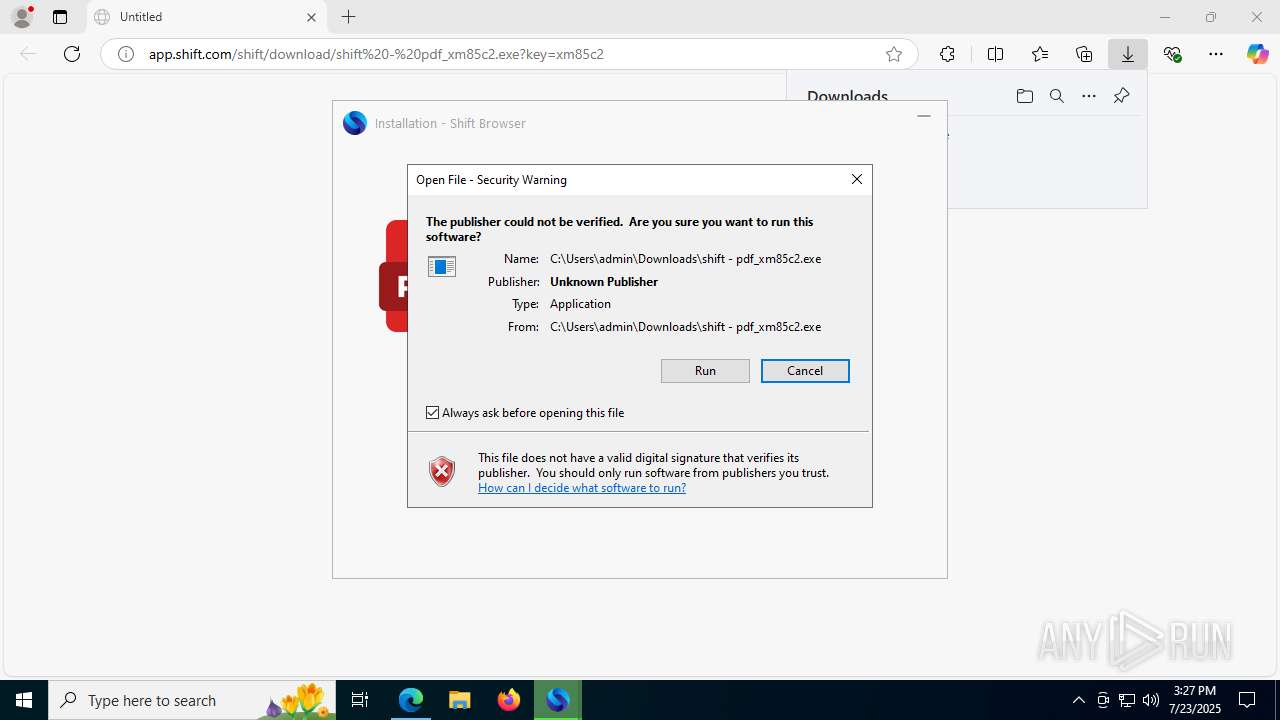
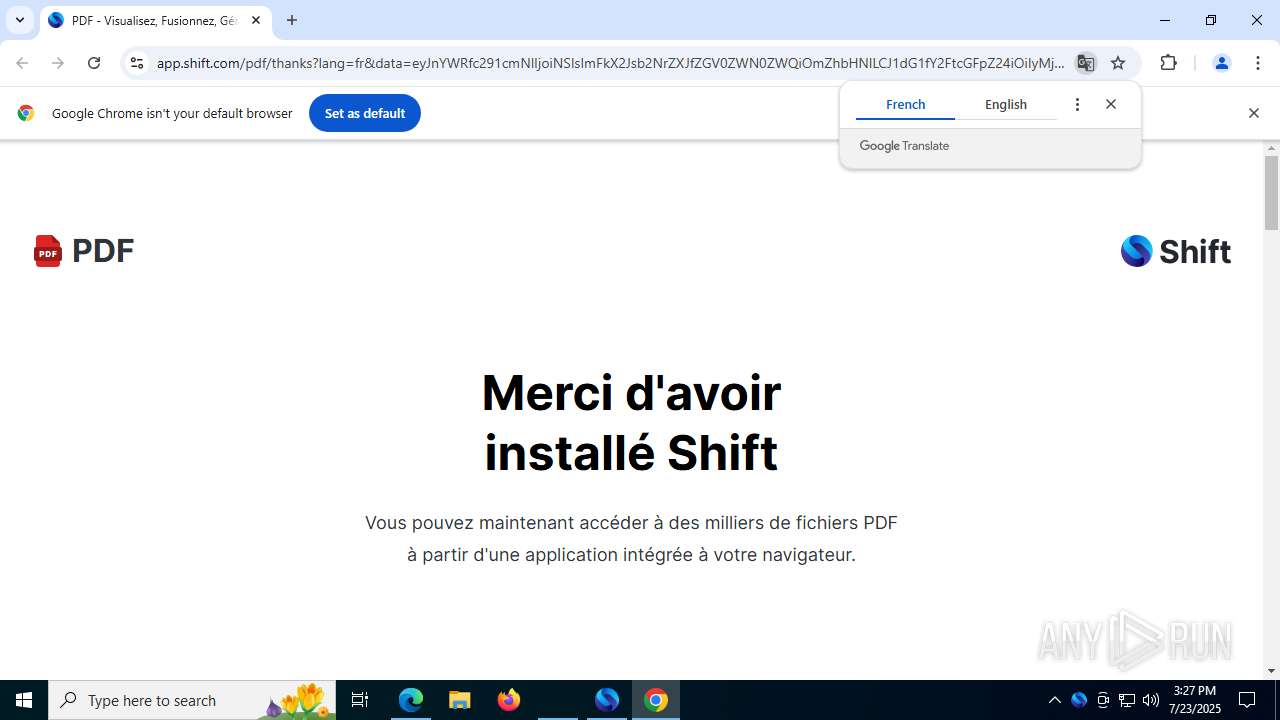
| URL: | app.shift.com/shift/download/shift%20-%20pdf_xm85c2.exe?key=xm85c2 |
| Full analysis: | https://app.any.run/tasks/2e91bb01-4805-4f3d-aa97-1ea1ca49eafb |
| Verdict: | Malicious activity |
| Threats: | Stealers are a group of malicious software that are intended for gaining unauthorized access to users’ information and transferring it to the attacker. The stealer malware category includes various types of programs that focus on their particular kind of data, including files, passwords, and cryptocurrency. Stealers are capable of spying on their targets by recording their keystrokes and taking screenshots. This type of malware is primarily distributed as part of phishing campaigns. |
| Analysis date: | July 23, 2025, 15:25:58 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Tags: | |
| Indicators: | |
| MD5: | 036AF5D398ADB182C7BCA2A1B6EE54F5 |
| SHA1: | 59CE8F46C6E5BCA415910EF5B0F00F24608C81A6 |
| SHA256: | 16290D7097C8FACBA01211B106C599B80EB8F2B029F9D186F2BAAF1D0B3C380B |
| SSDEEP: | 3:8VDNyGKSK2CR6d2JFTdn:8R4GKSK/R6d2Ddn |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 432 | "C:\Users\admin\AppData\Local\Shift\chromium\shift.exe" --type=utility --utility-sub-type=chrome.mojom.ProfileImport --lang=en-US --service-sandbox-type=none --no-pre-read-main-dll --field-trial-handle=2076,i,7800139102255505378,15508544063144219863,262144 --variations-seed-version --mojo-platform-channel-handle=3408 /prefetch:8 | C:\Users\admin\AppData\Local\Shift\chromium\shift.exe | shift.exe | ||||||||||||
User: admin Company: Shift Technologies Inc. Integrity Level: MEDIUM Description: Shift Browser Exit code: 0 Version: 135.1.10.2527 Modules
| |||||||||||||||
| 1288 | "c:\program files\google\chrome\application\chrome.exe" --type=utility --utility-sub-type=quarantine.mojom.Quarantine --lang=en-US --service-sandbox-type=none --disable-quic --string-annotations --field-trial-handle=6432,i,10455966573392577929,2082233218017757632,262144 --variations-seed-version=20250221-144540.991000 --mojo-platform-channel-handle=6068 /prefetch:8 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: MEDIUM Description: Google Chrome Exit code: 0 Version: 133.0.6943.127 Modules
| |||||||||||||||
| 1468 | "c:\program files\google\chrome\application\chrome.exe" --type=renderer --string-annotations --enable-dinosaur-easter-egg-alt-images --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=2 --enable-main-frame-before-activation --renderer-client-id=6 --field-trial-handle=3172,i,10455966573392577929,2082233218017757632,262144 --variations-seed-version=20250221-144540.991000 --mojo-platform-channel-handle=3180 /prefetch:1 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Version: 133.0.6943.127 Modules
| |||||||||||||||
| 1576 | "C:\Users\admin\AppData\Local\Shift\chromium\shift.exe" --type=gpu-process --no-pre-read-main-dll --start-stack-profiler --gpu-preferences=UAAAAAAAAADgAAAEAAAAAAAAAAAAAAAAAABgAAEAAAAAAAAAAAAAAAAAAAACAAAAAAAAAAAAAAAAAAAAAAAAABAAAAAAAAAAEAAAAAAAAAAIAAAAAAAAAAgAAAAAAAAA --field-trial-handle=2076,i,7800139102255505378,15508544063144219863,262144 --variations-seed-version --mojo-platform-channel-handle=2088 /prefetch:2 | C:\Users\admin\AppData\Local\Shift\chromium\shift.exe | — | shift.exe | |||||||||||
User: admin Company: Shift Technologies Inc. Integrity Level: LOW Description: Shift Browser Version: 135.1.10.2527 Modules
| |||||||||||||||
| 1844 | C:\WINDOWS\SysWOW64\WerFault.exe -u -p 5244 -s 2768 | C:\Windows\SysWOW64\WerFault.exe | Shift Setup_xm85c2.tmp | ||||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Problem Reporting Exit code: 0 Version: 10.0.19041.3996 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1948 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | taskkill.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 2428 | "c:\program files\google\chrome\application\chrome.exe" --type=renderer --string-annotations --enable-dinosaur-easter-egg-alt-images --video-capture-use-gpu-memory-buffer --lang=en-US --device-scale-factor=1 --num-raster-threads=2 --enable-main-frame-before-activation --renderer-client-id=5 --field-trial-handle=3164,i,10455966573392577929,2082233218017757632,262144 --variations-seed-version=20250221-144540.991000 --mojo-platform-channel-handle=3212 /prefetch:1 | C:\Program Files\Google\Chrome\Application\chrome.exe | — | chrome.exe | |||||||||||
User: admin Company: Google LLC Integrity Level: LOW Description: Google Chrome Version: 133.0.6943.127 Modules
| |||||||||||||||
| 2508 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=utility --utility-sub-type=storage.mojom.StorageService --lang=en-US --service-sandbox-type=service --disable-quic --string-annotations --always-read-main-dll --field-trial-handle=2740,i,2219317146450365383,10442760371570318705,262144 --variations-seed-version --mojo-platform-channel-handle=2764 /prefetch:8 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Version: 133.0.3065.92 Modules
| |||||||||||||||
| 2596 | "C:\Users\admin\AppData\Local\Temp\is-ED4EM.tmp\shift - pdf_xm85c2.tmp" /SL5="$30382,1545339,1164800,C:\Users\admin\Downloads\shift - pdf_xm85c2.exe" /PDATA=eyJnYWRfc291cmNlIjoiNSIsImFkX2Jsb2NrZXJfZGV0ZWN0ZWQiOmZhbHNlLCJ1dG1fY2FtcGFpZ24iOiIyMjUxMTEzNjk0MSIsInByb2ZpbGUiOiJzaGlmdC1wZGYiLCJ1dG1fbWVkaXVtIjoiIiwidWEiOiJjaHJvbWUiLCJpbnN0YWxsZXJfZmlsZW5hbWUiOiJzaGlmdC12MTM1LjEuMTAtd2ViLmV4ZSIsInV0bV90ZXJtIjoiIiwiZ2FkX2NhbXBhaWduaWQiOiIyMjUxNDY5Mzg4MSIsImdjbGlkIjoiRUFJYUlRb2JDaE1JN1lIU29wX1RqZ01WNTFhckFoMkZuUkFWRUFFWUFTQUFFZ0paSHZEX0J3RSIsInRoYW5rc191cmwiOiJodHRwczovL2FwcC5zaGlmdC5jb20vcGRmL3RoYW5rcz9sYW5nPWZyIiwibHBfdXJsIjoiaHR0cHM6Ly9hcHAuc2hpZnQuY29tL3BkZi8xIiwicHJvZmlsZV9pZCI6MTA4LCJkaXN0aW5jdF9pZCI6ImQzMzdiODhjLTUwMDctNGU2Zi1hZWM0LWU1MmU1MDg5NDEyYyIsImxhbmciOiJmciIsIndoaXRlbGFiZWwiOiJQREYiLCJ1dG1fY29udGVudCI6IiIsInV0bV9zb3VyY2UiOiJvaC1wbWF4IiwiaW5zdGFsbF90aW1lIjoxNzUzMjg0NDEyLCJkZWZhdWx0X2Jyb3dzZXIiOiJNU0VkZ2VIVE0iLCJpbml0aWFsX3ZlcnNpb24iOiIxMzUuMS4xMC4yNTI3IiwiYXR0cmlidXRpb25fa2V5IjoieG04NWMyIn0= /SPLITS=eyJzcGxpdCI6ImIiLCJzcGxpdDIiOiJhIiwibm9fc3BsaXQiOmZhbHNlLCJsb2NhbF9zcGxpdF90ZXN0cyI6e30sInNlcnZlcl9zaWRlX3NwbGl0X3Rlc3RzIjp7InNwbGl0X3N0NjEyNV9hbHRlcm5hdGVfZG93bmxvYWRfY2RuIjp7InZhbHVlIjoiY29udHJvbCJ9LCJzcGxpdF9zdDEzOTFfZG9udF9pbXBvcnRfaGlzdG9yeSI6eyJ2YWx1ZSI6InZhcmlhdGlvbiJ9LCJzcGxpdF9zdDEyMzJfcmVuYW1lX3Nob3J0Y3V0c19zaGlmdF9icm93c2VyIjp7InZhbHVlIjoidmFyaWF0aW9uIn0sInNwbGl0X3N0MTIzNl9waW5fcHJvZmlsZV9hcHBfdG9fdGFza2JhciI6eyJ2YWx1ZSI6ImNvbnRyb2wifSwic3BsaXRfc3QzMDg0X3VzZXJfUElMSUhfZW5hYmxlX2Rpc2FibGVfZGlhbG9ncyI6eyJ2YWx1ZSI6ImNvbnRyb2wifSwic3BsaXRfc3Q0NTczX2ltcHJvdmVfYnJpbmdfdG9fZm9yZWdyb3VuZCI6eyJ2YWx1ZSI6InZhcmlhdGlvbjIifSwic3BsaXRfc3Q2NDg4X2FtYXpvbl9tb25ldGl6ZWRfcHJlcGlubmVkIjp7InZhbHVlIjoiY29udHJvbCJ9LCJzcGxpdF9zdDcwNjhfdGVtcGxhdGVzX2FwcF9zcGxpdF90ZXN0Ijp7InZhbHVlIjoiY29udHJvbCJ9LCJzcGxpdF9zdDQzMzdfc3Q0MzM4X29wZW5fdmlzaXRlZF9zaXRlc19pbXBvcnRfaGlzdG9yeSI6eyJ2YWx1ZSI6InZhcmlhdGlvbiJ9LCJzcGxpdF9zdDU2NTRfcmVndWxhcl92c19zaW1wbGlmaWVkX2FwcF92aWV3Ijp7InZhbHVlIjoidmFyaWF0aW9uIn0sInNwbGl0X3N0NTU4Ml9waWxpaF9wcmltYXJ5X21vbml0b3IiOnsidmFsdWUiOiJjb250cm9sIn0sInNwbGl0X3N0NTA2M19icmluZ190b19mb3JlZ3JvdW5kX21heGltaXplZCI6eyJ2YWx1ZSI6InZhcmlhdGlvbiJ9LCJzcGxpdF9zdDUxMTFfcGlsaWhfbGltaXRlcl9vbl91bmxvY2siOnsidmFsdWUiOiJjb250cm9sIn19LCJhdHRyaWJ1dGlvbl9zcGxpdF90ZXN0cyI6e30sImVuY29kZWRfc3BsaXRzIjoiMDAwIn0= /LAUNCHER /VERYSILENT | C:\Users\admin\AppData\Local\Temp\is-ED4EM.tmp\shift - pdf_xm85c2.tmp | shift - pdf_xm85c2.exe | ||||||||||||
User: admin Company: Shift Technologies, Inc. Integrity Level: MEDIUM Description: Setup/Uninstall Exit code: 0 Version: 51.1052.0.0 Modules
| |||||||||||||||
| 2604 | "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --type=renderer --string-annotations --extension-process --renderer-sub-type=extension --video-capture-use-gpu-memory-buffer --lang=en-US --js-flags=--ms-user-locale= --device-scale-factor=1 --num-raster-threads=2 --enable-main-frame-before-activation --renderer-client-id=7 --always-read-main-dll --field-trial-handle=4320,i,2219317146450365383,10442760371570318705,262144 --variations-seed-version --mojo-platform-channel-handle=4332 /prefetch:2 | C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe | — | msedge.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: LOW Description: Microsoft Edge Exit code: 0 Version: 133.0.3065.92 Modules
| |||||||||||||||
| (PID) Process: | (3936) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | failed_count |
Value: 0 | |||
| (PID) Process: | (3936) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | state |
Value: 2 | |||
| (PID) Process: | (3936) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\ThirdParty |
| Operation: | write | Name: | StatusCodes |
Value: | |||
| (PID) Process: | (3936) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\ThirdParty |
| Operation: | write | Name: | StatusCodes |
Value: 01000000 | |||
| (PID) Process: | (3936) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\BLBeacon |
| Operation: | write | Name: | state |
Value: 1 | |||
| (PID) Process: | (3936) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Edge\StabilityMetrics |
| Operation: | write | Name: | user_experience_metrics.stability.exited_cleanly |
Value: 0 | |||
| (PID) Process: | (3936) msedge.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\EdgeUpdate\ClientStateMedium\{56EB18F8-B008-4CBD-B6D2-8C97FE7E9062}\LastWasDefault |
| Operation: | write | Name: | S-1-5-21-1693682860-607145093-2874071422-1001 |
Value: 12EE539C30992F00 | |||
| (PID) Process: | (3936) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\WindowProperties\459394 |
| Operation: | write | Name: | WindowTabManagerFileMappingId |
Value: {D5B96BB5-85C6-441B-8D9D-9705FEDAD1B1} | |||
| (PID) Process: | (3936) msedge.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\WOW6432Node\Microsoft\EdgeUpdate\ClientStateMedium\{56EB18F8-B008-4CBD-B6D2-8C97FE7E9062}\LastWasDefault |
| Operation: | write | Name: | S-1-5-21-1693682860-607145093-2874071422-1001 |
Value: 8211679C30992F00 | |||
| (PID) Process: | (3936) msedge.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run |
| Operation: | write | Name: | MicrosoftEdgeAutoLaunch_29EBC4579851B72EE312C449CF839B1A |
Value: "C:\Program Files (x86)\Microsoft\Edge\Application\msedge.exe" --no-startup-window --win-session-start | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3936 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\ClientCertificates\LOG.old~RF18d2ac.TMP | — | |
MD5:— | SHA256:— | |||
| 3936 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\ClientCertificates\LOG.old | — | |
MD5:— | SHA256:— | |||
| 3936 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\PersistentOriginTrials\LOG.old~RF18d2bc.TMP | — | |
MD5:— | SHA256:— | |||
| 3936 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\PersistentOriginTrials\LOG.old | — | |
MD5:— | SHA256:— | |||
| 3936 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\discounts_db\LOG.old~RF18d2eb.TMP | — | |
MD5:— | SHA256:— | |||
| 3936 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\discounts_db\LOG.old | — | |
MD5:— | SHA256:— | |||
| 3936 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\parcel_tracking_db\LOG.old~RF18d2eb.TMP | — | |
MD5:— | SHA256:— | |||
| 3936 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\LOG.old~RF18d2eb.TMP | — | |
MD5:— | SHA256:— | |||
| 3936 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\LOG.old | — | |
MD5:— | SHA256:— | |||
| 3936 | msedge.exe | C:\Users\admin\AppData\Local\Microsoft\Edge\User Data\Default\commerce_subscription_db\LOG.old~RF18d2fb.TMP | — | |
MD5:— | SHA256:— | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
5460 | msedge.exe | GET | 200 | 150.171.28.11:80 | http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:5ik87D1LhrCuc2Ju7Yu37ppg5v37vS_qOd3VU3M2aJY&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855 | US | text | 102 b | whitelisted |
1268 | svchost.exe | GET | 200 | 2.16.168.124:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | RU | binary | 825 b | whitelisted |
7780 | svchost.exe | HEAD | 200 | 199.232.214.172:80 | http://msedge.b.tlu.dl.delivery.mp.microsoft.com/filestreamingservice/files/bf8090eb-6e5c-4c51-9250-5bf9b46cf160?P1=1753784819&P2=404&P3=2&P4=j03PkSOsANoACWkfZFWNEBg8vjKYHuf5f4DJL1exk8JVdsPk%2bvP4QJjP9FbFE0ns%2fGRs3%2fsjAsIp3xVynzW93Q%3d%3d | US | — | — | whitelisted |
7756 | SIHClient.exe | GET | 200 | 23.35.229.160:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Product%20Root%20Certificate%20Authority%202018.crl | DE | binary | 420 b | whitelisted |
2876 | shift.exe | GET | 200 | 142.250.74.206:80 | http://clients2.google.com/time/1/current?cup2key=8:H6eFpcA-IbZRpWzkDWwvv6EJ1Ojksb51fjUMAlZL7J8&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855 | US | text | 107 b | whitelisted |
7780 | svchost.exe | HEAD | 200 | 199.232.214.172:80 | http://msedge.b.tlu.dl.delivery.mp.microsoft.com/filestreamingservice/files/4c4fdee0-d69c-42b7-bf5c-3ec046e9dfc9?P1=1753784823&P2=404&P3=2&P4=T39zlutoi%2bJxsekDJmvaZ59vNPkA9HYUCGBzoPunDutVTBIdr7mekkJhpoqlWmKdeHtIHd1xDJbTh9HM14w2FA%3d%3d | US | compressed | 764 b | whitelisted |
7780 | svchost.exe | HEAD | 200 | 199.232.214.172:80 | http://msedge.b.tlu.dl.delivery.mp.microsoft.com/filestreamingservice/files/9244b52a-55cc-41a2-b7c4-7f4983d8753c?P1=1753777632&P2=404&P3=2&P4=JnbMAThnTLWjnKj40q26y%2b%2fMIcyhDV8HEY1URL4CnFiJs%2brNiqmZJNhbCbzdUo0mYFTHz4NQ9JndxIhOISgs3w%3d%3d | US | binary | 2.98 Kb | whitelisted |
1844 | WerFault.exe | GET | 200 | 23.216.77.6:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 825 b | whitelisted |
7780 | svchost.exe | GET | — | 199.232.214.172:80 | http://msedge.b.tlu.dl.delivery.mp.microsoft.com/filestreamingservice/files/2ef98485-cbad-4d99-b4c2-cd4abac73fb4?P1=1753781226&P2=404&P3=2&P4=TdolYB8Pey%2fQYxHyJ6Tzd5GTACkpILdTb2eLhrnHSjKVMgNfCAfinTYrVA7FnO4DLc0h3kANPs7gQwK2y0dXNg%3d%3d | US | — | — | whitelisted |
7780 | svchost.exe | GET | 206 | 199.232.214.172:80 | http://msedge.b.tlu.dl.delivery.mp.microsoft.com/filestreamingservice/files/bf8090eb-6e5c-4c51-9250-5bf9b46cf160?P1=1753784819&P2=404&P3=2&P4=j03PkSOsANoACWkfZFWNEBg8vjKYHuf5f4DJL1exk8JVdsPk%2bvP4QJjP9FbFE0ns%2fGRs3%2fsjAsIp3xVynzW93Q%3d%3d | US | binary | 1.09 Kb | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
5944 | MoUsoCoreWorker.exe | 4.231.128.59:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
4024 | RUXIMICS.exe | 4.231.128.59:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
1268 | svchost.exe | 4.231.128.59:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
5460 | msedge.exe | 150.171.28.11:80 | edge.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5460 | msedge.exe | 13.107.42.16:443 | config.edge.skype.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5460 | msedge.exe | 150.171.27.11:443 | edge.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | US | whitelisted |
5460 | msedge.exe | 23.3.89.120:443 | copilot.microsoft.com | Akamai International B.V. | DE | whitelisted |
5460 | msedge.exe | 104.20.24.60:443 | app.shift.com | CLOUDFLARENET | — | whitelisted |
Domain | IP | Reputation |
|---|---|---|
google.com |
| whitelisted |
edge.microsoft.com |
| whitelisted |
config.edge.skype.com |
| whitelisted |
app.shift.com |
| whitelisted |
copilot.microsoft.com |
| whitelisted |
update.googleapis.com |
| whitelisted |
www.bing.com |
| whitelisted |
edgeassetservice.azureedge.net |
| whitelisted |
clients2.googleusercontent.com |
| whitelisted |
www.googleapis.com |
| whitelisted |
PID | Process | Class | Message |
|---|---|---|---|
2876 | shift.exe | Not Suspicious Traffic | INFO [ANY.RUN] An application monitoring request to sentry .io |
2876 | shift.exe | Not Suspicious Traffic | INFO [ANY.RUN] An application monitoring request to sentry .io |
2876 | shift.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
2876 | shift.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
2876 | shift.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
2876 | shift.exe | Not Suspicious Traffic | INFO [ANY.RUN] Google Tag Manager analytics (googletagmanager .com) |
2876 | shift.exe | Not Suspicious Traffic | INFO [ANY.RUN] Google Tag Manager analytics (googletagmanager .com) |
2876 | shift.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
2876 | shift.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
2876 | shift.exe | Generic Protocol Command Decode | SURICATA QUIC failed decrypt |
Process | Message |
|---|---|
shift.exe | RecursiveDirectoryCreate( C:\Users\admin\AppData\Local\Shift directory exists )
|