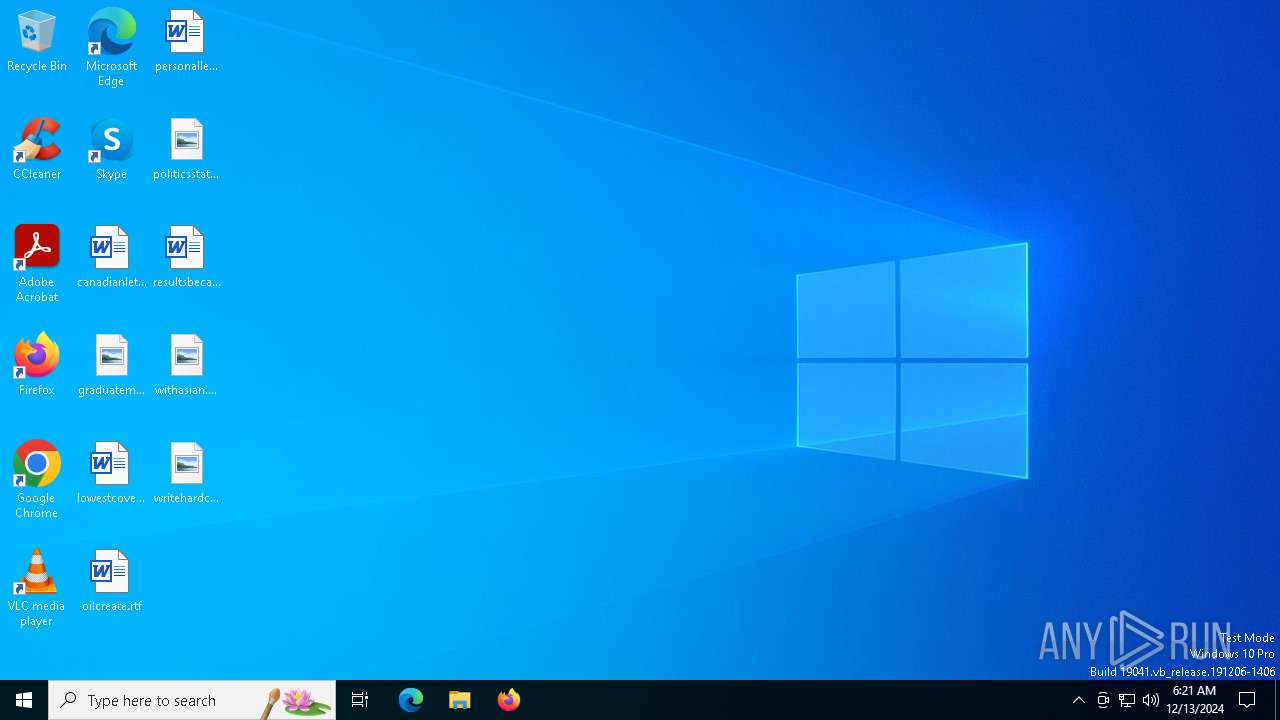
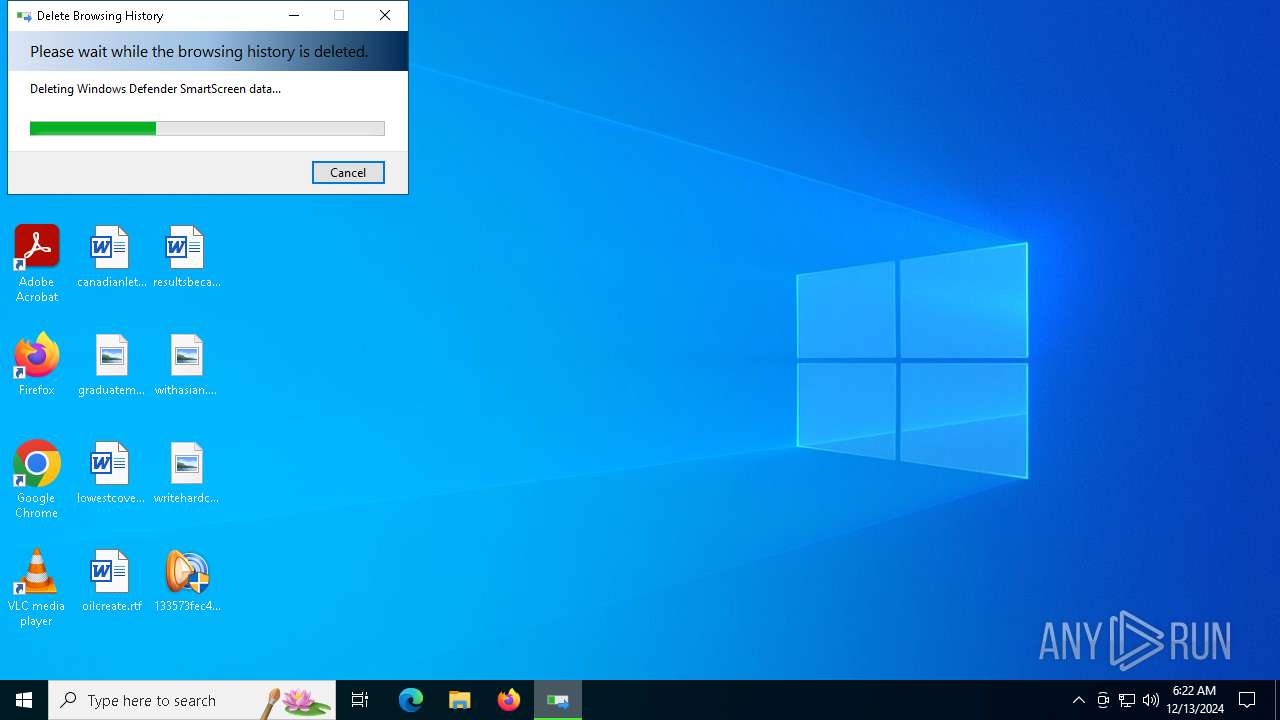
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | 133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3 |
| Full analysis: | https://app.any.run/tasks/1734760b-b09f-4f63-9309-214bbe5d0409 |
| Verdict: | Malicious activity |
| Analysis date: | December 13, 2024, 06:21:55 |
| OS: | Windows 10 Professional (build: 19045, 64 bit) |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386, for MS Windows, 4 sections |
| MD5: | 8F196DAE26F820859CD7364D48AEE5E1 |
| SHA1: | 4B0C91EAD868A76D84E6AD2A03BF8FEEDFFA4E08 |
| SHA256: | 133573FEC4D57C6D7CD662D283D8593C75FAC511874605020F0C83FF4E0A95E3 |
| SSDEEP: | 6144:vChvmvDvrEye5cLq2Ao6kpz5QEMzaaayI49FNjjjjbRhTYRdNCWclHIE7a7/NeZ/:vCqvrUwbAWoYtdeZam |
| .exe | | | Win32 Executable MS Visual C++ (generic) (42.2) |
|---|---|---|
| .exe | | | Win64 Executable (generic) (37.3) |
| .dll | | | Win32 Dynamic Link Library (generic) (8.8) |
| .exe | | | Win32 Executable (generic) (6) |
| .exe | | | Generic Win/DOS Executable (2.7) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2024:12:01 11:59:17+00:00 |
| ImageFileCharacteristics: | No relocs, Executable, No line numbers, No symbols, 32-bit |
| PEType: | PE32 |
| LinkerVersion: | 6 |
| CodeSize: | 278528 |
| InitializedDataSize: | 344064 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x30692 |
| OSVersion: | 4 |
| ImageVersion: | - |
| SubsystemVersion: | 4 |
| Subsystem: | Windows GUI |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 444 | taskkill /im Fondue.exe /f | C:\Windows\SysWOW64\taskkill.exe | — | 133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Terminates Processes Exit code: 128 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 624 | taskkill /im TslGame_BE.exe /f | C:\Windows\SysWOW64\taskkill.exe | — | 133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Terminates Processes Exit code: 128 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 640 | taskkill /im wscript.exe /f | C:\Windows\SysWOW64\taskkill.exe | — | 133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Terminates Processes Exit code: 128 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 836 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | taskkill.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1156 | taskkill /im iigw_server.exe /f | C:\Windows\SysWOW64\taskkill.exe | — | 133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Terminates Processes Exit code: 128 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1804 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | taskkill.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3080 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | taskkill.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3296 | Rundll32 InetCpl.cpl,ClearMyTracksByProcess 255 | C:\Windows\SysWOW64\rundll32.exe | — | 133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows host process (Rundll32) Exit code: 0 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 3364 | "C:\Users\admin\Desktop\133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3.exe" | C:\Users\admin\Desktop\133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: HIGH Exit code: 0 Modules
| |||||||||||||||
| 3560 | "C:\Users\admin\Desktop\133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3.exe" | C:\Users\admin\Desktop\133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3.exe | — | explorer.exe | |||||||||||
User: admin Integrity Level: MEDIUM Exit code: 3221226540 Modules
| |||||||||||||||
| (PID) Process: | (3296) rundll32.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Content |
| Operation: | write | Name: | CachePrefix |
Value: | |||
| (PID) Process: | (3296) rundll32.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Cookies |
| Operation: | write | Name: | CachePrefix |
Value: Cookie: | |||
| (PID) Process: | (3296) rundll32.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\History |
| Operation: | write | Name: | CachePrefix |
Value: Visited: | |||
| (PID) Process: | (3296) rundll32.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Internet Explorer\Main\WindowsSearch |
| Operation: | write | Name: | Version |
Value: WS not running | |||
| (PID) Process: | (3296) rundll32.exe | Key: | HKEY_USERS\S-1-5-19\SOFTWARE\Microsoft\Cryptography\TPM\Telemetry |
| Operation: | write | Name: | TraceTimeLast |
Value: 4DC21C54274DDB01 | |||
| (PID) Process: | (3296) rundll32.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Internet Explorer\LowRegistry\DOMStorage\Total |
| Operation: | delete key | Name: | (default) |
Value: | |||
| (PID) Process: | (3296) rundll32.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Internet Explorer\LowRegistry\DOMStorage |
| Operation: | delete key | Name: | (default) |
Value: | |||
| (PID) Process: | (3296) rundll32.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Internet Explorer\DomStorageState |
| Operation: | write | Name: | EdpCleanupState |
Value: 0 | |||
| (PID) Process: | (3296) rundll32.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Internet Explorer\TypedURLs |
| Operation: | delete key | Name: | (default) |
Value: | |||
| (PID) Process: | (3296) rundll32.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Internet Explorer\BrowserEmulation |
| Operation: | write | Name: | IECompatVersionHigh |
Value: 0 | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3364 | 133573fec4d57c6d7cd662d283d8593c75fac511874605020f0c83ff4e0a95e3.exe | C:\Users\admin\AppData\Local\TslGame\Saved\Config\WindowsNoEditor\GameUserSettings.ini | ini | |
MD5:3C3FBAFBA6BCDD1E4A2EA7537A32048A | SHA256:285C292385F2B3C0A0C1C6E0069D62CBDA5560877CE447570E39180BA735E0DE | |||
| 6432 | rundll32.exe | C:\Users\admin\AppData\Local\Packages\windows_ie_ac_001\AC\INetHistory\desktop.ini | text | |
MD5:FFFA3520C04320177050AA7C77C362E1 | SHA256:68CFDEB4843FD56030848AEAB87B86582F429080CAEA55D7A1F31B7A9E2E155F | |||
| 6432 | rundll32.exe | C:\Users\admin\AppData\Local\Packages\windows_ie_ac_001\AC\INetCache\MSIMGSIZ.DAT | binary | |
MD5:0392ADA071EB68355BED625D8F9695F3 | SHA256:B1313DD95EAF63F33F86F72F09E2ECD700D11159A8693210C37470FCB84038F7 | |||
| 6432 | rundll32.exe | C:\Users\admin\AppData\Local\Packages\windows_ie_ac_001\AC\INetCache\SmartScreenCache.dat | binary | |
MD5:1C7D3E30536E10B1EA45E1621B9E51C1 | SHA256:76910FBC1BCFA7296DD7E9CC5AD08904F9AD3FAA71BABBFA44F7EE4CBAB13B2D | |||
| 3296 | rundll32.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\INetCache\Low\SmartScreenCache.dat | binary | |
MD5:872FCA914B123250A14FD186E393438B | SHA256:20D2844CB3AB160F009E43526BC8DB41BFF018B0794DE0113F47DFAC00C62343 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
4308 | svchost.exe | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | NL | binary | 973 b | whitelisted |
4712 | MoUsoCoreWorker.exe | GET | 200 | 2.16.164.49:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 1.01 Kb | whitelisted |
4308 | svchost.exe | GET | 200 | 2.16.164.49:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 1.01 Kb | whitelisted |
6032 | RUXIMICS.exe | GET | 200 | 2.16.164.49:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | NL | binary | 1.01 Kb | whitelisted |
4712 | MoUsoCoreWorker.exe | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | NL | binary | 973 b | whitelisted |
6032 | RUXIMICS.exe | GET | 200 | 95.101.149.131:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | NL | binary | 973 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
6032 | RUXIMICS.exe | 51.104.136.2:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
— | — | 192.168.100.255:137 | — | — | — | whitelisted |
4308 | svchost.exe | 51.104.136.2:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4712 | MoUsoCoreWorker.exe | 51.104.136.2:443 | — | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
4712 | MoUsoCoreWorker.exe | 2.16.164.49:80 | crl.microsoft.com | Akamai International B.V. | NL | whitelisted |
4308 | svchost.exe | 2.16.164.49:80 | crl.microsoft.com | Akamai International B.V. | NL | whitelisted |
6032 | RUXIMICS.exe | 2.16.164.49:80 | crl.microsoft.com | Akamai International B.V. | NL | whitelisted |
4308 | svchost.exe | 95.101.149.131:80 | www.microsoft.com | Akamai International B.V. | NL | whitelisted |
4712 | MoUsoCoreWorker.exe | 95.101.149.131:80 | www.microsoft.com | Akamai International B.V. | NL | whitelisted |
Domain | IP | Reputation |
|---|---|---|
google.com |
| whitelisted |
crl.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
settings-win.data.microsoft.com |
| whitelisted |
self.events.data.microsoft.com |
| whitelisted |