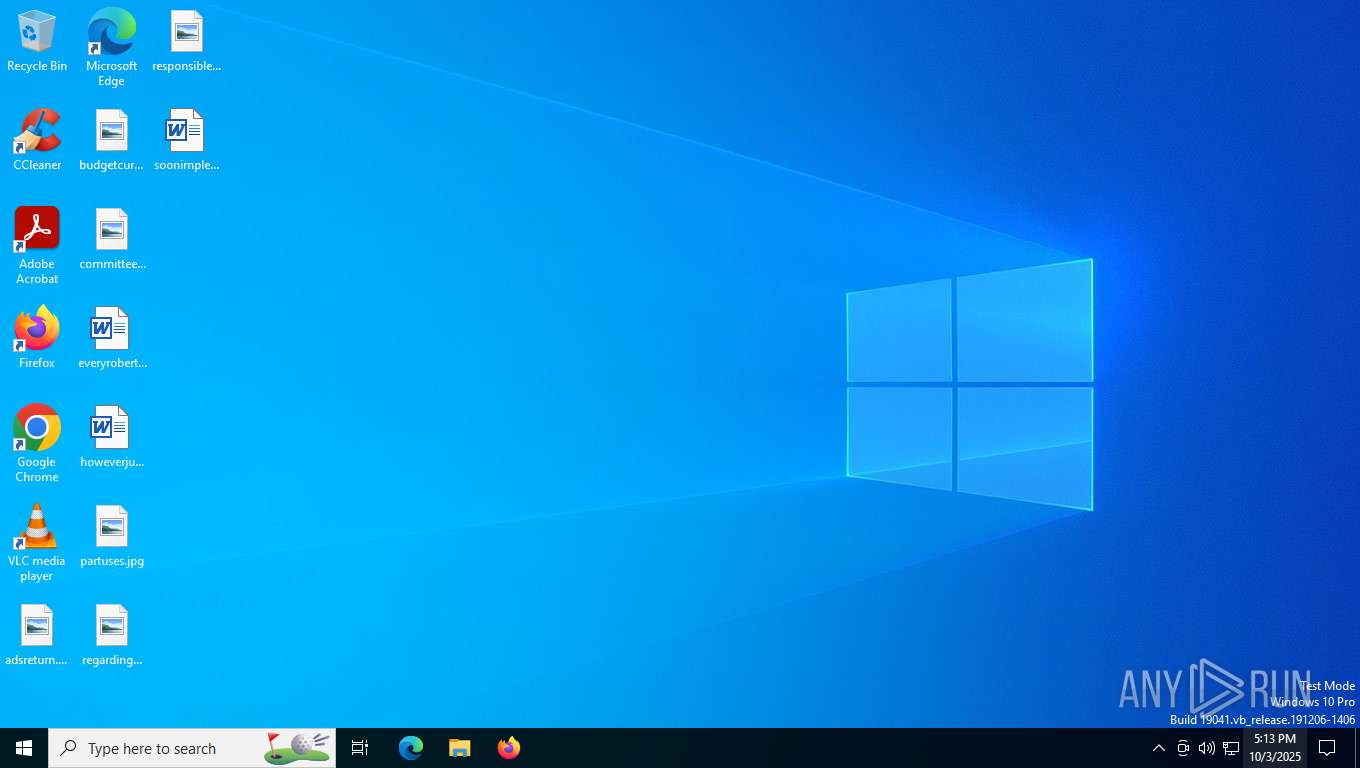
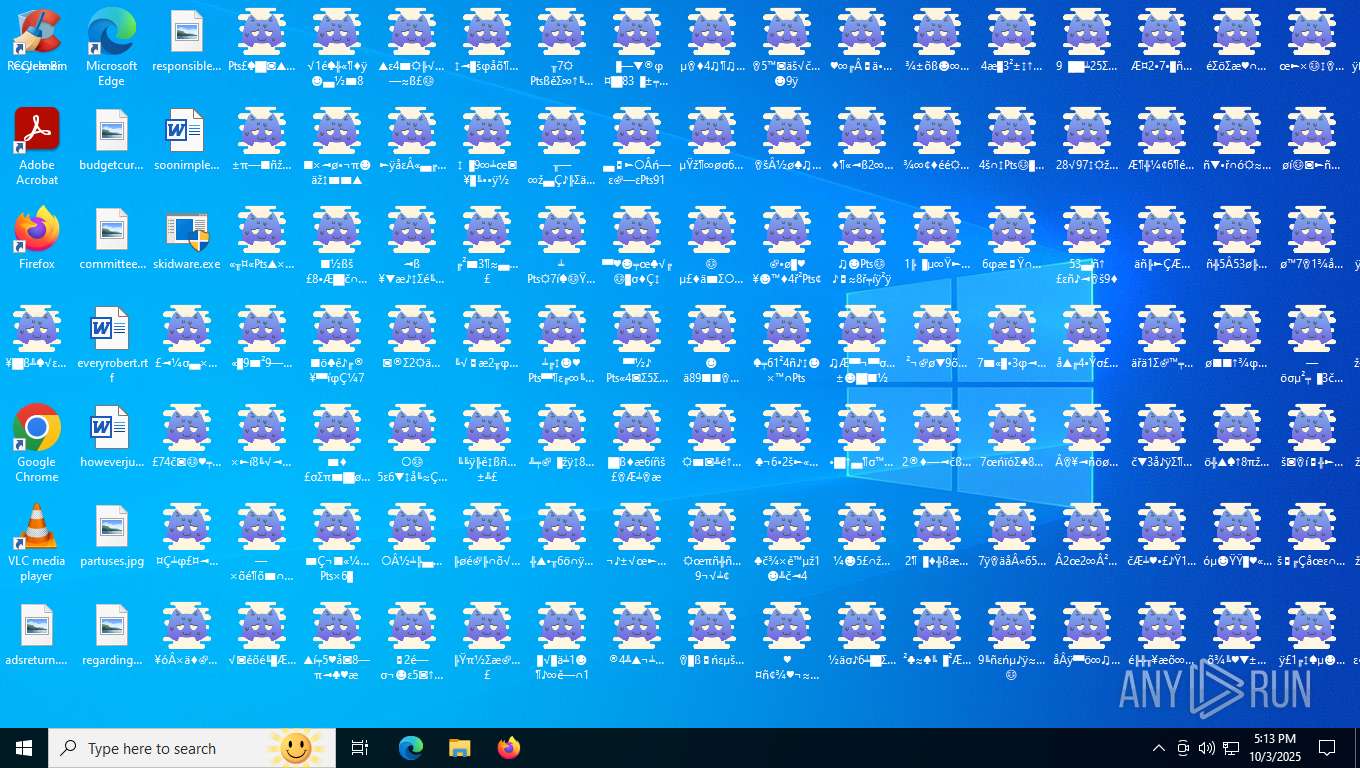
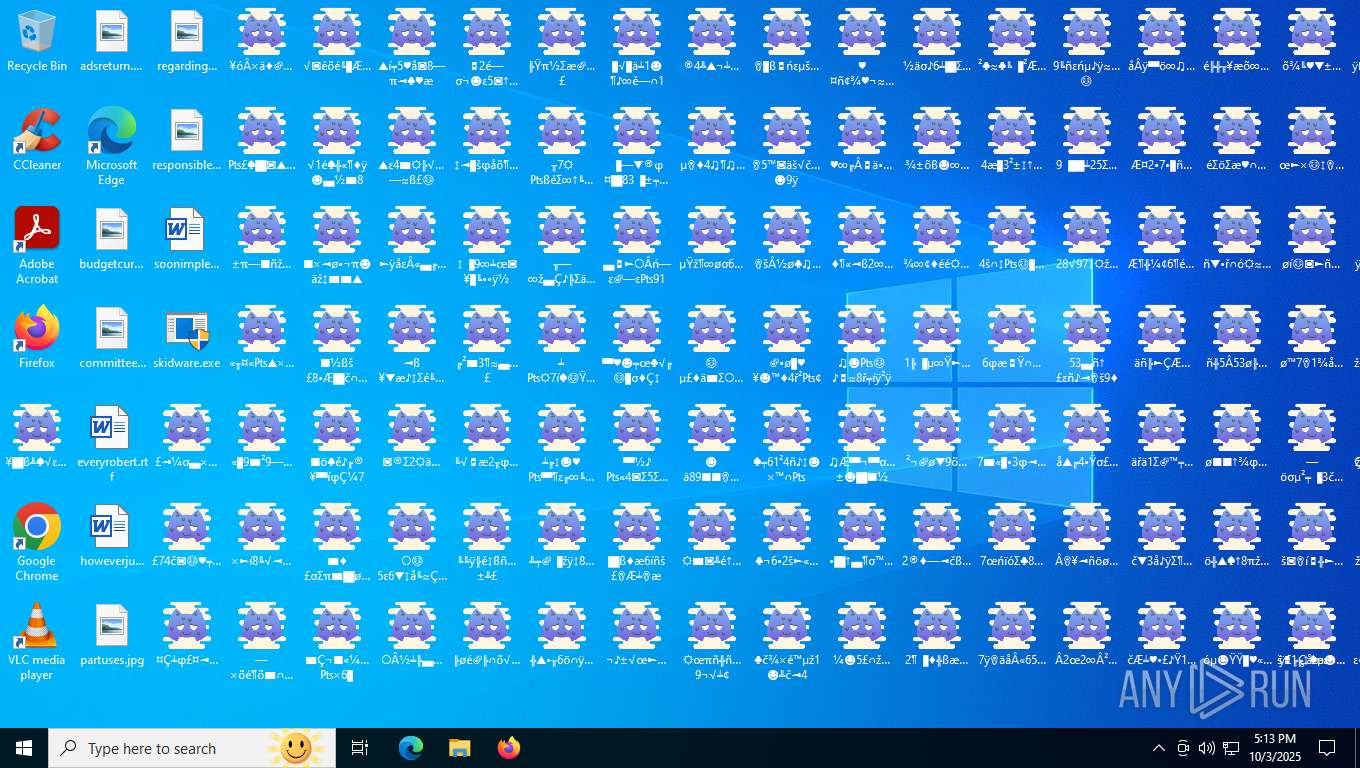
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | skidware.exe |
| Full analysis: | https://app.any.run/tasks/1a3b3a87-be9c-46b7-bc2a-ad2bc6084ec1 |
| Verdict: | Malicious activity |
| Analysis date: | October 03, 2025, 17:13:21 |
| OS: | Windows 10 Professional (build: 19044, 64 bit) |
| Indicators: | |
| MIME: | application/vnd.microsoft.portable-executable |
| File info: | PE32 executable (GUI) Intel 80386 Mono/.Net assembly, for MS Windows, 3 sections |
| MD5: | 0598662D503C30B11FEF8E1FF37B9CDF |
| SHA1: | 8B7B6BBD3D4C840F43804F8D689AD0EFCD751BAF |
| SHA256: | 12B6EA4413816F4F1B165BC936D50E3EFD7E3660BC5417E983697D449652A26D |
| SSDEEP: | 98304:OeMAaTG2W6bdhbU61xRrVoM0w0U0w0w0w0w0w0B0a0a0a0a0a0a0a0pwJnYyaWBW: |
| .exe | | | Generic CIL Executable (.NET, Mono, etc.) (63.1) |
|---|---|---|
| .exe | | | Win64 Executable (generic) (23.8) |
| .dll | | | Win32 Dynamic Link Library (generic) (5.6) |
| .exe | | | Win32 Executable (generic) (3.8) |
| .exe | | | Generic Win/DOS Executable (1.7) |
| MachineType: | Intel 386 or later, and compatibles |
|---|---|
| TimeStamp: | 2100:02:26 01:29:54+00:00 |
| ImageFileCharacteristics: | Executable, Large address aware |
| PEType: | PE32 |
| LinkerVersion: | 48 |
| CodeSize: | 2385408 |
| InitializedDataSize: | 5120 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x2482f2 |
| OSVersion: | 4 |
| ImageVersion: | - |
| SubsystemVersion: | 6 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 0.0.0.0 |
| ProductVersionNumber: | 0.0.0.0 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Win32 |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | Neutral |
| CharacterSet: | Unicode |
| FileDescription: | |
| FileVersion: | 0.0.0.0 |
| InternalName: | Cluttscape.exe |
| LegalCopyright: | |
| OriginalFileName: | Cluttscape.exe |
| ProductVersion: | 0.0.0.0 |
| AssemblyVersion: | 0.0.0.0 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 560 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 704 | net user å≈▲ÿń¾×Ÿεž×5╬▄ å≈▲ÿń¾×Ÿεž×5╬▄ /add | C:\Windows\System32\net.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Net Command Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 764 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 992 | net user 5½1ß◘♦æ√☺π♣äš× 5½1ß◘♦æ√☺π♣äš× /add | C:\Windows\System32\net.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Net Command Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 992 | net user πµ82◄7▀Æ▲Ç4í▌¬ πµ82◄7▀Æ▲Ç4í▌¬ /add | C:\Windows\System32\net.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Net Command Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 992 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 992 | C:\WINDOWS\system32\net1 user 1œžÿ1ßε█×♦å«ě5 1œžÿ1ßε█×♦å«ě5 /add | C:\Windows\System32\net1.exe | — | net.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Net Command Exit code: 0 Version: 10.0.19041.3636 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1136 | \??\C:\WINDOWS\system32\conhost.exe 0xffffffff -ForceV1 | C:\Windows\System32\conhost.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Console Window Host Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1188 | "C:\Windows\System32\cmd.exe" /k net user ♫×3¢¢╚¬¶▀öčΣžž ♫×3¢¢╚¬¶▀öčΣžž /add && exit | C:\Windows\System32\cmd.exe | — | skidware.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Windows Command Processor Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 1260 | net user ☼▲½š◙²øč汫╚Æń ☼▲½š◙²øč汫╚Æń /add | C:\Windows\System32\net.exe | — | cmd.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: HIGH Description: Net Command Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) | |||||||||||||||
| (PID) Process: | (3000) skidware.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | ProxyBypass |
Value: 1 | |||
| (PID) Process: | (3000) skidware.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | IntranetName |
Value: 1 | |||
| (PID) Process: | (3000) skidware.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | UNCAsIntranet |
Value: 1 | |||
| (PID) Process: | (3000) skidware.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | AutoDetect |
Value: 0 | |||
| (PID) Process: | (3000) skidware.exe | Key: | HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Keyboard Layout |
| Operation: | write | Name: | Scancode Map |
Value: 000000000000000051000000000021E000006CE000006DE0000011E000006BE0000050E000004BE000004DE0000048E0000040E0000042E000003BE000003EE000003CE000003FE0000058E0000007E0000041E0000057E0000043E0000023E000003DE00E0008E00000280000000C000000330000003400000035000000270000001A0000002B0000001B000000290000000D0000000B00000002000000030000000400000005000000060000000700000008000000090000000A0000001E000000300000002E0000002000000012000000210000002200000023000000240000003200000031000000180000001900000010000000130000001F00000014000000160000002F000000110000002D000000150000002C000000520000004F00000050000000510000004B0000004C0000004D0000004700000048000000490000000E00000053E000005FE000000000 | |||
| (PID) Process: | (3000) skidware.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System |
| Operation: | write | Name: | DisableTaskMgr |
Value: 1 | |||
| (PID) Process: | (3000) skidware.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System |
| Operation: | write | Name: | DisableRegistryTools |
Value: 1 | |||
| (PID) Process: | (3000) skidware.exe | Key: | HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon |
| Operation: | write | Name: | Shell |
Value: explorer.exe, cluttscape.exe | |||
| (PID) Process: | (3000) skidware.exe | Key: | HKEY_CURRENT_USER\Control Panel\Desktop |
| Operation: | write | Name: | AutoColorization |
Value: 1 | |||
| (PID) Process: | (3000) skidware.exe | Key: | HKEY_CURRENT_USER\Control Panel\Desktop |
| Operation: | write | Name: | WallPaper |
Value: C:\ProgramData\Microsoft\User Account Pictures\background.jpg | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 3000 | skidware.exe | C:\Windows\cluttscape.exe | executable | |
MD5:0598662D503C30B11FEF8E1FF37B9CDF | SHA256:12B6EA4413816F4F1B165BC936D50E3EFD7E3660BC5417E983697D449652A26D | |||
| 3000 | skidware.exe | C:\ProgramData\Microsoft\User Account Pictures\guest.bmp | image | |
MD5:31807E22503FD43248974C03CE11B61B | SHA256:32D5564C90DF8972F66E6B680CB725D6DF215D22ED8A611BEDB259E460A45D69 | |||
| 3000 | skidware.exe | C:\ProgramData\Microsoft\User Account Pictures\user.bmp | image | |
MD5:31807E22503FD43248974C03CE11B61B | SHA256:32D5564C90DF8972F66E6B680CB725D6DF215D22ED8A611BEDB259E460A45D69 | |||
| 3000 | skidware.exe | C:\ProgramData\Microsoft\User Account Pictures\background.jpg | image | |
MD5:2503DC1CC27BC4727456F514FC2DFD13 | SHA256:0A9ED9BEF18A3C864713ACC9745E72AF4F8AE5B2FF426CDED7A251A2942A5CAC | |||
| 3000 | skidware.exe | C:\ProgramData\Microsoft\User Account Pictures\user-192.png | image | |
MD5:12B879DCC2833BA4A9F19713955434F8 | SHA256:0C1132041C8EE4D924AF023A90D4BF42B9E2EF82D8812FB1626FA6D140B097D0 | |||
| 3000 | skidware.exe | C:\ProgramData\Microsoft\User Account Pictures\guest.png | image | |
MD5:12B879DCC2833BA4A9F19713955434F8 | SHA256:0C1132041C8EE4D924AF023A90D4BF42B9E2EF82D8812FB1626FA6D140B097D0 | |||
| 3000 | skidware.exe | C:\ProgramData\Microsoft\User Account Pictures\user-48.png | image | |
MD5:12B879DCC2833BA4A9F19713955434F8 | SHA256:0C1132041C8EE4D924AF023A90D4BF42B9E2EF82D8812FB1626FA6D140B097D0 | |||
| 3000 | skidware.exe | C:\ProgramData\Microsoft\User Account Pictures\kill.ico | image | |
MD5:708B6F1CE799360FC5295B85A54819CC | SHA256:8E243953C3BDF5FBD20027990CB88EA195BEAEEB1D57F2A65DB49AF43087E4E5 | |||
| 3000 | skidware.exe | C:\ProgramData\Microsoft\User Account Pictures\user.png | image | |
MD5:12B879DCC2833BA4A9F19713955434F8 | SHA256:0C1132041C8EE4D924AF023A90D4BF42B9E2EF82D8812FB1626FA6D140B097D0 | |||
| 3000 | skidware.exe | C:\ProgramData\Microsoft\User Account Pictures\user-40.png | image | |
MD5:12B879DCC2833BA4A9F19713955434F8 | SHA256:0C1132041C8EE4D924AF023A90D4BF42B9E2EF82D8812FB1626FA6D140B097D0 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
— | — | POST | 200 | 20.190.160.5:443 | https://login.live.com/RST2.srf | US | xml | 11.0 Kb | unknown |
— | — | POST | 204 | 92.123.104.62:443 | https://www.bing.com/web/xlsc.aspx?t=5&dl=1&wsbc=1 | unknown | — | — | unknown |
— | — | GET | 200 | 92.123.104.8:443 | https://www.bing.com/th?id=ODSWG.8229b0e5-fa8c-4e4a-af74-69717698b903&pid=dsb | unknown | image | 4.62 Kb | unknown |
— | — | GET | 200 | 20.165.94.63:443 | https://slscr.update.microsoft.com/SLS/%7B522D76A4-93E1-47F8-B8CE-07C937AD1A1E%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL | US | — | — | unknown |
— | — | GET | 200 | 20.3.187.198:443 | https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping | US | — | — | unknown |
8396 | SIHClient.exe | GET | 200 | 69.192.161.161:80 | http://www.microsoft.com/pkiops/crl/Microsoft%20ECC%20Product%20Root%20Certificate%20Authority%202018.crl | DE | binary | 419 b | whitelisted |
— | — | GET | 304 | 20.165.94.63:443 | https://slscr.update.microsoft.com/SLS/%7B522D76A4-93E1-47F8-B8CE-07C937AD1A1E%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL | US | — | — | unknown |
— | — | GET | 200 | 52.109.76.240:443 | https://officeclient.microsoft.com/config16/?syslcid=1033&build=16.0.16026&crev=3 | IE | xml | 183 Kb | unknown |
— | — | POST | 403 | 69.192.161.161:443 | https://go.microsoft.com/fwlink/?LinkID=2257403&clcid=0x409 | US | html | 384 b | unknown |
— | — | POST | 200 | 20.190.160.14:443 | https://login.live.com/RST2.srf | US | xml | 10.3 Kb | unknown |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
6016 | MoUsoCoreWorker.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
6904 | RUXIMICS.exe | 51.104.136.2:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
6016 | MoUsoCoreWorker.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5948 | svchost.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
5224 | SearchApp.exe | 184.86.251.22:443 | www.bing.com | Akamai International B.V. | DE | whitelisted |
4440 | svchost.exe | 20.190.159.0:443 | login.live.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | whitelisted |
3464 | svchost.exe | 172.211.123.249:443 | client.wns.windows.com | MICROSOFT-CORP-MSN-AS-BLOCK | FR | whitelisted |
8396 | SIHClient.exe | 135.232.92.137:443 | slscr.update.microsoft.com | LUCENT-CIO | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
www.bing.com |
| whitelisted |
login.live.com |
| whitelisted |
client.wns.windows.com |
| whitelisted |
slscr.update.microsoft.com |
| whitelisted |
www.microsoft.com |
| whitelisted |
fe3cr.delivery.mp.microsoft.com |
| whitelisted |
self.events.data.microsoft.com |
| whitelisted |
137.92.232.135.in-addr.arpa |
| whitelisted |