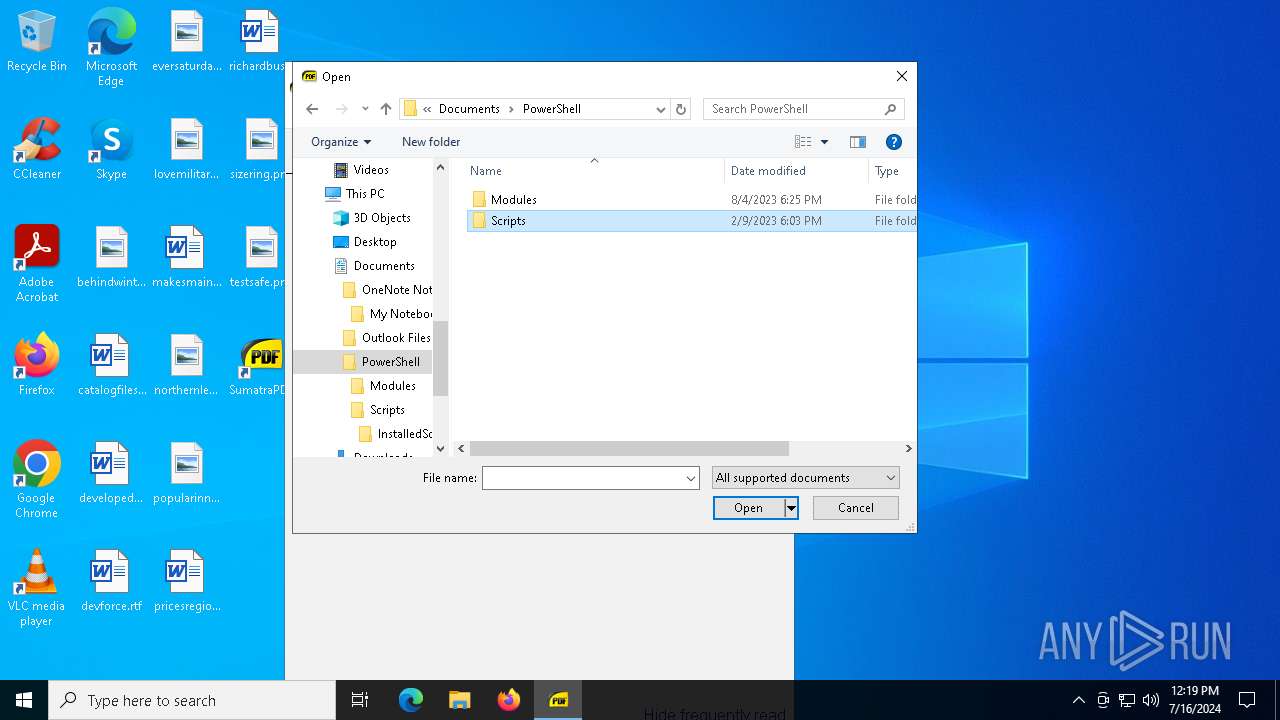
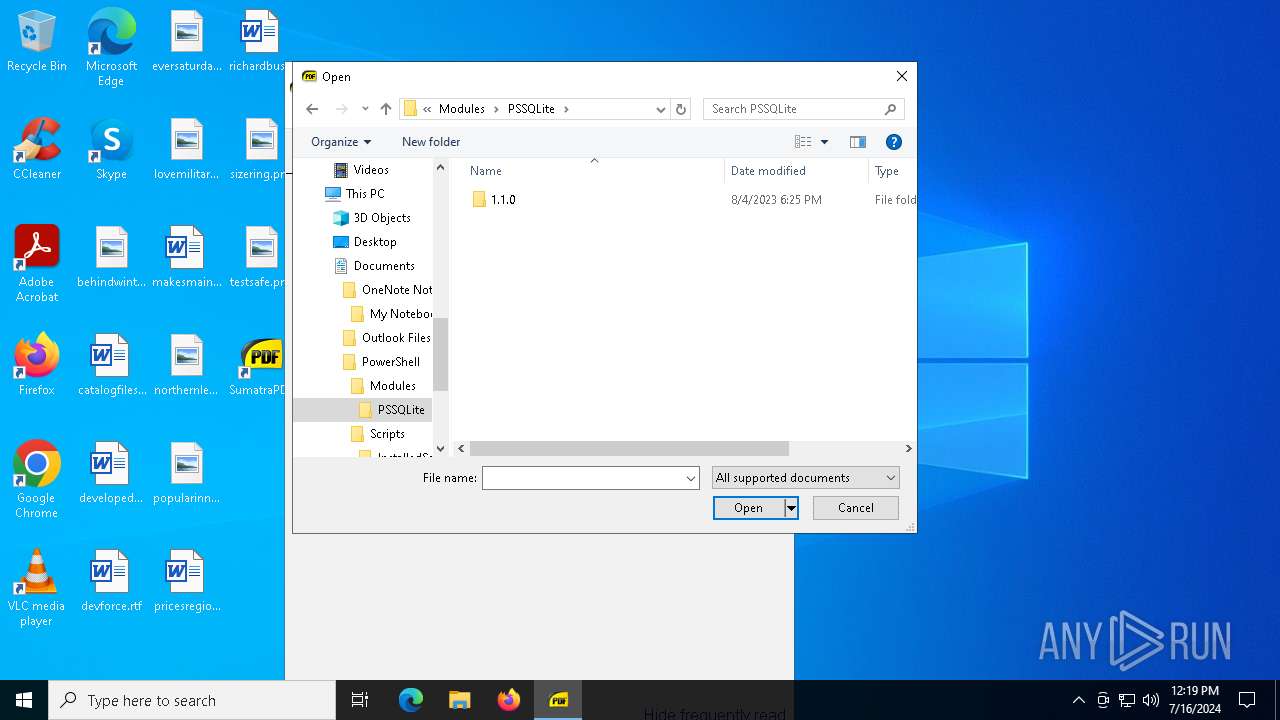
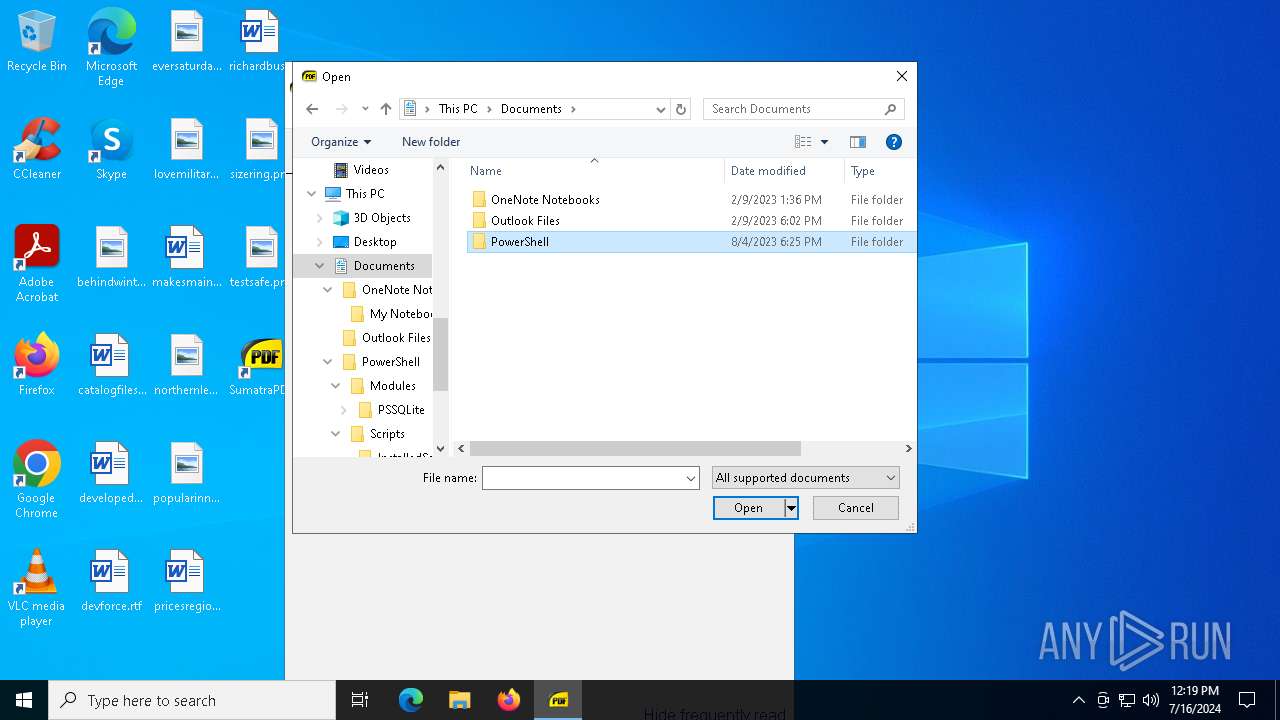
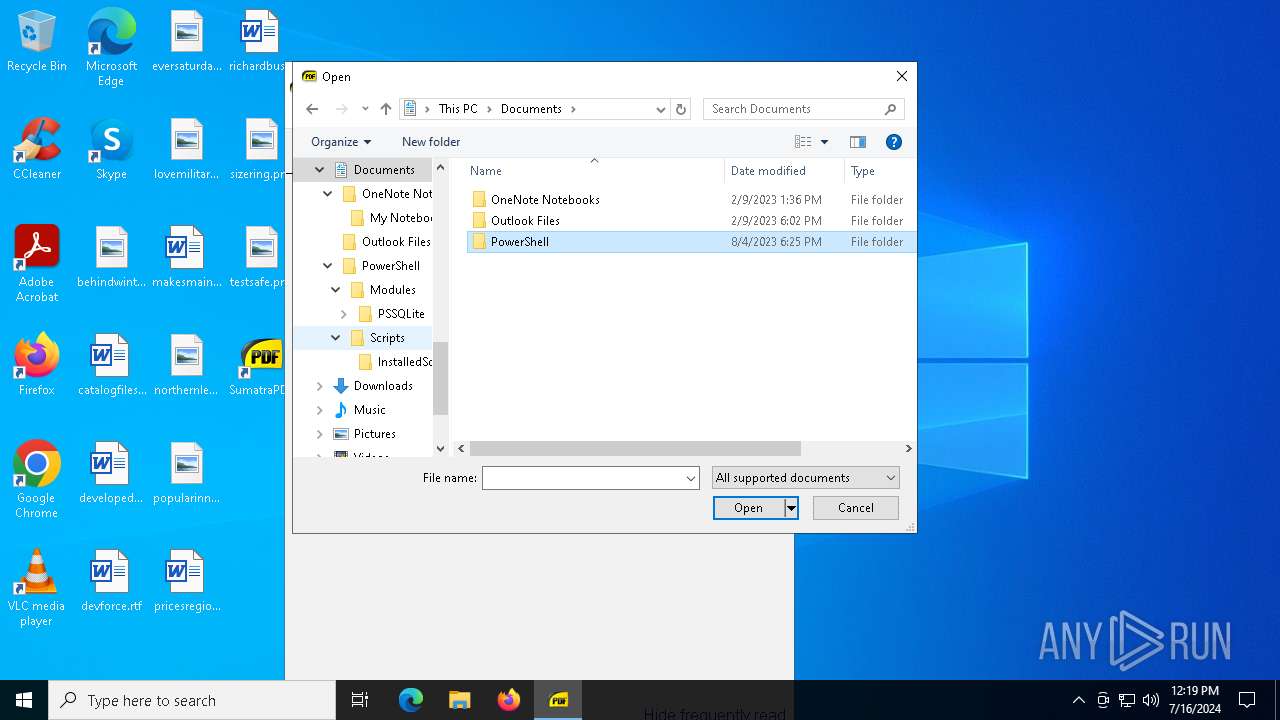
ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
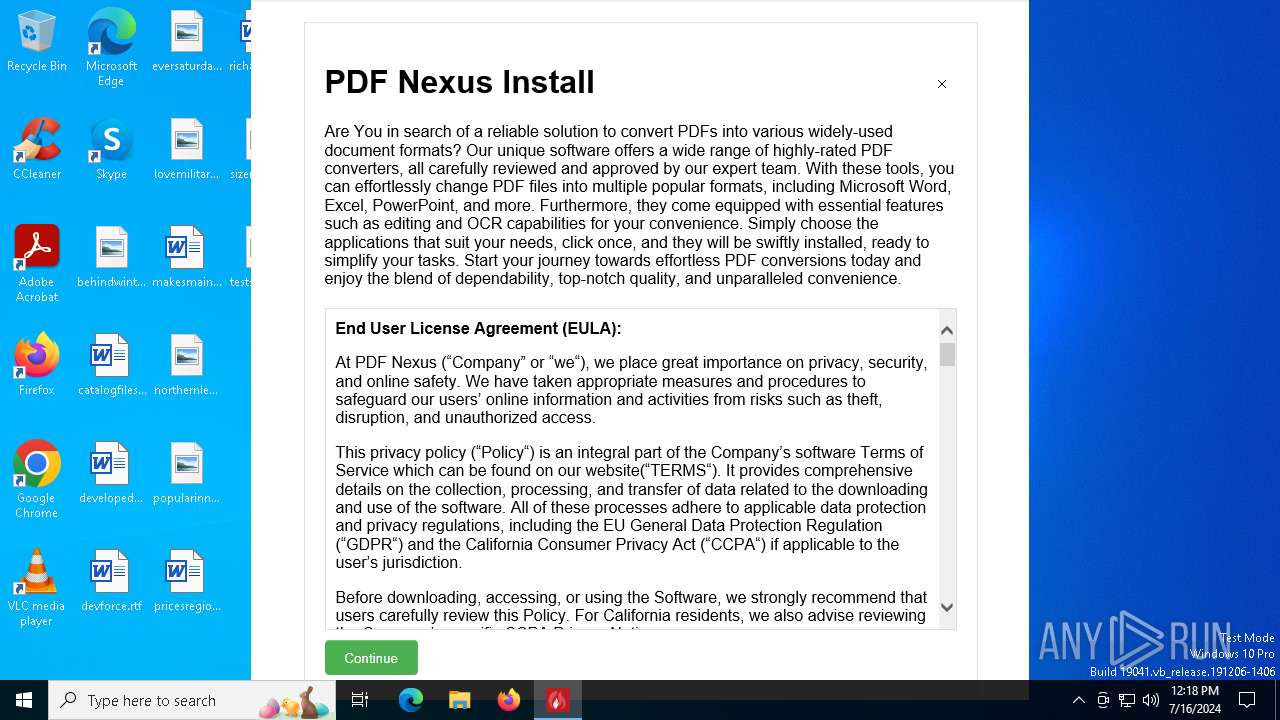
| File name: | PDFNexus.exe |
| Full analysis: | https://app.any.run/tasks/6d1b2486-16bc-4a6d-85e2-49da71fa3707 |
| Verdict: | Malicious activity |
| Analysis date: | July 16, 2024, 12:18:35 |
| OS: | Windows 10 Professional (build: 19045, 64 bit) |
| Indicators: | |
| MIME: | application/x-dosexec |
| File info: | PE32+ executable (GUI) x86-64 Mono/.Net assembly, for MS Windows |
| MD5: | C7974B329EF5787872C6A60045628BB6 |
| SHA1: | 0541718CADA0115D086C971462F1382CF442CB86 |
| SHA256: | 0C5C08FE244110EC1CE9F11E0C44F203194270970A73A485B94B57B557724F0B |
| SSDEEP: | 98304:laPGf3Lx51clR43g0ZtKC5/TF4i9bYvQCPjhPXq2fZWwZmchG6QjvOr/av7Vx6dO:Gm3qrzPw0jtrQr |
| .exe | | | Generic Win/DOS Executable (50) |
|---|---|---|
| .exe | | | DOS Executable Generic (49.9) |
| MachineType: | AMD AMD64 |
|---|---|
| TimeStamp: | 2070:01:06 02:11:59+00:00 |
| ImageFileCharacteristics: | Executable, Large address aware |
| PEType: | PE32+ |
| LinkerVersion: | 80 |
| CodeSize: | 8270848 |
| InitializedDataSize: | 114688 |
| UninitializedDataSize: | - |
| EntryPoint: | 0x0000 |
| OSVersion: | 4 |
| ImageVersion: | - |
| SubsystemVersion: | 6 |
| Subsystem: | Windows GUI |
| FileVersionNumber: | 1.0.0.0 |
| ProductVersionNumber: | 1.0.0.0 |
| FileFlagsMask: | 0x003f |
| FileFlags: | (none) |
| FileOS: | Win32 |
| ObjectFileType: | Executable application |
| FileSubtype: | - |
| LanguageCode: | Neutral |
| CharacterSet: | Unicode |
| Comments: | - |
| CompanyName: | - |
| FileDescription: | PDFNexus |
| FileVersion: | 1.0.0.0 |
| InternalName: | PDFNexus.exe |
| LegalCopyright: | Copyright © 2024 |
| LegalTrademarks: | - |
| OriginalFileName: | PDFNexus.exe |
| ProductName: | PDFNexus |
| ProductVersion: | 1.0.0.0 |
| AssemblyVersion: | 1.0.0.0 |
PID | CMD | Path | Indicators | Parent process | |||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| 3676 | C:\WINDOWS\System32\slui.exe -Embedding | C:\Windows\System32\slui.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows Activation Client Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
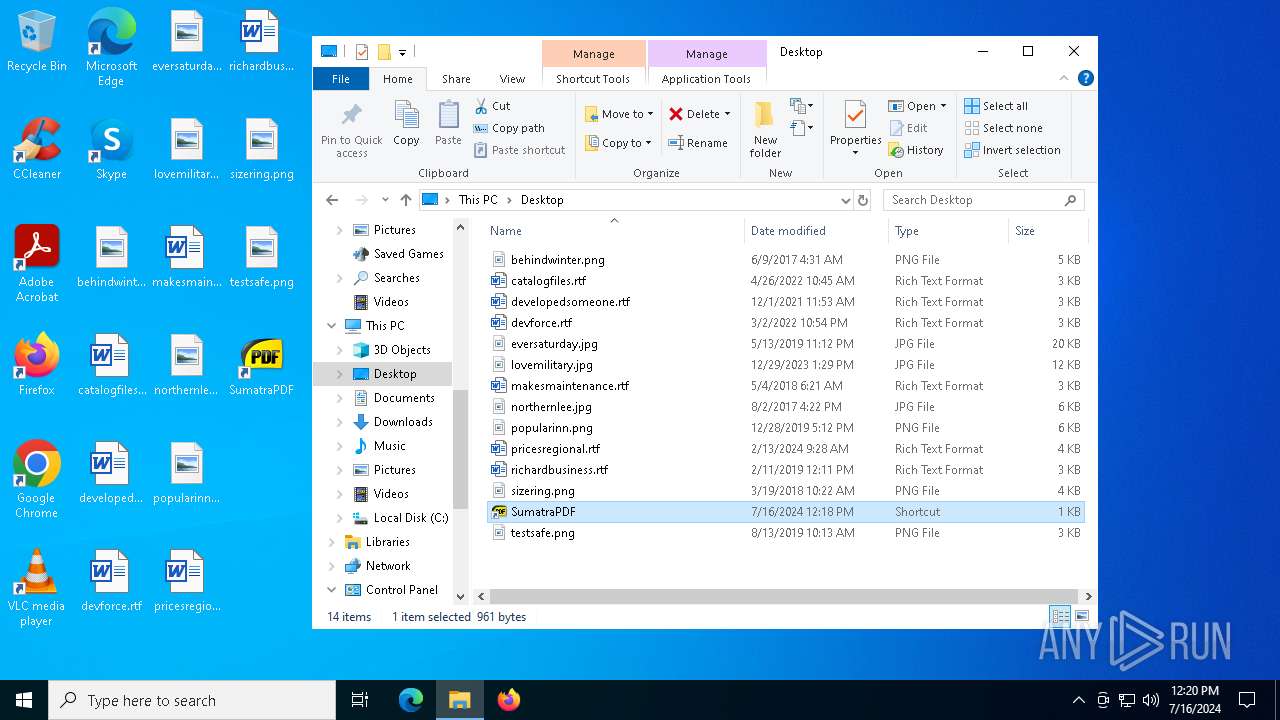
| 5896 | "C:\Users\admin\AppData\Local\Temp\PDFNexus.exe" | C:\Users\admin\AppData\Local\Temp\PDFNexus.exe | explorer.exe | ||||||||||||
User: admin Integrity Level: MEDIUM Description: PDFNexus Exit code: 0 Version: 1.0.0.0 Modules
| |||||||||||||||
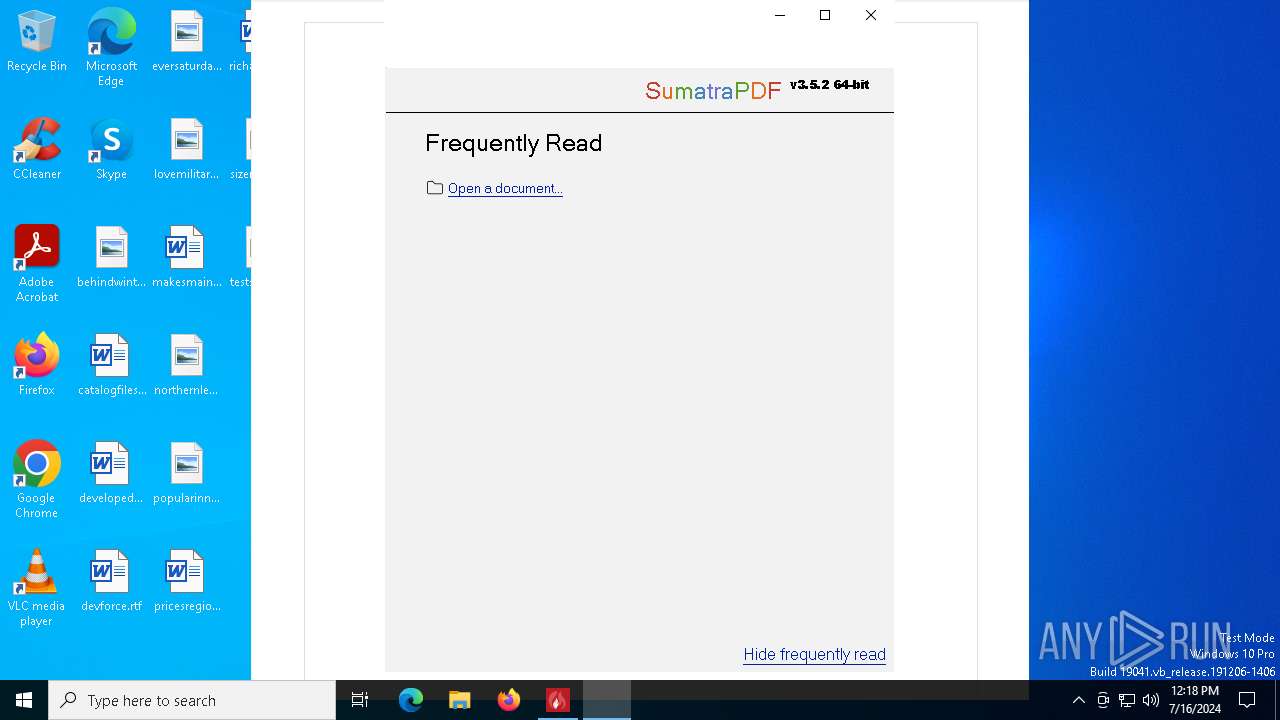
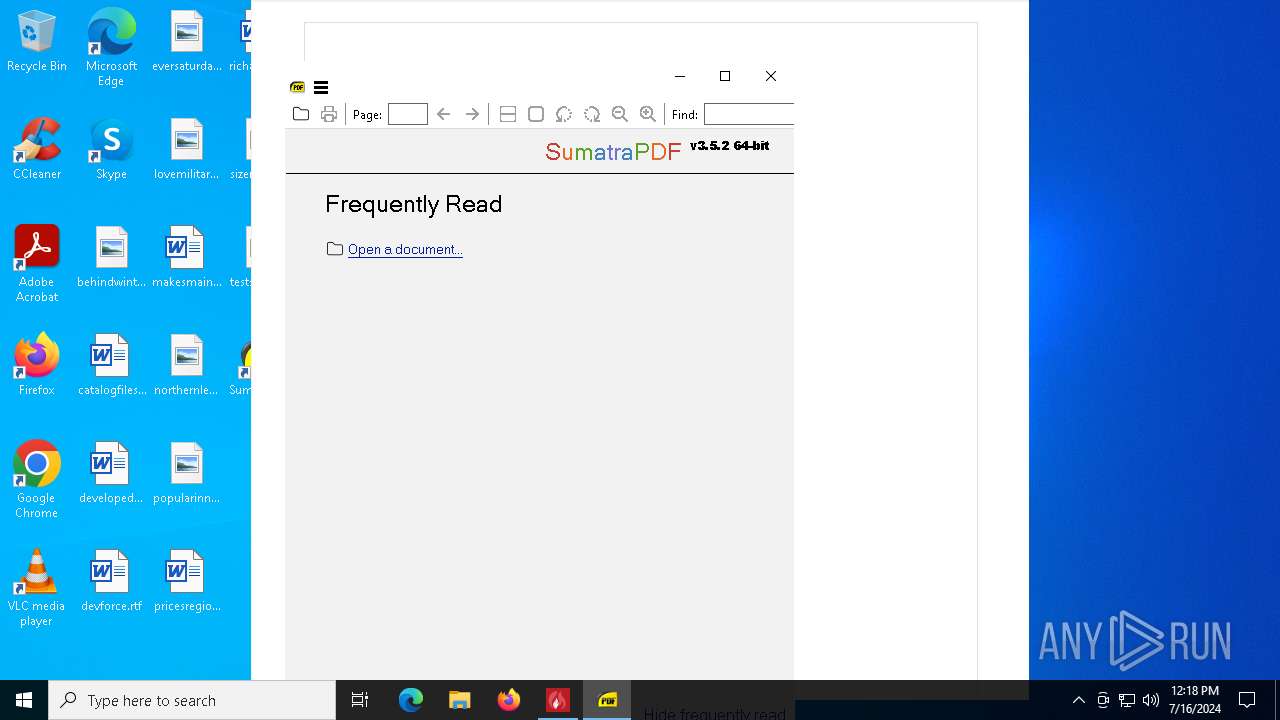
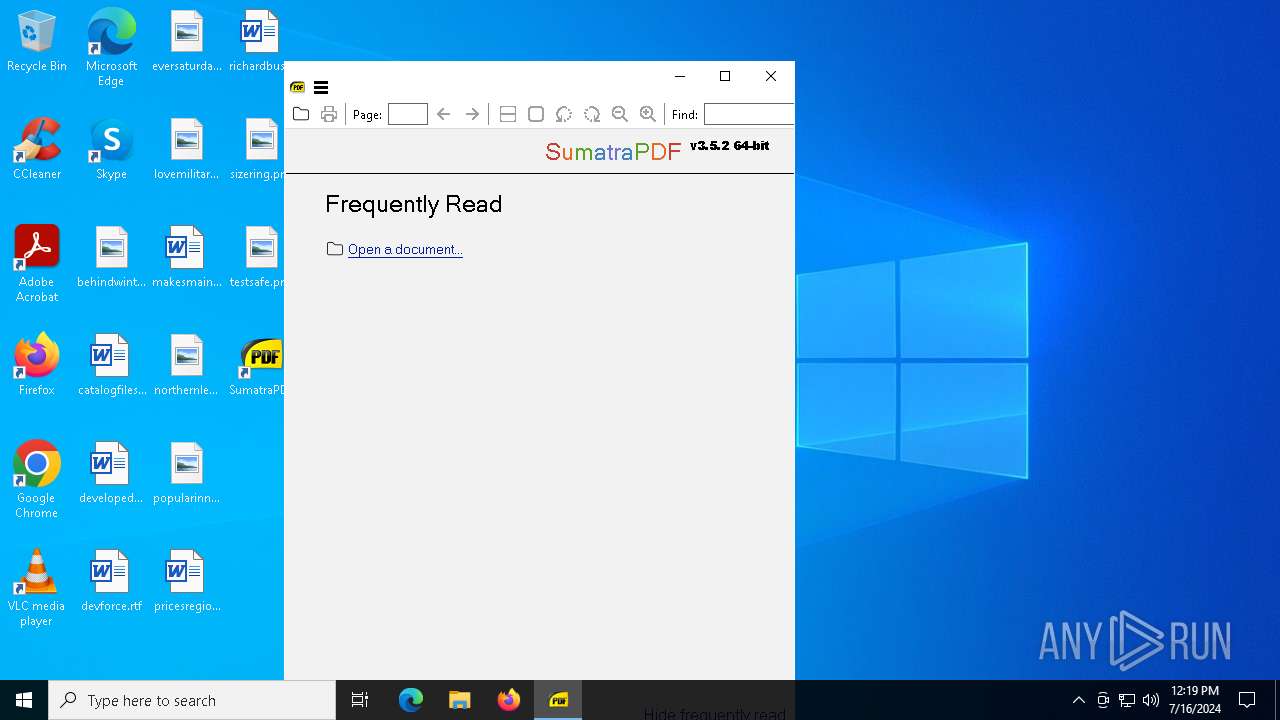
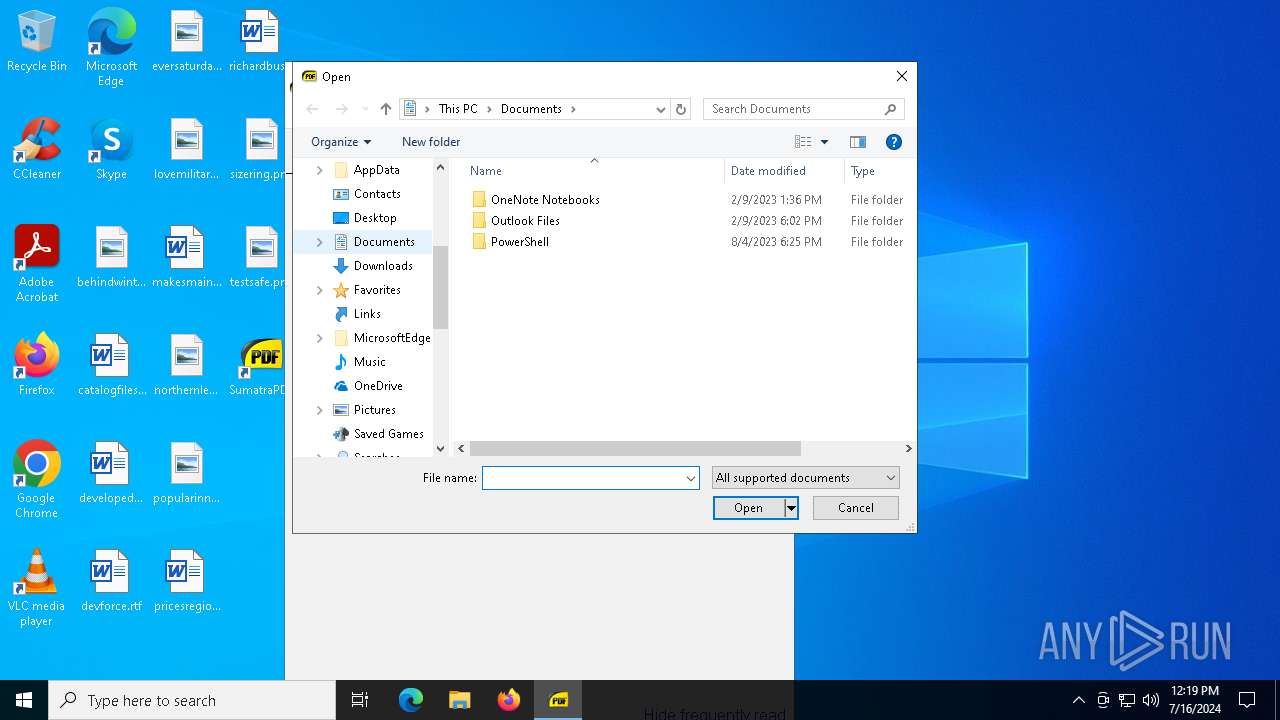
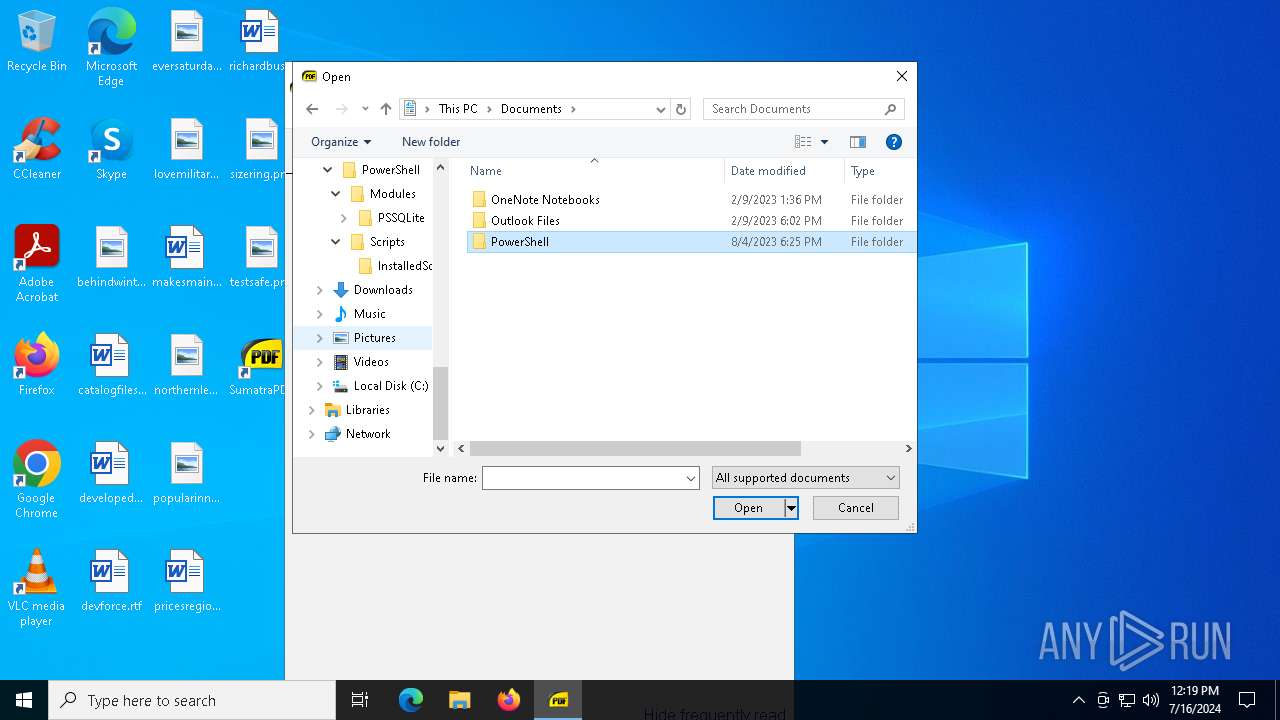
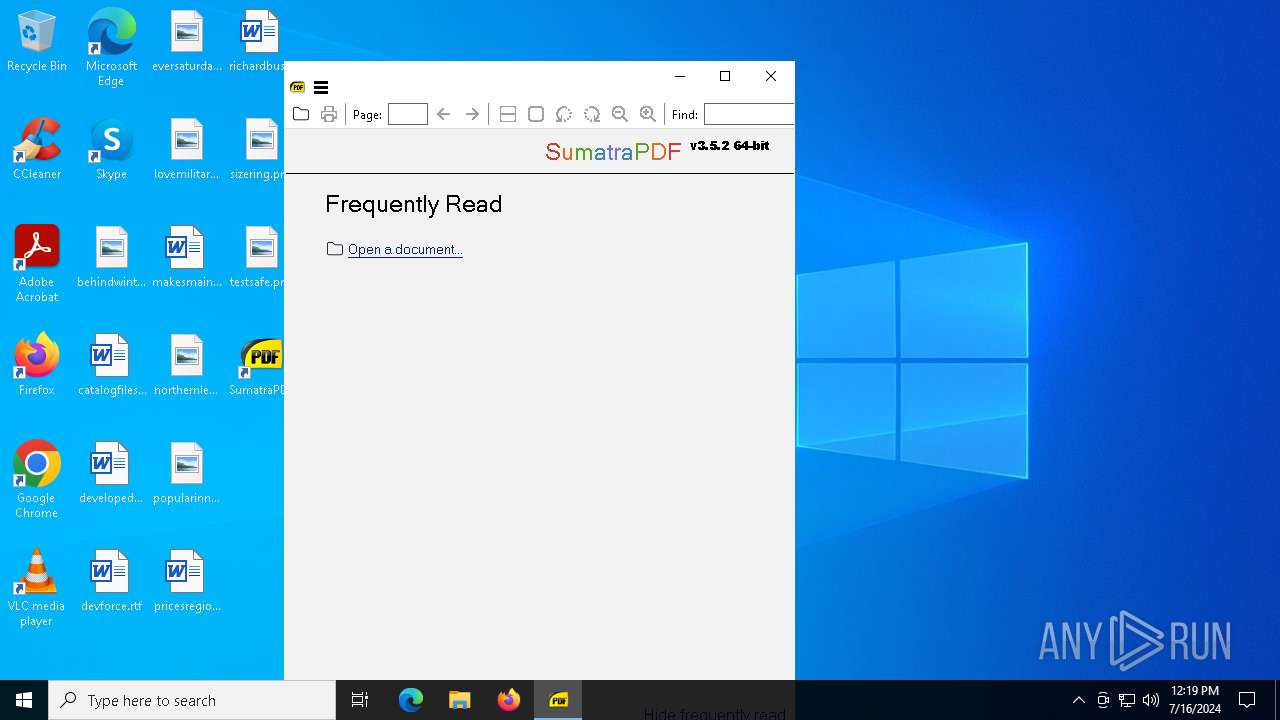
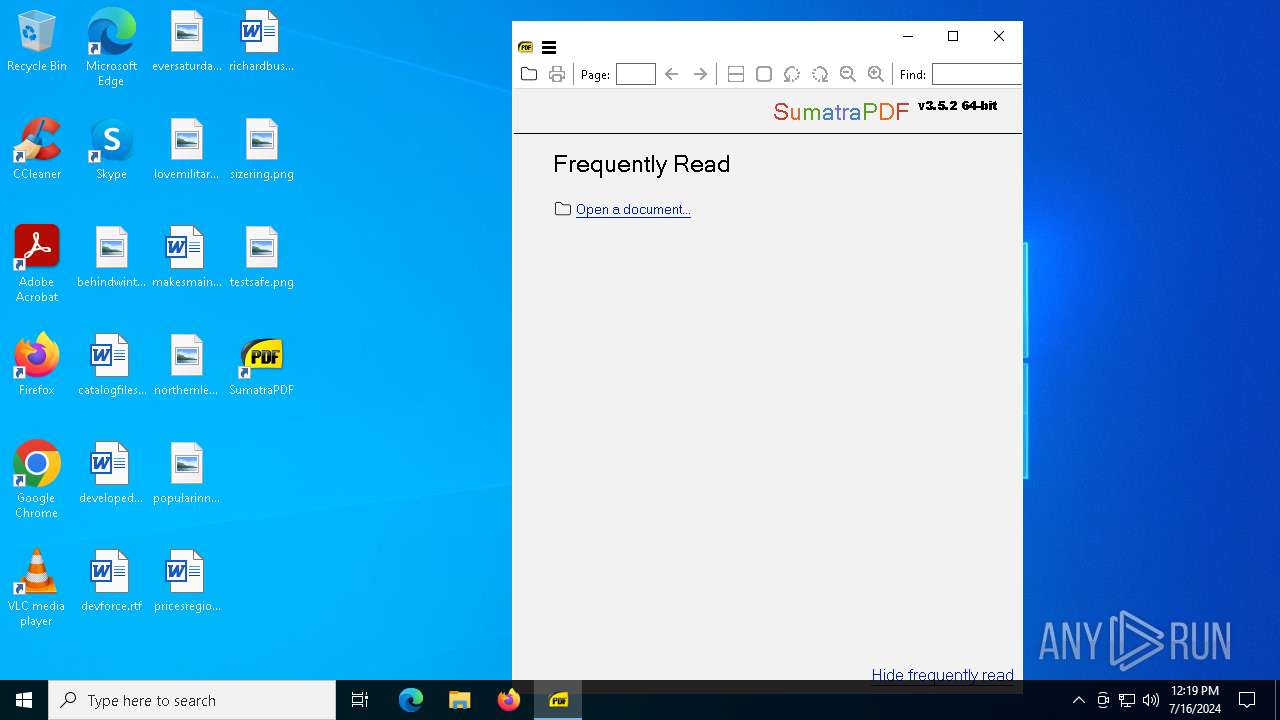
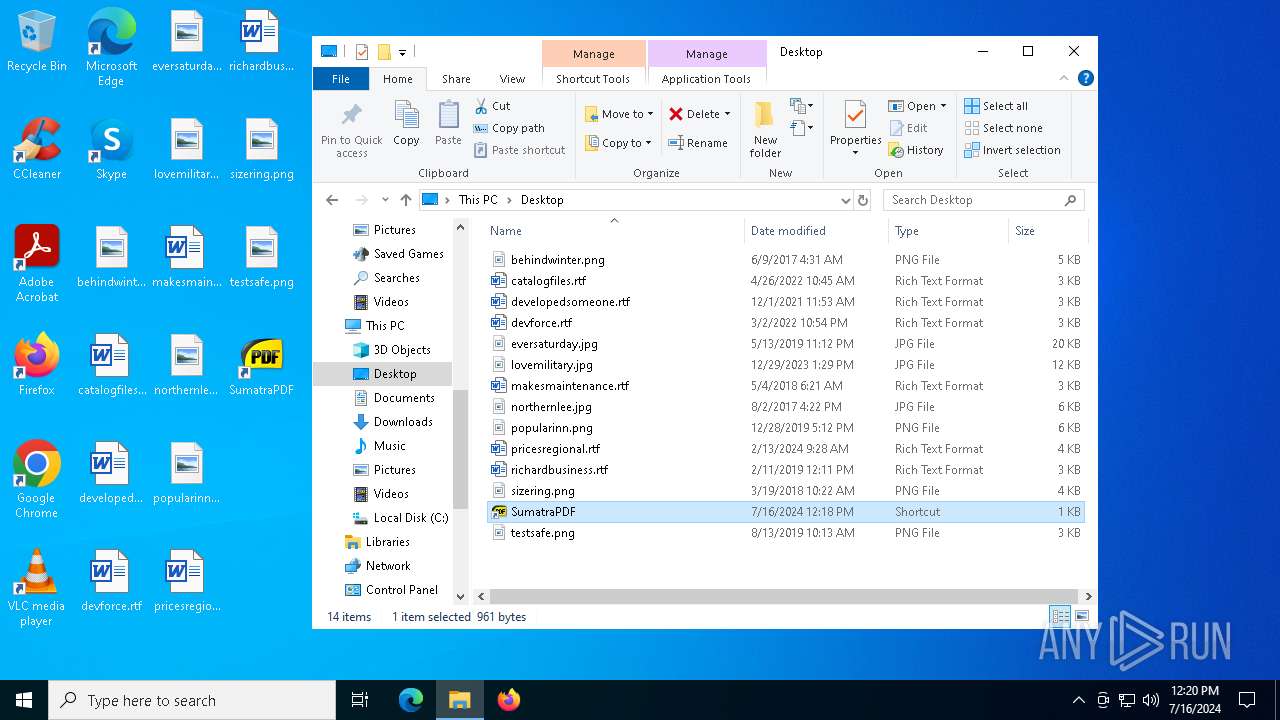
| 6408 | "C:\Users\admin\AppData\Roaming\SumatraPDF\SumatraPDF-3.5.2-64.exe" | C:\Users\admin\AppData\Roaming\SumatraPDF\SumatraPDF-3.5.2-64.exe | PDFNexus.exe | ||||||||||||
User: admin Company: Krzysztof Kowalczyk Integrity Level: MEDIUM Description: SumatraPDF Exit code: 0 Version: 3.5.2 Modules
| |||||||||||||||
| 6728 | C:\WINDOWS\system32\SppExtComObj.exe -Embedding | C:\Windows\System32\SppExtComObj.Exe | — | svchost.exe | |||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: KMS Connection Broker Version: 10.0.19041.3996 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6760 | "C:\WINDOWS\System32\SLUI.exe" RuleId=3482d82e-ca2c-4e1f-8864-da0267b484b2;Action=AutoActivate;AppId=55c92734-d682-4d71-983e-d6ec3f16059f;SkuId=4de7cb65-cdf1-4de9-8ae8-e3cce27b9f2c;NotificationInterval=1440;Trigger=TimerEvent | C:\Windows\System32\slui.exe | SppExtComObj.Exe | ||||||||||||
User: NETWORK SERVICE Company: Microsoft Corporation Integrity Level: SYSTEM Description: Windows Activation Client Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 6904 | C:\WINDOWS\System32\rundll32.exe C:\WINDOWS\System32\shell32.dll,SHCreateLocalServerRunDll {9aa46009-3ce0-458a-a354-715610a075e6} -Embedding | C:\Windows\System32\rundll32.exe | — | svchost.exe | |||||||||||
User: admin Company: Microsoft Corporation Integrity Level: MEDIUM Description: Windows host process (Rundll32) Exit code: 0 Version: 10.0.19041.1 (WinBuild.160101.0800) Modules
| |||||||||||||||
| 7020 | "C:\Users\admin\AppData\Roaming\SumatraPDF\SumatraPDF-3.5.2-64.exe" | C:\Users\admin\AppData\Roaming\SumatraPDF\SumatraPDF-3.5.2-64.exe | explorer.exe | ||||||||||||
User: admin Company: Krzysztof Kowalczyk Integrity Level: MEDIUM Description: SumatraPDF Exit code: 0 Version: 3.5.2 Modules
| |||||||||||||||
| (PID) Process: | (5896) PDFNexus.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | ProxyBypass |
Value: 1 | |||
| (PID) Process: | (5896) PDFNexus.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | IntranetName |
Value: 1 | |||
| (PID) Process: | (5896) PDFNexus.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | UNCAsIntranet |
Value: 1 | |||
| (PID) Process: | (5896) PDFNexus.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap |
| Operation: | write | Name: | AutoDetect |
Value: 0 | |||
| (PID) Process: | (5896) PDFNexus.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Content |
| Operation: | write | Name: | CachePrefix |
Value: | |||
| (PID) Process: | (5896) PDFNexus.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\Cookies |
| Operation: | write | Name: | CachePrefix |
Value: Cookie: | |||
| (PID) Process: | (5896) PDFNexus.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\Cache\History |
| Operation: | write | Name: | CachePrefix |
Value: Visited: | |||
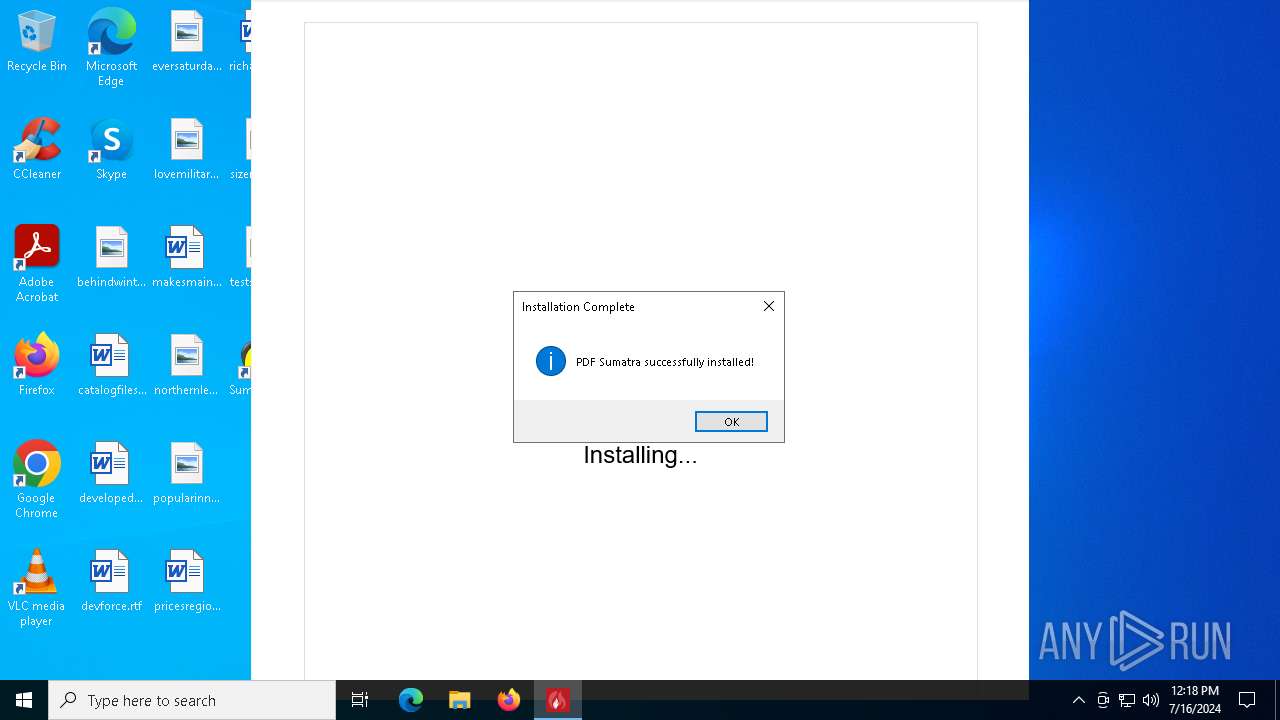
| (PID) Process: | (5896) PDFNexus.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\SumatraPDFUninstall |
| Operation: | write | Name: | DisplayName |
Value: SumatraPDF | |||
| (PID) Process: | (5896) PDFNexus.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall\SumatraPDFUninstall |
| Operation: | write | Name: | UninstallString |
Value: cmd /c rmdir /s /q "C:\Users\admin\AppData\Roaming\SumatraPDF" & del "C:\Users\admin\Desktop\SumatraPDF.lnk" & reg delete HKCU\Software\Microsoft\Windows\CurrentVersion\Uninstall\SumatraPDFUninstall /f | |||
| (PID) Process: | (5896) PDFNexus.exe | Key: | HKEY_CURRENT_USER\SOFTWARE\Microsoft\Internet Explorer\LowRegistry |
| Operation: | delete value | Name: | AddToFavoritesInitialSelection |
Value: | |||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 5896 | PDFNexus.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\05DDC6AA91765AACACDB0A5F96DF8199 | der | |
MD5:8D1040B12A663CA4EC7277CFC1CE44F0 | SHA256:3086094D4198A5BBD12938B0D2D5F696C4DFC77E1EAE820ADDED346A59AA8727 | |||
| 5896 | PDFNexus.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\B46811C17859FFB409CF0E904A4AA8F8 | der | |
MD5:1BFE0A81DB078EA084FF82FE545176FE | SHA256:5BA8817F13EEE00E75158BAD93076AB474A068C6B52686579E0F728FDA68499F | |||
| 5896 | PDFNexus.exe | C:\Users\admin\AppData\Local\Microsoft\Windows\INetCache\IE\RR3E01RZ\font[1].eot | binary | |
MD5:C6B85601ADBF8C674B4B444DAD696A5D | SHA256:EC8671B432FF49E1E77F48692397E57ECFA584555AC664C932DCCEA0C9A16044 | |||
| 5896 | PDFNexus.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\MetaData\05DDC6AA91765AACACDB0A5F96DF8199 | binary | |
MD5:7B3AFA8373F6F4D5FDA54098E0FA8383 | SHA256:0BD3A7699AFC92DFB49CFD6AF8EDC87031A7C08512D9029765410419BDD50E20 | |||
| 5896 | PDFNexus.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\8B2B9A00839EED1DFDCCC3BFC2F5DF12 | der | |
MD5:7FB5FA1534DCF77F2125B2403B30A0EE | SHA256:33A39E9EC2133230533A686EC43760026E014A3828C703707ACBC150FE40FD6F | |||
| 5896 | PDFNexus.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\MetaData\B46811C17859FFB409CF0E904A4AA8F8 | binary | |
MD5:2F7347A600F689A32C1418309A6D157F | SHA256:DB1F42376640063F0B149B8FFDB4A65023D12F6BA2E6CFDCAEF831D89ABB2435 | |||
| 5896 | PDFNexus.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\MetaData\8B2B9A00839EED1DFDCCC3BFC2F5DF12 | binary | |
MD5:EA6D3FA922F2B38F523BBDBA170D299A | SHA256:29A76F619FA4DCFA583CD95734D6CA9A66D956ACC023799C02669525B7E07435 | |||
| 5896 | PDFNexus.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\DDE8B1B7E253A9758EC380BD648952AF_857450206B889F4FEA0F888FA03D68DB | der | |
MD5:5472B509C2B20FDBB61940A5C1949DB9 | SHA256:CF1D223E59007BB49AAC397F89AB34B75A086424211E884FA5FFDE34BDDF4167 | |||
| 5896 | PDFNexus.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\Content\B3513D73A177A2707D910183759B389B_32201FF65E9A20A693462A3946A29CAE | der | |
MD5:5D5650AB608CD61702DE4FA6B7457044 | SHA256:4FF3F940A74F047AF60829D14365CE7744F3ADF895580338878CDF465ABCBF3F | |||
| 5896 | PDFNexus.exe | C:\Users\admin\AppData\LocalLow\Microsoft\CryptnetUrlCache\MetaData\DDE8B1B7E253A9758EC380BD648952AF_857450206B889F4FEA0F888FA03D68DB | binary | |
MD5:51938265154C159EB01917073A037451 | SHA256:0E1AA5D936A5E5B1BB6C074932E26CDD1A5594FAB0C572FB88804116790B61C7 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
3540 | svchost.exe | GET | 200 | 192.229.221.95:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBSAUQYBMq2awn1Rh6Doh%2FsBYgFV7gQUA95QNVbRTLtm8KPiGxvDl7I90VUCEAJ0LqoXyo4hxxe7H%2Fz9DKA%3D | US | binary | 471 b | whitelisted |
5896 | PDFNexus.exe | GET | 200 | 142.250.184.195:80 | http://c.pki.goog/r/r1.crl | US | binary | 854 b | whitelisted |
5896 | PDFNexus.exe | GET | 200 | 142.250.184.195:80 | http://c.pki.goog/r/r4.crl | US | binary | 436 b | whitelisted |
5896 | PDFNexus.exe | GET | 200 | 142.250.184.195:80 | http://c.pki.goog/r/gsr1.crl | US | binary | 1.70 Kb | whitelisted |
— | — | GET | 200 | 192.229.221.95:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBTrjrydRyt%2BApF3GSPypfHBxR5XtQQUs9tIpPmhxdiuNkHMEWNpYim8S8YCEAI5PUjXAkJafLQcAAsO18o%3D | US | binary | 313 b | whitelisted |
4536 | backgroundTaskHost.exe | GET | 200 | 192.229.221.95:80 | http://ocsp.digicert.com/MFEwTzBNMEswSTAJBgUrDgMCGgUABBQ50otx%2Fh0Ztl%2Bz8SiPI7wEWVxDlQQUTiJUIBiV5uNu5g%2F6%2BrkS7QYXjzkCEAn5bsKVVV8kdJ6vHl3O1J0%3D | US | binary | 471 b | whitelisted |
5896 | PDFNexus.exe | GET | 200 | 142.250.185.227:80 | http://o.pki.goog/wr2/MFEwTzBNMEswSTAJBgUrDgMCGgUABBRTQtSEi8EX%2BbYUTXd8%2ByMxD3s1zQQU3hse7XkV1D43JMMhu%2Bw0OW1CsjACEHViWUaptL4MEEkSmq4OScg%3D | US | binary | 471 b | whitelisted |
4392 | svchost.exe | GET | 200 | 23.48.23.166:80 | http://crl.microsoft.com/pki/crl/products/MicRooCerAut2011_2011_03_22.crl | DE | binary | 1.01 Kb | whitelisted |
4392 | svchost.exe | GET | 200 | 184.30.21.171:80 | http://www.microsoft.com/pkiops/crl/MicSecSerCA2011_2011-10-18.crl | DE | binary | 973 b | whitelisted |
5896 | PDFNexus.exe | GET | 200 | 142.250.185.227:80 | http://o.pki.goog/wr2/MFIwUDBOMEwwSjAJBgUrDgMCGgUABBRTQtSEi8EX%2BbYUTXd8%2ByMxD3s1zQQU3hse7XkV1D43JMMhu%2Bw0OW1CsjACEQC1wDSQwr%2F7UxDebtw0D9JJ | US | binary | 472 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
4 | System | 192.168.100.255:137 | — | — | — | whitelisted |
4392 | svchost.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | unknown |
3828 | RUXIMICS.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | unknown |
444 | MoUsoCoreWorker.exe | 40.127.240.158:443 | settings-win.data.microsoft.com | MICROSOFT-CORP-MSN-AS-BLOCK | IE | unknown |
4656 | SearchApp.exe | 104.126.37.136:443 | www.bing.com | Akamai International B.V. | DE | unknown |
— | — | 192.229.221.95:80 | ocsp.digicert.com | EDGECAST | US | whitelisted |
4032 | svchost.exe | 239.255.255.250:1900 | — | — | — | whitelisted |
4 | System | 192.168.100.255:138 | — | — | — | whitelisted |
5896 | PDFNexus.exe | 188.114.97.3:443 | pixel.pdfnexus.com | CLOUDFLARENET | NL | unknown |
5896 | PDFNexus.exe | 142.250.184.195:80 | c.pki.goog | GOOGLE | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
settings-win.data.microsoft.com |
| whitelisted |
google.com |
| whitelisted |
www.bing.com |
| whitelisted |
ocsp.digicert.com |
| whitelisted |
pixel.pdfnexus.com |
| unknown |
c.pki.goog |
| whitelisted |
fonts.googleapis.com |
| whitelisted |
o.pki.goog |
| whitelisted |
fonts.gstatic.com |
| whitelisted |
login.live.com |
| whitelisted |