File name:

0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe

Full analysis: https://app.any.run/tasks/6017cc25-b092-4485-a9ea-67774d177799
Verdict: Malicious activity
Threats:

DCrat, also known as Dark Crystal RAT, is a remote access trojan (RAT), which was first introduced in 2018. It is a modular malware that can be customized to perform different tasks. For instance, it can steal passwords, crypto wallet information, hijack Telegram and Steam accounts, and more. Attackers may use a variety of methods to distribute DCrat, but phishing email campaigns are the most common.

Analysis date: October 03, 2025, 16:19:27
OS: Windows 10 Professional (build: 19044, 64 bit)
Tags:
dcrat
rat
auto-sch
auto-reg
Indicators:
MIME: application/vnd.microsoft.portable-executable
File info: PE32 executable (GUI) Intel 80386, for MS Windows, 4 sections
MD5:

CEB8B85D3BA590BA3343BAE695D032C7

SHA1:

77602702BA29D9E6A514382E496EBA915DBDBE9E

SHA256:

0A0D0E3DB55D8C07AFD38656402556AD785B0EB0F7A182852E99C162326F227B

SSDEEP:

98304:RAfpsY3g+hna1iRRJx2gMSqqhV4btbwM+CQxxWhF7aq13xMT7aet1tE1l0i9P3wh:5+R

ANY.RUN is an interactive service which provides full access to the guest system. Information in this report could be distorted by user actions and is provided for user acknowledgement as it is. ANY.RUN does not guarantee maliciousness or safety of the content.
  • MALICIOUS

    • DCRAT mutex has been found

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • conhost.exe (PID: 9768)
      • conhost.exe (PID: 10864)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
      • conhost.exe (PID: 9516)
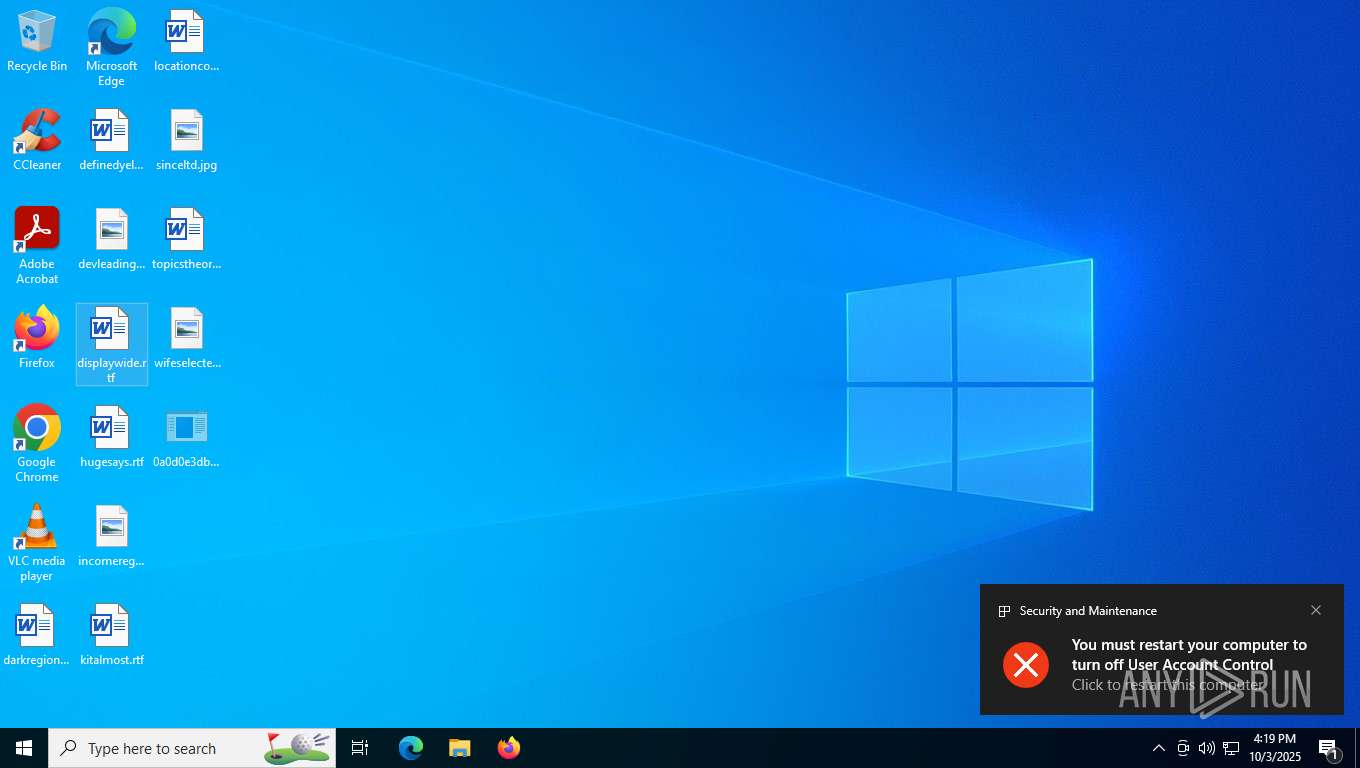
    • UAC/LUA settings modification

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • conhost.exe (PID: 9768)
      • conhost.exe (PID: 10864)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
      • conhost.exe (PID: 9516)
    • Changes the autorun value in the registry

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
    • Adds path to the Windows Defender exclusion list

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
    • Changes Windows Defender settings

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
    • Uses sleep, probably for evasion detection (SCRIPT)

      • wscript.exe (PID: 9080)
      • wscript.exe (PID: 10548)
      • wscript.exe (PID: 11236)
      • wscript.exe (PID: 8324)
      • wscript.exe (PID: 3240)
      • wscript.exe (PID: 10528)
      • wscript.exe (PID: 8512)
      • wscript.exe (PID: 9848)
      • wscript.exe (PID: 10804)
      • wscript.exe (PID: 8636)
      • wscript.exe (PID: 11108)
      • wscript.exe (PID: 7916)
      • wscript.exe (PID: 9656)
      • wscript.exe (PID: 10608)
      • wscript.exe (PID: 8492)
      • wscript.exe (PID: 8956)
      • wscript.exe (PID: 764)
      • wscript.exe (PID: 9836)
      • wscript.exe (PID: 10120)
      • wscript.exe (PID: 7568)
      • wscript.exe (PID: 8788)
      • wscript.exe (PID: 6320)
      • wscript.exe (PID: 1408)
      • wscript.exe (PID: 8916)
      • wscript.exe (PID: 10152)
      • wscript.exe (PID: 10764)
      • wscript.exe (PID: 1696)
      • wscript.exe (PID: 9308)
      • wscript.exe (PID: 9248)
      • wscript.exe (PID: 9156)
    • Deletes a file (SCRIPT)

      • wscript.exe (PID: 10548)
      • wscript.exe (PID: 8324)
      • wscript.exe (PID: 10528)
      • wscript.exe (PID: 8636)
      • wscript.exe (PID: 11108)
      • wscript.exe (PID: 10608)
      • wscript.exe (PID: 9848)
      • wscript.exe (PID: 8492)
      • wscript.exe (PID: 764)
      • wscript.exe (PID: 7568)
      • wscript.exe (PID: 6320)
      • wscript.exe (PID: 8916)
      • wscript.exe (PID: 10764)
      • wscript.exe (PID: 1696)
  • SUSPICIOUS

    • Reads security settings of Internet Explorer

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • conhost.exe (PID: 9768)
      • conhost.exe (PID: 10864)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
      • conhost.exe (PID: 9516)
    • Reads the date of Windows installation

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
    • Starts CMD.EXE for commands execution

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • conhost.exe (PID: 9768)
    • Executed via WMI

      • schtasks.exe (PID: 8344)
      • schtasks.exe (PID: 8368)
      • schtasks.exe (PID: 8424)
      • schtasks.exe (PID: 8480)
      • schtasks.exe (PID: 8464)
      • schtasks.exe (PID: 8444)
      • schtasks.exe (PID: 8512)
      • schtasks.exe (PID: 8580)
      • schtasks.exe (PID: 8620)
      • schtasks.exe (PID: 8640)
      • schtasks.exe (PID: 8676)
      • schtasks.exe (PID: 8320)
      • schtasks.exe (PID: 8784)
      • schtasks.exe (PID: 8816)
      • schtasks.exe (PID: 8404)
      • schtasks.exe (PID: 8884)
      • schtasks.exe (PID: 8912)
      • schtasks.exe (PID: 8948)
      • schtasks.exe (PID: 9032)
      • schtasks.exe (PID: 9008)
      • schtasks.exe (PID: 9052)
      • schtasks.exe (PID: 9072)
      • schtasks.exe (PID: 9092)
      • schtasks.exe (PID: 9112)
      • schtasks.exe (PID: 9144)
      • schtasks.exe (PID: 8712)
      • schtasks.exe (PID: 8744)
      • schtasks.exe (PID: 8536)
      • schtasks.exe (PID: 8836)
      • schtasks.exe (PID: 8088)
      • schtasks.exe (PID: 9196)
      • schtasks.exe (PID: 8340)
      • schtasks.exe (PID: 8376)
      • schtasks.exe (PID: 8348)
      • schtasks.exe (PID: 8408)
      • schtasks.exe (PID: 8500)
      • schtasks.exe (PID: 8576)
      • schtasks.exe (PID: 8492)
      • schtasks.exe (PID: 8584)
      • schtasks.exe (PID: 8632)
      • schtasks.exe (PID: 9176)
      • schtasks.exe (PID: 2172)
      • schtasks.exe (PID: 8732)
      • schtasks.exe (PID: 8844)
      • schtasks.exe (PID: 8820)
      • schtasks.exe (PID: 8812)
      • schtasks.exe (PID: 8620)
      • schtasks.exe (PID: 8756)
    • Executable content was dropped or overwritten

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • conhost.exe (PID: 10864)
    • The process creates files with name similar to system file names

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
    • Likely accesses (executes) a file from the Public directory

      • schtasks.exe (PID: 8676)
      • schtasks.exe (PID: 8712)
      • schtasks.exe (PID: 8744)
      • taskhostw.exe (PID: 9132)
      • taskhostw.exe (PID: 9156)
      • taskhostw.exe (PID: 10216)
    • Starts POWERSHELL.EXE for commands execution

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
    • Executing commands from a ".bat" file

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
    • Probably delay the execution using 'w32tm.exe'

      • w32tm.exe (PID: 11032)
      • cmd.exe (PID: 10992)
    • Script adds exclusion path to Windows Defender

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
    • The process executes VB scripts

      • conhost.exe (PID: 10864)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
      • conhost.exe (PID: 9516)
    • Creates FileSystem object to access computer's file system (SCRIPT)

      • wscript.exe (PID: 10548)
      • wscript.exe (PID: 9080)
      • wscript.exe (PID: 8324)
      • wscript.exe (PID: 11236)
      • wscript.exe (PID: 3240)
      • wscript.exe (PID: 10528)
      • wscript.exe (PID: 9848)
      • wscript.exe (PID: 8512)
      • wscript.exe (PID: 8636)
      • wscript.exe (PID: 10804)
      • wscript.exe (PID: 7916)
      • wscript.exe (PID: 11108)
      • wscript.exe (PID: 10608)
      • wscript.exe (PID: 9656)
      • wscript.exe (PID: 8492)
      • wscript.exe (PID: 764)
      • wscript.exe (PID: 9836)
      • wscript.exe (PID: 8956)
      • wscript.exe (PID: 7568)
      • wscript.exe (PID: 10120)
      • wscript.exe (PID: 8788)
      • wscript.exe (PID: 6320)
      • wscript.exe (PID: 8916)
      • wscript.exe (PID: 1408)
      • wscript.exe (PID: 10764)
      • wscript.exe (PID: 10152)
      • wscript.exe (PID: 1696)
      • wscript.exe (PID: 9308)
      • wscript.exe (PID: 9156)
      • wscript.exe (PID: 9248)
    • Uses WMI to retrieve WMI-managed resources (SCRIPT)

      • wscript.exe (PID: 10548)
      • wscript.exe (PID: 8324)
      • wscript.exe (PID: 10528)
      • wscript.exe (PID: 9848)
      • wscript.exe (PID: 8636)
      • wscript.exe (PID: 11108)
      • wscript.exe (PID: 10608)
      • wscript.exe (PID: 8492)
      • wscript.exe (PID: 764)
      • wscript.exe (PID: 7568)
      • wscript.exe (PID: 6320)
      • wscript.exe (PID: 8916)
      • wscript.exe (PID: 10764)
      • wscript.exe (PID: 1696)
      • wscript.exe (PID: 9156)
    • Executes WMI query (SCRIPT)

      • wscript.exe (PID: 10548)
      • wscript.exe (PID: 8324)
      • wscript.exe (PID: 10528)
      • wscript.exe (PID: 9848)
      • wscript.exe (PID: 8636)
      • wscript.exe (PID: 11108)
      • wscript.exe (PID: 10608)
      • wscript.exe (PID: 8492)
      • wscript.exe (PID: 764)
      • wscript.exe (PID: 7568)
      • wscript.exe (PID: 6320)
      • wscript.exe (PID: 8916)
      • wscript.exe (PID: 10764)
      • wscript.exe (PID: 1696)
      • wscript.exe (PID: 9156)
    • Gets full path of the running script (SCRIPT)

      • wscript.exe (PID: 10548)
      • wscript.exe (PID: 8324)
      • wscript.exe (PID: 10528)
      • wscript.exe (PID: 9848)
      • wscript.exe (PID: 8636)
      • wscript.exe (PID: 11108)
      • wscript.exe (PID: 10608)
      • wscript.exe (PID: 764)
      • wscript.exe (PID: 8492)
      • wscript.exe (PID: 7568)
      • wscript.exe (PID: 6320)
      • wscript.exe (PID: 8916)
      • wscript.exe (PID: 10764)
      • wscript.exe (PID: 1696)
    • Checks whether a specific file exists (SCRIPT)

      • wscript.exe (PID: 9080)
      • wscript.exe (PID: 11236)
      • wscript.exe (PID: 3240)
      • wscript.exe (PID: 8512)
      • wscript.exe (PID: 10804)
      • wscript.exe (PID: 7916)
      • wscript.exe (PID: 9656)
      • wscript.exe (PID: 8956)
      • wscript.exe (PID: 9836)
      • wscript.exe (PID: 10120)
      • wscript.exe (PID: 8788)
      • wscript.exe (PID: 1408)
      • wscript.exe (PID: 10152)
      • wscript.exe (PID: 9308)
      • wscript.exe (PID: 9248)
    • Runs shell command (SCRIPT)

      • wscript.exe (PID: 10548)
      • wscript.exe (PID: 8324)
      • wscript.exe (PID: 10528)
      • wscript.exe (PID: 9848)
      • wscript.exe (PID: 8636)
      • wscript.exe (PID: 11108)
      • wscript.exe (PID: 10608)
      • wscript.exe (PID: 8492)
      • wscript.exe (PID: 764)
      • wscript.exe (PID: 7568)
      • wscript.exe (PID: 6320)
      • wscript.exe (PID: 8916)
      • wscript.exe (PID: 10764)
      • wscript.exe (PID: 1696)
  • INFO

    • Reads Environment values

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
    • The sample compiled with english language support

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • conhost.exe (PID: 10864)
    • Reads the computer name

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • taskhostw.exe (PID: 9132)
      • StartMenuExperienceHost.exe (PID: 9056)
      • taskhostw.exe (PID: 9156)
      • conhost.exe (PID: 9196)
      • conhost.exe (PID: 8672)
      • sihost.exe (PID: 8464)
      • conhost.exe (PID: 8764)
      • conhost.exe (PID: 8356)
      • smss.exe (PID: 8332)
      • sihost.exe (PID: 8748)
      • MusNotificationUx.exe (PID: 8812)
      • firefox.exe (PID: 6836)
      • fontdrvhost.exe (PID: 6456)
      • dwm.exe (PID: 6916)
      • dwm.exe (PID: 9012)
      • sihost.exe (PID: 9320)
      • fontdrvhost.exe (PID: 9420)
      • conhost.exe (PID: 9500)
      • StartMenuExperienceHost.exe (PID: 9752)
      • conhost.exe (PID: 9808)
      • MusNotificationUx.exe (PID: 9968)
      • smss.exe (PID: 10108)
      • WmiPrvSE.exe (PID: 8960)
      • firefox.exe (PID: 9640)
      • taskhostw.exe (PID: 10216)
      • WmiPrvSE.exe (PID: 10040)
      • conhost.exe (PID: 10336)
      • conhost.exe (PID: 9768)
      • conhost.exe (PID: 10864)
      • StartMenuExperienceHost.exe (PID: 8484)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
      • conhost.exe (PID: 9516)
    • Checks supported languages

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • WmiPrvSE.exe (PID: 8960)
      • taskhostw.exe (PID: 9132)
      • StartMenuExperienceHost.exe (PID: 9056)
      • taskhostw.exe (PID: 9156)
      • conhost.exe (PID: 9196)
      • smss.exe (PID: 8332)
      • conhost.exe (PID: 8672)
      • conhost.exe (PID: 8764)
      • sihost.exe (PID: 8464)
      • conhost.exe (PID: 8356)
      • sihost.exe (PID: 8748)
      • MusNotificationUx.exe (PID: 8812)
      • fontdrvhost.exe (PID: 6456)
      • dwm.exe (PID: 6916)
      • firefox.exe (PID: 6836)
      • dwm.exe (PID: 9012)
      • conhost.exe (PID: 9500)
      • sihost.exe (PID: 9320)
      • fontdrvhost.exe (PID: 9420)
      • firefox.exe (PID: 9640)
      • StartMenuExperienceHost.exe (PID: 9752)
      • conhost.exe (PID: 9808)
      • MusNotificationUx.exe (PID: 9968)
      • smss.exe (PID: 10108)
      • WmiPrvSE.exe (PID: 10040)
      • conhost.exe (PID: 10336)
      • taskhostw.exe (PID: 10216)
      • conhost.exe (PID: 9768)
      • StartMenuExperienceHost.exe (PID: 8484)
      • conhost.exe (PID: 10864)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
      • conhost.exe (PID: 9516)
    • Reads the machine GUID from the registry

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • StartMenuExperienceHost.exe (PID: 9056)
      • taskhostw.exe (PID: 9132)
      • WmiPrvSE.exe (PID: 8960)
      • taskhostw.exe (PID: 9156)
      • conhost.exe (PID: 9196)
      • sihost.exe (PID: 8464)
      • conhost.exe (PID: 8764)
      • conhost.exe (PID: 8356)
      • smss.exe (PID: 8332)
      • sihost.exe (PID: 8748)
      • firefox.exe (PID: 6836)
      • MusNotificationUx.exe (PID: 8812)
      • conhost.exe (PID: 8672)
      • sihost.exe (PID: 9320)
      • dwm.exe (PID: 9012)
      • fontdrvhost.exe (PID: 9420)
      • conhost.exe (PID: 9500)
      • fontdrvhost.exe (PID: 6456)
      • dwm.exe (PID: 6916)
      • firefox.exe (PID: 9640)
      • StartMenuExperienceHost.exe (PID: 9752)
      • conhost.exe (PID: 9808)
      • MusNotificationUx.exe (PID: 9968)
      • taskhostw.exe (PID: 10216)
      • WmiPrvSE.exe (PID: 10040)
      • smss.exe (PID: 10108)
      • conhost.exe (PID: 10336)
      • conhost.exe (PID: 9768)
      • conhost.exe (PID: 10864)
      • StartMenuExperienceHost.exe (PID: 8484)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
      • conhost.exe (PID: 9516)
    • Process checks computer location settings

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • conhost.exe (PID: 9768)
      • conhost.exe (PID: 10864)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
      • conhost.exe (PID: 9516)
    • Process checks whether UAC notifications are on

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 6384)
      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • conhost.exe (PID: 9768)
      • conhost.exe (PID: 10864)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
      • conhost.exe (PID: 9516)
    • Creates files in the program directory

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
    • Launching a file from a Registry key

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
    • Creates files or folders in the user directory

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • BackgroundTransferHost.exe (PID: 10728)
    • Manual execution by a user

      • WmiPrvSE.exe (PID: 8960)
      • taskhostw.exe (PID: 9132)
      • StartMenuExperienceHost.exe (PID: 9056)
      • conhost.exe (PID: 9196)
      • smss.exe (PID: 8332)
      • taskhostw.exe (PID: 9156)
      • conhost.exe (PID: 8672)
      • conhost.exe (PID: 8764)
      • sihost.exe (PID: 8748)
      • sihost.exe (PID: 8464)
      • conhost.exe (PID: 8356)
      • MusNotificationUx.exe (PID: 8812)
      • dwm.exe (PID: 6916)
      • firefox.exe (PID: 6836)
      • fontdrvhost.exe (PID: 6456)
      • dwm.exe (PID: 9012)
      • sihost.exe (PID: 9320)
      • fontdrvhost.exe (PID: 9420)
      • conhost.exe (PID: 9500)
      • firefox.exe (PID: 9640)
      • conhost.exe (PID: 9808)
      • MusNotificationUx.exe (PID: 9968)
      • smss.exe (PID: 10108)
      • taskhostw.exe (PID: 10216)
      • StartMenuExperienceHost.exe (PID: 9752)
      • conhost.exe (PID: 10336)
      • WmiPrvSE.exe (PID: 10040)
      • conhost.exe (PID: 9768)
    • Reads security settings of Internet Explorer

      • BackgroundTransferHost.exe (PID: 10484)
      • BackgroundTransferHost.exe (PID: 10728)
      • BackgroundTransferHost.exe (PID: 9876)
      • BackgroundTransferHost.exe (PID: 9356)
    • Checks proxy server information

      • BackgroundTransferHost.exe (PID: 10728)
      • conhost.exe (PID: 10864)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • slui.exe (PID: 10032)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
    • Reads the software policy settings

      • BackgroundTransferHost.exe (PID: 10728)
      • slui.exe (PID: 10032)
    • Create files in a temporary directory

      • 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe (PID: 7116)
      • conhost.exe (PID: 10864)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
      • conhost.exe (PID: 9516)
    • Checks if a key exists in the options dictionary (POWERSHELL)

      • powershell.exe (PID: 10644)
      • powershell.exe (PID: 10628)
      • powershell.exe (PID: 8416)
      • powershell.exe (PID: 9016)
      • powershell.exe (PID: 2944)
      • powershell.exe (PID: 9136)
      • powershell.exe (PID: 8108)
      • powershell.exe (PID: 9108)
      • powershell.exe (PID: 10496)
      • powershell.exe (PID: 9132)
      • powershell.exe (PID: 9068)
      • powershell.exe (PID: 10708)
      • powershell.exe (PID: 10616)
    • Script raised an exception (POWERSHELL)

      • powershell.exe (PID: 10628)
      • powershell.exe (PID: 9108)
      • powershell.exe (PID: 10644)
      • powershell.exe (PID: 9136)
      • powershell.exe (PID: 10616)
      • powershell.exe (PID: 8416)
      • powershell.exe (PID: 2944)
      • powershell.exe (PID: 8108)
      • powershell.exe (PID: 9068)
      • powershell.exe (PID: 9132)
      • powershell.exe (PID: 10496)
      • powershell.exe (PID: 10708)
      • powershell.exe (PID: 9016)
    • Disables trace logs

      • conhost.exe (PID: 10864)
      • conhost.exe (PID: 8216)
      • conhost.exe (PID: 9084)
      • conhost.exe (PID: 10588)
      • conhost.exe (PID: 8736)
      • conhost.exe (PID: 9620)
      • conhost.exe (PID: 9052)
      • conhost.exe (PID: 8376)
      • conhost.exe (PID: 2364)
      • conhost.exe (PID: 8620)
      • conhost.exe (PID: 8524)
      • conhost.exe (PID: 5372)
      • conhost.exe (PID: 10260)
      • conhost.exe (PID: 5692)
Find more information about signature artifacts and mapping to MITRE ATT&CK™ MATRIX at the full report
No Malware configuration.

TRiD

.exe | Win32 Executable MS Visual C++ (generic) (42.2)
.exe | Win64 Executable (generic) (37.3)
.dll | Win32 Dynamic Link Library (generic) (8.8)
.exe | Win32 Executable (generic) (6)
.exe | Generic Win/DOS Executable (2.7)

EXIF

EXE

MachineType: Intel 386 or later, and compatibles
TimeStamp: 2012:07:13 22:47:16+00:00
ImageFileCharacteristics: No relocs, Executable, Large address aware, 32-bit
PEType: PE32
LinkerVersion: 9
CodeSize: 104448
InitializedDataSize: 1668096
UninitializedDataSize: -
EntryPoint: 0xcd2f
OSVersion: 5
ImageVersion: -
SubsystemVersion: 5
Subsystem: Windows GUI
FileVersionNumber: 5.15.2.0
ProductVersionNumber: 5.15.2.0
FileFlagsMask: 0x003f
FileFlags: (none)
FileOS: Win32
ObjectFileType: Dynamic link library
FileSubtype: -
LanguageCode: English (U.S.)
CharacterSet: Unicode
FileVersion: 5.15.2.0
OriginalFileName: libGLESv2.dll
ProductName: libGLESv2
ProductVersion: 5.15.2.0
No data.
screenshotscreenshotscreenshot
All screenshots are available in the full report
Total processes
338
Monitored processes
164
Malicious processes
54
Suspicious processes
0

Behavior graph

Click at the process to see the details

Process information

PID
CMD
Path
Indicators
Parent process
764"C:\WINDOWS\System32\WScript.exe" "C:\Users\admin\AppData\Local\Temp\78dbc494-2fa4-4623-b5a4-4ab7eef682bd.vbs" C:\Windows\SysWOW64\wscript.execonhost.exe
User:
admin
Company:
Microsoft Corporation
Integrity Level:
HIGH
Description:
Microsoft ® Windows Based Script Host
Exit code:
0
Version:
5.812.10240.16384
Modules
Images
c:\windows\syswow64\wscript.exe
c:\windows\system32\ntdll.dll
c:\windows\syswow64\ntdll.dll
c:\windows\system32\wow64.dll
c:\windows\system32\wow64win.dll
c:\windows\system32\wow64cpu.dll
c:\windows\syswow64\kernel32.dll
c:\windows\syswow64\kernelbase.dll
c:\windows\syswow64\msvcrt.dll
c:\windows\syswow64\oleaut32.dll
1408"C:\WINDOWS\System32\WScript.exe" "C:\Users\admin\AppData\Local\Temp\f05bd79f-3d8e-48ae-aadd-7774f317353a.vbs" C:\Windows\SysWOW64\wscript.execonhost.exe
User:
admin
Company:
Microsoft Corporation
Integrity Level:
HIGH
Description:
Microsoft ® Windows Based Script Host
Version:
5.812.10240.16384
Modules
Images
c:\windows\syswow64\wscript.exe
c:\windows\system32\ntdll.dll
c:\windows\syswow64\ntdll.dll
c:\windows\system32\wow64.dll
c:\windows\system32\wow64win.dll
c:\windows\system32\wow64cpu.dll
c:\windows\syswow64\kernel32.dll
c:\windows\syswow64\kernelbase.dll
c:\windows\syswow64\msvcrt.dll
c:\windows\syswow64\oleaut32.dll
1696"C:\WINDOWS\System32\WScript.exe" "C:\Users\admin\AppData\Local\Temp\eb76febf-42e0-42c5-ad0c-b26b432363c5.vbs" C:\Windows\SysWOW64\wscript.execonhost.exe
User:
admin
Company:
Microsoft Corporation
Integrity Level:
HIGH
Description:
Microsoft ® Windows Based Script Host
Exit code:
0
Version:
5.812.10240.16384
Modules
Images
c:\windows\syswow64\wscript.exe
c:\windows\system32\ntdll.dll
c:\windows\syswow64\ntdll.dll
c:\windows\system32\wow64.dll
c:\windows\system32\wow64win.dll
c:\windows\system32\wow64cpu.dll
c:\windows\syswow64\kernel32.dll
c:\windows\syswow64\kernelbase.dll
c:\windows\syswow64\msvcrt.dll
c:\windows\syswow64\oleaut32.dll
1852w32tm /stripchart /computer:localhost /period:5 /dataonly /samples:2 C:\Windows\System32\w32tm.exew32tm.exe
User:
admin
Company:
Microsoft Corporation
Integrity Level:
HIGH
Description:
Windows Time Service Diagnostic Tool
Exit code:
0
Version:
10.0.19041.1 (WinBuild.160101.0800)
Modules
Images
c:\windows\system32\w32tm.exe
c:\windows\system32\ntdll.dll
c:\windows\system32\kernel32.dll
c:\windows\system32\kernelbase.dll
c:\windows\system32\ucrtbase.dll
c:\windows\system32\sechost.dll
c:\windows\system32\rpcrt4.dll
c:\windows\system32\bcrypt.dll
c:\windows\system32\ws2_32.dll
c:\windows\system32\advapi32.dll
2128"C:\WINDOWS\SystemApps\ShellExperienceHost_cw5n1h2txyewy\ShellExperienceHost.exe" -ServerName:App.AppXtk181tbxbce2qsex02s8tw7hfxa9xb3t.mcaC:\Windows\SystemApps\ShellExperienceHost_cw5n1h2txyewy\ShellExperienceHost.exesvchost.exe
User:
admin
Company:
Microsoft Corporation
Integrity Level:
MEDIUM
Description:
Windows Shell Experience Host
Version:
10.0.19041.3758 (WinBuild.160101.0800)
Modules
Images
c:\windows\systemapps\shellexperiencehost_cw5n1h2txyewy\shellexperiencehost.exe
c:\windows\system32\ntdll.dll
c:\windows\system32\kernel32.dll
c:\windows\system32\kernelbase.dll
c:\windows\system32\combase.dll
c:\windows\system32\ucrtbase.dll
c:\windows\system32\rpcrt4.dll
c:\windows\system32\oleaut32.dll
c:\windows\system32\msvcp_win.dll
c:\windows\system32\wincorlib.dll
2172schtasks.exe /create /tn "fontdrvhostf" /sc MINUTE /mo 7 /tr "'C:\Windows\ShellComponents\fontdrvhost.exe'" /fC:\Windows\System32\schtasks.exeWmiPrvSE.exe
User:
admin
Company:
Microsoft Corporation
Integrity Level:
HIGH
Description:
Task Scheduler Configuration Tool
Exit code:
0
Version:
10.0.19041.1 (WinBuild.160101.0800)
Modules
Images
c:\windows\system32\schtasks.exe
c:\windows\system32\ntdll.dll
c:\windows\system32\kernel32.dll
c:\windows\system32\kernelbase.dll
c:\windows\system32\msvcrt.dll
c:\windows\system32\oleaut32.dll
c:\windows\system32\msvcp_win.dll
c:\windows\system32\ucrtbase.dll
c:\windows\system32\combase.dll
c:\windows\system32\rpcrt4.dll
2364"C:\Program Files (x86)\Windows Multimedia Platform\conhost.exe"C:\Program Files (x86)\Windows Multimedia Platform\conhost.exe
wscript.exe
User:
admin
Integrity Level:
HIGH
Exit code:
0
Version:
5.15.2.0
Modules
Images
c:\program files (x86)\windows multimedia platform\conhost.exe
c:\windows\system32\ntdll.dll
c:\windows\syswow64\ntdll.dll
c:\windows\system32\wow64.dll
c:\windows\system32\wow64win.dll
c:\windows\system32\wow64cpu.dll
c:\windows\syswow64\kernel32.dll
c:\windows\syswow64\kernelbase.dll
c:\windows\syswow64\ole32.dll
c:\windows\syswow64\ucrtbase.dll
2944"powershell" -Command Add-MpPreference -ExclusionPath 'C:/Users/'C:\Windows\SysWOW64\WindowsPowerShell\v1.0\powershell.exe0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe
User:
admin
Company:
Microsoft Corporation
Integrity Level:
HIGH
Description:
Windows PowerShell
Exit code:
1
Version:
10.0.19041.1 (WinBuild.160101.0800)
Modules
Images
c:\windows\syswow64\windowspowershell\v1.0\powershell.exe
c:\windows\system32\ntdll.dll
c:\windows\syswow64\ntdll.dll
c:\windows\system32\wow64.dll
c:\windows\system32\wow64win.dll
c:\windows\system32\wow64cpu.dll
c:\windows\syswow64\kernel32.dll
c:\windows\syswow64\kernelbase.dll
c:\windows\syswow64\apphelp.dll
c:\windows\syswow64\msvcrt.dll
3240"C:\WINDOWS\System32\WScript.exe" "C:\Users\admin\AppData\Local\Temp\61e709be-d7c8-46f5-9fa4-8e74e09005ae.vbs" C:\Windows\SysWOW64\wscript.execonhost.exe
User:
admin
Company:
Microsoft Corporation
Integrity Level:
HIGH
Description:
Microsoft ® Windows Based Script Host
Version:
5.812.10240.16384
Modules
Images
c:\windows\syswow64\wscript.exe
c:\windows\system32\ntdll.dll
c:\windows\syswow64\ntdll.dll
c:\windows\system32\wow64.dll
c:\windows\system32\wow64win.dll
c:\windows\system32\wow64cpu.dll
c:\windows\syswow64\kernel32.dll
c:\windows\syswow64\kernelbase.dll
c:\windows\syswow64\msvcrt.dll
c:\windows\syswow64\oleaut32.dll
5292"C:\WINDOWS\SysWOW64\cmd.exe" /c "C:\Users\admin\Desktop\0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe"C:\Windows\SysWOW64\cmd.exe
0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exe
User:
admin
Company:
Microsoft Corporation
Integrity Level:
HIGH
Description:
Windows Command Processor
Exit code:
0
Version:
10.0.19041.3636 (WinBuild.160101.0800)
Modules
Images
c:\windows\syswow64\cmd.exe
c:\windows\system32\ntdll.dll
c:\windows\syswow64\ntdll.dll
c:\windows\system32\wow64.dll
c:\windows\system32\wow64win.dll
c:\windows\system32\wow64cpu.dll
c:\windows\syswow64\kernel32.dll
c:\windows\syswow64\kernelbase.dll
c:\windows\syswow64\apphelp.dll
c:\windows\syswow64\msvcrt.dll
Total events
112 232
Read events
112 065
Write events
167
Delete events
0

Modification events

(PID) Process:(6384) 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeKey:HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System
Operation:writeName:EnableLUA
Value:
0
(PID) Process:(6384) 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeKey:HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap
Operation:writeName:ProxyBypass
Value:
1
(PID) Process:(6384) 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeKey:HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap
Operation:writeName:IntranetName
Value:
1
(PID) Process:(6384) 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeKey:HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap
Operation:writeName:UNCAsIntranet
Value:
1
(PID) Process:(6384) 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeKey:HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap
Operation:writeName:AutoDetect
Value:
0
(PID) Process:(7116) 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeKey:HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System
Operation:writeName:EnableLUA
Value:
0
(PID) Process:(7116) 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeKey:HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System
Operation:writeName:ConsentPromptBehaviorAdmin
Value:
0
(PID) Process:(7116) 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeKey:HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System
Operation:writeName:PromptOnSecureDesktop
Value:
0
(PID) Process:(7116) 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeKey:HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Action Center\Checks\{C8E6F269-B90A-4053-A3BE-499AFCEC98C4}.check.0
Operation:writeName:CheckSetting
Value:
23004100430042006C006F00620000000000000000000000010000000000000000000000
(PID) Process:(7116) 0a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeKey:HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run
Operation:writeName:smss
Value:
"C:\Program Files\Uninstall Information\smss.exe"
Executable files
58
Suspicious files
4
Text files
100
Unknown types
0

Dropped files

PID
Process
Filename
Type
71160a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeC:\Program Files\PowerShell\7\24dbde2999530etext
MD5:1BFC6A2D714E710A4AEF2D9162E7F0F2
SHA256:BD771D0003A367C83F58952F81A1BD741F96515ED6E306C64759260BE06F8AE0
71160a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeC:\Program Files\Uninstall Information\smss.exeexecutable
MD5:CEB8B85D3BA590BA3343BAE695D032C7
SHA256:0A0D0E3DB55D8C07AFD38656402556AD785B0EB0F7A182852E99C162326F227B
71160a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeC:\Program Files\PowerShell\7\WmiPrvSE.exeexecutable
MD5:CEB8B85D3BA590BA3343BAE695D032C7
SHA256:0A0D0E3DB55D8C07AFD38656402556AD785B0EB0F7A182852E99C162326F227B
71160a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeC:\Users\Public\Music\taskhostw.exeexecutable
MD5:CEB8B85D3BA590BA3343BAE695D032C7
SHA256:0A0D0E3DB55D8C07AFD38656402556AD785B0EB0F7A182852E99C162326F227B
71160a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeC:\Windows\Logs\NetSetup\conhost.exeexecutable
MD5:CEB8B85D3BA590BA3343BAE695D032C7
SHA256:0A0D0E3DB55D8C07AFD38656402556AD785B0EB0F7A182852E99C162326F227B
71160a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeC:\Windows\GameBarPresenceWriter\e13f7f13fb6ab6text
MD5:9AA48AD177FA3505737B72A18E672092
SHA256:F6778D87D39F4FB39926EA744C4D757038D6AA0E4AF44E8D628953A5F7CF9A57
71160a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeC:\Program Files\Uninstall Information\69ddcba757bf72text
MD5:788BD620A53234AC0BD69423E16CEB60
SHA256:E22103147B4DCC24E35EDFD3EC3A8653B236ABCA44D41F70584B7BF79CA06146
71160a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeC:\Windows\GameBarPresenceWriter\MusNotificationUx.exeexecutable
MD5:CEB8B85D3BA590BA3343BAE695D032C7
SHA256:0A0D0E3DB55D8C07AFD38656402556AD785B0EB0F7A182852E99C162326F227B
71160a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeC:\Recovery\Logs\088424020bedd6text
MD5:147D337B9409BD026AEAA481DD6829CA
SHA256:4ADD1BE5541D52C867048D2E023F762D44095326D37AC061C229499CF3BACB12
71160a0d0e3db55d8c07afd38656402556ad785b0eb0f7a182852e99c162326f227b.exeC:\Windows\Logs\NetSetup\088424020bedd6text
MD5:4ABF3A720C79795EE5EF21CC44CAF7F4
SHA256:9B90B3D035868519979BED45BAA85B630D947D01C9CB4BED671318233A80E958
Download PCAP, analyze network streams, HTTP content and a lot more at the full report
HTTP(S) requests
29
TCP/UDP connections
47
DNS requests
28
Threats
0

HTTP requests

PID
Process
Method
HTTP Code
IP
URL
CN
Type
Size
Reputation
POST
200
20.190.159.68:443
https://login.live.com/RST2.srf
US
xml
11.1 Kb
unknown
GET
200
2.18.29.185:443
https://www.bing.com/th?id=ODSWG.8229b0e5-fa8c-4e4a-af74-69717698b903&pid=dsb
unknown
4.62 Kb
unknown
POST
200
40.126.31.128:443
https://login.live.com/RST2.srf
US
xml
11.0 Kb
unknown
POST
200
20.190.159.73:443
https://login.live.com/RST2.srf
US
unknown
POST
204
2.18.29.131:443
https://www.bing.com/web/xlsc.aspx?t=5&dl=1&wsbc=1
unknown
unknown
GET
304
20.165.94.63:443
https://slscr.update.microsoft.com/SLS/%7B522D76A4-93E1-47F8-B8CE-07C937AD1A1E%7D/x64/10.0.19045.4046/0?CH=686&L=en-US&P=&PT=0x30&WUA=10.0.19041.3996&MK=DELL&MD=DELL
US
unknown
GET
200
2.18.29.176:443
https://www.bing.com/th?id=OADD2.1361195395705932_16F6RJMMW3GNBDO&pid=21.2&c=16&roil=0&roit=0&roir=1&roib=1&w=48&h=48&dynsize=1&qlt=90
unknown
image
921 b
unknown
POST
200
40.126.31.1:443
https://login.live.com/RST2.srf
US
xml
11.2 Kb
unknown
GET
200
20.242.39.171:443
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
US
unknown
GET
200
2.18.29.232:443
https://www.bing.com/DSB/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=US&setlang=en-us&clientDateTime=10%2F3%2F2025%2C%204%3A19%3A42%20PM
unknown
binary
59.0 Kb
unknown
Download PCAP, analyze network streams, HTTP content and a lot more at the full report

Connections

PID
Process
IP
Domain
ASN
CN
Reputation
6168
RUXIMICS.exe
4.231.128.59:443
settings-win.data.microsoft.com
MICROSOFT-CORP-MSN-AS-BLOCK
IE
whitelisted
4
System
192.168.100.255:137
whitelisted
6016
MoUsoCoreWorker.exe
4.231.128.59:443
settings-win.data.microsoft.com
MICROSOFT-CORP-MSN-AS-BLOCK
IE
whitelisted
2.18.29.147:443
www.bing.com
Akamai International B.V.
PL
whitelisted
4
System
192.168.100.255:138
whitelisted
6016
MoUsoCoreWorker.exe
51.104.136.2:443
settings-win.data.microsoft.com
MICROSOFT-CORP-MSN-AS-BLOCK
IE
whitelisted
5948
svchost.exe
51.104.136.2:443
settings-win.data.microsoft.com
MICROSOFT-CORP-MSN-AS-BLOCK
IE
whitelisted
5224
SearchApp.exe
2.18.29.224:443
www.bing.com
Akamai International B.V.
PL
whitelisted
5480
svchost.exe
20.190.159.71:443
login.live.com
MICROSOFT-CORP-MSN-AS-BLOCK
IE
whitelisted
3464
svchost.exe
172.211.123.250:443
client.wns.windows.com
MICROSOFT-CORP-MSN-AS-BLOCK
FR
whitelisted

DNS requests

Domain
IP
Reputation
settings-win.data.microsoft.com
  • 4.231.128.59
  • 51.104.136.2
whitelisted
www.bing.com
  • 2.18.29.147
  • 2.18.29.224
  • 2.18.29.185
  • 2.18.29.179
  • 2.18.29.192
  • 2.18.29.218
  • 2.18.29.170
  • 2.18.29.200
  • 2.18.29.201
  • 2.18.29.131
  • 2.18.29.210
  • 2.18.29.176
  • 2.18.29.145
  • 2.18.29.232
whitelisted
google.com
  • 172.217.23.110
whitelisted
login.live.com
  • 20.190.159.71
  • 40.126.31.67
  • 20.190.159.64
  • 20.190.159.73
  • 40.126.31.131
  • 40.126.31.1
  • 40.126.31.128
  • 20.190.159.68
whitelisted
client.wns.windows.com
  • 172.211.123.250
whitelisted
arc.msn.com
  • 20.223.35.26
whitelisted
slscr.update.microsoft.com
  • 135.232.92.137
whitelisted
www.microsoft.com
  • 72.247.166.29
whitelisted
fe3cr.delivery.mp.microsoft.com
  • 20.242.39.171
whitelisted
fd.api.iris.microsoft.com
  • 20.223.36.55
whitelisted

Threats

No threats detected
No debug info