ANY.RUN Interactive Sandbox
- Full browser-level visibility into phishing
- Huge database of samples and IOCs
- Interactivity in a safe environment
- Actionable Tier 1 reports
Get full visibility into malware and phishing behavior in a safe environment.
| File name: | duanj.me.apk |
| Full analysis: | https://app.any.run/tasks/6b43efc3-83cd-4c76-a199-4347a2d752a2 |
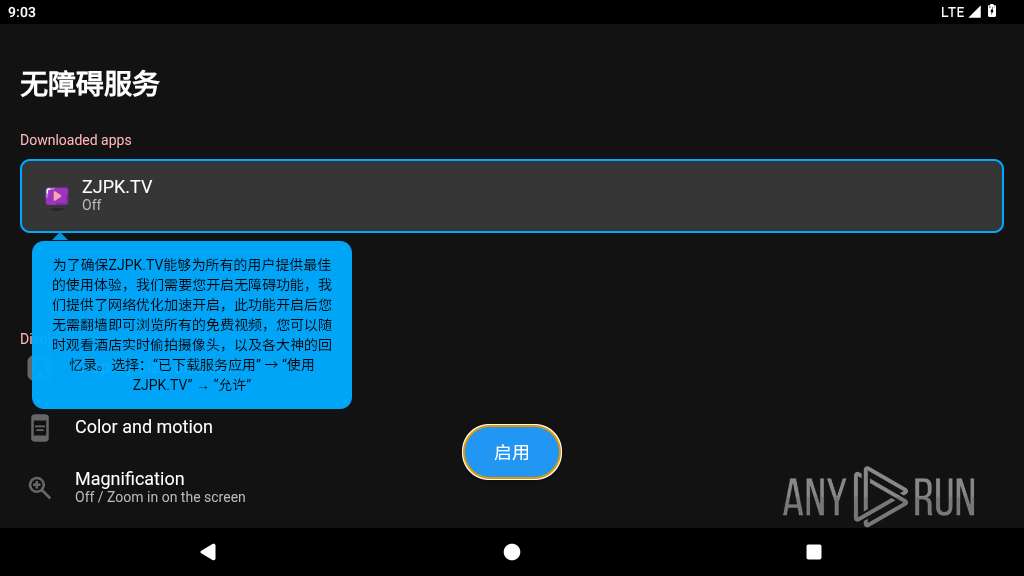
| Verdict: | Malicious activity |
| Threats: | BTMOB RAT is a remote access Trojan (RAT) designed to give attackers full control over infected devices. It targets Windows and Android endpoints. Its modular structure allows operators to tailor capabilities, making it suitable for espionage, credential theft, financial fraud, and establishing long-term footholds in corporate networks. |
| Analysis date: | March 15, 2026, 09:02:46 |
| OS: | Android 14 |
| Tags: | |
| Indicators: | |
| MIME: | application/vnd.android.package-archive |
| File info: | Android package (APK), with classes.dex |
| MD5: | 54D37F09251CBE283F42F64964083CA8 |
| SHA1: | 5C9D9649B439B86CF18987865B32DAB228ACE037 |
| SHA256: | 0628AD6D1FD836B13B22E75FA169502D8CE78B7AD20F0261EB5151DA98437BCA |
| SSDEEP: | 196608:VWaYCrD42MmgEeKcn6RhqRDovK3iTdUetUQ0DmFWZQ5uI+XpfufDoK:VW1CrDWmgOcn6fq5ordUJQnnAIkKEK |
| .apk | | | Android Package (54.1) |
|---|---|---|
| .jar | | | Java Archive (14.9) |
| .zan | | | BlueEyes Animation (13.9) |
| .vym | | | VYM Mind Map (12.8) |
| .zip | | | ZIP compressed archive (4.1) |
| ZipRequiredVersion: | 20 |
|---|---|
| ZipBitFlag: | 0xff49 |
| ZipCompression: | Deflated |
| ZipModifyDate: | 2026:01:17 04:35:34 |
| ZipCRC: | 0x83c67003 |
| ZipCompressedSize: | 585568 |
| ZipUncompressedSize: | 1355036 |
| ZipFileName: | classes.dex |
PID | CMD | Path | Indicators | Parent process |
|---|---|---|---|---|
| 2869 | updater.attester.responder | /system/bin/app_process64 | app_process64 | |
User: root Integrity Level: UNKNOWN Exit code: 0 | ||||
| 2903 | com.android.webview:webview_service | /system/bin/app_process32 | app_process32 | |
User: root Integrity Level: UNKNOWN Exit code: 0 | ||||
| 2905 | webview_zygote | /system/bin/app_process32 | — | app_process32 |
User: webview_zygote Integrity Level: UNKNOWN Exit code: 0 | ||||
| 2954 | com.android.webview:webview_apk | /system/bin/app_process32 | app_process32 | |
User: root Integrity Level: UNKNOWN Exit code: 0 | ||||
| 3071 | com.android.systemui.accessibility.accessibilitymenu | /system/bin/app_process64 | — | app_process64 |
User: root Integrity Level: UNKNOWN Exit code: 0 | ||||
PID | Process | Filename | Type | |
|---|---|---|---|---|
| 2869 | app_process64 | /data/data/updater.attester.responder/no_backup/androidx.work.workdb-wal | binary | |
MD5:95FEC4FB1F09D945641A887D629FAF65 | SHA256:A10CB76F869C48E79528740DCDB3B6696C3B55626ABA9A8D1231281A99F879CE | |||
| 2869 | app_process64 | /data/data/updater.attester.responder/app_webview/Default/Web Data-journal | binary | |
MD5:F88FA9349976CB6883E4738765A48319 | SHA256:1556BAA77EFB42A733B854BE4238181FB9420D42D41EE3508FE6D113437973F9 | |||
| 2869 | app_process64 | /data/data/updater.attester.responder/no_backup/androidx.work.workdb-journal | binary | |
MD5:681B28978150C71300222FF38E747D1B | SHA256:292BA5A19B27C1683991BD228DAB327086D90FB16BF675F3C90B53AF38D0829E | |||
| 2869 | app_process64 | /data/data/updater.attester.responder/shared_prefs/WebViewChromiumPrefs.xml | xml | |
MD5:9786BAD84CB7664E3E53A8801A55A8B8 | SHA256:3B9D18D5CC3AF6C0CB3E903327AE3DA35634C7C3A0B11413B9A3B1C10C640D5E | |||
| 2869 | app_process64 | /data/data/updater.attester.responder/shared_prefs/updater.attester.responder.xml | xml | |
MD5:5B532A98ECCD8DF3FC305EF244DAD8F2 | SHA256:5732203E66AB70DF46861067846E155BBB8E78A63E5AF21D02EF06D9E6E826BA | |||
| 2869 | app_process64 | /data/data/updater.attester.responder/app_webview/Default/Shared Dictionary/cache/index | binary | |
MD5:54CB446F628B2EA4A5BCE5769910512E | SHA256:FBCFE23A2ECB82B7100C50811691DDE0A33AA3DA8D176BE9882A9DB485DC0F2D | |||
| 2869 | app_process64 | /data/data/updater.attester.responder/app_webview/last-exit-info | text | |
MD5:83A458C0ACF750D886AEE9CA943EA840 | SHA256:1D8B22A079092FAB5DBFFE1431C4E1ABD1AE05D83528C827B4209018876E975C | |||
| 2869 | app_process64 | /data/data/updater.attester.responder/cache/WebView/Default/HTTP Cache/Code Cache/js/index | binary | |
MD5:54CB446F628B2EA4A5BCE5769910512E | SHA256:FBCFE23A2ECB82B7100C50811691DDE0A33AA3DA8D176BE9882A9DB485DC0F2D | |||
| 2869 | app_process64 | /data/data/updater.attester.responder/cache/WebView/Default/HTTP Cache/Code Cache/wasm/index | binary | |
MD5:54CB446F628B2EA4A5BCE5769910512E | SHA256:FBCFE23A2ECB82B7100C50811691DDE0A33AA3DA8D176BE9882A9DB485DC0F2D | |||
| 2869 | app_process64 | /data/data/updater.attester.responder/cache/WebView/Default/HTTP Cache/Code Cache/wasm/index-dir/temp-index | binary | |
MD5:CB3D4A83D5FDC2C2412E6B8E24A1D1D6 | SHA256:A38323200B1AC818BDB4FFC2BB9F04EA5FE8D974088CD20CB6D51908F00B4C75 | |||
PID | Process | Method | HTTP Code | IP | URL | CN | Type | Size | Reputation |
|---|---|---|---|---|---|---|---|---|---|
822 | app_process64 | GET | 204 | 142.250.186.68:443 | https://www.google.com/generate_204 | US | — | — | whitelisted |
1756 | app_process64 | POST | 200 | 142.251.173.81:443 | https://staging-remoteprovisioning.sandbox.googleapis.com/v1:fetchEekChain | US | binary | 778 b | whitelisted |
822 | app_process64 | GET | 204 | 172.217.20.131:80 | http://connectivitycheck.gstatic.com/generate_204 | US | — | — | whitelisted |
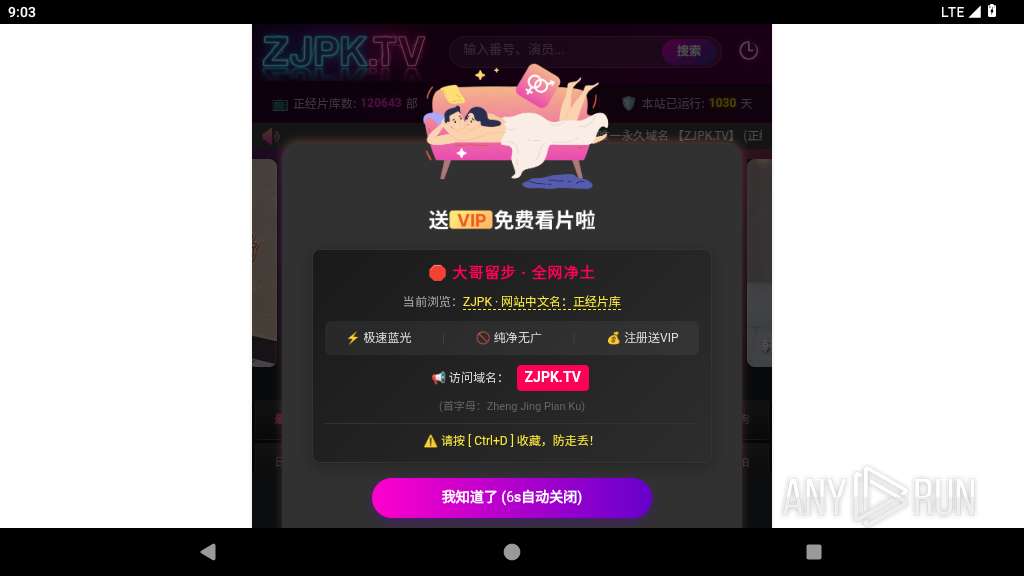
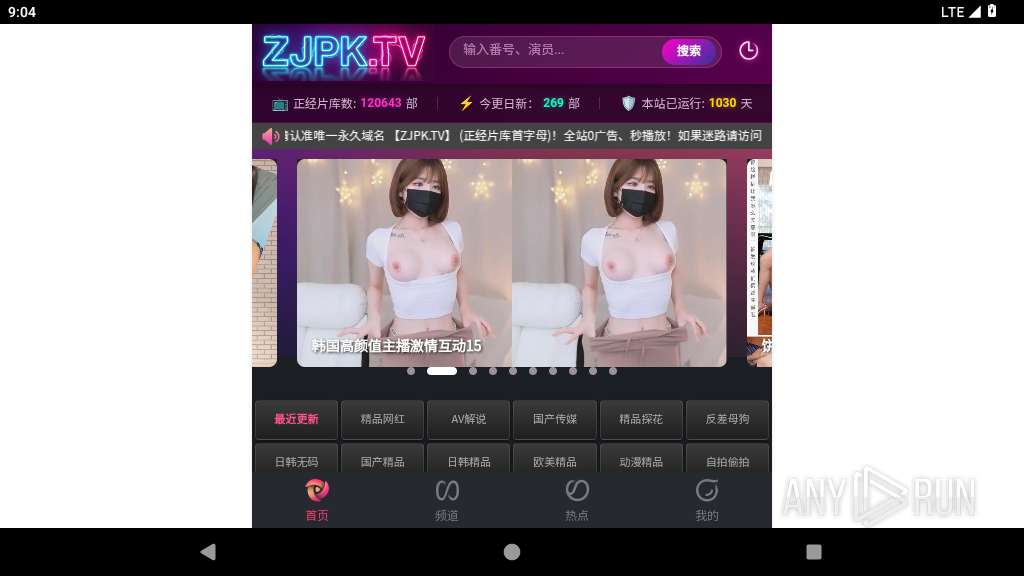
2869 | app_process64 | GET | 200 | 188.114.96.3:443 | https://www.zjpk.tv/static/js/jquery.js | US | text | 90.4 Kb | unknown |
2869 | app_process64 | GET | 200 | 188.114.96.3:443 | https://www.zjpk.tv/MDassets/js/madouym.js | US | text | 179 Kb | unknown |
2869 | app_process64 | GET | 200 | 188.114.96.3:443 | https://www.zjpk.tv/MDassets/js/theme/default/layer.css?v=3.1.1 | US | text | 17.0 Kb | unknown |
2869 | app_process64 | GET | 200 | 188.114.96.3:443 | https://www.zjpk.tv/MDassets/images/icons/notice_icon.png | US | image | 1.55 Kb | unknown |
2954 | app_process32 | POST | 200 | 142.251.141.99:443 | https://update.googleapis.com/service/update2/json?cup2key=15:-_4wcRuqAhI4zO6D2rTy04BprOvI6XhWWLWFmvkPv-E&cup2hreq=7ad47fb443b5631d5778d70750da95744656f92336bf2cf0337b0db423986eb2 | US | text | 1.92 Kb | whitelisted |
1756 | app_process64 | POST | 200 | 142.251.173.81:443 | https://staging-remoteprovisioning.sandbox.googleapis.com/v1:signCertificates?challenge=AAABnPC8H7kBILStY3f2ZVEBV8S493XXI0U4LB8=&request_id=8a240496-5076-43a6-ae2d-02da1371eef8 | US | binary | 11.8 Kb | whitelisted |
2954 | app_process32 | POST | 200 | 142.251.141.99:443 | https://update.googleapis.com/service/update2/json | US | text | 251 b | whitelisted |
PID | Process | IP | Domain | ASN | CN | Reputation |
|---|---|---|---|---|---|---|
— | — | 142.251.36.100:80 | — | GOOGLE | US | whitelisted |
443 | mdnsd | 224.0.0.251:5353 | — | — | — | whitelisted |
— | — | 172.217.20.131:80 | connectivitycheck.gstatic.com | GOOGLE | US | whitelisted |
— | — | 142.251.36.100:443 | — | GOOGLE | US | whitelisted |
571 | app_process64 | 216.239.35.0:123 | time.android.com | GOOGLE | US | whitelisted |
822 | app_process64 | 142.250.186.68:443 | www.google.com | GOOGLE | US | whitelisted |
822 | app_process64 | 172.217.20.131:80 | connectivitycheck.gstatic.com | GOOGLE | US | whitelisted |
1756 | app_process64 | 142.251.173.81:443 | staging-remoteprovisioning.sandbox.googleapis.com | GOOGLE | US | whitelisted |
2954 | app_process32 | 142.251.141.99:443 | update.googleapis.com | GOOGLE | US | whitelisted |
2954 | app_process32 | 34.104.35.123:443 | edgedl.me.gvt1.com | GOOGLE-CLOUD-PLATFORM | US | whitelisted |
Domain | IP | Reputation |
|---|---|---|
google.com |
| whitelisted |
connectivitycheck.gstatic.com |
| whitelisted |
www.google.com |
| whitelisted |
time.android.com |
| whitelisted |
staging-remoteprovisioning.sandbox.googleapis.com |
| whitelisted |
update.googleapis.com |
| whitelisted |
edgedl.me.gvt1.com |
| whitelisted |
clientservices.googleapis.com |
| whitelisted |
www.zjpk.tv |
| unknown |
www.svipx.cfd |
| unknown |
PID | Process | Class | Message |
|---|---|---|---|
822 | app_process64 | Misc activity | ET INFO Android Device Connectivity Check |
2869 | app_process64 | A Network Trojan was detected | MALWARE [ANY.RUN] Android/Btmob activity observed in HTTP request |
339 | netd | Misc activity | ET INFO Observed DNS Query to .cfd TLD |
339 | netd | Misc activity | INFO [ANY.RUN] .cc TLD domain request |
2869 | app_process64 | A Network Trojan was detected | MALWARE [ANY.RUN] Android/Btmob activity observed in HTTP request |
2869 | app_process64 | A Network Trojan was detected | MALWARE [ANY.RUN] Android/Btmob activity observed in HTTP request |
2869 | app_process64 | A Network Trojan was detected | MALWARE [ANY.RUN] Android/Btmob activity observed in HTTP request |