Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
35
Global rank
34 infographic chevron month
Month rank
53 infographic chevron week
Week rank

RedLine Stealer is a malicious program that collects users’ confidential data from browsers, systems, and installed software. It also infects operating systems with other malware.

Stealer
Type
ex-USSR
Origin
1 March, 2020
First seen
14 October, 2026
Last seen
Also known as
RedLine

How to analyze RedLine Stealer with ANY.RUN

Type
ex-USSR
Origin
1 March, 2020
First seen
14 October, 2026
Last seen

IOCs

IP addresses
23.11.40.157
23.59.18.102
188.114.96.3
150.171.109.105
135.232.92.137
172.211.123.248
95.100.135.112
48.192.1.64
2.16.204.141
48.209.138.189
40.126.31.71
149.154.166.110
92.205.2.170
74.178.76.54
193.122.130.0
204.79.197.203
20.165.94.63
150.171.109.98
48.209.133.15
131.253.33.203
Hashes
dc6c46c234c17bb65b4bfad053dcbd1b2c02ead4c3b1853b72deabec9db932b4
5f4afc766685e909e0c6803d916a2605f8b0db1975d0a442fcb0a1682ad52e12
3db4cd30fa85d28ea51d636349e36b4e32098b871ef249d8a70dec1b3950ebaf
55160bb1d98a38df635c0cbe81adc23b0a9bc55c758d4dce62f74db9a267535b
4a07c4b41cb4823ff4c95763c84dff62816046fb97dc3353d4abb62e7294b8a2
add805b49cf9a53945f078671bada146b57e68aa80161a9118af6ef78fcfcc5d
941a189bd84102c13255835bb2f4df77d9cb126be4e54faa179b9de469375fbe
b6b5da015ed9b1222c507c4df03d0351addf6621168f1dc3d3351afda7ab1d84
d728b368e5e07a3e57bd71370eca12ea6754b5dbde36946ab3792ee19c23b282
71453523c85ae94798b4935f8519f4bac0f7c53c0c99f4f5e24c3a8a1e5fab22
3139bb548ac470a2397678a14376c7495f41b8c1cd2338b091d552eb864be462
03cc37ce20e883a9f7dd14bfc75f814a0b7f8ed7826ff80e015902638ba2c12b
fc3ae3193436c0678d7d1f9e5f364aa1969c413987c5875e5e9c717e7a717681
2381dcdd93f572c5cf63024b2de56b6d5466f33434c9899ab6f9c3e6e021db71
7165ac760feeea55c06dc7951b6b9ddc7804eec2fbfed67d364830395e921bf6
8cca6e1373a54f117c23dfeb5086b1f30cb8a3c5ced543c90d9aac5c9e61f458
f7e4aae30ab2bda60bead5fd5a29a36685d768df007d3399d3047768babae200
83b3fb548b094aa66bbf9da57c4d5a49acaa76914121e90aa05fb53ab47367e0
3118a029c644a831c1ae3e55047b2598462c70c45053425d985de24c22b04eb1
66e6eed42917b8a0dd2a80c8bddbe153841bd7c307ae8fc09bf81be8e6549461
Domains
reallyfreegeoip.org
th.bing.com
settings-win.data.microsoft.com
activation-v2.sls.microsoft.com
ocsp.digicert.com
oneocsp.microsoft.com
crl.microsoft.com
www.bing.com
fe3cr.delivery.mp.microsoft.com
self.events.data.microsoft.com
www.microsoft.com
slscr.update.microsoft.com
api.telegram.org
mail.ujexchange.com
login.live.com
google.com
client.wns.windows.com
checkip.dyndns.org
ecs.office.com
www.google.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
http://checkip.dyndns.org/
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://reallyfreegeoip.org/xml/45.86.203.63
https://api.telegram.org/bot/sendmessage?chat_id=&text=%20%0d%0a%0d%0apc%20name:desktop-jglljld%0d%0adate%20and%20time:%2010/13/2026%20/%209:21:24%20pm%0d%0acountry%20name:%20%0d%0a%5b%20desktop-jglljld%20clicked%20on%20the%20file%20if%20you%20see%20nothing%20this's%20mean%20the%20system%20storage's%20empty.%20%5d
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
http://www.google.com/
http://www.bing.com/
https://th.bing.com/th?id=odswg.iotdlocalicon&w=16&h=16&c=1&rs=1&p=0
Last Seen at
Last Seen at

Recent blog posts

post image
Fake AI Tools Put US Companies at Risk: Insid...
watchers 832
comments 0
post image
What's Really Attacking Your Industry? Insigh...
watchers 2482
comments 0
post image
Making Threat Intelligence Work for SOC Teams...
watchers 10164
comments 0

What is RedLine Stealer?

RedLine Stealer or RedLine is malware that can collect users’ confidential information and deliver other malicious programs. The availability and flexibility of the stealer cause financial loss, data leakage, targeting both enterprise and personal devices. Healthcare and manufacturing sectors suffer the most from these attacks.

The malware appeared in March 2020 according to the Proofpoint investigation. Since then RedLine has just gained steam. It was on the rise during the COVID-19 pandemic and is still active. On July 1st, 2021 the malware was found on the legit-looking website that provides privacy tools. However, based on the payload analysis, only malware can be found there.

General description of RedLine malware

RedLine is an infostealer that takes information about users from browsers, systems instant messaging, and file transfer protocol clients. The main target is passwords, credit card information, username, location, autofill data, cookies, software set, and even hardware configuration like keyboard layout, UAC settings, etc. The virus is also capable of stealing cryptocurrency.

The malicious program acts as a typical stealer such as Raccoon or Pony: it uploads and downloads files, executes commands, and reports information about the infected machine. Moreover, attackers make use of RedLine to deliver ransomware, RATs, trojans, and miners.

The infostealer is quite popular as there is no problem finding it. Underground forums, C&C panels offer different options such as malware-as-a-service versions or a subscription. The price varies from $100 to $200.

One cannot tell that RedLine Stealer is a sophisticated malware like ransomware. It has the usual features typical for this family. However, it is .Net malware written in C# and the code quality is high enough to reveal an experienced programmer behind it. Cybercriminals also work hard to update malware, like downloading secondary payloads and advanced filtering features.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

RedLine malware analysis

ANY.RUN allows researchers to perform the analysis and watch the RedLine in action in an interactive sandbox simulation
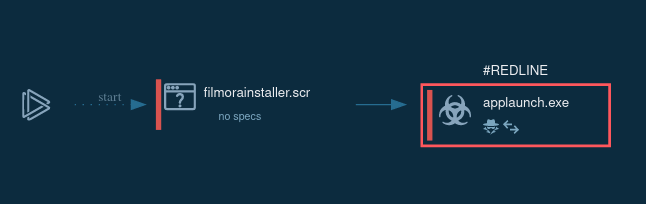
redline stealer process graph

Figure 1: Displays the lifecycle of RedLine in a visual form as a process graph generated by ANY.RUN
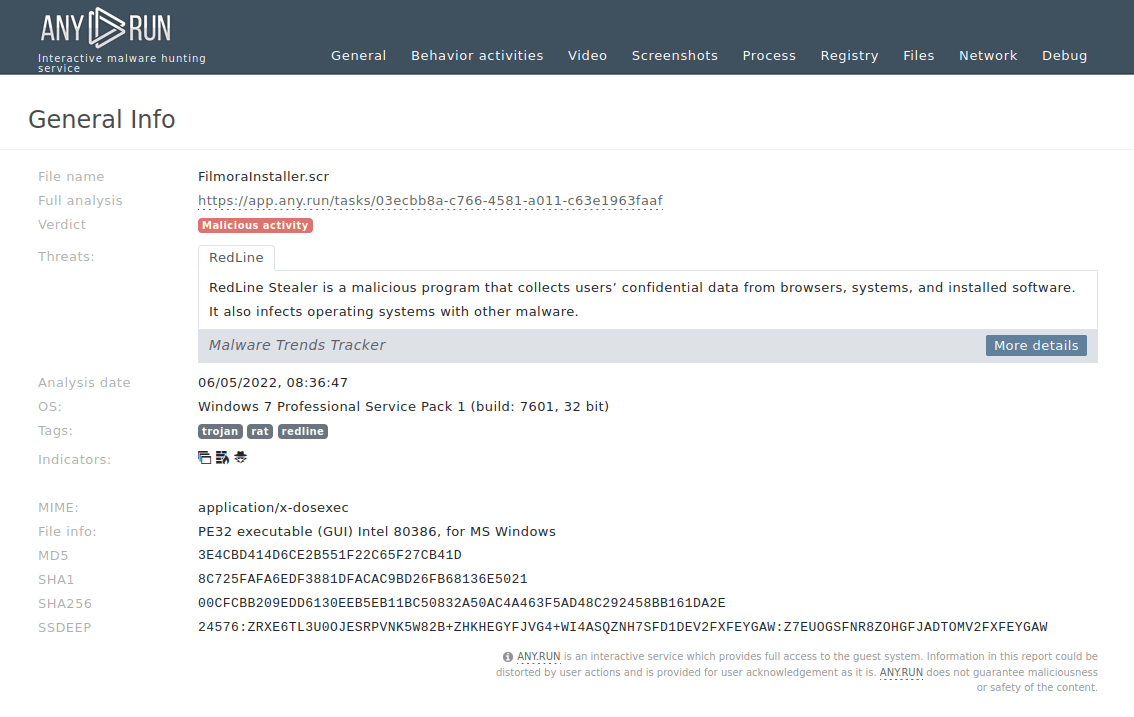
redline stealer report

Figure 2: A customizable text report generated by ANY.RUN allows users to take an even deeper look at the malware and helps to share the research results.

RedLine Stealer execution process

Typically the execution process of that stealer is plain and straightforward. Based on the analysis, the main binary launches itself and the parent process stops. It also may be dropped from another binary or be the main binary itself. When a child process is created, the main malicious activity starts – RedLine collects information from the infected system such as passwords and others, and sends it to the Command & Control panel. When all information is collected and sent, the stealer just quits execution. Stolen information is sent in both non-encrypted and base64 encoded formats.

Distribution of RedLine

Attackers are not very creative with the delivery method of the virus. However, as the ransomware story, the method works perfectly – social engineering for different email campaigns including business email compromise, spam, fake updates, ads in Google result in malicious attachments or links. We can notice the big variety of file formats here:

  • Office
  • PDF
  • RAR and ZIP
  • Executable files
  • JavaScript

If you open the files in the attachment, RedLine will download other malicious programs.

How to detect RedLine infostealer using ANY.RUN?

At the moment, analysts can quickly recognize the info stealer because it will be tagged after Suricata IDS rules are triggered. Since the malicious program sends the stolen info to its panel just right after the start of the execution, it won't take a lot of time.

Conclusion

The best way to protect your organization or device from RedLine is to be cautious with suspicious files and links that get into your email. Your staff should be aware that even trustworthy sources can lead to infection and password or other credentials’ theft. It won’t take long to check a file in a sandbox such as ANY.RUN. Several minutes will be enough to detect RedLine and you will be good to go. Stay safe.
HAVE A LOOK AT

Remote Access Trojan screenshot
Remote access trojans (RATs) are a type of malware that enables attackers to establish complete to partial control over infected computers. Such malicious programs often have a modular design, offering a wide range of functionalities for conducting illicit activities on compromised systems. Some of the most common features of RATs include access to the users’ data, webcam, and keystrokes. This malware is often distributed through phishing emails and links.
Read More
DonutLoader screenshot
DonutLoader
donutloader donut
DonutLoader is a versatile, open-source-based in-memory loader that turns .NET assemblies, executables, DLLs, and scripts into position-independent shellcode for execution entirely in RAM. Originally derived from the popular Donut tool, it enables threat actors to bypass traditional antivirus and EDR solutions by avoiding disk writes and injecting payloads directly into legitimate Windows processes.
Read More
Ramnit screenshot
Ramnit
ramnit
Ramnit is a highly modular banking trojan and worm that evolved from a file-infecting virus into a powerful cybercrime tool. It specializes in financial fraud, credential theft, remote access, and malware delivery, being a serious threat to businesses and individuals. First spotted in 2010, Ramnit became popular after the 2014 takedown of the GameOver Zeus botnet, as cybercriminals sought alternatives for banking fraud.
Read More
Pulsar RAT screenshot
Pulsar RAT
pulsar
Pulsar RAT is a derivative of Quasar RAT with extensive functionality including keylogging, cryptocurrency wallet clipping, credential theft, file management, remote shell execution, and data exfiltration capabilities. As a modular, open-source remote administration tool designed for Windows systems, Pulsar introduces significant enhancements over its predecessor.
Read More
Socelars screenshot
Socelars
socelars
Socelars is an information-stealing Trojan (often categorized as spyware/stealer) that focuses on collecting sensitive data from Windows systems, with standout reporting around Facebook Ads Manager and session cookie theft. Unlike “noisy” malware that immediately breaks something, Socelars quietly converts a single infected machine into access: logged-in sessions, business account data, and pathways to monetization.
Read More
HijackLoader screenshot
HijackLoader
hijackloader
HijackLoader is a modular malware acting as a vehicle for distributing different types of malicious software on compromised systems. It gained prominence during the summer of 2023 and has since been used in multiple attacks against organizations from various sectors, including hospitality businesses.
Read More