Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now
30
Global rank
29 infographic chevron month
Month rank
34 infographic chevron week
Week rank
0
IOCs

NanoCore is a Remote Access Trojan or RAT. This malware is highly customizable with plugins which allow attackers to tailor its functionality to their needs. Nanocore is created with the .NET framework and it’s available for purchase for just $25 from its “official” website.

Trojan
Type
USA
Origin
1 January, 2013
First seen
6 September, 2026
Last seen

How to analyze Nanocore with ANY.RUN

Type
USA
Origin
1 January, 2013
First seen
6 September, 2026
Last seen

IOCs

IP addresses
13.248.169.48
107.174.192.179
48.209.6.48
192.178.183.95
74.178.240.61
149.154.167.99
8.8.8.8
76.223.54.146
45.141.233.69
23.48.23.146
74.179.77.164
35.173.69.207
142.251.110.94
48.209.138.189
142.251.14.94
150.171.27.11
154.91.34.165
142.251.14.154
140.82.121.3
208.95.112.1
Hashes
3ff64f10603f0330fa2386ff99471ca789391ace969bd0ec1c1b8ce1b4a6db42
cd2c00ce027687ce4a8bdc967f26a8ab82f651c9becd703658ba282ec49702bd
17e098ffaf49f4eb7c98a94af360ed443bfe3bce0335b09e13778221919a007f
b82d5dad784762f378c3aff27426f3e27c1dc987f72640eebf6d4b541761258e
b692c6d704a3035deedf813d394d0727bb100283b6635d54afa3d7f76223fb6e
41db5386c9bafd7601f7d27986f4a9fbedb110ec14d13f397d559cb2dfeae716
71906270f94ea5ec124e0c1caa7612e4cc034e176cb1ae3498224992978eb8f0
f05fa13418376f1085a619d065c3cb16ba540b816d4ce1aa2674500e71ae6ef4
f6d38eb676bbbd710b670b563ea557a25e21c12f3e3ded44582db200c0128e96
0cbd6c3efea8fd8c555974d7fb8d3cf393966294c65c15984cecaf36e18bb2c9
6e4569fd60a7c9130d547406441493d063442ed84472b3d9e666ae2c7253d63d
aec2a4cd3c3f7753691a503e133a42524021e87f71386b7d319e3245eb4e766d
0b4db7a09ee3306e969fe0b32228422f223eb2f71bd5d1ec1a0d9ef16b405c58
82b9db18853a960a88dc865714229eeb57979339be6c49ddecfda0766eec9d4b
9f7a00b7385b15a3155dd0ace08d726f5a3b0196ebb4fb0b0aafebf770bc44e1
a0223b245c2a52e9671fa60bddb32283e43b66c363cc82a9af3663dc055fad3c
084134eab56d3f2b14a3a777c078f7b0119eeba0641af54dac74a00fd367cfa7
35329fdadfeeb2377d06e27515a597bd46832763f62af804326e30cdd561f488
5f193196db94f25aef709945465e2d33d18bdad144a39f38b63d82c0364aeeee
acbe8b2e9edcc95d5a4837b3ab1273be20e3144b0726825d9b4e526785baa7ba
Domains
ep1.adtrafficquality.google
edge.microsoft.com
ocsp.digicert.com
release-assets.githubusercontent.com
steamcommunity.com
www.bing.com
pagead2.googlesyndication.com
fonts.googleapis.com
consent.google.co.ck
fonts.gstatic.com
xpaywalletcdn.azureedge.net
login.live.com
crl.microsoft.com
www.gstatic.com
www.microsoft.com
update.googleapis.com
narrathfpt.top
cloud-api.yandex.net
encrypted-tbn2.gstatic.com
client.wns.windows.com
URLs
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
https://gateway.discord.gg/?v=9&encording=json
https://t.me/m00f3r
http://www.aieov.com/logo.gif
https://steamcommunity.com/profiles/76561199851454339
https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
https://settings-win.data.microsoft.com/settings/v3.0/onesettings/client?osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&localdeviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&attrdataver=186&osuilocale=en-us&osskuid=48&app=wosc&appver=&isflightingenabled=0&telemetrylevel=1&devicefamily=windows.desktop
https://api.pcloud.com/listfolder?path=/
https://cloud-api.yandex.net/v1/disk/resources?path=/&limit=500
https://login.live.com/rst2.srf
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://login.live.com/ppsecure/deviceaddcredential.srf
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://api.ipify.org/
http://ip-api.com/json/158.173.162.29
Last Seen at
Last Seen at

Recent blog posts

post image
Release Notes: Faster TI Investigations, Fres...
watchers 4347
comments 0
post image
Triage & Response Bottlenecks Eating into...
watchers 4009
comments 0
post image
Major Cyber Attacks in August 2026: US and EU...
watchers 9877
comments 0

What is NanoCore malware?

NanoCore is a Remote Access Trojan or RAT. This malware is highly customizable with plugins that allow attackers to tailor its functionality to their needs. Nanocore is created with the .NET framework and it’s available for purchase for just $25 from its “official” website.

This malware was recorded in the wild for the first time in 2013. Since then it has become extremely popular. It is now used in attacks all around the world. As a modular malware, the functionality of the NanoCore backdoor can be greatly expanded with plugins. This makes an already dangerous RAT potentially even more destructive for the company's cybersecurity.

Distributed on its own website with 24/7 technical support for just $25 with all official plugins included, the malware can also be downloaded from hacking forums where its "cracked" version has been leaked multiple times, making it an extremely accessible trojan to set up and use. Unfortunately, the accessibility, ease of use, and a bunch of information on NanoCore are still contributing to its growing popularity. It’s not completely certain whether the malware was being developed as a commercial program for institutions, or the creator had a goal to create malicious software from the beginning, Regardless, NanoCore author, Taylor Huddleston was tracked down and arrested by the FBI.

General Information about NanoCore RAT

According to the analysis, NanoCore’s first beta appeared in 2013. The latest version of the malware is being openly sold on its own website NANOCORE_dot_io. Unfortunately, this helped ensure the high popularity of the malware. Today NanoCore RAT targets victims worldwide. However, the majority of attacks are taking place in the US.

One of the key characteristics of this RAT is that technically savvy attackers are able to greatly expand the functionality of the malware, fine-tuning it to suit their needs, for instance, by adding screen locker functionality to the virus. Some essential plugins are already provided with the purchase bundle on the “official” website. Other even more sophisticated ones are being developed by the community of cybercriminals, that has formed around NanoCore.

For crooks that don’t want to engage in fiddling with plugins, NanoCore provides a straightforward user interface It allows even novice criminals to launch potentially destructive malicious campaigns. Thus further contributing to the popularity of the malware.

Interactive analysis of NanoCore

A video of the execution process provided by ANY.RUN malware hunting service allows us to perform the analysis of the lifecycle of the trojan or other malware such as WSHRAT or Vidar. We can watch NanoCore behavior as well as all processes as they unfold in a secure online environment.
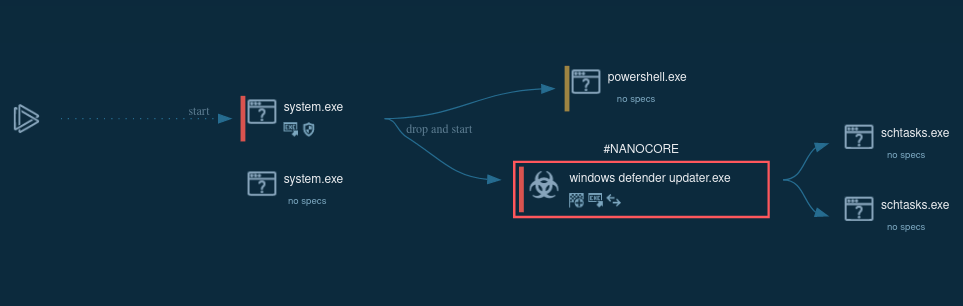
nanocore execution process graph

Figure 1: A visual graph of NanoCore execution processes generated by ANY.RUN

How does NanoCore spread?

NanoCore RAT is distributed using multiple methods. However, the most commonly used is spam email campaigns. They trick users into downloading malicious documents, often presented as price lists or purchase orders.

The emails sometimes contain malicious attachments with .img or .iso extension. The large size of these files makes it difficult to scan them. Some versions of malware are also spread by a ZIP file which evades secure email gateways. Several file structure works here: one file script will download the payload while the rest are decoys that ensure the malicious content goes unnoticed by the system's security.

PowerPoint files acquire the same scenario as the infection chain takes place over multiple stages before the final payload is executed.

NanoCore RAT execution process

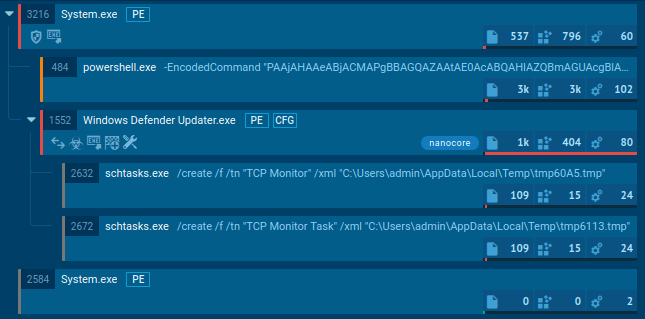
NanoCore is delivered to the victim’s PC using the AutoIt program. Not unlike Agent Tesla malware, which is somewhat typical for this type of RATs. Typically, NanoCore is spread using Microsoft Word documents. Infected files contain an embedded executable file or an exploit.

According to the RAT analysis, once the script file is opened an embedded macros download an executable script file and rename it. The downloaded executable file runs itself and creates a child process. The malware is able to use Regsvcs and Regasm to proxy the code execution through a trusted Windows utility.
nanocore execution process tree

Figure 2: A process tree of NanoCore execution processes generated by ANY.RUN

How to detect NanoCore malware using ANY.RUN?

You can identify whether you are dealing with a sample of NanoCore RAT or not by a quick analysis of the files and scripts created by the malware. Most often NanoCore injects into three processes RegSvcs.exe, RegAsm.exe, and MSBuild.exe.

Open "Advanced details of process" for these processes and look at the "Modified files" tab in the "Events" section. If a file named "run.dat" was created by one of these processes and placed in the %Root%:\Users\username\AppData\Roaming[GUID] folder, you can be sure that the malware you are observing is, in fact, NanoCore trojan.
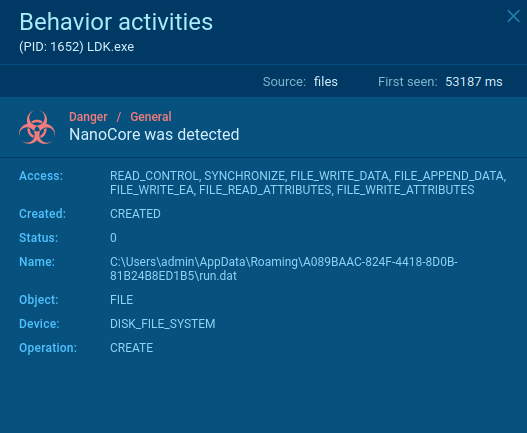
file created by nanocore Figure 3: File created by Nanocore

Conclusion

Thanks to accessibility, ease of use, customization, and plenty of information, the popularity of NanoCore escalated making it one of the most widespread RATs in the world. Even though NanoCores’ creator has been arrested by officials, due to the appearance of several cracked versions, NanoCore is still openly available on hacker forums.

Often, it can be acquired for free, allowing anybody to set up attacks. The popularity of the malware is further aided by the fact that one does not need much programming knowledge to use this Trojan, as it comes equipped with a user-friendly interface. At the same time, very sophisticated and destructive attacks can be carried out with NanoCore RAT by skillful hackers, since its malicious capabilities can be extended with custom plugins. Thankfully, modern analysis tools such as ANY.RUN allow researchers to examine malware in detail, learn about its behavior patterns and set up an appropriate cybersecurity response.
HAVE A LOOK AT

Balada Injector screenshot
Balada Injector is a long-running malware campaign that targets WordPress websites by exploiting vulnerabilities in plugins and themes. The attackers inject malicious code into compromised sites, leading to unauthorized redirects, data theft, and the creation of [backdoors](https://any.run/malware-trends/backdoor) for persistent access. The campaign operates in waves, with spikes in activity observed every few weeks, continually adapting to exploit newly discovered vulnerabilities.
Read More
BlackMatter screenshot
BlackMatter
blackmatter
BlackMatter is a ransomware strain operating as a Ransomware-as-a-Service (RaaS), designed to encrypt files, remove recovery options, and extort victims across critical industries. Emerging in 2021, it quickly became a major concern due to its ability to evade defenses, spread across networks, and cause large-scale operational disruption, forcing security teams to act against a highly destructive and persistent threat.
Read More
Emmenhtal screenshot
Emmenhtal
emmenhtal
First identified in 2024, Emmenhtal operates by embedding itself within modified legitimate Windows binaries, often using HTA (HTML Application) files to execute malicious scripts. It has been linked to the distribution of malware such as CryptBot and Lumma Stealer. Emmenhtal is typically disseminated through phishing campaigns, including fake video downloads and deceptive email attachments.
Read More
Tycoon 2FA screenshot
Tycoon 2FA
tycoon
Tycoon 2FA is a phishing-as-a-service (PhaaS) platform designed to bypass multi-factor authentication (MFA) protections, particularly targeting Microsoft 365 and Gmail accounts. Its advanced evasion techniques and modular architecture make it a significant threat to organizations relying on MFA for security.
Read More
RedLine screenshot
RedLine
redline stealer redline stealer malware
RedLine Stealer is a malicious program that collects users’ confidential data from browsers, systems, and installed software. It also infects operating systems with other malware.
Read More
Spyware screenshot
Spyware
spyware
Spyware is a stealth form of malware whose primary objective is to gather sensitive information, such as personal data, login credentials, and financial details, by monitoring user activities and exploiting system vulnerabilities. Spyware operates secretly in the background, evading detection while transmitting collected data to cybercriminals, who can then use it for malicious purposes like identity theft, financial fraud, or espionage.
Read More