Black friday Up to 3 extra licenses FOR FREE + Special offer for TI LOOKUP Get it now
Webinar
February 26
Better SOC with Interactive Sandbox Practical Use Cases
Register now

VanHelsing Ransomware

189
Global rank
189 infographic chevron month
Month rank
179 infographic chevron week
Week rank

VanHelsing is a sophisticated ransomware strain that appeared in early 2025, operating via the Ransomware-as-a-Service (RaaS) model and targeting primarily USA and France. It threatens mostly Windows systems but has variants for Linux, BSD, ARM, and ESXi, making it a multi-platform malware. It is also notable for its advanced evasion techniques, double extortion tactics, and rapid evolution.

Ransomware
Type
Unknown
Origin
1 March, 2025
First seen
10 April, 2026
Last seen

How to analyze VanHelsing Ransomware with ANY.RUN

Type
Unknown
Origin
1 March, 2025
First seen
10 April, 2026
Last seen

IOCs

IP addresses
48.192.1.64
20.165.94.63
20.73.194.208
20.165.94.54
40.126.31.3
172.66.2.5
51.104.136.2
40.127.240.158
23.59.18.102
2.16.241.201
2.16.164.49
204.79.197.203
172.211.123.250
23.216.77.28
Hashes
d4564a45cf3e8ddf2ce90f2b35fa97c3cc0bf22e7c4588aba22bfe4f893c97d1
4516ad42226e286b8545ce81e772c8e118737c5d01debb603a3e818b8791ccc8
6e5320d8f3343662294280ad2a8c19effefc55ff12089811dec3841f02934102
Domains
fe3cr.delivery.mp.microsoft.com
www.bing.com
crl.microsoft.com
settings-win.data.microsoft.com
activation-v2.sls.microsoft.com
ocsp.digicert.com
slscr.update.microsoft.com
www.microsoft.com
self.events.data.microsoft.com
login.live.com
google.com
oneocsp.microsoft.com
client.wns.windows.com
URLs
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaagb6jmmcovb6saaaaaaay%3d
https://login.live.com/rst2.srf
http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
https://login.live.com/ppsecure/deviceaddcredential.srf
https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
https://settings-win.data.microsoft.com/settings/v3.0/onesettings/client?osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&localdeviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&attrdataver=186&osuilocale=en-us&osskuid=48&app=wosc&appver=&isflightingenabled=0&telemetrylevel=1&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
https://slscr.update.microsoft.com/sls/ping
https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6&currentbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
http://crl.microsoft.com/pki/crl/products/microoceraut_2010-06-23.crl
Last Seen at

Recent blog posts

post image
Threat Coverage Digest: New Malware Reports a...
watchers 6945
comments 0
post image
Phishing Response Protocol: 3 Essential SOC S...
watchers 9046
comments 0
post image
Major Cyber Attacks in September 2026: US and...
watchers 13157
comments 0

What is VanHelsing Ransomware?

With its affiliate program launching in the dark web on March 7, 2025, VanHelsing ransomware spread rapidly infecting three victims within two weeks. This RaaS’s affiliates are demanded “not to target the Commonwealth of Independent States (CIS)”. VanHelsing’s double extortion model involves encrypting valuable data and threatening to leak it to extort ransom.

Known to demand up to $500,000 in Bitcoin, VanHelsing operates as a scalable platform, allowing affiliates to join with a $5,000 deposit and keep 80% of ransom payments, while operators take 20%. Government, manufacturing, pharmaceuticals have become the most affected industries, with further expansion to finance, healthcare, and critical infrastructure.

VanHelsing employs multiple initial access vectors: phishing emails, unpatched software or systems, RDP weaknesses, VPN services, cloud misconfigurations, legitimate remote management tools, supply chain attacks.

Once inside, VanHelsing uses techniques like Windows Management Instrumentation (WMI) for stealthy execution and credential dumping to escalate privileges. It encrypts files using strong encryption algorithms and appends the “.vanhelsing” extension, rendering them inaccessible. Then it alters the desktop wallpaper and drops a ransom note.

VanHelsing hunts for sensitive data (personal details, financial records, or corporate documents) for double extortion. Its persistence is maintained by modifying registry, scheduling tasks, or installing bootkits.

Get started today for free

Analyze malware and phishing in a fully-interactive sandbox

Create free account

VanHelsing Ransomware Prominent Features

VanHelsing poses significant risks due to:

  • Stealthy Encryption: Separates encryption from file renaming: even if security tools detect the renaming, the data is already encrypted.
  • Anti-Analysis and Debug Checks: Detects virtual machines, sandboxes, or debugging environments and halts malicious activity to avoid analysis.
  • WMI Abuse: Uses Windows Management Instrumentation for stealthy execution.
  • Rootkits and Direct Volume Access: Hides malicious activities by manipulating system volumes or installing rootkits.
  • Process Injection: Injects malicious code into legitimate processes.
  • Time-Based Evasion: Delays execution in sandbox environments to appear harmless during analysis.
  • Fast Flux Networks: Rapidly rotates IP addresses to render IP-based blocking ineffective and maintain resilient C2 communication.
  • Obfuscation: Makes its code difficult to analyze by anti-malware engines.

VanHelsing Execution Process and Technical Details

An illustrative example of VanHelsing’s attack paradigm can be found in the repository of fresh malware samples of ANY.RUN’s Interactive Sandbox.

View VanHelsing kill chain to explore its processes, connections, and IOCs.
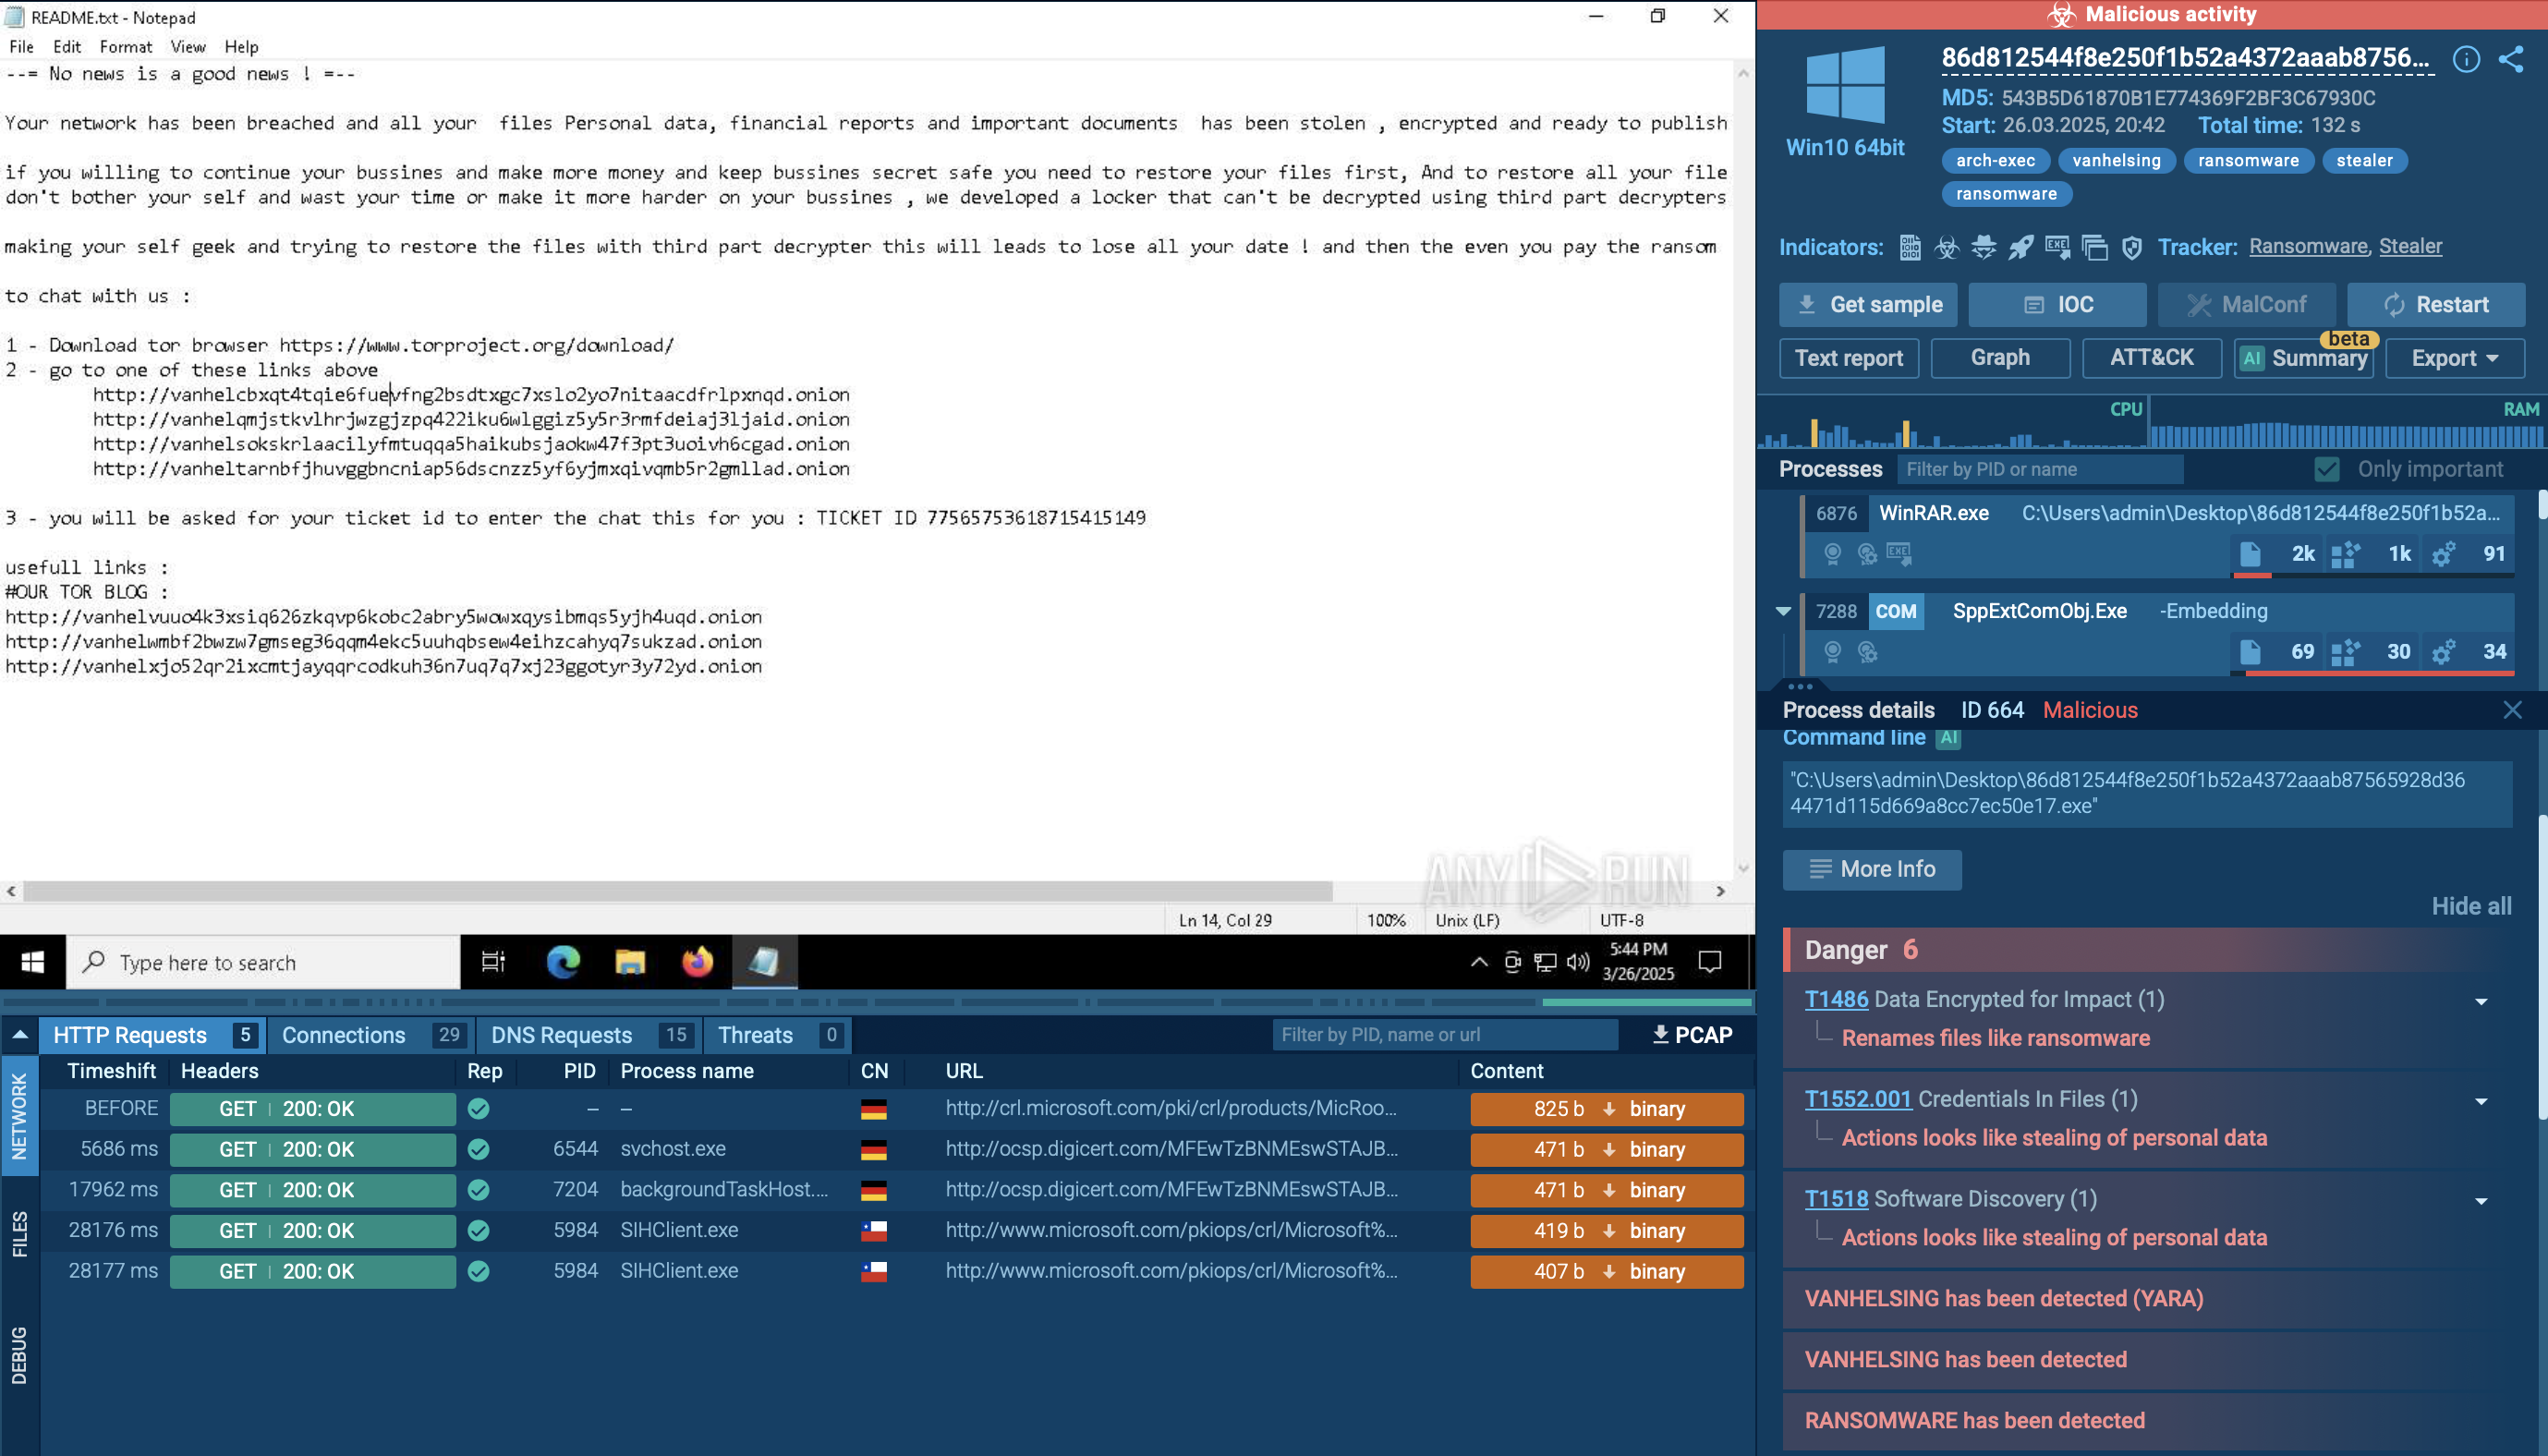
VanHelsing Ransomware analysis in ANY.RUN Sandbox _ VanHelsing Ransomware sample in ANY.RUN's Interactive Sandbox_

Once executed, the ransomware first enumerates all available drives on the system, including both local and network drives, while deliberately avoiding core system files to prevent rendering the system unbootable.

After identifying its targets, VanHelsing generates a unique encryption key and nonce. It uses the ChaCha20 algorithm for file encryption, with the key and nonce subsequently encrypted using an embedded Curve25519 public key. For files smaller than approximately 1 GB, the entire file is encrypted; for larger files, only the first 30% is encrypted to accelerate the process while retaining leverage over the victim.

The encrypted data, along with the key and nonce metadata, is stored in a structured format within each file. As files are encrypted, the ransomware appends the ".vanhelsing" or, in some cases, ".vanlocker" extension to the affected files. It also drops a ransom note — typically named README.txt — in every encrypted directory. This note informs the victim of the breach, warns against using third-party decryptors due to the risk of permanent data loss, and demands a ransom — often a significant amount in Bitcoin — for decryption and deletion of exfiltrated data.

VanHelsing creates a mutex named "VanHelsing" to prevent multiple instances from running simultaneously on the same system. It may also change the desktop wallpaper to display its branding. Additionally, this ransomware supports command-line arguments for silent execution, verbose logging, and selective targeting of specific drives, directories, or files. In our case, it used CMD and WMIC commands to delete shadow copies on the infected system.

What are the best-known VanHelsing attacks?

  • Texas Municipal Government Attack. One of the earliest confirmed victims was a municipal government in Texas. The attackers demanded a $500,000 ransom, threatening to leak exfiltrated data if payment was not made.

Why Specific Attack Details Are Limited

  • VanHelsing is a relatively new ransomware strain, its victim count and public exposure are still developing, and many attacks may remain undisclosed due to victim reticence or ongoing negotiations.
  • Double extortion means some victims may pay to avoid data leaks, reducing public reporting.
  • The prohibition on targeting Commonwealth of Independent States (CIS) countries suggest VanHelsing operates in a region where law enforcement scrutiny is minimal, potentially limiting detailed intelligence on victims.

Gathering Threat Intelligence on VanHelsing Ransomware

Threat intelligence is one of the main tools for detecting and preventing damage from VanHelsing. It is essential to monitor Indicators of Compromise (IOCs) like the “.vanhelsing” file extension, Tor-based C2 domains, or Bitcoin wallet addresses employed by ransomware operators. IOCs, IOA, IOBs, and malware samples found via ANY.RUN’s Threat Intelligence Lookup will provide you with actionable indicators for setting up monitoring and alerts, as well as with insights into the ransomware behavior and adversaries’ tactics.
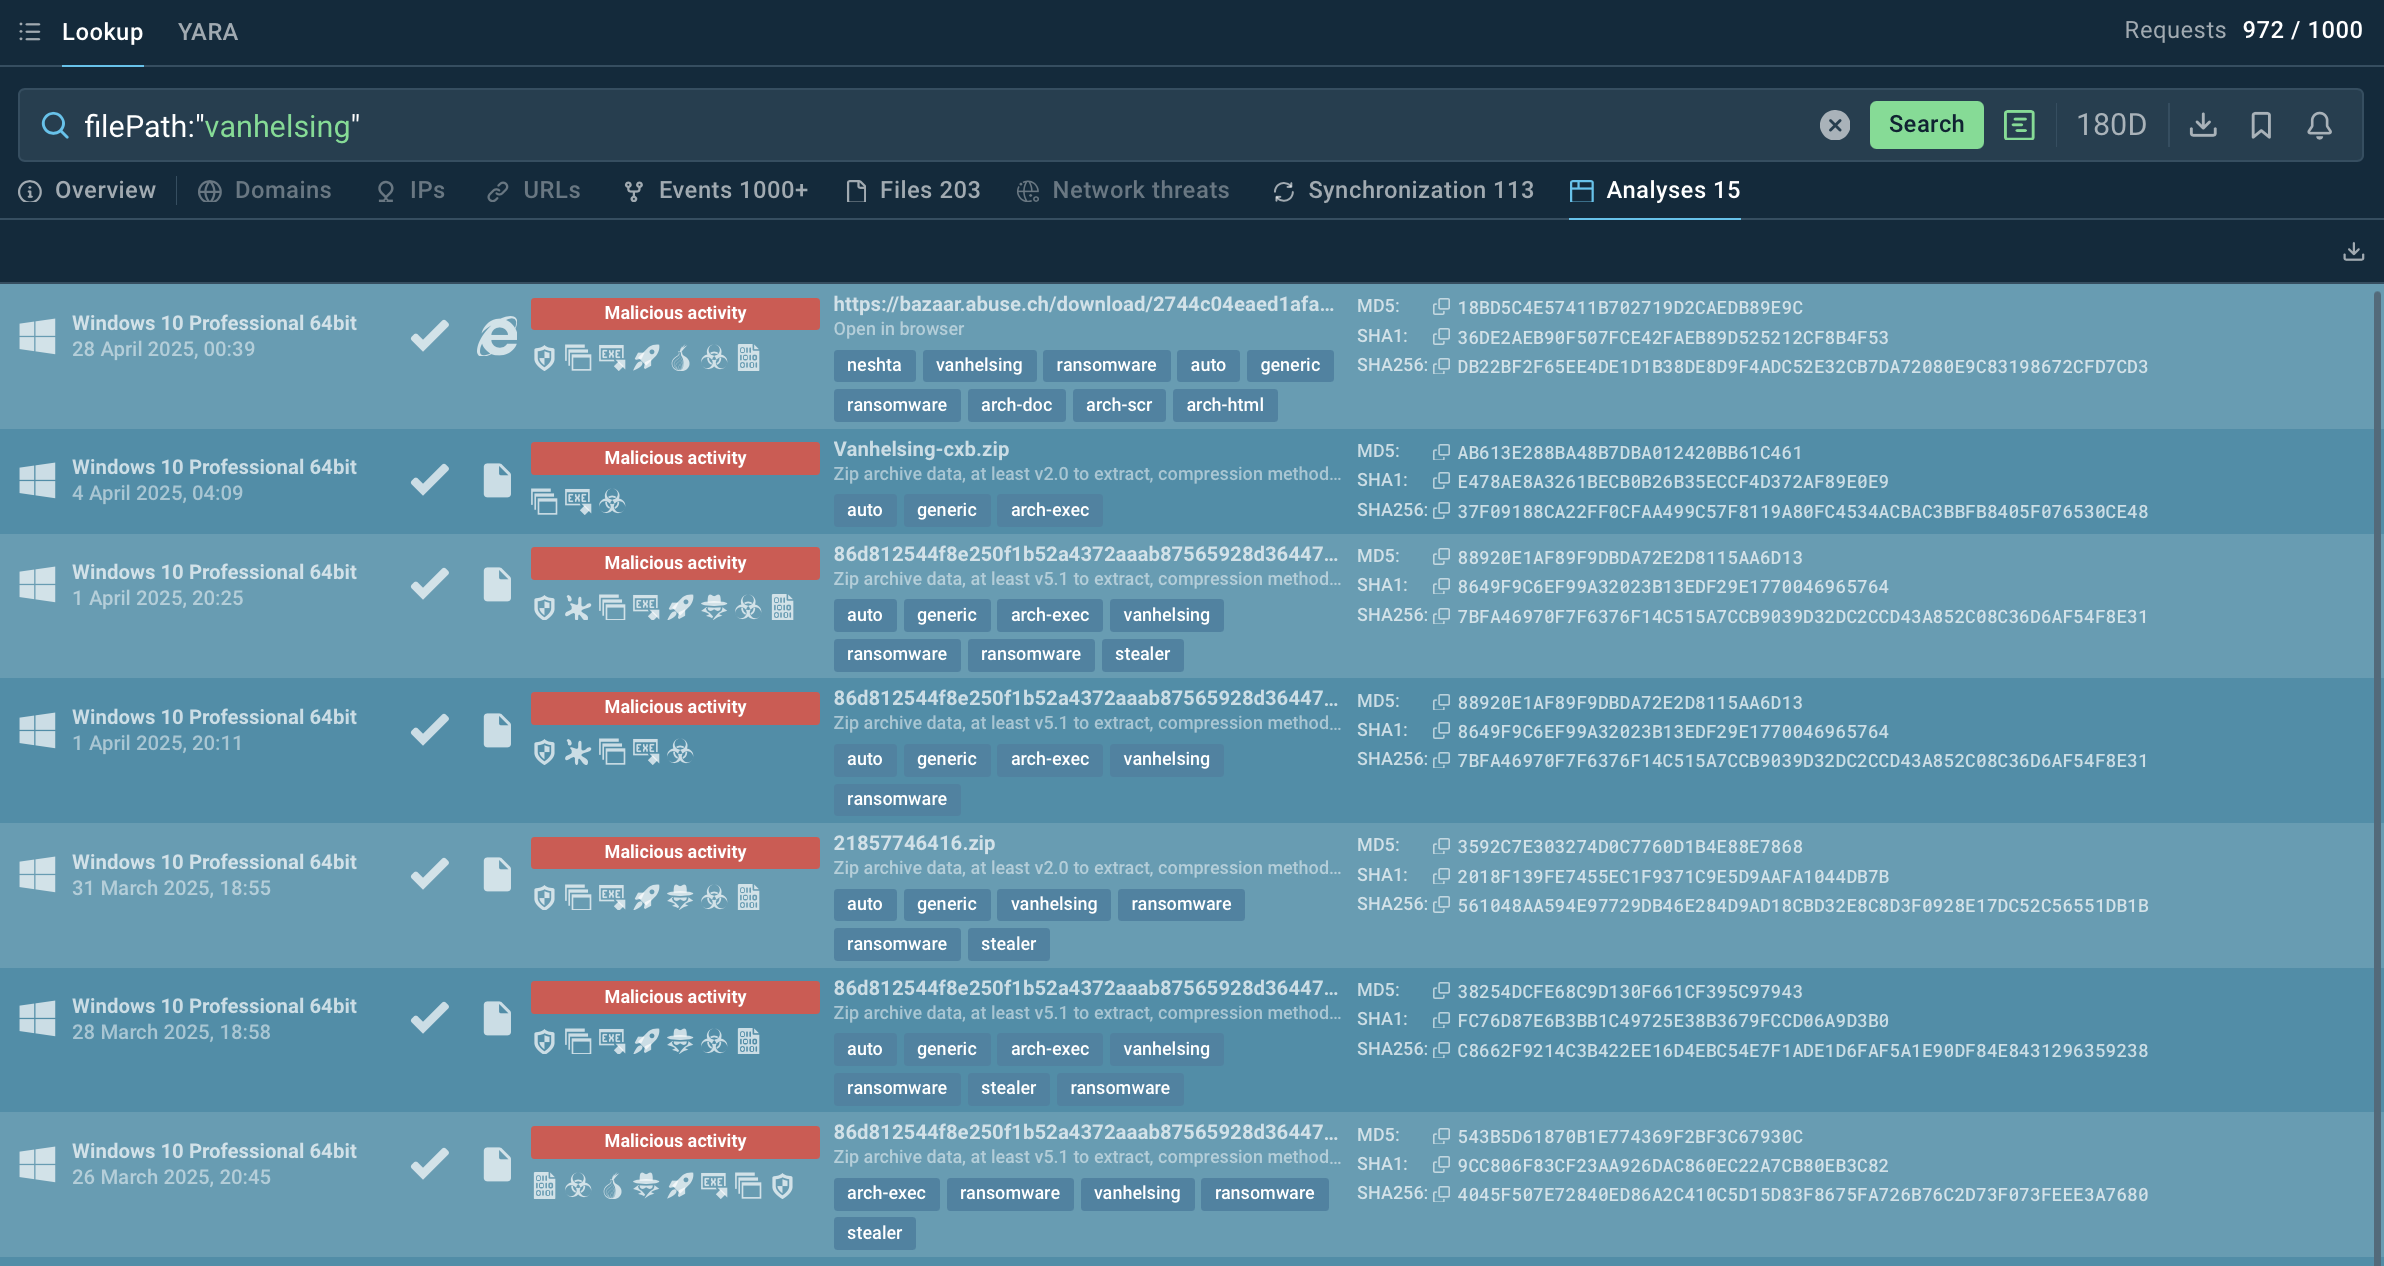
VanHelsing ransomware samples Sandbox malware analyses featuring VanHelsing
filePath:"vanhelsing"

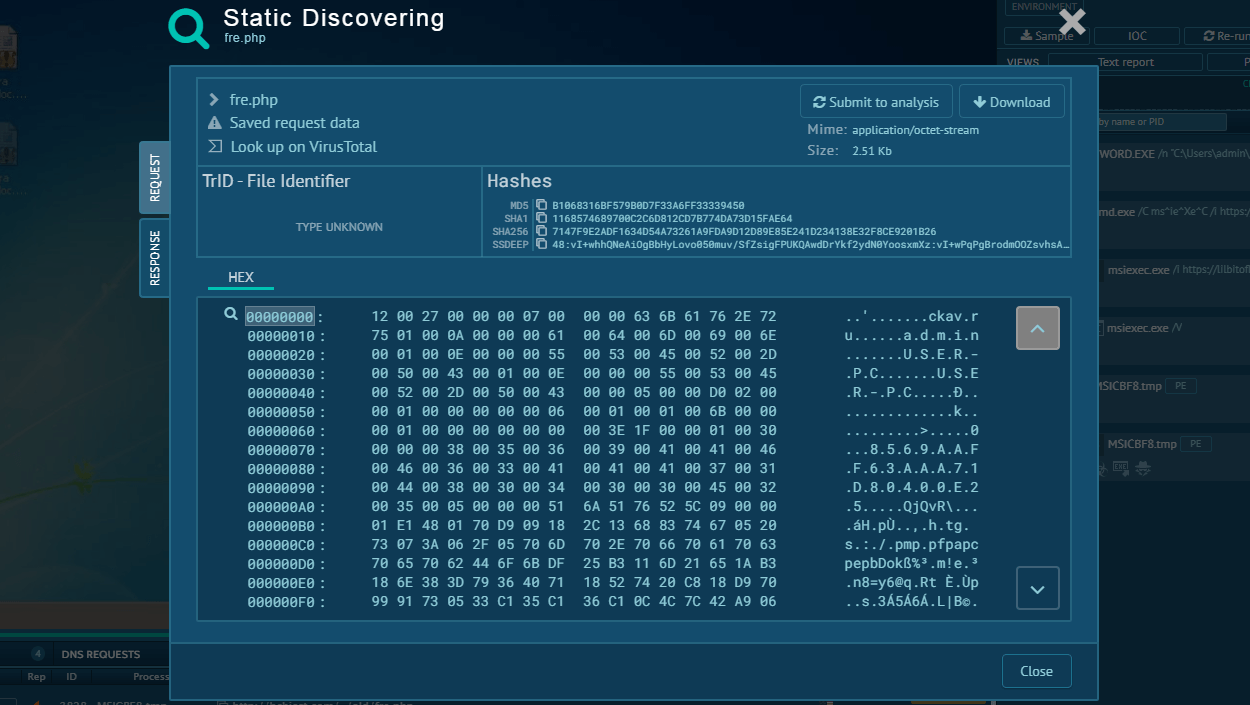
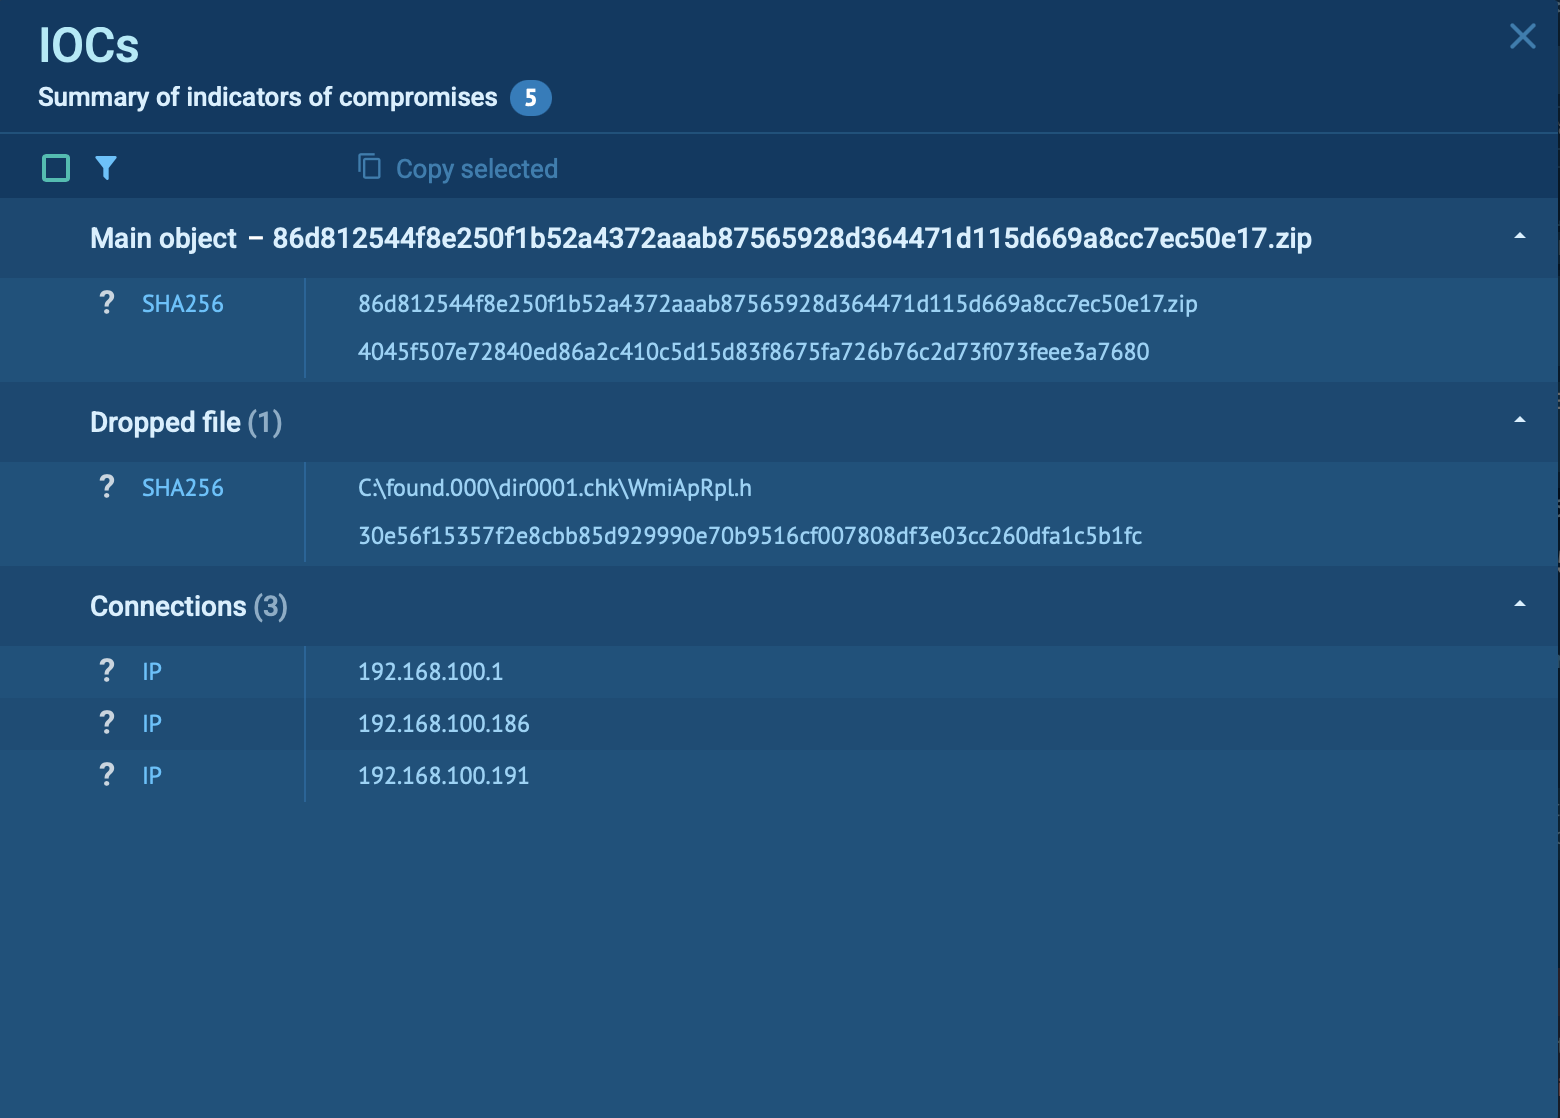
VanHelsing IOCs in Sandbox Additional VanHelsing IOCs retrieved in a sandbox analysis session

Integrate ANY.RUN’s threat intelligence solutions in your company

Contact us

Conclusion

VanHelsing’s rapid growth and evolving tactics suggest it will remain a significant threat. Its multi-platform capabilities could lead to attacks on critical infrastructure, while the RaaS model ensures scalability. Organizations must adopt a proactive, intelligence-driven approach to stay ahead of this threat.

By combining robust cybersecurity measures, advanced detection tools, and real-time threat intelligence provided by TI Lookup, businesses can mitigate the risks posed by VanHelsing and similar ransomware strains.
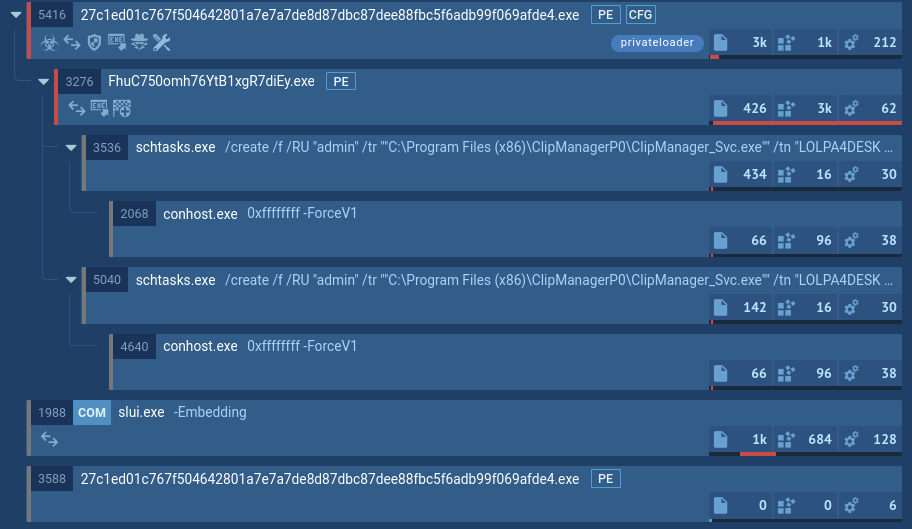
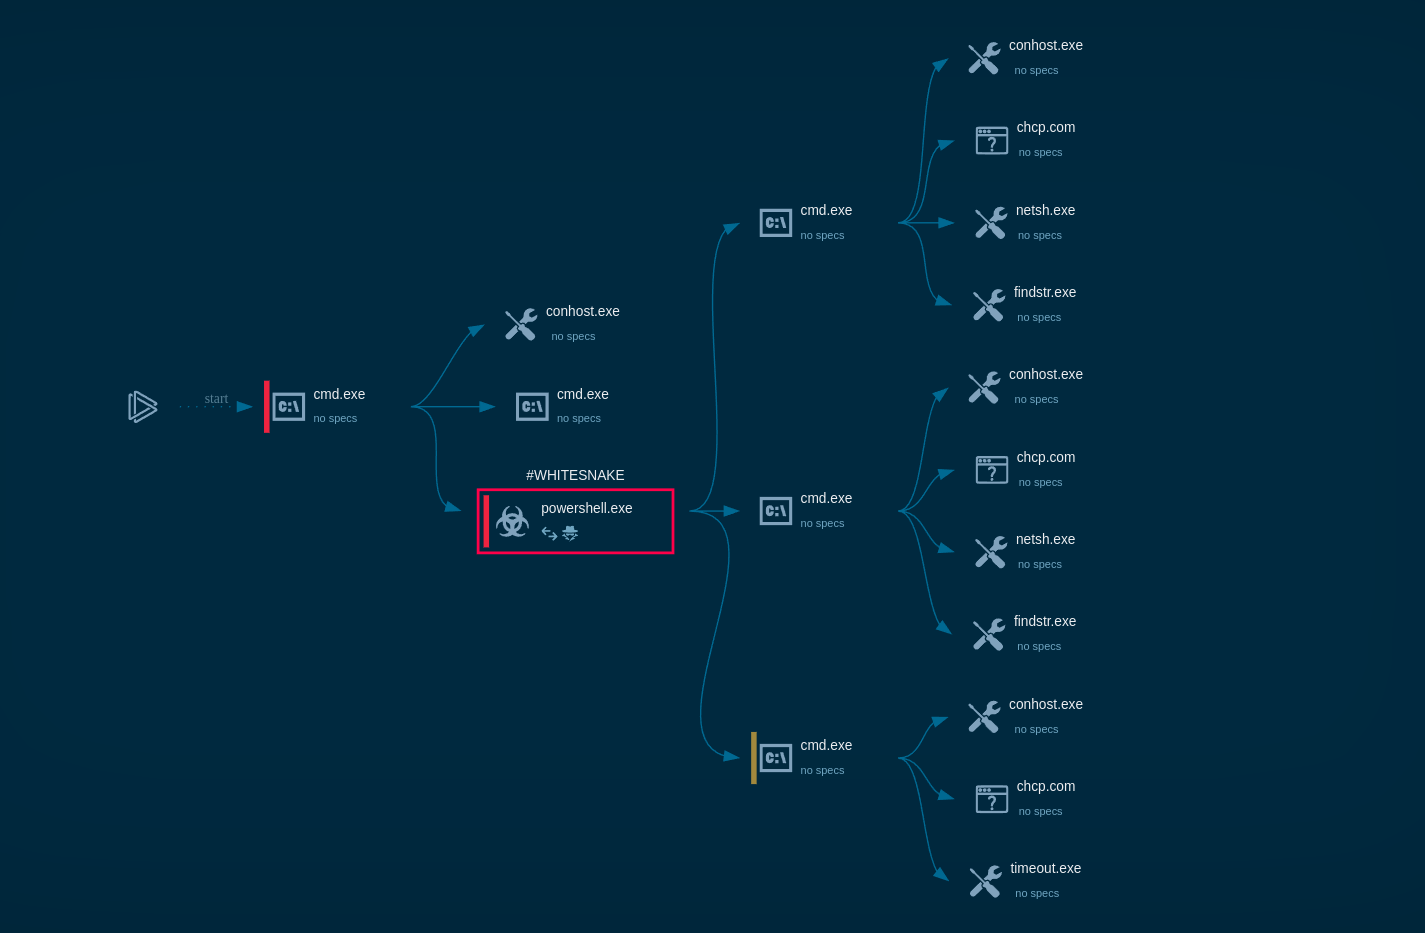
Use Threat Intelligence Lookup to research VanHelsing and prevent incidents: start with 50 test searches.

HAVE A LOOK AT

Loader screenshot
Loader
loader downloader
A loader is malicious software that infiltrates devices to deliver malicious payloads. This malware is capable of infecting victims’ computers, analyzing their system information, and installing other types of threats, such as trojans or stealers. Criminals usually deliver loaders through phishing emails and links by relying on social engineering to trick users into downloading and running their executables. Loaders employ advanced evasion and persistence tactics to avoid detection.
Read More
WhiteSnake screenshot
WhiteSnake
whitesnake
WhiteSnake is a stealer with advanced remote access capabilities. The attackers using this malicious software can control infected computers and carry out different malicious activities, including stealing sensitive files and data, recording audio, and logging keystrokes. WhiteSnake is sold on underground forums and often spreads through phishing emails.
Read More
LokiBot screenshot
LokiBot
lokibot loader trojan
LokiBot was developed in 2015 to steal information from a variety of applications. Despite the age, this malware is still rather popular among cybercriminals.
Read More
MassLogger screenshot
MassLogger
masslogger
MassLogger is a credential stealer and keylogger first identified in April 2020. It has been actively used in cyber campaigns to exfiltrate sensitive information from compromised systems. It is designed for easy use by less tech-savvy actors and is prominent for the capability of spreading via USB drives. It targets both individuals and organizations in various industries, mostly in Europe and the USA.
Read More
Cactus Ransomware screenshot
Cactus ransomware-as-a-service (RaaS) was first caught in March 2023 targeting corporate networks. It became known for its self-encrypting payload and double extortion tactics. Cactus primarily targets large enterprises across industries in finance, manufacturing, IT, and healthcare. It is known for using custom encryption techniques, remote access tools, and penetration testing frameworks to maximize damage.
Read More
DragonForce screenshot
DragonForce
dragonforce
DragonForce is a ransomware strain operating under the Ransomware-as-a-Service (RaaS) model. First reported in December 2023, it encrypts files with ChaCha8, renames them with random strings, and appends “.dragonforce_encrypted.” By disabling backups, wiping recovery, and spreading across SMB shares, DragonForce maximizes damage and pressures victims into multimillion-dollar ransom negotiations. It has targeted manufacturing, construction, IT, healthcare, and retail sectors worldwide, making it a severe threat to modern enterprises.
Read More